Complete Technical Paper Content — Memory Forensics Based Malware Detection Using Volatility
Overview & System Context
Memory Forensics Based Malware Detection Using Volatility: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~7991 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Protect your communities and organizations by giving investigative teams an advantage with stronger digital evidence.
Private sector organizations face mounting pressure to conduct fast, thorough investigations while… 2. System Architecture & Core Working Principles Whether it’s ransomware, business email compromise, data exfiltration, or an insider threat,… Complete the company & contact information form below and sales will be in touch with you shortly.
3. Software Implementation, Frameworks & Protocols Master the Volatility Framework with this complete 2025 guide. Learn how to install, configure, and use Volatility 3 for advanced memory forensics, malware hunting, and process analysis. The Volatility Framework is the world's most widely used framework for extracting digital artifacts from volatile memory (RAM) samples. Maintained by the Volatility Foundation, it is a completely open-source tool written in Python that allows forensic investigators to analyze the runtime state of a system. While traditional digital forensics focuses on data stored on hard drives (dead-box forensics), Volatility focuses on the data that disappears the moment a computer is turned off. By 2025, Volatility 3 has largely replaced the legacy Volatility 2, bringing significant improvements in speed, ease of use, and cross-platform compatibility. It supports memory dumps from Windows, Linux, and macOS systems, making it a unified solution for incident responders dealing with diverse environments. Its plugin-based architecture allows the community to write custom scripts to detect the latest malware strains, ensuring the tool remains relevant against evolving cyber threats. 2. The Critical Importance of Memory Forensics In modern cyber investigations, analyzing the hard drive alone is no longer sufficient. Sophisticated adversaries use "fileless" malware that operates entirely within the computer's RAM, leaving no trace on the physical disk.
Without memory forensics, these attacks would remain completely invisible to an investigator. Memory analysis allows investigators to retrieve ephemeral data that is critical for solving cases. This includes unencrypted passwords, encryption keys (for BitLocker or TrueCrypt), open network connections to Command and Control (C2) servers, and the content of clipboard buffers. It essentially provides a snapshot of the crime scene exactly as it was happening, capturing the attacker's tools and techniques in real-time. For incident response teams, Volatility is the primary weapon for identifying the "patient zero" process and understanding the scope of a compromise. 3. Installation and Setup Guide Setting up Volatility 3 is more streamlined than its predecessor because it removes the dependency on specific profiles. It requires Python 3 and a few dependencies. Step-by-Step Installation: Prerequisites: Ensure Python 3.6 or later is installed on your analysis machine (Linux, Windows, or macOS). Download: Clone the official repository from GitHub or download the latest stable release zip file. Dependencies: Install the required Python libraries using pip. Key libraries include `pefile` for Windows analysis and `yara-python` for malware scanning. Symbol Tables: Unlike Volatility 2 which required users to determine the exact OS profile, Volatility 3 uses symbol tables. It can often download the necessary symbol files (PDBs) from Microsoft's symbol server automatically during the first run, provided there is internet access. 4. Core Analysis Workflow The standard workflow for a memory investigation follows a logical path: Identify the system, list running processes, check for network activity, and hunt for injected malicious code. 4.1 Process Analysis (The First Step) Overview: The first goal is to determine what programs were running. Malware often disguises itself as legitimate system processes (like svchost.exe) but gives itself away through subtle anomalies. Key Plugins: windows.pslist: Lists active processes by walking the doubly-linked list in the kernel. This is the baseline view of the system. windows.psscan: Scans the memory dump for process headers (EPROCESS blocks). This helps identify hidden processes that have been unlinked by rootkits to hide from the standard task manager. windows.pstree: Visualizes processes in a parent-child tree structure. This is crucial for spotting anomalies, such as `cmd.exe` spawning from `winword.exe`, which often indicates a malicious macro payload. 4.2 Network Connection Analysis Overview: Investigating network artifacts helps identify if the compromised machine was communicating with external attacker infrastructure. Key Plugins: windows.netscan: Scans for network connections and sockets. It works on modern Windows versions (Vista and later) and shows local and remote IP addresses, ports, and the state of the connection (ESTABLISHED, LISTENING).
windows.netstat: Similar to the netstat command on a live system, this plugin retrieves the network stack information. Why It Is Essential: Mapping a malicious process ID (PID) to an established connection with a known bad IP address provides the "smoking gun" needed to confirm data exfiltration or C2 activity. 4.3 Malware Hunting and Code Injection Overview: Advanced malware hides code inside legitimate processes (injection) or uses packing techniques to avoid detection by antivirus. Key Plugins: windows.malfind: Scans for memory pages that have "Execute" and "Write" permissions simultaneously, a common indicator of code injection. It outputs a hex dump and assembly code for verification. yarascan: Allows investigators to scan the entire memory dump for specific strings or byte patterns using YARA rules. This is powerful for finding malware signatures even if the process list looks clean. windows.dlllist: Lists the Dynamic Link Libraries (DLLs) loaded by a process. This helps identify malicious DLLs that have been sideloaded into legitimate applications. 4.4 Extraction of Secrets and Passwords Overview: One of the most unique capabilities of memory forensics is the recovery of credentials that exist in cleartext or reversible formats in RAM. Key Plugins: windows.hashdump: Extracts NTLM password hashes from the registry hives loaded in memory. These hashes can be cracked to recover user passwords. windows.lsadump: Recovers LSA secrets, which may include service account passwords and default logic credentials. windows.filescan: While not a password tool per se, this scans memory for file objects, allowing investigators to extract files (like a password.txt or config file) directly from RAM before they were saved to disk. Comparative Analysis: Volatility 2 vs. Volatility 3 Feature Category Volatility 2 (Legacy) Volatility 3 (Modern) Investigator Benefit (Vol 3) Language Base Python 2.7 (Deprecated) Python 3 Better performance and long-term support Profile Selection Manual (--profile req.) Automatic (Symbol Tables) Faster setup, no guessing profiles Execution Speed Slower on large dumps Significantly Faster Analyzes gigabytes of RAM quickly Plugin Naming Simple (e.g., pslist) Structured (windows.pslist) Clearer distinction between OS plugins OS Support Win, Linux, Mac (Complex) Unified Cross-Platform Consistent commands across OSs Output Format Text, Grepable JSON, CSV, Pretty Text Easier integration with other tools Community Status End of Life Active Development Access to latest features and fixes 6. Future Trends in Memory Forensics As operating systems evolve, memory forensics is adapting to new challenges. The shift towards cloud computing has led to the development of tools for acquiring memory from virtual machines (VMs) and cloud instances without pausing them. We are also seeing a rise in automation, where Volatility is integrated into SOAR (Security Orchestration, Automation, and Response) platforms to automatically analyze memory dumps from triggered alerts. Furthermore, with the increasing use of encryption by malware, the ability of Volatility to extract encryption keys from RAM remains a critical area of focus for future development. 7. Career Scope for Memory Analysts Expertise in Volatility and memory forensics is a highly specialized skill that commands a premium in the cybersecurity job market. While general analysts focus on logs and disk artifacts, memory analysts can uncover the most sophisticated threats. Job Roles: Advanced Malware Analyst Incident Response Lead Threat Hunter Digital Forensics Consultant Salary Outlook: Professionals with deep memory forensics skills often earn between $100,000 and $160,000 annually, with specialized consultants in private firms earning significantly more depending on their experience and certifications. 8. Conclusion The Volatility Framework remains the definitive tool for memory forensics in 2025. Its transition to Python 3 and the removal of complex profile requirements have made it more accessible than ever, without sacrificing the power needed to hunt advanced adversaries. Whether you are dealing with a rootkit, a ransomware infection, or an insider threat, Volatility provides the visibility into the system's runtime state that no other tool can match. Mastering this framework is not just a technical skill; it is a necessity for any modern digital investigator aiming to see the complete picture of a cyber incident. Frequently Asked Questions (FAQ) What is the Volatility Framework? Volatility is an open-source command-line tool used to analyze volatile memory (RAM) dumps for digital forensics and incident response. Is Volatility free to use? Yes, Volatility is completely free and open-source software, released under the Volatility Software License. What is the difference between Volatility 2 and 3? Volatility 3 uses Python 3, is much faster, and automatically detects profiles using symbol tables, whereas Volatility 2 used Python 2. Can Volatility capture memory? No, Volatility analyzes memory. You need a separate acquisition tool like FTK Imager or WinPmem to capture the RAM first. What operating systems can Volatility analyze? It can analyze memory dumps from Windows, Linux, and macOS systems, covering almost all modern versions. What is a memory profile? In Volatility 2, a profile defined the OS version and architecture.
Volatility 3 replaces this with automatic symbol table detection. How do I list running processes? Use the `windows.pslist` plugin in Volatility 3 (or `pslist` in Volatility 2) to see all active processes. Can Volatility find hidden malware? Yes, plugins like `psscan` and `malfind` are designed specifically to detect hidden processes and injected malicious code. Does Volatility work on Linux? Yes, the framework itself runs on Linux, and it includes a suite of plugins specifically for analyzing Linux memory dumps. What is the netscan plugin? The netscan plugin scans the memory for active network connections and listening ports, useful for finding C2 communications. How do I install Volatility 3? You can clone the GitHub repository and install the required dependencies using Python 3's pip package manager. Can I recover passwords with Volatility? Yes, plugins like `hashdump` can recover NTLM hashes, and `lsadump` can recover LSA secrets from Windows memory. What file formats does Volatility support? It supports raw dumps (.dd, .raw), crash dumps, and hibernation files, among others. What is a symbol table? A symbol table acts as a map for Volatility 3 to understand the internal structures of the specific operating system being analyzed. Is there a GUI for Volatility? Volatility is a CLI tool, but third-party GUIs like "Volatility Workbench" exist to make it easier to use. What is malfind used for? The malfind plugin searches for memory pages that are both executable and writable, a strong indicator of code injection. Can I extract files from RAM? Yes, the `dumpfiles` or `filescan` plugins allow you to carve and extract files directly from the memory image. Why is memory forensics important? It allows investigators to see the runtime state of the system, including unencrypted data and fileless malware that disk forensics misses. Does Volatility support Windows 11? Yes, Volatility 3 fully supports memory dumps from Windows 10 and Windows 11. What is the dlllist command? The dlllist command lists all the dynamic link libraries (DLLs) loaded by a specific process, helping to spot malicious injections.
4. Practical Deployment, Analysis & Case Studies By 2025, Volatility 3 has largely replaced the legacy Volatility 2, bringing significant improvements in speed, ease of use, and cross-platform compatibility. It supports memory dumps from Windows, Linux, and macOS systems, making it a unified solution for incident responders dealing with diverse environments. Its plugin-based architecture allows the community to write custom scripts to detect the latest malware strains, ensuring the tool remains relevant against evolving cyber threats. 2. The Critical Importance of Memory Forensics In modern cyber investigations, analyzing the hard drive alone is no longer sufficient.
Sophisticated adversaries use "fileless" malware that operates entirely within the computer's RAM, leaving no trace on the physical disk. Without memory forensics, these attacks would remain completely invisible to an investigator. Memory analysis allows investigators to retrieve ephemeral data that is critical for solving cases. This includes unencrypted passwords, encryption keys (for BitLocker or TrueCrypt), open network connections to Command and Control (C2) servers, and the content of clipboard buffers. It essentially provides a snapshot of the crime scene exactly as it was happening, capturing the attacker's tools and techniques in real-time. For incident response teams, Volatility is the primary weapon for identifying the "patient zero" process and understanding the scope of a compromise. 3. Installation and Setup Guide Setting up Volatility 3 is more streamlined than its predecessor because it removes the dependency on specific profiles. It requires Python 3 and a few dependencies. Step-by-Step Installation: Prerequisites: Ensure Python 3.6 or later is installed on your analysis machine (Linux, Windows, or macOS). Download: Clone the official repository from GitHub or download the latest stable release zip file. Dependencies: Install the required Python libraries using pip. Key libraries include `pefile` for Windows analysis and `yara-python` for malware scanning. Symbol Tables: Unlike Volatility 2 which required users to determine the exact OS profile, Volatility 3 uses symbol tables. It can often download the necessary symbol files (PDBs) from Microsoft's symbol server automatically during the first run, provided there is internet access. 4. Core Analysis Workflow The standard workflow for a memory investigation follows a logical path: Identify the system, list running processes, check for network activity, and hunt for injected malicious code. 4.1 Process Analysis (The First Step) Overview: The first goal is to determine what programs were running. Malware often disguises itself as legitimate system processes (like svchost.exe) but gives itself away through subtle anomalies. Key Plugins: windows.pslist: Lists active processes by walking the doubly-linked list in the kernel. This is the baseline view of the system. windows.psscan: Scans the memory dump for process headers (EPROCESS blocks). This helps identify hidden processes that have been unlinked by rootkits to hide from the standard task manager. windows.pstree: Visualizes processes in a parent-child tree structure. This is crucial for spotting anomalies, such as `cmd.exe` spawning from `winword.exe`, which often indicates a malicious macro payload. 4.2 Network Connection Analysis Overview: Investigating network artifacts helps identify if the compromised machine was communicating with external attacker infrastructure. Key Plugins: windows.netscan: Scans for network connections and sockets. It works on modern Windows versions (Vista and later) and shows local and remote IP addresses, ports, and the state of the connection (ESTABLISHED, LISTENING).
windows.netstat: Similar to the netstat command on a live system, this plugin retrieves the network stack information. Why It Is Essential: Mapping a malicious process ID (PID) to an established connection with a known bad IP address provides the "smoking gun" needed to confirm data exfiltration or C2 activity. 4.3 Malware Hunting and Code Injection Overview: Advanced malware hides code inside legitimate processes (injection) or uses packing techniques to avoid detection by antivirus. Key Plugins: windows.malfind: Scans for memory pages that have "Execute" and "Write" permissions simultaneously, a common indicator of code injection. It outputs a hex dump and assembly code for verification. yarascan: Allows investigators to scan the entire memory dump for specific strings or byte patterns using YARA rules. This is powerful for finding malware signatures even if the process list looks clean. windows.dlllist: Lists the Dynamic Link Libraries (DLLs) loaded by a process. This helps identify malicious DLLs that have been sideloaded into legitimate applications. 4.4 Extraction of Secrets and Passwords Overview: One of the most unique capabilities of memory forensics is the recovery of credentials that exist in cleartext or reversible formats in RAM. Key Plugins: windows.hashdump: Extracts NTLM password hashes from the registry hives loaded in memory. These hashes can be cracked to recover user passwords. windows.lsadump: Recovers LSA secrets, which may include service account passwords and default logic credentials. windows.filescan: While not a password tool per se, this scans memory for file objects, allowing investigators to extract files (like a password.txt or config file) directly from RAM before they were saved to disk. Comparative Analysis: Volatility 2 vs. Volatility 3 Feature Category Volatility 2 (Legacy) Volatility 3 (Modern) Investigator Benefit (Vol 3) Language Base Python 2.7 (Deprecated) Python 3 Better performance and long-term support Profile Selection Manual (--profile req.) Automatic (Symbol Tables) Faster setup, no guessing profiles Execution Speed Slower on large dumps Significantly Faster Analyzes gigabytes of RAM quickly Plugin Naming Simple (e.g., pslist) Structured (windows.pslist) Clearer distinction between OS plugins OS Support Win, Linux, Mac (Complex) Unified Cross-Platform Consistent commands across OSs Output Format Text, Grepable JSON, CSV, Pretty Text Easier integration with other tools Community Status End of Life Active Development Access to latest features and fixes 6. Future Trends in Memory Forensics As operating systems evolve, memory forensics is adapting to new challenges. The shift towards cloud computing has led to the development of tools for acquiring memory from virtual machines (VMs) and cloud instances without pausing them. We are also seeing a rise in automation, where Volatility is integrated into SOAR (Security Orchestration, Automation, and Response) platforms to automatically analyze memory dumps from triggered alerts. Furthermore, with the increasing use of encryption by malware, the ability of Volatility to extract encryption keys from RAM remains a critical area of focus for future development. 7. Career Scope for Memory Analysts Expertise in Volatility and memory forensics is a highly specialized skill that commands a premium in the cybersecurity job market. While general analysts focus on logs and disk artifacts, memory analysts can uncover the most sophisticated threats. Job Roles: Advanced Malware Analyst Incident Response Lead Threat Hunter Digital Forensics Consultant Salary Outlook: Professionals with deep memory forensics skills often earn between $100,000 and $160,000 annually, with specialized consultants in private firms earning significantly more depending on their experience and certifications. 8. Conclusion The Volatility Framework remains the definitive tool for memory forensics in 2025. Its transition to Python 3 and the removal of complex profile requirements have made it more accessible than ever, without sacrificing the power needed to hunt advanced adversaries. Whether you are dealing with a rootkit, a ransomware infection, or an insider threat, Volatility provides the visibility into the system's runtime state that no other tool can match. Mastering this framework is not just a technical skill; it is a necessity for any modern digital investigator aiming to see the complete picture of a cyber incident. Frequently Asked Questions (FAQ) What is the Volatility Framework? Volatility is an open-source command-line tool used to analyze volatile memory (RAM) dumps for digital forensics and incident response. Is Volatility free to use? Yes, Volatility is completely free and open-source software, released under the Volatility Software License. What is the difference between Volatility 2 and 3? Volatility 3 uses Python 3, is much faster, and automatically detects profiles using symbol tables, whereas Volatility 2 used Python 2. Can Volatility capture memory? No, Volatility analyzes memory. You need a separate acquisition tool like FTK Imager or WinPmem to capture the RAM first. What operating systems can Volatility analyze? It can analyze memory dumps from Windows, Linux, and macOS systems, covering almost all modern versions. What is a memory profile? In Volatility 2, a profile defined the OS version and architecture.
Volatility 3 replaces this with automatic symbol table detection. How do I list running processes? Use the `windows.pslist` plugin in Volatility 3 (or `pslist` in Volatility 2) to see all active processes. Can Volatility find hidden malware? Yes, plugins like `psscan` and `malfind` are designed specifically to detect hidden processes and injected malicious code. Does Volatility work on Linux? Yes, the framework itself runs on Linux, and it includes a suite of plugins specifically for analyzing Linux memory dumps. What is the netscan plugin? The netscan plugin scans the memory for active network connections and listening ports, useful for finding C2 communications. How do I install Volatility 3? You can clone the GitHub repository and install the required dependencies using Python 3's pip package manager. Can I recover passwords with Volatility? Yes, plugins like `hashdump` can recover NTLM hashes, and `lsadump` can recover LSA secrets from Windows memory. What file formats does Volatility support? It supports raw dumps (.dd, .raw), crash dumps, and hibernation files, among others. What is a symbol table? A symbol table acts as a map for Volatility 3 to understand the internal structures of the specific operating system being analyzed. Is there a GUI for Volatility? Volatility is a CLI tool, but third-party GUIs like "Volatility Workbench" exist to make it easier to use. What is malfind used for? The malfind plugin searches for memory pages that are both executable and writable, a strong indicator of code injection. Can I extract files from RAM? Yes, the `dumpfiles` or `filescan` plugins allow you to carve and extract files directly from the memory image. Why is memory forensics important? It allows investigators to see the runtime state of the system, including unencrypted data and fileless malware that disk forensics misses. Does Volatility support Windows 11? Yes, Volatility 3 fully supports memory dumps from Windows 10 and Windows 11. What is the dlllist command? The dlllist command lists all the dynamic link libraries (DLLs) loaded by a specific process, helping to spot malicious injections.
In modern cyber investigations, analyzing the hard drive alone is no longer sufficient. Sophisticated adversaries use "fileless" malware that operates entirely within the computer's RAM, leaving no trace on the physical disk. Without memory forensics, these attacks would remain completely invisible to an investigator. Memory analysis allows investigators to retrieve ephemeral data that is critical for solving cases. This includes unencrypted passwords, encryption keys (for BitLocker or TrueCrypt), open network connections to Command and Control (C2) servers, and the content of clipboard buffers. It essentially provides a snapshot of the crime scene exactly as it was happening, capturing the attacker's tools and techniques in real-time. For incident response teams, Volatility is the primary weapon for identifying the "patient zero" process and understanding the scope of a compromise. 3. Installation and Setup Guide Setting up Volatility 3 is more streamlined than its predecessor because it removes the dependency on specific profiles. It requires Python 3 and a few dependencies. Step-by-Step Installation: Prerequisites: Ensure Python 3.6 or later is installed on your analysis machine (Linux, Windows, or macOS).
Download: Clone the official repository from GitHub or download the latest stable release zip file. Dependencies: Install the required Python libraries using pip. Key libraries include `pefile` for Windows analysis and `yara-python` for malware scanning. Symbol Tables: Unlike Volatility 2 which required users to determine the exact OS profile, Volatility 3 uses symbol tables. It can often download the necessary symbol files (PDBs) from Microsoft's symbol server automatically during the first run, provided there is internet access. 4. Core Analysis Workflow The standard workflow for a memory investigation follows a logical path: Identify the system, list running processes, check for network activity, and hunt for injected malicious code. 4.1 Process Analysis (The First Step) Overview: The first goal is to determine what programs were running. Malware often disguises itself as legitimate system processes (like svchost.exe) but gives itself away through subtle anomalies. Key Plugins: windows.pslist: Lists active processes by walking the doubly-linked list in the kernel. This is the baseline view of the system.
windows.psscan: Scans the memory dump for process headers (EPROCESS blocks). This helps identify hidden processes that have been unlinked by rootkits to hide from the standard task manager. windows.pstree: Visualizes processes in a parent-child tree structure. This is crucial for spotting anomalies, such as `cmd.exe` spawning from `winword.exe`, which often indicates a malicious macro payload. 4.2 Network Connection Analysis Overview: Investigating network artifacts helps identify if the compromised machine was communicating with external attacker infrastructure. Key Plugins: windows.netscan: Scans for network connections and sockets. It works on modern Windows versions (Vista and later) and shows local and remote IP addresses, ports, and the state of the connection (ESTABLISHED, LISTENING). windows.netstat: Similar to the netstat command on a live system, this plugin retrieves the network stack information. Why It Is Essential: Mapping a malicious process ID (PID) to an established connection with a known bad IP address provides the "smoking gun" needed to confirm data exfiltration or C2 activity. 4.3 Malware Hunting and Code Injection Overview: Advanced malware hides code inside legitimate processes (injection) or uses packing techniques to avoid detection by antivirus. Key Plugins: windows.malfind: Scans for memory pages that have "Execute" and "Write" permissions simultaneously, a common indicator of code injection. It outputs a hex dump and assembly code for verification. yarascan: Allows investigators to scan the entire memory dump for specific strings or byte patterns using YARA rules. This is powerful for finding malware signatures even if the process list looks clean. windows.dlllist: Lists the Dynamic Link Libraries (DLLs) loaded by a process. This helps identify malicious DLLs that have been sideloaded into legitimate applications. 4.4 Extraction of Secrets and Passwords Overview: One of the most unique capabilities of memory forensics is the recovery of credentials that exist in cleartext or reversible formats in RAM. Key Plugins: windows.hashdump: Extracts NTLM password hashes from the registry hives loaded in memory. These hashes can be cracked to recover user passwords. windows.lsadump: Recovers LSA secrets, which may include service account passwords and default logic credentials. windows.filescan: While not a password tool per se, this scans memory for file objects, allowing investigators to extract files (like a password.txt or config file) directly from RAM before they were saved to disk. Comparative Analysis: Volatility 2 vs. Volatility 3 Feature Category Volatility 2 (Legacy) Volatility 3 (Modern) Investigator Benefit (Vol 3) Language Base Python 2.7 (Deprecated) Python 3 Better performance and long-term support Profile Selection Manual (--profile req.) Automatic (Symbol Tables) Faster setup, no guessing profiles Execution Speed Slower on large dumps Significantly Faster Analyzes gigabytes of RAM quickly Plugin Naming Simple (e.g., pslist) Structured (windows.pslist) Clearer distinction between OS plugins OS Support Win, Linux, Mac (Complex) Unified Cross-Platform Consistent commands across OSs Output Format Text, Grepable JSON, CSV, Pretty Text Easier integration with other tools Community Status End of Life Active Development Access to latest features and fixes 6. Future Trends in Memory Forensics As operating systems evolve, memory forensics is adapting to new challenges. The shift towards cloud computing has led to the development of tools for acquiring memory from virtual machines (VMs) and cloud instances without pausing them. We are also seeing a rise in automation, where Volatility is integrated into SOAR (Security Orchestration, Automation, and Response) platforms to automatically analyze memory dumps from triggered alerts. Furthermore, with the increasing use of encryption by malware, the ability of Volatility to extract encryption keys from RAM remains a critical area of focus for future development. 7. Career Scope for Memory Analysts Expertise in Volatility and memory forensics is a highly specialized skill that commands a premium in the cybersecurity job market. While general analysts focus on logs and disk artifacts, memory analysts can uncover the most sophisticated threats. Job Roles: Advanced Malware Analyst Incident Response Lead Threat Hunter Digital Forensics Consultant Salary Outlook: Professionals with deep memory forensics skills often earn between $100,000 and $160,000 annually, with specialized consultants in private firms earning significantly more depending on their experience and certifications. 8. Conclusion The Volatility Framework remains the definitive tool for memory forensics in 2025. Its transition to Python 3 and the removal of complex profile requirements have made it more accessible than ever, without sacrificing the power needed to hunt advanced adversaries. Whether you are dealing with a rootkit, a ransomware infection, or an insider threat, Volatility provides the visibility into the system's runtime state that no other tool can match. Mastering this framework is not just a technical skill; it is a necessity for any modern digital investigator aiming to see the complete picture of a cyber incident. Frequently Asked Questions (FAQ) What is the Volatility Framework? Volatility is an open-source command-line tool used to analyze volatile memory (RAM) dumps for digital forensics and incident response. Is Volatility free to use? Yes, Volatility is completely free and open-source software, released under the Volatility Software License. What is the difference between Volatility 2 and 3? Volatility 3 uses Python 3, is much faster, and automatically detects profiles using symbol tables, whereas Volatility 2 used Python 2. Can Volatility capture memory? No, Volatility analyzes memory. You need a separate acquisition tool like FTK Imager or WinPmem to capture the RAM first. What operating systems can Volatility analyze? It can analyze memory dumps from Windows, Linux, and macOS systems, covering almost all modern versions. What is a memory profile? In Volatility 2, a profile defined the OS version and architecture. Volatility 3 replaces this with automatic symbol table detection. How do I list running processes? Use the `windows.pslist` plugin in Volatility 3 (or `pslist` in Volatility 2) to see all active processes. Can Volatility find hidden malware? Yes, plugins like `psscan` and `malfind` are designed specifically to detect hidden processes and injected malicious code. Does Volatility work on Linux? Yes, the framework itself runs on Linux, and it includes a suite of plugins specifically for analyzing Linux memory dumps. What is the netscan plugin? The netscan plugin scans the memory for active network connections and listening ports, useful for finding C2 communications. How do I install Volatility 3? You can clone the GitHub repository and install the required dependencies using Python 3's pip package manager. Can I recover passwords with Volatility? Yes, plugins like `hashdump` can recover NTLM hashes, and `lsadump` can recover LSA secrets from Windows memory. What file formats does Volatility support? It supports raw dumps (.dd, .raw), crash dumps, and hibernation files, among others. What is a symbol table? A symbol table acts as a map for Volatility 3 to understand the internal structures of the specific operating system being analyzed. Is there a GUI for Volatility? Volatility is a CLI tool, but third-party GUIs like "Volatility Workbench" exist to make it easier to use. What is malfind used for? The malfind plugin searches for memory pages that are both executable and writable, a strong indicator of code injection. Can I extract files from RAM? Yes, the `dumpfiles` or `filescan` plugins allow you to carve and extract files directly from the memory image.
Why is memory forensics important? It allows investigators to see the runtime state of the system, including unencrypted data and fileless malware that disk forensics misses. Does Volatility support Windows 11? Yes, Volatility 3 fully supports memory dumps from Windows 10 and Windows 11. What is the dlllist command? The dlllist command lists all the dynamic link libraries (DLLs) loaded by a specific process, helping to spot malicious injections.
5. Performance Evaluation & Extended Technical Observations Memory analysis allows investigators to retrieve ephemeral data that is critical for solving cases. This includes unencrypted passwords, encryption keys (for BitLocker or TrueCrypt), open network connections to Command and Control (C2) servers, and the content of clipboard buffers. It essentially provides a snapshot of the crime scene exactly as it was happening, capturing the attacker's tools and techniques in real-time. For incident response teams, Volatility is the primary weapon for identifying the "patient zero" process and understanding the scope of a compromise. 3. Installation and Setup Guide Setting up Volatility 3 is more streamlined than its predecessor because it removes the dependency on specific profiles. It requires Python 3 and a few dependencies. Step-by-Step Installation: Prerequisites: Ensure Python 3.6 or later is installed on your analysis machine (Linux, Windows, or macOS). Download: Clone the official repository from GitHub or download the latest stable release zip file. Dependencies: Install the required Python libraries using pip. Key libraries include `pefile` for Windows analysis and `yara-python` for malware scanning. Symbol Tables: Unlike Volatility 2 which required users to determine the exact OS profile, Volatility 3 uses symbol tables. It can often download the necessary symbol files (PDBs) from Microsoft's symbol server automatically during the first run, provided there is internet access. 4. Core Analysis Workflow The standard workflow for a memory investigation follows a logical path: Identify the system, list running processes, check for network activity, and hunt for injected malicious code. 4.1 Process Analysis (The First Step) Overview: The first goal is to determine what programs were running. Malware often disguises itself as legitimate system processes (like svchost.exe) but gives itself away through subtle anomalies. Key Plugins: windows.pslist: Lists active processes by walking the doubly-linked list in the kernel. This is the baseline view of the system. windows.psscan: Scans the memory dump for process headers (EPROCESS blocks). This helps identify hidden processes that have been unlinked by rootkits to hide from the standard task manager.
windows.pstree: Visualizes processes in a parent-child tree structure. This is crucial for spotting anomalies, such as `cmd.exe` spawning from `winword.exe`, which often indicates a malicious macro payload. 4.2 Network Connection Analysis Overview: Investigating network artifacts helps identify if the compromised machine was communicating with external attacker infrastructure. Key Plugins: windows.netscan: Scans for network connections and sockets. It works on modern Windows versions (Vista and later) and shows local and remote IP addresses, ports, and the state of the connection (ESTABLISHED, LISTENING). windows.netstat: Similar to the netstat command on a live system, this plugin retrieves the network stack information. Why It Is Essential: Mapping a malicious process ID (PID) to an established connection with a known bad IP address provides the "smoking gun" needed to confirm data exfiltration or C2 activity. 4.3 Malware Hunting and Code Injection Overview: Advanced malware hides code inside legitimate processes (injection) or uses packing techniques to avoid detection by antivirus. Key Plugins: windows.malfind: Scans for memory pages that have "Execute" and "Write" permissions simultaneously, a common indicator of code injection. It outputs a hex dump and assembly code for verification. yarascan: Allows investigators to scan the entire memory dump for specific strings or byte patterns using YARA rules. This is powerful for finding malware signatures even if the process list looks clean. windows.dlllist: Lists the Dynamic Link Libraries (DLLs) loaded by a process. This helps identify malicious DLLs that have been sideloaded into legitimate applications. 4.4 Extraction of Secrets and Passwords Overview: One of the most unique capabilities of memory forensics is the recovery of credentials that exist in cleartext or reversible formats in RAM. Key Plugins: windows.hashdump: Extracts NTLM password hashes from the registry hives loaded in memory. These hashes can be cracked to recover user passwords. windows.lsadump: Recovers LSA secrets, which may include service account passwords and default logic credentials. windows.filescan: While not a password tool per se, this scans memory for file objects, allowing investigators to extract files (like a password.txt or config file) directly from RAM before they were saved to disk. Comparative Analysis: Volatility 2 vs. Volatility 3 Feature Category Volatility 2 (Legacy) Volatility 3 (Modern) Investigator Benefit (Vol 3) Language Base Python 2.7 (Deprecated) Python 3 Better performance and long-term support Profile Selection Manual (--profile req.) Automatic (Symbol Tables) Faster setup, no guessing profiles Execution Speed Slower on large dumps Significantly Faster Analyzes gigabytes of RAM quickly Plugin Naming Simple (e.g., pslist) Structured (windows.pslist) Clearer distinction between OS plugins OS Support Win, Linux, Mac (Complex) Unified Cross-Platform Consistent commands across OSs Output Format Text, Grepable JSON, CSV, Pretty Text Easier integration with other tools Community Status End of Life Active Development Access to latest features and fixes 6.
Future Trends in Memory Forensics As operating systems evolve, memory forensics is adapting to new challenges. The shift towards cloud computing has led to the development of tools for acquiring memory from virtual machines (VMs) and cloud instances without pausing them. We are also seeing a rise in automation, where Volatility is integrated into SOAR (Security Orchestration, Automation, and Response) platforms to automatically analyze memory dumps from triggered alerts.
Furthermore, with the increasing use of encryption by malware, the ability of Volatility to extract encryption keys from RAM remains a critical area of focus for future development. 7. Career Scope for Memory Analysts Expertise in Volatility and memory forensics is a highly specialized skill that commands a premium in the cybersecurity job market. While general analysts focus on logs and disk artifacts, memory analysts can uncover the most sophisticated threats. Job Roles: Advanced Malware Analyst Incident Response Lead Threat Hunter Digital Forensics Consultant Salary Outlook: Professionals with deep memory forensics skills often earn between $100,000 and $160,000 annually, with specialized consultants in private firms earning significantly more depending on their experience and certifications. 8. Conclusion The Volatility Framework remains the definitive tool for memory forensics in 2025. Its transition to Python 3 and the removal of complex profile requirements have made it more accessible than ever, without sacrificing the power needed to hunt advanced adversaries. Whether you are dealing with a rootkit, a ransomware infection, or an insider threat, Volatility provides the visibility into the system's runtime state that no other tool can match. Mastering this framework is not just a technical skill; it is a necessity for any modern digital investigator aiming to see the complete picture of a cyber incident. Frequently Asked Questions (FAQ) What is the Volatility Framework? Volatility is an open-source command-line tool used to analyze volatile memory (RAM) dumps for digital forensics and incident response. Is Volatility free to use? Yes, Volatility is completely free and open-source software, released under the Volatility Software License. What is the difference between Volatility 2 and 3? Volatility 3 uses Python 3, is much faster, and automatically detects profiles using symbol tables, whereas Volatility 2 used Python 2. Can Volatility capture memory? No, Volatility analyzes memory. You need a separate acquisition tool like FTK Imager or WinPmem to capture the RAM first. What operating systems can Volatility analyze? It can analyze memory dumps from Windows, Linux, and macOS systems, covering almost all modern versions. What is a memory profile? In Volatility 2, a profile defined the OS version and architecture. Volatility 3 replaces this with automatic symbol table detection. How do I list running processes? Use the `windows.pslist` plugin in Volatility 3 (or `pslist` in Volatility 2) to see all active processes. Can Volatility find hidden malware? Yes, plugins like `psscan` and `malfind` are designed specifically to detect hidden processes and injected malicious code.
Does Volatility work on Linux? Yes, the framework itself runs on Linux, and it includes a suite of plugins specifically for analyzing Linux memory dumps. What is the netscan plugin? The netscan plugin scans the memory for active network connections and listening ports, useful for finding C2 communications. How do I install Volatility 3? You can clone the GitHub repository and install the required dependencies using Python 3's pip package manager. Can I recover passwords with Volatility? Yes, plugins like `hashdump` can recover NTLM hashes, and `lsadump` can recover LSA secrets from Windows memory. What file formats does Volatility support? It supports raw dumps (.dd, .raw), crash dumps, and hibernation files, among others. What is a symbol table? A symbol table acts as a map for Volatility 3 to understand the internal structures of the specific operating system being analyzed. Is there a GUI for Volatility? Volatility is a CLI tool, but third-party GUIs like "Volatility Workbench" exist to make it easier to use. What is malfind used for? The malfind plugin searches for memory pages that are both executable and writable, a strong indicator of code injection. Can I extract files from RAM? Yes, the `dumpfiles` or `filescan` plugins allow you to carve and extract files directly from the memory image. Why is memory forensics important? It allows investigators to see the runtime state of the system, including unencrypted data and fileless malware that disk forensics misses. Does Volatility support Windows 11? Yes, Volatility 3 fully supports memory dumps from Windows 10 and Windows 11. What is the dlllist command? The dlllist command lists all the dynamic link libraries (DLLs) loaded by a specific process, helping to spot malicious injections.
Setting up Volatility 3 is more streamlined than its predecessor because it removes the dependency on specific profiles. It requires Python 3 and a few dependencies. Step-by-Step Installation: Prerequisites: Ensure Python 3.6 or later is installed on your analysis machine (Linux, Windows, or macOS). Download: Clone the official repository from GitHub or download the latest stable release zip file. Dependencies: Install the required Python libraries using pip. Key libraries include `pefile` for Windows analysis and `yara-python` for malware scanning. Symbol Tables: Unlike Volatility 2 which required users to determine the exact OS profile, Volatility 3 uses symbol tables. It can often download the necessary symbol files (PDBs) from Microsoft's symbol server automatically during the first run, provided there is internet access. 4. Core Analysis Workflow The standard workflow for a memory investigation follows a logical path: Identify the system, list running processes, check for network activity, and hunt for injected malicious code. 4.1 Process Analysis (The First Step) Overview: The first goal is to determine what programs were running. Malware often disguises itself as legitimate system processes (like svchost.exe) but gives itself away through subtle anomalies. Key Plugins: windows.pslist: Lists active processes by walking the doubly-linked list in the kernel. This is the baseline view of the system. windows.psscan: Scans the memory dump for process headers (EPROCESS blocks). This helps identify hidden processes that have been unlinked by rootkits to hide from the standard task manager. windows.pstree: Visualizes processes in a parent-child tree structure. This is crucial for spotting anomalies, such as `cmd.exe` spawning from `winword.exe`, which often indicates a malicious macro payload. 4.2 Network Connection Analysis Overview: Investigating network artifacts helps identify if the compromised machine was communicating with external attacker infrastructure. Key Plugins: windows.netscan: Scans for network connections and sockets. It works on modern Windows versions (Vista and later) and shows local and remote IP addresses, ports, and the state of the connection (ESTABLISHED, LISTENING). windows.netstat: Similar to the netstat command on a live system, this plugin retrieves the network stack information. Why It Is Essential: Mapping a malicious process ID (PID) to an established connection with a known bad IP address provides the "smoking gun" needed to confirm data exfiltration or C2 activity. 4.3 Malware Hunting and Code Injection Overview: Advanced malware hides code inside legitimate processes (injection) or uses packing techniques to avoid detection by antivirus. Key Plugins: windows.malfind: Scans for memory pages that have "Execute" and "Write" permissions simultaneously, a common indicator of code injection. It outputs a hex dump and assembly code for verification. yarascan: Allows investigators to scan the entire memory dump for specific strings or byte patterns using YARA rules. This is powerful for finding malware signatures even if the process list looks clean. windows.dlllist: Lists the Dynamic Link Libraries (DLLs) loaded by a process. This helps identify malicious DLLs that have been sideloaded into legitimate applications. 4.4 Extraction of Secrets and Passwords Overview: One of the most unique capabilities of memory forensics is the recovery of credentials that exist in cleartext or reversible formats in RAM. Key Plugins: windows.hashdump: Extracts NTLM password hashes from the registry hives loaded in memory. These hashes can be cracked to recover user passwords. windows.lsadump: Recovers LSA secrets, which may include service account passwords and default logic credentials. windows.filescan: While not a password tool per se, this scans memory for file objects, allowing investigators to extract files (like a password.txt or config file) directly from RAM before they were saved to disk. Comparative Analysis: Volatility 2 vs. Volatility 3 Feature Category Volatility 2 (Legacy) Volatility 3 (Modern) Investigator Benefit (Vol 3) Language Base Python 2.7 (Deprecated) Python 3 Better performance and long-term support Profile Selection Manual (--profile req.) Automatic (Symbol Tables) Faster setup, no guessing profiles Execution Speed Slower on large dumps Significantly Faster Analyzes gigabytes of RAM quickly Plugin Naming Simple (e.g., pslist) Structured (windows.pslist) Clearer distinction between OS plugins OS Support Win, Linux, Mac (Complex) Unified Cross-Platform Consistent commands across OSs Output Format Text, Grepable JSON, CSV, Pretty Text Easier integration with other tools Community Status End of Life Active Development Access to latest features and fixes 6.
Future Trends in Memory Forensics As operating systems evolve, memory forensics is adapting to new challenges. The shift towards cloud computing has led to the development of tools for acquiring memory from virtual machines (VMs) and cloud instances without pausing them. We are also seeing a rise in automation, where Volatility is integrated into SOAR (Security Orchestration, Automation, and Response) platforms to automatically analyze memory dumps from triggered alerts.
Furthermore, with the increasing use of encryption by malware, the ability of Volatility to extract encryption keys from RAM remains a critical area of focus for future development. 7. Career Scope for Memory Analysts Expertise in Volatility and memory forensics is a highly specialized skill that commands a premium in the cybersecurity job market. While general analysts focus on logs and disk artifacts, memory analysts can uncover the most sophisticated threats. Job Roles: Advanced Malware Analyst Incident Response Lead Threat Hunter Digital Forensics Consultant Salary Outlook: Professionals with deep memory forensics skills often earn between $100,000 and $160,000 annually, with specialized consultants in private firms earning significantly more depending on their experience and certifications. 8. Conclusion The Volatility Framework remains the definitive tool for memory forensics in 2025. Its transition to Python 3 and the removal of complex profile requirements have made it more accessible than ever, without sacrificing the power needed to hunt advanced adversaries. Whether you are dealing with a rootkit, a ransomware infection, or an insider threat, Volatility provides the visibility into the system's runtime state that no other tool can match. Mastering this framework is not just a technical skill; it is a necessity for any modern digital investigator aiming to see the complete picture of a cyber incident. Frequently Asked Questions (FAQ) What is the Volatility Framework? Volatility is an open-source command-line tool used to analyze volatile memory (RAM) dumps for digital forensics and incident response. Is Volatility free to use? Yes, Volatility is completely free and open-source software, released under the Volatility Software License. What is the difference between Volatility 2 and 3? Volatility 3 uses Python 3, is much faster, and automatically detects profiles using symbol tables, whereas Volatility 2 used Python 2. Can Volatility capture memory? No, Volatility analyzes memory. You need a separate acquisition tool like FTK Imager or WinPmem to capture the RAM first. What operating systems can Volatility analyze? It can analyze memory dumps from Windows, Linux, and macOS systems, covering almost all modern versions. What is a memory profile? In Volatility 2, a profile defined the OS version and architecture. Volatility 3 replaces this with automatic symbol table detection. How do I list running processes? Use the `windows.pslist` plugin in Volatility 3 (or `pslist` in Volatility 2) to see all active processes. Can Volatility find hidden malware? Yes, plugins like `psscan` and `malfind` are designed specifically to detect hidden processes and injected malicious code.
Does Volatility work on Linux? Yes, the framework itself runs on Linux, and it includes a suite of plugins specifically for analyzing Linux memory dumps. What is the netscan plugin? The netscan plugin scans the memory for active network connections and listening ports, useful for finding C2 communications. How do I install Volatility 3? You can clone the GitHub repository and install the required dependencies using Python 3's pip package manager. Can I recover passwords with Volatility? Yes, plugins like `hashdump` can recover NTLM hashes, and `lsadump` can recover LSA secrets from Windows memory. What file formats does Volatility support? It supports raw dumps (.dd, .raw), crash dumps, and hibernation files, among others. What is a symbol table? A symbol table acts as a map for Volatility 3 to understand the internal structures of the specific operating system being analyzed. Is there a GUI for Volatility? Volatility is a CLI tool, but third-party GUIs like "Volatility Workbench" exist to make it easier to use. What is malfind used for? The malfind plugin searches for memory pages that are both executable and writable, a strong indicator of code injection. Can I extract files from RAM? Yes, the `dumpfiles` or `filescan` plugins allow you to carve and extract files directly from the memory image. Why is memory forensics important? It allows investigators to see the runtime state of the system, including unencrypted data and fileless malware that disk forensics misses. Does Volatility support Windows 11? Yes, Volatility 3 fully supports memory dumps from Windows 10 and Windows 11. What is the dlllist command? The dlllist command lists all the dynamic link libraries (DLLs) loaded by a specific process, helping to spot malicious injections.
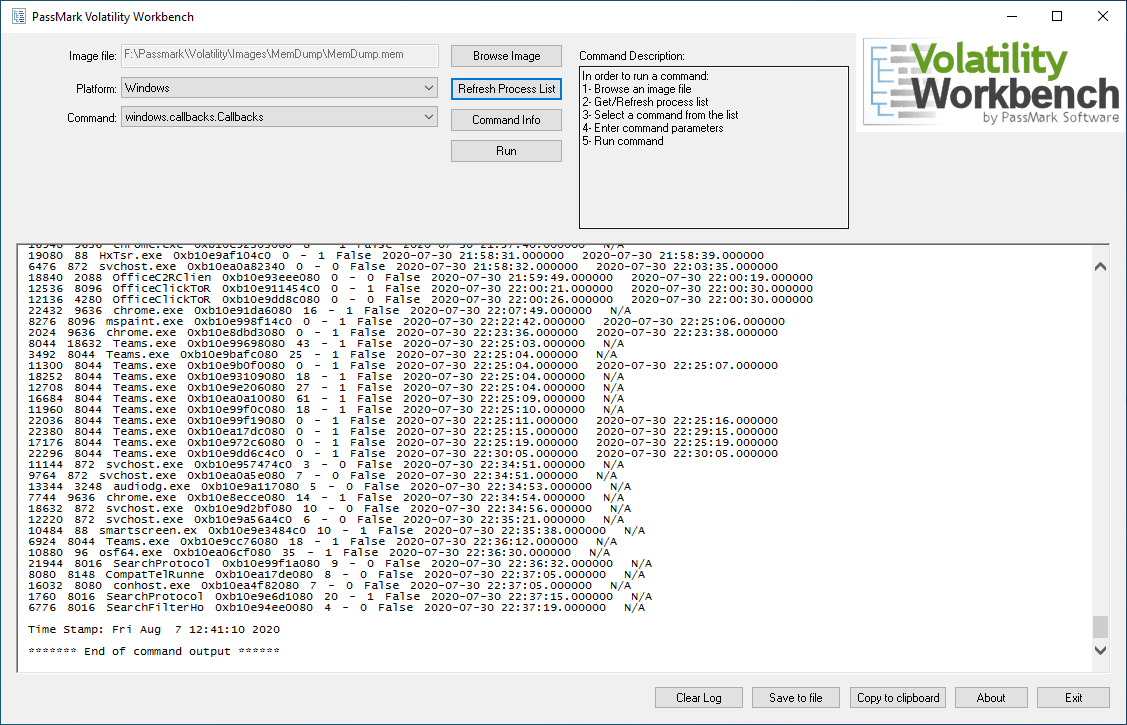
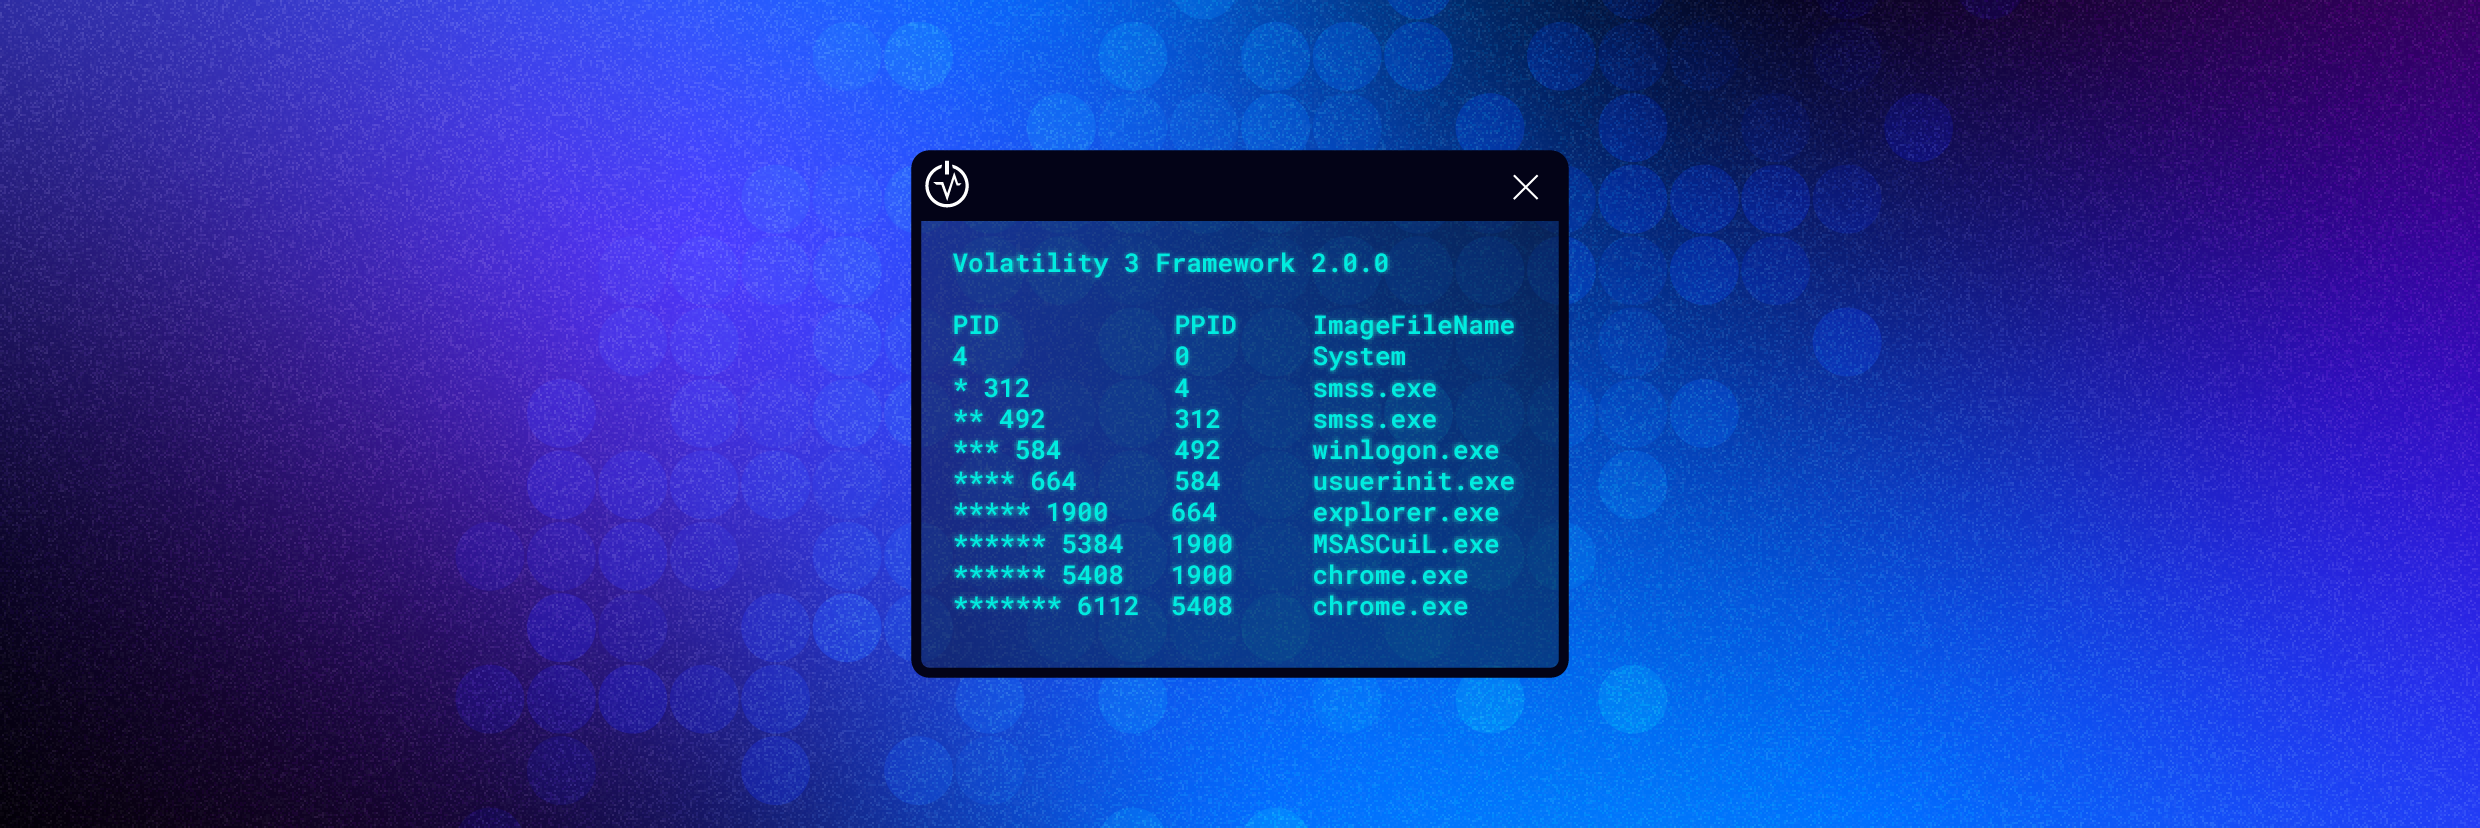
Figure 1: Volatility Workbench - A GUI for Volatility memory forensics Figure 2: Volatility: A Beginner's guide to Memory Forensics Figure 3: How to Use Volatility for Memory Forensics and Analysis | Varonis Harvested Online Documentation & Reference Sources • https://www.bing.com/aclick?ld=e8pQm74DZd9uBlirS01OVnoTVUCUz96KlfOmPVzA-C_yj0vMPow1zWhbTgNbCnaCJqsGs ipc4J8hM4M0M1l_uv3yOBBEq1bre4bU-qJcG5-w4nPcxwYU8DgLc1zkhJj2lBw0tkqoH1rOxpqnbKRETp4Fv8QlxU33V5Kams OpgmwiVZiGFvQRuH7NVOPwg5o9SOKI2POg&u=aHR0cHMlM2ElMmYlMmZ3d3cubWFnbmV0Zm9yZW5zaWNzLmNvbSU yZiUzZnV0bV9zb3VyY2UlM2RiaW5nJTI2dXRtX21lZGl1bSUzZFNlYXJjaCUyNnV0bV9jYW1wYWlnbiUzZFNlYXJjaF9CcmFu ZF9QdWJsaWNfRU1FQSUyNnV0bV9hdWRpZW5jZSUzZE1hZ25ldF9CcmFuZCUyNnV0bV90ZXJtJTNkbWFnbmV0JTI1MjB kaWdpdGFsJTI1MjBmb3JlbnNpY3MlMjZtc2Nsa2lkJTNkNGEyZThhMmUzNmY1MTVhOGVjMWJlMGZhZDA4M2YwZGE&rlid =4a2e8a2e36f515a8ec1be0fad083f0da • https://www.cyberforensicacademy.com/blog/volatility-framework-complete-memory-forensics-guide
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Memory Forensics Based Malware Detection Using Volatility.
[*] Metasploit Scan Running on Target Subnet for Memory Forensics Based Malware Detection Using Volatility... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |