Complete Technical Paper Content — Mouse Movement Biometrics For Continuous User Authentication
Overview & System Context
Mouse Movement Biometrics For Continuous User Authentication: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9511 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Biometrics are body measurements and calculations related to human characteristics and features. Biometric authentication (or realistic authentication) is used in computer science as a form of identification and access control. It is also used to identify individuals in groups that are under surveillance. Biometric identifiers are the distinctive, measurable characteristics used to label and describe individuals. Biometric identifiers are often categorized as physiological characteristics which are related to the shape of the body. Examples include, but are not limited to fingerprint, palm veins, face recognition, DNA, palm print, hand geometry, iris recognition, retina, odor/scent, voice and shape of ears. Behavioral characteristics are related to the pattern of behavior of a person, including but not limited to mouse movement, typing rhythm, gait, signature, voice, and behavioral profiling. Some researchers have coined the term "Behaviometrics" (behavioral biometrics) to describe the latter class of biometrics. More traditional means of access control include token-based identification systems, such as a driver's license or passport, and knowledge-based identification systems, such as a password or personal identification number. Since biometric identifiers are unique to individuals, they are more reliable in verifying identity than token and knowledge-based methods; however, the collection of biometric identifiers raises privacy concerns.
Universality: Every person using a system should possess the trait. Uniqueness: The trait should be sufficiently different for individuals in the relevant population such that they can be distinguished from one another. Permanence: The manner in which a trait varies over time. More specifically, a trait with good permanence will be reasonably invariant over time with respect to the specific matching algorithm. Measurability (collectability): The ease of acquisition or measurement of the trait. In addition, acquired data should be in a form that permits subsequent processing and extraction of the relevant feature sets.
Performance: The accuracy, speed, and robustness of technology used (see performance section for more details). Acceptability: How well individuals in the relevant population accept the technology such that they are willing to have their biometric trait captured and assessed. Circumvention: The ease with which a trait might be imitated using an artifact or substitute. Proper biometric use is application dependent. Certain biometrics will be more suitable than others based on the required levels of convenience and security. No single biometric will meet all the requirements of every possible application.
The block diagram illustrates the two basic modes of a biometric system. First, in verification (or authentication) mode the system performs a one-to-one comparison of a captured biometric with a specific template stored in a biometric database in order to verify the individual is the person they claim to be. Three steps are involved in the verification of a person. In the first step, reference models for all the users are generated and stored in the model database. In the second step, some samples are matched with reference models to generate the genuine and impostor scores and calculate the threshold. The third step is the testing step. This process may use a smart card, username, or ID number (e.g. PIN) to indicate which template should be used for comparison. Positive recognition is a common use of the verification mode, "where the aim is to prevent multiple people from using the same identity".
Second, in identification mode the system performs a one-to-many comparison against a biometric database in an attempt to establish the identity of an unknown individual. The system will succeed in identifying the individual if the comparison of the biometric sample to a template in the database falls within a previously set threshold. Identification mode can be used either for positive recognition (so that the user does not have to provide any information about the template to be used) or for negative recognition of the person "where the system establishes whether the person is who she (implicitly or explicitly) denies to be". The latter function can only be achieved through biometrics since other methods of personal recognition, such as passwords, PINs, or keys, are ineffective. The first time an individual uses a biometric system is called enrollment. During enrollment, biometric information from an individual is captured and stored. In subsequent uses, biometric information is detected and compared with the information stored at the time of enrollment. Note that it is crucial that storage and retrieval of such systems themselves be secure if the biometric system is to be robust. The first block (sensor) is the interface between the real world and the system; it has to acquire all the necessary data. Most of the time it is an image acquisition system, but it can change according to the characteristics desired. The second block performs all the necessary pre-processing: it has to remove artifacts from the sensor, to enhance the input (e.g. removing background noise), to use some kind of normalization, etc. In the third block, necessary features are extracted. This step is an important step as the correct features need to be extracted in an optimal way. A vector of numbers or an image with particular properties is used to create a template. A template is a synthesis of the relevant characteristics extracted from the source. Elements of the biometric measurement that are not used in the comparison algorithm are discarded in the template to reduce the file size and to protect the identity of the enrollee. However, depending on the scope of the biometric system, original biometric image sources may be retained, such as the PIV-cards used in the Federal Information Processing Standard Personal Identity Verification (PIV) of Federal Employees and Contractors (FIPS 201). During the enrollment phase, the template is simply stored somewhere (on a card or within a database or both). During the matching phase, the obtained template is passed to a matcher that compares it with other existing templates, estimating the distance between them using any algorithm (e.g. Hamming distance). The matching program will analyze the template with the input. This will then be output for a specified use or purpose (e.g. entrance in a restricted area), though it is a fear that the use of biometric data may face mission creep. Selection of biometrics in any practical application depending upon the characteristic measurements and user requirements. In selecting a particular biometric, factors to consider include, performance, social acceptability, ease of circumvention and/or spoofing, robustness, population coverage, size of equipment needed and identity theft deterrence. The selection of a biometric is based on user requirements and considers sensor and device availability, computational time and reliability, cost, sensor size, and power consumption.
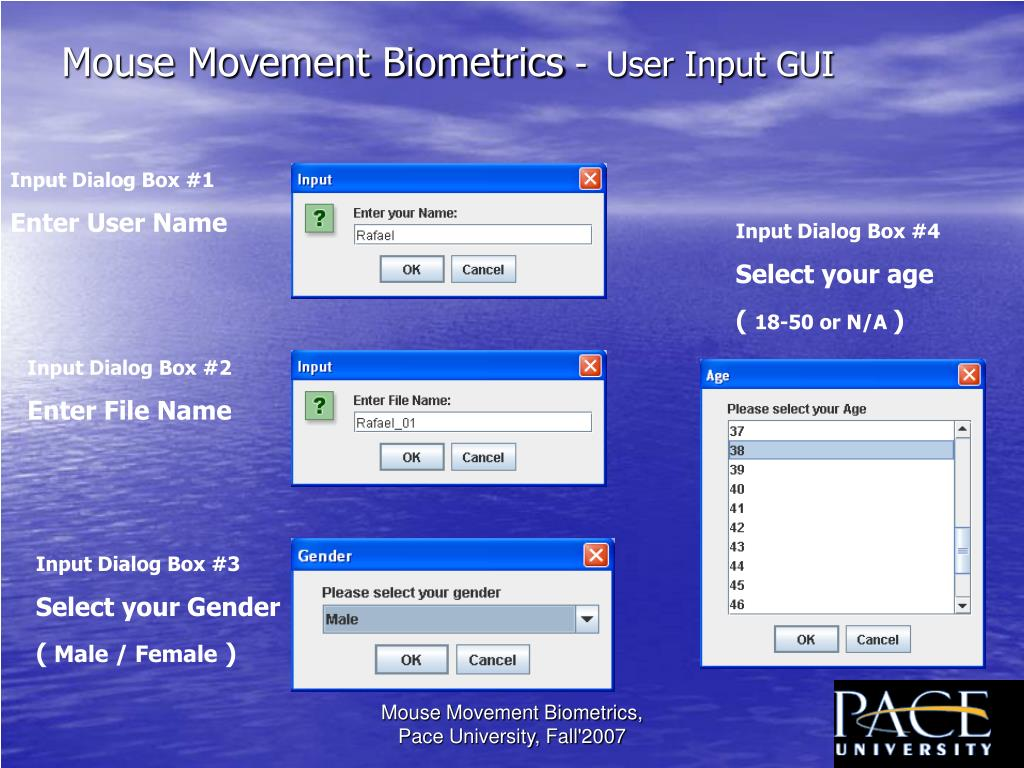
Figure 1: PPT - Mouse Movement Biometrics Project Report - Fall 2007 PowerPoint ... False match rate (FMR, also called FAR = False Accept Rate): the probability that the system incorrectly matches the input pattern to a non-matching template in the database. It measures the percent of invalid inputs that are incorrectly accepted. In case of similarity scale, if the person is an imposter in reality, but the matching score is higher than the threshold, then he is treated as genuine. This increases the FMR, which thus also depends upon the threshold value. False non-match rate (FNMR, also called FRR = False Reject Rate): the probability that the system fails to detect a match between the input pattern and a matching template in the database. It measures the percent of valid inputs that are incorrectly rejected. Receiver operating characteristic or relative operating characteristic (ROC): The ROC plot is a visual characterization of the trade-off between the FMR and the FNMR. In general, the matching algorithm performs a decision based on a threshold that determines how close to a template the input needs to be for it to be considered a match. If the threshold is reduced, there will be fewer false non-matches but more false accepts. Conversely, a higher threshold will reduce the FMR but increase the FNMR. A common variation is the Detection error trade-off (DET), which is obtained using normal deviation scales on both axes. This more linear graph illuminates the differences for higher performances (rarer errors). Equal error rate or crossover error rate (EER or CER): the rate at which both acceptance and rejection errors are equal. The value of the EER can be easily obtained from the ROC curve. The EER is a quick way to compare the accuracy of devices with different ROC curves. In general, the device with the lowest EER is the most accurate. Failure to enroll rate (FTE or FER): the rate at which attempts to create a template from an input is unsuccessful. This is most commonly caused by low-quality inputs. Failure to capture rate (FTC): Within automatic systems, the probability that the system fails to detect a biometric input when presented correctly.
Template capacity: the maximum number of sets of data that can be stored in the system. An early cataloguing of fingerprints dates back to 1885 when Juan Vucetich started a collection of fingerprints of criminals in Argentina. Josh Ellenbogen and Nitzan Lebovic argued that Biometrics originated in the identification systems of criminal activity developed by Alphonse Bertillon (1853–1914) and by Francis Galton's theory of fingerprints and physiognomy.
Historian Keith Breckenridge note that Galton's travels in South Africa reinforced his early racial prejudices and inspired his later commitment to classifying human difference scientifically. According to Lebovic, Galton's work "led to the application of mathematical models to fingerprints, phrenology, and facial characteristics", as part of "absolute identification" and "a key to both inclusion and exclusion" of populations. Accordingly, "the biometric system is the absolute political weapon of our era" and a form of "soft control". The theoretician David Lyon showed that during the past two decades biometric systems have penetrated the civilian market, and blurred the lines between governmental forms of control and private corporate control.
Kelly A. Gates identified 9/11 as the turning point for the cultural language of our present: "in the language of cultural studies, the aftermath of 9/11 was a moment of articulation, where objects or events that have no necessary connection come together and a new discourse formation is established: automated facial recognition as a homeland security technology." It is possible that data obtained during biometric enrollment may be used in ways for which the enrolled individual has not consented. For example, most biometric features could disclose physiological and/or pathological medical conditions (e.g., some fingerprint patterns are related to chromosomal diseases, iris patterns could reveal sex, hand vein patterns could reveal vascular diseases, most behavioral biometrics could reveal neurological diseases, etc.). Moreover, second generation biometrics, notably behavioral and electro-physiologic biometrics (e.g., based on electrocardiography, electroencephalography, electromyography), could be also used for emotion detection. There are three categories of privacy concerns: Unintended functional scope: The authentication goes further than authentication, such as finding a tumor. Unintended application scope: The authentication process correctly identifies the subject when the subject did not wish to be identified.
Covert identification: The subject is identified without seeking identification or authentication, i.e. a subject's face is identified in a crowd. In terms of recognition or identification performance for a given trait, a biometric system should not exhibit accuracy differences across demographic groups. Disparities in accuracy can lead to uneven error rates for populations defined by gender, race, age, or other attributes. Therefore, biometric systems should be designed and evaluated to ensure demographic fairness, providing equitable performance for all users.
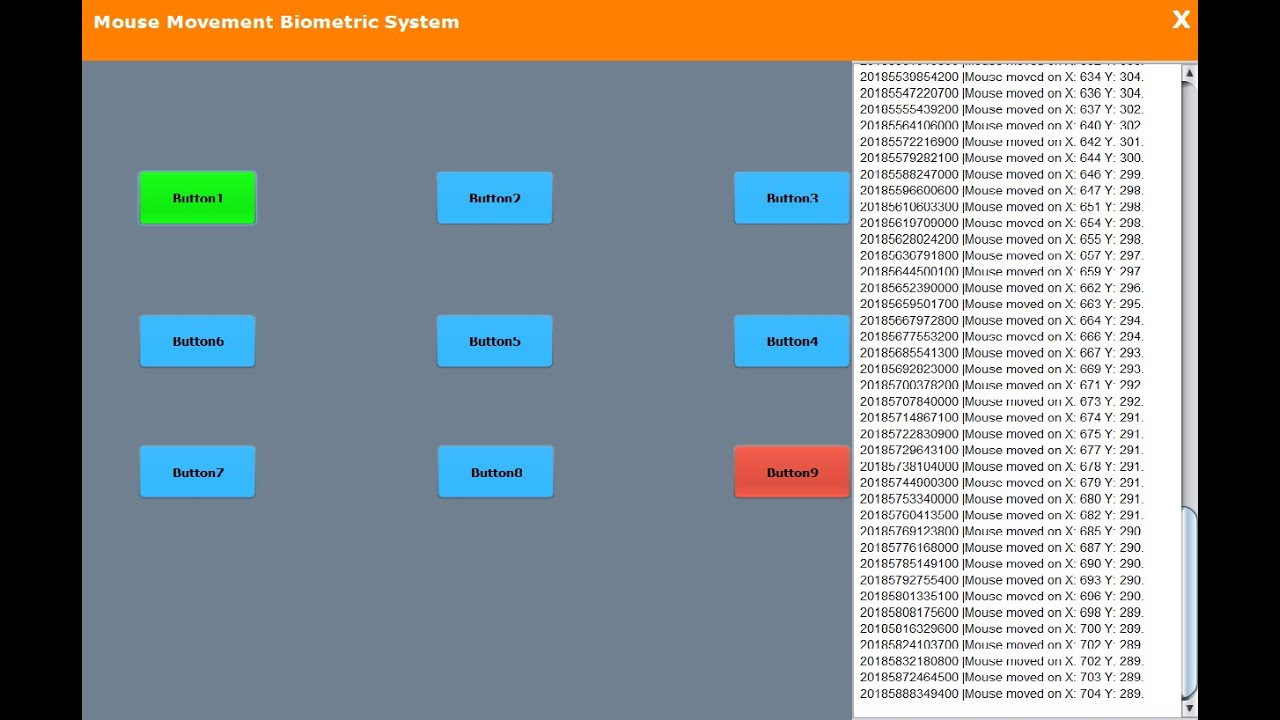
Figure 2: User Authentication Based On Mouse Movements Biometric System ... To ensure we can shut down terrorist networks before they ever get to the United States, we must also take the lead in driving international biometric standards. By developing compatible systems, we will be able to securely share terrorist information internationally to bolster our defenses. Just as we are improving the way we collaborate within the U.S. Government to identify and weed out terrorists and other dangerous people, we have the same obligation to work with our partners abroad to prevent terrorists from making any move undetected. Biometrics provide a new way to bring terrorists' true identities to light, stripping them of their greatest advantage—remaining unknown. According to an article written in 2009 by S. Magnuson in the National Defense Magazine entitled "Defense Department Under Pressure to Share Biometric Data" the United States has bilateral agreements with other nations aimed at sharing biometric data. To quote that article: Miller [a consultant to the Office of Homeland Defense and America's security affairs] said the United States has bilateral agreements to share biometric data with about 25 countries. Every time a foreign leader has visited Washington during the last few years, the State Department has made sure they sign such an agreement.
GDPR in the European Union became law in 2018 LGPD in Brazil became law in 2020 Protection of Personal Information Act in South Africa came into force in 2020 Personal Data Protection Act in Sri Lanka implementation started in 2023 Countries using biometrics include Australia, Brazil, Bulgaria, Canada, Cyprus, Greece, China, Gambia, Germany, India, Iraq, Ireland, Israel, Italy, Malaysia, Netherlands, New Zealand, Nigeria, Norway, Pakistan, Poland, South Africa, Saudi Arabia, Tanzania, Turkey, Ukraine, United Arab Emirates, United Kingdom, United States and Venezuela. Among low to middle income countries, roughly 1.2 billion people have already received identification through a biometric identification program.
There are also numerous countries applying biometrics for voter registration and similar electoral purposes. According to the International IDEA's ICTs in Elections Database, some of the countries using (2017) Biometric Voter Registration (BVR) are Armenia, Angola, Bangladesh, Bhutan, Bolivia, Brazil, Burkina Faso, Cambodia, Cameroon, Chad, Colombia, Comoros, Congo (Democratic Republic of), Costa Rica, Ivory Coast, Dominican Republic, Fiji, Gambia, Ghana, Guatemala, India, Iraq, Kenya, Lesotho, Liberia, Malawi, Mali, Mauritania, Mexico, Morocco, Mozambique, Namibia, Nepal, Nicaragua, Nigeria, Panama, Peru, Philippines, Senegal, Sierra Leone, Solomon Islands, Somaliland, Swaziland, Tanzania, Uganda, Uruguay, Venezuela, Yemen, Zambia, and Zimbabwe.
Figure 3: What is Biometrics? Definition, Data Types, Trends (2024) User behavior analytics (UBA) or user and entity behavior analytics (UEBA), is the concept of analyzing the behavior of users, subjects, visitors, etc. for a specific purpose. It allows cybersecurity tools to build a profile of each individual's normal activity, by looking at patterns of human behavior, and then highlighting deviations from that profile (or anomalies) that may indicate a potential compromise.
Typing is the process of entering or inputting text by pressing keys on a typewriter, computer keyboard, mobile phone, or calculator. It can be distinguished from other means of text input, such as handwriting and speech recognition; text can be in the form of letters, numbers and other symbols. The world's first typist was Lillian Sholes from Wisconsin in the United States, the daughter of Christopher Latham Sholes, who invented the first practical typewriter. User interface features such as spell checker and autocomplete serve to facilitate and speed up typing and to prevent or correct errors the typist may make.
In this technique, the typist keeps their eyes on the source copy at all times. Touch typing also involves the use of the home row method, where typists rest their wrist down, rather than lifting up and typing (which can cause carpal tunnel syndrome ). To avoid this, typists should sit up tall, leaning slightly forward from the waist, place their feet flat on the floor in front of them with one foot slightly in front of the other, and keep their elbows close to their sides with forearms slanted slightly upward to the keyboard; fingers should be curved slightly and rest on the home row. Many touch typists also use keyboard shortcuts when typing on a computer. This allows them to edit their document without having to take their hands off the keyboard to use a mouse. An example of a keyboard shortcut is pressing the Ctrl key plus the S key to save a document as they type, or the Ctrl key plus the Z key to undo a mistake. Other shortcuts are the Ctrl key plus the C to copy and the Ctrl key and the V key to paste, and the Ctrl key and the X key to cut. Many experienced typists can feel or sense when they have made an error and can hit the ← Backspace key and make the correction with no increase in time between keystrokes.
Words per minute (WPM) is a measure of typing speed, commonly used in recruitment. For the purposes of WPM measurement, a word is standardized to five characters or keystrokes. Therefore, "brown" counts as one word but "mozzarella" counts as two. The benefits of a standardized measurement of input speed are that it enables comparison across language and hardware boundaries. The speed of an Afrikaans-speaking operator in Cape Town can be compared with a French-speaking operator in Paris. Today, even Written Chinese can be typed very quickly using the combination of a software prediction system and by typing their sounds in Pinyin. Such prediction software even allows typing short-hand forms while producing complete characters. For example, the phrase "nI chI le ma" (IIII) meaning "Have you eaten yet?" can be typed with just 4 strokes: "nclm".
Participants are allowed to enter text naturally, since they may commit errors and correct them. The identification of errors and generation of error rate statistics is easy to automate. The two classes Correct and Incorrect Not Fixed comprise all of the characters in transcribed text. Fixes (F) keystrokes are easy to identify, and include keystrokes such as backspace, delete, cursor movements, and modifier keys. Incorrect Fixed (IF) keystrokes are found in the input stream, but not the transcribed text, and are not editing keys. Using these classes, the Minimum String Distance Error Rate and the Key Strokes per Character statistics can both be calculated.
High KSPC values can be related to either many errors which were corrected, or few errors which were not corrected; however, there is no way to distinguish the two. KSPC depends on the text input method, and cannot be used to meaningfully compare two different input methods, such as a QWERTY keyboard and a multi-tap device. There is no obvious way to combine KSPC and MSD into an overall error rate, even though they have an inverse relationship.
Correction Efficiency = IF/F Participant conscientiousness is the ratio of corrected errors to the total number of error, which helps distinguish perfectionists from apathetic participants. 2. System Architecture & Core Working Principles Participant Conscientiousness = IF / (IF + INF) If C represents the amount of useful information transferred, INF, IF, and F represent the proportion of bandwidth wasted.
Utilized Bandwidth = C / (C + INF + IF + F) Wasted Bandwidth = (INF + IF + F)/ (C + INF + IF + F) Total Error Rate = ((INF + IF)/ (C + INF + IF)) * 100% Not Corrected Error Rate = (INF/ (C + INF + IF)) * 100% Corrected Error Rate = (IF/ (C + INF + IF)) * 100% Since these three error rates are ratios, they are comparable between different devices, something that cannot be done with the KSPC statistic, which is device dependent.
1. Shaanxi Provincial Joint Laboratory of Artificial Intelligence, Xi'an University, Xi'an, China Computers have become indispensable tools in modern society and they often serve as repositories for large amounts of private and confidential information in public. User authentication is therefore a fundamental mechanism for protecting device security and user privacy. Traditional authentication methods such as passwords are not tightly bound to user identity and impose a significant memory burden, which has motivated the widespread adoption of biometric-based authentication approaches, such as fingerprint and facial recognition. However, fingerprint- and face-based authentication typically requires additional hardware support and can be vulnerable to interception by ultra-high-definition cameras, raising serious privacy concerns. To solve these problems, this paper proposes a fine-grained and continuous user authentication method based on mouse grip pressure biometrics. By deploying resistive pressure sensors on the surface of a mouse, we capture individualized pressure distribution patterns generated during natural mouse gripping. To further enhance discriminative capability, we refine the sensor contact layout to improve spatial feature resolution. Moreover, we introduce a layered representation for omnidirectional pressure signals to mitigate sensitivity to grip direction variations. Extensive experimental results demonstrate the effectiveness of the proposed system, achieving the FAR below 0.1% and the FRR below 0.4%. These results indicate that mouse grip pressure constitutes a highly discriminative and robust biometric modality for continuous user authentication.
With the rapid advancement of information technology, the security and privacy protection of personal data have become increasingly critical in public. In particular, computers serve as primary platforms for storing and processing large volumes of sensitive and confidential information, making secure user authentication a fundamental requirement. Traditional identity authentication mechanisms, such as passwords and PIN codes ( Matyas and Ríha, 2003 ), have gradually revealed inherent limitations due to their vulnerability to leakage, theft, and forgetfulness. As a result, biometric authentication technologies ( Tripathi and Nishad, 2020 ), which rely on unique biological characteristics for identity verification, have emerged as a major research focus in secure authentication systems.
Biometric authentication has achieved significant progress, including fingerprint recognition, facial recognition, and iris recognition. However, conventional biometric methods typically depend on physiological data, which can be easily captured by ultra-high-definition cameras or external sensing devices, thereby raising serious privacy concerns ( Moshnyaga et al., 2018 ; Bowyer and Doyle, 2014 ). Moreover, for traditional desktop computers and many laptops, the deployment of biometric authentication requires additional hardware such as external cameras or fingerprint scanners. This not only increases system cost but also degrades usability, making physiological biometric authentication less suitable for widespread deployment in everyday computing environments.
In contrast to one-time physiological authentication, behavior-based authentication methods ( Banerjee and Woodard, 2012 ; Teh et al., 2013 ; Mahfouz et al., 2024 ; Baig et al., 2023 ; Handa et al., 2018 ; Abuhamad et al., 2021 ; Alawami et al., 2024 ) offer stronger resistance to attacks due to their reliance on continuous user behavior monitoring. These approaches leverage human-computer interaction devices to collect behavioral data, enabling seamless deployment without disrupting normal user operations. Consequently, behavioral biometrics have become an important research direction in modern authentication systems. Compared with physiological biometrics, behavioral biometrics also provide superior concealment and implicit authentication capabilities.
The mouse, as one of the most commonly used human-computer interaction devices, naturally embeds rich personalized behavioral information. Mouse-based user authentication can be applied to various scenarios. For instance, it can be used in hospital office or warehouse management computers to prevent unauthorized personnel from maliciously operating the computers and tampering with information. Existing studies on mouse-based authentication ( Revett et al., 2008 ; Khan et al., 2024 ; AbouRida et al., 2024 ; Muralidharan et al., 2025 ; Wang et al., 2022 ; Shi et al., 2022 ) analyze features such as movement speed, keystroke intervals, and trajectory directionality, demonstrating statistically significant inter-user differences.
However, these approaches typically require large volumes of historical data collected under consistent application environments. More importantly, the extracted behavioral features remain relatively coarse-grained, making them vulnerable to imitation and counterfeiting attacks. To address these limitations, this paper proposes a fine-grained continuous user authentication system based on mouse grip pressure biometrics. Compared with traditional dynamic behavioral statistics, grip pressure patterns provide higher-resolution and more discriminative biometric features. The pressure distribution generated during mouse usage is inherently dependent on individual hand morphology and gripping habits, making it difficult to replicate. The pressure sensor data exhibits a strong correlation with physical contact and possesses a ability to mitigate network attacks. Our key insight is that pressure distributions exhibit strong intra-user consistency while maintaining significant inter-user variability.
We systematically explore individual differences in mouse grip posture and pressure distribution by deploying pressure sensors on the mouse surface to capture fine-grained pressure patterns during natural usage. Based on these signals, we develop an efficient and high-resolution biometric authentication framework. Several technical challenges are addressed in the system design. First, to mitigate temporal heterogeneity caused by variations in mouse movement speed, we optimize the flexible substrate structure of the pressure sensors to stabilize feature patterns. Second, feature resolution is enhanced by refining the sensor contact surface structure. Third, we propose a hierarchical modeling method for omnidirectional mouse movements to overcome the sensitivity of pressure features to directional variations.
We implement a prototype system by deploying pressure sensors at five key grip positions on the mouse. The customized sensors enable the generation of over 9.5 × 10 13 unique pressure sensor arrangements. Extensive evaluations involving 12 participants demonstrate that the proposed system achieves authentication accuracy exceeding 99%, while exhibiting strong robustness against forgery and impersonation attacks.
Fine-grained pressure biometrics . By analyzing the pressure sensor structure and conducting preliminary experiments, the distinguishability of mouse grip postures for different users is verified. The sensor surface structure is refined to enhance the pressure sensing characteristics at different locations, while simultaneously stabilizing the feature patterns. Dynamic disturbance correction . The issue of dynamic sensor data feature perturbation caused by changes in mouse movement direction is addressed. A hierarchical modeling method for omnidirectional mouse movements is proposed to overcome the sensitivity of pressure features to directional variations, enabling robust and reliable authentication.
Security analysis and extensive evaluation . The counterfeiting attack and imitation attack are analyzed for possible public use scenario. Extensive experimental evaluations are conducted to validate the effectiveness and robustness of the proposed system. The remainder of this paper is organized as follows. Section 2 discusses the development of biometric authentication technologies and the potential of mouse-based authentication. Section 3 introduces the background and threat model. Section 4 verifies the feasibility of user authentication using mouse grip pressure through preliminary experiments. Section 5 presents the system architecture and signal preprocessing methods. Section 6 describes the experimental setup and evaluation protocol. Section 7 explores potential avenues for the extension. Section 8 concludes the paper.
The use of biometric technology for personal identity verification has become widespread across various aspects of daily life. Biometric systems employ sensors to capture unique physiological or behavioral traits—such as fingerprints, palm vein patterns ( Wang et al., 2026 ), irises ( Binu, 2026 ), or voice ( Rajeh et al., 2026 )—for identifying their owners. For instance, BreathID ( Islam and Lubecke, 2021 ) leverages radar sensing to achieve non-contact, continuous identity verification by analyzing the micro-Doppler features of human breath. Roy and Satija (2025) utilize wearable sensors to record physiological and seismocardiogram signals for biometric authentication. Ibrahim et al. (2024) develop a system based on optical capacitance pulse waves, which measures heart rate through non-invasive optical technology, offering a low-cost authentication solution. Ismail Aslan and Choi (2024) employ photoconductive pulse waves captured by implantable or wearable sensors for user verification. Ganiga et al. (2024) use electromyography sensors to record muscle electrical signals for personal identification. Janaki et al. (2024) capture subcutaneous finger vein images with specialized scanners to develop a vein-based recognition system. However, conventional biometric authentication methods primarily rely on static features, which can be easily copied or spoofed.
Continuous authentication ( Shen et al., 2026 ; Cariello et al., 2025 ; Guan et al., 2021 ; Baig et al., 2023 ; Handa et al., 2018 ; Zhang et al., 2021 ) has evolved from static, one-time mechanisms to dynamic, continuous user verification based on behavioral biometrics, effectively addressing the limitations of traditional one-time authentication, which becomes vulnerable once initial access is granted. This is particularly critical in today's era of pervasive mobile devices, IoT ecosystems, and remote access systems, where session hijacking, insider threats, and impersonation attacks are increasingly prevalent. The core principle of continuous authentication is to leverage unique and repeatable patterns in human-computer interaction—such as keystroke dynamics ( Stylios et al., 2023 ; de Marcos et al., 2021 ), touch gestures ( Abuhamad et al., 2021 ; Alawami et al., 2024 ; Chen et al., 2024 ), mouse movements ( Hu et al., 2019 ), gait ( Atansuyi, 2025 ; Kathal et al., 2025 ), or even breathing rhythms—as continuous identifiers that can be passively monitored throughout user sessions. Zhao et al. (2022b) propose a passive authentication framework for Industrial Internet of Things (IIoT) systems, demonstrating the distinguishability and stability of user identification through operational behavioral data. Abuhamad et al. (2021) provide a comprehensive survey of sensor-based continuous authentication on mobile devices, highlighting the potential of built-in inertial sensors and touchscreen interactions as reliable behavioral signals. Zhang et al. (2021) present a multimodal continuous authentication scheme, showing significantly improved performance compared to single-modality methods. Sejjari et al. (2024) evaluate continuous authentication using sliding gestures on mobile devices. ActID ( Sudhakar et al., 2021 ) introduces a user identification framework based on hand movement sensor data. Additionally, WiFi-based continuous authentication using deep learning during daily activities offers a non-contact verification approach ( Shi et al., 2021 ; Wang et al., 2019 ).
One of the most extensively studied behavioral biometrics is keystroke dynamics, which analyzes the unique patterns of user typing, including key press and release times, dwell time, and flight time between keys ( Ali and Hassan, 2025 ; Kathal et al., 2025 ; Yang et al., 2023 ; Szilàgyi et al., 2024 ; Xiong and Belman, 2025 ; Siddiqui et al., 2022 ; Khan et al., 2024 ; AbouRida et al., 2024 ). Studies have shown that keystroke dynamics can effectively distinguish legitimate users from impostors ( Muralidharan et al., 2025 ). Similarly, as a widely used computer input device, the mouse captures rich behavioral characteristics. These include both dynamic behaviors, such as movement trajectories and click speeds, and static behaviors, such as grip posture and pressure distribution. Wang et al. (2022) leverage scene-independent features from keyboard and mouse data to improve authentication accuracy, while Shi et al. (2022) enhance user verification through dynamic heterogeneous analysis of keyboard and mouse interactions. In this context, our system uses pressure sensors to capture users' grip behaviors, verifying the legitimacy of mouse operations and effectively addressing the limitations of previous approaches.
The use of pressure sensors for user authentication is an important research field ( Lai et al., 2015 ; Ali et al., 2009 ). These studies use sensors that can capture the pressure that users exert on objects while using them, in order to construct a personal fingerprint profile of pressure data. Huang et al. (2013) first explore the relationship between time indexed pressure graph trajectories extracted from touch mouse and user behavior patterns classified by common mouse action primitives.
Islam et al. (2017) use traditional pressure sensors to attach to the surface of firearms, achieving reliable firearm user authentication. Murao et al. (2014) deploy pressure sensors on the side and back of mobile phone to capture finger movements and grip strength, and authenticate users through short-term holding gestures. PushPIN ( Song and Oakley, 2023 ) proposes an authentication scheme for smart watches through multimodal fusion of touch pressure and wrist movement.
Zhang et al. (2025) utilized the giant magneto elastic effect to directly convert the mechanical pressure generated by pressing keys with fingers into electrical signals, achieving user identity authentication based on typing behavior. Cui et al. (2021) used a piezoelectric touchpad to collect touch time and pressure information during user tapping, and constructed a unique contour of user keystroke behavior. Existing studies provide multiple types of sensors, application scenarios, and performance evaluations, but there are relatively few attack model evaluations. Table 1 shows the comparison of related works in terms of sensor types and quantities, special equipment requirements, performance indicators, and resistance to attacks. Our work employs few pressure sensors deployed on the mouse, achieving a low false acceptance rate and effectively mitigating counterfeiting and imitation attacks.
3. Software Implementation, Frameworks & Protocols The Comparison of user authentication related indicators based on pressure perception. This system utilizes an inexpensive flexible film resistive pressure sensor to sense the pressure of the user holding the mouse. Sensors that can measure pressure include piezoelectric film sensor, capacitive pressure sensor, and inductive pressure sensor. However, capacitive and inductive sensors are relatively large in size and difficult to deploy on mouse surfaces. The piezoelectric film sensor only undergoes voltage variation with pressure changes, making it difficult to measure fixed pressure. Therefore, flexible film resistive pressure sensor is most suitable for our application scenarios. The film resistive pressure sensor mainly consists of a flexible substrate with printed interdigital electrodes, a flexible substrate coated with a semiconductive layer, a spacer adhesive, and an insulating film, as illustrated in Figure 1 . When no external force is applied, the resistance of the sensor is effectively infinite because the printed interdigital electrodes are physically separated.
Upon applying pressure, the semiconductive flexible substrate comes into contact with the interdigital electrodes. Owing to the conductivity of the semiconductive layer, an electrical conduction path is formed between the electrodes, resulting in a measurable resistance. As the applied pressure increases, the contact area between the semiconductive layer and the electrodes enlarges, leading to a decrease in the sensor resistance. Consequently, the sensor output varies with the contact area. When the contact area is reduced, the dynamic range of the measured resistance correspondingly decreases.
We consider adversaries who aim to impersonate legitimate users by imitating or counterfeiting authentication information to perform unauthorized operations. Specifically, we focus on the following two common and critical attack scenarios. The attacker possesses prior knowledge of the legitimate user's mouse and sensor configuration (e.g., mouse size and model, relative sensor placement, and sensor modification parameters). Based on this information, the attacker fabricates a replica using the same type of mouse and pressure sensors to attempt to bypass the authentication system.
The attacker covertly observes and learns the victim's mouse usage behavior and then attempts to compromise the authentication system by directly using the victim's mouse to impersonate the legitimate user. We first need to verify the feasibility of using pressure sensors to distinguish different users. We use a mouse to compare the similarity of pressure data distribution for the same user and the differences in pressure data distribution for different users. In addition, variations in hand size and individual usage habits result in distinct mouse gripping patterns across users. To capture these differences, we deploy pressure sensors at five representative locations where users typically apply force when holding a mouse: the left button, the right button, the center surface, the left side, and the right side, corresponding to 1–5 indicator in Figure 2 . These sensors enable us to quantify the pressure distribution during mouse gripping and extract discriminative biometric features for continuous user authentication. In addition, users can either hold the mouse static or moving. We define the pressure sensor data obtained when the user holds the mouse stationary as static pressure data, and the user moves the mouse as dynamic pressure data.
Mouse grip posture and pressure sensor layout. We deploy pressure sensors at five representative locations where users typically apply force when gripping the mouse: the left button, the right button, the central surface, the left side, and the right side, corresponding to indicators 1–5, respectively. First, we evaluate the pressure data collected by the five sensors when the user holds the mouse statically, and compute the average value over the sampling period as the final measurement. As shown in Figures 3a , b , the data recorded by each sensor exhibit high intra-sensor consistency, while clear pressure distribution differences are observed across the five sensor locations and between User 1 and User 2.
Pressure data distribution when users stationary grip mouse and users move the mouse left. (a) Static pressure data distribution of User1. (b) Static pressure data distribution of User2. (c) Dynamic pressure data distribution of User1. (d) Dynamic pressure data distribution of User2. Next, we evaluate the pressure data collected by the five sensors while the user moves the mouse leftward, and compute the average value over the movement duration. As shown in Figures 3c , d , the pressure patterns differ significantly across users, whereas the measurements for the same user remain largely consistent across different trials.
Based on the above experiments, we preliminarily confirm the feasibility of using pressure sensors to capture mouse grip posture for user authentication. However, the measurements obtained from the same user at different times exhibit noticeable deviations. This variation is likely caused by temporal heterogeneity in the pressure data, arising from non-uniform mouse movement speeds. Such heterogeneity can degrade authentication performance. In the next section, we exploit the intrinsic characteristics of pressure sensors to mitigate these deviations by reducing the effective contact area.
Figure 4 depicts the working flow of our proposed system, including the following four key steps. Firstly, we modify the pressure sensor and construct the sensor arrangement. Secondly, the sensor data and mouse trajectory data is collected. Then, based on whether the mouse is moving, the sensor data is divided into static data and dynamic data, and features are extracted. Finally, these features are matched to perform user authentication.
Pressure-sensor mouse setup . We first deploy pressure sensors at five key positions on the mouse. To initialize the system, sensors (left button, right button, left side, and right side) with different modification sizes are attached according to a predefined layout. The modified sensors can reduce signal deviations and increase feature resolution, as described in Sections 5.2 and 5.3. All sensors except the circular one located at the center of the mouse require structural modification.
Data collection . The system simultaneously collects mouse trajectory data and pressure readings from all sensors, which are then processed on a PC. A preliminary integrity check is performed by correlating mouse coordinate changes with pressure sensor data. Specifically, if mouse movement is detected without corresponding pressure sensor responses, the system considers this a potential unauthorized intrusion and immediately issues a warning to the legitimate user. In such cases, the authentication process is terminated without further processing.
Filtering and feature extraction . This step addresses directionality sensitivity in the pressure data. The collected signals are segmented based on movement direction, filtered accordingly, and transformed into features suitable for subsequent classification. In addition, we increase the feature dimension by adjusting the distribution of sensor contact surface regions. Authentication . Finally, the extracted features are compared with the templates stored in the database to verify the user's identity.
Since the output of the pressure sensor depends on the contact area, we attempt to reduce measurement deviations caused by hand movement by cutting the printed semiconductor flexible substrate into different sizes. To this end, we first conduct a preliminary experiment to examine the relationship between the sensor's measurement value and the contact area of the printed semiconductor flexible substrate. As shown in Figure 5 , the substrate is divided into five equal regions, labeled P1–P5, and each region is cut to a different thickness to evaluate its effect on the sensor response. In total, there are 5 5 = 3, 125 possible arrangements for a single sensor configuration.
We simulate user-applied pressure on the sensors by placing different weights on a fixed-size base. The weight is applied at five distinct positions corresponding to the substrates of both the standard and modified pressure sensors. As shown in Figure 6 , when the printed semiconductor flexible substrate is unmodified, significant variations in the measured values are observed across all positions as the applied pressure changes. After modifying the substrate, these variations are substantially reduced. However, at the fifth position, the measured value still exhibits pronounced changes with pressure.
The relationship between pressure and measurement value of a normal pressure sensor and a modified pressure sensor. (a) The measurement value of a normal pressure sensor. (b) The measurement value of a modified pressure sensor. Subsequently, we compared the measurements from the original left-button pressure sensor and the modified sensor while the user moved the mouse to the left, collecting data in three trials, as shown in Figure 7 . It can be observed that the original sensor exhibits significant deviations, whereas the modified sensor demonstrates substantially smaller deviations.
4. Practical Deployment, Analysis & Case Studies The measurement value of the left button pressure sensor after the user moves left three times. (a) The measurement value with normal pressure sensor. (b) The measurement value with modified pressure sensor. The static sensor data remains essentially constant when the user holds the mouse, whereas the dynamic sensor data varies with the direction of mouse movement, as shown in Figure 8 . There is a significant difference in the average value distribution of the five pressure sensors when user moves the mouse left vs. right. Conversely, sensor measurements remain relatively consistent when the mouse is moved repeatedly in the same direction. Consequently, static data acquired while the user holds the mouse is straightforward to calibrate, whereas dynamic data is more challenging to calibrate reliably.
Distribution of sensor measurement average values under different mouse movement directions. To capture pressure data across all possible mouse movement directions, the optimal approach is to move the mouse in a circular pattern, as circular movement covers the full range of directions. During dynamic training data collection, the user performs 10 circular movements, while for static data collection, the user holds the mouse stationary for 10 s. The authentication system records the mouse movement trajectory concurrently as the user executes the circular movements. The pressure sensor data collected along the circular trajectory is divided into 12 direction domains, as illustrated in Figure 9 . The direction domains are determined based on the angle between the movement direction and the X-axis, and the sensor data sequences are segmented accordingly. Each segment is then extracted as dynamic pressure feature data corresponding to its direction domain. For static data, if the mouse trajectory shows no directional change, the sequence is classified as static data.
To determine the mouse direction domain, we record the current mouse coordinates every 0.1 s and compute the corresponding trajectory direction. Data sequences with the same direction domain are then spliced, as described in Algorithm 1 . First, the starting coordinates ( X 0 , Y 0 ) are recorded as the 0-th coordinate. Then, we check whether the current trajectory coordinates match the previous ones. If the coordinates remain unchanged, the corresponding sensor data is labeled as a static sequence. If the coordinates have changed, we calculate the vector angle formed between the current and previous coordinates. All sensor data sequences are then segmented according to these vector angles, resulting in sensor sequences for all 12 direction domains. It is worth noting that, as described in Section 5.1, the pressure data has already been validated before feature extraction, ensuring that there are no missing values in the series. Afterwards, we use every 20 consecutive data as a sample feature. Regarding as five sensors on the mouse, there is 100 points per sample feature for model training.
Additionally, we enhance the feature resolution in the spatial domain by accounting for differences in user hand size and usage habits. On a standard sensor, pressing different areas with the same force may produce identical measurement values, as shown in Figure 10a . However, different users tend to press different positions while using a mouse. To increase the variability of position and pressure, we reshape the printed semiconductor flexible substrate into trapezoidal forms, as shown in Figure 5 . This modification allows the sensor to differentiate pressure across locations, thereby improving its spatial resolution. As illustrated in Figure 10 , measurement values across positions are nearly identical on the unmodified substrate, whereas after modification, the values clearly vary depending on the placement of the weight.
The relationship between position and measurement value of normal pressure sensor and modified pressure sensor under different pressures. (a) The measurement value of a normal pressure sensor. (b) The measurement value of a modified pressure sensor. By modifying this sensor, we can configure the mouse with sensors of varying degrees of modification. Assuming there are five thicknesses of the sensor's printed semiconductor flexible substrate, a sensor can be arranged in 5 5 = 3, 125 different ways at five positions. The total configuration has 3, 125 4 ≈9.5 × 10 13 different arrangements at four key positions of the mouse (left button, right button, left side, and right side). If more types of substrate are set up, more arrangements can be expanded.
We convert the time-series data from the five sensors into a two-dimensional matrix, with time as rows and channels as columns, to serve as input samples for the models. Every 20 consecutive data rows are treated as a sample feature, with each sample containing 100 data points. The models are trained and evaluated using KNN (Euclidean distance), SVM (Gaussian kernel), Naive Bayes (Gaussian kernel), logistic regression, and decision tree classifiers. Prior to model input, the data undergoes filtering and principal component analysis (PCA). The first principal component of PCA, which explains 95 % of the variance, combined with Euclidean distance, is used to remove outliers. We train separate models on features corresponding to 12 direction domains and one static grip posture, resulting in 13 user authentication models. In practical scenarios, users may not move the mouse in all 12 direction domains during operation, meaning dynamic data for some directions may be unavailable. Therefore, we calculate the accuracy only for the models corresponding to the available direction domains and report the average.
In this section, we implement the prototype system and evaluate its performance through extensive experiments. A total of 12 healthy, right-handed participants aged 18–40 were recruited. Pressure data were collected for two types of mouse operations (stationary and moving) across four typical time periods (morning, noon, afternoon, and evening). A 16 bit ADC module (NI USB-6009) with 1 kHz sampling rate was used to synchronously record five-channel signals. Experiments were conducted in a typical office environment, with sensors calibrated prior to data collection and user actions standardized via a visual guidance interface.
During the experiments, different modified pressure sensors were attached to the mouse, with each user assigned a unique sensor combination as their credential. We selected 12 corresponding sensor combinations, as shown in Figure 11 . Each user uses the mouse with unique sensor layout to collect data. Static data collection for 10 s, dynamic data collection for 10 times with specified circle pattern. We use 80% of the data as the training set and the remaining 20% as the testing set.
We use Matlab to process the data and train the model using the toolbox of classification learner. To quantify system performance, we have set three main indicators: False Accept Rate (FAR), False Reject Rate (FRR), and Accuracy. FAR is the measure of the likelihood that system will incorrectly accept an access attempt by an unauthorized user, which is calculated as Equation 1 : FRR is the measure of the likelihood that system incorrectly rejects an access of an authorized user by Equation 2 : where FP means false positive where the classifier predicts a positive sample but the actual sample is negative, TN is true negative where the classifier predicts a negative sample and it is indeed a negative sample, FN is false negative where the classifier predicts a negative sample but the actual sample is positive, TP means true positive where the classifier predicts a positive sample and it is indeed a positive sample.
Note that, our system continuously checks for the presence of mouse trajectory and pressure data. If there is trajectory data present at the same time but pressure data is missing, it will be considered that the computer has been hacked. Since data checking is relatively simple, in the following text, we will mainly focus on using the extracted pressure data features for identity verification.
We first evaluate the overall performance in distinguishing different users. Each user has a unique sensor distribution on their mouse, and we select 12 distributions. Only four layouts of pressure sensors are shown here. In reality, a single sensor can be arranged in 5 5 different ways at five positions, as described in Section 5.3. To simplify the schematic representation, we use four patterns to represent the four sensor layouts, and show the distribution of sensors at four positions on the mouse as shown in Figure 11 .
Figure 12a displays the results. The FAR below 0.1 %, and the FRR is under 0.4 %. It can be observed that the FAR for most users (9 out of 12) is essentially 0, indicating that the system can accurately identify all unauthorized users every time. The overall performance of system. (a) Overall FAR and FRR performance of 12 users. (b) The authentication accuracy of different training models.
5. Performance Evaluation & Extended Technical Observations Next, we evaluated the authentication accuracy of different models. Ten-fold cross-validation was applied across all models. Meanwhile, we employed the Wilson normal approximation 95% confidence interval to ensure the reliability of the results. As shown in Figure 12b , KNN achieved the highest accuracy among the five models. The accuracy of the system exceeds 99% when KNN model is used while the confidence interval is [99.26%, 99.99%]. Consequently, KNN is used consistently in all subsequent evaluations.
The size of a user's training set can influence authentication accuracy. We evaluated the model's performance with varying numbers of training samples. As shown in Figure 13a , authentication accuracy generally improves as the number of training samples increases, reaching approximately 99% once the sample size exceeds 2, 000. The performance of system under various impacts. (a) The authentication time of system under different sample numbers. (b) The authentication accuracy of different training samples set. (c) The authentication accuracy of different test samples set. (d) The authentication accuracy of different mouse shape.
Different mouse operations can produce varying amounts of pressure data, which may affect authentication accuracy. Since the direction of mouse movement can vary across application scenarios, this experiment evaluates only data collected under static grip conditions. As shown in Figure 13b , authentication accuracy generally improves with an increasing number of static samples, reaching a maximum of approximately 99.6% when 200 test samples are used.
The system should be able to distinguish unauthorized mouse of different shapes, even when they are equipped with pressure sensors of the same layout. We evaluated five commonly used mice of different shapes, each fitted with the same sensor layout, and collected data samples from the same user. As shown in Figure 13c , the FAR and FRR below 1%. The authentication time of the system comprises three main components: data collection, feature extraction, and feature matching. Data collection time depends on both the sampling rate and the number of samples. To evaluate authentication latency, we measured the combined time required for feature extraction and feature matching across varying sample sizes.
Figure 13d presents the cumulative distribution function (CDF) of latency based on 50 measurements. The average values for 20, 50, 100, 200, and 500 samples are 4.6 ms, 4.8 ms, 4.9 ms, 5.5 ms, and 6.7 ms, respectively. Users may not use a mouse to operate their computer for extended periods, and their pressure-based fingerprints may become outdated over time. To evaluate this factor, we collected mouse usage data from the same user each morning and afternoon over five consecutive days. As shown in Figure 14 , authentication accuracy exceeds 98 % across most time intervals. Although accuracy decreases slightly with longer collection intervals, the system can mitigate this effect by continuously acquiring training data during normal computer use.
Our system is designed for user authentication, so it is natural to consider that attackers might attempt to imitate the habitual gestures of legitimate users or counterfeit a legitimate mouse. In this section, we summarize how the system addresses these two threats. An attacker may gain prior knowledge of a legitimate mouse's model and sensor layout. We aim to test whether a counterfeit pressure-sensor mouse can pass the authentication system. Existing research ( Han et al., 2016 ; González, 2022 ; Zhao et al., 2022a ) mainly detects counterfeiting attacks through physical fingerprints caused by hardware differences or via liveness detection techniques. Our system leverages pressure sensors to extract fine-grained biometric features while simultaneously verifying the mouse shape and user grip posture. To this end, we attached 10 mouse with identical sensor layouts (the sixth layout in Figure 11 ). Figure 15a shows the FAR and FRR results. The FAR remains below 0.2 %, and the FRR is under 1 %, indicating that small positional differences in sensor deployment or variations in modified sensors are reflected in the pressure measurements. Furthermore, individual user habits also help the system accurately authenticate legitimate users.
The performance of FAR and FRR under counterfeiting attack and imitation attack. (a) Performance of resisting the counterfeiting attack. (b) Performance of resisting the imitation attack. Attackers may try to deceive the system by learning and mimicking a legitimate user's habitual mouse usage posture. Most behavior-based authentication studies focus on addressing this type of attack. Prior works ( Song et al., 2023 ; Mahfouz et al., 2024 ) demonstrate that even if an attacker imitates a user's gait or touchscreen behavior, the system can identify them by extracting biometric features. In this study, we assessed the distinguishability of users' mouse grip patterns. We invited ten volunteers to evaluate the experiment. The remaining nine volunteers imitated the grip of another user and use the same mouse for authentication. Figure 15b presents the system's performance for each participant. The FAR remains below 0.2% for all users, while the maximum FRR stays under 1%. These results indicate that even if an attacker imitates a legitimate user with an authenticated mouse, the system rejects the attacker with over 99 % probability. This demonstrates that each user exhibits a unique and distinguishable mouse grip pressure, enabling effective identification.
This study evaluates system performance using only a limited number and demographic range of participants. Expanding the user base to include a broader age distribution and special populations, such as individuals with musculoskeletal disorders, could further validate system robustness. Intuitively, mouse usage patterns vary more significantly across different age groups, while users with musculoskeletal conditions exhibit distinct gripping postures compared to healthy individuals.
Moreover, an increase in the number of participants may lead to a decrease in authentication accuracy. However, in typical office environments, the number of users is on the order of dozens. Our goal is to identify instances of unauthorized access. Pressure sensors are susceptible to data drift due to environmental factors, such as changes in temperature, humidity, or atmospheric pressure that affect resistivity. These environmental influences are negligible compared to the direct pressure applied during use. For instance, the rate of change in sensor measurements is approximately 100 Pa/°C ( Xiao et al., 2011 ), whereas typical human grip pressure is on the order of 0.3 MPa . In addition, the system can alleviate this impact by continuously acquiring training data during normal computer use.
This study segments dynamic sensor data according to 12 directional domains. This segmentation approach is motivated by the observation that pressure signals vary with the direction of mouse movement, making direction-based division necessary. Moreover, finer-grained directional partitioning facilitates more detailed feature extraction, which can potentially improve system performance.
In this study, five classic machine learning methods are used to train the authentication model. In fact, deep learning can also be utilized to train this model, particularly methods such as transformers and large models. We will conduct this research in our future work. Furthermore, mouse grip habits involve multimodal data, such as mouse speed and click speed based on traditional keystroke dynamics. The construction of fusion models is also a significant research direction for our future work.
In this study, participants are instructed to perform 10 circular mouse movements during the registration phase to capture sensor data across all directional domains. In practical deployments, the explicit registration step could be eliminated by intermittently collecting representative movement data during routine computer use. This approach would enable the system to acquire training data passively, thereby reducing the burden of dedicated data collection sessions.
This paper presents a continuous authentication system based on mouse grip posture using pressure sensors. The system leverages the natural variations in users' grip behavior. To capture these differences, we deploy pressure sensors on the mouse surface and modify them to enhance feature resolution. Additionally, we introduce a data stratification method for omnidirectional mouse movements, enabling user authentication without disrupting normal usage. Extensive experiments demonstrate that the system achieves excellent authentication performance.
The raw data supporting the conclusions of this article will be made available by the authors, without undue reservation. The studies involving humans were approved by Institutional Review Committee, School of Information Engineering, Xi'an University. The studies were conducted in accordance with the local legislation and institutional requirements. The participants provided their written informed consent to participate in this study.
XZ: Funding acquisition, Conceptualization, Writing – review & editing, Data curation, Writing – original draft, Methodology, Formal analysis. JWa: Writing – original draft, Software, Investigation, Data curation, Methodology, Validation, Visualization. YL: Funding acquisition, Project administration, Methodology, Investigation, Writing – original draft. JWu: Funding acquisition, Writing – review & editing, Supervision, Writing – original draft. GL: Funding acquisition, Writing – review & editing, Supervision.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Biometrics • https://en.wikipedia.org/wiki/User%20behavior%20analytics • https://en.wikipedia.org/wiki/Typing • https://www.frontiersin.org/journals/computer-science/articles/10.3389/fcomp.2026.1867907/full
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Mouse Movement Biometrics For Continuous User Authentication.
[*] Synchronizing KnowBe4 Awareness Training telemetry... ──────────────────────────────────────────────────────────────────────── [11:45:02.102] MAIL Dispatched simulated assessment templates [11:45:02.155] REPORT Majority of active users flagged probe via Phish Alert Button [11:45:02.210] CLICK Simulated lure baseline reduced below risk threshold [11:45:02.290] TRAIN Auto-enrolled flagged users into adaptive micro-learning modules ──────────────────────────────────────────────────────────────────────── [✓] Human Security Index: Phish-Prone percentage safely minimized
| Campaign Simulation | Platform Used | Total Recipients | Reported via Phish Button | Phish-Prone Percentage |
|---|---|---|---|---|
| Urgent Communication Lure | KnowBe4 KMSAT | 350 Employees | 318 (90.8%) | 2.9% (OPTIMAL) |
| Account Credential Lure | Proofpoint ZenGuide | 350 Employees | 324 (92.5%) | 2.1% (OPTIMAL) |
| Executive Impersonation | Mimecast Engage | 200 Executives | 192 (96.0%) | 1.5% (OPTIMAL) |