Complete Technical Paper Content — Multi Cloud Key Management Service Simulation Project
Overview & System Context
Multi Cloud Key Management Service Simulation Project: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9512 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Cloud management refers to the administration and oversight of cloud computing products and services. Public clouds are managed by cloud service providers, which operate the underlying infrastructure such as servers, storage, networking, and data center facilities. Users may also opt to manage their public cloud services with a third-party cloud management tool.
Users of public cloud services can generally select from three basic cloud provisioning categories: User self-provisioning: Customers purchase cloud services directly from the provider, typically through a web form or console interface. The customer pays on a per-transaction basis. Advanced provisioning: Customers contract in advance a predetermined amount of resources, which are prepared in advance of service. The customer pays a flat fee or a monthly fee.
Dynamic provisioning: The provider allocates resources when the customer needs them, then decommissions them when they are no longer needed. The customer is charged on a pay-per-use basis. Managing a private cloud requires software tools to help create a virtualized pool of compute resources, provide a self-service portal for end users and handle security, resource allocation, tracking and billing. Management tools for private clouds tend to be service driven, as opposed to resource driven, because cloud environments are typically highly virtualized and organized in terms of portable workloads. In hybrid cloud environments, compute, network and storage resources must be managed across multiple domains, so a good management strategy should start by defining what needs to be managed, and where and how to do it. Policies to help govern these domains should include configuration and installation of images, access control, and budgeting and reporting. Access control often includes the use of Single sign-on (SSO), in which a user logs in once and gains access to all systems without being prompted to log in again at each of them.
Provisioning and orchestration: create, modify, and delete resources as well as orchestrate workflows and management of workloads Automation: Enable cloud consumption and deployment of app services via infrastructure-as-code and other DevOps concepts Security and compliance: manage role-based access of cloud services and enforce security configurations Service request: collect and fulfill requests from users to access and deploy cloud resources. Monitoring and logging: collect performance and availability metrics as well as automate incident management and log aggregation Inventory and classification: discover and maintain pre-existing brownfield cloud resources plus monitor and manage changes Cost management and optimization: track and rightsize cloud spend and align capacity and performance to actual demand Migration, backup, and DR: enable data protection, disaster recovery, and data mobility via snapshots and/or data replication Organizations may group these criteria into key use cases including Cloud Brokerage, DevOps Automation, Governance, and Day-2 Life Cycle Operations. Enterprises with large-scale cloud implementations may require more robust cloud management tools which include specific characteristics, such as the ability to manage multiple platforms from a single point of reference, or intelligent analytics to automate processes like application lifecycle management. High-end cloud management tools should also have the ability to handle system failures automatically with capabilities such as self-monitoring, an explicit notification mechanism, and include failover and self-healing capabilities.
On-premises private cloud - Where the cloud environment exists within the customer organization. Platforms such as VMWare and OpenStack as well as integrated systems such as those from Nutanix, HPE, and others should be integrated to manage private cloud resources. Capabilities should also include integration with container orchestrators such as Kubernetes. CSP hosted private cloud – Sometimes called dedicated or managed cloud. Private hosted cloud resources are managed via APIs made available by the private cloud provider, in much the same way as public cloud resources and often include additional staffing to fully manage day to day operations. Public cloud service – The CMP must integrate with required public cloud services such as Amazon Web Services (AWS), Microsoft Azure, Google Cloud Platform (GCP), IBM Cloud, Oracle, etc to enable management of resources residing in public cloud services. Integration can be achieved by use of the public APIs of the target cloud service, or by an agent running within the public cloud service environment. IT Service Management – It is typical for CMPs to rely on existing enterprise management systems to provide capabilities such as incident management, configuration management, asset management, and financial management. Service Automation – Organizations may consider CMP integration with existing automation tools to simplify resource management. Integration with configuration management tools such as Chef and Puppet, and deployment tools such as Terraform are key considerations.
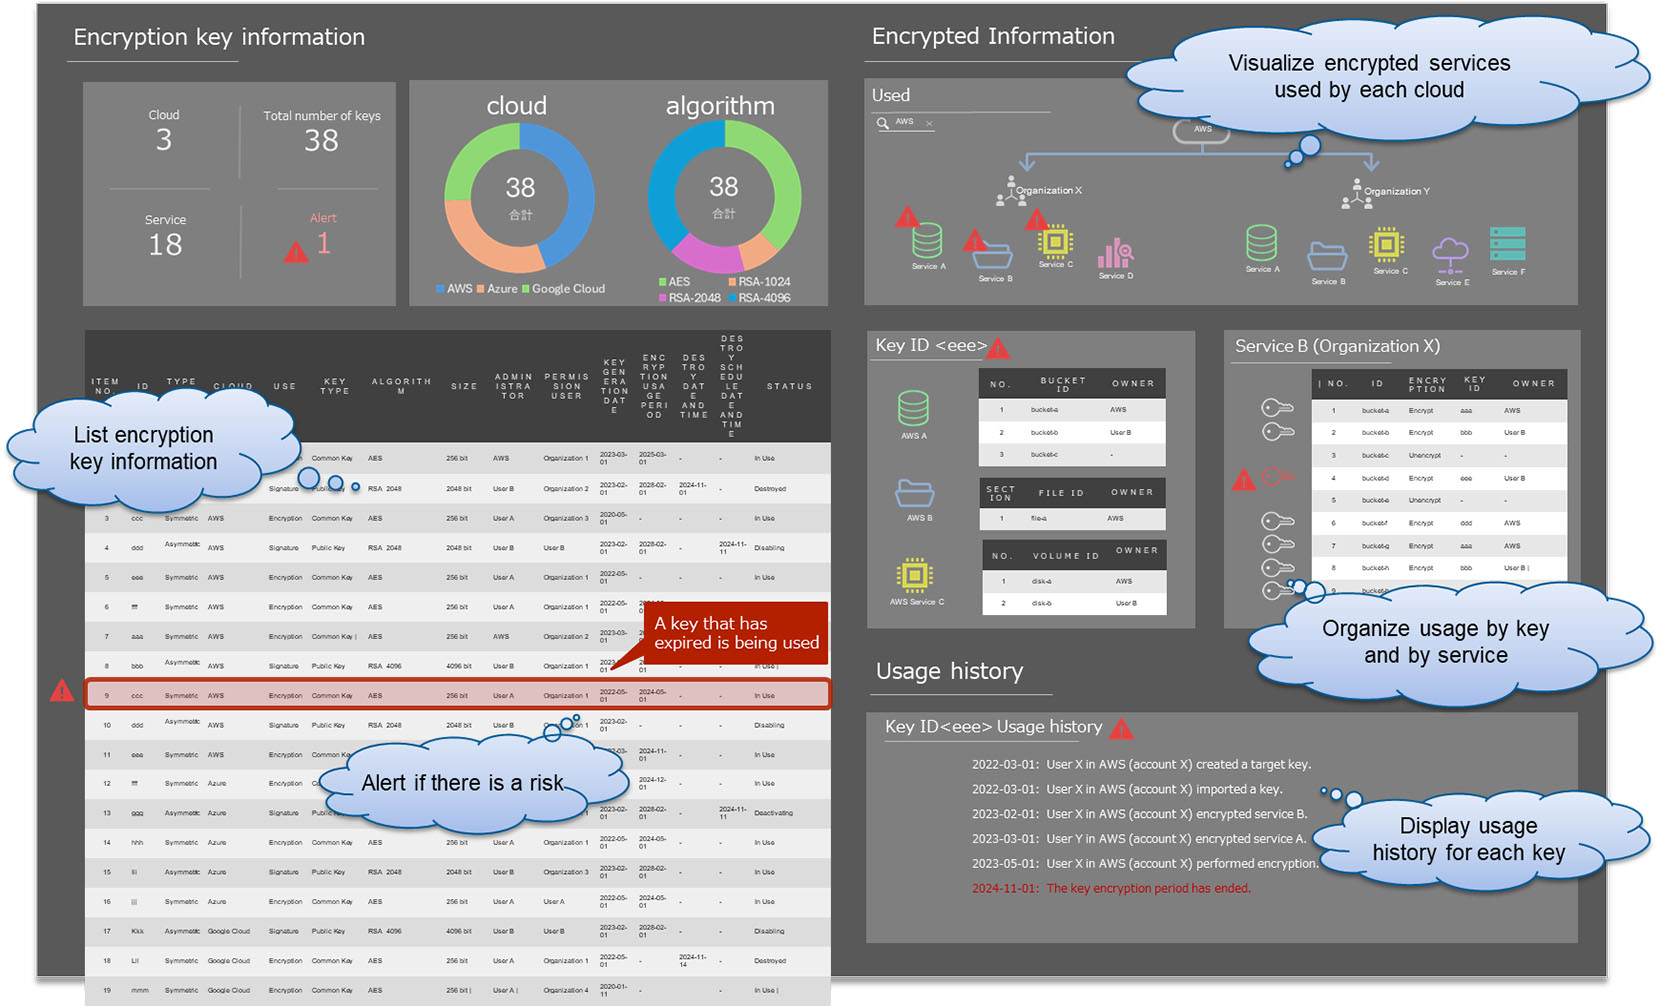
Figure 1: What is Multi-Cloud Encryption Key Monitoring to Improve Crypto Agility ... Microsoft Azure, sometimes stylized Azure, and formerly Windows Azure, is the cloud computing platform developed by Microsoft. It offers management, access and development of applications and services to individuals, companies, and governments through its global infrastructure. Microsoft Azure supports multiple programming languages, tools, and frameworks, including Microsoft-specific and third-party software and systems. Azure was first introduced at the Professional Developers Conference (PDC) in October 2008 under the code name "Project Red Dog". It was officially launched as Windows Azure in February 2010 and later renamed to Microsoft Azure on March 25, 2014.
Event Hubs, which provides event and telemetry ingress to the cloud at a massive scale, with low latency and high reliability. For example, an event hub can be used to track data from cell phones such as coordinating with a GPS in real time. Queues, which allows one-directional communication. A sender application would send the message to the service bus queue and a receiver would read from the queue. Though there can be multiple readers for the queue, only one would process a single message. Topics, which provides one-directional communication using a subscriber pattern. It is similar to a queue; however, each subscriber will receive a copy of the message sent to a Topic. Optionally, the subscriber can filter out messages based on specific criteria defined by the subscriber. Relays, which provides bi-directional communication. Unlike queues and topics, a relay does not store in-flight messages in its memory; instead, it just passes them on to the destination application.
Through Azure Blockchain Workbench, Microsoft is providing the required infrastructure to set up a consortium network in multiple topologies using a variety of consensus mechanisms. Microsoft provides integration from these blockchain platforms to other Microsoft services to streamline the development of distributed applications. Microsoft supports many general-purpose blockchains, including Ethereum and Hyperledger Fabric and purpose-built blockchains like Corda.
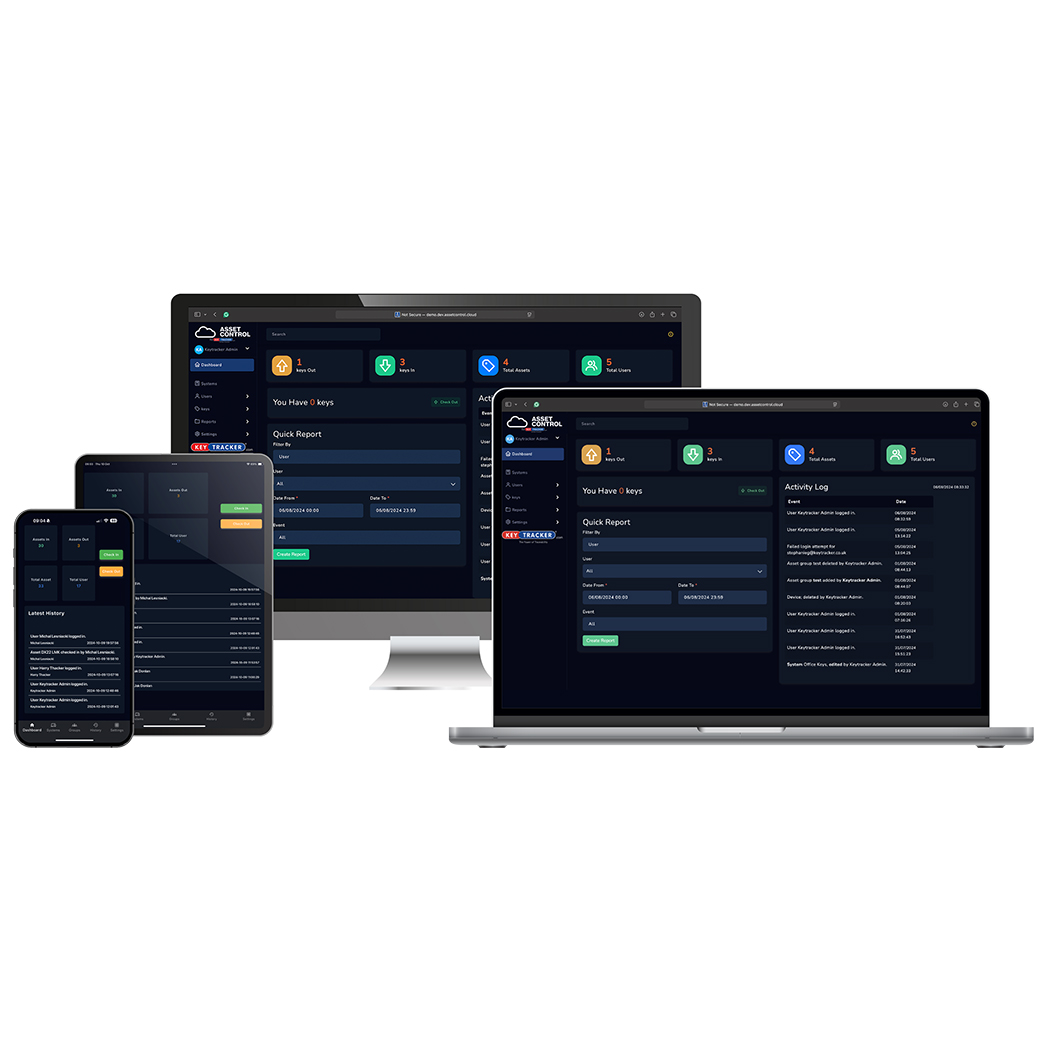
In 2005, Microsoft took over Groove Networks, and Bill Gates made Groove's founder Ray Ozzie one of his 5 direct reports as one of 3 chief technology officers. Ozzie met with Amitabh Srivastava, which let Srivastava change course. They convinced Dave Cutler to postpone his retirement, and their teams developed a cloud operating system. Figure 2: Key Management Solutions from KeyTracker Ltd October 2008 (PDC LA) – Announced the Windows Azure Platform. March 2009 – Announced SQL Azure Relational Database. November 2009 – Updated Windows Azure CTP, Enabled full trust, PHP, Java, CDN CTP, and more. February 1, 2010 – Windows Azure Platform commercially available. June 2010 – Windows Azure Update, .NET Framework 4, OS Versioning, CDN, SQL Azure Update. October 2010 (PDC) – Platform enhancements, Windows Azure Connect, improved Dev / IT Pro Experience. December 2011 – Traffic manager, SQL Azure reporting, HPC scheduler. June 2012 – Websites, Virtual machines for Windows and Linux, Python SDK, new portal, locally redundant storage. April 2014 – Windows Azure renamed Microsoft Azure, ARM Portal introduced at Build 2014. July 2014 – Azure Machine Learning public preview.
November 2014 – Outage affecting major websites, including MSN.com. September 2015 – Azure Cloud Switch introduced as a cross-platform Linux distribution. Currently known as SONiC. December 2015 – Azure ARM Portal (codename "Ibiza") released. March 2016 – Azure Service Fabric is generally available. November 15, 2016 – Azure Functions is generally available. May 10, 2017 – Azure Cosmos DB is generally available. May 7, 2018 – Azure Maps is generally available. July 16, 2018 – Azure Service Fabric Mesh public preview. September 24, 2018 – Microsoft Azure IoT Central is generally available.
October 10, 2018 – Microsoft joins the Linux-oriented group Open Invention Network. April 17, 2019 – Azure Front Door Service is now available. March 2020 – Microsoft said that there was a 775% increase in Microsoft Teams usage in Italy due to the COVID-19 pandemic. The company estimates there are now 44 million daily active users of Teams worldwide. January 17, 2023 – Azure OpenAI Service is generally available. At fiscal year-end 2025, Microsoft reported that Azure surpassed US$75 billion in annual revenue and operated over 400 datacenters across 70 regions.
Azure Fundamentals Azure Data Fundamentals Azure AI Engineer Associate Azure AI Fundamentals Azure Cosmos DB Developer Specialty Azure Administrator Associate Azure Data Engineer Associate Azure Data Scientist Associate Azure Database Administrator Associate Azure Developer Associate Azure Enterprise Data Analyst Associate Azure Security Engineer Associate Azure Security Operations Analyst Associate Azure Identity and Access Administrator Associate Azure Security, Compliance, and Identity Fundamentals Azure Network Engineer Associate Azure Windows Server Hybrid Administrator Associate Azure Virtual Desktop Specialty Azure for SAP Workloads Specialty Azure Customer Data Platform Specialty Azure Cybersecurity Architect Expert Azure Solutions Architect Expert Azure Power Platform Solution Architect Expert Azure DevOps Engineer Expert Azure IoT Developer Specialty Azure Stack Hub Operator Associate Azure Machine Learning Specialty Business process management (BPM) is the discipline in which people use various methods to discover, model, analyze, measure, improve, optimize, and automate business processes. Any combination of methods used to manage a company's business processes is BPM. Processes can be structured and repeatable or unstructured and variable. Though not required, enabling technologies are often used with BPM. As an approach, BPM treats processes as important organizational assets that must be understood, managed, and continuously improved in order to create and deliver value to clients or customers.
This approach closely resembles other total quality management or continual improvement process methodologies. ISO 9000:2015 promotes the process approach to managing an organization. ...promotes the adoption of a process approach when developing, implementing and improving the effectiveness of a quality management system, to enhance customer satisfaction by meeting customer requirements. BPM proponents also claim that this approach can be supported, or enabled, through technology. Therefore, multiple BPM articles and scholars frequently discuss BPM from one of two viewpoints: people and/or technology. BPM streamlines business processing by automating workflows; while RPA automates tasks by recording a set of repetitive activities performed by humans. Organizations maximize their business automation leveraging both technologies to achieve better results.
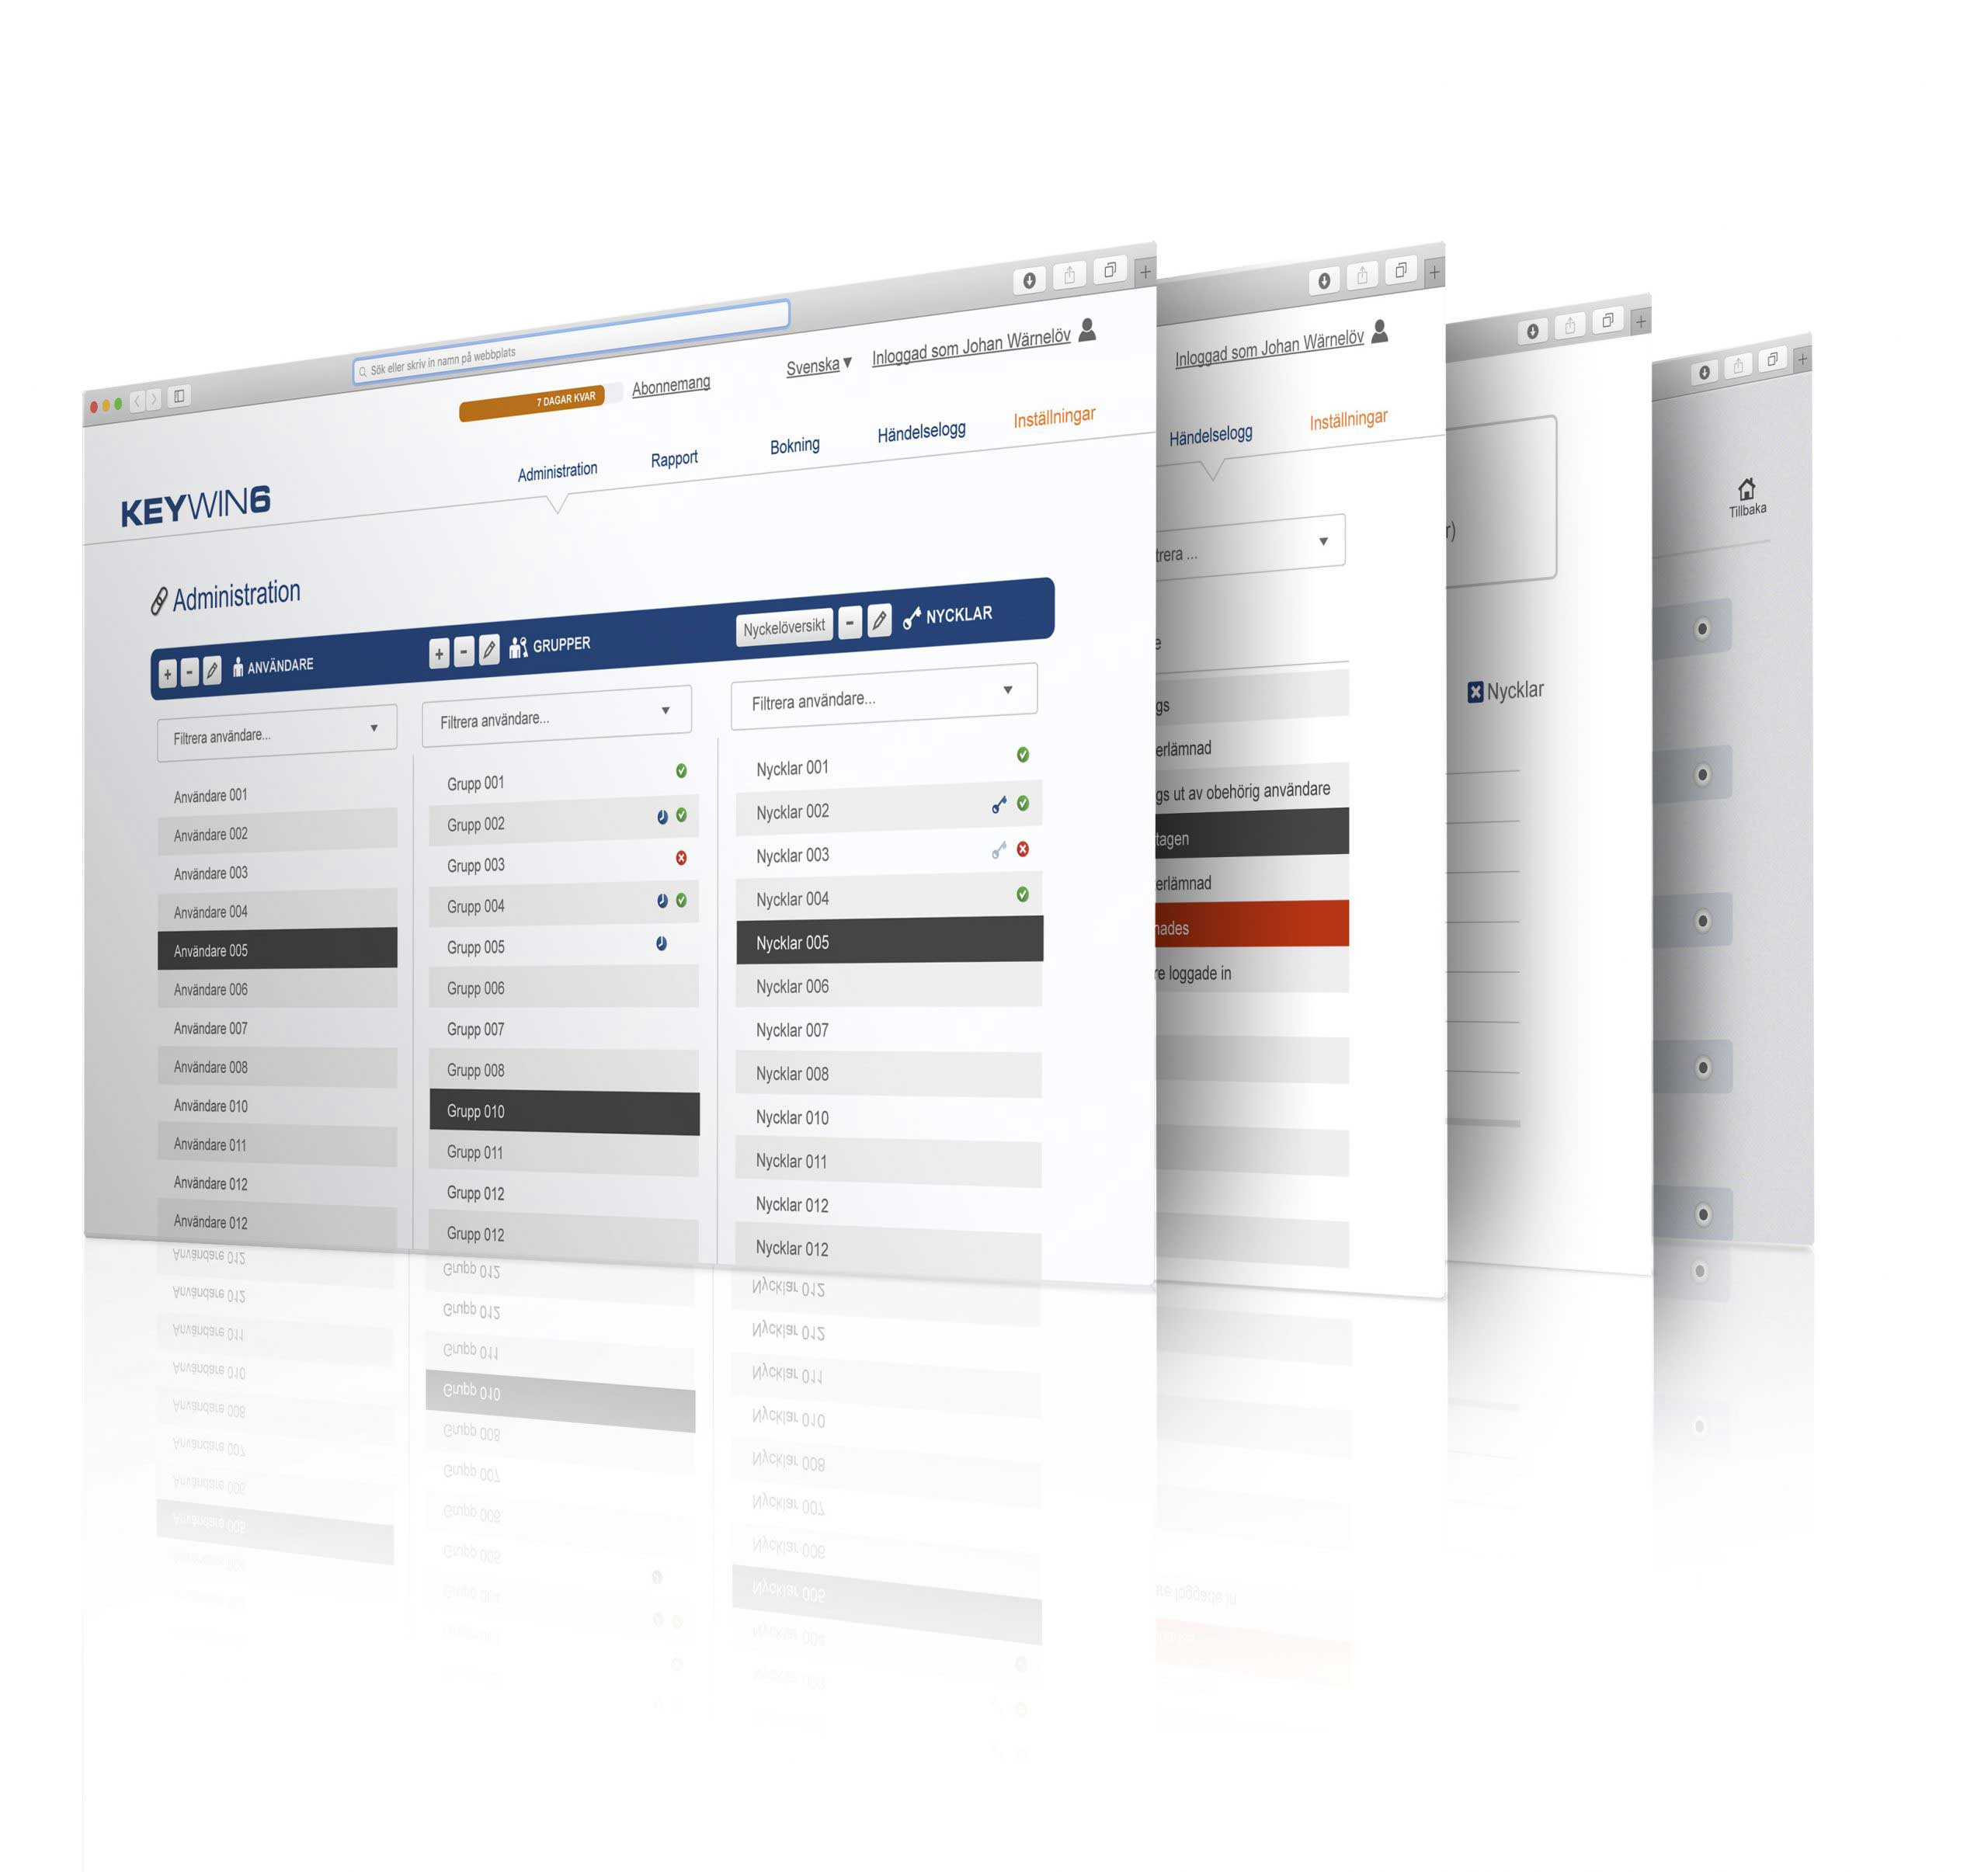
Figure 3: Key Management System Solutions for Enterprises | CSI Business process management (BPM) is a discipline involving any combination of modeling, automation, execution, control, measurement and optimization of business activity flows, in support of enterprise goals, spanning systems, employees, customers and partners within and beyond the enterprise boundaries. The Association of Business Process Management Professionals defines BPM as: Business process management (BPM) is a disciplined approach to identify, design, execute, document, measure, monitor, and control both automated and non-automated business processes to achieve consistent, targeted results aligned with an organization's strategic goals. BPM involves the deliberate, collaborative and increasingly technology-aided definition, improvement, innovation, and management of end-to-end business processes that drive business results, create value, and enable an organization to meet its business objectives with more agility. BPM enables an enterprise to align its business processes to its business strategy, leading to effective overall company performance through improvements of specific work activities either within a specific department, across the enterprise, or between organizations. Gartner defines business process management as: "the discipline of managing processes (rather than tasks) as the means for improving business performance outcomes and operational agility. Processes span organizational boundaries, linking together people, information flows, systems, and other assets to create and deliver value to customers and constituents." It is common to confuse BPM with a BPM suite (BPMS).
BPM is a professional discipline done by people, whereas a BPMS is a technological suite of tools designed to help the BPM professionals accomplish their goals. BPM should also not be confused with an application or solution developed to support a particular process. Suites and solutions represent ways of automating business processes, but automation is only one aspect of BPM.
visualize – functions and processes measure – determine the appropriate measure to determine success analyze – compare the various simulations to determine an optimal improvement improve – select and implement the improvement control – deploy this implementation and by use of user-defined dashboards monitor the improvement in real time and feed the performance information back into the simulation model in preparation for the next improvement iteration re-engineer – revamp the processes from scratch for better results This brings with it the benefit of being able to simulate changes to business processes based on real-world data (not just on assumed knowledge). Also, the coupling of BPM to industry methodologies allows users to continually streamline and optimize the process to ensure that it is tuned to its market need. As of 2012 research on BPM has paid increasing attention to the compliance of business processes. Although a key aspect of business processes is flexibility, as business processes continuously need to adapt to changes in the environment, compliance with business strategy, policies, and government regulations should also be ensured. The compliance aspect in BPM is highly important for governmental organizations. As of 2010 BPM approaches in a governmental context largely focus on operational processes and knowledge representation. There have been a number of technical studies on operational business processes in the public and private sectors, but researchers rarely take legal compliance activities into account—for instance, the legal implementation processes in public-administration bodies.
Process design encompasses both the identification of existing processes and the design of "to-be" processes. Areas of focus include representation of the process flow, the factors within it, alerts and notifications, escalations, standard operating procedures, service level agreements, and task hand-over mechanisms. Whether or not existing processes are considered, the aim of this step is to ensure a correct and efficient new design. The proposed improvement could be in human-to-human, human-to-system or system-to-system workflows, and might target regulatory, market, or competitive challenges faced by the businesses. Existing processes and design of a new process for various applications must synchronize and not cause a major outage or process interruption.
Modeling takes the theoretical design and introduces combinations of variables (e.g., changes in rent or materials costs, which determine how the process might operate under different circumstances). It may also involve running "what-if analysis"(Conditions-when, if, else) on the processes: "What if I have 75% of resources to do the same task?" "What if I want to do the same job for 80% of the current cost?".
Business process execution is broadly about enacting a discovered and modeled business process. Business rules have been used by systems to provide definitions for governing behavior, and a business rule engine can be used to drive process execution and resolution. A market has developed for enterprise software leveraging the business process management concepts to organize and automate processes. The recent convergence of this software from distinct pieces such as business rules engine, business process modelling, business activity monitoring and Human Workflow has given birth to integrated business process management suites. Forrester Research recognize the BPM suite space through three different lenses: Human-centric BPM Integration-centric BPM (enterprise service bus) Document-centric BPM (dynamic case management) However, standalone integration-centric and document-centric offerings have matured into separate, standalone markets.
Rapid application development using no-code/low-code principles is becoming an ever prevalent feature of BPMS platforms. RAD enables businesses to deploy applications more quickly and more cost effectively, while also offering improved change and version management. Gartner notes that as businesses embrace these systems, their budgets rely less on the maintenance of existing systems and show more investment in growing and transforming them.
While the steps can be viewed as a cycle, economic or time constraints are likely to limit the process to only a few iterations. This is often the case when an organization uses the approach for short to medium term objectives rather than trying to transform the organizational culture. True iterations are only possible through the collaborative efforts of process participants. In a majority of organizations, complexity requires enabling technology (see below) to support the process participants in these daily process management challenges. To date, some organizations often start a BPM project or program with the objective of optimizing an area that has been identified as an area for improvement. Currently, the international standards for the task have limited BPM to the application in the IT sector, and ISO/IEC 15944 covers the operational aspects of the business. However, some corporations with the culture of best practices do use standard operating procedures to regulate their operational process. Other standards are currently being worked upon to assist in BPM implementation (BPMN, enterprise architecture, Business Motivation Model).
Process engine – a robust platform for modeling and executing process-based applications, including business rules Business analytics – enable managers to identify business issues, trends, and opportunities with reports and dashboards and react accordingly Content management – provides a system for storing and securing electronic documents, images, and other files Collaboration tools – remove intra- and interdepartmental communication barriers through discussion forums, dynamic workspaces, and message boards BPM also addresses a number of the critical IT issues underpinning these business drivers, including: Managing end-to-end, customer-facing processes Consolidating data and increasing visibility into and access to associated data and information Increasing the flexibility and functionality of current infrastructure and data Integrating with existing systems and leveraging service oriented architecture (SOA) Establishing a common language for business-IT alignment Validation of BPMS is another technical issue that vendors and users must be aware of, if regulatory compliance is mandatory. The validation task could be performed either by an authenticated third party or by the users themselves. Either way, validation documentation must be generated. The validation document usually can either be published officially or retained by users.
According to Gartner, 20% of all the "shadow business processes" are supported by BPM cloud platforms. Gartner refers to all the hidden organizational processes that are supported by IT departments as part of legacy business processes such as Excel spreadsheets, routing of emails using rules, phone calls routing, etc. These can, of course also be replaced by other technologies such as workflow and smart form software.
2. System Architecture & Core Working Principles The emerging Internet of Things presents challenges for managing and controlling the flow of information across large numbers of connected devices. To address these challenges, approaches such as BPM Everywhere have been proposed, combining traditional business process management techniques with additional capabilities designed to support the coordination and automation of distributed devices.
ABPMP.org The Association of Business Process Management Professionals The NIST Definition of Cloud Computing. Peter Mell and Timothy Grance, NIST Special Publication 800-145 (September 2011). National Institute of Standards and Technology, U.S. Department of Commerce. Cloud Computing Synopsis and Recommendations. Peter Mell and Timothy Grance, NIST Special Publication 800-146 (May 2011). National Institute of Standards and Technology, U.S. Department of Commerce. Process execution through application ontologies. The movie demonstrates how semantic technologies can be applied as execution engine. Business Process Management is primarily an attitude. A YouTube movie on BPM approaches explaining the use case of BPM.
Cloud Key Management Service allows you to create, import, and manage cryptographic keys and perform cryptographic operations in a single centralized cloud service. You can use these keys and perform these operations by using Cloud KMS directly, by using Cloud HSM or Cloud External Key Manager, or by using Customer-Managed Encryption Keys (CMEK) integrations within other Google Cloud services.
With Cloud KMS you are the ultimate custodian of your data, you can manage cryptographic keys in the cloud in the same ways you do on-premises, and you have a provable and monitorable root of trust over your data. Access 20+ free products for common use cases, including AI APIs, VMs, data warehouses, and more. This tutorial teaches you how to encrypt and decrypt data using symmetric Cloud KMS keys.
Explore and deploy the components of a secure Google Cloud solution through hands on labs. Learn best practices for securing applications and data and mitigation techniques for attacks at many points in a Google Cloud-based infrastructure, including Distributed Denial-of-Service attacks, phishing attacks, and threats involving content classification and use. In this lab you'll learn how to use some advanced features of Google Cloud Security and Privacy APIs, including: setting up a secure Cloud Storage bucket, managing keys and encrypted data, and viewing Cloud Storage audit logs.
Shows how to set up an access-controlled credit and debit card tokenization service on Cloud Functions. To set up the service, the article uses IAM, Cloud KMS, and Datastore. PCI DSS Functions Datastore Learn how to implement the Payment Card Industry Data Security Standard (PCI DSS) for your business on Google Cloud. PCI DSS Compliance Security code samples are licensed under the Apache 2.0 License . For details, see the Google Developers Site Policies . Java is a registered trademark of Oracle and/or its affiliates.
Cloud Key Management Service (Cloud KMS) lets you create and manage cryptographic keys for use in compatible Google Cloud services and in your own applications. Using Cloud KMS, you can do the following: You can use the following table to identify which type of encryption meets your needs for each use case. The best solution for your needs might include a mix of encryption approaches. For example, you might use software keys for your least sensitive data and hardware or external keys for your most sensitive data. For additional information about the encryption options described in this section, see Protecting data in Google Cloud on this page. For more information about the service level agreement (SLA) that applies when using Cloud KMS, Cloud HSM, and Cloud EKM keys, see Service Level Agreement .
Encryption type Cost Compatible services Features Google-owned and Google-managed encryption keys (Google Cloud default encryption) Included All Google Cloud services that store customer data No configuration required. Automatically encrypts customer data saved in any Google Cloud service. Most services automatically rotate keys. Supports encryption using AES-256. FIPS 140-3 Level 1 validated. Customer-managed encryption keys - software (Cloud KMS keys) $0.06 per key version 40+ services You control automatic key rotation schedule; IAM roles and permissions; enable, disable, or destroy key versions. Supports symmetric and asymmetric keys for encryption and decryption . Automatically rotates symmetric keys .
Supports several common algorithms . FIPS 140-3 Level 1 validated. Keys are unique to a customer. Customer-managed encryption keys - hardware (Cloud HSM keys) $1.00 to $2.50 per key version per month 40+ services Optionally managed through Cloud KMS Autokey. You control automatic key rotation schedule; IAM roles and permissions; enable, disable, or destroy key versions. Supports symmetric and asymmetric keys for encryption and decryption . Automatically rotates symmetric keys . Supports several common algorithms . FIPS 140-2 Level 3 validated. Keys are unique to a customer. You can create and manage your own Single-tenant Cloud HSM instance to have more cryptographic isolation and greater administrative control of your HSM keys. Single-tenant Cloud HSM instances incur additional costs. Customer-managed encryption keys - external (Cloud EKM keys) $3.00 per key version per month 30+ services You control IAM roles and permissions; enable, disable, or destroy key versions. Keys are never sent to Google. Key material resides in a compatible external key management (EKM) provider . Compatible Google Cloud services connect to your EKM provider over the internet or a Virtual Private Cloud (VPC) . Supports symmetric keys for encryption and decryption . Manually rotate your keys in coordination with Cloud EKM and your EKM provider. FIPS 140-2 Level 2 or FIPS 140-2 Level 3 validated, depending on the EKM. Keys are unique to a customer. Client-side encryption using Cloud KMS keys Cost of active key versions depends on the protection level of the key. Use client libraries in your applications You control automatic key rotation schedule; IAM roles and permissions; enable, disable, or destroy key versions. Supports symmetric and asymmetric keys for encryption, decryption, signing, and signature validation . Functionality varies by key protection level. Cloud HSM for Google Workspace Flat rate monthly fee for each instance, plus cost of active key versions and cryptographic operations. Use Multi-tenant Cloud HSM keys for client-side encryption in Google Workspace You control automatic key rotation schedule; IAM roles and permissions; enable, disable, or destroy key versions. Use symmetric keys for encryption and decryption. Customer-supplied encryption keys Might increase costs associated with Compute Engine or Cloud Storage Cloud Storage Compute Engine You provide key materials when needed. Key material resides in-memory - Google does not permanently store your keys on our servers. Confidential Computing Additional cost for each confidential VM; might increase log usage and associated costs Compute Engine GKE Managed Service for Apache Spark Provides encryption-in-use for VMs handling sensitive data or workloads. Keys can't be accessed by Google. Protecting data in Google Cloud Google-owned and Google-managed encryption keys (Google Cloud default encryption) By default, data at rest in Google Cloud is protected by keys in Keystore, Google Cloud's internal key management service. Keys in Keystore are managed automatically by Google Cloud, with no configuration required on your part. Most services automatically rotate keys for you. Keystore supports a primary key version and a limited number of older key versions. The primary key version is used to encrypt new data encryption keys. Older key versions can still be used to decrypt existing data encryption keys. You can't view or manage these keys or review key usage logs. Data from multiple customers might use the same key encryption key. This default encryption uses cryptographic modules that are validated to be FIPS 140-3 Level 1 compliant. Customer-managed encryption keys (CMEKs) Cloud KMS keys that are used to protect your resources in CMEK-integrated services are customer-managed encryption keys (CMEKs).
You can own and control CMEKs, while delegating key creation and assignment tasks to Cloud KMS Autokey. Using Autokey is simpler than provisioning keys yourself, and is the recommended choice if the keys created by Autokey meet all of your requirements. To learn more about automating provisioning for CMEKs, see Cloud Key Management Service with Autokey . You can use your Cloud KMS keys in compatible services to help you meet the following goals: Own your encryption keys.
Control and manage your encryption keys, including choice of location, protection level, creation, access control, rotation, use, and destruction. Selectively delete data protected by your keys in the case of off-boarding or to remediate security events (crypto-shredding). Create dedicated, single-tenant keys that establish a cryptographic boundary around your data. Log administrative and data access to encryption keys. Meet current or future regulation that requires any of these goals. When you use Cloud KMS keys with CMEK-integrated services , you can use organization policies to ensure that CMEKs are used as specified in the policies. For example, you can set an organization policy that ensures that your compatible Google Cloud resources use your Cloud KMS keys for encryption. Organization policies can also specify which project the key resources must reside in. The features and level of protection provided depend on the protection level of the key: Software keys - You can generate software keys in Cloud KMS and use them in all Google Cloud locations. You can create symmetric keys with automatic rotation or asymmetric keys with manual rotation. Customer-managed software keys use FIPS 140-3 Level 1 validated software cryptography modules. You also have control over the rotation period, Identity and Access Management (IAM) roles and permissions, and organization policies that govern your keys. You can use your software keys with many compatible Google Cloud resources . Imported software keys - You can import software keys that you created elsewhere for use in Cloud KMS. You can import new key versions to manually rotate imported keys. You can use IAM roles and permissions and organization policies to govern usage of your imported keys. Hardware keys with Multi-tenant Cloud HSM - You can generate hardware keys in a cluster of FIPS 140-2 Level 3 Hardware Security Modules (HSMs). You have control over the rotation period, IAM roles and permissions, and organization policies that govern your keys. When you create HSM keys using Cloud HSM, Google Cloud manages the HSM clusters so you don't have to. You can use your HSM keys with many compatible Google Cloud resources —the same services that support software keys. For the highest level of security compliance, use hardware keys. Hardware keys with Single-tenant Cloud HSM - You can generate hardware keys in a cluster of dedicated partitions in FIPS 140-2 Level 3 Hardware Security Modules (HSMs) that you control. You have control over the rotation period, IAM roles and permissions, and organization policies that govern your keys. When you create a Single-tenant Cloud HSM instance, Google Cloud hosts the HSM clusters so you don't have to, but you control access to the instance and maintain it with a quorum of designated administrators. Instance operations require two-factor authentication using security keys that you own outside of Google Cloud. You can use your single-tenant HSM keys with many compatible Google Cloud resources —the same services that support software keys. For the highest level of security compliance with cryptographic isolation, use hardware keys. External keys and Cloud EKM - You can use keys that reside in an external key manager (EKM). Cloud EKM lets you use keys held in a supported key manager to secure your Google Cloud resources. You can connect to your EKM over the internet or over a Virtual Private Cloud (VPC) . Some Google Cloud services that support Cloud KMS keys don't support Cloud EKM keys. To learn more about which Cloud KMS locations support which protection levels, see Cloud KMS locations .
By default, data at rest in Google Cloud is protected by keys in Keystore, Google Cloud's internal key management service. Keys in Keystore are managed automatically by Google Cloud, with no configuration required on your part. Most services automatically rotate keys for you. Keystore supports a primary key version and a limited number of older key versions. The primary key version is used to encrypt new data encryption keys. Older key versions can still be used to decrypt existing data encryption keys. You can't view or manage these keys or review key usage logs. Data from multiple customers might use the same key encryption key.
This default encryption uses cryptographic modules that are validated to be FIPS 140-3 Level 1 compliant. Cloud KMS keys that are used to protect your resources in CMEK-integrated services are customer-managed encryption keys (CMEKs). You can own and control CMEKs, while delegating key creation and assignment tasks to Cloud KMS Autokey. Using Autokey is simpler than provisioning keys yourself, and is the recommended choice if the keys created by Autokey meet all of your requirements. To learn more about automating provisioning for CMEKs, see Cloud Key Management Service with Autokey .
You can use your Cloud KMS keys in compatible services to help you meet the following goals: Control and manage your encryption keys, including choice of location, protection level, creation, access control, rotation, use, and destruction. Selectively delete data protected by your keys in the case of off-boarding or to remediate security events (crypto-shredding).
Create dedicated, single-tenant keys that establish a cryptographic boundary around your data. When you use Cloud KMS keys with CMEK-integrated services , you can use organization policies to ensure that CMEKs are used as specified in the policies. For example, you can set an organization policy that ensures that your compatible Google Cloud resources use your Cloud KMS keys for encryption. Organization policies can also specify which project the key resources must reside in.
The features and level of protection provided depend on the protection level of the key: Software keys - You can generate software keys in Cloud KMS and use them in all Google Cloud locations. You can create symmetric keys with automatic rotation or asymmetric keys with manual rotation. Customer-managed software keys use FIPS 140-3 Level 1 validated software cryptography modules. You also have control over the rotation period, Identity and Access Management (IAM) roles and permissions, and organization policies that govern your keys. You can use your software keys with many compatible Google Cloud resources .
Imported software keys - You can import software keys that you created elsewhere for use in Cloud KMS. You can import new key versions to manually rotate imported keys. You can use IAM roles and permissions and organization policies to govern usage of your imported keys. Hardware keys with Multi-tenant Cloud HSM - You can generate hardware keys in a cluster of FIPS 140-2 Level 3 Hardware Security Modules (HSMs). You have control over the rotation period, IAM roles and permissions, and organization policies that govern your keys. When you create HSM keys using Cloud HSM, Google Cloud manages the HSM clusters so you don't have to. You can use your HSM keys with many compatible Google Cloud resources —the same services that support software keys. For the highest level of security compliance, use hardware keys.
Hardware keys with Single-tenant Cloud HSM - You can generate hardware keys in a cluster of dedicated partitions in FIPS 140-2 Level 3 Hardware Security Modules (HSMs) that you control. You have control over the rotation period, IAM roles and permissions, and organization policies that govern your keys. When you create a Single-tenant Cloud HSM instance, Google Cloud hosts the HSM clusters so you don't have to, but you control access to the instance and maintain it with a quorum of designated administrators. Instance operations require two-factor authentication using security keys that you own outside of Google Cloud. You can use your single-tenant HSM keys with many compatible Google Cloud resources —the same services that support software keys. For the highest level of security compliance with cryptographic isolation, use hardware keys.
3. Software Implementation, Frameworks & Protocols External keys and Cloud EKM - You can use keys that reside in an external key manager (EKM). Cloud EKM lets you use keys held in a supported key manager to secure your Google Cloud resources. You can connect to your EKM over the internet or over a Virtual Private Cloud (VPC) . Some Google Cloud services that support Cloud KMS keys don't support Cloud EKM keys.
You can use your Cloud KMS keys in custom applications using the Cloud KMS client libraries or Cloud KMS API . The client libraries and API let you encrypt and decrypt data, sign data, and validate signatures. You can use your Multi-tenant Cloud HSM keys in Cloud HSM for Google Workspace to manage the keys used for client-side encryption (CSE) in Google Workspace. You can Onboard to Cloud HSM for Google Workspace .
You can use the Confidential Computing platform to encrypt your data-in-use. Confidential Computing ensures that your data stays private and encrypted even while it's being processed. code samples are licensed under the Apache 2.0 License . For details, see the Google Developers Site Policies . Java is a registered trademark of Oracle and/or its affiliates.
Stay informed about the latest best practices, reports, and solutions in cloud security with CSA research. Stay connected with the cloud security community by attending local events, workshops, and global CSA conferences. Engage with industry leaders, gain new insights, and build valuable professional relationships—both virtually and in person. Join the countless professionals who have selected CSA for their training and certification needs.
Stay informed with the latest in cloud security news - visit our blog to keep your competitive edge sharp. Cryptographic key management is pivotal for ensuring the confidentiality and integrity of sensitive data. In the era of cloud computing, information sharing of access and data between multi-cloud environments has become common. While key management in single-provider implementations is relatively straightforward, managing keys across multiple cloud service providers (CSPs) is significantly more complex. Key management services and solutions (KMS) are critical for information protection throughout the key and certificate lifecycle, including the creation, storage, exchange, usage, rotation, and deletion of the certificates and keys.
The Cloud Security Alliance (CSA) Cloud Key Management Working Group has published this paper to share their recommendations for multi-cloud KMS. This document analyzes the security, regulatory, technical, and business considerations associated with key management in multi-cloud environments and recommends considerations for safeguarding symmetric and asymmetric keys, certificates, and secrets in such implementations.
This paper’s recommendations align with established key management frameworks including NIST SP 800-57 (Recommendation for Key Management) and NIST SP 800-130 (A Framework for Designing Cryptographic Key Management Systems), which provide comprehensive guidance applicable throughout multi-cloud environments. When cryptographic operations should be performed across multiple cloud models, providers, or deployments, key management complexity is significantly increased. Such operations may include encrypting and decrypting information to uphold confidentiality, signing and validating signed data to protect data integrity, or securely authenticating between platforms to establish trust.
Disparate CSPs, applications, environments, and cloud models vary significantly in governance, responsibility, deployment model (e.g., public, private, hybrid), and risks. CSPs often design their KMS to protect sensitive encryption keys from export, further complicating the synchronization and usage of symmetric keys or asymmetric key pairs between multiple providers. On the other hand, Bring-Your-Own-Key (BYOK) and Hold-Your-Own-Key (HYOK) responsibility models require organizational maturity and key management expertise. Third-party KMS solutions may solve many of these issues but also introduce secondary risks (security and operational risks) by introducing a vendor to mitigate these challenges. This paper addresses the common risks and challenges by suggesting strategies and solutions based on best practices for maintaining and using keys securely.
The scope of this paper is limited to understanding implementations common in multi-cloud architectures where the sharing or usage of keys, key material, and secrets affect more than one CSP entity, service provider, hybrid usage, or modality and how distinct KMS approaches address identified risks. This paper includes security, technical, regulatory, and business considerations associated with various key management models in multi-cloud environments. To aid the reader in first understanding key management complexities as they relate to key management models and relevant multi-cloud patterns, several such usages are presented, identifying where keys, key material, and secrets may involve multiple providers throughout the key management lifecycle (Figure 1). Following a review of these models and use cases, this document briefly discusses the critical risks or other business factors that may impact key management practices. In addition, three common key management approaches are discussed, sharing how each addresses identified risks or is otherwise suited for organizations based on the identified determinants. This approach is intended to allow the reader to relate to one or more models best suited for their environment and architecture, with a clear understanding of impacts and residual risks.
This document is designed for cloud architects and key management teams who must secure and access sensitive information across heterogeneous cloud environments; governance teams and auditors seeking to evaluate controls against industry best practice criteria; and vendor management teams who need to navigate complex technical and business factors that contribute to selection of solutions to aid in delivery of these services.
It is important to understand the complexity of managing keys to understand key management models and how multi-cloud architectures can affect the key lifecycle, access to key materials, locus of cryptographic operations, capabilities, limitations, and responsibilities for underlying key material. Additionally, concepts related to key management models, patterns, and architectures may overlap or use similar terminology.
An example of this is the term BYOK, commonly used in reference to a key type (external origin), a KMS architecture (customer on-premises KMS), and a key responsibility model (the implied responsibilities associated with the usage of such keys and system). While multi-cloud use cases, risks, and architectures are discussed herein, key management best practices for these implementations are explored in further depth in other CSA resources. The authors recommend reviewing the following CSA resources about best practices before proceeding: The first step in identifying the best approach for key management between cloud providers is to document the use cases involving key usage and flow within and between the various cloud providers. It is recommended that the entity analyze each use case, where all relevant cryptographic operations should be performed, which keys should be present, and document these findings.
This exercise should include identifying each distinct key as part of a documented cryptosystem containing, at minimum, the key name, unique identification (e.g., resource name), cryptography details (e.g., cipher, cryptographic algorithm, bit strength), origin, lifecycle protections, and allowed usage. It is then important to identify how keys are used by each application/service, how keys are managed, and how risks are mitigated through access limitations. A full understanding of how each key is managed, shared, used, and monitored with respect to this multi-cloud environment is required to determine the least privileges necessary to perform activities and risks associated with each, and also understand where other factors such as latency, storage limitations, key access, or regulatory compliance factors may influence architecture.
An example analysis is included below, whereby a custom application is deployed to one cloud provider, a Platform-as-a-Service (PaaS) provider ( CSP1 ), and information is processed from a relational database ( RD ) then delivered to a SaaS application ( App ) for further processing, which is hosted by a second PaaS provider ( CSP2 ). Once processing is complete, the results are forwarded to CSP1 for storage in a data warehouse service ( DW ). In this example, unique CSP- and customer-managed keys may be present for each applied protection.
This information above may be captured in tabular form, similar to the example in Table 1: This discussion considers the following common multi-cloud architectures, models, and patterns. In each example, unique factors such as key attributes, key ownership, data portability, or management responsibilities may impact the reader’s ultimate recommendations and decisions for managing keys and data across multiple cloud providers. Before considering how KMS architecture models affect an organization’s operations, it is important to understand how the key lifecycle itself may be affected by the entity’s multi-cloud implementation models and the risks these activities commonly incur.
The following section reviews common multi-cloud architectures and the critical key management considerations in the context of each workload. 4. Practical Deployment, Analysis & Case Studies KMS is crucial for ensuring data security stored in the data lake. It manages the generation, storage, rotation, and access of encryption keys that protect sensitive information both at rest and in transit. KMS integrates with the cloud provider’s identity and access management (IAM) to enforce access control policies.
When managing keys for data lake services, it is important to consider the compatibility of the KMS and desired data lake services. During the data lake provisioning process, customer-provided key preferences should be specified, and encryption keys in KMS should be created to meet all applicable security requirements for data protection and encryption keys 1 . For all subsequent data access, the key is required with every data read/write to ensure transparent data encryption/decryption; however, modern implementations often use envelope encryption where a data encryption key (DEK) is cached temporarily after KMS-authorized decryption.
Data is encrypted using a DEK, which is itself encrypted with a master key, or Key Encryption Key (KEK), managed in the KMS. Clients fetch the encrypted DEK securely, and the KMS handles decryption under strict access policies. Envelope encryption minimizes key exposure to applications. Client-side encryption implementations should retrieve keys from KMS rather than managing keys independently, as shown in Figures 2 and 3.
In addition, the data lake provider often natively supports its own encryption at rest through its native tooling, with or without customer access to such keys. While native tooling secures the infrastructure, customers usually lack direct control over those keys and it should be an important consideration while building regulatory-compliant data lakes. Figure 3: Client-Side Application Encryption (Application-Managed DEK with KMS Integration) In addition to these complexities, data lakes may implement additional data protection techniques: Dynamic Data Masking: Presents redacted views of sensitive data based on user privileges. This is typically an access control layer managed through the data lake’s policy engine and does not involve separate cryptographic key management Tokenization: Replaces sensitive data elements (e.g., payment card numbers) with non-sensitive, non-mathematically-derived tokens. A secure token vault maintains the mapping between tokens and original values. In multi-cloud environments, ensuring consistent access, security, and lifecycle management for the tokenization keys and vault becomes a critical key management challenge. This infrastructure should be integrated with or governed by the same KMS strategies discussed in Section 4 to maintain a unified security posture Additionally, using key strengths appropriate to the protected data classification is recommended for enhanced data security within the data lake.
When implementing customer-managed encryption for data lakes at petabyte scale, several operational trade-offs emerge: KMS API Call Patterns: While envelope encryption minimizes KMS interactions by caching decrypted DEKs in memory, large-scale data lakes still generate significant KMS traffic. A typical scenario involves decrypting DEKs once per cache expiration period (e.g., every 5–60 minutes) per processing node, but with thousands of distributed workers processing diverse datasets with multiple DEKs, aggregate KMS API volume can reach tens or hundreds of thousands of calls per hour Performance Considerations: KMS API latency (10–50ms same-region, 50–200ms+ cross-region/cross-cloud) affects job startup time and cold-start scenarios Cost Implications: Cloud KMS services charge per API call ($0.03–$0.15 per 10,000 requests depending on provider/operation). For data lakes with hundreds or thousands of processing nodes continuously refreshing DEK caches, monthly KMS costs can range from hundreds to thousands of dollars, becoming a significant operational expense at scale Key Rotation at Scale: Rotating KEKs for petabyte-scale data lakes requires re-encrypting potentially millions of DEKs (not the data itself), which demands careful orchestration to avoid cache invalidation storms and service disruptions These trade-offs inform the architectural decisions discussed in Section 4, where solutions like customer-held keys (Section 4.2) may provide different performance/cost/control balances optimized for specific scale and compliance requirements.
Data pipelines process and transmit large volumes of data across multiple stages (ingestion, transformation, aggregation, and storage). All sensitive data flowing through pipelines requires encryption key management strategy aligned with data sensitivity and compliance requirements. The focus of this section is on the encryption of data in motion and ensuring confidentiality and integrity with the help of KMS.
While data masking or tokenization 2 is a suitable approach for privacy-preserving, these concepts were intentionally left out to maintain focus. Session-Level Encryption: Data in transit between pipeline components (e.g., Kafka to Spark to data lake) should be protected using Transport Layer Security (TLS) 1.2+ or mutual TLS (mTLS) for mutual authentication. This protects against network interception but assumes trust in pipeline processing environments Application-Level Encryption: For zero-trust or high-security scenarios, encrypt data before it enters the pipeline using approved algorithms (AES-256-GCM) Encrypted data remains protected even if pipeline infrastructure is compromised, the CSP administrators access systems, and even if data temporarily lands in lower-security intermediate storage.
One trade-off would be that, although application-level encryption provides stronger confidentiality, it increases complexity (key distribution to all pipeline stages) and may impact performance (encrypt/decrypt overhead at each stage). In multi-cloud key management, when pipelines span multiple CSPs (e.g., ingest in AWS, process in Azure, store in GCP), key management becomes complex and the following considerations should be taken into account as per examples: Disparate Authorization Models: AWS IAM policies ≠ Azure RBAC ≠ GCP IAM, requiring consistent access control translation across providers Key Synchronization: Ensure pipeline stages in different clouds can access the same encryption keys through unified KMS or federated key access Independent Keys per Cloud: Alternatively, use separate keys per CSP to contain blast radius, re-encrypting data when crossing cloud boundaries Centralized Key Management: Unified KMS across the pipeline enables consistent key rotation, centralized audit logging, and simplified compliance (e.g., single audit trail vs. correlating logs from multiple CSPs) 5. Performance Evaluation & Extended Technical Observations Best Practice: Match encryption strength to data classification. Financial transactions and PII require AES-256 with application-level encryption; operational metrics may need only TLS in transit with CSP-native encryption at rest.
Data streaming involves the continuous flow of data from producers through brokers (e.g., Apache Kafka, AWS Kinesis, Azure Event Hubs, Google Pub/Sub) to consumers. In multi-cloud environments, producers and consumers may operate across different cloud platforms, introducing complexities in managing cryptographic keys and certificates for secure communication. Streaming systems employ multiple layers of encryption, each addressing different threat models: Transport Encryption (TLS/mTLS): All communication channels between producers, brokers, and consumers should use TLS 1.2 or higher to protect data in transit. For Zero Trust architectures, the mutual transport layer security (mTLS) provides bidirectional authentication where both clients and brokers present certificates, enabling cryptographic verification of service identity. Many managed streaming services support Bring-Your-Own-Certificate (BYOC), allowing organizations to use certificates issued by enterprise or third-party Public Key Infrastructure (PKI) services rather than CSP-generated certificates [1], [2]. This enables control over certificate lifecycle management (issuance, rotation, revocation), consistent certificate policies across multi-cloud brokers, and integration with existing enterprise PKI infrastructure Broker Encryption at Rest: Messages persisted by brokers for durability and replay (e.g., Kafka logs, Kinesis shards, Event Hubs partitions) should be encrypted at rest. Organizations can choose between CSP-managed keys or customer-managed keys (CMEK/BYOK). Customer-managed keys provide independent key control separate from the CSP, the ability to revoke broker access to historical messages, and compliance with regulations requiring customer-held encryption keys. Broker encryption protects against unauthorized access to storage media but does not protect data from the broker service itself or CSP administrators Application-Level Encryption (End-to-End): For highly sensitive data (e.g., PII, financial transactions, healthcare records), organizations should encrypt message payloads before publishing to the broker, ensuring data remains protected even while stored or processed by the broker as shown in Figure 4.
Figure 4, shows an End-to-end encryption workflow showing how producers encrypt message payloads with DEKs obtained from a multi-cloud KMS before publishing to streaming brokers. The encrypted message travels with a wrapped (encrypted) DEK that enables authorized consumers to decrypt the payload via KMS, while the broker handles only ciphertext throughout. This pattern ensures data confidentiality even if broker infrastructure or CSP administrators are compromised.
This pattern protects data even if the broker is compromised, prevents CSP administrators from accessing message content, and meets compliance requirements for end-to-end encryption. Trade-Offs: Brokers cannot perform content-based routing, filtering, or analytics on encrypted payloads. Both producers and consumers require KMS access, adding latency to message processing. Key rotation requires coordination across all producers and consumers to prevent message loss or processing failures.
Cross-Cloud Key Access: When producers in one cloud publish to brokers in another cloud, with consumers in a third cloud, all components need access to encryption keys. Options include: Key Rotation with Active Streams: Unlike batch processing, streams operate continuously. Key rotation should account for: Performance Considerations: High-throughput streams (millions of messages per second) make encryption overhead significant: Key caching should balance performance (longer cache periods reduce KMS calls) against security (shorter cache periods enable faster key rotation response).
Best Practice: Use TLS 1.2+ or mTLS for all producer-broker-consumer connections. Apply broker encryption at rest for regulatory compliance and data durability. Implement application-level encryption for highly sensitive data where brokers should not access plaintext. For multi-cloud streaming architectures, evaluate centralized KMS solutions or customer-held KMS to simplify key distribution, rotation, and access control across cloud providers.
When users conduct online transactions such as shopping, streaming videos, or sending emails, key exchange protocols secure data and communication between the consumer and provider. Key exchange is also commonly performed between separate cloud services and providers, where negotiated keys using PKI enable the establishment of trust and protection of data transmission via application- or packet-level encryption [1] . Common examples include TLS handshakes (described in Section 2.2.5) and IPsec VPNs using IKE protocol for key exchange. While VPC peering enables network connectivity between clouds, it does not perform key exchange and relies on the cloud provider’s existing security controls.
Key exchange algorithms such as RSA [3] and Diffie-Hellman (DH) face potential vulnerabilities from quantum computing. RSA’s security depends on the computational difficulty of factoring large prime products, while DH’s security relies on the discrete logarithm problem. Shor’s algorithm, executable on sufficiently powerful quantum computers, can efficiently solve both problems, rendering current public-key exchange methods vulnerable.
To address quantum threats, organizations are transitioning to post-quantum cryptographic (PQC) algorithms. Key Encapsulation Mechanisms (KEMs) provide quantum-resistant key exchange based on mathematical problems believed to be hard for both classical and quantum computers, including lattice-based problems (e.g., Kyber, selected as NIST’s ML-KEM standard), code-based cryptography, and hash-based signatures. KEMs enable two entities to establish a shared secret key that can subsequently be used with symmetric algorithms (e.g., AES-256) for bulk encryption. Symmetric algorithms like AES require only increased key sizes to maintain security against quantum attacks (Grover’s algorithm provides quadratic speedup, making AES-256 equivalent to AES-128 against quantum computers). Organizations implementing multi-cloud architectures should evaluate PQC readiness across cloud providers, as adoption timelines and supported algorithms vary between AWS, Azure, and Google Cloud.
For management of the public and private keys used to establish trust for these operations, the use of a cloud certificate manager is required, which is a specialized KMS used for managing certificates, usage, and trust. Cloud-native certificate managers (e.g., AWS Certificate Manager, Google Certificate Authority Service, Azure Key Vault Certificates) typically operate within a single CSP’s environment, performing critical functions such as generating, signing, storing, managing, and retiring cryptographic keys and certificates.
In a multi-cloud environment, extending key and certificate management capabilities across cloud platforms presents distinct challenges for each function. For key management interoperability, organizations should consider solutions that support Public Key Cryptographic Standard #11 (PKCS#11) and/or Key Management Interoperability Protocol (KMIP), OASIS standards that enable heterogeneous KMS to communicate using a common message format and protocol. These interoperability standards allow centralized or federated key lifecycle operations, including generation, rotation, and destruction that may otherwise use incompatible native APIs or protocols.
For certificate management across multiple clouds, organizations face the challenge of coordinating trust between independent PKI systems, each with its own certificate authorities, validation policies, cryptographic algorithm support, and lifecycle rules. While cloud-native certificate managers operate within a single provider’s trust boundary, multi-cloud deployments require mechanisms to ensure consistent certificate issuance, renewal, and revocation. Automated Certificate Management Environment (ACME, RFC 8555) provides standardized automation for certificate lifecycle operations and is supported by multiple certificate authorities, though organizations should verify provider-specific implementations. Certificate Management Protocol (CMP, RFC 4210) and Enrollment over Secure Transport (EST, RFC 7030) offer additional options for certificate enrollment and management across heterogeneous environments.
Regardless of the approach, multi-cloud key and certificate management requires a centralized policy orchestration layer to enforce uniform security controls across providers. This includes consistent key rotation schedules, synchronized revocation checking, consolidated audit logging, and coordinated incident response procedures. Organizations should evaluate whether their multi-cloud KMS or certificate management solution can integrate with each cloud’s native services while maintaining compliance with applicable regulatory frameworks across all deployment locations.
TLS is a common protocol used for many forms of secure authentication and communication, facilitating secure online transactions, web browsing, credit card payments, sending/receiving emails, file uploads, and more. TLS is also commonly used to authenticate and securely transmit sensitive data between multiple cloud providers. TLS versions 1.2 and 1.3 are currently considered secure for sensitive data transmission.
When TLS communication is initialized between two systems, the TLS handshake process performs acknowledgment, verifies and establishes cryptographic algorithms, and exchanges the symmetric session keys used to encrypt communications, as described in Section 2.2.4. The TLS protocol ensures non-repudiation authenticity and protects data integrity and confidentiality.
Where multi-cloud implementations require authentication, one server may need to generate a public and private key, send the public key to a CA service to be signed (usually as a PKCS#12 certificate signing request or CSR), and then transmit the public key to server or service to which it will ultimately authenticate (usually as an X.509 certificate). Similarly, where a service provides a TLS-secured endpoint, a key pair should be randomly generated, the public key should be signed as described above, and the signed certificate should be loaded into the certificate manager and provided to the remote client at the time of connection.
In multi-cloud environments, TLS is typically used to protect data in transit. However, when establishing trust between services, brokers, or workloads across cloud providers, mTLS provides an additional level of assurance by requiring both parties to authenticate using X.509 certificates. mTLS ensures cryptographically-verified workload identity, enabling secure service-to-service communication and greatly reducing the risk of impersonation or unauthorized access. In environments where data flows across cloud boundaries or involves multiple messaging layers, mTLS helps verify the identity of brokers and endpoints before granting access to protected resources or signing keys. Many Zero Trust architectures consider mTLS a foundational control for cross-cloud communication. Key management considerations for mTLS in multi-cloud: Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Cloud%20management • https://en.wikipedia.org/wiki/Microsoft%20Azure • https://en.wikipedia.org/wiki/Business%20process%20management • https://docs.cloud.google.com/kms/docs • https://docs.cloud.google.com/kms/docs/key-management-service • https://cloudsecurityalliance.org/artifacts/key-management-in-cloud-services • https://cloudsecurityalliance.org/artifacts/multi-cloud-kms
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Multi Cloud Key Management Service Simulation Project.
[*] Metasploit Scan Running on Target Subnet for Multi Cloud Key Management Service Simulation Project... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |