Complete Technical Paper Content — Network Access Control System Using 802.1x Authentication
Overview & System Context
Network Access Control System Using 802.1X Authentication: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9535 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background IEEE 802.1X is an IEEE Standard for port-based network access control. It is part of the IEEE 802.1 group of networking protocols. It provides an authentication mechanism to devices wishing to attach to a LAN or Wireless LAN. The standard directly addresses an attack technique called Hardware Addition where an attacker posing as a guest, customer or staff smuggles a hacking device into the building that they then plug into the network giving them full access. A notable example of the issue occurred in 2005 when a machine attached to Walmart's network hacked thousands of their servers. IEEE 802.1X defines the encapsulation of the Extensible Authentication Protocol (EAP) over wired IEEE 802 networks and over 802.11 wireless networks, which is known as "EAP over LAN" or EAPOL. EAPOL was originally specified for IEEE 802.3 Ethernet, IEEE 802.5 Token Ring, and FDDI (ANSI X3T9.5/X3T12 and ISO 9314) in 802.1X-2001, but was extended to suit other IEEE 802 LAN technologies such as IEEE 802.11 wireless in 802.1X-2004. The EAPOL was also modified for use with IEEE 802.1AE ("MACsec") and IEEE 802.1AR (Secure Device Identity, DevID) in 802.1X-2010 to support service identification and optional point to point encryption over the internal LAN segment. 802.1X is part of the logical link control (LLC) sublayer of the 802 reference model.
802.1X authentication involves three parties: a supplicant, an authenticator, and an authentication server. The supplicant is a client device (such as a laptop) that wishes to attach to the LAN/WLAN. The term 'supplicant' is also used interchangeably to refer to the software running on the client that provides credentials to the authenticator. The authenticator is a network device that provides a data link between the client and the network and can allow or block network traffic between the two, such as an Ethernet switch or wireless access point; and the authentication server is typically a trusted server that can receive and respond to requests for network access, and can tell the authenticator if the connection is to be allowed, and various settings that should apply to that client's connection or setting. Authentication servers typically run software supporting the RADIUS and EAP protocols. In some cases, the authentication server software may be running on the authenticator hardware. The authenticator acts like a security guard to a protected network. The supplicant (i.e., client device) is not allowed access through the authenticator to the protected side of the network until the supplicant's identity has been validated and authorized.
With 802.1X port-based authentication, the supplicant must initially provide the required credentials to the authenticator - these will have been specified in advance by the network administrator and could include a user name/password or a permitted digital certificate. The authenticator forwards these credentials to the authentication server to decide whether access is to be granted. If the authentication server determines the credentials are valid, it informs the authenticator, which in turn allows the supplicant (client device) to access resources located on the protected side of the network.
Initialization On detection of a new supplicant, the port on the switch (authenticator) is enabled and set to the "unauthorized" state. In this state, only 802.1X traffic is allowed; other traffic, such as the Internet Protocol (and with that TCP and UDP), is dropped. Initiation To initiate authentication the authenticator will periodically transmit EAP-Request Identity frames to a special Layer 2 MAC address (01:80:C2:00:00:03) on the local network segment. The supplicant listens at this address, and on receipt of the EAP-Request Identity frame, it responds with an EAP-Response Identity frame containing an identifier for the supplicant such as a User ID. The authenticator then encapsulates this Identity response in a RADIUS Access-Request packet and forwards it on to the authentication server. The supplicant may also initiate or restart authentication by sending an EAPOL-Start frame to the authenticator, which will then reply with an EAP-Request Identity frame. Negotiation (Technically EAP negotiation) The authentication server sends a reply (encapsulated in a RADIUS Access-Challenge packet) to the authenticator, containing an EAP Request specifying the EAP Method (The type of EAP based authentication it wishes the supplicant to perform). The authenticator encapsulates the EAP Request in an EAPOL frame and transmits it to the supplicant. At this point, the supplicant can start using the requested EAP Method, or do a NAK ("Negative Acknowledgement") and respond with the EAP Methods it is willing to perform. Authentication If the authentication server and supplicant agree on an EAP Method, EAP Requests and Responses are sent between the supplicant and the authentication server (translated by the authenticator) until the authentication server responds with either an EAP-Success message (encapsulated in a RADIUS Access-Accept packet), or an EAP-Failure message (encapsulated in a RADIUS Access-Reject packet). If authentication is successful, the authenticator sets the port to the "authorized" state and normal traffic is allowed. If it is unsuccessful, the port remains in the "unauthorized" state. When the supplicant logs off, it sends an EAPOL-logoff message to the authenticator, the authenticator then sets the port to the "unauthorized" state, once again blocking all non-EAP traffic.
An open-source project named Open1X produces a client, Xsupplicant. This client is currently available for both Linux and Windows. The main drawbacks of the Open1X client are that it does not provide comprehensible and extensive user documentation and that most Linux vendors do not provide a package for it. The more general wpa_supplicant can be used for 802.11 wireless networks and wired networks. Both support a very wide range of EAP types. ChromeOS has supported 802.1X since mid-2011. Avenda Systems provides a supplicant for Windows, Linux and macOS. They also have a plugin for the Microsoft NAP framework. Avenda also offers health checking agents.
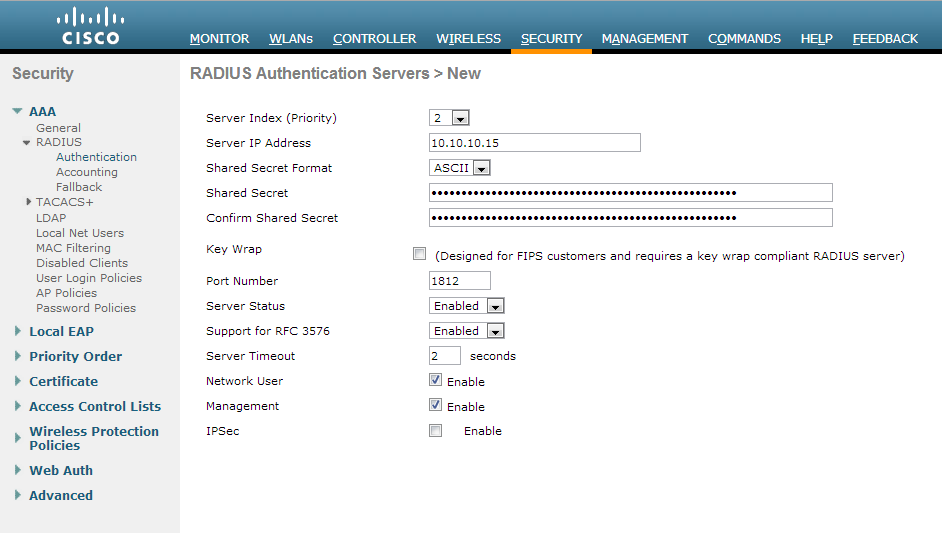
Figure 1: Tutorial: 802.1X Authentication via WiFi – Active Directory + Network ... IEEE Standard for Local and Metropolitan Area Networks--Port-Based Network Access Control Port-based network access control allows a network administrator to restrict the use of IEEE 802(R) LAN service access points (ports) to secure communication between authenticated and authorized devices. This standard specifies a common architecture, functional elements, and protocols that support mutual authentication between the clients of ports attached to the same LAN and that secure communication between the ports, including the media access method independent protocols that are used to discover and establish the security associations used by IEEE 802.1AE(TM) MAC Security.
Current projects that have been authorized by the IEEE SA Standards Board to develop a standard. This document defines time-sensitive networking profiles for industrial automation. The profiles select features, options, configurations, defaults, protocols, and procedures of bridges, end stations, and Local Area Networks (LANs) to build industrial automation networks. This document also specifies YANG modules defining read-only information available online and offline as a digital data sheet. This document also specifies YANG modules for remote procedure calls and actions to address requirements arising from industrial automation networks.
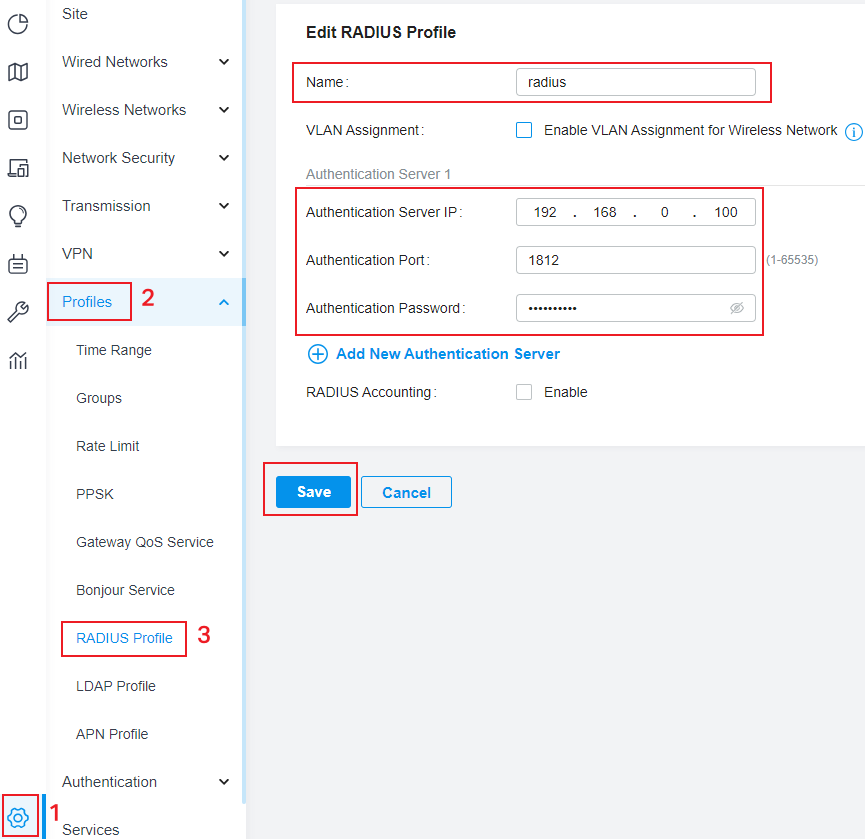
Figure 2: How to build an 802.1X access authentication system using Switches on ... This project adds support of the Internal Sublayer Service by the IEEE Std 802.15.6 MAC entity. This amendment also includes technical and editorial corrections in the description of existing IEEE Std 802.1AC functionality. Learn More About P802.1ACea The scope of this standard is to specify provision of connectionless user data confidentiality, frame data integrity, and data origin authenticity by media access independent protocols and entities that operate transparently to MAC Clients.
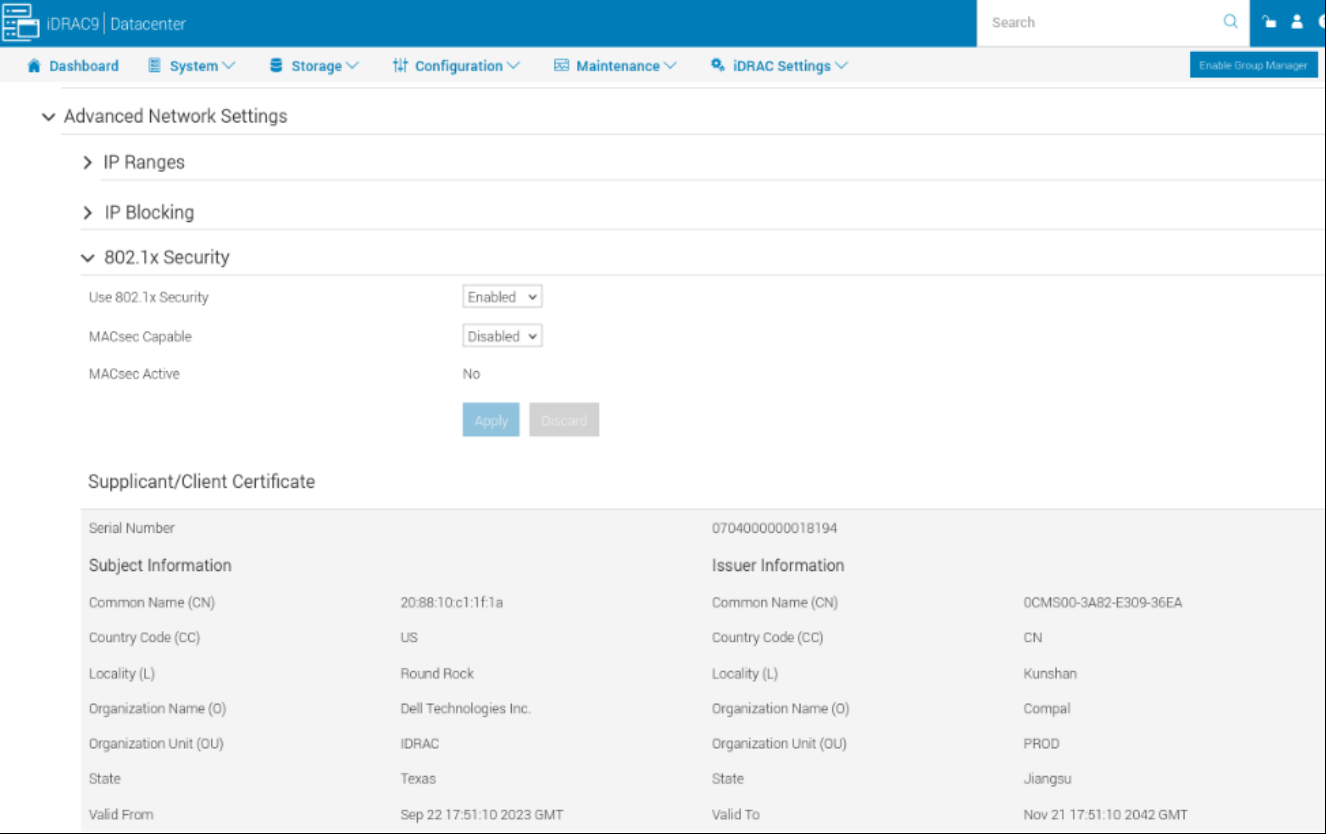
This amendment specifies optional use of the Ascon-AEAD128 authenticated encryption with associated data scheme, as specified in NIST SP 800-232, as a MACsec (Media Access Control security) Cipher Suite. Figure 3: How to configure iDRAC | iDRAC 802.1X Port-Based Network Access Control ... Learn More About P802.1AEef This standard specifies unique per-device identifiers (DevID) and the management and cryptographic binding of a device to its identifiers, the relationship between an initially installed identity and subsequent locally significant identities, and interfaces and methods for use of DevIDs with existing and new provisioning and authentication protocols.
This standard specifies protocols, procedures, and managed objects to support the synchronization requirements of time-sensitive network applications. These applications include audio, video, and time-sensitive control using IEEE 802 Local Area Networks and similar media. Synchronized time is maintained during normal operation and during network reconfiguration following the addition, removal, or failure of network components. This standard includes a profile of IEEE Std 1588™.
This amendment provides additions and modifications to enable the Announce message functionality to be optional on new implementations, while maintaining the ability for implementations to support backward compatibility, interoperability, and full conformance with IEEE Std 1588™-2019. Protocols, procedures, and managed objects are updated if and as required to reflect the availability and use of Announce. This amendment also includes technical and editorial corrections in the description of existing IEEE Std 802.1AS functionality.
Learn More About P802.1ASeb This standard specifies procedures, managed objects, and protocols for bridges and end systems that provide identification and replication of packets for redundant transmission, identification of duplicate packets, and elimination of duplicate packets. It is not concerned with the creation of the multiple paths over which the duplicates are transmitted.
This amendment refines the sequence recovery function and adds an informative annex describing recommended values for the sequence recovery function parameters, and provides guidance regarding frame buffering in relay and end systems to assist in the usage of Frame Replication and Elimination for Reliability. This amendment also includes technical and editorial corrections in the description of existing IEEE Std 802.1CB functionality.
Learn More About P802.1CBec This standard defines profiles that select features, options, configurations, defaults, protocols and procedures of bridges, stations, and local area networks that are necessary to build networks that are capable of transporting fronthaul streams, which are time-sensitive.
This standard specifies protocols, procedures, and managed objects for resource allocation in bridged local area networks for dynamic creation and maintenance of data streams. This standard supports control signaling through data paths and through separate control paths in support of centralized control. This standard makes provisions for backward compatibility with the Stream Reservation Protocol specified in IEEE Std 802.1Q.
This amendment selects IEEE 802.1AS time synchronization options, defaults, and parameter values and provides configuration guidelines and constraints for automotive in-vehicle bridged IEEE 802.3 Ethernet networks. Learn More About P802.1DGei This standard specifies Cut-Through Forwarding (CTF) bridges based on the IEEE 802.1Q bridge architecture, including protocols, procedures, and managed objects. CTF bridges interconnect individual local area networks (LANs) using different or identical media access control (MAC) methods with and without support for CTF. This standard also details the usage of CTF bridges in bridged networks.
This standard specifies protocols, procedures, and managed objects to support forward signaling of telemetry in dedicated tags added to data frames. This standard supports Medium Access Control (MAC) bridges, Customer Virtual Local Area Network (C-VLAN) bridges, Service Virtual Local Area Network (S-VLAN) bridges, and end stations. Telemetry in conjunction with IEEE Std 802.1AE MAC Security is also supported. This standard specifies a service interface to enable higher layer protocols to initiate and retrieve telemetry from the data link layer. This standard supports managed objects and a YANG data model for initiating and recording telemetry.
This standard specifies procedures, protocols, and managed objects for Backward Notification (BN) to signal data center network conditions toward the source end station. This standard supports Medium Access Control (MAC) bridges, Customer Virtual Local Area Network (C-VLAN) bridges and Service Virtual Local Area Network (S-VLAN) bridges and end stations in data center networks. The BN mechanism conveys information for congestion management, path rebalancing, and failure recovery. This standard specifies how BNs are triggered and constructed, and a service interface for exposing the information to entities above the data link layer. This standard supports managed objects and a YANG data model for backward notification.
This standard specifies Bridges that interconnect individual LANs, each supporting the IEEE 802 MAC Service using a different or identical media access control method, to provide Bridged Networks and VLANs. This amendment to IEEE Std 802.1Q-2022 as amended by IEEE Std 802.1Qcz-2023, IEEE Std 802.1Qcw-2023, IEEE Std 802.1Qcj-2023, IEEE Std 802.1Qdj-2024, IEEE Std 802.1Qdx-2024, and IEEE Std 802.1Qdy-2025.
Learn More About P802.1Qdq This amendment specifies procedures and managed objects for automated Priority-based Flow Control (PFC) headroom calculation and Media Access Control Security (MACsec) protection of PFC frames, using point-to-point roundtrip measurement and enhancements to the Data Center Bridging Capability Exchange protocol (DCBX). This amendment places emphasis on the requirements for low latency and lossless transmission in large-scale and geographically dispersed data centers. This amendment also addresses errors of the existing IEEE Std 802.1Q functionality.
Learn More About P802.1Qdt This amendment specifies procedures and YANG data models to extend bridge attributes for traffic engineering for bridged networks that include wireless technologies whose delay variance is beyond that of point-to-point wireline MAC technologies. Additionally, this amendment addresses technical and editorial corrections to existing IEEE Std 802.1Q functionality.
Learn More About P802.1Qee For the purpose of providing compatible authentication, authorization, and cryptographic key agreement mechanisms to support secure communication between devices connected by IEEE 802(R) Local Area Networks (LANs), this standard a) Specifies a general method for provision of port-based network access control. b) Specifies protocols that establish secure associations for IEEE Std 802.1AE(TM) MAC Security. c) Facilitates the use of industry standard authentication and authorization protocols.
Standards approved by the IEEE SA Standards Board that are within the 10-year lifecycle. This document defines time-sensitive networking profiles for industrial automation. The profiles select features, options, configurations, defaults, protocols, and procedures of bridges, end stations, and LANs to build industrial automation networks. This document also specifies YANG modules defining read-only information available online and offline as a digital data sheet. This document also specifies YANG modules for remote procedure calls and actions to address requirements arising from industrial automation networks.
Learn More About 60802-2026 An overview to the family of IEEE 802® standards is provided in this standard. It describes the reference models for the IEEE 802 standards and explains the relationship of these standards to the higher layer protocols; it specifies the structure of IEEE 802 MAC addresses; it specifies identification of public, private, prototype, and standard protocols; it specifies an object identifier hierarchy used within IEEE 802 for uniform allocation of object identifiers used in IEEE 802 standards; and it specifies a method for higher layer protocol identification.
A protocol and a set of managed objects that can be used for discovering the physical topology from adjacent stations in IEEE 802® LANs are defined in this document. Learn More About 802.1AB-2026 The MAC Service and the Internal Sublayer Service (ISS) are defined in this standard. This standard specifies media-dependent convergence functions that map IEEE 802® MAC interfaces to the ISS. The MAC Service is derived from the ISS.
Learn More About 802.1AC-2026 How all or part of a network can be secured transparently to peer protocol entities that use the MAC Service provided by IEEE 802® LANs to communicate is specified in this standard. MAC security (MACsec) provides connectionless user data confidentiality, frame data integrity, and data origin authenticity.(The PDF of this standard is available at no cost to you compliments of the IEEE GET program https://ieeexplore.ieee.org/browse/standards/get-program/page) Learn More About 802.1AE-2018 How all or part of a network can be secured transparently to peer protocol entities that use the MAC Service provided by IEEE 802(R) LANs to communicate is specified in this standard. AC security (MACsec) provides connectionless user data confidentiality, data frame integrity, and data origin authenticity. (The PDF of this standard is available at no cost compliments of the IEEE GET program at https://ieeexplore.ieee.org/browse/standards/get-program/page/series?id=68) Learn More About 802.1AE-2018/Cor 1-2020 This amendment specifies a MAC Privacy protection encapsulating protocol and its use in conjunction with the MAC Security protocol (MACsec) to hide the source and destination MAC addresses of user data frames, and to reduce any correlation between observable frame sizes and transmission timing. This helps to protect user and application identities and to hide the purpose and content of communications. Management of MACsec and privacy protection is supported by YANG models and SNMP MIBs. Privacy considerations for bridged networks are reviewed. (The PDF of this standard is available at no cost compliments of the IEEE GET Program https://ieeexplore.ieee.org/browse/standards/get-program/page/series?id=68) Learn More About 802.1AEdk-2023 A Secure Device Identifier (DevID) is cryptographically bound to a device and supports authentication of the device's identity.
An Initial Device Identifier (IDevID) provide by the supplier of a device can be supplemented by Local Device Identifiers (LDevIDs) facilitating enrollment (provisioning of authentication and authorization credentials) by local network administrators. (The PDF of this standard is available at no cost compliments of the IEEE GET Program at https://ieeexplore.ieee.org/browse/standards/get-program/page) Learn More About 802.1AR-2018 A Secure Device Identifier (DevID) is cryptographically bound to a device and supports authentication of the device's identity.
An Initial Device Identifier (IDevID) provide by the supplier of a device can be supplemented by Local Device Identifiers (LDevIDs) facilitating enrollment (provisioning of authentication and authorization credentials) by local network administrators. Learn More About 802.1AReg-2026 Protocols, procedures, and managed objects for the transport of timing over local area networks are defined in this standard. It includes the transport of synchronized time, the selection of the timing source (i.e., best timeTransmitter), and the indication of the occurrence and magnitude of timing impairments (i.e., phase and frequency discontinuities).
Learn More About 802.1AS-2025 This amendment to IEEE Std 802.1AS™-2025 specifies protocols, procedures, and managed objects that support IEEE Std 802.3 Clause 4 Media Access Control (MAC) operating in half-duplex while retaining existing functionality and backward compatibility, and remaining a profile of IEEE Std 1588™-2019.
Learn More About 802.1ASds-2026 This amendment to IEEE Std 802.1AS™-2025 specifies protocols, processes, procedures, functions, mechanisms, and managed objects to enable fault-tolerant timing by increasing the availability of the time and adding time integrity. This is achieved using two or more generalized precision time protocol (gPTP) domains, multiple time distribution paths, the local oscillator clock, and a time selection function with individual processes for times that have interdependencies and times that do not have interdependencies. Fault-tolerant timing includes fault-tolerant time generation and distribution.
Learn More About 802.1ASed-2026 Link Aggregation allows parallel point-to-point links to be used as if they were a single link and also supports the use of multiple links as a resilient load-sharing interconnect between multiple nodes in two separately administered networks. This standard defines a MAC-independent Link Aggregation capability and provides general information relevant to specific MAC types.
Learn More About 802.1AX-2020 (The PDF of this standard is available at no cost compliments of the IEEE GET program located at https://ieeexplore.ieee.org/browse/standards/get-program/page/series?id=68). This amendment to IEEE Std 802.1AX-2020 specifies a Unified Modeling Language (UML)-based model and YANG modules for Link Aggregation configuration and status reporting.
Learn More About 802.1AXdz-2025 Profiles that select features, options, configurations, defaults, protocols, and procedures of bridges, stations, and LANs that are necessary to build networks that are capable of transporting time-sensitive audio and/or video data streams are defined in this standard.
The PDF of this standard is available at no cost via the IEEE GET program at https://ieeexplore.ieee.org/browse/standards/get-program/page/series?id=68 Learn More About 802.1BA-2021 2. System Architecture & Core Working Principles (The PDF of this standard is available at no cost via the IEEE GET Program at https://ieeexplore.ieee.org/browse/standards/get-program/page/series?id=68) This standard specifies procedures, managed objects, and protocols for bridges and end systems that provide identification and replication of packets for redundant transmission, identification of duplicate packets, and elimination of duplicate packets. It is not concerned with the creation of the multiple paths over which the duplicates are transmitted.
Learn More About 802.1CB-2017 This corrigendum to IEEE Std 802.1CB™-2017 provides technical and editorial corrections. Learn More About 802.1CB-2017/Cor 1-2026 This amendment specifies YANG data models and MIB modules that allow configuration and status reporting for bridges and end systems with the capabilities for Frame Replication and Elimination for Reliability (FRER) and Stream identification. (The PDF of this standard is available at no cost to you through the IEEE GET program https://ieeexplore.ieee.org/browse/standards/get-program/page/series?id=68) Learn More About 802.1CBcv-2021 This amendment specifies procedures, managed objects, and protocols for bridges and end systems that provide identification and replication of packets for redundant transmission, identification of duplicate packets, and elimination of duplicate packets. It is not concerned with the creation of the multiple paths over which the duplicates are transmitted.
Learn More About 802.1CBdb-2021 An access network (which connects terminals to their access routers) utilizing technologies based on the family of IEEE 802(R) standards is specified in this recommended practice. An access network reference model (NRM) that includes entities and reference points along with behavioral and functional descriptions of communications among those entities is provided in this recommended practice. (The PDF of this standard is available at no cost to you compliments of the IEEE GET program https://ieeexplore.ieee.org/browse/standards/get-program/page/series?id=68) Learn More About 802.1CF-2019 This standard defines profiles that select features, options, configurations, defaults, protocols, and procedures of bridges, stations, and LANs that are necessary to build networks that are capable of transporting fronthaul streams, which are time sensitive. (The PDF of this standard is available at not cost compliments of the IEEE GET Program at https://ieeexplore.ieee.org/browse/standards/get-program/page) Learn More About 802.1CM-2018 Enhancements to fronthaul profiles are defined in this amendment to IEEE Std 802.1CM-2018 in order to address new developments in fronthaul interface standards and in related synchronization and syntonization standards. (The PDF of this standard is available at no cost to you compliments of the IEEE GET program https://ieeexplore.ieee.org/browse/standards/get-program/page/series?id=68) Learn More About 802.1CMde-2020 Protocols, procedures, and managed objects for a Link-local Registration Protocol (LRP) to replicate a registration database from one end to the other of a point-to-point link and to replicate changes to parts of that database are specified in this standard. A facility is provided to purge the replicated database if the source becomes unresponsive. LRP is optimized for databases on the order of 1 Mbyte. (The PDF of this standard is available at no cost to you compliments of the IEEE GET program at https://ieeexplore.ieee.org/browse/standards/get-program/page/series?id=68.
Learn More About 802.1CS-2020 This corrigendum corrects errors in the YANG module, SNMP MIBs, and TLV encoding in IEEE Std 802.1CS-2020. (The PDF of this standard is available at no cost compliments of the IEEE GET program https://ieeexplore.ieee.org/browse/standards/get-program/page/series?id=68) Learn More About 802.1CS-2020/Cor 1-2024 This standard specifies procedures and managed objects for quality of service (QoS) features specified in IEEE Std 802.1Q, such as Per-Stream Filtering and Policing, queuing, transmission selection, stream control, and frame preemption, in a network system that is not a Bridge. (The PDF of this standard is available at no cost compliments of the IEEE GET program https://ieeexplore.ieee.org/browse/standards/get-program/page/series?id=68) Learn More About 802.1DC-2024 Profiles for bounded latency automotive in-vehicle bridged IEEE 802.3 Ethernet networks based on IEEE 802.1 Time-Sensitive Networking (TSN) standards are specified in this standard.
Learn More About 802.1DG-2025 Profiles of IEEE 802.1 Time-Sensitive Networking (TSN) for aerospace onboard bridged IEEE 802.3 Ethernet networks are specified in this standard. The profiles select features, options, configurations, defaults, protocols, and procedures of bridges, end stations, and Local Area Networks to build deterministic networks for aerospace onboard communications.
Learn More About 802.1DP-2025 This standard specifies how the Media Access Control (MAC) Service is supported by Bridged Networks, the principles of operation of those networks, and the operation of MAC Bridges and VLAN Bridges, including management, protocols, and algorithms. (The PDF of this standard is available at no cost compliments of the IEEE GET program https://ieeexplore.ieee.org/browse/standards/get-program/page/series?id=68) Learn More About 802.1Q-2022 This amendment to IEEE Std 802.1Q-2022 as amended by IEEE Std 802.1Qcz-2023 and IEEE Std 802.1Qcw-2023 specifies protocols, procedures, and management objects for auto attachment of network devices to Provider Backbone service instances using Type, Length, Value (TLVs) within the Link Layer Discovery Protocol (LLDP). (PDF of this Standard is available at no charge, compliments of the IEEE GET program at https://ieeexplore.ieee.org/browse/standards/get-program/page/series?id=68).
Learn More About 802.1Qcj-2023 This amendment specifies YANG data models that allow configuration and status reporting for Bridges and Bridge components with the capabilities of scheduled traffic, frame preemption, and Per-Stream Filtering and Policing. (The PDF of the standard is available at no cost, compliments of the IEEE GET program at https://ieeexplore.ieee.org/browse/standards/get-program/page/series?id=68).
Learn More About 802.1Qcw-2023 This amendment to IEEE Std 802.1Q™-2022 specifies protocols, procedures, and managed objects that support the isolation of congesting data flows within data center environments. The PDF of this standard is available at no cost compliments of the IEEE GET program https://ieeexplore.ieee.org/browse/standards/get-program/page/series?id=68.
Learn More About 802.1Qcz-2023 This amendment to IEEE Std 802.1Q-2022 as amended by IEEE Std 802.1Qcz-2023, IEEE Std 802.1Qcw-2023, and IEEE Std 802.1Qcj-2023 describes the relationships and division of responsibilities between Centralized User Configuration (CUC) components, that can be used to configure end stations' use of Time-Sensitive Networking (TSN) capabilities, and a Centralized Network Configuration (CNC) component that can be used to configure network resources within an administrative Configuration Domain. A YANG model and modules that can be used by a network configuration protocol, such as NETCONF, to provide communication between the CNC and a CUC is specified.
Learn More About 802.1Qdj-2024 A YANG data model that supports configuration and status reporting for credit-based shaper algorithm capabilities in Bridges and end stations is specified in this amendment to IEEE Std 802.1Q-2022 as amended by IEEE Std 802.1Qcz-2023, IEEE Std 802.1Qcw-2023, IEEE Std 802.1Qcj-2023, and IEEE Std 802.1Qdj-2024. (The PDF of this standard is available at no cost compliments of the IEEE GET program at https://ieeexplore.ieee.org/browse/standards/get-program/page/series?id=68) Learn More About 802.1Qdx-2024 This amendment to IEEE Std 802.1Q-2022 as amended by IEEE Std 802.1Qcz-2023, IEEE Std 802.1Qcw-2023, IEEE Std 802.1Qcj-2023, IEEE Std 802.1Qdj-2024, and IEEE Std 802.1Qdx-2024 addresses Multiple Spanning Tree Protocol (MSTP) requirements arising from industrial automation networks. It specifies YANG for Bridge and Bridge component RSTP as well as MSTP configuration and status reporting.(Note: The PDF of this standard is available at no charge compliments of the IEEE GET program https://ieeexplore.ieee.org/browse/standards/get-program/page/series?id=68) Learn More About 802.1Qdy-2025 This corrigendum to IEEE Std 802.1X-2020 corrects the when statement for the augment of the interfaces container in the IEEE 802.1x YANG module to avoid unduly restricting the applicability of the IEEE 802.1x YANG module to specific interface types.
Learn More About 802.1X-2020/Cor 1-2026 A privacy threat model for IEEE 802® technologies is specified by this recommended practice. The document also provides recommendations on how to protect against privacy threats and promotes a consistent approach to the mitigation of privacy threats by IEEE 802 protocol developers.
Learn More About 802E-2020 A protocol and a set of managed objects that can be used for discovering the physical topology from adjacent stations in IEEE 802® LANs are defined in this document A protocol and a set of managed objects that can be used for discovering the physical topology from adjacent stations in IEEE 802® LANs are defined in this document.
Learn More About 8802-1AB-2017 This amendment to IEEE Std 802.1AB-2016 specifies a Unified Modeling Language (UML)-based information model and a YANG data model that allows configuration and status reporting for bridges and bridge components with regards to topology discovery.
Learn More About 8802-1AB:2017/Amd 1-2023
Abstract
This amendment to IEEE Std 802.1AB™-2016 specifies protocols, procedures, and managed objects that support the transmission and reception of a set of Link Layer Discovery Protocol (LLDP) Type/Length/Values (TLVs) that exceed the space available in a single frame. Learn More About 8802-1AB:2017/Amd 2-2023 The Internal Sublayer Service for the IEEE 802.15.3 MAC entity is defined in this amendment.
Abstract Art
Learn More About 8802-1AC:2018/Amd 1-2023 How all or part of a network can be secured transparently to peer protocol entities that use the MAC Service provided by IEEE 802® LANs to communicate is specified in this standard. MAC security (MACsec) provides connectionless user data confidentiality, frame data integrity, and data origin authenticity.
Abstract Definition
Learn More About 8802-1AE/Cor1-2021-2020 The scope of this standard is to specify provision of connectionless user data confidentiality, frame data integrity, and data origin authenticity by media access independent protocols and entities that operate transparently to MAC Clients. NOTE--The MAC Clients are as specified in IEEE Std 802, IEEE Std 802.1Q™, and IEEE Std 802.1X™.
Abstraction
Learn More About 8802-1AE:2020/Amd.4:2024-2024 Protocols, procedures, and managed objects for the transport of timing over local area networks are defined in this standard. It includes the transport of synchronized time, the selection of the timing source (i.e., best master), and the indication of the occurrence and magnitude of timing impairments (i.e., phase and frequency discontinuities).
Abstraction Tadc
Learn More About 8802-1AS-2021 This amendment to IEEE Std 802.1AS™-2020 replaces terminology with alternative terminology identified by IEEE Std 1588g™-2022. All changes made in figures are only to replace terminology. Learn More About 8802-1AS-2021_Amd1:2025-2025 Technical and editorial corrections to IEEE Std 802.1AS-2020 are provided in this corrigendum.
Abstract Meaning
Learn More About 8802-1AS:2021/Cor 1-2023 Link Aggregation allows parallel point-to-point links to be used as if they were a single link and also supports the use of multiple links as a resilient load-sharing interconnect between multiple nodes in two separately administered networks. This standard defines a MAC-independent Link Aggregation capability and provides general information relevant to specific MAC types.
Abstract Noun
Learn More About 8802-1AX-2021 Profiles that select features, options, configurations, defaults, protocols, and procedures of bridges, stations, and LANs that are necessary to build networks that are capable of transporting time-sensitive audio and/or video data streams are defined in this standard.
Abstract Painting
Learn More About 8802-1BA-2023 3. Software Implementation, Frameworks & Protocols This standard specifies the operation of Bridge Port Extenders, including management, protocols, and algorithms. Bridge Port Extenders operate in support of the MAC Service by Extended Bridges.
Abstract Expressionism
Learn More About 8802-1BR-2016 This amendment specifies procedures, managed objects, and protocols for bridges and end systems that provide identification and replication of packets for redundant transmission, identification of duplicate packets, and elimination of duplicate packets. It is not concerned with the creation of the multiple paths over which the duplicates are transmitted.
Abstracted Jax
Learn More About 8802-1CB:2019/Amd 2-2023 Enhancements to fronthaul profiles are defined in this amendment to IEEE Std 802.1CM(TM)-2018 in order to address new developments in fronthaul interface standards and in related synchronization and syntonization standards. Learn More About 8802-1CM:2019/Amd1-2021 Protocols, procedures, and managed objects for a Link-local Registration Protocol (LRP) to replicate a registration database from one end to the other of a point-to-point link and to replicate changes to parts of that database are specified in this standard. A facility is provided to purge the replicated database if the source becomes unresponsive. LRP is optimized for databases on the order of 1 Mbyte.
Learn More About 8802-1CS-2021 This corrigendum corrects errors in the YANG module, SNMP MIBs, and TLV encoding in IEEE Std 802.1CS™-2020. Learn More About 8802-1CS:2022/Cor 1-2025 This standard specifies procedures and managed objects for quality of service (QoS) features specified in IEEE Std 802.1Q, such as Per-Stream Filtering and Policing, queuing, transmission selection, stream control, and frame preemption, in a network system that is not a Bridge.
Learn More About 8802-1DC-2025 This standard specifies how the Media Access Control (MAC) Service is supported by Bridged Networks, the principles of operation of those networks, and the operation of MAC Bridges and VLAN Bridges, including management, protocols, and algorithms.
Learn More About 8802-1Q-2020 This standard specifies how the Media Access Control (MAC) Service is supported by Bridged Networks, the principles of operation of those networks, and the operation of MAC Bridges and VLAN Bridges, including management, protocols, and algorithms.
Learn More About 8802-1Q-2024 Extensions to the Virtual Station Interface (VSI) Discovery and Configuration Protocol (VDP) to support using the protocol between an end station and a device doing encapsulation/decapsulation for Network Virtualization Overlays Over Layer 3 (NVO3) are specified in this amendment to IEEE Std 802.1Q-2018. The extensions include adding format types [e.g., Internet Protocol (IP) addresses] and enhancing indication of migration events.
Learn More About 8802-1Q-2020/Amd3-2021 Enhancements to the configuration of time-sensitive streams are provided by this amendment to IEEE Std 8802.1Q-2018. Learn More About 8802-1Q-2020/Amd31-2021 A YANG data model in support of configuration and operational status information for a subset of Bridging capabilities is provided in this amendment to IEEE Std 802.1Q(TM)-2018.
Learn More About 8802-1Q-2020_Amd2-2021 Learn More About 8802-1Q-2024_Amd36-2025 Correction of technical and editorial errors identified by the IEEE 802.1 maintenance activity are presented in this document. Learn More About 8802-1Q:2016/Cor 1-2017 This amendment to IEEE Std 802.1Q-2022 as amended by IEEE Std 802.1Qcz-2023 and IEEE Std 802.1Qcw-2023 specifies protocols, procedures, and management objects for auto attachment of network devices to Provider Backbone service instances using Type, Length, Value (TLVs) within the Link Layer Discovery Protocol (LLDP).
Learn More About 8802-1Q:2024/Amd 37-2025 Learn More About 8802-1Q:2024/Amd 38-2025 Learn More About 8802-1Q:2024/Amd.35:2024-2024 Explicit path control, bandwidth reservation, and redundancy (protection, restoration) for data flows are specified in this amendment to IEEE Std 802.1Q-2014.
Learn More About 8802-1Q_Amd 1-2017 Enhancements to the forwarding process that supports scheduled traffic is provided in this amendment to IEEE Std 802.1Q-2014. Learn More About 8802-1Q_Amd 3 Port-based network access control allows a network administrator to restrict the use of IEEE 802(R) LAN service access points (ports) to secure communication between authenticated and authorized devices. This standard specifies a common architecture, functional elements, and protocols that support mutual authentication between the clients of ports attached to the same LAN and that secure communication between the ports, including the media access method independent protocols that are used to discover and establish the security associations used by IEEE 802.1AE(TM) MAC Security.
Learn More About 8802-1X-2021 The YANG module containing the EtherType information, including a compact human-readable name and description, for a subset of EtherTypes taken from the IEEE Registration Authority EtherType public listing is specified in this amendment. This amendment also addresses errors and omissions in IEEE Std 802 description of existing functionality.
Learn More About 8802-A:2015/Amd.3-2025 These standards have been replaced with a revised version of the standard, or by a compilation of the original active standard and all its existing amendments, corrigenda, and errata. Superseded by IEEE Std 802-2001 This IEEE Standards product is part of the 802 family on LAN/MAN. This document provides an overview to the family of IEEE 802 Standards, defines compliance with the family of IEEE 802 Standards, describes the relationship of the IEEE 802 Standards to the Open Systems Interconnections Basic Reference Model [ISO 7498:1984] and explains the relationship of these standards to the higher layer protocols, and provides a standard for identification of public, private, and standard protocols.
IEEE Std 802-2001, IEEE Standards for Local and Metropolitan Area Networks: Overview and Architecture, provides an overview to the family of IEEE 802 Standards. It defines compliance with the family of IEEE 802 Standards; it describes the relationship of the IEEE 802 Standards to the Open Systems Interconnection Basic Reference Model [ISO/IEC 7498-1:1994] and explains the relationship of these standards to the higher layer protocols; it provides a standard for the structure of LAN MAC addresses; and it provides a standard for identification of public, private, and standard protocols.
This standard provides an overview to the family of IEEE 802® standards. It describes the reference models for the IEEE 802 standards and explains the relationship of these standards to the higher layer protocols; it provides a standard for the structure of IEEE 802 MAC addresses; it provides a standard for identification of public, private, prototype, and standard protocols; it specifies an object identifier hierarchy used within IEEE 802 for uniform allocation of object identifiers used in IEEE 802 standards; and it specifies a method for higher layer protocol identification. (The PDF of this standard is available at no charge compliments of the IEEE GET Program.
Visit https://ieeexplore.ieee.org/browse/standards/get-program/page/series?id=68 for more details.) This document defines a protocol and a set of managed objects that can be used for discovering the physical topology from adjacent stations in 802 LANs.
Learn More About 802.1AB-2005 This document defines a protocol and a set of managed objects that can be used for discovering the physical topology from adjacent stations in IEEE 802 LANs. Learn More About 802.1AB-2009 This document defines a protocol and a set of managed objects that can be used for discovering the physical topology from adjacent stations in IEEE 802(R) LANs. (The PDF of this standard is available at no cost compliments of the IEEE GET program.
Additional downloads are attached or can be downloaded at https://ieeexplore.ieee.org/browse/standards/get-program/page) Learn More About 802.1AB-2016 Technical and editorial errors identified by the IEEE 802.1 Working Group's maintenance activity are corrected by this corrigendum.
Learn More About 802.1AB-2009/Cor 1-2013 Technical and editorial errors identified by the IEEE 802.1 Working Group's maintenance activity are corrected by this corrigendum to IEEE 802.1AB(TM)-2009. Learn More About 802.1AB-2009/Cor 2-2015 This amendment to IEEE Std 802.1AB-2016 specifies a Unified Modeling Language (UML)-based information model and a YANG data model that allows configuration and status reporting for bridges and bridge components with regards to topology discovery. (The PDF of this standard is available at no charge compliments of the IEEE GET program https://ieeexplore.ieee.org/browse/standards/get-program/page/series?id=68) Learn More About 802.1ABcu-2021 This amendment to IEEE Std 802.1AB(TM)-2016 specifies protocols, procedures and managed objects that support the transmission and reception of a set of Link Layer Discovery Protocol (LLDP) Type/Length/Values (TLVs) that exceed the space available in a single frame. (The PDF of this standard is available at no charge compliments of the IEEE GET program at https://ieeexplore.ieee.org/browse/standards/get-program/page/series?id=68) Learn More About 802.1ABdh-2021 The MAC service provided by all IEEE 802(R) MACs along with the Internal Sublayer Service (ISS) that is provided by IEEE 802 MACs to the relay function of a Media Access Control(MAC) Bridge are defined in this standard.
Learn More About 802.1AC-2012 The MAC Service and the Internal Sublayer Service (ISS) are defined in this standard. This standard specifies media-dependent convergence functions that map IEEE 802(R) MAC interfaces to the ISS. The MAC Service is derived from the ISS. (The PDF of this standard is available at no charge compliments of the IEEE GET Program https://ieeexplore.ieee.org/browse/standards/get-program/page) Learn More About 802.1AC-2016 This corrigendum to IEEE Std 802.1AC™-2016 corrects the value of the LLC Encapsulation EtherType.(The PDF of this standard is available at no cost to you compliments of the IEEE GET program https://ieeexplore.ieee.org/browse/standards/get-program/page) Learn More About 802.1AC-2016/Cor 1-2018 The Internal Sublayer Service for the IEEE 802.15.3 MAC entity is defined in this amendment. (The PDF of this standard is available at no cost via the IEEE GET program at https://ieeexplore.ieee.org/browse/standards/get-program/page/series?id=68) Learn More About 802.1ACct-2021 This amendment enables a service provider to use the architecture and protocols of IEEE Std 802.1Q to offer the equivalent of separate LANs, Bridged Local Area Networks, or Virtual Bridged Local Area Networks to a number of customers, while requiring no cooperation between the customers, and minimal cooperation between each customer and the service provider.
Learn More About 802.1ad-2005 4. Practical Deployment, Analysis & Case Studies This standard specifies how all or part of a network can be secured transparently to peer protocol entities that use the MAC Service provided by IEEE 802® LANs to communicate. MAC security (MACsec) provides connectionless user data confidentiality, frame data integrity, and data origin authenticity.
Learn More About 802.1AE-2006 This amendment specifies the GCM-AES-256 Cipher Suite as an option in addition to the existing mandatory to implement Default Cipher Suite, GCM-AES-128. Learn More About 802.1AEbn-2011 The optional use of Cipher Suites that make use of a 64-bit (PN) to allow more than 232 MACsec protected frames to be sent with a single Secure Association Key are specified by this amendment.
Learn More About 802.1AEbw-2013 Ethernet Data Encryption devices (EDEs) are specified in this amendment. An EDE is a two-port bridge that uses MACsec to provide secure connectivity for attached customer bridges, or for attached provider bridges. EDEs may allow the customer (or provider) bridges to continue to use a VLAN Identifier (VID) in transmitted frames to select Learn More About 802.1AEcg-2017 This amendment specifies protocols, procedures, and managed objects to support connectivity fault management. These allow discovery and verification of the path, through bridges and LANs, taken for frames addressed to and from specified network users. Connectivity faults can be detected and isolated to an individual bridge or LAN.
Learn More About 802.1ag-2007 This amendment defines an architecture and bridge protocols for interconnection of multiple Provider Bridged Networks, allowing a Provider to support up tot 2^20 service instances. Learn More About 802.1ah-2008 This amendment to IEEE Std 802.1Q specifies the function of a MAC Relay with two MACs, and the protocols and procedures to support its operation. A MAC Relay is transparent to all frame-based media independent protocols except those explicitly addressed to this device. It is remotely manageable through at least one of its external MACs, and signals a failure of either MAC's LAN through the other MAC.
Learn More About 802.1aj-2009 This amendment specifies a set of protocols that replaces the GARP, GMRP, and GVRP protocols specified in earlier versions of IEEE Std 802.1Q. Learn More About 802.1ak-2007 This amendment includes management information base (MIB) definitions in IEEE Std 802.1Q.
Learn More About 802.1ap-2008 This amendment to IEEE Std 802.1Q-2011 specifies shortest path bridging of unicast and multicast frames, including protocols to calculate multiple active topologies that can share learned station information, and support of a virtual local area network (VLAN) by multiple, per topology VLAN identifiers (VIDs). (Additional downloads for this standard are attached or can be downloaded at http://standards.ieee.org/downloads/802.1/index.html) Learn More About 802.1aq-2012 A secure device identifier (DevID) is cryptographically bound to a device and supports authentication of the device's identity.
Locally significant identities can be securely associated with an initial manufacturer-provisioned DevID and used in provisioning and authentication protocols to allow a network administrator to establish the trustworthiness of a device and select appropriate policies for transmission and reception of data and control protocols to and from the device. Learn More About 802.1AR-2009 This standard defines a protocol and procedures for the transport of timing over bridged and virtual bridged local area networks. It includes the transport of synchronized time, the selection of the timing source (i.e., best master), and the indication of the occurrence and magnitude of timing impairments (i.e., phase and frequency discontinuities).
Learn More About 802.1AS-2011 Protocols, procedures, and managed objects for the transport of timing over local area networks are defined in this standard. It includes the transport of synchronized time, the selection of the timing source (i.e., best master), and the indication of the occurrence and magnitude of timing impairments (i.e., phase and frequency discontinuities).
Learn More About 802.1AS-2020 This corrigendum to IEEE Std 802.1AS - 2011 corrects minor errors, bugs, ambiguities, and inconsistencies that were missed when the document was balloted. It does not contain new material. Learn More About 802.1AS-2011/Cor 1-2013 Technical and editorial corrections are provided by this corrigendum to IEEE Std 802.1AS.
Learn More About 802.1AS-2011/Cor 2-2015 Technical and editorial corrections to IEEE Std 802.1AS™-2020 are provided in this corrigendum. Learn More About 802.1AS-2020/Cor 1-2021 This amendment to IEEE Std 802.1AS™-2020 specifies hot standby and addresses errors and omissions in the description of existing functionality. (The PDF of this standard is available at no cost compliments of the IEEE GET program) Learn More About 802.1ASdm-2024 A YANG data model that allows configuration and state reporting for all managed objects of the base standard is specified in this amendment.
Learn More About 802.1ASdn-2024 This amendment to IEEE Std 802.1AS™-2020 replaces terminology with alternative terminology identified by IEEE Std 1588g™-2022. All changes made in figures are only to replace terminology. Learn More About 802.1ASdr-2024 Link Aggregation allows one or more links to be aggregated together to form a Link Aggregation Group, such that a Media Access Control (MAC) Client can treat the Link Aggregation Group as if it were a single link. To this end, it specifies the establishment of data terminal equipment (DTE) to DTE logical links, consisting of N parallel instances of full duplex point-to-point links operating at the same data rate. This standard defines the MAC independent Link Aggregation capability, and general information relevant to specific MAC types that support link aggregation.
Learn More About 802.1AX-2008 MAC-independent Link Aggregation capability and general information relevant to specific MAC types are defined in this standard. Link Aggregation allows parallel full-duplex point-to-point links to be used as if they were a single link and also supports the use of multiple links as a resilient load sharing interconnect between multiple nodes in two separately administered networks. (The PDF of this standard is available at no cost compliments of the IEEE GET program. Additional downloads are attached or can be downloaded at https://ieeexplore.ieee.org/browse/standards/get-program/page) Learn More About 802.1AX-2014 Technical and editorial corrections are provided in this corrigendum to IEEE Std 802.1AX-2014.
Learn More About 802.1AX-2014/Cor 1-2017 Link Aggregation allows one or more links to be aggregated together to form a Link Aggregation Group, such that a Media Access Control (MAC) Client can treat the Link Aggregation Group as if it were a single link. To this end, it specifies the establishment of data terminal equipment (DTE) to DTE logical links, consisting of N parallel instances of full-duplex, point-to-point links operating at the same data rate. The MAC independent Link Aggregation capability, and general information relevant to specific MAC types that support Link Aggregation, are defined in this standard.
Learn More About 802.1AXbk-2012 Profiles that select features, options, configurations, defaults, protocols and procedures of bridges, stations and LANs that are necessary to build networks that are capable of transporting time-sensitive audio and/or video data streams are defined in this standard. (This PDF of this standard is available as part of the IEEE Get program. Through the IEEE SA and industry support, select IEEE standards are available for download at no charge. For more details go to our web page at https://ieeexplore.ieee.org/browse/standards/get-program/page.) Learn More About 802.1BA-2011 Technical and editorial errors identified by the IEEE 802.1 Working Group's maintenance activity are corrected in this corrigendum to IEEE Std 802.1BA-2011.
Learn More About 802.1BA-2011/Cor 1-2016 An architecture for the interconnection of IEEE 802(R) Local Area Networks (LANs) below the MAC Service boundary is defined. MAC Bridges, as specified by this standard, allow communications between end stations attached to separate LANs, each with its own separate MAC, to be transparent to logical link control (LLC) and network layer protocols, just as if the stations were attached to the same LAN.
Learn More About 802.1D-2004 This IEEE Standards product is part of the 802 family on LAN/MAN. This standard defines an architecture for Virtual Bridged LANs, the services provided in Virtual Bridged LANs, and the protocols and algorithms involved in the provision of those services.
Learn More About 802.1Q-1998 This standard specifies how the MAC Service is supported by Virtual Bridged Local Area Networks, the principles of operation of those networks, and the operation of VLAN-aware Bridges, including management, protocols, and algorithms. Learn More About 802.1Q-2005 This standard specifies how the MAC Service is supported by Virtual Bridged Local Area Networks, the principles of operation of those networks, and the operation of VLAN-aware Bridges, including management, protocols, and algorithms. Incorporates IEEE Std 802.1Q-2005, IEEE Std 802.1ad-2005, IEEE Std 802.1ak-2007, IEEE Std 802.1ag-2007, IEEE Std 802.1ah-2008, IEEE Std 802-1Q-2005/Cor-1-2008, IEEE Std 802.1ap-2008, IEEE Std 802.1Qaw-2009, IEEE Std 802.1Qay-2009, IEEE Std 802.1aj-2009, IEEE Std 802.1Qav-2009, IEEE Std Qau-2010, and IEEE Std Qat-2010.
Learn More About 802.1Q-2011 This standard specifies how the Media Access Control (MAC) Service is supported by Bridged Networks, the principles of operation of those networks, and the operation of MAC Bridges and VLAN Bridges, including management, protocols, and algorithms. This revision includes the following amendments and corrigenda: IEEE 802.1Qbe-2011 IEEE 802.1Qbc-2011 IEEE 802.1Qbb-2011 IEEE 802.1Qaz-2011 IEEE 802.1Qbf-2011 IEEE 802.1Qbg-2012 IEEE 802.1aq-2012 IEEE 802.1Q-2011/Cor 2-2012 IEEE 802.1Qbp-2014./index.html. It also supersedes IEEE 802.1D-2004.
Learn More About 802.1Q-2014 This standard specifies how the Media Access Control (MAC) Service is supported by Bridged Networks, the principles of operation of those networks, and the operation of MAC Bridges and VLAN Bridges, including management, protocols, and algorithms. Supersedes 802.1Q™-2014. IEEE 802.1Qcd™-2015, IEEE 802.1Qca™-2015,IEEE 802.1Q™-2014_Cor-1-2015, IEEE 802.1Qbv™-2015, IEEE 802.1Qbu™-2016, IEEE 802.1Qbz™-2016, IEEE 802.1Qci™-2017 and IEEE 802.1Qch™-2017.
Learn More About 802.1Q-2018 This standard defines an architecture for Virtual Bridged LANs, the services provided in Virtual Bridged LANs, and the protocols and algorithms involved in the provision of those services. (Incorporates IEEE Std 802.1Q-1998, IEEE Std 802.1u-2001, IEEE Std 802.1v-2001, and IEEE Std 802.1s-2002) Learn More About 802.1Q, 2003 Edition-2003 This corrigendum to IEEE Std 802.1Q corrects errors in the MRP protocol specification.
5. Performance Evaluation & Extended Technical Observations Learn More About 802.1Q-2005/Cor 1-2008 This corrigendum to IEEE Std 802.1Q-2011 corrects technical and editorial errors identified by the IEEE 802.1 Working Group's maintenance activity.
Learn More About 802.1Q-2011/Cor 2-2012 Correction of technical and editorial errors identified by the IEEE 802.1 maintenance activity are presented in this document. Learn More About 802.1Q-2014/Cor 1-2015 This amendment specifies protocols, procedures, and managed objects, usable by existing higher layer mechanisms, that allow network resources to be reserved for specific traffic streams traversing a bridged local area network. (The PDF of this standard is available at not cost compliments of the GETIEEE802 program located at https://ieeexplore.ieee.org/browse/standards/get-program/page) Learn More About 802.1Qat-2010 This amendment specifies protocols, procedures and managed objects that support congestion management of long-lived data flows within network domains of limited bandwidth-delay product. This is achieved by enabling bridges to signal congestion to end stations capable of transmission rate limiting to avoid frame loss.
Learn More About 802.1Qau-2010 This amendment to IEEE Std 802.1Q defines enhancements to the forwarding and queueing functions of a VLAN Bridge to support the transmission of time sensitive data streams. Learn More About 802.1Qav-2009 This amendment extends the connectivity fault management capabilities introduced in IEEE Std 802.1ag-2007 to include tools to facilitate diagnosis and isolation of faults sensitive to, or caused by, particular data patterns in frames transmitted by a service user.
Learn More About 802.1Qaw-2009 This amendment specifies changes to IEEE Std 802.1Q-2005, as amended by IEEE Std 802.1ad-2005, IEEE Std 802.1ag-2007, IEEE Std 802.1ak-2007, IEEE Std 802.1ah-2008, and IEEE Std 802.1ap-2008, that support provisioning systems that explicitly select traffic engineered paths within Provider Backbone Bridged Networks. Changes are applied to the base text of IEEE Std 802.1Q-2005 as amended by IEEE Std 802.1ad-2005, IEEE Std 802.1ak-2007, IEEE Std 802.1ag-2007, IEEE Std 802.1ah-2008, and IEEE Std 802.1ap-2008.
Learn More About 802.1Qay-2009 This amendment to IEEE Std 802.1Q-2011 defines enhancements to transmission selection to support allocation of bandwidth amongst traffic classes, plus a protocol for controlling the application of Data Center Bridging features. Learn More About 802.1Qaz-2011 This amendment to IEEE Std 802.1Q-2011 specifies protocols, procedures, and managed objects that enable flow control per traffic class on IEEE 802(R) point-to-point full duplex links. This is achieved by a mechanism similar to IEEE 802.3 Annex 31B PAUSE, but operating on individual priorities.
Learn More About 802.1Qbb-2011 This amendment to IEEE Std 802.1Q-2011 specifies the use of service virtual local area networks (S-VLANs) to provide customer service interfaces in one Provider Bridged Network for customer interface local area networks (LANs) attached to another Provider Bridged Network.
Learn More About 802.1Qbc-2011 This amendment to IEEE Std 802.1Q-2011 specifies protocols, procedures, and managed objects to support topology change signaling to alter the binding (held in an I-Component) of Customer addresses to Backbone addresses on a per-I-SID basis. This is accomplished by extending the use of the Multiple Registration Protocol (MRP).
Learn More About 802.1Qbe-2011 This amendment to IEEE Std 802.1Q-2011 specifies localized protection of selected Traffic Engineered Service Instances traversing a common sequence of Provider Network Ports. Learn More About 802.1Qbf-2011 This amendment to IEEE Std 802.1Q-2011 specifies protocols, procedures, and managed objects that -- Provide for the discovery, configuration, and control of a pair of direct-attached limited-function Service VLAN (S-VLAN) components to extend the services of a customer bridge to remote ports and enable coexistence of multiple services onstation-resident ports (e.g., embedded bridging). -- Provide for discovery, configuration, and control of a Reflective Relay Service for a bridge port. -- Provide for discovery of, and coordinated configuration of, edge relays (ERs) and other devices that utilize the reflective relay service. -- Provide for dynamic profile-driven port configuration. (Additional files are attached or can be found at http://standards.ieee.org/downloads/802.1/ Learn More About 802.1Qbg-2012 Routing algorithms and relay behavior supporting equal cost multipath forwarding in shortest path bridged VLANs are specified in this amendment to IEEE Std 802.1Q.
Learn More About 802.1Qbp-2014 Enhancements to the forwarding process that support frame preemption are provided in this amendment to IEEE Std 802.1Q-2014. Learn More About 802.1Qbu-2016 Enhancements to the forwarding process that supports scheduled traffic is provided in this amendment to IEEE Std 802.1Q-2014.
Additional downloads are attached or can be downloaded at http://standards.ieee.org/downloads/802.1/index.html) Learn More About 802.1Qbv-2015 Protocols, procedures, and managed objects to allow IEEE 802.11 media to provide internal connections within bridged networks, as well as access to bridged networks, are provided in this amendment.
Learn More About 802.1Qbz-2016 Explicit path control, bandwidth reservation, and redundancy (protection, restoration) for data flows are specified in this amendment to IEEE Std 802.1Q-2014. Learn More About 802.1Qca-2015 Enhancements to the configuration of time-sensitive streams are provided by this amendment to IEEE Std 802.1Q-2018.
Learn More About 802.1Qcc-2018 Enhancements to the set of TLVs used by the Data Center Bridging eXchange protocol (DCBX) for the purpose of simplifying the management of networks utilizing Data Center Bridging (DCB) features are defined in this amendment to IEEE Std 802.1Q-2014.
Learn More About 802.1Qcd-2015 The use of traffic scheduling and per-stream filtering and policing to support cyclic queuing and forwarding are described in this amendment to IEEE Std 802.1Q-2014. Learn More About 802.1Qch-2017 Enhancements to the forwarding process that support per-stream filtering and policing are provided in this amendment to IEEE Std 802.1Q-2014.
Learn More About 802.1Qci-2017 A YANG data model in support of configuration and operational status information for a subset of Bridging capabilities is provided in this amendment to IEEE Std 802.1Q-2018. Learn More About 802.1Qcp-2018 Procedures and managed objects for Bridges and end stations to perform Asynchronous Traffic Shaping over full-duplex links with constant bit data rates are specified in this amendment to IEEE Std 802.1Q(TM)-2018.
Learn More About 802.1Qcr-2020 YANG data model that supports configuration, status reporting, and monitoring for Connectivity Fault Management (CFM) for Two-Port MAC Relays, Customer VLAN Bridges, and Provider Bridges is further developed by this amendment to IEEE Std 802.1Q™-2018. See also IEEE Std 802.1Qcp™-2018 for the introduction of this YANG data model.
Learn More About 802.1Qcx-2020 Extensions to the Virtual Station Interface (VSI) Discovery and Configuration Protocol (VDP) to support using the protocol between an end station and a device doing encapsulation/decapsulation for Network Virtualization Overlays Over Layer 3 (NVO3) are specified in this amendment to IEEE Std 802.1Q-2018. The extensions include adding format types [e.g., Internet Protocol (IP) addresses] and enhancing indication of migration events.
Learn More About 802.1Qcy-2019 This standard extends the architecture, protocols, and algorithms specified in IEEE Std 802.1Q, 1998 Edition, to allow data traffic belonging to different VLANs to be allocated to different spanning trees, while retaining interoperability with bridges conformant to that prior specification.
Learn More About 802.1s-2002 This amendment to IEEE 802.1Q,1998 Edition is intended to document maintenance items identified in the text of IEEE Std 802.1Q, 1998 Edition.IEEE Std 802.1u-2001 identifies any proposed changes to IEEE Std 802.1Q, 1998 Edition that have arisen as a consequence of maintenance activity. The changes are documented in the usual form for an amendment to IEEE 802 standards; i.e., as an explicit set of editing instructions that, if correctly applied to the text of IEEE Std 802.1Q,1998 Edition, will create a corrected document.
Learn More About 802.1u-2001 This amendment to IEEE Std 802.1Q,1998 Edition describes enhancements to allow for classification of incoming packets by methods other than source port. Specifically, it defines rules for classification based on data-link layer protocol identification. The document identifies proposed changes to the text of IEEE Std 802.1Q,1998 Edition that have arisen as a consequence of this activity. These are documented in the usual form for amendments to IEEE 802 standards; i.e., as an explicit set of editing instructions that, if correctly applied to the text of IEEE Std 802.1Q,1998 Edition, will create a corrected document.
Learn More About 802.1v-2001 Revision of IEEE Std 802.1X-2001 Port-based network access control makes use of the physical access characteristics of IEEE 802 Local Area Networks (LAN) infrastructures in order to provide a means of authenticating and authorizing devices attached to a LAN port that has point-to-point connection characteristics, and of preventing access to that port in cases in which the authentication and authorization process fails.
Learn More About 802.1X-2004 Port-based network access control allows a network administrator to restrict the use of IEEE 802 LAN service access points (ports) to secure communication between authenticated and authorized devices. This standard specifies a common architecture, functional elements, and protocols that support mutual authentication between the clients of ports attached to the same LAN and that secure communication between the ports, including the media access method independent protocols that are used to discover and establish the security associations used by IEEE 802.1AE MAC Security.
Learn More About 802.1X-2010 Media Access Control security (MACsec) Key Agreement protocol (MKA) data elements and procedures that provide additional security and manageability capabilities, including the ability to maintain secure communication while the operation of MKA is suspended, when used in conjunction with MACsec Cipher Suites that support Extended Packet Numbering are added in this amendment.
Learn More About 802.1Xbx-2014 Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/IEEE%20802.1X • https://standards.ieee.org/standard/802_1X-2020.html
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Network Access Control System Using 802.1x Authentication.
! Define Extended Access List to Block Malicious Traffic ip access-list extended SECURE_PERIMETER_ACL remark Block Inbound Telnet and Unencrypted Services deny tcp any any eq 23 log remark Permit Verified Web SSL Traffic permit tcp any any eq 443 permit tcp any any eq 80 remark Mitigate ICMP Flood and Ping Sweeps permit icmp any any echo-reply deny icmp any any echo log deny ip any any log
! Apply ACL to Ingress Interface GigabitEthernet0/0 interface GigabitEthernet0/0 ip access-group SECURE_PERIMETER_ACL in no shutdown end write memory
Extended IP access list SECURE_PERIMETER_ACL (Cisco Packet Tracer) ──────────────────────────────────────────────────────────────────────── 10 deny tcp any any eq telnet log (142 matches) [Probes Dropped] 20 permit tcp any any eq 443 (18402 matches) [TLS 1.3 Traffic Permitted] 30 permit tcp any any eq 80 (4812 matches) 40 deny icmp any any echo log (524 matches) [Flood Mitigated] 50 deny ip any any log (38 matches) [Default Implicit Deny Rule] ──────────────────────────────────────────────────────────────────────── [✓] Packet Tracer Verification: 0 Unsanitized Ingress Leaks on Gi0/0
| Interface Port | Network Zone | Filter Applied | Traffic Processed | Firewall Decision |
|---|---|---|---|---|
| Gig0/0 (WAN) | Untrusted External | Extended ACL 101 | 24,810 Packets | INSPECTED & FILTERED |
| Gig0/1 (DMZ) | Public Web Services | Port 443 Only | 18,402 Packets | PERMITTED |
| Gig0/2 (LAN) | Corporate Users | 802.1X Port Security | 142 Probes | DENIED & QUARANTINED |