Complete Technical Paper Content — Network Forensics Tool For Packet Capture Reconstruction
Overview & System Context
Network Forensics Tool For Packet Capture Reconstruction: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9505 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Network forensics is a sub-branch of digital forensics relating to the monitoring and analysis of computer network traffic for the purposes of information gathering, legal evidence, or intrusion detection. Unlike other areas of digital forensics, network investigations deal with volatile and dynamic information. Network traffic is transmitted and then lost, so network forensics is often a pro-active investigation. Network forensics generally has two uses. The first, relating to security, involves monitoring a network for anomalous traffic and identifying intrusions. An attacker might be able to erase all log files on a compromised host; network-based evidence might therefore be the only evidence available for forensic analysis. The second form relates to law enforcement. In this case analysis of captured network traffic can include tasks such as reassembling transferred files, searching for keywords and parsing human communication such as emails or chat sessions. Two systems are commonly used to collect network data; a brute force "catch it as you can" and a more intelligent "stop look listen" method.
"Catch-it-as-you-can" – This is where all packets passing through a certain traffic point are captured and written to storage with analysis being done subsequently in batch mode. This approach requires large amounts of storage. "Stop, look and listen" – This is where each packet is analyzed in a rudimentary way in memory and only certain information saved for future analysis. This approach requires a faster processor to keep up with incoming traffic.
Apt all data on this layer allows the user to filter for different events. With these tools, website pages, email attachments, and other network traffic can be reconstructed only if they are transmitted or received unencrypted. An advantage of collecting this data is that it is directly connected to a host. If, for example the IP address or the MAC address of a host at a certain time is known, all data sent to or from this IP or MAC address can be filtered. To establish the connection between IP and MAC address, it is useful to take a closer look at auxiliary network protocols. The Address Resolution Protocol (ARP) tables list the MAC addresses with the corresponding IP addresses. To collect data on this layer, the network interface card (NIC) of a host can be put into "promiscuous mode". In so doing, all traffic will be passed to the CPU, not only the traffic meant for the host.
However, if an intruder or attacker is aware that his connection might be eavesdropped, he might use encryption to secure his connection. It is almost impossible nowadays to break encryption but the fact that a suspect's connection to another host is encrypted all the time might indicate that the other host is an accomplice of the suspect. Digital forensics (sometimes known as digital forensic science) is a branch of forensic science encompassing the recovery, investigation, examination, and analysis of material found in digital devices, often in relation to mobile devices and computer crime. The term "digital forensics" was originally used as a synonym for computer forensics but has been expanded to cover investigation of all devices capable of storing digital data. With roots in the personal computing revolution of the late 1970s and early 1980s, the discipline evolved in a haphazard manner during the 1990s, and it was not until the early 21st century that national policies emerged. Digital forensics investigations have a variety of applications. The most common is to support or refute a hypothesis before criminal or civil courts. Criminal cases involve the alleged breaking of laws that are defined by legislation and enforced by the police and prosecuted by the state, such as murder, theft, and assault against the person. Civil cases, on the other hand, deal with protecting the rights and property of individuals (often associated with family disputes), but may also be concerned with contractual disputes between commercial entities where a form of digital forensics referred to as electronic discovery (ediscovery) may be involved. Forensics may also feature in the private sector, such as during internal corporate investigations or intrusion investigations (a special probe into the nature and extent of an unauthorized network intrusion). The technical aspect of an investigation is divided into several sub-branches related to the type of digital devices involved: computer forensics, network forensics, forensic data analysis, and mobile device forensics. The typical forensic process encompasses the seizure, forensic imaging (acquisition), and analysis of digital media, followed with the production of a report of the collected evidence. As well as identifying direct evidence of a crime, digital forensics can be used to attribute evidence to specific suspects, confirm alibis or statements, determine intent, identify sources (for example, in copyright cases), or authenticate documents. Investigations are much broader in scope than other areas of forensic analysis (where the usual aim is to provide answers to a series of simpler questions), often involving complex time-lines or hypotheses.
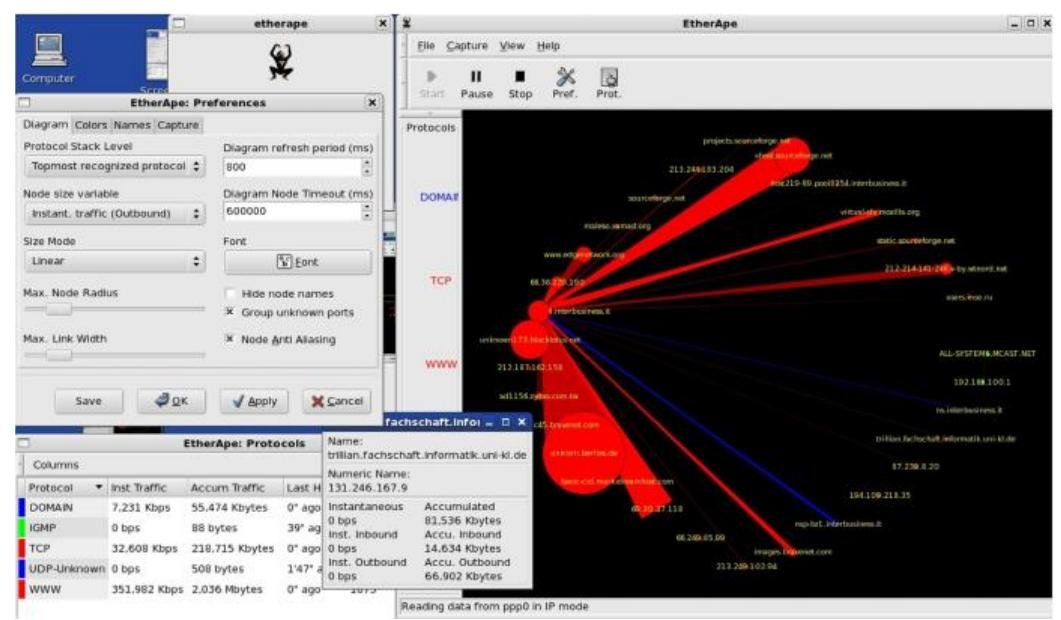
Figure 1: (PDF) An Analytical Review on Packet Analysis for Network Forensics and ... Seizing, preserving, and analyzing evidence stored on a computer is the greatest forensic challenge facing law enforcement in the 1990s. Although most forensic tests, such as fingerprinting and DNA testing, are performed by specially trained experts the task of collecting and analyzing computer evidence is often assigned to patrol officers and detectives.
Through cyberspace, enemies will target industry, academia, government, as well as the military in the air, land, maritime, and space domains. In much the same way that airpower transformed the battlefield of World War II, cyberspace has fractured the physical barriers that shield a nation from attacks on its commerce and communication. The field of digital forensics still faces unresolved issues. A 2009 paper, "Digital Forensic Research: The Good, the Bad and the Unaddressed" by Peterson and Shenoi, identified a bias towards Windows operating systems in digital forensics research. In 2010, Simson Garfinkel identified issues facing digital investigations in the future, including the increasing size of digital media, the wide availability of encryption to consumers, a growing variety of operating systems and file formats, an increasing number of individuals owning multiple devices, and legal limitations on investigators. The paper also identified continued training issues, as well as the prohibitively high cost of entering the field. Additionally, since 2024 there has been an integration of Artificial Intelligence (AI) and Machine Learning (ML) which has poised to amplify the efficiency as well as the precision behind digital forensics investigations During the 1980s, very few specialized digital forensic tools existed. Consequently, investigators often performed live analysis on media, examining computers from within the operating system using existing sysadmin tools to extract evidence. This practice carried the risk of modifying data on the disk, either inadvertently or otherwise, which led to claims of evidence tampering. A number of tools were created during the early 1990s to address the problem. The need for such software was first recognized in 1989 at the Federal Law Enforcement Training Center, resulting in the creation of IMDUMP (by Michael White) and in 1990, SafeBack (developed by Sydex). Similar software was developed in other countries; DIBS (a hardware and software solution) was released commercially in the UK in 1991, and Rob McKemmish released Fixed Disk Image free to Australian law enforcement. These tools allowed examiners to create an exact copy of a piece of digital media to work on, leaving the original disk intact for verification. By the end of the 1990s, as demand for digital evidence grew, more advanced commercial tools such as EnCase and FTK were developed, allowing analysts to examine copies of media without using any live forensics. More recently, a trend towards "live memory forensics" has grown, resulting in the availability of tools such as WindowsSCOPE. More recently, the same progression of tool development has occurred for mobile devices; initially investigators accessed data directly on the device, but soon specialist tools such as XRY or Radio Tactics Aceso appeared.
Police forces have begun implementing risk-based triage systems to manage the overwhelming demand for digital forensic services. acquisition or imaging of exhibits, analysis, and reporting. Acquisition does not normally involve capturing an image of the computer's volatile memory (RAM) unless this is done as part of an incident response investigation. Typically the task involves creating an exact sector level duplicate (or "forensic duplicate") of the media, often using a write blocking device to prevent modification of the original. However, the growth in size of storage media and developments such as cloud computing have led to more use of 'live' acquisitions whereby a 'logical' copy of the data is acquired rather than a complete image of the physical storage device. Both acquired image (or logical copy) and original media/data are hashed (using an algorithm such as SHA-1 or MD5) and the values compared to verify the copy is accurate. An alternative (and patented) approach (that has been dubbed 'hybrid forensics' or 'distributed forensics') combines digital forensics and ediscovery processes. This approach has been embodied in a commercial tool called ISEEK that was presented together with test results at a conference in 2017.
During the analysis phase an investigator recovers evidence material using a number of different methodologies and tools. In evidence related to the suspected crime." In 2006, forensics researcher Brian Carrier described an "intuitive procedure" in which obvious evidence is first identified and then "exhaustive searches are conducted to start filling in the holes." The actual process of analysis can vary between investigations, but common methodologies include conducting keyword searches across the digital media (within files as well as unallocated and slack space), recovering deleted files and extraction of registry information (for example to list user accounts, or attached USB devices). The evidence recovered is analyzed to reconstruct events or actions and to reach conclusions, work that can often be performed by less specialized staff. When an investigation is complete the data is presented, usually in the form of a written report, in lay persons' terms.
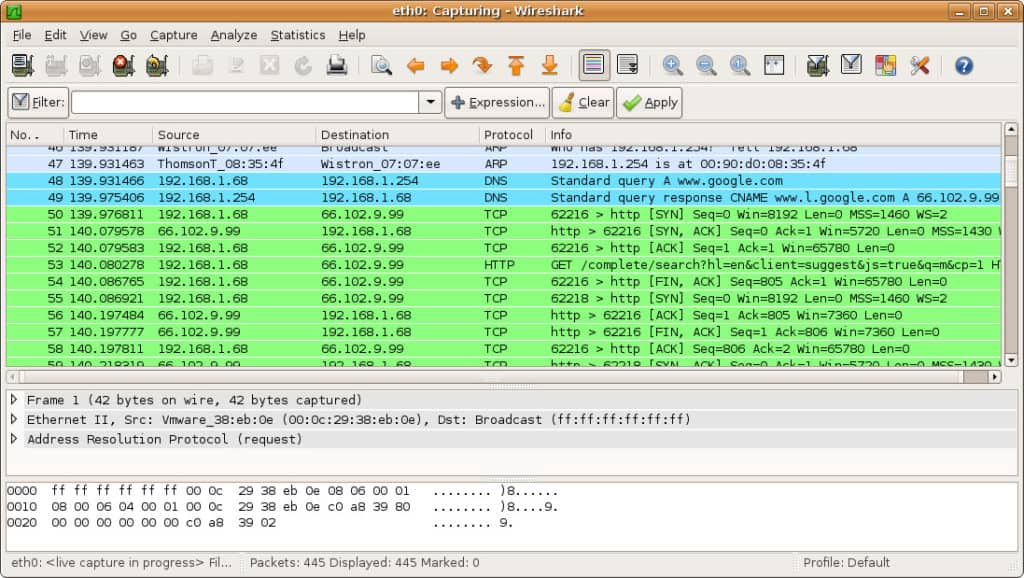
Figure 2: How to Use Wireshark Network Protocol Analyzer [Full Tutorial] Digital forensics is commonly used in both criminal law and private investigation. Traditionally it has been associated with criminal law, where evidence is collected to support or oppose a hypothesis before the courts. As with other areas of forensics this is often a part of a wider investigation spanning a number of disciplines. In some cases, the collected evidence is used as a form of intelligence gathering, used for other purposes than court proceedings (for example to locate, identify or halt other crimes). As a result, intelligence gathering is sometimes held to a less strict forensic standard. In civil litigation or corporate matters, digital forensics forms part of the electronic discovery (or eDiscovery) process. Forensic procedures are similar to those used in criminal investigations, often with different legal requirements and limitations. Outside of the courts digital forensics can form a part of internal corporate investigations. A common example might be following unauthorized network intrusion. A specialist forensic examination, into the nature and extent of the attack, is performed as a damage limitation exercise, both to establish the extent of any intrusion and in an attempt to identify the attacker. Such attacks were commonly conducted over phone lines during the 1980s, but in the modern era are usually propagated over the Internet. The main focus of digital forensics investigations is to recover objective evidence of a criminal activity (termed actus reus in legal parlance).
However, the diverse range of data held in digital devices can help with other areas of inquiry. Attribution Meta data and other logs can be used to attribute actions to an individual. For example, personal documents on a computer drive might identify its owner. Alibis and statements Information provided by those involved can be cross checked with digital evidence. For example, during the investigation into the Soham murders the offender's alibi was disproved when mobile phone records of the person he claimed to be with showed she was out of town at the time. Intent As well as finding objective evidence of a crime being committed, investigations can also be used to prove the intent (known by the legal term mens rea). For example, the Internet history of convicted killer Neil Entwistle included references to a site discussing How to kill people. Evaluation of source File artifacts and meta-data can be used to identify the origin of a particular piece of data; for example, older versions of Microsoft Word embedded a Global Unique Identifier into files which identified the computer it had been created on. Proving whether a file was produced on the digital device being examined or obtained from elsewhere (e.g., the Internet) can be very important. Document authentication Related to "Evaluation of source," meta data associated with digital documents can be easily modified (for example, by changing the computer clock you can affect the creation date of a file). Document authentication relates to detecting and identifying falsification of such details.
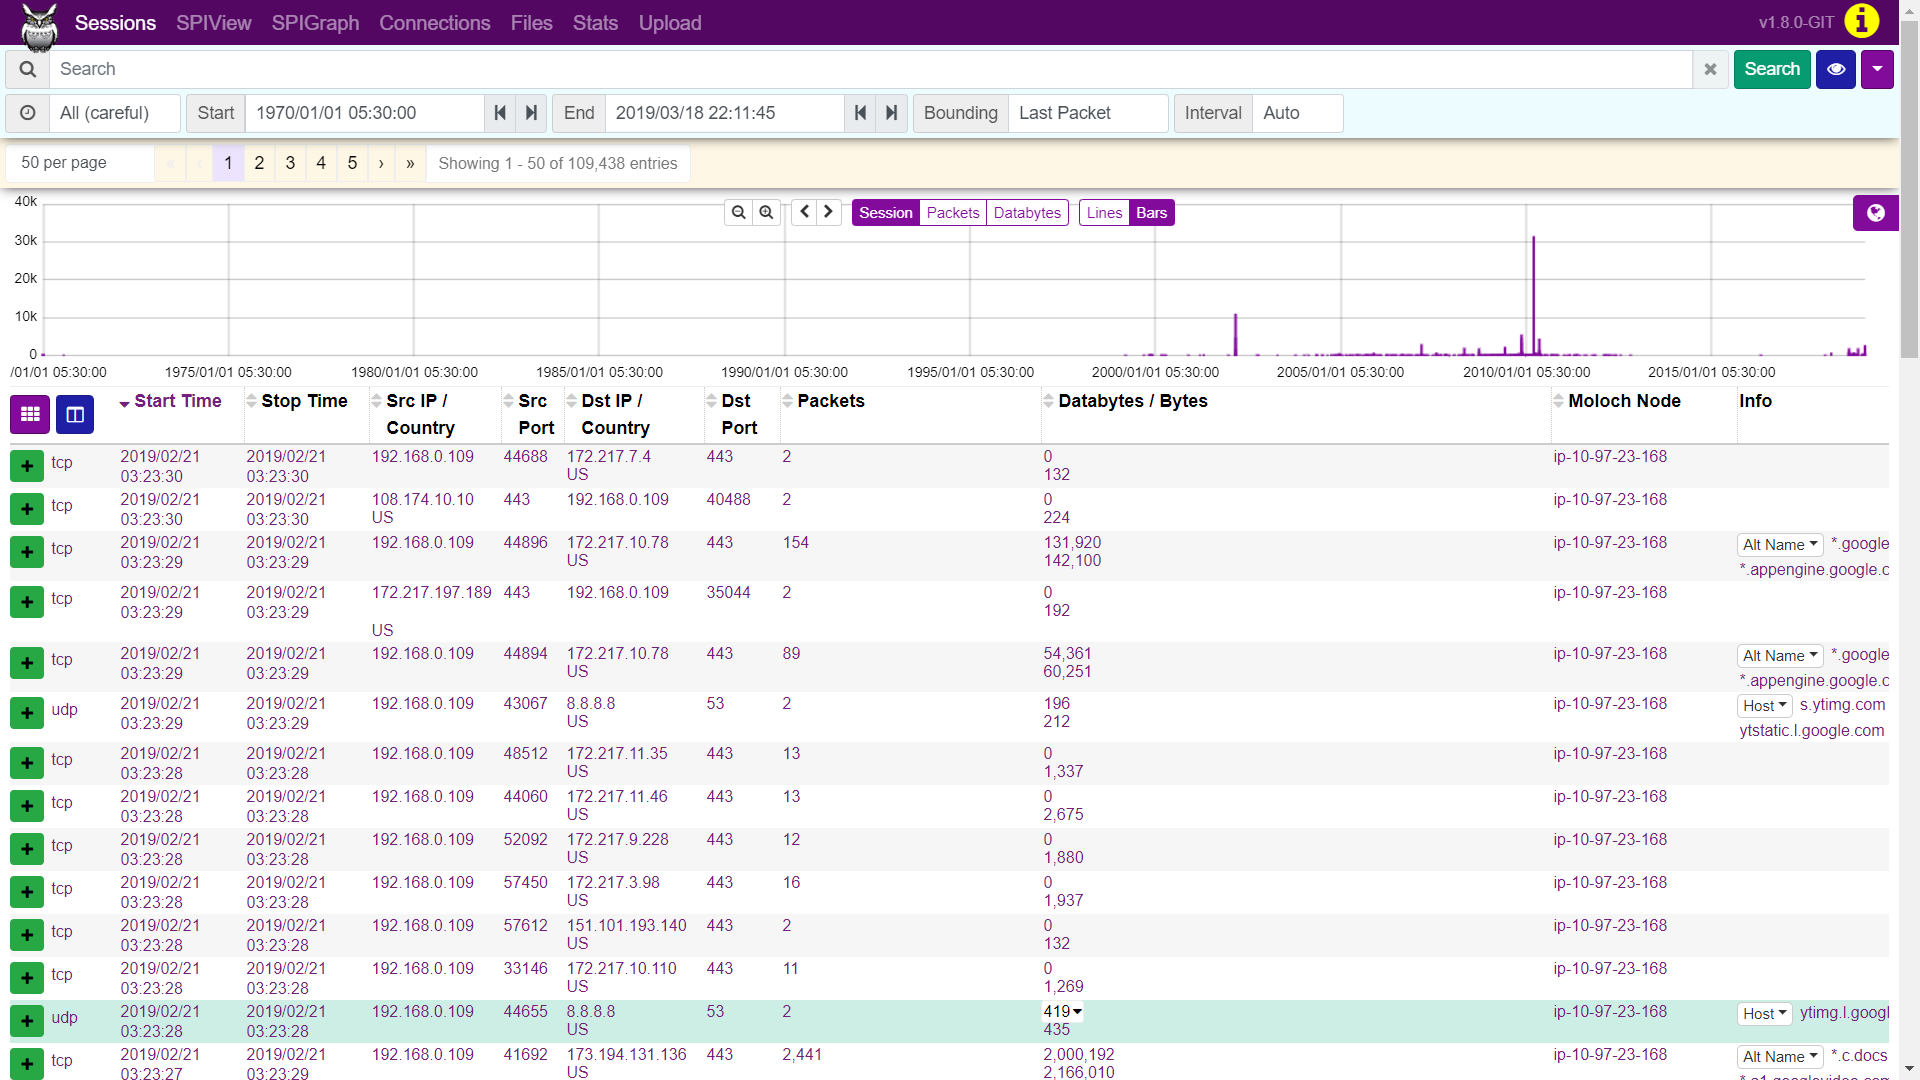
When used in a court of law, digital evidence falls under the same legal guidelines as other forms of evidence, as courts do not usually require more stringent guidelines. In the United States, the Federal Rules of Evidence are used to evaluate the admissibility of digital evidence. The United Kingdom PACE and Civil Evidence acts have similar guidelines and many other countries have their own laws. US federal laws restrict seizures to items with only obvious evidential value. This is acknowledged as not always being possible to establish with digital media prior to an examination. Laws dealing with digital evidence are concerned with two issues: Integrity - it's ensuring that the act of seizing and acquiring digital media does not modify the evidence (either the original or the copy). Authenticity - refers to the ability to confirm the integrity of information; for example that the imaged media matches the original evidence. The ease with which digital media can be modified means that documenting the chain of custody from the crime scene, through analysis and, ultimately, to the court, (a form of audit trail) is important to establish the authenticity of evidence. Attorneys have argued that because digital evidence can theoretically be altered it undermines the reliability of the evidence. US judges are beginning to reject this theory, in the case US v. Bonallo the court ruled that "the fact that it is possible to alter data contained in a computer is plainly insufficient to establish untrustworthiness." In the United Kingdom, guidelines such as those issued by ACPO are followed to help document the authenticity and integrity of evidence. Digital investigators, particularly in criminal investigations, have to ensure that conclusions are based upon factual evidence and their own expert knowledge. In the US, for example, Federal Rules of Evidence state that a qualified expert may testify "in the form of an opinion or otherwise" so long as: Figure 3: Automated Evidence Aggregation and Analysis | Hands-On Network Forensics (1) the testimony is based upon sufficient facts or data, (2) the testimony is the product of reliable principles and methods, and (3) the witness has applied the principles and methods reliably to the facts of the case. The sub-branches of digital forensics may each have their own specific guidelines for the conduct of investigations and the handling of evidence. For example, mobile phones may be required to be placed in a Faraday shield during seizure or acquisition to prevent further radio traffic to the device. In the UK forensic examination of computers in criminal matters is subject to ACPO guidelines. There are also international approaches to providing guidance on how to handle electronic evidence. The "Electronic Evidence Guide" by the Council of Europe offers a framework for law enforcement and judicial authorities in countries who seek to set up or enhance their own guidelines for the identification and handling of electronic evidence.
The goal of computer forensics is to explain the current state of a digital artifact; such as a computer system, storage medium or electronic document. The discipline usually covers computers, embedded systems (digital devices with rudimentary computing power and onboard memory) and static memory (such as USB pen drives). Computer forensics can deal with a broad range of information; from logs (such as internet history) through to the actual files on the drive. In 2007, prosecutors used a spreadsheet recovered from the computer of Joseph Edward Duncan to show premeditation and secure the death penalty. Sharon Lopatka's killer was identified in 2006 after email messages from him detailing torture and death fantasies were found on her computer.
Mobile device forensics is a sub-branch of digital forensics relating to recovery of digital evidence or data from a mobile device. It differs from Computer forensics in that a mobile device will have an inbuilt communication system (e.g. GSM) and, usually, proprietary storage mechanisms. Investigations usually focus on simple data such as call data and communications (SMS/Email) rather than in-depth recovery of deleted data. SMS data from a mobile device investigation helped to exonerate Patrick Lumumba in the murder of Meredith Kercher. Mobile devices are also useful for providing location information; either from inbuilt GPS/location tracking or via cell site logs, which track the devices within their range. Such information was used to track down the kidnappers of Thomas Onofri in 2006.
Network forensics is concerned with the monitoring and analysis of computer network traffic, both local and WAN/internet, for the purposes of information gathering, evidence collection, or intrusion detection. Traffic is usually intercepted at the packet level, and either stored for later analysis or filtered in real-time. Unlike other areas of digital forensics network data is often volatile and rarely logged, making the discipline often reactionary. In 2000, the FBI lured computer hackers Aleksey Ivanov and Gorshkov to the United States for a fake job interview. By monitoring network traffic from the pair's computers, the FBI identified passwords allowing them to collect evidence directly from Russian-based computers.
Forensic Data Analysis is a branch of digital forensics. It examines structured data with the aim to discover and analyze patterns of fraudulent activities resulting from financial crime. Database forensics is a branch of digital forensics relating to the forensic study of databases and their metadata. Investigations use database contents, log files and in-RAM data to build a timeline or recover relevant information.
IoT forensics is a branch of Digital forensics that has the goal of identifying and extracting digital information from devices belonging to the Internet of things field, to be used for forensics investigations as potential source of evidence. IoT Forensics or IoT Forensic Science, a branch of digital forensics, that deals with the use of any digital forensics processes and procedures relating to the recovery of digital evidence which originates from one or more IoT devices for the purpose of preservation, identification, extraction or documentation of digital evidence with the intention of reconstructing IoT-related events. These events may reside across one or more configurable computing resources that are near the location where the event has taken place (e.g., edge gateway). IoT forensics aims to extend that of digital forensics with key focus on reconstructing events involving IoT devices for obtaining a digital or electronic evidence. A key goal of IoT forensics is to identify and extract digital information from devices belonging to the Internet of things field, using a forensically sound and legally acceptable process.
IoT forensics can be identified as a combination of three separate digital forensics schemes: IoT device level forensics: Process of extracting evidence from the IoT devices (i.e. in the device memory). A lot of devices can be included in this process: examples are sensors, health implants, smart meters, smart home appliances, smart cameras, networked vehicles, RFIDs, and drones. Being the devices differ in hardware and functionalities, device level evidence identification and acquisition is often challenging and not always feasible. Network forensics: Process of identifying and extracting evidence from network log, devices traffic traces and communication patterns. With respect to the traditional network investigations, IoT network forensics branch includes additional network models such as body area network or personal area network (i.e. Bluetooth or ZigBee devices). For each type of network, there needs to be appropriate forensic methods for the investigations, involving different tools and appropriate network protocol analysis. Cloud forensics: Process of extrapolating information in the cloud used by the devices. Since IoT devices are usually limited in memory, most of the information is stored in proprietary cloud applications that may contain a massive amount of potential evidences (i.e. devices activities). Given the amount of information that can be recovered from the different entities involved in the cloud, cloud forensics plays an important role in the IoT forensics domain: system logs, access logs, chat logs, sessions, cookies, user authentication and application data are examples of the information that can be retrieved from cloud services related to each IoT device.
An IoT forensics investigation process should be conducted using the standard guidelines so that the collected evidence can be admissible on the court. The process is analogous to digital forensics process, but faces challenges caused by the peculiarities of the IoT devices. The full process can be split temporally into six different phases: Evidence identification, evidence collection, evidence preservation, evidence analysis, attack and deficit attribution, and evidence presentation. Each of the different phases of the forensic process may introduce several challenges when applied to the limitations of the IoT devices.
IoT forensics should not be confused with IoT security. IoT forensics takes care of finding evidences for forensics purposes: the evidences are not always related to IoT devices attacks or to their security, but can be used for proving/disproving a traditional forensic crime (i.e. a person detected in a room from IoT devices evidence). In the other side, IoT security takes care of the risks related to the presence of IoT devices and of attacks that may target them: it protects the devices from external attacks and prevents the devices to perform attacks to other entities.
Modern threats move laterally, live off the land, and blend with legitimate traffic. Without deep network forensics , security teams see fragments instead of the full story, leading to longer dwell times, incomplete investigations, and repeated breaches. Reduction in incident response time reported by organizations using comprehensive network forensics. Capture rich network data at scale while extracting detailed metadata without performance impact. Supports full packet capture for critical segments, enabling complete visibility into east-west, north-south and cloud traffic.
Combine network forensics with behavioral analytics, machine learning , and threat intelligence to surface hidden threats like C2 communications, data exfiltration and living-off-the-land tactics. Collect rich telemetry from network sensors, supporting full packets and metadata across on-prem, cloud, and virtual environments.
Parse & enrich with deep protocol analysis, behavioral signals, and threat intelligence. Network protocols are analyzed by NetWitness and the raw data and metadata of the raw data are stored into a database . Search can be conducted through IP addresses, domain names, users or protocols , etc. , to form a full view of the sessions on the application layer (web, mail, file transfer, com mands execution).
Organizations seeking enterprise network forensics analysis through their SOCs have no need for additional detection capabilities. When an organization reaches the point where they have to choose the right product, the issue is clear – they understand that their detection systems are raising alerts but providing no insight into how the attack happened, how far the attacker moved, and what data was affected.
The worldwide average cost of data breaches amounts to $4.88 million and operational disruptions impact 70% of businesses , thus , investigating security incidents requires more than just alerts and summary information about connection attempts. According to industry research, 63% of all daily security alerts remain uninvestigated due to the lack of context in telemetry, as attackers are using credential abuse (22% of breaches) and software vulnerabilities (20%) for evading initial controls.
Closing the existing gap requires detailed packet-level information and automated session reconstruction. While traditional Network Detection and Response (NDR) solutions are using sampled traffic statistics or even just NetFlow information, NetWitness sees the network traffic as a forensic evidence material. Using the combination of PCAP, metadata search, protocol parsing, and cross-domain correlation allows security analysts to move from suspicious signals to attack reconstruction.
The enterprise network handles terabytes of data per day. Collecting packets of data without organizing it leads to a huge data storage center that is almost impossible to utilize in an ongoing attack. However, collecting only high-level telemetry does not help much in post-event analysis. NetWitness makes up for this by possessing five key platform features aimed at deep analysis and threat reconstruction.
Every enterprise environment balances storage costs, regulatory compliance, and forensic depth differently. NetWitness provides architecture-level flexibility, allowing organizations to combine full packet capture (PCAP) with enriched metadata generation. 2. System Architecture & Core Working Principles Effective network forensic analysis requires both deep visibility and efficient storage strategies. NetWitness allows organizations to balance long-term evidence retention with operational performance through flexible capture architectures.
This hybrid approach ensures security teams retain the exact depth of evidence required without paying for unnecessary storage overhead. Searching through raw packet files during an incident is slow and operationally inefficient. NetWitness continuously processes raw traffic on the wire, generating over 100 structured metadata keys.
Searchable metadata is a foundational component of network forensics analysis, enabling rapid network traffic analysis across large environments without manually reviewing raw packet data. Instead of starting an investigation with a massive PCAP download, analysts begin with structured, searchable metadata attributes: Analysts can query, filter, and pivot across weeks of network activity in seconds, surfacing relevant sessions before extracting deep packet details.
Attackers do not function as isolated alarms; rather, they create connections that stay alive, send remote commands, plant tools, and steal files. NetWitness automatically decodes network protocols to create the entire session at the application layer exactly as it happened over the network. Instead of viewing hexadecimal representations of packets in an external tool, analysts examine web sessions, command-line communications, email transactions, and file transfers right from inside the NetWitness interface.
NetWitness uses its patent protected stream analytics technology on the raw input data received from the network. As the data passes through the NetWitness Sensor, its behavior engines perform analysis based on connection behavior, protocol anomaly, and threat intelligence feeds all at the same time. These capabilities support both network threat detection and proactive threat hunting by identifying suspicious behaviors as traffic flows through the network.
Network artifacts are never seen alone. Advanced Persistent Threats (APTs) use stolen credentials, run scripts on the endpoint, and traverse from cloud to hybrid environments. NetWitness natively correlates network forensics data with system logs and EDR data. This broader network security monitoring capability helps analysts understand attacker behavior across network, endpoint, and cloud environments.
Most enterprise security operations struggle not from a lack of detection, but from manual labor required to reconstruct incidents across siloed tools. The table below illustrates how NetWitness shifts SOC operations from reactive alert triage to comprehensive attack reconstruction. When a serious incident occurs, the primary goal of the investigation is establishing absolute proof. NetWitness guides analysts through a structured, 7-step operational workflow to fully map the attack lifecycle.
This structured process transforms routine alerts into actionable cybersecurity investigation workflows, helping analysts quickly determine attack scope and business impact. NetWitness identifies anomalous network behavior using continuous behavioral analytics, statistical rule engines, and integrated threat intelligence.
The analyst isolates the initial signal, gaining immediate visibility into the affected host, destination IP, user identity, and associated network sessions. Using indexed metadata keys, the analyst pivots backward in time to identify related infrastructure, subdomains, or communication patterns preceding the initial trigger.
Where deeper payload inspection is necessary, the analyst executes single-click session reconstruction to inspect application payloads, transferred binaries, or command-and-control (C2) instructions. The analyst queries historical metadata to identify lateral movement. This includes searching for internal SMB/RDP connections, credential reuse across adjacent hosts, or staging servers.
NetWitness ties together the telemetry from the packet and from the endpoint. The analyst establishes which exact process initiated the outbound connection. The analysis ends with the creation of a confirmed timeline of events. The analyst confirms entry point, lateral movement, affected systems, and amount of exfiltrated data.
Organizations looking to deploy network forensics analysis and network security monitoring solutions should assess vendors’ capabilities against six technical requirements: In dealing with critical incidents on a business level, confirmation is not sufficient. Security officers need to provide a rationale for how the intruder came in, what measures he used, how much he went past the boundary point, and whether any information got out.
Traditional detection engines leave these questions unanswered. By combining flexible capture models, real-time metadata indexing, deep session reconstruction, and cross-domain correlation, NetWitness delivers advanced network forensics analysis capabilities that support network threat detection , improve network visibility , and accelerate cybersecurity investigations. The result is a complete understanding of how network attack enter, move through, and impact enterprise environments.
The best network forensics analysis tools should provide more than network alerts. Enterprise platforms should support meaningful network visibility, metadata analysis, packet-level evidence where required, protocol analysis, historical investigation, and efficient workflows for reconstructing incidents. NetWitness supports these capabilities by combining network detection with packet capture, metadata enrichment, protocol parsing, session reconstruction, and broader threat investigation.
The process of network forensics involves spotting suspicious activities, collection and analysis of network data, review of communications and sessions, host identification, attack timelines, attack scope determination, among others. The objective is not simply to confirm that something malicious occurred. It is to understand how the attack unfolded. In selecting a network forensics analysis tool, consider the depth of evidence available on the network, capability for full packet capture, ability to analyze metadata, visibility of protocols, historical searching, investigation process, scalability, and integration with other threat detection/response activities.
Another important consideration is whether the tool will assist in attack reconstruction rather than producing more alerts. Organizations should look for strong network security forensics capabilities, deep network traffic analysis, flexible evidence collection, support for session reconstruction, and the ability to connect network evidence with other security telemetry. The platform should help analysts investigate the root cause and full scope of an incident.
NetWitness provides network forensics capabilities that encompass the following: packet capture, metadata enrichment, protocol parsing, session reconstruction, behavioral analysis, threat intelligence, and cross-domain investigation. The analyst can thus go from responding to alerts to investigating and conducting a thorough reconstruction of attack activities.
Full packet capture can provide deeper evidence for investigations when connection records and logs do not provide enough context. It can support detailed examination of network communications and help investigators validate what occurred during an incident. For organizations with demanding forensic requirements, packet-level evidence can play an important role in digital forensics, attack reconstruction, and incident response.
3. Software Implementation, Frameworks & Protocols Network Forensics is a comprehensive toolkit for analyzing network traffic , reconstructing security incidents, and investigating intrusions through packet-level analysis. Network Forensics Analysis Toolkit - Packet capture analysis, traffic reconstruction, protocol dissection, and intrusion investigation NetForensics brings together practical utilities, wireless and packet-capture labs, field guides, and books for analysts who need to investigate real network attacks.
Wireless forensics is one major part of NetForensics, but the resource library is broader: packets, logs, malware traffic, protocol abuse, encrypted sessions, timelines, reporting, and repeatable investigation workflows. The site pairs working utilities with field notes, labs, and book companion material so analysts can move from raw artifacts to validated conclusions.
Use practical tools to extract evidence, review packet captures, and keep analysis notes tied to repeatable methods. The books provide structured learning paths while the site gives readers practical utilities, labs, and reference notes. Every tool and guide should help an analyst preserve evidence, explain observations, and validate conclusions. Upload authorized captures, extract 802.11 events, review WPA/WPA3 posture, identify rogue AP candidates, and export reports.
Normalize MAC addresses, classify local/global/multicast addresses, and explain vendor confidence for investigations. Generate common display filters for DNS, TLS, HTTP, EAPOL, deauthentication, beacon, and suspicious endpoint review. Understand PCAP sources, timestamps, hashes, chain of custody, and how to avoid overclaiming from incomplete captures. Move from protocols and endpoints to timelines, suspicious flows, wireless artifacts, malware traffic, and service abuse.
Convert observations into a defensible investigation narrative with validation filters and supporting raw artifacts. Nipun Jaswal's network forensics books are paired with practical companion material: utilities, labs, checklists, and topic pages that support hands-on study. A broader practical path through traffic analysis, logs, malware investigation, wireless forensics, and incident response.
A hands-on introduction to investigating network attacks and finding evidence with common forensic tools. Network evidence comes in several forms, each trading detail for cost and retention. Knowing which source answers your question saves hours of pulling the wrong data. Most investigations start with the cheapest, longest-retained source and work toward full packet capture only where it's still available. NetFlow can tell you a host talked to a suspicious IP for weeks; pcap tells you exactly what was sent, but only if someone was capturing at the time.
Raw packet captures are large and mostly irrelevant to any given question. The skill is narrowing down to what matters and rebuilding the conversation from the pieces. Wireshark is the well-known GUI tool for this kind of analysis, with a command-line counterpart for scripted or headless work. Zeek takes a different approach: instead of showing raw packets, it watches traffic and generates structured logs (connections, DNS queries, HTTP requests) that are easier to search at scale.
Reconstructing a session means rebuilding the actual exchange from captured packets. For HTTP, that's pairing a request with its response. For DNS, it's matching a query to its answer. TLS encryption hides the request and response content, but it doesn't hide everything. The Server Name Indication (SNI) field in the handshake reveals the hostname being requested on most traffic, certificate details are visible, and traffic timing and volume are observable regardless of encryption. Encrypted Client Hello, a newer extension some providers and browsers now support, can hide SNI too, so an investigator can't assume it's always there.
JA3 and JA3S are documented fingerprinting techniques that identify client and server software from characteristics of the TLS handshake itself, such as the offered cipher suites and extensions. This works even when the encrypted payload is completely opaque, though newer clients that randomize their handshake extensions degrade JA3's reliability, which is why the successor fingerprint JA4 is increasingly used alongside it.
Command-and-control traffic often looks different from normal user traffic once you know what to look for, even when the payload itself is encrypted. Working a network forensics question follows a consistent order, moving from what's available to what actually answers the question.
Network evidence is strongest when it corroborates what chapters 3 and 4 already found on the host, turning a suspected connection into a confirmed one. An investigator needs to determine whether a host has been beaconing to a suspicious IP over the past three months, but full packet capture for that period no longer exists. What's the best source to check next? Which characteristic most reliably distinguishes automated C2 beaconing from normal human-driven web browsing? A session is encrypted with TLS. Which of the following is still visible to an investigator without decrypting the traffic? In a controlled study by Horizon3 researchers, models that explicitly identified a trap in their reasoning still attacked it 73.4% of the time. Read the findings and see what they mean for canaries, decoys, and early detection.
Packet capture analysis is the most complete record of what happened on the network. Endpoints log what they know happened locally. SIEM correlates events across systems. Network packet capture contains everything that was transmitted — including data that was encrypted end-to-end (observable at the metadata level even if not readable), protocols that generate no endpoint logs, and lateral movement across network segments.
Not every incident requires PCAP analysis — endpoint forensics and log analysis are often sufficient. But when an investigation needs to establish: what data left the network, how C2 communication was structured, what credentials were transmitted in cleartext, or how an attacker moved laterally across network segments, PCAP is the evidence source that provides the answer. This guide covers the practical workflow.
Before analysis, you need the PCAP file. The capture point determines what traffic is visible. PCAP at the perimeter captures all traffic entering and leaving the network — the best vantage point for detecting C2 communications, data exfiltration, and external scanning. Configure port mirroring on your edge firewall or core switch to send all traffic to a capture device (a Security Onion node, a network tap, or a dedicated capture server running tcpdump). At enterprise scale, capturing all perimeter traffic requires significant storage — typically filter to capture-on-rule-match mode where specific protocol triggers initiate capture.
For targeted capture on a specific suspected host: Wireshark installed on the endpoint (with admin rights) can capture all traffic from that host's network interface in real time. This is appropriate during an active incident when you want to observe what a specific machine is doing right now. Limitation: encrypted traffic shows IP/port metadata but not content. For malware that uses TLS for C2, you still see connection patterns, volumes, and timing — all forensically useful even without decryption.
Security Onion, Zeek/Bro, and NDR platforms (Darktrace, ExtraHop, Vectra) passively record network metadata and often full-packet data on rolling buffers. During an incident, query these platforms for the affected IP ranges and time windows first — you may already have the PCAP without a new capture deployment. Ask: does our network security monitoring platform have full-packet retention, and if so, what is the retention window? 4. Practical Deployment, Analysis & Case Studies Wireshark's display filter language is the core skill for PCAP analysis. These filters address the most common incident response scenarios.
ip.addr == 10.1.2.3 — all traffic to or from a specific IP. ip.src == 10.1.2.3 and ip.dst == 8.8.8.8 — specific source to destination. tcp.stream eq 15 — follow a specific TCP conversation identified by stream index. Right-click any packet > Follow > TCP Stream is the fastest way to read the full content of a session including HTTP requests, form submissions, and any cleartext credentials.
dns — all DNS traffic (look for DGA-pattern domains, unusually high DNS query volumes to a single domain, DNS TXT record queries used for C2). http.request.method == POST — all HTTP POST requests (data being sent from client to server — look for large POSTs to unusual external IPs that indicate exfiltration). ftp or telnet — cleartext protocol use that should not exist in modern environments and almost always indicates either legacy systems or an attacker using these protocols deliberately.
smtp — email traffic (outbound email exfiltration or spam relay). Statistics > Conversations > Sort by Bytes (descending). Large data transfers from internal IPs to external destinations appear at the top. A 500MB conversation from a workstation to an external IP over an unusual port or protocol is an exfiltration signal. Also: Statistics > Endpoints shows total bytes per IP — an endpoint sending 10x more data than typical warrants investigation.
This statistical view surfaces anomalies faster than packet-by-packet analysis. C2 malware communicates with its controller at regular intervals (beaconing) — typically every 30-300 seconds. In Wireshark: filter to a suspected C2 IP, view the packet list, and look for regular-interval packets. Statistics > IO Graph with a delta filter shows communication timing patterns. A consistent 60-second interval of outbound packets to a single external IP is a strong C2 beacon indicator. Also: look for HTTP connections with unusual User-Agent strings, small packet sizes (C2 check-in), and consistent connection timing.
Wireshark's GUI becomes impractical for PCAP files above 1-2GB. tshark (Wireshark's command-line interface) processes large captures efficiently and supports pipe-based workflows. tshark -r capture.pcap -Y dns -T fields -e dns.qry.name | sort | uniq -c | sort -rn | head 50 — extracts all DNS queries, sorts by frequency, shows top 50 domains queried. DGA domain patterns (random-looking strings) and unusual TLD use (domains ending in .ru, .cn, .pw queried from corporate hosts) appear clearly in this output. Process a 10GB PCAP in minutes.
tshark -r capture.pcap -Y http.request -T fields -e ip.src -e ip.dst -e http.host -e http.request.uri -e http.content_length — tabular output of every HTTP request: source IP, destination IP, host header, URI, and content size. Pipe to grep to filter for specific hosts or URI patterns. Sort by content_length to identify large data transfers. tshark -r capture.pcap -Y 'ip.src == 10.1.2.3' -T fields -e ip.dst | sort -u — all unique destination IPs from a specific source.
Cross-reference the output against your threat intelligence feeds: grep -F -f malicious_ips.txt from the tshark output identifies any connections to known-malicious infrastructure in the capture. Zeek is an open source network analysis framework that processes PCAP files and produces structured logs — conn.log (all connections), dns.log, http.log, ssl.log, files.log, and others — that are far easier to query than raw PCAP. Installing Zeek and running it against a PCAP file reduces analysis time dramatically.
zeek -r capture.pcap — processes the PCAP and outputs structured log files in the current directory. conn.log contains every connection with src/dst IP, ports, bytes, duration, and state. dns.log extracts all DNS queries and responses. files.log extracts metadata for all files transferred over HTTP/FTP including hashes — allowing you to identify transferred malware or exfiltrated documents by hash without manual extraction.
cat conn.log | zeek-cut id.orig_h id.resp_h orig_bytes | sort -k3 -rn | head 20 — lists connections by bytes sent from origin to responder (outbound data volume), sorted by largest first. Exfiltration events appear as very large orig_bytes values to external destination IPs. This is faster than the Wireshark Statistics view for large captures. Zeek's ssl.log includes JA3 and JA3S fingerprints — MD5 hashes derived from TLS ClientHello and ServerHello fields. These fingerprints identify the TLS client implementation being used. Malware families often have distinctive JA3 fingerprints — known-malicious JA3s are published by Salesforce and other researchers. grep the JA3 values from your ssl.log against published malicious JA3 feeds to identify encrypted C2 sessions without decryption.
PCAP analysis answers the questions that endpoint and SIEM logs cannot: what data left the network, how the attacker communicated with C2, and what the lateral movement path looked like at the network level. Wireshark's display filters and conversation statistics handle most triage use cases in minutes. tshark and Zeek handle large captures efficiently without requiring the full GUI. For organizations that do not currently capture network traffic, a Security Onion deployment on the perimeter or a cloud-based NDR sensor is the infrastructure investment that makes PCAP analysis available retroactively during the next incident.
Full-packet capture volume depends on network throughput. At 1 Gbps sustained traffic, full capture generates approximately 450GB per hour. Enterprise networks typically sustain 2-10% of peak bandwidth during normal hours. Practical storage for a 1 Gbps perimeter with 10% average utilization and 30-day retention is approximately 30-40TB. Most organizations implement capture on trigger (capture only when specific signatures fire) or metadata-only (Zeek logs without raw packets) rather than full-packet indefinite retention. 7-day full-packet retention with 90-day metadata retention is a common operational balance.
Without the server's private key or a TLS session key log file, Wireshark cannot decrypt TLS traffic. What you can see: source and destination IPs and ports, TLS handshake metadata (Server Name Indication field reveals the domain even in encrypted traffic, JA3/JA3S fingerprints identify the TLS implementation), packet sizes and timing (beacon pattern detection works on encrypted traffic), and certificate details (the server's certificate is transmitted unencrypted). For incident response, SSL inspection at a proxy or the server's private key are required for content decryption.
Zeek (formerly Bro) is a network analysis framework that produces structured logs from PCAP — focused on network metadata and protocol analysis, not signature detection. Suricata and Snort are signature-based IDS/IPS engines — they alert on traffic that matches known attack signatures. For incident response PCAP analysis, Zeek is typically more useful because it produces queryable logs for all connections and protocols rather than only alerting on signature matches. In production deployment, run both: Zeek for metadata and protocol analysis, Suricata for signature-based alerting.
25 actively exploited vulnerabilities with CVSS scores, exploit status, and patch availability. Print it, pin it, share it with your SOC team. Step-by-step 24-hour IR checklist covering detection, containment, eradication, and recovery. Built for SOC teams, IR leads, and CISOs.
50,000+ security professionals read Decryption Digest for early warnings on zero-days, ransomware, and nation-state campaigns. Free, daily, no spam. Cybersecurity professional with expertise in threat intelligence, vulnerability research, and enterprise security. Covers zero-days, ransomware, and nation-state operations for 50,000+ security professionals every morning.
Actionable threat intelligence for working practitioners. Free. No spam. Trusted by 50,000+ SOC analysts, CISOs, and security engineers. Network forensics is a cornerstone of Digital Forensics and Incident Response (DFIR). Whether you are competing in a Capture The Flag (CTF) event or investigating a live corporate breach, understanding how to dissect network traffic is an invaluable skill. While advanced malware might delete its tracks on a hard drive or hide stealthily in RAM, it almost always leaves a footprint on the wire. Attackers eventually need to communicate with Command and Control (C2) servers, download secondary payloads, or exfiltrate stolen data. In this guide, we will explore the fundamentals of analyzing Packet Capture (PCAP) files to uncover and track malicious activity.
Before diving into packet analysis, you need the right tools in your DFIR toolkit. While there are many commercial products available, the open-source community provides industry-standard tools that every analyst should master. Wireshark is the world’s most widely used network protocol analyzer. It allows you to see what is happening on your network at a microscopic level. It provides a graphical interface to drill down into individual packets, follow TCP streams, and extract files transferred over plaintext protocols. You can download it directly from their official site or find its source code on the Wireshark GitHub repository.
While Wireshark is incredible for deep-diving into individual packets, opening a 50GB PCAP file in a GUI will quickly crash your system. This is where Zeek shines. Zeek is a powerful Network Security Monitor (NSM) that processes raw network traffic and converts it into high-level, human-readable transaction logs (like dns.log , http.log , and conn.log ). It is perfect for quickly triaging massive amounts of network data before narrowing your focus to a specific timeframe in Wireshark.
Let us imagine a classic DFIR scenario: an Intrusion Detection System (IDS) alerts you to suspicious outbound traffic from a workstation. You are handed a PCAP file containing the network traffic leading up to the alert. Here is how you can begin your investigation. Malware rarely hardcodes C2 IP addresses because infrastructure is frequently taken down by authorities. Instead, attackers use Domain Generation Algorithms (DGA) or dynamic DNS services. Your first step in Wireshark should be to look at the DNS traffic.
Scroll through the queried domains. If you see randomized, nonsensical domain names (e.g., xkqz129b[.]com ), you are likely looking at DGA traffic. Make a note of the IP addresses returned in the DNS responses (which you can view by changing the filter to dns.flags.response == 1 ), as these belong to the attacker’s infrastructure. Once you have identified the suspicious IP addresses, the next step is to examine how the compromised host is communicating with them. Often, malware will use HTTP or HTTPS to blend in with normal web traffic. C2 communication usually takes the form of recurring “beacons”—automated check-ins where the malware asks the server for new commands.
Look for anomalies in the HTTP headers. For example, malicious tools often use default or hardcoded User-Agent strings (like “python-requests/2.25.1” or generic base64 encoded strings in the URI). If the traffic is unencrypted HTTP, you can right-click the packet in Wireshark and select Follow > HTTP Stream to view the exact commands being sent and received. If the compromised machine downloaded a secondary payload—such as a ransomware executable or a reverse shell script—over an unencrypted protocol, you can extract that file directly from the PCAP.
In Wireshark, navigate to File > Export Objects > HTTP . This will open a dialog box listing all the files transferred over HTTP during the capture. You can save these files to your local disk for further static and dynamic malware analysis. Remember to execute extracted malware only in a safely isolated sandbox environment! Network forensics is just one piece of the puzzle. Once you have extracted Indicators of Compromise (IoCs) like C2 IP addresses, malicious domains, and downloaded filenames, you must pivot to the endpoint to complete the picture.
For instance, if you noticed a large file download followed by rapid outbound connections, you should investigate what process initiated those connections. If the payload was injected directly into memory to avoid touching the disk, you will want to pivot to analyzing fileless malware in memory to capture the injected code. Similarly, analyzing the endpoint’s logs can reveal how the attacker initially gained access and if they established a foothold.
Using the timestamps from your PCAP file, you can cross-reference the activity using Windows event log analysis to spot scheduled tasks, malicious service installations, or lateral movement attempts occurring at the exact same moment. Mastering network forensics takes time, but it is a highly rewarding skill for any DFIR analyst or CTF player. By leveraging tools like Wireshark and Zeek, you can peel back the layers of a cyber attack, trace the adversary’s steps, and safely extract their tools for further analysis. Practice by downloading sample PCAPs from public repositories like Malware-Traffic-Analysis, and you will soon be tracking down threats with confidence.
5. Performance Evaluation & Extended Technical Observations Wireshark is a graphical packet analyzer used to inspect individual packets and follow specific network streams in deep detail. Zeek is a Network Security Monitor that processes network traffic in bulk and generates summarized, easily searchable logs of network activity, making it better for triaging large datasets.
Yes, but only if you have the session keys or the server’s private RSA key (for older TLS versions). In many corporate environments, SSL/TLS decryption is performed at the firewall or proxy, and the PCAP is captured post-decryption. Alternatively, if you have the endpoint’s SSLKEYLOGFILE, Wireshark can use it to decrypt the captured traffic. There are many excellent resources for practice. The website Malware-Traffic-Analysis.net provides a massive archive of real-world malware PCAPs complete with exercises and answers. Additionally, platforms like CyberDefenders and Blue Team Labs Online offer dedicated network forensics challenges.
I'm passionate about everything whats IT related. In 2015 decided to persuade my dream and started career in LE. In 2018 finally got opportunity to work as digital forensics specialist. From first day I knew digital forensics and incident response (DFIR) is field in which I want to learn more and share my experience with others. Master packet capture for forensic investigations. Learn how to reconstruct network sessions and extract evidence from PCAP files.
This project demonstrates practical network traffic investigation using Wireshark within a controlled cybersecurity lab environment. The objective of this lab is to develop practical experience with packet capture analysis, traffic filtering, protocol investigation, and evidence-based reporting.
Packet analysis is a critical skill for SOC analysts, incident responders, threat hunters, and network defenders. Wireshark provides deep visibility into packet-level network behavior, making it one of the most important tools used in cybersecurity operations. The packet capture confirmed successful traffic monitoring and protocol-level analysis within the lab environment.
This project successfully demonstrates practical packet-level traffic investigation using Wireshark within a cybersecurity lab. The project reflects real-world network investigation techniques used by SOC analysts and incident response teams during cybersecurity operations. Hands-on Wireshark investigation lab demonstrating DNS analysis, HTTP inspection, TCP stream reconstruction, packet-level forensic analysis, and SOC investigation methodologies.
Flow records tell you that a workstation sent 4 GB to an external IP at 2 a.m. Firewall logs confirm the connection was permitted. But neither source answers the question forensic investigators actually need answered: what was in that traffic? Was it a large legitimate backup job, or was it a staged archive of customer records moving to an attacker-controlled endpoint? Packet capture (PCAP) is the definitive answer. It preserves the content of every frame crossing an interface — the actual HTTP request bodies, the DNS queries, the SMB handshakes, the TLS ClientHello fingerprints, and, when session keys are available, the decrypted application payloads. When lateral movement is suspected, PCAP lets you reconstruct exactly which credentials were sprayed, which internal services were probed, and which ones responded.
Confirming suspected lateral movement. Network flow anomalies — a workstation connecting to internal hosts it has never reached before — can be lateral movement or a legitimate software deployment. PCAP confirms which: you see the actual SMB authentication, the RPC calls, the WMI queries. If the connection carries PsExec service installation payloads, the question is settled.
Preserving evidence of data exfiltration. Once an attacker is evicted from an environment, the evidence is gone unless you captured it. A targeted capture triggered on high-volume outbound connections to unusual destinations preserves the exfil payload, the file names extracted from HTTP multipart uploads or DNS tunnelling queries, and the timing for correlation with access logs.
Reconstructing attack sequences post-incident. A continuous ring-buffer capture running at low bandwidth (headers only, or sampled) on critical segments provides a retrospective view. When the SOC alarm fires three days after the initial compromise, the PCAP ring buffer may contain the original foothold — the initial C2 connection, the first credential theft, the first internal scan.
The standard advice — sudo tcpdump — grants root for the duration of the capture. A safer model assigns only the CAP_NET_RAW capability to the binary: With this configuration, a user in a netcap group can run tcpdump without sudo . The process has precisely the privilege needed to open a raw socket and nothing else. A parser vulnerability in tcpdump cannot escalate to full root.
Use the -Z flag to drop privileges to a non-privileged user immediately after the interface is opened: The -Z flag requires that the target user exists and that the output directory is writable by that user. Structure your capture directory accordingly: dumpcap is the capture engine that ships with Wireshark. It is explicitly designed for privilege-separated operation: a small binary with CAP_NET_RAW and CAP_NET_ADMIN does only capture; analysis happens in a separate unprivileged process.
dumpcap writes pcapng format by default, which embeds interface metadata and capture comments — useful for chain-of-custody documentation. Broad captures create evidence management problems and privacy exposure. Berkeley Packet Filter (BPF) expressions at capture time limit collected data to traffic relevant to the investigation. BPF filtering happens in the kernel before data is copied to userspace, which also reduces CPU overhead significantly on high-traffic interfaces.
The -s 96 flag sets the snap length to 96 bytes — enough to capture Ethernet, IP, and TCP/UDP headers without any payload. For reconstruction you need full packets ( -s 0 ), but for connection metadata without payload privacy exposure, header-only capture is the correct default for continuous recording. Packet capture on a corporate network intercepts communications that may include personal data: employee emails, authentication credentials, instant messages, browsing history. Before deploying any capture infrastructure, verify: A PCAP file is a direct recording of network credentials, personal data, and proprietary communications. It must be treated as a high-sensitivity asset.
Document chain of custody. For any capture that may become legal evidence, generate a cryptographic hash at capture time and record it in an append-only log: Access control. PCAP files should be readable only by the investigator and the IR lead. Group ownership on the captures directory with chmod 750 and audited with auditd rules on file access: tshark (Wireshark’s CLI frontend) applies the same dissectors as the GUI, making it useful for quick protocol-aware filtering that BPF cannot express: For custom capture tooling, the Go gopacket library (wrapping libpcap ) allows building purpose-specific sensors: gopacket -based tools are commonly used for building inline sensors that feed events to a SIEM in real time without writing full PCAP to disk.
Interactive protocol analysis: Open in Wireshark. Use Statistics > Conversations to identify top talkers. Apply the tcp.stream display filter to follow individual TCP sessions. Use File > Export Objects > HTTP to extract all HTTP-transferred files in a single operation. Detecting beacon patterns. C2 beacons produce packets at regular intervals — every 30 seconds, every 5 minutes. To identify beaconing in a PCAP: Low-variance inter-arrival times on a single destination IP are a strong beacon indicator.
When a TLS session key log is available, Wireshark can decrypt TLS traffic in a PCAP without the private key. This works for traffic generated by Firefox, Chrome, and curl when the SSLKEYLOGFILE environment variable is set. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Network%20forensics • https://en.wikipedia.org/wiki/Digital%20forensics • https://en.wikipedia.org/wiki/IoT%20forensics • https://www.netwitness.com/use-cases/network-forensics/ • https://www.netwitness.com/blog/network-forensics-analysis/ • https://github.com/janderik/network-forensics • https://www.netforensics.net/ • https://h3ad-sec.github.io/H3AD-LEARN/digital-forensics/06-network-forensics.html • https://www.decryptiondigest.com/blog/network-forensics-pcap-analysis-wireshark-incident-response • https://dfir.quest/2026/09/17/network-forensics-in-dfir-a-beginners-guide-to-analyzing/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Network Forensics Tool For Packet Capture Reconstruction.
! Define Extended Access List to Block Malicious Traffic ip access-list extended SECURE_PERIMETER_ACL remark Block Inbound Telnet and Unencrypted Services deny tcp any any eq 23 log remark Permit Verified Web SSL Traffic permit tcp any any eq 443 permit tcp any any eq 80 remark Mitigate ICMP Flood and Ping Sweeps permit icmp any any echo-reply deny icmp any any echo log deny ip any any log
! Apply ACL to Ingress Interface GigabitEthernet0/0 interface GigabitEthernet0/0 ip access-group SECURE_PERIMETER_ACL in no shutdown end write memory
Extended IP access list SECURE_PERIMETER_ACL (Cisco Packet Tracer) ──────────────────────────────────────────────────────────────────────── 10 deny tcp any any eq telnet log (142 matches) [Probes Dropped] 20 permit tcp any any eq 443 (18402 matches) [TLS 1.3 Traffic Permitted] 30 permit tcp any any eq 80 (4812 matches) 40 deny icmp any any echo log (524 matches) [Flood Mitigated] 50 deny ip any any log (38 matches) [Default Implicit Deny Rule] ──────────────────────────────────────────────────────────────────────── [✓] Packet Tracer Verification: 0 Unsanitized Ingress Leaks on Gi0/0
| Interface Port | Network Zone | Filter Applied | Traffic Processed | Firewall Decision |
|---|---|---|---|---|
| Gig0/0 (WAN) | Untrusted External | Extended ACL 101 | 24,810 Packets | INSPECTED & FILTERED |
| Gig0/1 (DMZ) | Public Web Services | Port 443 Only | 18,402 Packets | PERMITTED |
| Gig0/2 (LAN) | Corporate Users | 802.1X Port Security | 142 Probes | DENIED & QUARANTINED |