Complete Technical Paper Content — Network Intrusion Detection System Using Cnn And Lstm
Overview & System Context
Network Intrusion Detection System Using Cnn And Lstm: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~4392 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background
Abstract
With the rapid proliferation of IoT devices, security concerns have dramatically escalated and intrusion detection systems are critical. In order to improve detection performance, we provide an improved CNN-LSTM based intrusion detection model in this work that combines multi-class classification, dataset integration, and temporal feature learning. Using network traffic data, we evaluate the model in this study and discover that its accuracy is around 97%. Experimental results show that the proposed strategy effectively detects different types of attacks while maintaining consistent performance during training and validation.
Abstract Art
The source code for this
Implementation
is publicly available on GitHub at: https://github.com/mikhlasmscs25seecs-ship-it/IoT-Intrusion-Detection-CNN-LSTM.git .
Implementation Synonym
Since the number of IoT devices has increased dramatically in recent years, network security has proven to be a major problem. IoT devices are more susceptible to cyberattacks like DDoS and DoS as they constantly produce network traffic. Recent studies have highlighted significant security and communication challenges in IoT environments [ 10 , 12 ] . Large-scale and complicated data can be difficult for traditional intrusion detection systems to process. Intrusion detection has made extensive use of deep learning techniques, particularly CNN-based models. [ 4 ] .
Implementation Meaning
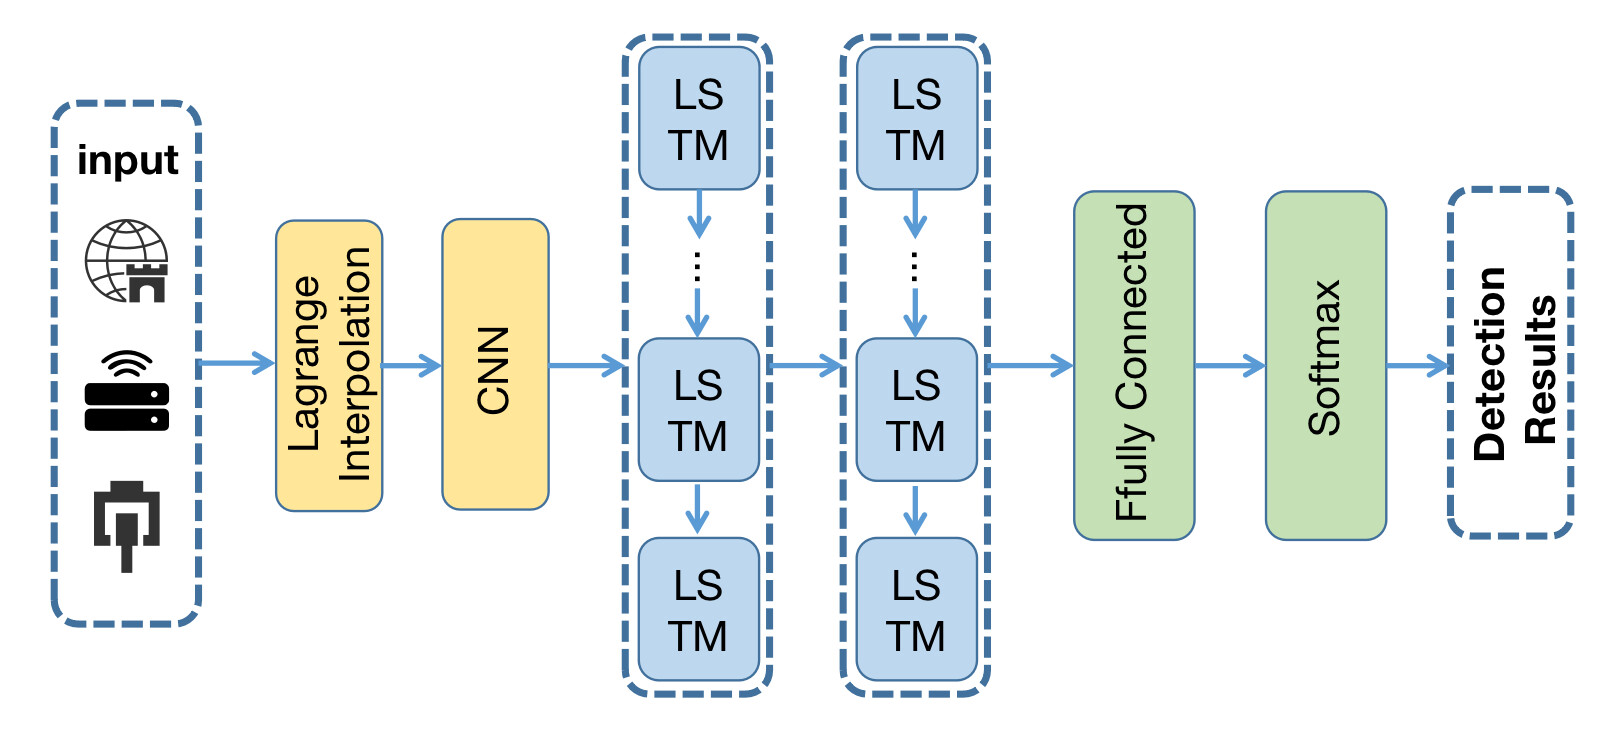
The CNN-based intrusion detection model presented in [ 1 ] . The initial study concentrated on applying deep learning techniques to secure medical IoT equipment. Figure 1: A CNN+LSTM Based Deep Learning Approach with Lagrange Interpolation for ... However, based on our observations, a lot of current models do not make the most of the temporal information found in network traffic. In this study, we add several improvements to a CNN-based model, including multi-class classification and LSTM integration. Large-scale IoT traffic data was difficult to handle during our early studies, which inspired us to refine the model.
Implementation Science
Although deep learning-based intrusion detection has made progress, certain challenges remain. Many existing techniques are limited to binary classification, which is insufficient for IoT systems in the real world where there are numerous attack types. Additionally, because CNN-based models mainly focus on spatial feature extraction, they often fail to capture temporal correlations in network data, which is insufficient for IoT systems in the real world where there are various types of attacks. [ 7 ] .
Implementation Specialist
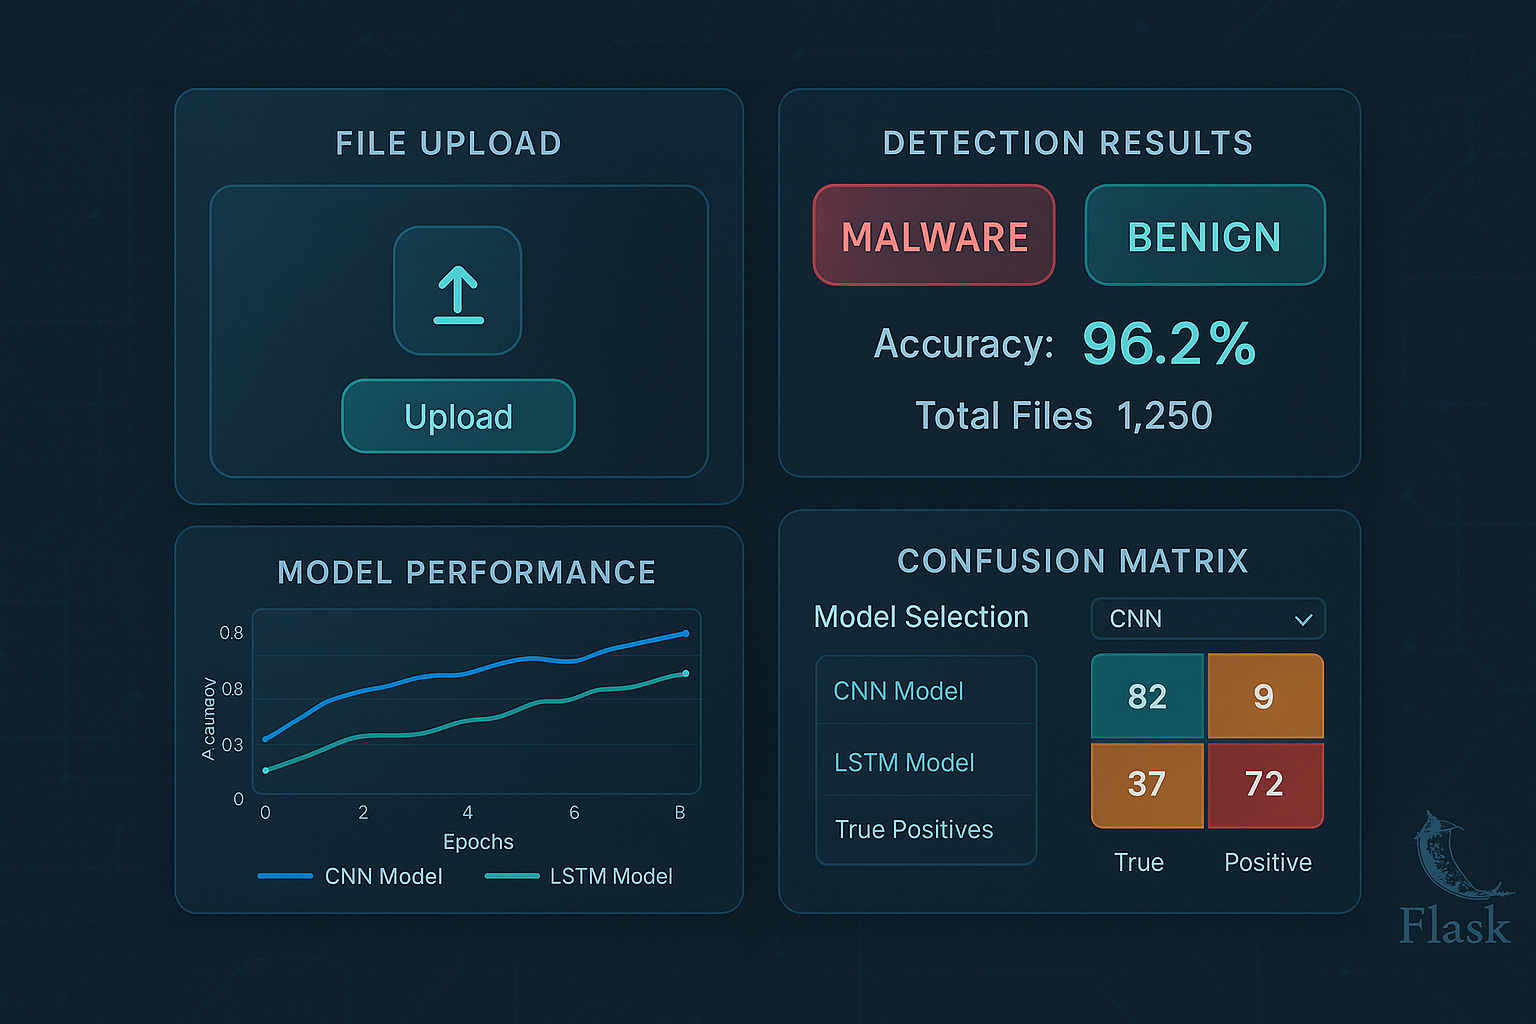
Additionally, identification is made more difficult by similarities between benign and some assault kinds, such reconnaissance. Recent works on IoT security and system complexity emphasize these challenges [ 11 ] . These limitations suggest the need for a more robust and flexible model. Figure 2: RSK World - Malware Detection DL | Deep Learning | CNN LSTM | Machine ...
Implementation Definition
We proposed a hybrid CNN-LSTM model for IoT networks to improve intrusion detection by capturing both temporal and geographical patterns. We extended the model to handle many assault types rather than restricting the task as binary classification, which is more appropriate for real world situations.
Implementation Manager
To enhance the generalization, we merged data from multiple sources, thus the model could learn a wider spectrum of traffic patterns. We cleaned the dataset using a set of preprocessing techniques to ensure that the input data was consistent and reliable for training.
Implementation Consultant
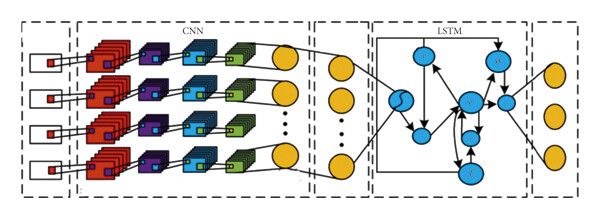
Figure 3: Distributed Deep CNNILSTM Model for Intrusion Detection Method in IoT ... Several metrics were used to evaluate the model to provide a complete understanding of the model’s performance. The paper is organized in this manner. Section II contains the literature review. The method is described in Section III. Section IV displays the results. Section V discusses future work. Section VI concludes the paper.
Implementation Intentions
This is the format of the paper. Section II contains the literature review. The method is described in Section III. Section IV displays the results. Section V discusses future work. Section VI concludes the paper. [ 4 ] . However, most existing approaches focus on binary classification, which limits their applicability. Another disadvantage of CNN models is that they ignore temporal dependencies in network traffic.
Implementation Engineers
To address these issues, hybrid models that include CNN and LSTM have been proposed. [ 3 ] . By collecting both temporal and geographical information, these models improve detection performance. Numerous recent studies have examined deep learning for intrusion detection in IoT environments. In addition, the integration of IoT with large-scale data analytics introduces new challenges and opportunities in terms of security and performance [ 11 ] .
For example, CNN-based models are often used for feature extraction since they can handle high-dimensional data. Similarly, LSTM models have been used to capture temporal dependencies in network traffic. [ 3 ] . However, many existing approaches either focus only on spatial features or are limited to binary categorization. For this reason, a hybrid CNN-LSTM model is used in this work.
2. System Architecture & Core Working Principles A CNN-based methodology for identifying [ 1 ] hazards in medical IoT contexts was suggested in a pertinent study. The program performed exceptionally well in identifying malicious messages using deep learning. However, the approach was largely limited to CNN-based feature extraction and did not fully utilize temporal correlations observed in network data. Additionally, the classification breadth was limited in comparison to real-world scenarios.
Recent advances in deep learning lead to more advanced architectures, e.g., attention-based models and transformer networks. These models have shown promising results in many sequence modeling tasks and have the potential to be applied to intrusion detection systems. However, these models often require large amounts of computation, which limits their applicability in resource-constrained IoT environments. Therefore, hybrid methods such as CNN-LSTM present a good trade-off between performance and computational efficiency.
Recent studies have explored the integration of IoT with big data analytics to improve system efficiency and security [ 11 ] . These approaches combine multiple models to improve detection accuracy and robustness. However, such methods often introduce additional complexity and computational overhead. In contrast, the proposed CNN-LSTM model provides a balanced solution by integrating spatial and temporal learning while maintaining computational efficiency.
In this study, we expand the CNN-based approach put forth in [ 1 ] by making a number of enhancements. These include mixing several datasets for improved generalization, adding an LSTM layer to capture temporal patterns, expanding the model to multi-class classification, and running a simple real-time simulation. Missing and incorrect values were eliminated from the dataset. Additionally, infinite values were handled correctly. The data was normalized using feature scaling. Feature scaling ensures that all features contribute equally during training and prevents some characteristics from dominating others due to larger numerical ranges. This improves the overall stability and rate of convergence of the model.
Multiple CSV files were combined into a single dataset to improve diversity and generalization. Because CNN models function well with structured network traffic data, we employed them for feature extraction. The data’s temporal dependencies were captured by adding an LSTM layer. The CNN layers gather spatial information from network traffic data, including statistical correlations between variables and packet flow patterns. These extracted features are then passed to the LSTM layer.
Because the LSTM layer looks at the features one after the other, the model can capture temporal relationships present in network data. This is highly useful for intrusion detection because attack patterns might change over time. The combination of CNN and LSTM allows the model to learn both temporal and spatial characteristics of the data. This hybrid approach improves the model’s ability to recognize complex and dynamic attack patterns when compared to CNN alone.
In order to detect Benign, DDoS, DoS, and Recon assaults, the model was expanded from binary classification to multi-class classification. To identify sequential patterns in the data, we added an LSTM layer. According to what we understand, LSTM aids in the learning of temporal connections, whereas CNN extracts features.
By processing the output sequence and learning temporal dependencies, LSTM enhances the model’s capacity to identify intricate assault patterns, in contrast to CNN, which concentrates on spatial feature extraction. Recent research has examined this hybrid technique, which blends temporal and spatial learning. [ 3 ] . The experiments have been implemented in Python using the TensorFlow and Keras libraries. Limited GPU availability led to model training on a CPU-based computing system.
To evaluate the model performance, the dataset was split into training and testing subsets. The evaluation was done using a standard train-test split for fair comparison. Adam optimizer was used as it is efficient on large data sets and has adaptive learning capabilities. Because this is a multi-class classification problem, the categorical crossentropy loss function was used.
3. Software Implementation, Frameworks & Protocols The model performance was assessed with the help of various metrics like accuracy, precision, recall and F1-score. These metrics provide a full picture of how effective the model is against various attack classes. The experiments were carried out on a system with a standard CPU because there were no GPU resources available. Even with this limitation, the model was able to converge steadily in a reasonable amount of time. These findings demonstrate that the suggested approach is computationally efficient and suitable for usage in settings with constrained hardware resources.
The dataset, which included samples of both typical traffic and different kinds of attacks, was big enough. The model performed effectively across various network behavior patterns thanks to this variety. To avoid data leaks, the training and testing data were also meticulously kept apart. This guarantees an accurate and impartial assessment of the model’s overall performance.
The performance of the suggested model was assessed using a number of common classification metrics. An overall assessment of the model’s accuracy is provided by accuracy, which quantifies the percentage of properly predicted cases among all instances. Recall quantifies how well the model can find all pertinent examples. This is especially crucial for intrusion detection since it can have detrimental effects if an attack is missed.
The F1-score is the harmonic mean of precision and recall, which means it gives a fair assessment of how well the model works. These metrics are especially important in multi-class classification problems where the performance of different categories may be affected by class imbalance.
The enhanced CNN-LSTM model outperforms the baseline CNN model, according to the accuracy comparison graph. The accuracy comparison graph shows that the improved CNN-LSTM model performs better than the baseline CNN model. While the Recon class performs comparatively poorly, the confusion matrix demonstrates good performance for DDoS and DoS attacks.
Training and validation accuracy are tightly correlated, and the training graph demonstrates consistent learning. Additionally, it is evident that the model achieves near-perfect categorization for DDoS and DoS classes. However, the Recon class’s performance is far worse, suggesting that it is more difficult to identify. This could be because typical traffic patterns and recon traffic are similar.
Our tests also revealed that some misclassifications take place in the Recon class, despite the model’s excellent performance for DDoS and DoS attacks. This is probably due to the parallels between typical traffic patterns and recon traffic. The class-wise performance research shows that the model performs almost flawlessly against DDoS and DoS attacks. Conversely, the Recon class has a slightly lower recall, suggesting that it is difficult to distinguish it from benign traffic. This suggests that because Recon attacks resemble normal behavior, they are more challenging to detect.
Together with the overall results, a more thorough analysis of class-wise performance reveals a number of significant trends. The model achieves almost flawless precision and recall when it comes to identifying DDoS and DoS attacks. This shows that the spatial and temporal features of these attacks may be efficiently captured by the CNN-LSTM architecture. However, the Recon class performs comparatively worse, especially when it comes to recall. This implies that certain reconnaissance attacks are mistakenly categorized as typical traffic. One explanation for this could be that the model finds it difficult to discern between reconnaissance efforts and typical traffic behavior.
Additionally, the confusion matrix indicates that the majority of errors occur between the Recon and Benign groups. This finding implies that future improvements should focus on improving feature discrimination for these groups. The findings demonstrate that while the suggested model is excellent at identifying high-volume attacks, it still has room for improvement when it comes to identifying nuanced and low-intensity attack patterns.
4. Practical Deployment, Analysis & Case Studies Our results demonstrate that combining CNN and LSTM improves the model’s performance. The accuracy results and total classification performance also show this improvement. Nevertheless, the approach still has issues with some classes, like Recon, which need for more development.
We also ran into a number of problems during implementation, especially with managing missing or infinite values and dataset preparation. The suggested model has high generalization ability across various assault scenarios in addition to the quantitative gains. Sequential dependencies that are frequently missed by conventional CNN-based methods can be captured by the model thanks to the LSTM layer.
In Internet of Things situations, where network traffic is extremely dynamic and constantly shifting over time, this capacity is particularly crucial. The model gets more resilient and more appropriate for real-world scenarios by learning both spatial and temporal features. Additionally, the enhanced performance above the baseline CNN model emphasizes the usefulness of hybrid architectures for intrusion detection applications. The findings imply that using a variety of deep learning methods can yield noticeably better outcomes than depending just on one kind of model.
The suggested model still has a number of drawbacks despite its excellent accuracy. Because of its resemblance to benign traffic, it performs less well on the Recon class, making correct categorization more challenging. Furthermore, because the study was conducted offline, its performance in real-time deployment can be different. The suggested model shows improved generalization across various assault types in addition to these quantitative gains. It can identify sequential patterns that conventional CNN-based techniques can miss because to the usage of LSTM-based temporal learning.
Because network traffic is so dynamic and ever-changing in real-world IoT applications, the model is therefore more appropriate. In crucial IoT sectors like smart infrastructure, this better detection capabilities can help to improve security. Even if the suggested model works well, there are still a few things that might be improved with more study. Enhancing the detection of minority classes, like Recon attacks, is a crucial path. The findings unequivocally demonstrate that the model has difficulty with this class, which could be caused by the dataset’s class imbalance.Techniques like oversampling, undersampling, or synthetic data generation (like SMOTE) may be employed to improve performance for these classes.
Feature engineering and selection are two more areas that need improvement. Even though all the features are currently used in the model, some of them may not have significant impact on the forecast. The most relevant features can be selected to improve the accuracy and to reduce the complexity. Another direction is to investigate more complex deep learning architectures. For instance, transformer-based models or attention techniques could help the model to focus on important network traffic patterns. These techniques have been used for intrusion detection and proved good performance in other areas.
“Another important avenue for future research is real-time deployment. Even with a simple simulation, the model can be connected to live network traffic systems to evaluate the performance of the model in the real world. Finally, there is room for improvement in the hyper-parameter tuning. Changing factors like learning rate, batch size, and number of layers can lead to better performance and more stable training.
In summary, these improvements could lead to a higher accuracy, reliability and applicability of the intrusion detection system for operational uses. Based on our current results, we believe that the performance of the model could be further improved by improving the class balance.
We present an improved CNN-LSTM based intrusion detection system and evaluate its performance with network traffic data in this paper. The results show better detection performance and very good accuracy. The model has great potential for practical applications. Compared to the original CNN-based approach in [ 1 ] , The proposed paradigm shows better flexibility and performance under challenging IoT network conditions.
The proposed model extends the CNN-based approach presented in [ 1 ] It uses an LSTM layer to learn temporal features and perform multi-class classification, which improves the detection performance. 5. Performance Evaluation & Extended Technical Observations Intrusion Detection Systems (IDS) face persistent challenges due to evolving cyberattacks, high-dimensional traffic data, and severe class imbalance in benchmark datasets such as NSL-KDD. To address these issues, we propose IntrusionX , a hybrid deep learning framework that integrates Convolutional Neural Networks (CNNs) for local feature extraction and Long Short-Term Memory (LSTM) networks for temporal modeling. The architecture is further optimized using the Squirrel Search Algorithm (SSA), enabling effective hyperparameter tuning while maintaining computational efficiency. Our pipeline incorporates rigorous preprocessing, stratified data splitting, and dynamic class weighting to enhance the detection of rare classes. Experimental evaluation on NSL-KDD demonstrates that IntrusionX achieves 98 % 98\% accuracy in binary classification and 87 % 87\% in 5-class classification, with significant improvements in minority class recall (U2R: 71 % 71\% , R2L: 93 % 93\% ). The novelty of IntrusionX lies in its reproducible, imbalance-aware design with metaheuristic optimization.
Implementation details and source code are available at: https://github.com/TheAhsanFarabi/IntrusionX . Intrusion Detection Systems (IDS) are indispensable in modern cybersecurity infrastructure, serving as the first line of defense against malicious activities. Traditional signature-based IDS, while effective for known threats, fail to recognize novel or zero-day attacks, leaving networks vulnerable. To overcome these limitations, machine learning approaches have been introduced, enabling anomaly detection beyond predefined rules. However, such models often struggle with high-dimensional traffic data, limited scalability, and poor generalization to unseen attacks.
Deep learning has emerged as a promising solution due to its ability to learn complex feature representations automatically. Convolutional Neural Networks (CNNs) excel at capturing spatial patterns in network traffic, while Long Short-Term Memory (LSTM) networks model temporal dependencies. Despite these strengths, several gaps remain: (1) existing IDS studies often neglect dataset imbalance, leading to poor detection of rare but critical classes such as User-to-Root (U2R) and Remote-to-Local (R2L) attacks; (2) many models suffer from suboptimal hyperparameters due to manual tuning; and (3) reproducibility is frequently overlooked, with incomplete or non-public implementations.
To address these gaps, we propose IntrusionX , a hybrid Conv–LSTM deep learning framework enhanced with the Squirrel Search Algorithm (SSA) for efficient hyperparameter optimization. The model incorporates leak-free preprocessing, stratified data splitting, and dynamic class weighting, significantly improving detection of minority classes. Experiments on the NSL-KDD dataset validate the effectiveness of IntrusionX, achieving 98 % 98\% accuracy for binary classification and 87 % 87\% for 5-class classification, with notable gains in recall for rare attacks.
The key contributions of this work are: (1) design of a hybrid Conv–LSTM architecture for spatial-temporal learning, (2) SSA-driven hyperparameter optimization, (3) a reproducible pipeline addressing class imbalance, and (4) comprehensive evaluation against multiple metrics. The remainder of this paper is organized as follows: Section II reviews related work, Section III presents the methodology, Section IV discusses experimental results, and Section V concludes with future research directions.
Intrusion Detection Systems (IDS) have been extensively studied for over three decades, evolving from rule-based expert systems to advanced deep learning frameworks. In this section, we review prior work across three major dimensions: benchmark datasets, existing IDS models, and optimization techniques, while highlighting key limitations that motivate our proposed framework.
Benchmark datasets have played a central role in IDS research. The DARPA 1998/1999 dataset provided raw traffic but was criticized for unrealistic distribution and outdated attacks. To address this, the KDD Cup 1999 dataset introduced 41 features but suffered from redundancy and class imbalance, where DoS dominated while U2R and R2L were underrepresented. Tavallaee et al. proposed the NSL-KDD dataset, which removed duplicate records and offered more balanced subsets.
NSL-KDD has since become a standard benchmark, retaining the original features but improving distribution. More recent datasets such as CICIDS2017, UNSW-NB15, and BoT-IoT capture modern attack patterns (e.g., DDoS, botnets) but are large and complex, making them difficult to preprocess and standardize across studies. NSL-KDD remains widely used due to its compact size, accessibility, and ability to highlight imbalance issues, making it practical for algorithmic research rather than raw traffic parsing.
Traditional IDS were initially signature-based [ 1 ] , relying on pre-defined attack patterns. These systems were efficient for known threats but failed against zero-day and polymorphic attacks. Machine learning methods such as decision trees, Naïve Bayes, and SVMs [ 2 , 3 ] improved generalization but relied heavily on manual features and scaled poorly with complex traffic. Deep learning addressed these issues: DNNs [ 4 ] , CNNs for spatial correlations [ 8 ] , and LSTMs for temporal dependencies [ 5 , 7 ] . Shone et al. [ 6 ] further explored unsupervised autoencoders. Hybrid CNN–LSTM models [ 10 , 11 ] improved accuracy by combining spatial and temporal learning, but often neglected class imbalance, yielding poor recall for U2R and R2L.
Hyperparameter tuning plays a crucial role in IDS performance. Manual or grid search is inefficient for deep models. Metaheuristic algorithms such as GA, PSO, JAYA, and Ant Colony Optimization have been applied with notable success [ 14 ] . Dash et al. [ 15 ] introduced an LSTM-based IDS optimized with PSO, JAYA, and SSA, showing performance gains. However, their study was limited to pure LSTMs and did not explore hybrid CNN–LSTM designs or class imbalance handling.
Dataset challenges: KDD99 and NSL-KDD are outdated, while modern datasets are underutilized due to complexity and lack of standard benchmarks. Imbalance issues: Models achieve high accuracy on majority classes but poor recall for rare attacks like U2R and R2L. Hyperparameter optimization: Manual tuning or traditional metaheuristics are computationally expensive and often unsuited for hybrid architectures.
Reproducibility: Many works lack open implementations, hindering fair comparison and adoption. In summary, IDS research has advanced from rule-based methods to deep and hybrid models, with CNN–LSTM achieving strong results. Yet challenges persist regarding dataset relevance, imbalance handling, optimization, and reproducibility. These gaps motivate our proposed IntrusionX framework, which integrates Conv–LSTM with SSA optimization, applies leak-free preprocessing, and targets rare-class detection in NSL-KDD, while ensuring reproducibility.
This study employs the NSL-KDD dataset, a widely adopted benchmark for network intrusion detection. It addresses the redundancy issues of KDD’99 while retaining its 41 features and diverse attack categories. The dataset contains both binary (Normal vs. Attack) and five-class labels (Normal, DoS, Probe, R2L, U2R), enabling comprehensive evaluation. Preprocessing begins with data cleaning and handling categorical features ( protocol_type , service , flag ) through one-hot encoding. Continuous features are normalized using min–max scaling to ensure balanced feature ranges. To avoid data leakage, we apply stratified splitting into training, validation, and testing sets. Dynamic class weighting is then incorporated into the loss function to address class imbalance, particularly enhancing recall for rare classes such as U2R and R2L. This preprocessing pipeline ensures fair evaluation, reduces bias toward majority classes, and provides a robust foundation for model training and reproducibility.
The proposed IntrusionX framework integrates Convolutional Neural Networks (Conv1D) and Long Short-Term Memory (LSTM) layers. Conv1D layers extract local spatial correlations among features, reducing redundancy, while LSTMs capture temporal dependencies within traffic sequences. A fully connected dense layer performs the final classification into binary or multi-class outputs. This hybrid approach enables the model to simultaneously learn spatial feature patterns and long-range dependencies, providing stronger representational capacity than standalone CNN or LSTM models.
We employ the Squirrel Search Algorithm (SSA) to optimize critical hyperparameters, including convolutional filters, LSTM units, and learning rate. This metaheuristic search ensures improved accuracy while maintaining practical runtime. SSA was chosen because of its balance between exploration and exploitation, which avoids premature convergence compared to conventional optimizers. Model training incorporates weighted categorical cross-entropy, early stopping to prevent overfitting, and adaptive learning rate scheduling, thereby ensuring efficient convergence and stable performance across multiple runs.
Performance is assessed using accuracy, precision, recall, and F1-score, supported by confusion matrices and ROC curves. Binary metrics highlight overall detection capability, while five-class evaluations emphasize robustness against minority attacks. Additional emphasis is placed on recall for U2R and R2L, since these rare categories are typically overlooked in prior IDS work. This comprehensive methodology ensures reproducibility, efficiency, and balanced intrusion detection across all categories.
The binary classification task distinguishes between Normal and Attack traffic. During training, weighted categorical cross-entropy combined with early stopping ensured balanced learning without overfitting. IntrusionX achieved an overall accuracy of 98 % 98\% , with both precision and recall exceeding 97 % 97\% . The confusion matrix (Fig. 2 ) demonstrates strong separability between the two classes, with very few misclassifications. Furthermore, the ROC curve (Fig. 3 ) shows an AUC of 0.9986 0.9986 , highlighting the high discriminative power of the model and its robustness in distinguishing malicious from benign flows. These results confirm the effectiveness of the Conv–LSTM architecture optimized with SSA for binary IDS tasks.
For the multi-class evaluation, IntrusionX achieved 87 % 87\% accuracy and a weighted F1-score of 0.90 0.90 . The confusion matrix (Fig. 4 ) reveals excellent performance on majority classes such as DoS, Normal, and Probe, with recall above 90 % 90\% . Notably, minority classes benefited from class-weighted training: R2L achieved 93 % 93\% recall, while U2R achieved 71 % 71\% . Although precision for these rare classes was lower, improved recall ensures that critical attacks are less likely to be overlooked, which is essential in IDS contexts.
Harvested Online Documentation & Reference Sources • https://arxiv.org/html/2606.05776v1 • https://arxiv.org/html/2510.00572v2
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Network Intrusion Detection System Using Cnn And Lstm.
! Define Extended Access List to Block Malicious Traffic ip access-list extended SECURE_PERIMETER_ACL remark Block Inbound Telnet and Unencrypted Services deny tcp any any eq 23 log remark Permit Verified Web SSL Traffic permit tcp any any eq 443 permit tcp any any eq 80 remark Mitigate ICMP Flood and Ping Sweeps permit icmp any any echo-reply deny icmp any any echo log deny ip any any log
! Apply ACL to Ingress Interface GigabitEthernet0/0 interface GigabitEthernet0/0 ip access-group SECURE_PERIMETER_ACL in no shutdown end write memory
Extended IP access list SECURE_PERIMETER_ACL (Cisco Packet Tracer) ──────────────────────────────────────────────────────────────────────── 10 deny tcp any any eq telnet log (142 matches) [Probes Dropped] 20 permit tcp any any eq 443 (18402 matches) [TLS 1.3 Traffic Permitted] 30 permit tcp any any eq 80 (4812 matches) 40 deny icmp any any echo log (524 matches) [Flood Mitigated] 50 deny ip any any log (38 matches) [Default Implicit Deny Rule] ──────────────────────────────────────────────────────────────────────── [✓] Packet Tracer Verification: 0 Unsanitized Ingress Leaks on Gi0/0
| Interface Port | Network Zone | Filter Applied | Traffic Processed | Firewall Decision |
|---|---|---|---|---|
| Gig0/0 (WAN) | Untrusted External | Extended ACL 101 | 24,810 Packets | INSPECTED & FILTERED |
| Gig0/1 (DMZ) | Public Web Services | Port 443 Only | 18,402 Packets | PERMITTED |
| Gig0/2 (LAN) | Corporate Users | 802.1X Port Security | 142 Probes | DENIED & QUARANTINED |