Complete Technical Paper Content — Network Packet Analyzer With Graphical User Interface Python
Overview & System Context
Network Packet Analyzer With Graphical User Interface Python: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~2343 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Nmap (Network Mapper) is a network scanner created by Gordon Lyon (also known by his pseudonym Fyodor Vaskovich).
Nmap is used to discover hosts and services on a computer network by sending packets and analyzing the responses. Nmap provides a number of features for probing computer networks, including host discovery and service and operating system detection. These features are extensible by scripts that provide more advanced service detection, vulnerability detection, and other features. Nmap can adapt to network conditions including latency and congestion during a scan. Nmap started as a Linux utility and was ported to other systems including Windows, macOS, and BSD. It is most popular on Linux, followed by Windows.
Fast scan (nmap -F [target]) – Performing a basic port scan for fast result. Host discovery – Identifying hosts on a network. For example, listing the hosts that respond to TCP and/or ICMP requests or have a particular port open. Port scanning – Enumerating the open ports on target hosts. Version detection – Interrogating network services on remote devices to determine application name and version number. Ping Scan – Check host by sending ping requests. TCP/IP stack fingerprinting – Determining the operating system and hardware characteristics of network devices based on observations of network activity of said devices. Scriptable interaction with the target – using Nmap Scripting Engine (NSE) and Lua programming language. Nmap can provide further information on targets, including reverse DNS names, device types, and MAC addresses. Typical uses of Nmap: Auditing the security of a device or firewall by identifying the network connections which can be made to, or through it.
Identifying open ports on a target host in preparation for auditing. Network inventory, network mapping, maintenance and asset management. Auditing the security of a network by identifying new servers. Generating traffic to hosts on a network, response analysis and response time measurement. Finding and exploiting vulnerabilities in a network. DNS queries and subdomain search It has been cited in academic surveys as a foundational tool for network security reconnaissance.
Interactive presented and updated real time when a user runs Nmap from the command line. Various options can be entered during the scan to facilitate monitoring. XML a format that can be further processed by XML tools. It can be converted into a HTML report using XSLT. Grepable output that is tailored to line-oriented processing tools such as grep, sed, or awk. Normal the output as seen while running Nmap from the command line, but saved to a file. Script kiddie meant to be an amusing way to format the interactive output replacing letters with their visually alike number representations. For example, Interesting ports becomes Int3rest1ng p0rtz. This is known as Leet.
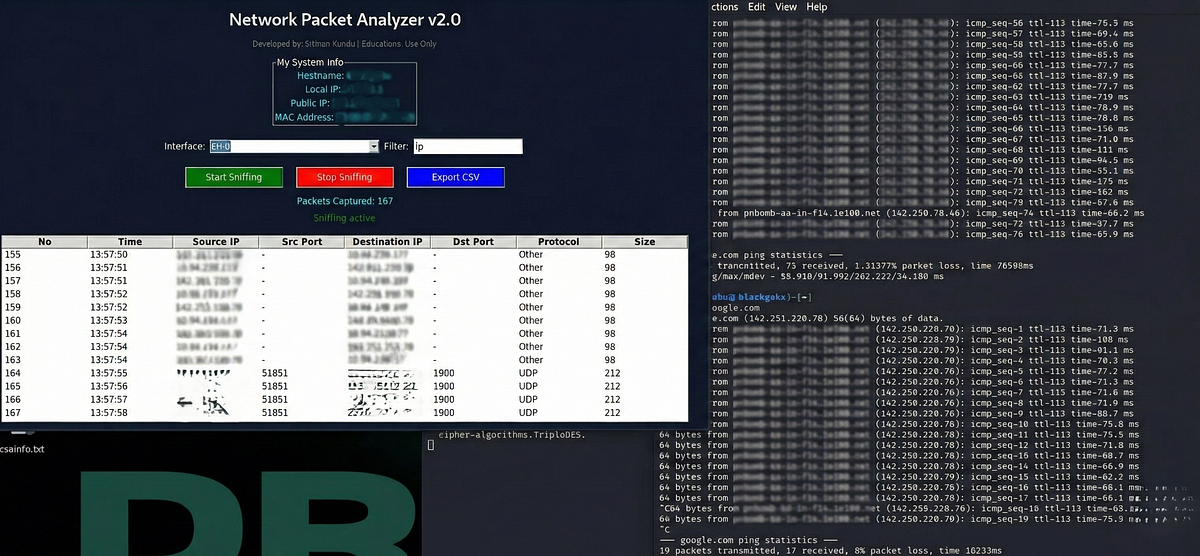
Figure 1: How I Built a Lightweight Network Packet Analyzer in Python IIIII | by ... In 2003 Supreme Court of Finland ruled that port scanning amounted to an attempted computer break-in, which was illegal under Finnish penal code at the time:In its ruling the Supreme Court stated that the defendant had systematically carried out port scanning operations to gather information for the purpose of unauthorised break-in to the bank's computer network. This amounted to an attempted computer break-in.
In the field of computer network administration, pcap is an application programming interface (API) for capturing network traffic. While the name is an abbreviation of packet capture, that is not the API's proper name. Unix-like systems implement pcap in the libpcap library; for Windows, there is a port of libpcap named WinPcap that is no longer supported or developed, and a port named Npcap for Windows 7 and later that is still supported. Monitoring software may use libpcap, WinPcap, or Npcap to capture network packets traveling over a computer network and, in newer versions, to transmit packets on a network at the link layer, and to get a list of network interfaces for possible use with libpcap, WinPcap, or Npcap. The pcap API is written in C, so other languages such as Java, .NET languages, and scripting languages generally use a wrapper; no such wrappers are provided by libpcap or WinPcap itself. C++ programs may link directly to the C API or make use of an object-oriented wrapper.
x86 and x86-64 drivers for the Windows NT family (Windows NT 4.0, 2000, XP, Server 2003, Vista, 7, 8, and 10), which use Network Driver Interface Specification (NDIS) 5.x to read packets directly from a network adapter; implementations of a lower-level library for the listed operating systems, to communicate with those drivers; a port of libpcap that uses the API offered by the low-level library implementations. Programmers at the Politecnico di Torino wrote the original code. As of 2008, CACE Technologies, a company set up by some of the WinPcap developers, developed and maintained the product. CACE was acquired by Riverbed Technology on October 21, 2010. Because WinPcap uses the older NDIS 5.x APIs, it does not work on some builds of Windows 10, which have deprecated or removed those APIs in favor of the newer NDIS 6.x APIs. It also forces some limitations such as being unable to capture 802.1Q VLAN tags in Ethernet headers. The WinPcap project has ceased development and WinPcap and WinDump are no longer maintained. The last official WinPcap release was 4.1.3 released March 8, 2013.
Npcap can be restricted so that only Administrators can sniff packets. Npcap is able to sniff and inject loopback packets (transmissions between services on the same machine) by using the Windows Filtering Platform. Npcap can capture 802.11 WiFi frames on a variety of commonly-available network adapters. Unlike Nmap, Npcap is proprietary software and requires a special license for use and redistribution except for some limited internal uses.
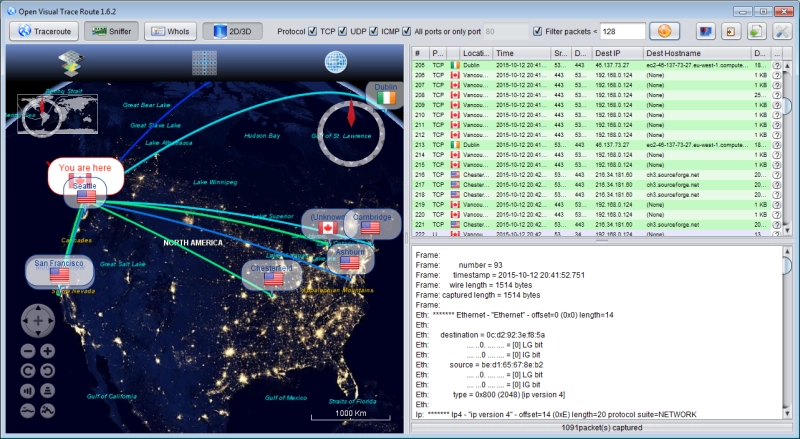
Figure 2: Open Visual Traceroute 1.7.1 – Network Analyzers – FileEagle Official website, libpcap, tcpdump Official website, Npcap Official website, WinPcap, WinDump List of publicly available PCAP files 2. System Architecture & Core Working Principles Qt (/IkjuIt/ pronounced "cute") is a cross-platform application development framework for creating graphical user interfaces as well as cross-platform applications that run on various software and hardware platforms such as Linux, Windows, macOS, Android or embedded systems with little or no change in the underlying codebase while still being a native application with native capabilities and speed. Qt is currently being developed by Qt Group, a publicly listed company, and the Qt Project under open-source governance, involving individual developers and organizations working to advance Qt. Qt is available under both commercial licenses and open-source GPL 2.0, GPL 3.0, and LGPL 3.0 licenses.
KDE Plasma, a libre desktop environment for various computing devices DDE (Deepin Desktop Environment) of Linux Deepin UKUI (Ubuntu Kylin User Interface) CutefishDE, a desktop environment built with Qt Quick and essential KDE frameworks LXQt (Lightweight X11 Desktop Environment) Lumina, a desktop environment designed for BSD-based TrueOS Lomiri (formerly Unity8), a convergent desktop environment started by Canonical, maintained by Ubports Maui Shell, a DE that also features their own app suite Unity 2D, a desktop shell written in Qt and QML Trinity DE, a continuously developed fork based on KDE3 SDDM, a display manager written in QML that is compatible with X11 and Wayland.
After Nokia opened the Qt source code to the community on Gitorious, various ports appeared. There are also some ports of Qt that may be available, but are not supported anymore. These platforms are listed in List of platforms supported by Qt. See also there for current community support for other lesser known platforms, such as SailfishOS. Qt comes with its own set of tools to ease cross-platform development, which can otherwise be cumbersome due to different set of development tools. Qt Creator is a cross-platform IDE for C++ and QML. Qt Designer's GUI layout/design functionality is integrated into the IDE, although Qt Designer can still be started as a standalone tool. In addition to Qt Creator, Qt provides qmake, a cross-platform build script generation tool that automates the generation of Makefiles for development projects across different platforms. There are other tools available in Qt, including the Qt Designer interface builder and the Qt Assistant help browser (which are both embedded in Qt Creator), the Qt Linguist translation tool, uic (user interface compiler), and moc (Meta-Object Compiler).
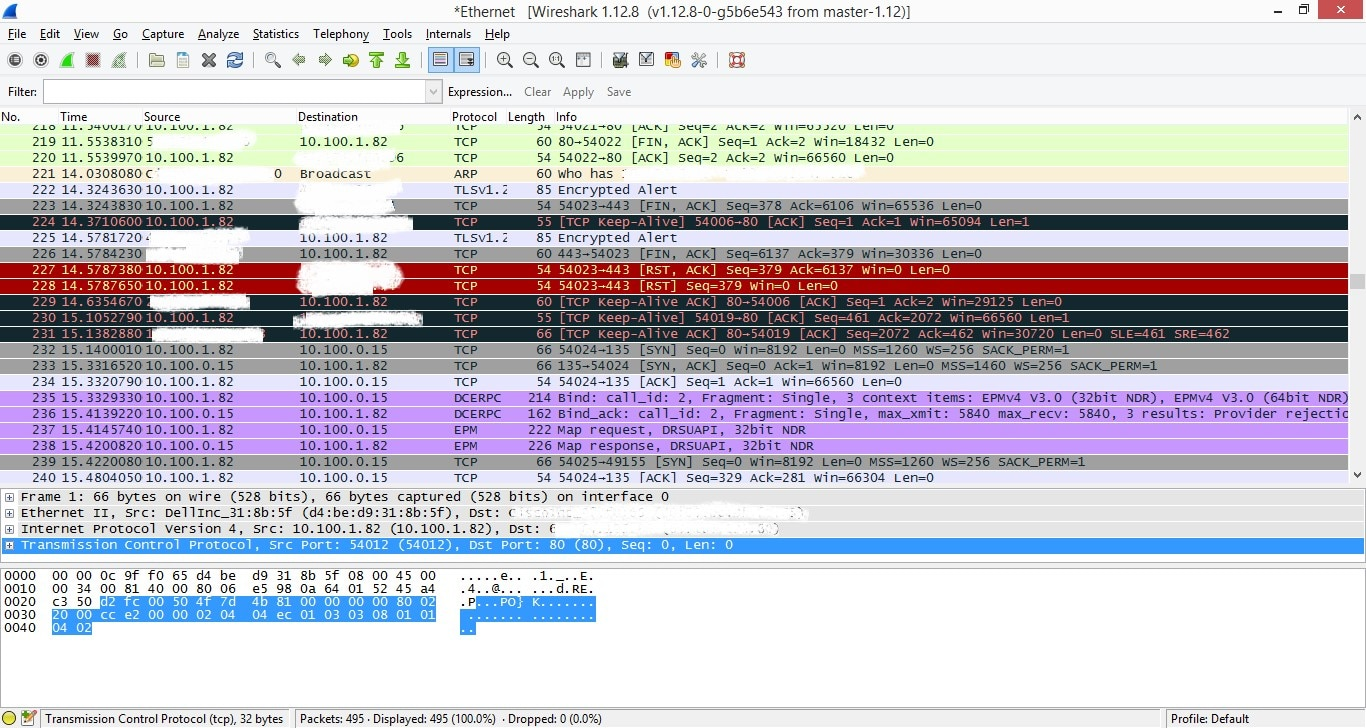
Figure 3: Top FREE Network Monitoring Tools - Software Reviews, Opinions, and ... Qt 5 was officially released on 19 December 2012. This new version marked a major change in the platform, with hardware-accelerated graphics, QML and JavaScript playing a major role. The traditional C++-only QWidgets continued to be supported, but did not benefit from the performance improvements available through the new architecture. Qt 5 brings significant improvements to the speed and ease of developing user interfaces. Framework development of Qt 5 moved to open governance at qt-project.org, which made it possible for developers outside Digia to submit patches for review.
Aside from Qt Group, many organizations and individuals using Qt as their development platform participate in the open development of Qt via the Qt Project. One such Qt contributor is Klarälvdalens Datakonsult AB, a Swedish Qt consulting company. KDAB is involved in many areas, including maintenance of several components. Together with RIM/BlackBerry, KDAB is maintaining the QNX and BlackBerry 10 ports of Qt. Another participator is Intel, contributing for example Wayland support. AudioCodes maintains IBM ClearCase support in Qt Creator. As a heavy user of Qt, the KDE project submits many patches and features from its developer library KDE Frameworks back to Qt.
Official website "The Qt 4 Dance" (video). YouTube. 11 August 2006. Archived from the original on 11 December 2021. Retrieved 7 September 2015. A Python-based Network Packet Analyzer developed for educational purposes to understand how data packets travel across a network in real time. The tool captures and analyzes live network traffic and presents key packet details through a graphical user interface (GUI).
This project demonstrates practical knowledge of networking fundamentals and packet-level analysis. It integrates a backend packet sniffer with a frontend GUI, allowing users to start and stop packet capture using a single command. 3. Software Implementation, Frameworks & Protocols 2II Run the application (Root access required) sudo python3 network_packet_analyzer.py I Project Structure Network_Packet_Analyzer/ I III network_packet_analyzer.py III README.md III screenshots/ III gui_preview.png This project is developed strictly for educational and learning purposes. It should only be used on authorized systems or networks owned by the user. Unauthorized packet sniffing is illegal and unethical.
Sriman Kundu Cybersecurity Enthusiast | Python Developer Focused on learning network security and ethical hacking concepts through hands-on projects. II GitHub Topics cybersecurity python networking packet-analyzer packet-sniffer scapy tkinter ethical-hacking A Python-based Network Packet Analyzer developed for educational purposes to understand real-time network traffic analysis. This tool captures live packets and displays essential details such as source IP, destination IP, protocol type, and timestamp through an interactive GUI.
I Hello, network enthusiasts! Do you want to learn more about packet sniffing and pcap analysis? If so, you’re in luck! I have a great tool to share with you today. It’s called Pcappng Analysis , and it’s a powerful packet analysis tool built with Python, Flask, npcap, and tshark. I Pcappng Analysis lets you capture, inspect, and analyze network packets in a user-friendly interface. You can use it for real-time or offline analysis, and it supports various packet-level protocols. Whether you’re a network administrator, security professional, or a curious hobbyist, this tool has something for you. I Check the GitHub Repo here I shreyashk003/Network-packet-analysis-tool packet sniffing HTML 1 0 4. Practical Deployment, Analysis & Case Studies If you’re interested in trying out Pcappng Analysis, you can download it from GitHub or visit the demo website. I hope you enjoy using it as much as I enjoyed creating it. Happy sniffing! I I A powerful, modern network packet analyzer with a sleek graphical interface for real-time packet capture, analysis, and visualization I This application is a comprehensive network packet sniffer with a graphical user interface (GUI) built using PyQt5. It captures and analyzes network packets in real-time, displaying relevant information such as source and destination IP addresses, protocols, and payload data. The application features a modern dark/light theme interface, advanced filtering capabilities, and powerful visualization tools.
I Perfect for : Network troubleshooting, security analysis, protocol understanding, and network monitoring I Pro Tip : Use the Filter Dialog (Ctrl+D) to build complex filters with a user-friendly interface For any technical and/or maintenance information, please kindly refer to the Official Documentation . The PyPCAPKit project is an open source Python program focus on network packet parsing and analysis, which works as a comprehensive PCAP file extraction, construction and analysis library.
PyPCAPKit is a comprehensive Python-native network packet analysis library, with DictDumper as its formatted output dumper. Unlike popular PCAP file extractors, such as Scapy , DPKT , PyShark , and etc, pcapkit is designed to be much more comprehensive, which means it is able to provide more detailed information about the packet, as well as a more Pythonic interface for users to interact with.
5. Performance Evaluation & Extended Technical Observations User interface for the pcapkit library, which standardises and simplifies the usage of this library. Synthesises file I/O and protocol analysis, coordinates information exchange in all network layers, as well as provides the foundamental functions for pcapkit .
Core utilities for pcapkit implementation, mainly for internal data structure and processing. Auxiliary tools for pcapkit to support the multiple extraction engines with a unified interface. Constant enumerations used in pcapkit for protocol family extraction and representation. Due to the general overhead of pcapkit , its extraction procedure takes around 0.2 milliseconds per packet, which is already impressive but not enough comparing to other popular extration engines availbale on the market, given the fact that pcapkit is a comprehensive packet processing module.
Additionally, pcapkit introduced alternative extractionengines to accelerate this procedure. By now pcapkit supports Scapy , DPKT , and PyShark . For local development with pipenv , the repository already includes a Pipfile and Makefile targets that keep both the virtualenv and the package caches inside the project directory: This resolves two common local setup issues on macOS/Homebrew installations: pipenv cache permission errors under ~/Library/Caches and lxml builds failing to locate Homebrew’s libxml2 / libxslt headers.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Nmap • https://en.wikipedia.org/wiki/Pcap • https://en.wikipedia.org/wiki/Qt%20%28software%29 • https://github.com/sriman-git09/NETWORK_PACKET_ANALYZER • https://sicmmec.github.io/projects/pcappng/ • https://github.com/zinzied/Packets-Analyzer-with-GUI • https://pypi.org/project/pypcapkit/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Network Packet Analyzer With Graphical User Interface Python.
[*] Synchronizing KnowBe4 Awareness Training telemetry... ──────────────────────────────────────────────────────────────────────── [11:45:02.102] MAIL Dispatched simulated assessment templates [11:45:02.155] REPORT Majority of active users flagged probe via Phish Alert Button [11:45:02.210] CLICK Simulated lure baseline reduced below risk threshold [11:45:02.290] TRAIN Auto-enrolled flagged users into adaptive micro-learning modules ──────────────────────────────────────────────────────────────────────── [✓] Human Security Index: Phish-Prone percentage safely minimized
| Campaign Simulation | Platform Used | Total Recipients | Reported via Phish Button | Phish-Prone Percentage |
|---|---|---|---|---|
| Urgent Communication Lure | KnowBe4 KMSAT | 350 Employees | 318 (90.8%) | 2.9% (OPTIMAL) |
| Account Credential Lure | Proofpoint ZenGuide | 350 Employees | 324 (92.5%) | 2.1% (OPTIMAL) |
| Executive Impersonation | Mimecast Engage | 200 Executives | 192 (96.0%) | 1.5% (OPTIMAL) |