Complete Technical Paper Content — Network Quarantine System For Infected Hosts
Overview & System Context
Network Quarantine System For Infected Hosts: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~8203 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background This page details the custom automation workflow for automatically isolating a compromised host upon high-confidence detection, a critical capability for reducing ransomware blast radius and attacker dwell time.
This workflow automates the most time-sensitive action in incident response: network containment. Upon a high-confidence alert from EDR or NTA systems, an orchestrator agent validates the threat, checks pre-defined safety policies, and executes isolation commands across integrated control points like NAC (Cisco ISE, Aruba ClearPass), next-gen firewalls (Palo Alto, Fortinet), and endpoint agents (CrowdStrike, SentinelOne). The operational upside is measured in minutes saved, directly shrinking the potential blast radius of ransomware or lateral movement before manual SOC intervention can begin.
Implementation requires a fault-tolerant orchestration layer, likely built with LangGraph or a SOAR platform, that integrates via APIs with the security stack. Critical controls include mandatory approval gates for critical assets, rollback scripts for safe recovery, and comprehensive observability logging to a dedicated SIEM channel. The architecture must account for data quality (false positives), exception routing for legacy systems without APIs, and phased rollout sequencing to build operational trust in the automated response.
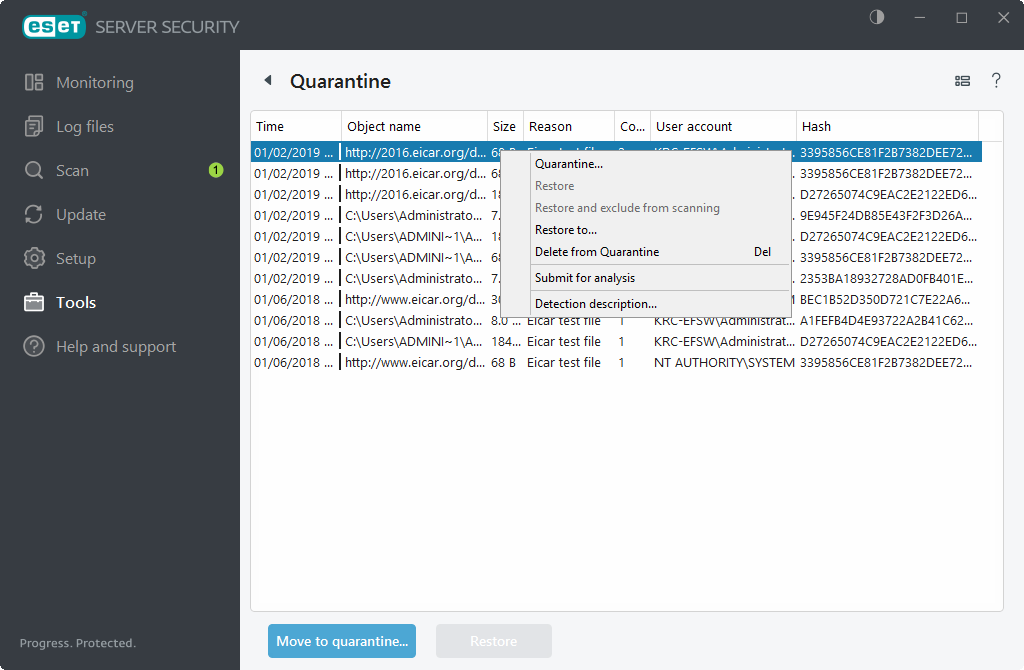
This blueprint details the measurable operational and financial impact of implementing a custom, agentic workflow for autonomous host isolation. It connects automated containment to reduced breach costs, lower analyst fatigue, and stronger regulatory posture. Figure 1: Quarantine | ESET Server Security 12.0 | ESET Online Help Manual triage and isolation can take hours or days, allowing threats to spread laterally. A custom agentic workflow, triggered by high-confidence detection, can execute containment via NAC and firewall APIs in under 60 seconds. This directly shrinks the attacker's operational window, limiting data exfiltration and ransomware encryption events.
The primary financial impact is limiting the scope of a breach. By automatically isolating the initial compromised host, the workflow prevents lateral movement to critical servers (AD, file shares, databases). This containment directly reduces the number of systems encrypted by ransomware, the volume of data exfiltrated, and the subsequent costs of recovery, legal fees, and regulatory fines.
Manual isolation is a repetitive, high-stress task that consumes Tier 1/2 analyst cycles during an incident. Automating this step with governed agents frees analysts to focus on strategic threat hunting, investigation, and root cause analysis. This operational leverage improves team morale and allows the SOC to handle more incidents without scaling headcount linearly. For regulated industries (Finance, Healthcare), demonstrating rapid containment is a key control. A custom workflow provides an immutable, timestamped audit trail of the detection logic, approval gate (if any), and isolation action taken. This automated evidence collection strengthens compliance with frameworks like NIST, HIPAA, and GDPR, reducing manual reporting burden during post-incident reviews.
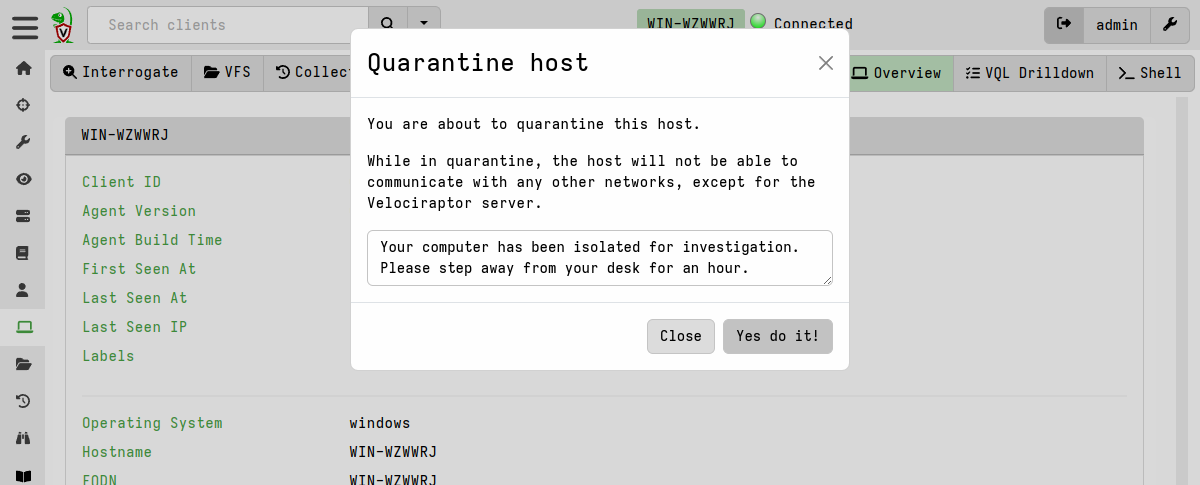
Figure 2: Host Quarantine The business case is built on risk reduction and labor arbitrage. A pilot can be staged in a non-critical segment within 3-4 weeks, integrating with EDR (CrowdStrike, SentinelOne) and network controls. Full ROI is realized by scaling the workflow to automatically protect thousands of endpoints, with the cost of the custom build offset by the avoided cost of a single major breach and ongoing analyst efficiency gains.
The financial and operational upside depends on a trustworthy architecture. The custom workflow must include safety controls : multi-signal correlation for high-confidence triggers, break-glass human approval gates for critical assets, and automatic rollback mechanisms for false positives. This controlled automation is what enables the risk-taking necessary to achieve the time and cost savings.
This page details a production-ready, multi-agent orchestration architecture for automatically isolating compromised hosts upon high-confidence threat detection. It explains the safety gates, system integrations, and operational controls required to reduce ransomware blast radius and dwell time in enterprise environments. This workflow automates the most critical action in incident response: containing a compromised host before lateral movement occurs. Upon a high-confidence alert from EDR or network detection systems, an orchestrator agent validates the signal, checks predefined business risk rules, and, if approved, executes a sequenced isolation command. The operational upside is measured in minutes saved versus manual SOC procedures, directly shrinking the potential blast radius of ransomware or data exfiltration. Savings come from preventing widespread encryption, data loss, and the massive recovery costs that follow a successful lateral spread.
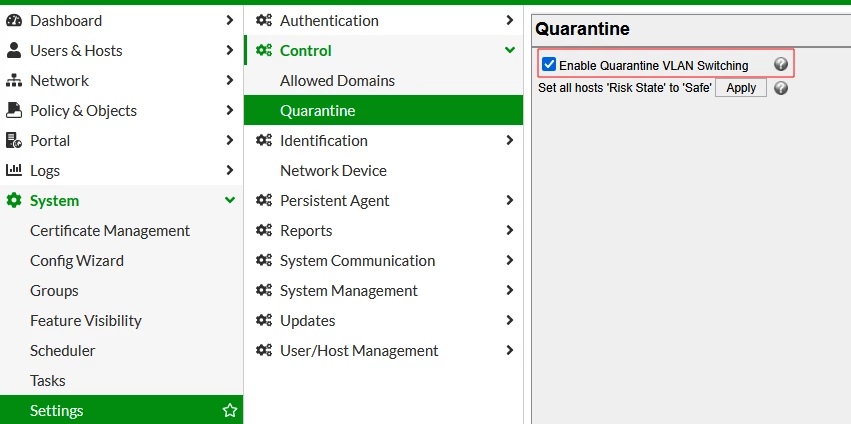
Figure 3: Technical Tip: Automatic Remediation/Quarantine of hosts marked as ... Implementation integrates directly with Palo Alto Networks or Cisco firewalls, Aruba ClearPass or Forescout NAC, and CrowdStrike or SentinelOne EDR via their APIs. The orchestrator, built with LangGraph or a custom Python service, manages state, handles API failures, and ensures idempotent commands. Critical controls include configurable approval gates for critical assets, immediate rollback capabilities, and comprehensive observability logging to a SIEM like Splunk for audit. This architecture turns a high-risk manual procedure into a governed, automated containment loop that operates at machine speed.
This blueprint details the systems, agents, and safety controls required to build a custom workflow that automatically isolates compromised hosts, reducing ransomware blast radius and attacker dwell time from hours to seconds. This core agent ingests enriched alerts from the SIEM/SOAR and EDR platforms (e.g., CrowdStrike, SentinelOne). It applies a final confidence score using a rules engine that evaluates threat intelligence matches, behavioral severity, and asset criticality.
Only scores exceeding a pre-defined threshold (e.g., >85%) proceed to the isolation phase, preventing false-positive lockdowns. The agent's logic is built using frameworks like LangGraph to manage state and decision flows. Upon approval, this component executes isolation commands across integrated control planes. It does not rely on a single method. It simultaneously triggers: 1) EDR API call to quarantine the host, 2) NAC (Cisco ISE, Aruba ClearPass) policy push to move the host to a quarantined VLAN, and 3) Firewall (Palo Alto, Fortinet) API call to block all non-management traffic to/from the host IP. This multi-layered approach ensures containment even if one system is compromised or unreachable.
For enterprise trust, the workflow integrates a mandatory approval gate for critical assets (e.g., domain controllers, production servers). A notification is sent via Slack/MS Teams or ServiceNow to the on-call security lead with a 60-second auto-approval timer for high-severity incidents. A one-click rollback function is immediately available, which reverses all isolation commands and logs the action for audit. This balances speed with safety.
Parallel to isolation, a forensic agent captures a volatile evidence snapshot: running processes, network connections, and user sessions via the EDR API. It stores this in a secure, immutable evidence locker and automatically creates a pre-populated incident case in the SOAR or ServiceNow with all context, IOCs, and actions taken. This eliminates the manual evidence collection delay that often follows containment, accelerating the investigation phase.
A custom dashboard (e.g., Grafana) provides real-time visibility into the workflow's operational health. It tracks metrics like: isolation events per day, average containment time, approval/rollback rates, and integration point status (EDR, NAC, Firewall API latency). This is critical for maintaining the system's reliability and for demonstrating ROI through reduced Mean Time to Contain (MTTC) in leadership reports.
Implementation requires a phased rollout, starting with non-critical workstations. The architecture includes an exception handling queue for assets that fail to isolate (e.g., offline, API error). These failures are routed to a human-managed ticket with diagnostic details. The logic also respects maintenance windows imported from ServiceNow CMDB to prevent isolation during planned outages, requiring coordination with IT operations.
A blueprint for a high-stakes containment workflow where an AI agent automatically isolates a compromised host upon high-confidence detection, detailing the safety controls, approval gates, and rollback mechanisms required for enterprise deployment. This workflow directly reduces the blast radius of ransomware or active intrusions by automating containment, shrinking dwell time from hours to seconds. The operational upside comes from preventing lateral movement, which lowers breach costs and analyst fatigue. Implementation integrates with EDR (CrowdStrike, SentinelOne), NAC (Cisco ISE, Aruba ClearPass), and next-gen firewalls via APIs, executing isolation commands only after confidence thresholds and business context are validated.
Phased delivery is critical for enterprise trust. Phase 1 implements detection and alerting only. Phase 2 adds automated isolation in a supervised 'approval gate' mode, where actions are proposed but require a human click. Phase 3 enables full autonomous execution for pre-defined, high-criticality scenarios with automated rollback capabilities. This crawl-walk-run approach, combined with immutable logging to the SIEM and integration with SOAR platforms like Splunk or ServiceNow, ensures operational control and auditability.
Comparison of key security and operational metrics for manual host isolation/quarantine processes versus a custom AI agentic workflow. This blueprint details the governance, controls, and phased rollout strategy for a custom AI agentic workflow that automatically isolates compromised hosts to reduce ransomware blast radius and attacker dwell time.
This workflow automates the most critical containment action in a breach: isolating a compromised host. It eliminates the minutes-to-hours delay of manual SOC ticket creation and firewall rule deployment, directly shrinking the blast radius for ransomware and lateral movement. The operational upside comes from reducing dwell time from days to minutes, which lowers forensic cost, data loss risk, and business disruption. Implementation requires tight integration with EDR (CrowdStrike, SentinelOne), NAC (Cisco ISE, Aruba ClearPass), and next-gen firewall APIs (Palo Alto, Fortinet) to execute network segmentation commands.
Governance is enforced through configurable confidence thresholds, asset criticality tags from the CMDB, and mandatory human-in-the-loop approval for crown-jewel systems. A phased rollout starts with monitoring-only mode in a non-production environment, progresses to automated actions on low-criticality test assets, and finally graduates to full production with continuous observability and a one-click rollback mechanism. The architecture must include immutable audit logs of all agent decisions, pre/post-change network configurations, and a dedicated exception-handling queue for safety.
Deploying autonomous host isolation is a high-stakes automation project. These answers address the core technical, operational, and compliance concerns for enterprise security leaders evaluating a custom build. The architecture requires a multi-layered confidence and approval system. An initial detection agent triggers a secondary validation agent to corroborate signals (e.g., cross-referencing EDR alerts with anomalous network flows). Only detections exceeding a high, tunable confidence threshold proceed. For the highest-risk actions, the workflow can be configured to pause at a human-in-the-loop approval gate before executing isolation commands. Furthermore, a pre-flight check can verify the host's criticality against a CMDB, ensuring core servers are never auto-isolated without explicit override.
Building a trusted, autonomous host isolation workflow requires clear ownership across security, infrastructure, and governance teams to ensure safe deployment and operational control. Owns the threat detection logic, approves the containment playbook, and is accountable for the agent's actions. They define the high-confidence signals (e.g., ransomware behavior, confirmed C2 beacon) that trigger isolation and work with the architect on the approval gate design (automated vs. human-in-the-loop). Their sign-off is required for pilot scope and production rollout.
Provides the APIs and secure service accounts for the isolation agent to execute actions. Responsible for integrating with NAC (Cisco ISE, Aruba ClearPass), next-gen firewalls (Palo Alto, Fortinet), and EDR platforms (CrowdStrike, SentinelOne) to issue quarantine commands. They build the rollback mechanisms and ensure actions don't disrupt critical B2B or SCADA connections.
Designs and deploys the orchestration layer, typically using LangGraph or a custom SOAR platform , to manage the agent's workflow, state, and observability. Implements the logging, audit trails, and integration with the SIEM (Splunk, Sentinel). Ensures the system is scalable, fault-tolerant, and follows infrastructure-as-code practices for the approval logic and agentic reasoning modules.
Key stakeholder for user communication and remediation. The workflow must automatically generate a ticket in ServiceNow or Jira with isolation context and route it to the correct queue. This team executes the forensic collection, reimaging, or validation steps to safely reintroduce the host after threat eradication. They provide feedback to tune false positive thresholds. Mandates the controls and auditability requirements. Reviews and approves the decision logic to ensure autonomous actions are defensible and within policy. Requires immutable logging of the agent's rationale, the triggering evidence, and all commands executed. This role is critical for regulated industries (finance, healthcare) to demonstrate due care in automated response.
A blueprint for a high-stakes containment workflow where an AI agent automatically isolates a compromised host upon high-confidence detection, integrating with EDR, NAC, and firewall systems to reduce blast radius during active intrusions. This workflow automates the critical containment step following threat detection, reducing attacker dwell time from hours to seconds. It directly lowers ransomware impact and data exfiltration risk by instantly severing network access for compromised endpoints. The business value comes from shrinking the blast radius, which minimizes recovery costs, regulatory fines, and operational disruption. Implementation requires integrating with CrowdStrike or SentinelOne EDR APIs, Cisco ISE or Aruba ClearPass for NAC control, and Palo Alto or Fortinet firewalls for segment-level enforcement.
The architecture mandates a multi-layered safety control: isolation triggers only after confidence scoring exceeds a configurable threshold, with optional pre-approval gates for critical servers. The orchestrator, built with LangGraph or a custom Python agent, must log all actions to SIEM for audit and support immediate rollback via API reversal. Exception handling routes low-confidence cases to human review in ServiceNow, while monitoring dashboards track false-positive rates and containment latency. This creates a defensible, automated response loop that scales SOC analyst leverage without compromising operational safety.
This table compares the operational and security outcomes of three approaches to containing a compromised host, from reactive human processes to static automation to intelligent, autonomous agentic workflows. Prasad Kumkar is the CEO & MD of Inference Systems and writes about AI systems architecture, LLM infrastructure, model serving, evaluation, and production deployment. Over 5+ years, he has worked across computer vision models, L5 autonomous vehicle systems, and LLM research, with a focus on taking complex AI ideas into real-world engineering systems.
His work and writing cover AI systems, large language models, AI agents, multimodal systems, autonomous systems, inference optimization, RAG, evaluation, and production AI engineering. To create an automation profile for FortiGate Quarantine or FortiSwitch Quarantine via FortiLink , the incoming webhook needs to be setup on FortiGate to accept requests from FortiNDR . You can register them in Security Fabric > Automation Framework .
The following example shows you how to set up webhooks for FortiGate Quarantine to quarantine infected hosts through FortiGate. Ensure the selected Administrator profile has sufficient privileges to execute CLI scripts. Do not use the characters < > ( ) # " ' in the administrator username. Using these characters in an administrator username might have a cross site scripting (XSS) vulnerability.
A REST API administrator should have the minimum permissions required to complete the request. 2. System Architecture & Core Working Principles Certificate matching is supported as an extra layer of security. Both the client certificate and token must match to be granted access to the API.
Cross Origin Resource Sharing (CORS) allows third-party web apps to make API requests to the FortiGate using the token. Select Incoming Webhook and enter a Name to be used to register the automation profile. This example requires two webhooks, one that executes the Ban IP action (this ip_blocker example). Another webhook executes the unban IP action.
We recommend maintaining a consistent naming pattern for the Stitch and Trigger names. For example, ip_blocker and ip_unblocker . In the New Automation Stitch CLI Script section, enter the following script for the unban IP action. Substitute root with a VDOM.
For the CLI script example, config vdom edit root is not needed when FortiGate disabled VDOM mode. The hosts page lists compromised hosts and their associated threat levels. From here, you can monitor and mitigate malware detections on a per host basis. Compromised hosts are systems for which there is a high confidence that attackers have gained unauthorized access. When a host is compromised, the attacker can do several things to the computer, such as: Compromised hosts are listed as secure intelligence data feeds (also called information sources.) The data feed lists the IP address or IP subnet of the host along with a threat level; for example, 130.131.132.133 and threat level 5. Once threats are identified, you can create threat prevention policies to take enforcement actions on the inbound and outbound traffic on these infected hosts.
Export DataâIIClick the Export button to download compromised host data to a CSV file. You are prompted to narrow the data download to a selected time-frame. Set the global threat level to block infected hosts. When a host is found to be compromised, it is assigned a threat level. Based on the global threat level you set here, 1-10 with 10 being the highest threat, compromised hosts with the set threat level and above are added to the infected hosts lists and can subsequently be blocked by policies configured on the SRX Series Firewall. See Hosts Overview and Configure the SRX Series Firewall to Block Infected Hosts for more information.
You can configure Juniper ATP Cloud to send e-mails when certain threat levels are reached for infected hosts. For example, you can send e-mails to an IT department when thresholds of 5 are met and send e-mails to an escalation department when thresholds of 9 are met. You can send e-mails to any account; you are not restricted to administrator e-mails defined in the Users window. The Web UI does not verify if an e-mail account is valid.
Email alerts for infected hosts call immediate attention to administrators when a possible network security issue arises. Email alerts can be configured for only specific administrators and not all users of the web portal, targeting alerts more narrowly. Click the plus sign to create e-mail alerts, or click the pencil icon to edit existing ones. Configure the fields described in the table below.
Select a threat level between 1 and 10. When this level is reached, an e-mail is sent to the address you provided. When a host is marked as infected and added to the infected hosts feed, it is blocked from the network by policies configured on the SRX Series Firewall. There are options for unblocking individual hosts on the Host Details page in the Juniper ATP Cloud Web Portal. See Hosts Overview for information. If you want to unblock multiple host IP addresses based on time period and threat level, you would use the Automatically Expire Blocked Hosts feature on the Infected Hosts page in the Web Portal.
From the Global Infected Hosts page, you can set infected hosts to expire after a configured time based on a minimum and maximum threat level. Once the time period is reached, blocked IP addresses are no longer marked as infected and therefore no longer blocked. One example of when you might use this feature is if you are using DHCP addressing and reallocating addresses on a set schedule. In that case, you might want to set an expiration time for infected hosts (based on IP address lease times), after which addresses are no longer marked as infected.
(System Administrators and Operators only) Enable Automatically Expire Blocked Hosts and select one of the following: Expire a range of hosts âIIEnter a range of IPv4 or IPv6 addresses. Any of the following IPv4 formats are valid: 1.2.3.4/30, or 1.2.3.4-1.2.3.6 Any of the following IPv6 formats are valid: 1111::1-1111::9, or 1111:1::0/64 No more than a block of /16 IPv4 addresses and /48 IPv6 addresses are accepted. For example, 10.0.0.0-10.0.255.255 is valid, but 10.0.0.0-10.1.0.0 is not.
Bitmasks: The maximum amount of IP addresses covered by bitmask in a subnet record for IPv4 is 16 and for IPv6 is 48. For example, 10.0.0.0/15 and 1234::/47 are not valid. CIDR notation is also accepted. For both Expire all hosts or Expire a range of hosts , you must also set expiration time and threat levels. Click the plus + sign to create an entry and set the following in the Expiration Time table.
Click the table entry under Minimum Threat Level to access a pulldown menu. Select a minimum threat level (1-10). The level you select is included in the minimum setting. Click the table entry under Maximum Threat Level to access a pulldown menu. Select a maximum threat level (1-10). The level you select is included in the maximum setting.
Click the table entry under Hours to Unblock . You can select Never, 6, 12, 18, or 24 hours. After the set amount of hours, the infected label expires and the hosts are no longer blocked. For example, if you set the minimum at 6 and the maximum at 8 with hours to unblock as 24, the following would occur. All infected hosts with a threat level of 6 and above and 8 and below would expire after 24 hours.
You can create multiple entries in this table, setting different expiration times for different threat levels. Once unblock settings are entered in the table, you can use the table to change existing settings or to delete settings. In this video, we will demonstrate how to network contain a system with CrowdStrike Falcon®. This capability is also referred to as “network quarantine” or “network isolation” and is typically used by administrators to remove an infected (or possibly infected) system from the network. This removes the ability for malware to spread or for an attacker to move latterly across the network. With CrowdStrike Falcon®, once a system is network contained, it can only make network connections to the CrowdStrike cloud infrastructure or to local IPs that are specified by the administrator. It is also possible to un-contain a system after the system is verified as clean.
When FortiGate detects a host classified as compromised high severity by FortiGate itself, either FortiGuard or FortiAnalyzer with an IOC license can identify the compromised endpoint MAC address, can apply MAC-based quarantine on managed FortiSwitches and FortiAPs, and can send an email notification to administrators with the appropriate automation stitch configuration. The automation stitch configuration is as follows: Trigger condition: config system automation-action edit "Quarantine on FortiSwitch + FortiAP" set description "Default automation action configuration for quarantining a MAC address on FortiSwitches and FortiAPs." set action-type quarantine next edit "Access Layer Quarantine" set description "Quarantine the MAC address on access layer devices (FortiSwitch and FortiAP)." set action-type quarantine next end After setting up the correct configuration, follow the steps below to confirm that the automation stitch is working as intended.
diagnose debug reset diagnose debug application autod -1 diagnose debug console timestamp enable diagnose debug enable In the debug output for a successful execution of the automation stitch, the following results are expected: Related article: Technical Tip: FortiGate automation stitch repeatedly triggered by system log Enter your E-mail address. We'll send you an e-mail with instructions to reset your password.
To create an automation profile for FortiGate Quarantine (Formerly Ban IP action) or FortiSwitch Quarantine via FortiLink , the incoming webhook needs to be setup on FortiGate to accept requests from FortiNDR. You can register them in Security Fabric > Automation Framework . The following example shows you how to set up webhooks for FortiGate Quarantine to quarantine infected hosts through FortiGate.
Ensure the selected Administrator profile has sufficient privileges to execute CLI scripts. 3. Software Implementation, Frameworks & Protocols You can also restrict access to FortiNDR by setting up Trusted Hosts for the API profile. Select Incoming Webhook and enter a Name to be used to register the automation profile.
This example requires two webhooks, one that executes the Ban IP action (this ip_blocker example). Another webhook executes the unban IP action. We recommend maintaining a consistent naming pattern for the Stitch and Trigger names. For example, ip_blocker and ip_unblocker .
In the New Automation Stitch CLI Script section, enter the following script for the unban IP action. Substitute root with a VDOM. For the CLI script example, config vdom edit root is not needed when FortiGate disabled VDOM mode. When critical vulnerabilities are detected on the host machine, FortiClient EMS isolates those files and applications in Quarantine Management. However, the Quarantine Management feature is only operational on Windows OS.
If the intention is to prevent these endpoints (Linux, Windows or Mac) from accessing resources, set up a ZTNA tag and configure a deny firewall policy. Conversely, if the aim is to prevent the vulnerable host from accessing the networks, quarantine the host accordingly. Note that the quarantine feature only works for windows, however. Quarantining an endpoint from FortiOS using EMS - FortiClient EMS administration guide .
This article will demonstrate the setup of a workaround to quarantine Windows and Linux OSes based on critical vulnerability detection. For the quarantine features to function effectively, managed endpoints must have FortiGate as their default gateway. This could be a directly connected interface or endpoints that are connected to a VPN tunnel, provided they have access to FortiClient EMS and FortiOS.
In this example environment, there is an auto-connect SSL-VPN tunnel established and the endpoint is connected to the FortiClient EMS server through the VPN tunnel. Vulnerability scans are performed by EMS endpoint profiles and FortiClient shares all the vulnerability records to FortiClient EMS. Subsequently, FortiClient EMS shares those records with FortiGate via the FortiTelemetry connection.
In FortiGate, vulnerability records logs are stored under Endpoints Event ( Log and Report -> System Event -> Endpoints Event ). Download the logs to craft the automation stitches. date=2024-02-14 time=21:23:57 eventtime=1705037037002219460 tz="-0800" logid="0107045071" type="event" subtype="endpoint" level="notice" vd="root" logdesc="FortiClient Vulnerability Scan" fctuid="3DA7882B6A1641BFA6C531B1DF8B3EF7" scantime=1705065851 srcip =10.212.134.200 srcname="DESKTOP-74GOVRE" srcmac="e0-db-55-c3-2b-d6" vulnid=4392 vulnname="Security Vulnerabilities fixed in Adobe Acrobat APSA11-04" vulncat="Applications" severity =" Critical " cveid="CVE-2011-2462"vendorurl=" https://www.adobe.com/support/security/advisories/apsa11-04.html " msg="Endpoint Vulnerability Scan Entry. " For automation to trigger, it must meet all of the criteria. In this case, the FortiOS 'Forticlient Vulnerability Scan' Event triggers when a critical severity is detected.
For an action to quarantine the endpoint, it is necessary to provide a key parameter ( srcip ) from the key-value pair (srcip=10.212.134.200) of the event logs. After this action, EMS and FortiOS both display that the endpoint is quarantined Lastly, set the automation stitches by attaching an automation trigger and an automation action field. Craft the automation action field depending on event logs and automation trigger setup.
Enter your E-mail address. We'll send you an e-mail with instructions to reset your password. The impact of quarantine strategies on malware dynamics in a network with heterogeneous immunity In this paper, we investigate the influence of two types of isolation on malware propagation within a computer network. Model 1 proposes the network quarantine strategy, where infected computers are fully disconnected from the network. As for model 2, the control strategy is the anti-virus software quarantine, where infected files in a computer are contained in an isolation folder. Both models consider the aspect of heterogeneous immunity, that is, weak and strong immunization of computers in a network. Analytical examinations produced a virus-free equilibrium and an endemic equilibrium for each model. It has been observed that the quarantine reproduction number R q plays an essential role in the existence and stability of the equilibrium points. Furthermore, numerical simulations are accomplished to substantiate the qualitative results. Finally, a sensitivity analysis is executed to specify the dominant parameters on R q . It is found that the performance of network quarantine is better than anti-virus software quarantine in controlling malware propagation.
In this paper, we investigate the influence of two types of isolation on malware propagation within a computer network. Model 1 proposes the network quarantine strategy, where infected computers are fully disconnected from the network. As for model 2, the control strategy is the anti-virus software quarantine, where infected files in a computer are contained in an isolation folder. Both models consider the aspect of heterogeneous immunity, that is, weak and strong immunization of computers in a network. Analytical examinations produced a virus-free equilibrium and an endemic equilibrium for each model. It has been observed that the quarantine reproduction number R q plays an essential role in the existence and stability of the equilibrium points. Furthermore, numerical simulations are accomplished to substantiate the qualitative results. Finally, a sensitivity analysis is executed to specify the dominant parameters on R q . It is found that the performance of network quarantine is better than anti-virus software quarantine in controlling malware propagation.
Copyright (c) 2022 The Author(s). Published by Vilnius Gediminas Technical University. S. M. Al-Tuwairqi and W. Bahashwan. A dynamic model of viruses with the effect of removable media on a computer network with heterogeneous immunity.
Adv Differ Equ, 260, 2020.
https://doi.org/10.1186/s13662-020-02710-0" > https://doi.org/10.1186/s13662-020-02710-0 C. Gan, X. Yang and Q. Zhu. Global stability of a computer virus propagation model with two kinds of generic nonlinear probabilities.
Abstract
and Applied Analysis, 2014, 2014.
Abstract Art
https://doi.org/10.1155/2014/735327" > https://doi.org/10.1155/2014/735327 C. Gan, X. Yang, Q. Zhu and W. Liu. A propagation model of computer virus with nonlinear vaccination probability. Commun Nonlinear Sci Numer Simulat, 19:92–100, 2014.
Abstract Definition
https://doi.org/10.1016/j.cnsns.2013.06.018" > https://doi.org/10.1016/j.cnsns.2013.06.018 Z. Hu, H. Wang, F. Liao and W. Ma. Stability analysis of a computer virus model in latent period. Chaos, Solitons & Fractals, 75:20–28, 2015. https://doi.org/10.1016/j.chaos.2015.02.001" > https://doi.org/10.1016/j.chaos.2015.02.001 J. O. Kephart and S. R. White. Directed-graph epidemiological models of computer viruses. IEEE Symposium on Security and Privacy, pp. 343–358, 1991.
Abstraction
N.H. Khanh. Dynamical analysis and approximate iterative solutions of an antidotal computer virus model. Int. J. Appl. Comput. Math, 3:S829–S841, 2017.
Abstraction Tadc
https://doi.org/10.1007/s40819-017-0385-6" > https://doi.org/10.1007/s40819-017-0385-6 S. Koonprasert and N. Channgam. Global stability and sensitivity analysis of SEIQR worm virus propagation model with quarantined state in mobile internet. Global Journal of Pure and Applied Mathematics, 13:3833–3850, 2017.
Abstract Meaning
M. Kumar, B.K. Mishra and T.C. Panda. Stability analysis of a quarantined epidemic model with latent and breaking-out over the internet. International Journal of Hybrid Information Technology, 8(7):133–148, 2015.
Abstract Noun
https://doi.org/10.14257/ijhit.2015.8.7.12" > https://doi.org/10.14257/ijhit.2015.8.7.12 A. Lanz, D. Rogers and T.L. Alford. An epidemic model of malware virus with quarantine. Journal of Advances in Mathematics and Computer Science, 33(4):1–10, 2019.
Abstract Painting
https://doi.org/10.9734/jamcs/2019/v33i430182" > https://doi.org/10.9734/jamcs/2019/v33i430182 D. Li, J. Chen, B.L. Jianwei, B. Qianhong Wu and Weiran Liu. Modeling and hopf bifurcation analysis of benign worms with quarantine strategy. Springer International Publishing, 2:103–118, 2017.
Abstract Expressionism
W. Liu, C. Liu, X. Liu, S. Cui and X. Huang. Modeling the spread of malware with the influence of heterogeneous immunization. Applied Mathematical Modelling, 40:3141–3152, 2016. https://doi.org/10.1016/j.apm.2015.09.105" > https://doi.org/10.1016/j.apm.2015.09.105 M. Martcheva. An Introduction to Mathematical Epidemiology. Springer, 2015. https://doi.org/10.1007/978-1-4899-7612-3" > https://doi.org/10.1007/978-1-4899-7612-3 B. K. Mishra and D. K. Saini. SEIRS epidemic model with delay for transmission of malicious objects in computer network.
Abstracted Jax
Applied Mathematics and Computation, 188(2):1476–1482, 2007.
https://doi.org/10.1016/j.amc.2006.11.012" > https://doi.org/10.1016/j.amc.2006.11.012 B.K. Mishra and N. Jha. SEIQRS model for the transmission of malicious objects in computer network. Applied Mathematical Modelling, 34(3):710–715, 2010. https://doi.org/10.1016/j.apm.2009.06.011" > https://doi.org/10.1016/j.apm.2009.06.011 M.R. Parsaei, R. Javidan, N. Shayegh Kargar and H. Saberi Nik. On the global stability of an epidemic model of computer viruses.
Theory in Biosciences, 136(34):169–178, 2017.
https://doi.org/10.1007/s12064-017-0253-2" > https://doi.org/10.1007/s12064-017-0253-2 L. Perko. Differential Equations and Dynamic Systems. Springer Verlag, 1991. https://doi.org/10.1007/978-1-4684-0392-3" > https://doi.org/10.1007/978-1-4684-0392-3 J. Piqueira and C. Batistela. Considering quarantine in the SIRA malware propagation model. Mathematical Problems in Engineering, 2019, 2019. https://doi.org/10.1155/2019/6467104" > https://doi.org/10.1155/2019/6467104 J. Piqueira, A. deVasconcelos, C. Gabriel and V. Araujo. Dynamic models for computer viruses. Computers and Security, 27(7-8):355–359, 2008. https://doi.org/10.1016/j.cose.2008.07.006" > https://doi.org/10.1016/j.cose.2008.07.006 Y.S. Rao, P.K. Nayak, H. Saini and T.C. Panda. Behavioral modeling of malicious objects in a highly infected network under quarantine defence.
International Journal of Information Security and Privacy, 13(1):17–29, 2019.
https://doi.org/10.4018/IJISP.2019010102" > https://doi.org/10.4018/IJISP.2019010102 R. Upadhyay, S. Kumari and A. Misra. Modeling the virus dynamics in computer network with SVEIR model and nonlinear incident rate.
Journal of Applied Mathematics and Computing, 54(1-2):485–509, 2017.
https://doi.org/10.1007/s12190-016-1020-0" > https://doi.org/10.1007/s12190-016-1020-0 R. Upadhyay and P. Singh. Modeling and control of computer virus attack on a targeted network. Physica A: Statistical Mechanics and its Applications, 538:122617, 2020.
https://doi.org/10.1016/j.physa.2019.122617" > https://doi.org/10.1016/j.physa.2019.122617 4. Practical Deployment, Analysis & Case Studies F. Wang, Y. Zhang, C. Wang, J. Ma and S.J. Moon. Stability analysis of a SEIQV epidemic model for rapid spreading worms.
Computers and Security, 29(4):410–418, 2010.
https://doi.org/10.1016/j.cose.2009.10.002" > https://doi.org/10.1016/j.cose.2009.10.002 J. Watmough and P. van den Driessche. Reproduction numbers and subthreshold endemic equilibria for compartmental models of disease transmission.
Mathematical Biosciences, 180:29–48, 2002.
https://doi.org/10.1016/S00255564(02)00108-6" > https://doi.org/10.1016/S00255564(02)00108-6 L. Yang and X. Yang. An epidemic model of computer viruses with vaccination and generalized nonlinear incidence rate. Physica A, 392:6523–6535, 2013. L. Yang and X. Yang. The impact of nonlinear infection rate on the spread of computer virus. Nonlinear Dynamics, 82(1-2):85–95, 2015. https://doi.org/10.1007/s11071-015-2140-z" > https://doi.org/10.1007/s11071-015-2140-z L. Yang, X. Yang, Q. Zhu and L. Wen. A computer virus model with graded cure rates. Nonlinear Analysis: Real World Applications, 14:414–422, 2013.
https://doi.org/10.1016/j.nonrwa.2012.07.005" > https://doi.org/10.1016/j.nonrwa.2012.07.005 Y. Yao, X. w. Xie, H. Guo, F. x. Gao and G. Fu. The worm propagation model with dual dynamic quarantine strategy.
Communications in Computer and Information Science, 135(PART 2):497–502, 2011.
https://doi.org/10.1007/9783-642-18134-4_79" > https://doi.org/10.1007/9783-642-18134-4_79 C.C. Zou, W. Gong and D. Towsley. Worm propagation modeling and analysis under dynamic quarantine defense. In Proceedings of the 2003 ACM Workshop on Rapid Malcode, WORM 03, pp. 51–60, New York, NY, USA, 2003. Association for Computing Machinery.
Copyright (c) 2022 The Author(s). Published by Vilnius Gediminas Technical University. Learn how to remove viruses on a network or troubleshoot and respond to active security threats. Troubleshooting and responding to threats and viruses on a network involves the following: To contain and eliminate a threat, you must know all of the threats that are present on the computer, and what the threats were designed to do. You must also understand which methods the threats use to propagate throughout the network.
To identify the threats, follow the instructions under the condition that applies, based on whether or not you have identified infected or suspicious files. Symantec Endpoint Protection (SEP) detects a threat, and you need additional information about the threat; or, Endpoint Protection does NOT detect a threat, but you have identified a suspect file that you believe to be malicious.
Symantec Security Response can identify all known malicious files. In the event that additional information is required, submit the file to Symantec Security Response for further research. If the file is a new malicious file, Symantec Security Response can create virus definitions to detect it. Network scanning allows Auto-Protect to scan files the computer accesses from remote computers. This helps prevent malware from spreading, and can result in identification of the threat in cases when Auto-Protect is not functioning on an infected computer.
Endpoint Protection does not detect a threat and you need to determine which files are infected, if any. Increasing the heuristic level allows Symantec Endpoint Protection to detect more threats based on their behavior. Network scanning allows Auto-Protect to scan files that the computer accesses from remote computers. This helps prevent malware from spreading and can result in identification of the threat in cases when Auto-Protect is not functioning on an infected computer.
Additional resources within Endpoint Protection for identifying the threat and its behaviors Endpoint Protection employs additional tools to help troubleshoot, contain, and remediate threats within an Enterprise environment. Once you have identified the threat, you must determine if other computers are infected.
You can use the Endpoint Protection Manager to identify infected computers (see Using Endpoint Protection Manager reports and logs to identify infected computers for details), but there are circumstances that may require additional methods. ( Recommended ) Update virus definitions with a signature file that detects the variant of the threat ( Good ) If virus definitions are not available for the threat, or if parts of the network are not protected by Endpoint Protection, then use other means to identify possible infected computers.
Monitor DNS server logs or perimeter firewall logs for the external IP address or URL the threat is using for communication. This should reveal which computers may be infected. Endpoint Protection employs additional tools to help troubleshoot, contain, and remediate threats within an enterprise environment.
After you have identified a threat and you understand how the threat spreads, you have to prevent the threat from spreading through the network. It is critical that you remove the compromised computer from the network or add it to a "quarantine network." Otherwise, the threat will spread as it infects other computers on the network.
Physically unplug the network cable from the infected computer and disable all wireless connections. On occasion, a compromised computer is mission-critical and cannot be isolated from the network. In some cases, depending on the infection, these can be isolated in so-called quarantine networks with some heavily restricted network access. Naturally, this only works for cases where the threat's activity does not coincide with the functions needed by the compromised computer.
The quarantine network itself is a carefully configured subnet designed to restrict the traffic that the threat needs to propagate to other computers. This will allow the infected computer some restricted form of use. Due to business need, you may not be able to quarantine some infected systems or remove them from the network. You may need to configure special rules to allow them to function within their current subnet and still prevent the threat from spreading.
This may include any combination of the following actions depending on the attack vector used by the threat. Caution: This action carries with it a high degree of risk. Seriously evaluate the risk before you follow these steps. Learn more in Step 5 . Endpoint Protection employs additional tools to help troubleshoot, contain, and remediate threats within an enterprise environment.
With the threat isolated to individual computers, you can remove the threat and reverse its side effects. As you take the steps outlined in this section, you should assess the following: Before proceeding with a disinfection of a compromised computer, it is important to consider the level of compromise when a backdoor or a rootkit is present. These malicious code subclasses allow threat writers to gain access and hide their malicious files and activities.
In both cases, determining the extent of the damage done to a computer is difficult and may increase the difficulty of removing all malicious functions from the computer. Under such circumstances, it is often less time consuming to re-image the operating system and restore needed data from clean backups. In order to remove the malicious files from the computer, you must stop any processes used by the threat. There are three primary options for doing this.
The simplest way to remove the threat from the computer is to run a full system scan on the compromised computer. With the latest definitions installed, the scan should be able to remove the threat in most cases without incident. If the threat is a worm or Trojan, you can manually remove the files. Caution: Do not attempt manual removal of file infectors; it is impossible to determine which files are infected and which are not. The added complexity of threats leaves it possible to overlook something when you attempt manual removal.
Threats can make a number of changes to a computer in addition to installing files. Threats can also lower security settings and reduce system functionality based on changes to the computer's configuration. In many cases, Endpoint Protection can restore these settings to the default security setting. Some cases require you to confirm settings or restore them manually after removing a threat. You can further adjust these settings to suit the needs of the network.
There may additional cases where Symantec software cannot reverse the changes because we are unable to determine the previous setting. Threats create or modify registry entries that perform functions ranging from loading the threat when the operating system starts to granting Internet access through the Windows Firewall.
Leaving these entries unchanged after the threat has been removed may cause error messages to appear as the computer boots or when using the computer. In some cases, this may prevent the user from logging in after they restart the computer. 5. Performance Evaluation & Extended Technical Observations Remove or restore any registry items added by the threat to the computer's default setting or, if possible, to a more secure setting. You can do this manually, with a script, or with a Group Policy Object.
Threats may use several system files used by the operating system. When cleaning a computer, check the following items for signs of modification: After you have successfully cleaned a computer, Symantec recommends one final safety check: an antivirus scan with the latest definitions. If the scan comes back clean, reconnect the computer back to the production network.
Note: Connect only a few computers at a time to ensure that you have properly remediated the threat and that no secondary symptoms present themselves. Endpoint Protection employs additional tools to help troubleshoot, contain, and remediate threats within an Enterprise environment.
Some people believe that security and usability are inversely proportionate to each other, with an increase in security increasing the steps needed to perform a task. Ease-of-use, while more efficient, can open security holes that make it easier for threats to spread. Weak points in a network are usually those technologies that make computers more accessible and user-friendly.
Under normal circumstances and best practices, threats cannot re-infect a protected hard drive without security software detecting the threat. If this seems to happen, re-examine the system and security software configuration. Also, review the following security weak points and ensure that you have closed common attack vectors. Malicious code can exploit vulnerabilities due to software flaws. You can repair flaws and prevent security incidents using patches provided by the software vendor.
You should have a Patch and Configuration Management Policy in place for your network to test new patches and roll them out to client computers. AutoPlay is a Windows feature that enables users to choose which program opens or plays files from CDs, DVDs, and removable drives such as USB. This feature has become one of the largest attack vectors in the enterprise environment.
While removable drives may provide an initial source of infection, most network drives also use AutoPlay. AutoPlay allows threats to attack from a network drive as soon as a user maps the drive. Companies design antivirus software to scan the local hard drive; therefore, the threat can attack the client computer without detection or prevention, unless additional measures like Network Auto-Protect are employed.
To protect your network, you should disable AutoPlay. You can do this on individual computers, push this to client computers using the Group Policy editor, configure a policy in Endpoint Protection, or entirely disable the external media ports on the computer from within the BIOS. Caution: A known Windows vulnerability may turn on AutoPlay unless you apply specific Windows patches.
Access to all network shares should require a strong password not easily guessed. "Open shares" are network shares that allow the inherited permissions from the user to validate access. Open shares do not require additional authentication, which allows threats to spread very fast. Because of this, you should minimize the use of open shares as much as possible. When they are essential to business continuity, open shares should be restricted to use write and execute privileges.
If a user only needs to obtain files from a source, grant them read access. For added security, you can limit write access for users needing file transfer capabilities to a "temporary" storage folder on a file server, which you set to clear semi-regularly. Limit execution permissions to administrators or power users who have such a need. The problem with the aforementioned shares is that regardless of whether strong passwords are in place, once a user is logged on to a system with elevated rights, any threat present can use the credentials to access Admin$ or IPC$ shares available on the network.
Once the user logs in, their rights and permissions are implicit -- the door has been unlocked. Anything accessible through the user’s account will also be accessible to anything that impersonates the account. While not as prevalent, attackers still use email attachments to spread malicious code. Most mail servers provide the ability to strip certain attachment types from emails. Limiting the types of files that are valid as attachments handicaps many threats' ability to spread.
Investing in antispam software is another way of reducing exposure to threats. Doing so reduces the number of phishing scams and spam that reach end-users, and thus the network as a whole. Perimeter firewalls are critical to protecting the network as a whole, but cannot cover all points of entry. Client firewalls add an extra layer of security by protecting individual computers from malicious behavior, such as Denial of Service attacks, and are critical to managing today's threat landscape. Beyond basic firewalls, network and host-based Intrusion Detection Systems (IDS) and Intrusion Protection Systems (IPS) can help monitor unwanted activity on the network, and in many cases stops or alerts on the offending traffic in real-time. Many client-side firewalls today provide these features.
An educated end-user is a safer one. Ensure that your users understand the basics of safe computing, such as the following: Even after you complete all tasks, you need to prepare for the worst-case scenario. Draft a plan that details how to respond to a potential outbreak, and assign tasks and responsibilities to members of your emergency response team. Having plans in place for these things makes dealing with unpleasant situations much easier and saves both time and money.
Symantec Security Response encourages all users and administrators to adhere to the following basic security best practices: Use rapid release virus definitions when facing an outbreak or when Technical Support or Symantec Security Response suggests its use. The primary focus of these detection signatures is the rapid detection of newly emerging threats. Rapid release virus definitions have undergone basic quality assurance testing by Symantec Security Response. While Symantec Security Response makes every effort to ensure that all virus definitions function correctly, the rapid release virus definitions may pose some risks such as a higher potential for false positives. Rapid release virus definitions are most useful for perimeter defenses or for all protection tiers as a means of mitigating fast-spreading virus outbreaks. These signatures are released approximately once per hour.
Learn how to update Endpoint Protection Manager with rapid release virus definitions so that it can update clients as they check in. If you believe that a threat has infected a file and Endpoint Protection has not detected the threat, submit the suspicious file to Symantec Security Response.
Customers making submissions to Security Response are encouraged to create a support case at the same time. This will allow the support representative to confirm that you have submitted to the correct queue, which will dramatically affect the ability of Symantec Security Response to provide a timely response. Access to this page requires authorization. You can try signing in or changing directories .
Cluster node quarantine is a protective feature in Windows Server Failover Clustering that temporarily isolates unstable or problematic nodes to safeguard cluster health and application workloads. A quarantined node can't host cluster roles, such as virtual machines (VMs), until it exits quarantine, either automatically or through administrator intervention. Several issues can trigger a quarantine, including repeated health check failures, persistent service failures, hardware issues, or storage or network communication problems. This article provides a thorough approach to investigating and resolving node quarantine incidents to help administrators ensure cluster stability and minimal downtime.
Before you contact Microsoft Support, you can gather the following information about your issue. Efficient quarantine and release procedures are essential for promptly isolating infected devices, minimizing disruptions to the enterprise network. This streamlined approach enhances endpoint security, swiftly addressing security incidents and reducing the risk of further compromise. A proactive strategy in implementing these measures contributes to a resilient and secure network environment.
Upon enabling network quarantine for an infected endpoint it will remain isolated from all networks while maintaining a connection only with the Endpoint Central server(all capabilities of Endpoint Central can still be efficiently performed). Upon unblocking network quarantine on the device, it will regain full connectivity to all networks. Before proceeding, it is crucial to confirm that all identified threats on the endpoint have been effectively resolved.
Unblock should occur instantly. If an on-demand connection failure occurs, allow up to 5 hours for the process to complete. If the issue continues after this time, please refer to the manual steps below. If a device remains quarantined, you can manually remove it by following these steps to manually de-isolate it from network quarantine: The Fortinet Security Fabric offers endpoint visibility at various monitoring levels. When the Security Fabric includes the following network devices, you can configure the system to automatically quarantine an endpoint on which an Indicator of Compromise (IoC) is detected. This requires the following network components: The following lists the prerequisites that must be met for FortiClient, EMS, and the FortiGate.
FortiClient must be installed on the endpoint and connected to EMS as part of a Security Fabric. You may also elect to enable a pre-defined automation stitch instead of completing 1-3 above. You can generate logs that will be flagged as an IOC by visiting http://195.22.28.198 from the test endpoint. When the FortiGate detects devices that have lower trust scores, lack mandatory installed software, or are sending out malicious traffic, an administrator can quarantine the device from the normal switch VLAN to the quarantine VLAN. This can limit the device's access, or provide them specific information on the quarantine portal page.
The quarantined device is moved to the quarantine VLAN, and the configuration of the FortiSwitch port does not change. The quarantined device gets its IP address from the DHCP server on the quarantine VLAN interface. The network locations that the device can access depends on the firewall policies that are configured for the quarantine VLAN interface. By default, the device must acknowledge and accept the information on the Quarantine Portal before it can access any part of the network.
Harvested Online Documentation & Reference Sources • https://inferensys.com/automate/autonomous-threat-hunting-and-mitigation/ai-agentic-workflow-for-autonomous-host-isolatio n-and-quarantine • https://docs.fortinet.com/document/fortindr/7.6.1/administration-guide/637981 • https://www.juniper.net/documentation/us/en/software/nm-apps26.1/junos-space-security-director/policy-enforcer-user-guide /topics/concept/sky-atp-host-overview.html • https://www.juniper.net/documentation/us/en/software/atp-cloud/atp-cloud-user-guide/topics/concept/atp-cloud-global-config -overview.html • https://www.crowdstrike.com/en-gb/resources/videos/how-to-contain-an-infected-system/ • https://community.fortinet.com/fortigate-3/technical-tip-automation-stitch-configuration-for-compromised-host-quarantine-and -debugging-of-execution-222563 • https://docs.fortinet.com/document/fortindr/7.2.1/administration-guide/637981/fortigate-quarantine-webhook-setup-example • https://community.fortinet.com/forticlient-4/technical-tip-quarantine-forticlient-endpoints-automatically-using-automation-stitc hes-159484 • https://journals.vilniustech.lt/index.php/MMA/article/view/14391 • https://knowledge.broadcom.com/external/article/152063/virus-removal-and-troubleshooting-on-a-n.html
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Network Quarantine System For Infected Hosts.
! Define Extended Access List to Block Malicious Traffic ip access-list extended SECURE_PERIMETER_ACL remark Block Inbound Telnet and Unencrypted Services deny tcp any any eq 23 log remark Permit Verified Web SSL Traffic permit tcp any any eq 443 permit tcp any any eq 80 remark Mitigate ICMP Flood and Ping Sweeps permit icmp any any echo-reply deny icmp any any echo log deny ip any any log
! Apply ACL to Ingress Interface GigabitEthernet0/0 interface GigabitEthernet0/0 ip access-group SECURE_PERIMETER_ACL in no shutdown end write memory
Extended IP access list SECURE_PERIMETER_ACL (Cisco Packet Tracer) ──────────────────────────────────────────────────────────────────────── 10 deny tcp any any eq telnet log (142 matches) [Probes Dropped] 20 permit tcp any any eq 443 (18402 matches) [TLS 1.3 Traffic Permitted] 30 permit tcp any any eq 80 (4812 matches) 40 deny icmp any any echo log (524 matches) [Flood Mitigated] 50 deny ip any any log (38 matches) [Default Implicit Deny Rule] ──────────────────────────────────────────────────────────────────────── [✓] Packet Tracer Verification: 0 Unsanitized Ingress Leaks on Gi0/0
| Interface Port | Network Zone | Filter Applied | Traffic Processed | Firewall Decision |
|---|---|---|---|---|
| Gig0/0 (WAN) | Untrusted External | Extended ACL 101 | 24,810 Packets | INSPECTED & FILTERED |
| Gig0/1 (DMZ) | Public Web Services | Port 443 Only | 18,402 Packets | PERMITTED |
| Gig0/2 (LAN) | Corporate Users | 802.1X Port Security | 142 Probes | DENIED & QUARANTINED |