Complete Technical Paper Content — Network Security Auditing Tool For Small Businesses
Overview & System Context
Network Security Auditing Tool For Small Businesses: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9551 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Network security is an umbrella term to describe security controls, policies, processes and practices adopted to prevent, detect and monitor unauthorized access, misuse, modification, or denial of a computer network and network-accessible resources. Network security involves the authorization of access to data in a network, which is controlled by the network administrator. Users choose or are assigned an ID and password or other authenticating information that allows them access to information and programs within their authority. Network security covers a variety of computer networks, both public and private, that are used in everyday jobs: conducting transactions and communications among businesses, government agencies and individuals. Networks can be private, such as within a company, and others which might be open to public access. Network security is involved in organizations, enterprises, and other types of institutions. It does as its title explains: it secures the network, as well as protecting and overseeing operations being done. The most common and simple way of protecting a network resource is by assigning it a unique name and a corresponding password.
Passive Network Wiretapping – Third-party monitoring of electronic communicationsPages displaying short descriptions of redirect targets Passive Port scanner – Application designed to probe for open ports Idle scan – Method of attacking a remote computer Encryption – Process of converting plaintext to ciphertext Traffic analysis – Process of intercepting and examining messages Active: Network virus (router viruses) Eavesdropping – Act of secretly listening to the private conversation of others Data modification An information security audit is an audit of the level of information security in an organization. It is an independent review and examination of system records, activities, and related documents. These audits are intended to improve the level of information security, avoid improper information security designs, and optimize the efficiency of the security safeguards and security processes. Within the broad scope of auditing information security there are multiple types of audits, multiple objectives for different audits, etc. Most commonly the controls being audited can be categorized as technical, physical and administrative. Auditing information security covers topics from auditing the physical security of data centers to auditing the logical security of databases, and highlights key components to look for and different methods for auditing these areas. When centered on the Information technology (IT) aspects of information security, it can be seen as a part of an information technology audit. It is often then referred to as an information technology security audit or a computer security audit. However, information security encompasses much more than IT.
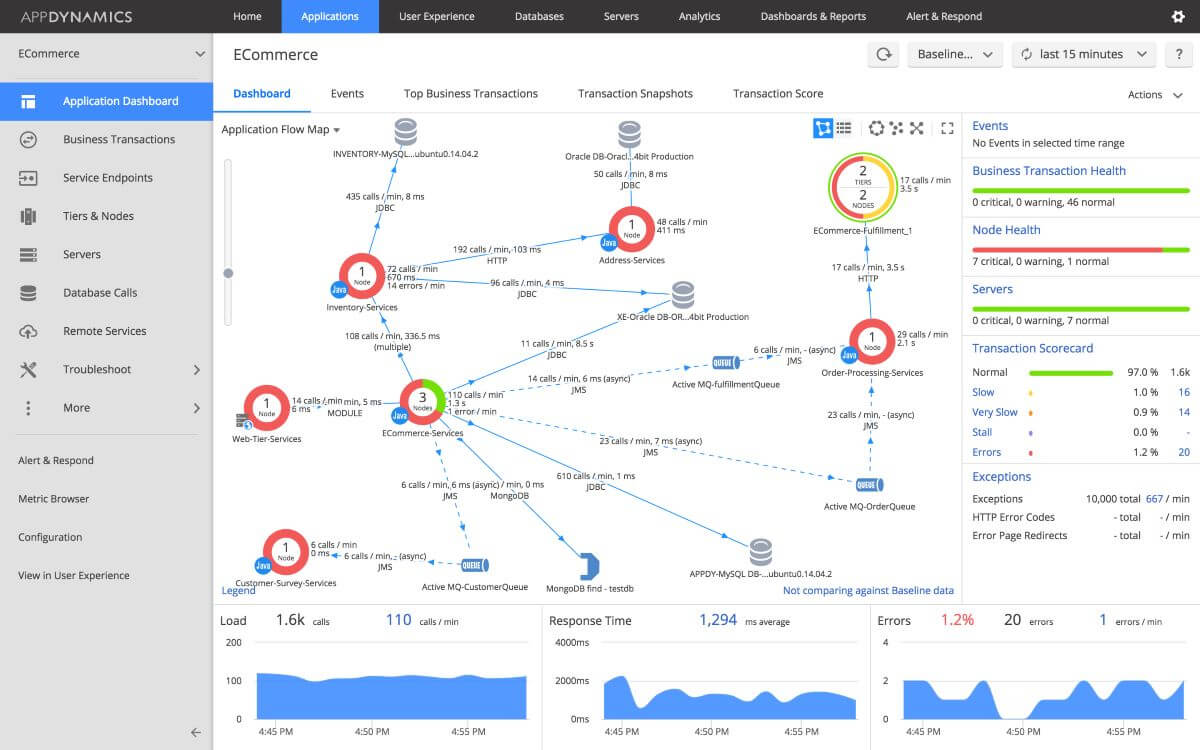
Security policy and standards Organizational and Personal security Communication, Operation and Asset management Physical and environmental security Access control and Compliance IT systems development and maintenance IT security incident management Disaster recovery and business continuity management Risk management Figure 1: 30 Network Auditing Tools for Network Assessments in 2024 - Obkio Meet with IT management to determine possible areas of concern Review the current IT organization chart Review job descriptions of data center employees Research all operating systems, software applications, and data center equipment operating within the data center Review the company's IT policies and procedures Evaluate the company's IT budget and systems planning documentation Review the data center's disaster recovery plan Personnel procedures and responsibilities, including systems and cross-functional training Change management processes are in place and followed by IT and management personnel Appropriate backup procedures are in place to minimize downtime and prevent the loss of important data The data center has adequate physical security controls to prevent unauthorized access to the data center Adequate environmental controls are in place to ensure equipment is protected from fire and flooding Data centre personnel – All data center personnel should be authorized to access the data center (key cards, login ID's, secure passwords, etc.). Datacenter employees are adequately educated about data center equipment and properly perform their jobs. Vendor service personnel are supervised when doing work on data center equipment. The auditor should observe and interview data center employees to satisfy their objectives. Equipment – The auditor should verify that all data center equipment is working properly and effectively. Equipment utilization reports, equipment inspection for damage and functionality, system downtime records and equipment performance measurements all help the auditor determine the state of data center equipment. Additionally, the auditor should interview employees to determine if preventative maintenance policies are in place and performed. Policies and Procedures – All data center policies and procedures should be documented and located at the data center. Important documented procedures include data center personnel job responsibilities, back up policies, security policies, employee termination policies, system operating procedures and an overview of operating systems.
Physical security / environmental controls – The auditor should assess the security of the client's data center. Physical security includes bodyguards, locked cages, man traps, single entrances, bolted-down equipment, and computer monitoring systems. Additionally, environmental controls should be in place to ensure the security of data center equipment. These include Air conditioning units, raised floors, humidifiers and an uninterruptible power supply. Backup procedures – The auditor should verify that the client has backup procedures in place in the case of system failure. Clients may maintain a backup data center at a separate location that allows them to instantaneously continue operations in the instance of system failure The auditors' procedures and findings The auditors' recommendations Objective, scope, and methodologies Overview/conclusions The report may optionally include rankings of the security vulnerabilities identified throughout the performance of the audit and the urgency of the tasks necessary to address them. Rankings like "high", "low", and "medium" can be used to describe the imperativeness of the tasks.
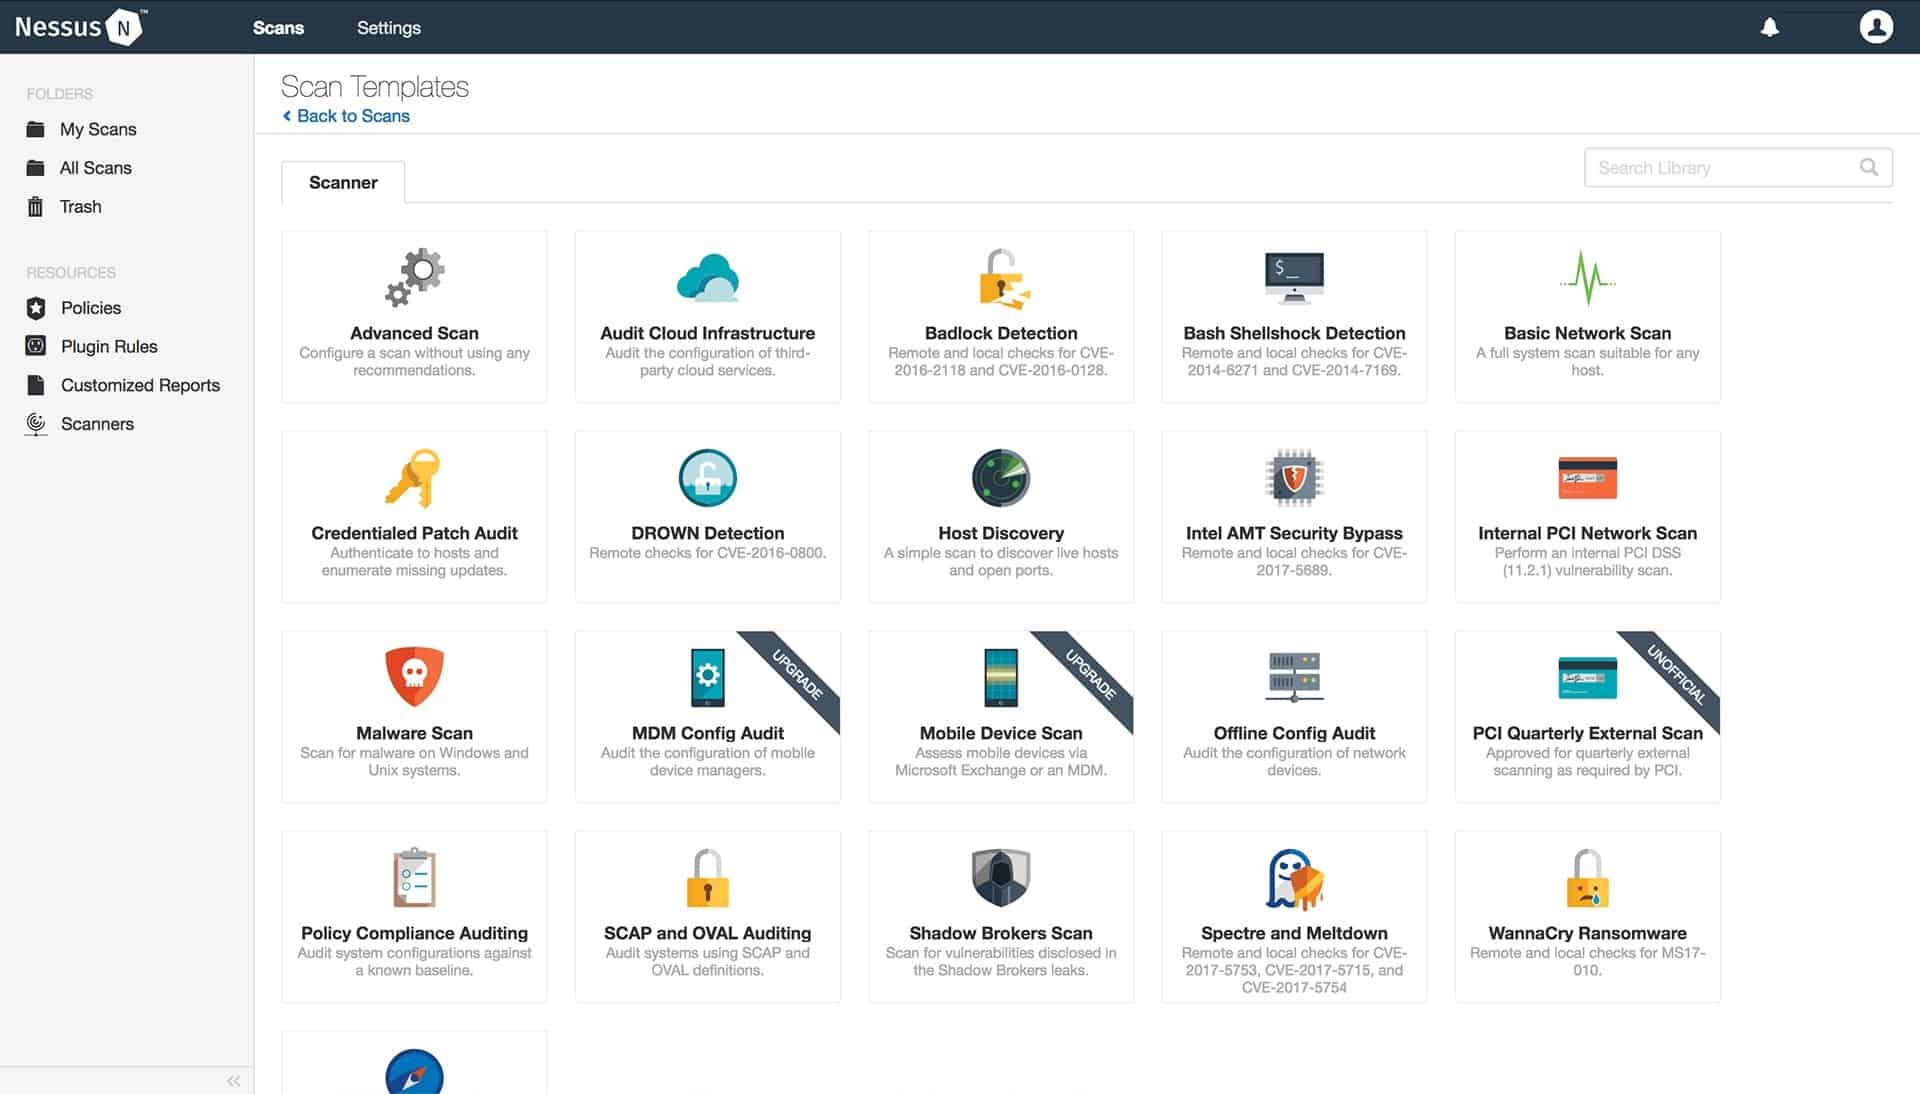
Figure 2: 15 Best Network Security Auditing Tools for 2024 (Paid & Free) Federal or State Regulators Information security audits would primarily be prepared by the partners of these regulators. Examples include: Certified accountants, Cybersecurity and Infrastructure Security Agency (CISA), Federal Office of Thrift Supervision (OTS), Office of the Comptroller of the Currency (OCC), U.S. Department of Justice (DOJ), etc. Corporate Internal Auditors If the information security audit is an internal audit, it may be performed by internal auditors employed by the organization. Examples include: Certificated accountants, Cybersecurity and Infrastructure Security Agency (CISA), and Certified Internet Audit Professional (CIAP) External Auditors Typically, third-party experts employed by an independent organization and specializing in the field of data security are hired when state or federal auditors are not accessible.
Consultants Outsourcing the technology auditing where the organization lacks the specialized skill set. In certain regulated industries, information security audits may be mandated by law. In the United States healthcare sector, the Health Insurance Portability and Accountability Act (HIPAA) Security Rule requires covered entities and business associates to conduct periodic security risk assessments to evaluate the likelihood and impact of potential threats to electronic protected health information.
To assist organizations in meeting these requirements, the Office of the National Coordinator for Health Information Technology (ONC) and OCR developed a free Security Risk Assessment Tool for small and medium-sized healthcare practices. Certified Information Security Manager (CISM) Certified in Risk and Information Systems Control (CRISC) Certified in the Governance of Enterprise IT (CGEIT) Certified Information System Auditor (CISA) CSX (Cybersecurity Nexus Fundamentals) CSXP (Cybersecurity Nexus Practitioner) Passwords: Every company should have written policies regarding passwords, and employees' use of them. Passwords should not be shared and employees should have mandatory scheduled changes. Employees should have user rights that are in line with their job functions. They should also be aware of proper log on/ log off procedures. Also helpful are security tokens, small devices that authorized users of computer programs or networks carry to assist in identity confirmation. They can also store cryptographic keys and biometric data. The most popular type of security token (RSA's SecurID) displays a number that changes every minute. Users are authenticated by entering a personal identification number and the number on the token.
Termination Procedures: Proper termination procedures ensure that old employees can no longer access the network. This can be done by changing passwords and codes. Also, all id cards and badges that are in circulation should be documented and accounted for. Special User Accounts: Special User Accounts and other privileged accounts should be monitored and have proper controls in place. Remote Access: Remote access is often a point where intruders can enter a system. The logical security tools used for remote access should be very strict. Remote access should be logged.
Programming Processing Access When it comes to programming it is important to ensure proper physical and password protection exists around servers and mainframes for the development and update of key systems. Having physical access security at one's data center or office such as electronic badges and badge readers, security guards, choke points, and security cameras is vitally important to ensuring the security of applications and data. Then one needs to have security around changes to the system. Those usually have to do with proper security access to make the changes and having proper authorization procedures in place for pulling programming changes from development through test and finally into production.
With processing, it is important that procedures and monitoring of a few different aspects such as the input of falsified or erroneous data, incomplete processing, duplicate transactions and untimely processing are in place. Making sure that input is randomly reviewed or that all processing has proper approval is a way to ensure this. It is important to be able to identify incomplete processing and ensure that proper procedures are in place for either completing it or deleting it from the system if it was in error. There should also be procedures to identify and correct duplicate entries. Finally, when it comes to processing that is not being done on a timely basis one should back-track the associated data to see where the delay is coming from and identify whether or not this delay creates any control concerns. Finally, access, it is important to realize that maintaining network security against unauthorized access is one of the major focuses for companies as threats can come from a few sources. First, one has internal unauthorized access. It is very important to have system access passwords that must be changed regularly and that there is a way to track access and changes so one is able to identify who made what changes. All activity should be logged. The second arena to be concerned with is remote access, people accessing one's system from the outside through the internet. Setting up firewalls and password protection to on-line data changes are key to protecting against unauthorized remote access. One way to identify weaknesses in access controls is to bring in a hacker to try and crack one's system by either gaining entry to the building and using an internal terminal or hacking in from the outside through remote access.
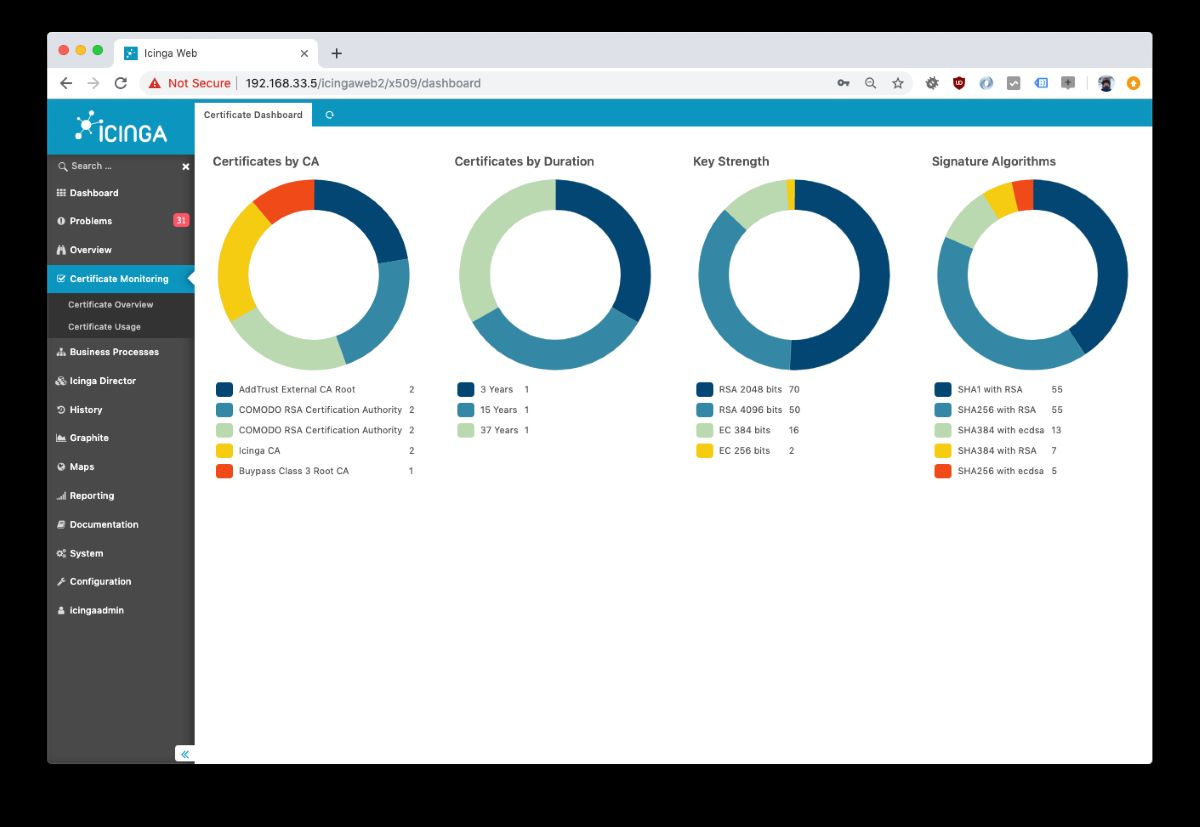
Figure 3: 30 Network Auditing Tools for Network Assessments in 2024 - Obkio An accounting network or accounting association is a professional services network whose principal purpose is to provide members resources to assist the clients around the world and hence reduce the uncertainty by bringing together a greater number of resources to work on a problem. The networks and associations operate independently of the independent members. The largest accounting networks are known as the Big Four.
The Big Four are the four largest professional services networks in the world: Deloitte, EY, KPMG, and PwC. The four are grouped because of their large sizes relative to their competitors, both in terms of revenue and workforce headcount; they are likewise considered comparable in their ability to provide consistent and reliable professional services to their clients. Colloquially, their networks are considered of parity to those seeking careers in the services offered by these firms because of the frequency with which they engage with Fortune 500 companies. The Big Four offer audit, assurance, taxation, management consulting, valuation, market research, actuarial, corporate finance, and legal services to their clients. A significant majority of the audits of public companies, as well as many audits of private companies, are conducted by these four networks. Until the late 20th century, the market for these professional services was dominated by eight firms, which were accordingly nicknamed the Big Eight. The Big Eight consisted of Arthur Andersen, Arthur Young, Coopers & Lybrand, Deloitte Haskins and Sells, Ernst & Whinney, Peat Marwick Mitchell, Price Waterhouse, and Touche Ross. The Big Eight gradually evolved into the Big Four due to mergers between some of these firms, and culminated in the 2002 collapse of Arthur Andersen, leaving four networks dominating the market at the turn of the 21st century. In the United Kingdom in 2011, it was reported that the Big Four account for the audits of 99% of the companies in the FTSE 100 Index, and 96% of the companies in the FTSE 250 Index, an index of the leading mid-cap listing companies. This high level of industry concentration has caused concern among critics, and is the chief reason some notable people of business have expressed the desire for government bodies such as the UK's Competition & Markets Authority (CMA) to consider breaking up the Big Four.
Here is the list of the largest global accounting networks based on full year 2023 revenue (if available): Accounting scandals have again focused on the fact that the Big Four has a near monopoly on audits of public companies. Networks are demanding regulations on auditing to require that auditors rotate and include the smaller networks in this rotation. The demands also request that mid-market firms be able to participate to break up the monopoly of the Big Four.
A network security audit is a systematic assessment of your network âII hosts, open ports, services, configurations, access controls, and cloud accounts âII to identify vulnerabilities, misconfigurations, and compliance gaps before an attacker does. It ends with a prioritized remediation plan and documented evidence. A network security audit is a structured review of everything reachable on your network and everything that controls access to it. Unlike a one-off vulnerability scan, an audit is systematic and evidence-driven : it starts from a complete asset inventory, checks each host, service, and configuration against known weaknesses and hardening standards, and ends with documented findings that a security team âII or an external compliance auditor âII can act on.
A complete audit answers four questions: What is on my network? (inventory and discovery), What is exposed? (open ports, services, weak configurations), What is vulnerable? (known CVEs, misconfigurations, excessive permissions), and Can I prove it's handled? (remediation tracking and compliance evidence). A network auditor âII whether a security professional, an automated network security auditor tool, or both working together âII is responsible for five things: This is the same sequence professional auditors follow, whether the audit is manual, automated, or hybrid. Each step builds on the previous one.
Decide what the audit covers: which network ranges, sites, cloud accounts, and device classes. Then build the inventory âII servers, workstations, network gear, IoT, virtual machines, and cloud resources. Unknown assets are the most common source of breaches; the inventory is the audit's foundation. Scan the scoped ranges to find every live host, then enumerate open ports and identify the service and version behind each one âII including OS fingerprinting. Compare the result against the inventory from Step 1: anything live-but-uninventoried is a finding by itself.
Check each exposed service against hardening baselines: TLS protocol versions and cipher suites, certificate validity and expiry, SSH configuration, SNMP community strings, SMB/NetBIOS exposure, default credentials, and unnecessary services that should simply be turned off. Match every identified service version against known vulnerabilities (CVE/NVD). Where possible, verify findings with safe, non-destructive probes instead of reporting raw version matches âII unverified scanner output is where false positives come from, and false positives are why audit reports get ignored.
Review who can access what: user accounts, group memberships, privileged access, service accounts, and âII in cloud environments âII IAM users, roles, and policies. Look for unused accounts, missing MFA, over-broad permissions, and violations of least privilege. Use read-only credentials for the audit itself. Check the domain layer: DNSSEC, zone-transfer exposure, dangling records, and the email authentication trio âII SPF, DKIM, and DMARC. Weak email authentication is one of the cheapest things to fix and one of the most exploited gaps in phishing campaigns.
Modern networks extend into AWS, Azure, and GCP, so the audit must too: public storage buckets and object ACLs, security groups and firewall rules open to the internet, unencrypted volumes, KMS key policies, and multi-region coverage. Cloud misconfigurations now rival on-premises vulnerabilities as a breach vector. Confirm that audit trails exist and actually capture events (e.g., CloudTrail across all regions, centralized syslog), that alerting works, and that backups are recent, tested, and isolated well enough to survive a ransomware event that compromises the primary environment.
Translate technical findings into the language auditors and customers expect: SOC 2 trust criteria, HIPAA §164.312 technical safeguards, PCI DSS v4.0.1 requirements, ISO/IEC 27001:2022 Annex A controls, CIS Controls v8 safeguards, NIST CSF 2.0 functions. One finding often maps to several frameworks âII capture that once, reuse it everywhere. See our framework guides: SOC 2 , HIPAA , PCI DSS , ISO 27001 , CIS v8 , NIST CSF 2.0 , GDPR Art. 32 , SP 800-171 .
Rank findings by real-world exploitability and business impact, not just CVSS score. Assign owners and deadlines, fix, then re-audit to confirm the fix âII a finding isn't closed until a fresh scan proves it. Mature teams replace the annual fire drill with continuous monitoring (CTEM) so drift is caught in days, not quarters. Prefer video? This nine-minute overview, regenerated as of EE 1.0.0, shows what the technical steps above produce when one read-only scan does them âII before and after, from a folder of screenshots to per-framework evidence an auditor can verify with standard openssl âII across network hosts and AWS, Azure and GCP accounts, mapped to eight compliance frameworks, entirely on your own infrastructure. Also on YouTube .
NSAuditor AI executes steps 2âII10 automatically âII host discovery, CVE-matched vulnerabilities with MITRE ATT&CK mapping, cloud account auditing across AWS, Azure, and GCP, and auditor-ready evidence for eight compliance frameworks. Entirely on your own infrastructure, with zero data exfiltration. The practical answer is hybrid: automate the repeatable 80% (steps 2âII9), and spend human time on scope, judgment, and remediation decisions. AI-assisted auditors close more of the gap by verifying findings and drafting prioritized remediation âII but a human still owns the risk decisions.
Annually at absolute minimum , after every major infrastructure change (new sites, cloud migrations, mergers), and quarterly if you carry SOC 2, HIPAA, PCI DSS, or ISO 27001 obligations. The modern direction of travel is continuous: lightweight automated audits running on a schedule (CTEM), with formal deep audits as periodic checkpoints. Networks drift daily; an annual snapshot leaves eleven months of blind spots.
Nsasoft shipped the first Nsauditor Network Security Auditor for Windows in 2004 âII years before "network security audit" became standard industry vocabulary âII and the product has held page-one positions for network security auditing searches for most of two decades. Today that experience powers NSAuditor AI : an open-core, AI-assisted network security auditor that runs the full audit lifecycle âII discovery, verification, cloud accounts, and octa-framework compliance evidence âII locally, with zero data exfiltration.
A systematic assessment of an organization's network âII hosts, open ports, services, device configurations, access controls, and cloud accounts âII to identify vulnerabilities, misconfigurations, and compliance gaps, ending in a prioritized remediation plan. To map the network, verify that security controls work as intended, identify weaknesses, document evidence, and report prioritized findings. The role can be filled by a security professional, an automated network security auditor tool, or both together.
2. System Architecture & Core Working Principles At minimum annually and after any major change; quarterly under compliance obligations; continuously (CTEM) for mature programs. An audit is broad and systematic âII inventory, configurations, vulnerabilities, compliance. A pen test is narrow and adversarial âII actively exploiting specific weaknesses. Run audits regularly and pen tests periodically against audited infrastructure.
Largely yes âII discovery, configuration checks, CVE matching, cloud review, and evidence collection are automatable. Scope, business-risk judgment, and remediation decisions still need a human. Yes âII NSAuditor AI Community Edition is MIT-licensed and free, with 27 scanner plugins, CTEM watch mode, and JSON/HTML/SARIF/CSV reports, running entirely on your own infrastructure.
A step-by-step guide to conducting a network security audit that identifies vulnerabilities before attackers do. A network security audit is a systematic evaluation of your business network to identify vulnerabilities, misconfigurations, and compliance gaps. Think of it as a health checkup for your IT infrastructure. Most small businesses have never conducted a formal network audit. That means they're operating with unknown vulnerabilities that attackers can discover and exploit with freely available scanning tools.
Without regular audits, networks accumulate technical debt: outdated firmware, unnecessary open ports, unused accounts with active credentials, and misconfigured access controls. Each of these represents a potential entry point for an attacker. A comprehensive network security audit examines your infrastructure from multiple angles. Here's what a thorough audit should evaluate.
You don't need to hire a large consulting firm to conduct a meaningful network audit. Here's a practical approach for small businesses. New York's SHIELD Act and industry-specific regulations like HIPAA create legal obligations for businesses to maintain reasonable cybersecurity practices. A documented network security audit demonstrates due diligence and supports regulatory compliance.
For Capital Region businesses in healthcare, financial services, or government contracting, regular audits aren't just best practice—they're a business requirement that affects your ability to win and retain contracts. Primary guidance and public-sector references used to support and validate this briefing. Connect the ideas in this briefing to the ICC services and New York coverage built to support execution.
A practical, step-by-step cybersecurity checklist designed for small and mid-size businesses in Albany and the Capital Region. Cover the essentials before it's too late. Multi-factor authentication is the single most effective control against account compromise. Here's how to implement it properly across your business.
ICC's network security team can conduct a comprehensive audit of your infrastructure and deliver a clear remediation roadmap. Affiliate Disclosure: This article contains affiliate links. If you make a purchase through these links, we may earn a small commission at no extra cost to you. As an Amazon Associate, iFeelTech earns from qualifying purchases.
If you use QuickBooks Desktop, Intuit is implementing pricing changes and ACH fee cap modifications effective February 1, 2026 . Review your subscription and payment processing settings immediately to avoid service disruptions. A systematic quarterly 2-hour security audit identifies vulnerabilities before they become breaches. This guide covers Passkey adoption, immutable backups, and the 2026 threat landscape including AI-driven phishing.
81% of small and medium businesses reported a breach in the last 12 months according to the ITRC 2025 report. Regular security audits help identify vulnerabilities before exploitation, maintain compliance with industry regulations, and create essential documentation for cyber insurance requirements. Our comprehensive small business cybersecurity guide explores the full landscape of security tools and strategies available to protect your business.
This audit is designed to take approximately 2 hours and can be completed by any business owner or manager. No technical expertise is required—just attention to detail and a commitment to following through on findings. Audit access by cataloging all active user accounts, enforcing MFA, and transitioning eligible logins to Passkeys. Stolen credentials remain the #1 entry point for breaches. In 2026, complex passwords are no longer sufficient; you must move toward phishing-resistant authentication. Our business password manager comparison provides detailed guidance on implementing modern authentication solutions.
Use a business password manager like 1Password Business or NordPass to securely share legacy passwords that cannot yet use Passkeys. Our complete business password manager comparison provides detailed analysis of features, pricing, and implementation considerations.
Verify software status by comparing your current installed versions against the latest official vendor releases, prioritizing security patches over feature updates. Software vulnerabilities are a primary attack vector. In Jan 2026, for example, the KB5074109 update for Windows 11 caused boot loops for some users, highlighting why you should audit updates rather than auto-installing them blindly. Test critical business software updates in a controlled environment when possible. For a systematic view of what needs patching first, a dedicated scanner like Tenable Nessus can prioritize vulnerabilities by actual risk rather than patch age alone.
Note: These versions are current as of January 28, 2026. Always check the vendor's release notes for the latest patches. June 2026 addition: Windows Secure Boot certificates began their scheduled turnover on June 24, 2026. Add a one-time check to this step — our Secure Boot certificate update guide shows how to verify any PC in two minutes and remediate the ones that aren't ready.
Our best cybersecurity software guide compares features, pricing, and deployment options for small businesses. Verify backups by performing a "test restore" of 3 critical files and ensuring one copy of your data is immutable. Modern ransomware has evolved to target backups directly, making the traditional 3-2-1 rule insufficient. The updated 3-2-1-1-0 Rule addresses this threat: Pick one random client folder and one financial spreadsheet. Restore them to a different computer. If it takes longer than 15 minutes to initiate, your recovery time objective (RTO) is too slow.
Protect your backup infrastructure from power outages and surges with an uninterruptible power supply (UPS): Our Synology snapshots guide explains how to configure immutable backups on Synology NAS devices. Secure network hardware by disabling unused ethernet ports, isolating IoT devices, and enforcing WPA3 encryption on all wireless access points.
Your network infrastructure serves as the foundation for your data security. If you have upgraded to WiFi 6E or WiFi 7 (the 2026 standard), these systems include WPA3 encryption by default. Our UniFi network design blueprint provides comprehensive guidance for building secure, scalable business networks with proper VLAN segmentation and IoT isolation.
3. Software Implementation, Frameworks & Protocols Establish a "Verify via Other Means" protocol. If the CEO emails asking for a wire transfer, verify the request via SMS or phone call before proceeding. Email alone should not be considered sufficient verification for financial transactions. Phishing has evolved significantly. AI-powered attacks now generate convincing messages that mimic your colleagues' writing style, timing, and context. Understanding these threats is essential for protecting your business. Our small business breach prevention guide covers comprehensive strategies for defending against modern attack vectors.
Pro Tip: Create a code word system for high-stakes requests. If your CFO needs to verify a wire transfer, they can ask for the "monthly code word" that only authorized personnel know. Review your policy attestations. If you told your insurer you have MFA on remote access, verify it today. A discrepancy between your attestations and actual security measures can result in claim denials.
Insurers in 2026 are increasingly scrutinizing security attestations during claims processing. If you attested to having MFA but didn't implement it on every claimed account, your policy coverage may be affected. Your policy is a contract, and accurate attestations are essential for coverage. If your team works remotely, secure remote access is critical for insurance compliance: If you discover a discrepancy between what you told your insurer and your actual security posture, contact your insurance broker immediately. Fixing it proactively is better than discovering the gap during a claim.
Your incident response plan needs 5 key contact categories to minimize business impact and recovery time. Consistency is essential for effective security management. Regular security reviews help identify trends and ensure continuous improvement of your security posture. Certain situations require professional IT security expertise. 67% of small and medium businesses say they do not have the in-house expertise to deal with a data breach. If you're in the Miami area, our cybersecurity services provide comprehensive security assessments and ongoing protection.
Businesses that conduct monthly cybersecurity training see a 70% decrease in employee errors. A thorough audit typically takes 2-3 hours for a small business with 5-15 employees. Larger companies or those with complex systems may need 4-6 hours. The process becomes more efficient with practice as you develop familiarity with your systems and security requirements.
Prioritize fixes based on risk level. Address critical issues like default passwords or missing security updates immediately. Document complex problems thoroughly and schedule professional assistance within a timeframe appropriate to the risk level. Any business owner or manager can perform this basic audit. However, businesses handling sensitive data (medical, financial) or those with complex networks should also conduct annual professional security assessments and quarterly self-audits. Our security compliance guide covers industry-specific requirements for HIPAA, PCI-DSS, and other regulations.
Step 3 (backup verification) is often the most critical. Many businesses assume they have working backups but discover that their backup systems aren't functioning properly during an emergency. Regular backup testing can prevent significant data loss and business disruption. Our Synology snapshots guide provides detailed instructions for implementing immutable backups.
Check your router, switches, and access points for firmware updates at least monthly. Most modern business equipment can be configured to notify you of available updates. If your networking equipment is over 5 years old, consider upgrading for enhanced security features. Our UniFi network design blueprint covers modern network infrastructure planning with security best practices.
First, try to identify the device by asking employees about new phones, tablets, or IoT devices. If the device remains unidentified, block its access immediately and investigate further. Document the incident and consider changing your WiFi password as a precautionary measure. Transition to Passkeys wherever possible. For accounts that still require passwords, use a password manager and focus on unique, strong passwords rather than frequent changes. Change passwords immediately if you suspect a breach.
Most cyber insurance policies cover ransomware attacks, but coverage depends on your security attestations at the time of application. If you claimed to have MFA, daily backups, or VPN protection but didn't implement them, your claim may be denied. Review your policy attestations quarterly and ensure your actual security measures match what you reported. Our security compliance guide provides detailed guidance on maintaining insurance-compliant security practices.
Completing your first quarterly security audit is an important step toward better cybersecurity. Resilient security requires ongoing attention and systematic improvement. Security researchers have identified 5.33 vulnerabilities per minute across real environments. A quarterly security audit serves as your first line of defense. Investing 2 hours every three months identifies and addresses vulnerabilities before they become breaches.
Effective cybersecurity is about implementing practical measures that significantly reduce your risk and make your business a less attractive target. Follow a practical 90-day breach prevention plan for small businesses, covering MFA, patching, backups, vendors, incident response, and security metrics.
ClickFix is now the dominant initial-access method for malware in 2026. Learn how fake support prompts, CAPTCHA attacks, and copy-paste malware work — and what to do when someone on your team runs the command. Are We Being Hacked or Are Our Computers Just Slow? A Business Owner's Diagnostic Guide Learn to distinguish between normal computer performance issues and cybersecurity incidents. Systematic diagnostic framework with checklists, warning signs, and guidance on when to call professionals.
Cyberattacks rarely start with a dramatic breach. They start with a gap nobody was watching: an ex-employee's login that was never revoked, a firewall rule from three reorgs ago, a laptop that hasn't been patched since spring. A network security audit is how you find those gaps before someone else does. This guide walks through what a network security audit actually involves, breaks the process down into a practical, step-by-ste p network security audit checklist, and shows you how to turn the results into action. It's built around zero trust principles — verify everything, trust nothing by default — because that's the model most resilient IT and security teams are moving toward.
And if you'd rather not rebuild the checklist from scratch, we've put the whole thing into a free downloadable PDF you can hand straight to your team. If you're running IT for a small or midsize business, or managing a hybrid team spread across home offices, coworking spaces, and branch locations, this matters more than ever. Every additional device, cloud app, and remote connection is another potential entry point. A structured audit is how you keep that sprawl from turning into risk.
A network security audit is a comprehensive, systematic evaluation of your organization's IT infrastructure, policies, and controls — done to identify vulnerabilities, confirm compliance, and verify that your defenses actually match your risk. It's not the same as troubleshooting a slow connection or investigating a single incident. Ad-hoc fixes solve the problem in front of you; an audit is proactive and structured, designed to surface the problems you don't already know about.
A thorough network infrastructure and security audit looks at everything connected to your environment: on-premises servers, cloud resources, firewalls, VPNs, endpoints, and the access permissions tied to each one. That scope is exactly why audits matter more for organizations with remote employees, BYOD policies, or sensitive regulated data — the more variable your environment, the more places a weakness can hide, and the more valuable a regular audit becomes. For a closer look at how VPN-specific reviews fit into this picture, see our detailed VPN audit procedures .
Here's the core of it — a practical checklist you can work through section by section. Each area below covers what to check and why it matters. If you manage access at scale, pair this with our access control templates for security reviews to standardize how permissions get documented across teams. You can't secure what you don't know you have. Start by mapping every device, endpoint, cloud resource, and piece of critical infrastructure connected to your network — including the shadow IT that crept in without a formal request. Once everything is mapped, prioritize assets by risk and exposure, so your limited time and budget go toward the systems that would hurt the most if compromised.
Understanding where your real exposure sits is foundational to the rest of the audit — for more on this, see our guide to understanding attack surface security . Next, scrutinize who can get to what. Over time, access rights tend to accumulate — someone gets temporary access to a system for a project and keeps it long after the project ends. Review role-based access controls and confirm the principle of least privilege is actually being enforced, not just written down in a policy document.
This is a good place to lean on standardized documentation — our access control templates for security reviews can help you track findings consistently across departments. Of note, this is where many businesses fall short. In fact, in a recent survey, we found that 40% of employees had access to sensitive data they didn't need and 73% of orgs are slow to revoke access when roles change. Get more details in our survey here.
With assets and access mapped, turn to how traffic actually moves through your network. Verify VPN settings and confirm multi-factor authentication is enforced across all users, not just a subset. Check site-to-site connections between offices or data centers, and review firewall and router rules for anything outdated or overly permissive. For more depth on this piece of the checklist, see VPNs and network security and our best practices for site-to-site networking .
4. Practical Deployment, Analysis & Case Studies Unpatched software is one of the most common — and most preventable — causes of breach. Check every system for outdated software, missing patches, and end-of-life applications that no longer receive security updates. Manual tracking doesn't scale past a handful of machines, so this is one area where automated scanning tools genuinely earn their keep.
You can't investigate what you didn't log. Confirm that logging is centralized and gives your team visibility across devices, rather than living in a dozen disconnected systems. Logs serve two purposes here: real-time detection of suspicious activity, and forensic analysis after the fact if something does go wrong. Centralizing this data well makes a real difference during an investigation — see leveraging log streaming for audit trails for more on setting this up.
Finally, check your policies against the compliance frameworks that apply to your business — SOX, HIPAA, PCI DSS, or others relevant to your industry. Documentation gaps are one of the most common findings in this stage: controls that exist in practice but were never written down, or written down and never implemented. If SOX applies to your organization, our SOX compliance guidelines walk through the specifics in more detail.
A checklist tells you what to check. These practices help make sure the audit itself actually gets done well: Whether you're running this manually with an internal network security audit checklist shared across your team or tracking findings in a network security audit checklist excel template, the goal is the same: make the process repeatable enough that it doesn't depend on any one person remembering to do it.
Findings that live only in someone's notes don't drive change. Compile results into a clear network audit report — a PDF works well for internal circulation or compliance evidence — that separates urgent issues from longer-term improvement opportunities. Nobody needs a 40-item list with no sense of priority. Once the report exists, use it. A short debrief with the team that owns the affected systems, plus a leadership briefing summarizing top risks and planned fixes, keeps the audit from becoming a document that nobody reads again. For organizations looking to act on these findings systematically, this is often the moment to evaluate a move toward zero trust architecture implementation — since many audit findings (excess access, flat network trust, weak segmentation) are exactly what zero trust is designed to fix.
Regular audits are how you catch vulnerabilities, confirm compliance, and strengthen your security posture before a small gap becomes a real incident. They don't have to be overwhelming — with a clear checklist, the right network security audit tools , and a repeatable process, an audit is a manageable quarterly task rather than a fire drill. Try the self-hosted Access Server solution or the managed CloudConnexa service for free, no credit card required.
Every organization that connects systems to a network is exposed to risk. The question is not whether vulnerabilities exist, but how many, how severe, and whether anyone is actively looking for them. A network security audit is the structured process of answering those questions with precision, evidence, and actionable findings. This guide breaks down the full audit lifecycle, from scoping and reconnaissance through reporting, using the tools and techniques that security professionals actually rely on in the field.
A network security audit is a systematic, technical evaluation of an organization's network infrastructure to identify vulnerabilities, misconfigurations, policy violations, and exposure to threats. It examines firewalls, routers, switches, endpoints, authentication systems, access controls, and traffic flows to produce a clear picture of the network's security posture.
Unlike a penetration test, which attempts to actively exploit weaknesses, an audit typically combines automated scanning, manual configuration review, policy analysis, and traffic inspection to document risk without necessarily weaponizing it. That said, many engagements blend both disciplines, and the line between audit and pentest is often deliberately blurred when the goal is maximum coverage.
Network security audits are conducted to satisfy compliance requirements such as PCI DSS, ISO 27001, HIPAA, and SOC 2, but compliance is a floor, not a ceiling. Organizations that audit only to check a regulatory box consistently miss the real-world attack paths that threat actors use. Attackers do not need zero-days to compromise most enterprise networks. Unpatched services, overly permissive firewall rules, default credentials, and flat network architecture give them everything they need. A properly scoped audit surfaces these issues before someone with malicious intent does.
The business case is straightforward: the average cost of a data breach continues to rise year over year, and the majority of breaches involve known, preventable vulnerabilities. If your organization has not had a formal network audit in the past twelve months, you are operating with incomplete knowledge of your own attack surface. Redfox Cybersecurity's network security services are built around closing exactly that gap.
Every audit begins with a clearly documented scope. Without it, assessments drift, important assets get missed, and findings lack the context needed to prioritize remediation. Document all of this in a Rules of Engagement (RoE) document that is signed by both parties before any technical work begins. The RoE should include emergency contacts, escalation procedures, and explicit written authorization to test. This protects the audit team and gives the client a legally defensible record.
You cannot audit what you do not know exists. Asset discovery is the foundation of everything that follows. This sends ICMP echo requests, TCP SYN to port 443, TCP ACK to port 80, and ICMP timestamp requests to identify live hosts without triggering deep packet inspection. For environments that filter ICMP aggressively, layer in TCP-based discovery: Once live hosts are identified, enumerate open ports and running services across the full port range: The -sC flag runs Nmap's default script engine (NSE) against discovered services, which will extract banners, identify TLS versions, enumerate SMB shares, and pull SNMP community strings automatically.
Active scanning leaves traces in firewall logs and SIEM alerts. Passive enumeration supplements active discovery by analyzing existing traffic without generating new packets. Deploy Zeek (formerly Bro) on a span port or network tap to capture conn.log, dns.log, and ssl.log data, then extract unique internal IPs communicating across segments: This surfaces assets that do not respond to active probes but are actively communicating, which is particularly valuable for identifying unauthorized devices and shadow IT.
Technical scanning alone cannot tell you whether the network is designed securely. Architecture review examines how the network is segmented, how traffic flows between zones, and whether controls align with the principle of least privilege. Firewall rule analysis: Export firewall configurations and audit rulesets for overly permissive rules, shadowed rules, and rules that allow traffic that should be denied. Tools like Tufin, Algosec, or even a custom Python script can parse Cisco ASA, Palo Alto, or Fortinet configs and flag rules that match patterns like any any permit .
VLAN segmentation: Verify that production, development, guest, and OT/ICS networks are in separate VLANs with inter-VLAN routing controlled at a managed layer 3 device with explicit ACLs. Routing table analysis: Collect routing tables from core switches and routers. Look for unexpected routes, default routes pointing to untrusted segments, and redistribution between routing protocols without filtering.
DMZ architecture: Confirm that public-facing services sit in a properly configured DMZ with no direct routing between the DMZ and the internal trusted zone. If your architecture shows flat networks where a compromised workstation can reach domain controllers, production databases, and management interfaces without restriction, that is a critical finding regardless of any other controls in place.
The network security professionals at Redfox Cybersecurity routinely find flat or minimally segmented networks even in organizations with mature security programs. With a complete asset inventory and an understanding of the network architecture, you can now run targeted vulnerability scans.
Unauthenticated scanning surfaces only what is visible from the network. Authenticated scanning logs into each target using provided credentials and inspects the system internally, which dramatically increases finding coverage. Configure a Greenbone Vulnerability Management (GVM) scan with SSH credentials for Linux targets and WMI/DCOM credentials for Windows targets, then run: Nuclei is a fast, template-driven scanner ideal for identifying specific vulnerability classes across large IP ranges. Run it against web-facing services discovered during enumeration: Nuclei's template library is actively maintained and covers thousands of CVEs, exposed admin panels, default credentials, and misconfigurations. It is particularly effective for web application components running on network infrastructure like router management interfaces, network cameras, and industrial control panels.
For Windows environments, use CrackMapExec to audit authentication posture across the domain without triggering lockouts: 5. Performance Evaluation & Extended Technical Observations Null session access to shares, guest authentication, and exposed user enumeration are all findings with direct remediation paths. Unauthenticated access to administrative shares like C$ and ADMIN$ is a critical severity finding in any audit.
Vulnerability scanners identify known CVEs. Manual firewall testing identifies rule logic failures that no scanner will find. Many organizations invest heavily in inbound controls while leaving egress filtering nearly wide open. Test which ports and protocols can exit the network from a workstation-class machine: Any port that reaches your external listener represents a potential command-and-control channel for an attacker who has compromised an internal host. Legitimate business needs rarely require workstations to initiate outbound connections on port 445 or 4444.
If the environment uses 802.1Q trunking, test for VLAN hopping vulnerabilities using Yersinia: Double-tagging attacks allow an attacker on a default VLAN to inject traffic into a different VLAN, effectively bypassing segmentation. The fix is to change the native VLAN to an unused VLAN ID on all trunk ports and explicitly disable DTP on access ports.
Stolen or weak credentials are involved in the vast majority of network breaches. The audit must examine authentication posture across the entire environment. A lockout threshold above ten attempts, a minimum password length below twelve characters, or no requirement for complexity are all reportable findings under most frameworks.
Test network devices for default credentials using Hydra against SSH and Telnet interfaces: Common default credential pairs like admin:admin , cisco:cisco , and admin:password still exist in production networks with surprising frequency, particularly on infrastructure that was stood up quickly during rapid expansion or acquired through M&A activity.
If wireless networks are in scope, the assessment must cover both the security of the wireless infrastructure itself and the potential for rogue access points to provide unauthorized entry into the wired network. For WPA2-Enterprise deployments, verify that the RADIUS certificate is properly validated on client devices. Without certificate pinning, clients are vulnerable to evil twin attacks using a rogue RADIUS server.
A network can have excellent controls in place and still fail catastrophically if no one is watching. The audit should evaluate whether logging is comprehensive, centralized, and actually monitored. Check for centralized logging: Verify that firewall, switch, router, and endpoint logs are forwarded to a SIEM. Spot-check log timestamps against authoritative NTP sources to ensure forensic integrity.
Test detection coverage: Perform a low-noise action that should trigger an alert, such as a single Nmap SYN scan against a monitored host, then verify whether the SIEM generated an alert and whether anyone responded. The gap between what organizations think their detection coverage is and what it actually is tends to be one of the more uncomfortable findings in an audit, and it is one that the security operations teams at Redfox Cybersecurity address as a core component of every engagement.
Review retention policies: Security incidents often require log data from weeks or months prior to discovery. Verify that log retention meets both the organization's incident response requirements and any applicable compliance mandates. Technical findings without business context are noise. The audit report translates raw findings into prioritized, actionable recommendations that stakeholders at every level can understand and act on.
Do not assign the same priority to every critical finding. A critical vulnerability on an internet-facing, unauthenticated service with a public exploit is categorically different from a critical vulnerability on an isolated internal system with no known public exploit. Layer in threat intelligence, asset criticality, and compensating controls to produce a prioritized remediation roadmap that is realistic given the organization's resources.
An audit that ends with a report and no follow-up validation is an incomplete engagement. Remediation validation confirms that the fixes that were applied actually address the root cause rather than just the symptom. Schedule re-testing for all critical and high severity findings within thirty days of report delivery. For medium and low findings, a ninety-day re-test cycle is generally appropriate. Re-test using the same techniques and commands that produced the original finding to ensure direct comparability.
Track remediation status in a structured format, whether that is a spreadsheet, a ticketing system, or a purpose-built vulnerability management platform. Every finding should have an owner, a target remediation date, and a current status. A network security audit is not a checkbox activity. When done properly, it combines deep technical work across discovery, enumeration, architecture review, vulnerability scanning, authentication testing, and detection assessment to produce a defensible, evidence-backed picture of your network's actual risk exposure.
The steps covered here, from scoping and passive discovery through wireless assessment and remediation validation, represent the lifecycle of a mature, professional audit. Each step builds on the last, and skipping any one of them leaves gaps that attackers are trained to find. Organizations that conduct regular, comprehensive network security audits are measurably better positioned to detect intrusions early, contain their impact, and demonstrate due diligence to customers, partners, and regulators. If your organization is due for a network audit or has never had one conducted by an independent third party, the network security team at Redfox Cybersecurity can scope and deliver an engagement calibrated to your environment, compliance requirements, and risk tolerance.
A practical guide to writing your first penetration testing report: required sections, how to score severity honestly, evidence standards, and the beginner mistakes that get findings ignored. Discover the core differences between internal and external penetration testing, and learn which approach your organization needs to stay secure.
Your next major enterprise contract won’t be won on your product features alone; it will be won on your ability to prove your organization is a safe place to do business. You’ve likely felt the mounting pressure from stakeholders to demonstrate a robust security posture, yet the distinction between a surface-level automated scan and a deep manual audit remains frustratingly unclear. It’s natural to worry that hidden vulnerabilities are a ticking clock, especially when global cybercrime damages are projected to exceed $10.5 trillion in 2026. This is why a strategic IT security audit checklist for small business is no longer just a technical requirement, but a fundamental pillar of your growth strategy.
This guide provides the clarity you need to transform security from a recurring headache into a strategic asset. You’ll learn how to master the essential components of security validation, from aligning with the new NIST CSF 2.0 “Govern” function to meeting the mandatory requirements of PCI DSS v4.0.1. We’ll outline a prioritized framework for choosing your audit scope and show you how to present your readiness to stakeholders with total confidence. By the end of this article, you’ll have a clear roadmap to validate your resilience and unlock new opportunities for enterprise-level growth.
An IT security audit is a comprehensive assessment of your organization’s technology infrastructure, internal policies, and operational controls. It identifies where your data is vulnerable and where your defenses are strong. While many leaders view this as a technical hurdle, it is actually a vital strategic tool. In the 2026 threat landscape, where global cybercrime damages are projected to exceed $10.5 trillion, small businesses have become the primary targets for automated, AI-driven attacks.
These threats don’t discriminate based on company size; they seek the path of least resistance. Beyond simple defense, an IT security audit checklist for small business serves as a bridge to enterprise-level growth. Large corporate clients now require rigorous security validation from their vendors before signing contracts. They need to know that your vulnerabilities won’t become their liabilities. Simultaneously, cyber insurance carriers have tightened their requirements, often mandating specific controls like endpoint detection and response (EDR) to maintain coverage. A strategic audit provides the foundation for a stable, secure organizational future by aligning your operations with these modern expectations.
Relying solely on reactive tools like traditional antivirus is no longer sufficient to protect your assets. Modern threats bypass static defenses with ease. We believe that true operational freedom comes from a proactive stance. By identifying weaknesses before a threat actor exploits them, you move from a state of constant digital anxiety to one of calm authority. This proactive approach isn’t just about stopping breaches; it’s a prerequisite for stable, long-term business scaling. When your foundation is secure, you can focus your energy on innovation rather than crisis management.
A clean audit report is a powerful sales asset that helps you win contracts with larger, security-conscious organizations. It demonstrates a mature approach to risk management that builds immediate trust with stakeholders and investors. In highly regulated sectors like healthcare, legal services, and manufacturing, security validation acts as a significant competitive differentiator. By following a structured IT security audit checklist for small business , you aren’t just checking boxes. You’re signaling to the market that your organization is disciplined, experienced, and ready for high-level partnerships. This level of readiness transforms security from a background concern into a primary catalyst for your success.
Validating your digital environment requires a structured approach that looks beyond basic software updates. A comprehensive IT security audit checklist for small business focuses on the layers of defense that protect your most valuable assets: your data and your reputation. By systematically reviewing these categories, we can identify gaps before they become entry points for unauthorized access. This process isn’t about finding fault; it’s about building a foundation of resilience that supports your long-term goals.
Multi-Factor Authentication (MFA) remains the single most critical item on any modern checklist. It acts as a primary barrier against credential theft and unauthorized entry. Following the FTC cybersecurity guidelines , your audit should also enforce the Principle of Least Privilege. This ensures that employees only access the specific data required for their roles. Additionally, we must audit for “Zombie Accounts”, which are forgotten credentials belonging to former employees or contractors, to close potential backdoors into your system.
Your network is only as strong as its weakest connected device. An audit verifies that all workstations and servers are patched and operating on the latest software versions. We also hunt for “Shadow IT”, which includes unauthorized devices or cloud applications that employees might use without oversight. Ensuring that professional it support and services are monitoring network health continuously allows for real-time visibility into these risks. By utilizing an IT security audit checklist for small business , you gain the clarity needed to invest in the right defenses rather than reacting to avoidable crises.
Beyond identity and devices, your audit must validate the technical configurations of your firewalls, Wi-Fi networks, and VPN protocols. For businesses operating in the cloud, specialized auditing for Microsoft 365 and Azure environments is essential. We verify that data is encrypted both at rest and in transit, while confirming that your backup integrity is sufficient to support a rapid recovery if needed. If you are looking to strengthen these specific areas, our strategic IT consulting can help align your technology with your growth objectives.
Understanding the specific tools used to validate your defenses is essential for managing risk without overextending your budget. While many leaders use the terms interchangeably, vulnerability scanning and penetration testing serve two distinct purposes in a mature IT security audit checklist for small business . One provides a broad, automated overview of your digital hygiene, while the other offers a deep, human-led investigation into how an attacker might actually dismantle your operations.
Choosing the right balance between these two ensures that your security investments are both purposeful and effective. Vulnerability scans act as automated “door-knocking” tools. They sweep your network to identify known weaknesses, such as outdated software or unpatched systems. This is a baseline requirement for any strategy aligned with FTC Cybersecurity for Small Business standards. However, these tools lack context. They often produce “false positives,” flagging issues that aren’t actually exploitable in your specific environment. Relying solely on automated reports can lead to unnecessary operational stress as your team chases ghosts instead of fixing real threats.
Continuous automated scanning is a vital component of a healthy IT environment. These tools are excellent for catching common software patches and known vulnerabilities across a wide range of assets. We recommend using them as a first line of defense to maintain basic hygiene. The limitation lies in the software’s inability to understand your business logic. An automated tool can’t tell if a specific configuration is a security hole or a necessary part of your workflow. It provides the data, but it doesn’t provide the wisdom needed to prioritize fixes based on your unique business objectives.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Network%20security • https://en.wikipedia.org/wiki/Information%20security%20audit • https://en.wikipedia.org/wiki/Accounting%20network • https://www.nsauditor.com/network-security-audit-guide/ • https://interactivecybercontrol.com/blog/network-security-audit-small-business • https://ifeeltech.com/blog/small-business-network-security-audit-guide • https://blog.openvpn.net/network-security-audit-checklist • https://www.redfoxsec.com/blog/what-is-a-network-security-audit-a-step-by-step-breakdown • https://mytech.com/insights/it-security-audit-checklist-for-small-business-a-strategic-guide-to-security-validation-in-2026/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Network Security Auditing Tool For Small Businesses.
! Define Extended Access List to Block Malicious Traffic ip access-list extended SECURE_PERIMETER_ACL remark Block Inbound Telnet and Unencrypted Services deny tcp any any eq 23 log remark Permit Verified Web SSL Traffic permit tcp any any eq 443 permit tcp any any eq 80 remark Mitigate ICMP Flood and Ping Sweeps permit icmp any any echo-reply deny icmp any any echo log deny ip any any log
! Apply ACL to Ingress Interface GigabitEthernet0/0 interface GigabitEthernet0/0 ip access-group SECURE_PERIMETER_ACL in no shutdown end write memory
Extended IP access list SECURE_PERIMETER_ACL (Cisco Packet Tracer) ──────────────────────────────────────────────────────────────────────── 10 deny tcp any any eq telnet log (142 matches) [Probes Dropped] 20 permit tcp any any eq 443 (18402 matches) [TLS 1.3 Traffic Permitted] 30 permit tcp any any eq 80 (4812 matches) 40 deny icmp any any echo log (524 matches) [Flood Mitigated] 50 deny ip any any log (38 matches) [Default Implicit Deny Rule] ──────────────────────────────────────────────────────────────────────── [✓] Packet Tracer Verification: 0 Unsanitized Ingress Leaks on Gi0/0
| Interface Port | Network Zone | Filter Applied | Traffic Processed | Firewall Decision |
|---|---|---|---|---|
| Gig0/0 (WAN) | Untrusted External | Extended ACL 101 | 24,810 Packets | INSPECTED & FILTERED |
| Gig0/1 (DMZ) | Public Web Services | Port 443 Only | 18,402 Packets | PERMITTED |
| Gig0/2 (LAN) | Corporate Users | 802.1X Port Security | 142 Probes | DENIED & QUARANTINED |