Complete Technical Paper Content — Network Topology Mapper And Vulnerability Scanner Project
Overview & System Context
Network Topology Mapper And Vulnerability Scanner Project: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~8530 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background In computer science, computer engineering, and telecommunications, a network is a group of communicating computers and peripherals called hosts, which communicate data to other hosts via communication protocols, as facilitated by networking hardware. Within a computer network, hosts are identified by network addresses, which allow networking hardware to locate and identify hosts. Hosts may also have hostnames, memorable labels for the host nodes, which can be mapped to a network address using a hosts file or a name server such as Domain Name Service. The physical medium that supports information exchange includes wired media like copper cables, optical fibers, and wireless radio-frequency media. The arrangement of hosts and hardware within a network architecture is known as the network topology. The first computer network was created in 1940 when George Stibitz connected a terminal at Dartmouth to his Complex Number Calculator at Bell Labs in New York.
Today, almost all computers are connected to a computer network, such as the global Internet or embedded networks such as those found in many modern electronic devices. Many applications have only limited functionality unless they are connected to a network. Networks support applications and services, such as access to the World Wide Web, digital video and audio, application and storage servers, printers, and email and instant messaging applications.
The transmission media used to link devices to form a computer network include electrical cable, optical fiber, and free space. In the OSI model, the software to handle the media is defined at layers 1 and 2 — the physical layer and the data link layer. Common examples of networking technologies include: Ethernet is a widely adopted family of networking technologies that use copper and fiber media in local area networks (LAN).
The media and protocol standards that enable communication between networked devices over Ethernet are defined by IEEE 802.3. Wireless LAN standards, which use radio waves. Some standards use infrared signals as a transmission medium. Power line communication uses a building's power cabling to transmit data. Coaxial cable is widely used for cable television systems, office buildings, and other work-sites for local area networks.
Transmission speed ranges from 200 million bits per second to more than 500 million bits per second. ITU-T G.hn technology uses existing home wiring (coaxial cable, phone lines and power lines) to create a high-speed local area network. Twisted pair cabling is used for wired Ethernet and other standards. It typically consists of 4 pairs of copper cabling that can be utilized for both voice and data transmission. The use of two wires twisted together helps to reduce crosstalk and electromagnetic induction. The transmission speed ranges from 2 Mbit/s to 10 Gbit/s. Twisted pair cabling comes in two forms: unshielded twisted pair (UTP) and shielded twisted-pair (STP). Each form comes in several category ratings, designed for use in various scenarios.
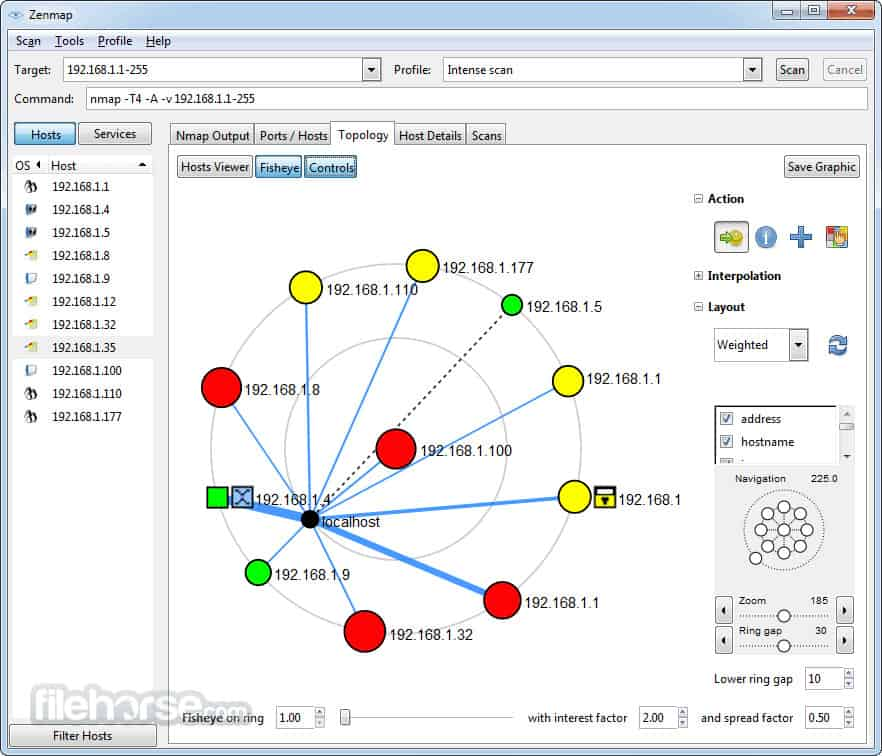
Figure 1: Definitive Guide to Nmap: How it Works & Scanning Basics - Updated 2024 An optical fiber is a glass fiber that carries pulses of light that represent data via lasers and optical amplifiers. Some advantages of optical fibers over metal wires are very low transmission loss and immunity to electrical interference. Using dense wave division multiplexing, optical fibers can simultaneously carry multiple streams of data on different wavelengths of light, which greatly increases the rate that data can be sent to up to trillions of bits per second. Optic fibers can be used for long runs of cable carrying very high data rates, and are used for undersea communications cables to interconnect continents.
There are two basic types of fiber optics, single-mode optical fiber (SMF) and multi-mode optical fiber (MMF). Network connections can be established wirelessly using radio or other electromagnetic means of communication. Terrestrial microwave – Terrestrial microwave communication uses Earth-based transmitters and receivers resembling satellite dishes. Terrestrial microwaves are in the low gigahertz range, which limits all communications to line-of-sight. Relay stations are spaced approximately 40 miles (64 km) apart. Communications satellites – Satellites also communicate via microwave. The satellites are stationed in space, typically in geosynchronous orbit 35,400 km (22,000 mi) above the equator.
These Earth-orbiting systems are capable of receiving and relaying voice, data, and TV signals. Cellular networks use several radio communications technologies. The systems divide the region covered into multiple geographic areas. Each area is served by a low-power transceiver. Radio and spread spectrum technologies – Wireless LANs use a high-frequency radio technology similar to digital cellular. Wireless LANs use spread spectrum technology to enable communication between multiple devices in a limited area. IEEE 802.11 defines a common flavor of open-standards wireless radio-wave technology known as Wi-Fi. Free-space optical communication uses visible or invisible light for communications. In most cases, line-of-sight propagation is used, which limits the physical positioning of communicating devices. Extending the Internet to interplanetary dimensions via radio waves and optical means, the Interplanetary Internet. IP over Avian Carriers was a humorous April fool's Request for Comments, issued as RFC 1149. It was implemented in real life in 2001. The last two cases have a large round-trip delay time, which gives slow two-way communication but does not prevent sending large amounts of information (they can have high throughput).
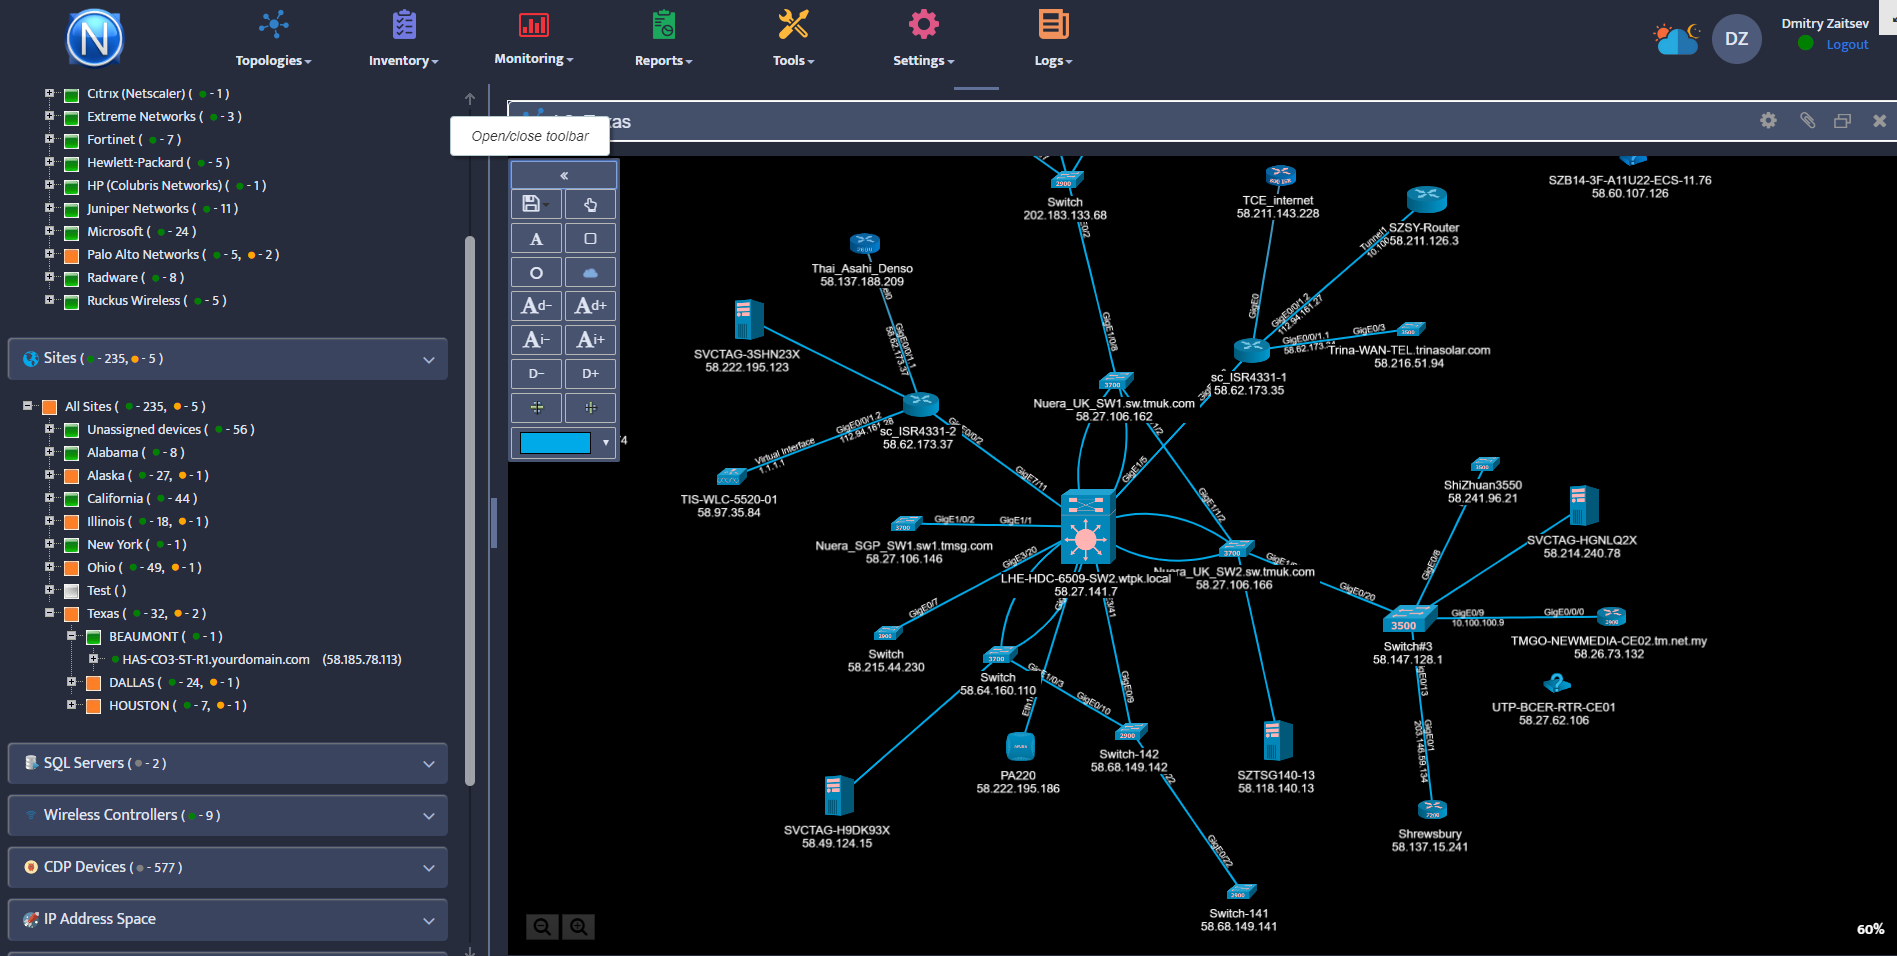
Apart from any physical transmission media, networks are built from additional basic system building blocks, such as network interface controllers, repeaters, hubs, bridges, switches, routers, modems, and firewalls. Any particular piece of equipment will frequently contain multiple building blocks and so may perform multiple functions. Figure 2: Personal Network Mapping Tool | Open Source Network Mapping Software – HZRL A network interface controller (NIC) is computer hardware that connects the computer to the network media and has the ability to process low-level network information. For example, the NIC may have a connector for plugging in a cable, or an aerial for wireless transmission and reception, and the associated circuitry. In Ethernet networks, each NIC has a unique Media Access Control (MAC) address—usually stored in the controller's permanent memory. To avoid address conflicts between network devices, the Institute of Electrical and Electronics Engineers (IEEE) maintains and administers MAC address uniqueness. The size of an Ethernet MAC address is six octets. The three most significant octets are reserved to identify NIC manufacturers.
These manufacturers, using only their assigned prefixes, uniquely assign the three least-significant octets of every Ethernet interface they produce. A repeater is an electronic device that receives a network signal, cleans it of unnecessary noise and regenerates it. The signal is retransmitted at a higher power level, or to the other side of obstruction so that the signal can cover longer distances without degradation. In most twisted-pair Ethernet configurations, repeaters are required for cable that runs longer than 100 meters.
With fiber optics, repeaters can be tens or even hundreds of kilometers apart. Repeaters work on the physical layer of the OSI model but still require a small amount of time to regenerate the signal. This can cause a propagation delay that affects network performance and may affect proper function. As a result, many network architectures limit the number of repeaters used in a network, e.g., the Ethernet 5-4-3 rule. An Ethernet repeater with multiple ports is known as an Ethernet hub. In addition to reconditioning and distributing network signals, a repeater hub assists with collision detection and fault isolation for the network. Hubs and repeaters in LANs have been largely obsoleted by modern network switches.
Network bridges and network switches are distinct from a hub in that they only forward frames to the ports involved in the communication whereas a hub forwards to all ports. Bridges only have two ports but a switch can be thought of as a multi-port bridge. Switches normally have numerous ports, facilitating a star topology for devices, and for cascading additional switches. Bridges and switches operate at the data link layer (layer 2) of the OSI model and bridge traffic between two or more network segments to form a single local network. Both are devices that forward frames of data between ports based on the destination MAC address in each frame. They learn the association of physical ports to MAC addresses by examining the source addresses of received frames and only forward the frame when necessary. If an unknown destination MAC is targeted, the device broadcasts the request to all ports except the source, and discovers the location from the reply. Bridges and switches divide the network's collision domain but maintain a single broadcast domain. Network segmentation through bridging and switching helps break down a large, congested network into an aggregation of smaller, more efficient networks.
A router is an internetworking device that forwards packets between networks by processing the addressing or routing information included in the packet. The routing information is often processed in conjunction with the routing table. A router uses its routing table to determine where to forward packets and does not require broadcasting packets which is inefficient for very big networks.
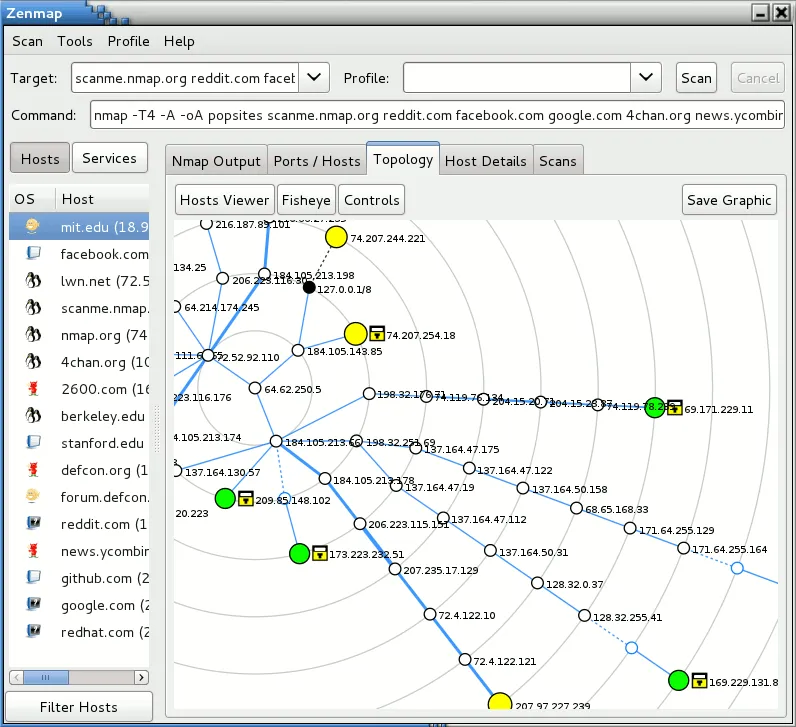
Figure 3: 10 Vulnerability Scanning Tools: Commercial and Open Source Options ... Modems (modulator-demodulator) are used to connect network nodes via wire not originally designed for digital network traffic, or for wireless. To do this one or more carrier signals are modulated by the digital signal to produce an analog signal that can be tailored to give the required properties for transmission. Early modems modulated audio signals sent over a standard voice telephone line. Modems are still commonly used for telephone lines, using a digital subscriber line technology and cable television systems using DOCSIS technology.
A firewall is a network device or software for controlling network security and access rules. Firewalls are inserted in connections between secure internal networks and potentially insecure external networks such as the Internet. Firewalls are typically configured to reject access requests from unrecognized sources while allowing actions from recognized ones. The vital role firewalls play in network security grows in parallel with the constant increase in cyber attacks.
A communication protocol is a set of rules for exchanging information over a network. Communication protocols have various characteristics, such as being connection-oriented or connectionless, or using circuit switching or packet switching. In a protocol stack, often constructed per the OSI model, communications functions are divided into protocol layers, where each layer leverages the services of the layer below it until the lowest layer controls the hardware that sends information across the media. The use of protocol layering is ubiquitous across the field of computer networking. An important example of a protocol stack is HTTP, the World Wide Web protocol. HTTP runs over TCP over IP, the Internet protocols, which in turn run over IEEE 802.11, the Wi-Fi protocol. This stack is used between a wireless router and a personal computer when accessing the web.
Most modern computer networks use protocols based on packet-mode transmission. A network packet is a formatted unit of data carried by a packet-switched network. Packets consist of two types of data: control information and user data (payload). The control information provides data the network needs to deliver the user data, for example, source and destination network addresses, error detection codes, and sequencing information. Typically, control information is found in packet headers and trailers, with payload data in between. With packets, the bandwidth of the transmission medium can be better shared among users than if the network were circuit switched. When one user is not sending packets, the link can be filled with packets from other users, and so the cost can be shared, with relatively little interference, provided the link is not overused. Often the route a packet needs to take through a network is not immediately available. In that case, the packet is queued and waits until a link is free. The physical link technologies of packet networks typically limit the size of packets to a certain maximum transmission unit (MTU). A longer message may be fragmented before it is transferred and once the packets arrive, they are reassembled to construct the original message.
Routing is the process of selecting network paths to carry network traffic. Routing is performed for many kinds of networks, including circuit switching networks and packet switched networks. In packet-switched networks, routing protocols direct packet forwarding through intermediate nodes. Intermediate nodes are typically network hardware devices such as routers, bridges, gateways, firewalls, or switches. General-purpose computers can also forward packets and perform routing, though because they lack specialized hardware, may offer limited performance. The routing process directs forwarding on the basis of routing tables, which maintain a record of the routes to various network destinations. Most routing algorithms use only one network path at a time. Multipath routing techniques enable the use of multiple alternative paths. Routing can be contrasted with bridging in its assumption that network addresses are structured and that similar addresses imply proximity within the network. Structured addresses allow a single routing table entry to represent the route to a group of devices. In large networks, the structured addressing used by routers outperforms unstructured addressing used by bridging. Structured IP addresses are used on the Internet. Unstructured MAC addresses are used for bridging on Ethernet and similar local area networks.
Bus network: all nodes are connected to a common medium along this medium. This was the layout used in the original Ethernet, called 10BASE5 and 10BASE2. This is still a common topology on the data link layer, although modern physical layer variants use point-to-point links instead, forming a star or a tree. Star network: all nodes are connected to a special central node. This is the typical layout found in a small switched Ethernet LAN, where each client connects to a central network switch, and logically in a wireless LAN, where each wireless client associates with the central wireless access point.
Ring network: each node is connected to its left and right neighbor node, such that all nodes are connected and that each node can reach each other node by traversing nodes left- or rightwards. Token Ring networks, and the Fiber Distributed Data Interface (FDDI), made use of such a topology. Mesh network: each node is connected to an arbitrary number of neighbors in such a way that there is at least one traversal from any node to any other. Fully connected network: each node is connected to every other node in the network. Tree network: nodes are arranged hierarchically. This is the natural topology for a larger Ethernet network with multiple switches and without redundant meshing. The physical layout of the nodes in a network may not necessarily reflect the network topology. As an example, with FDDI, the network topology is a ring, but the physical topology is often a star, because all neighboring connections can be routed via a central physical location. Physical layout is not completely irrelevant, however, as common ducting and equipment locations can represent single points of failure due to issues like fires, power failures and flooding.
An overlay network is a virtual network that is built on top of another network. Nodes in the overlay network are connected by virtual or logical links. Each link corresponds to a path, perhaps through many physical links, in the underlying network. The topology of the overlay network may (and often does) differ from that of the underlying one. For example, many peer-to-peer networks are overlay networks. They are organized as nodes of a virtual system of links that run on top of the Internet.
Overlay networks have been used since the early days of networking, back when computers were connected via telephone lines using modems, even before data networks were developed. The Internet was initially built as an overlay on the telephone network. Each Internet node can communicate with virtually any other through an underlying mesh of sub-networks of different topologies and technologies. Address resolution and routing are the means that allow mapping of a fully connected IP overlay network to its underlying network. Another example of an overlay network is a distributed hash table, which maps keys to nodes in the network. In this case, the underlying network is an IP network, and the overlay network is a table (actually a map) indexed by keys. Overlay networks have also been proposed as a way to improve Internet routing, such as through quality of service guarantees achieve higher-quality streaming media. Previous proposals such as IntServ, DiffServ, and IP multicast have not seen wide acceptance largely because they require modification of all routers in the network. On the other hand, an overlay network can be incrementally deployed on end-hosts running the overlay protocol software, without cooperation from Internet service providers. The overlay network has no control over how packets are routed in the underlying network between two overlay nodes, but it can control, for example, the sequence of overlay nodes that a message traverses before it reaches its destination. For example, Akamai Technologies manages an overlay network that provides reliable, efficient content delivery (a kind of multicast). Academic research includes end system multicast, resilient routing and quality of service studies, among others.
Networks may be characterized by many properties or features, such as physical capacity, organizational purpose, user authorization, access rights, and others. Another distinct classification method is that of the physical extent or geographic scale. A home area network (HAN) is a residential LAN used for communication between digital devices typically deployed in the home, usually a small number of personal computers and accessories, such as printers and mobile computing devices. An important function is the sharing of Internet access, often a broadband service through a cable Internet access or digital subscriber line (DSL) provider. A storage area network (SAN) is a dedicated network that provides access to consolidated, block-level data storage. SANs are primarily used to make storage devices, such as disk arrays, tape libraries, and optical jukeboxes, accessible to servers so that the storage appears as locally attached devices to the operating system. A SAN typically has its own network of storage devices that are generally not accessible through the local area network by other devices. The cost and complexity of SANs dropped in the early 2000s to levels allowing wider adoption across both enterprise and small to medium-sized business environments.
An enterprise private network or intranet is a network that a single organization builds to interconnect its office locations (e.g., production sites, head offices, remote offices, shops) so they can share computer resources. An internetwork is the connection of multiple different types of computer networks to form a single computer network using higher-layer network protocols and connecting them together using routers. The Internet is the largest example of internetwork. It is a global system of interconnected governmental, academic, corporate, public, and private computer networks. It is based on the networking technologies of the Internet protocol suite. It is the successor of the Advanced Research Projects Agency Network (ARPANET) developed by DARPA of the United States Department of Defense. The Internet utilizes copper communications and an optical networking backbone to enable the World Wide Web (WWW), the Internet of things, video transfer, and a broad range of information services. Participants on the Internet use a diverse array of methods of several hundred documented, and often standardized, protocols compatible with the Internet protocol suite and the IP addressing system administered by the Internet Assigned Numbers Authority and address registries. Service providers and large enterprises exchange information about the reachability of their address spaces through the Border Gateway Protocol (BGP), forming a redundant worldwide mesh of transmission paths.
Network delay is a design and performance characteristic of a telecommunications network. It specifies the latency for a bit of data to travel across the network from one communication endpoint to another. Delay may differ slightly, depending on the location of the specific pair of communicating endpoints. Engineers usually report both the maximum and average delay, and they divide the delay into several components, the sum of which is the total delay: Processing delay – time it takes a router to process the packet header Queuing delay – time the packet spends in routing queues Transmission delay – time it takes to push the packet's bits onto the link Propagation delay – time for a signal to propagate through the media A certain minimum level of delay is experienced by signals due to the time it takes to transmit a packet serially through a link. This delay is extended by more variable levels of delay due to network congestion. IP network delays can range from less than a microsecond to several hundred milliseconds.
The introduction and rapid growth of e-commerce on the World Wide Web in the mid-1990s made it obvious that some form of authentication and encryption was needed. Netscape took the first shot at a new standard. At the time, the dominant web browser was Netscape Navigator. Netscape created a standard called secure socket layer (SSL). SSL requires a server with a certificate. When a client requests access to an SSL-secured server, the server sends a copy of the certificate to the client.
The SSL client checks this certificate (all web browsers come with an exhaustive list of root certificates preloaded), and if the certificate checks out, the server is authenticated and the client negotiates a symmetric-key cipher for use in the session. The session is now in a very secure encrypted tunnel between the SSL server and the SSL client. 2. System Architecture & Core Working Principles This article incorporates public domain material from Federal Standard 1037C. General Services Administration. Archived from the original on 2022-01-22.
FireWire is a largely deprecated interface standard for a serial bus for high-speed communications and isochronous real-time data transfer. It was developed in the late 1980s and early 1990s by Apple in cooperation with a number of companies, primarily Sony and Panasonic. It is most commonly known by the Apple name FireWire, but also referred to by the Sony name i.LINK and the Texas Instruments name Lynx. Most consumer electronics manufacturers phased it out in the 2010s. The standard was also adopted by the IEEE as IEEE 1394. The copper cable used in its most common implementation can be up to 4.5 m (15 ft) long. Power and data are carried over this cable, allowing devices with moderate power requirements to operate without a separate power supply. FireWire is also available in Cat 5 and optical fiber versions. The 1394 interface is comparable to USB. USB was developed subsequently and gained much greater market share. USB requires a host controller whereas IEEE 1394 is cooperatively managed by the connected devices.
FireWire is Apple's name for the IEEE 1394 High Speed Serial Bus. Its development was initiated by Apple in 1986, and developed by the IEEE P1394 Working Group, largely driven by contributions from Sony (102 patents), Apple (58 patents), Panasonic (46 patents), and Philips (43 patents), in addition to contributions made by engineers from LG Electronics, Toshiba, Hitachi, Canon, INMOS/SGS Thomson (now STMicroelectronics), and Texas Instruments. FireWire is a serial bus architecture for high-speed data transfer, serial meaning that information is transferred one bit at a time. Parallel buses utilize a number of different physical connections, and as such are usually more costly and typically heavier. IEEE 1394 fully supports both isochronous and asynchronous applications. Apple intended FireWire to be a serial replacement for the parallel SCSI bus, while providing connectivity for digital audio and video equipment. Apple's development began in the late 1980s, later presented to the Institute of Electrical and Electronics Engineers (IEEE), and was completed in January 1995. In 2007, IEEE 1394 was a composite of four documents: the original IEEE Std. 1394–1995, the IEEE Std. 1394a-2000 amendment, the IEEE Std. 1394b-2002 amendment, and the IEEE Std. 1394c-2006 amendment. On June 12, 2008, all these amendments as well as errata and some technical updates were incorporated into a superseding standard, IEEE Std. 1394–2008. Apple first included onboard FireWire in some of its 1999 Mac models (though it had been a build-to-order option on some Macintosh models since 1997), and most Apple Mac computers manufactured from 2000 through 2011 included FireWire ports.
However, in February 2011, Apple introduced its first Mac with Thunderbolt, which superseded FireWire. Apple released its last computers with FireWire in 2012. By 2014, Thunderbolt had become a standard feature across Apple's entire line of computers (with some exceptions), effectively becoming the spiritual successor to FireWire in the Apple ecosystem. Apple's last Mac products with FireWire, the Apple Thunderbolt Display and 2012 13-inch MacBook Pro, were discontinued in 2016.
Apple sold a Thunderbolt to FireWire adapter, with a single FireWire 800 port, until 2023. A separate adapter was required to use it with Thunderbolt 3. Sony's implementation of the system, i.LINK, used a smaller connector with only four signal conductors, omitting the two conductors that provide power for devices in favor of a separate power connector. This style was later added into the 1394a amendment. This port is sometimes labeled S100 or S400 to indicate speed in Mbit/s. The system was commonly used to connect data storage devices and DV (digital video) cameras, but was also popular in industrial systems for machine vision and professional audio systems. Many users preferred it over the more common USB 2.0 for its then greater effective speed and power distribution capabilities. Benchmarks show that the sustained data transfer rates are higher for FireWire than for USB 2.0, but lower than USB 3.0. Results are marked on Apple Mac OS X but more varied on Microsoft Windows.
A person or company was able to review the actual 1394 Patent Portfolio License upon request to the licensing administrator. The licensing administrator did not provide assurance of protection to licensees beyond its own patents. At least one formerly licensed patent is known to have been removed from the pool, and other hardware patents exist that reference IEEE 1394. The 1394 High Performance Serial Bus Trade Association (the 1394 TA) was formed to aid the marketing of IEEE 1394. Its bylaws prohibit dealing with intellectual property issues. The 1394 Trade Association operates on an individual no cost membership basis to further enhancements to 1394 standards. The Trade Association also is the library source for all 1394 documentation and standards available.
The original release of IEEE 1394-1995 specified what is now known as FireWire 400. It can transfer data between devices at 100, 200, or 400 Mbit/s half-duplex data rates (the actual transfer rates are 98.304, 196.608, and 393.216 Mbit/s, i.e., 12.288, 24.576 and 49.152 MB/s respectively). These different transfer modes are commonly referred to as S100, S200, and S400. Cable length is limited to 4.5 m (15 ft), although up to 16 cables can be daisy chained using active repeaters, e.g., external hubs or the internal hubs that are often present in FireWire equipment. The S400 standard limits any configuration's maximum cable length to 72 m (236 ft). The 6-conductor connector is commonly found on desktop computers and can supply the connected device with power. The 6-conductor powered connector, now referred to as an alpha connector, adds power output to support external devices. Typically a device can pull about 7 to 8 watts from the port; however, the voltage varies significantly from different devices. Voltage is specified as unregulated and should nominally be about 25 volts (range 24 to 30). Apple's implementation on laptops is typically related to battery power and can be as low as 9 V.
IEEE 1394b-2002 introduced FireWire 800 (Apple's name for the 9-conductor S800 bilingual version of the IEEE 1394b standard). This specification added a new encoding scheme termed beta mode which allowed compliant devices to operate at 786.432 Mbit/s full-duplex. It is backwards compatible with the slower rates and 6-conductor alpha connectors of FireWire 400. However, while the IEEE 1394a and IEEE 1394b standards are compatible, FireWire 800's connector, referred to as a beta connector, is different from FireWire 400's alpha connectors, making legacy cables incompatible. A bilingual cable allows the connection of older devices to the newer port. In 2003, Apple was the first to introduce commercial products with the new connector, including a new model of the Power Mac G4 and a 17" PowerBook G4. The full IEEE 1394b specification supports data rates up to 3200 Mbit/s (i.e., 400 MB/s) over beta-mode or optical connections up to 100 m (330 ft) in length. Standard category 5e cable supports 100 m (330 ft) at S100. The original 1394 and 1394a standards used data/strobe (D/S) encoding, now known as alpha mode, with the cables, while 1394b added a data encoding scheme called 8b/10b referred to as beta mode. Beta mode is based on 8b/10b (from Gigabit Ethernet, also used for many other protocols). 8b/10b encoding involves expanding an 8-bit data word into 10 bits, with the extra bits after the 5th and 8th data bits. The partitioned data is sent through a Running Disparity calculator function. The Running Disparity calculator attempts to keep the number of 1s transmitted equal to 0s, thereby assuring a DC-balanced signal. Then, the different partitions are sent through a 5b/6b encoder for the 5-bit partition and a 3b/4b encoder for the 3-bit partition. This gives the packet the ability to have at least two 1s, ensuring synchronization of the PLL at the receiving end to the correct bit boundaries for reliable transfer. An additional function of the coding scheme is to support the arbitration for bus access and general bus control. This is possible due to the surplus symbols afforded by the 8b/10b expansion. (While 8-bit symbols can encode a maximum of 256 values, 10-bit symbols permit the encoding of up to 1024.) Symbols invalid for the current state of the receiving PHY indicate data errors.
1394 Trade Association at the Wayback Machine (archived 2019-03-28) 1394 Standards Orientation, Introduction at the Wayback Machine (archived 2021-02-03) IEEE 1394 connectors pinout This is a list of TCP and UDP port numbers used by protocols for operation of network applications. The Transmission Control Protocol (TCP) and the User Datagram Protocol (UDP) only need one port for bidirectional traffic. TCP usually uses port numbers that match the services of the corresponding UDP implementations, if they exist, and vice versa. The Internet Assigned Numbers Authority (IANA) is responsible for maintaining the official assignments of port numbers for specific uses.
However, many unofficial uses of both well-known and registered port numbers occur in practice. Similarly, many of the official assignments refer to protocols that were never or are no longer in common use. This article lists port numbers and their associated protocols that have experienced significant uptake. The port numbers in the range from 0 to 1023 (0 to 210 − 1) are the well-known ports or system ports. They are used by system processes that provide widely used types of network services. On Unix-like operating systems, a process must execute with superuser privileges to be able to bind a network socket to an IP address using one of the well-known ports.
The range of port numbers from 1024 to 49151 (210 to 215 + 214 − 1) are the registered ports. They are assigned by IANA for specific service upon application by a requesting entity. On most systems, registered ports can be used without superuser privileges. The range 49152–65535 (215 + 214 to 216 − 1), 16 384 ports, contains dynamic or private ports that cannot be registered with IANA. This range is used for private or customized services, for temporary purposes, and for automatic allocation of ephemeral ports.
NTMVA is a modern cybersecurity platform for network discovery, topology visualization, vulnerability assessment, CVE mapping, and risk analysis powered by Nmap and the Nmap Scripting Engine (NSE) . The platform provides an interactive dashboard to discover hosts, identify services, visualize network topology, analyze attack surfaces, and prioritize vulnerabilities using risk scoring.
I Discover Hosts I Detect Operating Systems I Enumerate Services I Run NSE Scripts I Analyze Vulnerabilities I Generate Network Topology I Calculate Risk Scores I Display Security Findings This project is intended for educational and authorized security assessment purposes only . Always obtain proper authorization before scanning networks or systems you do not own.
NTMVA (Network Topology Mapper & Vulnerability Analyzer) is a cybersecurity platform that combines network discovery, topology visualization, service enumeration, and vulnerability assessment using Nmap and NSE. It maps network assets, identifies exposed services, and provides risk insights through an interactive dashboard. NTM release notes includes new features, upgrade notes, fixed and known issues, and end-of-life notices.
Step-by-step instructions and checklists to help you plan, prepare, and then install or upgrade. Automatically discover your entire network to create comprehensive, detailed network topology maps quickly without having to rescan multiple times. Save valuable resources, bandwidth, and time. One map is rarely enough to comprehensively discover your environment: you can designate sub-admins to discover just their segments of network.
NA maps can be rolled-up: when you need the maps to contain applications, systems, services, interfaces, IPSLAs This video provides a step-by-step walkthrough of SolarWinds Network Topology Mapper (NTM). It covers how to configure SNMP, WMI, and VMware credentials, define scan parameters, and interpret the resulting network maps. You'll learn how to use features like bridge table data, auto-arrange layouts, and inventory reports to gain deeper visibility into your network infrastructure. Ideal for IT professionals looking to streamline network mapping and reporting.
Network reconnaissance is the cornerstone of cybersecurity assessment, penetration testing, and network administration. Among all the tools available for network discovery and security auditing, Nmap (Network Mapper) stands as the undisputed champion—a Swiss Army knife that has been the go-to tool for security professionals, system administrators, and ethical hackers for over two decades.
Understanding network reconnaissance with Nmap isn't just about learning commands; it's about developing a methodical approach to network discovery, service enumeration, and vulnerability assessment. This comprehensive guide will take you from basic host discovery to advanced scripting techniques, providing the knowledge needed to conduct thorough and responsible network assessments.
II Ethical Use Disclaimer : This guide is intended for educational purposes, authorized penetration testing, and legitimate security assessments only. Always ensure you have explicit permission before scanning networks or systems you don't own. Unauthorized network scanning may violate laws and organizational policies. 3. Software Implementation, Frameworks & Protocols Network reconnaissance is the systematic process of gathering information about network infrastructure, services, and potential vulnerabilities. It's the intelligence-gathering phase that precedes any security assessment or penetration test, providing the foundation for understanding the attack surface of a target environment.
Passive Reconnaissance : Gathering information without directly interacting with the target systems. This includes DNS lookups, WHOIS queries, and social media intelligence gathering. Active Reconnaissance : Directly probing target systems to gather information. This includes port scanning, service enumeration, and vulnerability scanning—where Nmap excels.
Windows : Download from the official Nmap website (nmap.org) or use package managers like Chocolatey. Host Discovery : Determines which hosts are alive on the network Port Scanning : Identifies open, closed, and filtered ports Service Detection : Determines service versions and configurations OS Detection : Attempts to identify the target operating system Scripting Engine : Runs specialized scripts for advanced functionality Host discovery is the first step in any network reconnaissance. Nmap offers multiple techniques to identify live hosts on a network.
Port scanning is Nmap's core functionality, offering various techniques optimized for different scenarios and firewall evasion. Once ports are identified, determining the services and their versions is crucial for vulnerability assessment. OS detection helps identify the target system type, which is valuable for selecting appropriate attack vectors and tools. The Nmap Scripting Engine is one of Nmap's most powerful features, allowing for custom functionality through Lua scripts.
Modern networks employ various security measures that can detect or block reconnaissance attempts. Nmap provides numerous evasion techniques. Proper documentation is crucial for effective reconnaissance. Nmap supports multiple output formats. Always Obtain Authorization : Never scan networks or systems without explicit written permission. This includes: Understanding reconnaissance techniques is equally important for defenders. This section covers detection and mitigation strategies.
Network reconnaissance with Nmap represents both an art and a science, requiring technical expertise, methodical thinking, and ethical responsibility. As we've explored throughout this comprehensive guide, Nmap's capabilities extend far beyond simple port scanning to encompass sophisticated network discovery, service enumeration, vulnerability assessment, and automation frameworks.
Master the Fundamentals : Understanding basic networking concepts, TCP/IP protocols, and common services forms the foundation for effective reconnaissance. Without this knowledge, even the most sophisticated Nmap techniques will yield limited value. Develop Methodology : Successful reconnaissance follows structured approaches rather than random scanning. Establish clear phases, document findings systematically, and maintain consistent procedures across different environments.
Balance Speed and Stealth : The eternal trade-off between comprehensive coverage and detection avoidance requires careful consideration of timing, target prioritization, and evasion techniques based on the specific engagement context. Embrace Automation : Manual reconnaissance doesn't scale. Developing scripted workflows, integrating with other tools, and building automated analysis capabilities multiplies effectiveness and consistency.
Practice Ethical Responsibility : With great power comes great responsibility. Always ensure proper authorization, minimize impact on target systems, and follow responsible disclosure practices when vulnerabilities are discovered. Cloud-Native Environments : Traditional network boundaries are dissolving as organizations adopt cloud-first architectures. Modern reconnaissance must account for: Artificial Intelligence Integration : ML and AI are increasingly integrated into both offensive and defensive capabilities: Zero Trust Architectures : The shift toward zero trust networking models creates new reconnaissance challenges and opportunities: Quantum Computing Impact : While still emerging, quantum computing will eventually impact: Network reconnaissance with Nmap is a journey rather than a destination. The field continuously evolves with new technologies, attack vectors, and defensive measures. Success requires: Continuous Learning : Technology changes rapidly. Stay current with new Nmap releases, emerging protocols, and evolving attack techniques through regular training and practice.
4. Practical Deployment, Analysis & Case Studies Ethical Foundation : Always maintain the highest ethical standards. The skills learned through reconnaissance can be powerful tools for both protection and harm—use them responsibly. Practical Application : Theory without practice is limited. Build lab environments, participate in capture-the-flag events, and seek hands-on experience through authorized testing.
Community Engagement : Join professional communities, attend conferences, and contribute to the security field through knowledge sharing and collaborative learning. Documentation and Process : Develop systematic approaches to reconnaissance, maintain detailed documentation, and continuously refine methodologies based on experience and results.
The mastery of network reconnaissance with Nmap opens doors to advanced cybersecurity roles, from penetration testing and security consulting to incident response and threat hunting. Whether you're defending organizational networks or conducting authorized security assessments, the knowledge and techniques covered in this guide provide a solid foundation for professional growth and contribution to the cybersecurity community.
Remember that with knowledge comes responsibility. Use these powerful reconnaissance capabilities ethically, legally, and in service of improving security for organizations and individuals alike. The cybersecurity field needs skilled professionals who can both understand and defend against the techniques we've explored. As you continue your journey in network security, keep learning, keep practicing, and most importantly, keep contributing to making the digital world more secure for everyone.
Have you implemented advanced Nmap techniques in your security assessments? Share your experiences and favorite NSE scripts in the comments below! This documentation provides an in-depth exploration of vulnerability scanning techniques essential for penetration testing and the OSCP certification. Content is derived from OffSec PEN-200 courseware, rephrased and organized for practical application.
The industry-standard port scanner with powerful NSE scripting capabilities for lightweight vulnerability detection. Professional vulnerability scanner with extensive plugin library covering 67,000+ CVEs. Open-source vulnerability assessment framework with 50,000+ Network Vulnerability Tests (NVTs). Mohamed Trigui is a cybersecurity enthusiast completing a Master's in Cybersecurity at Illinois Tech. Currently preparing for OSCP certification through hands-on practice on Hack The Box and developing custom security tools.
Current Projects: - Replicating vulnerabilities on Linux and writing Lua patches - Developing Nmap NSE scripts for zero-day reconnaissance - Writing HTB machine walkthroughs and exploit documentation This guide is for educational purposes only . Always obtain proper authorization before scanning any systems. Unauthorized vulnerability scanning is illegal and unethical.
Content is derived from OffSec PEN-200 (OSCP) training materials, rephrased and adapted for educational purposes. All credit for the original methodology and techniques goes to Offensive Security. This documentation is provided as-is for educational purposes. When using these techniques: NMAP is a widely-used network scanning tool that provides functionality for host discovery and service enumeration. It offers various scanning techniques that can be used by security professionals, systems administrators, and network researchers for authorized network mapping and analysis, thereby creating a “map” of the network. Its primary functions include host discovery, port scanning, OS detection, and version detection, although it can also be extended to accommodate more advanced features through its scripting engine.
The importance of NMAP in cybersecurity cannot be overstated. Modern networks are increasingly complex, comprising a wide range of devices, operating systems, and application services. Malicious actors frequently exploit vulnerabilities in these devices or services to gain unauthorized access, exfiltrate data, or disrupt operations. As a result, proactive network scanning and vulnerability analysis have become critical steps in protecting an organization’s infrastructure. NMAP stands out as one of the most trusted tools for these tasks, not only because it is free and open-source but also because it has a long track record of reliability and continuous development.
The Nmap Project, driven by a dedicated community, has significantly contributed to network security through continuous updates and improvements. Developed by Gordon “Fyodor” Lyon, NMAP was first introduced in an article titled "The Art of Port Scanning" published in Phrack Magazine Issue 51, Article 11 in September 1997. The tool has been continuously updated since its initial release, with regular contributions from the security community. With its user base spanning security researchers, penetration testers, educators, and hobbyists, NMAP is more than just a simple port scanner—it is a platform that supports a variety of scanning methodologies and scripting possibilities.
In this comprehensive guide, we will delve into the fundamental concepts behind NMAP, discuss its evolution and functionality, and explore various scanning techniques and real-world use cases. Whether you are a newcomer looking to understand why NMAP is so highly regarded, or an experienced professional seeking to expand your usage of the tool, this article will provide insights and practical knowledge that can be confirmed by NMAP’s official documentation and numerous real-world deployments.
NMAP’s journey began in the mid-1990s, a period marked by the nascent stages of mainstream internet adoption. In 1997, Gordon Lyon published an article titled “The Art of Port Scanning” in Phrack Magazine, introducing NMAP to the cybersecurity community. The timing was ideal—security professionals were in dire need of efficient ways to map networks and identify vulnerabilities, and NMAP offered precisely that.
From its earliest versions, NMAP adopted a philosophy of openness, reliability, and versatility. Its first implementations were simple compared to today’s standards but already featured several innovative techniques. Over time, the tool evolved to integrate more advanced scanning technologies, including: Nmap's functionality can be extended through companion tools like Ncat for networking and Nping for packet generation. The Nmap Scripting Engine (NSE) enables network stress testing and vulnerability assessment through customizable scripts, when authorized to do so.
Throughout these developments, NMAP has remained free and open-source. Its community-driven approach, backed by a dedicated core of developers, allowed the tool to remain on the cutting edge of scanning methodologies. Today, NMAP is trusted by corporations, government agencies, educational institutions, and hobbyists worldwide. Before diving into the more nuanced aspects of scanning, it is important to understand what NMAP fundamentally does. At its most basic level, NMAP sends specially crafted network packets to target hosts and then analyzes the responses. By examining how a host responds—or does not respond—to these probes, NMAP can deduce valuable information such as: 5. Performance Evaluation & Extended Technical Observations These functionalities can be integrated into various scenarios, ranging from simple network inventory tasks to comprehensive penetration tests. Administrators often rely on NMAP to verify that only the necessary services are publicly exposed, while security researchers use it to discover potential entry points.
NMAP’s utility also stems from its flexibility in handling diverse networking environments. It supports multiple scanning protocols (TCP, UDP, SCTP), can perform both IPv4 and IPv6 scanning, and offers customizable options such as timing templates, which help in balancing scan speed and stealth. In environments where scanning might trigger intrusion detection systems, NMAP’s ability to slow down or randomize probes can be critical for avoiding detection—though such use must be done ethically and within the bounds of legal permission.
NMAP primarily operates through a command-line interface (CLI), making it a powerful and script-friendly utility on Linux, macOS, and Windows. Though there is a GUI front-end called Zenmap, the CLI remains the most direct way to access the full breadth of NMAP’s capabilities. Below is a quick primer on some essential NMAP commands and parameters: Even at this basic level, NMAP offers a powerful range of capabilities. The flexibility to specify ports, detect services, and map operating systems provides significant insights that can aid in network administration and security evaluations. When running Nmap, especially in sensitive environments, it is crucial to have proper authorization and administrator privileges to ensure ethical use and avoid detection by security systems.
One of NMAP’s greatest strengths is its variety of port scan techniques, particularly its capability to perform comprehensive port scanning tasks essential for identifying open ports on local and remote networks, thereby enhancing overall cybersecurity practices. Each technique has its particular use cases, depending on network conditions, target configuration, and the goal of the scan. Below are some of the most common scanning methods: Knowing which scan type to use in a given situation is key to getting accurate results quickly while minimizing the risk of detection. In a production environment with strict firewall rules, for example, one might choose a SYN stealth scan over a full TCP connect scan to avoid generating excessive logs.
The Nmap Scripting Engine (NSE) is one of the features that truly sets NMAP apart from other scanning tools. NSE uses the Lua scripting language, allowing for the creation of custom scripts that can perform a wide range of tasks, from simple checks to complex reconnaissance and vulnerability assessments. NSE scripts are categorized into several groups: To use NSE scripts, you can specify the --script parameter along with the script name or category. For instance: This command will run all scripts in the “vuln” category against the target. Alternatively, you can run a specific script: One of the major benefits of NSE is that it transforms NMAP from a port scanner into a more comprehensive vulnerability assessment tool. Researchers continuously add and update scripts to reflect the latest threats and techniques, ensuring the tool remains relevant in a quickly evolving security landscape.
NMAP offers various performance and timing settings that allow the user to balance speed against accuracy and stealth. The timing templates, specified with the -T flag, range from -T0 (Paranoid) to -T5 (Insane), each adjusting the delay between probes, timeouts, and other parameters. Here is a quick overview: In addition to these templates, NMAP allows manual adjustments to retry counts, host timeouts, and packet pacing. For large-scale scans—such as scanning an entire Class B network range—properly tuning these parameters can make the difference between a successful scan and a prolonged, resource-intensive process.
When performing penetration tests or security audits, proper documentation is crucial. NMAP provides multiple output formats to facilitate reporting and data analysis. Using the -oA parameter, for example, you can generate three types of output in one go: nmap -sV -oA myscan 192.168.1.0/24 This produces: The Nmap Output tab presents specific scan results for individual devices, allowing users to view relevant information alongside the port status for those hosts.
Alternatively, you can opt for specific formats like -oX for XML, -oN for normal text, and -oG for grepable output. These features enable seamless integration with larger workflows, such as importing scan results into vulnerability management platforms or custom dashboards. NMAP’s versatility lends itself to a multitude of practical applications. Below are some common scenarios in which NMAP proves invaluable: Network scanning without explicit authorization is illegal in many jurisdictions and may violate computer misuse laws. Before conducting any network scans: When conducting vulnerability assessments or penetration tests, obtain a signed scope of work detailing what is allowed.
With the growing adoption of IPv6, NMAP has integrated features to scan IPv6 addresses effectively. The syntax is similar to IPv4 scanning, but you must specify IPv6 addresses or CIDR blocks and use the -6 flag: Additionally, NMAP can handle more specialized protocols like SCTP scans for certain telecommunication and VoIP networks. It also supports proxy options, decoy scanning, and spoofed scans for highly specialized use cases. Each of these advanced features has practical scenarios, though they are typically used by experienced practitioners who understand potential legal and ethical implications.
Even the most seasoned professionals encounter occasional hiccups when using NMAP. Here are some common issues and tips for resolving them: NMAP’s output formats make it easy to integrate with a variety of security and IT management tools. For instance, many vulnerability scanners (such as OpenVAS) can import NMAP’s XML output to enrich their scanning results. Similarly, custom Python or Bash scripts can parse the grepable output to automate post-scan actions, such as generating email alerts for newly discovered open ports or services.
Nmap results can be exported in different formats, such as XML, CSV, or HTML, making it easier to create reports or analyze data for both technical and non-technical users. Many penetration testing frameworks support Nmap integration. For example, Metasploit can import Nmap scan results in XML format through specific commands, allowing testers to use the scan data for further analysis. The exact integration capabilities may vary depending on the versions of both tools being used.
Nmap is a powerful tool in the field of cybersecurity, widely used for network discovery, vulnerability scanning, and security auditing. Its features make it an essential component of any cybersecurity professional’s toolkit. One of the primary uses of Nmap in cybersecurity is network discovery. By identifying active hosts and open ports, Nmap helps security professionals map out the network infrastructure. This is crucial for understanding the layout of a network, identifying potential entry points, and ensuring that all devices are accounted for. The ability to scan multiple IP addresses and detect open ports allows for a comprehensive view of the network, which is the first step in any security audit.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Computer%20network • https://en.wikipedia.org/wiki/FireWire • https://en.wikipedia.org/wiki/List%20of%20TCP%20and%20UDP%20port%20numbers • https://github.com/AmmarKhan-0/Network-Topology-Mapper-Vulnerability-Analyzer • https://documentation.solarwinds.com/en/success_center/ntm/content/ntm_documentation.htm • https://documentation.solarwinds.com/en/success_center/ntm/content/ntm_getting_started_guide.htm • https://www.solarwinds.com/resources/video/getting-started-with-network-topology-mapper • https://dev.to/caffinecoder54/network-reconnaissance-with-nmap-the-complete-guide-4jp7 • https://medtrigui.github.io/vulnerability-scanning/ • https://www.startupdefense.io/blog/nmap-a-comprehensive-guide-to-the-network-mapper-tool
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Network Topology Mapper And Vulnerability Scanner Project.
[*] Initializing Burp Suite Spider & Vulnerability Engine for Network Topology Mapper And Vulnerability Scanner Project... [✓] Burp Extender / Macro Automation Hook Synced ──────────────────────────────────────────────────────────────────────── [11:42:01.104] AUDIT Crawled dynamic endpoints | Injecting input vectors [11:42:01.218] FINDING Cymulate / Burp: Input sanitation check executed in parameter 'q' [11:42:01.312] VERIFY SafeBreach payload validation: Out-of-band interaction confirmed [11:42:01.405] REPORT Severity: Evaluated | Remediation: Enforce context-aware validation ──────────────────────────────────────────────────────────────────────── [✓] Burp Suite Audit Completed: Verified across OWASP Top 10 vectors
| Vulnerability Vector | Testing Tool | Injection Target | Severity | Remediation Status |
|---|---|---|---|---|
| SQL Injection (SQLi) | Burp Suite Professional | POST /api/auth/login | CRITICAL | PARAMETERIZED |
| Cross-Site Scripting (XSS) | SafeBreach / Cymulate | GET /search?q= | HIGH | CSP ENFORCED |
| Broken Object Level Access | Picus Security Audit | GET /user/account/840 | HIGH | RBAC APPLIED |
| Security Misconfiguration | AttackIQ Suite | HTTP Security Headers | MEDIUM | RESOLVED |