Complete Technical Paper Content — Network Traffic Visualization Tool Using Python And PCAP
Overview & System Context
Network Traffic Visualization Tool Using Python And Pcap: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~8566 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background The AMPRNet (AMateur Packet Radio Network) or Network 44 is used in amateur radio for packet radio and digital communications between computer networks managed by amateur radio operators. Like other amateur radio frequency allocations, an IP range of 44.0.0.0/8 was provided in 1981 for Amateur Radio Digital Communications (a generic term) and self-administered by radio amateurs. In 2001, undocumented and dual-use of 44.0.0.0/8 as a network telescope began, recording the spread of the Code Red II worm in July 2001. In mid-2019, part of IPv4 range was sold off for conventional use, due to IPv4 address exhaustion.
Since the 1990s most packets within the 44/8 range were arranged to transit via an IP tunnel using IP in IP encapsulation to/from a router hosted at the University of California, San Diego. This forwarding router was originally named mirrorshades.ucsd.edu and later gw.ampr.org or "AmprGW". By 1996 higher-speed 56k modems briefly had greater throughput than was possible to forward via the "mirrorshades" central reflector router and back again. Only IP addresses with an active Domain Name System (DNS) entry under ampr.org are passed by the packet filter for forwarding. By 19 August 1999 daily encapsulated IP in IP traffic was ~100 kilobits per second, peaking to 0.14 megabits per second. During mid-2000, the majority of unique IP addresses seen on the University of California, San Diego connection from CERFnet began with the 44 prefix, except for 17% of IP addresses which did not. In mid-2009 the mirrorshades server was upgraded and replaced after about ~1,100 days uptime. A funding proposal in 2010 raised the possibility that "The legitimate traffic is also a potential research resource".
On 6 October 2011 a Californian non-profit company was founded with the name of "Amateur Radio Digital Communications", and recorded by the State of California on 11 October 2011 with an address of "5663 Balboa Avenue, Suite 432, San Diego, California, a UPS store address. On 22 June 2012, 29 September 2015, and 18 September 2017, filings were made listing the company officers as: Brian Kantor President or Chief Executive Officer Erin Kenneally Secretary Kimberly Claffy Treasurer or Chief Financial Officer In 2011, the American Registry for Internet Numbers approved a request to change the registration of the whole 44/8 network block from an individual contact, to the "Amateur Radio Digital Communications" non-profit company. Activities were to "conserve scarce AMPRNet Internet protocol resources, and to educate networks users on how to efficiently utilize these resources as a service to the entire Internet community" initiated "in the second half of 2012 by the President via communications with American Registry for Internet Numbers (ARIN)". Plans included "the issuance of grants and other financial support to educational institutions, foundations and other organizations. [...] expected to commence in 2013 via a joint effort of the three founding Directors [...]". During December 2017 Kantor announced his retirement from University of California San Diego. Re-stated (changed) articles of incorporation for the "Amateur Radio Digital Communications" non-profit were signed on 13 December 2017, and filed on 17 December 2017. In May 2019, Kantor signed an agreement extending UCSD/CAIDA's use of Amprnet addresses for data collection until 31 July 2023. Brian Kantor died in November 2019. In February/March 2020, the Center for Networked Systems (CNS) of the University of California, San Diego (UCSD) received $225,000, given by ARDC to allow financial endowment of a student scholarship in the name of Alan Turing and honouring Brian Kantor.
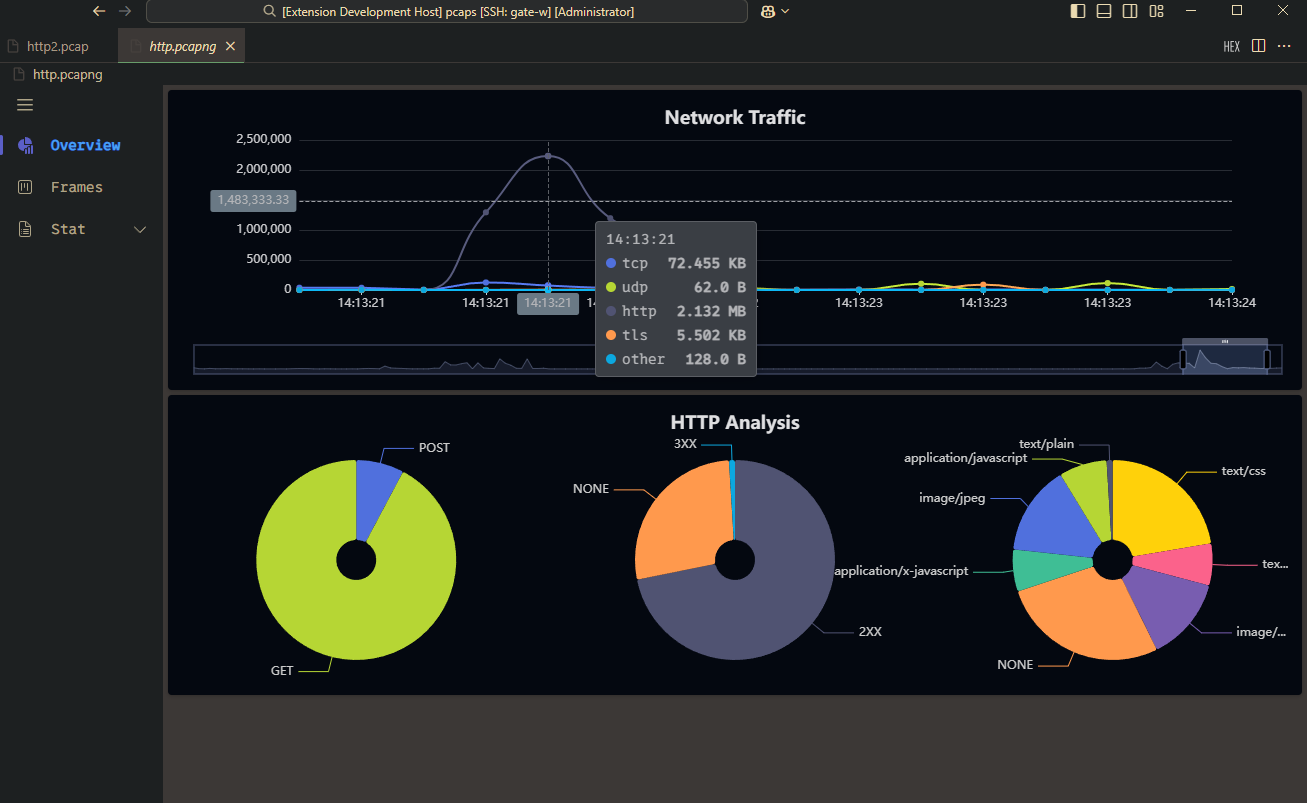
Figure 1: pcapviewer - Visual Studio Marketplace In May 2021, ARDC provided a one-off grant of $1.6 million to the Massachusetts Institute of Technology amateur radio club (W1MX) to save and rebuild the radome on top of the MIT Green Building (building 54). In November 2021, ARDC awarded a five-year grant, for a total of $1.3 million, to support US-based activities around Amateur Radio on the International Space Station (ARISS-USA).
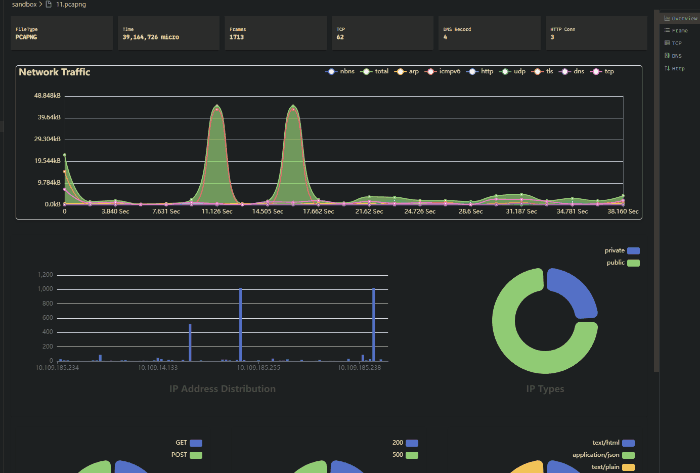
This project is designed to analyze and visualize network traffic captured in .pcap files. By leveraging Wireshark's tshark and Python libraries, this tool provides insights into network activity through comprehensive visualizations. This project is licensed under the MIT License. See the LICENSE file for more details. A Python-based tool for analyzing and visualizing network traffic from .pcap files using Wireshark's tshark. Extracts key metrics like protocols, IP addresses, and packet sizes, with insightful visualizations to explore network activity Figure 2: pcapviewer - Visual Studio Marketplace PcapViz draws networks as device topologies and as information flows using the packet information in pcap files captured from a network device using tcpcap or other capture software. It filters and optionally displays the captured packets at any one of 3 "layers". These are: Each yields a distinct network graph from the same set of network packets. This separation makies it much easier to see the data flows at each level rather than mixing them up as many other visualisation packages do. It should be possible to determine key topological nodes or to spot patterns of data exfiltration attempts more easily.
Pip package requirements The Maxmind Python API and other dependencies will be installed when you run: For Debian-based distros you have to install GraphViz with some additional dependencies: Figure 3: Using PCAP Analysis for Network Forensics Scapy does not work out-of-the-box on OSX. Follow the platform specific instruction from the scapy website Note that there are at present 2 warnings about deprecated features in graphviz and for tests to work, you may need to adjust the fake args to point to your copy of the geoIP data file. Without access to the geoIP data, two of the tests will always fail.
Free, practical tutorials on capturing and analyzing network traffic âII from TCP retransmissions to DNS queries. Thirteen teaching captures, built packet by packet so every checksum is correct. Download them, open them in Wireshark, or read them right in the browser. Click-by-click instructions with filter commands you can paste straight into Wireshark.
Understand TCP , HTTP , DNS , TLS and more âII not just what to click, but why it matters. Start with the basics of packet capture and work up to expert-level troubleshooting techniques. Identify the hardware vendor behind any MAC address âII full IEEE registry, in your browser The lineage behind every capture tool âII the Unix original, the dead Windows port, and the NDIS 6 successor.
Use the built-in pktmon tool to capture, filter, and convert traffic to pcapng âII zero install. Header structure, flags, sequence numbers, three-way handshake, flow control, and retransmission mechanisms. Methods, headers, status codes, HTTP/2 binary framing, and how to analyze HTTP traffic in Wireshark. Query/response types, resource records, response codes, DNS caching, and troubleshooting name resolution.
Frame format, MAC addressing, VLAN 802.1Q tags, jumbo frames, and Wireshark analysis filters. Wireshark is a powerful network protocol analyzer used to capture and inspect packets traveling across a network. It helps users understand traffic flow, detect issues, and analyze protocols in deep detail. Wireshark captures network traffic by placing your Network Interface Card (NIC) into promiscuous mode, allowing it to view all packets on the network segment, not just those addressed to your system.
After capturing, Wireshark offers powerful tools to analyze packets in depth. You can narrow the view using display filters, making it easier to inspect specific conversations or protocols. Packet sniffing is a crucial part of network reconnaissance, monitoring, and troubleshooting. Capture filters in Wireshark allow you to restrict which packets are recorded before the capture begins. They help reduce noise by collecting only the traffic you're interested in.
Plugins make Wireshark adaptable for advanced network forensics and custom workflow needs. Analyzing network traffic often feels like trying to read a library's worth of information one letter at a time. When you open a raw PCAP file in a traditional packet editor, you are greeted by thousands of rows of hex code and metadata. While the data is all there, the story of what happened on your network is buried.
2. System Architecture & Core Working Principles In modern cybersecurity, speed is everything. To find a needle in a haystack, it helps if the haystack is organized. This is where visualization comes in. By transforming raw packets into timelines, topologies, and maps, you can spot anomalies in seconds that would take hours to find manually.
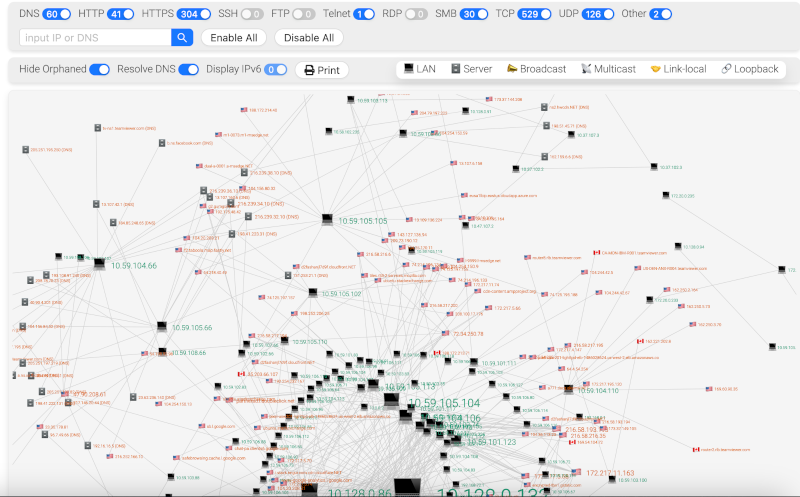
In this guide, we will walk through the step-by-step process of using apackets.com to visualize your network traffic and turn complex data into actionable insights. Before we dive into the "how," let's talk about the "why." Human brains are evolved to recognize patterns, colors, and spatial relationships much faster than strings of text. Visualization allows you to: The first thing you need to understand is the shape of the conversation. Who is talking to whom? When you upload a file to apackets.com , the tool automatically generates a Network Topology Graph . This creates a visual node for every IP address and a line for every connection.
A Time-Series Heatmap or Timeline shows the volume of packets over the duration of the capture. In a globalized world, knowing the physical destination of your data is the fastest way to confirm a breach. The Geo-IP Map plots every external IP address on a world map. This turns abstract numbers into a clear geographical narrative.
Use Heatmaps and Tree Maps to visualize bandwidth distribution. These visuals represent the volume of data as the size of a square. Visualizing your PCAP is only the first half of the battle. The goal is to move from Insight to Action . Once apackets reveals a suspicious node or a strange geographical connection: Manual packet analysis is a vital skill, but visualization is your shortcut to expertise. By using the browser-based tools at apackets.com , you can skip the steep learning curve of complex desktop software and get straight to the answers.
Whether you are hunting for a hidden rootkit or just trying to understand why the office Wi-Fi is slow, a single graph is worth a thousand packets. Self-hosted PCAP analysis tool for black-box network traffic forensics — reconstruct devices, topology, sessions, and threats from captured packets alone, with no prior knowledge of the network.
TracePcap is a self-hosted PCAP analysis workbench for black-box network analysis — situations where you work from the traffic itself , with no documentation or prior knowledge of the network. Upload one or more packet captures and TracePcap characterises devices, maps topology, reconstructs sessions, detects threats, tracks changes over time, and generates AI-powered narratives — all derived purely from observed traffic. It runs fully offline / air-gapped and keeps packet data on your own infrastructure.
TracePcap's capabilities fall into five pillars. Each links to its full page in the documentation . PCAP Upload & Management (PCAP/PCAPNG/CAP with MinIO object storage, duplicate detection, configurable limits) · Real-time asynchronous processing with stage-by-stage progress · Multi-protocol support (TCP, UDP, ICMP, TLS, HTTP, DNS, QUIC, and L2: ARP, STP, LLDP, CDP) · Export as PDF report (with live topology capture), per-conversation or bulk PCAP, and CSV.
The default stack's container limits total ~4.4GB (~5.4GB with the Keycloak auth overlay). Upload size is derived from APP_MEMORY_MB (max upload ≈ 16% of it; 327MB at the default 2048 ). See Container Resource Limits for the per-service breakdown and tuning. Note: First startup may take a minute while PostgreSQL and MinIO initialise. AI features require a running LLM server pointed to by LLM_API_BASE_URL ; all other features work without it. TracePcap is built to run fully offline — LLM_API_BASE_URL must point to a self- or LAN-hosted server, never a public/internet API.
Build a picture of an unknown network from captures taken at different times, and track how it changes between them: The Monitor assumes you know nothing about the network upfront: there is no persistent agent or sensor — you feed in PCAPs and it compares them. Subnets, device roles, and topology are all inferred from traffic rather than imported from a CMDB, and the first snapshot becomes the implicit baseline for change detection. See Network Monitor for the full change-detection event reference.
Full documentation is at https://notyusheng.github.io/TracePcap . Start here for anything not covered in this README: Interactive API docs (Swagger UI) are at http://localhost:80/swagger-ui.html when the app is running. Data is shared across all authenticated users (no per-user ownership) in this version; per-user scoping is tracked separately (issues #360, #444).
The sample-files/ directory contains example PCAPs, including atm_capture1.cap (ATM traffic), free5gc.pcap (5G core), demo_all_rules.pcap (triggers the full set of custom signature demo rules), dns_demo.pcap and http_demo.pcap (classification demos, each with a gen_*.py regenerator), and monitor_large/ (8 weekly snapshots of a simulated 550-node network for the Network Monitor). A full set of demo rules is in signatures.sample.yml .
Self-hosted PCAP analysis platform with LLM-powered incident triage, signature-based threat detection, and AI-generated incident narratives. Features network change monitoring across captures, deep packet inspection via nDPI, and automated Wireshark filter generation. Runs fully offline with local LLMs (Ollama, LM Studio). In computer networking, network traffic refers to the amount of data transmitted in the form of packets between internetworked computers or Cyber-Physical Systems. Monitoring and analyzing network traffic is crucial for ensuring the performance, security, and reliability of a network. However, a significant challenge in network traffic analysis is to process diverse data packets including both ciphertext and plaintext. While many methods have been adopted to analyze network traffic, they often rely on different datasets for performance evaluation. This inconsistency results in substantial manual data processing efforts and unfair comparisons. Moreover, some data processing methods may cause data leakage due to improper separation of training and testing data. To address these issues, we introduce the NetBench , a large-scale and comprehensive benchmark dataset for assessing machine learning models, especially foundation models, in both network traffic classification and generation tasks. NetBench is built upon seven publicly available datasets and encompasses a broad spectrum of 20 tasks, including 15 classification tasks and 5 generation tasks. Furthermore, we evaluate eight State-Of-The-Art (SOTA) classification models (including two foundation models) and two generative models using our benchmark. The results show that foundation models significantly outperform the traditional deep learning methods in traffic classification. We believe NetBench will facilitate fair comparisons among various approaches and advance the development of foundation models for network traffic. Our benchmark is available at https://github.com/WM-JayLab/NetBench .
In the domain of computer networking, network traffic [ 12 ] is the amount of data transmitted in the form of packets between interconnected computers or systems. Generally, a network packet is composed of two parts: a header containing meta features and a commonly encrypted payload, as shown in Fig. 1 . Analyzing network traffic is critical for enhancing network security and management. However, it is challenging to analyze network traffic due to the diversity of packet types, such as TCP and UDP, as well as the presence of both encrypted and unencrypted data.
Over the past decades, machine learning-based methods have been extensively developed for network traffic analysis. Earlier studies [ 6 , 5 , 19 , 15 , 7 ] primarily assessed the proposed methods on a single dataset encompassing at most 2 classification tasks. Despite achieving notable performance, these studies suffer from disparate data processing pipelines and insufficiently comprehensive evaluations. To address this issue, some recent works [ 3 , 4 , 22 ] have evaluated performance across multiple datasets and a broader range of classification tasks. For instance, the foundation model ET-BERT [ 4 ] was pre-trained on 7 datasets to learn intrinsic representations and then fine-tuned for 5 downstream tasks. However, the data processing techniques in existing works are often customized for themselves. Moreover, some studies randomly split the extracted packets from the same flow into training and testing dataset for packet-level evaluation, which may cause data leakage since the packets from same flow are strongly correlated. Additionally, certain research practices [ 20 , 18 ] only focused on traffic generation for network simulation rather than traffic classification. In summary, there is a lack of evaluation against a unified and comprehensive network benchmark that encompasses both network traffic classification and generation, making it hard to fairly compare performance.
To address existing limitations, we propose NetBench , a large-scale and comprehensive network traffic benchmark covering 7 distinct datasets, featuring 15 classification tasks and 5 generation tasks, as illustrated in Table 1 . For the classification benchmark, we construct 15 tasks across 7 datasets, including ISCXVPN 2016 [ 1 ] , ISCXTor 2016 [ 2 ] , USTC-TFC 2016 [ 17 ] , Cross-Platform [ 14 ] dataset containing both Android and IOS applications, CIRA-CIC-DoHBrw 2020 [ 9 ] , and CIC IoT Dataset 2023 [ 10 ] . The specific tasks for each dataset are outlined in table 1 . For the generation benchmark, we devise five tasks tailored to essential header fields [ 20 ] at the packet level, including IP addresses (Source/Destination), port number (Source/Destination) and packet length over the same 7 datasets above. This benchmark can help create valid network packets for network simulation.
To prevent data leakage, we first split the original network traffic data into training, validation, and testing sets, from which we extract flows and packets. Then, we anonymize sensitive header fields and employ a unified hexadecimal encoding to standardize different data formats. Moreover, our benchmark provides both flow-level and packet-level evaluations for each dataset, accommodating various input types. To the best of our knowledge, NetBench is the first network traffic benchmark that covers a wide range of tasks through a unified data processing method. Furthermore, we evaluate eight SOTA models (including two foundation models, ET-BERT [ 4 ] and YaTC [ 22 ] ) on 15 classification tasks and two generative models on 5 generation tasks using our benchmark. We believe that our benchmark has laid a solid foundation for evaluating network traffic models fairly, which will significantly contribute to the development of foundation models for network traffic.
Comprehensive Network Traffic Benchmark. We first create a large-scale and comprehensive network traffic benchmark from 7 distinct datasets with 20 tasks. Our benchmark offers diverse data types for foundation model training and a wide range of downstream tasks for fair evaluation in both network traffic classification and generation. Unified Data Processing. We introduce a uniform hexadecimal encoding method to process diverse network traffic data with anonymization in sensitive header fields. Our data processing method unifies data pre-processing, data standardization, and data segmentation, which can offer a fair evaluation opportunity and save human labor.
Benchmarking SOTA Methods. We compare the performance of eight SOTA classifiers (including two foundation models) and two generative models using our benchmark. The evaluation results demonstrate the superiority of foundation models over other approaches in traffic classification. 3. Software Implementation, Frameworks & Protocols Evaluation on Single Dataset. Most earlier machine learning-based studies have been evaluated using a single dataset focused on no more than two tasks. For example, FS-Net [ 6 ] assessed its performance on a campus network dataset [ 5 ] with 18 classes by extracting statistical features like packet length as model input. Similarly, BiLSTM_ATTN [ 19 ] implemented traffic segmentation and unwanted information removal for data processing before evaluation on the ISCXVPN-detection dataset [ 1 ] . DataNet [ 15 ] employed balanced subsets, byte vectorization, and normalization in its preprocessing steps, but its testing was confined to the ISCX VPN-application task. In addition, DeepPacket [ 7 ] built upon earlier efforts [ 19 , 15 ] to eliminate irrelevant packets for evaluation on the ISCXVPN dataset. STAN [ 18 ] applied normalization and one-hot encoding for pre-processing before it was evaluated on a selected subset from UGR’16 [ 8 ] dataset across 2 generation tasks. While these approaches have shown promising results, their evaluations were restricted to single dataset and a limited range of tasks. Moreover, the variance in their data processing techniques could result in biased comparisons.
Evaluation on Multiple datasets. To achieve a more comprehensive evaluation, recent works have assessed their models on more datasets covering a variety of tasks. For instance, TSCRNN [ 3 ] was evaluated on 3 public datasets following the pre-processing pipelines established in [ 19 , 15 ] . More recently, Transformer-based foundation models like ET-BERT [ 4 ] pre-trained on 6 public and 1 collected dataset to learn network traffic representations and then fine-tuned for 5 classification tasks. However, the construction of their packet-level evaluation datasets through random sampling raises the potential issue of data leakage, as highly correlated packets from the same flow could appear in both the training and testing datasets.
Additionally, the foundation model YaTC [ 22 ] pre-trained on 4 datasets for better representation and fine-tuned on 5 public datasets to test its generalization ability. Nevertheless, it faces a similar risk of data leakage for packet-level evaluation due to its use of a data processing methodology akin to ET-BERT. Meanwhile, NetShare [ 20 ] evaluated its generative performance across six datasets, although it is not designed for traffic classification tasks.
In summary, while current approaches have been assessed across various datasets and tasks, the comprehensiveness and fairness of these evaluations remain questionable due to the variance in data processing approaches. To our best knowledge, there has yet to be an establishment of a large-scale and comprehensive benchmark that enables a fair comparison across different models.
In this section, we create a large-scale and comprehensive benchmark dataset named NetBench , designed to standardize the evaluation of network traffic analysis models. Our benchmark contains 7 datasets with 20 tasks, including 15 classification tasks and 5 generation tasks. To create a large-scale and comprehensive benchmark, we first collect raw data samples from 7 publicly available datasets, as detailed in table 1 . Then, our next step is to convert them into a standardized format as model input. Fig. 2 shows the proposed pipeline of data preparation, which consists of three steps: Data Pre-Processing, Data Standardization, and Data Segmentation.
Data Pre-Processing. Network traffic data encompasses flows of network packets containing privacy-sensitive information. As network traffic packets are captured and saved in Packet Capture (PCAP) files, we firstly segments PCAP files into distinct set for training, validation, and testing. This strategy ensures that high-correlated packets from the same flow will not be simultaneously present in both training and testing data. This effectively reduces the risk of data leakage. Subsequently, we extract flows containing multiple packets from these PCAP files according to distinct combinations of IP addresses, port numbers and protocols [ 11 ] . To protect data privacy, we further anonymize each packet by masking the source/destination IP addresses and port numbers (replaced with 0). This not only preserves data integrity but also protects data privacy.
Data Standardization. Since data packets include both plaintext and ciphertext, we need to convert anonymized flows into a hexadecimal format, thereby unifying both header and payloads’ formats and reducing the complexity to process network traffic data. This standardization offers a fair and uniform basis for model comparison, benchmarking more accurately among different tasks in network traffic classification and generation. Following the same methodology in [ 4 ] , we employ the WordPiece algorithm to segment the hexadecimal data into 4-digit blocks, incorporating specific symbols ( for sequence ends,
for header separation, andData Segmentation. To capture the underlying characteristics of network traffic, we offer evaluation on each dataset at both flow level and packet level. Flow-level data is ideal for high-level analysis, allowing for the identification of trends, such as increasing or decreasing volumes of data over time, shifts in the types of traffic, and overall patterns of network use. Conversely, packet-level data enables a detailed examination of packet content and specific network traffic patterns. In addition to classification, we extract IP addresses, port numbers, and packet length for packet-level data as additional labels for generation tasks. By enabling evaluation at both levels, we can comprehensively evaluate the performance of different models in both classification and generation tasks.
Utilizing the described pipeline on seven collected traffic datasets, we construct a benchmark dataset for network traffic called NetBench . This dataset encompasses a total of 20 downstream tasks, including 15 traffic classification and 5 traffic generation tasks. Table 1 provides a detailed summary of NetBench . To our best knowledge, NetBench is the largest and most comprehensive benchmark in network traffic domain. It offers significant benefits for the development of foundational models and enables fair assessment of their performance.
To better understand different tasks, we give two representative examples about traffic classification and generation as follows. Classification Tasks: We utilize the ISCXVPN 2016 [ 1 ] dataset as an illustrative example. This dataset showcases the emulation of real-world internet behaviors by setting up user accounts to interact with each other on popular applications in VPN-routed or non-VPN scenarios. It involves capturing both VPN-routed and non-VPN internet sessions. There are three tasks: VPN Detection (Task 1) aims to ascertain the use of VPNs; VPN Service Detection (Task 2) seeks to identify 6 specific services, namely P2P, Streaming, Email, Chat, VoIP, and File Transfer; and VPN Application Detection (Task 3) strives to differentiate 17 distinct applications, including Facebook, Skype, YouTube, and more. Similarly, the remaining 12 tasks from other 6 datasets perform different types of classifications.
Generation Tasks: The goal of this task is to generate five pivotal header fields: the source IP address (Task 16), destination IP address (Task 17), source port (Task 18), destination port (Task 19), and the packet length (Task 20) [ 20 ] . This generation process entails the synthesis of 5 header fields to facilitate the creation of network traffic packets that closely mirrors real-world scenarios. Such generations are crucial to the evaluation of innovative networking hardware and software solutions [ 20 , 21 ] .
In this section, we perform a fair and holistic evaluation of SOTA models on the NetBench in both network traffic classification and generation tasks. SOTA Models . We assess the performance of 8 major SOTA open-source models on NetBench to ensure a comprehensive and unbiased comparison. Specifically, they include 7 classification models, DataNet [ 15 ] , FS-Net [ 6 ] , BiLSTM_ATTN [ 19 ] , DeepPacket [ 7 ] , TSCRNN [ 3 ] , ET-BERT [ 4 ] , YaTC [ 22 ] , as well as two competitive generative models, STAN [ 18 ] and Netshare [ 20 ] . Note that, ET-BERT and YaTC are foundation models which could be pre-trained and then fine-tuned on different classification tasks. The detailed experimental settings of each model are described below. For FS-Net, we follow its setting that only evaluate its performance in classification tasks at flow-level. For DataNet, DeepPacket, TSCRNN, and BiLSTM_ATTN, we assess their performance on all classification tasks at both flow level and packet level. Regarding ET-Bert and YaTC, we employ the released pre-trained weights and fine-tune them with the entirety of prepared training dataset. For generative models, we following the same setting in prior work [ 20 ] to randomly sample consecutive packets from each dataset, ensuring a consistent evaluation for future studies.
Dataset. We split our benchmark into training, validation, and testing data with a ratio of 8:1:1 respectively. Evaluation metrics. For assessing SOTA models in traffic understanding tasks, we employ two principal metrics: Accuracy (AC) and Macro F1 Score (F1). To evaluate the traffic generation performance, we utilize the Jensen-Shannon Divergence (JSD) and Total Variation Distance (TVD). JSD quantifies the similarity of two probability distributions, indicating their shared information, while TVD measures the largest difference between two probability distributions, capturing the maximum discrepancy.
Classification Tasks. Table 3 and 4 illustrate the comparison results of the 8 SOTA models for traffic classification using NetBench . From the evaluation results, we can conclude with three main insights: (1) Traditional deep learning methods, such as DataNet, DeepPacket, FS-Net, TSCRNN and BiLSTM_ATTN, exhibit limitations in generalizing to new tasks, with a noticeable tendency to bias classifications towards dominant classes. This is evidenced by the f1-score that is consistently below 0.5 with low recall score due to data imbalance. (2) Foundation models like ET-BERT and YaTC significantly outperform these traditional approaches, showcasing their superior prediction accuracy and generalization ability. (3) Although a flow with multiple packets inherently contains richer information compared to a single packet, foundation models trained at flow level do not surpass those trained on packet-level in tasks 3, 8, and 10. This is attributed to the constraints on the input length for foundation models as the input flows exceeding a specified length will be truncated.
Generation Tasks. We also compare the generation performance of two open-sourced generative models, STAN and NetShare, as shown in Table 5 . It can be observed that NetShare performs well in generating IP addresses and port numbers, while STAN achieves better performance on packet length generation. The main reason is that NetShare designs bitwise encoding [ 20 ] for IP addresses and IP2Vec encoding [ 13 ] for port numbers, which helps generating these fields accurately. Conversely, STAN integrates both CNN and mixture density neural layers to capture joint distribution of packet length effectively, explaining its superior performance in generating packet lengths.
We introduced NetBench , a large-scale and comprehensive benchmark for network traffic analysis, which addressed the critical issue of fair evaluation and comparison among different methods. Characterized by its comprehensive design, NetBench included a total of 20 evaluation tasks across 7 datasets through a unified data processing approach. Furthermore, we evaluated some SOTA models on our benchmark. The experimental results underscored the benefits of foundation models, which demonstrated superior performance across a wide range of classification tasks. These observations highlighted the significant potential of foundation models to revolutionize network traffic analysis. For traffic generation, very few foundation models have investigated in this field. This remains to explore in the future as foundation models have the potential to excel in generation tasks as they do in classification [ 16 ] . Besides, longer input length is needed for foundation models to better understand the increasingly complex network traffic. In short, future research could leverage NetBench to train foundation models in a convenient and straightforward manner for a variety of downstream network traffic classification and generation tasks. We believe that our benchmark will promote advancements in foundation models for network traffic through fair and comprehensive comparisons.
arXivLabs is a framework that allows collaborators to develop and share new arXiv features directly on our website. Both individuals and organizations that work with arXivLabs have embraced and accepted our values of openness, community, excellence, and user data privacy. arXiv is committed to these values and only works with partners that adhere to them.
Have an idea for a project that will add value for arXiv's community? Learn more about arXivLabs . A comprehensive D3.js visualization tool for analyzing and diagnosing network traffic from pcapng files. Features include zoom, pan, protocol-specific coloring, anomaly detection, and more. This project is a powerful and interactive network traffic visualization tool built using D3.js. It is designed to help network engineers, cybersecurity professionals, and researchers analyze and diagnose network traffic from pcapng files. The tool offers a variety of features to enhance data analysis, including zoom and pan capabilities, protocol-specific coloring, anomaly detection, and more.
Ensure tshark is installed: On Ubuntu/Debian: sudo apt-get install tshark On macOS (with Homebrew): brew install wireshark Open your web browser : Open your web browser: Navigate to http://localhost:3000 to access the visualization tool. Upload a pcapng file : Use the web interface to upload a pcapng file and explore the network traffic visualization. Contributions are welcome! If you have suggestions or improvements, feel free to create a pull request or open an issue.
A comprehensive D3.js visualization tool for analyzing and diagnosing network traffic from pcapng files. Features include zoom, pan, protocol-specific coloring, anomaly detection, and more. PCAPviz is a user interface for packet capture (PCAP) analytics. Built as an integrated frontend for Packet Café, PCAPviz can be deployed in multiple environments, including your local machine. It helps system administrators identify devices on a network, review traffic encryption, and see port listening ranges.
IQT Labs is pleased to release PCAPviz, a visualization interface for Packet Café , an automated packet capture (PCAP) analysis platform. PCAPviz and Packet Café are available as an integrated software package on GitHub. Both can be run locally at http://0.0.0.0/ and once you drag and drop a PCAP file into the application, PCAPviz gets to work bringing together the output of multiple Packet Café analytics in an easy-to-review visual dossier.
Since the "packet is the fundamental unit of information transport in all modern computer networks," PCAP analysis is a critical capability for system administrators, security teams, and digital forensics investigators who typically work with large collections of captured packets. This process frequently requires context-switching across different tools and different levels of analysis. We built PCAPviz to reduce the friction involved.
4. Practical Deployment, Analysis & Case Studies PCAPviz organizes the output of the Packet Café analysis platform into an intuitive card- and icon-based interface, along with accompanying visualizations. Users can see a high-level overview displaying a PCAP timestamp, capture duration (in seconds), file size (in kB), and related packet statistics. From there, one can proceed to more detailed views of the data. Our premise is that this combination enhances Packet Caf√© and makes several everyday PCAP analysis tasks less cumbersome and more efficient.
PCAPviz differs from many existing network analysis workflows in that it takes a device-centric approach to displaying PCAP outputs (rather than a more traditional protocol- or topology-based view of the data). It also differs in that existing packet capture visualization tools tend to be complex, with intricate protocol dissectors , multi-pane tabular displays, and force-directed graphs that sometimes make it challenging for administrators to spot security issues.
Along with interface complexity, today's PCAP analytics have an added drawback in that they focus on deterministic features, such as operating system fingerprints , protocol tags , and round-trip time . Few existing tools generate hypotheses about device roles (e.g., printer vs. active directory controller), which can be difficult to infer. Fewer still display categorical uncertainty present in the data, which prior IQT Labs work explains, "arises when things are sorted into predefined categories and an attempt is made to quantify the probability of misclassifying something as the wrong type of thing." Having access to Packet Café enabled us to go beyond these limitations by taking advantage of an existing analysis capability called NetworkML , which performs device role identification and outputs multiple hypotheses about network devices, also known as endpoints. Using host- and session-level data, the underlying machine learning model infers each device's functional role (e.g., printer or email server), which is an important element of piecing together a coherent picture of a PCAP.
To scope the initial set of features that would be most valuable to Packet Café users, we conducted nine key informant interviews with colleagues who work with PCAP data. This user research helped us identify common pain points, such as aggregating groups of devices and sharing findings with non-technical audiences. For this reason, PCAPviz enables users to export visualizations to share their findings with colleagues. The PCAPviz quick export tool is accessible through a collapsed menu icon (‚â°). It gives users three data format options: .svg and .png , which are widely used multimedia formats, and .csv , which enables further data analysis. This feature helps promote communication and eases the creation of incident reports, network security presentations, and digital forensics assessments.
Importantly, IQT Labs built PCAPviz to help users take advantage of the multiple analytics available in Packet Café. To see the this functionality in action, let's upload a sample PCAP and see how the PCAPviz interface summarizes it. In the PCAPviz Endpoint Summary view above, each card represents a group of devices, or endpoints, that appear to share a similar role on the network. PCAPviz displays the total number of devices within each group in teal (in this case, 26 devices captured within smallFlows, the majority of which appear to be Developer Workstations). Users can then explore additional device details in the Device Summary by either clicking on a card or selecting the relevant device category from a dropdown menu that remains visible at the top of PCAPviz data views. Below is an example of the types of comparisons that PCAPviz makes possible.
In the screenshot above, we see a device at the IPv4 address 192.168.3.99, which is either a printer or an Active Directory controller, or less likely, a GPU laptop. Given the potential for misclassification in this context, PCAPviz also provides categorical uncertainty data, displaying how confident NetworkML is in each device label. In this case, the confidence label of 63.54%, and the corresponding iconographic fill rate under Primary Label, highlights the fact that Packet Café's NetworkML module is almost 64% certain that the first device is, in fact, a printer. In considering the alterative hypotheses (Secondary and Tertiary label), we see that NetworkML assigns a 35.86% probability that the first device in the table above is an Active Directory controller (ADC) and a less than half of 1% probability it is a GPU laptop.
Categorical uncertainty arises when things are sorted into predefined categories and an attempt is made to quantify the probability of misclassifying something as the wrong type of thing. This is significant because these device types have little in common, highlighting the high degree of categorical uncertainty around this device so the user can investigate further and follow up appropriately. By comparison, the second device (a workstation at 173.178.118.29) in the table above has a lower level of associated uncertainty. Both the labels and fill rate displayed reflect that difference at a glance. At the bottom of the PCAPviz interface, the user can see additional traffic information in a series of adjacent visualizations (example below).
In the Traffic Summary view, PCAPviz presents the user with a simple bar chart that breaks down traffic into three categories (Encrypted, Plaintext, and Unknown). Packet Café determines whether a packet, traffic segment, or byte sequence is plaintext by tokenizing the packet header into words. If Packet Café finds any English words, PCAPviz considers the data plaintext. Conversely, if Packet Café cannot parse a given packet or if the packet is not UDP/TCP (i.e. contains ICMP, DNS, or DHCP traffic), PCAPviz marks the associated traffic as unknown.
From there, the Traffic Summary visualization enables the user to compare results across three levels of analysis (packets within the PCAP; conversations, or traffic between two specific endpoints; and bytes within the packet header), export their results, and proceed to further analysis. PCAPs provide rich snapshots of data traveling over networks. At the same time, PCAP analysis is a complicated sensemaking challenge compounded by multi-step workflows across deeply nested menus.
In building PCAPviz as an extension to Packet Café, we sought to consolidate multiple analytic outputs in a single graphical user interface (GUI) featuring linked views and easy export. Our aim was to apply two interface design principles — progressive disclosure (decluttering by layering) and recognition over recall (using icons for concreteness) — to help improve the usability of PCAP analytics, and we invite you to try it out for yourself.
PCAPviz and Packet Café are available as an integrated software package under the Apache 2.0 License. To start using PCAPviz (as well as the full range of analytics in Packet Café) on your own network capture data, make sure to review the prerequisites . Interested in contributing to PCAPviz? Please check out the Packet Cafe code repo for more details.
To learn more about prior IQT Labs research that informed our work on PCAPviz, please explore the following related blog posts: I Alternatively, visit High Stakes Design to see older dataviz-related posts from IQT Labs. Thank you to various colleagues, partners, and Packet Café end-users for thoughtful review and critique.
The packet loss is intermittent. The application team blames the network. The network team needs proof. Without visibility into what is actually moving across the wire, that argument drags on while users complain and the deal stalls. Network traffic analysis gives you the evidence to close that loop. It tells you what is happening on the network, where congestion lives, which endpoints are chattering the loudest, and whether that traffic looks suspicious. According to Mordor Intelligence (2026), the global network traffic analysis market is estimated at $4.91 billion in 2026, growing at 11.06% annually through 2031, driven largely by security and threat detection use cases, which account for nearly a third of current market revenue. The tools that serve this market range from free packet capture utilities to enterprise flow monitoring platforms and virtual network security suites. Picking the wrong layer wastes time. This guide helps you pick the right one.
This guide is for network engineers, security analysts, IT operations leads, and presales teams supporting technical validation. Tools were selected based on: The guide compares four tool types: Packet capture and command-line analyzers, commercial flow monitoring platforms, visibility infrastructure (TAPs and SPAN ports), and observability stack components including indexing and visualization tools.
Network traffic analysis software helps teams capture, inspect, summarize, and interpret data moving across a network so they can troubleshoot performance, investigate security events, and understand traffic behavior. The category covers several distinct approaches. Understanding which one you need is the first decision. Packet capture records raw packets for deep inspection. You see exactly what was in each frame, including protocol headers, payload content, timing, and retransmission patterns. This is how you prove what happened.
Flow analysis summarizes network conversations. Instead of recording every packet, flow protocols such as NetFlow, sFlow, and IPFIX report who talked to whom, on which port, for how long, and how many bytes moved. Flow analysis answers scale questions: Bandwidth usage, top talkers, application mix, and capacity trends. Traffic access methods such as network TAPs and SPAN ports are not analysis tools. They get packets to the analysis tool.
Without reliable traffic access, the best analyzer sees nothing. Security monitoring looks for anomalies, unauthorized connections, lateral movement, and policy violations. Some tools specialize here; others treat security as a downstream use of packet or flow data. Observability stack components such as Elasticsearch and Kibana store, index, and visualize traffic telemetry at scale. They belong in the stack when volume is high or cross-team investigation is needed.
5. Performance Evaluation & Extended Technical Observations An application is slow, but the cause is unclear. Packet capture lets you see retransmissions, TCP window issues, DNS delays, and congestion patterns that logs rarely surface. Flow analysis narrows the window faster: You can identify which source generated the spike, which application consumed the bandwidth, and when the problem started. Use both layers when the symptoms are elusive.
Security teams reach for traffic data when something looks wrong: A host calling out to an unexpected destination, unusual volume from an internal system, or traffic patterns that suggest lateral movement. Traffic analysis does not replace endpoint detection or SIEM controls, but it provides the network-layer evidence that corroborates or refutes a theory. The detail level matters: Packet capture shows payload context, while flow data shows connection patterns at scale.
Flow analysis tools built around application performance monitoring can show you which branch office is saturating its uplink, which application consumes the most bandwidth during business hours, and how traffic trends shift over weeks. For presales teams, this use case is common during technical validation: Buyers want proof that a monitoring tool can show usage patterns over time, not just point-in-time snapshots.
These tools are not interchangeable. Some inspect packets, some summarize flows, some provide visibility infrastructure, and others help index or visualize traffic telemetry. The table below positions each tool by its primary job, not by feature count. These tools do different jobs. Choose based on the question you need traffic data to answer, not on brand recognition alone. Wireshark is the reference tool for packet-level network analysis. Free, open-source, and available on Windows, macOS, and Linux, it captures live traffic and reads saved capture files with support for hundreds of protocols. Network engineers, security analysts, and developers have used it for decades to diagnose performance problems, investigate security incidents, and understand protocol behavior.
Best for: Network engineers and security analysts who need free, deep packet inspection with no licensing constraints. Why choose Wireshark: Wireshark is unmatched for protocol-level depth and community maturity. If your question is "what exactly happened in that TCP session," Wireshark gives you the answer. It is not a flow dashboard and does not replace long-term bandwidth reporting, so pair it with a flow tool for larger environments.
Wireshark pricing: Wireshark is free software distributed under the GNU General Public License version 2. There is no license fee. SolarWinds NetFlow Traffic Analyzer is a commercial flow-based traffic monitoring platform for bandwidth visibility and congestion troubleshooting. It collects flow data from network devices using NetFlow, sFlow, J-Flow, IPFIX, and several other flow protocols, then presents that data through dashboards, top-talker views, custom reports, and threshold-based alerts. IT operations teams use it to identify bandwidth-heavy applications, plan capacity, and document historical usage trends.
Best for: IT operations teams that need multi-vendor flow monitoring and enterprise-grade bandwidth visibility across a managed network. Why choose SolarWinds NetFlow Traffic Analyzer: The tool fits teams that need ongoing bandwidth visibility at scale, not one-time packet forensics. Packet-level investigation still belongs to a dedicated capture tool. SolarWinds gives you the summary layer; Wireshark or Tshark gives you the detail when a specific session needs examination. These layers are complementary, not redundant. Presales teams supporting application security testing or infrastructure evaluations will find its traffic-mapping reports useful for buyer validation conversations.
SolarWinds NetFlow Traffic Analyzer pricing: Pricing runs through sales and requires a custom quote. A fully functional 30-day trial is available on the product page. Tshark is Wireshark's terminal-based network protocol analyzer. Part of the Wireshark project, it captures and analyzes traffic from the command line without requiring a graphical interface. Engineers use it on remote servers, in automated scripts, and in headless environments where a GUI is impractical. Tshark reads and writes the same pcap and pcapng formats Wireshark uses, so captures transfer between the two without conversion.
Best for: Engineers who need Wireshark-grade protocol analysis in terminal sessions, automation pipelines, or remote server environments. Why choose Tshark: Tshark fits teams that are comfortable in the CLI and need packet analysis baked into scripts or CI/CD pipelines. It covers the same protocol depth as Wireshark without the GUI overhead. Teams using API monitoring tools alongside traffic analysis will find Tshark useful for correlating application-layer calls with raw network behavior.
Tshark pricing: Free, distributed as part of the Wireshark project under the same open-source license. Tcpdump is the classic command-line packet capture utility available on virtually every Unix-like operating system. It captures packets on a network interface, applies Berkeley Packet Filter expressions to narrow the capture, and prints packet summaries to the terminal or writes them to a pcap file for later analysis. Many engineers reach for it first during remote diagnostics because it is almost always present without additional installation.
Best for: Fast packet capture on servers, appliances, and remote systems where speed and availability matter more than a full analysis environment. Why choose Tcpdump: Tcpdump excels at rapid evidence collection. You run it, grab the pcap, and carry the file to Wireshark for detailed inspection. For presales teams demonstrating observability or bot detection product capabilities, Tcpdump output serves as credible raw evidence during technical validation sessions.
Tcpick is a text-mode, libpcap-based TCP stream sniffer focused on tracking and reconstructing TCP connections from captured traffic. Where Wireshark and Tcpdump capture everything, Tcpick narrows attention to TCP stream content, printing sessions in hexdump, printable-character, or raw mode. It reads live interfaces or existing pcap files. Best for: Analysts who need TCP stream reconstruction during targeted packet investigations without loading a full protocol analyzer.
Why choose Tcpick: Tcpick is a specialist tool. Use it when you need to follow a specific TCP session end to end and extract content, alongside a broader capture tool like Tcpdump. It handles the extraction step so you do not have to dig through raw hex manually. NGrep applies grep-like pattern matching to network traffic. It accepts extended regular expressions and hexadecimal patterns and matches them against packet payloads in real time or from pcap files. Engineers use it for quick protocol checks, payload searches, and rapid identification of specific strings or patterns moving across the wire. BPF filter support means you can narrow the scope before the regex runs.
Best for: Engineers who need to search packet streams for specific payload content or patterns quickly, without loading a full packet analyzer. Why choose NGrep: NGrep is fast and targeted. When you know what you are looking for and need to find it quickly, NGrep cuts search time compared to loading a full pcap into Wireshark. Its scope is narrow by design: It is not a dashboard, not a flow platform, and it cannot see inside encrypted payloads. Use it for plaintext protocol investigation and incident scoping.
NGrep pricing: Open-source; verify current license terms at the project repository before deployment. Elastic Packetbeat is a lightweight network packet analyzer that passively monitors traffic and ships application-layer transaction data to Elasticsearch or Logstash. Instead of storing raw packets, Packetbeat decodes protocols such as HTTP, DNS, MySQL, Redis, and others at the transaction level, recording request/response pairs, latency, status codes, and error rates. Teams already running the Elastic Stack use it to add network-layer context to their observability and security workflows.
Best for: Teams using the Elastic Stack who want application-layer network visibility without storing full pcap data. Why choose Elastic Packetbeat: Packetbeat fits environments where the Elastic Stack is already the central observability platform. It bridges the gap between network behavior and application performance without requiring separate packet storage infrastructure. Presales teams selling observability platforms will recognize its relevance to business activity monitoring conversations, where buyers want to connect network events to service-level outcomes.
Elastic Packetbeat pricing: Packetbeat itself is open and free to use. Deploying it into an Elastic Cloud environment runs on usage-based pricing; the Elastic Cloud hosted plans start at $99 per month for a Standard configuration. A network TAP (test access point) is a hardware device that sits inline on a network link and passes a full-duplex copy of all traffic to one or more monitoring tools, without interrupting the live network path. TAPs are the preferred traffic access method for serious packet capture and monitoring deployments because they copy every frame regardless of load, unlike switch mirroring which can drop packets under congestion.
Garland Technology, one of the reference vendors in this category, offers copper, fiber, and virtual TAP configurations across a range of port speeds and deployment scenarios. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/AMPRNet • https://github.com/subhashpolisetti/network-traffic-visualizer • https://github.com/1ultimat3/PcapViz • https://www.openpcap.com/ • https://www.geeksforgeeks.org/computer-networks/wireshark-packet-capturing-and-analyzing/ • https://apackets.com/blog/visualizing-invisible-pcap-data-network-insights • https://github.com/NotYuSheng/TracePcap • https://arxiv.org/html/2403.10319v2 • https://arxiv.org/abs/2203.12410 • https://github.com/webpro255/network-traffic-visualization
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Network Traffic Visualization Tool Using Python And PCAP.
! Define Extended Access List to Block Malicious Traffic ip access-list extended SECURE_PERIMETER_ACL remark Block Inbound Telnet and Unencrypted Services deny tcp any any eq 23 log remark Permit Verified Web SSL Traffic permit tcp any any eq 443 permit tcp any any eq 80 remark Mitigate ICMP Flood and Ping Sweeps permit icmp any any echo-reply deny icmp any any echo log deny ip any any log
! Apply ACL to Ingress Interface GigabitEthernet0/0 interface GigabitEthernet0/0 ip access-group SECURE_PERIMETER_ACL in no shutdown end write memory
Extended IP access list SECURE_PERIMETER_ACL (Cisco Packet Tracer) ──────────────────────────────────────────────────────────────────────── 10 deny tcp any any eq telnet log (142 matches) [Probes Dropped] 20 permit tcp any any eq 443 (18402 matches) [TLS 1.3 Traffic Permitted] 30 permit tcp any any eq 80 (4812 matches) 40 deny icmp any any echo log (524 matches) [Flood Mitigated] 50 deny ip any any log (38 matches) [Default Implicit Deny Rule] ──────────────────────────────────────────────────────────────────────── [✓] Packet Tracer Verification: 0 Unsanitized Ingress Leaks on Gi0/0
| Interface Port | Network Zone | Filter Applied | Traffic Processed | Firewall Decision |
|---|---|---|---|---|
| Gig0/0 (WAN) | Untrusted External | Extended ACL 101 | 24,810 Packets | INSPECTED & FILTERED |
| Gig0/1 (DMZ) | Public Web Services | Port 443 Only | 18,402 Packets | PERMITTED |
| Gig0/2 (LAN) | Corporate Users | 802.1X Port Security | 142 Probes | DENIED & QUARANTINED |