Complete Technical Paper Content — Network Vulnerability Scanner Using Python Nmap Module
Overview & System Context
Network Vulnerability Scanner Using Python Nmap Module: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9606 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background The Metasploit Project is a computer security project that provides information about security vulnerabilities and aids in penetration testing and IDS signature development. It is owned by Rapid7, a Boston-based security company. Its best-known sub-project is the open-source Metasploit Framework, a tool for developing and executing exploit code against a remote target machine. Other important sub-projects include the Opcode Database, shellcode archive and related research. The Metasploit Project includes anti-forensic and evasion tools, some of which are built into the Metasploit Framework. In various operating systems it comes pre installed.
Optionally checking whether the intended target system is vulnerable to an exploit. Choosing and configuring an exploit (code that enters a target system by taking advantage of one of its bugs; about 900 different exploits for Windows, Unix/Linux and macOS systems are included). Choosing and configuring a payload (code that will be executed on the target system upon successful entry; for instance, a remote shell or a VNC server). Metasploit often recommends a payload that should work.
Choosing the encoding technique so that hexadecimal opcodes known as "bad characters" are removed from the payload, these characters will cause the exploit to fail. Executing the exploit. This modular approach – allowing the combination of any exploit with any payload – is the major advantage of the Framework. It facilitates the tasks of attackers, exploit writers and payload writers. Metasploit runs on Unix (including Linux and macOS) and on Windows. The Metasploit Framework can be extended to use add-ons in multiple languages. To choose an exploit and payload, some information about the target system is needed, such as operating system version and installed network services. This information can be gleaned with port scanning and TCP/IP stack fingerprinting tools such as Nmap. Vulnerability scanners such as Nessus, and OpenVAS can detect target system vulnerabilities. Metasploit can import vulnerability scanner data and compare the identified vulnerabilities to existing exploit modules for accurate exploitation.
A command-line interface for controlling exploit modules. Database for managing scan data and exploit results. Import of network scan results from external scanning utilities such as Nmap. Scanning support using the integrated `db_nmap` feature for automated execution and data integration. Over 1,500 built-in exploits, with the ability of adding custom exploit modules or automated resource scripts. The Metasploit Framework is implemented in Ruby and uses a modular software architecture.
Command shell enables users to run collection scripts or run arbitrary commands against the host. Meterpreter (the Metasploit Interpreter) enables users to control the screen of a device using VNC and to browse, upload and download files. Dynamic payloads enable users to evade anti-virus defense by generating unique payloads. Static payloads enable static IP address/port forwarding for communication between the host and the client system.
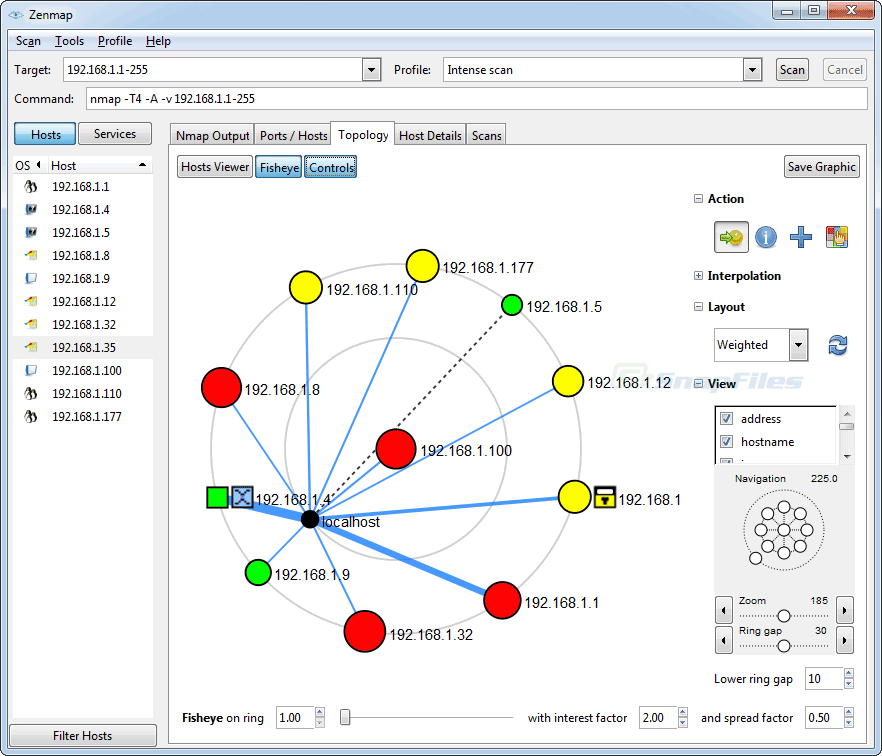
Figure 1: Nmap Security Scanner screenshot and download at SnapFiles.com H. D. Moore (founder and chief architect) Matt Miller (core developer from 2004–2008) Dean McNamee (Spoonm) (core developer from 2003–2008) Heartbleed is a security bug in some outdated versions of the OpenSSL cryptography library, which is a widely used implementation of the Transport Layer Security (TLS) protocol. It was introduced into the software in 2012 and publicly disclosed in April 2014. Heartbleed could be exploited regardless of whether the vulnerable OpenSSL instance is running as a TLS server or client. It resulted from improper input validation (due to a missing bounds check) in the implementation of the TLS heartbeat extension. Thus, the bug's name derived from heartbeat. The vulnerability was classified as a buffer over-read, a situation where more data can be read than should be allowed. Heartbleed was registered in the Common Vulnerabilities and Exposures database as CVE-2014-0160. A fixed version of OpenSSL was released on 7 April 2014, on the same day Heartbleed was publicly disclosed. TLS implementations other than OpenSSL, such as GnuTLS, Mozilla's Network Security Services, and the Windows platform implementation of TLS, were not affected because the defect existed in the OpenSSL's implementation of TLS rather than in the protocol itself. System administrators were frequently slow to patch their systems. As of 20 May 2014, 1.5% of the 800,000 most popular TLS-enabled websites were still vulnerable to the bug, and by 21 June 2014, 309,197 public web servers remained vulnerable. According to a 23 January 2017 report from Shodan, nearly 180,000 internet-connected devices were still vulnerable to the bug, but by 6 July 2017, the number had dropped to 144,000 according to a search performed on shodan.io for the vulnerability. Around two years later, 11 July 2019, Shodan reported that 91,063 devices were vulnerable. The U.S. had the most vulnerable devices, with 21,258 (23%), and the 10 countries with the most vulnerable devices had a total of 56,537 vulnerable devices (62%). The remaining countries totaled 34,526 devices (38%).
The report also broke the devices down by 10 other categories such as organization (the top 3 were wireless companies), product (Apache httpd, Nginx), and service (HTTPS, 81%). At the time of disclosure, some 17% (around half a million) of the Internet's secure web servers certified by trusted authorities were believed to be vulnerable to the attack, allowing theft of the servers' private keys and users' session cookies and passwords. The Electronic Frontier Foundation, Ars Technica, and Bruce Schneier all deemed the Heartbleed bug "catastrophic". Forbes cybersecurity columnist Joseph Steinberg wrote:Some might argue that Heartbleed is the worst vulnerability found (at least in terms of its potential impact) since commercial traffic began to flow on the Internet. An unidentified UK Cabinet Office spokesman recommended that: People should take advice on changing passwords from the websites they use. Most websites have corrected the bug and are best placed to advise what action, if any, people need to take. On the day of disclosure, The Tor Project advised: If you need strong anonymity or privacy on the Internet, you might want to stay away from the Internet entirely for the next few days while things settle. The Sydney Morning Herald published a timeline of the discovery on 15 April 2014, showing that some organizations had been able to patch the bug before its public disclosure. In some cases, it is not clear how they found out.
By reusing the same private key, a site that was affected by the Heartbleed bug still faces exactly the same risks as those that have not yet replaced their SSL certificates. eWeek said, "[Heartbleed is] likely to remain a risk for months, if not years, to come." Cloudflare revoked all TLS certificates and estimated that publishing its certificate revocation list would cost the issuer, GlobalSign, $400,000 per month that year.
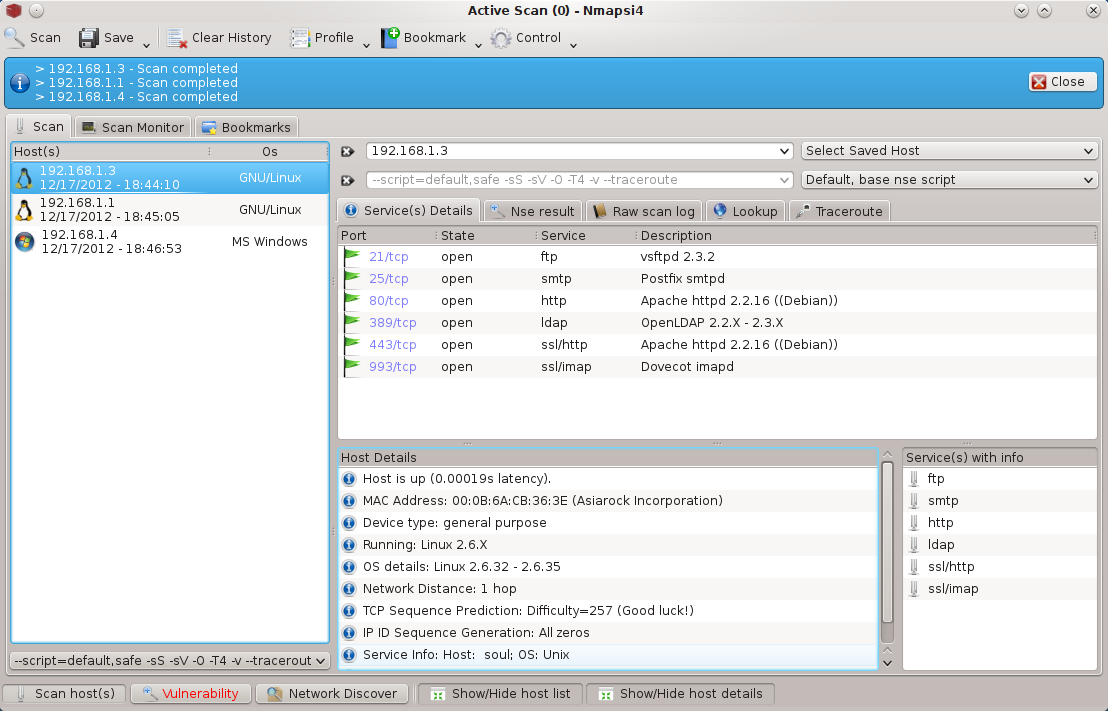
Figure 2: nmapsi4 v0.4.1: nmap Graphical User Interface | Turorial Grapich Design ... The RFC 6520 Heartbeat Extension tests TLS/DTLS secure communication links by allowing a computer at one end of a connection to send a Heartbeat Request message, consisting of a payload, typically a text string, along with the payload's length as a 16-bit integer. The receiving computer then must send exactly the same payload back to the sender. The affected versions of OpenSSL allocate a memory buffer for the message to be returned based on the length field in the requesting message, without regard to the actual size of that message's payload. Because of this failure to do proper bounds checking, the message returned consists of the payload, possibly followed by whatever else happened to be in the allocated memory buffer. Heartbleed is therefore exploited by sending a malformed heartbeat request with a small payload and large length field to the vulnerable party (usually a server) in order to elicit the victim's response, permitting attackers to read up to 64 kibibytes of the victim's memory that was likely to have been used previously by OpenSSL. Where a Heartbeat Request might ask a party to "send back the four-letter word 'bird'", resulting in a response of "bird", a malicious "Heartbleed request" of "send back the 500-letter word 'bird'" would cause the victim to return "bird" followed by whatever 496 subsequent characters the victim happened to have in active memory. Attackers in this way could receive sensitive data, compromising the confidentiality of the victim's communications. Although an attacker has some control over the disclosed memory block's size, it has no control over its location, and therefore cannot choose what content is revealed.
The Canadian federal government temporarily shut online services of the Canada Revenue Agency (CRA) and several government departments over Heartbleed bug security concerns. Before the CRA online services were shut down, a hacker obtained approximately 900 social insurance numbers. Another Canadian Government agency, Statistics Canada, had its servers compromised due to the bug and also temporarily took its services offline. Platform maintainers like the Wikimedia Foundation advised their users to change passwords. The servers of LastPass were vulnerable, but due to additional encryption and forward secrecy, potential attacks were not able to exploit this bug. However, LastPass recommended that its users change passwords for vulnerable websites. The Tor Project recommended that Tor relay operators and hidden service operators revoke and generate fresh keys after patching OpenSSL, but noted that Tor relays use two sets of keys and that Tor's multi-hop design minimizes the impact of exploiting a single relay. 586 relays later found to be susceptible to the Heartbleed bug were taken off-line as a precautionary measure. Game-related services including Steam, Minecraft, Wargaming, League of Legends, GOG.com, Origin, Sony Online Entertainment, Humble Bundle, and Path of Exile were affected and subsequently fixed.
Several Hewlett-Packard server applications, such as HP System Management Homepage (SMH) for Linux and Windows. Some versions of FileMaker 13 LibreOffice 4.2.0 to 4.2.2 (fixed in 4.2.3) LogMeIn claimed to have "updated many products and parts of our services that rely on OpenSSL". Multiple McAfee products, in particular some versions of software providing anti-viral coverage for Microsoft Exchange, software firewalls, and McAfee Email and Web Gateways Oracle MySQL Connector/C 6.1.0-6.1.3 and Connector/ODBC 5.1.13, 5.2.5-5.2.6, 5.3.2 Oracle Big Data Appliance (includes Oracle Linux 6) Primavera P6 Professional Project Management (includes Primavera P6 Enterprise Project Portfolio Management) WinSCP (FTP client for Windows) 5.5.2 and some earlier versions (only vulnerable with FTP over TLS/SSL, fixed in 5.5.3) Multiple VMware products, including VMware ESXi 5.5, VMware Player 6.0, VMware Workstation 10 and the series of Horizon products, emulators and cloud computing suites Several other Oracle Corporation applications were affected.
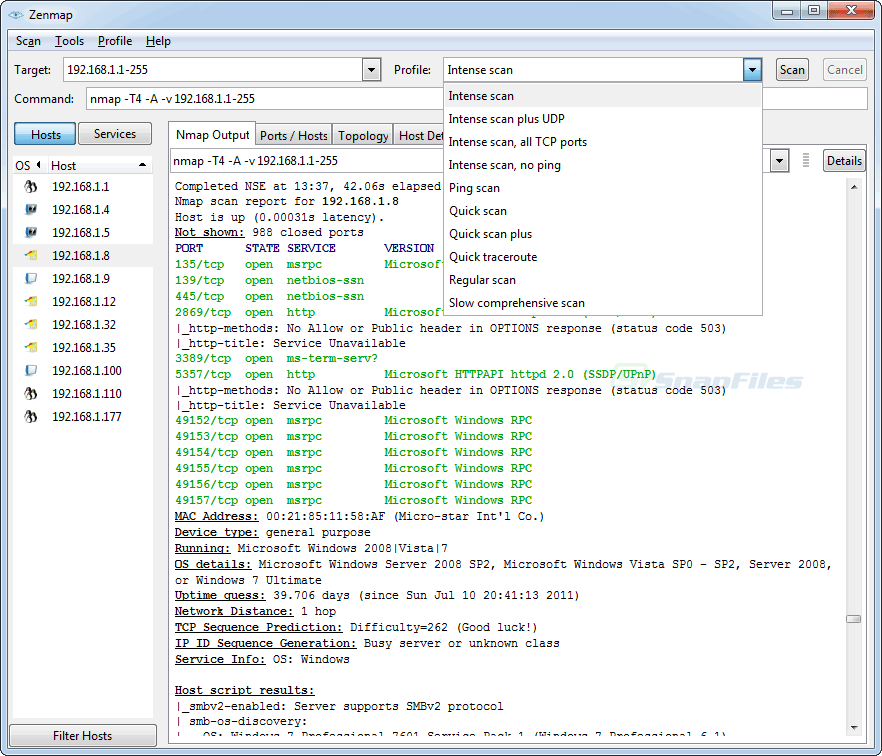
Android 4.1.1, used in various portable devices. Chris Smith writes in Boy Genius Report that just this one version of Android is affected but that it is a popular version of Android (Chitika claim 4.1.1 is on 50 million devices; Google describe it as less than 10% of activated Android devices). Other Android versions are not vulnerable as they either have heartbeats disabled or use an unaffected version of OpenSSL. Firmware for some AirPort base stations Firmware for some Cisco Systems routers Firmware for some Juniper Networks routers pfSense 2.1.0 and 2.1.1 (fixed in 2.1.2) DD-WRT versions between and including 19163 and 23881 (fixed in 23882) Western Digital My Cloud product family firmware Figure 3: Download The Free Nmap Security Scanner For Linux/Mac/Windows – SJDBG Tripwire SecureScan AppCheck – static binary scan and fuzzing, from Synopsys Software Integrity Group (formerly Codenomicon) Arbor Network's Pravail Security Analytics Norton Safeweb Heartbleed Check Tool Heartbleed testing tool by a European IT security company Heartbleed test by Italian cryptographer Filippo Valsorda Heartbleed Vulnerability Test by Cyberoam Critical Watch Free Online Heartbleed Tester Metasploit Heartbleed scanner module Heartbleed Server Scanner by Rehmann Lookout Mobile Security Heartbleed Detector, an app for Android devices that determines the OpenSSL version of the device and indicates whether the vulnerable heartbeat is enabled Heartbleed checker hosted by LastPass Online network range scanner for Heartbleed vulnerability by Pentest-Tools.com Official Red Hat offline scanner written in the Python language Qualys SSL Labs' SSL Server Test which not only looks for the Heartbleed bug, but can also find other SSL/TLS implementation errors. Browser extensions, such as Chromebleed and FoxBleed SSL Diagnos CrowdStrike Heartbleed Scanner – Scans routers, printers and other devices connected inside a network including intranet web sites. Netcraft Site Report – indicates whether a website's confidentiality could be jeopardized due to a past exploitation of Heartbleed by checking data from Netcraft's SSL Survey to determine whether a site offered the heartbeat TLS Extension prior to the Heartbleed disclosure. The Netcraft Extensions for Chrome, Firefox and Opera also perform this check, whilst looking for potentially compromised certificates. Other security tools have added support for finding this bug. For example, Tenable Network Security wrote a plugin for its Nessus vulnerability scanner that can scan for this fault. The Nmap security scanner includes a Heartbleed detection script from version 6.45. Sourcefire has released Snort rules to detect Heartbleed attack traffic and possible Heartbleed response traffic. Open source packet analysis software such as Wireshark and tcpdump can identify Heartbleed packets using specific BPF packet filters that can be used on stored packet captures or live traffic.
OpenSSL core developer Ben Laurie claimed that a security audit of OpenSSL would have caught Heartbleed. Software engineer John Walsh commented: Think about it, OpenSSL only has two [fulltime] people to write, maintain, test, and review 500,000 lines of business critical code. The OpenSSL foundation's president, Steve Marquess, said "The mystery is not that a few overworked volunteers missed this bug; the mystery is why it hasn't happened more often." David A. Wheeler described audits as an excellent way to find vulnerabilities in typical cases, but noted that "OpenSSL uses unnecessarily complex structures, which makes it harder to both humans and machines to review." He wrote: There should be a continuous effort to simplify the code, because otherwise just adding capabilities will slowly increase the software complexity. The code should be refactored over time to make it simple and clear, not just constantly add new features. The goal should be code that is "obviously right", as opposed to code that is so complicated that "I can't see any problems". According to security researcher Dan Kaminsky, Heartbleed is sign of an economic problem which needs to be fixed. Seeing the time taken to catch this simple error in a simple feature from a "critical" dependency, Kaminsky fears numerous future vulnerabilities if nothing is done. When Heartbleed was discovered, OpenSSL was maintained by a handful of volunteers, only one of whom worked full time. Yearly donations to the OpenSSL project were about US$2,000. The Heartbleed website from Codenomicon advised money donations to the OpenSSL project. After learning about donations for the 2 or 3 days following Heartbleed's disclosure totaling US$841, Kaminsky commented "We are building the most important technologies for the global economy on shockingly underfunded infrastructure." Core developer Ben Laurie has qualified the project as "completely unfunded". Although the OpenSSL Software Foundation has no bug bounty program, the Internet Bug Bounty initiative awarded US$15,000 to Google's Neel Mehta, who discovered Heartbleed, for his responsible disclosure. Mehta later donated his reward to a Freedom of the Press Foundation fundraiser. Paul Chiusano suggested Heartbleed may have resulted from failed software economics. The industry's collective response to the crisis was the Core Infrastructure Initiative, a multimillion-dollar project announced by the Linux Foundation on 24 April 2014 to provide funds to critical elements of the global information infrastructure. The initiative intends to allow lead developers to work full time on their projects and to pay for security audits, hardware and software infrastructure, travel, and other expenses. OpenSSL is a candidate to become the first recipient of the initiative's funding. After the discovery Google established Project Zero which is tasked with finding zero-day vulnerabilities to help secure the Web and society.
Summary and Q&A about the bug by Codenomicon Ltd Information for Canadian organizations and individuals List of all security notices Archived 19 July 2018 at the Wayback Machine This is a list of TCP and UDP port numbers used by protocols for operation of network applications. The Transmission Control Protocol (TCP) and the User Datagram Protocol (UDP) only need one port for bidirectional traffic. TCP usually uses port numbers that match the services of the corresponding UDP implementations, if they exist, and vice versa. The Internet Assigned Numbers Authority (IANA) is responsible for maintaining the official assignments of port numbers for specific uses.
However, many unofficial uses of both well-known and registered port numbers occur in practice. Similarly, many of the official assignments refer to protocols that were never or are no longer in common use. This article lists port numbers and their associated protocols that have experienced significant uptake. The port numbers in the range from 0 to 1023 (0 to 210 − 1) are the well-known ports or system ports. They are used by system processes that provide widely used types of network services. On Unix-like operating systems, a process must execute with superuser privileges to be able to bind a network socket to an IP address using one of the well-known ports.
The range of port numbers from 1024 to 49151 (210 to 215 + 214 − 1) are the registered ports. They are assigned by IANA for specific service upon application by a requesting entity. On most systems, registered ports can be used without superuser privileges. The range 49152–65535 (215 + 214 to 216 − 1), 16 384 ports, contains dynamic or private ports that cannot be registered with IANA. This range is used for private or customized services, for temporary purposes, and for automatic allocation of ephemeral ports.
This documentation provides an in-depth exploration of vulnerability scanning techniques essential for penetration testing and the OSCP certification. Content is derived from OffSec PEN-200 courseware, rephrased and organized for practical application. The industry-standard port scanner with powerful NSE scripting capabilities for lightweight vulnerability detection.
Professional vulnerability scanner with extensive plugin library covering 67,000+ CVEs. Open-source vulnerability assessment framework with 50,000+ Network Vulnerability Tests (NVTs). Mohamed Trigui is a cybersecurity enthusiast completing a Master's in Cybersecurity at Illinois Tech. Currently preparing for OSCP certification through hands-on practice on Hack The Box and developing custom security tools.
Current Projects: - Replicating vulnerabilities on Linux and writing Lua patches - Developing Nmap NSE scripts for zero-day reconnaissance - Writing HTB machine walkthroughs and exploit documentation This guide is for educational purposes only . Always obtain proper authorization before scanning any systems. Unauthorized vulnerability scanning is illegal and unethical.
Content is derived from OffSec PEN-200 (OSCP) training materials, rephrased and adapted for educational purposes. All credit for the original methodology and techniques goes to Offensive Security. This documentation is provided as-is for educational purposes. When using these techniques: The Nmap Scripting Engine (NSE) is a built-in framework that extends Nmap from a port scanner into a vulnerability detection platform, with over 600 Lua scripts included in the standard distribution (Nmap.org). You point it at discovered services, and it checks for known CVEs, misconfigurations, weak authentication, and backdoors without needing a separate tool.
Having used Nmap across hundreds of security assessments over the years, NSE is the part that separates casual scanning from actual vulnerability work. The port scan tells you what is running. NSE tells you what is broken. When the Heartbleed vulnerability affected hundreds of thousands of systems in 2014, Nmap's developers shipped a detection script within 48 hours (Nmap.org). That speed of response, combined with community-maintained scripts covering everything from SMB exploits to database enumeration, is why NSE remains the go-to for practitioners who need fast, scriptable vulnerability detection.
NSE is a scripting framework built into Nmap that runs Lua scripts alongside or after your scans. If you followed our Nmap Network Scanning guide , you already know how to find open ports and identify services. NSE answers the next question: what vulnerabilities exist on those services? Scripts execute automatically based on what Nmap discovers. Find an open port 443? NSE can check for Heartbleed, weak ciphers, and certificate issues in the same scan pass. Find MySQL on 3306? It can enumerate databases, test default credentials, and match the version against known CVEs.
The power of NSE is integration. Unlike standalone vulnerability scanners, everything happens within your existing Nmap workflow. One tool chain from discovery through to vulnerability assessment. NSE organises its 600+ scripts into 14 categories based on function and risk level. Understanding these categories is essential because they control what runs and how aggressive it gets.
The risk boundary that matters most: default , safe , and vuln are appropriate for production network audits and authorised assessments. Everything above auth requires explicit authorisation, a controlled environment, and documented approval. Running exploit or dos scripts against production systems without written permission is both illegal and irresponsible. Scripts can belong to multiple categories. The ssl-heartbleed script, for example, sits in vuln , safe , and discovery because it checks for a vulnerability without any risk of crashing the target.
That single flag runs every script tagged with the vuln category against your target. Combine it with -sV for version detection and the scripts have more context to work with. Which categories should you never run on production systems? The dos , exploit , and fuzzer categories can crash services, corrupt data, or cause outages. The brute category generates massive log entries and can lock out legitimate user accounts.
Keep these in your lab environments. The --script vuln flag tells Nmap to run every script in the vuln category against discovered services. This is your primary vulnerability assessment workflow, and understanding exactly what it does matters more than most people realise. 2. System Architecture & Core Working Principles Nmap first performs service detection ( -sV ), then passes those results to every vuln-category script. Each script checks whether the detected service version matches a known vulnerability. If it finds one, the output explicitly marks it as VULNERABLE with the relevant CVE reference.
Here is what it checks for (this is not exhaustive, but covers the scripts practitioners encounter most often): When nothing is found, most vuln scripts produce no output at all. No news is good news. One thing that catches people out: --script vuln does NOT include the popular vulners.nse or vulscan.nse scripts. Those are external scripts that need separate installation. The vuln category only contains scripts bundled with the Nmap distribution. I have seen pentesters assume they are getting CVE database matching from --script vuln when they are actually only getting the built-in checks. If you want CVE matching against service versions, you need vulners.nse (covered in the next section).
The syntax variations --script vuln and --script=vuln are identical. Both work. Use whichever you prefer. The vulners.nse script queries the vulners.com API to match detected service versions against their CVE database. It is one of the most popular third-party NSE scripts because it automates what practitioners used to do manually: scan a service, note the version, then search for known vulnerabilities against that version.
Important: vulners.nse is not included with Nmap by default. You need to install it separately from the nmap-vulners GitHub repository . The -sV flag is mandatory here. Without version detection, vulners.nse has nothing to match against. It needs to know the exact service version to query the CVE database.
By default, vulners.nse returns every CVE match regardless of severity. On a server running multiple services, this can produce pages of low-severity results that bury the critical findings. The mincvss argument filters output by CVSS score. This only displays CVEs with a CVSS score of 7.0 or higher (High and Critical severity). For a quick triage during a time-pressured assessment, I typically start at mincvss=9.0 to find critical issues first, then widen to 7.0 for the full high-severity picture.
For most assessments, vulners.nse is the better choice. Use vulscan when you are scanning air-gapped networks or environments where outbound API calls are restricted. Building your security toolkit? Our Cybersecurity Skills Roadmap maps out what to learn and in what order. Beyond the vuln category and vulners.nse, NSE includes scripts that target individual vulnerabilities and protocols. The queries I see most often from practitioners involve a handful of high-value scripts.
The ssl-heartbleed script tests whether a server is vulnerable to the Heartbleed bug in OpenSSL, which allows attackers to read server memory contents including private keys and session data. The output is binary: VULNERABLE or nothing. The script sits in the vuln , safe , and discovery categories, meaning it is safe to run against production systems. Despite Heartbleed being disclosed in 2014, unpatched instances still exist. It remains one of the most commonly requested NSE checks in CTF environments and real-world audits alike.
This checks for EternalBlue (MS17-010, the exploit behind WannaCry), MS08-067, and other critical Windows SMB flaws. Indispensable when auditing Windows environments. This table covers the scripts that appear most frequently in workflows and requests. Each entry includes the exact script name, category membership, and a ready-to-use command.
Use nmap --script-help=script-name to see available arguments for any script. The full NSE script library is browsable at nmap.org/nsedoc . Individual scripts are useful, but real assessments combine multiple scan techniques. These are the workflows I reach for most often.
SYN scan for speed ( -sS ), version detection for context ( -sV ), all built-in vulnerability scripts ( --script vuln ), and output saved in all formats ( -oA ). This is the standard starting point for any authorised assessment. Same foundation, but using vulners.nse instead of the built-in vuln category. The mincvss=7.0 filter cuts noise and surfaces only High and Critical severity CVEs. Run this after the quick assessment to get the CVE-level detail.
Targeted web assessment: enumerates directories and files, grabs HTTP headers, lists allowed HTTP methods, and checks for missing security headers. All safe-category scripts, appropriate for production web servers. Sweeps an entire subnet for known SMB vulnerabilities. The * wildcard matches all smb-vuln scripts. Essential for Windows environment audits where EternalBlue and related exploits remain a real threat.
Scans common database ports (MSSQL, MySQL, PostgreSQL, MongoDB) and runs info and enumeration scripts. Identifies exposed databases, default configurations, and information disclosure. Checks for known backdoors including NSA's DoublePulsar and backdoored versions of UnrealIRCd, vsftpd, and ProFTPd (Nmap.org). Fast to run and safe for production systems.
Once you are comfortable with the basics, script arguments and advanced techniques give you much finer control. The comma-separated list runs scripts from both categories. This is more thorough than vuln alone because safe-category scripts add enumeration data that helps you understand the attack surface around any vulnerabilities found. The + prefix forces a script to run even when Nmap did not detect the expected service on that port. Useful when services run on non-standard ports or when initial detection was inconclusive.
The * wildcard matches all scripts starting with http-vuln- . This runs every HTTP vulnerability check without needing to list them individually. Script names appear prefixed with a pipe character ( | ). VULNERABLE findings are explicitly marked with state and risk factor. CVE references link to further research. When a script finds nothing, it typically produces no output.
Always save your results with -oA filename . The XML output ( -oX ) integrates with Metasploit, Burp Suite, and vulnerability management platforms for downstream analysis. Scripts in the exploit, dos, brute, and intrusive categories can damage systems. Running them without explicit written authorisation is illegal and unethical.
Start with default and safe categories. Use vuln on authorised targets only. Never run exploit or dos on production systems. Test in labs first using platforms like TryHackMe, HackTheBox, or your own VMs. If you are building a practice environment, our guide to building a cybersecurity homelab walks through the full process. Apply the same principles from our Linux Basics for Hackers guide: safe, authorised, and documented testing only.
It runs every NSE script in the vuln category against your target, checking for known vulnerabilities like Heartbleed, EternalBlue, and Shellshock. Combine it with -sV for best results: nmap -sV --script vuln target.com . It does not include external scripts like vulners.nse. Use nmap --script vuln target.com or equivalently nmap --script=vuln target.com . Both syntaxes work identically and run every script tagged with the vuln category.
NSE is a built-in Nmap framework that runs Lua scripts for vulnerability detection, service enumeration, brute force testing, and exploitation. Over 600 scripts are included in the standard Nmap distribution, organised into 14 categories by function and risk level. The mincvss argument filters vulners.nse output by minimum CVSS score. Setting --script-args mincvss=7.0 only displays CVEs rated High or Critical, cutting through low-severity noise. Useful values: 9.0 for critical only, 7.0 for high and critical, 5.0 for medium and above.
No. vulners.nse is a third-party script maintained on GitHub. You need to download it separately from the nmap-vulners repository and copy it to your Nmap scripts directory. Run nmap --script-updatedb after installation. NSE has 14 categories: default, safe, vuln, discovery, auth, brute, intrusive, exploit, malware, dos, version, broadcast, external, and fuzzer. Each category groups scripts by function and risk level. Use default and safe freely. Use vuln on authorised targets. Treat everything else with caution.
3. Software Implementation, Frameworks & Protocols The dos , exploit , and fuzzer categories can crash services, corrupt data, or cause outages. The brute category triggers account lockouts and generates massive log entries. These categories should only be used in controlled lab environments with explicit authorisation.
NSE turns Nmap from a port scanner into a vulnerability assessment platform. The --script vuln category gives you built-in detection for critical flaws like Heartbleed and EternalBlue. The vulners.nse script adds CVE database matching with severity filtering through the mincvss argument. Combined with the network scanning fundamentals and Linux command proficiency , NSE completes your reconnaissance and vulnerability assessment toolkit.
Start with --script vuln for built-in checks. Add vulners.nse for CVE matching. Use individual scripts like ssl-heartbleed and smb-vuln-* for targeted testing. Save everything with -oA and feed it into the rest of your security stack. I am a red team operator, and a security enthusiast I write blogs and articles related to cyber-sec topics. I am a red team operator, and a security enthusiast I write blogs and articles related to cyber-sec topics.
I am a red team operator, and a security enthusiast I write blogs and articles related to cyber-sec topics. Network Scanning or network recon is a fingerprinting method used by hackers to find open ports, services, service versions, and possible vulnerabilities. But the question is how these scanners work and how can we implement them using a few open-source modules or build one.
In this blog, I will be discussing various things a network scanner does, and for this explanation, I will be explaining using nmap (network mapper) as a medium of scans and we will be implementing a simple network scanner using python and Python-Nmap module. Network scanners, as the name suggests, scan an IP or a HOSTNAME for open ports, services, service version, and also vulnerability assessment. Scanners are used in information on a target this provides the security personnel crucial insight into the networking side of the target.
If information is found by an attacker, it can cause serious damage as it can lead to a successful breach of the system and cause damage to data and its integrity such networking related are safely maintained by firewalls and incident response personnel and occasionally tested by white hat hackers and testers to ensure its security is intact and do possible patches to enhance the security.
Network scanners such as nmap use the TCP protocol to communicate with the ports and check whether the service is active, closed, or if not defined filtered. There are different methods and different scan types used to determine ports and which are open and which are closed but mainly the filters also work as bypass tools to escape detection. For this explanation, we will be looking into NMAP or Network Mapper one of the most widely used and accurate network scanners we will be looking into its basic working mechanism and look into how they are used by the scanner to decide its outputs.
NMAP uses the conversation and the various SYN ACK requests to determine whether the port is open, closed, or filtered this also has a few added benefits of also gaining more knowledge on the service, service version, and the software specification running behind the open port which can help in determining if the service is vulnerable or not. It also closely examines the scan fingerprints and segments over several packets to analyze the OS or the Service running as each Service or OS has its different segment values for the packet sent, we will be looking into OS and Service fingerprinting in a bit.
The above output is a simple scan on the target website. There is a detailed output on the service and if the service is open closed or filtered. By checking the packets, the service can also check for the Linux OS version and possibly the kernel version. This is a vital part of the scan outputs that can be used to further analyze the server for deciding the best exploit.
Scanners of such fashion are used in many areas other than just hacking some use them for defense and some use them to debug and test specific services. When in a network environment we will have to find many processes and services and keeping track of such information is tedious checking whether they have proper functionality also plays a vital role. Network scanners check for the connectivity and the configuration structure by performing connection requests and also by conducting basic configuration tests to make sure that the configuration is good enough for further procedures.
In a network environment where data is considered a priority maintaining security is vital that is where hackers and Pentester use scanners and other related tools to scan the network internally and externally for crucial information such as vulnerabilities loopholes information leaks miss configs etc and help in rectifying them to avoid future threats. These Scans are the bases of all the other scans in the system each scanned work mainly on the 3-Way Handshake that the Client-Server system makes to determine whether the IP is active, PORT is OPEN or to find the OS information and service information.
The TCP scan or connect() scan is a type of scan that, unlike SYN scans, will send connection requests on the port specified for example instead of checking whether the port is open via a simple hello. It checks if the port is open by trying to connect it and if there is an open port there will be an exchange of banner data signalling an open port. This scan uses a complete 3-Way Handshake unlike SYN scan or FIN scan. This scan has a high chance of getting caught but can provide accurate results when used with appropriate measures.
The SYN scan or stealth scan is a scan done where a half handshake sequence is conducted. This happens when there is a conversation where the client sends an SYN request and when the server responds with an SYN-ACK the client will end the conversation without sending the ACK request. This leads to the server resetting the conversation with an RST signal. This is most commonly used to conduct DoS attacks on services and can also mitigate detection to a certain extent.
The scan is used by security testers to check the target information without getting detected that includes sending requests and receiving data the logging system will record the incident to prevent getting logged the program will gain as much information as possible with just half a conversation and ends the conversation without sending any further requests after the timeout period the server ends the conversation with an RST signal stating the end of the conversation to prevent any DoS attacks this also stops the logging to a certain point but it is still logged as an incomplete connection for future reference.
ARP or Address Resolution Protocol is used for local device discovery over IPV4 addresses and can be used to discover a large number of devices on a given subnet this can be used to discover various other devices connected to a local network. This works by sending ARP requests over the local subnet addresses and based on how the IP addresses respond to the request whether they are active or inactive this is a versatile utility as this can be used in conjunction with other scans to resolve and scan through an extensive range of targets.
UDP just like TCP is widely used in almost all systems and they have support for every single networking device kernel, therefore, is effective for scanning as it does not need a 3-Way Handshake like the TCP scans but instead moves to the TLS connection. These scans are relatively slow compared to the 3-Way Handshake method but are also highly effective scanning methods for the newer QUIC method introduced in HTTP3 Methods which works on UDP packet transfer.
These scan outputs are simple if the probs return with data it signifies that the port is open if the probs have no returning data that signifies that the port is closed or filtered and if there is an error then it signifies the port is closed. Traceroute is a system command and is used in networking to map the data transfer from the Server to Client systems. Commonly used to diagnose the network latency and to also discover the various hops the data makes before it reaches its destination.
Traceroute is a default system command and also has a lot of features to list the intermediary devices and also to reverse engineer proxies. Fast Scan is a TCP scan that is done only for the first 400-500 ports and excludes the rest of them. This is a simple and fast method to check for fewer ports and needs. This is used when you know that there is a vulnerability in one of the 0-400/500 ports and also when you don’t have enough bandwidth to scan all 65535 ports if you have no clue how many are open and how many are closed.
Os fingerprinting works by checking each packet’s fingerprint over 5-6 packets and based on the matches in each box we can determine which Os it is as each Os has a unique sequence of matches. In nmap specifically, they use a database to verify the Os. They have a nmap-os-DB with many matches and sequences listed for a huge array of operating systems and using this the nmap code can guess what kernel is used and also narrow the search by guessing the closes Os to the sequence.
Finding out which Os is running in the backend is very vital to determine any exploits mainly kernel-based exploits. Service fingerprinting works in the same way as Os fingerprinting does by analyzing. Nmap does it like this. Service fingerprinting works by first scanning for the port each port has a dedicated service for example 22 is for SSH, 21 telnets, etc. Using this information, the services can narrow down to a few ports to be fingerprinted.
After getting to know the open ports the scanner can check the contents of the packets with the database the TCP data of the packets are analyzed over a sequence of consecutive packets and then the service is determined. Nmap is also based on the same concept and using the same technique the algorithm determines the services. Services and service versions are used to detect cve for specific services and their versions if you know the service and its respective version you can search the vulnerability and exploits over the internet in resources such as exploit-DB or any cve database.
4. Practical Deployment, Analysis & Case Studies Now let’s get to the interesting part: let’s build a Network Mapper implementation. In this example we will be using 2 python modules. One is subprocess and the second is python-nmap we will be implementing the nmap in two ways one is using the os installed nmap which is fast and reliable and the second is python nmap which is also fast but the output retravel is not that convenient.
In python-nmap, all the scan features are predetermined the most important functions we can use are: This will scan the localhost and show a CSV output from this we can understand how we can declare the nmap module. Let’s take the IP/Hostname from the user also with arguments that he wants to scan specifically and see a JSON output. Now instead of showing a console output, let’s convert JSON output into an HTML report.
This was a simple implementation via a few command-line inputs and an HTML report generation but we can use this to achieve much more for example implementing this on a flask webpage for a static web page with such a crazy implementation. Subprocess is a python module that is used to run system commands and using this we can run nmap directly on the system and redirect the CSV output into JSON format and then to an HTML format We will not implement all the things step by step but write a complete code and explain the code.
In conclusion, we can see how a network mapper works and also see various other technologies involved using a few python programs and a few lines of code we can implement a console wrapper code to run nmap and create a simple port scanner. The main source for all the data is personal experience and research documents from nmap. If you want to get in touch with me you can do that via LinkedIn using the below link.
I am a red team operator, and a security enthusiast I write blogs and articles related to cyber-sec topics. Network scanning is the starting point of nearly every penetration test, vulnerability assessment, and security audit. Before you can exploit anything, you need to understand what is running, where it is running, and how it is configured. Nmap, the Network Mapper, is the tool that makes that discovery possible with precision and depth that no other scanner matches.
This walkthrough covers Nmap from the ground up, moving through host discovery, port scanning, service enumeration, OS detection, NSE scripting, and evasion techniques. Every section includes real commands with practical flags, output interpretation, and the reasoning behind each approach. This is not a surface-level introduction. It is the kind of working knowledge that belongs in every practitioner's toolkit.
Nmap is a free, open-source network scanner originally written by Gordon Lyon (Fyodor) and first released in 1997. It has grown into one of the most comprehensive and widely used tools in the security industry, present on virtually every penetration tester's machine and referenced in countless security certifications, job descriptions, and real-world engagement reports.
What makes Nmap exceptional is its layered capability. At the most basic level, it tells you which hosts are alive and which ports are open. At a deeper level, it identifies services and their versions, detects the underlying operating system, runs scripted vulnerability checks, and can fingerprint firewall behavior. All of this is available through a single, well-documented CLI tool.
If you are beginning your penetration testing journey and want structured guidance on applying Nmap and other professional tools in real engagement scenarios, Redfox Cybersecurity Academy offers hands-on training that puts these skills in the context of full attack chains. Nmap is pre-installed on Kali Linux and most security-focused distributions. On other systems, installation is straightforward.
Building from source ensures you have the most recent NSE scripts, service fingerprints, and OS detection signatures, which matters during engagements where you are dealing with newer services or operating system versions. Choosing the right scan type is not a minor detail. Different scan types produce different results, generate different levels of noise on the network, and interact differently with firewalls and intrusion detection systems. Understanding what each scan does at the packet level is foundational knowledge for any practitioner.
The SYN scan is the default when Nmap is run with root privileges. It sends a SYN packet and waits for a response. An open port responds with SYN/ACK. A closed port responds with RST. A filtered port produces no response or an ICMP unreachable message. The SYN scan never completes the three-way handshake, which means it is faster than a full connect scan and less likely to be logged by application-layer logging on the target.
The connect scan completes the full TCP handshake. It does not require root privileges, which makes it useful when running Nmap as a standard user. It is slower and more likely to appear in application logs on the target. UDP scanning is slower and more complex than TCP scanning because UDP is connectionless. Nmap sends a UDP packet to each port. A closed port returns an ICMP port unreachable message. An open port may return a response or simply produce no reply, which Nmap marks as open/filtered.
UDP scanning matters because critical services such as DNS (53), SNMP (161), NTP (123), and TFTP (69) run over UDP. Skipping UDP means missing potentially significant attack surface. These scan types exploit a behavior defined in RFC 793: closed ports should respond to packets with unexpected flag combinations with RST, while open ports should drop them silently. This behavior does not apply to Windows systems, which makes these scans most useful against Unix and Linux targets.
These scan types can bypass certain stateless packet filters that only block SYN packets, making them useful in environments where a standard SYN scan returns filtered results. Scanning every port on a large network without first identifying live hosts is inefficient. Nmap's host discovery phase lets you quickly map which addresses are active before committing to deeper scans.
The -sn flag disables port scanning and performs host discovery only. Nmap sends ICMP echo requests, TCP SYN to port 443, TCP ACK to port 80, and ICMP timestamp requests by default when run as root. When ICMP is blocked and targets appear dead in a ping sweep, skip host discovery entirely and scan directly: The -Pn flag tells Nmap to treat all targets as online and proceed directly to port scanning. This is essential when scanning through a firewall that drops ICMP packets.
On the local subnet, ARP scanning is the most reliable host discovery method because ARP requests cannot be filtered at the IP layer: By default, Nmap scans the 1,000 most common ports. For thorough assessments, this default is often insufficient. The --min-rate flag sets a floor on packet transmission rate. A value of 5000 packets per second significantly accelerates full-port scans. Use this carefully in sensitive environments, as it generates noticeable traffic volume.
The -F flag limits scanning to the top 100 ports. The -T4 timing template increases speed while remaining stable on most networks. Knowing that port 80 is open tells you something. Knowing it is running Apache 2.4.49 tells you significantly more, including that it may be vulnerable to CVE-2021-41773, a path traversal and remote code execution vulnerability.
The -sV flag probes open ports and attempts to determine the service name, version, and in some cases the application name. Nmap uses a database of service fingerprints ( nmap-service-probes ) to match responses. Higher intensity values cause Nmap to send more probes per port, increasing the likelihood of identifying obscure or custom services at the cost of additional time and network traffic.
Operating system detection works by analyzing subtle differences in how network stacks implement the TCP/IP protocol. Nmap sends a series of crafted packets and compares the responses against a database of known OS fingerprints. For more aggressive OS detection that attempts to guess even when fingerprint confidence is low: 5. Performance Evaluation & Extended Technical Observations OS detection requires at least one open and one closed TCP port to function accurately. When both are present, Nmap typically achieves high confidence. When only open ports are visible (common behind firewalls), accuracy drops and Nmap will indicate this in its output.
Knowing the OS informs your attack path significantly. A Linux target running SSH and a web server leads you toward web exploitation and SSH key attacks. A Windows target opens paths involving SMB, WinRM, RDP, and Active Directory enumeration. The Nmap Scripting Engine is where Nmap transitions from a scanner into a lightweight vulnerability assessment and enumeration platform. NSE scripts are written in Lua and organized into categories including auth , brute , discovery , exploit , safe , vuln , and others.
The script database on Kali Linux lives at /usr/share/nmap/scripts/ . There are over 600 scripts available by default. The -sC flag runs scripts in the default category, which covers safe enumeration tasks like grabbing HTTP titles, SSH host keys, FTP banners, and SMB information. The -A flag enables OS detection, version detection, default scripts, and traceroute simultaneously: This is the most common comprehensive scan used during initial host enumeration on an authorized engagement.
The vuln category includes scripts that check for specific known vulnerabilities including EternalBlue (MS17-010), Shellshock, Heartbleed, and others. # HTTP brute force with custom credentials sudo nmap -p 80 --script http-brute \ --script-args http-brute.path=/admin,userdb=users.txt,passdb=passwords.txt \ 192.168.56.10 If you want to build genuine fluency with NSE scripting and understand how to chain Nmap output into follow-on exploitation workflows, Redfox Cybersecurity Academy covers the full reconnaissance-to-exploitation pipeline in practical, lab-based training modules.
Output management is a professional habit. On real engagements, you need to produce evidence, feed results into other tools, and refer back to earlier scans. Nmap supports multiple output formats designed for these different use cases. The -oA flag produces three files simultaneously: .nmap for human-readable output, .gnmap for grepable output, and .xml for tool ingestion.
The resulting HTML file provides a formatted, shareable report of your scan results, useful for interim deliverables during longer engagements. A scan that gets blocked, filtered, or immediately triggers an IDS alert has limited value. Nmap includes several techniques for reducing detection probability and bypassing basic packet filtering.
Splitting packets into smaller fragments can bypass some packet filters that inspect full packets but cannot reassemble fragments: Decoy scanning spoofs traffic from multiple source IPs, making it harder for a defender to identify the true origin of the scan: RND:10 generates ten random decoy addresses. The real scan traffic is mixed in with the spoofed traffic. Note that this technique is less effective against modern stateful firewalls and NDR systems, but remains relevant against simpler filtering mechanisms.
Some firewalls allow traffic from trusted source ports like 53 (DNS) or 80 (HTTP). Spoofing the source port can sometimes bypass these rules: Timing templates control how aggressively Nmap sends packets. Slower templates reduce the scan's network footprint and can evade IDS rules that trigger on high packet rates: These timing modes are impractical for large ranges but appropriate when scanning a single high-value target where stealth is the priority.
By default, Nmap scans targets in sequential order. Randomizing the scan order makes the traffic pattern less recognizable to behavioral detection systems: Professional penetration testers do not run a single Nmap command and move on. They use a phased approach that balances speed, depth, and stealth according to the engagement scope.
This phased approach is how structured reconnaissance is conducted on real engagements. Each phase informs the next, and the output files provide a documented evidence trail that feeds directly into your report. Students at Redfox Cybersecurity Academy practice this exact workflow against realistic lab environments, learning not just how to run the commands but how to interpret and act on the results.
Nmap is not a tool you learn once and set aside. It is a tool you develop a deeper relationship with over hundreds of hours of practice. The scan types, timing controls, NSE scripts, output formats, and evasion techniques covered in this walkthrough represent the practical working knowledge that separates an Nmap user from an Nmap practitioner. To summarize the core principles: start host discovery before port scanning, choose your scan type deliberately based on environment and stealth requirements, always save output in multiple formats, use NSE scripts to extract maximum intelligence from open ports, and build a phased workflow that scales from quick triage to thorough enumeration.
Every technique covered here is applicable immediately in a properly configured home lab or an authorized engagement environment. None of it requires anything beyond Nmap itself and a solid understanding of what each flag actually does at the packet level. When you are ready to apply these skills in structured, guided penetration testing scenarios with professional mentorship, Redfox Cybersecurity Academy is the next step.
Earn CJEH, CWAPT, CAIPT, CWRT, CAPT and RCPT with Redfox Cybersecurity Academy. Hands-on ethical hacking certifications with real labs and tools. Comparing OSCP certification prep with Redfox Cybersecurity Academy's career-focused training to help you choose the right penetration testing path.
Udemy vs Redfox Cybersecurity Academy: Cheap Courses or Career-Focused Cybersecurity Training? Udemy courses are affordable and convenient, but are they enough to launch a cybersecurity career? Compare Udemy with career-focused training at Redfox Cybersecurity Academy. Nmap turns tens of thousands of monthly searches into one recurring question: how do you actually use it without breaking something, scanning a network you don’t own, or drowning in flags you don’t understand. The tool itself hasn’t slowed down.
Nmap 7.991 shipped on August 6, 2026, and the project pushed a further point release, 7.992, on October 15, 2026, according to the Nmap Project — nearly three decades after Gordon Lyon (“Fyodor”) first released it in 1997, it’s still the default answer when a security team needs to know what’s actually listening on a network. This tutorial walks through installing Nmap, running your first Nmap commands safely and legally, reading the output, layering on service and OS detection, using the Nmap Scripting Engine (NSE) for vulnerability checks, and building the same kind of repeatable audit workflow that penetration testers and network admins run every week. By the end you’ll have a working project: a scheduled scan script that discovers hosts, fingerprints services, flags common misconfigurations, and writes a report you can hand to a manager or a client. Nmap is one piece of a much larger toolkit — for the wider picture of what security teams are defending against in 2026, see our full cybersecurity coverage .
Add Tech Insider once in the Google app and our stories appear in your news suggestions. Nmap (Network Mapper) is a free, open-source command-line tool for network discovery and security auditing. It sends specially crafted packets to target hosts and interprets the responses to determine which hosts are online, which ports are open, which services and versions are running behind those ports, and, in many cases, which operating system a host is running. It ships for Linux, Windows, and macOS, and its scripting engine extends it well past simple port scanning into light vulnerability detection, brute-force testing (used carefully and only with authorization), and service enumeration.
The project remains actively maintained, and the release cadence over the past year and a half shows it: 7.96 shipped in May 2025, 7.97 followed on May 12, 2025, 7.98 landed on August 21, 2025, 7.99 arrived on March 26, 2026, 7.991 became stable on August 6, 2026, and the current release, 7.992, shipped October 15, 2026, according to the official Nmap changelog. The 7.95 release in that run added 336 new OS-detection signatures (bringing the total to 6,036 fingerprints) and grew the service/version detection database by 1.4% to 12,089 signatures covering 1,246 protocols, according to the official Nmap announcement on the Nmap-announce mailing list. Recent releases have also expanded Nmap Scripting Engine coverage into industrial control system (ICS) protocols such as IEC 61850 MMS and PROFINET, and the bundled Npcap packet-capture driver for Windows has continued to receive performance upgrades release over release, most recently bumped from version 1.88 to 1.89 in the 7.992 release.
Why does a text-based scanner from the 1990s still outrank flashier commercial tools in day-to-day use? Speed of iteration, zero licensing cost, and universal support in every pentesting distribution (Kali Linux, Parrot OS) and every cloud shell. Nmap is also the reference implementation that scanner comparisons get measured against — reviews of Tenable, Qualys, and Rapid7 still cite Nmap as the open-source baseline for raw port-scanning accuracy. If you’re new to network security tooling, Nmap is also the cheapest way to learn how TCP/IP actually behaves, because you’re reading raw packet responses instead of a vendor’s abstracted dashboard.
You don’t need expensive hardware or a lab full of servers to follow this tutorial. A single laptop and a machine you’re authorized to scan (your own router, a virtual machine, or a company-sanctioned test target) is enough. Here’s the exact stack this guide assumes. You should also be comfortable with a basic terminal. Nothing here requires programming experience, though the final “complete project” section includes a short Bash script you can adapt without writing code from scratch.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Metasploit • https://en.wikipedia.org/wiki/Heartbleed • https://en.wikipedia.org/wiki/List%20of%20TCP%20and%20UDP%20port%20numbers • https://medtrigui.github.io/vulnerability-scanning/ • https://blog.cyberdesserts.com/nmap-nse-scripting-engine/ • https://hackernoon.com/network-scanner-working-and-implementation • https://www.redfoxsec.com/blog/network-scanning-with-nmap-a-complete-walkthrough • https://tech-insider.org/how-to-use-nmap-network-scanning-2026/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Network Vulnerability Scanner Using Python Nmap Module.
[*] Initializing Burp Suite Spider & Vulnerability Engine for Network Vulnerability Scanner Using Python Nmap Module... [✓] Burp Extender / Macro Automation Hook Synced ──────────────────────────────────────────────────────────────────────── [11:42:01.104] AUDIT Crawled dynamic endpoints | Injecting input vectors [11:42:01.218] FINDING Cymulate / Burp: Input sanitation check executed in parameter 'q' [11:42:01.312] VERIFY SafeBreach payload validation: Out-of-band interaction confirmed [11:42:01.405] REPORT Severity: Evaluated | Remediation: Enforce context-aware validation ──────────────────────────────────────────────────────────────────────── [✓] Burp Suite Audit Completed: Verified across OWASP Top 10 vectors
| Vulnerability Vector | Testing Tool | Injection Target | Severity | Remediation Status |
|---|---|---|---|---|
| SQL Injection (SQLi) | Burp Suite Professional | POST /api/auth/login | CRITICAL | PARAMETERIZED |
| Cross-Site Scripting (XSS) | SafeBreach / Cymulate | GET /search?q= | HIGH | CSP ENFORCED |
| Broken Object Level Access | Picus Security Audit | GET /user/account/840 | HIGH | RBAC APPLIED |
| Security Misconfiguration | AttackIQ Suite | HTTP Security Headers | MEDIUM | RESOLVED |