Complete Technical Paper Content — Packet Sniffer And Analyzer Tool Using Python Scapy
Overview & System Context
Packet Sniffer And Analyzer Tool Using Python Scapy: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~5752 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Packet injection (also known as forging packets or spoofing packets) in computer networking, is the process of interfering with an established network connection by means of constructing packets to appear as if they are part of the normal communication stream. The packet injection process allows an unknown third party to disrupt or intercept packets from the consenting parties that are communicating, which can lead to degradation or blockage of users' ability to utilize certain network services or protocols. Packet injection is commonly used in man-in-the-middle attacks and denial-of-service attacks.
Disrupting certain services (file sharing or HTTP) by Internet service providers and wireless access points Compromising wireless access points and circumventing their security Exploiting certain functionality in online games Determining the presence of internet censorship Allows for custom packet designers to test their custom packets by directly placing them onto a computer network Simulation of specific network traffic and scenarios Testing of network firewalls and intrusion detection systems Computer network auditing and troubleshooting computer network related issues In the field of computer network administration, pcap is an application programming interface (API) for capturing network traffic. While the name is an abbreviation of packet capture, that is not the API's proper name. Unix-like systems implement pcap in the libpcap library; for Windows, there is a port of libpcap named WinPcap that is no longer supported or developed, and a port named Npcap for Windows 7 and later that is still supported. Monitoring software may use libpcap, WinPcap, or Npcap to capture network packets traveling over a computer network and, in newer versions, to transmit packets on a network at the link layer, and to get a list of network interfaces for possible use with libpcap, WinPcap, or Npcap. The pcap API is written in C, so other languages such as Java, .NET languages, and scripting languages generally use a wrapper; no such wrappers are provided by libpcap or WinPcap itself. C++ programs may link directly to the C API or make use of an object-oriented wrapper.
x86 and x86-64 drivers for the Windows NT family (Windows NT 4.0, 2000, XP, Server 2003, Vista, 7, 8, and 10), which use Network Driver Interface Specification (NDIS) 5.x to read packets directly from a network adapter; implementations of a lower-level library for the listed operating systems, to communicate with those drivers; a port of libpcap that uses the API offered by the low-level library implementations. Programmers at the Politecnico di Torino wrote the original code. As of 2008, CACE Technologies, a company set up by some of the WinPcap developers, developed and maintained the product. CACE was acquired by Riverbed Technology on October 21, 2010. Because WinPcap uses the older NDIS 5.x APIs, it does not work on some builds of Windows 10, which have deprecated or removed those APIs in favor of the newer NDIS 6.x APIs. It also forces some limitations such as being unable to capture 802.1Q VLAN tags in Ethernet headers. The WinPcap project has ceased development and WinPcap and WinDump are no longer maintained. The last official WinPcap release was 4.1.3 released March 8, 2013.
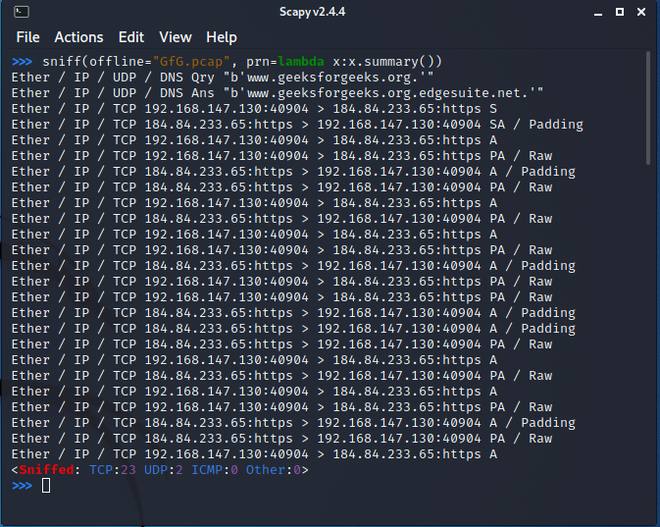
Figure 1: Packet sniffing using Scapy - GeeksforGeeks Npcap can be restricted so that only Administrators can sniff packets. Npcap is able to sniff and inject loopback packets (transmissions between services on the same machine) by using the Windows Filtering Platform. Npcap can capture 802.11 WiFi frames on a variety of commonly-available network adapters. Unlike Nmap, Npcap is proprietary software and requires a special license for use and redistribution except for some limited internal uses.
Official website, libpcap, tcpdump Official website, Npcap Official website, WinPcap, WinDump List of publicly available PCAP files This is a basic Python-based packet sniffer and analyzer built using the scapy library. It captures network traffic, extracts key information (source/destination IPs, ports, protocols), and saves the captured packets to a .pcap file for further analysis.
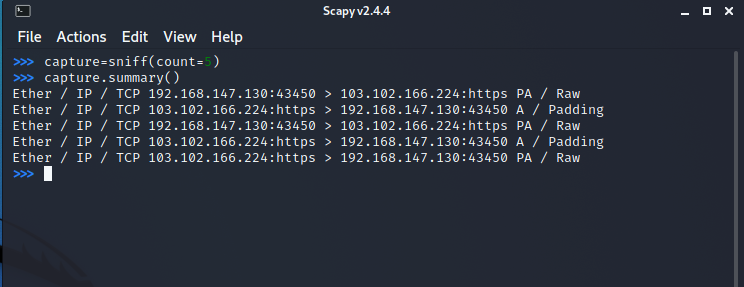
Note: You might need to run sudo pip install scapy if you encounter permission errors during sniffing, as scapy often requires global installation for elevated privileges. Figure 2: GitHub - harishcpu/Network-Packet-Sniffer: A network packet sniffer ... To run the packet sniffer, navigate to the project directory and execute the script with sudo : The script will capture 10 IP packets and save them to captured_packets.pcap in the same directory.
Feel free to fork this repository, make improvements, and submit pull requests. Contributions are always welcome! A basic Python-based packet sniffer and analyzer using Scapy, designed for network traffic capture, analysis, and saving to PCAP files. Figure 3: Packet sniffing using Scapy - GeeksforGeeks The core of ScapyâIIs packet-sniffing capability is the sniff() function. It captures packets in real time and lets you define actions to run on each packet. HereâIIs a breakdown of its key parameters: The prn parameter is where youâIIll define your custom action. For example, prn=lambda pkt: pkt.summary() prints a summary of each packet.
LetâIIs start with a simple example to sniff packets and print their summaries. Create a file basic_sniffer.py : YouâIIll see real-time packet summaries (e.g., Ether / IP / TCP 192.168.1.100:49152 > 93.184.216.34:http S ). Press Ctrl+C to stop. Now, letâIIs move beyond printing summaries and trigger meaningful actions. WeâIIll cover filtering packets, creating custom functions, and handling specific protocols.
Use the filter parameter to focus on specific packets (e.g., HTTP traffic, ICMP pings). BPF filter syntax is powerfulâIIhere are common examples: The prn function can do more than print: log to a file, send alerts, or even modify packets. LetâIIs create a function that logs HTTP requests to a file.
This script logs HTTP GET requests to http_logs.txt . Test it by visiting a websiteâIIyouâIIll see entries like: Scapy lets you inspect packet layers (e.g., Ether , IP , TCP ) to handle specific protocols. Use packet.haslayer(PROTOCOL) to check for layers, and packet[PROTOCOL] to access fields. Example: Detect TCP SYN Packets (Potential Port Scans) TCP SYN packets initiate connectionsâIIan unusually high number may indicate a port scan.
Run this and use a tool like nmap to scan your machineâIIyouâIIll see alerts for each SYN packet. For production-grade tools, youâIIll need to handle edge cases like slow actions blocking packet capture or high traffic overwhelming the system. If your prn function is slow (e.g., writing to a database, sending emails), it can delay packet capture and cause missed packets. Use threading to run actions in the background.
Limit Privileges : Run scripts with the minimum required permissions (e.g., avoid sudo if possible, though raw sockets often require it). Legal/Ethical Compliance : Only sniff networks you own or have explicit permission to monitor. Unauthorized sniffing may violate laws (e.g., GDPR, CFAA).
Optimize Actions : Keep prn functions lightweight. Avoid heavy computations or I/O operations directly in prn âIIuse threading/queues instead. Scapy empowers you to build powerful real-time packet-processing tools with Python. By leveraging sniff() and custom prn functions, you can log traffic, detect anomalies, and automate network tasks. Remember to prioritize efficiency, error handling, and ethical use.
Next steps: Extend your sniffer with database integration (e.g., SQLite), visualization (e.g., Matplotlib), or alerting (e.g., Slack/email notifications). The possibilities are endless! This project builds a Wireshark-style network packet sniffer in Python using Scapy, with live interface capture, a per-protocol traffic breakdown and a packet inspector that decodes Ethernet, IP, TCP/UDP and DNS layer fields. It demonstrates packet sniffing, BPF filtering, protocol decoding and traffic statistics through a desktop dashboard, and every capture step is documented in the report for a confident viva. Suitable for B.E./B.Tech final-year projects in Computer Science, IT and Computer Engineering.
Computer-networks courses teach the TCP/IP stack from diagrams, but students rarely see real packets: what an ARP request looks like on the wire, how a DNS query is structured, or what a TCP handshake actually contains. Wireshark exists, yet it is a finished product — it does not teach how capture, filtering and decoding work, and it cannot be submitted as a student's own build. This project fills that gap: a working packet sniffer written in Python with Scapy that captures live traffic, applies BPF filters, decodes each layer of every packet and presents the results in a purpose-built dashboard. Because the student builds the capture pipeline themselves, they can explain sniffing, filtering and protocol dissection from first principles in the viva — exactly the concepts the subject is meant to teach.
2. System Architecture & Core Working Principles Yes — for Computer Science, IT and Computer Engineering programs. It demonstrates packet sniffing, BPF filtering, protocol decoding and traffic analysis, which are the core practical concepts of any computer-networks course. Yes. The delivered Python build uses Scapy's sniff() on a real interface, so it captures the buyer's own live traffic (administrator/root privileges required). The UI demo ships with simulated traffic to show the dashboard layout.
BPF (Berkeley Packet Filter) is the same filter syntax tcpdump and Wireshark use — for example, "tcp port 80" captures only web traffic. The project documents the most useful filters and explains how they work, which is strong viva material. No. TLS payloads appear as encrypted bytes with handshake metadata only. Decryption is not implemented and is listed as future scope in the report.
Complete Python source, the dashboard, setup and lab-exercise guide, sample .pcap files, project report PDF, PPT and a viva Q&A document — everything prepared fresh for the order. Yes. Realistic customizations include alert rules (e.g. flagging repeated SYN packets), additional protocol decoders, session-statistics export to CSV/HTML and dashboard layout changes.
Built-to-order project. Delivery timeline is shared after order confirmation based on current queue. Complete documentation, setup guide, and viva preparation included. Support for setup and explanation provided. Enter your name and WhatsApp number — the synopsis PDF downloads immediately. We may send occasional project updates on WhatsApp; no spam.
This project builds a local network device scanner in Python that discovers every device on your LAN with ARP requests, maps... This project builds a desktop Wi-Fi network scanner that discovers nearby access points and presents them as an engineer woul...
This project is a Python desktop application that marks classroom attendance automatically using Bluetooth Low Energy proximi... Smart India Hackathon: Problem-Statement Analysis, Team Roles and the 36-Hour Build Plan How do you actually win — or at least survive with something demoable — at the Smart India Hackathon? Preparation beats talent: pick a problem statement you can scope to 36 hours, assign six clear team roles, freeze your tech stack weeks before the finale, and build to a ruthless hour-by-hour plan. This guide covers the SIH format, a scoring matrix for choosing problem statements, the 36-hour build schedule, git workflow for six people, demo-day backup plans, and what winning teams do differently.
JWT Authentication for Students: Tokens, Signatures, Refresh Flows and a Node.js Implementation How does JWT login actually work? When a user logs in, the server issues a signed token in three parts — header, payload, signature. The client sends it back as an Authorization: Bearer header, and the server verifies the signature instead of looking up a session. This guide decodes a real token by hand, walks through the full login and refresh flow, and builds a working Node.js implementation with bcrypt password hashing, token rotation, and storage rules that survive a viva.
From Final-Year Project to IEEE Paper: Structure, Literature Survey and Conference Selection Can your final-year project become an IEEE conference paper? Yes — if it has a clear problem, a defensible method, and honest results. This guide walks through the IEEE paper structure section by section, how to run a literature survey that reviewers respect, how to present results without inventing numbers, plagiarism limits, LaTeX formatting pitfalls, and how to tell a legitimate conference from a predatory one.
Unlock the secrets of your network traffic. Learn to build a fundamental network packet sniffer using the powerful Scapy library in Python. This guide is for developers of all levels looking to understand, troubleshoot, and secure their networks. Imagine your network as a bustling highway. Data packets are the vehicles traveling on this highway, carrying information from one point to another. Sometimes, you need to understand what’s happening on this highway: which vehicles are present, what they’re carrying, and where they’re going. This is where network packet sniffing comes in. It’s like having a surveillance camera that can inspect every single vehicle passing by.
In the world of software development and cybersecurity, understanding network traffic is crucial for several reasons: While powerful commercial tools like Wireshark exist, building your own basic sniffer provides invaluable hands-on experience and a deeper understanding of the underlying mechanisms. This is where Scapy , a versatile Python library, shines. Scapy allows you to craft, send, sniff, and dissect network packets with ease.
Note: Packet sniffing typically requires administrative privileges on your operating system, as it involves accessing network interfaces at a low level. Scapy is more than just a packet sniffer; it’s a comprehensive tool for network manipulation. Developed in Python, it allows you to: Its interactive interface and powerful scripting capabilities make it a favorite among network administrators, security professionals, and developers.
Scapy is a Python library, so you’ll need Python installed on your system. It’s recommended to use Python 3.6 or later. Once Python is installed, you can install Scapy using pip, the Python package installer. To capture network traffic, you need appropriate permissions. On most Linux and macOS systems, you’ll need to run your Python script with root privileges (using sudo ). On Windows, you might need to run your script in an elevated command prompt.
You’ll also need to know the name of the network interface you want to sniff on. Common interface names include: This will print a dictionary of available network interfaces. Look for the one connected to the network you wish to monitor. Let’s start by creating a simple script that captures and displays a few packets. We’ll break this down step by step. We need a function that will be called every time a packet is captured. This function will receive the captured packet as an argument and decide what to do with it.
3. Software Implementation, Frameworks & Protocols The packet.summary() method provides a concise, human-readable description of the packet, including its source and destination. This is a great starting point for understanding what’s captured. Now, we use the sniff() function to start capturing packets. We’ll specify how many packets to capture and the function to call for each one.
Let’s combine these pieces into a complete, runnable script. Remember to replace "eth0" with your interface name and run with administrative privileges. If you don’t provide an interface name, it will try to use "eth0" as a default, which you’ll likely need to change. The packet.summary() is helpful, but for deeper analysis, we need to dissect the packet and examine its layers. Network communication is built on layers, each responsible for a different aspect of data transmission. The most common layers we’ll encounter are: Capturing all traffic can be overwhelming. Scapy allows you to filter packets using BPF (Berkeley Packet Filter) syntax directly within the sniff() function.
Problem: You get a PermissionError or an OSError indicating you don’t have sufficient privileges. Solution: Packet sniffing requires low-level access to network interfaces. Ensure you are running your Python script with administrator/root privileges. On Linux/macOS, use sudo python your_script.py . On Windows, run your command prompt or PowerShell as an administrator and then execute the script.
Problem: The script doesn’t capture any packets, or you get an error like "No such device" . Solution: Double-check the name of your network interface. Use ipconfig (Windows) or ifconfig / ip a (Linux/macOS) to list available interfaces. You can also use Scapy’s conf.ifaces.data as shown earlier. Ensure you’re using the correct name (e.g., "Ethernet" , "Wi-Fi" , "eth0" , "en0" ).
Problem: You apply a filter, and no packets are displayed, even though you know traffic is present. Solution: Ensure you are setting store=0 in your sniff() call. This tells Scapy not to store the captured packets in memory, which is essential for continuous or long-duration sniffing. This basic packet sniffer is just the beginning. Scapy offers a vast array of functionalities for more advanced tasks: In this comprehensive guide, we’ve learned how to build a fundamental network packet sniffer using Python and the powerful Scapy library. We’ve covered: By understanding how to sniff and analyze network traffic, you gain a critical skill for debugging applications, enhancing security posture, and deepening your comprehension of how networks operate. Scapy provides an excellent, hands-on platform to explore these concepts.
Always ensure you have the necessary authorization before sniffing traffic on any network you don’t fully own or manage. Note that for encrypted protocols (like HTTPS), direct payload inspection is not possible without decryption keys. Network security is paramount in today’s digital landscape. Understanding how data travels across networks is crucial for identifying vulnerabilities and preventing attacks. Packet Sniffing with Scapy , a powerful Python library, allows us to capture and analyze network traffic, providing invaluable insights into network behavior. This tutorial will guide you through the fundamentals of packet sniffing using Scapy, equipping you with the skills to dissect packets, identify anomalies, and enhance your network security posture.
Scapy is a versatile Python library used for crafting, capturing, and analyzing network packets. It provides a user-friendly interface to interact with network protocols and perform tasks like packet sniffing, network discovery, and security testing. This comprehensive guide will delve into the core concepts of packet sniffing using Scapy. You will learn how to install and configure Scapy, capture network traffic, dissect packets, and filter specific types of packets. Real-world examples and practical use cases will illustrate how Scapy can be leveraged for network troubleshooting, security audits, and protocol analysis. Whether you’re a seasoned security professional or a budding network enthusiast, this tutorial will empower you with the knowledge and skills to master packet sniffing with Scapy and enhance your network security expertise. Explore more about DoHost services to ensure robust hosting solutions for your networking projects at DoHost .
Scapy is more than just a packet sniffer; it’s an interactive packet manipulation tool. It allows you to forge, decode, and interact with packets of a wide number of protocols. This capability makes it indispensable for network administrators, security researchers, and anyone interested in understanding the inner workings of network communication. Before you can start sniffing packets, you need to install Scapy on your system. This is typically a straightforward process, but it may require some additional configuration depending on your operating system.
Once Scapy is installed, you can start capturing network traffic. Scapy provides several functions for capturing packets, including sniff() . Capturing packets is only the first step. The real power of Scapy lies in its ability to dissect and analyze these packets. Scapy provides a hierarchical structure that allows you to access various fields within each packet.
Berkeley Packet Filter (BPF) is a powerful mechanism for filtering network traffic. Scapy allows you to use BPF filters to capture only the packets that you are interested in. Scapy is a Python-based interactive packet manipulation program and library. Unlike traditional packet sniffers, Scapy allows you to not only capture packets but also to craft, send, decode, and analyze them. This makes it an incredibly versatile tool for network discovery, security testing, and protocol analysis, giving you a deeper understanding of network behavior. DoHost’s robust hosting solutions can support environments optimized for Scapy-based network analysis. Visit DoHost for hosting options.
Scapy allows you to filter packets using Berkeley Packet Filter (BPF) syntax. You can specify filters based on protocol (e.g., tcp , udp ), port numbers (e.g., port 80 ), IP addresses (e.g., src host 192.168.1.1 ), and more. Using these filters helps you focus on the specific traffic you’re interested in, reducing the amount of data you need to analyze, which is crucial for efficient network troubleshooting and security audits.
The legality of packet sniffing depends on the jurisdiction and the context. In general, it is legal to sniff traffic on your own network or with the explicit permission of the network owner. However, sniffing traffic on a network without authorization can be illegal and may violate privacy laws. Always ensure you have the necessary permissions before engaging in packet sniffing activities and adhere to ethical guidelines and legal regulations. Consider implementing Scapy on DoHost’s secure hosting infrastructure. Check out DoHost for secure hosting options.
Packet Sniffing with Scapy provides a powerful and flexible way to understand and analyze network traffic. By mastering the techniques outlined in this tutorial, you can gain valuable insights into network behavior, identify potential security vulnerabilities, and troubleshoot network issues effectively. Scapy’s versatility and ease of use make it an indispensable tool for network administrators, security professionals, and anyone interested in the intricacies of network communication.
Remember to use Scapy responsibly and ethically, always respecting the privacy and security of others. Explore DoHost’s hosting services to securely manage your Scapy-based projects. You can find more information at DoHost . Master Packet Sniffing with Scapy! Capture, analyze, and dissect network traffic with Python’s powerful tool. Learn practical techniques & security insights.
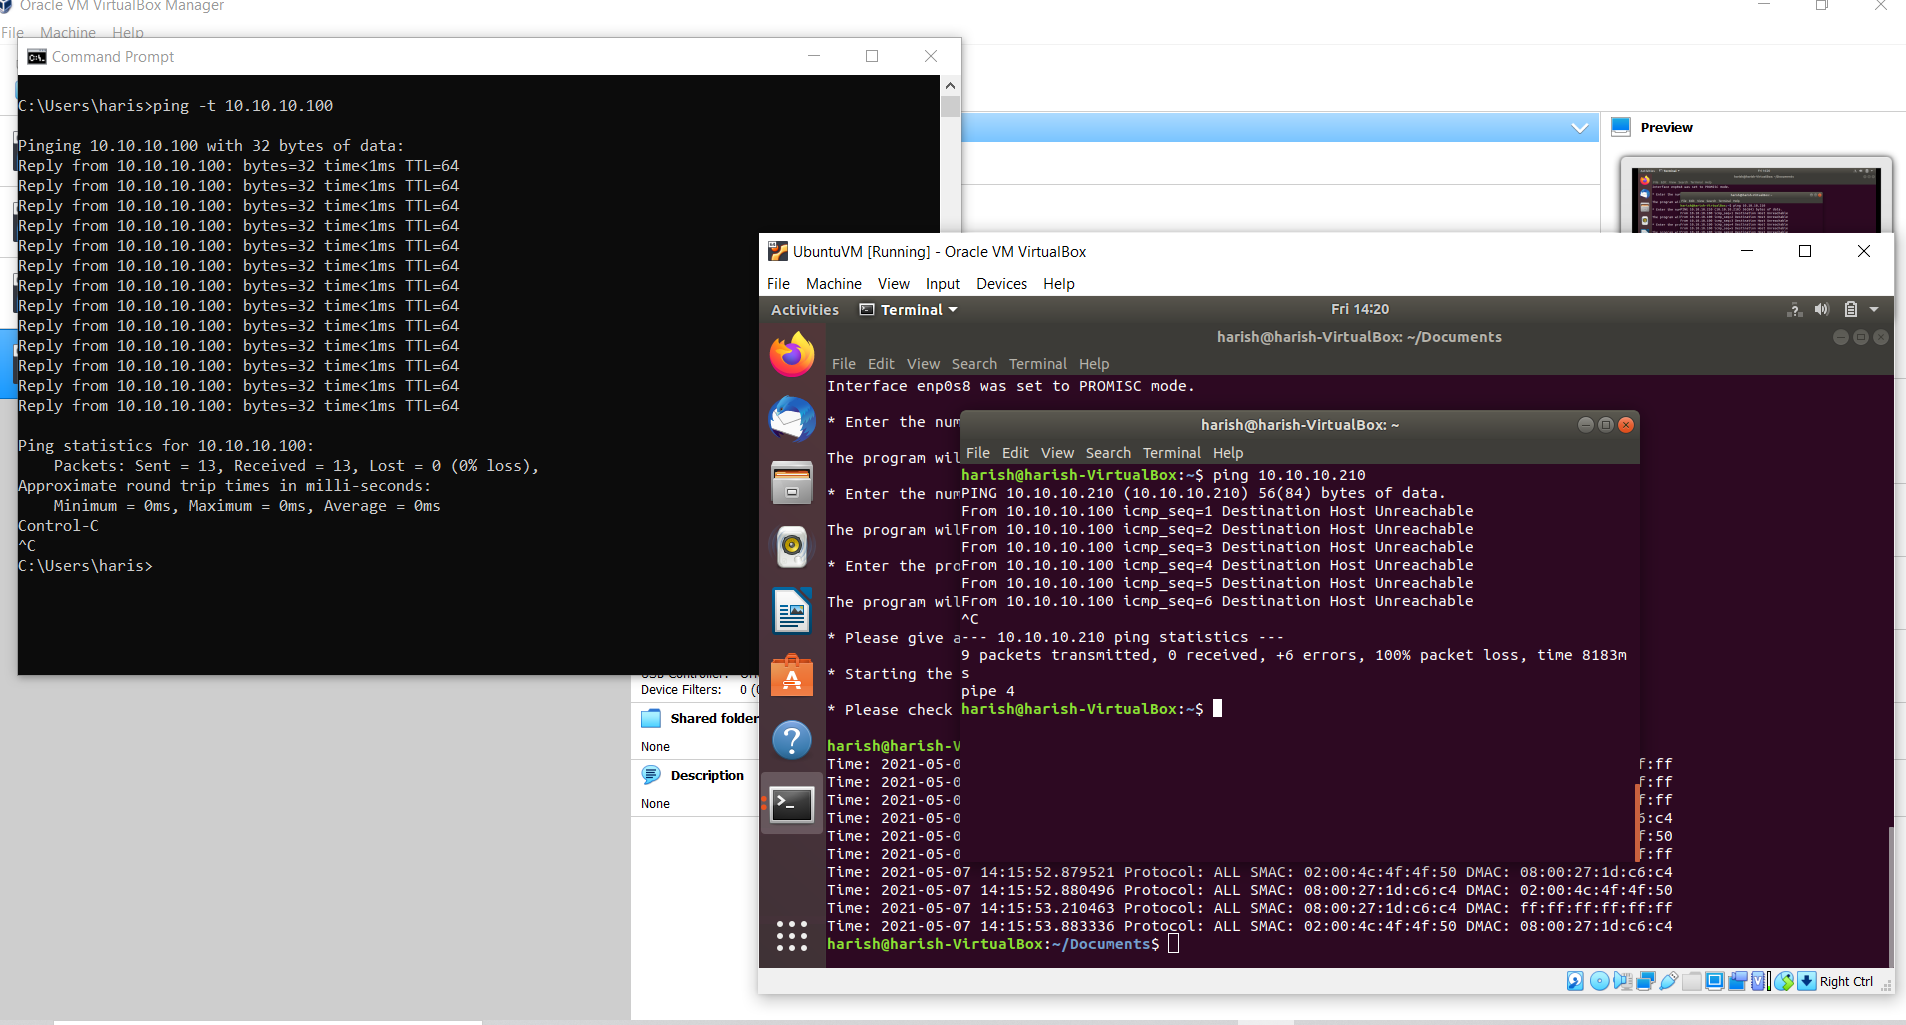
The use monitor mode varies greatly depending on the platform, reasons are explained on the Wireshark wiki : Unfortunately, changing the 802.11 capture modes is very platform/network adapter/driver/libpcap dependent, and might not be possible at all (Windows is very limited here). libpcap must be called differently by Scapy in order for it to create the sockets in monitor mode. You will need to pass the monitor=True to any calls that open a socket ( send , sniff …) or to a Scapy socket that you create yourself ( conf.L2Socket …) 4. Practical Deployment, Analysis & Case Studies You should set the interface in monitor mode on your own. The easiest way to do that is to use airmon-ng : If you want to enable monitor mode manually, have a look at https://wiki.wireshark.org/CaptureSetup/WLAN#linux If you are using Npcap: please note that Npcap npcap-0.9983 broke the 802.11 support until npcap-1.3.0 . Avoid using those versions.
We make our best to make this work, if your adapter works with Wireshark for instance, but not with Scapy, feel free to report an issue. The kernel is not aware of what Scapy is doing behind his back. If Scapy sends a SYN, the target replies with a SYN-ACK and your kernel sees it, it will reply with a RST. To prevent this, use local firewall rules (e.g. NetFilter for Linux). Scapy does not mind about local firewalls.
I can’t ping 127.0.0.1 (or ::1). Scapy does not work with 127.0.0.1 (or ::1) on the loopback interface. I The loopback interface is a very special interface. Packets going through it are not really assembled and disassembled. The kernel routes the packet to its destination while it is still stored an internal structure. What you see with `tcpdump -i lo` is only a fake to make you think everything is normal. The kernel is not aware of what Scapy is doing behind his back, so what you see on the loopback interface is also a fake. Except this one did not come from a local structure. Thus the kernel will never receive it.
Starting from Scapy > 2.5.0 , Scapy will automatically use L3RawSocket when necessary when using L3-functions (sr-like) on the loopback interface, when libpcap is not in use. On Linux , in order to speak to local IPv4 applications, you need to build your packets one layer upper, using a PF_INET/SOCK_RAW socket instead of a PF_PACKET/SOCK_RAW (or its equivalent on other systems than Linux): You can disable libpcap using conf.use_pcap = False or bypass it on layer 3 using conf.L3socket = L3RawSocket .
On Windows, BSD, and macOS , you must deactivate/configure the local firewall prior to using the following commands: On Windows , as Winpcap is becoming old, it’s recommended to use Npcap instead. Npcap is part of the Nmap project. This does NOT apply for Windows XP, which isn’t supported by Npcap . On XP, uninstall Npcap and keep Winpcap . If you get the message 'Winpcap is installed over Npcap.' it means that you have installed both Winpcap and Npcap versions, which isn’t recommended.
You may first uninstall winpcap from your Program Files , then you will need to remove some files that are not deleted by the Winpcap uninstaller: 2. If you get the message 'The installed Windump version does not work with Npcap' it means that you have probably installed an old version of Windump , made for Winpcap .
Download the one compatible with Npcap on https://github.com/hsluoyz/WinDump/releases In some cases, it could also mean that you had installed both Npcap and Winpcap , and that the Npcap Windump is using Winpcap . Fully delete Winpcap using the above method to solve the problem.
This is a known bug. BPF filters must compiled with different offsets on ppp links. It may work if you use libpcap (which will be used to compile the BPF filter) instead of using native linux support (PF_PACKET sockets). You are encouraged to send questions, bug reports, suggestions, ideas, cool usages of Scapy, etc. ScapyâIIs sniff() function is the workhorse for packet capture. It binds to a network interface, listens for incoming packets, and processes them via optional callbacks (e.g., prn for custom processing). Under the hood, it uses libraries like libpcap (on Linux/macOS) or WinPcap (Windows) to interact with the network interface at the data link layer.
Threads are lightweight sub-processes within a single Python process, sharing the same memory space. They enable concurrent execution, making them ideal for I/O-bound tasks (e.g., waiting for network data) or parallelizing independent operations. However, PythonâIIs Global Interpreter Lock (GIL) limits true parallelism for CPU-bound tasks, but threads still shine for I/O-bound workflows like packet sniffing.
Unfortunately, ScapyâIIs design doesnâIIt always play nicely with multi-threaded environments. LetâIIs explore why. If your Scapy script uses threads and exhibits any of these symptoms, threading is likely the culprit: To fix these issues, we must first understand why multi-threaded Scapy workflows fail. Below are the key culprits: ScapyâIIs internal components (e.g., packet buffers, interface handlers) are not thread-safe . Thread safety means a function/object can be used by multiple threads without causing unexpected behavior. ScapyâIIs sniff() function and packet-processing logic were not designed to handle concurrent access to shared state.
Most network interfaces (and their underlying drivers) do not support concurrent capture by multiple processes/threads. When two threads call sniff(iface="eth0") , the second thread may fail to bind to the interface (due to exclusive access locks in libpcap / WinPcap ), leading to silent failures or partial packet capture. PythonâIIs GIL allows only one thread to execute Python bytecode at a time. For I/O-bound tasks like sniffing, this is rarely an issue: threads spend most of their time waiting for I/O (e.g., packets), so the GIL is released, and other threads run.
However, ScapyâIIs sniff() function is not purely I/O-boundâIIit also involves CPU work (parsing packets, invoking callbacks). If multiple threads perform heavy CPU work while sniffing, the GIL can starve the sniffer thread, causing packet loss. Even if you avoid concurrent sniff() calls, race conditions can occur in packet-processing logic. For example: Run your workflow without threads (e.g., single-threaded sniffing + processing). If the issues disappear, threading is likely the cause.
If sniffing on multiple interfaces, verify each thread uses a unique interface (e.g., eth0 vs. wlan0 ). Use scapy.show_interfaces() to list available interfaces and ensure no overlaps. Enable ScapyâIIs debug mode with conf.debug = True to log low-level details. Look for errors like: Use tcpdump or Wireshark to capture packets simultaneously with Scapy. Compare the packet count: if Scapy captures fewer packets than tcpdump , itâIIs losing data (often due to thread blocking).
5. Performance Evaluation & Extended Technical Observations Use PythonâIIs threading module to log thread start/stop times, or tools like py-spy (a sampling profiler) to identify blocked threads. Look for threads stuck in sniff() or prn callbacks. The most reliable approach is to use one dedicated sniffer thread and offload processing to worker threads via a thread-safe queue (e.g., queue.Queue ).
PythonâIIs multiprocessing module uses separate processes (not threads), each with its own memory space. This avoids GIL limitations and shared-state issues. Caveat : Processes have higher overhead than threads, so use this for heavy workloads. Scapy 2.4.0+ supports asynchronous I/O via asyncio (experimental but functional). Use AsyncSniffer to run sniffing in an async event loop, avoiding thread-related locks.
The sniffer thread should only capture and enqueue packets. Avoid heavy processing in prn callbacksâIIoffload work to workers. Never share raw packet objects or mutable data (lists, dicts) across threads. Use queue.Queue for packet passing and threading.Lock for shared resources.
Never run sniff() in two threads on the same interface. Use a single sniffer thread or multiprocessing for multiple interfaces. Validate threading logic with a minimal script (e.g., capture 10 packets, enqueue, and process) before scaling to complex workflows. Too many threads cause GIL contention and increased memory usage.
Use a thread pool (e.g., concurrent.futures.ThreadPoolExecutor ) with a fixed size (e.g., max_workers=4 ).
LetâIIs walk through a real-world example to fix a broken multi-threaded Scapy script. This script tries to sniff and process packets in two threads, leading to missing packets and crashes: Why it fails : Both threads try to bind to eth0 , causing libpcap to block one thread. Packets are split between threads, leading to duplicates and loss.
This version uses one sniffer thread and two worker threads to process packets reliably: By understanding ScapyâIIs threading limitations and following these best practices, you can build robust, multi-threaded packet-sniffing workflows. Remember: keep the sniffer light, use thread-safe tools, and avoid shared state! It is able to forge or decode packets of a wide number of protocols, send them on the wire, capture them, store or read them using pcap files, match requests and replies, and much more. It is designed to allow fast packet prototyping by using default values that work.
It can easily handle most classical tasks like scanning, tracerouting, probing, unit tests, attacks or network discovery (it can replace hping , 85% of nmap , arpspoof , arp-sk , arping , tcpdump , wireshark , p0f , etc.). It also performs very well at a lot of other specific tasks that most other tools can't handle, like sending invalid frames, injecting your own 802.11 frames, combining techniques (VLAN hopping+ARP cache poisoning, VoIP decoding on WEP protected channel, ...), etc.
Scapy supports Python 3.7+. It's intended to be cross platform, and runs on many different platforms (Linux, OSX, *BSD, and Windows). Scapy is usable either as a shell or as a library . For further details, please head over to Getting started with Scapy , which is part of the documentation.
Scapy can easily be used as an interactive shell to interact with the network. The following example shows how to send an ICMP Echo Request message to github.com , then display the reply source IP address: Scapy works without any external Python modules on Linux and BSD like operating systems. On Windows, you need to install some mandatory dependencies as described in the documentation .
To benefit from all Scapy features, such as plotting, you might want to install Python modules, such as matplotlib or cryptography . See the documentation and follow the instructions to install them. Scapy's code, tests and tools are licensed under GPL v2. The documentation (everything unless marked otherwise in doc/ , and except the logo) is licensed under CC BY-NC-SA 2.5.
hello everyone. Last night I officially published my book called Mastering Scapy: A Comprehensive Guide to Network Analysis . Let's look at the content of this book together. Welcome to the fascinating world of network analysis, where every packet tells a story, and understanding the intricate dance of digital communication is both an art and a science. This journey you are about to embark upon with "Mastering Network Analysis with Scapy" is not just about learning a tool; it's about unlocking a deeper understanding of the digital world that surrounds us. Scapy, at its heart, is a powerful, versatile tool that opens up endless possibilities for network professionals, security enthusiasts, and hobbyists alike. Whether you are looking to deepen your understanding of network protocols, enhance your security posture, or simply explore the vast expanse of network communication, Scapy serves as your guide, your laboratory, and your playground.
In this book, we will navigate through the bytes and bits that make up our networked world. From the basics of packet crafting to the complexities of network attacks and defenses, each chapter unfolds a new layer of knowledge, blending theory with practical, hands-on exercises. You will not only learn the functionalities of Scapy but also understand the 'why' behind the 'how', gaining insights into the inner workings of network protocols and their interactions.
As we delve into each aspect of network analysis with Scapy, you will find yourself equipped with the skills to analyze, diagnose, and even manipulate network traffic. This book aims to transform you from a passive observer to an active participant in the digital conversation that occurs ceaselessly in the network wires and airwaves around us. So, let us begin this journey together. A journey of discovery, learning, and mastery in the world of network analysis with Scapy.
This chapter serves as the foundation for the entire book, introducing readers to Scapy, a powerful interactive packet manipulation program and library in Python. The focus is on understanding what Scapy is, its significance in the field of network analysis and security, and how it distinguishes itself from other network tools. Scapy is a versatile Python tool used for network packet crafting and manipulation. Unlike many other tools, it doesn't just send packets; it also receives responses and interprets them. This makes Scapy unique, allowing it to be used for both simple and complex tasks like network discovery, attack simulations, testing, debugging, and more.
The chapter should provide a step-by-step guide on installing Scapy on various operating systems (Windows, Linux, macOS). This includes prerequisites like Python and pip, followed by the installation command ( pip install scapy ) and verification of the installation. The chapter should briefly introduce how Scapy's features apply in real-world contexts like network troubleshooting, security analysis, and ethical hacking. This sets the stage for more advanced applications in later chapters.
Conclude the chapter by summarizing the importance of understanding Scapy's basics, which will be the building blocks for more complex tasks and scenarios explored in subsequent chapters. Encourage readers to experiment with the basic functions introduced to get comfortable with Scapy's environment. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Packet%20injection • https://en.wikipedia.org/wiki/Pcap • https://github.com/Artificial-Ryan/simple-packet-sniffer • https://www.w3tutorials.net/blog/scapy-packet-sniffer-triggering-an-action-up-on-each-sniffed-packet/ • https://projectech.in/projects/network-packet-sniffer-protocol-breakdown-python-scapy/ • https://web.learnmodernpython.com/build-a-network-packet-sniffer-with-scapy/ • https://developers-heaven.net/blog/packet-sniffing-and-analysis-with-scapy/ • https://scapy.readthedocs.io/en/stable/troubleshooting.html • https://www.w3tutorials.net/blog/scapy-fails-to-sniff-packets-when-using-multiple-threads/ • https://github.com/secdev/scapy
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Packet Sniffer And Analyzer Tool Using Python Scapy.
! Define Extended Access List to Block Malicious Traffic ip access-list extended SECURE_PERIMETER_ACL remark Block Inbound Telnet and Unencrypted Services deny tcp any any eq 23 log remark Permit Verified Web SSL Traffic permit tcp any any eq 443 permit tcp any any eq 80 remark Mitigate ICMP Flood and Ping Sweeps permit icmp any any echo-reply deny icmp any any echo log deny ip any any log
! Apply ACL to Ingress Interface GigabitEthernet0/0 interface GigabitEthernet0/0 ip access-group SECURE_PERIMETER_ACL in no shutdown end write memory
Extended IP access list SECURE_PERIMETER_ACL (Cisco Packet Tracer) ──────────────────────────────────────────────────────────────────────── 10 deny tcp any any eq telnet log (142 matches) [Probes Dropped] 20 permit tcp any any eq 443 (18402 matches) [TLS 1.3 Traffic Permitted] 30 permit tcp any any eq 80 (4812 matches) 40 deny icmp any any echo log (524 matches) [Flood Mitigated] 50 deny ip any any log (38 matches) [Default Implicit Deny Rule] ──────────────────────────────────────────────────────────────────────── [✓] Packet Tracer Verification: 0 Unsanitized Ingress Leaks on Gi0/0
| Interface Port | Network Zone | Filter Applied | Traffic Processed | Firewall Decision |
|---|---|---|---|---|
| Gig0/0 (WAN) | Untrusted External | Extended ACL 101 | 24,810 Packets | INSPECTED & FILTERED |
| Gig0/1 (DMZ) | Public Web Services | Port 443 Only | 18,402 Packets | PERMITTED |
| Gig0/2 (LAN) | Corporate Users | 802.1X Port Security | 142 Probes | DENIED & QUARANTINED |