Complete Technical Paper Content — Password Spray Attack Detection In Active Directory
Overview & System Context
Password Spray Attack Detection In Active Directory: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~7577 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Cozy Bear, also known as APT29, is a Russian advanced persistent threat hacker group believed to be associated with Russian foreign intelligence by United States intelligence agencies and those of allied countries. Dutch signals intelligence (AIVD) and American intelligence had been monitoring the group since 2014 and were able to link the hacker group to the Russian foreign intelligence agency (SVR) after compromising security cameras in their office. CrowdStrike and Estonian intelligence reported a tentative link to the Russian domestic/foreign intelligence agency (FSB). Various groups designate it CozyCar, CozyDuke, Dark Halo, The Dukes, Midnight Blizzard, NOBELIUM, Office Monkeys, StellarParticle, UNC2452 with a tentative connection to Russian hacker group YTTRIUM. Symantec reported that Cozy Bear had been compromising diplomatic organizations and national governments since at least 2010. Der Spiegel published documents in 2023 purporting to link Russian IT firm NTC Vulkan to Cozy Bear operations.
APT29 has been observed to utilize a malware platform dubbed "Duke" which Kaspersky Lab reported in 2013 as "MiniDuke", observed in 2008 against United States and Western European targets. Its initial development was reportedly in assembly language. After Kaspersky's public reporting, later versions added C/C++ components and additional anti-analysis features which were dubbed "Cozyduke", "Cosmicduke", "SeaDuke" and "OnionDuke" Cozy Bear has been observed using an initial exploit or phishing email with malicious attachments to load a dropper which installs a Duke variant as a persistent trojan onto the target computer. It then gathers and sends data to a command and control server based on its configuration and/or live operator commands. Cozy Bear has been observed updating and refining its malware to improve cryptography, interactive functionality, and anti-analysis (including virtual machine detection). CosmicDuke was observed in 2013 as an updated version of MiniDuke with a more flexible plugin framework. In 2014 OnionDuke leveraged the Tor network to conceal its command and control traffic and was distributed by infecting binary executables on the fly if they were transmitted unencrypted through a Russia-based Tor exit node. "SeaDuke" appears to be a specialized trojan used in conjunction with other tools to compromise high-value targets. The group reportedly developed the 'HAMMERTOSS' trojan in 2015 to evade detection by relaying commands over covert channels on Twitter and GitHub.
Cozy Bear and fellow Russian hacking group Fancy Bear (likely the GRU) were identified as perpetuating the Democratic National Committee intrusion. While the two groups were both present in the DNC's servers at the same time, they appeared to operate independently. Further confirming their independent operations, computer forensics determined that Fancy Bear had only compromised the DNC for a few weeks while Cozy Bear had done so for over a year.
On 8 December 2020, U.S. cybersecurity firm FireEye disclosed that their internal tools had been stolen by a nation-state. Later investigations implicated an internal compromise of software deployments of SolarWinds Orion IT management product to distribute a trojan that FireEye dubbed SUNBURST. SolarWinds later confirmed that it had been compromised by a foreign nation state. and the U.S. Cybersecurity and Infrastructure Security Agency (CISA) to issue an emergency directive that U.S.
government agencies rebuild the affected software from trusted sources. It also attributed the intrusion campaign to the Russian SVR. Approximately 18,000 SolarWinds clients were vulnerable to the compromised Orion software. Estimates based on DNS C2 activity indicate that around one percent of these SolarWinds clients were selected for stage-two operations, where the perpetrators installed backdoors to remotely control the vulnerable SolarWinds installations. The Washington Post cited anonymous sources that attributed Cozy Bear as the perpetrator. According to Microsoft, the hackers compromised SolarWinds code signing certificates and deployed a backdoor that allowed impersonation of a target's user account via a malicious Security Assertion Markup Language definition.
Figure 1: Password Spraying Explained | Semperis Identity Attack Catalog Fortinet, Inc. is an American cybersecurity company headquartered in Sunnyvale, California. It develops and sells security products including firewalls, endpoint security and intrusion detection systems. Fortinet has offices in the US, Canada, and UK. Founded in 2000 by brothers Ken Xie and Michael Xie, the company's first and main product was FortiGate, a physical firewall. The company later added wireless access points, sandbox and messaging security. The company went public in November 2009.
In 2019, Fortinet grew to 21,000 WAN edge customers, according to a Gartner report. In February 2020, Fortinet released FortiAI, a threat-detection program that uses artificial intelligence. In July 2020, Fortinet launched multi-cloud SD-WAN. That year, BT Security selected Fortinet and other Threat Alliance members as Critical Partners. Access to this page requires authorization. You can try signing in or changing directories .
This article provides guidance on identifying and investigating password spray attacks within your organization and taking the required remediation actions to protect information and minimize further risks. Figure 2: Password Spraying Detection in Active Directory | Semperis Guides Before starting the investigation, make sure you have completed the setup for logs and alerts and other system requirements.
For Microsoft Entra monitoring, follow our recommendations and guidance in our Microsoft Entra SecOps Guide . By default, the Microsoft Active Directory Federation Services (ADFS) in Windows Server 2016 has a basic level of auditing enabled. With basic auditing, administrators can see five or less events for a single request. Set logging to the highest level and send the AD FS (& security) logs to a SIEM to correlate with AD authentication and Microsoft Entra ID.
Select Start , navigate to Programs > Administrative Tools , and then select Local Security Policy . Figure 3: Protecting against password spray attacks with Azure Sentinel and Azure AD Navigate to the Security Settings\Local Policies\User Rights Management folder, and then double-click Generate security audits .
On the Local Security Setting tab, verify that the ADFS service account is listed. If it isn't present, select Add User or Group and add it to the list, and then select OK . To enable auditing, open a command prompt with elevated privileges and run the following command: Next, open the ADFS Management snap-in, select Start , navigate to Programs > Administrative Tools , and then select ADFS Management .
The Microsoft Entra Connect Health for ADFS agent allows you to have greater visibility into your federation environment. It provides you with several preconfigured dashboards like usage, performance monitoring and risky IP reports. To install ADFS Connect Health, go through the requirements for using Microsoft Entra Connect Health , and then install the Azure ADFS Connect Health Agent .
After Microsoft Entra Connect Health for ADFS is configured, you should monitor and set up alerting using the ADFS Risky IP report workbook and Azure Monitor. The benefits of using this report are: Connect the Security Information and Event Management (SIEM) tool to Microsoft Defender for Cloud Apps, which currently supports Micro Focus ArcSight and generic common event format (CEF).
You can connect SIEM with the Microsoft Graph Security API by using any of the following options: For more information, see Security solution integrations using the Microsoft Graph Security API . You can also download the password spray and other incident playbook checklists as an Excel file . Let's understand a few password spray attack techniques before proceeding with the investigation.
Password compromise: An attacker guessed the user's password but hasn't been able to access the account due to other controls such as multifactor authentication (MFA). Account compromise: An attacker guessed the user's password and gained access to the account. As the first step, you need to check what authentication type is used for a tenant/verified domain that you're investigating.
To obtain the authentication status for a specific domain name, use the Get-MgDomain PowerShell command. Here's an example: If the authentication is federated, then successful sign-ins are stored in Microsoft Entra ID. The failed sign-ins are in their Identity Provider (IDP). For more information, see AD FS troubleshooting and event logging .
If the authentication type is managedâIIcloud-only, password hash sync (PHS), or pass-through authentication (PTA)âIIthen successful and failed sign-ins are stored in the Microsoft Entra sign-in logs. The Staged Rollout feature allows the tenant domain name to be federated but specific users to be managed. Determine if any users are members of this group.
To check whether you're storing and correlating logs in a Security Information and Event Management (SIEM) or in any other system: 2. System Architecture & Core Working Principles It's important that you understand the logs that you're seeing to be able to determine compromise. Here are quick guides to understanding Microsoft Entra sign-ins and MFA reporting: An incident trigger is an event or a series of events that causes predefined alert to trigger. An example is the number of bad password attempts above your predefined threshold. Here are further examples of triggers that can be alerted in password spray attacks and where these alerts are surfaced. Incident triggers include: Unusual spikes in activity are key indicators through Microsoft Entra Health Connect (assuming this component is installed).
Other indicators are: Risky IP alerts occur when the customized threshold has been reached for bad passwords in an hour and bad password count in a day and extranet lockouts. The details of failed attempts are available in the tabs IP address and extranet lockouts .
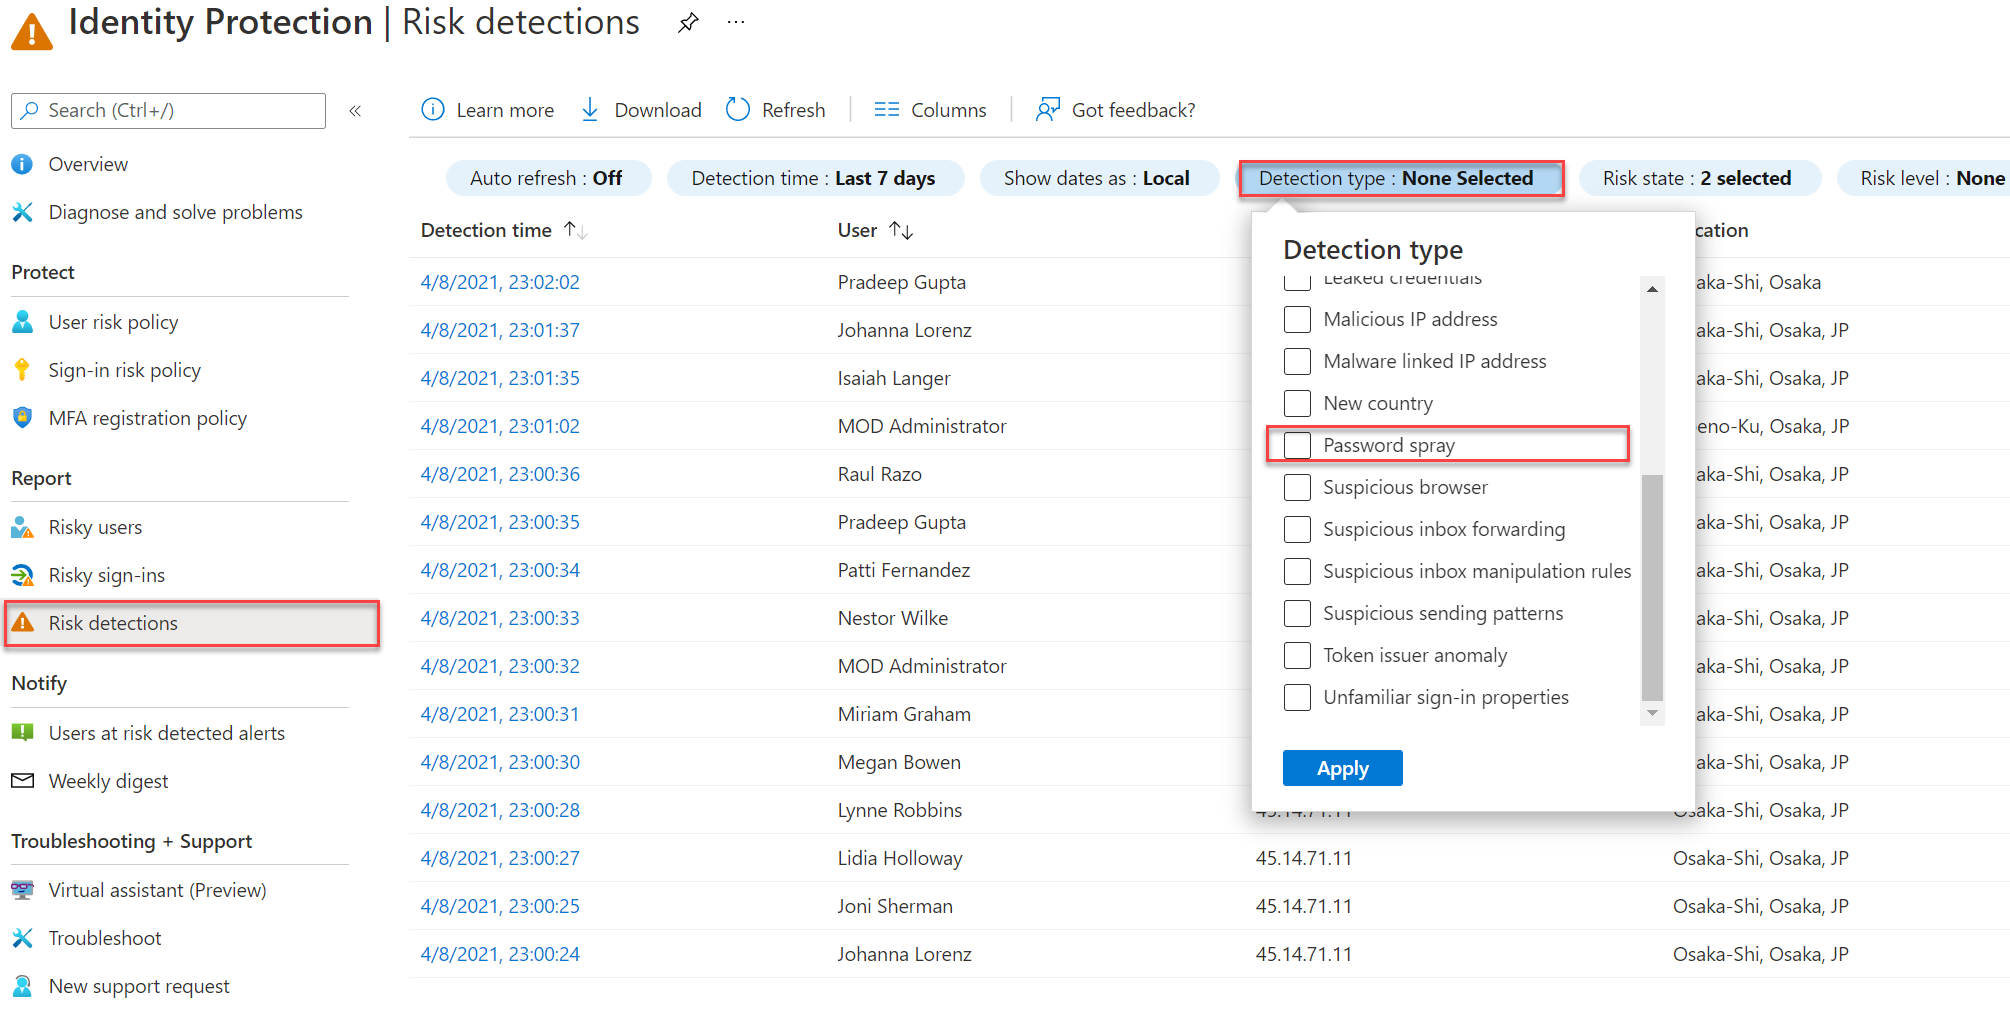
Azure Identity Protection is a Microsoft Entra ID P2 feature that has a password-spray detection risk alert and search feature that provides more information or automatic remediation. Low and slow attack indicators are when thresholds for account lockout or bad passwords aren't being hit. You can detect these indicators through: You can perform investigation and mitigation simultaneously during sustained/ongoing attacks.
Determine the attacker IP address (might be multiple sources and multiple IP addresses) from the firewall, ADFS, SIEM, or Microsoft Entra ID. Once password spray confirmed, you might have to inform the local agencies (police, third parties, among others). To collect the Audit Event 411 - failed authentication requests, use the following script : Along with the above event IDs, collate the Audit Event 1203 âII Fresh Credential Validation Error .
You can get all the Event IDs from the Microsoft Sentinel Playbook that is available on GitHub . Isolate the ADFS and Microsoft Entra successful and interrupted sign-in events. These are your accounts of interest. Block the IP Address ADFS 2012R2 and above for federated authentication. Here's an example: Microsoft Entra Sign-In reports include ADFS sign-in activity when you use Microsoft Entra Connect Health. Filter sign-in logs by Token Issuer Type "Federated".
Here's an example PowerShell command to retrieve sign-in logs for a specific IP address: Also, search the Azure portal for time frame, IP address and successful and interrupted sign-in as shown in these images. You can then download this data as a .csv file for analysis. For more information, see Sign-in activity reports in the Microsoft Entra admin center .
It's important to be able to react to the most critical threat. This threat can indicate that the attacker has successfully obtained access to an account and therefore can access/exfiltrate data; the attacker has the password but might not be able to access the account. For example, they have the password but aren't passing the MFA challenge. Also, the attacker couldn't be guessing passwords correctly but continuing to try. During analysis, prioritize these findings: Most attacks use legacy authentication. There are many ways to determine the protocol of the attack.
Or if you have an Azure workspace, you can use the prebuilt legacy authentication workbook located in the Microsoft Entra admin center under Monitoring and Workbooks . If they haven't and this activity is unusual, flag the user and investigate all of their activities. Ensure you record successful passwords but failed MFA responses, as this activity indicates that the attacker is getting the password but not passing MFA.
Set aside any account that appears to be a normal sign-in, for example, passed MFA, location and IP not out of the ordinary. It's important to also check MFA logs to determine if an attacker guessed a password but are failing the MFA prompt. The Microsoft Entra multifactor authentication logs show authentication details for events when a user is prompted for multifactor authentication. Check and make sure there are no large suspicious MFA logs in Microsoft Entra ID. For more information, see how to use the sign-ins report to review Microsoft Entra multifactor authentication events .
In Defender for Cloud Apps, investigate activities and file access of the compromised account. For more information, see: Check whether the user has access to more resources, such as virtual machines (VMs), domain account permissions, storage, among others. If there's a data breach, you should inform more agencies, such as the police. Implement password protection on Microsoft Entra ID and on-premises by enabling the custom-banned password lists. This configuration prevents users from setting weak passwords or passwords associated with your organization: Tag the IP addresses in Defender for Cloud Apps to receive alerts related to future use: In Defender for Cloud Apps, "tag" IP address for the IP scope and set up an alert for this IP range for future reference and accelerated response.
Set up alerting in your SIEM tool and look at improving logging gaps. Integrate ADFS, Microsoft Entra ID, Office 365 and Defender for Cloud Apps logging. 3. Software Implementation, Frameworks & Protocols In a controlled study by Horizon3 researchers, models that explicitly identified a trap in their reasoning still attacked it 73.4% of the time. Read the findings and see what they mean for canaries, decoys, and early detection.
Password spray is the most common cloud identity attack technique because it works: enterprise users frequently choose passwords based on company name + year + special character (CompanyName2024!), and spray tools test these patterns across the entire tenant in minutes. Microsoft reports password spray as the technique behind the majority of compromised Microsoft 365 accounts.
The attack is designed to be invisible to standard monitoring: each individual account sees only one failed attempt, well below lockout thresholds. Detection requires aggregate analysis across accounts: looking for a single source IP failing against many different accounts within a time window. Microsoft Entra ID Identity Protection (P2) includes a Password Spray risk detection that fires automatically when its machine learning model detects spray patterns.
Password spray detection requires aggregate analysis: count distinct TargetUserName values (on-prem: Event 4625 with SubStatus 0xC000006A) or distinct UserPrincipalName values (cloud: SigninLogs with ResultType != 0) per source IP in a rolling window: alert when 15-20+ unique accounts fail from a single IP within 30 minutes. In Entra ID, enable Identity Protection P2 for built-in spray detection (risk event type: passwordSpray). Constrain spray damage with Entra Password Protection (banned company-specific passwords), Smart Lockout, and Conditional Access blocking logins from non-operating countries. MFA enforcement on all accounts prevents spray from being a complete compromise: correct password found still requires a second factor.
Brute force attacks target a single account with many different passwords: easily detected by account lockout and by high Event 4625 counts for one TargetUserName. Password spray tests one (or a few) passwords against many different accounts: avoiding lockout by staying below the threshold per account. Detection requires counting distinct TargetUserName values per source IP rather than total failures per account. Both appear as Event 4625 on Windows DCs, but spray generates high unique account counts, while brute force generates high total failure counts per account.
Smart Lockout in Entra ID tracks failed attempts per credential hash rather than per IP address. This means legitimate users authenticating from multiple locations or different IPs are not affected when an attacker sprays against their account from a different IP. The attacker's IP gets incrementally blocked after the lockout threshold. Smart Lockout is enabled by default; adjust the threshold (default: 10) and lockout duration (default: 60 seconds) in Entra admin center > Protection > Authentication Methods > Password Protection.
Password spray detection requires different thresholds than brute force. Brute force: many failures against one account. Password spray: few failures (1-3) against many accounts from a single source. SIEM detection query: group Event ID 4625 (logon failure) by SubjectUserName (or IpAddress for network logons), count distinct TargetUserName values per source in a 1-hour window, and alert when a single source hits more than 20 distinct accounts with failures. Also check: failed authentications for accounts with names following a predictable corporate pattern ( [email protected] ) from a single IP; and a spike in overall failed logins across the domain compared to a 7-day baseline.
How do I configure Active Directory lockout policies to balance security and availability? Account lockout policy recommendations from Microsoft and NIST: Account Lockout Threshold: 5-10 invalid attempts (5 blocks spray attacks quickly; 10 reduces helpdesk calls for clumsy typists). Observation Window: 15 minutes (the window during which failures accumulate toward the threshold). Account Lockout Duration: 15-30 minutes with administrator unlock enabled (auto-unlock reduces helpdesk burden; a 15-minute wait frustrates attackers while being manageable for users). For Fine-Grained Password Policies (available in AD DS 2008+): apply stricter policies to privileged accounts (Domain Admins, service accounts) with a threshold of 3 failures, and more lenient policies for standard user accounts. Fine-grained policies override the default domain policy for specific groups.
Entra ID Password Protection maintains a global banned password list (updated based on Azure AD's analysis of breach password datasets) and an optional custom banned password list. When users set or change passwords, the service checks against both lists: common passwords like 'Password1!' and 'Summer2023' are blocked even with complexity requirements technically satisfied. For on-premises Active Directory, deploy the Entra ID Password Protection DC Agent (free) on each domain controller: it downloads the banned password list and enforces it during AD password changes, extending cloud-based protection to hybrid and on-premises environments. Enable in Entra admin center > Security > Authentication Methods > Password Protection.
How do you detect password spray originating from a compromised internal machine rather than an external attacker IP? Internal spray detection requires adjusted thresholds because the source IP is trusted by default. On-premises Event 4625 is the primary signal: filter to LogonType 3 (network logon) from internal source IPs, then count distinct TargetUserName values per source IP in a 30-minute window. Internal machines should fail authentication against very few accounts under normal conditions -- more than 5-10 unique accounts failing from a single internal workstation IP is anomalous and warrants immediate investigation. For Kerberos-based internal spray: monitor Event ID 4771 (Kerberos pre-authentication failed) on domain controllers with Error Code 0x18 (wrong password), since spray tools targeting Kerberos generate 4771 rather than 4625. Combine the detection with process-level context: if the spray originates from an interactive session on a workstation, correlate the source IP back to process creation events (Sysmon Event 1) to identify which process is generating the authentication attempts. Internal spray from a compromised machine is typically more targeted than external spray and uses a shorter account list, so lower your unique-account threshold for internal source IPs.
25 actively exploited vulnerabilities with CVSS scores, exploit status, and patch availability. Print it, pin it, share it with your SOC team. Step-by-step 24-hour IR checklist covering detection, containment, eradication, and recovery. Built for SOC teams, IR leads, and CISOs.
50,000+ security professionals read Decryption Digest for early warnings on zero-days, ransomware, and nation-state campaigns. Free, daily, no spam. Cybersecurity professional with expertise in threat intelligence, vulnerability research, and enterprise security. Covers zero-days, ransomware, and nation-state operations for 50,000+ security professionals every morning.
Actionable threat intelligence for working practitioners. Free. No spam. Trusted by 50,000+ SOC analysts, CISOs, and security engineers. In a controlled study by Horizon3 researchers, models that explicitly identified a trap in their reasoning still attacked it 73.4% of the time. Read the findings and see what they mean for canaries, decoys, and early detection.
Password spray attacks succeed in real environments because standard lockout policies protect individual accounts but create no visibility when the attack is distributed. An environment with a 5-attempt lockout threshold and a 30-minute reset window is vulnerable to a spray that sends exactly 4 attempts per account from a single source, at scale, across all user accounts. The spray hits every account in the directory and the lockout counter never triggers. Detecting this requires correlation across accounts over time, not per-account monitoring.
Authentication failures must be logged before you can detect spray. Enable the correct audit policies on domain controllers: Computer Configuration > Windows Settings > Security Settings > Advanced Audit Policy Configuration > Account Logon > Audit Credential Validation = Failure and Audit Kerberos Authentication Service = Failure. Both are needed: Event ID 4625 captures NTLM authentication failures; Event ID 4771 (Kerberos pre-auth failure, SubStatus 0x18 for bad password) captures Kerberos-based spray. These events are generated on domain controllers, not on member workstations. Confirm the audit policy is applied: auditpol /get /subcategory:'Credential Validation' and auditpol /get /subcategory:'Kerberos Authentication Service'. Ensure Events 4625 and 4771 are reaching your SIEM from all DCs -- spray detection requires data from every DC, not just one.
The spray signature: many distinct target accounts failing authentication within a short window from the same source IP. Query in Defender XDR Advanced Hunting: DeviceLogonEvents | where ActionType == 'LogonFailed' and Timestamp > ago(1h) | summarize FailedAccounts = dcount(AccountName), Attempts = count() by RemoteIP | where FailedAccounts > 20. In KQL for Sentinel: SecurityEvent | where EventID == 4625 and TimeGenerated > ago(1h) | summarize UniqueTargets = dcount(TargetUserName), Attempts = count() by IpAddress | where UniqueTargets > 20 and Attempts > 30. Adjust the thresholds based on your baseline authentication volume. The ratio of UniqueTargets to Attempts is the spray indicator: a ratio close to 1 (one attempt per account) is classic spray; a high ratio of attempts to accounts is brute force. Kerberos spray query: SecurityEvent | where EventID == 4771 and Status == '0x18' and TimeGenerated > ago(1h) | summarize UniqueTargets = dcount(TargetUserName) by IpAddress | where UniqueTargets > 20.
Microsoft Defender for Identity (MDI) provides automated spray detection if you have a sensor deployed on all domain controllers. MDI alert: 'Password spray attack' in the MDI portal or Defender XDR incident queue -- triggers when MDI's baseline model detects anomalous failed authentication volume across accounts. MDI provides the spray source IP, the list of targeted accounts, and the timing of the spray. The advantage over raw event log queries: MDI applies baseline normalization -- it knows your normal authentication volume and compares against it, reducing false positives during high-traffic periods like Monday mornings after a long weekend. If you do not have MDI, raw event log queries as above are the alternative. For cloud-side spray against Entra ID: the Entra ID sign-in logs provide failed sign-in data with similar query patterns. Entra ID Smart Lockout provides built-in cloud-side spray mitigation.
When a spray is detected: first, determine if any accounts were successfully compromised. Query for accounts that had a failed logon from the spray source IP followed by a successful logon: SecurityEvent | where EventID in (4625, 4624) and IpAddress == 'spray_source_ip' and TimeGenerated between(starttime .. endtime) | order by Account, TimeGenerated | project TimeGenerated, EventID, Account, LogonType. Any account with a 4625 from the spray source followed by a 4624 is potentially compromised. Also check Defender for Identity for accounts flagged as 'Suspected Account Compromised' or 'Suspicious logon' in the same timeframe. For each potentially compromised account: check what they accessed after the successful logon (DeviceLogonEvents for the account, file access logs, Exchange or SharePoint access logs). Reset passwords for any confirmed or suspected compromised accounts, revoke Entra ID sessions, and check for mailbox forwarding rules added after the spray event.
Standard account lockout policies do not prevent spray (attackers stay under the threshold) but they do limit the number of attempts per account. Recommended settings: lockout threshold of 10 (not 5 -- false lockouts from fat-fingered passwords have a support cost and low thresholds train users to call the help desk). Lockout duration of 30 minutes. Observation window of 30 minutes. For service accounts and privileged accounts that are high-value spray targets, use a Fine-Grained Password Policy (FGPP) with stricter settings (threshold 3, duration 60 minutes) applied via a Password Settings Object (PSO) to the specific accounts or groups. Entra ID Smart Lockout: for hybrid environments where password spray can come against Entra ID (cloud-side), Smart Lockout is a built-in Entra ID feature that learns your normal sign-in patterns and applies IP-reputation-based lockouts that preserve legitimate user access while blocking spray sources. Smart Lockout threshold is configurable in the Authentication Methods > Password Protection policy in the Entra admin center.
Spray detection requires cross-account correlation over a time window -- something no single account's lockout counter captures. Enable Kerberos pre-auth failure auditing (Event 4771) alongside NTLM failure auditing (Event 4625), deploy the KQL queries to alert on high unique-target failure counts from a single source, and use Defender for Identity for automatic detection with lower false-positive rates. Respond quickly: if any account shows a failed attempt followed by a success from the spray source, treat it as compromised and reset immediately.
A fat-finger failure pattern shows multiple failures for the same account from the same IP over a short window. A spray pattern shows one or a few failures for many distinct accounts from the same IP over a short window. The UniqueTargets to Attempts ratio is the distinguishing metric: close to 1 means spray, significantly less than 1 means brute force or fat-finger. A single user forgetting their password generates 5 failures for 1 account; a spray generates 1 failure for 500 accounts.
Password spray tests a single known weak password (or a few) against many accounts in a target organization. Credential stuffing takes credentials leaked from other breaches (email and password pairs) and tests them against your environment, based on the likelihood that users reuse passwords. Both result in Event ID 4625, but credential stuffing typically comes with a higher variety of usernames (leaked emails that may or may not be in your directory) while spray typically uses valid usernames extracted from your organization's directory. Defender for Identity distinguishes between the two via its baseline model.
No. Smart Lockout operates on cloud-side Entra ID authentication. For on-premises Kerberos and NTLM authentication against domain controllers, Smart Lockout has no effect. Spray against on-premises AD requires the DC-level detection and lockout policies described in this guide. For hybrid environments using Password Hash Sync or Pass-Through Authentication, cloud-side spray is handled by Smart Lockout; on-premises spray requires DC-level controls. Both surfaces need independent coverage.
A threshold of 3 creates high false-positive lockout rates: users mistype their password twice on a Monday morning and are locked out before they reach IT. The support burden is significant and trains users to call the help desk for lockouts, which attackers can exploit via social engineering. A threshold of 10 is the common operational recommendation. The detection approach above identifies spray before it reaches 10 attempts per account when looking at the cross-account signature.
Check the source IP and workstation name in Event ID 4625. Internal spray from a compromised endpoint shows authentication attempts originating from a domain-joined machine name and internal IP address. External spray typically comes from unusual IP addresses (non-RFC1918 addresses if VPN is not in use) or from the same IP authenticating against many different accounts in rapid succession (which internal clients do not do). Defender for Identity's Suspected Password Spray Attack alert enriches the source IP with threat intelligence and geolocation. For purely on-premises DC event logs, cross-reference the source IP against your asset inventory -- a source IP not assigned to any known internal machine is a strong indicator of external origin.
Several conditional access policies address password spray directly: sign-in risk-based conditional access (requires Entra ID P2) blocks or requires MFA for sign-in attempts that Entra's risk engine classifies as suspicious based on behavioral signals like atypical login location, unfamiliar device, or impossible travel. This catches spray attempts from credentials that successfully authenticated. Block legacy authentication (all policies blocking Exchange Active Sync, POP, IMAP, Basic Auth clients) is critical -- legacy protocols cannot use MFA and are the primary target for spray since MFA cannot be enforced.
Require Authenticator app or phishing-resistant MFA (FIDO2, certificate) so that even a successful spray does not yield access without the second factor. For high-value accounts: configure smart lockout settings in Entra ID (Password protection > Lockout threshold) to lock accounts after 10 failed attempts and customize the lockout duration to increase exponentially for repeated lockouts, which slows automated spray tools significantly.
4. Practical Deployment, Analysis & Case Studies 25 actively exploited vulnerabilities with CVSS scores, exploit status, and patch availability. Print it, pin it, share it with your SOC team. Step-by-step 24-hour IR checklist covering detection, containment, eradication, and recovery. Built for SOC teams, IR leads, and CISOs.
50,000+ security professionals read Decryption Digest for early warnings on zero-days, ransomware, and nation-state campaigns. Free, daily, no spam. Cybersecurity professional with expertise in threat intelligence, vulnerability research, and enterprise security. Covers zero-days, ransomware, and nation-state operations for 50,000+ security professionals every morning.
Actionable threat intelligence for working practitioners. Free. No spam. Trusted by 50,000+ SOC analysts, CISOs, and security engineers. Password spraying detection is a vital ability for all organizations. In a password spraying attack , the attacker attempts to gain unauthorized access by trying a few common or weak passwords across many accounts rather than targeting a single account with many passwords. The idea is to test several passwords, hoping that some users have chosen a weak password.
In the context of Active Directory (AD), password spraying attacks are concerning because any authenticated user in an AD environment can use LDAP to query accounts. This enables an attacker with minimal privileges to attempt common or weak passwords across many accounts without triggering account lockout policies ( Figure 1 ). Microsoft estimates that password spraying attacks are responsible for more than one-third of all account compromises, highlighting the threat that this method poses to organizations.
Password spraying attacks can generate both a significant amount of activity in the Security event logs of a domain controller (DC) and a large volume of network traffic ( Figure 2 ). Numerous failed logons can be noisy. Therefore, an attacker might introduce a delay between attempts in a password spraying attack ( Figure 3 ). Because Security event logs on DCs are often generated within seconds, this delay helps the attack blend with normal activity, reducing the chances of detection.
The logs on a DC show that the timestamps of these failed logon attempts occur at consistent intervals, caused by introducing a delay of 10 seconds between each attempt. This spread-out timing makes the activity less suspicious than multiple failed logon attempts that happen simultaneously ( Figure 4 ). Adding a delay makes a password spraying attack less suspicious. However, the attack will still trigger the An account failed to log on event on the DC.
Kerberos pre-authentication can make password spraying detection more difficult. Failed attempts that use such pre-authentication do not generate the standard logon failure events in the Security event logs. In this way, the attacker can guess passwords without triggering the typical alerts associated with failed login attempts ( Figure 5 ). In this type of attack, instead of seeing the typical An account failed to log on events in the Security event logs, you will observe Kerberos Pre-Authentication failed events. These events include the hex value 0x18, which means that an incorrect password was entered ( Figure 6 ).
Another way to make password spraying detection more difficult is by disrupting the predictable patterns for which security systems often monitor ( Figure 7 ). This randomness makes the attack blend in with normal traffic, making attack detection and response more challenging for systems and security teams. A password spraying attack with randomized delays still generates log events. However, the irregular timing between attempts can make password spraying detection more difficult. Instead of a consistent pattern, the logs show login attempts spread out unpredictably, making the attack less conspicuous ( Figure 8 ).
The same concept can be applied by randomizing delay intervals during a password spraying attack that uses Kerberos pre-authentication. Because 4771 events are not typically closely monitored, introducing randomized delays makes detection even more difficult than previously discussed ( Figure 9 ). As in the previous example, randomization of the delay intervals between each login attempt can make this activity look like normal behavior in the logs ( Figure 10 ).
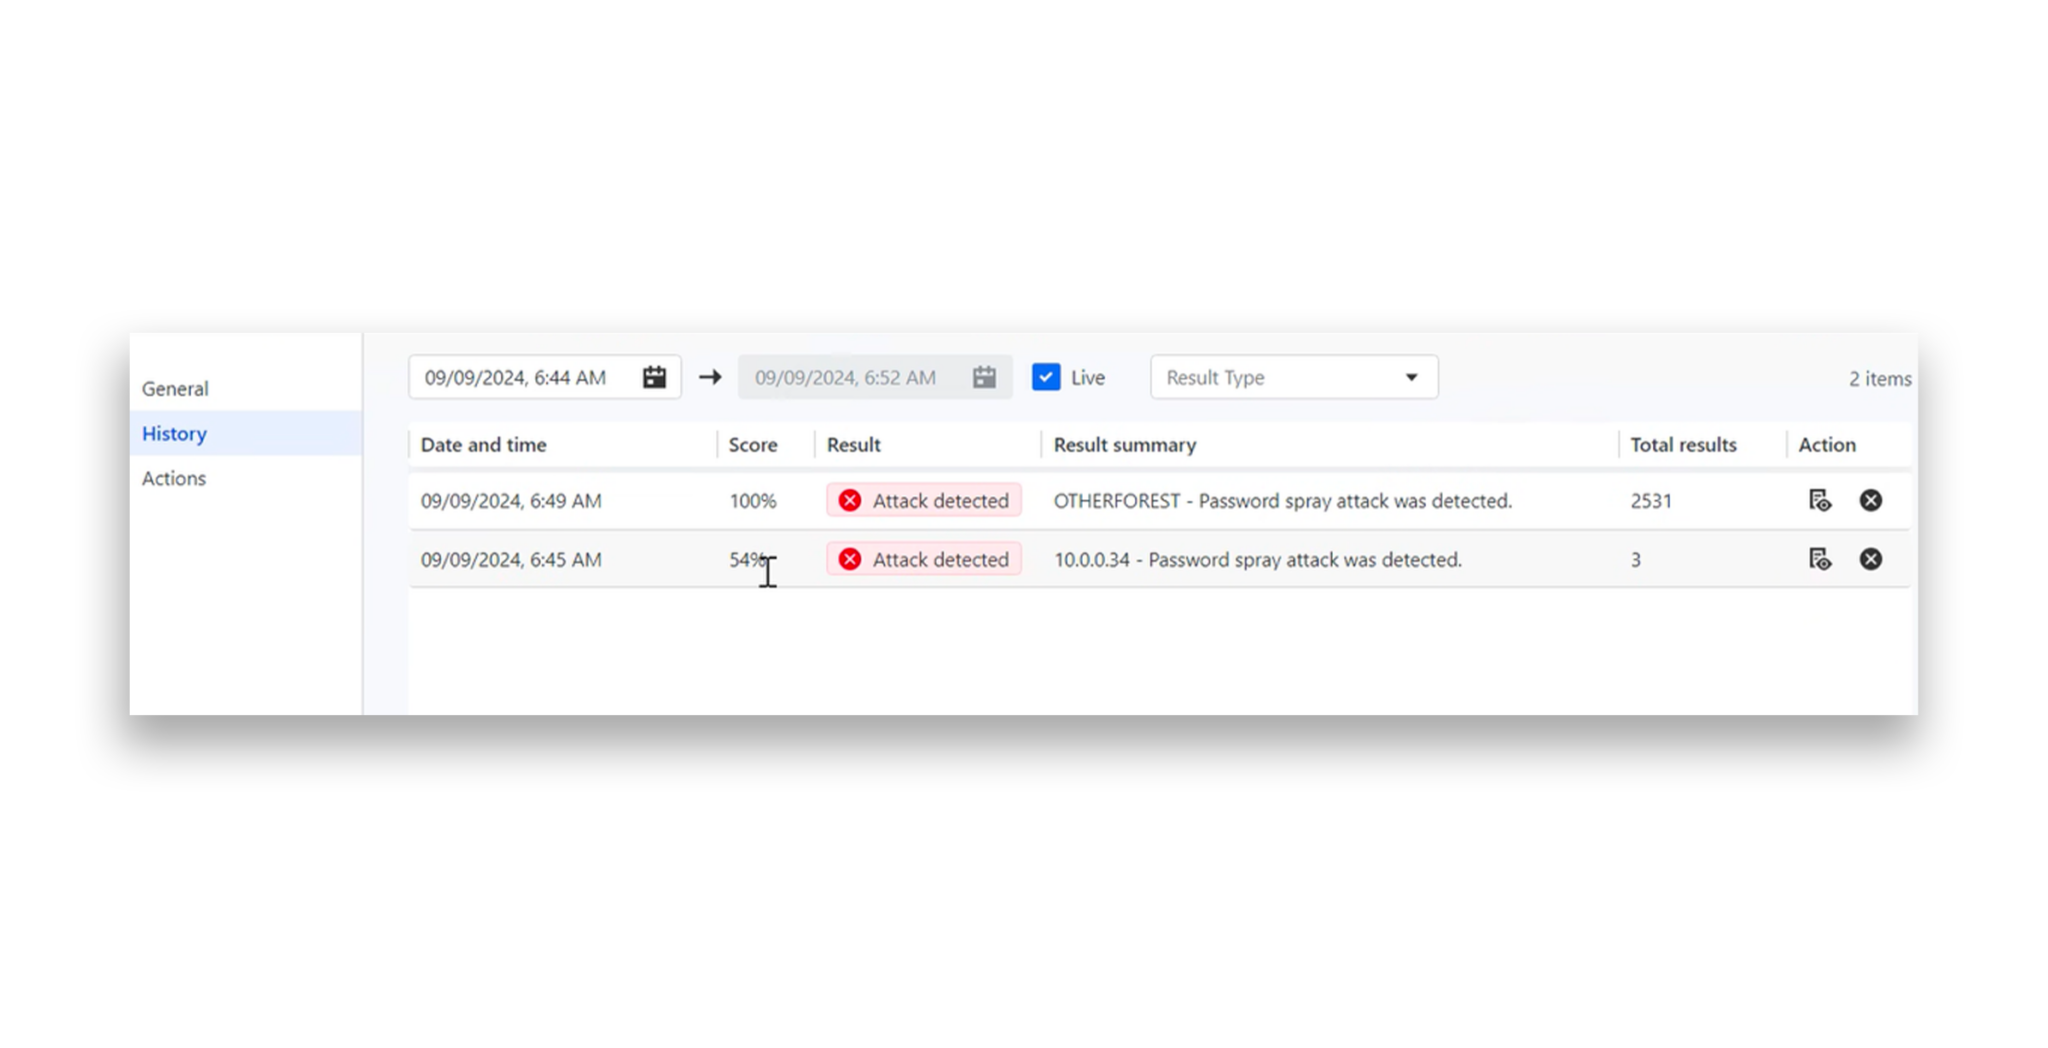
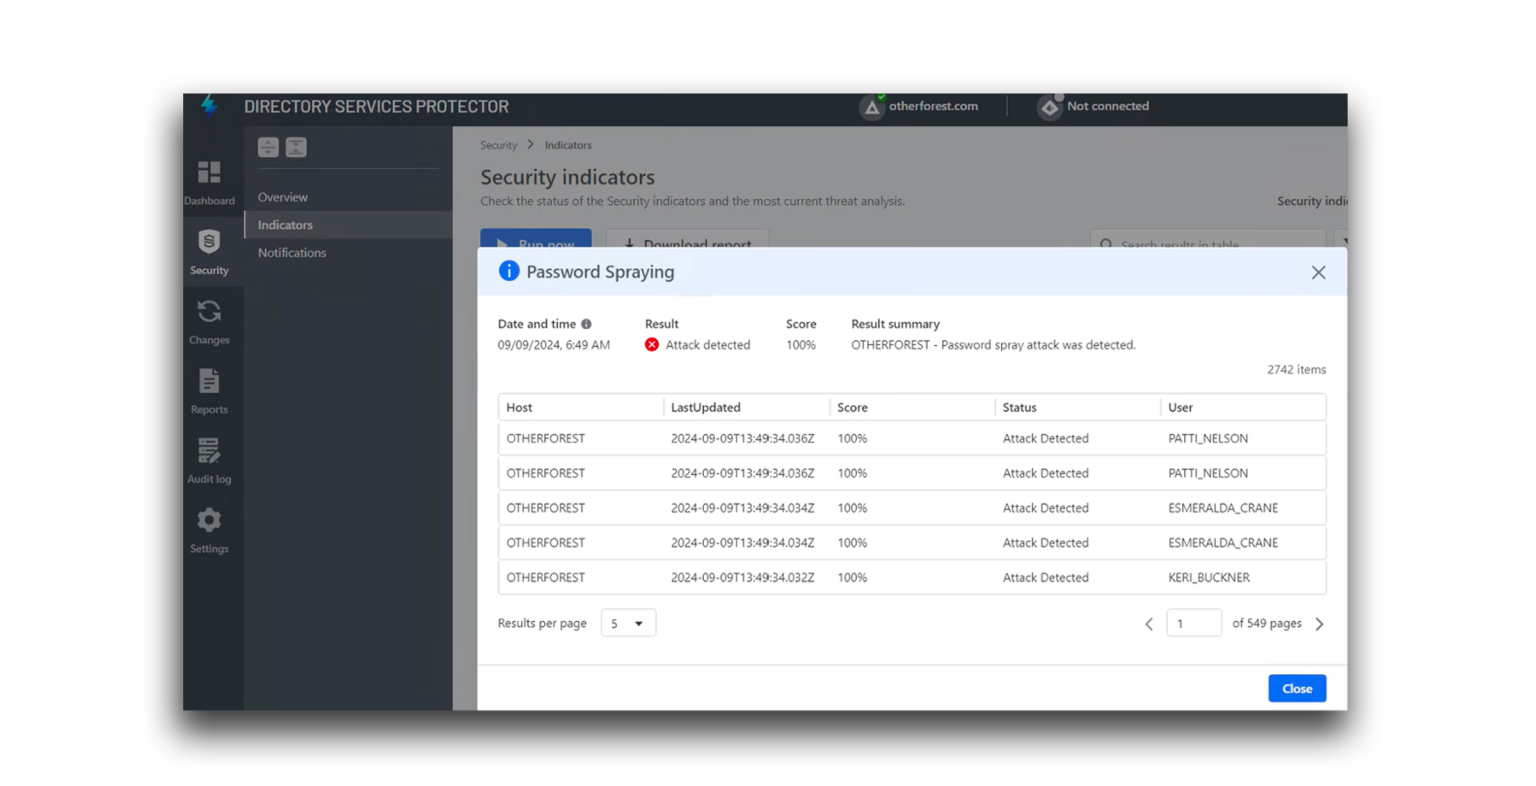
Identity Runtime Protection (IRP), a feature of the Semperis Lighting Platform , uses various attack-pattern indicators and anomaly detection to monitor for and detect identity-based attacks. Lightning IRP typically needs 7 to 10 days to learn the patterns of an environment through behavior analysis. Figure 11 shows Lightning IRP successfully identifying two password spraying attacks. Based on these alerts, you can determine which accounts were targeted and the corresponding detection scores.
Figure 12 shows Lightning IRP password spraying detection of an attack that randomized the delay intervals for each password spraying attempt via Kerberos pre-authentication. The detection score is low in this case because the attack was designed for greater stealth. However, Lighting IRP was able to detect the behavior even though the traffic was intended to look typical and not raise alarms.
Performing a password spraying attack without randomizing delay intervals typically results in a higher detection score, as shown in Figure 13 . This method is more likely to be flagged with a higher detection score (100% in this example) because of its predictable and noisy nature, which makes password spraying detection and categorization easier. To reduce the risk of successful password spraying attacks, it is important to enforce strong password policies, including implementing account lockout mechanisms (either temporary or permanent) after several consecutive failed login attempts.
Organizations should ensure that such password policies are enforced through a default domain policy or fine-grained password policies in Active Directory. Organizations that use Entra ID P1 or that have the appropriate Enterprise Mobility + Security (EMS) or Microsoft 365 licensing can achieve an additional layer of protection by deploying Entra Password Protection or a similar solution for Active Directory. This tool proactively prevents users from creating or using passwords that are easily guessable or that have been compromised in previous breaches. By integrating this solution, organizations can improve the likelihood of successful password spraying detection.
Figure 14 shows is an example in which Entra ID Password Protection has prevented a user from setting a password that does not comply with the organization's current password policy. Simulate an external attacker performing a password spray against a set of domain accounts, then trace the resulting telemetry through Splunk to build a working detection — including validating what happens if the spray succeeds and the attacker attempts to use the compromised account further.
Password spraying (MITRE ATT&CK T1110.003 ) uses one or a small number of common passwords against many usernames, rather than many passwords against one account — this keeps each account's failed-attempt count under typical lockout thresholds while still finding weak credentials across a large user base. users.txt contained 5 domain accounts ( Admin1 , BigGen , NightMan , serv-app , Employee1 ); passwords.txt contained 5 candidate passwords, keeping per-account attempts at or below a typical 3-attempt lockout policy.
One account ( Employee1 ) was deliberately set to match a password in the list, to produce a realistic mixed result: several STATUS_LOGON_FAILURE responses and one successful authentication — rather than an all-fail run that doesn't reflect how a real spray plays out. Confirmed remote code execution against the target using the compromised account, and confirmed it was a domain account ( lab.local\Employee1 ).
CrackMapExec returned a [+] (execution succeeded), but this only confirms the remote command ran — not that its own logic succeeded. Employee1 was not present — the escalation failed. This is expected: a standard domain account has no delegated rights to modify Domain Admins membership. The permission check happens at the Active Directory layer regardless of whether the request originates locally or remotely — the identity behind the request is what's evaluated, not the path it arrives by.
5. Performance Evaluation & Extended Technical Observations Logic: flags any single source IP generating failed logons against 5+ distinct accounts inside a 3-minute window — the defining shape of a spray (many accounts, one source) rather than a brute force (one account, many attempts). The spray successfully compromised one low-privilege domain account. The attempted escalation to Domain Admins was correctly blocked by AD's built-in permission model, and this was independently verified through both the target's actual state and the absence of a corresponding audit event — demonstrating that a compromised account does not automatically equal full domain compromise, and that log evidence should be treated as authoritative over tool output.
Simulated and detected a password spraying attack against Active Directory using Kali, Splunk, and Windows Server. It includes full attack chain, detection logic, and troubleshooting Password spraying is one of the most consistent initial access techniques in enterprise breaches: a single password tested against hundreds of accounts avoids lockout policies while maximising the chance of a hit. This guide covers the telemetry, Sigma rules, and KQL queries defenders need to detect spray campaigns against Active Directory and Entra ID.
Password spraying is classified as T1110.003 in MITRE ATT&CK. The technique is simple: instead of hammering a single account with many passwords (which triggers lockout), an attacker tries one password against every account in the directory. Most enterprise lockout policies trigger after five to ten failed attempts per account. A spray campaign that tries one password every 30 minutes against 500 accounts generates 500 failures across 500 accounts — well under the threshold for any individual user, but a coherent signal if you know what to look for.
The persistence of this technique reflects a structural problem: password reuse. A single credential dump from a prior breach, a seasonal password like Summer2026! , or a company-name variation catches accounts regularly enough that threat actors keep using it. MSTIC data shows that spray campaigns continue to be the dominant credential access technique for nation-state initial access, with Entra ID accounts in cloud-only and hybrid environments as the primary target.
Large NAT environments : Many users sharing a single public IP will generate correlated failures that look like spraying. Maintain an allowlist of known corporate egress IPs and adjust thresholds accordingly. Tune the KQL queries to exclude these IP ranges. Password expiration waves : When organisational password policies expire a large cohort at the same time, genuine users failing to authenticate with expired credentials can trigger spray alerts. Correlate with EventID 4625 SubStatus 0xc0000071 (expired password) separately.
Service account misconfigurations : A service account with a wrong password configured in dozens of places generates exactly the failure distribution of a spray. These are identifiable because they fail with the same username repeatedly rather than rotating through accounts. Load balancers and proxies : Authenticate traffic aggregated behind a proxy will present a single source IP for many legitimate users.
Password spraying remains effective because of password reuse, weak policy enforcement, and lack of detection coverage on Kerberos and legacy auth protocols. The detection rules above provide coverage across the primary spray vectors in AD and Entra ID environments. A self-built home lab simulating a real-world Security Operations Center (SOC) workflow: standing up Active Directory, forwarding logs to a SIEM, launching an attack against the environment, and writing the detection logic to catch it.
All VMs were built in VirtualBox on a shared NAT Network so the DC and client could communicate on the same subnet. I simulated a password spray - a technique where an attacker tries one common password against many different usernames, rather than many passwords against one account (which would trip a lockout policy faster). Using PowerShell's System.DirectoryServices.AccountManagement namespace, I validated a single incorrect password against five domain accounts in quick succession: Note on method: my first attempt used Get-WmiObject -Credential , which silently ran locally instead of authenticating against the domain because no -ComputerName was specified - it generated no failed-logon events at all. Switching to ValidateCredentials forced a genuine authentication attempt against AD, which is what actually produces Event ID 4625 in the Security log.
With Windows Security logs flowing into Splunk, I searched for failed logon events ( Event ID 4625 ) and grouped them to spot the spray pattern. This surfaced five distinct accounts - owilson , jsmith , cdior , bwayne , amarie - all failing within a 53-millisecond window , clearly distinguishable from the scattered, single-account failures generated by normal background noise (mistyped logins, service accounts, etc.).
This confirmed each of the five targeted accounts failed exactly once, in contrast to organic noise like repeated Administrator login failures spread across hours. To make the attack scenario more realistic, I re-ran the spray from Client01 (a domain-joined Windows workstation) instead of running it directly on the DC console - reflecting how a real attacker would more likely pivot from a compromised endpoint rather than have direct access to the Domain Controller itself.
10.0.2.20 is Client01's static IP, and the workstation name matches its local hostname - confirming the failed logon attempts genuinely originated from a separate domain-joined machine, not the DC itself. Detection lab: Active Directory + Splunk SIEM, simulated password spray attack and detection logic Monitor for activities and techniques associated with Password Spraying attacks within Active Directory environments.
In a password spraying attack, adversaries leverage one or a small list of commonly used / popular passwords against a large volume of usernames to acquire valid account credentials. Unlike a Brute Force attack that targets a specific user or small group of users with a large number of passwords, password spraying follows the opposite aproach and increases the chances of obtaining valid credentials while avoiding account lockouts. This allows adversaries to remain undetected if the target organization does not have the proper monitoring and detection controls in place. Password Spraying can be leveraged by adversaries across different stages in an attack. It can be used to obtain an iniial access to an environment but can also be used to escalate privileges when access has been already achieved. In some scenarios, this technique capitalizes on a security policy most organizations implement, password rotation. As enterprise users change their passwords, it is possible some pick predictable, seasonal passwords such as $CompanyNameWinter , Summer2021 , etc. Specifically, this Analytic Story is focused on detecting possible Password Spraying attacks against Active Directory environments leveraging Windows Event Logs in the Account Logon and Logon/Logoff Advanced Audit Policy categories. It presents 16 detection analytics which can aid defenders in identifying instances where one source user, source host or source process attempts to authenticate against a target or targets using a high or statiscally unsual, number of unique users. A user, host or process attempting to authenticate with multiple users is not common behavior for legitimate systems and should be monitored by security teams. Possible false positive scenarios include but are not limited to vulnerability scanners, remote administration tools, multi-user systems and missconfigured systems. These should be easily spotted when first implementing the detection and addded to an allow list or lookup table. The presented detections can also be used in Threat Hunting exercises.
A home lab that simulates a password spray attack against an Active Directory domain and detects it from raw Windows authentication logs using a custom Python detection built on a sliding time window and distinct-account analysis. This project covers both sides of the engagement: running the attack (red) and building the detection that catches it (blue). I stood up a single-domain Active Directory environment, instrumented it with Windows logon auditing and Sysmon, ran a password spray against seven domain accounts, and wrote a detection that identifies the spray from the resulting failed-logon events (Windows Event ID 4625).
The detection is deliberately built around distinct accounts targeted per source within a time window , not raw failure counts. This is the difference between catching a real spray and drowning an analyst in false positives from users who simply forgot their password. Password spraying is one of the most common initial-access techniques against identity systems, and it is a pattern every SOC analyst is expected to recognise. I wanted to understand it from both ends: what the attack actually generates in the logs, and what logic reliably separates that signal from normal failed-login noise. Reading about it is not the same as watching 126 failed-logon events line up across seven accounts and then writing the rule that flags them.
Networking used a NAT adapter for internet and an isolated internal adapter ( lab-net ) so the attack traffic never touched the host network. A password spray is one common password tried across many accounts, low and slow, to stay under account-lockout thresholds. My first attempt tried multiple passwords per account, which is closer to brute force; I corrected it to a single-password sweep across all seven users, which is the accurate definition and produces a cleaner signal.
One account ( bwhite ) was seeded with a weak password present in the spray list, so the run produced the realistic worst case: a wall of failures across every account plus one successful compromise. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Cozy%20Bear • https://en.wikipedia.org/wiki/Fortinet • https://learn.microsoft.com/en-us/security/operations/incident-response-playbook-password-spray • https://www.decryptiondigest.com/blog/how-to-detect-password-spray-attacks-active-directory • https://www.decryptiondigest.com/blog/active-directory-password-spray-detection-prevention-guide • https://www.semperis.com/blog/password-spraying-detection-in-active-directory/ • https://github.com/princeudochi/Password-Spraying-Detection • https://blueteambrief.com/articles/detecting-password-spray-active-directory-t1110-003-sigma-kql-2026/ • https://github.com/RaheemC4/cyber-project-ad-detection-lab • https://research.splunk.com/stories/active_directory_password_spraying/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Password Spray Attack Detection In Active Directory.
[*] Metasploit Scan Running on Target Subnet for Password Spray Attack Detection In Active Directory... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |