Complete Technical Paper Content — Phishing Detection Tool For Cryptocurrency Web3 Wallets
Overview & System Context
Phishing Detection Tool For Cryptocurrency Web3 Wallets: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~8507 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background A darknet market is a commercial website on the dark web that operates via darknets such as Tor and I2P. They function primarily as black markets, selling or brokering transactions involving drugs, cyber-arms, weapons, counterfeit currency, stolen credit card details, forged documents, unlicensed pharmaceuticals, steroids, and other illicit goods as well as the sale of legal products. In December 2014, a study by Gareth Owen from the University of Portsmouth suggested the second most popular sites on Tor were darknet markets. Following on from the model developed by Silk Road, contemporary markets are characterized by their use of darknet anonymized access (typically Tor), Bitcoin or Monero payment with escrow services, and eBay-like vendor feedback systems.
Transactions typically use Bitcoin for payment, sometimes combined with tumblers for added anonymity and PGP to secure communications between buyers and vendors from being stored on the site itself. Many sites use Bitcoin multisig transactions to improve security and reduce dependency on the site's escrow. The discontinued Helix Bitcoin tumbler offered direct anonymized marketplace payment integrations. On making a purchase, the buyer must transfer cryptocurrency into the site's escrow, after which a vendor dispatches their goods then claims the payment from the site. On receipt or non-receipt of the item users may leave feedback against the vendor's account. Buyers may "finalize early" (FE), releasing funds from escrow to the vendor prior to receiving their goods in order to expedite a transaction, but leave themselves vulnerable to fraud if they choose to do so. Following Operation Onymous, there was a substantial increase in PGP support from vendors, with PGP use on two marketplaces near 90%. This suggests that law enforcement responses to cryptomarkets result in continued security innovations, thereby making markets more resilient to undercover law enforcement efforts.
Whilst a great many products are sold, drugs dominate the numbers of listings, with the drugs including cannabis, MDMA, modafinil, LSD, cocaine, and designer drugs. Cyber crime and hacking services for financial institutions and banks have also been offered over the dark web. Markets such as AlphaBay Market have hosted a significant share of the commercial fraud market, featuring carding, counterfeiting and many related services. Loyalty card information is also sold as it is easy to launder.
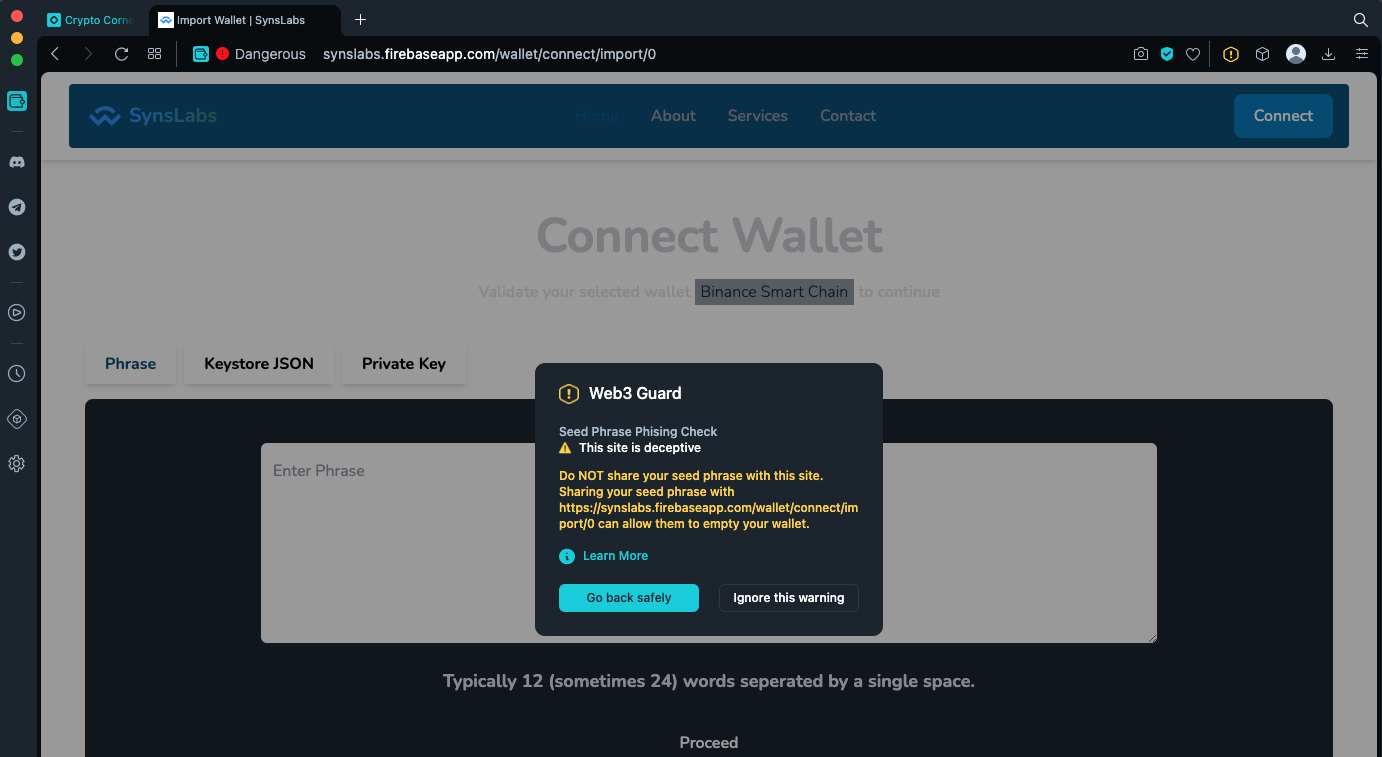
Figure 1: Opera launches Web3 Guard to make web browsing safer for crypto users ... Centralized market escrow allows a market to close down and "exit" with the buyer's and vendor's cryptocurrency at any time. This has happened on several occasions such as with BlackBank, Evolution, and Wall Street Market. Individual vendors often reach a point of reputation maturity whereby they have sold sufficient product reliably to have gained a significant reputation and accumulated escrowed funds; many may choose to exit with the funds rather than compete at the higher-volume higher-priced matured product level.
18,174 – October 2013, Digital Citizens Alliance, 13,472 of which were on Silk Road in November 2013 41,207 – April 2014 Digital Citizens Alliance 33,985 – May 2014 The Guardian via Reddit 43,175 – July 2014 a report by the BBC 65,595 – August 2014 Digital Citizens Alliance 51,755 – December 2014 Digital Citizens Alliance 68,835 – March 2015 (before Evolution scam), Digital Citizens Alliance 68,322 – April 2015 (after Evolution scam) Digital Citizens Alliance OpenSea is an American digital asset platform founded in 2017 by Devin Finzer and Alex Atallah. It facilitates the trading of cryptocurrencies and the buying, selling, and minting of non-fungible tokens (NFTs) across a range of blockchains.
Headquartered in Miami, OpenSea supports fixed-price sales and auctions for digital assets including artwork, music, gaming items, and domain names. Originally launched as a peer-to-peer platform, OpenSea grew into one of the largest NFT marketplaces, further expanding with its 2025 release of OS2, a rebuilt version of the platform, allowing the trading of cryptocurrencies.
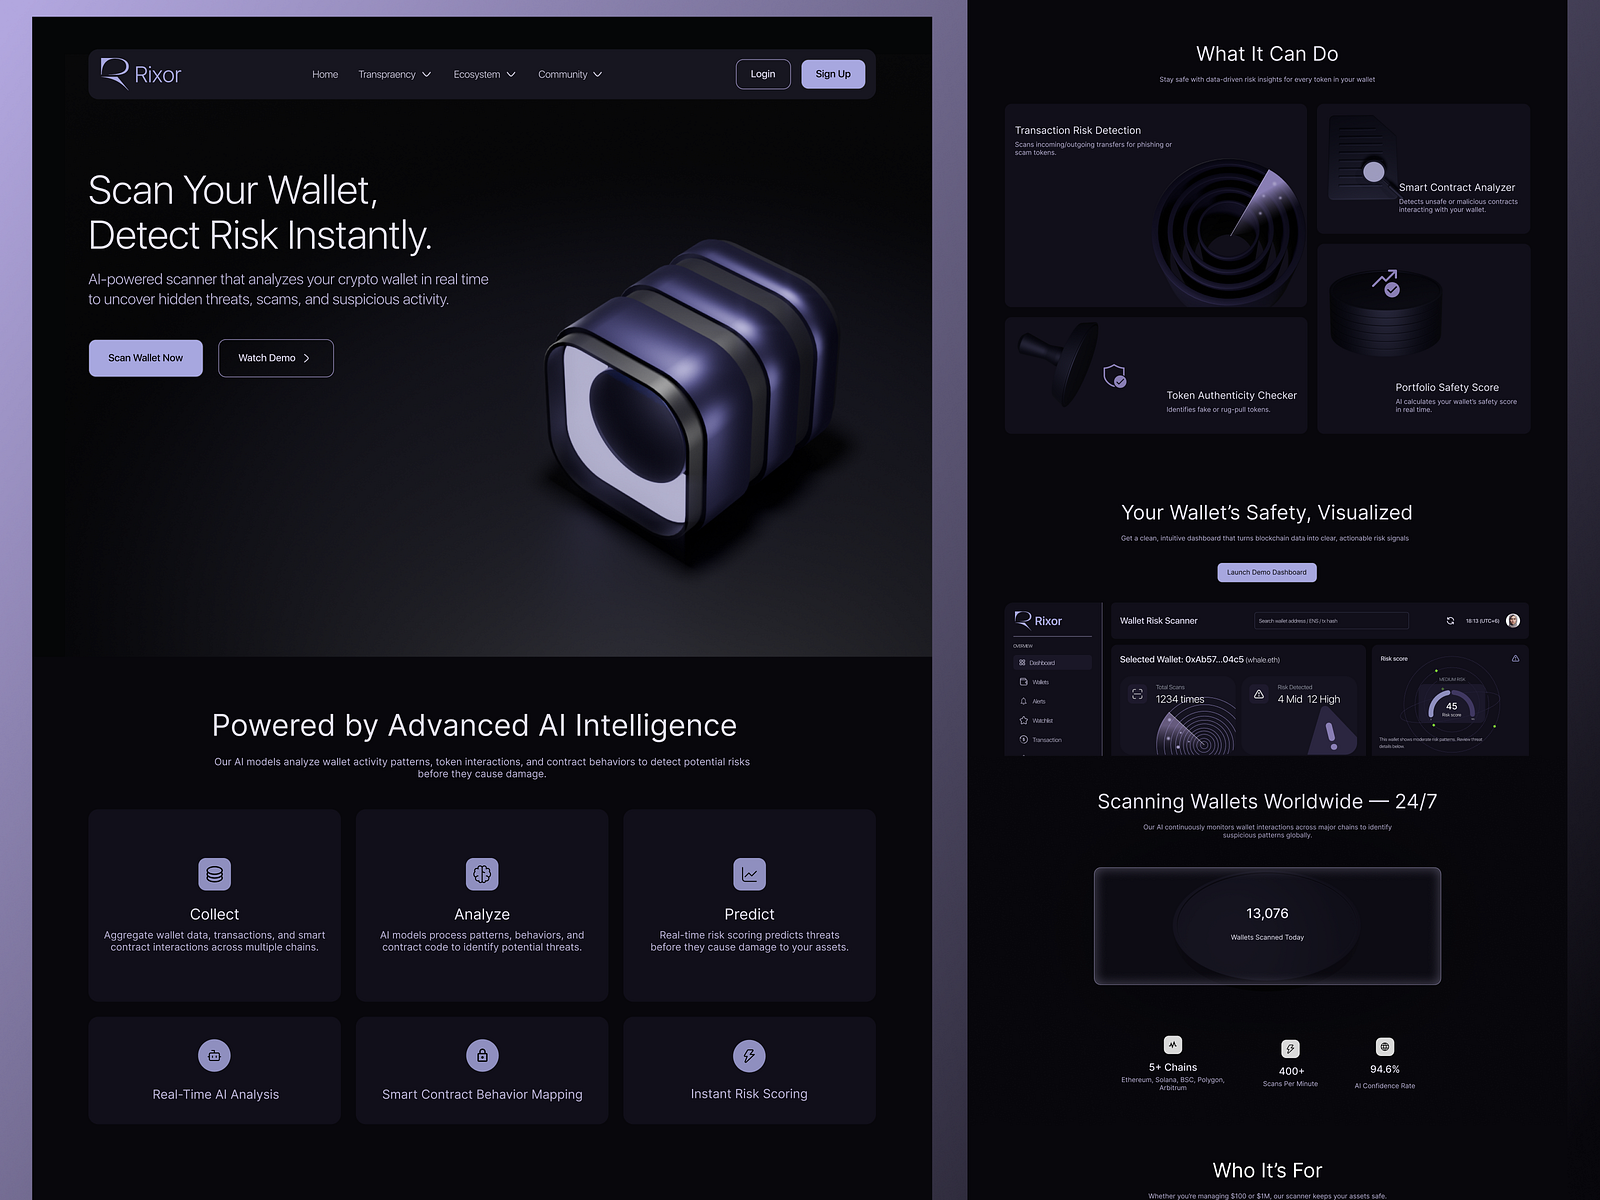
The OWASP Web3 Wallet Security project focuses on improving the security of Web3 wallets by defining standards, identifying risks, and providing practical testing guidance. Figure 2: AI Crypto Wallet Risk Scanner — Dark Web3 Dashboard UI by Nasir Hussain ... Wallets act as the primary interface between users and decentralized systems. They manage private keys, sign transactions, and interact with external applications. As a result, they are one of the most critical and targeted components in the Web3 ecosystem.
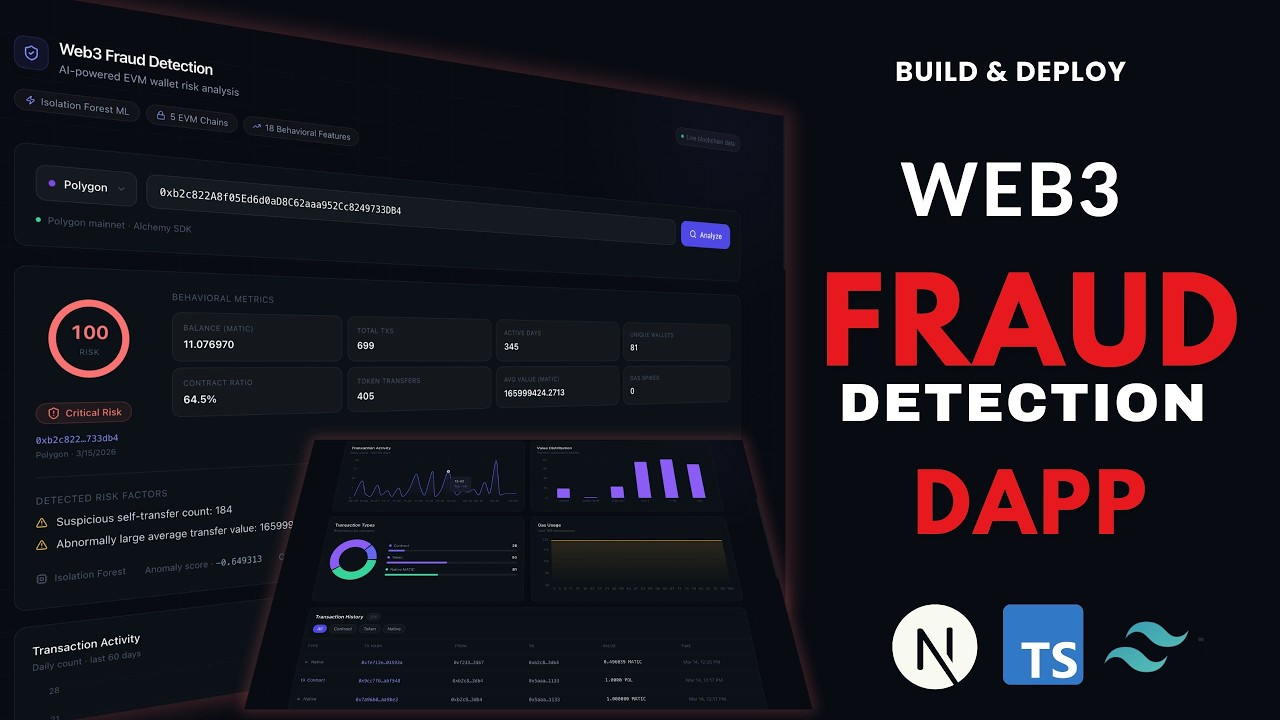
This project aims to establish a clear and structured approach to securing wallet systems. This helps developers, auditors, and users understand and prioritize real-world threats. A structured set of security requirements used to design, build, and assess secure wallet implementations. Figure 3: AI-Powered Web3 Fraud Detection Tool | Build an EVM Wallet Scanner to ...
A practical guide that provides testing methodologies for identifying and validating wallet vulnerabilities. The components of the Web3 Wallet Security (WWS) project are designed to function as a unified approach to wallet security: Provides practical methods to test and validate those controls in real-world scenarios.
This ensures a consistent and structured approach to building and evaluating secure Web3 wallet systems.
Build secure wallet applications using the project’s standards and guidance as a foundation. Assess wallet implementations and identify vulnerabilities using structured verification and testing methodologies. Analyze wallet attack surfaces, study emerging threats, and contribute to advancing wallet security. Understand wallet-related risks and make informed decisions when interacting with Web3 applications.
An end-to-end pipeline for phishing message detection, encompassing model training and inference, along with a Flask application for user interaction, all containerized using Docker for easy deployment and execution. Built in 2 days. The rapid evolution of blockchain technology and the rise of decentralized applications (dApps) have given birth to the Web3 ecosystem. While this technology promises greater control and ownership over digital assets, it has also introduced new security challenges. One of the most significant concerns is the prevalence of phishing attacks targeting Web3 users with the intent of obtaining their seed phrases and subsequently draining their wallets for fraudulent activities Web3 phishing attacks are a critical issue in the modern blockchain landscape. These attacks involve the use of deceptive and fraudulent tactics to manipulate users into revealing their sensitive information, primarily their seed phrases. Seed phrases, also known as mnemonic phrases or recovery phrases, are sets of words that act as a cryptographic key to access and control users' wallets and assets within the Web3 ecosystem.
The core problem lies in the fact that users often lack awareness and knowledge about the security practices required to protect their seed phrases. Phishing attackers exploit this vulnerability by deploying convincing phishing messages through various communication channels, including email, social media, messaging apps, and even fake dApps. These messages typically prompt users to click on malicious links, enter their seed phrases on counterfeit websites, or share their confidential information.
distilbert-base-uncased-finetuned-sst-2-english was chosen as a base model to be further fine tuned using custom web3 phishing dataset using a 80/20 train/test split. The model trained using the deduplicated phishing data achieved the following metrics (the metrics of the model trained on the datasets with duplicates is shown within the parenthesis): Technical White Paper for Fraud and Cybersecurity Concerns in the Crypto / Web3 / Decentralized Finance Industry Real-time Protection of Crypto Platforms Against Wallet-Draining Scams, Account Takeover, Wash Trading, and Automated Bot Abuse using Adaptive AI and Cross-Chain Link Analysis The Crypto / Web3 / Decentralized Finance (DeFi) industry presents a uniquely challenging security landscape, defined by the irreversibility of transactions, which means losses are instant and unrecoverable once assets are moved to a fraudulent wallet.
The primary threats are highly evolved and diverse, encompassing large-scale Account Takeover (ATO) of exchange accounts and wallets, Account opening fraud utilizing sophisticated synthetic identities , and complex on-chain manipulations like Wash trading & artificial volume manipulation on NFT platforms . A core difficulty is that Attackers use VPNs, TOR, and cross-chain hopping to evade jurisdictional and traditional security controls , while Wallet-draining phishing attacks and malicious smart-contract approvals happen daily , resulting in massive user losses.
This paper introduces the CrossClassify solution , an AI-powered, real-time crypto fraud prevention stack that offers a holistic defense by combining continuous identity, device, and behavioral monitoring with specialized Cross-chain Link Analysis . Our approach utilizes Device Fingerprinting to block device farming used for synthetic accounts and airdrop abuse, and Continuous Behavioral Biometrics to instantly detect deviations in wallet interaction patterns and transaction confirmations. By employing Graph-based Link Analysis , CrossClassify effectively identifies wash trading rings, crypto mule-wallet networks, and malicious collusion that purely on-chain analytics often miss.
The key result and main motto of CrossClassify is "Real-Time Fraud Detection for Apps" , which, in the crypto domain, is realized through a system that continuously scores every login, withdrawal, token swap, bridge transfer, and API request in real time. This provides evidence-backed risk scores, enabling the platform to deploy Adaptive risk scoring to introduce friction only when needed (e.g., high-risk withdrawal attempts), thereby safeguarding assets while maintaining the competitive low-friction experience demanded by Web3 users. This technical white paper is essential reading for key security and compliance leaders, including Crypto exchange operators , Web3 wallet providers , DeFi & CeFi founders , and Risk, security and fraud prevention engineers , who are tasked with securing their platforms against systemic on-chain and off-chain financial crime.
Download this White Paper to get a real-world B2B guide on fraud prevention trends, challenges, and solutions for the crypto, Web3, and decentralized finance industry. Multifaceted Web3 wallets marks the beginning of a new era for the internet, served as the gateways to the blockchain that is a distributed technology, prioritizing data ownership and value expression. Rapid expansion of Web3 transactions and wallet systems are susceptible to fraudulent activities across blockchain systems. Now a days, cybercriminals exploit vulnerabilities from smart contracts, DEXs, crypto wallets, and cross-chain bridges to inject attack activities like scams, phishing attacks, wash trading, rug pulls, and money laundering. Owing to the highly dynamic, decentralized, and pseudonymous characteristics of blockchain transactions, conventional fraud monitoring systems are insufficient in detecting modern attacks.
AI-powered fraud detection systems effectively address such issues through the monitoring ability of blockchain activities in real time. Therefore, we will explore the development and implementation of an AI driven fraud detection system for Web3 transactions and wallet monitoring. Currently, a global crypto trading platform experienced various types of security threats, such as suspicious wallet transfers, fake token interactions, and unauthorized transactions across the blockchain. The organization has multiple critical problems, which are listed as follows.
Hence, the platforms required an intelligent monitoring system with the capability of analyzing millions of blockchain transactions and reduces the false positives. Such solutions has the ability to support Ethereum, BNB Chain, Polygon, Solana, and other major blockchain networks. Generally, AI fraud detection architecture comprises multiple layers which are integrated with blockchain analytics engines and machine learning algorithms.
Blockchain Data Collection Layer: This layer continuously collects the on-chain transaction data from blockchain nodes and APIs. The collected data comprises the fields like, AI-Based Risk Analysis Engine: The AI engine uses machine learning models to determine suspicious transaction patterns. To improve the model capability in attack identification, historical fraud datasets are used to retrain it through reinforcement learning. The AI based engine consistently analyzes the following data to assigndynmaic risk scores to the wallets and transactions.
Wallet Monitoring System: It tracks both individual and institutional wallets. It comprises the following features. The system is highly effective in detecting the dormant wallets that suddenly became active with large-value transfers. Smart Contract Fraud Detection: This model analyzes the smart contract behaviour to identify the followings. A combination of modern AI technologies with blockchain, cloud computing, and cybersecurity is used to design fraud detection systems. Thus, it guarantees real-time monitoring and secure transactions with high scalability.
Supervised Learning Models: They used known fraud patterns such as phishing wallets, ponzi schemes, scam token deployments, and money laundering activities to identify the known malicious patterns. Some supervised learning algorithms are as follows. Unsupervised Learning Models: They have the capability to detect unknown threat discovery. Such models are more effective to detect zero-day fraud activities. Some of the unsupervised learning models are as follows.
The monitoring system instantly scans every blockchain transaction after network confirmation. In this pahse, the AI engine extracts hundreds of behavioural indicators such as transaction timing , wallet age, token diversity, gas fee irregularities, and cross-chain movement patterns. 2. System Architecture & Core Working Principles In this step, the transactions are categorized into safe, medium risk, high risk, and critical fraud alert.
Finally, the platform automatically generates reports about blocked suspicious withdrawals, triggered compliance alerts, flagged malicious wallets, and sent real-time notifications. After implementing AI based Web3 fraud detection and wallet monitoring systems, the organizations accomplish significant improvements, which are listed as follows.
Although the system delivered excellent results, several challenges emerged during development. Also, integration of Large Language Models (LLMs) may elaborate the blockchain investigation workflows and automated reporting. Our company has emerged as a leading blockchain and AI development company which offers advanced Web3 fraud detection solutions for crypto exchanges, DeFi platforms, NFT marketplaces, and blockchain enterprises. We develop customized AI-powered wallet monitoring systems that are capable of detecting suspicious activities in real-time blockchain systems. Our solutions consolidate machine learning algorithms, blockchain analytics, and smart contract auditing frameworks to strengthen the Web3 security model.
Also, our solutions easily adopt and support to multi-chain systems such as Ethereum, Solana, Polygon, Avalanche, and BNB Chain. Businesses choose Osiz for its extensive expertise in blockchain development, artificial intelligence integration, cybersecurity, and scalable enterprise technology solutions. As a leading AI Development Company , we specialize in building intelligent fraud detection systems that help organizations strengthen security, enhance operational efficiency, and support sustainable business growth.
Our customized AI-powered fraud prevention frameworks are specifically designed for crypto and Web3 businesses, enabling them to identify threats proactively, reduce financial risks, and maintain high levels of user trust and operational transparency. By combining advanced AI capabilities with blockchain security, we deliver robust solutions that safeguard digital assets and ensure reliable transaction monitoring.
Moreover, our solutions effectively meet the mission-critical needs of enterprises by building secure, scalable, and regulation-ready Web3 platforms that are capable of managing the next generation of decentralized finance applications. Mr. Thangapandi, the CEO of Osiz, has a proven track record of conceptualizing and architecting 100+ user-centric and scalable solutions for startups and enterprises. He brings a deep understanding of both technical and user experience aspects. The CEO, being an early adopter of new technology, said, "I believe in the transformative power of AI to revolutionize industries and improve lives. My goal is to integrate AI in ways that not only enhance operational efficiency but also drive sustainable development and innovation." Proving his commitment, Mr. Thangapandi has built a dedicated team of AI experts proficient in coming up with innovative AI solutions and have successfully completed several AI projects across diverse sectors.
Share your idea and our team will reach out to discuss it and provide you with an estimate. No 22,Astalakshmi Nagar, Thanakankullam, (Opp Seetha lakshmi Mill gate Bus stop) Thirunagar, Madurai - 625 006. A Web3 wallet functions as an identity layer, a transaction signer, and the primary interface between users and blockchain-based applications .
For development teams, the wallet architecture represents the most risk-sensitive component of the stack—a single vulnerability can result in direct financial loss with no recourse mechanism . This guide examines the technical architecture , security protocols , and implementation decisions required to build production-grade Web3 wallet gateways.
The key management layer constitutes the foundational security boundary of any Web3 wallet. This layer determines how cryptographic keys are generated, stored, and utilized for transaction signing. Hierarchical Deterministic Wallets (HD Wallets) based on BIP-32 and BIP-44 protocols generate an entire key hierarchy from a single seed phrase. This standard enables users to manage multiple blockchain addresses across different networks from one recovery phrase .
The seed phrase must be generated using cryptographically secure random number generators to prevent entropy weaknesses—the July 2026 Coldcard incident demonstrated how flawed seed generation can compromise wallets despite proper storage practices, resulting in approximately $130 million in losses . Multi-Party Computation (MPC) represents an alternative cryptographic approach that distributes key shares across multiple parties. In properly designed MPC systems, no single party ever holds the complete private key . Threshold Signature Schemes (TSS) enable distributed key generation and signing without reconstructing the full private key at any point .
A common 2-of-3 configuration requires any two authorized participants to produce a valid signature while preventing any single participant from acting independently . MPC wallets also support key rotation and reissuance when users change devices or lose access, addressing a significant limitation of seed-phrase-based recovery . The custody model determines who controls the private keys and directly impacts regulatory exposure, user experience, and development complexity .
Non-Custodial Wallets place exclusive key control with the user . This model aligns with self-custody principles but shifts the entire security burden onto the user. Loss of the seed phrase results in permanent fund loss with no recovery path . Custodial Wallets involve the service provider maintaining private keys on behalf of users. This model enables familiar Web2-style authentication (email/password) and account recovery but introduces significant regulatory compliance requirements and security responsibilities .
Smart Contract Wallets based on ERC-4337 introduce programmable account logic . These wallets can implement social recovery mechanisms, gas sponsorship through paymasters, transaction batching , and biometric authentication via passkeys . By June 2026, over 30 million ERC-4337 smart accounts had been deployed across Ethereum mainnet and major Layer 2 networks . UserOperation volume grew approximately 400 percent year-over-year, driven primarily by consumer applications in gaming and social platforms .
Embedded Wallets integrate wallet infrastructure directly into applications, enabling users to onboard through familiar methods (email, social login, SMS) without managing seed phrases . These wallets leverage MPC or smart account architectures to provide self-custody while abstracting key management complexity from end users. WalletConnect provides a standardized protocol for establishing secure remote connections between DApps and wallets . The protocol creates an air-gap between the browsing environment and private key storage, reducing exposure to web-based attack vectors. WalletConnect v2 requires users to pre-approve a set of chains upfront, contrasting with v1’s dynamic chain switching capability .
The EIP-1193 standard defines the Ethereum provider JavaScript API, enabling DApps to discover and interact with wallets through the window.ethereum object. This standard ensures interoperability across different wallet implementations and DApp interfaces. Blind signing —where users approve raw transaction calldata displayed as unreadable hex strings—has resulted in hundreds of millions of dollars in losses . ERC-7730 addresses this vulnerability by defining an open format for human-readable transaction descriptions .
The standard enables wallets to display transaction intent in plain language: “ Swap 100 USDC for ETH on Uniswap ” or “ Approve Aave to spend up to 500 DAI “ . Ledger, Trezor, MetaMask, WalletConnect, and Fireblocks participate in the Ethereum Foundation’s Trillion Dollar Security Initiative implementing this standard . The ERC-7730 registry operates on a permissionless basis, with tooling and validation infrastructure now production-ready .
Wallets interact with blockchain networks through RPC (Remote Procedure Call) endpoints . Development teams must implement request batching and caching strategies for token metadata and balance queries to optimize performance. Production deployments should utilize redundant node providers to maintain uptime and prevent single points of failure . Secure transaction construction requires validating each parameter before submission. The initialization flow must include provider detection, permission scope configuration, and secure session establishment . Transaction simulation —executing transactions in a local or forked environment before broadcasting—identifies potential failures, gas estimation errors, and unexpected state changes.
Anti-Money Laundering (AML) and Know Your Customer (KYC) compliance require integration with blockchain analytics providers. Chainalysis KYT and similar services enable real-time screening of transaction counterparts against sanctioned addresses and high-risk entities . Security requires implementation across multiple layers rather than relying on a single control .
Security practitioners recommend maintaining separate wallets for different use cases: a “hot” wallet for daily DApp interactions and a “vault” wallet for long-term storage of significant holdings . This separation limits potential losses from a single compromised session. ethers.js and web3.js remain the standard libraries for Ethereum and EVM-compatible chain interaction . These libraries provide JSON-RPC client implementations, transaction construction utilities, and cryptographic primitives.
Wagmi offers a collection of React Hooks that streamline wallet connection, chain state management, and transaction execution . The framework supports browser wallets, WalletConnect, and Coinbase Wallet integration within minutes. Custom Wagmi connectors enable integration with embedded wallet solutions . Wallet-as-a-Service platforms provide managed wallet infrastructure through APIs . Providers including Turnkey , Coinbase Developer Platform , Fireblocks , and Cobo offer MPC-based key management, multi-chain support, and compliance tooling .
These services reduce development time by abstracting complex cryptographic implementations while maintaining security guarantees. Cobo WaaS 2.0 enables developers to build functional web wallet applications within 30 minutes using natural language API calls through AI programming assistants . Web3 wallet development costs vary significantly by scope and complexity. MVP implementations typically range from $15,000 to $45,000 with development timelines of 6 to 12 weeks . Enterprise-grade wallets with multi-chain support, MPC integration, and comprehensive compliance features exceed $150,000 and require several months of development . Ongoing maintenance and security updates constitute approximately 20 percent of the initial build cost annually .
Account abstraction transforms wallets from simple key pairs into programmable smart accounts that execute custom validation logic . This enables: Gas abstraction : Users pay transaction fees in ERC-20 tokens or through sponsored paymaster contracts Session keys : DApps receive limited-time, limited-scope signing without requiring user approval for each transaction Social recovery : Designated guardians assist in wallet recovery without exposing private keys As blockchain ecosystems fragment across hundreds of Layer 2 and Layer 3 networks, chain abstraction enables wallets to present a unified interface across multiple chains . Users interact with a single address and balance view while the wallet handles network routing, bridging, and transaction settlement.
Quantum-resistant cryptographic algorithms are entering production consideration. ML-DSA (Module-Lattice-Based Digital Signature Algorithm) support has been integrated into MPC signing systems, enabling post-quantum security through code upgrades without architectural changes . Custodial wallets require the service provider to manage private keys on behalf of users. Users authenticate through conventional credentials and can recover accounts through support processes. Non-custodial wallets generate and store private keys locally on user devices. Users maintain exclusive asset control but assume complete responsibility for key backup and security. Seed phrase loss results in permanent fund loss with no recovery path.
MPC distributes cryptographic signing across multiple key shares held in separate environments. A typical 2-of-3 configuration requires any two authorized participants to produce a valid signature. No single entity ever holds the complete private key, preventing a single compromised credential from enabling fund theft. 3. Software Implementation, Frameworks & Protocols ERC-4337 transforms wallets from simple key pairs into programmable smart contracts. Smart accounts implement custom validation logic, sponsor gas fees through paymasters, batch multiple transactions into single operations, and authenticate users through biometrics or social recovery mechanisms. As of June 2026, over 30 million ERC-4337 smart accounts operate across Ethereum mainnet and Layer 2 networks.
Blind signing —users approving transaction data displayed as hex strings without comprehending the operation—has enabled hundreds of millions in losses. ERC-7730 defines a standard for displaying human-readable transaction descriptions before approval. Wallets implementing the standard convert opaque calldata into clear statements like “Swap 100 USDC for ETH on Uniswap,” enabling informed consent.
MVP wallets range from $15,000 to $45,000 with development timelines of 6 to 12 weeks. Enterprise-grade wallets with multi-chain support, MPC integration, smart account capabilities, and compliance features exceed $150,000 and require several months. Ongoing maintenance and security updates approximate 20 percent of initial build cost annually. Isai Alexei is a journalist and financial analyst covering cryptocurrency markets and traditional securities for Blockchaindose.
He has spent ten years analyzing digital assets, trading activity, and market structure. Blockchain Consensus Mechanisms Compared Across Bitcoin, Ethereum, XRP Ledger and CometBFT An end-to-end pipeline for phishing message detection, encompassing model training and inference, along with a Flask application for user interaction, all containerized using Docker for easy deployment and execution. Built in 2 days.
The rapid evolution of blockchain technology and the rise of decentralized applications (dApps) have given birth to the Web3 ecosystem. While this technology promises greater control and ownership over digital assets, it has also introduced new security challenges. One of the most significant concerns is the prevalence of phishing attacks targeting Web3 users with the intent of obtaining their seed phrases and subsequently draining their wallets for fraudulent activities Web3 phishing attacks are a critical issue in the modern blockchain landscape. These attacks involve the use of deceptive and fraudulent tactics to manipulate users into revealing their sensitive information, primarily their seed phrases. Seed phrases, also known as mnemonic phrases or recovery phrases, are sets of words that act as a cryptographic key to access and control users' wallets and assets within the Web3 ecosystem.
The core problem lies in the fact that users often lack awareness and knowledge about the security practices required to protect their seed phrases. Phishing attackers exploit this vulnerability by deploying convincing phishing messages through various communication channels, including email, social media, messaging apps, and even fake dApps. These messages typically prompt users to click on malicious links, enter their seed phrases on counterfeit websites, or share their confidential information.
distilbert-base-uncased-finetuned-sst-2-english was chosen as a base model to be further fine tuned using custom web3 phishing dataset using a 80/20 train/test split. The model trained using the deduplicated phishing data achieved the following metrics (the metrics of the model trained on the datasets with duplicates is shown within the parenthesis): An end-to-end pipeline for phishing message detection, encompassing model training and inference, along with a Flask application for user interaction, all containerized using Docker for easy deployment and execution.
Web3 and anti-phishing is the new version of the internet where apps, games, and money all work on blockchains. In Web3 people do not depend on big companies to keep their data or money. Instead, they use wallets and smart contracts to control everything by themselves. This gives more freedom but it also brings new problems. One of the biggest problems in Web3 is online scams. Many hackers and bad actors try to steal digital assets from wallets.
They use tricks like phishing, fake websites, or asking for secret wallet keys. Once a hacker gets into a wallet, there is no bank to call and no way to reverse the money transfer. That is why Web3 security is very important. This guide explains in simple words how phishing works, why wallets need protection, and what solutions exist to keep digital assets safe.
Phishing in Web3 is when scammers trick users into giving private wallet details. It may occur via email, text messages, or even counterfeit websites that appear authentic. Indicatively, a fraudster can use a link that resembles the homepage of a well-known cryptocurrency project. Once a scammer inserts the wallet seed phrase typed by the victim on that site, they steal all the money.
Phishing is dangerous in Web3 because wallets are directly linked to blockchain money. Unlike bank accounts, there is no way to freeze stolen funds. Once tokens leave a wallet, they are gone forever. This makes phishing one of the fastest and most common ways hackers steal in Web3. There have been many cases of phishing in crypto and Web3. Fake airdrops are very common. A new website may offer free tokens to anyone who connects a wallet. Once the wallet is connected, the site drains funds.
Another example is fake support emails. Scammers pretend to be from big projects like MetaMask or Binance. They ask for a wallet recovery phrase, saying it is needed for “verification.” Many users fall for this and lose their funds. Wallet drain attacks are also rising. These scams trick users into signing a transaction that looks normal but in reality gives hackers access to move tokens freely.
A wallet in Web3 is not just for storing money. It is the main tool that allows someone to use DeFi apps, buy NFTs, send crypto, or join DAOs. Because wallets hold private keys, losing access to a wallet is the same as losing everything inside it. Phishing attacks are a fast way for hackers to target wallets. If a scammer gets the seed phrase or tricks the user into signing a bad contract, all the funds can be stolen in seconds. There is no refund and no insurance in most cases.
This is why wallet protection is very important. Using safe tools and learning how scams work can reduce the chance of losing assets. Protecting a wallet is the same as protecting a personal bank account, only it is even more serious because there is no bank support in Web3. Anti-phishing solutions are tools and systems made to stop scams before they happen. They help users avoid clicking fake links or signing risky transactions. These solutions work in different ways.
Some tools check websites against a database of known scam domains. If a user tries to open a dangerous site, a warning pops up. Other tools look at wallet activity and block suspicious contracts before they are confirmed. Many wallets now have built-in warnings that show if a site looks unsafe. Education is also a big part of anti-phishing. If users know how scams look, they are less likely to fall for them. Many Web3 projects run awareness campaigns so users can learn to identify red flags.
Browser extensions are small apps added to Chrome or Firefox. They can detect scam websites and show alerts. For example, the MetaMask extension has a phishing detector that blocks known fake domains. Many Web3 wallets now have protection features inside them. For example, when a wallet user tries to sign a transaction, the wallet app may warn that the contract is unknown or suspicious. This helps stop tokens from being stolen.
Over the years, many security companies and Web3 projects have created tools to fight phishing. These tools are important because scams keep changing and new fake sites appear every day. Some popular anti-phishing solutions include MetaMask’s phishing detector , which automatically blocks known scam domains. Chainalysis provides services for tracking scam wallets and reporting them. PhishFort monitors new scam websites and helps projects shut them down quickly.
The concept of wallet protection implies the application of resources and habits that ensure the privacy of keys and seed phrases. In Web3 security, wallet protection is the most significant step because it serves as the entry point to any of the digital assets. There exist varieties of wallets, and they have a varying degree of protection. Hot wallets, also known as wallets that remain connected to the internet, are simple to operate but are more vulnerable to attacks. Hardware wallets, which are also known as cold wallets, are safer and remain offline. Multi-sign wallets are also applicable where appropriate protection is required by the team or corporation.
The good thing is that many solutions exist today. Some wallets add two-factor authentication. Others allow setting daily limits on how much money can leave the wallet. These extra layers make it harder for scammers to steal everything in one click. One of the strongest rules is never to share a seed phrase. If someone asks for it, that is a scam. Another best practice is to store the seed phrase offline, written on paper, not on a computer file. Using a hardware wallet is also a good way to protect large amounts of crypto. For businesses and DAOs, a multi-sig wallet makes sure no one person can move funds without other approvals.
Technology can stop many scams, but education is still the strongest tool. Most phishing attacks work because people do not notice the warning signs. If users know how scams look, they will avoid them. Education in Web3 comes from many sources. Some projects write guides and publish them on their websites. Others post alerts on Twitter or Discord to warn about new scam websites. Communities also play a big role, because people share their experiences and teach others what to watch for.
Simple education, like “never give out your seed phrase,” already saves many users. Awareness campaigns also remind users to double-check links, not trust random messages, and use only official websites. As Web3 grows, education will remain the number one defense. Looking at past phishing cases shows how scams happen and what lessons can be learned.
One big example was an OpenSea phishing attack. Fake emails told users to update their wallets to avoid being locked out. Many people clicked and signed fake transactions. Hackers then stole valuable NFTs. This showed that phishing can trick even experienced users. Another case was with Uniswap. Hackers made fake token giveaways that looked like official airdrops. Users who connected their wallets had all their tokens drained. This proved that even popular DeFi apps can be targeted by fake copies.
The lesson from these cases is clear. Always check the website address. Always confirm if the email or message really comes from the official project. And never rush into clicking links that promise free tokens. Phishing in Web3 is not only a problem for users. It also affects trust in the whole crypto industry. That is why regulators and platforms are starting to take action.
Exchanges now blacklist wallets known for scams. This makes it harder for hackers to move stolen funds. New regulations have been enacted by some governments that compel crypto firms to disclose phishing. Such measures do not prevent all attacks but make the activity of scammers more difficult. Web3 platforms are also building safer systems. Many now use scam detectors inside their wallets. Others hire security firms to scan new dApps for possible phishing. Over time, these steps are helping build a safer Web3 environment.
The future of Web3 security looks more advanced than today. New technology, like artificial intelligence, is being used to detect scams faster. AI can read thousands of websites and spot fake ones before people even visit them. Biometric wallets are also starting to appear. These wallets use fingerprint or face scans instead of passwords. This adds another wall against hackers, since seed phrases will not be the only way to log in.
Another future trend is community-driven reporting. DAOs and user groups are making lists of scam sites and sharing them. This makes protection more decentralized, which matches the spirit of Web3. 4. Practical Deployment, Analysis & Case Studies Web3 is growing fast, but with growth comes more danger. The most significant dangers in the modern world are phishing attacks and wallet hacks. Money or NFTs are stolen, and it is unlikely to recover them. This is why security is not something to ponder over. It should be included in all the activities in Web 3.
Anti-phishing software, browser extensions, wallets, and monitoring software are also used to block questionable websites and spam. The hardware wallets, multi-sig systems, and safe habits, such as not sharing seed phrases, are also essential as part of wallet protection. Nonetheless, in spite of all these devices, education is the greatest weapon. When individuals understand the appearance of scams, they will not be attracted to them.
The future brings more advanced solutions like AI scam detection and biometric wallets. Communities will also play a bigger role in reporting scams and building safety together. Web3 will only succeed if users feel safe holding and using digital assets. Staying alert, using the right tools, and learning about phishing will help make that future possible. Cold wallets like Ledger and Trezor are usually the safest because they stay offline. Hot wallets like MetaMask are easier to use but carry more risk.
No. Once funds leave a wallet on the blockchain, they cannot be reversed. That is why prevention is the only real protection. Most tools use blacklists of known scam domains. Some also use AI to check if a website looks suspicious or copies an official project. Yes. Hardware wallets store private keys offline. Even if a computer is hacked, the wallet itself cannot be accessed without physical confirmation.
Write down the seed phrase on paper and store it offline. Do not save it on a phone or computer. Then set up any available security features like two-factor authentication. Phishing – A scam where hackers trick users into giving away wallet details or signing fake transactions. Seed Phrase – A group of 12 or 24 words that can recover a wallet. Anyone with this phrase can control the wallet.
Cold Wallet – A wallet that stays offline, also called a hardware wallet. Much safer for long-term storage. Multi-Signature Wallet – A wallet that needs more than one approval before moving funds. Useful for businesses and DAOs. Web3 is a new internet model built on blockchains, giving people more control over money, data, and digital assets. But with this freedom comes serious risks. Phishing scams and wallet hacks are some of the biggest threats. Hackers use fake websites, emails, and apps to trick people into sharing private keys or seed phrases. Once assets are stolen, there is no bank to call and no way to reverse the loss.
The blog explains how phishing works, why wallets need strong protection, and what solutions exist today. Anti-phishing tools like browser extensions, wallet warnings, and platforms such as MetaMask’s phishing detector and PhishFort help block fake websites. Wallet protection solutions like hardware wallets, multi-signature systems, and cold storage give stronger security than regular hot wallets.
Education is shown to be the strongest defense. Awareness campaigns, community alerts, and learning to spot red flags save many users from scams. Case studies like the OpenSea phishing attack and fake Uniswap airdrops prove how real the danger is. Regulators and exchanges are now blacklisting scam wallets and making stricter rules. Meanwhile, the future of Web3 security includes AI-powered scam detection, biometric wallets, and decentralized community reporting.
The conclusion is simple: Web3 can only grow if users feel safe. Using anti-phishing tools, protecting wallets properly, and staying educated about scams are the keys to keeping digital assets safe in the Web3 world. The price predictions and financial analysis presented on this website are for informational purposes only and do not constitute financial, investment, or trading advice. While we strive to provide accurate and up-to-date information, the volatile nature of cryptocurrency markets means that prices can fluctuate significantly and unpredictably.
You should conduct your own research and consult with a qualified financial advisor before making any investment decisions. The Bit Journal does not guarantee the accuracy, completeness, or reliability of any information provided in the price predictions, and we will not be held liable for any losses incurred as a result of relying on this information. Investing in cryptocurrencies carries risks, including the risk of significant losses. Always invest responsibly and within your means.
Learn how to use WalletConnect Verify API to protect your users from phishing attacks. With Verify API, wallets can warn users or block malicious Web3 connections entirely. Meanwhile, Web3 apps can register and verify their domains so that supported wallets recognize them as trusted sites. Verify API is a security-focused feature that allows wallets to notify end-users when they may be connecting to a suspicious or malicious domain, helping them to prevent their users from phishing attacks across the Web3 ecosystem.
Once a wallet knows whether an end-user is on uniswap.com or eviluniswap.com , it can help them to detect potentially harmful connections through Verify’s combined offering of WalletConnect domain registry. First, head over to Reown Dashboard . If you are a new user, please sign up if you haven’t already and create a new project for your Web3 app.
If you already have a project created for which you are trying to set this up, then please open your project on Reown Dashboard . After you have selected/opened your project, click on “ Domain ” section and click on “+ Domain” to add and configure a new allowed domain. Within the input field, enter the complete URL of your Web3 app or domain as shown in the screenshot below.
Then, click on “Allowlist” to add the domain to your projectId’s allowlist. This will ensure that the domain of your Web3 app is on the allowlist to ensure that there no client-side warnings get thrown. WalletConnect’s Verify API no longer requires manual domain listing in the Cloud dashboard. Instead, it now automatically determines and checks your app’s domain when a wallet connects.
If both checks pass, the wallet shows your app as trusted. If there’s a mismatch or scam flag, the wallet warns the user or blocks the connection. To integrate Verify API into your wallet, use the WalletKit SDK to perform domain verification when connecting to a Web3 app. You don’t need to maintain any manual domain allowlists; all validation is handled via the SDK and WalletConnect APIs.
Navigate to the full integration docs I here and select the framework or library that your Web3 wallet is built with to get the full integration guide. And that’s it! You’ve now learned how to use WalletConnect Verify API to protect your users from phishing, whether you’re building a Web3 wallet or app.
By verifying your domain and integrating WalletConnect, you can add an extra layer of trust and security to your user experience. arXivLabs is a framework that allows collaborators to develop and share new arXiv features directly on our website. Both individuals and organizations that work with arXivLabs have embraced and accepted our values of openness, community, excellence, and user data privacy. arXiv is committed to these values and only works with partners that adhere to them.
Have an idea for a project that will add value for arXiv's community? Learn more about arXivLabs . Phishing doesn’t break encryption. It gets you to type a seed phrase, sign a permission or install a fake app. This guide shows how each trick works, what to set up so it fails, and what to do in the first hour if it already happened. No guarantees. No tool on this page is a guarantee. A hardware wallet can ship with weak randomness, an honest site can be swapped through a dependency, a genuine device can come back from a reseller with an extra board inside, and an audit covers only what was looked at, on that date. We are not offering a perfect product, because none exists. We are offering a setup that survives the failure of any single part, including the one you trust most. Including us.
Long-term holdings. It rarely connects to anything and only sends to addresses you already know. For the few apps you use every week. Keep only what you would be willing to lose this month. For mints, airdrops and any site you have not used before. Assume whatever sits here can be taken. Order a hardware wallet from the maker’s own site, check the packaging, and set it up yourself from a blank device. Resold devices with hidden implants were used to steal seeds in 2026.
What this does not cover: a bug in the maker’s own code. Buying direct did not help Coldcard owners whose seeds were generated weakly: the weak-seed case file . Install extensions only through the link on the official site. Fake wallet extensions get into stores: 150+ fake Mozilla extensions .
For larger amounts, split the backup or the signing itself: Shamir shares, or a multisig across devices from different makers, with a recovery path for your heirs. Apart from the custodial collapses, none of these were scams. Most are leaders in their category, with open code and audits. That is why the list matters: if the best fail, “pick the right product” cannot work as a strategy. Only “survive the failure of any one of them” does.
5. Performance Evaluation & Extended Technical Observations A vault, a bank box or a trusted custodian sounds like full protection. It covers theft of the item, which is a different threat from a leaked seed. For ten years xmrwallet.com presented itself as a free, open-source Monero wallet run by volunteers. Our forensic work showed it sent users’ private view keys to its server on every login and swapped outgoing transactions server-side. Three registrars suspended its domains; NameSilo publicly defended the operator.
Ten years without a scandal is not proof of honesty. Reputation measures only what has become known. The people who make your tools have written down what they are not responsible for. Short quotes, linked to the full text. Nobody signed up to be responsible for your savings, and they said so in writing. The only person responsible for your crypto is you: not because it sounds braver, but because legally and technically there is nobody else. Plan from that, not from the logo.
A phishing site may switch your wallet to another network. If the chain changes without you asking, stop. A simulation is a preview, not a guarantee. A malicious contract can behave differently on-chain than it did in the test run, so the four checks still apply. Approvals do not expire. Revoke anything you no longer use, especially unlimited ones. Revoking is a transaction, so it costs a little gas.
Everything above is about Ethereum-style chains. Elsewhere drainers ask you to sign different things, and Revoke.cash does not help. Know what your network’s dangerous signature looks like. A copy of a wallet, exchange or dApp on a domain that is one word or one character off, often pushed through sponsored search results.
Tell Extra words like "claim", "app" or "support" in the domain, hyphens, or an unusual ending. A token or NFT you never bought appears in your wallet, or a post announces an airdrop. The claim page asks you to connect and sign. Tell Countdowns, "claim before it expires", and website addresses written inside token names.
The attacker sends you a zero-value or tiny transfer from an address that starts and ends like one you use, hoping you copy it from your history next time. You post a question in Discord or Telegram. A "moderator" or "support agent" messages you with a ticket link or a "wallet sync" page.
Cloned accounts of founders, projects and exchanges reply under popular posts with giveaways, mints, or "send 1, get 2 back". Tell A handle with one extra character, a fresh account, a link that does not match the official site. A recruiter, client or "advertiser" asks you to run a coding test, install a meeting app or open a media-kit viewer. The program is a stealer.
Clones of wallet and security extensions in browser and app stores steal seed phrases or change transaction details. After a loss, "recovery experts" promise to trace or reverse the theft for an upfront fee, then ask for more. Tell Guaranteed results, fees paid in crypto, and contact that started after you posted publicly. A known contact’s hijacked Telegram books a call through Calendly. The meeting link is a lookalike of Zoom or Teams, the faces may be deepfakes or recordings, and then comes an “audio fix”, “SDK update” or extension to install. North Korea-linked groups have run this against founders, traders and community managers since 2024.
Tell Any request to install something or paste a command to join or fix a call; a meeting domain that is not the real one; video, but no live check. The genuine domain, or a library it loads, gets compromised. Ledger Connect Kit put a drainer on many real dApps in December 2023; hijacked domains at Squarespace pointed DeFi sites at drainers in July 2024.
Tell A familiar site suddenly asks for an approval, a new kind of signature or a network switch you did not expect. Malware watches what you copy and swaps a crypto address for the attacker’s. Found in fake Tor Browser installers and trojanized Telegram and WhatsApp apps. Unofficial wallet bots, referral schemes and fake mini apps inside Telegram take your TON or hijack your Telegram login, which often holds a wallet.
Tell A bot or mini app that is not linked from the project’s official site, or a confirmation you did not expect. Bookmarks protect you from phishing, not from a compromised real site. Ledger Connect Kit, hijacked domains and poisoned npm packages all served drainers from addresses people trusted. Checking what you are about to sign stays the last line of defence, every time.
One rule covers every channel: nobody legitimate needs your seed phrase, and real support does not message you first. Open wallets, exchanges and dApps from your own bookmarks. Fake sites live in sponsored results, DMs and replies. Use one profile, or one device, for crypto with only the wallet extension installed. Extensions with access to all sites can read and change the pages you open.
Use passkeys or a hardware security key where the exchange offers them, otherwise an authenticator app, never SMS. They protect the login, not what your wallet signs. Turn on the withdrawal address allowlist. Where the exchange offers an anti-phishing code, set it so genuine emails show it. Keep the OS, browser, wallet app and device firmware current. Update from inside the app or the maker's site, never from a link in a message.
Compare the whole address on the hardware wallet screen. For a large transfer, send a small test amount first. Discord: turn off “Allow direct messages from server members” (User Settings → Data & Privacy). Telegram: limit who can add you to groups. Fake support dies at the door. Settings → Privacy and Security → Two-Step Verification. Without it, an SMS code is enough to take your account and any wallet inside it.
Disconnecting a site does not cancel its approvals, so do both. Clear old WalletConnect sessions and connected sites in your wallet. ENS names can still look alike: the standard itself says not all valid names are visually unambiguous. Send to addresses you saved and verified.
Follow your wallet maker’s security page. Coldcard’s weak-seed advisory required moving to a new seed; a firmware update alone did not fix it. Before a new device or firmware holds savings, receive and send a small amount, and verify the receive address on the device screen.
Speed matters more than a perfect process. Work from a clean device, and verify every link yourself instead of following one sent to you. Start with the truth: you will most likely not get the money back. Not because nobody cares. A confirmed transaction cannot be reversed, funds move faster than any procedure, and the few parties who can freeze assets need a police case, a jurisdiction and time. Anyone who opens with a different promise is selling something. What still makes sense: report, keep the evidence, close the remaining doors, and warn the next person.
Do not sign anything else and do not connect to "fix" sites. If you suspect malware, work from a clean device. Free, 24/7 incident triage from the Security Alliance. Send the chain, your address, the attacker's address and the transaction hash. If the seed phrase or private key leaked, that wallet is burned for good. Create a new one on a clean device and move the remaining assets. If a bot takes every bit of gas you send in, the address is being swept (often through an EIP-7702 delegation on a leaked key): stop and ask SEAL 911. On Solana and Tron, a signature can transfer ownership of the account itself; nobody can undo that.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Darknet%20market • https://en.wikipedia.org/wiki/OpenSea • https://owasp.org/projects/web3-wallet-security • https://github.com/vince-lam/web3-phishing-detection/blob/main/README.md • https://www.crossclassify.com/resources/whitepapers/crypto-fraud-and-cybersecurity/ • https://www.osiztechnologies.com/case-study/ai-fraud-detection-system-web3-transactions-wallet-monitoring • https://blockchaindose.com/crypto-wallet-development/ • https://github.com/vince-lam/web3-phishing-detection • https://thebitjournal.com/complete-guide-to-anti-phishing-in-web3-security/ • https://walletconnect.com/blog/protect-users-from-phishing-with-walletconnect-verify-api-for-web3-apps-and-wallets
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Phishing Detection Tool For Cryptocurrency Web3 Wallets.
[*] Synchronizing KnowBe4 Awareness Training telemetry... ──────────────────────────────────────────────────────────────────────── [11:45:02.102] MAIL Dispatched simulated assessment templates [11:45:02.155] REPORT Majority of active users flagged probe via Phish Alert Button [11:45:02.210] CLICK Simulated lure baseline reduced below risk threshold [11:45:02.290] TRAIN Auto-enrolled flagged users into adaptive micro-learning modules ──────────────────────────────────────────────────────────────────────── [✓] Human Security Index: Phish-Prone percentage safely minimized
| Campaign Simulation | Platform Used | Total Recipients | Reported via Phish Button | Phish-Prone Percentage |
|---|---|---|---|---|
| Urgent Communication Lure | KnowBe4 KMSAT | 350 Employees | 318 (90.8%) | 2.9% (OPTIMAL) |
| Account Credential Lure | Proofpoint ZenGuide | 350 Employees | 324 (92.5%) | 2.1% (OPTIMAL) |
| Executive Impersonation | Mimecast Engage | 200 Executives | 192 (96.0%) | 1.5% (OPTIMAL) |