Complete Technical Paper Content — Physical Unclonable Function Based Device Authentication
Overview & System Context
Physical Unclonable Function Based Device Authentication: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~4211 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background In computing and cryptography, a physical unclonable function or PUF is a physical object whose operation cannot be reproduced ("cloned") in a physical way (by making another system using the same technology), such that for a given input and conditions (challenge), provides a physically defined "digital fingerprint" output (response) that serves as a unique identifier—most often for a semiconductor device such as a microprocessor or a material producing an optical signal. PUFs are often based on unique physical variations occurring naturally during semiconductor manufacturing. A PUF is a physical entity embodied in a physical structure. PUFs can be implemented in integrated circuits, including FPGAs, and can be used in applications with high-security requirements, more specifically cryptography, Internet of things (IOT) devices and privacy protection. The term is also commonly expanded as a physically unclonable function in the academic literature.
Explicit PUF randomness is created explicitly in a separate technological operation. It is a disadvantage because a separate operation imposes additional costs and because manufacturer can intentionally replace that separate operation with something else, which can reduce randomness and compromise security characteristics. Implicit PUF uses technology imperfections as a source of randomness by designing a PUF as a device which operation is strongly affected by technology imperfections instead of being unaffected, as it is done for usual circuitry, and fabricating it simultaneously with the rest of the device. Since foundries themselves cannot defeat the imperfections of the technology despite having strong economic incentive in being capable to fabricate more performant and more reliable chips, it gives some protection from foundry backdooring such PUFs this way. Backdooring PUFs by tampering with lithographic masks can be detected by reverse engineering the resulting devices. Fabricating the PUF as the part of the rest of the device makes it cheaper than explicit PUFs.
Over 40 types of PUF have been suggested. These range from PUFs that evaluate an intrinsic element of a pre-existing integrated electronic system to concepts that involve explicitly introducing random particle distributions to the surface of physical objects for authentication. All PUFs are subject to environmental variations such as temperature, supply voltage and electromagnetic interference, which can affect their performance. Therefore, rather than just being random, the real power of a PUF is its ability to be different between devices but simultaneously to be the same under different environmental conditions on the same device.
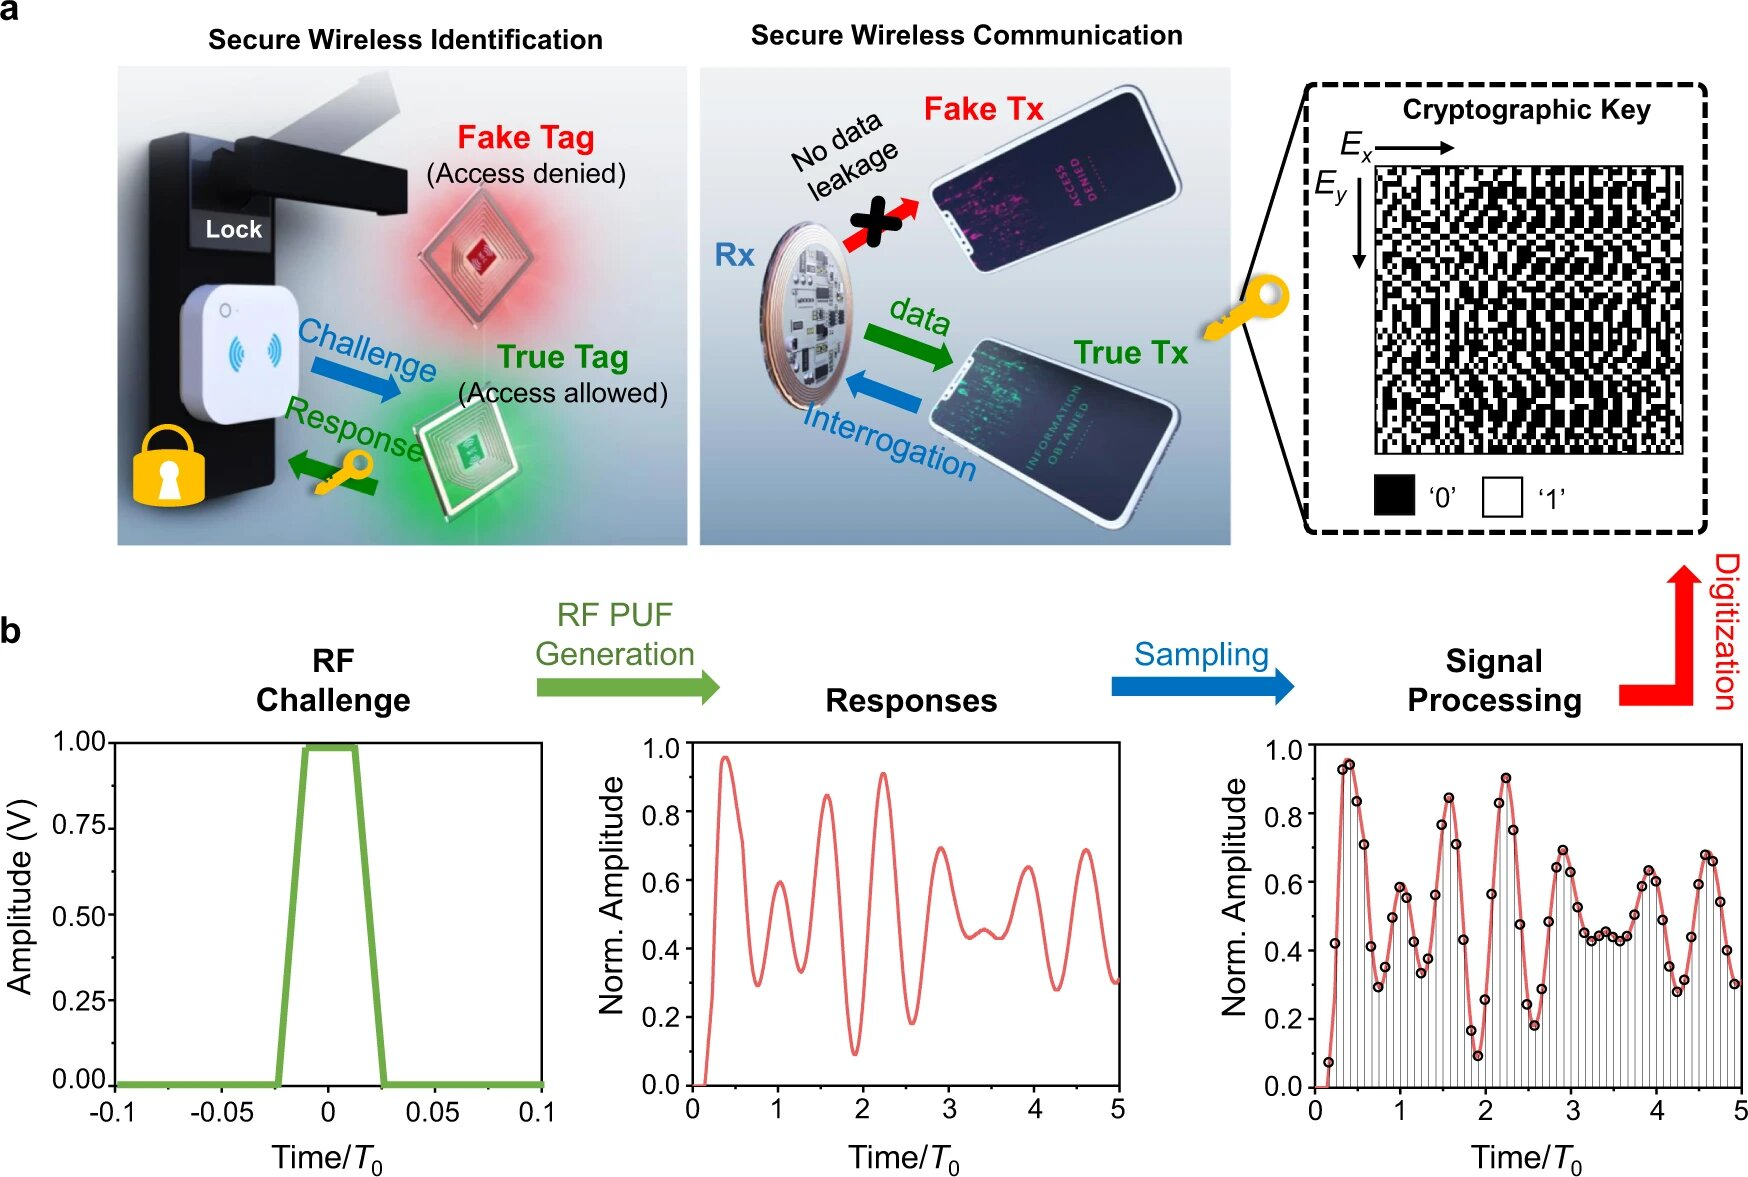
f H D ( A , B ) = 1 a b ∑ I = 1 a ∑ J = 1 b ( A ⊕ B ) I J {\displaystyle fHD(A,B)={\frac {1}{ab}}\sum _{I=1}^{a}\sum _{J=1}^{b}(A\oplus B)_{IJ}} Figure 1: Using quantum physics to secure wireless devices where A and B are binary arrays representing two responses, a and b are the dimensions of these arrays, and ⊕ denotes the bitwise XOR operation. The summation is carried out over all pixel positions I (1, 2, ..., a) and J (1, 2, ..., b) in the arrays. The result gives a normalized measure of similarity between the two arrays, ranging from 0 (identical) to 1 (completely different). In practice, the fHD is often applied to sets of responses. For example, in intra-PUF reliability analysis, the fHD is calculated across repeated measurements (the 'C' set), and the mean value of the fHD is reported as the reliability value.
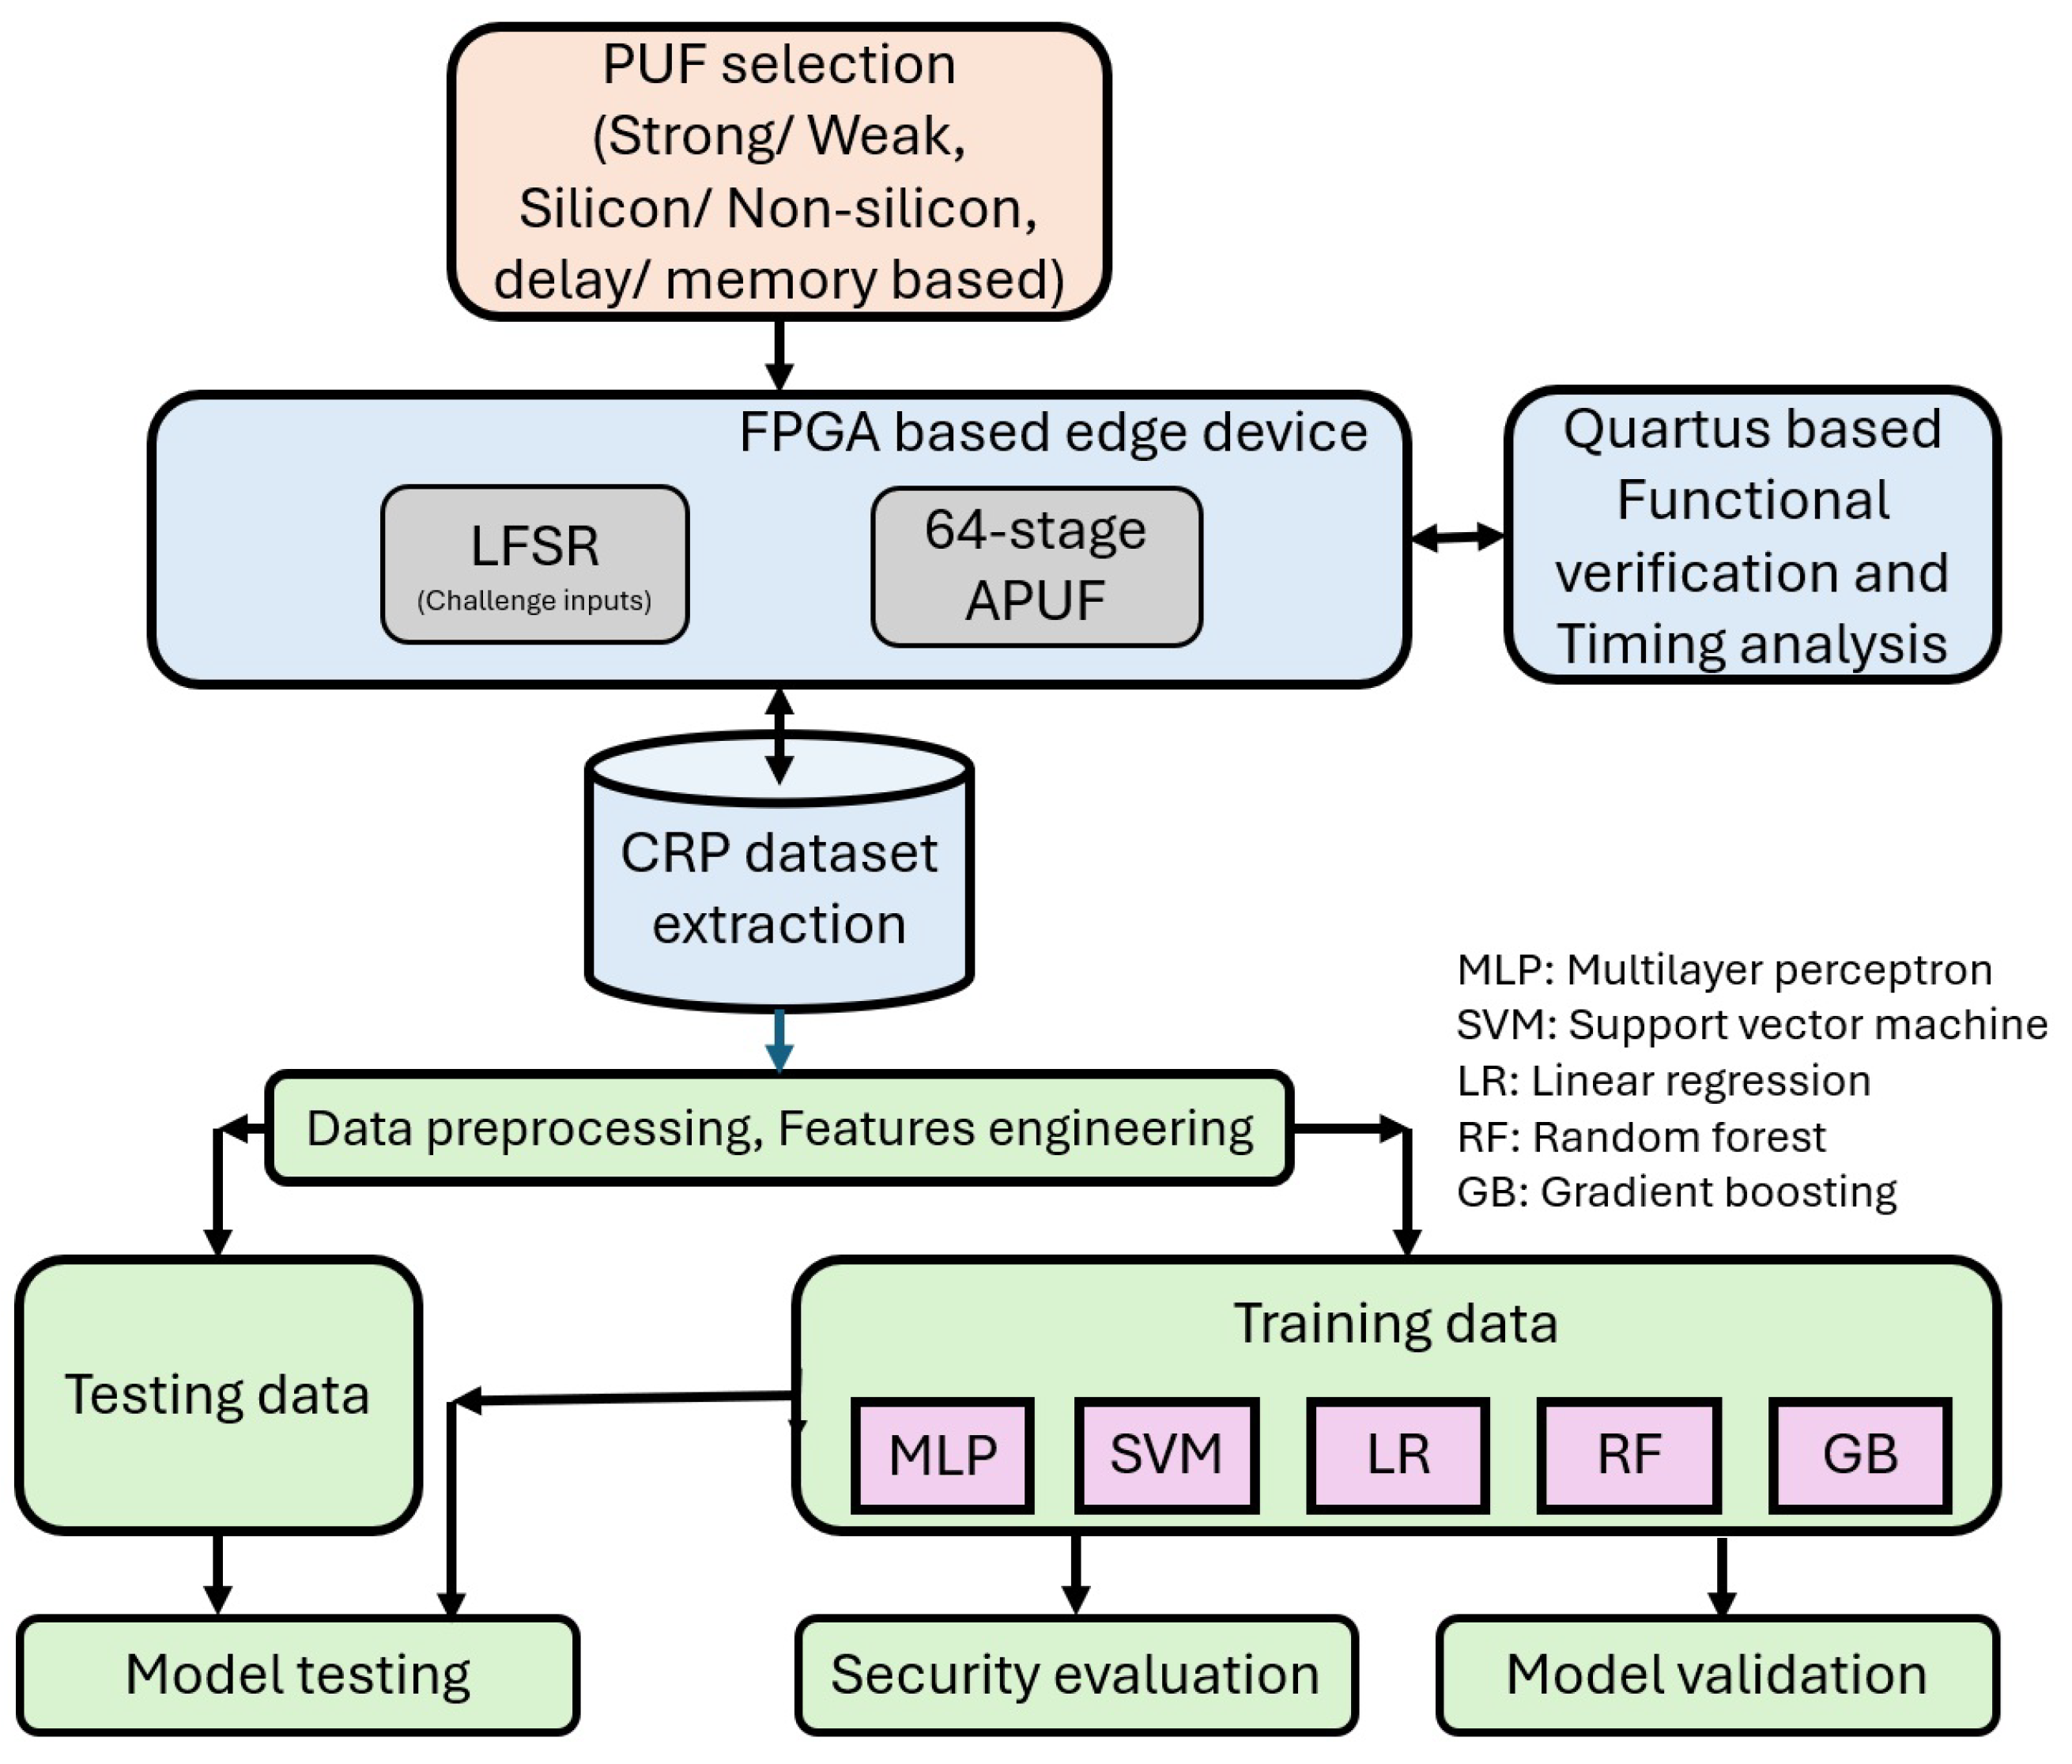
µ 2 = 1 ( N 2 ) ∑ x = 1 N − 1 ∑ y = x + 1 N f H D ( D x , D y ) {\displaystyle \mu _{2}={\frac {1}{\binom {N}{2}}}\sum _{x=1}^{N-1}\sum _{y=x+1}^{N}fHD(D_{x},D_{y})} where µ2 is the inter-fHD mean, N is the number of inter-device responses, and Dx and Dy are arrays from the inter-device set {D}. Thus, N is also the total number of arrays in the set {D}.< The parameter commonly reported as "uniqueness" is then expressed as: U n i q u e n e s s = µ 2 × 100 % {\displaystyle Uniqueness=\mu _{2}\times 100\%} Figure 2: Integrating Physical Unclonable Functions with Machine Learning for the ...
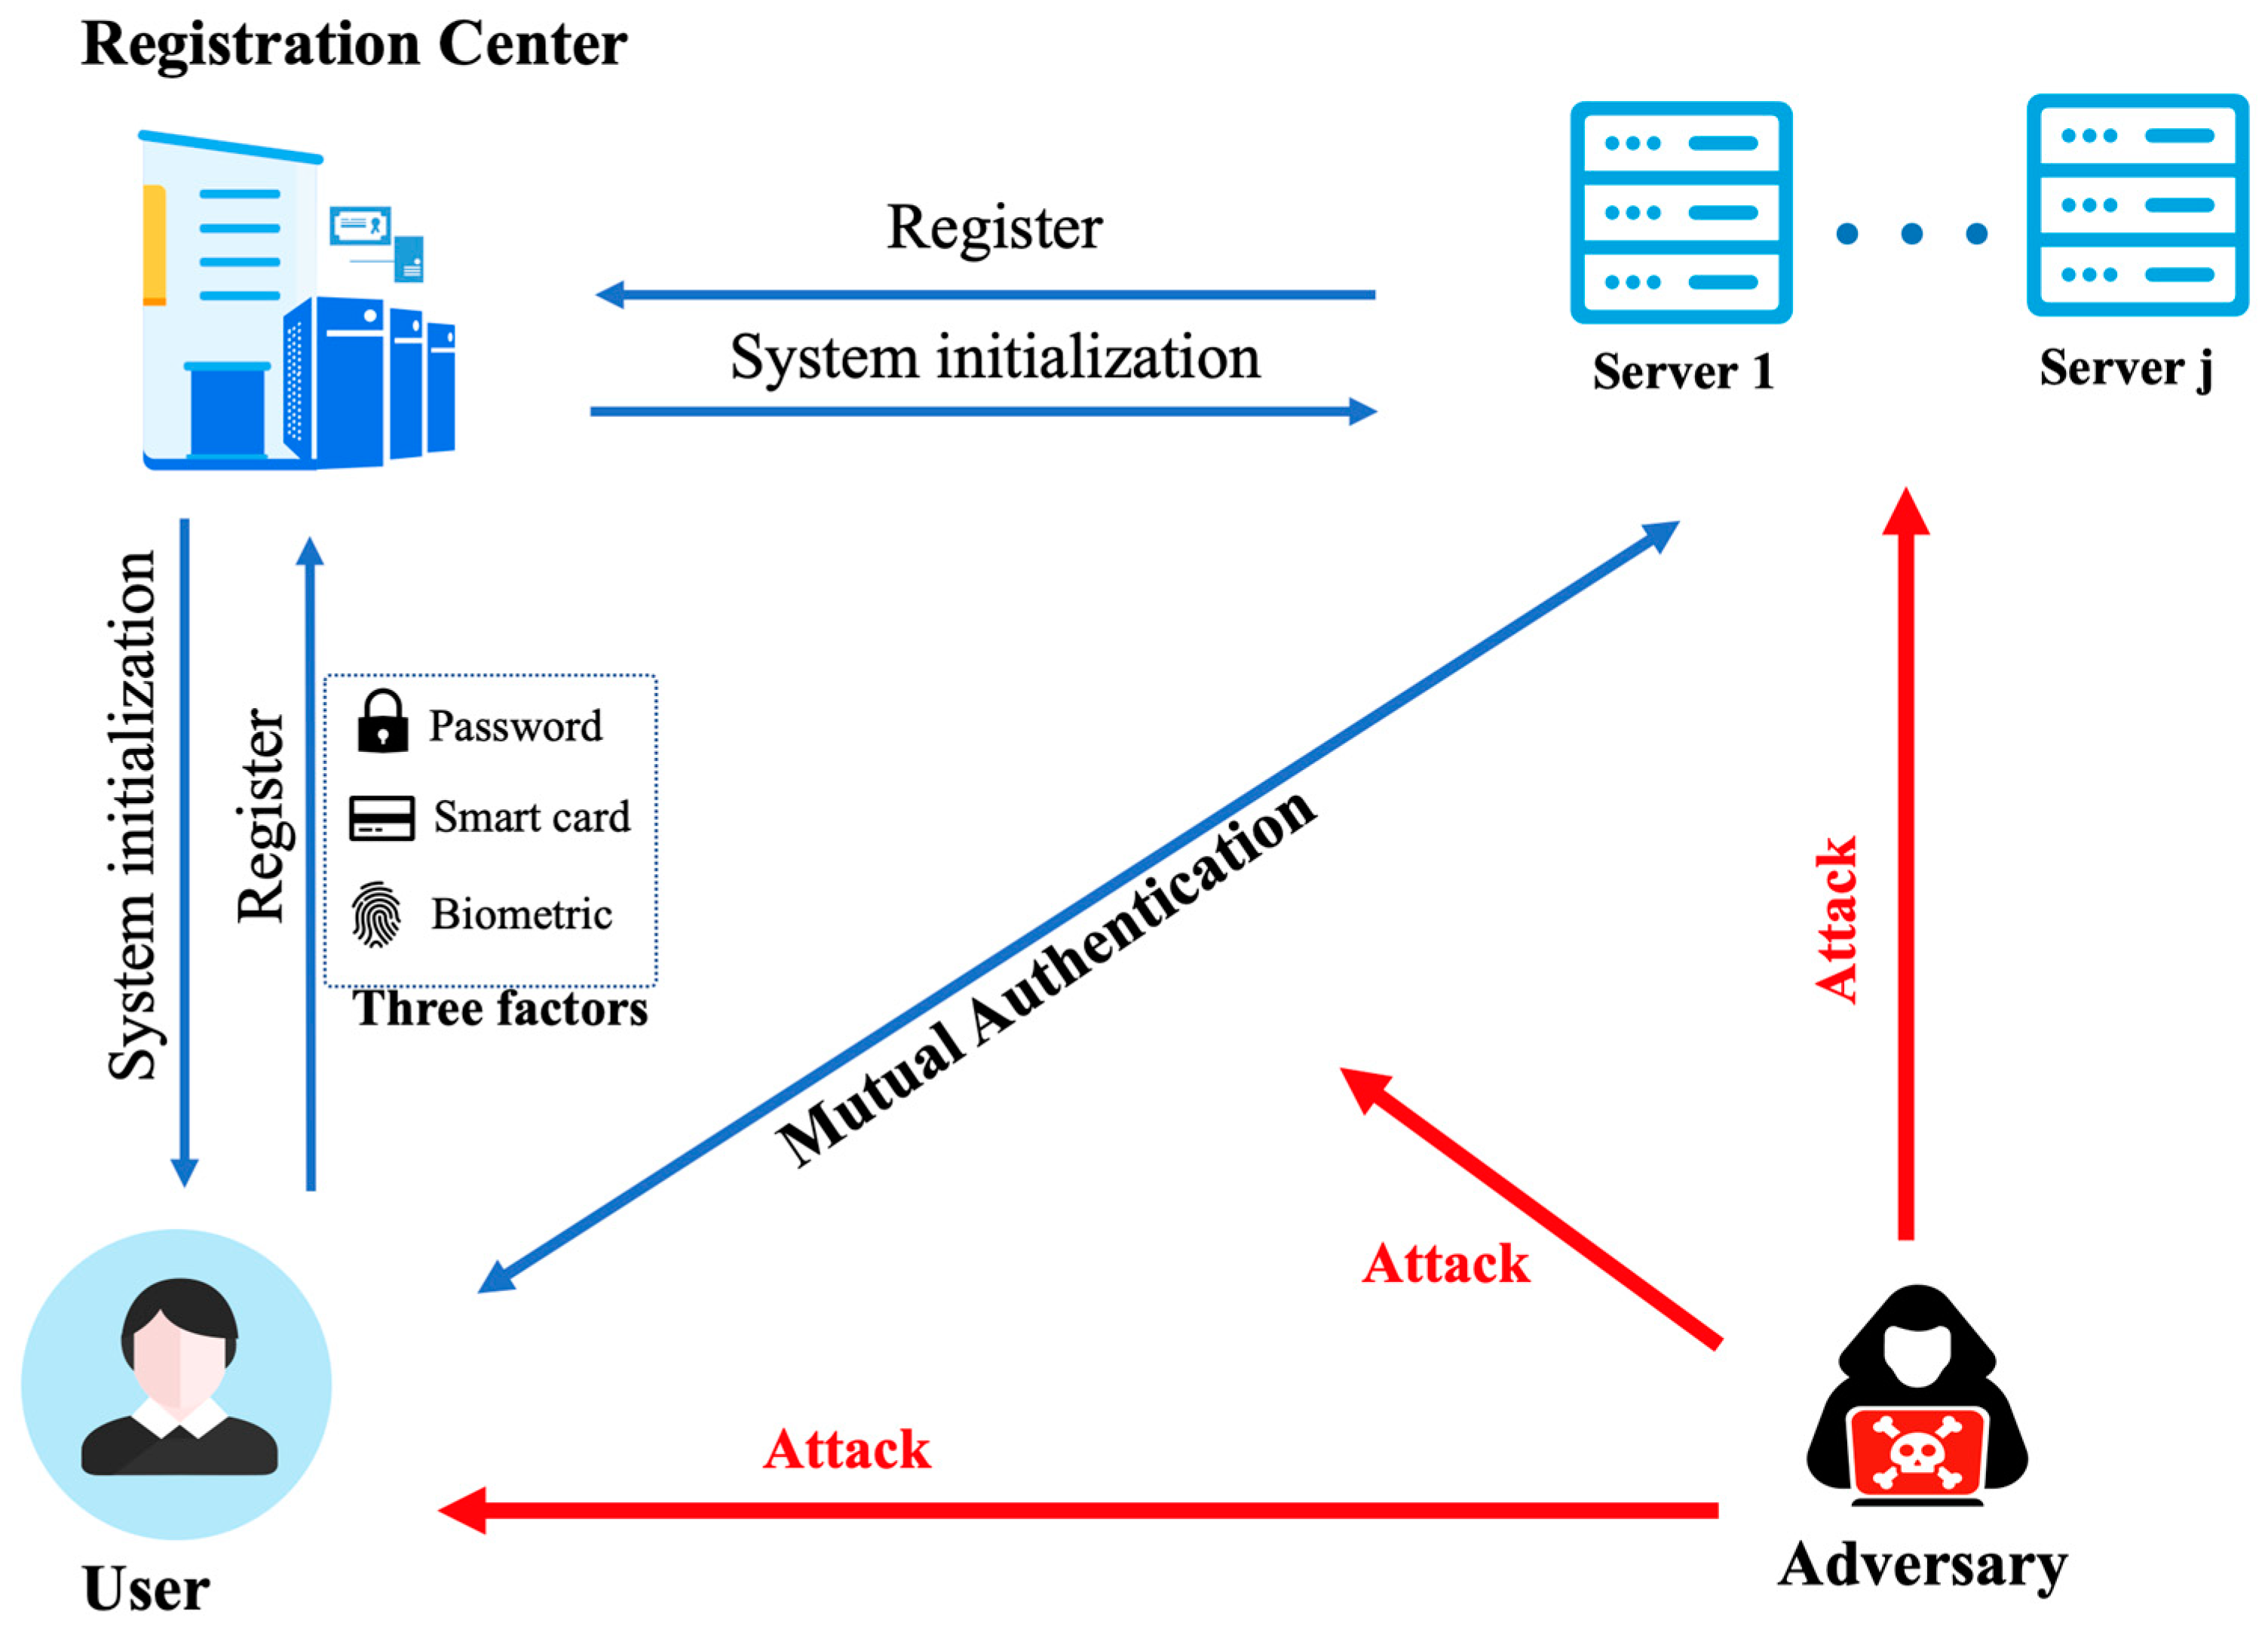
2. System Architecture & Core Working Principles The ideal value for µ2 is 0.5. This indicates that, on average, different PUF instances produce responses that differ in 50% of their bits, demonstrating both randomness and uniqueness. µ 1 = 1 ( N 2 ) ∑ x = 1 N − 1 ∑ y = x + 1 N f H D ( C x , C y ) {\displaystyle \mu _{1}={\frac {1}{\binom {N}{2}}}\sum _{x=1}^{N-1}\sum _{y=x+1}^{N}fHD(C_{x},C_{y})} where µ1 is the intra-fHD mean, N is the number of repeated measurements, and Cx and Cy are arrays from the intra-device set {C}. Reliability is then defined as: R e l i a b i l i t y = ( 1 − µ 1 ) × 100 % {\displaystyle Reliability=(1-\mu _{1})\times 100\%} Figure 3: Physical-Unclonable-Function-Based Lightweight Three-Factor ...
Ideally, µ1 would be 0, indicating that repeated measurements of the same PUF instance produce identical responses. In practice, however, achieving an intra-fHD mean of 0 is difficult for reasonably sized identifiers due to factors such as noise, alignment errors, and other environmental influences, which increase the observed intra-fHD. U n = 1 a ⋅ b ∑ I = 1 a ∑ J = 1 b D n , I , J {\displaystyle U_{n}={\frac {1}{a\cdot b}}\sum _{I=1}^{a}\sum _{J=1}^{b}D_{n,I,J}} U = 1 N ∑ n = 1 N U n {\displaystyle U={\frac {1}{N}}\sum _{n=1}^{N}U_{n}} Here, U n {\displaystyle U_{n}} is a number between 0 and 1 representing the average pixel value of the array. The set { D } {\displaystyle \{D\}} is sometimes used to analyze uniformity across multiple devices.
3. Software Implementation, Frameworks & Protocols N = µ 2 ( 1 − µ 2 ) σ 2 2 {\displaystyle N={\frac {\mu _{2}(1-\mu _{2})}{\sigma _{2}^{2}}}} where N {\displaystyle N} is the ENIB, µ 2 {\displaystyle \mu _{2}} is the mean of the inter-fractional Hamming distance (inter-fHD) distribution, and σ 2 {\displaystyle \sigma _{2}} is its standard deviation (with σ 2 2 {\displaystyle \sigma _{2}^{2}} representing the variance). In some literature, this metric is also referred to as the degrees of freedom (DoF) of the PUF response.
d ′ = | µ 1 − µ 2 | σ 1 2 + σ 2 2 2 {\displaystyle d'={\frac {|\mu _{1}-\mu _{2}|}{\sqrt {\frac {\sigma _{1}^{2}+\sigma _{2}^{2}}{2}}}}} where d ′ {\displaystyle d'} represents decidability, µ 1 {\displaystyle \mu _{1}} is the mean of the intra-fractional Hamming distance (intra-fHD) distribution, µ 2 {\displaystyle \mu _{2}} is the mean of the inter-fHD distribution, σ 1 {\displaystyle \sigma _{1}} is the standard deviation of the intra-fHDs, and σ 2 {\displaystyle \sigma _{2}} is the standard deviation of the inter-fHDs.
On-chip ECC units increase size, power, and data processing time overheads; they also expose vulnerabilities to power analysis attacks that attempt to model the PUF mathematically. Alternatively, some PUF designs like the EC-PUF do not require an on-chip ECC unit. Strategies have been developed which lead SRAM PUF to become more reliable over time without degrading the other PUF quality measures such as security and efficiency. Research at Carnegie Mellon University into various PUF implementations found that some error reduction techniques reduced errors in PUF response in a range of ~70 percent to ~100 percent. Research at the University of Massachusetts Amherst to improve the reliability of SRAM PUF-generated keys posited an error correction technique to reduce the error rate. Joint reliability–secrecy coding methods based on transform coding are used to obtain significantly higher reliabilities for each bit generated from a PUF such that low-complexity error-correcting codes such as BCH codes suffice to satisfy a block error probability constraint of 1 bit errors out of 1 billion bits. Nested polar codes are used for vector quantization and error correction jointly. Their performance is asymptotically optimal in terms of, for a given blocklength, the maximum number of secret bits generated, the minimum amount of private information leaked about the PUF outputs, and minimum storage required. The fuzzy commitment scheme and fuzzy extractors are shown to be suboptimal in terms of the minimum storage.
A physically unclonable function (PUF) is a physical entity that can serve as a hardware security primitive, particularly useful in authentication and anti-counterfeiting applications. PUFs generate identifiers based on unique, complex physical structures or responses that are difficult to replicate or model. Their evaluation typically involves measuring physical properties or optical features associated with the specific device. PUFs leverage inherently non-reproducible physical properties to generate unique identifiers, making them promising for authentication and anti-counterfeiting applications. All PUFs are subject to environmental variations such as temperature, supply voltage, or electromagnetic interference, which can affect their responses. Their utility lies not only in producing random outputs, but in reliably reproducing the same response under varying conditions for a given challenge. Compared to traditional anti-counterfeit methods like holograms, PUFs are harder to clone due to the intrinsic randomness of their fabrication.
Reliability: Thanks to the metallic property, once "via" or "contact" are formed in a structure, they stay there nearly permanently regardless of PVT variation, which means 0% of bit error rate and thus the post processing stages such as error correction code or helper data algorithm are not required. The technology is verified by the JEDEC standard tests and passed the Automotive Electronics Council Q-100 Grade 3 test for automotive applications. Randomness of the Via PUF achieves 0.4972 of Hamming weight closed to the ideal value of 0.5. The technology passed NIST Special Publication 800-92 and NIST SP 800-90B randomness tests. Uniqueness and ‘InbornID’: Uniqueness is an important property of PUF since it would guarantee that one chip ID is always different from other chips. The Via PUF reports 0.4999 of Hamming Distance value closed to the ideal uniqueness of 0.5. The 'InbornID' of the Via PUF stands for on-chip unique ‘inborn’ ID of a silicon chip.
Obscurity is one of the great advantages of using the Via PUF technology in IC implementation. The Via or Contact holes of PUF are scattered around all over the chip. No need to form array blocks like the SRAM PUF. Practically impossible to distinguish PUF Vias from regular logic Vias, making IC reverse engineering almost impossible. Standard Manufacturing Process: The Via PUF technology uses standard cell structures from standard digital library with regular core voltage. No high voltage, and so no special circuitry like charge pump. There is no extra mask layer required in the IC manufacturing process.
The Via PUF based Hardware RoT (Root of Trust) chips are currently applied in various markets such as telecommunications, appliances, and IoT devices in the forms of Wifi/BLE modules, smart door locks, IP cameras, IR sensor hub, etc. The technology supports the security functionalities such as anti-counterfeiting, secure boot, secure firmware copy protection, secure firmware update and secure data integrity.
Temperature and voltage stability: Temperature and voltage (TV) variations represent one of the most significant challenges for PUFs in applications that require re-generation of exactly the same bitstring later in time, e.g., encryption. Metal resistance (unlike transistors) varies linearly with temperature and is independent of voltage. Therefore, metal resistance provides a very high level of robustness to changing environmental conditions. Ubiquity: Metal is (currently) the only conducting material on the chip that is layered, effectively enabling high density, and very compact, PUF entropy sources. Advanced processes create 11 or more metal layers on top of the (x,y) plane of the underlying transistors. Reliability: The wear-out mechanism for metal is electro-migration, which like TV variations, adversely affects the ability of the PUF to reproduce the same bitstring over time. However, the electro-migration process is well understood and can be completely avoided with proper sizing of the metal wires, vias and contacts. Transistor reliability issues, e.g., NBTI (negative-bias temperature instability) and HCI, on the other hand, are more difficult to mitigate. Resiliency: Recent reports have shown that transistor-based PUFs, in particular the SRAM PUF, are subject to cloning. Metal resistance PUFs are not subject to these types of cloning attacks due to the high complexity associated with 'trimming' wires in the clone as a means of matching resistances. Moreover, by adding one or more shielding layers in the thicker upper metal layers that overlay the underlying PUF (which is built using the lower metal layers), front-side probing attacks designed to extract the metal resistances for the clone is extremely difficult or impossible.
4. Practical Deployment, Analysis & Case Studies Personalizing the magnetic PUF: The personal data encoded on the magnetic stripe contributes another layer of randomness. When the card is encoded with personal identifying information, the odds of two encoded magstripe cards having an identical magnetic signature are approximately 1 in 10 billion. The encoded data can be used as a marker to locate significant elements of the PUF. This signature can be digitized and is generally called a magnetic fingerprint. An example of its use is in the Magneprint brand system. Stimulating the magnetic PUF: The magnetic head acts as a stimulus on the PUF and amplifies the random magnetic signal. Because of the complex interaction of the magnetic head, influenced by speed, pressure, direction and acceleration, with the random components of the PUF, each swipe of the head over the magnetic PUF will yield a stochastic, but very distinctive signal. Think of it as a song with thousands of notes. The odds of the same notes recurring in an exact pattern from a single card swiped many times are 1 in 100 million, but overall the melody remains very recognizable.
Uses for a magnetic PUF: The stochastic behavior of the PUF in concert with the stimulus of the head makes the magnetic stripe card an excellent tool for dynamic token authentication, forensic identification, key generation, one-time passwords, and digital signatures. Authentication (from Greek: αIθεντικIς authentikos, "real, genuine", from αIθIντης authentes, "author") is the act of proving an assertion, such as the identity of a computer system user. In contrast with identification, the act of indicating a person or thing's identity, authentication is the process of verifying that identity. Authentication is relevant to multiple fields. In art, antiques, and anthropology, a common problem is verifying that a given artifact was produced by a certain person, or in a certain place (i.e. to assert that it is not counterfeit), or in a given period of history (e.g. by determining the age via carbon dating). In computer science, verifying a user's identity is often required to allow access to confidential data or systems. It might involve validating personal identity documents.
Authentication can be considered to be of three types: The first type of authentication is accepting proof of identity given by a credible person who has first-hand evidence that the identity is genuine. When authentication is required for art or physical objects, this proof could be a friend, family member, or colleague attesting to the item's provenance, perhaps by having witnessed the item in its creator's possession. With autographed sports memorabilia, this could involve someone attesting that they witnessed the object being signed. A vendor selling branded items implies authenticity, while they may not have evidence that every step in the supply chain was authenticated. The second type of authentication is comparing the attributes of the object itself to what is known about objects of that origin. For example, an art expert might look for similarities in the style of painting, check the location and form of a signature, or compare the object to an old photograph. An archaeologist, on the other hand, might use carbon dating to verify the age of an artifact, do a chemical and spectroscopic analysis of the materials used, or compare the style of construction or decoration to other artifacts of similar origin. The physics of sound and light, and comparison with a known physical environment, can be used to examine the authenticity of audio recordings, photographs, or videos. Documents can be verified as being created on ink or paper readily available at the time of the item's implied creation.
Attribute comparison may be vulnerable to forgery. In general, it relies on the facts that creating a forgery indistinguishable from a genuine artifact requires expert knowledge, that mistakes are easily made, and that the amount of effort required to do so is considerably greater than the amount of profit that can be gained from the forgery. In art and antiques, certificates are of great importance for authenticating an object of interest and value. Certificates can, however, also be forged, and the authentication of these poses a problem. For instance, the son of Han van Meegeren, the well-known art-forger, forged the work of his father and provided a certificate for its provenance as well. Criminal and civil penalties for fraud, forgery, and counterfeiting can reduce the incentive for falsification, depending on the risk of getting caught. Currency and other financial instruments commonly use this second type of authentication method. Bills, coins, and cheques incorporate hard-to-duplicate physical features, such as fine printing or engraving, distinctive feel, watermarks, and holographic imagery, which are easy for trained receivers to verify. The third type of authentication relies on documentation or other external affirmations. In criminal courts, the rules of evidence often require establishing the chain of custody of evidence presented. This can be accomplished through a written evidence log, or by testimony from the police detectives and forensics staff that handled it. Some antiques are accompanied by certificates attesting to their authenticity. Signed sports memorabilia is usually accompanied by a certificate of authenticity. These external records have their own problems of forgery and perjury and are also vulnerable to being separated from the artifact and lost.
Taggant fingerprinting – uniquely coded microscopic materials that are verified from a database Encrypted micro-particles – unpredictably placed markings (numbers, layers and colors) not visible to the human eye Holograms – graphics printed on seals, patches, foils or labels and used at the point of sale for visual verification Micro-printing – second-line authentication often used on currencies Serialized barcodes UV printing – marks only visible under UV light Track and trace systems – use codes to link products to the database tracking system Water indicators – become visible when contacted with water DNA tracking – genes embedded onto labels that can be traced Color-shifting ink or film – visible marks that switch colors or texture when tilted Tamper evident seals and tapes – destructible or graphically verifiable at point of sale 2d barcodes – data codes that can be tracked RFID chips NFC chips A difficult-to-reproduce physical artifact, such as a seal, signature, watermark, special stationery, or fingerprint. A shared secret, such as a passphrase, in the content of the message. An electronic signature; public-key infrastructure is often used to cryptographically guarantee that a message has been signed by the holder of a particular private key. The opposite problem is the detection of plagiarism, where information from a different author is passed off as a person's own work. A common technique for proving plagiarism is the discovery of another copy of the same or very similar text, which has different attribution. In some cases, excessively high quality or a style mismatch may raise suspicion of plagiarism.
The ways in which someone may be authenticated fall into three categories, based on what is known as the factors of authentication: something the user knows, something the user has, and something the user is. Each authentication factor covers a range of elements used to authenticate or verify a person's identity before being granted access, approving a transaction request, signing a document or other work product, granting authority to others, and establishing a chain of authority. Security research has determined that for a positive authentication, elements from at least two, and preferably all three, factors should be verified. The three factors (classes) and some of the elements of each factor are: Knowledge: Something the user knows (e.g., a password, partial password, passphrase, personal identification number (PIN), challenge–response (the user must answer a question or pattern), security question). Ownership: Something the user has (e.g., wrist band, ID card, security token, implanted device, cell phone with a built-in hardware token, software token, or cell phone holding a software token). Inherence: Something the user is or does (e.g., fingerprint, retinal pattern, DNA sequence (there are assorted definitions of what is sufficient), signature, face, voice, unique bio-electric signals, or other biometric identifiers). Historically, fingerprints have been used as the most authoritative method of authentication, but court cases in the US and elsewhere have raised fundamental doubts about fingerprint reliability. Outside of the legal system as well, fingerprints are easily spoofable, with British Telecom's top computer security official noting that "few" fingerprint readers have not already been tricked by one spoof or another. Hybrid or two-tiered authentication methods offer a compelling solution, such as private keys encrypted by fingerprint inside of a USB device.
Multi-factor authentication involves two or more authentication factors (something you know, something you have, or something you are). Two-factor authentication is a special case of multi-factor authentication involving exactly two factors. For example, using a bank card (something the user has) along with a PIN (something the user knows) provides two-factor authentication. Business networks may require users to provide a password (knowledge factor) and a pseudorandom number from a security token (ownership factor). Access to a very-high-security system might require a mantrap screening of height, weight, facial, and fingerprint checks (several inherence factor elements) plus a PIN and a day code (knowledge factor elements), but this is still a two-factor authentication.
5. Performance Evaluation & Extended Technical Observations Enrollment – an individual applies to a credential service provider (CSP) to initiate the enrollment process. After successfully proving the applicant's identity, the CSP allows the applicant to become a subscriber. Authentication – After becoming a subscriber, the user receives an authenticator e.g., a token and credentials, such as a user name. He or she is then permitted to perform online transactions within an authenticated session with a relying party, where they must provide proof that he or she possesses one or more authenticators. Life-cycle maintenance – the CSP is charged with the task of maintaining the user's credential over the course of its lifetime, while the subscriber is responsible for maintaining his or her authenticator(s).
The authentication of information can pose special problems with electronic communication, such as vulnerability to man-in-the-middle attacks, whereby a third party taps into the communication stream, and poses as each of the two other communicating parties, in order to intercept information from each. Extra identity factors can be required to authenticate each party's identity.
You are seeing this because the administrator of this website has set up Anubis to protect the server against the scourge of AI companies aggressively scraping websites. This can and does cause downtime for the websites, which makes their resources inaccessible for everyone. Anubis is a compromise. Anubis uses a Proof-of-Work scheme in the vein of Hashcash, a proposed proof-of-work scheme for reducing email spam. The idea is that at individual scales the additional load is ignorable, but at mass scraper levels it adds up and makes scraping much more expensive.
Ultimately, this is a placeholder solution so that more time can be spent on fingerprinting and identifying headless browsers (EG: via how they do font rendering) so that the challenge proof of work page doesn't need to be presented to users that are much more likely to be legitimate. Please note that Anubis requires the use of modern JavaScript features that plugins like JShelter will disable. Please disable JShelter or other such plugins for this domain.
Unified multiphysics fusion helps multi-die teams validate earlier and sign off faster. Synopsys is the world’s leading provider of security IP for embedded systems based on physical unclonable function (PUF) technology. The technology provides an additional level of hardware security by utilizing the inherent uniqueness of each and every silicon chip. The IP can be delivered as IP or software and applied easily to almost any chip – from tiny microcontrollers to high-performance FPGAs – and at any stage of a product’s lifecycle. It is an important component for a hardware root of trust to validate payment systems, secure connectivity, authenticate sensors, and protect sensitive government and aerospace data and systems.
Synopsys PUF IP has been deployed and proven in over a billion devices certified by EMVCo, Visa, CC EAL6+, PSA, ioXt, and governments across the globe. Our secure and robust PUF technology generates unique identifiers (IDs) and cryptographic keys, seamlessly enabling the highest level of security in the most cost-effective way. Identifiers and keys extracted from a PUF cannot be cloned, guessed, stolen, or shared, and keys don’t remain stored on the system, providing the highest level of protection.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Physical%20unclonable%20function • https://en.wikipedia.org/wiki/Types%20of%20physical%20unclonable%20function • https://en.wikipedia.org/wiki/Authentication • https://hal.science/hal-05111870v1/document • https://www.synopsys.com/designware-ip/security-ip/cryptography-ip/puf.html
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Physical Unclonable Function Based Device Authentication.
[*] Metasploit Scan Running on Target Subnet for Physical Unclonable Function Based Device Authentication... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |