Complete Technical Paper Content — Portable Executable Malware Detection Using Pefile Python
Overview & System Context
Portable Executable Malware Detection Using Pefile Python: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~4292 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background pefile is a multi-platform Python module to parse and work with Portable Executable (PE) files . Most of the information contained in the PE file headers is accessible, as well as all the sections' details and data.
The structures defined in the Windows header files will be accessible as attributes in the PE instance. The naming of fields/attributes will try to adhere to the naming scheme in those headers. Only shortcuts added for convenience will depart from that convention. pefile requires some basic understanding of the layout of a PE file — with it, it is possible to explore nearly every single feature of the PE file format.
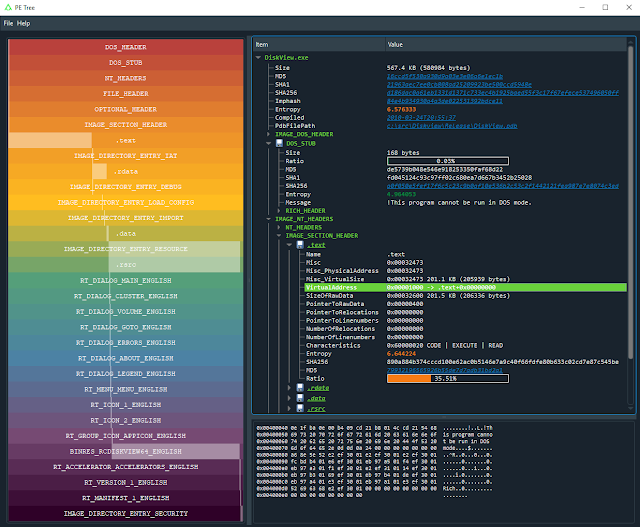
Please, refer to Usage Examples for some code snippets that demonstrate how to use pefile . Figure 1: PE Tree – Python Module For Viewing Portable Executable (PE) Files ... Here are a few examples of what a dump produced with pefile looks like for different types of files: To work with authenticated binaries, including Authenticode signatures , please check the project verify-sigs .
pefile runs in several pipelines scanning hundreds of thousands of new PE files every day, and, while not perfect, it has grown to be pretty robust over time. That being said, small glitches are found now and then. If you bump into a PE that does not appear to be processed correctly, do report it, please! It will help make pefile a tiny bit more powerful. pefile is self-contained. The module has no dependencies; it is endianness independent; and it works on Windows, macOS, and Linux.
Figure 2: GitHub - Dazzy17/Malicious-PE-Files-Detection-using-Machine-Learning The following links provide detailed information about the PE format and its structures. All of the basic PE file structures are available with their default names as attributes of the instance returned. Processed elements, such as the import table, are available with lowercase names to differentiate them from the uppercase basic-structure names.
pefile has been tested against many edge cases, such as corrupted and malformed PEs, as well as malware, which often attempts to abuse the format beyond its intended use. To the best of my knowledge, most of the abuse is handled gracefully. Figure 3: GitHub - Yousinator/Malware-Detection-Using-PE-Imports: A deep learning ... This directory entry will provide information on the DLLs this PE file has been bound to (if bound at all). The structure will contain the name and timestamp of the DLL at the time of binding so that the loader can know whether it differs from the one currently present in the system and must, therefore, re-bind the PEâIIs imports.
It expects to be supplied the name of the file to load, or PE data to process and an optional argument fast_load (None by default), which controls whether to load all the directories information, which can be quite time consuming. The fast_load argument can be set to a default by setting its value in the module like this: pefile.fast_load = True . That will make all the subsequent instances not to load the whole PE structure. The full_load() method can be used to parse the missing data at a later stage.
All of them will contain among their attributes the members of the corresponding structures as defined in WINNT.H . The raw data corresponding to the header (from the beginning of the file up to the start of the first section) will be available in the instanceâIIs attribute header as a string. The sections will be available as a list in the sections attribute. Each entry will contain as attributes all the structureâIIs members.
Directory entries will be available as attributes (if they exist). No other entries are processed at this point. The following dictionary attributes provide ways of mapping different constants. They will accept the numeric value and return the string representation and the opposite, feed in the string and get the numeric constant: This method will load the data directories which might not have been loaded if the fast_load option was used.
Given a RVA and the size of the chunk to retrieve, this method will find the section where the data lies and return the data. Returns None if the value canâIIt be read (i.e., the RVA canâIIt be mapped to a file offset). The offset is assumed to index into a dword array. So setting it to N will return a dword out of the data starting at offset N*4 . The data includes the PE header and the sections loaded at offsets corresponding to their relative virtual addresses (the VirtualAddress section header member). Any offset in this data corresponds to the absolute memory address ImageBase+offset .
The optional argument max_virtual_address provides with means of limiting which sections are processed. Any section with their VirtualAddress beyond this value will be skipped. Normally, sections with values beyond this range are just there to confuse tools. ItâIIs a common trick to see in packed executables. If the optional ImageBase argument is supplied, the fileâIIs relocations will be applied to the image by calling the relocate_image() method. Beware that the relocation information is applied permanently.
Given a RVA , this method will find the section where the data lies and return the offset within the file. 2. System Architecture & Core Working Principles Get the data appended to the file and not contained within the area described in the headers. Get the offset of data appended to the file and not contained within the area described in the headers.
Returns None if the value canâIIt be read (i.e., the RVA canâIIt be mapped to a file offset). The offset is assumed to index into a word array. So setting it to N will return a dword out of the data starting at offset N*8 . This method will scan all entries in the resources directory of the PE, if there is one, and will return a list of the strings. Non-critical problems found when parsing the PE file are appended to a list of warnings. This method returns the full list.
Returns None if the value canâIIt be read (i.e., the RVA canâIIt be mapped to a file offset). The offset is assumed to index into a word array. So setting it to N will return a dword out of the data starting at offset N*2 . This will return true only if there are reliable indicators of the image being a driver. This will return true only if the file has the IMAGE_FILE_EXECUTABLE_IMAGE flag set and the IMAGE_FILE_DLL not set and the file does not appear to be a driver either.
If the optional directories argument is provided, only the directories at the specified indexes will be parsed. Such functionality allows parsing of areas of interest without the burden of having to parse all others. The directories can then be specified as: If directories is a list, the ones that are processed will be removed, leaving only the ones that are not present in the image. If forwarded_exports_only is True, then the IMAGE_DIRECTORY_ENTRY_EXPORT attribute will only contain exports that are forwarded to another DLL.
If import_dllnames_only is True, then symbols will not be parsed from the import table and the entries in the IMAGE_DIRECTORY_ENTRY_IMPORT attribute will not have a symbols attribute. The exports will be made available as a list of ExportData instances in the IMAGE_DIRECTORY_ENTRY_EXPORT PE attribute.
It will fill a list, which will be available as the dictionary attribute imports . Its keys will be the DLL names and the values of all the symbols imported from that object. The root will have the corresponding member of its structure, IMAGE_RESOURCE_DIRECTORY plus entries , a list of all the entries in the directory.
Those entries will have, correspondingly, all the structureâIIs members ( IMAGE_RESOURCE_DIRECTORY_ENTRY ) and an additional one, directory , pointing to the IMAGE_RESOURCE_DIRECTORY structure representing upper layers of the tree. This one will also have an entries attribute, pointing to the third, and last, level. Another directory with more entries. Those last entries will have a new attribute (both leaf or data_entry can be used to access it). This structure finally points to the resource data. All the members of this structure, IMAGE_RESOURCE_DATA_ENTRY , are available as its attributes.
The sections will be readily available in the sections attribute. Its attributes will contain all the section information plus data , a buffer containing the sectionâIIs data. The characteristics member will be processed and attributes representing the section characteristics (with IMAGE_SCN_ trimmed from the constantsâII names) will be added to the section instance.
StringFileInfo structures will have a list as an attribute named StringTable containing all the StringTable structures. Each of those structures contains a dictionary entries with all the key/value version information string pairs. VarFileInfo structures will have a list as an attribute named Var containing all Var structures. Each Var structure will have a dictionary as an attribute named entry which will contain the name and value of the Var .
This method will apply the relocation information to the image. Given the new base, all the relocations will be processed and both the raw data and the sectionâIIs data will be fixed accordingly. In order to get something that would more closely match what could be found in memory once the Windows loader finished its work.
Return True if successful, False otherwise. It can fail if the offset is outside the fileâIIs boundaries. Overwrite, with the given string, the bytes at the file offset corresponding to the given RVA. Return True if successful, False otherwise. It can fail if the offset is outside the fileâIIs boundaries. Non-critical problems found when parsing the PE file are appended to a list of warnings. This method prints the full list to standard output.
3. Software Implementation, Frameworks & Protocols This function will process all headers and components of the PE file and include all changes made (by just assigning to attributes in the PE objects) and write the changes back to a file whose name is provided as an argument. The filename is optional, if not provided the data will be returned as a string.
Query data from the section by passing the addresses where the PE file would be loaded by default. It is then possible to retrieve code and data by their real addresses as they would be if loaded. A list of strings will be wrapped on the object with the hope that any overlapping will clarify its type. Such RVA could indicate the natural end of the string and will be checked to see if thereâIIs a Unicode NULL character there.
Will return a list of (flag, value) pairs for all flags in flag_dict matching the filter flag_filter . The object obj will gain attributes named after the flags provided in flags and valued True/False, matching the results of applying each flag value from flags to flag_field . PE (Portable Executable) files are the standard format for executable files on Windows. Malware analysts often examine these files to identify suspicious or malicious behavior. The pefile library in Python is a powerful tool to parse and analyze PE files.
To get started, you’ll need to install the pefile package in Python. You can do this using pip : To get basic information about the PE file, such as its DOS header, PE signature, and file type: The PE file is divided into sections that hold the actual code, data, and other resources. You can view the section headers with: You can extract readable strings from a PE file by examining the sections for ASCII or Unicode strings. Use the get_data function to read data from a section and then search for printable strings: If the PE file contains resources (e.g., icons, strings, images), you can extract them using pefile as well: Malware often relies on Windows APIs, so examining the import table (which lists external libraries and functions) can be a key step in analysis. Here's how you can print the imported functions: Malware often exhibits telltale signs in the PE file structure, such as unusual imports (e.g., CreateRemoteThread , LoadLibrary , WinExec , RegSetValueEx ) or suspicious section names.
This can help you identify potential malicious actions, like creating threads or modifying the registry. Some malware adds additional data after the PE file’s last section, which isn’t part of the official PE structure but can contain additional code. To check for this: PE Header Analysis : The PE file header and optional header provide critical information about the file's structure, entry point, and dependencies.
Sections : Malware often hides code or data in specific sections; knowing how to analyze them is crucial. Imports : Analyzing imports can help identify suspicious behavior, like remote thread creation or process injection. Strings and Resources : Extracting strings and resources can quickly reveal hidden domains, C2 servers, and other indicators of compromise (IOCs).
Overlays : Malware often appends additional malicious code after the legitimate PE structure. By using pefile , you can gain deep insight into the inner workings of PE files, helping you spot malicious behavior or even extract useful data for further analysis. This script combines string extraction and suspicious import checking in one place, helping you get a comprehensive view of the PE file.
In today’s ever-evolving threat landscape, proactive Malware Identification with YARA and PEfile is crucial. This blog post delves into the powerful combination of YARA (Yet Another Recursive Acronym) and PEfile (a Python module for parsing Portable Executable files) for malware analysis. We’ll explore how to use these tools to identify, classify, and understand malicious software, providing you with the knowledge and skills to defend against cyber threats effectively. From understanding YARA rule syntax to extracting valuable metadata from PE files, this guide will equip you with the arsenal needed to enhance your cybersecurity posture. We’ll cover practical examples and real-world use cases, ensuring that you can immediately apply these techniques in your own investigations.
Malware analysis is becoming increasingly complex. Attackers are constantly devising new methods to bypass traditional security measures. The combined power of YARA’s pattern-matching capabilities and PEfile’s file parsing functionalities provide a robust approach to understanding the underlying characteristics of malware, ultimately strengthening our defenses against these evolving threats. Dive in and learn how to make a difference! YARA is like a super-powered search engine for malware. It allows you to create rules that describe malware families based on textual or binary patterns. Understanding its syntax is key to effective malware hunting. Let’s explore.
yara rule ExampleMalware { meta: author = “Cybersecurity Analyst” description = “Detects a specific malware sample” date = “2024-10-27” reference = “https://example.com/malware-analysis” strings: $magic_number = { 4D 5A } // MZ Header $string1 = “This is a malicious string” $string2 = “Another suspicious string” 4. Practical Deployment, Analysis & Case Studies PEfile is a Python library that allows you to dissect Portable Executable (PE) files, the backbone of Windows executables.
Understanding how to use PEfile is essential for extracting valuable information about malware. print(f”Image Base: {pe.OPTIONAL_HEADER.ImageBase}”) print(f”Entry Point: {pe.OPTIONAL_HEADER.AddressOfEntryPoint}”) for section in pe.sections: print(f” Section Name: {section.Name.decode(‘utf-8’).rstrip(‘\x00’)}”) print(f” Virtual Address: {section.VirtualAddress}”) print(f” Size of Raw Data: {section.SizeOfRawData}”) for entry in pe.DIRECTORY_ENTRY_IMPORT: print(f” DLL: {entry.dll.decode(‘utf-8’)}”) for imp in entry.imports: print(f” Function: {imp.name.decode(‘utf-8’) if imp.name else hex(imp.address)}”) except pefile.PEFormatError as e: print(f”Error: {e}”) except FileNotFoundError: print(“Error: File not found.”) The true power comes from combining YARA and PEfile. You can use PEfile to extract specific data from a PE file and then use YARA to search for patterns within that data.
def analyze_with_yara_and_pefile(file_path, yara_rule_path): try: pe = pefile.PE(file_path) # Extract the entire file as bytes with open(file_path, ‘rb’) as f: file_bytes = f.read() # Extract relevant info for context image_base = pe.OPTIONAL_HEADER.ImageBase entry_point = pe.OPTIONAL_HEADER.AddressOfEntryPoint if matches: print(f”YARA matches found in {file_path}:”) for match in matches: print(f” Rule: {match.rule}”) print(f” Namespace: {match.namespace}”) print(f” Tags: {match.tags}”) print(f” Strings: {match.strings}”) else: print(f”No YARA matches found in {file_path}.”) except pefile.PEFormatError as e: print(f”PE Format Error: {e}”) except FileNotFoundError: print(“File not found.”) except yara.Error as e: print(f”YARA Error: {e}”) yara rule ExampleMalwareCombined { meta: description = “Detects a specific combined characteristic.” author = “Analyst” Writing efficient YARA rules is as crucial as writing them. Badly written rules can slow down scans and generate false positives.
Static analysis involves examining the code and structure of a malware sample without executing it, often using tools like YARA and PEfile. Dynamic analysis, on the other hand, involves executing the malware in a controlled environment (like a sandbox) and observing its behavior. Static analysis is useful for identifying code patterns and metadata, while dynamic analysis reveals the malware’s actions on a system. I Improving YARA rule accuracy involves several strategies. First, focus on highly specific indicators that are unique to the malware family you are targeting. Second, combine multiple indicators in your rules to reduce the likelihood of false positives.
Finally, thoroughly test your rules against a variety of samples, including both malicious and benign files, to refine their accuracy. I While PEfile is designed for Windows PE files, YARA is platform-agnostic and can be used on various operating systems, including Linux and macOS. On non-Windows platforms, YARA can be used to analyze other types of executable files, such as ELF files on Linux. You can parse other file format data using various parsing tools and libraries available for those systems, and then use YARA to scan the extracted data. I Malware Identification with YARA and PEfile offers a powerful and versatile approach to combating modern cyber threats. By mastering YARA rule syntax and understanding how to parse PE files with PEfile, you can gain valuable insights into the inner workings of malware, improving your ability to detect, classify, and respond to security incidents. The combination of these tools empowers security professionals to stay ahead of evolving threats and protect their organizations effectively. Remember to keep your knowledge and tools up-to-date as the threat landscape continues to evolve. This proactive approach is key to maintaining a robust cybersecurity posture. Keep learning, experimenting, and contributing to the community, and together, we can make the digital world a safer place. I Master malware analysis! Learn how to use YARA and PEfile for effective Malware Identification with YARA and PEfile and classification. Real-world examples included.
Optionally, setting the fast_load argument to True will prevent parsing the directories. In large PE files this can make loading significantly faster and it might be a good idea to use it none of the information from the data directories is needed. Once the PE file is successfully parsed, the data is readily available as attributes of the PE instance. All the structures and members defined in the PE format should be available with the same names. Some convenient shortcuts exist, for instance the sections list. Usually, all the structures containing a member Characteristics (or similar fields of flags) will contain attributes set to True or False according to the value of the corresponding flag.
Sections are added to a list accesible as the attribute sections in the PE instance. The common structure members of the section header are reachable as attributes. Each directory, if it exists in the PE file being processed, has an entry as DIRECTORY_ENTRY_directoryname in the PE instance. The imported symbols can be listed as follows: We can use pefile together with tools like pydasm to build a small disassembler. A toy example might look like the following.
We first fetch the entry point address, the retrieve 100 bytes starting at the entry point and we loop through the data disassembling as we go: Sometimes we might not want to process an entire file if itâIIs very large. Parsing can be time consuming in some cases an we might only be interested in a subset of the information provided by the headers and directories.
It is possible to indicate pefile to only load a minimal set of the headers (up to the NT Headers) with the fast_load keyword argument and leave the directories unprocessed. The directories can be parsed later on, on demand. The following example loads the basic headers and then goes on to parse most of the directories avoiding the relocation information.
5. Performance Evaluation & Extended Technical Observations A lightweight web-based PE malware detection prototype that combines a FastAPI backend, a simple frontend dashboard, and a machine learning classifier to analyze Windows Portable Executable files. The application is intended as a demo or educational project and uses a synthetic PE-style dataset by default for the initial model training.
A Python-based malware analysis project that inspects Windows PE files, extracts key metadata and security-relevant features, and provides insights into executable behavior using static analysis techniques. The Static-Analysis-Tool is designed for analyzing Portable Executable (PE) files and performing online malware scans using VirusTotal. This tool provides detailed insights into PE file headers, sections, imported/exported functions, and resource information. Additionally, it computes file hashes (MD5, SHA1, SHA256), extracts strings, calculates entropy, and integrates with VirusTotal for malware detection.
A Python-based tool designed to analyze Portable Executable (PE) files and perform online malware scans using VirusTotal. With detailed insights into PE file headers, hash calculations, and entropy analysis, the tool also features a user-friendly GUI powered by Tkinter. It’s an essential solution for malware detection and binary analysis This project implements a machine learning-based approach to detect malware in Portable Executable (PE) files. By analyzing features extracted from PE file headers and sections, the tool distinguishes between malicious and benign executables using various machine learning algorithms. The research was published in the IEEE Xplore journal under the title Malware poses a significant threat to digital systems, and detecting it in executable files is critical for cybersecurity. This project leverages the structure of PE files, commonly used in Windows executables, to extract features such as header information, section entropy, and other metadata. These features are used to train machine learning models to classify files as either malicious or benign.
A Portable Executable (PE) file is a file format used by Windows operating systems for executable files, such as programs (.exe), dynamic link libraries (.dll), and other types of system files. Think of a PE file as a structured container that holds everything needed to run a program: the code, data, and instructions for the operating system on how to load and execute it. PE files are widely used in Windows, making them a common target for malware because they can hide malicious code within their complex structure.
Malware, short for “malicious software,” is any program designed to harm or exploit a computer system, network, or user. Malware can steal data, disrupt operations, or give attackers unauthorized access. It often disguises itself as legitimate software to trick users into installing it. Malware can hide in PE files by exploiting redundant fields or manipulating sections, making detection challenging.
Traditional malware detection relies on signatures (unique patterns in known malware), but modern malware often changes its code to evade detection. Machine learning offers a smarter approach by analyzing patterns in PE file features (like header data or section entropy) to identify suspicious files without needing exact matches. This project uses machine learning to “learn” what makes a file malicious or benign based on a dataset of examples.
This project focuses on static analysis, meaning it examines the file’s structure without running it, which is safer but may miss behaviors only visible during execution. To train the machine learning models on the dataset, run the learning.py script. The script processes a dataset of PE files, extracts features, and trains multiple classifiers.
To analyze a specific PE file for malware, run the checker.py script with the path to the test file. The dataset used contains 137,444 PE files (EXE, DLL, etc.), with 40,918 malware files and 96,526 benign files. It was sourced from Kaggle and VirusShare. Key features extracted include: S. Tyagi, A. Baghela, K. M. Dar, A. Patel, S. Kothari and S. Bhosale, “Malware Detection in PE files using Machine Learning,” 2022 OPJU International Technology Conference on Emerging Technologies for Sustainable Development (OTCON), algorithms;Supervised learning;Static analysis;Malware;Libraries;Classification algorithms;Decision trees;Malware Detection;Static malware analysis;Opcode N-grams;Byte N-grams;PE Header;PE file;Machine Learning}, This work was conducted at the Symbiosis Institute of Technology, Symbiosis International (Deemed University), Pune, India, under the guidance of Dr. Sonali Kothari and Dr. Snehal Bhosale.
This research was conducted as part of my final year specialisation project at Symbiosis Institute of Technology (Feb, 2023). The full research paper and implementation details are available for academic and educational purposes. In this lab, we will explore some basic analysis of portable executable files (PE), as a means of differentiating between malicious software and benign software. We will use the Python library pefile to achieve this. We can import the pefile library and call the help function to learn more about this.
We can easily pass a EXE file using the command below. We can then print the information about this file using the function print_info This starts to look quite useful - it will provide us with details of the DLL (dynamic linked libraries) that are called by the executable.
In the cells above, we are simply iterating over the data instances in the DIRECTORY_ENTY_IMPORT fields. We learn to access the name and the imports list. We could begin to curate a dataset of malicious and benign files based on the DLL characteristics of each group. pefile is a multi-platform Python module to parse and work with Portable Executable (PE) files .
All the PE file basic structures are available with their default names as attributes of the instance returned. Processed elements such as the import table are made available with lowercase names, to differentiate them from the upper case basic structure names. pefile has been tested against many edge cases such as corrupted and malformed PEs as well as malware, which often attempts to abuse the format way beyond its standard use. To the best of my knowledge most of the abuse is handled gracefully.
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation . Harvested Online Documentation & Reference Sources • https://github.com/erocarrera/pefile • https://pefile.readthedocs.io/en/latest/modules/pefile.html • https://github.com/CommodoreAlex/Malware-Analysis-and-Reverse-Engineering/blob/main/PEPython.md • https://developers-heaven.net/blog/using-yara-and-pefile-for-malware-identification-and-classification/ • https://pefile.readthedocs.io/en/latest/usage/UsageExamples.html • https://github.com/tanay-codes/PE-File-Malware-Detector • https://github.com/rehabmohamed2/Static-Malware-Analysis_Tool-Using-Python • https://achintya-esbee.github.io/posts/malware-detection-in-pe-files/ • https://pa-legg.github.io/csa/2223-lab/lab-11-malware_analysis.html • https://pefile.readthedocs.io/en/latest/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Portable Executable Malware Detection Using Pefile Python.
[*] Metasploit Scan Running on Target Subnet for Portable Executable Malware Detection Using Pefile Python... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |