Complete Technical Paper Content — Public Key Infrastructure Simulation System In Java
Overview & System Context
Public Key Infrastructure Simulation System In Java: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9526 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background AnyLogic is a multimethod simulation modeling tool developed by The AnyLogic Company (formerly XJ Technologies). It supports agent-based, discrete event, and system dynamics simulation methodologies. AnyLogic is cross-platform simulation software that works on Windows, macOS and Linux. AnyLogic is used to simulate: markets and competition, healthcare, manufacturing, supply chains and logistics, retail, business processes, social and ecosystem dynamics, defense, project and asset management, pedestrian dynamics and road traffic, IT, and aerospace. It is considered to be among the major players in the simulation industry, especially within the domain of business processes is acknowledged to be a powerful tool.
In 1998, the success of this research inspired the DCN laboratory to organize a company with the mission of developing a new generation of simulation software. Development emphasis was placed on applied methods: simulation, performance analysis, behavior of stochastic systems, optimization, and visualization. The resulting software was released in 2000 and featured the latest information technologies: an object-oriented approach, elements of the UML standard, the use of Java, and a modern GUI. The tool was named AnyLogic because it supported all three well-known modeling approaches: system dynamics, discrete event simulation, agent-based modeling, and any combination of these approaches within a single model.
The first version of AnyLogic was V4 because the numbering continues the numbering of COVERS 3.0. AnyLogic 5 was released in 2003. The new version was focused on business simulation in different industries. AnyLogic 7 was released in 2014. It featured many updates aimed at simplifying model building, including support for multimethod modeling, a decreased need for coding, renewed libraries, and other usability improvements. AnyLogic 7.1, also released in 2014, included a new GIS implementation: in addition to shapefile-based maps, AnyLogic started to support tile maps from free online providers, including OpenStreetMap. 2015 marked the release of AnyLogiI 7.2 with the built-in database and the Fluid Library. Since 2015, AnyLogic Personal Learning Edition (PLE) has been available for free for the purposes of education and self-education.
The PLE license is perpetual, but created models are limited in size. The new Road Traffic Library was introduced in 2016 with AnyLogic 7.3. AnyLogic 8 was released in 2017. Beginning with Version 8.0, the AnyLogic model development environment was integrated with AnyLogic Cloud, a web service for simulation analytics. The platform for the AnyLogic 8 model development environment is Eclipse. Starting with version 8.2, the software introduced dynamic imaging and improved GIS mapping. The Material Handling Library was added in version 8.3, providing advanced tools for simulating factories and warehouses. Subsequent versions continued to enhance these features, allowing for more complex and multi-level simulations, such as buildings and automated guided vehicle systems. AnyLogic 8.4 and later versions further refined transport and material handling capabilities, including introducing transporters that move without guidance paths and more flexible conveyor systems. AnyLogic 8.7 expanded capabilities with overhead cranes, pedestrian area simulations with capacity restrictions, and support for social distancing rules. With version 8.8, the transition to Java 11 streamlined the coding process, enhancing model creation and execution. AnyLogic 8.9 incorporated Git for better version control and introduced a memory dump analyzer for improved debugging. In AnyLogic 8.9.2, the NVIDIA Omniverse Connector was introduced, allowing users to link their simulations with detailed animations. This connection lets users export 3D models from AnyLogic to NVIDIA Omniverse, enhancing the visual quality and facilitating collaboration.
AnyLogic includes a graphical modeling language and also allows the user to extend simulation models with Java code. The Java nature of AnyLogic lends itself to custom model extensions via Java coding Stock & Flow Diagrams are used for System Dynamics modeling. Statecharts are used mostly in Agent Based modeling to define agent behavior. They are also often used in Discrete Event modeling, e.g. to simulate machine failure. Action charts are used to define algorithms. They may be used in Discrete Event modeling, e.g. for call routing, or in Agent Based modeling, e.g. for agent decision logic. Process flowcharts are the basic construction used to define processes in Discrete Event modeling. Looking at this flowchart you may see why the Discrete Event style is often called Process Centric. The language also includes low-level modeling constructions (variables, equations, parameters, events etc.), presentation shapes (lines, polylines, ovals etc.), analysis facilities (datasets, histograms, plots), connectivity tools, standard images, and experiments frameworks.
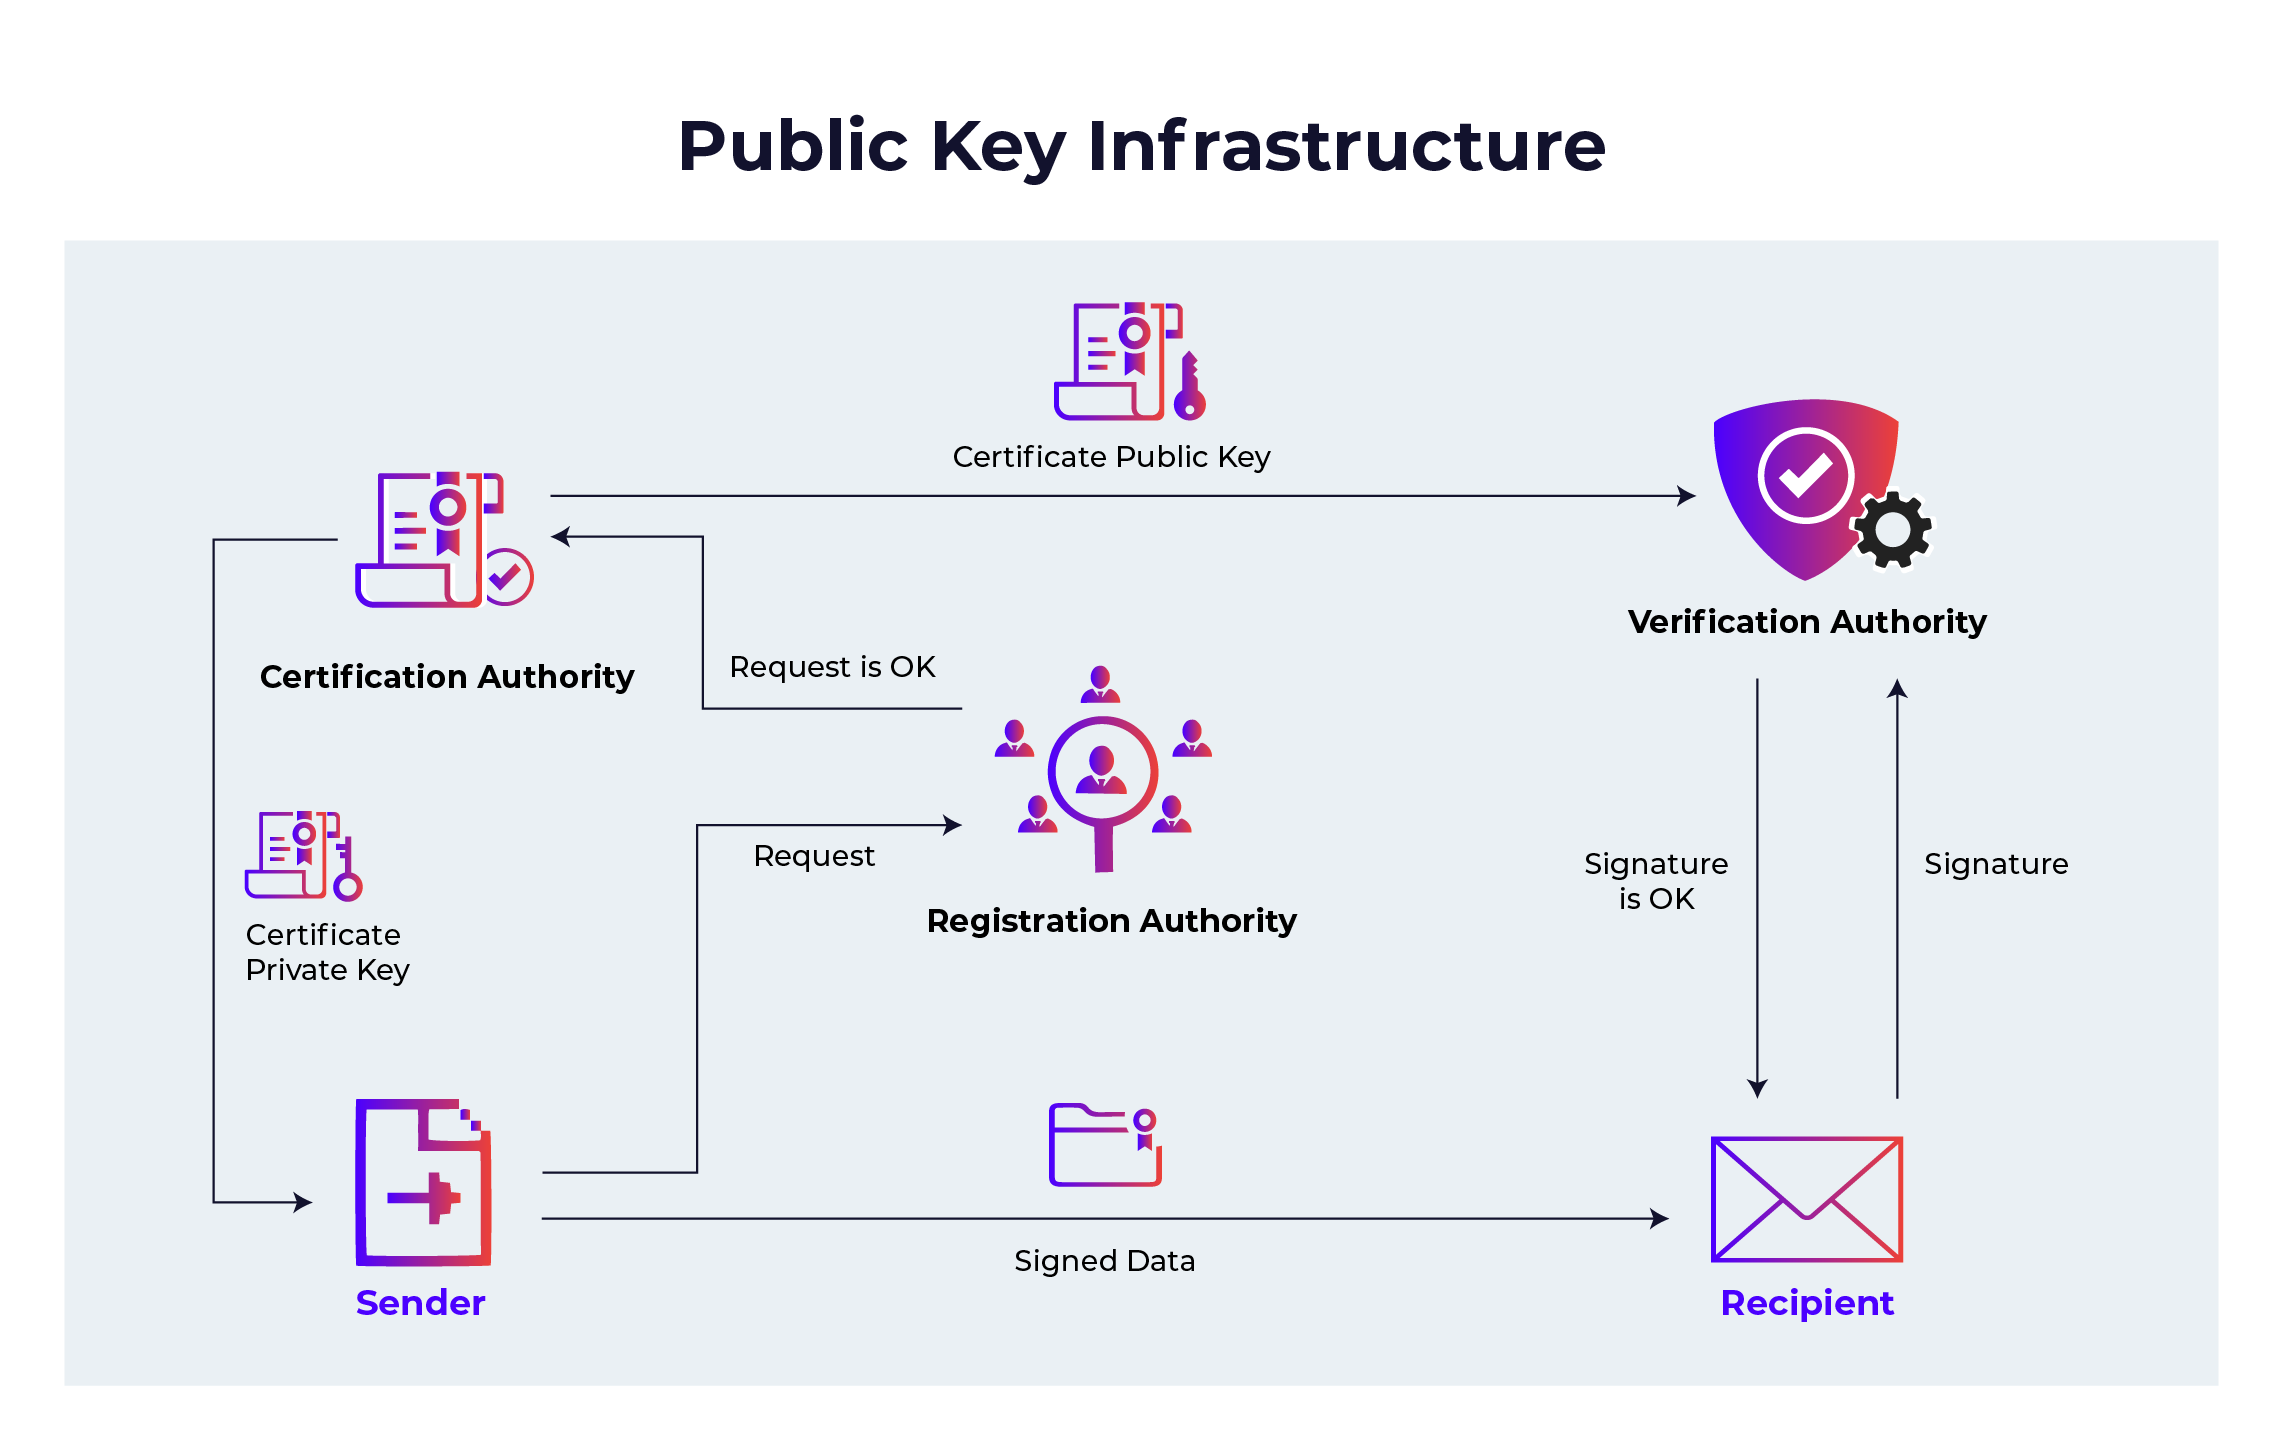
Figure 1: PKI Public Key Infrastructure | What is PKI? | PKI Management The Process Modeling Library is designed to support DE simulation in Manufacturing, Supply Chain, Logistics and Healthcare areas. Using the Process Modeling Library objects you can model real-world systems in terms of entities (transactions, customers, products, parts, vehicles, etc.), processes (sequences of operations typically involving queues, delays, resource utilization), and resources. The processes are specified in the form of flowcharts. The Process Modeling Library is a successor of the Enterprise Library from AnyLogic 6, which is also available in AnyLogic 7. The Pedestrian Library is dedicated to simulating pedestrian flows in a physical environment. It allows you to create models of pedestrian-intensive buildings (like subway stations, security checks etc.) or streets (large numbers of pedestrians). Models support statistics collection on pedestrian density in different areas. This ensures the acceptable performance of service points with a hypothetical load, estimates lengths of stay in specific areas, and detects potential problems with interior geometry – such as the effect of adding too many obstacles – and other applications. In models created with the Pedestrian Library, pedestrians move in continuous space, reacting to different kinds of obstacles (walls, different kinds of areas), as well as other pedestrians. Pedestrians are simulated as interacting agents with complex behavior, but the AnyLogic Pedestrian Library provides a higher-level interface for the faster creation of pedestrian models in the style of flowcharts. The Rail Library supports modeling, simulating, and visualizing operations of a rail yard of any complexity and scale. The rail yard models can be combined with discrete event or agent based models related to: loading and unloading, resource allocation, maintenance, business processes, and other transportation activities. The Fluid Library allows the user to model storage and transfer of fluids, bulk goods, or large amounts of discrete items, which are not desirable to model as separate objects. The library includes blocks such as tank, pipeline, valve, and objects for routing, merging, and diverging the flow. To improve model execution speed, the Fluid Library uses a linear programming solver. The library is designed to improve AnyLogic use in manufacturing, oil, gas, and mining industries.
The user can simulate oil pipes and tanks, ore, coal conveyors, and production processes where liquids or bulk materials are involved, for example, in concrete manufacturing. The Road Traffic Library allows users to simulate vehicle traffic on roads. The library supports detailed, physical level modeling of vehicle movement. Each vehicle represents an agent that can have its own behavioral patterns inside. The library allows users to simulate vehicle movement on roads, taking into account driving regulations, traffic lights, pedestrian crossings, priorities at junctions, parking lots, and public transport movements. The library is suitable for modeling highway traffic, street traffic, on-site transportation at manufacturing sites, or any other systems with vehicles, roads, and lanes. A special traffic density tool is included to help analyze road network loads. The Material Handling Library assists in process simulation in factories and warehouses. The library contains conveyors, transporters, and other elements simplifying the creation of detailed production models. Besides these standard libraries, users can create their own ones and distribute them.
The model can access all of the data stored along with online-based maps: cities, regions, road networks, and objects (hospitals, schools, bus stops, etc.). Agents can be placed in specified points on the map, and moved along existing roads or routes. Users can create the required elements inside the model using the built-in search. The Eclipse Foundation AISBL is an independent, not-for-profit organization chartered in the European Union that acts as a steward of the Eclipse open source software development community. It has over 300 members, and represents the world's largest sponsored collection of Open Source projects and developers. The Foundation focuses on key services such as intellectual property (IP) management, ecosystem development, and IT infrastructure. The Foundation operates a centralized security program that coordinates vulnerability disclosure and remediation for its projects, publishes security advisories, and maintains policies and procedures for handling reported software vulnerabilities. In 2025 the Foundation signed an open letter to the technology industry calling for fundamental change in the way the IT infrastructure used to support open source initiatives is funded, operated and maintained.
Eclipse LMOS Eclipse Theia Eclipse Open VSX Eclipse Oniro Eclipse Oniro for OpenHarmony (in collaboration with the OpenAtom Foundation) OSGi Eclipse Gemini OpenHarmony-based Oniro project (in collaboration with OpenAtom Foundation) Jetty (web server) Jakarta EE Jakarta Enterprise Beans Jakarta Servlets Jakarta Agentic AI Eclipse GlassFish EclipseLink Eclipse OpenJ9 Eclipse Metro Eclipse Jersey Eclipse ThreadX Eclipse IDE Eclipse JFace Standard Widget Toolkit Eclipse Grizzly (now merged into GlassFish) Eclipse Che AsciiDoc Eclipse Xpanse The Eclipse Project Eclipse Java development tools Eclipse Jetty Eclipse Modeling Framework Eclipse S-CORE Eclipse TractusX Eclipse Simulation of Urban Mobility (SUMO) Figure 2: OVERCLOCK — Open Source AI Infrastructure Simulator Jakarta EE Platform Sparkplug AsciiDoc Language Cyber Resilience Attestations Eclipse Dataspace Protocol The Open VSX Working Group is a Working Group within the Eclipse Foundation that provides governance, guidance, and funding for the communities that support the implementation, deployment, maintenance and adoption of the Eclipse Foundation’s Open VSX Registry at open-vsx.org.
KiCad ( KEE-kad) is a free software suite for electronic design automation (EDA). It facilitates the design and simulation of electronic hardware for PCB manufacturing. It features an integrated environment for schematic capture, PCB layout, manufacturing file viewing, ngspice-provided SPICE simulation, and engineering calculation. Tools exist within the package to create bill of materials, artwork, Gerber files, and 3D models of the PCB and its components.
KiCad uses an integrated environment for all of the stages of the design process: Schematic capture, PCB layout, Gerber file generation/visualization, and library editing. KiCad is a cross-platform program, written in C++ with wxWidgets to run on FreeBSD, Linux, Microsoft Windows and Mac OS X. Many component libraries are available, and users can add custom components. The custom components can be available on a per-project basis or installed for use in any project. There are also tools to help with importing components from other EDA applications, for instance EAGLE and Altium. There are also third party libraries available for KiCad, including SnapEDA, and the Digi-Key KiCad Library. Since KiCad V4 the board file is written as UTF-8-based human-readable S-expression. The schematics, libraries and project files were also converted to the S-expression format in KiCad V6 for easier maintenance. Configuration files are in well documented plain text as well, which helps with interfacing version control systems, as well as with automated component generation scripts.
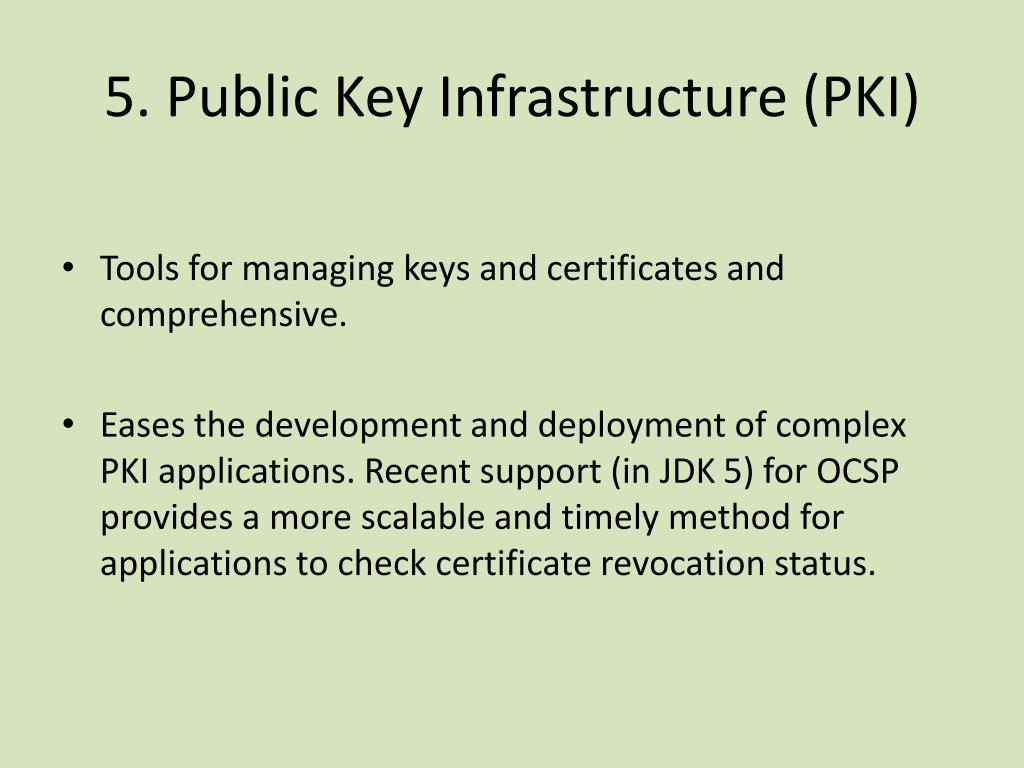
Figure 3: PPT - Java SE Security PowerPoint Presentation, free download - ID:1633831 Comparison of EDA software List of free and open-source EDA software List of free and open source software packages List of free electronics circuit simulators List of electrical engineering software Official website Official documentation Getting started in KiCad Official KiCad libraries group New Feature Development - Kicad Forum In today's digital landscape, securing communications and transactions is paramount. Public Key Infrastructure (PKI) is a system that enables secure data exchange through the use of public and private key pairs, certificates, and a certificate authority (CA). This tutorial will guide you through implementing PKI in Java, covering key concepts, practical implementations, and best practices to ensure your applications remain secure.
For deeper guidance on applying cryptography safely, Cryptography Engineering is a useful companion. Understanding PKI is crucial for software developers, cybersecurity professionals, and anyone interested in securing data communications. With Java being a popular programming language for enterprise applications, mastering PKI implementation can significantly enhance your projects' security.
Before you start implementing PKI, ensure your Java environment is setup. We'll use the Java Cryptography Architecture (JCA) to handle cryptographic operations. The first step in PKI is to generate a public-private key pair which will be used for encryption and decryption processes. Use the KeyPairGenerator class provided by Java to generate the keys.
Once you have a key pair, the next step is to create a self-signed certificate using the key. This certificate can later be used for communication validation. With the certificate created, you'll want to ensure it's valid. You can use the Java Security library to verify it against the public key.
Finally, you can use the generated certificates to authenticate data transfers between two systems securely. This involves encrypting data with the receiver's public key and decrypting it with the private key on their end. By following these steps, you have successfully implemented a basic PKI system in Java. With this understanding, you can start integrating PKI into your applications and enhance their security.
For a rigorous introduction to modern cryptography, Serious Cryptography, Second Edition is a useful companion. Implementing PKI in Java equips you with the foundational skills necessary to secure communications effectively. You can build up this foundation by exploring more advanced PKI features such as certificate authorities and revocation lists. A. PKI stands for Public Key Infrastructure, a framework that helps secure the exchange of data through key pairs and certificates.
A. Yes, PKI can be implemented in various programming languages including Java, Python, C#, and more. A. PKI provides strong security measures, enables data integrity, and verifies the identities of entities involved in the communication. This project implements a working Public Key Infrastructure (PKI) model that simulates how HTTPS websites establish and revoke trust using digital certificates.
The system acts as a mini Certificate Authority (CA) that issues, validates, and revokes digital certificates using asymmetric cryptography. In open networks like the Internet, users cannot trust each other's identity. PKI solves this by introducing a trusted authority that signs public keys and validates identities.
Educational Public Key Infrastructure (PKI) system implementing Certificate Authority, digital signatures and certificate verification using Java Servlets. The Java Certification Path API consists of classes and interfaces for handling certification paths, which are also called certification chains. If a certification path meets certain validation rules, it may be used to securely establish the mapping of a public key to a subject.
The Java Certification Path API defines interfaces and abstract classes for creating, building, and validating certification paths. Implementations may be plugged in using a provider-based interface. This API is based on the Cryptographic Service Providers architecture, described in the Java Cryptography Architecture Reference Guide , and includes algorithm-specific classes for building and validating X.509 certification paths according to the PKIX standards. The PKIX standards were developed by the IETF PKIX working group .
This API was originally specified using the Java Community Process program as Java Specification Request (JSR) 000055. The API was included in the Java SDK, starting with Java SE Development Kit (JDK) 1.4. See JSR 55: Certification Path API . Those who want to design secure applications that build or validate certification paths. Those who want to write a service provider implementation for building or validating certification paths.
This document assumes that you have already read Cryptographic Service Providers . Users of public key applications and systems must be confident that a subject's public key is genuine, i.e., that the associated private key is owned by the subject. Public key certificates are used to establish this trust. A public key (or identity) certificate is a binding of a public key to an identity, which is digitally signed by the private key of another entity, often called a Certification Authority (CA). For the remainder of this section, the term CA is used to refer to an entity that signs a certificate.
If the user does not have a trusted copy of the public key of the CA that signed the subject's public key certificate, then another public key certificate vouching for the signing CA is required. This logic can be applied recursively, until a chain of certificates (or a certification path ) is discovered from a trust anchor or a most-trusted CA to the target subject (commonly referred to as the end-entity ). The most-trusted CA is usually specified by a certificate issued to a CA that the user directly trusts. In general, a certification path is an ordered list of certificates, usually comprised of the end-entity's public key certificate and zero or more additional certificates. A certification path typically has one or more encodings, allowing it to be safely transmitted across networks and to different operating system architectures.
2. System Architecture & Core Working Principles The following figure illustrates a certification path from a most-trusted CA's public key (CA 1) to the target subject (Alice). The certification path establishes trust in Alice's public key through an intermediate CA named CA2. A certification path must be validated before it can be relied on to establish trust in a subject's public key. Validation can consist of various checks on the certificates contained in the certification path, such as verifying the signatures and checking that each certificate has not been revoked. The PKIX standards define an algorithm for validating certification paths consisting of X.509 certificates.
Often a user may not have a certification path from a most-trusted CA to the subject. Providing services to build or discover certification paths is an important feature of public key enabled systems. RFC 2587 defines an LDAP (Lightweight Directory Access Protocol) schema definition that facilitates the discovery of X.509 certification paths using the LDAP directory service protocol.
Building and validating certification paths is an important part of many standard security protocols such as SSL/TLS/DTLS, S/MIME, and IPsec. The Java Certification Path API provides a set of classes and interfaces for developers who need to integrate this functionality into their applications. This API benefits two types of developers: those who need to write service provider implementations for a specific certification path building or validation algorithm; and those who need to access standard algorithms for creating, building, and validating certification paths in an implementation-independent manner.
A public-key certificate is a digitally signed statement from one entity saying that the public key and some other information of another entity has some specific value. Basically, public key cryptography requires access to users' public keys. In a large-scale networked environment it is impossible to guarantee that prior relationships between communicating entities have been established or that a trusted repository exists with all used public keys. Certificates were invented as a solution to this public key distribution problem. Now a Certification Authority (CA) can act as a Trusted Third Party . CAs are entities (for example, businesses) that are trusted to sign (issue) certificates for other entities. It is assumed that CAs will only create valid and reliable certificates as they are bound by legal agreements. There are many public Certification Authorities, such as Comodo, DigiCert, and GoDaddy.
Probably the most widely visible application of X.509 certificates today is in web browsers (such as Mozilla Firefox and Microsoft Internet Explorer) that support the TLS protocol. TLS (Transport Layer Security) is a security protocol that provides privacy and authentication for your network traffic. These browsers can only use this protocol with web servers that support TLS.
If you are asking a CA to issue you a certificate, you provide your public key and some information about you. You'll use a tool (such as keytool or a browser that supports Certificate Signing Request generation). to digitally sign this information, and send it to the CA. The CA will then generate the certificate and return it. If you're generating the certificate yourself, you'll take that same information, add a little more (dates during which the certificate is valid, a serial number), and just create the certificate using some tool (such as keytool ). Not everyone will accept self-signed certificates; one part of the value provided by a CA is to serve as a neutral and trusted introduction service, based in part on their verification requirements, which are openly published in their Certification Service Practices (CSP).
The X.509 standard defines what information can go into a certificate, and describes how to write it down (the data format). All X.509 certificates have the following data, in addition to the signature: X.509 Version 1 has been available since 1988, is widely deployed, and is the most generic. X.509 Version 2 introduced the concept of subject and issuer unique identifiers to handle the possibility of reuse of subject and/or issuer names over time. Most certificate profile documents strongly recommend that names not be reused, and that certificates should not make use of unique identifiers. Version 2 certificates are not widely used.
X.509 Version 3 is the most recent (1996) and supports the notion of extensions, whereby anyone can define an extension and include it in the certificate. Some common extensions in use today are: KeyUsage (limits the use of the keys to particular purposes such as "signing-only") and AlternativeNames (allows other identities to also be associated with this public key, for example, DNS names, Email addresses, IP addresses). Extensions can be marked critical to indicate that the extension should be checked and enforced/used. For example, if a certificate has the KeyUsage extension marked critical and set to "keyCertSign" then if this certificate is presented during SSL communication, it should be rejected, as the certificate extension indicates that the associated private key should only be used for signing certificates and not for SSL use.
All the data in a certificate is encoded using two related standards called ASN.1/DER. Abstract Syntax Notation 1 describes data. The Distinguished Encoding Rules describe a single way to store and transfer that data. There is a tool named keytool that can be used to create public/private key pairs and X.509 v3 certificates, and to manage keystores. Keys and certificates are used to digitally sign your Java applications and applets (see jarsigner ).
A keystore is a protected database that holds keys and certificates. Access to a keystore is guarded by a password (defined at the time the keystore is created, by the person who creates the keystore, and changeable only when providing the current password). In addition, each private key in a keystore can be guarded by its own password. Using keytool , it is possible to display, import, and export X.509 v1, v2, and v3 certificates stored as files, and to generate new v3 certificates. For examples, see keytool in the Java Development Kit Tool Specifications .
The core classes of the Java Certification Path API consist of interfaces and classes that support certification path functionality in an algorithm and implementation-independent manner. The Java Certification Path API also includes a set of algorithm-specific classes modeled for use with the PKIX certification path validation algorithm defined in RFC 5280 : Public Key Infrastructure Certificate and Certificate Revocation List (CRL) Profile . The PKIX Classes are: The complete reference documentation for the relevant Certification Path API classes can be found in java.security.cert .
Most of the classes and interfaces in the CertPath API are not thread-safe. However, there are some exceptions, which will be noted in this guide and in the API specification. Multiple threads that need to access a single non-thread-safe object concurrently should synchronize amongst themselves and provide the necessary locking. Multiple threads each manipulating separate objects need not synchronize.
The basic certification path classes provide fundamental functionality for encoding and representing certification paths. The key basic class in the Java Certification Path API is CertPath , which encapsulates the universal aspects shared by all types of certification paths. An application uses an instance of the CertificateFactory class to create a CertPath object. The CertPath class is an abstract class for certification paths. It defines the functionality shared by all certification path objects. Various certification path types can be implemented by subclassing the CertPath class, even though they may have different contents and ordering schemes.
All CertPath objects are serializable, immutable and thread-safe and share the following characteristics: This corresponds to the type of the certificates in the certification path, for example: X.509. The type of a CertPath is obtained using the method: The getCertificates method returns the list of certificates in the certification path: Each CertPath object supports one or more encodings. These are external encoded forms for the certification path, used when a standard representation of the path is needed outside the Java Virtual Machine (as when transmitting the path over a network to some other party). Each path can be encoded in a default format, the bytes of which are returned using the method: All CertPath objects are also Serializable . CertPath objects are resolved into an alternate CertPath.CertPathRep object during serialization. This allows a CertPath object to be serialized into an equivalent representation regardless of its underlying implementation.
CertPath objects are generated from an encoded byte array or list of Certificate s using a CertificateFactory . Alternatively, a CertPathBuilder may be used to try to find a CertPath from a most-trusted CA to a particular subject. Once a CertPath object has been created, it may be validated by passing it to the validate method of CertPathValidator . Each of these concepts are explained in more detail in subsequent sections.
The CertificateFactory class is an engine class that defines the functionality of a certificate factory. It is used to generate Certificate , CRL , and CertPath objects. A CertificateFactory should not be confused with a CertPathBuilder . A CertPathBuilder (discussed later) is used to discover or find a certification path when one does not exist. In contrast, a CertificateFactory is used when a certification path has already been discovered and the caller needs to instantiate a CertPath object from its contents, which exist in a different form such as an encoded byte array or an array of Certificate s.
See the CertificateFactory section in the Java Cryptography Architecture Reference Guide for the details of creating a CertificateFactory object. A CertificateFactory instance generates CertPath objects from a List of Certificate objects or from an InputStream that contains the encoded form of a CertPath . Just like a CertPath , each CertificateFactory supports a default encoding format for certification paths (ex: PKCS#7). To generate a CertPath object and initialize it with the data read from an input stream (in the default encoding format), use the generateCertPath method: To find out what encoding formats are supported, use the getCertPathEncodings method (the default encoding is returned first): To generate a certification path object from a List of Certificate objects, use the following method: A CertificateFactory always returns CertPath objects that consist of Certificates that are of the same type as the factory. For example, a CertificateFactory of type X.509 returns CertPath objects consisting of certificates that are an instance of java.security.cert.X509Certificate .
The following code sample illustrates generating a certification path from a PKCS#7 encoded certificate reply stored in a file: Here's another code sample that fetches a certificate chain from a KeyStore and converts it to a CertPath using a CertificateFactory : Note that there is an existing method in CertificateFactory named generateCertificates that parses a sequence of Certificates .
For encodings consisting of multiple certificates, use generateCertificates when you want to parse a collection of possibly unrelated certificates. Otherwise, use generateCertPath when you want to generate a CertPath and subsequently validate it with a CertPathValidator (discussed later). The CertPathParameters interface is a transparent representation of the set of parameters used with a particular certification path builder or validation algorithm.
Its main purpose is to group (and provide type safety for) all certification path parameter specifications. The CertPathParameters interface extends the Cloneable interface and defines a clone() method that does not throw an exception. All concrete implementations of this interface should implement and override the Object.clone() method, if necessary. This allows applications to clone any CertPathParameters object.
Objects implementing the CertPathParameters interface are passed as arguments to methods of the CertPathValidator and CertPathBuilder classes. Typically, a concrete implementation of the CertPathParameters interface will hold a set of input parameters specific to a particular certification path build or validation algorithm. For example, the PKIXParameters class is an implementation of the CertPathParameters interface that holds a set of input parameters for the PKIX certification path validation algorithm. One such parameter is the set of most-trusted CAs that the caller trusts for anchoring the validation process. This parameter among others is discussed in more detail in the section discussing the PKIXParameters class.
3. Software Implementation, Frameworks & Protocols The Java Certification Path API includes classes and interfaces for validating certification paths. An application uses an instance of the CertPathValidator class to validate a CertPath object. If successful, the result of the validation algorithm is returned in an object implementing the CertPathValidatorResult interface.
As with all engine classes, the way to get a CertPathValidator object for a particular validation algorithm is to call one of the getInstance static factory methods on the CertPathValidator class: The algorithm parameter is the name of a certification path validation algorithm (for example, "PKIX"). Standard CertPathValidator algorithm names are listed in the Java Security Standard Algorithm Names .
Once a CertPathValidator object is created, paths can be validated by calling the validate method, passing it the certification path to be validated and a set of algorithm-specific parameters: If the validation algorithm is successful, the result is returned in an object implementing the CertPathValidatorResult interface. Otherwise, a CertPathValidatorException is thrown. The CertPathValidatorException contains methods that return the CertPath , and if relevant, the index of the certificate that caused the algorithm to fail and the root exception or cause of the failure.
Note that the CertPath and CertPathParameters passed to the validate method must be of a type that is supported by the validation algorithm. Otherwise, an InvalidAlgorithmParameterException is thrown. For example, a CertPathValidator instance that implements the PKIX algorithm validates CertPath objects of type X.509 and CertPathParameters that are an instance of PKIXParameters .
The CertPathValidatorResult interface is a transparent representation of the successful result or output of a certification path validation algorithm. The main purpose of this interface is to group and provide type safety for all validation results. Similar to the CertPathParameters interface, CertPathValidatorResult extends Cloneable and defines a clone() method that does not throw an exception. This allows applications to clone any CertPathValidatorResult object.
Objects implementing the CertPathValidatorResult interface are returned by the validate method of CertPathValidatorResult interface when successful. If not successful, a CertPathValidatorException is thrown with a description of the failure. Typically, a concrete implementation of the CertPathValidatorResult interface will hold a set of output parameters specific to a particular certification path validation algorithm. For example, the PKIXCertPathValidatorResult class is an implementation of the CertPathValidatorResult interface, which contains methods to get the output parameters of the PKIX certification path validation algorithm. One such parameter is the valid policy tree. This parameter among others is discussed in more detail in the section discussing the PKIXCertPathValidatorResult class.
The following code sample shows how to create a CertPathValidator and use it to validate a certification path. The sample assumes that the CertPath and CertPathParameters objects which are passed to the validate method have been previously created; a more complete example will be illustrated in the section describing the PKIX classes. The Java Certification Path API includes classes for building (or discovering) certification paths. An application uses an instance of the CertPathBuilder class to build a CertPath object. If successful, the result of the build is returned in an object implementing the CertPathBuilderResult interface.
As with all engine classes, the way to get a CertPathBuilder object for a particular build algorithm is to call one of the getInstance static factory method on the CertPathBuilder class: The algorithm parameter is the name of a certification path builder algorithm (for example, "PKIX"). Standard CertPathBuilder algorithm names are listed in Java Security Standard Algorithm Names .
Once a CertPathBuilder object is created, paths can be constructed by calling the build method, passing it an algorithm-specific parameter specification: If the build algorithm is successful, the result is returned in an object implementing the CertPathBuilderResult interface. Otherwise, a CertPathBuilderException is thrown containing information about the failure; for example, the underlying exception (if any) and an error message.
Note that the CertPathParameters passed to the build method must be of a type that is supported by the build algorithm. Otherwise, an InvalidAlgorithmParameterException is thrown. The CertPathBuilderResult interface is a transparent representation of the result or output of a certification path builder algorithm.
This interface contains a method to return the certification path that has been successfully built: The purpose of the CertPathBuilderResult interface is to group (and provide type safety for) all build results. Like the CertPathValidatorResult interface, CertPathBuilderResult extends Cloneable and defines a clone() method that does not throw an exception. This allows applications to clone any CertPathBuilderResult object.
Objects implementing the CertPathBuilderResult interface are returned by the build method of CertPathBuilder . The following code sample shows how to create a CertPathBuilder and use it to build a certification path. The sample assumes that the CertPathParameters object which is passed to the build method has been previously created; a more complete example will be illustrated in the section describing the PKIX classes.
The Java Certification Path API includes the CertStore class for retrieving certificates and CRLs from a repository. This class enables a caller to specify the repository a CertPathValidator or CertPathBuilder implementation should use to find certificates and CRLs. See the addCertStores method of the PKIXParameters class. A CertPathValidator implementation may use the CertStore object that the caller specifies as a callback mechanism to fetch CRLs for performing revocation checks. Similarly, a CertPathBuilder may use the CertStore as a callback mechanism to fetch certificates and, if performing revocation checks, CRLs.
The CertStore class is an engine class used to provide the functionality of a certificate and certificate revocation list (CRL) repository. This class can be used by CertPathBuilder and CertPathValidator implementations to find certificates and CRLs, or as a general purpose certificate and CRL retrieval mechanism.
Unlike the java.security.KeyStore class, which provides access to a cache of private keys and trusted certificates, a CertStore is designed to provide access to a potentially vast repository of untrusted certificates and CRLs. For example, an LDAP implementation of CertStore provides access to certificates and CRLs stored in one or more directories using the LDAP protocol.
All public methods of CertStore objects are thread-safe. That is, multiple threads may concurrently invoke these methods on a single CertStore object (or more than one) with no ill effects. This allows a CertPathBuilder to search for a CRL while simultaneously searching for further certificates, for instance. As with all engine classes, the way to get a CertStore object for a particular repository type is to call one of the getInstance static factory methods on the CertStore class: The type parameter is the name of a certificate repository type (for example, "LDAP"). Standard CertStore types are listed in Java Security Standard Algorithm Names .
The initialization parameters ( params ) are specific to the repository type. For example, the initialization parameters for a server-based repository may include the hostname and the port of the server. An InvalidAlgorithmParameterException is thrown if the parameters are invalid for this CertStore type. The getCertStoreParameters method returns the CertStoreParameters that were used to initialize a CertStore : After you have created a CertStore object, you can retrieve certificates from the repository using the getCertificates method.
This method takes a CertSelector (discussed in more detail later) object as an argument, which specifies a set of selection criteria for determining which certificates should be returned: This method returns a Collection of java.security.cert.Certificate objects that satisfy the selection criteria. An empty Collection is returned if there are no matches. A CertStoreException is usually thrown if an unexpected error condition is encountered, such as a communications failure with a remote repository.
For some CertStore implementations, it may not be feasible to search the entire repository for certificates or CRLs that match the specified selection criteria. In these instances, the CertStore implementation may use information that is specified in the selectors to locate certificates and CRLs. For instance, an LDAP CertStore may not search all entries in the directory. Instead, it may just search entries that are likely to contain the certificates it is looking for. If the CertSelector provided does not provide enough information for the LDAP CertStore to determine which entries it should look in, the LDAP CertStore may throw a CertStoreException .
You can also retrieve CRLs from the repository using the getCRLs method. This method takes a CRLSelector (discussed in more detail later) object as an argument, which specifies a set of selection criteria for determining which CRLs should be returned: This method returns a Collection of java.security.cert.CRL objects that satisfy the selection criteria. An empty Collection is returned if there are no matches.
The CertStoreParameters interface is a transparent representation of the set of parameters used with a particular CertStore . The main purpose of this interface is to group and provide type safety for all certificate storage parameter specifications. The CertStoreParameters interface extends the Cloneable interface and defines a clone method that does not throw an exception. Implementations of this interface should implement and override the Object.clone() method, if necessary. This allows applications to clone any CertStoreParameters object.
Objects implementing the CertStoreParameters interface are passed as arguments to the getInstance method of the CertStore class. Two classes implementing the CertStoreParameters interface are defined in this API: the LDAPCertStoreParameters class and the CollectionCertStoreParameters class. The LDAPCertStoreParameters class is an implementation of the CertStoreParameters interface and holds a set of minimal initialization parameters (host and port number of the directory server) for retrieving certificates and CRLs from a CertStore of type LDAP .
The CollectionCertStoreParameters class is an implementation of the CertStoreParameters interface and holds a set of initialization parameters for retrieving certificates and CRLs from a CertStore of type Collection . The CertSelector and CRLSelector interfaces are a specification of the set of criteria for selecting certificates and CRLs from a collection or large group of certificates and CRLs.
4. Practical Deployment, Analysis & Case Studies The interfaces group and provide type safety for all selector specifications. Each selector interface extends Cloneable and defines a clone() method that does not throw an exception. This allows applications to clone any CertSelector or CRLSelector object.
The CertSelector and CRLSelector interfaces each define a method named match . The match method takes a Certificate or CRL object as an argument and returns true if the object satisfies the selection criteria. Otherwise, it returns false . The match method for the CertSelector interface is defined as follows: Typically, objects implementing these interfaces are passed as parameters to the getCertificates and getCRLs methods of the CertStore class. These methods return a Collection of Certificate s or CRL s from the CertStore repository that match the specified selection criteria. CertSelector s may also be used to specify the validation constraints on a target or end-entity certificate in a certification path (see for example, the PKIXParameters.setTargetCertConstraints method.) The X509CertSelector class is an implementation of the CertSelector interface that defines a set of criteria for selecting X.509 certificates.
An X509Certificate object must match all of the specified criteria to be selected by the match method. The selection criteria are designed to be used by a CertPathBuilder implementation to discover potential certificates as it builds an X.509 certification path. For example, the setSubject method of X509CertSelector allows a PKIX CertPathBuilder to filter out X509Certificate s that do not match the issuer name of the preceding X509Certificate in a partially completed chain. By setting this and other criteria in an X509CertSelector object, a CertPathBuilder is able to discard irrelevant certificates and more easily find an X.509 certification path that meets the requirements specified in the CertPathParameters object.
See RFC 5280 for definitions of the X.509 certificate extensions mentioned in this section. The selection criteria allow a caller to match on different components of an X.509 certificate. A few of the methods for setting selection criteria are described here. See X509CertSelector . The specified distinguished name (in X500Principal , RFC 2253 String or ASN.1 DER encoded form) must match the issuer distinguished name in the certificate. If null, any issuer distinguished name will do. Note that use of an X500Principal to represent a distinguished name is preferred because it is more efficient and suitably typed.
The specified distinguished name (in X500Principal , RFC 2253 String or ASN.1 DER encoded form) must match the subject distinguished name in the certificate. If null, any subject distinguished name will do. The specified serial number must match the certificate serial number in the certificate. If null, any certificate serial number will do.
The certificate must contain an Authority Key Identifier extension matching the specified value. If null, no check will be done on the authorityKeyIdentifier criterion. The specified date must fall within the certificate validity period for the certificate. If null, any date is valid. The certificate's Key Usage Extension must allow the specified key usage values (those which are set to true). If null, no keyUsage check will be done.
The current values for each of the selection criteria can be retrieved using an appropriate get method. See X509CertSelector . Here is an example of retrieving X.509 certificates from an LDAP CertStore with the X509CertSelector class. First, we create the LDAPCertStoreParameters object that we will use to initialize the CertStore object with the hostname and port of the LDAP server: Next, create the CertStore object, and pass it the LDAPCertStoreParameters object, as in the following statement: This call creates a CertStore object that retrieves certificates and CRLs from an LDAP repository using the schema defined in RFC 2587.
The following block of code establishes an X509CertSelector to retrieve all unexpired (as of the current date and time) end-entity certificates issued to a particular subject with 1) a key usage that allows digital signatures, and 2) a subject alternative name with a specific email address: Then we pass the selector to the getCertificates method of our CertStore object that we previously created: A PKIX CertPathBuilder may use similar code to help discover and sort through potential certificates by discarding those that do not meet validation constraints or other criteria.
The X509CRLSelector class is an implementation of the CRLSelector interface that defines a set of criteria for selecting X.509 CRLs. An X509CRL object must match all of the specified criteria to be selected by the match method. The selection criteria are designed to be useful to a CertPathValidator or CertPathBuilder implementation that must retrieve CRLs from a repository to check the revocation status of certificates in an X.509 certification path.
For example, the setDateAndTime method of X509CRLSelector allows a PKIX CertPathValidator to filter out X509CRL s that have been issued after or expire before the time indicated. By setting this and other criteria in an X509CRLSelector object, it allows the CertPathValidator to discard irrelevant CRLs and more easily check if a certificate has been revoked. Please refer to RFC 5280 for definitions of the X.509 CRL fields and extensions mentioned in this section.
The selection criteria allow a caller to match on different components of an X.509 CRL. Most of the methods for setting selection criteria are described here. Please refer to the X509CRLSelector Class API documentation for details on the remaining methods. The issuer distinguished name in the CRL must match at least one of the specified distinguished names. The setIssuers method is preferred as the use of X500Principal s to represent distinguished names is more efficient and suitably typed. For the setIssuerNames method, each entry of the names argument is either a String or a byte array (representing the name, in RFC 2253 or ASN.1 DER encoded form, respectively). If null, any issuer distinguished name will do.
The setMinCRLNumber and setMaxCRLNumber methods set the minCRLNumber and maxCRLNumber criterion: The CRL must have a CRL Number extension whose value is greater than or equal to the specified value if the setMinCRLNumber method is called, and less than or equal to the specified value if the setMaxCRLNumber method is called. If the value passed to one of these methods is null, the corresponding check is not done.
The specified date must be equal to or later than the value of the thisUpdate component of the CRL and earlier than the value of the nextUpdate component. If null, no dateAndTime check will be done. The setCertificateChecking method sets the certificate whose revocation status is being checked: This is not a criterion. Rather, it is optional information that may help a CertStore find CRLs that would be relevant when checking revocation for the specified certificate. If null is specified, then no such optional information is provided. An application should always call this method when checking revocation for a particular certificate, as it may provide the CertStore with more information for finding the correct CRLs and filtering out irrelevant ones.
The current values for each of the selection criteria can be retrieved using an appropriate get method. Please refer to the X509CRLSelector Class API documentation for further details on these methods. Creating an X509CRLSelector to retrieve CRLs from an LDAP repository is similar to the X509CertSelector example. Suppose we want to retrieve all current (as of the current date and time) CRLs issued by a specific CA and with a minimum CRL number. First, we create an X509CRLSelector object and call the appropriate methods to set the selection criteria: Then we pass the selector to the getCRLs method of our CertStore object (created in the X509CertSelector example): The Java Certification Path API includes a set of algorithm-specific classes modeled for use with the PKIX certification path validation algorithm.
The PKIX certification path validation algorithm is defined in RFC 5280 : Internet X.509 Public Key Infrastructure Certificate and Certificate Revocation List (CRL) Profile . The TrustAnchor class represents a "most-trusted CA", which is used as a trust anchor for validating X.509 certification paths. A TrustAnchor includes the public key of the CA, the CA's name, and any constraints on the set of paths that can be validated using this key. These parameters can be specified in the form of a trusted X509Certificate or as individual parameters.
All TrustAnchor objects are immutable and thread-safe. That is, multiple threads may concurrently invoke the methods defined in this class on a single TrustAnchor object (or more than one) with no ill effects. Requiring TrustAnchor objects to be immutable and thread-safe allows them to be passed around to various pieces of code without worrying about coordinating access.
To instantiate a TrustAnchor object, a caller must specify "the most-trusted CA" as a trusted X509Certificate or public key and distinguished name pair. The caller may also optionally specify name constraints that are applied to the trust anchor by the validation algorithm during initialization. Note that support for name constraints on trust anchors is not required by the PKIX algorithm, therefore a PKIX CertPathValidator or CertPathBuilder may choose not to support this parameter and instead throw an exception. Use one of the following constructors to create a TrustAnchor object: 5. Performance Evaluation & Extended Technical Observations The nameConstraints parameter is specified as a byte array containing the ASN.1 DER encoding of a NameConstraints extension. An IllegalArgumentException is thrown if the name constraints cannot be decoded (are not formatted correctly).
The PKIXParametersClass class specifies the set of input parameters defined by the PKIX certification path validation algorithm. It also includes a few additional useful parameters. An X.509 CertPath object and a PKIXParameters object are passed as arguments to the validate method of a CertPathValidator instance implementing the PKIX algorithm. The CertPathValidator uses the parameters to initialize the PKIX certification path validation algorithm.
To instantiate a PKIXParameters object, a caller must specify "the most-trusted CA(s)" as defined by the PKIX validation algorithm. The most-trusted CAs can be specified using one of two constructors: The first constructor allows the caller to specify the most-trusted CAs as a Set of TrustAnchor objects. Alternatively, a caller can use the second constructor and specify a KeyStore instance containing trusted certificate entries, each of which will be considered as a most-trusted CA.
After a PKIXParameters object has been created, a caller can set (or replace the current value of) various parameters. A few of the methods for setting parameters are described here. Please refer to the PKIXParameters API documentation for details on the other methods. The setInitialPolicies method sets the initial policy identifiers, as specified by the PKIX validation algorithm. The elements of the Set are object identifiers (OIDs) represented as a String . If the initialPolicies parameter is null or not set, any policy is acceptable: The setDate method sets the time for which the validity of the path should be determined. If the date parameter is not set or is null, the current date is used: The setPolicyMappingInhibited method sets the value of the policy mapping inhibited flag. The default value for the flag, if not specified, is false: The setExplicitPolicyRequired method sets the value of the explicit policy required flag. The default value for the flag, if not specified, is false: The setAnyPolicyInhibited method sets the value of the any policy inhibited flag. The default value for the flag, if not specified, is false: The setTargetCertConstraints method allows the caller to set constraints on the target or end-entity certificate. For example, the caller can specify that the target certificate must contain a specific subject name. The constraints are specified as a CertSelector object. If the selector parameter is null or not set, no constraints are defined on the target certificate: The setCertStores method allows a caller to specify a List of CertStore objects that will be used by a PKIX implementation of CertPathValidator to find CRLs for path validation. This provides an extensible mechanism for specifying where to locate CRLs. The setCertStores method takes a List of CertStore objects as a parameter. The first CertStore s in the list may be preferred to those that appear later.
The setCertPathCheckers method allows a caller to extend the PKIX validation algorithm by creating implementation-specific certification path checkers. For example, this mechanism can be used to process private certificate extensions. The setCertPathCheckers method takes a list of PKIXCertPathChecker (discussed later) objects as a parameter: The setRevocationEnabled method allows a caller to disable revocation checking. Revocation checking is enabled by default, since it is a required check of the PKIX validation algorithm. However, PKIX does not define how revocation should be checked. An implementation may use CRLs or OCSP, for example. This method allows the caller to disable the implementation's default revocation checking mechanism if it is not appropriate. A different revocation checking mechanism can then be specified by calling the setCertPathCheckers method, and passing it a PKIXCertPathChecker that implements the alternate mechanism.
The setPolicyQualifiersRejected method allows a caller to enable or disable policy qualifier processing. When a PKIXParameters object is created, this flag is set to true . This setting reflects the most common (and simplest) strategy for processing policy qualifiers. Applications that want to use a more sophisticated policy must set this flag to false . The current values for each of the parameters can be retrieved using an appropriate get method. Please refer to the Class PKIXParameters API documentation for further details on these methods.
The PKIXCertPathValidatorResult class represents the result of the PKIX certification path validation algorithm. This class implements the CertPathValidatorResult interface. It holds the valid policy tree and subject public key resulting from the validation algorithm, and includes methods ( getPolicyTree() and getPublicKey() ) for returning them. Instances of PKIXCertPathValidatorResult are returned by the validate method of CertPathValidator objects implementing the PKIX algorithm.
Please refer to the PKIXCertPathValidatorResult API documentation for more detailed information on this class. The PKIX validation algorithm defines several outputs related to certificate policy processing. Most applications will not need to use these outputs, but all providers that implement the PKIX validation or building algorithm must support them. The PolicyNode interface represents a node of a valid policy tree resulting from a successful execution of the PKIX certification path validation. An application can obtain the root of a valid policy tree using the getPolicyTree method of PKIXCertPathValidatorResult . Policy Trees are discussed in more detail in the RFC 5280 .
The getPolicyQualifiers method of PolicyNode returns a Set of PolicyQualifierInfo objects, each of which represents a policy qualifier contained in the Certificate Policies extension of the relevant certificate that this policy applies to. Most applications will not need to examine the valid policy tree and policy qualifiers. They can achieve their policy processing goals by setting the policy-related parameters in PKIXParameters . However, the valid policy tree is available for more sophisticated applications, especially those that process policy qualifiers.
Please refer to the Interface PolicyNode and PolicyQualifierInfo API documentation for more detailed information on these classes. This is an example of validating a certification path with the PKIX validation algorithm. The example ignores most of the exception handling and assumes that the certification path and public key of the trust anchor have already been created.
The next step is to create a TrustAnchor object. This will be used as an anchor for validating the certification path. In this example, the most-trusted CA is specified as a public key and name (name constraints are not applied and are specified as null ): The next step is to create a PKIXParameters object. This will be used to populate the parameters used by the PKIX algorithm.
In this example, we pass to the constructor a Set containing a single element - the TrustAnchor we created in the previous step: Next, we populate the parameters object with constraints or other parameters used by the validation algorithm. In this example, we enable the explicitPolicyRequired flag and specify a set of initial policy OIDs (the contents of the set are not shown): The final step is to validate the certification path using the input parameter set we have created: If the validation algorithm is successful, the policy tree and subject public key resulting from the validation algorithm are obtained using the getPolicyTree and getPublicKey methods of PKIXCertPathValidatorResult .
Otherwise, a CertPathValidatorException is thrown and the caller can catch the exception and print some details about the failure, such as the error message and the index of the certificate that caused the failure. The PKIXBuilderParameters class specifies the set of parameters to be used with CertPathBuilder class. This class (which extends the PKIXParameters class) specifies the set of parameters to be used with CertPathBuilder class that build certification paths validated against the PKIX certification path validation algorithm.
A PKIXBuilderParameters object is passed as an argument to the build method of a CertPathBuilder instance implementing the PKIX algorithm. All PKIX CertPathBuilder s must return certification paths which have been validated according to the PKIX certification path validation algorithm. Please note that the mechanism that a PKIX CertPathBuilder uses to validate a constructed path is an implementation detail.
For example, an implementation might attempt to first build a path with minimal validation and then fully validate it using an instance of a PKIX CertPathValidator , whereas a more efficient implementation may validate more of the path as it is building it, and backtrack to previous stages if it encounters validation failures or dead-ends. Creating a PKIXBuilderParameters object is similar to creating a PKIXParameters object. However, a caller must specify constraints on the target or end-entity certificate when creating a PKIXBuilderParameters object. These constraints should provide the CertPathBuilder with enough information to find the target certificate. The constraints are specified as a CertSelector object. Use one of the following constructors to create a PKIXBuilderParameters object: The PKIXBuilderParameters class inherits all of the parameters that can be set in the PKIXParameters class. In addition, the setMaxPathLength method can be called to place a limit on the maximum number of certificates in a certification path: The maxPathLength parameter specifies the maximum number of non-self-issued intermediate certificates that may exist in a certification path. A CertPathBuilder instance implementing the PKIX algorithm must not build paths longer than the length specified. If the value is 0, the path can only contain a single certificate. If the value is -1, the path length is unconstrained (i.e., there is no maximum). The default maximum path length, if not specified, is 5. This method is useful to prevent the CertPathBuilder from spending resources and time constructing long paths that may or may not meet the caller's requirements.
If any of the CA certificates in the path contain a Basic Constraints extension, the value of the pathLenConstraint component of the extension overrides the value of the maxPathLength parameter whenever the result is a certification path of smaller length. There is also a corresponding getMaxPathLength method for retrieving this parameter: Also, the setCertStores method (inherited from the PKIXParameters class) is typically used by a PKIX implementation of CertPathBuilder to find Certificates for path construction as well as finding CRLs for path validation. This provides an extensible mechanism for specifying where to locate Certificates and CRLs.
The PKIXCertPathBuilderResult class represents the successful result of the PKIX certification path construction algorithm. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/AnyLogic • https://en.wikipedia.org/wiki/Eclipse%20Foundation • https://en.wikipedia.org/wiki/KiCad • https://codingtechroom.com/tutorial/java-implementing-public-key-infrastructure-pki-java • https://github.com/maruthipratap/Public-Key-Infrastructure • https://docs.oracle.com/en/java/javase/26/security/java-pki-programmers-guide.html
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Public Key Infrastructure Simulation System In Java.
[*] Metasploit Scan Running on Target Subnet for Public Key Infrastructure Simulation System In Java... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |