Complete Technical Paper Content — Qr Code Encryption And Decryption System For Payments
Overview & System Context
Qr Code Encryption And Decryption System For Payments: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~7272 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Signal is an open-source, encrypted messaging service for instant messaging, voice calls, and video calls. The instant messaging function includes sending text, voice notes, images, videos, and other files. Communication may be one-to-one between users or may involve group messaging. The application uses a centralized computing architecture and is cross-platform software. It is developed by the nonprofit Signal Foundation and its subsidiary Signal Messenger LLC. Signal's software is free and open-source. Its mobile clients, desktop client, and server are all published under the AGPL-3.0-only license. The official Android app generally uses the proprietary Google Play Services, although it is designed to be able to work without them. Signal is also distributed for iOS and desktop programs for Windows, macOS, and Linux. Registration for desktop use requires an iOS or Android device. Signal uses mobile telephone numbers to register and manage user accounts, though configurable usernames were added in March 2024 to allow users to hide their phone numbers from other users. After removing support for SMS on Android in 2023, the app now secures all communications with end-to-end encryption. The client software includes mechanisms by which users can independently verify their contacts' identities and the data channel's integrity. The nonprofit Signal Foundation was launched in February 2018 with initial funding of $50 million from WhatsApp co-founder Brian Acton. As of January 2025, the platform had approximately 70 million monthly active users. As of January 2025, it had been downloaded more than 220 million times.
Open Whisper Systems' website was launched in January 2013. In February 2014, Open Whisper Systems introduced the second version of their TextSecure Protocol (now Signal Protocol), which added end-to-end encrypted group chat and instant messaging capabilities to TextSecure. Toward the end of July 2014, they announced plans to merge the RedPhone and TextSecure applications as Signal. This announcement coincided with the initial release of Signal as a RedPhone counterpart for iOS. The developers said that their next steps would be to provide TextSecure instant messaging capabilities for iOS, unify the RedPhone and TextSecure applications on Android, and launch a web client. Signal was the first iOS app to enable end-to-end encrypted voice calls for free. TextSecure compatibility was added to the iOS application in March 2015.
From its launch in May 2010 until March 2015, the Android version of Signal (then called TextSecure) included support for encrypted SMS/MMS messaging. From version 2.7.0 onward, the Android application only supported sending and receiving encrypted messages via the data channel. Reasons for this included security flaws of SMS/MMS and problems with the key exchange. Open Whisper Systems' abandonment of SMS/MMS encryption prompted some users to create a fork named Silence (initially called SMSSecure) that is meant solely for the exchange of encrypted SMS and MMS messages. In November 2015, the TextSecure and RedPhone applications on Android were merged to become Signal for Android. A month later, Open Whisper Systems announced Signal Desktop, a Chrome app that could link with a Signal mobile client. At launch, the app could only be linked with the Android version of Signal. On 26 September 2016, Open Whisper Systems announced that Signal Desktop could now be linked with the iOS version of Signal as well. On 31 October 2017, Open Whisper Systems announced that the Chrome app was deprecated. At the same time, they announced the release of a standalone desktop client (based on the Electron framework) for Windows, macOS and certain Linux distributions. On 4 October 2016, the American Civil Liberties Union (ACLU) and Open Whisper Systems published a series of documents revealing that OWS had received a subpoena requiring them to provide information associated with two phone numbers for a federal grand jury investigation in the first half of 2016. Only one of the two phone numbers was registered on Signal, and because of how the service is designed, OWS was only able to provide "the time the user's account had been created and the last time it had connected to the service". Along with the subpoena, OWS received a gag order requiring OWS not to tell anyone about the subpoena for one year. OWS approached the ACLU, and they were able to lift part of the gag order after challenging it in court. OWS said it was the first time they had received a subpoena, and that they were "committed to treating any future requests the same way". In March 2017, Open Whisper Systems transitioned Signal's calling system from RedPhone to WebRTC, also adding the ability to make video calls with the mobile apps.
On 21 February 2018, Moxie Marlinspike and WhatsApp co-founder Brian Acton announced the formation of the Signal Technology Foundation, a 501(c)(3) nonprofit organization whose mission is "to support, accelerate, and broaden Signal's mission of making private communication accessible and ubiquitous". Acton started the foundation with $50 million in funding and became the foundation's executive chairman after leaving WhatsApp's parent company Facebook in September 2017.
Marlinspike continued as Signal Messenger's first CEO. As of 2020, Signal ran entirely on donations, as a nonprofit. Between November 2019 and February 2020, Signal added iPad support, view-once images and videos, stickers, and reactions. They also announced plans for a new group messaging system and an "experimental method for storing encrypted contacts in the cloud." Signal was reportedly popularized in the United States during the George Floyd protests. Heightened awareness of police monitoring led protesters to use the platform to communicate. Black Lives Matter organizers had used the platform "for several years". During the first week of June, the encrypted messaging app was downloaded over five times more than it had been during the week prior to the murder of George Floyd. In June 2020, Signal Foundation announced a new feature that enables users to blur faces in photos, in response to increased federal efforts to monitor protesters. On 7 January 2021, Signal saw a surge in new user registrations, which temporarily overwhelmed Signal's capacity to deliver account verification messages. CNN and MacRumors linked the surge with a WhatsApp privacy policy change and a Signal endorsement by Elon Musk and Edward Snowden via Twitter. The surge was also tied to the attack on the United States Capitol. International newspapers reported similar trends in the United Arab Emirates. Reuters reported that more than 100,000 people had installed Signal between 7 and 8 January. Between 12 and 14 January 2021, the number of Signal installations listed on Google Play increased from over 10 million to over 50 million. On 15 January 2021, due to the surge of new users, Signal was overwhelmed with the new traffic and was down for all users. On the afternoon of 16 January, Signal announced via Twitter that service had been restored. On 10 January 2022, Moxie Marlinspike announced that he was stepping down from his role as CEO of Signal Messenger. He continues to remain on the Signal Foundation's board of directors and Brian Acton has volunteered to serve as interim CEO during the search for a new CEO. In August 2022, Signal notified 1900 users that their data had been affected by the Twilio breach including user phone numbers and SMS verification codes. At least one journalist had his account re-registered to a device he did not control as a result of the attack. In September 2022 Signal Messaging LLC announced that AI researcher and noted critic of big tech Meredith Whittaker would fill the newly created position of president. In August 2024, Reuters reported on the blocking of Signal in Venezuela and Russia. In Venezuela, the blocking was a result of protests after the controversial presidential elections in which Nicolas Maduro declared his victory. In Russia, the reason was that Signal did not meet the requirements of legislation in the field of countering terrorism and extremism. In May 2026, Signal threatened to leave Canada because of the Lawful Access Act, stating that "Bill C-22 could potentially allow hackers to exploit these very vulnerabilities engineered into electronic systems, with private messaging services serving as an ideal target for foreign adversaries".
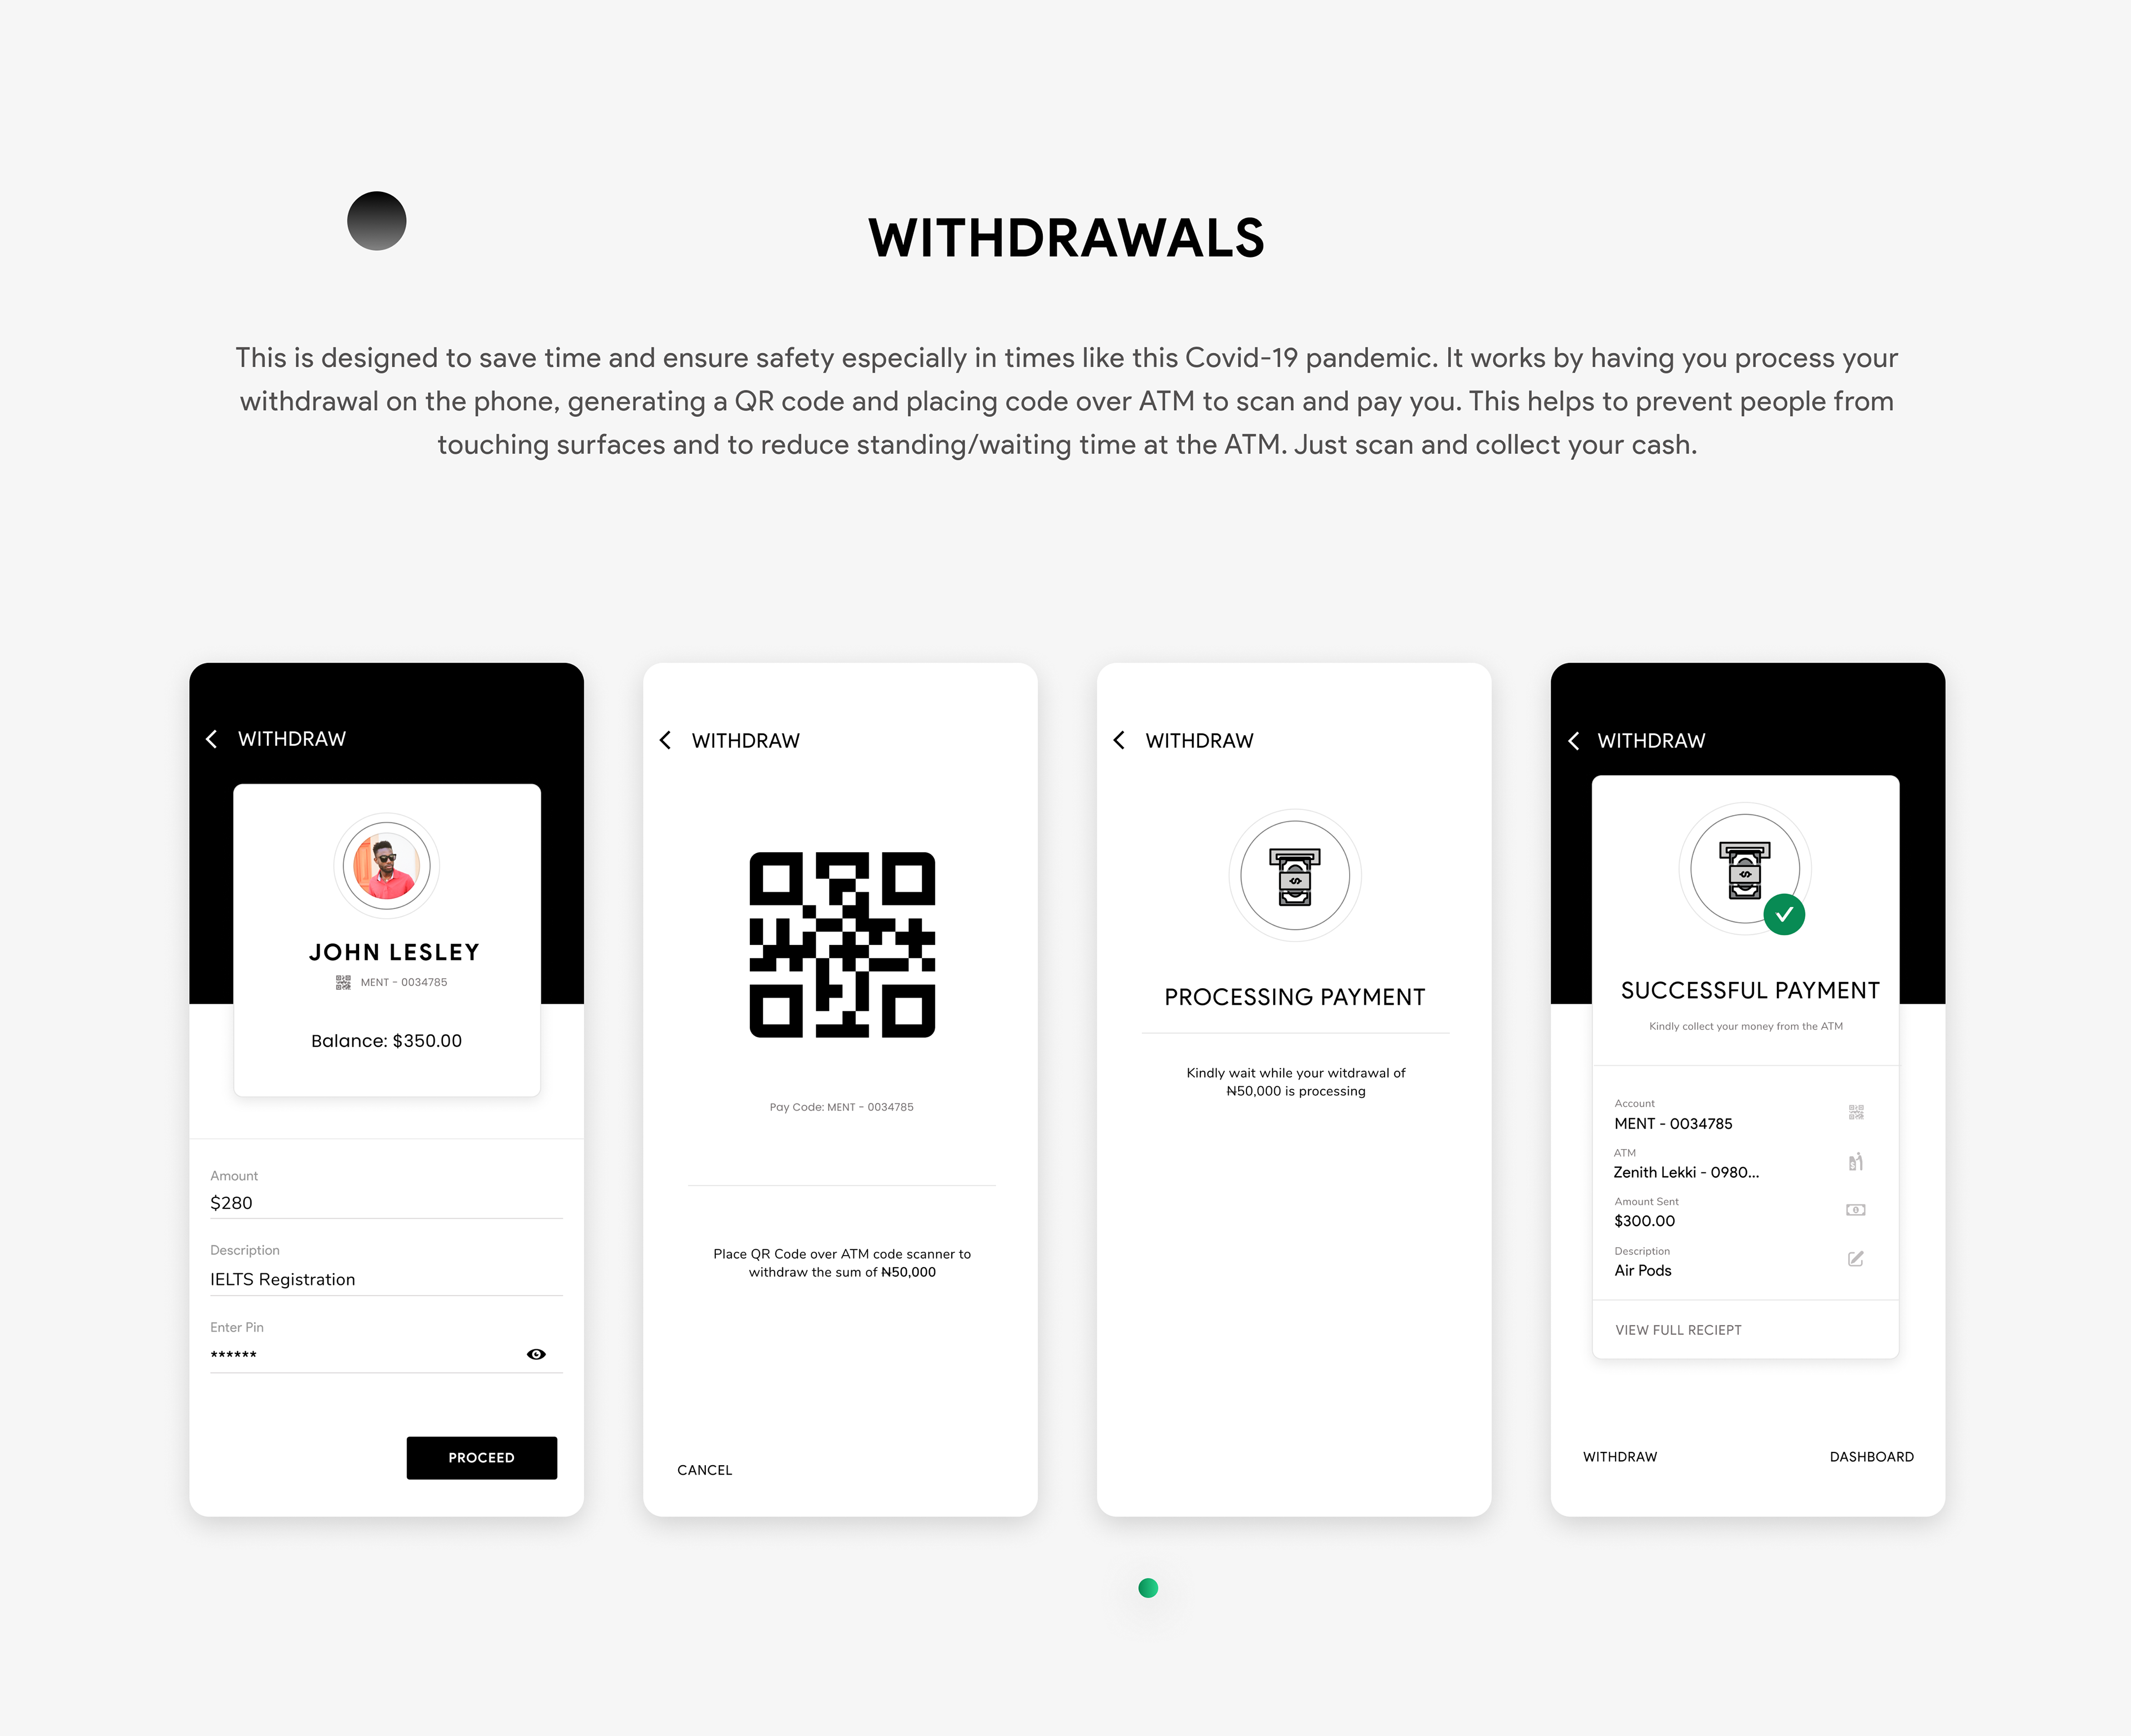
Figure 1: QR Code Payment UI :: Behance Signal messages are encrypted with the Signal Protocol (formerly known as the TextSecure Protocol). The protocol combines the Double Ratchet Algorithm, prekeys, and an Extended Triple Diffie–Hellman (X3DH) handshake. It uses Curve25519, AES-256, and HMAC-SHA256 as primitives. The protocol provides confidentiality, integrity, authentication, participant consistency, destination validation, forward secrecy, backward secrecy (a.k.a. future secrecy), causality preservation, message unlinkability, message repudiation, participation repudiation, and asynchronicity. It does not provide anonymity preservation, and requires servers for the relaying of messages and storing of public key material. The Signal Protocol also supports end-to-end encrypted group chats. The group chat protocol is a combination of a pairwise double ratchet and multicast encryption. In addition to the properties provided by the one-to-one protocol, the group chat protocol provides speaker consistency, out-of-order resilience, dropped message resilience, computational equality, trust equality, subgroup messaging, as well as contractible and expandable membership. According to a 2023 technical report, Signal adopted a protocol called Sender Keys for group messaging, and favors the protocol where possible (rather than the double ratchet) for group messaging, even in small groups. In October 2014, researchers from Ruhr University Bochum (RUB) published an analysis of the Signal Protocol. Among other findings, they presented an unknown key-share attack on the protocol, but in general, they found that it was secure. In October 2016, researchers from UK's University of Oxford, Queensland University of Technology in Australia, and Canada's McMaster University published a formal analysis of the protocol. They concluded that the protocol was cryptographically sound. In July 2017, researchers from RUB found during another analysis of group messengers a purely theoretic attack against the group protocol of Signal: A user who knows the secret group ID of a group (due to having been a group member previously or stealing it from a member's device) can become a member of the group.
Since the group ID cannot be guessed and such member changes are displayed to the remaining members, this attack is likely to be difficult to carry out without being detected. As of August 2018, the Signal Protocol has been implemented into WhatsApp, Facebook Messenger, Skype, and Google Allo, making it possible for the conversations of "more than a billion people worldwide" to be end-to-end encrypted. In Google Allo, Skype and Facebook Messenger, conversations are not encrypted with the Signal Protocol by default; they only offer end-to-end encryption in an optional mode. Up until March 2017, Signal's voice calls were encrypted with SRTP and the ZRTP key-agreement protocol, which was developed by Phil Zimmermann. In March 2017, Signal transitioned to a new WebRTC-based calling system that introduced the ability to make video calls. Signal's voice and video calling functionalities use the Signal Protocol channel for authentication instead of ZRTP.
In December 2016, Egypt blocked access to Signal. In response, Signal's developers added domain fronting to their service. This allows Signal users in a specific country to circumvent censorship by making it look like they are connecting to a different internet-based service. As of May 2022, Signal's domain fronting is enabled by default in Egypt, UAE, Oman, Qatar, Iran, Cuba, Pakistan and Uzbekistan. As of January 2018, Signal was blocked in Iran. Signal's domain fronting feature relies on the Google App Engine (GAE) service. This does not work in Iran because Google has blocked Iranian access to GAE in order to comply with U.S. sanctions. In early 2018, Google App Engine made an internal change to stop domain fronting for all countries. Due to this issue, Signal made a public change to use Amazon CloudFront for domain fronting. However, AWS also announced that they would be making changes to their service to prevent domain fronting. As a result, Signal said that they would start investigating new methods/approaches. Signal switched from AWS back to Google in April 2019. In January 2021, Iran removed the app from app stores, and blocked Signal. Signal was later blocked by China in March 2021, followed by its removal from the App Store in China on 19 April 2024. On August 9, 2024, Signal was blocked in Russia. Roskomnadzor claimed that this was due to "violations of the law on combating terrorism and extremism". Around the same time, Signal was also blocked in Venezuela following the contested 2024 presidential election and subsequent protests.
In March 2025, it was revealed that senior members of the Trump administration—including vice president JD Vance, secretary of state Marco Rubio, and defense secretary Pete Hegseth—were using Signal to discuss sensitive information, including details of military attack plans in Yemen. The existence of the chat was disclosed by The Atlantic editor-in-chief Jeffrey Goldberg, who was accidentally added to the chat. Brian Hughes of the National Security Council later confirmed the authenticity of Goldberg's account. On October 4, 2025, The Minnesota Star Tribune reported that Deputy Homeland Security Advisor Anthony Salisbury had been seen in public exchanging information on Signal with other government officials. Subjects discussed included potential troop deployments to Portland, Oregon, upcoming Immigration and Customs Enforcement (ICE) operations in Chicago, Vice President JD Vance's desire to prosecute two unnamed Florida influencers, and Federal Bureau of Investigation director Kash Patel's firing of FBI employees.
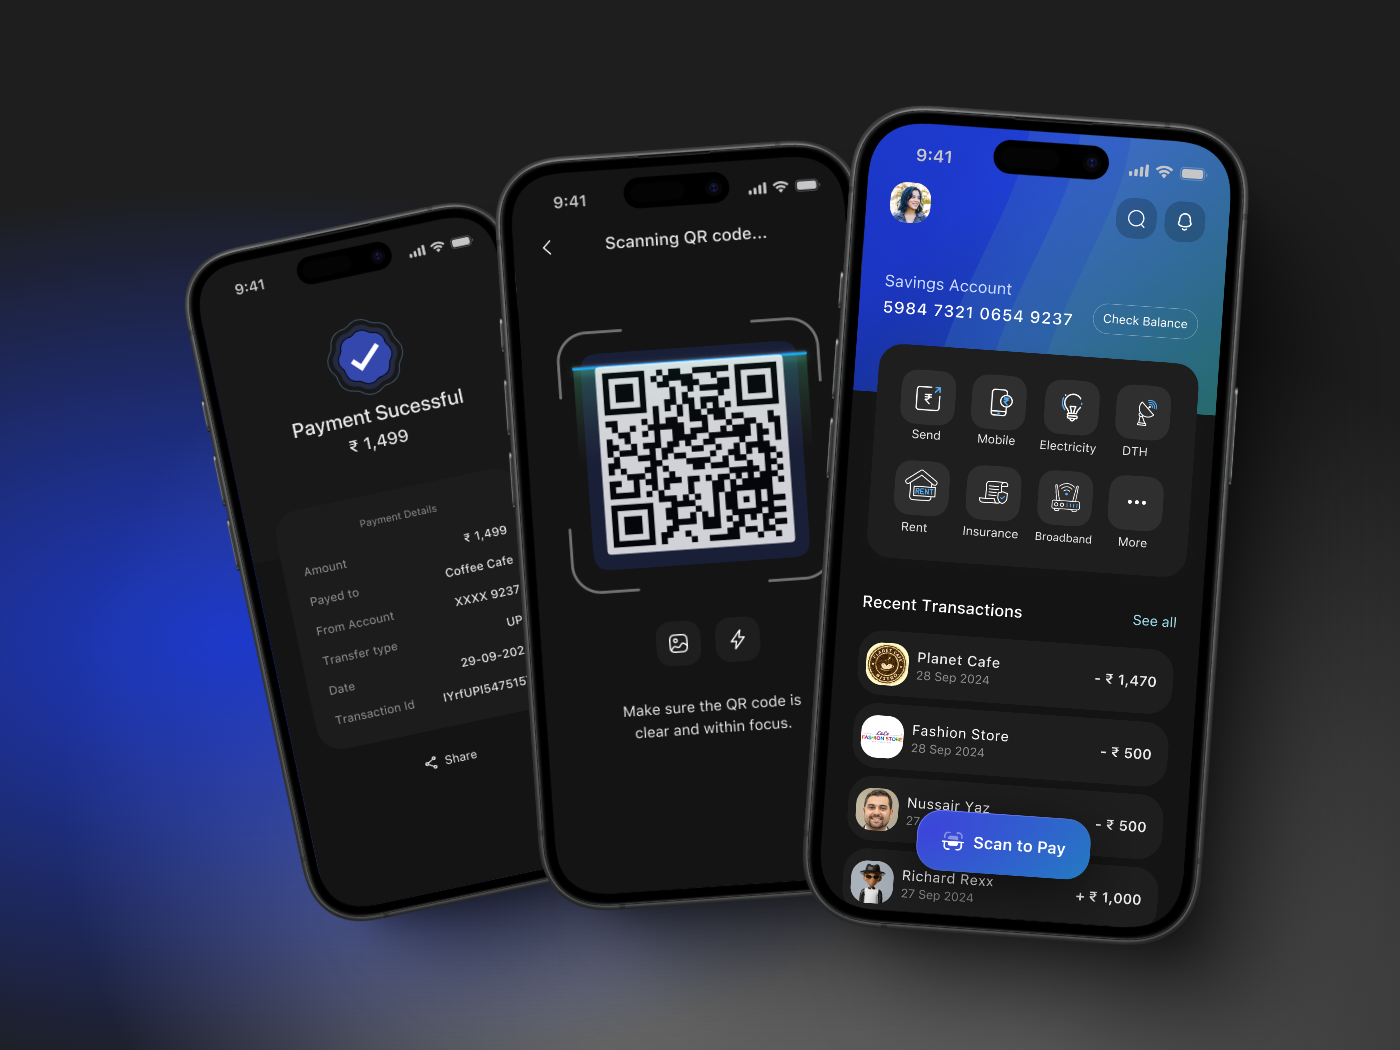
Comparison of cross-platform instant messaging clients Comparison of VoIP software Internet privacy List of video telecommunication services and product brands Secure communication Figure 2: Payment App & QR Code Scanning Design by Irshad Madambi on Dribbble Messenger is an American proprietary instant messaging service developed by Meta Platforms, the company that operates Facebook. Originally developed as Facebook Chat in 2008, the client application of Messenger is currently available on iOS and Android mobile platforms, through the Messenger.com web application, and on the standalone Meta Portal hardware.
Messenger is used to send messages and exchange photos, videos, stickers, audio, and files, and also react to other users' messages and interact with bots. The service also supports voice and video calling. The standalone apps support using multiple accounts, conversations with end-to-end encryption, and playing games. There are also group chats where you can connect with multiple people at once in a private space such as Panama Chat. With a monthly userbase of over 1 billion people, it is among the largest social media platforms.
2. System Architecture & Core Working Principles Following tests of a new instant messaging platform on Facebook in March 2008, the feature, then-titled "Facebook Chat", was gradually released to users in April 2008. Facebook revamped its messaging platform in November 2010, and subsequently acquired group messaging service Beluga in March 2011, which the company used to launch its standalone iOS and Android mobile apps on August 9, 2011. Facebook later launched a BlackBerry version in October 2011. An app for Windows Phone, though lacking features including voice messaging and chat heads, was released in March 2014. In April 2014, Facebook announced that the messaging feature would be removed from the main Facebook app and users will be required to download the separate Messenger app. An iPad-optimized version of the iOS app was released in July 2014. On April 8, 2015, Facebook launched a website interface for Messenger. A Tizen app was released on July 13, 2015. Facebook launched Messenger for Windows 10 in April 2016. In October 2016, Facebook released Messenger Lite, a stripped-down version of Messenger with a reduced feature set. The app is aimed primarily at old Android phones and regions where high-speed Internet is not widely available. In April 2017, Messenger Lite was expanded to 132 more countries. In May 2017, Facebook revamped the design for Messenger on Android and iOS, bringing a new home screen with tabs and categorization of content and interactive media, red dots indicating new activity, and relocated sections. Facebook announced a Messenger program for Windows 7 in a limited beta test in November 2011. The following month, Israeli blog TechIT leaked a download link for the program, with Facebook subsequently confirming and officially releasing the program. The program was eventually discontinued in March 2014. A Firefox web browser add-on was released in December 2012, but was also discontinued in March 2014. In December 2017, Facebook announced Messenger Kids, a new app aimed for persons under 13 years of age.
The app comes with some differences compared to the standard version. In 2019, Messenger announced to be the 2nd most downloaded mobile app of the decade, from 2011 to 2019. In December 2019, Messenger dropped support for users to sign in using only a mobile number, meaning that users must sign in to a Facebook account in order to use the service. In March 2020, Facebook started to ship its dedicated Messenger for macOS app through the Mac App Store. The app is currently live in regions including France, Australia, Mexico, Poland, and many others. In April 2020, Facebook began rolling out a new feature called Messenger Rooms, a video chat feature that allows users to chat with up to 50 people at a time. The feature rivals Zoom, an application that gained a lot of popularity during the COVID-19 pandemic. Privacy concerns arose since the feature uses the same data collection policies as mainstream Facebook. In July 2020, Facebook added a new feature in Messenger that lets iOS users to use Apple's Face ID or Touch ID to lock their chats. The feature is called App Lock and is a part of several changes in Messenger regarding privacy and security. The option to view only "Unread Threads" was removed from the inbox, requiring the account holder to scroll through the entire inbox to be certain every unread message has been seen. On October 13, 2020, the Messenger application introduced cross-app messaging with Instagram, which was launched in September 2021. In addition to the integrated messaging, the application announced the introduction of a new logo, which should be an amalgamation of the Messenger and Instagram logo. The desktop app of Messenger was shut down on December 15, 2025. Messaging services were moved to the Facebook website or Messenger's site for those without an account on the former. The Messenger site was discontinued on April 16, 2026. Messaging services were moved to the Facebook website on the morning of April 17, 2026; users without a Messenger account were required to use a Facebook account. However, later in 2026, the Messenger.com site continued to be functional.
Messenger Kids Comparison of cross-platform instant messaging clients Comparison of VoIP software A smart card (SC), chip card, or integrated circuit card (ICC or IC card), is a card used to control access to a resource. It is typically a plastic credit card-sized card with an embedded integrated circuit (IC) chip. Many smart cards include a pattern of metal contacts to electrically connect to the internal chip. Others are contactless, and some are both. Smart cards can provide personal identification, authentication, data storage, and application processing. Applications include identification, financial, public transit, computer security, schools, and healthcare. Smart cards may provide strong security authentication for single sign-on (SSO) within organizations. Numerous nations have deployed smart cards throughout their populations. The universal integrated circuit card (UICC) for mobile phones, installed as pluggable SIM card or embedded eSIM, is also a type of smart card. As of 2015, 10.5 billion smart card IC chips are manufactured annually, including 5.44 billion SIM card IC chips.
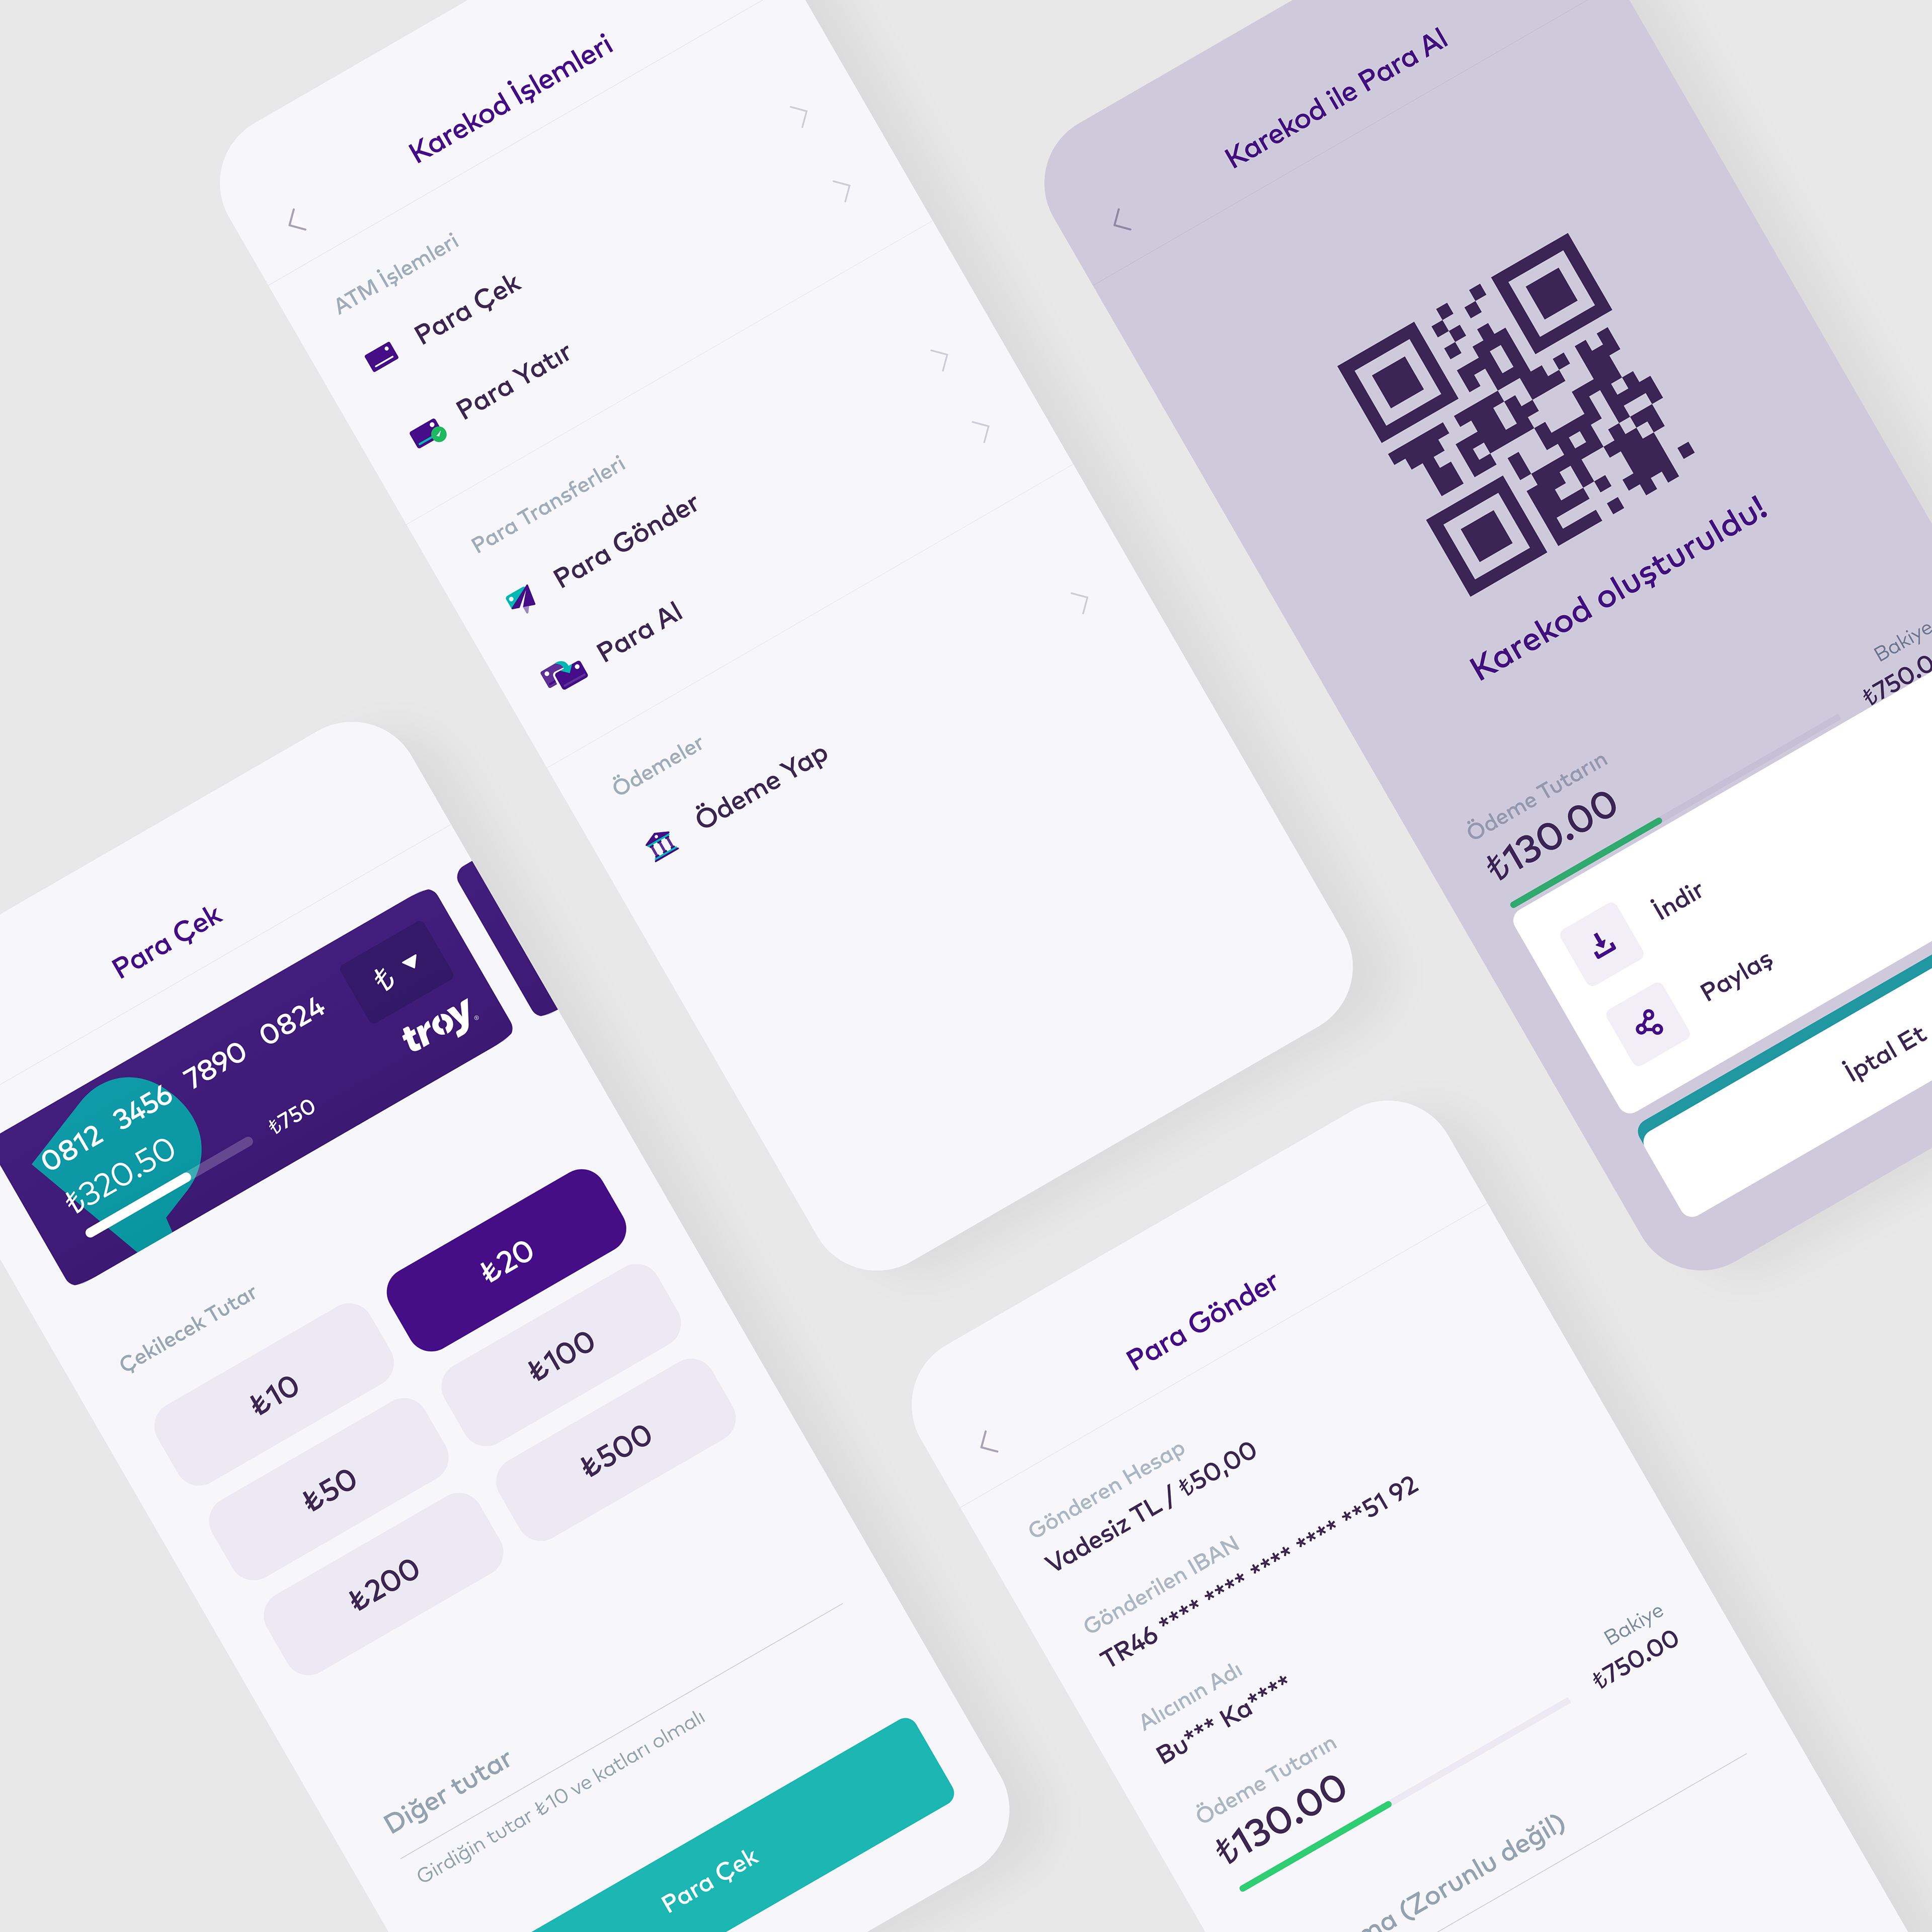
The basis for the smart card is the silicon integrated circuit (IC) chip, which was invented by Robert Noyce at Fairchild Semiconductor in 1959. In the late 1960s, this invention led to the idea of incorporating the IC chip onto a plastic card. Figure 3: Param - QR Code Payment UI :: Behance The idea of incorporating an integrated circuit chip onto a plastic card was first introduced by the German engineer Helmut Gröttrup. In February 1967, Gröttrup filed the patents DE1574074 and DE1574075 in West Germany for a tamper-proof identification switch based on a semiconductor device and described contactless communication via inductive coupling. Its primary use was intended to provide individual copy-protected keys for releasing the tapping process at unmanned gas stations. In September 1968, Gröttrup, together with Jürgen Dethloff as an investor, filed further patents for this identification switch, first in Austria and in 1969 as subsequent applications in the United States, Great Britain, West Germany and other countries. Independently, Kunitaka Arimura of the Arimura Technology Institute in Japan developed a similar idea of incorporating an integrated circuit onto a plastic card, and filed a smart card patent in March 1970. The following year, Paul Castrucci of IBM filed an American patent titled "Information Card" in May 1971. In 1974 Roland Moreno patented a secured memory card later dubbed the "smart card". In 1976, Jürgen Dethloff introduced the known element (called "the secret") to identify gate user as of USP 4105156. In 1977, Michel Ugon from Honeywell Bull invented the first microprocessor smart card with two chips: one microprocessor and one memory, and in 1978, he patented the self-programmable one-chip microcomputer (SPOM) that defines the necessary architecture to program the chip. Three years later, Motorola used this patent in its "CP8". At that time, Bull had 1,200 patents related to smart cards. In 2001, Bull sold its CP8 division together with its patents to Schlumberger, who subsequently combined its own internal smart card department and CP8 to create Axalto. In 2006, Axalto and Gemplus, at the time the world's top two smart-card manufacturers, merged and became Gemalto. In 2008, Dexa Systems spun off from Schlumberger and acquired Enterprise Security Services business, which included the smart-card solutions division responsible for deploying the first large-scale smart-card management systems based on public key infrastructure (PKI). The first mass use of the cards was as a telephone card for payment in French payphones, starting in 1983.
Europay MasterCard Visa (EMV)-compliant cards and equipment are widespread with the deployment led by European countries. The United States started later deploying the EMV technology in 2014, with the deployment still in progress in 2019. Typically, a country's national payment association, in coordination with MasterCard International, Visa International, American Express and Japan Credit Bureau (JCB), jointly plan and implement EMV systems. Historically, in 1993 several international payment companies agreed to develop smart-card specifications for debit and credit cards. The original brands were MasterCard, Visa, and Europay. The first version of the EMV system was released in 1994. In 1998 the specifications became stable. EMVCo maintains these specifications. EMVco's purpose is to assure the various financial institutions and retailers that the specifications retain backward compatibility with the 1998 version. EMVco upgraded the specifications in 2000 and 2004. EMV compliant cards were first accepted into Malaysia in 2005 and later into United States in 2014.
MasterCard was the first company that was allowed to use the technology in the United States. The United States has felt pushed to use the technology because of the increase in identity theft. The credit card information stolen from Target in late 2013 was one of the largest indicators that American credit card information is not safe. Target made the decision on 30 April 2014 that it would try to implement the smart chip technology to protect itself from future credit card identity theft. Before 2014, the consensus in America was that there were enough security measures to avoid credit card theft and that the smart chip was not necessary. The cost of the smart chip technology was significant, which was why most of the corporations did not want to pay for it in the United States. The debate finally ended when Target sent out a notice stating unauthorized access to magnetic strips costing Target over 300 million dollars along with the increasing cost of online credit theft was enough for the United States to invest in the technology. The adaptation of EMV's increased significantly in 2015 when the liability shifts occurred in October by the credit card companies.
Contactless smart cards do not require physical contact between a card and reader. They are becoming more popular for payment and ticketing. Typical uses include mass transit and motorway tolls. Visa and MasterCard implemented a version deployed in 2004–2006 in the U.S., with Visa's current offering called Visa Contactless. Most contactless fare collection systems are incompatible, though the MIFARE Standard card from NXP Semiconductors has a considerable market share in the US and Europe. Use of "Contactless" smart cards in transport has also grown through the use of low cost chips NXP Mifare Ultralight and paper/card/PET rather than PVC. This has reduced media cost so it can be used for low cost tickets and short term transport passes (up to 1 year typically). The cost is typically 10% that of a PVC smart card with larger memory.
They are distributed through vending machines, ticket offices and agents. Use of paper/PET is less harmful to the environment than traditional PVC cards. Smart cards are also being introduced for identification and entitlement by regional, national, and international organizations. These uses include citizen cards, drivers’ licenses, and patient cards. In Malaysia, the compulsory national ID MyKad enables eight applications and has 18 million users. Contactless smart cards are part of ICAO biometric passports to enhance security for international travel.
One or more buttons, A digital keyboard, An alphabetic keyboard, A touch keyboard, A small display, for a dynamic Card Security Code (CSC) for instance, A larger digital display, for OTP or balance, QR code An alphanumeric display, A fingerprint sensor, A LED, A buzzer or speaker. While first generation Complex Cards were battery powered, the second generation is battery-free and receives power through the usual card connector and/or induction . Sound, generated by a buzzer, was the preferred means of communication for the first projects involving Complex Cards. Later, with the progress of displays, visual communication is now present in almost all Complex Cards.
One Time Password, Provide account information, Provide computation capabilities, Provide a means of transaction security, Provide a means of user authentication. 3. Software Implementation, Frameworks & Protocols Standard Chartered, Singapore, Bank of America, USA, Erste Bank, Croatia, Verisign, USA, RSA Security.
Getin Bank, Poland, TEB, Turkey. The latest generation of battery free, button free, Complex Cards can display a balance or other kind of information without requiring any input from the card holder. The information is updated during the use of the card. For instance, in a transit card, key information such as the monetary value balance, the number of remaining trips or the expiry date of a transit pass can be displayed.
MotionCode, first developed by NagraID Security, a company later acquired by IDEMIA, DCV, the solution offered by Thales, EVC (Ellipse Verification Code) by Ellipse, a Los Angeles, USA based company. The advantage of the Dynamic Card Security Code (DCSC) is that new information is transmitted with the payment transactions, thus making it useless for a potential fraudster to memorize or store it. A transaction with a Dynamic Card Security Code is carried out exactly the same way, with the same processes and use of parameters as a transaction with a static code in a card-not-present transaction. Upgrading to a DCSC allows cardholders and merchants to continue their payment habits and processes undisturbed.
Thales: Biometric card, IDEMIA: F.Code, originally developed by NagraID Security, IDEX Biometrics, NXP Semiconductors Select one action, such as which account to obtain the balance, or the unit (e.g. currency or number of trips) in which the information is displayed, Enter numeric data via the addition of a digital keypad, Enter text data via the addition of an alphanumeric keyboard. While separate keys have been used on prototypes in the early days, capacitive keyboards are the most popular solution now, thanks to technology developments by AudioSmartCard International SA. The interaction with a capacitive keyboard requires constant power, therefore a battery and a mechanical button are required to activate the card.
Liquid-crystal display (LCD) : LCDs are easily available from a wide variety of suppliers, and they are able to display either digits or alphabetical data. However, to be fitted in a complex smart card, LCDs need to have a certain degree of flexibility. Also, LCDs need to be powered to keep information displayed. Bistable displays, also known as Ferroelectric liquid crystal displays, are increasingly used as they only require power to refresh the displayed information. The displayed data remains visible, without the need for of any power supply. Bistable displays are also available in a variety of specifications, displaying digits or pixels. Bistable displays are available from E Ink Corporation among others.
Manufacturing, Personalization, User enrollment, if needed by the application, Provisioning, Active life, Cancellation, Recycling / destruction. As Complex Cards bring more functionalities than standard smart cards and, due to their complexity, their personalization can take longer or require more inputs. Having Complex Cards that can be personalized by the same machines and the same processes as regular smart cards allows them to be integrated more easily in existing manufacturing chains and applications. First generation, battery-operated Complex Cards require specific recycling processes, mandated by different regulatory bodies. Additionally, keeping battery-operated Complex Cards in inventory for extended periods of time may reduce their performance due to battery ageing. Second-generation battery-free technology ensures operation during the entire lifetime of the card and eliminates self-discharge, providing extended shelf life, and is more eco-friendly.
ABSA, South Africa, Banco Bicentenario, Venezuela, Banco MontePaschi, Belgium, Erste Bank, Croatia, Getin Bank, Poland, Standard Chartered Bank, Singapore. NagraID Security also delivered One-Time Password cards to companies including: Bank of America, HID Security, PayPal, RSA Security, Verisign. In 2014, NagraID Security was sold to Oberthur Technologies (now IDEMIA).
4. Practical Deployment, Analysis & Case Studies ABSA, South Africa, Banca MontePaschi Belgio, Bank of America, USA, BPCE Group, France, Carpatica Bank, Romania, Credit Europe Bank, Romania, Erste & Steiermärkische Bank, Croatia Getin Bank, Poland, Newcastle Banking Society, UK, Orange Bank, France, PayPal, USA, Sinopac, Taiwan, Société Générale, France, Standard Chartered Bank, Singapore, Symantec, TEB, Turkey.
Dimensions similar to those of a credit card. ID-1 of the ISO/IEC 7810 standard defines cards as nominally 85.60 by 53.98 millimetres (3.37 in × 2.13 in). Another popular size is ID-000, which is nominally 25 by 15 millimetres (0.98 in × 0.59 in) (commonly used in SIM cards). Both are 0.76 millimetres (0.030 in) thick. Contains a tamper-resistant security system (for example a secure cryptoprocessor and a secure file system) and provides security services (e.g., protects in-memory information). Managed by an administration system, which securely interchanges information and configuration settings with the card, controlling card blacklisting and application-data updates. Communicates with external services through card-reading devices, such as ticket readers, ATMs, Dip reader, etc. Smart cards are typically made of plastic, generally polyvinyl chloride, but sometimes polyethylene-terephthalate-based polyesters, acrylonitrile butadiene styrene or polycarbonate. Since April 2009, a Japanese company has manufactured reusable financial smart cards made from paper.
EEPROM only. EEPROM, ROM, RAM, and microprocessor. EEPROM, ROM, RAM, microprocessor, and secure element. In cards with microprocessors, the microprocessor sits inline between the reader and the other components. The operating system that runs on the microprocessor mediates the reader's access to those components to prevent unauthorized access. Contact smart cards have a contact area of approximately 1 square centimetre (0.16 sq in), comprising several gold-plated contact pads. These pads provide electrical connectivity when inserted into a reader, which is used as a communications medium between the smart card and a host (e.g., a computer, a point of sale terminal) or a mobile telephone. Cards do not contain batteries; power is supplied by the card reader. The ISO/IEC 7810 and ISO/IEC 7816 series of standards define: physical shape and characteristics, electrical connector positions and shapes, electrical characteristics, communications protocols, including commands sent to and responses from the card, basic functionality. Because the chips in financial cards are the same as those used in subscriber identity modules (SIMs) in mobile phones, programmed differently and embedded in a different piece of PVC, chip manufacturers are building to the more demanding GSM/3G standards. So, for example, although the EMV standard allows a chip card to draw 50 mA from its terminal, cards are normally well below the telephone industry's 6 mA limit. This allows smaller and cheaper financial card terminals. Communication protocols for contact smart cards include T=0 (character-level transmission protocol, defined in ISO/IEC 7816-3) and T=1 (block-level transmission protocol, defined in ISO/IEC 7816-3).
Contactless smart cards communicate with readers under protocols defined in the ISO/IEC 14443 standard. They support data rates of 106–848 kbit/s. These cards require only proximity to an antenna to communicate. Like smart cards with contacts, contactless cards do not have an internal power source. Instead, they use a loop antenna coil to capture some of the incident radio-frequency interrogation signal, rectify it, and use it to power the card's electronics. Contactless smart media can be made with PVC, paper/card and PET finish to meet different performance, cost and durability requirements. APDU transmission by a contactless interface is defined in ISO/IEC 14443-4.
Hybrid cards implement contactless and contact interfaces on a single card with unconnected chips including dedicated modules/storage and processing. Dual-interface Dual-interface cards implement contactless and contact interfaces on a single chip with some shared storage and processing. An example is Porto's multi-application transport card, called Andante, which uses a chip with both contact and contactless (ISO/IEC 14443 Type B) interfaces. Numerous payment cards worldwide are based on hybrid card technology allowing them to communicate in contactless as well as contact modes.
Visa: Visa Contactless, Quick VSDC, "qVSDC", Visa Wave, MSD, payWave Mastercard: PayPass Magstripe, PayPass MChip American Express: ExpressPay Discover: Zip Unionpay: QuickPass Roll-outs started in 2005 in the U.S. Asia and Europe followed in 2006. Contactless (non-PIN) transactions cover a payment range of ~$5–50. There is an ISO/IEC 14443 PayPass implementation. Some, but not all, PayPass implementations conform to EMV. Non-EMV cards work like magnetic stripe cards. This is common in the U.S. (PayPass Magstripe and Visa MSD). The cards do not hold or maintain the account balance. All payment passes without a PIN, usually in off-line mode. The security of such a transaction is no greater than with a magnetic stripe card transaction. EMV cards can have either contact or contactless interfaces. They work as if they were a normal EMV card with a contact interface. Via the contactless interface they work somewhat differently, in that the card commands enabled improved features such as lower power and shorter transaction times. EMV standards include provisions for contact and contactless communications. Typically modern payment cards are based on hybrid card technology and support both contact and contactless communication modes.
5. Performance Evaluation & Extended Technical Observations Smart cards, used as transit passes, and integrated ticketing are used by many public transit operators. Card users may also make small purchases using the cards. Some operators offer points for usage, exchanged at retailers or for other benefits. Examples include Singapore's CEPAS, Malaysia's Touch 'n Go, Ontario's Presto card, Hong Kong's Octopus card, Tokyo's Suica and PASMO cards, London's Oyster card, Ireland's Leap Card, Brussels' MoBIB, Québec's Opus card, Boston's CharlieCard, San Francisco's Clipper card, Washington, D.C.'s SmarTrip, Auckland's AT Hop, Brisbane's go card, Perth's SmartRider, Sydney's Opal card and Victoria's myki. However, these present a privacy risk because they allow the mass transit operator (and the government) to track an individual's movement. In Finland, for example, the Data Protection Ombudsman prohibited the transport operator Helsinki Metropolitan Area Council (YTV) from collecting such information, despite YTV's argument that the card owner has the right to a list of trips paid with the card. Earlier, such information was used in the investigation of the Myyrmanni bombing. The UK's Department for Transport mandated smart cards to administer travel entitlements for elderly and disabled residents. These schemes let residents use the cards for more than just bus passes. They can also be used for taxi and other concessionary transport. One example is the "Smartcare go" scheme provided by Ecebs. The UK systems use the ITSO Ltd specification. Other schemes in the UK include period travel passes, carnets of tickets or day passes and stored value which can be used to pay for journeys. Other concessions for school pupils, students and job seekers are also supported. These are mostly based on the ITSO Ltd specification. Many smart transport schemes include the use of low cost smart tickets for simple journeys, day passes and visitor passes. Examples include Glasgow SPT subway. These smart tickets are made of paper or PET which is thinner than a PVC smart card e.g. Confidex smart media. The smart tickets can be supplied pre-printed and over-printed or printed on demand. In Sweden, as of 2018–19, the old SL Access smart card system has started to be phased out and replaced by smart phone apps. The phone apps have less cost, at least for the transit operators who don't need any electronic equipment (the riders provide that). The riders are able buy tickets anywhere and don't need to load money onto smart cards. New NFC smart cards are still in use for foreseeable future (as of 2024).
Tracking student attendance As an electronic purse, to pay for items at canteens, vending machines, laundry facilities, etc. Tracking and monitoring food choices at the canteen, to help the student maintain a healthy diet Tracking loans from the school library Access control for admittance to restricted buildings, dormitories, and other facilities. This requirement may be enforced at all times (such as for a laboratory containing valuable equipment), or just during after-hours periods (such as for an academic building that is open during class times, but restricted to authorized personnel at night), depending on security needs. Access to transportation services Smart health cards can improve the security and privacy of patient information, provide a secure carrier for portable medical records, reduce health care fraud, support new processes for portable medical records, provide secure access to emergency medical information, enable compliance with government initiatives (e.g., organ donation) and mandates, and provide the platform to implement other applications as needed by the health care organization.
Smart cards have been advertised as suitable for personal identification tasks, because they are engineered to be tamper resistant. The chip usually implements some cryptographic algorithm. There are, however, several methods for recovering some of the algorithm's internal state. Differential power analysis involves measuring the precise time and electric current required for certain encryption or decryption operations. This can deduce the on-chip private key used by public key algorithms such as RSA. Some implementations of symmetric ciphers can be vulnerable to timing or power attacks as well.
Smart cards can be physically disassembled by using acid, abrasives, solvents, or some other technique to obtain unrestricted access to the on-board microprocessor. Although such techniques may involve a risk of permanent damage to the chip, they permit much more detailed information (e.g., photomicrographs of encryption hardware) to be extracted. Portability Increasing data storage capacity Reliability that is virtually unaffected by electrical and magnetic fields.
The plastic or paper card in which the chip is embedded is fairly flexible. The larger the chip, the higher the probability that normal use could damage it. Cards are often carried in wallets or pockets, a harsh environment for a chip and antenna in contactless cards. PVC cards can crack or break if bent/flexed excessively. However, for large banking systems, failure-management costs can be more than offset by fraud reduction. The production, use and disposal of PVC plastic is known to be more harmful to the environment than other plastics. Alternative materials including chlorine free plastics and paper are available for some smart applications. If the account holder's computer hosts malware, the smart card security model may be broken. Malware can override the communication (both input via keyboard and output via application screen) between the user and the application. Man-in-the-browser malware (e.g., the Trojan Silentbanker) could modify a transaction, unnoticed by the user. Banks like Fortis and Belfius in Belgium and Rabobank ("random reader") in the Netherlands combine a smart card with an unconnected card reader to avoid this problem. The customer enters a challenge received from the bank's website, a PIN and the transaction amount into the reader. The reader returns an 8-digit signature. This signature is manually entered into the personal computer and verified by the bank, preventing point-of-sale-malware from changing the transaction amount. Smart cards have also been the targets of security attacks. These attacks range from physical invasion of the card's electronics, to non-invasive attacks that exploit weaknesses in the card's software or hardware. The usual goal is to expose private encryption keys and then read and manipulate secure data such as funds. Once an attacker develops a non-invasive attack for a particular smart card model, he or she is typically able to perform the attack on other cards of that model in seconds, often using equipment that can be disguised as a normal smart card reader. While manufacturers may develop new card models with additional information security, it may be costly or inconvenient for users to upgrade vulnerable systems. Tamper-evident and audit features in a smart card system help manage the risks of compromised cards. Another problem is the lack of standards for functionality and security. To address this problem, the Berlin Group launched the ERIDANE Project to propose "a new functional and security framework for smart-card based Point of Interaction (POI) equipment".
The Accredited Standards Committee X9 Inc. ( X9 ) today announced that it has released a standard for QR Code Protection Using Cryptographic Solutions, X9.148. The new standard guides the financial services industry in deploying cryptography to create trusted, secure QR codes, including definitions and descriptions for the secure usage of QR codes in financial applications. It is now available from ANSI for download .
QR (Quick Response) codes have become popular for their fast readability and greater storage capacity compared to standard Universal Product Code (UPC) barcodes. The various applications for QR codes increasingly include payments, where security is particularly important. (In fact, X9.148 complements X9’s ongoing work to develop a standard for using QR codes for payments.) While the QR code might be protected as a data element within a message, the QR code does not protect itself from malfeasance. Adoption of X9.148 corrects this problem.
Untrusted, unsecured QR codes are vulnerable to modification, duplication and masquerading, while a trusted QR code secured using cryptographic solutions will be protected against actions by unauthorized entities. Those potentially benefiting from the new standard include merchants, financial institutions, regulatory organizations, service providers, hardware and software manufacturers, auditors and assessors, as well as users of their products and services.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Signal%20%28software%29 • https://en.wikipedia.org/wiki/Facebook%20Messenger • https://en.wikipedia.org/wiki/Smart%20card • https://x9.org/x9-publishes-standard-for-qr-code-protection-using-cryptography/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Qr Code Encryption And Decryption System For Payments.
[*] Metasploit Scan Running on Target Subnet for Qr Code Encryption And Decryption System For Payments... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |