Complete Technical Paper Content — Ransomware Forensics And File Restoration Helper Tool
Overview & System Context
Ransomware Forensics And File Restoration Helper Tool: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~8695 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background In October 2023, Rhysida, a hacker group, attacked the online information systems of the British Library. They demanded a ransom of 20 bitcoin, at the time around £596,000, to restore services and return the stolen data. When the British Library did not acquiesce to the demands, Rhysida publicly released approximately 600GB of leaked material online. Services at the library were severely disrupted for months. It has been described as "one of the worst cyber incidents in British history". The main catalogue returned online on 15 January 2024 in a read-only format, although some of the library's services are expected to remain unavailable for months.
A targeted attack that copied full sections of network drives of the Library's Finance, Technology and People teams, which made up 60% of all content copied. A keyword attack which scanned for files and folders that used sensitive keywords in their names, including 'passport' or 'confidential', which constituted 40% of the copied data and included files from corporate networks and personal drives used by staff. A hijacking of native utilities, which were then used to forcibly create backup copies of 22 databases of data including contact details of external users and customers. Furthermore, Rhysida and its affiliates destroyed servers to inhibit system recovery and forensic analysis.
Library items from its Boston Spa branch could not be transferred to the London site. Around 20,000 writers, illustrators and translators who usually received Public Lending Right payments from borrowed books had their payments delayed. The Library's 2024–25 visiting fellowship programme was suspended. The computerised catalogue was offline for months, with partial restoration in January 2024. The EThOS collection of British doctoral theses remained offline as of 19 December 2023.
It returned to functionality on 8 July 2026. An estimated £6–7 million in costs to recover from the attack. As of 4 November 2024, British Library electronic resources web pages redirect to a page with the statement, "We're continuing to experience a major technology outage as a result of a cyber-attack. Our buildings are open as usual, however, the outage is still affecting our website, online systems and services, as well as some onsite services. This is a temporary website, with limited content, which outlines the services that are currently available, as well as what's on at the Library." Electronic Legal Deposit (NPLD) remained unavailable in the British Library Reading Rooms until summer 2026. The other five legal deposit libraries (National Libraries of Wales and Scotland, the Bodleian Libraries, Cambridge University Library and the Library of Trinity College Dublin) provided access to material deposited before October 2023 via an interim platform, which could be used onsite in their reading rooms. British Library Readers could apply for free Reader Passes to access this content onsite at one of these libraries.
Steganography ( , STEG-I-NOG-rI-fee) is the practice of representing information within another message or physical object, in such a manner that the presence of the concealed information would not be evident to an unsuspecting person's examination. In computing and electronic contexts, a computer file, message, image, or video is concealed within another file, message, image, or video. Generally, the hidden messages appear to be (or to be part of) something else: images, articles, shopping lists, or some other cover text. For example, the hidden message may be in invisible ink between the visible lines of a private letter. Some implementations of steganography that lack a formal shared secret are forms of security through obscurity, while key-dependent steganographic schemes try to adhere to Kerckhoffs's principle. The word steganography comes from Greek steganographia, which combines the words steganós (στεγανIς), meaning "covered or concealed", and -graphia (γραφI) meaning "writing". The first recorded use of the term was in 1499 by Johannes Trithemius in his Steganographia, a treatise on cryptography and steganography, disguised as a book on magic. The advantage of steganography over cryptography alone is that the intended secret message does not attract attention to itself as an object of scrutiny. Plainly visible encrypted messages, no matter how unbreakable they are, arouse interest and may in themselves be incriminating in countries in which encryption is illegal. Whereas cryptography is the practice of protecting the contents of a message alone, steganography is concerned with concealing both the fact that a secret message is being sent and its contents. Steganography includes the concealment of information within computer files. In digital steganography, electronic communications may include steganographic coding inside a transport layer, such as a document file, image file, program, or protocol. Media files are ideal for steganographic transmission because of their large size. For example, a sender might start with an innocuous image file and adjust the color of every hundredth pixel to correspond to a letter in the alphabet. The change is so subtle that someone who is not looking for it is unlikely to notice the change.
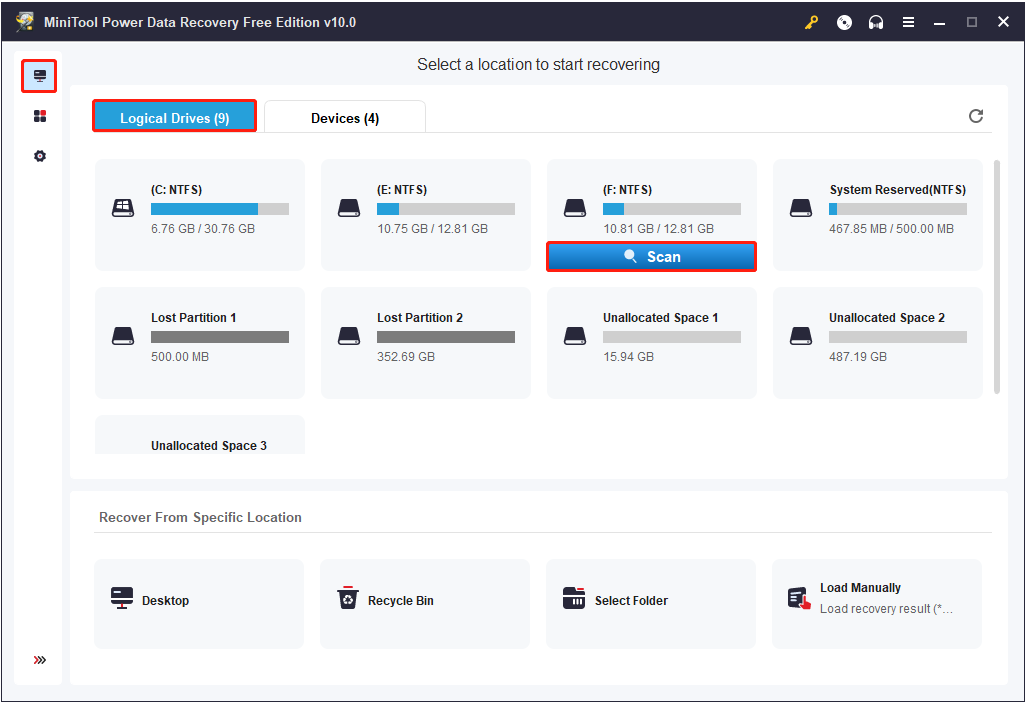
Figure 1: How to Perform Ransomware Recovery and How to Protect Your Data - MiniTool The first recorded uses of steganography can be traced back to 440 BC in Greece, when Herodotus mentions two examples in his Histories. Histiaeus sent a message to his vassal, Aristagoras, by shaving the head of his most trusted servant, "marking" the message onto his scalp, then sending him on his way once his hair had regrown, with the instruction, "When thou art come to Miletus, bid Aristagoras shave thy head, and look thereon." Additionally, Demaratus sent a warning about a forthcoming attack to Greece by writing it directly on the wooden backing of a wax tablet before applying its beeswax surface.
Wax tablets were in common use then as reusable writing surfaces, sometimes used for shorthand. Greek writer Aeneas Tacticus also devised a method of steganography now known as the pinhole cipher. He tells of a method where you are to write a letter and mark specific characters inside the letter with a dot-shaped hole. The recipient of said letter will simply note down all letters below the holes and string them together to form a message. He also suggested writing down a message and whitening it, making it invisible, so that when soaked in water the message would be revealed. He suggests many other hiding methods, such as hiding a message in leaves, in the foot of a messenger's sandal, and even in animal bladders. In his Compendium of Mechanics, Philo of Byzantium describes a recipe for invisible ink. He says to write down a message with crushed gallnuts dissolved in water. Then it could be revealed by being soaked by a sponge of ferrous sulfate. This recipe was inspired by the recipe for gall ink. Ferrous sulfate and crushed gallnuts dissolved in water both react to make ink so when they combine the message is revealed. In his Ars Amatoria, Roman poet Ovid noted of a primitive form of invisible ink using milk to be used in writing love letters. Naturalist Pliny the Elder also wrote of the tithymalus plant in his Natural History, and how its milk could be used for invisible ink. The first recorded use of the term steganography was by Johannnes Trithemius with his Steganographia, a book seemingly about summoning angels to hide messages. In reality however, the book was about steganography, the angel summoning being a cover text. Every angel corresponded to a different method of steganography.
He had written a letter to Arnold Bostius about his book, how it contained many methods of secret writing, how it could be used to communicate without speaking, signing or even nodding and much more. Bostius had died before he could receive the letter, however his colleagues had read and published it, accusing him of conversing with demons. Trithemius had also invited Charles de Bovelles to read his book before de Bovelles threw it away, claiming Trithemius was a magician. This situation led Trithemius to quit the book, not however, his interest in steganography. In his work Polygraphiae, Trithemius developed his Ave Maria cipher, a polyalphabetic substitution cipher and form of steganography that can hide information in a Latin praise of God. It consists of around 384 alphabets of 24 letters corresponding to 24 words to praise God. To encode a message, take the first letter of your message and replace that letter with the corresponding word in the first alphabet. Do that for the second, the third, and so on. "Conservator magnus conservans cuncta iuftis fuis in felicitatibus amen", for example, contains the concealed word SECRET. In the year 1606, Book I and II of the Steganographia were printed in Frankfurt, along with an incomplete Book III, and the Clavis Steganographie. The Clavis explained how to extract the secret of the Steganographia from Book I and II. Simply select an incantation to summon an "angel" and extract every other letter of every other word to find the secret steganographic method associated with that angel. With this publication came a slew of books vindicating Trithemius by explaining the steganography, acquitting him of magic. However, Book III was still widely regarded as a work of magic, with no clear way to extract its secrets. It would take until the late 1990s when Jim Reeds and Thomas Ernst independently discovered that it too, was secretly a work of steganography.
Numerous techniques throughout history have been developed to embed a message within another medium. Hiding a message in the title and context of a shared video or image. Misspelling names or words that are popular in the media in a given week, to suggest an alternative meaning. Hiding a picture that can be traced by using Paint or any other drawing tool.
Since the dawn of computers, techniques have been developed to embed messages in digital cover mediums. The message to conceal is often encrypted, then used to overwrite part of a much larger block of encrypted data or a block of random data (an unbreakable cipher like the one-time pad generates ciphertexts that look perfectly random without the private key). Examples of this include changing pixels in image or sound files, properties of digital text such as spacing and font choice, chaffing and winnowing, mimic functions, modifying the echo of a sound file (echo steganography), and including data in ignored sections of a file.
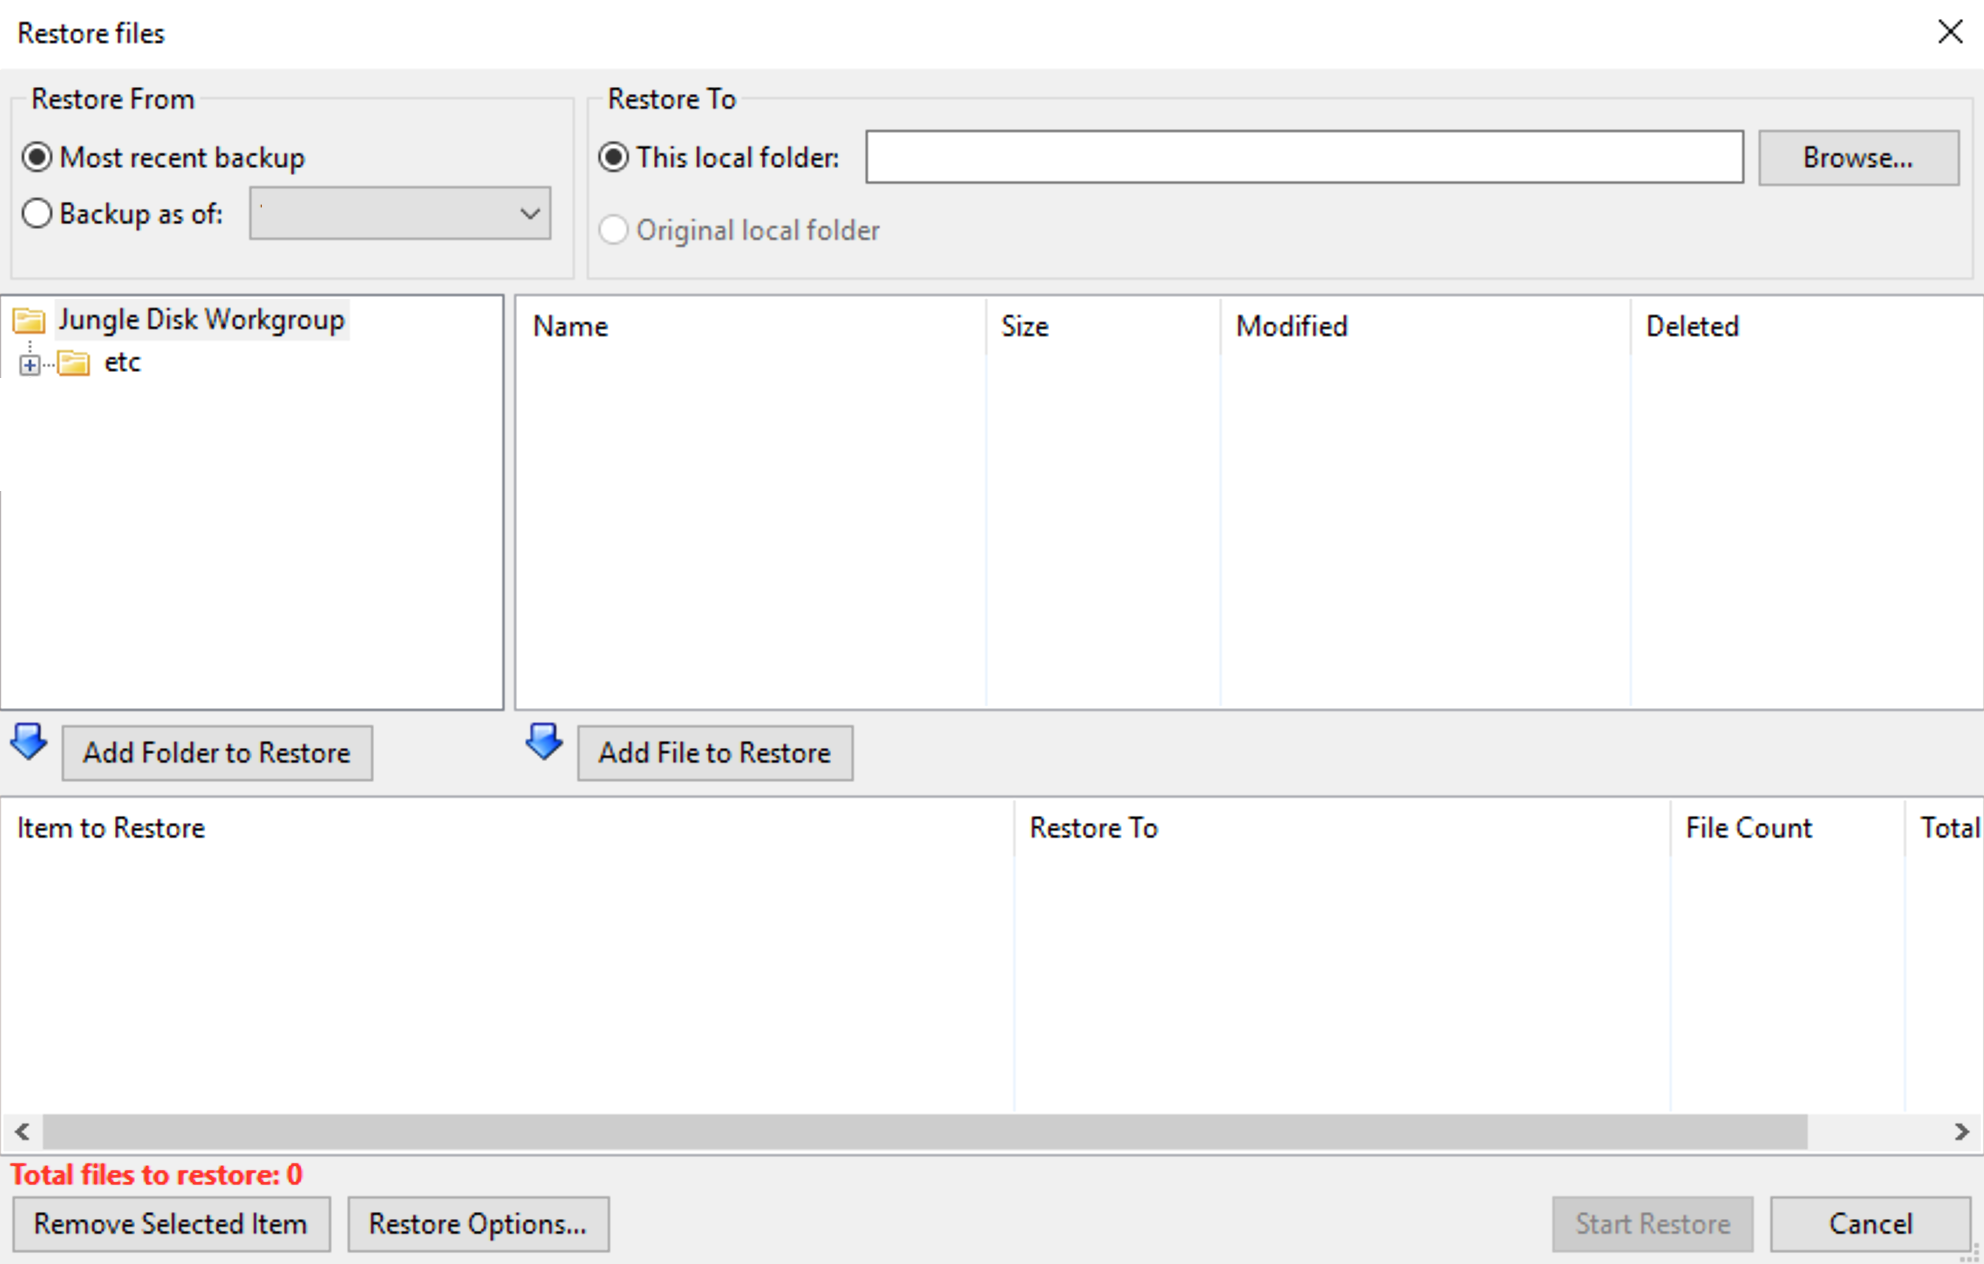
Figure 2: Handling Ransomware – CyberFortress Support Although not classic steganography, some types of modern color laser printers integrate the model, serial number, and timestamps on each printout for traceability reasons using a dot-matrix code made of small, yellow dots not recognizable to the naked eye (see: Printer tracking dots, for details).
2. System Architecture & Core Working Principles Steganophony – the concealment of messages in Voice-over-IP conversations, e.g. the employment of delayed or corrupted packets that would normally be ignored by the receiver (this method is called LACK – Lost Audio Packets Steganography), or, alternatively, hiding information in unused header fields. WLAN Steganography – transmission of steganograms in Wireless Local Area Networks. A practical example of WLAN Steganography is the HICCUPS system (Hidden Communication System for Corrupted Networks) Discussions of steganography generally use terminology analogous to and consistent with conventional radio and communications technology. However, some terms appear specifically in software and are easily confused. These are the most relevant ones to digital steganographic systems: The payload is the data covertly communicated. The carrier is the signal, stream, or data file that hides the payload, which differs from the channel, which typically means the type of input, such as a JPEG image. The resulting signal, stream, or data file with the encoded payload is sometimes called the package, stego file, or covert message. The proportion of bytes, samples, or other signal elements modified to encode the payload is called the encoding density and is typically expressed as a number between 0 and 1. In a set of files, the files that are considered likely to contain a payload are suspects. A suspect identified through some type of statistical analysis can be referred to as a candidate.
Some modern computer printers use steganography, including Hewlett-Packard and Xerox brand color laser printers. The printers add tiny yellow dots to each page. The barely visible dots contain encoded printer serial numbers and date and time stamps. The Electronic Frontier Foundation confirmed the marks are a forensic tracking tool, reportedly part of a secret agreement between printer manufacturers and governments to help track counterfeiters.
It is possible to steganographically hide computer malware into digital images, videos, audio and various other files in order to evade detection by antivirus software. This type of malware is called stegomalware. It can be activated by external code, which can be malicious or even non-malicious if some vulnerability in the software reading the file is exploited. Stegomalware can be removed from certain files without knowing whether they contain stegomalware or not. This is done through content disarm and reconstruction (CDR) software, and it involves reprocessing the entire file or removing parts from it. Various methods can be employed within CDR software to counter stegomalware with varying levels of mitigation relative to visual integrity disruption. Actually detecting stegomalware in a file can be difficult and may involve testing the file behaviour in virtual environments or deep learning analysis of the file.
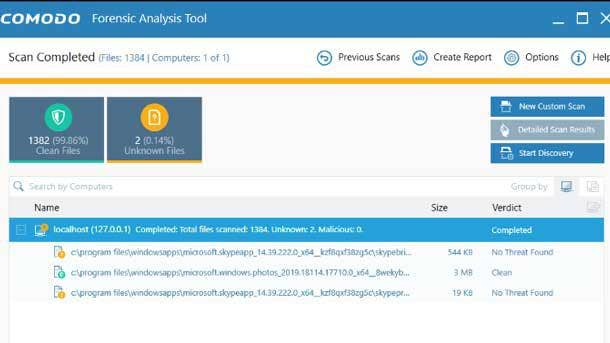
Figure 3: 10 Ransomware Protection Tools You Need To Know About | CRN Chosen stego attack: the stegoanalyst perceives the final target stego and the steganographic algorithm used. Known cover attack: the stegoanalyst comprises the initial conductive target and the final target stego. Known stego attack: the stegoanalyst knows the initial carrier target and the final target stego, in addition to the algorithm used. Stego only attack: the stegoanalyst perceives exclusively the stego target. Chosen message attack: the stegoanalyst, following a message selected by him, originates a stego target. Known message attack: the stegoanalyst owns the stego target and the hidden message, which is known to them.
Passive steganalysis: does not alter the target stego, therefore, it examines the target stego in order to establish whether it carries hidden information and recovers the hidden message, the key used or both. Active steganalysis: changes the initial stego target, therefore, it seeks to suppress the transfer of information, if it exists. An overview of digital steganography, particularly within images, for the computationally curious by Chris League, Long Island University, 2015 Examples showing images hidden in other images Information Hiding: Steganography & Digital Watermarking. Papers and information about steganography and steganalysis research from 1995 to the present. Includes Steganography Software Wiki list. Dr. Neil F. Johnson. Detecting Steganographic Content on the Internet. 2002 paper by Niels Provos and Peter Honeyman published in Proceedings of the Network and Distributed System Security Symposium (San Diego, CA, 6–8 February 2002). NDSS 2002. Internet Society, Washington, D.C. Covert Channels in the TCP/IP Suite Archived 23 October 2012 at the Wayback Machine – 1996 paper by Craig Rowland detailing the hiding of data in TCP/IP packets. Network Steganography Centre Tutorials Archived 16 December 2017 at the Wayback Machine. How-to articles on the subject of network steganography (Wireless LANs, VoIP – Steganophony, TCP/IP protocols and mechanisms, Steganographic Router, Inter-protocol steganography). By Krzysztof Szczypiorski and Wojciech Mazurczyk from Network Security Group. Invitation to BPCS-Steganography. Steganography by Michael T. Raggo, DefCon 12 (1 August 2004) File Format Extension Through Steganography by Blake W. Ford and Khosrow Kaikhah Computer steganography. Theory and practice with Mathcad (Rus) 2006 paper by Konakhovich G. F., Puzyrenko A. Yu. published in MK-Press Kyiv, Ukraine In the fields of computer security and information technology, computer security incident management involves the monitoring and detection of security events on a computer or computer network, and the execution of proper responses to those events.
Computer security incident management is a specialized form of incident management, the primary purpose of which is the development of a well understood and predictable response to damaging events and computer intrusions. Incident management requires a process and a response team which follows this process. In the United States, This definition of computer security incident management follows the standards and definitions described in the National Incident Management System (NIMS). The incident coordinator manages the response to an emergency security incident. In a Natural Disaster or other event requiring response from Emergency services, the incident coordinator would act as a liaison to the emergency services incident manager.
Roles and Responsibilities Lists the IRT members and their duties Communication protocols Training and awareness Logging policies and configurations Event status definitions and thresholds Playbooks and runbooks for common incident types Legal and compliance considerations 3. Software Implementation, Frameworks & Protocols Official websites use .gov A .gov website belongs to an official government organization in the United States.
Secure .gov websites use HTTPS A lock ( ) or https:// means you’ve safely connected to the .gov website. Share sensitive information only on official, secure websites. If you have experienced a ransomware attack, CISA strongly recommends using the following checklist provided in a Joint CISA and Multi-State Information Sharing and Analysis Center (MS-ISAC) Ransomware Guide to respond. This information will take you through the response process from detection to containment and eradication.
A technical, step-by-step 2026 checklist for responding to ransomware attacks. This guide covers immediate containment, forensic preservation, and secure recovery using NIST-aligned methodologies. Essential for SOC analysts and incident responders to manage high-pressure encryption events Ransomware has evolved into the most significant threat facing global organizations in 2026, moving far beyond simple file encryption to include complex data exfiltration and multi stage extortion tactics. As these attacks become more targeted and destructive, the difference between a minor disruption and a total business collapse often depends on the speed and precision of the response team initial actions. This professional guide provides a comprehensive and beginner friendly checklist designed to guide your organization through the chaos of a live ransomware incident with a calm and structured approach. We will explore the critical steps required to identify the scope of the infection, isolate compromised systems, and safely restore services while maintaining the forensic evidence needed for a thorough investigation. By following this standardized roadmap, your security team can minimize the impact of the attack and protect the long term reputation of the business. Throughout this post, we will break down the complex technical procedures of ransomware remediation into actionable stages that integrate people, processes, and modern security tools to ensure a resilient defense in the current digital landscape.
The first few minutes of a ransomware attack are the most vital for determining the overall outcome of the incident. Detection often begins when users report an inability to access files or when security tools trigger alerts regarding unusual file system activity or large scale data movements. It is critical to move quickly to verify that the event is a legitimate ransomware infection and not a different type of system failure or a false positive from your monitoring software. Verification involves looking for specific indicators of compromise such as ransom notes, changed file extensions, and high CPU usage associated with encryption processes. Once the threat is confirmed, the incident response team must be activated immediately to begin the formal response process. The following points represent the essential first steps in the detection and verification phase to ensure the team has an accurate understanding of the situation before taking further technical action. Ransom Note Identification involves searching for text or image files left by the attackers that explain their demands and contact information.
File Extension Analysis checks if common data files have been renamed with unusual or known ransomware suffixes to confirm the encryption type. System Performance Monitoring identifies machines with abnormally high processor and disk activity which often indicates an active encryption process. User Report Triage centralizes all incoming notifications from employees to map out which departments and locations are currently experiencing issues. Security Tool Alert Review examines the logs from EDR and SIEM platforms to find the specific point in time when the malicious activity started. Initial Impact Scoping determines whether the attack is limited to a single server or has already spread across the entire local area network. Formal Declaration of a security incident occurs once the threat is verified to ensure that all necessary stakeholders are alerted according to plan.
Verification involves looking for specific indicators of compromise such as ransom notes, changed file extensions, and high CPU usage associated with encryption processes. Once the threat is confirmed, the incident response team must be activated immediately to begin the formal response process. The following points represent the essential first steps in the detection and verification phase to ensure the team has an accurate understanding of the situation before taking further technical action.
Ransom Note Identification involves searching for text or image files left by the attackers that explain their demands and contact information. File Extension Analysis checks if common data files have been renamed with unusual or known ransomware suffixes to confirm the encryption type. System Performance Monitoring identifies machines with abnormally high processor and disk activity which often indicates an active encryption process. User Report Triage centralizes all incoming notifications from employees to map out which departments and locations are currently experiencing issues. Security Tool Alert Review examines the logs from EDR and SIEM platforms to find the specific point in time when the malicious activity started. Initial Impact Scoping determines whether the attack is limited to a single server or has already spread across the entire local area network. Formal Declaration of a security incident occurs once the threat is verified to ensure that all necessary stakeholders are alerted according to plan.
Containment is the highest priority once a ransomware infection has been confirmed, as the goal is to stop the encryption from spreading to other systems and reaching your critical data backups. This phase requires decisive action that may include temporarily shutting down parts of the network or disconnecting high value servers to prevent further damage. The speed of containment directly impacts the amount of data that will eventually need to be recovered or restored. Professional containment strategies must be executed in a way that prioritizes the most valuable assets first while ensuring that the response team maintains a secure way to communicate and manage the investigation. It is often a delicate balance between saving the rest of the environment and causing operational downtime for the business. The following points describe the professional isolation procedures used by security teams to box in a ransomware threat and protect the organization infrastructure. Network Disconnection involves physically or logically cutting off infected machines from the rest of the company network to stop lateral movement. Endpoint Isolation uses EDR tools to prevent compromised laptops and servers from talking to anything other than the security management console. Wireless Network Deactivation prevents the ransomware from spreading through the office Wi-Fi to mobile devices and guest machines in the building. Backup System Protection ensures that all backup servers and cloud storage are immediately taken offline or placed behind a strict air gap.
Account Suspension focuses on disabling the administrative and service accounts that the attacker is using to execute the malicious encryption code. Internet Gateway Closure blocks the communication between the ransomware and the attacker command and control servers to stop the encryption key exchange. Shared Drive Disconnection prevents the malware from accessing and encrypting the centralized data stores that are used by multiple departments every day.
Professional containment strategies must be executed in a way that prioritizes the most valuable assets first while ensuring that the response team maintains a secure way to communicate and manage the investigation. It is often a delicate balance between saving the rest of the environment and causing operational downtime for the business. The following points describe the professional isolation procedures used by security teams to box in a ransomware threat and protect the organization infrastructure. Network Disconnection involves physically or logically cutting off infected machines from the rest of the company network to stop lateral movement. Endpoint Isolation uses EDR tools to prevent compromised laptops and servers from talking to anything other than the security management console. Wireless Network Deactivation prevents the ransomware from spreading through the office Wi-Fi to mobile devices and guest machines in the building. Backup System Protection ensures that all backup servers and cloud storage are immediately taken offline or placed behind a strict air gap.
Account Suspension focuses on disabling the administrative and service accounts that the attacker is using to execute the malicious encryption code. Internet Gateway Closure blocks the communication between the ransomware and the attacker command and control servers to stop the encryption key exchange. Shared Drive Disconnection prevents the malware from accessing and encrypting the centralized data stores that are used by multiple departments every day.
4. Practical Deployment, Analysis & Case Studies While the containment is underway, a separate part of the response team must focus on the technical analysis of the ransomware to identify the specific strain and the group responsible. This information is vital for determining if a public decryptor exists and for understanding the likelihood that data has also been stolen before the encryption started. Analysis provides the necessary context for the leadership team to make informed decisions about the recovery strategy and potential legal duties. Technical analysis involves examining the malware code, analyzing the ransom note for unique identifiers, and searching global threat intelligence databases for similar attack patterns. This phase also includes a forensic look at the logs to find the root cause of the infection so the vulnerability can be patched before the recovery begins. The following points outline the professional analysis steps required to understand the full scope and nature of a ransomware threat in 2026.
Malware Sample Collection involves safely capturing a copy of the ransomware file from an infected machine for analysis in a secure lab. Strains Identification uses online tools and databases to match the encryption behavior and ransom note to a specific family of ransomware. Exfiltration Analysis checks network traffic logs for large outbound data transfers that would indicate the attackers stole sensitive files before encryption. Persistence Mechanism Search looks for hidden backdoors or scheduled tasks that the attacker may have left behind to regain access later. Root Cause Investigation tracks the initial entry point of the attacker whether it was through a phishing email or a vulnerable remote service. Decryptor Search involves checking with reputable security organizations to see if a free tool is available to unlock the files without paying. Attacker Communication Monitoring involves safely observing the dark web portals mentioned in the ransom note to gather more information about the group.
Technical analysis involves examining the malware code, analyzing the ransom note for unique identifiers, and searching global threat intelligence databases for similar attack patterns. This phase also includes a forensic look at the logs to find the root cause of the infection so the vulnerability can be patched before the recovery begins. The following points outline the professional analysis steps required to understand the full scope and nature of a ransomware threat in 2026. Malware Sample Collection involves safely capturing a copy of the ransomware file from an infected machine for analysis in a secure lab.
Strains Identification uses online tools and databases to match the encryption behavior and ransom note to a specific family of ransomware. Exfiltration Analysis checks network traffic logs for large outbound data transfers that would indicate the attackers stole sensitive files before encryption. Persistence Mechanism Search looks for hidden backdoors or scheduled tasks that the attacker may have left behind to regain access later. Root Cause Investigation tracks the initial entry point of the attacker whether it was through a phishing email or a vulnerable remote service. Decryptor Search involves checking with reputable security organizations to see if a free tool is available to unlock the files without paying. Attacker Communication Monitoring involves safely observing the dark web portals mentioned in the ransom note to gather more information about the group.
To help you manage the various moving parts of a ransomware crisis, we have provided an essential action table that highlights the primary responsibilities and priorities for different stages of the response. This table serves as a quick reference for the incident manager to ensure that no critical tasks are overlooked during the high pressure environment of a live attack. Use this summary to coordinate the activities between your technical investigators and your organizational leadership. Each phase of the response requires a different set of skills and tools, and this table helps clarify exactly what should be happening at each point in the timeline. It is important to remember that these actions often occur simultaneously, requiring constant communication and updates across the entire team. Use the data below to validate your current incident response readiness and to identify where your organizational plan might need additional detail or specialized professional resources. Response Stage Priority Action Primary Goal Owner Detection Incident Verification Confirm Threat SOC Team Containment Network Isolation Stop Spread Security Engineer Analysis Forensic Collection Identify Root Cause Forensic Lead Recovery Backup Restoration Restore Business IT Ops Team Each phase of the response requires a different set of skills and tools, and this table helps clarify exactly what should be happening at each point in the timeline. It is important to remember that these actions often occur simultaneously, requiring constant communication and updates across the entire team. Use the data below to validate your current incident response readiness and to identify where your organizational plan might need additional detail or specialized professional resources.
Response Stage Priority Action Primary Goal Owner Detection Incident Verification Confirm Threat SOC Team Containment Network Isolation Stop Spread Security Engineer Analysis Forensic Collection Identify Root Cause Forensic Lead Recovery Backup Restoration Restore Business IT Ops Team Recovery is the stage where the organization begins the careful process of bringing systems back online and restoring data from clean and verified backups. This phase must be handled with extreme caution to ensure that the ransomware is not re activated during the restoration process. It is essential to verify that the environment is completely clean and that all vulnerabilities have been patched before any critical business services are allowed to resume normal operations. A professional recovery strategy involves prioritizing the most important business functions first and using a phased approach to restoration. This ensures that the company can begin operating at a basic level as quickly as possible while the more complex systems are being cleaned and tested. The following points represent the essential steps for a safe and effective recovery operation following a major ransomware incident in a professional corporate environment. Clean Environment Build involves creating a new and secure network segment where systems can be restored without fear of re infection. Backup Integrity Verification ensures that the data being used for restoration has not been corrupted or encrypted by the attackers. Phased Restoration brings the most critical business applications online first to support the primary mission of the organization.
System Hardening involves applying all necessary patches and security updates to the systems before they are reconnected to the production network. Continuous Monitoring uses high intensity alerts to watch the restored systems for any signs of the ransomware returning or being re activated. Password Reset Enforcement requires every user and service account to change their credentials to ensure the attacker cannot use stolen passwords. Data Validation involves working with the business owners to confirm that the restored information is accurate and complete for their needs.
A professional recovery strategy involves prioritizing the most important business functions first and using a phased approach to restoration. This ensures that the company can begin operating at a basic level as quickly as possible while the more complex systems are being cleaned and tested. The following points represent the essential steps for a safe and effective recovery operation following a major ransomware incident in a professional corporate environment. Clean Environment Build involves creating a new and secure network segment where systems can be restored without fear of re infection. Backup Integrity Verification ensures that the data being used for restoration has not been corrupted or encrypted by the attackers.
Phased Restoration brings the most critical business applications online first to support the primary mission of the organization. System Hardening involves applying all necessary patches and security updates to the systems before they are reconnected to the production network. Continuous Monitoring uses high intensity alerts to watch the restored systems for any signs of the ransomware returning or being re activated. Password Reset Enforcement requires every user and service account to change their credentials to ensure the attacker cannot use stolen passwords. Data Validation involves working with the business owners to confirm that the restored information is accurate and complete for their needs.
Beyond the technical response, a ransomware attack triggers a complex series of legal and regulatory requirements that must be managed by the organization leadership and legal teams. In 2026, many jurisdictions have strict laws regarding the notification of data breaches and the payment of ransoms to criminal groups. Managing these duties is essential for avoiding massive fines and for maintaining the trust of customers, partners, and the general public during the crisis. Professional communication involves providing regular and honest updates to all affected parties without disclosing technical details that could be used by other attackers. It is also important to work closely with law enforcement and insurance providers from the very beginning of the incident to ensure that all required evidence is preserved. The following points highlight the critical legal and communication steps that must be part of any comprehensive ransomware response checklist. Regulatory Notification involves informing data protection authorities about the breach within the timeframes required by laws like the GDPR. Law Enforcement Engagement provides the necessary reports to agencies like the FBI or Interpol to assist in the global fight against cybercrime. Insurance Provider Liaison ensures that the organization meets the requirements of its cyber insurance policy to qualify for coverage of the incident costs. Stakeholder Communication provides clear and accurate information to employees, board members, and investors about the impact of the attack. Customer Notification involves informing those whose personal data may have been accessed or stolen by the ransomware attackers. Legal Review assesses the organization liability and ensures that all actions taken during the response are compliant with current laws. External PR Management uses professional communication experts to manage the organization public image and respond to media inquiries.
Professional communication involves providing regular and honest updates to all affected parties without disclosing technical details that could be used by other attackers. It is also important to work closely with law enforcement and insurance providers from the very beginning of the incident to ensure that all required evidence is preserved. The following points highlight the critical legal and communication steps that must be part of any comprehensive ransomware response checklist. Regulatory Notification involves informing data protection authorities about the breach within the timeframes required by laws like the GDPR. Law Enforcement Engagement provides the necessary reports to agencies like the FBI or Interpol to assist in the global fight against cybercrime. Insurance Provider Liaison ensures that the organization meets the requirements of its cyber insurance policy to qualify for coverage of the incident costs. Stakeholder Communication provides clear and accurate information to employees, board members, and investors about the impact of the attack. Customer Notification involves informing those whose personal data may have been accessed or stolen by the ransomware attackers. Legal Review assesses the organization liability and ensures that all actions taken during the response are compliant with current laws.
External PR Management uses professional communication experts to manage the organization public image and respond to media inquiries. The final part of the response process is building long term resilience to ensure that a similar ransomware attack can never succeed again. This involves a deep and honest look at the failures that led to the breach and a commitment to investing in the people and technology needed to strengthen the defense. Continuous improvement is the only way to stay ahead of attackers who are constantly changing their methods. Building resilience also means fostering a culture of security throughout the organization where every employee understands their role in protecting the company digital assets. By treating the incident as a learning opportunity, the organization can emerge from the crisis stronger and more prepared for the challenges of the future. Professional resilience is built on the foundation of constant vigilance and adaptive security measures. Effective resilience strategies include the implementation of zero trust architectures where no user or device is trusted by default on the network. Additionally, regular incident response drills and updated security awareness training ensure that the team remains sharp and ready for any future threats.
5. Performance Evaluation & Extended Technical Observations Building resilience also means fostering a culture of security throughout the organization where every employee understands their role in protecting the company digital assets. By treating the incident as a learning opportunity, the organization can emerge from the crisis stronger and more prepared for the challenges of the future. Professional resilience is built on the foundation of constant vigilance and adaptive security measures. Effective resilience strategies include the implementation of zero trust architectures where no user or device is trusted by default on the network. Additionally, regular incident response drills and updated security awareness training ensure that the team remains sharp and ready for any future threats.
Effective resilience strategies include the implementation of zero trust architectures where no user or device is trusted by default on the network. Additionally, regular incident response drills and updated security awareness training ensure that the team remains sharp and ready for any future threats. Additionally, regular incident response drills and updated security awareness training ensure that the team remains sharp and ready for any future threats.
Managing a ransomware incident in 2026 is an intense and complex challenge that requires a perfectly coordinated response across the entire organization. By following the professional checklist provided in this guide, you can navigate the difficult path from initial detection and containment to full recovery and future resilience. Each phase of the response is critical, and the speed and accuracy of your actions will ultimately determine how well your business survives the crisis. Remember that the best response to ransomware is preparation, and having a well tested plan in place before an attack occurs is the most valuable asset you can have. As you continue to build your cybersecurity expertise, focus on the fundamentals of network isolation, data backup integrity, and clear organizational communication. These core principles remain the most effective defense against the evolving tactics of cyber extortionists. We hope this guide empowers you to build a stronger and more resilient security posture, protecting your data and your reputation in an increasingly hostile digital world. Stay vigilant, stay prepared, and remember that every lesson learned from a security event is a stepping stone toward a safer future for your organization and your customers.
The first action is to immediately disconnect the infected device from the network to stop the encryption from spreading further. Should our organization pay the ransom to get our files back? Law enforcement generally advises against paying as it does not guarantee file recovery and encourages future attacks against other organizations. What is a ransomware decryptor tool? A decryptor is a specialized software tool developed by security researchers that can sometimes unlock files without paying the attacker ransom. How does ransomware usually enter an organization? Ransomware most commonly enters through phishing emails, vulnerable remote desktop services, or by exploiting unpatched software bugs on network servers.
What is the difference between encryption and exfiltration? Encryption locks your files so you cannot use them, while exfiltration involves the attacker stealing your sensitive data to leak it publicly. How can we protect our backups from ransomware? Backups should be stored offline or in an immutable cloud format so that the ransomware cannot find or encrypt them during an attack. What is lateral movement in a ransomware attack? Lateral movement is the technique used by attackers to navigate through a network once they have gained initial access to a single device. How long does it take to recover from ransomware? Recovery can take anywhere from a few days to several weeks depending on the amount of data and the quality of your backups. Do we have to report a ransomware attack to the police? Reporting to law enforcement is highly recommended as they can provide assistance and it helps track the criminal groups responsible for the attacks. What is cyber insurance and does it cover ransomware? Cyber insurance is a policy that helps cover the financial losses from a breach, often including forensic costs and business interruption expenses. What is an immutable backup? An immutable backup is a copy of your data that cannot be changed or deleted for a set period, making it ransomware proof. How do I find the root cause of the infection? Finding the root cause involves a forensic review of the logs to see the initial entry point and the actions of the attacker. What is an indicator of compromise (IOC)? An IOC is a piece of digital evidence like a specific file name or IP address that proves a system has been breached. Can antivirus software stop ransomware? Modern EDR tools are very effective at stopping ransomware by identifying its behavior even if the specific strain has never been seen before.
What is a double extortion attack? In a double extortion attack, the hacker demands money to unlock your files and a second payment to not release your stolen data. Should we tell our customers about the ransomware? Yes, honest communication is vital if customer data has been compromised and it is often a legal requirement in many professional jurisdictions. What is a zero trust security architecture? Zero trust is a security model where every user and device must be verified before gaining access to any part of the network. How can we test our ransomware response plan? You can test your plan using tabletop exercises where the team discusses how they would handle a hypothetical ransomware scenario in real time. What is a bit for bit forensic image? A bit for bit image is an exact copy of a hard drive used by forensic investigators to analyze evidence without changing the original. What are common ransomware families in 2026? While strains change frequently, professional groups often reuse code from known families like LockBit or Conti in their modern and sophisticated attacks.
Law enforcement generally advises against paying as it does not guarantee file recovery and encourages future attacks against other organizations. What is a ransomware decryptor tool? A decryptor is a specialized software tool developed by security researchers that can sometimes unlock files without paying the attacker ransom. How does ransomware usually enter an organization? Ransomware most commonly enters through phishing emails, vulnerable remote desktop services, or by exploiting unpatched software bugs on network servers. What is the difference between encryption and exfiltration? Encryption locks your files so you cannot use them, while exfiltration involves the attacker stealing your sensitive data to leak it publicly. How can we protect our backups from ransomware? Backups should be stored offline or in an immutable cloud format so that the ransomware cannot find or encrypt them during an attack. What is lateral movement in a ransomware attack? Lateral movement is the technique used by attackers to navigate through a network once they have gained initial access to a single device. How long does it take to recover from ransomware? Recovery can take anywhere from a few days to several weeks depending on the amount of data and the quality of your backups. Do we have to report a ransomware attack to the police? Reporting to law enforcement is highly recommended as they can provide assistance and it helps track the criminal groups responsible for the attacks. What is cyber insurance and does it cover ransomware? Cyber insurance is a policy that helps cover the financial losses from a breach, often including forensic costs and business interruption expenses.
What is an immutable backup? An immutable backup is a copy of your data that cannot be changed or deleted for a set period, making it ransomware proof. How do I find the root cause of the infection? Finding the root cause involves a forensic review of the logs to see the initial entry point and the actions of the attacker. What is an indicator of compromise (IOC)? An IOC is a piece of digital evidence like a specific file name or IP address that proves a system has been breached. Can antivirus software stop ransomware? Modern EDR tools are very effective at stopping ransomware by identifying its behavior even if the specific strain has never been seen before. What is a double extortion attack? In a double extortion attack, the hacker demands money to unlock your files and a second payment to not release your stolen data. Should we tell our customers about the ransomware? Yes, honest communication is vital if customer data has been compromised and it is often a legal requirement in many professional jurisdictions. What is a zero trust security architecture? Zero trust is a security model where every user and device must be verified before gaining access to any part of the network. How can we test our ransomware response plan? You can test your plan using tabletop exercises where the team discusses how they would handle a hypothetical ransomware scenario in real time. What is a bit for bit forensic image? A bit for bit image is an exact copy of a hard drive used by forensic investigators to analyze evidence without changing the original. What are common ransomware families in 2026? While strains change frequently, professional groups often reuse code from known families like LockBit or Conti in their modern and sophisticated attacks.
A decryptor is a specialized software tool developed by security researchers that can sometimes unlock files without paying the attacker ransom. How does ransomware usually enter an organization? Ransomware most commonly enters through phishing emails, vulnerable remote desktop services, or by exploiting unpatched software bugs on network servers. What is the difference between encryption and exfiltration? Encryption locks your files so you cannot use them, while exfiltration involves the attacker stealing your sensitive data to leak it publicly. How can we protect our backups from ransomware? Backups should be stored offline or in an immutable cloud format so that the ransomware cannot find or encrypt them during an attack. What is lateral movement in a ransomware attack? Lateral movement is the technique used by attackers to navigate through a network once they have gained initial access to a single device. How long does it take to recover from ransomware? Recovery can take anywhere from a few days to several weeks depending on the amount of data and the quality of your backups. Do we have to report a ransomware attack to the police? Reporting to law enforcement is highly recommended as they can provide assistance and it helps track the criminal groups responsible for the attacks. What is cyber insurance and does it cover ransomware? Cyber insurance is a policy that helps cover the financial losses from a breach, often including forensic costs and business interruption expenses. What is an immutable backup? An immutable backup is a copy of your data that cannot be changed or deleted for a set period, making it ransomware proof. How do I find the root cause of the infection? Finding the root cause involves a forensic review of the logs to see the initial entry point and the actions of the attacker. What is an indicator of compromise (IOC)? An IOC is a piece of digital evidence like a specific file name or IP address that proves a system has been breached. Can antivirus software stop ransomware? Modern EDR tools are very effective at stopping ransomware by identifying its behavior even if the specific strain has never been seen before.
What is a double extortion attack? In a double extortion attack, the hacker demands money to unlock your files and a second payment to not release your stolen data. Should we tell our customers about the ransomware? Yes, honest communication is vital if customer data has been compromised and it is often a legal requirement in many professional jurisdictions. What is a zero trust security architecture? Zero trust is a security model where every user and device must be verified before gaining access to any part of the network. How can we test our ransomware response plan? You can test your plan using tabletop exercises where the team discusses how they would handle a hypothetical ransomware scenario in real time. What is a bit for bit forensic image? A bit for bit image is an exact copy of a hard drive used by forensic investigators to analyze evidence without changing the original. What are common ransomware families in 2026? While strains change frequently, professional groups often reuse code from known families like LockBit or Conti in their modern and sophisticated attacks.
Ransomware most commonly enters through phishing emails, vulnerable remote desktop services, or by exploiting unpatched software bugs on network servers. What is the difference between encryption and exfiltration? Encryption locks your files so you cannot use them, while exfiltration involves the attacker stealing your sensitive data to leak it publicly. How can we protect our backups from ransomware? Backups should be stored offline or in an immutable cloud format so that the ransomware cannot find or encrypt them during an attack. What is lateral movement in a ransomware attack? Lateral movement is the technique used by attackers to navigate through a network once they have gained initial access to a single device. How long does it take to recover from ransomware? Recovery can take anywhere from a few days to several weeks depending on the amount of data and the quality of your backups. Do we have to report a ransomware attack to the police? Reporting to law enforcement is highly recommended as they can provide assistance and it helps track the criminal groups responsible for the attacks. What is cyber insurance and does it cover ransomware? Cyber insurance is a policy that helps cover the financial losses from a breach, often including forensic costs and business interruption expenses. What is an immutable backup? An immutable backup is a copy of your data that cannot be changed or deleted for a set period, making it ransomware proof. How do I find the root cause of the infection? Finding the root cause involves a forensic review of the logs to see the initial entry point and the actions of the attacker. What is an indicator of compromise (IOC)? An IOC is a piece of digital evidence like a specific file name or IP address that proves a system has been breached. Can antivirus software stop ransomware? Modern EDR tools are very effective at stopping ransomware by identifying its behavior even if the specific strain has never been seen before. What is a double extortion attack? In a double extortion attack, the hacker demands money to unlock your files and a second payment to not release your stolen data. Should we tell our customers about the ransomware? Yes, honest communication is vital if customer data has been compromised and it is often a legal requirement in many professional jurisdictions. What is a zero trust security architecture? Zero trust is a security model where every user and device must be verified before gaining access to any part of the network. How can we test our ransomware response plan? You can test your plan using tabletop exercises where the team discusses how they would handle a hypothetical ransomware scenario in real time. What is a bit for bit forensic image? A bit for bit image is an exact copy of a hard drive used by forensic investigators to analyze evidence without changing the original. What are common ransomware families in 2026? While strains change frequently, professional groups often reuse code from known families like LockBit or Conti in their modern and sophisticated attacks.
Official websites use .gov A .gov website belongs to an official government organization in the United States. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/British%20Library%20cyberattack • https://en.wikipedia.org/wiki/Steganography • https://en.wikipedia.org/wiki/Computer%20security%20incident%20management • https://www.cisa.gov/ransomware-response-checklist • https://www.cyberforensicsinstitute.com/blog/ransomware-incident-response-checklist • https://www.cisa.gov/stopransomware/ransomware-guide • https://thehgtech.com/guides/ransomware-response-playbook.html • https://www.digitalforensics.com/cyber-security/ransomware-attack
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Ransomware Forensics And File Restoration Helper Tool.
[*] Metasploit Scan Running on Target Subnet for Ransomware Forensics And File Restoration Helper Tool... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |