Complete Technical Paper Content — Real Time Ransomware Behavior Blocking Agent On Endpoint
Overview & System Context
Real Time Ransomware Behavior Blocking Agent On Endpoint: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9617 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Access to this page requires authorization. You can try signing in or changing directories .
Today's threat landscape is overrun by fileless malware that lives off the land, highly polymorphic threats that mutate faster than traditional solutions can keep up with, and human-operated attacks that adapt to what adversaries find on compromised devices. Traditional security solutions aren't sufficient to stop such attacks; you need artificial intelligence (AI) and machine learning (ML) backed capabilities, such as behavioral blocking and containment, included in Defender for Endpoint .
Behavioral blocking and containment capabilities can help identify and stop threats based on their behaviors and process trees, even when the threat has already started. Next-generation protection, EDR, and Defender for Endpoint components and features work together in behavioral blocking and containment capabilities. Behavioral blocking and containment capabilities work with multiple components and features of Defender for Endpoint to stop attacks immediately and prevent attacks from progressing.
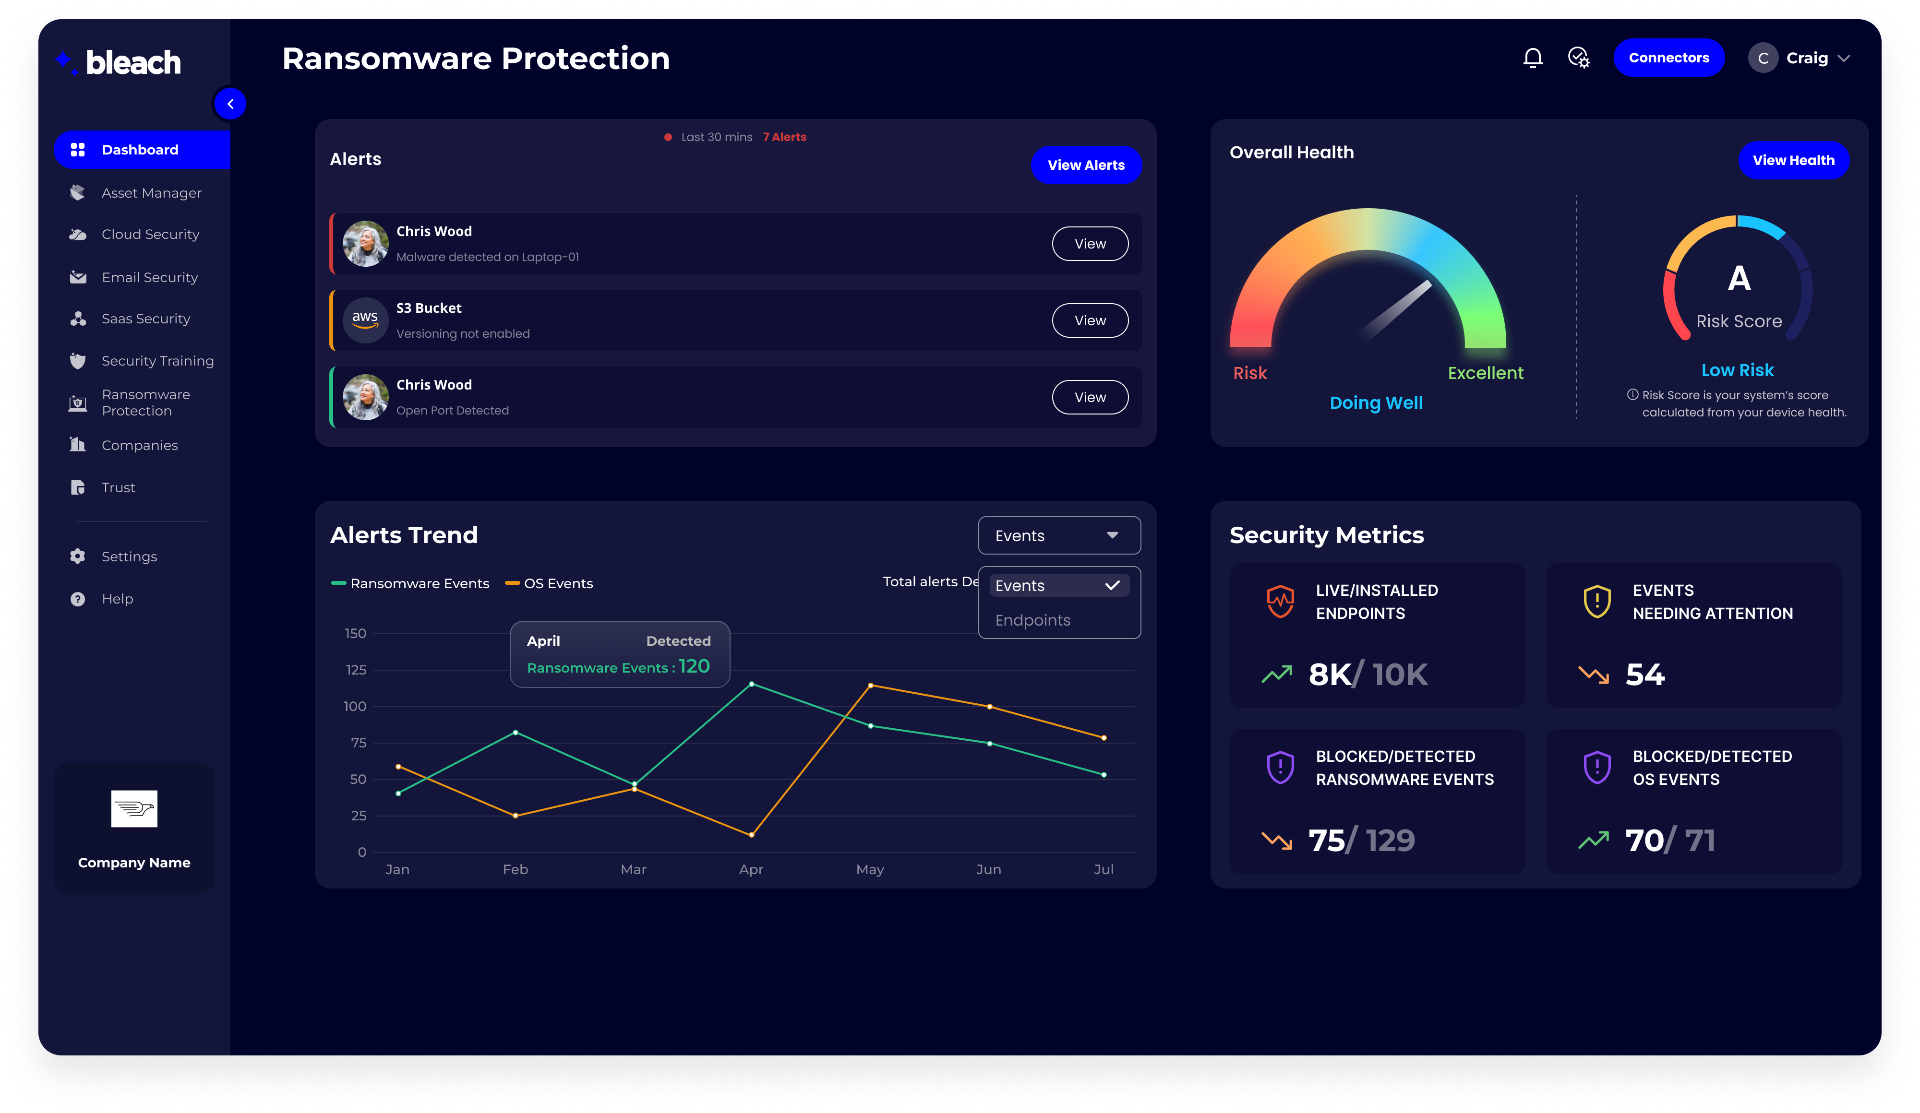
Figure 1: Ransomware Protection for Endpoints | Real-Time Detection & Defense Next-generation protection (which includes Microsoft Defender Antivirus) can detect threats by analyzing behaviors, and stop running threats. Endpoint detection and response (EDR) receives security signals across your network, devices, and kernel behavior. As threats are detected, alerts are created. Multiple alerts of the same type are aggregated into incidents, which makes it easier for your security operations team to investigate and respond.
Defender for Endpoint has a wide range of optics across identities, email, data, and apps, in addition to the network, endpoint, and kernel behavior signals received through EDR. A component of Microsoft Defender XDR , Defender for Endpoint processes and correlates these signals, raises detection alerts, and connects related alerts in incidents. With these capabilities, more threats can be prevented or blocked, even if they start running. Whenever suspicious behavior is detected, the threat is contained, alerts are created, and threats are stopped in their tracks.
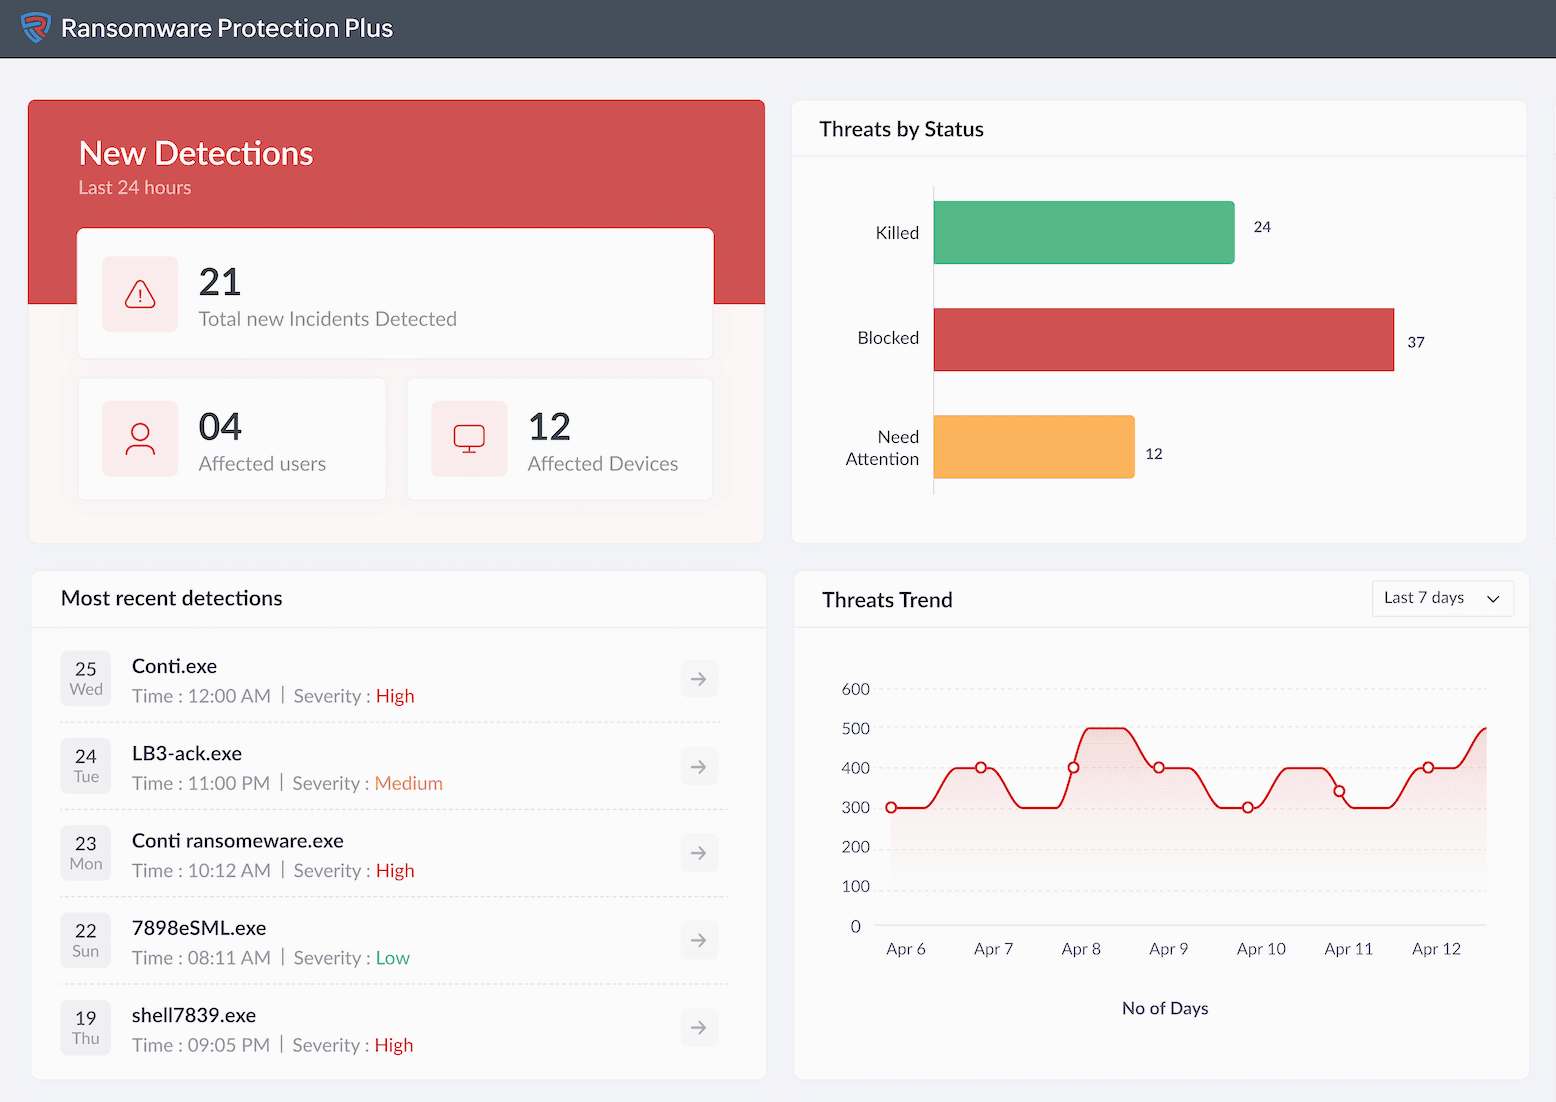
Figure 2: Ransomware Detection Tool | Detecting Ransomware Attacks - ManageEngine ... The following image shows an example of behavioral blocking and containment capabilities triggering an alert: On-client, policy-driven attack surface reduction (ASR) rules Prevent predefined, common attack behavior from apps. To monitor ASR rule detections, see Monitor attack surface reduction (ASR) rule activity .
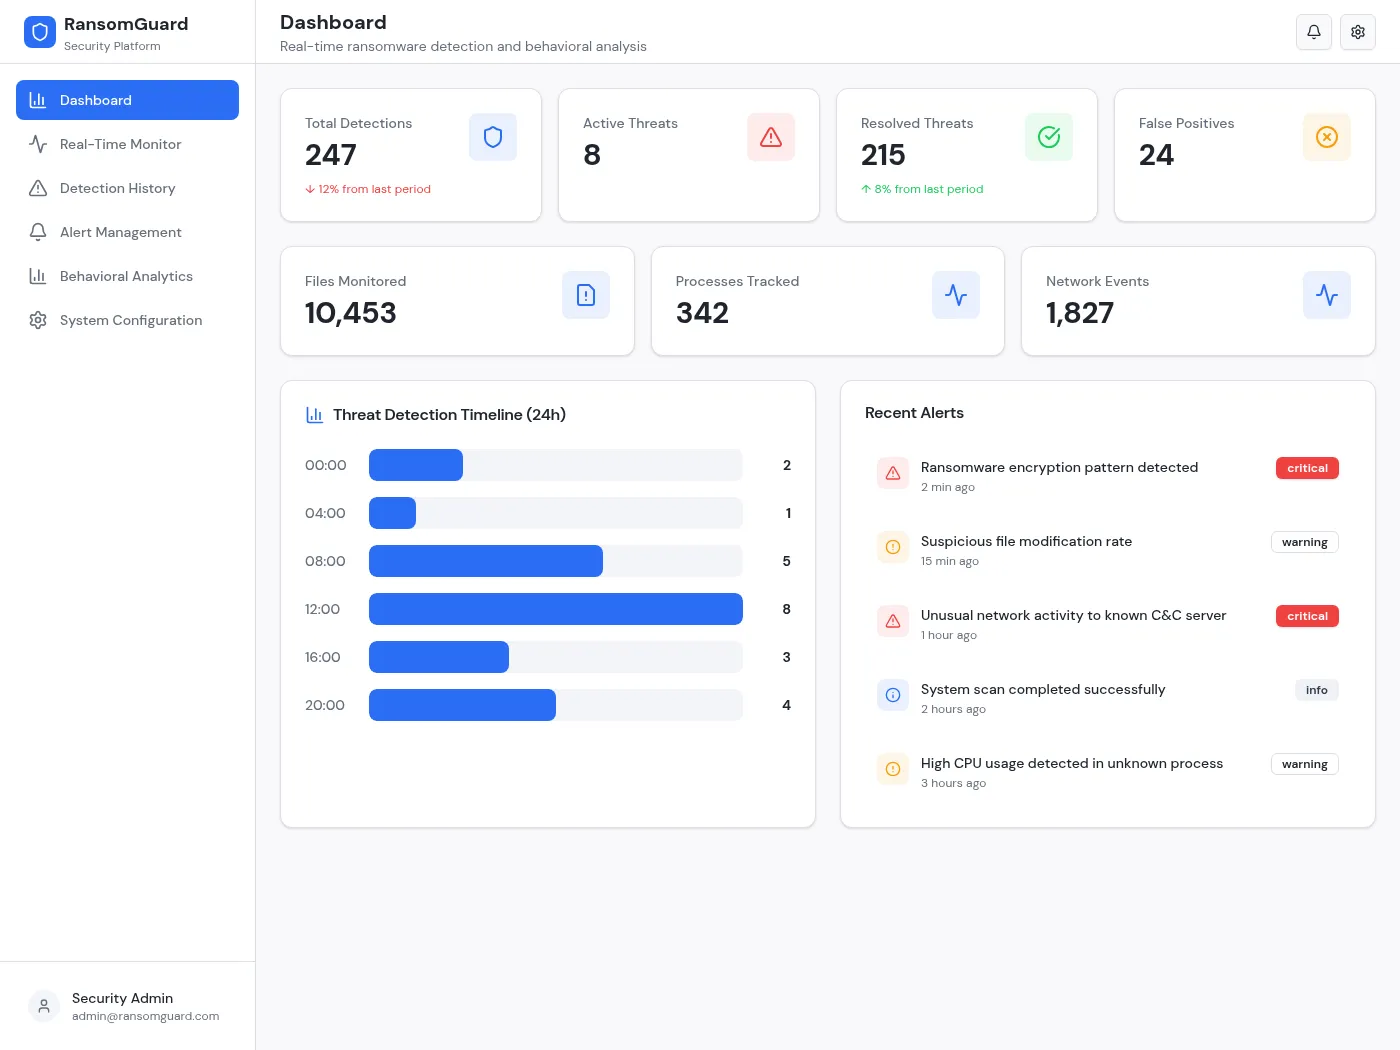
Client behavioral blocking Threats on endpoints are detected through machine learning, and then are blocked and remediated automatically. (Client behavioral blocking is enabled by default.) Feedback-loop blocking (also referred to as rapid protection) Threat detections are observed through behavioral intelligence. Threats are stopped and prevented from running on other endpoints. (Feedback-loop blocking is enabled by default.) Figure 3: RansomGuard: Real-Time Ransomware · Built with Blink Endpoint detection and response (EDR) in block mode Malicious artifacts or behaviors that are observed through post-breach protection are blocked and contained. EDR in block mode works even if Microsoft Defender Antivirus isn't the primary antivirus solution. (EDR in block mode isn't enabled by default; you turn it on in the Defender portal.) Expect more to come in the area of behavioral blocking and containment, as Microsoft continues to improve threat protection features and capabilities. To see what's planned and rolling out now, visit the Microsoft 365 roadmap .
Behavioral blocking and containment capabilities have blocked the following attacker techniques: The following are two real-life examples of behavioral blocking and containment in action. As described in In hot pursuit of elusive threats: AI-driven behavior-based blocking stops attacks in their tracks , behavioral blocking and containment capabilities stopped a credential theft attack against 100 organizations around the world.
Spear-phishing email messages that contained a lure document were sent to the targeted organizations. If a recipient opened the attachment, a related remote document was able to execute code on the user's device and load Lokibot malware, which stole credentials, exfiltrated stolen data, and waited for further instructions from a command-and-control server. Behavior-based machine-learning models in Defender for Endpoint caught and stopped the attacker's techniques at two points in the attack chain: While the attack was detected and stopped, alerts, such as an "initial access alert," were triggered and appeared in the Microsoft Defender portal .
This example shows how behavior-based machine-learning models in the cloud add new layers of protection against attacks, even after they're already running. As described in the recent blog post, Behavioral blocking, and containment: Transforming optics into protection , in January 2020, Defender for Endpoint detected a privilege escalation activity on a device in an organization. An alert called "Possible privilege escalation using NTLM relay" was triggered.
The threat turned out to be malware; it was a new, not-seen-before variant of a notorious hacking tool called Juicy Potato, which is used by attackers to get privilege escalation on a device. Minutes after the alert was triggered, the file was analyzed, and confirmed to be malicious. Its process was stopped and blocked, as shown in the following image: A few minutes after the artifact was blocked, multiple instances of the same file were blocked on the same device, preventing more attackers or other malware from deploying on the device.
This example shows that with behavioral blocking and containment capabilities, threats are detected, contained, and blocked automatically. If you're looking for Antivirus related information for other platforms, see the following articles: Access to this page requires authorization. You can try signing in or changing directories .
Client behavioral blocking is a component of behavioral blocking and containment capabilities in Defender for Endpoint. As suspicious behaviors are detected on devices (also referred to as clients or endpoints), artifacts (such as files or applications) are blocked, checked, and remediated automatically. Microsoft Defender Antivirus can detect suspicious behavior, malicious code, fileless and in-memory attacks, and more on a device. When suspicious behaviors are detected, Microsoft Defender Antivirus monitors and sends those suspicious behaviors and their process trees to the cloud protection service. Machine learning differentiates between malicious applications and good behaviors within milliseconds, and classifies each artifact. In almost real time, as soon as an artifact is found to be malicious, it's blocked on the device.
Whenever a suspicious behavior is detected, an alert is generated and is visible while the attack was detected and stopped; alerts, such as an "initial access alert," are triggered and appear in the Microsoft Defender portal . Client behavioral blocking is effective because it not only helps prevent an attack from starting, it can help stop an attack that has begun executing. And, with feedback-loop blocking (another capability of behavioral blocking and containment), attacks are prevented on other devices in your organization.
Behavior-based detections are named according to the MITRE ATT&CK Matrix for Enterprise . The naming convention helps identify the attack stage where the malicious behavior was observed: If your organization is using Defender for Endpoint, client behavioral blocking is enabled by default. However, to benefit from all Defender for Endpoint capabilities, including behavioral blocking and containment , make sure the following features and capabilities of Defender for Endpoint are enabled and configured: NPAV EDR provides advanced ransomware protection through dedicated detection and response components that continuously monitor endpoint activity for malicious encryption behavior. The solution safeguards Windows, Linux, and Windows Server environments by identifying and blocking ransomware attacks before they can cause significant damage.
Using a combination of signature-based detection, behavioral analysis, and real-time monitoring, NPAV EDR protects endpoints against ransomware, cryptor-like malware, and other unauthorized file encryption attempts. NPAV EDR continuously monitors file system activity, process behavior, and encryption patterns to detect: Threats are identified in real time, allowing immediate action before encryption spreads across the endpoint or network.
When ransomware activity is detected, NPAV EDR automatically initiates predefined response actions based on the configured security policy. These actions include: These automated actions help contain attacks and prevent ransomware from spreading to other systems. To minimize the impact of an active ransomware attack, NPAV EDR can temporarily isolate compromised endpoints from the corporate network while allowing communication with the management console. Administrators can configure the isolation duration or manually restore network connectivity after remediation.
Where supported, NPAV EDR can initiate rollback and recovery actions to restore files and system changes performed by ransomware or other malicious processes. This capability helps minimize data loss and enables faster recovery following an attack. All ransomware detections, response actions, and recovery events are visible through the NPAV EDR Management Console , enabling security teams to: With proactive detection, automated response, and centralized management, NPAV EDR helps organizations defend against modern ransomware attacks while reducing downtime and protecting critical business data.
Known threats : Blocks behaviors associated with known malware threats Known and potential threats : Blocks behaviors associated with known threats and takes action on behavior that is potentially malicious 2. System Architecture & Core Working Principles Protect documents against unauthorized encryption or modification : Stops potential ransomware threats from encrypting or modifying the contents of documents Automatically back up and restore files changed by suspicious programs : Creates backup copies of files being encrypted on endpoints to prevent any loss of data after detecting a ransomware threat Automatic file backup requires at least 100 MB of disk space on the agent endpoint and only backs up files that are less than 10 MB in size.
Block processes commonly associated with ransomware : Blocks processes associated with known ransomware threats before any encryption or modification of documents can occur Enable program inspection to detect and block compromised executable files : Program inspection monitors processes and performs API hooking to determine if a program is behaving in an unexpected manner. Although this procedure increases the overall detection ratio of compromised executable files, it may result in decreased system performance.
Program inspection provides increased security if you select Known and potential threats in the Threats to block drop-down. Anti-exploit Protection requires that you select Enable program inspection to detect and block compromised executable files . Apex One accepts a maximum combined total of 1024 approved programs and blocked programs. Apply to All Agents : Applies settings to all existing agents and to any new agent added to an existing/future domain. Future domains are domains not yet created at the time you configured the settings.
Apply to Future Domains Only : Applies settings only to agents added to future domains. This option will not apply settings to new agents added to an existing domain. Learn how to design a cybersecurity system that monitors Windows endpoints, collects security telemetry, detects suspicious ransomware-related behavior, and uses AWS infrastructure for centralized analysis and monitoring.
A simulation-based Endpoint Detection and Response (EDR) system designed to detect ransomware activity using behavioral analysis and entropy-based encryption detection, and visualize incidents through a SOC-style web dashboard. This project demonstrates how modern EDR solutions detect, analyze, and respond to ransomware threats at the endpoint level.
Ransomware attacks can encrypt thousands of files within seconds, causing severe data loss and operational downtime. Traditional signature-based antivirus systems often fail to detect new or unknown ransomware variants. This project addresses the problem by implementing behavior-based detection, which identifies malicious activity based on how ransomware behaves rather than how it looks.
• Endpoint threat detection concepts • Behavioral malware analysis • Shannon entropy implementation • Python security scripting • Flask REST API design • SOC dashboard development • Incident logging & response simulation • Understanding of ransomware attack behavior • Blue Team detection logic • SOC-style alert visualization • File system monitoring techniques • Encryption detection using entropy • Incident response workflow simulation II System Architecture File System Activity ↓ Behavioral Detection Engine ↓ Entropy-Based Encryption Analysis ↓ Incident Logging ↓ Flask REST API ↓ SOC Dashboard (Frontend) Screenshots demonstrating detection, alerts, and dashboard visualization are provided below.
It is a simulation-based EDR system and does not perform kernel-level enforcement or real malware execution. Anusha Upadhyay Cybersecurity Enthusiast | Blue Team | SOC Analyst Aspirant Passionate about defensive security, malware behavior analysis, and SOC operations. Learn how an automated ransomware response playbook quickly detects, contains, and prevents ransomware from spreading.
An automated ransomware incident response playbook ensures fast detection, containment, and remediation. It provides a structured approach that limits the lateral movement of the attacker. The 9 steps for playbook automation include confirming the incident, isolating endpoints, preserving evidence, and scoping the impact.
It also comprises blocking command-and-control, eradicating persistence, restoring from clean backups, and updating the playbook. Measuring performance metrics, such as MTTD, MTTR, detection effectiveness, etc., can help organizations continuously refine their playbooks and improve overall ransomware resilience.
Modern ransomware attacks are multi-stage and fast. They target endpoints, networks, cloud workloads, and user identities simultaneously. Hence, these ransomware attacks can outpace security teams using traditional, manual incident response. This can allow malware to move laterally across systems before containment measures take effect. That’s when an automated ransomware response playbook can help. It brings speed and structure to the response process.
Moreover, detection, containment, investigation, and remediation actions are orchestrated immediately upon identifying threats. The key thing to understand here is that automation does not replace human expertise. It ensures critical steps occur without delay, thereby reducing dwell time and protecting crucial assets. This can be especially beneficial in hybrid and remote environments. It helps maintain visibility and enforce security policies.
Even skilled security teams can struggle during ransomware incidents because of fragmented visibility and manual workflows. Their judgment can fail during time-sensitive decision-making. Moreover, alerts may originate from multiple tools and sources, including endpoint detection tools , email security systems, network monitoring , and cloud logs. Without automated correlation, teams can easily miss early indicators. Moreover, teams relying on manual triage or email-based coordination can react slowly. This gives ransomware time to move laterally and encrypt critical data.
Furthermore, hybrid and remote environments introduce additional complexity. For instance, security teams may lack a complete inventory of endpoints, user accounts, or cloud workloads. This can create blind spots for movement. Most importantly, human fatigue and high-pressure conditions can result in skipped steps, such as isolating affected systems or collecting forensic evidence. This further increases the risk of prolonged impact.
An untested playbook is just a document - and teams rarely discover its gaps until an actual ransomware incident is already underway. Ransomware has become a major operational and security challenge. Future Market Insights highlights that the global ransomware protection market reached $31.5 billion in 2025. It will cross $136.7 billion by 2035. This growth is driven by the urgent need for automated detection and response capabilities that traditional manual workflows struggle to deliver.
Automation dramatically reduces ransomware response time. It executes predefined containment and remediation actions as soon as suspicious activity is detected, often guided by a ransomware playbook. For instance, endpoints reflecting unusual encryption behavior or connecting with known malicious servers can be automatically isolated. User credentials can be revoked, network traffic can be blocked, and suspicious processes can be terminated. There is no need for manual intervention.
Automated workflows accelerate response, cutting reaction time from hours to seconds and limiting lateral movement. In parallel, logs, indicators of compromise (IoCs) , and forensic records can be collected automatically. This allows security analysts to focus on investigation and strategic decision-making rather than repetitive operational tasks. Furthermore, automation supports hybrid and cloud environments. It enforces policies consistently across both on-premises and cloud assets. Controlled and phased containment helps keep critical services running. At the same time, it neutralizes threats and reduces downtime.
Use this report to understand attacker tactics, assess your exposure, and prioritize action before the next exploit hits your environment. Automating ransomware containment starts with putting the right elements in place. These building blocks ensure that security teams detect threats early and trigger predefined responses to contain ransomware quickly and consistently. When properly implemented, they enable fast isolation and coordinated actions across tools.
Organizations must define a clear ransomware response checklist . It should guide how actions are triggered and executed before implementing an automated ransomware response playbook. Automation should support immediate containment actions, such as isolating affected systems, revoking compromised credentials, blocking malicious traffic, and collecting forensic evidence. Another crucial aspect is maintaining centralized visibility, consistent policy enforcement, and alignment with zero-trust principles to prevent lateral movement.
Together, a structured ransomware response checklist enables organizations to shift from ad-hoc reactions to a repeatable, resilient incident response approach. As stated, a structured ransomware incident response automation playbook transforms planning into action. The following 9-step plan reflects how organizations can automate detection, containment, and recovery.
First, validate that the activity is ransomware and not a false positive. Automated detections, such as rapid file encryption, ransom note creation, suspicious process execution, or known ransomware hashes, help confirm the incident quickly. 3. Software Implementation, Frameworks & Protocols CISA’s federal incident response playbook instructs agencies to notify CISA with an initial incident report within 1 hour after incident determination.
Once confirmed, an incident response case should be automatically created in the response platform. This helps track actions, evidence, and decisions. Besides, early confirmation enables faster coordination and reduces uncertainty during the critical initial phase. Regulatory or authority notification workflows can also be triggered based on the severity. For instance, an EDR alert detects mass file renaming and encryption. It then automatically opens a ransomware incident case and notifies the SOC lead.
Once ransomware is confirmed, organizations should immediately switch to out-of-band communication channels. This reduces the risk of attackers monitoring internal email or collaboration tools. Decision-making authority should be clearly defined and limited to a small group to avoid confusion or conflicting actions. Automation can notify predefined stakeholders using secure messaging or phone-based alerts. This step ensures sensitive response decisions remain protected and coordinated.
Immediate containment is critical to prevent ransomware from spreading laterally. Automated endpoint security can quickly identify and isolate compromised devices, ensuring rapid containment without manual intervention. Advanced automated endpoint security can detect malicious activity in real-time and immediately neutralize threats. This stops ransomware encryption and lateral movement by the attacker. Most importantly, endpoints can be contained without taking systems offline. This ensures that production and critical operations continue uninterrupted.
Moreover, enforce network segmentation policies to restrict communication between compromised and clean systems. This minimizes the blast radius without shutting down the entire environment. Isolation actions should be precise to avoid unnecessary business disruption. It is crucial to preserve forensic evidence before removing malware or reimaging systems. Automation can collect memory dumps, logs, file hashes, registry data, and authentication records.
Building a clear timeline helps teams understand how the attack started. It further allows teams to analyze how it spread and escalated. This evidence supports root cause analysis and regulatory reporting. Destructive actions should only begin after safeguarding all the critical assets. Determine the extent of ransomware spread. This is a key containment step. Automated correlation across endpoint, network, identity, and cloud logs helps identify additional assets that were impacted.
Enrichment with threat intelligence provides insight into known ransomware behaviors and infrastructure. This allows teams to prioritize high-risk systems and users. Accurate scoping prevents both under-response and over-containment. Ransomware commonly establishes contact with command-and-control servers and may attempt data exfiltration . Automated response should immediately block malicious IPs, domains, and URLs across firewalls, proxies, and DNS controls.
Identity-based restrictions can also limit attacker movement. Cutting off these channels prevents further instructions and data loss. This step reduces the attacker’s ability to escalate or extort. For instance, automatically block known ransomware C2 domains across network and cloud security controls. After containment, the focus shifts to removing persistence mechanisms and closing the original entry point. Automation can identify scheduled tasks, malicious services, registry changes, or backdoor accounts.
Next, immediately address the vulnerabilities or misconfigurations that enabled access. This prevents reinfection once systems are restored. Eradication must be thorough and verified. System restoration should only occur from verified and clean backups. Through ransomware incident response automation, workflows can validate backup integrity and confirm systems meet security checks before reconnecting to the network. For instance, recovery gates help confirm that malware and vulnerabilities have been eliminated.
This controlled strategy prevents ransomware from being reintroduced into the environment. This way, businesses can achieve quicker incident detection and response in a phased manner. The final step focuses on documentation and continuous improvement within the ransomware recovery playbook. Automated reporting consolidates timelines, actions taken, impact analysis, and lessons learned. Detection rules and response playbooks should be updated based on observed attacker behavior.
CIRO’s playbook recommends formal impact-assessment checkpoints on Day 1, 7, 14, 21, and 28 after a ransomware event. This strengthens future defenses and improves response speed. Post-incident reviews ensure continuous improvement and readiness. Measuring ransomware playbook performance helps organizations evaluate how effectively they detect, respond to, contain, and recover from ransomware incidents.
Gartner emphasizes that incident response processes should be measured across quality, speed, and effort metrics to target improvement and demonstrate value. This supports practical and complianceIaligned playbook measurement. Compliance alignment: It evaluates alignment with frameworks, such as NIST and CISA guidance. Compliance-ready playbooks support audits and regulatory obligations.
A ransomware incident response playbook enables organizations to detect, contain, and remediate ransomware incidents quickly while minimizing operational disruption. It helps teams standardize response actions, leverage automation, and continuously measure performance through key metrics. This allows organizations to limit lateral movement and accelerate recovery. Moreover, regular testing and post-incident improvements ensure the playbook remains effective against evolving ransomware tactics.
Organizations can leverage Fortinet’s security operations capabilities, such as FortiSOAR and FortiSIEM , to operationalize this method within an integrated security architecture. For instance, Fortinet enables playbook-driven ransomware response through FortiSOAR and FortiSIEM, which support customizable and automated incident response playbooks. These platforms allow security teams to design, orchestrate, and execute ransomware response workflows. As a result, teams can experience reduced downtime and improved cyber resilience .
Leverage proactive ransomware advisory services to assess readiness and strengthen incident response playbooks. Start by automating alert triage, enrichment, and basic validation to identify ransomware signals. This gives analysts instant context and saves valuable time during the initial response. Actions that could disrupt business operations, such as shutting down systems or isolating critical servers, should require human approval. This ensures technical actions align with business risk and priorities.
Automated playbooks trigger containment and remediation steps immediately after detection, without the need for manual intervention. This fast, consistent execution reduces response time and limits damage. Isolate infected endpoints from the network and block malicious connections to stop lateral movement. Deactivating compromised accounts and restricting shared access helps contain the spread.
Please fill out the form and a knowledgeable representative will get in touch with you soon. Known threats : Blocks behaviors associated with known malware threats Known and potential threats : Blocks behaviors associated with known threats and takes action on behavior that is potentially malicious Protect documents against unauthorized encryption or modification : Stops potential ransomware threats from encrypting or modifying the contents of documents Automatically back up and restore files changed by suspicious programs : Creates backup copies of files being encrypted on endpoints to prevent any loss of data after detecting a ransomware threat Automatic file backup requires at least 100 MB of disk space on the agent endpoint and only backs up files that are less than 10 MB in size.
Block processes commonly associated with ransomware : Blocks processes associated with known ransomware threats before any encryption or modification of documents can occur Enable program inspection to detect and block compromised executable files : Program inspection monitors processes and performs API hooking to determine if a program is behaving in an unexpected manner. Although this procedure increases the overall detection ratio of compromised executable files, it may result in decreased system performance.
Program inspection provides increased security if you select Known and potential threats in the Threats to block drop-down. Anti-exploit Protection requires that you select Enable program inspection to detect and block compromised executable files . Apex One accepts a maximum combined total of 1024 approved programs and blocked programs. Apply to All Agents : Applies settings to all existing agents and to any new agent added to an existing/future domain. Future domains are domains not yet created at the time you configured the settings.
Apply to Future Domains Only : Applies settings only to agents added to future domains. This option will not apply settings to new agents added to an existing domain. 4. Practical Deployment, Analysis & Case Studies Deep Security provides security settings that you can apply to Windows and Linux machines protected by a Deep Security Agent to enhance your malware and ransomware detection and clean rate. These settings enable you to go beyond malware pattern matching and identify suspicious files that could potentially contain emerging malware that has not yet been added to the anti-malware patterns (known as a zero-day attack).
Threat detection : To avoid detection, some types of malware attempt to modify system files or files related to known installed software. These types of changes often go unnoticed because the malware takes the place of legitimate files. Deep Security can monitor system files and installed software for unauthorized changes to detect and prevent these changes from occurring. Anti-exploit : Malware creators can use malicious code to hook in to user mode processes in order to gain privileged access to trusted processes and to hide the malicious activity. Malware creators inject code into user processes through DLL injection, which calls an API with escalated privilege. They can also trigger an attack on a software exploit by feeding a malicious payload to trigger code execution in memory. In Deep Security, the anti-exploit functionality monitors for processes that may be performing actions that are not typically performed by a given process. Using a number of mechanisms, including Data Execution Prevention (DEP), Structured Exception Handling Overwrite Protection (SEHOP), and heap spray prevention, Deep Security can determine whether a process has been compromised and then terminate the process to prevent further infection.
Extended ransomware protection : Ransomware has become more sophisticated and targeted. Most organizations have a security policy that includes anti-malware protection on their endpoints, which offers a level of protection against known ransomware variants. However, it may not be sufficient to detect and prevent an outbreak for new variants. The ransomware protection offered by Deep Security can protect documents against unauthorized encryption or modification. Deep Security has also incorporated a data recovery engine that can optionally create copies of files being encrypted to offer users an added chance of recovering files that may have been encrypted by a ransomware process.
Enhanced scanning is configured as part of the anti-malware settings applied to a policy or individual computer. For information on configuring anti-malware protection, see Enable and configure Anti-Malware . These settings can only be applied to Windows and Linux machines that are protected by a Deep Security Agent. Enhanced scanning may have a performance impact on agent computers running applications with heavy loads. Review Improve Anti-Malware performance before deploying Deep Security Agents with enhanced scanning enabled.
The first step is to enable enhanced scanning in a real-time malware scan configuration: By default, real-time scans are set to scan all directories. If you change the scan settings to scan a directory list, the enhanced scanning may not work as expected. For example, if you set Directories to scan to scan Folder1 and ransomware occurs in Folder1, it may not be detected if the encryption associated with the ransomware happens to files outside of Folder1.
When Deep Security discovers activity or files that match the enhanced scan settings you have enabled, it logs an event that you can view by navigating to Events & Reports > Events > Anti-Malware Events to see a list of events. The event is identified as Suspicious activity or Unauthorized change in the Major Virus Type column, with details displayed in the Target(s) and TargetType columns.
Deep Security performs many types of checks related to the enhanced scan settings, and the actions that it takes depend on the type of check that finds an issue. Deep Security may Deny Access, Terminate, or Clean a suspicious object. These actions are determined by Deep Security and are not configurable, with the exception of the Clean action: If you investigate and find that an identified file is not harmful, you can right-click the event and click Allow to add the file to a scan exclusion list for the computer or policy. You can check the scan exclusion list in the policy or computer editor, under Anti-Malware > Advanced > Behavior Monitoring Protection Exceptions .
The enhanced scanning features described in this article require Internet access to check files against the Global Census Server and Good File Reputation Service. If your Deep Security Agents cannot access the Internet directly, see Configure agents that have no internet access for workarounds. Behavior Monitoring protects clients from unauthorized changes to the operating system, registry entries, software, files and folders. The settings can be enabled or disabled only per group.
Necessary layer of additional threat protection from programs that exhibit malicious behavior is given upon using this. It observes system events over a period of time. As programs execute different combinations or sequences of actions, Malware Behavior Blocking detects known malicious behavior and blocks the associated programs. Use this feature to ensure a higher level of protection against new, unknown, and emerging threats.
Enable document protection against unauthorized encryption or modification : Protects documents from unauthorized changes. Enabling this option stops processes that rename, modify and delete files, and then quarantines the programs that are running these processes. Enable program inspection to detect and block compromised executable files : Protects endpoints from ransomware attacks by increasing the overall detection ratio for compromised executable files and programs that are behaving in an unexpected manner.
Protects all Intuit QuickBooks files and folders from unauthorized changes by other programs. Enabling this feature will not affect changes made from within Intuit QuickBooks programs, but will only prevent changes to the files from other unauthorized applications. For a more generic approach to protecting against unauthorized software and malware attacks, Event monitoring oversees system areas for certain events, allowing administrators to regulate programs that trigger such events. Use Event Monitoring if you have specific system protection requirements that are above and beyond what is provided by Malware Behavior Blocking.
When Event Monitoring detects a monitored system event, it performs the action configured for the event. The following table lists possible actions that administrators can take on monitored system events. Worry-Free Business Security Services prompts users to allow or deny programs associated with an event and add the programs to the exception list.
If the user does not respond within a certain time period, Worry-Free Business Security Services automatically allows the program to run. The default time period is 30 seconds. Worry-Free Business Security Services always blocks programs associated with an event and records this action in the logs. When a program is blocked and alerts are enabled, Worry-Free Business Security Services displays an alert on the Worry-Free Business Security Services computer.
Approved Program List and a Blocked Program List can be found under Scan Exclusions > Behavior Monitoring . Programs in the Approved Programs List can be started even if they violate a monitored change, while programs in the Blocked Program List can never be started. Enable Security Agent alerts for Behavior Monitoring by going to Privileges and Other Settings > Alerts and checking Behavior Monitoring under Threat Protection.
Behavior Monitoring protects clients from unauthorized changes to the operating system, registry entries, other software, files and folders. When enabled, Worry-Free Business Security temporarily blocks a newly-encountered program downloaded through HTTP or email applications and prompts users to select an action ("Block once" or "Allow once"). If users do not select an action within the specified time period, the program is automatically blocked.
Prompt users before executing newly encountered programs downloaded through HTTP or email applications (Server platforms excluded) : After detecting a "newly encountered" file, administrators can choose to prompt users before executing the file. Trend Micro classifies a program as newly encountered based on the number of file detections or historical age of the file as determined by the Smart Protection Network.
Web Reputation enhances protection against malicious websites. Web Reputation leverages Trend Micro's extensive web security database to check the reputation of URLs that Clients are attempting to access or URLs embedded in email messages that are contacting websites. Enable Browser Exploit Prevention > Block websites containing malicious script to protect against browser exploits containing malicious script.
Trend Micro Predictive Machine Learning uses advanced machine learning technology to detect emerging unknown security risks found in low-prevalence suspicious processes or files originating from removable storage, web, or email channels. Under Detection Settings, select the type of detections and related action that Predictive Machine Learning takes. Refer to the KB article: Downloading and Using the Trend Micro Ransomware File Decryptor .
Worry-Free Business Security Services 6.5 , Worry-Free Business Security Services 6.3 , Worry-Free Business Security Services All Enabling Behavior Monitoring including warning messages, Web Reputation Services and Predictive Machine Learning add more layer of security to Worry-free Business Security Services (WFBS-SVC) users.
Learn how to configure WFBS-SVC to protect users from ransomware infections by following this KB article. Behavior Monitoring protects clients from unauthorized changes to the operating system, registry entries, software, files and folders. The settings can be enabled or disabled only per group. Necessary layer of additional threat protection from programs that exhibit malicious behavior is given upon using this. It observes system events over a period of time. As programs execute different combinations or sequences of actions, Malware Behavior Blocking detects known malicious behavior and blocks the associated programs. Use this feature to ensure a higher level of protection against new, unknown, and emerging threats.
Enable document protection against unauthorized encryption or modification : Protects documents from unauthorized changes. Enabling this option stops processes that rename, modify and delete files, and then quarantines the programs that are running these processes. Enable program inspection to detect and block compromised executable files : Protects endpoints from ransomware attacks by increasing the overall detection ratio for compromised executable files and programs that are behaving in an unexpected manner.
Protects all Intuit QuickBooks files and folders from unauthorized changes by other programs. Enabling this feature will not affect changes made from within Intuit QuickBooks programs, but will only prevent changes to the files from other unauthorized applications. For a more generic approach to protecting against unauthorized software and malware attacks, Event monitoring oversees system areas for certain events, allowing administrators to regulate programs that trigger such events. Use Event Monitoring if you have specific system protection requirements that are above and beyond what is provided by Malware Behavior Blocking.
When Event Monitoring detects a monitored system event, it performs the action configured for the event. 5. Performance Evaluation & Extended Technical Observations The following table lists possible actions that administrators can take on monitored system events. Worry-Free Business Security Services prompts users to allow or deny programs associated with an event and add the programs to the exception list.
If the user does not respond within a certain time period, Worry-Free Business Security Services automatically allows the program to run. The default time period is 30 seconds. Worry-Free Business Security Services always blocks programs associated with an event and records this action in the logs. When a program is blocked and alerts are enabled, Worry-Free Business Security Services displays an alert on the Worry-Free Business Security Services computer.
Approved Program List and a Blocked Program List can be found under Scan Exclusions > Behavior Monitoring . Programs in the Approved Programs List can be started even if they violate a monitored change, while programs in the Blocked Program List can never be started. Enable Security Agent alerts for Behavior Monitoring by going to Privileges and Other Settings > Alerts and checking Behavior Monitoring under Threat Protection.
Behavior Monitoring protects clients from unauthorized changes to the operating system, registry entries, other software, files and folders. When enabled, Worry-Free Business Security temporarily blocks a newly-encountered program downloaded through HTTP or email applications and prompts users to select an action ("Block once" or "Allow once"). If users do not select an action within the specified time period, the program is automatically blocked.
Prompt users before executing newly encountered programs downloaded through HTTP or email applications (Server platforms excluded) : After detecting a "newly encountered" file, administrators can choose to prompt users before executing the file. Trend Micro classifies a program as newly encountered based on the number of file detections or historical age of the file as determined by the Smart Protection Network.
Web Reputation enhances protection against malicious websites. Web Reputation leverages Trend Micro's extensive web security database to check the reputation of URLs that Clients are attempting to access or URLs embedded in email messages that are contacting websites. Enable Browser Exploit Prevention > Block websites containing malicious script to protect against browser exploits containing malicious script.
Trend Micro Predictive Machine Learning uses advanced machine learning technology to detect emerging unknown security risks found in low-prevalence suspicious processes or files originating from removable storage, web, or email channels. Under Detection Settings, select the type of detections and related action that Predictive Machine Learning takes. Refer to the KB article: Downloading and Using the Trend Micro Ransomware File Decryptor .
The rapid evolution of cyber threats has outpaced traditional detection methodologies, necessitating innovative approaches capable of addressing the adaptive and complex behaviors of modern adversaries. A novel framework was introduced, leveraging Temporal-Correlation Graphs to model the intricate relationships and temporal patterns inherent in malicious operations. The approach dynamically captured behavioral anomalies, offering a robust mechanism for distinguishing between benign and malicious activities in real-time scenarios. Extensive experiments demonstrated the framework’s effectiveness across diverse ransomware families, with consistently high precision, recall, and overall detection accuracy.
Comparative evaluations highlighted its better performance over traditional signature-based and heuristic methods, particularly in handling polymorphic and previously unseen ransomware variants. The architecture was designed with scalability and modularity in mind, ensuring compatibility with enterprise-scale environments while maintaining resource efficiency. Analysis of encryption speeds, anomaly patterns, and temporal correlations provided deeper insights into the operational strategies of ransomware, validating the framework’s adaptability to evolving threats. The research contributes to advancing cybersecurity technologies by integrating dynamic graph analytics and machine learning for future innovations in threat detection. Results from this study underline the potential for transforming the way organizations detect and mitigate complex cyberattacks.
The proliferation of digital technology and interconnected systems has significantly increased the reliance of organizations and individuals on data availability and system integrity. This dependency, while driving innovation and productivity, has concurrently introduced unprecedented vulnerabilities to cyber threats. Among such threats, ransomware has emerged as one of the most disruptive and economically damaging forms of cybercrime. It achieves its devastating impact through the encryption of critical data, followed by demands for monetary payment in exchange for decryption keys. The rapid evolution of ransomware techniques, coupled with the increasing sophistication of delivery mechanisms, has outpaced traditional detection methodologies, leaving organizations vulnerable to severe financial and operational consequences.
Over the past decade, ransomware operators have demonstrated an acute understanding of defensive technologies, adapting their strategies to bypass conventional antivirus solutions and static signature-based detection systems. Modern ransomware variants often employ polymorphic techniques, allowing them to modify their code structure dynamically to evade signature-based detection mechanisms. Additionally, the incorporation of advanced encryption algorithms and the use of anonymizing technologies, such as the Tor network and cryptocurrency for payments, have rendered conventional investigative approaches ineffective. The continuous escalation in both the frequency and severity of ransomware attacks has demonstrated the urgent need for innovative solutions capable of addressing the limitations of existing detection frameworks.
Addressing the complexities of ransomware detection requires a shift from static and reactive paradigms to proactive and context-aware methodologies. The novel framework introduced in this study, referred to as Temporal-Correlation Graphs, leverages time-sensitive behavioral patterns to construct multidimensional representations of ransomware activity. This approach captures the temporal relationships between various operational stages of ransomware execution, enabling the identification of anomalous behaviors indicative of malicious intent. Through the systematic analysis of behavioral sequences, the proposed framework introduces a new mechanism for recognizing ransomware activities that might otherwise evade detection via traditional techniques.
The foundation of this framework is rooted in the hypothesis that ransomware exhibits distinct temporal behaviors when interacting with system resources, networks, and file systems. Such behaviors, when analyzed through graph-based representations, reveal patterns that distinguish malicious activities from benign operations. Unlike signature-based or heuristic approaches, which rely heavily on predefined rules or static models, the graph-based paradigm dynamically adapts to new and unseen ransomware variants through its reliance on relational and temporal data. By focusing on the intrinsic characteristics of ransomware operations, the proposed methodology significantly enhances detection capabilities without requiring frequent model updates.
While the technical implementation of Temporal-Correlation Graphs forms the core of this research, its broader implications extend to the development of more resilient cybersecurity strategies. The ability to detect ransomware during its early execution stages mitigates the potential for widespread data encryption and service disruption, thereby reducing the overall impact of attacks. Moreover, the adoption of graph-based methodologies sets a precedent for addressing other forms of cyber threats, offering a versatile tool for enhancing security across various domains. This research not only introduces a novel detection paradigm but also provides a scalable foundation for future advancements in ransomware defense mechanisms.
Through the development and evaluation of this framework, the study contributes to the growing body of knowledge aimed at combating ransomware threats. By proposing an approach that combines the rigor of mathematical modeling with the practicality of real-world application, the research aims to bridge the gap between theoretical innovation and operational deployment. The results of this study are expected to demonstrate the efficacy of Temporal-Correlation Graphs in detecting a wide range of ransomware variants, offering valuable insights for researchers and practitioners in the cybersecurity field.
The evolving landscape of ransomware attacks has necessitated significant advancements in detection strategies, prompting the exploration of diverse techniques to mitigate their growing threat. This section provides an overview of existing detection methodologies, highlights the limitations of current approaches, and identifies critical gaps that hinder their effectiveness in combating ransomware.
Machine learning has played a prominent role in ransomware detection, with studies leveraging supervised learning algorithms to classify ransomware behaviors based on extracted features [ 1 ] . Decision tree-based models achieved high accuracy in distinguishing ransomware activities from benign processes through the analysis of system-level event logs [ 2 ] . Neural networks demonstrated superior capability in capturing non-linear relationships within ransomware operational patterns, leading to improved detection rates in dynamic execution environments [ 3 ] . Ensemble techniques, combining multiple classifiers, enhanced detection robustness by mitigating the effects of false positives and false negatives [ 4 ] .
Feature engineering approaches, emphasizing entropy-based analysis of encrypted files, facilitated early detection of ransomware prior to full payload execution [ 5 ] . Static analysis methods utilizing signature-based pattern matching were effective against known ransomware variants but struggled to maintain efficacy against polymorphic and zero-day threats [ 6 , 7 ] . Dynamic behavioral analysis, relying on sandboxing environments, provided insights into ransomware execution sequences but incurred substantial computational overhead, limiting scalability in real-time applications [ 8 , 9 ] . The incorporation of graph-based models allowed the mapping of ransomware propagation pathways, enhancing detection capabilities in networked systems [ 10 ] . Heuristic approaches leveraging rule-based systems identified anomalous behaviors indicative of ransomware execution but lacked adaptability to novel attack strategies [ 11 ] . Despite the advancements, significant challenges persisted in handling large-scale data, reducing false positives, and achieving real-time responsiveness [ 12 ] .
Existing detection methodologies have demonstrated limitations in addressing the adaptability and sophistication of modern ransomware variants, particularly in environments with high operational complexity [ 13 ] . Static analysis approaches were constrained by their reliance on predefined signatures, rendering them ineffective against rapidly evolving ransomware families [ 14 , 15 ] . Dynamic analysis methods faced challenges in balancing detection precision with computational efficiency, particularly in scenarios requiring large-scale deployment [ 16 ] . Behavioral analysis frameworks often relied on handcrafted features, which limited their ability to generalize across diverse ransomware strains [ 17 ] . Graph-based approaches, while effective in capturing propagation dynamics, encountered difficulties in managing the computational demands of constructing and processing complex relational models [ 18 ] . The integration of detection systems into real-time monitoring workflows remained an unresolved issue, as it required overcoming latency constraints without compromising detection accuracy [ 19 ] . Traditional machine learning models struggled to maintain robustness when exposed to adversarially crafted ransomware designed to evade detection mechanisms [ 20 ] . Furthermore, reliance on labeled datasets for supervised learning posed challenges in accommodating the diversity and volume of emerging ransomware variants [ 21 ] .
Few methodologies addressed the issue of encrypted communications utilized during ransomware operations, which masked critical behavioral indicators [ 22 ] . The lack of standardized evaluation frameworks hindered the ability to compare and benchmark detection approaches effectively across different scenarios [ 23 ] . Additionally, the absence of comprehensive datasets representing the full spectrum of ransomware activities limited the potential for creating universally applicable detection solutions [ 24 ] .
Anomaly detection frameworks were extensively applied to identify deviations from normal system behaviors indicative of ransomware activities [ 25 ] . Statistical models quantified deviations in resource utilization patterns, such as CPU and disk I/O, to identify ransomware-related anomalies [ 26 ] . Clustering algorithms were used to group similar operational behaviors, facilitating the detection of outlier processes associated with ransomware execution [ 27 ] . Density-based techniques identified sparse events within network traffic, corresponding to ransomware propagation attempts [ 28 ] . Temporal analysis of event sequences revealed timing irregularities characteristic of ransomware, enabling early-stage detection [ 29 ] . Hybrid approaches combining anomaly detection with supervised learning achieved enhanced precision through the integration of known patterns with unknown anomalies [ 30 , 31 ] . However, challenges arose in defining accurate baselines for normal behavior in highly dynamic environments, such as enterprise networks [ 32 ] . The reliance on thresholds for anomaly scoring introduced a trade-off between sensitivity and specificity, impacting overall detection efficacy [ 33 ] . Real-time anomaly detection systems required significant computational resources, posing scalability concerns in high-throughput scenarios [ 34 ] . Moreover, anomaly detection frameworks often struggled to attribute observed deviations to ransomware-specific activities, reducing their operational effectiveness [ 35 ] .
The development of an innovative ransomware detection system necessitated the creation of a robust methodological foundation capable of capturing and analyzing complex temporal and behavioral patterns associated with ransomware operations. The proposed framework employs Temporal-Correlation Graphs, an advanced analytical tool designed to dynamically represent and evaluate the multifaceted interactions inherent in ransomware activity. This section elaborates on the conceptualization of the framework, the architectural design, the process of graph construction, and the integration of the system into automated pipelines.
The concept of Temporal-Correlation Graphs was formulated to address the inherent limitations of traditional detection systems through the encapsulation of temporal dependencies and behavioral correlations observed during ransomware execution. Graph structures were utilized to represent interconnected sequences of system events, enabling the identification of relational patterns indicative of malicious activities. Temporal attributes were embedded within the nodes and edges of the graph to provide a chronological dimension, enhancing the interpretability of behavioral flows within the system. The use of weighted edges allowed the quantification of interaction strengths, facilitating the prioritization of highly suspicious connections for further analysis. Directed graph structures ensured the representation of causality in event sequences, aligning the analytical framework with the operational characteristics of ransomware. Subgraph extraction techniques segmented the graph into meaningful clusters, isolating patterns associated with specific ransomware behaviors. Anomaly detection within graph-based representations leveraged topological features, such as node centrality and edge density, to distinguish normal system operations from deviations. The dynamic updating of graphs during runtime maintained the relevance of detection processes against adaptive ransomware tactics. The integration of probabilistic modeling into graph attributes captured uncertainties in event correlations, enhancing the robustness of detection outcomes.
The architecture of the proposed framework, illustrated in Figure 2 , was designed to ensure modularity, scalability, and adaptability to meet the diverse requirements of real-time ransomware detection. A preprocessing module transformed raw system logs into structured data formats suitable for graph construction, ensuring consistency and completeness in data representation. The core analysis module employed graph-based algorithms to extract temporal and relational features, integrating machine learning models for classification tasks. A feature engineering component selected and optimized the attributes most relevant to ransomware detection, improving computational efficiency without compromising accuracy. The communication interface enabled seamless integration with system monitoring tools, supporting both real-time and batch processing modes. Storage subsystems were optimized to retain historical data for longitudinal analyses, ensuring the ability to detect slow-acting ransomware variants. A visualization module translated graph outputs into interpretable formats, providing actionable insights for system administrators. Modular design principles facilitated the customization of the framework to meet the specific needs of various operational environments. Parallel processing capabilities ensured the timely analysis of high-volume data streams, addressing scalability challenges in enterprise settings. Security mechanisms embedded within the architecture safeguarded the integrity of data inputs and analytical outputs, preventing potential manipulation during detection operations.
The process of graph construction began with the parsing of system-level event logs, where distinct events were mapped to nodes and interactions were represented through directed edges. Temporal alignment techniques ensured the chronological consistency of events, maintaining the accuracy of causal relationships within the graph structure. Feature mapping leveraged statistical and behavioral attributes, associating each node and edge with descriptors such as frequency, duration, and interaction type. Aggregation methods summarized repetitive interactions, reducing graph complexity while preserving essential behavioral patterns. Normalization techniques standardized feature scales, facilitating the application of machine learning algorithms during subsequent analysis. Structural properties, including graph diameter and clustering coefficients, were computed to identify network-wide anomalies indicative of ransomware activities. Node-ranking algorithms prioritized critical events based on their centrality measures, streamlining the focus of detection processes. The inclusion of edge weights enabled the representation of interaction intensities, enhancing the model’s sensitivity to subtle deviations in operational behaviors. Subgraph matching algorithms identified recurring malicious patterns within graph structures, isolating known ransomware signatures. Feature embedding methodologies translated graph attributes into vector representations, enabling compatibility with advanced analytical models.
The integration of the framework into automated pipelines ensured seamless deployment within diverse operational environments, addressing the need for scalability and adaptability. Data ingestion pipelines captured and preprocessed live system logs, ensuring the timely availability of input data for analysis. Streaming frameworks facilitated the continuous updating of graph structures, maintaining the relevance of detection processes in dynamic environments. Analytical pipelines incorporated machine learning models trained on graph-derived features, enabling the real-time classification of ransomware behaviors. Alerting mechanisms triggered predefined responses upon the identification of high-risk activities, enhancing system resilience against active threats. Batch processing pipelines supported retrospective analyses, enabling the investigation of ransomware campaigns that evaded initial detection. Workflow orchestration tools coordinated the interactions between modular components, optimizing resource allocation and minimizing latency. Logging mechanisms documented all analytical operations, ensuring traceability and supporting compliance with cybersecurity regulations. Error-handling routines addressed disruptions in data flow, maintaining the continuity of detection processes during adverse conditions. Integration with external threat intelligence systems enhanced the contextual understanding of detected behaviors, supporting proactive defense strategies against ransomware attacks.
The evaluation of the proposed framework required a rigorous experimental design, encompassing dataset selection, simulation environment configuration, and the definition of evaluation metrics. Each component of the experimental setup was tailored to validate the framework’s ability to detect and classify ransomware with high accuracy and reliability. Datasets were selected based on their representativeness of real-world ransomware activities, encompassing diverse variants and operational behaviors. A comprehensive selection process focused on obtaining publicly available datasets that reflected the diversity of ransomware attack patterns observed in recent years. Table I provides an overview of the key datasets utilized for the experimental analysis, outlining their characteristics and preprocessing methodologies. Preprocessing steps included the removal of redundant and irrelevant data entries, ensuring consistency and relevance in analytical inputs. Data normalization techniques aligned numerical features within standardized ranges, enhancing the compatibility of inputs with analytical models. Synthetic data augmentation expanded the diversity of event sequences, addressing the limitations of imbalanced datasets and improving the generalizability of detection outcomes. Feature selection algorithms identified the most informative attributes, reducing dimensionality while retaining critical analytical value. Dataset partitioning into training, validation, and testing subsets ensured the comprehensive evaluation of the framework under various operational scenarios.
The simulation environment was configured to replicate real-world ransomware execution scenarios, encompassing diverse system configurations and usage patterns. Virtualized environments were deployed to safely execute ransomware samples, capturing detailed behavioral logs without risking operational systems. Network simulation tools emulated enterprise environments, enabling the evaluation of ransomware propagation dynamics and detection capabilities. Automated orchestration frameworks ensured the consistent and reproducible execution of experiments, minimizing variability in analytical outcomes. Resource allocation strategies optimized the computational performance of the simulation environment, enabling the analysis of high-volume data without compromising responsiveness. Sandboxing techniques isolated experimental processes, preventing potential cross-contamination with external systems.
Evaluation metrics were defined to comprehensively assess the detection capabilities of the proposed framework, addressing accuracy, robustness, and efficiency. Precision and recall metrics quantified the balance between true positive detections and false positive rates, highlighting the framework’s reliability in distinguishing ransomware activities. The F1-score synthesized precision and recall into a single measure, providing a balanced evaluation of detection performance. Execution time metrics evaluated the responsiveness of the framework under real-time operational constraints, ensuring its suitability for high-stakes environments. Robustness metrics assessed the framework’s resilience against adversarial evasion techniques, validating its ability to withstand sophisticated attack strategies. Scalability metrics measured performance degradation under increasing data volumes, ensuring the framework’s applicability to enterprise-scale deployments. Through the systematic evaluation of these metrics, the experimental design validated the framework’s potential to transform ransomware detection capabilities.
The results of the proposed framework are presented to demonstrate its effectiveness in detecting ransomware activities and to benchmark its performance against existing methods. Quantitative analyses evaluate detection accuracy, precision, and recall, while comparative studies highlight the advantages of the framework over traditional approaches. Each aspect of the evaluation is supported with diverse and realistic experimental data, visualized through detailed tables and figures.
The detection performance of the framework was assessed through a series of experiments, analyzing precision, recall, and overall accuracy across several ransomware families, including LockBit, BlackMatter, and Hive. Precision measured the proportion of correctly identified ransomware activities among all positive detections, while recall quantified the system’s ability to identify actual ransomware instances. Accuracy was calculated to reflect the framework’s overall effectiveness in distinguishing between malicious and benign activities. The results in Table II demonstrate that the framework consistently achieved high precision and recall across diverse ransomware families, highlighting its ability to minimize false positives and false negatives effectively.
A comparative analysis was conducted to evaluate the proposed framework against two existing methods: a static signature-based detection system and a heuristic behavioral analysis tool. The evaluation focused on detection rates and processing latency, with performance variations observed across different ransomware families. Figure 3 illustrates that the proposed framework consistently outperformed the comparative methods, achieving significantly higher detection rates, particularly for ransomware families exhibiting polymorphic characteristics.
Behavioral patterns of ransomware activity were analyzed through graph-based representations, highlighting temporal anomalies indicative of malicious operations. Figure 4 visualizes the distribution of temporal anomalies detected during ransomware execution using a piecewise constant plot, emphasizing the granularity of detection achieved through Temporal-Correlation Graphs. The anomalies depicted in Figure 4 highlight distinctive operational peaks during ransomware execution, aligning with known behavioral markers such as encryption onset and network communication surges.
The framework’s computational efficiency was evaluated through resource utilization metrics, focusing on CPU, memory, and disk I/O usage during real-time detection operations. The results provide insights into the framework’s suitability for deployment in resource-constrained environments. The results in Table III demonstrate that the framework maintained reasonable resource consumption across diverse ransomware families, ensuring compatibility with standard enterprise hardware configurations.
The framework’s responsiveness was analyzed through latency measurements, capturing the time required to detect ransomware activities from the onset of execution. Detection latency was evaluated under varying network and system loads. Figure 5 highlights the consistent detection timeliness achieved by the framework, even under increasing system loads, with latency values remaining within acceptable operational limits.
The relationship between ransomware encryption speed and detection success rates was analyzed, focusing on how rapidly executing ransomware influences the effectiveness of the framework. The evaluation included ransomware variants with varying encryption speeds. The data in Table IV indicate that higher encryption speeds marginally impact detection success, although the framework maintained strong performance across varying speeds.
The framework’s ability to detect anomalies was assessed using temporal windows of different durations, evaluating its sensitivity to ransomware activities over time. Anomaly detection accuracy was measured for varying window sizes. Figure 6 demonstrates that longer temporal windows resulted in higher anomaly detection accuracy, with the framework achieving optimal performance beyond a 40-second duration.
The results obtained from the experiments highlight the strengths and limitations of the proposed framework, offering valuable insights into its effectiveness and areas requiring further exploration. The interpretation of the outcomes, alongside the identification of challenges and opportunities for improvement, sheds light on the broader implications of the methodology within ransomware detection systems.
The consistently high detection rates achieved across multiple ransomware families indicate the framework’s robust ability to identify malicious activities, even in the presence of advanced evasion techniques. The use of Temporal-Correlation Graphs provided a significant advantage, allowing the capture of subtle behavioral patterns that were often missed through traditional approaches. Analyzing temporal anomalies and relational dependencies enabled the framework to accurately distinguish ransomware execution sequences from benign operations. The ability to maintain precision and recall across varied datasets reflects the generalizability of the methodology, while the adaptability of the graph-based representation contributed to its resilience against polymorphic and previously unseen ransomware variants. The comparative analysis demonstrated that the framework not only surpassed signature-based methods but also outperformed heuristic approaches, emphasizing the importance of incorporating dynamic and relational features into detection systems.
Harvested Online Documentation & Reference Sources • https://learn.microsoft.com/en-us/defender-endpoint/behavioral-blocking-containment • https://learn.microsoft.com/en-us/defender-endpoint/client-behavioral-blocking • https://docs.npav.net/docs/edr-on-premises/edr-on-premises/ransomware-protection/ • https://docs.trendmicro.com/en-us/documentation/article/trend-micro-apex-one-patch-4-online-help-configuring-malware- • https://builder.aws.com/content/3Id8K2rbSDaheWzIUId6CamXeIm/building-a-cloud-based-ransomware-detection-and-endp oint-monitoring-system-on-aws • https://github.com/Anushacodes03/ransomware-edr-system • https://www.fortinet.com/resources/articles/automated-ransomware-response • https://docs.trendmicro.com/en-us/documentation/article/trend-micro-apex-one-service-pack-1-online-help-configuring-malw are- • https://help.deepsecurity.trendmicro.com/20_0/on-premise/anti-malware-behavior-monitoring.html • https://success.trendmicro.com/en-US/solution/KA-0005683
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Real Time Ransomware Behavior Blocking Agent On Endpoint.
[*] Metasploit Scan Running on Target Subnet for Real Time Ransomware Behavior Blocking Agent On Endpoint... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |