Complete Technical Paper Content — Red Team Automated Emulation
Overview & System Context
Red Team Automated Emulation: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9529 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background An automated teller machine (ATM) is an electronic telecommunications device that enables customers of financial institutions to perform financial transactions, such as cash withdrawals, deposits, funds transfers, balance or account information inquiries, at any time and without the need for direct interaction with bank staff. ATMs are known by a variety of other names, including automatic teller machines (ATMs) in the United States (sometimes redundantly as "ATM machine"). In Canada, the term automated banking machine (ABM) is also used, although ATM is also very commonly used in Canada, with many Canadian organizations using ATM rather than ABM. In British English, the terms cashpoint, cash machine and hole in the wall are also used. ATMs that are not operated by a financial institution are known as "white-label" ATMs. Using an ATM, customers can access their bank deposit or credit accounts in order to make a variety of financial transactions, most notably cash withdrawals and balance checking, as well as transferring credit to and from mobile phones. ATMs can also be used to withdraw cash in a foreign country. If the currency being withdrawn from the ATM is different from that in which the bank account is denominated, the money will be converted at the financial institution's exchange rate. Customers are typically identified by inserting a plastic ATM card (or some other acceptable payment card) into the ATM, with authentication being by the customer entering a personal identification number (PIN), which must match the PIN stored in the chip on the card (if the card is so equipped), or in the issuing financial institution's database. According to the ATM Industry Association (ATMIA), as of 2015, there were close to 3.5 million ATMs installed worldwide. However, the use of ATMs is gradually declining with the increase in cashless payment systems.
A cash machine was installed at Barclays Bank, Enfield, North London in the United Kingdom, on 27 June 1967. This is generally considered the world's first ATM. This machine was inaugurated by English actor Reg Varney as part of the launch publicity. This invention is credited to the engineering team led by John Shepherd-Barron of printing firm De La Rue, who was awarded an OBE in the 2005 New Year Honours. Transactions were initiated by inserting paper cheques issued by a teller or cashier, marked with carbon-14 for machine readability and security, which in a later model were matched with a four-digit personal identification number (PIN). Shepherd-Barron stated: It struck me there must be a way I could get my own money, anywhere in the world or the UK. I hit upon the idea of a chocolate bar dispenser, but replacing chocolate with cash.
The Barclays–De La Rue machine (called De La Rue Automatic Cash System or DACS) beat the Swedish saving banks' and a company called Metior's machine (a device called Bankomat) by a mere nine days and British Westminster Bank's Smith Industries Chubb system (called Chubb MD2) by a month. The online version of the Swedish machine is listed to have been operational on 6 May 1968, while claiming to be the first online ATM in the world, ahead of similar claims by IBM and Lloyds Bank in 1971, and Oki in 1970. The collaboration of a small start-up called Speytec and Midland Bank developed a fourth machine which was marketed after 1969 in Europe and the US by the Burroughs Corporation. The patent for this device (GB1329964) was filed in September 1969 (and granted in 1973) by John David Edwards, Leonard Perkins, John Henry Donald, Peter Lee Chappell, Sean Benjamin Newcombe, and Malcom David Roe. Both the DACS and MD2 accepted only a single-use token or voucher which was retained by the machine, while the Speytec worked with a card with a magnetic stripe at the back. They used principles including Carbon-14 and low-coercivity magnetism in order to make fraud more difficult. The idea of a PIN stored on the card was developed by a group of engineers working at Smiths Group on the Chubb MD2 in 1965 and which has been credited to James Goodfellow (patent GB1197183 filed on 2 May 1966 with Anthony Davies). The essence of this system was that it enabled the verification of the customer with the debited account without human intervention. This patent is also the earliest instance of a complete "currency dispenser system" in the patent record. This patent was filed on 5 March 1968 in the US (US 3543904) and granted on 1 December 1970. It had a profound influence on the industry as a whole. Not only did future entrants into the cash dispenser market such as NCR Corporation and IBM license Goodfellow's PIN system, but a number of later patents reference this patent as "Prior Art Device".
Asea Metior's Bancomat was the first ATM installed in Spain on 9 January 1969, in central Madrid by Banesto. This device dispensed 1,000 peseta bills (1 to 5 max). Each user had to introduce a security personal key using a combination of the ten numeric buttons. In March of the same year an ad with the instructions to use the Bancomat was published in the same newspaper. In West Germany, the first ATM was installed in the 50,000-people university city of Tübingen on 27 May 1968, by Kreissparkasse Tübingen. It was built by Aalen-based safe builder Ostertag AG in cooperation with AEG-Telefunken. Each of the 1,000 selected users were given a double-bit key to open the safe with "Geldausgabe" written on it, a plastic identification card, and ten punched cards. One punch card functioned as a withdrawal slip for a 100 DM bill, the maximum limit for daily use was 400 DM.
Figure 1: Redc - IIIIIIIIIIIIIII | Red Team Infrastructure Multi-Cloud Automated ... After looking firsthand at the experiences in Europe, in 1968, the ATM was pioneered in the US by Donald Wetzel, who was a department head at a company called Docutel. Docutel was a subsidiary of Recognition Equipment Inc of Dallas, Texas, which was producing optical scanning equipment and had instructed Docutel to explore automated baggage handling and automated gasoline pumps. On 2 September 1969, Chemical Bank installed a prototype ATM in the US at its branch in Rockville Centre, New York. The first ATMs were designed to dispense a fixed amount of cash when a user inserted a specially coded card. A Chemical Bank advertisement boasted "On Sept. 2 our bank will open at 9:00 and never close again." Chemical's ATM, initially known as a Docuteller was designed by Donald Wetzel and his company Docutel. Chemical executives were initially hesitant about the electronic banking transition given the high cost of the early machines. Additionally, executives were concerned that customers would resist having machines handling their money. In 1995, the Smithsonian National Museum of American History recognized Docutel and Wetzel as the inventors of the networked ATM. To show confidence in Docutel, Chemical installed the first four production machines in a marketing test that proved they worked reliably, customers would use them and even pay a fee for usage. Based on this, banks around the country began to experiment with ATM installations. By 1974, Docutel had acquired 70 percent of the US market; but as a result of the early 1970s worldwide recession and its reliance on a single product line, Docutel lost its independence and was forced to merge with the US subsidiary of Olivetti. In 1973, Wetzel was granted U.S. Patent # 3,761,682 Archived 5 September 2017 at the Wayback Machine; the application had been filed in October 1971. However, the US patent record cites at least three previous applications from Docutel, all relevant to the development of the ATM and where Wetzel does not figure, namely US Patent # 3,662,343 Archived 5 September 2017 at the Wayback Machine, U.S. Patent # 3651976 Archived 5 September 2017 at the Wayback Machine and U.S. Patent # 3,68,569 Archived 5 September 2017 at the Wayback Machine. These patents are all credited to Kenneth S. Goldstein, MR Karecki, TR Barnes, GR Chastian and John D. White.
ATMs can be placed at any location but are most often placed near or inside banks, shopping centers, airports, railway stations, metro stations, grocery stores, gas stations, restaurants, and other locations. ATMs are also found on cruise ships and on some US Navy ships, where sailors can draw out their pay. ATMs may be on- and off-premises. On-premises ATMs are typically more advanced, multi-function machines that complement a bank branch's capabilities, and are thus more expensive. Off-premises machines are deployed by financial institutions where there is a simple need for cash, so they are generally cheaper single-function devices. Independent ATM deployers unaffiliated with banks install and maintain white-label ATMs. In the US, Canada and some Gulf countries, banks may have drive-thru lanes providing access to ATMs using an automobile. In recent times, countries like India and some countries in Africa are installing solar-powered ATMs in rural areas.
The world's highest ATM is located at the Khunjerab Pass in Pakistan. Installed at an elevation of 4,693 metres (15,397 ft) by the National Bank of Pakistan, it is designed to work in temperatures as low as -40-degree Celsius. Most ATMs are connected to interbank networks, enabling people to withdraw and deposit money from machines not belonging to the bank where they have their accounts or in the countries where their accounts are held (enabling cash withdrawals in local currency). Some examples of interbank networks include NYCE, PULSE, PLUS, Cirrus, AFFN, Interac, Interswitch, STAR, LINK, MegaLink, and BancNet. ATMs rely on the authorization of a financial transaction by the card issuer or other authorizing institution on a communications network. This is often performed through an ISO 8583 messaging system. Many banks charge ATM usage fees. In some cases, these fees are charged solely to users who are not customers of the bank that operates the ATM; in other cases, they apply to all users. To allow a more diverse range of devices to attach to their networks, some interbank networks have passed rules expanding the definition of an ATM to be a terminal that either has the vault within its footprint or utilizes the vault or cash drawer within the merchant establishment, which allows for the use of a scrip cash dispenser. In addition to methods employed for transaction security and secrecy, all communications traffic between the ATM and the Transaction Processor may also be encrypted using methods such as SSL.
There are no hard international or government-compiled numbers totaling the complete number of ATMs in use worldwide. Estimates as of 2015 developed by ATMIA placed the number of ATMs in use at 3 million units, or approximately 1 ATM per 3,000 people in the world. To simplify the analysis of ATM usage around the world, financial institutions generally divide the world into seven regions, based on the penetration rates, usage statistics, and features deployed. Four regions (USA, Canada, Europe, and Japan) have high numbers of ATMs per million people. Despite the large number of ATMs, there is additional demand for machines in the Asia/Pacific area as well as in Latin America. Macau may have the highest density of ATMs at 254 ATMs per 100,000 adults. With the uptake of cashless payment solutions in the late 2010s, ATM numbers and usage started to decline. This happened first in developed countries at a time when ATM numbers were still increasing in Asia and Africa. As of 2021, there had been a global decline in the number of ATMs in use, with the average dropping to 39 per 100,000 adults from a peak of 41 per 100,000 adults in 2020.
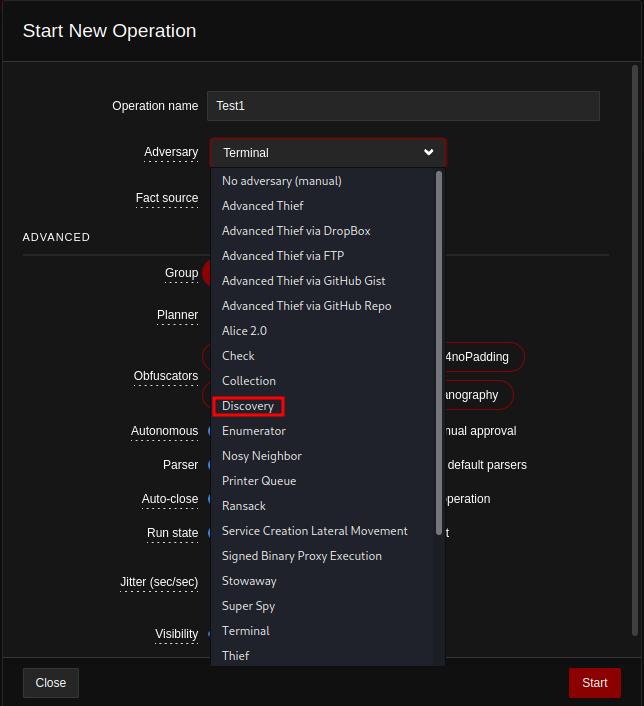
Figure 2: Caldera: Red Team Emulation (Part 1) CPU (to control the user interface and transaction devices) Magnetic or chip card reader (to identify the customer) a PIN pad for accepting and encrypting personal identification number EPP4 (similar in layout to a touch tone or calculator keypad), manufactured as part of a secure enclosure Secure cryptoprocessor, generally within a secure enclosure Display (used by the customer for performing the transaction) Function key buttons (usually close to the display) or a touchscreen (used to select the various aspects of the transaction) Record printer (to provide the customer with a record of the transaction) Vault (to store the parts of the machinery requiring restricted access) Housing (for aesthetics and to attach signage to) Sensors and indicators Due to heavier computing demands and the falling price of personal computer–like architectures, ATMs have moved away from custom hardware architectures using microcontrollers or application-specific integrated circuits and have adopted the hardware architecture of a personal computer, such as USB connections for peripherals, Ethernet and IP communications, and use personal computer operating systems. Business owners often lease ATMs from service providers.
However, based on the economies of scale, the price of equipment has dropped to the point where many business owners are simply paying for ATMs using a credit card. New ADA voice and text-to-speech guidelines imposed in 2010, but required by March 2012 have forced many ATM owners to either upgrade non-compliant machines or dispose them if they are not upgradable, and purchase new compliant equipment. This has created an avenue for hackers and thieves to obtain ATM hardware at junkyards from improperly disposed decommissioned machines.
The vault of an ATM is within the footprint of the device itself and is where items of value are kept. Scrip cash dispensers, which print a receipt or scrip instead of cash, do not incorporate a vault. Mechanisms found inside the vault may include: Dispensing mechanism (to provide cash or other items of value) Deposit mechanism including a cheque processing module and bulk note acceptor (to allow the customer to make deposits) Security sensors (magnetic, thermal, seismic, gas) Locks (to control access to the contents of the vault) Journaling systems; many are electronic (a sealed flash memory device based on in-house standards) or a solid-state device (an actual printer) which accrues all records of activity including access timestamps, number of notes dispensed, etc. This is considered sensitive data and is secured in a similar fashion to the cash as it is a similar liability. ATM vaults are supplied by manufacturers in several grades. Factors influencing vault grade selection include cost, weight, regulatory requirements, ATM type, operator risk avoidance practices and internal volume requirements.
Industry standard vault configurations include Underwriters Laboratories UL-291 "Business Hours" and Level 1 Safes, RAL TL-30 derivatives, and CEN EN 1143-1 - CEN III and CEN IV. ATM manufacturers recommend that a vault be attached to the floor to prevent theft, though there is a record of a theft conducted by tunneling into an ATM floor. With the migration to commodity Personal Computer hardware, standard commercial "off-the-shelf" operating systems and programming environments can be used inside of ATMs. Typical platforms previously used in ATM development include RMX or OS/2. Today, the vast majority of ATMs worldwide use Microsoft Windows. In early 2014, 95% of ATMs were running Windows XP. A small number of deployments may still be running older versions of the Windows OS, such as Windows NT, Windows CE, or Windows 2000, even though Microsoft only supports Windows 10 and Windows 11. There is a computer industry security view that general public desktop operating systems have greater risks as operating systems for cash dispensing machines than other types of operating systems like (secure) real-time operating systems (RTOS). RISKS Digest has many articles about ATM operating system vulnerabilities. Linux is also finding some reception in the ATM marketplace.
An example of this is Banrisul, the largest bank in the south of Brazil, which has replaced the MS-DOS operating system in its ATMs with Linux. Banco do Brasil is also migrating ATMs to Linux. Indian-based Vortex Engineering is manufacturing ATMs that operate only with Linux. Common application layer transaction protocols, such as Diebold 91x (911 or 912) and NCR NDC or NDC+ provide emulation of older generations of hardware on newer platforms with incremental extensions made over time to address new capabilities, although companies like NCR continuously improve these protocols issuing newer versions (e.g. NCR's AANDC v3.x.y, where x.y are subversions). Most major ATM manufacturers provide software packages that implement these protocols. Newer protocols such as IFX have yet to find wide acceptance by transaction processors. With the move to a more standardized software base, financial institutions have been increasingly interested in the ability to pick and choose the application programs that drive their equipment. WOSA/XFS, now known as CEN XFS (or simply XFS), provides a common API for accessing and manipulating the various devices of an ATM. J/XFS is a Java implementation of the CEN XFS API. While the perceived benefit of XFS is similar to Java's "write once, run anywhere" mantra, often different ATM hardware vendors have different interpretations of the XFS standard. The result of these differences in interpretation means that ATM applications typically use a middleware to even out the differences among various platforms. With the onset of Windows operating systems and XFS on ATMs, the software applications have the ability to become more intelligent. This has created a new breed of ATM applications commonly referred to as programmable applications. These types of applications allow for an entirely new host of applications in which the ATM terminal can do more than only communicate with the ATM switch. It is now empowered to connect to other content servers and video banking systems. Notable ATM software that operates on XFS platforms include Triton PRISM, Diebold Agilis EmPower, NCR APTRA Edge, Absolute Systems AbsoluteINTERACT, KAL Kalignite Software Platform, Phoenix Interactive VISTAatm, Wincor Nixdorf ProTopas, Euronet EFTS and Intertech inter-ATM.
With the move of ATMs to industry-standard computing environments, concern has risen about the integrity of the ATM's software stack. Figure 3: VIPER - AI Red Team Platform for Automated Adversary Emulation | Creati.ai ATM security has several dimensions. ATMs also provide a practical demonstration of a number of security systems and concepts operating together and how various security concerns are addressed.
Early ATM security focused on making the terminals invulnerable to physical attack; they were effectively safes with dispenser mechanisms. A number of attacks resulted, with thieves attempting to steal entire machines by ram-raiding. Since the late 1990s, criminal groups operating in Japan improved ram-raiding by stealing and using a truck loaded with heavy construction machinery to effectively demolish or uproot an entire ATM and any housing to steal its cash. Another attack method, plofkraak (a Dutch term), is to seal all openings of the ATM with silicone and fill the vault with a combustible gas or to place an explosive inside, attached, or near the machine. This gas or explosive is ignited and the vault is opened or distorted by the force of the resulting explosion and the criminals can break in. ATM bombings began in the Netherlands, but as the nation reduced the number of machines in the country from 20000 to 5000 and discouraged cash use, the mostly Moroccan-Dutch gangs expert in the attacks moved elsewhere. Such theft has also occurred in Belgium, France, Denmark, Germany, Australia, and the United Kingdom. When anti-gas explosion prevention devices and reinforced ATMs were installed, criminals began using leaf blowers to remove smoke, and more powerful solid explosives. Despite German banks spending more than €300 million on additional security, the Federal Criminal Police Office estimated that as of 2024 60% of attacks on ATMs in the country succeeded. Several attacks in the UK (at least one of which was successful) have involved digging a concealed tunnel under the ATM and cutting through the reinforced base to remove the money. Modern ATM physical security, per other modern money-handling security, concentrates on denying the use of the money inside the machine to a thief by using different types of intelligent banknote neutralization systems (IBNS). A common method is to simply rob the staff filling the machine with money. To avoid this, the schedule for filling them is kept secret, varying and random. The money is often kept in cassettes, which will dye the money if incorrectly opened.
There have also been a number of incidents of fraud by man-in-the-middle attacks, where criminals have attached fake keypads or card readers to existing machines. These have then been used to record customers' PINs and bank card information in order to gain unauthorized access to their accounts. Various ATM manufacturers have put in place countermeasures to protect the equipment they manufacture from these threats. Alternative methods to verify cardholder identities have been tested and deployed in some countries, such as finger and palm vein patterns, iris, and facial recognition technologies. Cheaper mass-produced equipment has been developed and is being installed in machines globally that detect the presence of foreign objects on the front of ATMs. Current tests have shown 99% detection success for all types of skimming devices.
Openings on the customer side of ATMs are often covered by mechanical shutters to prevent tampering with the mechanisms when they are not in use. Alarm sensors are placed inside ATMs and their servicing areas to alert their operators when doors have been opened by unauthorized personnel. To protect against hackers, ATMs have a built-in firewall. Once the firewall has detected malicious attempts to break into the machine remotely, the firewall locks down the machine. Rules are usually set by the government or ATM operating body that dictate what happens when integrity systems fail. Depending on the jurisdiction, a bank may or may not be liable when an attempt is made to dispense a customer's money from an ATM and the money either gets outside of the ATM's vault, or is exposed in a non-secure fashion, or they are unable to determine the state of the money after a failed transaction. Customers often commented that it is difficult to recover money lost in this way, but this is often complicated by the policies regarding suspicious activities typical of the criminal element.
At least as far back as 30 July 1986, consultants of the industry have advised for the adoption of an emergency PIN system for ATMs, where the user can send a silent alarm in response to a threat. Legislative efforts to require an emergency PIN system have appeared in Illinois, Kansas and Georgia, but none has succeeded yet. In January 2009, Senate Bill 1355 was proposed in the Illinois Senate that revisits the issue of the reverse emergency PIN system. The bill is again supported by the police and opposed by the banking lobby. In 1998, three towns outside Cleveland, Ohio, in response to an ATM crime wave, adopted legislation requiring that an emergency telephone number switch be installed at all outdoor ATMs within their jurisdiction. In the wake of a homicide in Sharon Hill, Pennsylvania, the city council passed an ATM security bill as well. In China and elsewhere, many efforts to promote security have been made. On-premises ATMs are often located inside the bank's lobby, which may be accessible 24 hours a day. These lobbies have extensive security camera coverage, a courtesy telephone for consulting with the bank staff, and a security guard on the premises. Bank lobbies that are not guarded 24 hours a day may also have secure doors that can only be opened from outside by swiping the bank card against a wall-mounted scanner, allowing the bank to identify which card enters the building. Most ATMs will also display on-screen safety warnings and may also be fitted with convex mirrors above the display allowing the user to see what is happening behind them. As of 2013, the only claim available about the extent of ATM-connected homicides is that they range from 500 to 1,000 per year in the US, covering only cases where the victim had an ATM card and the card was used by the killer after the known time of death.
ATMs were originally developed as cash dispensers, and have evolved to provide many other bank-related functions: Paying routine bills, fees, and taxes (utilities, phone bills, social security, legal fees, income taxes, etc.) Printing or ordering bank statements Updating passbooks Cash advances Cheque Processing Module Paying (in full or partially) the credit balance on a card linked to a specific current account. Transferring money between linked accounts (such as transferring between accounts) Deposit currency recognition, acceptance, and recycling In some countries, especially those which benefit from a fully integrated cross-bank network (e.g.: Multibanco in Portugal), ATMs include many functions that are not directly related to the management of one's own bank account, such as: Loading monetary value into stored-value cards Adding pre-paid mobile phone credit Purchasing Concert tickets Gold Lottery tickets Movie tickets Postage stamps. Train tickets Shopping mall gift certificates. Donating to charities Increasingly, banks are seeking to use the ATM as a sales device to deliver pre approved loans and targeted advertising using products such as ITM (the Intelligent Teller Machine) from Aptra Relate from NCR. ATMs can also act as an advertising channel for other companies.* However, several different ATM technologies have not yet reached worldwide acceptance, such as: Videoconferencing with human tellers, known as video tellers Biometrics, where authorization of transactions is based on the scanning of a customer's fingerprint, iris, face, etc. Cheque/cash Acceptance, where the machine accepts and recognizes cheques and/or currency without using envelopes Expected to grow in importance in the US through Check 21 legislation. Bar code scanning On-demand printing of "items of value" (such as movie tickets, traveler's cheques, etc.) Dispensing additional media (such as phone cards) Co-ordination of ATMs with mobile phones Integration with non-banking equipment Games and promotional features CRM through the ATM Videoconferencing teller machines are currently referred to as Interactive Teller Machines. Benton Smith writes in the Idaho Business Review, "The software that allows interactive teller machines to function was created by a Salt Lake City-based company called uGenius, a producer of video banking software. NCR, a leading manufacturer of ATMs, acquired uGenius in 2013 and married its own ATM hardware with uGenius' video software." Before an ATM is placed in a public place, it typically has undergone extensive testing with both test money and the backend computer systems that allow it to perform transactions. Banking customers also have come to expect high reliability in their ATMs, which provides incentives to ATM providers to minimize machine and network failures. Financial consequences of incorrect machine operation also provide high degrees of incentive to minimize malfunctions. ATMs and the supporting electronic financial networks are generally very reliable, with industry benchmarks typically producing 98.25% customer availability for ATMs and up to 99.999% availability for host systems that manage the networks of ATMs. If ATM networks do go out of service, customers could be left without the ability to make transactions until the beginning of their bank's next time of opening hours.
This said, not all errors are to the detriment of customers; there have been cases of machines giving out money without debiting the account, or giving out higher-value notes as a result of incorrect denomination of banknote being loaded in the money cassettes. The result of receiving too much money may be influenced by the cardholder agreement in place between the customer and the bank. Errors that can occur may be mechanical (such as card transport mechanisms; keypads; hard disk failures; envelope deposit mechanisms); software (such as operating system; device driver; application); communications; or purely down to operator error. To aid in reliability, some ATMs print each transaction to a roll-paper journal that is stored inside the ATM, which allows its users and the related financial institutions to settle things based on the records in the journal in case there is a dispute. In some cases, transactions are posted to an electronic journal to remove the cost of supplying journal paper to the ATM and for more convenient searching of data. Improper money checking can cause the possibility of a customer receiving counterfeit banknotes from an ATM. While bank personnel are generally trained better at spotting and removing counterfeit cash, the resulting ATM money supplies used by banks provide no guarantee for proper banknotes, as the Federal Criminal Police Office of Germany has confirmed that there are regularly incidents of false banknotes having been dispensed through ATMs. Some ATMs may be stocked and wholly owned by outside companies, which can further complicate this problem. Bill validation technology can be used by ATM providers to help ensure the authenticity of the cash before it is stocked in the machine; those with cash recycling capabilities include this capability. In India, whenever a transaction fails with an ATM due to network or technical issues and if the amount does not get dispensed in spite of the account being debited then the banks are supposed to return the debited amount to the customer within seven working days from the day of receipt of a complaint. Banks are also liable to pay the late fees in case of delay in repayment of funds post seven days.
As with any device containing objects of value, ATMs and the systems they depend on to function are the targets of fraud. Fraud against ATMs and people's attempts to use them takes several forms. The first known instance of a fake ATM was installed at a shopping mall in Manchester, Connecticut, in 1993. By modifying the inner workings of a Fujitsu model 7020 ATM, a criminal gang known as the Bucklands Boys stole information from cards inserted into the machine by customers.
WAVY-TV reported an incident in Virginia Beach in September 2006 where a hacker, who had probably obtained a factory-default administrator password for a filling station's white-label ATM, caused the unit to assume it was loaded with US$5 bills instead of $20s, enabling himself—and many subsequent customers—to walk away with four times the money withdrawn from their accounts. This type of scam was featured on the TV series The Real Hustle. ATM behavior can change during what is called "stand-in" time, where the bank's cash dispensing network is unable to access databases that contain account information (possibly for database maintenance). To give customers access to cash, customers may be allowed to withdraw cash up to a certain amount that may be less than their usual daily withdrawal limit, but may still exceed the amount of available money in their accounts, which could result in fraud if the customers intentionally withdraw more money than they had in their accounts.
World Map and Chart of Automated Teller Machines per 100,000 Adults by Lebanese-economy-forum, World Bank data Breach and attack simulation (BAS) refers to technologies that allow organizations to test their security defenses against simulated cyberattacks. BAS solutions provide automated assessments that help identify weaknesses or gaps in an organization's security posture.
Automated testing: simulations can be scheduled to run repeatedly without manual oversight. Threat modeling: simulations are designed based on real adversarial tactics, techniques and procedures. Attack surface coverage: can test internal and external-facing assets. Security control validation: integrates with other security tools to test efficacy. Reporting: identifies vulnerabilities and prioritizes remediation efforts.
The 2016 Cyber Grand Challenge (CGC) was a challenge created by The Defense Advanced Research Projects Agency (DARPA) in order to develop automatic defense systems that can discover, prove, and correct software flaws in real-time. The event placed machine versus machine (no human intervention) in what was called the "world's first automated network defense tournament." The final event was held on August 4, 2016 at the Paris Hotel & Conference Center in Las Vegas, Nevada within the 24th DEF CON hacker convention. It resembled in structure the long-standing capture the flag (CTF) security competitions, and the winning system indeed competed against humans in the "classic" DEF CON CTF held in the following days. The Cyber Grand Challenge featured, however, a more standardized scoring and vulnerability-proving system: all exploits and patched binaries were submitted and evaluated by the referee infrastructure. In addition to the CGC, DARPA has also conducted prize competitions in other areas of technology.
2. System Architecture & Core Working Principles Automatic vulnerability finding on previously-unknown binaries. Automatic patching of binaries without sacrificing performance. Automatic exploit generation within the framework's limitations. Implementing a security strategy: balancing resource-assignment among the available servers (a variation of the multi-armed bandit problem), responding to competitors (e.g., analyzing their patches, reacting to exploitation), evaluating own action's effect on the final score, ... Teams described their approach in various venues.
Additionally, the third-place finisher (Shellphish) released their entire system's source code. Due to the complexity of the task, players had to combine multiple techniques and do so in a fully-unattended and time-efficient fashion. For instance, the highest attack score was reached by discovering vulnerabilities via a combination of guided fuzzing and symbolic execution—i.e., an AFL-based fuzzer combined with the angr binary analysis framework, leveraging a QEMU-based emulation and execution-tracing system.
CodeJitsu, a team of researchers from the University of California at Berkeley, Cyberhaven, and Syracuse (funded track). CSDS, a team of researchers from the University of Idaho (open track). Deep Red, a team of specialized engineers from Raytheon (open track). disekt, a computer security team that participates in various Capture the Flag security competitions hosted by other teams, universities and organizations (open track). ForAllSecure, a security startup composed of researchers and security experts (funded track). Shellphish, a hacking team from the University of California, Santa Barbara (open track).
TECHx, a team of software analysis experts from GrammaTech, Inc. and the University of Virginia (funded track). Upon qualification, each one of the above seven teams received $750,000 in funding to prepare for the final event. "Mayhem" - developed by ForAllSecure, of Pittsburgh, Pa. - $2 million "Xandra" - developed by team TECHx consisting of GrammaTech Inc., Ithaca, N.Y., and UVa, Charlottesville, Va. - $1 million "Mechanical Phish" - developed by Shellphish, UC Santa Barbara, Ca. - $750,000 The other competing systems were: Rubeus - developed by Raytheon, Deep Red of Arlington, Va. Galactica - developed by CodeJitsu of Berkeley, Ca., Syracuse, N.Y., and Lausanne, Switzerland Jima - developed by CSDS of Moscow, Id. Crspy - system developed by disekt of Athens, Ga.
Security teams that rely solely on annual penetration tests are operating with a dangerous blind spot. Between engagements, infrastructure changes, new services deploy, and fresh vulnerabilities emerge — all untested. Building an internal adversary emulation framework mapped to MITRE ATT&CK transforms penetration testing from a periodic checkbox into a continuous validation capability.
This guide walks through designing, building, and operating a repeatable adversary emulation framework that your red team can run weekly without burning the building down. Traditional penetration testing answers one question: “Can someone break in?” Adversary emulation answers a far more useful one: “Can a specific threat actor achieve their objectives against our environment, and would we detect them doing it?” The distinction matters. Adversary emulation uses documented threat intelligence — real TTPs from real adversary groups — to simulate realistic attack chains. Instead of throwing every tool at the wall, you replicate what APT29, FIN7, or a ransomware operator would actually do against your industry vertical.
The benefits compound over time. Each emulation run produces structured data you can compare against previous runs, track detection coverage trends, and feed directly into your vulnerability management program. The execution engine is the core. We will build it around a modular Python framework with YAML-defined attack plans. Each attack plan maps to specific ATT&CK techniques and chains them into realistic sequences: The engine reads plans, enforces safety constraints, executes each phase, and records results: The safety layer deserves its own section because getting it wrong means turning your red team exercise into an actual incident. Every emulation framework must enforce: Scope locking. The engine must refuse to touch any host outside the defined network ranges. This is not a suggestion — it is a hard block in the execution path. Validate every target IP before any packet leaves.
Time boxing. Set maximum durations per plan and per phase. If an attack chain stalls and an operator walks away, the framework should terminate gracefully after the timeout. De-escalation triggers. Define conditions that automatically pause or abort execution. Achieving SYSTEM or root privileges unexpectedly, hitting too many unreachable hosts (indicating network issues), or detecting production workload disruption should all halt the run.
Kill switch. Implement an out-of-band kill mechanism — a file on a shared path, an API endpoint, or a message queue topic. If anything goes wrong, any team member should be able to stop all running emulations instantly: Running attacks without checking whether your defenses saw them is only half the exercise. Integrate with your SIEM to validate detection coverage: Every emulation run produces a structured JSON report that feeds into your vulnerability management pipeline: The gaps array is the most actionable output — these are techniques that succeeded without generating any detection. Feed these directly into your detection engineering backlog.
Running the framework once is a project. Running it weekly is a program. To operationalize: Schedule regular runs. Use cron or your CI/CD platform to execute baseline attack plans against staging environments weekly. Compare detection coverage week over week. Maintain a plan library. Map your threat model to specific adversary groups. Build and maintain plans for each. When threat intelligence identifies a new campaign targeting your sector, build a plan for it within 48 hours.
Track coverage metrics. The detection coverage percentage over time is your north star metric. Plot it monthly. Share it with leadership. It is the single most honest measure of your defensive posture. Feed findings into remediation. Every gap identified should create a ticket in your vulnerability management system with the ATT&CK technique, the specific procedure that succeeded, and a recommended detection rule.
Building adversary emulation as an internal capability requires significant upfront investment, but the return is a security team that knows — not hopes — that their defenses work against the threats that matter. A complete Red Team guide covering adversary emulation, operations, tradecraft, and safety. RedTeam-Agent is an AI-powered red team framework using a skill-first terminal workflow. AI reads project skills, discovers tools, executes commands in terminal, and summarizes high-signal findings.
3. Software Implementation, Frameworks & Protocols Core philosophy: no manual tool-by-tool operation. Let AI orchestrate the workflow end-to-end. AI will read the repository skill and .github/copilot-instructions.md , then execute terminal commands directly. RedTeam-Agent: AI-Powered Autonomous Red Team Framework via Model Context Protocol. AIIIIIIIIIIIIIIII gogo, fscan, httpx, nuclei, impacket, playwright I 15+ IIIIII LLM IIIIIIIIIII Caldera™ is an adversary emulation platform designed to easily run autonomous breach-and-attack simulation exercises. It can also be used to run manual red-team engagements or automated incident response. Caldera is built on the MITRE ATT&CK ™ framework and is an active research project at MITRE.
1. The core system . This is the framework code, including an asynchronous command-and-control (C2) server with a REST API and a web interface. 2. Plugins . These are separate repositories that hang off of the core framework, providing additional functionality. Examples include agents, GUI interfaces, collections of TTPs and more.
For getting familiar with the project, visit Getting started , which documents step-by-step guides for the most common use cases of Caldera, and Basic usage , which documents how to use some of the basic components in core Caldera. Visit Learning the terminology for in depth definitions of the terms used throughout the project. For information about Caldera plugins, visit Plugin Library and How to Build Plugins if you are interested in building your own.
The following section contains information intended to help developers understand the inner workings of the Caldera adversary emulation tool, Caldera plugins, or new tools that interface with the Caldera server. Strike48 University SOC Program Brings Agentic AI Into Cybersecurity Education - Learn More → Every simulated kill chain was detected. Every lateral movement attempt triggered an alert. The board sees improving KPIs.
None of it accounts for the 30% of your environment that produces no alerts at all, because your SIEM never ingested those log sources in the first place. The confidence is real. The coverage is not. Adversaries have adopted agentic tooling that scales campaigns and compresses dwell time. Manual pentests on quarterly cycles cannot keep pace. But the conversation about automation has fixated on testing methodology while ignoring the data foundation that determines whether test results mean anything.
Walk us through your current SIEM coverage and we'll show you where the blind spots live in stacks like yours. Automated red teaming uses software agents to continuously simulate adversarial tactics, techniques, and procedures against an organization's environment. Where annual or quarterly penetration tests provide depth at a single point in time, automated programs run ongoing simulations at a cadence that matches how fast environments change and attackers adapt.
Four categories occupy this space, and procurement conversations routinely conflate them. BAS tells you whether your existing detections fire. CART tells you what attack paths exist regardless of whether you have detections written for them. Organizations running BAS alone are validating the rules they already wrote, not discovering the gaps they have not. APRT addresses the next category over: attack patterns scripted BAS tools were never designed to simulate. Both OWASP's Top 10 for LLMs and MITRE ATLAS treat these as first-class threats.
2025 arXiv research found that automated red teaming achieves a 69.5% vulnerability discovery success rate versus 47.6% for manual testing alone, identifying 37% more unique vulnerabilities. Automated tools follow programmatic playbooks. They cannot replicate the context-dependent attack chains a skilled operator constructs by reading an environment's specific topology. A human tester notices that a service account has overly broad permissions and pivots the engagement around it.
Automation tests whether the known TTPs work. The cost of running manual-only programs is compounding, not stable. Only 26% of organizations conduct proactive security testing specific to AI systems, while 97% have already experienced GenAI-related security incidents . Multi-agent denial-of-service attacks succeeded in over 80% of tests in ACL 2025 research. Quarterly manual pentests cannot keep pace with adversaries who have no scheduling constraints, and the gap compounds with every quarter teams stay on that schedule.
That cadence is widening the gap. See what continuous detection validation with agents looks like. Two structural factors determine what CART can reliably find. Log coverage completeness is the first. The data architecture underneath it is the second. IDC research shows the average enterprise monitors only two-thirds of its environment. A CART program running against a SIEM that covers 60-70% of the environment produces confident findings about a fraction of the actual attack surface. The remaining 30-40% is invisible. No alerts, no CART findings, no remediation.
When a CART platform reports “no exploitable path found,” that finding is only as trustworthy as the log coverage underneath it. No CART vendor has an incentive to tell you this . The detection gap is invisible unless it is measured directly. Findings count, mean time to detect, and high-severity remediation rates do not reveal whether the underlying log environment is complete. A program can report steadily improving KPIs while an entire cloud environment, OT segment, or SaaS layer remains structurally invisible.
The diagnostic question that changes the meaning of every red team report: what percentage of our log sources are currently monitored, and how was that percentage determined? Most SIEM teams will struggle to answer with precision. That struggle is the problem. Strike48 covers why this baseline matters in its security log management breakdown. Legacy SIEMs require teams to make parsing decisions at ingestion time: which log sources to parse, normalize, and retain.
The cost penalty for indexing every source is prohibitive, so teams make budget-driven exclusions that create structural blind spots. A red teaming program layered over this infrastructure validates detection logic against a subset of the real attack surface. Federated search , also called search-in-place, decouples storage decisions from upfront parsing. Logs stay where they originate, in the cheapest storage available. Parsing applies only when a query runs against that data. Organizations achieve complete log coverage at a fraction of traditional SIEM cost because they no longer pay to parse and re-index every source at ingestion.
Immediate log access also means agents validate detection logic against new log sources without waiting for schema definition and pipeline cycles. A cloud workload spins up. Logs become queryable through Strike48 immediately. CART validation runs today, not after six weeks of engineering. Strike48 closes the loop from attack simulation to detection validation. Strike48 Pick , the open-source reconnaissance agent, runs inside target environments and covers port scanning, device enumeration, WiFi discovery, ARP analysis, and PCAP collection from a single binary. Reconnaissance data feeds directly into the AI layer, where micro-agents correlate findings against log data across every connected source. The reconnaissance finds the surface , search-in-place makes the data available, and agents correlate what red teaming found against what the detection infrastructure actually observed.
4. Practical Deployment, Analysis & Case Studies Automated red teaming is a data foundation problem first and a testing methodology problem second. The same constraint binds every CART program, every BAS playbook, and every manual pentest. The attack paths they find exist only in the portion of the environment that generates observable signals. Fix the visibility, and you fix what red teaming can reliably validate. Strike48's approach to building this foundation starts with the agentic security architecture that makes complete visibility the prerequisite for agent deployment.
The intelligence is already in your logs. Strike48 gives agents the visibility to find attack paths and the completeness to trust that what they do not find is genuinely absent, not hidden behind a coverage gap. If your CART program is reporting confidence you cannot verify against the full attack surface, it is testing what is convenient to monitor, not what adversaries are actually targeting.
Penetration testing is human-led, scoped, and point-in-time, conducted annually or quarterly for compliance evidence. Automated red teaming uses software to simulate attacks continuously, running kill-chain scenarios across the environment without requiring a human operator on each exercise. The key distinction is cadence: pentesting tests a moment in time, automated red teaming tests a state that changes daily.
CART is a category of automated red teaming defined by ongoing, autonomous adversarial simulation aligned to frameworks like MITRE ATT&CK. Unlike scripted BAS tools that replay predefined scenarios, CART platforms run continuously and simulate a broad range of TTPs without manual scheduling. CART catches the attack paths that open between quarterly manual exercises.
CART programs are bounded by the same log visibility constraint as everything else in the SOC. The average enterprise monitors roughly two-thirds of its environment, so a CART program running against a standard SIEM tests approximately 70% of the attack surface. Strike48's federated search architecture addresses this by making 100% log coverage economically viable, so CART validation runs against the full environment.
Three metrics matter when tracked together: mean time to detect simulated attacks (target under eight minutes), reduction in high-severity undetected findings over rolling 90-day periods, and detection coverage percentage . The third is the one most programs do not track and the one that determines whether the first two are meaningful. Learn how automated red teaming strengthens cybersecurity through continuous adversarial testing, attack simulation, exploit validation, and risk prioritization. Discover methodologies, tools, workflows, best practices, and implementation strategies for enterprise security teams.
Automated Red Teaming: The Complete Guide to Continuous Adversarial Security Validation Although traditional penetration testing remains valuable,annual or quarterly assessments no longer provide sufficient visibility into an organization’s constantly changing attack surface. Rather than relying solely on manual engagements, organizations can simulate realistic attacker behavior repeatedly, validate defensive controls, identify exploitable attack paths, and prioritize remediation based on actual business risk.
This comprehensive guide explores automated red teaming, its methodology, implementation, benefits, limitations, and its role within Continuous Threat Exposure Management (CTEM) strategies. For the Red Team Maturity Framework - see the detailed article linked here. Unlike vulnerability scanners that simply identify weaknesses, automated red teaming attempts to approach the external attack surface like an attacker, chaining vulnerabilities together, exploiting security gaps where appropriate, validating defensive controls, and determining whether an attacker could achieve specific objectives. The AI agents are continually adapting to introduce new ways of probing for vulnerabilities.
The objective is continuous validation, backed by real-world evidential proof of the vulnerability rather than one-time assessment. It's important to acknowledge that traditional engagements remain valuable because experienced operators demonstrate creativity that can go far beyond automation alone. Automated platforms complement—not replace—human-led exercises by providing continuous validation between major assessments.
The threats particularly from AI tools that are picking up zero day source code issues in the supply chain are massively escalating the risks. A penetration test completed six months ago cannot accurately represent today’s exposure. Automated red teaming continuously evaluates whether changes introduce exploitable weaknesses before adversaries discover them.
Attack path analysis identifies how multiple weaknesses combine into a successful compromise. Automated platforms simulate known threat actor behaviors using recognized frameworks such as: These simulations reproduce realistic attack chains while remaining controlled and measurable. VerifiedThreat uses the MITRE ATT&CK Framework to map each and every known threat per sector or domain - and test for the specific threats across the external risk surface.
Automated attacks evaluate whether defensive technologies successfully detect or block malicious activity. A mature automated red team follows a structured lifecycle as shown below in the table: Continuous Threat Exposure Management emphasizes ongoing identification, validation, prioritization, and remediation of cyber risk.
Instead of relying solely on CVSS scores, organizations understand which vulnerabilities genuinely place critical assets at risk. Automation is most effective when combined with skilled security professionals who can interpret results, refine attack scenarios, and address complex business risks. Automation continues to evolve rapidly through advances in artificial intelligence, machine learning, and attack path analytics.
In fact the adversarial nature of the Red Team v. Blue team simulation can be extremely useful in Machine Learning to determine the overall risk scores using a confusion matrix. See detailed article on AI and adversarial testing . As organizations embrace zero trust architectures, cloud-first strategies, and continuous software delivery, automated red teaming will become an essential capability for maintaining confidence in defensive controls and reducing exploitable exposure.
5. Performance Evaluation & Extended Technical Observations The primary goal of Blue Team incident response is to minimize the impact of a cybersecurity incident, swiftly containing and mitigating the threat to prevent further damage. In practice, it’s extremely hard to maintain a schedule of Red Team v Blue simulations, given all the other pressing issues competing for resources. Many organizations try to make the simulations an annual event. VerifiedThreat agentic AI model is learning on a daily basis, and is constantly updated for new threat types with the latest intelligence.
Purple teaming is a collaborative exercise in which offensive (Red Team) and defensive (Blue Team) professionals work together to test security controls, improve detection capabilities, and strengthen incident response. Most security teams discover detection gaps during a real incident—not before one. Industry data shows SOC teams face over 11,000 alerts per day, with 70% ignored due to alert fatigue, creating blind spots where real threats hide in the noise.
Purple teaming exists to catch that gap on your own schedule: emulate the technique an attacker would use, watch what your detections actually do with it, and fix what stays silent. This guide walks through how to run that offense-defense loop safely, technique by technique, with the MITRE ATT&CK IDs that keep the exercise measurable instead of guesswork.
Emulating a technique only proves something if you close the loop back to a working detection. Here’s the cycle a SOC actually runs, not just the attack simulation part. Start from current threat intel or a known ATT&CK technique relevant to your stack, not a generic checklist item. Reproduce the attacker’s exact behavior in a controlled environment, so the test reflects a real intrusion path.
Check what your EDR, SIEM, and log sources actually recorded while the technique ran, not what they’re supposed to record. Did an alert fire? How fast, and how much noise came with it? A missed or delayed detection is a finding, not a failure. Tune the rule, rerun the same technique, and log the result as evidence your coverage actually improved. Testing detections in a lab tells you very little. Real production environments have configuration drift, noisy logging, and integrations that a clean test environment doesn’t. If you want to know how to test EDR detections safely in production , the plan matters more than the payload, and that plan is the foundation of any purple teaming program.
Modern breach and attack simulation tools are built specifically to run this way, mimicking behaviors like process injection or credential dumping without touching real data or causing downtime. The goal isn’t to see if you can crash something. It’s to see if your EDR notices, and to log that result against the specific MITRE ATT&CK technique you ran so the finding means something to a detection engineer later. That single checkpoint—where a human approves anything with real risk before it fires—is the same principle behind human-in-the-loop governance in security operations, where automation speed never comes at the cost of human judgment.
Once the ground rules are set, adversary emulation starts. This is the offense half of the loop: running specific ATT&CK techniques and watching what your stack catches. Not every technique needs the same approach, and lumping them together is how gaps stay hidden. You don’t need to encrypt real files to know how to emulate ransomware behavior safely . Focus on the behaviors ransomware relies on, which is what ATT&CK catalogs as Data Encrypted for Impact: If your EDR flags the behavioral pattern instead of a known file signature, you’ll catch new variants too, not just the ones already sitting in a threat feed.
When teams ask how to emulate phishing initial access techniques , the mistake is usually testing the wrong thing, whether users click a link. That’s a training question, not a detection question. What actually matters is whether your email gateway, browser isolation, or endpoint tooling catches the payload delivery itself, such as: Privilege escalation tests work best when you hand the simulated attacker a starting foothold, like local admin rights, then watch what happens next. That’s the whole approach behind how to test privilege escalation detections : Living off the land techniques are the hardest to detect because they abuse legitimate system binaries and scripting interpreters—PowerShell, WMI, certutil, regsvr32—that ATT&CK tracks under Command and Scripting Interpreter (T1059) and System Binary Proxy Execution (T1218). These tools are present in every Windows environment and used daily by administrators, making behavioral detection the only viable approach. PowerShell alone shows up in the majority of these attacks, according to recent telemetry, and CISA has gone as far as saying its own red teams routinely use these techniques while network defenders rarely catch them.
Figuring out how to validate detections for living-off-the-land techniques means testing both sides at once: A rule that fires on every PowerShell script isn’t a working detection. It’s a false positive machine your team will eventually learn to ignore. For a broader look at how automated adversary emulation strings techniques like these into a realistic attack chain instead of testing them one at a time, Secure.com breaks down what an automated purple team loop looks like end to end .
Endpoint testing only covers part of the picture. Attackers move into cloud infrastructure and identity systems just as often, and those layers need their own validation, not a rubber stamp from your EDR results. A misconfigured storage bucket or an overly permissive IAM role can sit quietly for months before anyone notices, which is why how to validate cloud attack detections has become its own discipline. Cover common attacker moves: Run the tests across each cloud you use, since coverage that works in AWS doesn’t automatically carry over to Azure or GCP. That inconsistency is exactly why running three clouds usually means running three separate security postures unless something pulls them together .
A stolen password and a stolen identity aren’t the same problem, and your detections should treat them differently. That’s the core of how to validate identity attack detections : The goal is catching the difference between a valid password and a valid user, since attackers with working credentials rarely trip a traditional malware alert.
Working out how to test data exfiltration detections means following the path data would actually take out the door: If your DLP or network monitoring only catches exfiltration over known bad domains, you’re missing everything a patient attacker does through a legitimate cloud storage service instead. A single emulation run across a mid-market SOC stack, scored against the techniques that were actually fired.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/ATM • https://en.wikipedia.org/wiki/Breach%20and%20attack%20simulation • https://en.wikipedia.org/wiki/2016%20Cyber%20Grand%20Challenge • https://culpur.net/2026/03/30/automated-adversary-emulation-building-a-repeatable-penetration-testing-framework/ • https://github.com/rashidaalexander/RedTeam-Complete-Guide • https://github.com/ktol1/RedTeam-Agent • https://caldera.readthedocs.io/en/latest/ • https://www.strike48.com/post/automated-red-teaming • https://www.verifiedthreat.com/knowledge-centre-articles/automated-red-teaming-complete-guide-to-continuous-adversarial- security-testing • https://www.secure.com/blog/red-team/technique-emulation-detection-testing
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Red Team Automated Emulation.
[*] Metasploit Scan Running on Target Subnet for Red Team Automated Emulation... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |