Complete Technical Paper Content — Reversible Data Hiding In Encrypted Images Using Python
Overview & System Context
Reversible Data Hiding In Encrypted Images Using Python: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9524 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background NT File System (NTFS) is a proprietary journaling file system developed by Microsoft in the 1990s. It was developed to overcome scalability, security and other limitations with FAT. NTFS adds several features that FAT and HPFS lack, including: access control lists (ACLs); filesystem encryption; transparent compression; sparse files; file system journaling and volume shadow copy, a feature that allows backups of a system while in use. Starting with Windows NT 3.1, it is the default file system of the Windows NT family superseding the File Allocation Table (FAT) file system. NTFS read/write support is available on Linux and BSD using NTFS3 in Linux and NTFS-3G in both Linux and BSD. NTFS uses several files hidden from the user to store metadata about other files stored on the drive which can help improve speed and performance when reading data.
The NTFS.sys version number (e.g. v5.0 in Windows 2000) is based on the operating system version; it should not be confused with the NTFS version number (v3.1 since Windows XP). Although subsequent versions of Windows added new file system-related features, they did not change NTFS itself. For example, Windows Vista implemented NTFS symbolic links, Transactional NTFS, partition shrinking, and self-healing. NTFS symbolic links are a new feature in the file system; all the others are new operating system features that make use of NTFS features already in place.
In NTFS, each file or folder is assigned a security descriptor that defines its owner and contains two access control lists (ACLs). The first ACL, called discretionary access control list (DACL), defines exactly what type of interactions (e.g. reading, writing, executing or deleting) are allowed or forbidden by which user or groups of users. For example, files in the C:\Program Files folder may be read and executed by all users but modified only by a user holding administrative privileges. Windows Vista adds mandatory access control info to DACLs. DACLs are the primary focus of User Account Control in Windows Vista and later. The second ACL, called system access control list (SACL), defines which interactions with the file or folder are to be audited and whether they should be logged when the activity is successful, failed or both. For example, auditing can be enabled on sensitive files of a company, so that its managers get to know when someone tries to delete them or make a copy of them, and whether they succeed.
Encrypting File System (EFS) provides user-transparent encryption of any file or folder on an NTFS volume. EFS works in conjunction with the EFS service, Microsoft's CryptoAPI and the EFS File System Run-Time Library (FSRTL). EFS works by encrypting a file with a bulk symmetric key (also known as the File Encryption Key, or FEK), which is used because it takes a relatively small amount of time to encrypt and decrypt large amounts of data than if an asymmetric key cipher is used. The symmetric key that is used to encrypt the file is then encrypted with a public key that is associated with the user who encrypted the file, and this encrypted data is stored in an alternate data stream of the encrypted file. To decrypt the file, the file system uses the private key of the user to decrypt the symmetric key that is stored in the data stream. It then uses the symmetric key to decrypt the file. Because this is done at the file system level, it is transparent to the user. Also, in case of a user losing access to their key, support for additional decryption keys has been built into the EFS system, so that a recovery agent can still access the files if needed. NTFS-provided encryption and NTFS-provided compression are mutually exclusive, meaning they can not be used for the same files at the same time; however, NTFS can be used for one and a third-party tool for the other. The support of EFS is not available in Basic, Home, and MediaCenter versions of Windows, and must be activated after installation of Professional, Ultimate, and Server versions of Windows or by using enterprise deployment tools within Windows domains.
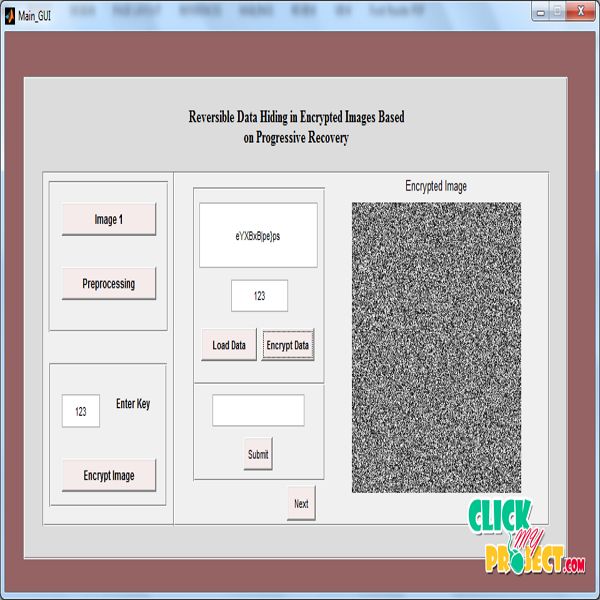
Figure 1: Reversible Data Hiding in Encrypted Images Based on Progressive ... The incompatibility of the $LogFile versions implemented by Windows 8, Windows 10, Windows 11 prevents Windows 7 (and earlier versions of Windows) from recognizing version 2.0 of the $LogFile. Backward compatibility is provided by downgrading the $LogFile to version 1.1 when an NTFS volume is cleanly dismounted. It is again upgraded to version 2.0 when mounting on a compatible version of Windows. However, when hibernating to disk in the logoff state (a.k.a. Hybrid Boot or Fast Boot, which is enabled by default), mounted file systems are not dismounted, and thus the $LogFiles of any active file systems are not downgraded to version 1.1. The inability to process version 2.0 of the $LogFile by versions of Windows older than 8.0 results in an unnecessary invocation of the CHKDSK disk repair utility. This is particularly a concern in a multi-boot scenario involving pre- and post-8.0 versions of Windows, or when frequently moving a storage device between older and newer versions. A Windows Registry setting exists to prevent the automatic upgrade of the $LogFile to the newer version. The problem can also be dealt with by disabling Hybrid Boot. The USN Journal (Update Sequence Number Journal) is a system management feature that records (in $Extend\$UsnJrnl) changes to files, streams and directories on the volume, as well as their various attributes and security settings. The journal is made available for applications to track changes to the volume.
This journal can be enabled or disabled on non-system volumes. Alternate data streams allow more than one data stream to be associated with a filename (a fork), using the format "filename:streamname" (e.g., "text.txt:extrastream"). These streams are not shown to or made editable by users through any typical GUI application built into Windows by default, disguising their existence from most users. Although intended for helpful metadata, their arcane nature makes them a potential hiding place for malware, spyware, unseen browser history, and other potentially unwanted information. Alternate streams are not listed in Windows Explorer, and their size is not included in the file's size. When the file is copied or moved to another file system without ADS support the user is warned that alternate data streams cannot be preserved. No such warning is typically provided if the file is attached to an e-mail, or uploaded to a website. Thus, using alternate streams for critical data may cause problems. Microsoft provides a downloadable tool called Streams to view streams on a selected volume. Starting with Windows PowerShell 3.0, it is possible to manage ADS natively with six cmdlets: Add-Content, Clear-Content, Get-Content, Get-Item, Remove-Item, Set-Content. A small ADS named Zone.Identifier is added by Internet Explorer and by most browsers to mark files downloaded from external sites as possibly unsafe to run; the local shell would then require user confirmation before opening them. When the user indicates that they no longer want this confirmation dialog, this ADS is deleted. This functionality is also known as "Mark of the Web". All Chromium (e.g. Google Chrome) and Firefox-based web browsers also write the Zone.Identifier stream to downloaded files. Malware has used alternate data streams to hide code. Since the late 2000s, some malware scanners and other special tools check for alternate data streams. Due to the risks associated with ADS, particularly involving privacy and the Zone.Identifier stream, there exists software specifically designed to strip streams from files (certain streams with perceived risk or all of them) in a user-friendly way. NTFS Streams were introduced in Windows NT 3.1, to enable Services for Macintosh (SFM) to store resource forks. Although current versions of Windows Server no longer include SFM, third-party Apple Filing Protocol (AFP) products (such as GroupLogic's ExtremeZ-IP) still use this feature of the file system.
Since Windows 10, Microsoft has introduced new file compression scheme based on the XPRESS algorithm with 4K/8K/16K block size and the LZX algorithm; both are variants of LZ77 updated with Huffman entropy coding and range coding, which LZNT1 lacked. These compression algorithms were taken from Windows Imaging Format (WIM file). The new compression scheme is used by CompactOS feature, which reduces disk usage by compressing Windows system files. CompactOS is not an extension of NTFS file compression and does not use the 'compressed' attribute; instead, it sets a reparse point on each compressed file with a WOF (Windows Overlay Filter) tag, but the actual data is stored in an alternate data stream named "WofCompressedData", which is decompressed on-the-fly by a WOF filesystem filter driver, and the main file is an empty sparse file. This design is meant purely for read-only access, so any writes to compressed files result in an automatic decompression. CompactOS compression is intended for OEMs who prepare OS images with the /compact flag of the DISM tool in Windows ADK, but it can also be manually turned on per file with the /exe flag of the compact command. CompactOS algorithm avoids file fragmentation by writing compressed data in contiguously allocated chunks, unlike core NTFS compression. CompactOS file compression is an improved version of WIMBoot feature introduced in Windows 8.1. WIMBoot reduces Windows disk usage by keeping system files in a compressed WIM image on a separate hidden disk partition.
Similarly to CompactOS, Windows system directories only contain sparse files marked by a reparse point with a WOF tag, and Windows Overlay Filter driver decompresses file contents on-the-fly from the WIM image. WIMBoot is less effective than CompactOS though, as new updated versions of system files need to be written to the system partition, consuming disk space.
Sparse files are files interspersed with empty segments for which no actual storage space is used. To the applications, the file looks like an ordinary file with empty regions seen as regions filled with zeros; the file system maintains an internal list of such regions for each sparse file. A sparse file does not necessarily include sparse zeros areas; the "sparse file" attribute just means that the file is allowed to have them. Database applications, for instance, may use sparse files. As with compressed files, the actual sizes of sparse files are not taken into account when determining quota limits.
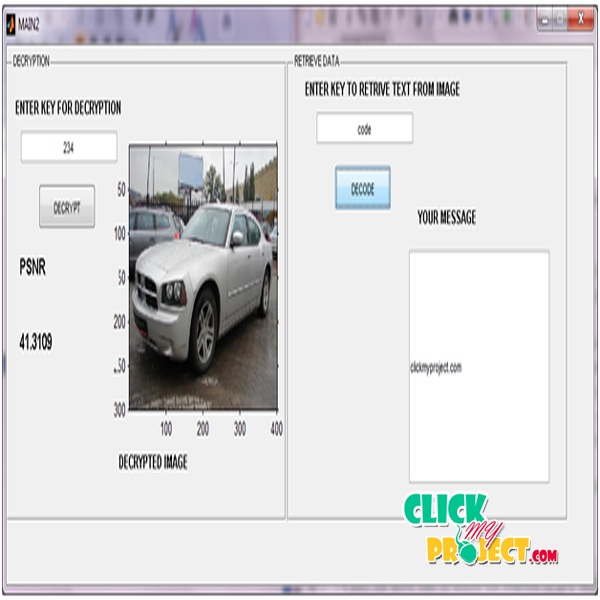
Figure 2: SEPARABLE REVERSIBLE DATA HIDING IN ENCRYPTED IMAGE - ClickMyproject Introduced in NTFS v3, NTFS reparse points are used by associating a reparse tag in the user space attribute of a file or directory. Microsoft includes several default tags including symbolic links, directory junction points and volume mount points. When the Object Manager parses a file system name lookup and encounters a reparse attribute, it will reparse the name lookup, passing the user controlled reparse data to every file system filter driver that is loaded into Windows. Each filter driver examines the reparse data to see whether it is associated with that reparse point, and if that filter driver determines a match, then it intercepts the file system request and performs its special functionality.
This boot partition format is roughly based upon the earlier FAT filesystem, but the fields are in different locations. Some of these fields, especially the "sectors per track", "number of heads" and "hidden sectors" fields may contain dummy values on drives where they either do not make sense or are not determinable. The OS first looks at the 8 bytes at 0x30 to find the cluster number of the $MFT, then multiplies that number by the number of sectors per cluster (1 byte found at 0x0D). This value is the sector offset (LBA) to the $MFT, which is described below.
These metafiles are treated specially by Windows, handled directly by the NTFS.SYS driver and are difficult to directly view: special purpose-built tools are needed. As of Windows 7, the NTFS driver completely prohibits user access, resulting in a BSoD whenever an attempt to execute a metadata file is made. One such tool is the nfi.exe ("NTFS File Sector Information Utility") that is freely distributed as part of the Microsoft "OEM Support Tools". For example, to obtain information on the "$MFT"-Master File Table Segment the following command is used: nfi.exe c:\$MFT Another way to bypass the restriction is to use 7-Zip's file manager and go to the low-level NTFS path \\.\X:\ (where X:\ resembles any drive/partition). Here, 3 new folders will appear: $EXTEND, [DELETED] (a pseudo-folder that 7-Zip uses to attach files deleted from the file system to view), and [SYSTEM] (another pseudo-folder that contains all the NTFS metadata files). This trick can be used from removable devices (USB flash drives, external hard drives, SD cards, etc.) inside Windows, but doing this on the active partition requires offline access (namely WinRE).
For each file in the MFT, the attributes identified by attribute type, attribute name must be unique. Additionally, NTFS has some ordering constraints for these attributes. There is a predefined null attribute type, used to indicate the end of the list of attributes in one MFT record. It must be present as the last attribute in the record (all other storage space available after it will be ignored and just consists of padding bytes to match the record size in the MFT). Some attribute types are required and must be present in each MFT record, except unused records that are just indicated by null attribute types. This is the case for the $STANDARD_INFORMATION attribute that is stored as a fixed-size record and contains the timestamps and other basic single-bit attributes (compatible with those managed by FAT in DOS or Windows 9x). Some attribute types cannot have a name and must remain anonymous. This is the case for the standard attributes, or for the preferred NTFS "filename" attribute type, or the "short filename" attribute type, when it is also present (for compatibility with DOS-like applications, see below). It is also possible for a file to contain only a short filename, in which case it will be the preferred one, as listed in the Windows Explorer. The filename attributes stored in the attribute list do not make the file immediately accessible through the hierarchical file system. In fact, all the filenames must be indexed separately in at least one other directory on the same volume. There it must have its own MFT record and its own security descriptors and attributes that reference the MFT record number for this file. This allows the same file or directory to be "hardlinked" several times from several containers on the same volume, possibly with distinct filenames. The default data stream of a regular file is a stream of type $DATA but with an anonymous name, and the ADSs are similar but must be named. On the other hand, the default data stream of directories has a distinct type, but are not anonymous: they have an attribute name ("$I30" in NTFS 3+) that reflects its indexing format. All attributes of a given file may be displayed by using the nfi.exe ("NTFS File Sector Information Utility") that is freely distributed as part of the Microsoft "OEM Support Tools". Windows system calls may handle alternate data streams. Depending on the operating system, utility and remote file system, a file transfer might silently strip data streams. A safe way of copying or moving files is to use the BackupRead and BackupWrite system calls, which allow programs to enumerate streams, to verify whether each stream should be written to the destination volume and to knowingly skip unwanted streams.
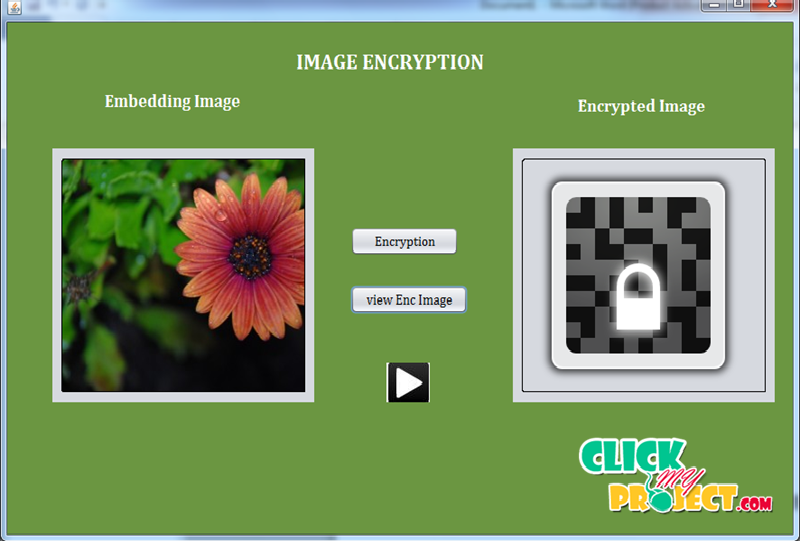
Figure 3: Reversible Data Hiding in Encrypted Image with Distributed Source ... 2. System Architecture & Core Working Principles Some attributes (such as the preferred filename, the basic file attributes) cannot be made non-resident. For non-resident attributes, their allocation map must fit within MFT records. Encrypted-by-NTFS, sparse data streams, or compressed data streams cannot be made resident. The format of the allocation map for non-resident attributes depends on its capability of supporting sparse data storage. In the current implementation of NTFS, once a non-resident data stream has been marked and converted as sparse, it cannot be changed back to non-sparse data, so it cannot become resident again, unless this data is fully truncated, discarding the sparse allocation map completely. When a non-resident attribute is so fragmented that its effective allocation map cannot fit entirely within one MFT record, NTFS stores the attribute in multiple records. The first one among them is called the base record, while the others are called extension records. NTFS creates a special attribute $ATTRIBUTE_LIST to store information mapping different parts of the long attribute to the MFT records, which means the allocation map may be split into multiple records. The $ATTRIBUTE_LIST itself can also be non-resident, but its own allocation map must fit within one MFT record. When there are too many attributes for a file (including ADS's, extended attributes, or security descriptors), so that they cannot fit all within the MFT record, extension records may also be used to store the other attributes, using the same format as the one used in the base MFT record, but without the space constraints of one MFT record. The allocation map is stored in a form of data runs with compressed encoding. Each data run represents a contiguous group of clusters that store the attribute value. For files on a multi-GB volume, each entry can be encoded as 5 to 7 bytes, which means a 1 KB MFT record can store about 100 such data runs. However, as the $ATTRIBUTE_LIST also has a size limit, it is dangerous to have more than 1 million fragments of a single file on an NTFS volume, which also implies that it is in general not a good idea to use NTFS compression on a file larger than 10 GB. The NTFS file system driver will sometimes attempt to relocate the data of some of the attributes that can be made non-resident into the clusters, and will also attempt to relocate the data stored in clusters back to the attribute inside the MFT record, based on priority and preferred ordering rules, and size constraints. Since resident files do not directly occupy clusters ("allocation units"), it is possible for an NTFS volume to contain more files on a volume than there are clusters. For example, a 74.5 GB partition NTFS formats with 19,543,064 clusters of 4 KB. Subtracting system files (a 64 MB log file, a 2,442,888-byte Bitmap file, and about 25 clusters of fixed overhead) leaves 19,526,158 clusters free for files and indices. Since there are four MFT records per cluster, this volume theoretically could hold almost 4 × 19,526,158 = 78,104,632 resident files.
Level 2 (or shared) oplock: multiple readers, no writers (i.e. read caching). Level 1 (or exclusive) oplock: exclusive access with arbitrary buffering (i.e. read and write caching). Batch oplock (also exclusive): a stream is opened on the server, but closed on the client machine (i.e. read, write and handle caching). Filter oplock (also exclusive): applications and file system filters can "back out" when others try to access the same stream (i.e. read and write caching) (since Windows 2000) Opportunistic locks have been enhanced in Windows 7 and Windows Server 2008 R2 with per-client oplock keys.
The Iris Affair is a British thriller television series created by Neil Cross, and stars Niamh Algar and Tom Hollander in the lead roles. The series premiered on 16 October 2025 on Sky Atlantic. Instagram is an American photo and short-form video sharing social networking service owned by Meta Platforms. It allows users to upload media that can be edited with filters, be organized by hashtags, and be associated with a location via geographical tagging. Posts can be shared publicly or with preapproved followers. Users can browse other users' content by tags and locations, view trending content, like photos, and follow other users to add their content to a personal feed. A Meta-operated image-centric social media platform, it is available on iOS, Android, Windows, and the Web. Users can take photos and edit them using built-in filters and other tools, then share them on other social media platforms like Facebook. It supports 33 languages including English, Hindi, Spanish, French, Japanese, and Korean. Instagram was originally distinguished by allowing content to be framed only in a square (1:1) aspect ratio of 640 pixels to match the display width of the iPhone at the time. In 2015, this restriction was eased with an increase to 1080 pixels. It also added messaging features, the ability to include multiple images or videos in a single post, and a Stories feature—similar to its main competitor at the time, Snapchat, which allowed users to post their content to a sequential feed, with each post accessible to others for 24 hours. As of January 2019, Stories was used by 500 million people daily.
Instagram was launched for iOS in October 2010 by Kevin Systrom and the Brazilian software engineer Mike Krieger. It rapidly gained popularity, reaching 1 million registered users in two months, 10 million in a year, and 1 billion in June 2018. In April 2012, Facebook acquired the service for approximately US$1 billion in cash and stock. The Android version of Instagram was released in April 2012, followed by a feature-limited desktop interface in November 2012, a Fire OS app in June 2014, an app for Windows 10 in October 2016, and an app for iPadOS in September 2025. Although often admired for its success and influence, Instagram has also been criticized for negatively affecting teens' mental health, its policy and interface changes, its alleged censorship, and illegal and inappropriate content uploaded by users.
Instagram began development in San Francisco as Burbn, a mobile check-in app created by Kevin Systrom and Mike Krieger. On March 5, 2010, Systrom closed a $500,000 (equivalent to $700,000 in 2024) seed funding round with Baseline Ventures and Andreessen Horowitz while working on Burbn. Realizing that it was too similar to Foursquare, they refocused their app on photo-sharing, which had become a popular feature among its users. They renamed it Instagram, a portmanteau of instant camera and telegram.
Josh Riedel joined the company in October as Community Manager, Shayne Sweeney joined in November as an engineer, and Jessica Zollman joined as a Community Evangelist in August 2011. The first Instagram post was a photo of South Beach Harbor at Pier 38, posted by Mike Krieger at 5:26 p.m. on July 16, 2010. On October 6, 2010, the Instagram iOS app was officially released through the App Store. In February 2011, it was reported that Instagram had raised $7 million (equivalent to $9,601,662 in 2024) in Series A funding from a variety of investors, including Benchmark Capital, Jack Dorsey, Chris Sacca (through Capital fund), and Adam D'Angelo. The deal valued Instagram at around $20 million. In April 2012, Instagram raised $50 million (equivalent to $67,320,000 in 2024) from venture capitalists with a valuation of $500 million (equivalent to $673,200,000 in 2024). Joshua Kushner was the second largest investor in Instagram's Series B fundraising round, leading his investment firm, Thrive Capital, to double its money after the sale to Facebook.
In November 2012, Instagram launched website profiles, allowing anyone to see user feeds from a web browser with limited functionality, as well as a selection of badges, and web widget buttons to link to profiles. Since the app's launch it had used the Foursquare API technology to provide named location tagging. In March 2014, Instagram started to test and switch the technology to use Facebook Places.
In June 2015, the desktop website user interface was redesigned to become more flat and minimalistic, but with more screen space for each photo and to resemble the layout of Instagram's mobile website. Furthermore, one row of pictures only has three instead of five photos to match the mobile layout. The slideshow banner on the top of profile pages, which simultaneously slide-showed seven picture tiles of pictures posted by the user, alternating at different times in a random order, has been removed. In addition, the formerly angular profile pictures became circular.
In April 2016, Instagram released a Windows 10 Mobile app, after years of demand from Microsoft and the public to release an app for the platform. The platform previously had a beta version of Instagram, first released on November 21, 2013, for Windows Phone 8. The new app added support for videos (viewing and creating posts or stories, and viewing live streams), album posts and direct messages. Similarly, an app for Windows 10 personal computers and tablets was released in October 2016. In May, Instagram updated its mobile website to allow users to upload photos, and to add a "lightweight" version of the Explore tab.
On May 11, 2016, Instagram revamped its design, adding a black-and-white flat design theme for the app's user interface, and a less skeuomorphistic, more abstract, "modern" and colorful icon. Rumors of a redesign first started circulating in April, when The Verge received a screenshot from a tipster, but at the time, an Instagram spokesperson simply told the publication that it was only a concept. On December 6, 2016, Instagram introduced comment liking. However, unlike post likes, the user who posted a comment does not receive notifications about comment likes in their notification inbox. Uploaders can optionally decide to deactivate comments on a post.
The mobile website allows uploading pictures since May 4, 2017. Image filters and the ability to upload videos were not introduced then. On April 30, 2019, the Windows 10 Mobile app was discontinued, though the mobile website remains available as a progressive web application (PWA) with limited functionality. The app remains available on Windows 10 computers and tablets, also updated to a PWA in 2020.
3. Software Implementation, Frameworks & Protocols In April 2024, Instagram announced that they would start testing new tools "within weeks" to fight sextortion, a form of blackmail involving intimate pictures sent online. On August 2, 2024, Turkey blocked Instagram after the platform deleted posts from users offering condolences for the death of Hamas leader Ismail Haniyeh. In December 2024, Instagram and MTA collaborated and sold Metrocards ft. creators such as New York Nico, Overheard in New York, and SubwayTakes. On September 3, 2025, Instagram launched a native iPadOS app, which before relied on the iOS app and did not utilize the larger screen size of tablets. In February 2026, Meta announced a new safety feature on Instagram that will alert parents if their teenage children repeatedly search for content related to suicide or selfIharm, as part of expanded parental supervision tools amid legal scrutiny of its impact on youth. Meta scheduled an end of support for end-to-end encryption in Instagram direct messaging in May 2026. Following this change, messages are no longer protected by end-to-end encryption and are not exclusively accessible only to the communicating users. As a result, the level of confidentiality in direct messages is reduced compared to fully encrypted communications, and message content may be accessible under certain conditions, depending on applicable policies and regulatory frameworks. The change prompted concerns among privacy researchers and digital rights commentators regarding reduced message confidentiality and broader implications for messaging privacy and data protection. In August 2026, Instagram updated its wordmark for the first time in about a decade, replacing its previous script-style lettering with a redesigned typeface that combines script and print elements. The camera icon remained unchanged.
Users can upload photographs and short videos, follow other users' feeds, and geotag images with the name of a location. Users can set their account as "private", thereby requiring that they approve any new follower requests. Users can connect their Instagram account to other social networking sites, enabling them to share uploaded photos to those sites. In September 2011, a new version of the app included new and live filters, instant tilt–shift, high-resolution photographs, optional borders, one-click rotation, and an updated icon. Photos were initially restricted to a square, 1:1 aspect ratio; since August 2015, the app supports portrait and widescreen aspect ratios as well. Users could formerly view a map of a user's geotagged photos.
The feature was removed in September 2016, citing low usage. Since December 2016, posts can be "saved" into a private area of the app. The feature was updated in April 2017 to let users organize saved posts into named collections. Users can also "archive" their posts in a private storage area, out of visibility for the public and other users. The move was seen as a way to prevent users from deleting photos that don't garner a desired number of "likes" or are deemed boring, but also as a way to limit the "emergent behavior" of deleting photos, which deprives the service of content. In August, Instagram announced that it would start organizing comments into threads, letting users more easily interact with replies. Since February 2017, up to ten pictures or videos can be included in a single post, with the content appearing as a swipeable carousel. The feature originally limited photos to the square format, but received an update in August to enable portrait and landscape photos instead. In April 2018, Instagram launched its version of a portrait mode called "focus mode", which gently blurs the background of a photo or video while keeping the subject in focus when selected. In November, Instagram began to support Alt text to add descriptions of photos for the visually impaired. They are either generated automatically using object recognition (using existing Facebook technology) or manually specified by the uploader. On March 1, 2021, Instagram launched a new feature named Instagram Live Rooms, which lets four people go live together. In May 2021, Instagram announced a new accessibility feature for videos on Instagram Reels and Stories to allow creators to place closed captions on their content.
IGTV was a vertical video application launched by Instagram in June 2018. Basic functionality is also available within the Instagram app and website. IGTV allows uploads of up to 10 minutes in length with a file size of up to 650 MB, with verified and popular users allowed to upload videos of up to one hour in length with a file size of up to 5.4 GB. The app automatically begins playing videos as soon as it is launched, which CEO Kevin Systrom contrasted to video hosts where one must first locate a video. In March 2022, the application was shut down.
Instagram Reels is the short-form section of the American social media platform Instagram. Reels focuses on vertical videos that are less than 90 seconds of duration and various features for user interaction. As of November 2024, Reels averages at 150 billion views a day. Creators earn money based on the amount of views they receive, or through ad revenue. In November 2019, it was announced that Instagram would start to roll out a new feature to Brazil known as Instagram Reels. It would then expand to France and Germany. Instagram Reels was officially launched in Pakistan in August 2022, two years after its global rollout in August 2020. It functions similarly to the Chinese video service TikTok, focusing on allowing users to create short videos already set to existing sounds from other clips. Users could make up to 15 (later 30) second videos using this feature. Reels also uses existing Instagram filters and editing tools. In July 2020, Instagram rolled out Reels to India after TikTok was banned in the country. Then, the following month, Reels officially launched in 50 countries including the United States, Canada and United Kingdom. Then in August of that year, Instagram introduced a reels button on the home page. On June 17, 2021, Instagram launched full-screen advertisements in Reels. The ads are similar to regular reels and can run up to 30 seconds. They are distinguished from regular content by the "sponsored" tag under the account name. Despite the "TikTokification" of Reels and the parent company Meta spending millions on courting content creators, user engagement continued to lag way behind TikTok as of 2022. Then Instagram started rolling out a new feature with made Reels up to 90 seconds long beginning in June 2022. After a period of testing, a duration of up to three minutes was announced in January 2025. On February 26, 2025, Instagram Reels came under fire after numerous users reported a sudden surge in violent and graphic content appearing in their feeds. Meta issued a public apology, stating that a technical error led to the unintended recommendation of such content. A Meta spokesperson explained, "We have fixed an error that caused some users to see content in their Instagram Reels feed that should not have been recommended. We apologize for the mistake." Since its inception in 2020, the usage of Instagram Reels has continuously increased. In September 2022, Instagram Reels generated over 140 billion views daily. The number of monthly users also increased from 1.5 billion in 2022 to 1.8 billion as of 2024.
Researchers from the Guizhou University of Finance and Economics and Western Michigan University found that short-form videos like YouTube Shorts, TikTok, and Instagram Reels may make it easier for young adults and children to develop addictive behavior because short-form videos provide "short bursts of thrills". These researchers found that college students in the U.S. and China watch short-form videos for entertainment, knowledge, and to build social identities. The Wall Street Journal reported that some parents are concerned about the effects of short-form videos on their children, as there is no way to disable Instagram or set limits. When children watch short-form videos, they learn to expect continual stimulation and fast-paced changes, which can cause problems when engaging in activities that require greater focus, such as reading.
Recent studies highlighted the connection between short-form videos such as Instagram Reels and the brain's reward system, specifically dopamine release. According to Dr. Anna Lembke, a psychiatrist and chief of Stanford University's dual diagnosis addiction clinic, brief attention-grabbing videos act as powerful stimuli triggering dopamine surges akin to other addictive behaviors. The rapid and easily consumable nature of short-form videos can elicit high levels of dopamine; since dopamine serves as a motivator rather than a direct source of pleasure, individuals are compelled to seek rewarding activities and become addicted to them. Such neurochemical responses lead to addictive patterns and behaviors, entering a vicious cycle.
Digital addiction can lead to shorter attention spans and slower cognitive processing. In August 2016, Instagram launched Instagram Stories, a feature that allows users to take photos, add effects and layers, and add them to their Instagram story. Images uploaded to a user's story expire after 24 hours. The media noted the feature's similarities to Snapchat. In response to criticism that it copied functionality from Snapchat, CEO Kevin Systrom told Recode that "Day One: Instagram was a combination of Hipstamatic, Twitter [and] some stuff from Facebook like the 'Like' button. You can trace the roots of every feature anyone has in their app, somewhere in the history of technology". Although Systrom acknowledged the criticism as "fair", Recode wrote that "he likened the two social apps' common features to the auto industry: Multiple car companies can coexist, with enough differences among them that they serve different consumer audiences".
Systrom further stated that "When we adopted [Stories], we decided that one of the really annoying things about the format is that it just kept going and you couldn't pause it to look at something, you couldn't rewind. We did all that, we implemented that." He also told the publication that Snapchat "didn't have filters, originally. They adopted filters because Instagram had filters and a lot of others were trying to adopt filters as well." In November, Instagram added live video functionality to Instagram Stories, allowing users to broadcast themselves live, with the video disappearing immediately after ending. In January 2017, Instagram launched skippable ads, where five-second photo and 15-second video ads appear in-between different stories. In April 2017, Instagram Stories incorporated augmented reality stickers, a "clone" of Snapchat's functionality.
In May 2017, Instagram expanded the augmented reality sticker feature to support face filters, letting users add specific visual features onto their faces. Later in May, TechCrunch reported about tests of a Location Stories feature in Instagram Stories, where public Stories content at a certain location are compiled and displayed on a business, landmark or place's Instagram page. A few days later, Instagram announced "Story Search", in which users can search for geographic locations or hashtags and the app displays relevant public Stories content featuring the search term. In June 2017, Instagram revised its live-video functionality to allow users to add their live broadcast to their story for availability in the next 24 hours, or discard the broadcast immediately. In July, Instagram started allowing users to respond to Stories content by sending photos and videos, complete with Instagram effects such as filters, stickers, and hashtags. Stories were made available for viewing on Instagram's mobile and desktop websites in late August 2017. On December 5, 2017, Instagram introduced "Story Highlights", also known as "Permanent Stories", which are similar to Instagram Stories, but don't expire. They appear as circles below the profile picture and biography and are accessible from the desktop website as well. In June 2018, the daily active story users of Instagram had reached 400 million users, and monthly active users had reached 1 billion active users. In December 2024, Instagram announced that it was trialing a feature designed to help users reconnect with content they may have missed from their mutual followers. This new functionality showcases unseen Story Highlights at the end of the Stories tray, which is situated at the top of the feed. By doing so, users can easily access curated Stories from the past week that they might not have seen previously.
Importantly, this feature will only display Story Highlights—curated collections of Stories saved by users—rather than standard Stories that disappear after 24 hours. Users will only be able to view these Highlights after they have gone through all current Stories in their tray, meaning that those who follow many accounts may find it challenging to see these updates. Sharenting is when parents post content, including images, about their children. Instagram is one of the main sites for sharenting. The hashtag #letthembelittle contains over 10 million images related to children on Instagram. Bare 2020 analysed 300 randomly selected images under the hashtag and found they tended to contain children's personal information, including name, age and location.
After being released in October 2010, Instagram had one million registered users in December 2010. In June 2011, it announced that it had 5 million users, which increased to 10 million in September. This growth continued to 30 million users in April 2012, 80 million in July 2012, 100 million in February 2013, 130 million in June 2013, 150 million in September 2013, 300 million in December 2014, 400 million in September 2015, 500 million in June 2016, 600 million in December 2016, 700 million in April 2017, and 800 million in September 2017. In June 2011, Instagram passed 100 million photos uploaded to the service.
This grew to 150 million in August 2011, and by June 2023, there were over 50 billion photos uploaded to the service. In October 2016, Instagram Stories reached 100 million active users, two months after launch. This increased to 150 million in January 2017, 200 million in April, surpassing Snapchat's user growth, and 250 million active users in June 2017. In April 2017, Instagram Direct had 375 million monthly users.
Like many social media sites, Instagram employs a combination of automated algorithms, user reports and human review to identify and remove illegal content such as child abuse and encouragement of terrorism. The system also aims to identify cyberbullying, hate speech and misinformation. Although the U.S. government has little direct power to force social media sites to remove specific content, Instagram has on occasion done so voluntarily, especially to avoid being seen as aiding the spread of fake news. On October 30, 2020, Instagram temporarily removed the "recent" tab on hashtag pages to prevent the spread of misinformation regarding the 2020 United States presidential election. On January 7, 2021, following the attack on the U.S. Capitol by supporters of then-President Donald Trump, Trump was banned from Instagram "indefinitely". Zuckerberg stated "We believe the risks of allowing the President to continue to use our service during this period are simply too great." Instagram has been criticized in India for not taking steps to counter homophobic and transphobic contents. According to the LGBT activist Indrajeet Ghorpade, "Hateful homophobic content in English is removed but the same in Indian languages is allowed to remain on the platform... despite flagging the hateful and homophobic content to Instagram, no action has been taken." In 2023, a 16-year-old queer artist allegedly died by suicide after receiving thousands of hate comments on Instagram.
Instagram has a clear set of rules about what is and isn't allowed on the site. We encourage people who come across illegal or inappropriate content to report it to us using the built-in reporting tools next to every photo, video or comment, so we can take action. People can't buy things on Instagram, we are simply a place where people share photos and videos. However, new incidents of illegal drug trade have occurred in the aftermath of the 2013 revelation, with Facebook, Inc., Instagram's parent company, asking users who come across such content to report the material, at which time a "dedicated team" reviews the information. In 2019, Facebook announced that influencers are no longer able to post any vape, tobacco products, and weapons promotions on Facebook and Instagram.
Instagram has been blocked by China following the 2014 Hong Kong protests as many confrontations with police and incidents occurring during the protests were recorded and photographed. Hong Kong and Macau were not affected as they are part of special administrative regions of China. Sometimes the phrase "Chinese Instagram" is used to refer to Xiaohongshu, a competitor social media app.
Instagram was one of the last freely available global social media sites in Iran. According to the IFJ, Instagram is popular among Iranians because it is seen as an outlet for freedom and a "window to the world". Still, Iran has sentenced citizens to prison for posts made on their Instagram accounts. The Iranian government blocked Instagram periodically during anti-government protests in 2019-20. In July 2021, Instagram temporarily censored videos with the phrase "death to Khamenei". As of September 2022, it was blocked permanently, along with WhatsApp, with an exception made for tourists and corporations who request its use.
A few days after a fire incident that happened in the Koryo Hotel in North Korea on June 11, 2015, authorities blocked Instagram to prevent photos of the incident from being spread. 4. Practical Deployment, Analysis & Case Studies In May 2017, a survey conducted by the United Kingdom's Royal Society for Public Health, featuring 1,479 people aged 14–24 and asking them to rate social media platforms depending on anxiety, depression, loneliness, bullying and body image, concluded that Instagram was the "worst for young mental health". Some have suggested it may contribute to digital dependence, whilst this same survey noticed its positive effects, including self-expression, self-identity, and community building. In response to the survey, Instagram said that "Keeping Instagram a safe and supportive place for young people was a top priority". The company filters out the reviews and accounts. If some of the accounts violate Instagram's community guidelines, it will take action, which could include banning them. In 2017, researchers from Harvard University and University of Vermont demonstrated a machine learning tool that successfully outperformed general practitioners' diagnostic success rate for depression. The tool used color analysis, metadata components, and face detection of users' feeds. In 2019, Instagram began to test the hiding of like counts for posts made by its users, with the feature later made available to everyone.
In 2021, Instagram announced that like counts would return to be publicly viewable by default. Users can choose to switch them off for their whole feed or on a per-post basis. Correlations have been made between Instagram content and dissatisfaction with one's body, as a result of people comparing themselves to other users. In a recent survey, half of the applicants admitted to photo editing behavior which has been linked with concerns over body image. In October 2021, CNN published an article and interviews on two young women, Ashlee Thomas and Anastasia Vlasova, saying Instagram endangered their lives due to it having toxic effects on their diets. In October 2023, 42 U.S. states filed a lawsuit against Instagram and parent company Meta, accusing them of contributing to a youth mental health crisis due to the addictive nature of the platforms. The lawsuit claimed that Meta and its Instagram unit repeatedly misled the public about the dangers of its platforms and knowingly induced young children and teenagers into addictive and compulsive social media use. Meta representatives replied that they were disappointed with the lawsuit and were hoping instead to continue working with other companies from the industry to create new and better standards for applications teens use.
To help us deliver interesting paid or sponsored content or promotions, you agree that a business or other entity may pay us to display your username, likeness, photos (along with any associated metadata), and/or actions you take, in connection with paid or sponsored content or promotions, without any compensation to you. There was no option for users to opt out of the changed Terms of Service without deleting their accounts before the new policy went into effect on January 16, 2013. The move garnered severe criticism from users, prompting Instagram CEO Kevin Systrom to write a blog post one day later, announcing that they would "remove" the offending language from the policy. Citing misinterpretations about its intention to "communicate that we'd like to experiment with innovative advertising that feels appropriate on Instagram", Systrom also stated that it was "our mistake that this language is confusing" and that "it is not our intention to sell your photos".
Furthermore, he wrote that they would work on "updated language in the terms to make sure this is clear". The policy change and its backlash caused competing photo services to use the opportunity to "try to lure users away" by promoting their privacy-friendly services, and some services experienced substantial gains in momentum and user growth following the news. On December 20, Instagram announced that the advertising section of the policy would be reverted to its original October 2010 version. The Verge wrote about that policy as well, however, noting that the original policy gives the company right to "place such advertising and promotions on the Instagram Services or on, about, or in conjunction with your Content", meaning that "Instagram has always had the right to use your photos in ads, almost any way it wants. We could have had the exact same freakout last week, or a year ago, or the day Instagram launched". The policy update also introduced an arbitration clause, which remained even after the language pertaining to advertising and user content had been modified.
The most-liked photo on Instagram is a carousel of photos from footballer Lionel Messi celebrating winning the 2022 FIFA World Cup, The post has over 76 million likes. In 2022, Instagram was the second most downloaded mobile app of the year. Criticism of Facebook Dronestagram Instagram face – Beauty standard based on digitally altered photographs Instagram husband – Unacknowledged photographer behind another's social media posts Internet celebrity – Person who has become famous through their use of the InternetPages displaying short descriptions of redirect targets List of social networking services Pheed – Pay-per-view social media platform Pixnet – Taiwanese social media service Social media and suicide Timeline of social media Official website Rose, Kevin (May 30, 2013). "A #Nofilter Conversation with the founders of Instagram" (podcast).
Commonwealth Club. "Instagram: Kevin Systrom and Mike Krieger" (podcast). How I Built This. NPR. September 19, 2016. BBC News Hindi (July 2, 2026). Instagram III IIII II IIIII IIIIII II IIIIIIIII - BBC Eye II II IIIIIIIIIIIII (BBC Hindi) [A terrifying world hidden within Instagram exposed]. Retrieved July 5, 2026 – via YouTube.
Thank you for visiting nature.com. You are using a browser version with limited support for CSS. To obtain the best experience, we recommend you use a more up to date browser (or turn off compatibility mode in Internet Explorer). In the meantime, to ensure continued support, we are displaying the site without styles and JavaScript. The technique of reversible data hiding in encrypted images (RDH-EI) has experienced significant interest as it allows for precise extraction of embedded data without compromising the confidentiality of the original image. This research introduces a novel RDH-EI technique designed to accommodate multiple data hiders. To tackle this challenge, we propose a sophisticated RDH-EI method that integrates secret sharing Founded on the Learning With Errors (LWE) problem alongside adaptive coding strategies. On the content owner’s side, the original image is first distributed to multiple data hiders using a method Founded on the Learning With Errors (LWE) problem. Then, block permutation along with stream cipher encryption are performed to completely preserve the spatial correlation between image blocks. The proposed method benefits from the robust security provided by LWE. Initially, we examine the spread of the most significant bit planes to detect segments that are suitable for data embedding. Next, the data hider produces extra data and embeds errors within the encrypted image to guarantee precise image reconstruction. To increase data storage capacity, the most significant bits (MSB) The blocks suitable for embedding are adaptively compressed based on their frequency of occurrence. The extra data may be inserted into the (MSB) of the encrypted image, where it is combined with inverse Huffman codewords and supplementary auxiliary information. At the receiving side, the initial image can still be completely restored Losslessly, even if some shares happen to be damaged or missing, provided that a sufficient number of valid shares are available. Experimental findings demonstrate that the RDH-EI approach exceeds the performance of various cutting-edge methods, including those employing secret sharing (SS), in terms of embedding capacity.
Separable reversible data hiding by vacating room after encryption using encrypted pixel difference High-capacity reversible data hiding in encrypted images using dual-stage bit-plane compression and CP-ABE-based recovery authorization Reversible data hiding and authentication scheme for encrypted image based on prediction error compression An image data hiding system involves two main components: The secret information is embedded into the cover image to produce a stego-image that appears identical to the original to the human eye. Two scenarios must be addressed in an image data hiding system. In one scenario, the focus is on safeguarding the secret data, and restoring the original cover image is unnecessary. The other scenario requires that both the secret data and the cover image are essential and must be perfectly recovered at the decoder side, which is crucial in applications like military and medical fields. It is evident that the first scenario represents irreversible data hiding, while the second corresponds to reversible data hiding (RDH). RDH has gained growing interest because of its ability to allow complete reversibility. Until now, most RDH techniques have primarily been developed using difference expansion (DE), histogram shifting (HS), lossless compression, and prediction error expansion (PEE). These RDH techniques strive to maintain an ideal compromise between the volume of embedded data and the extent of modifications made to the image. As cloud computing advances rapidly, the demand for privacy protection continues to grow.
To safeguard data privacy while still allowing necessary operations, processing multimedia signals in the encrypted domain has drawn significant interest 1 , 2 , 3 , 4 . In many scenarios, like cloud storage, image owners typically encrypt their images before being uploaded them to a cloud server machine to ensure content protection. Once the encrypted image is received, the cloud server might need to insert extra data for tasks like storage management or image annotation. As a result, the approach of reversible data hiding in encrypted images (RDH-EI) has been introduced 5 , 6 . This method enables the image owner to encrypt the image, while also permitting a data hider to insert secret information into it while keeping the original content hidden. With the appropriate encryption keys, it is possible to completely restore both the original image and the hidden data.
5. Performance Evaluation & Extended Technical Observations In 2008, Puech and colleagues proposed a (RDH-EI) technique 5 , in which one bit is embedded per block within an image encrypted with the (AES). The concealed bit may be recovered by evaluating the local variation in pixel values within the block of the image.
A few years later, Zhang introduced a novel RDH-EI method in which the image is first encrypted using a stream cipher, and then extra data is embedded using a bit flipping technique 6 . Building upon these methods, numerous novel RDH-EI techniques have been designed employing a range of different strategies 7 , 8 , 9 .
Reversible data hiding in encrypted images (RDH-EI) schemes are typically classified into two main types: vacating room after encryption (VRAE) 6 , 7 , 8 , 9 and reserving room before encryption (RRBE) 10 , 11 , 12 , 13 , 14 . In the VRAE method, the original image undergoes encryption first, after which the confidential data is embedded into the encoded picture. Conversely, the RRBE method reserves region for embedding data prior to the encryption process. Unlike the VRAE approach, the RRBE technique takes benefit of the spatial correlation within the initial image and generally offers a higher embedding space.
A prominent example of the RRBE strategy is the RDH-EI scheme introduced by Puteaux and Puech, which employs prediction of the pixels’ (MSB) 14 . This approach effectively leverages the local correlation present in the initial image, which causes a notable rise in the embedding capacity. Building upon this approach, Yin et al. 15 proposed a adaptive-length MSB prediction technique utilizing Huffman encoding, while Mohammadi et al. 16 improved the approach by including more important bits.
Zhang 17 and Qian and Zhang 18 suggested more adaptable distinct techniques that compress specific LSB planes of a stream cipher-encrypted image to generate space for embedding data. This method allows data extraction to be performed without the need for the encoding key and operates independently of the image reconstruction process. In 19 , secret bits are embedded by randomly selecting pixels from the image encrypted using a stream cipher and replacing the higher-order bit-planes. Because each high bit-plane can be either “0” or “1,” the prediction errors for both cases are examined to precisely restore the original image.
While RRBE-based techniques provide strong embedding performance, they can encounter practical challenges because the content owner might not be informed about the data hiding process that follows or may lack the computational resources needed for preprocessing. To address this limitation, specialized encryption-based techniques called VRBE-based methods have been developed.
References 20 , 21 , and 23 describe generating the encrypted image through block rearrangement and block-oriented bitwise XOR, which preserves the internal correlation of each encrypted block. Following this, data hiding is performed using methods like difference histogram shifting (DHS) 20 , adaptive block encoding 21 , and difference compression 23 . In 24 and 25 , The initial image has been encrypted through bit-plane rearrangement and Block shuffling, successfully transferring The extra space from the initial image into the encrypted image.
In the mentioned RDHEI techniques, the original image is first encrypted and then uploaded to the cloud. However, the encrypted image could be targeted by a third party attack, resulting in incorrect retrieval of the image at the receiver’s end. To enhance the resilience of RDHEI, various methods incorporating secret sharing (SS) have been introduced 26 , 27 , 28 , 29 , 30 , 31 , 32 .
Recently, RDH-EI schemes utilizing secret sharing methods have been presented in 33 , 34 , 35 , 36 . In the methods outlined in 33 , 34 , 35 , 36 , the owner of the image utilizes secret sharing techniques to encode the image into n separate encrypted shares, which are then stored on a cloud server. Each cloud server is capable of independently embedding data into its respective encrypted segment. The original image can be completely restored by gathering t of these encrypted segments.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/NTFS • https://en.wikipedia.org/wiki/The%20Iris%20Affair • https://en.wikipedia.org/wiki/Instagram • https://www.nature.com/articles/s41598-025-28912-8
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Reversible Data Hiding In Encrypted Images Using Python.
[*] Metasploit Scan Running on Target Subnet for Reversible Data Hiding In Encrypted Images Using Python... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |