Complete Technical Paper Content — Rogue Application Installer Detection Tool On Android
Overview & System Context
Rogue Application Installer Detection Tool On Android: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9523 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Google Play, also known as the Google Play Store or Play Store, and formerly known as the Android Market, is a digital distribution service operated and developed by Google. It serves as the official app store for certified devices running on the Android operating system and its derivatives, as well as ChromeOS, allowing users to browse and download applications developed with the Android software development kit and published through Google. Google Play has also served as a digital media store, with it offering various media for purchase (as well as certain things available free) such as books, movies, musical singles, television programs, and video games. Content that has been purchased on Google TV and Google Play Books can be accessed on a web browser (such as, for example, Google Chrome) and through certain Android and iOS apps.
An individual's Google Account can feature a diverse collection of materials to be heard, read, watched, or otherwise interacted with. The nature of the various things offered through Google Play's services have changed over time given the particular history of the Android operating system. Applications are available through Google Play either for free or at a cost. They can be downloaded directly on an Android device through the proprietary Google Play Store mobile app or by deploying the application to a device from the Google Play website. Applications utilizing the hardware capabilities of a device can be targeted at users of devices with specific hardware components, such as a motion sensor (for motion-dependent games) or a front-facing camera (for online video calling). The Google Play Store had over 82 billion app downloads in 2016 and over 3.5 million apps published in 2017, while after a purge of apps, it is back to over 3 million. It has been the subject of multiple issues concerning security, in which malicious software has been approved and uploaded to the store and downloaded by users, with varying degrees of severity. Google Play was launched on March 6, 2012, bringing together Android Market, Google Music, Google Movies, and Google Books under one brand, marking a shift in Google's digital distribution strategy.
Following their rebranding, Google has expanded the geographical support for each of the services. Since 2021, Google has gradually sunsetted the Play brand: Google Play Newsstand was discontinued and replaced by Google News, Google Play Music was discontinued and replaced by YouTube Music on December 3, 2020, and Play Movies & TV was rebranded as Google TV on November 11, 2021.
By the end of 2017, Google Play featured more than 3.5 million Android applications. After Google purged many apps from the Google Play Store starting in 2024, there were 1.68 million Android applications in 2024. As of 2017, developers in more than 150 locations could distribute apps on Google Play, though not every location supports merchant registration. Developers receive 85% of the application price, while the remaining 15% goes to the distribution partner and operating fees.
Developers can set up sales, with the original price struck out and a banner underneath informing users when the sale ends. Google Play allows developers to release early versions of apps to a select group of users, as alpha or beta tests. Users can pre-order select apps (as well as movies, music, books, and games) to have the items delivered as soon as they are available. Some network carriers offer billing for Google Play purchases, allowing users to opt for charges in the monthly phone bill rather than on credit cards. Users can request refunds within 48 hours after a purchase.
At the Google I/O 2013 Developer Conference, Google announced the introduction of Google Play Games. Google Play Games is an online gaming service for Android that features real-time multiplayer gaming capabilities, cloud saves, social and public leaderboards, and achievements. Its standalone mobile app was launched on July 24, 2013. Google Play Books is an ebook digital distribution service. Google Play offers over five million ebooks available for purchase, and users can also upload up to 1,000 of their own ebooks in the form of PDF or EPUB file formats. As of January 2017, Google Play Books is available in 75 countries.
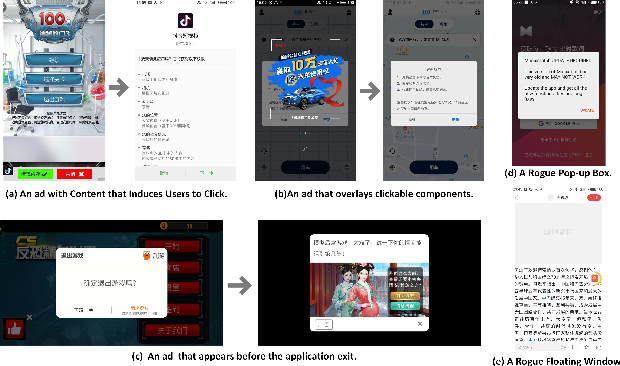
Figure 1: Figure 1 from Automated Rogue Behavior Detection for Android ... Google Play Movies & TV was a video on demand service offering movies and television shows available for purchase or rental, depending on availability. As of January 2017, movies are available in over 110 countries, while TV shows are available only in Australia, Austria, Canada, France, Germany, Japan, Switzerland, the United States and the United Kingdom. In October 2020, Google Play Movies & TV was renamed Google TV. Google announced on March 22, 2022, that Google Play will remove Play Movies & TV from their store and will be moved to Google TV by May 2022.
On September 23, 2019, Google launched its Google Play Pass games and apps subscription service in the US. As of September 2019, subscribers could access the games and apps without ads and in-app purchases. The program is invitation-only for app developers, who then can integrate the service into their existing apps. Security: Media Codecs, Media Framework Components, DNS Resolver, Conscrypt Privacy: Documents UI, Permission Controller, ExtServices Consistency: Time zone data, ANGLE (developers opt-in), Module Metadata, Networking components, Captive Portal Login, Network Permission Configuration On December 4, 2019, Qualcomm announced their Snapdragon 865 supports GPU drivers updated via the Google Play Store. This feature was initially introduced with Android Oreo but vendors had not added support yet.
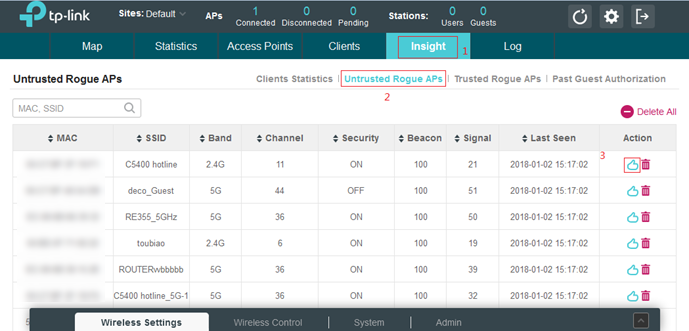
Google Play (previously styled Google play) originated from three distinct products: Android Market, Google Music, and Google Books (formerly Google eBookstore). Figure 2: Configure rogue AP detection on EAP/Omada Controller | Asistencia de ... Google Play Music was a music and podcast Streaming media and online music locker. It features over 40 million songs, and gives users free cloud storage of up to 50,000 songs. As of May 2017, Google Play Music was available in 64 countries. In June 2018, Google announced plans to shut down Play Music by 2020 and offered users to migrate to YouTube Music, migration to Google Podcasts was announced in May 2020. In October 2020, the music store for Google Play Music was shut down. Google Play Music was shut down in December 2020 and was replaced by YouTube Music and Google Podcasts.
Google Play Newsstand was a news aggregator and digital newsstand service offering subscriptions to digital magazines and topical news feeds. Google released Newsstand in November 2013, combining the features of Google Play Magazines and Google Currents into a single product. On May 15, 2018, the mobile app merged with Google News & Weather to form Google News. The Newsstand section continued to appear on the Google Play website until November 5, 2018, but now is only available through the Google News app.
Until March 2015, Google Play had a "Devices" section for users to purchase Google Nexus devices, Chromebooks, Chromecasts, other Google-branded hardware, and accessories. A separate online hardware retailer called the Google Store was introduced on March 11, 2015, replacing the Devices section of Google Play. Apart from searching for content by name, apps can also be searched through keywords provided by the developer. When searching for apps, users can press on suggested search filters, helping them to find apps matching the determined filters. For app discoverability, Google Play Store consists of lists featuring top apps in each category, including "Top Free", a list of the most popular free apps of all time; "Top Paid", a list of the most popular paid apps of all time; "Top Grossing", a list of apps generating the highest amounts of revenue; "Trending Apps", a list of apps with recent installation growth; "Top New Free", a list of the most popular new free apps; "Top New Paid", a list of the most popular new paid apps; "Featured", a list of new apps selected by the Google Play team; "Staff Picks", a frequently updated list of apps selected by the Google Play team; "Editors' Choice", a list of apps considered the best of all time; and "Top Developer", a list of apps made by developers considered the best. In March 2017, Google added a "Free App of the Week" section, offering one normally paid app for free. In July 2017, Google expanded its "Editors' Choice" section to feature curated lists of apps deemed to provide good Android experiences within overall themes, such as fitness, video calling, and puzzle games. Google Play enables users to know the popularity of apps by displaying the number of times the app has been downloaded. The download count is a color-coded badge, with special color designations for surpassing certain app download milestones, including grey for 100, 500, 1,000, and 5,000 downloads, blue for 10,000 and 50,000 downloads, green for 100,000 and 500,000 downloads, and red/orange for 1 million, 5 million, 10 million, and 1 billion downloads. Users can submit reviews and ratings for apps and digital content distributed through Google Play, which are displayed publicly. Ratings are based on a 5-point scale. App developers can respond to reviews using the Google Play Console.
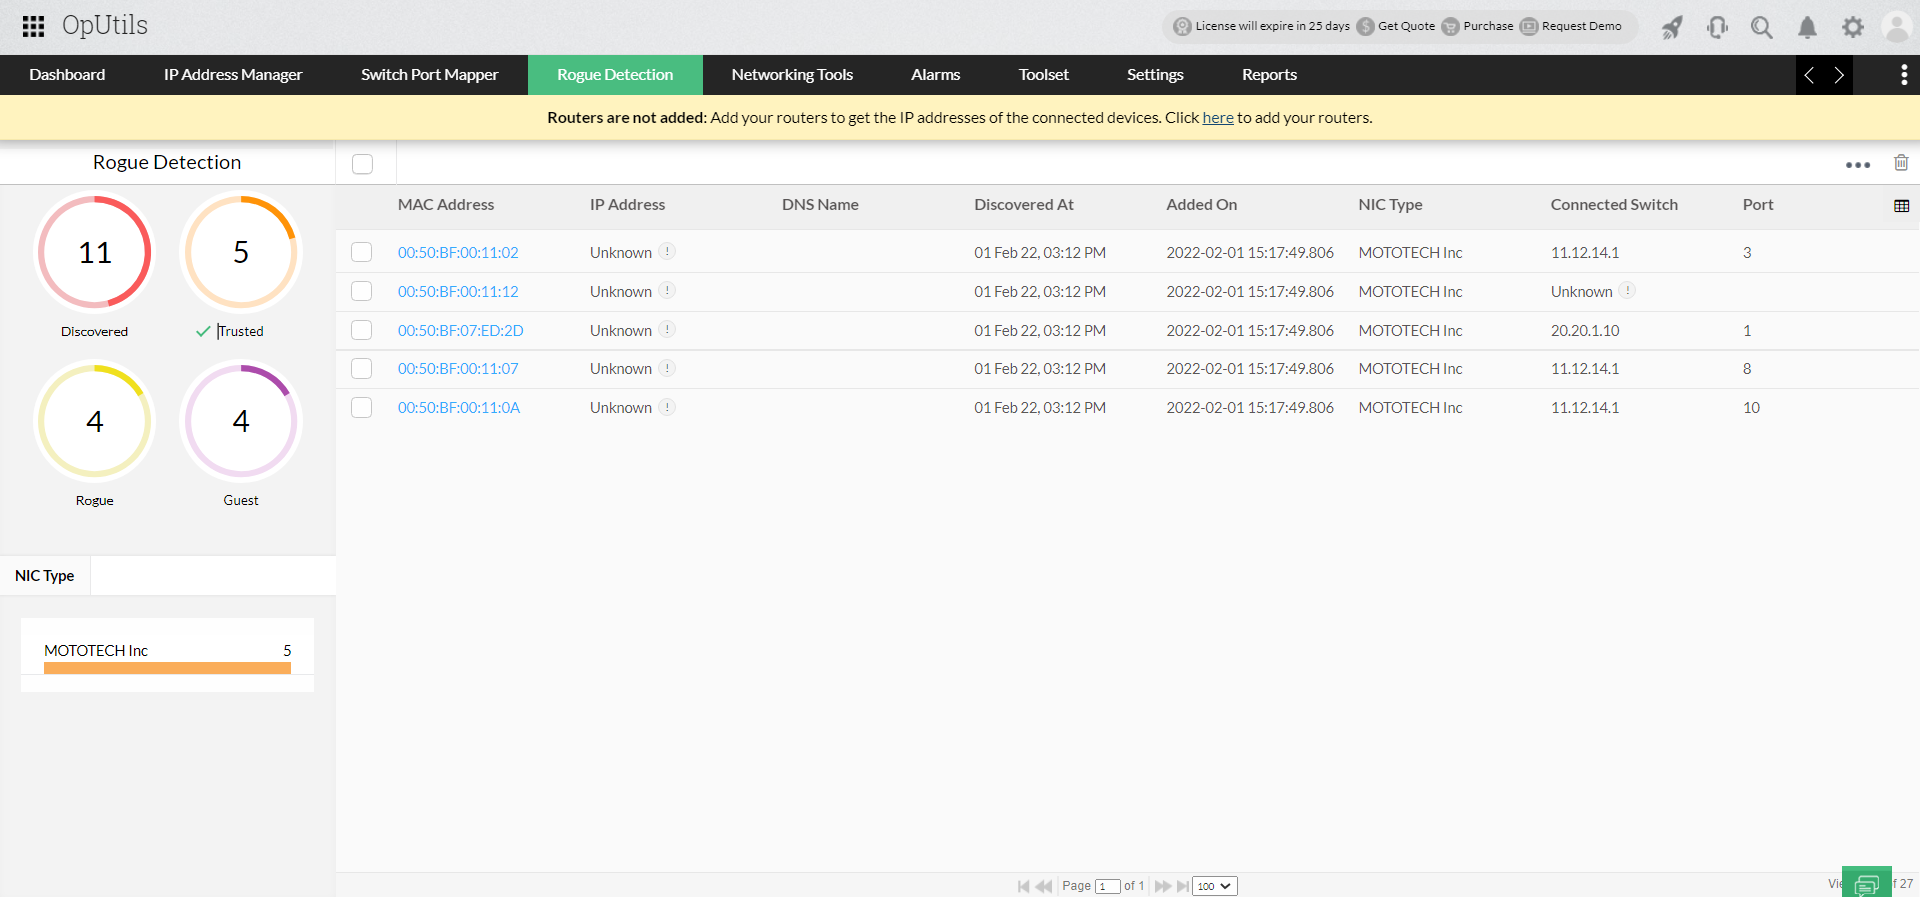
Figure 3: Rogue Device Detection Software | OpUtils Google allows users to purchase content with credit or debit cards, carrier billing, gift cards, or through PayPal. Google began rolling out carrier billing for purchases in May 2012, followed by support for PayPal in May 2014. On July 31, 2023, Hong Kong and Macau added support for China UnionPay cards, and users can bind UnionPay cards through the Play Store app.
Google Play Store, shortened to Play Store on the Home screen and App screen, is Google's official pre-installed app store on Android-certified devices. It provides access to content on Google Play, including apps, books, magazines, music, movies, and television programs. Devices do not ship with the Google Play Store in China, with manufacturers offering their own alternative. Google Play Store filters the list of apps to those compatible with the user's device. Developers can target specific hardware components (such as compass), software components (such as widget), and Android versions (such as 7.0 Nougat). Carriers can also ban certain apps from being installed on users' devices, for example tethering applications. There is no requirement that Android applications be acquired using the Google Play Store. Users may download Android applications from a developer's website or through a third-party app store alternative. Google Play Store applications are self-contained Android Package files (APK), similar to .exe files used to install programs on Microsoft Windows computers. On Android devices, an "Unknown sources" feature in Settings allows users to bypass the Google Play Store and install APKs from other sources. Depending on developer preferences, some apps can be installed to a phone's external storage card. In 2020, Google decided to rewrite the Play Store app's UI code using Jetpack Compose, which was in pre-alpha at the time. It stated that the "existing code was 10+ years old and had incurred tremendous tech debt over countless Android platform releases and feature updates." In 2012, Google began decoupling certain aspects of its Android operating system (particularly its core applications) so they could be updated through the Google Play store independently of the OS. One of those components, Google Play Services, is a closed-source system-level process providing APIs for Google services, installed automatically on nearly all devices running Android 2.2 "Froyo" and higher. With these changes, Google can add new system functionality through Play Services and update apps without having to distribute an upgrade to the operating system itself. As a result, Android 4.2 and 4.3 "Jelly Bean" contained relatively fewer user-facing changes, focusing more on minor changes and platform improvements.
On Monday, several applications that enable tethering were removed from the Android Market catalog because they were in violation of T-Mobile's terms of service in the US. Based on Android's Developer Distribution Agreement (section 7.2), we remove applications from the Android Market catalog that violate the terms of service of a carrier or manufacturer. We inadvertently unpublished the applications for all carriers, and today we have corrected the problem so that all Android Market users outside the T-Mobile US network will now have access to the applications. We have notified the affected developers. In April 2011, Google removed the Grooveshark app from the store due to unspecified policy violations. CNET noted that the removal came "after some of the top music labels have accused the service of violating copyright law". TechCrunch wrote approximately two weeks later that Grooveshark had returned to Android, "albeit not through the official App Market", but rather "Playing on Android's ability to install third-party applications through the browser, Grooveshark has taken on the responsibility of distributing the application themselves". In May 2011, Google banned the account of the developer of several video game emulators. Neither Google nor the developer publicly revealed the reason for the ban. In March 2013, Google began to pull ad blocking apps from the Google Play Store, per section 4.4 of the developers' agreement, which prohibits apps that interfere with servers and services. Apps that exempt themselves from power management policies introduced on Android Marshmallow without being "adversely affected" by them are banned. In July 2018, Google banned additional categories of apps, including those that perform cryptocurrency mining on-device, apps that "facilitate the sale of explosives, firearms, ammunition, or certain firearms accessories", are only used to present ads, contain adult content but are aimed towards children, "multiple apps with highly similar content and user experience," and "apps that are created by an automated tool, wizard service, or based on templates and submitted to Google Play by the operator of that service on behalf of other persons." In 2022, two Iranian state-supported ridesharing apps and three messenger apps were deleted through Play Protect for being malware and spyware.
Malware (a portmanteau of malicious software) is any software intentionally designed to cause disruption or destruction to a computer, server, client, or computer network, leak private information, gain unauthorized access to information or systems, deprive access to information, or interfere with the user's computer security and privacy without their knowledge. Researchers tend to classify malware into one or more sub-types (i.e. computer viruses, worms, Trojan horses, logic bombs, ransomware, spyware, adware, rogue software, wipers and keyloggers). Malware poses serious threats to individuals and businesses on the Internet. According to Symantec's 2018 Internet Security Threat Report (ISTR), the number of malware variants increased to 669,947,865 in 2017, which is twice as many malware variants as in 2016. Cybercrime, which includes malware attacks as well as other crimes committed by computer, was predicted to cost the global economy US$6 trillion in 2021, and is increasing at a rate of 15% per year. Since 2021, malware has been designed to target computer systems that run critical infrastructure such as the electricity distribution network. The defense strategies against malware differ according to its type, but most can be prevented by installing antivirus software or firewalls, applying regular patches, securing networks, creating backups, and isolating infected systems. Malware can be designed to evade antivirus software detection algorithms.
The notion of a self-reproducing computer program can be traced back to initial theories about the operation of complex automata. John von Neumann showed that in theory a program could reproduce itself. This constituted a plausibility result in computability theory. Fred Cohen experimented with computer viruses and confirmed Neumann's postulate and investigated other properties of malware such as detectability and self-obfuscation using rudimentary encryption. His 1987 doctoral dissertation was on the subject of computer viruses. The combination of cryptographic technology as part of the payload of the virus, exploiting it for attack purposes was initialized and investigated from the mid-1990s, and includes initial ransomware and evasion ideas. Before Internet access became widespread, viruses spread on personal computers by infecting executable programs or boot sectors of floppy disks. By inserting a copy of itself into the machine code instructions in these programs or boot sectors, a virus causes itself to be run whenever the program is run or the disk is booted. Early computer viruses were written for the Apple II and Mac, but they became more widespread with the dominance of the IBM PC and MS-DOS. The first IBM PC virus in the wild was a boot sector virus dubbed (c)Brain, created in 1986 by the Farooq Alvi brothers in Pakistan. Malware distributors would trick the user into booting or running from an infected device or medium. For example, a virus could make an infected computer add autorunnable code to any USB stick plugged into it. Anyone who then attached the stick to another computer set to autorun from USB would in turn become infected, and also pass on the infection in the same way. Older email software would automatically open HTML email containing potentially malicious JavaScript code. Users may also execute disguised malicious email attachments. The 2018 Data Breach Investigations Report by Verizon, cited by CSO Online, states that emails are the primary method of malware delivery, accounting for 96% of malware delivery around the world. The first worms, network-borne infectious programs, originated not on personal computers, but on multitasking Unix systems. The first well-known worm was the Morris worm of 1988, which infected SunOS and VAX BSD systems. Unlike a virus, this worm did not insert itself into other programs. Instead, it exploited security holes (vulnerabilities) in network server programs and started itself running as a separate process. This same behavior is used by today's worms as well. With the rise of the Microsoft Windows platform in the 1990s, and the flexible macros of its applications, it became possible to write infectious code in the macro language of Microsoft Word and similar programs. These macro viruses infect documents and templates rather than applications (executables), but rely on the fact that macros in a Word document are a form of executable code. Many early infectious programs, including the Morris Worm, the first internet worm, were written as experiments or pranks. Today, malware is used by both black hat hackers and governments to steal personal, financial, or business information. Today, any device that plugs into a USB port – even lights, fans, speakers, toys, or peripherals such as a digital microscope – can be used to spread malware. Devices can be infected during manufacturing or supply if quality control is inadequate.
A computer virus is software usually hidden within another seemingly harmless program that can produce copies of itself and insert them into other programs or files, and that usually performs a harmful action (such as destroying data). They have been likened to biological viruses. An example of this is a portable execution infection, a technique, usually used to spread malware, that inserts extra data or executable code into PE files. A computer virus is software that embeds itself in some other executable software (including the operating system itself) on the target system without the user's knowledge and consent and when it is run, the virus is spread to other executable files.
A worm is a stand-alone malware software that actively transmits itself over a network to infect other computers and can copy itself without infecting files. These definitions lead to the observation that a virus requires the user to run an infected software or operating system for the virus to spread, whereas a worm spreads itself. Once malicious software is installed on a system, it is essential that it stays concealed, to avoid detection. Software packages known as rootkits allow this concealment, by modifying the host's operating system so that the malware is hidden from the user. Rootkits can prevent a harmful process from being visible in the system's list of processes, or keep its files from being read. Some types of harmful software contain routines to evade identification or removal attempts, not merely to hide themselves. An early example of this behavior is recorded in the Jargon File tale of a pair of programs infesting a Xerox CP-V time sharing system: Each ghost-job would detect the fact that the other had been killed, and would start a new copy of the recently stopped program within a few milliseconds. The only way to kill both ghosts was to kill them simultaneously (very difficult) or to deliberately crash the system.
A backdoor is a broad term for a computer program that allows an attacker persistent unauthorised remote access to a victim's machine often without their knowledge. The attacker typically uses another attack (such as a trojan, worm or virus) to bypass authentication mechanisms usually over an unsecured network such as the Internet to install the backdoor application. A backdoor can also be a side effect of a software bug in legitimate software that is exploited by an attacker to gain access to a victim's computer or network. The idea has often been suggested that computer manufacturers preinstall backdoors on their systems to provide technical support for customers, but this has never been reliably verified. It was reported in 2014 that US government agencies had been diverting computers purchased by those considered "targets" to secret workshops where software or hardware permitting remote access by the agency was installed, considered to be among the most productive operations to obtain access to networks around the world. Backdoors may be installed by Trojan horses, worms, implants, or other methods.
A Trojan horse misrepresents itself to masquerade as a regular, benign program or utility in order to persuade a victim to install it. A Trojan horse usually carries a hidden destructive function that is activated when the application is started. The term is derived from the Ancient Greek story of the Trojan horse used to invade the city of Troy by stealth. Trojan horses are generally spread by some form of social engineering, for example, where a user is duped into executing an email attachment disguised to be unsuspicious, (e.g., a routine form to be filled in), or by drive-by download. Although their payload can be anything, many modern forms act as a backdoor, contacting a controller (phoning home) which can then have unauthorized access to the affected computer, potentially installing additional software such as a keylogger to steal confidential information, cryptomining software or adware to generate revenue to the operator of the trojan. While Trojan horses and backdoors are not easily detectable by themselves, computers may appear to run slower, emit more heat or fan noise due to heavy processor or network usage, as may occur when cryptomining software is installed. Cryptominers may limit resource usage or only run during idle times in an attempt to evade detection. Unlike computer viruses and worms, Trojan horses generally do not attempt to inject themselves into other files or otherwise propagate themselves. Modern Trojans are often disguised within legitimate-looking applications, making them particularly effective at bypassing basic user awareness and simple antivirus measures. In spring 2017, Mac users were hit by the new version of Proton Remote Access Trojan (RAT) trained to extract password data from various sources, such as browser auto-fill data, the Mac-OS keychain, and password vaults.
Droppers are a sub-type of Trojans that solely aim to deliver malware upon the system that they infect with the desire to subvert detection through stealth and a light payload. It is important not to confuse a dropper with a loader or stager. A loader or stager will merely load an extension of the malware (for example a collection of malicious functions through reflective dynamic link library injection) into memory. The purpose is to keep the initial stage light and undetectable. A dropper merely downloads further malware to the system.
Ransomware prevents a user from accessing their files until a ransom is paid. There are two variations of ransomware, being crypto ransomware and locker ransomware. Locker ransomware just locks down a computer system without encrypting its contents, whereas crypto ransomware locks down a system and encrypts its contents. For example, programs such as CryptoLocker encrypt files securely, and only decrypt them on payment of a substantial sum of money. Lock-screens, or screen lockers is a type of "cyber police" ransomware that blocks screens on Windows or Android devices with a false accusation in harvesting illegal content, trying to scare the victims into paying up a fee. Jisut and SLocker impact Android devices more than other lock-screens, with Jisut making up nearly 60 percent of all Android ransomware detections.
Encryption-based ransomware, like the name suggests, is a type of ransomware that encrypts all files on an infected machine. These types of malware then display a pop-up ad informing the user that their files have been encrypted and that they must pay (usually in Bitcoin) to recover them. Some examples of encryption-based ransomware are CryptoLocker and WannaCry. According to Microsoft's Digital Crimes Unit in May 2025, Lumma Stealer ("Lumma"), which steals passwords, credit cards, bank accounts, and cryptocurrency wallets, is the favored info-stealing malware used by hundreds of cyber threat actors and enables criminals to empty bank accounts, hold schools for ransom, and disrupt critical services.
Grayware is any unwanted application or file that can worsen the performance of computers and may cause security risks but which there is insufficient consensus or data to classify them as malware. Types of grayware typically include spyware, adware, fraudulent dialers, joke programs ("jokeware") and remote access tools. For example, at one point, Sony BMG compact discs silently installed a rootkit on purchasers' computers with the intention of preventing illicit copying.
2. System Architecture & Core Working Principles Real-time protection: They can provide real time protection against the installation of malware software on a computer. This type of malware protection works the same way as that of antivirus protection in that the anti-malware software scans all incoming network data for malware and blocks any threats it comes across. Removal: Anti-malware software programs can be used solely for detection and removal of malware software that has already been installed onto a computer. This type of anti-malware software scans the contents of the Windows registry, operating system files, and installed programs on a computer and will provide a list of any threats found, allowing the user to choose which files to delete or keep, or to compare this list to a list of known malware components, removing files that match. Sandboxing: Sandboxing confines applications within a controlled environment, restricting their operations and isolating them from other applications on the host while limiting access to system resources. Browser sandboxing isolates web processes to prevent malware and exploits, enhancing security.
Further Reading: Research Papers and Documents about Malware on IDMARCH (Int. Digital Media Archive) Archived 22 September 2016 at the Wayback Machine Advanced Malware Cleaning – a Microsoft video Antivirus software (abbreviated to AV software), also known as anti-malware, is software intended to prevent, detect, and remove malware. Antivirus software was originally developed to detect and remove computer viruses, hence the name.
However, with the proliferation of other malware, antivirus software started to protect against other computer threats. Some products also include protection from malicious URLs, spam, and phishing. Powerful macros used in word processor applications, such as Microsoft Word, presented a risk. Virus writers could use the macros to write viruses embedded within documents. This meant that computers could now also be at risk from infection by opening documents with hidden attached macros. The possibility of embedding executable objects inside otherwise non-executable file formats can make opening those files a risk. Later email programs, in particular Microsoft's Outlook Express and Outlook, were vulnerable to viruses embedded in the email body itself. A user's computer could be infected by just opening or previewing a message. In 2005, F-Secure was the first security firm that developed an Anti-Rootkit technology, called BlackLight. Because most users are usually connected to the Internet on a continual basis, Jon Oberheide first proposed a Cloud-based antivirus design in 2008. In February 2008 McAfee Labs added the industry-first cloud-based anti-malware functionality to VirusScan under the name Artemis. It was tested by AV-Comparatives in February 2008 and officially unveiled in August 2008 in McAfee VirusScan. Cloud AV created problems for comparative testing of security software – part of the AV definitions was out of testers control (on constantly updated AV company servers) thus making results non-repeatable. As a result, Anti-Malware Testing Standards Organisation (AMTSO) started working on method of testing cloud products which was adopted on May 7, 2009. In 2011, AVG introduced a similar cloud service, called Protective Cloud Technology.
Sandbox detection: a particular behavioural-based detection technique that, instead of detecting the behavioural fingerprint at run time, it executes the programs in a virtual environment, logging what actions the program performs. Depending on the actions logged which can include memory usage and network accesses, the antivirus engine can determine if the program is malicious or not. If not, then, the program is executed in the real environment. Although this technique has shown to be quite effective, given its heaviness and slowness, it is rarely used in end-user antivirus solutions. Data mining techniques: one of the latest approaches applied in malware detection. Data mining and machine learning algorithms are used to try to classify the behaviour of a file (as either malicious or benign) given a series of file features, that are extracted from the file itself.
Anti-virus software can attempt to scan for rootkits. A rootkit is a type of malware designed to gain administrative-level control over a computer system without being detected. Rootkits can change how the operating system functions and in some cases can tamper with the anti-virus program and render it ineffective. Rootkits are also difficult to remove, in some cases requiring a complete re-installation of the operating system.
Some apparent antivirus programs are actually malware masquerading as legitimate software, such as WinFixer, MS Antivirus, and Mac Defender. May 2007: a faulty virus signature issued by Symantec mistakenly removed essential operating system files, leaving thousands of PCs unable to boot. May 2007: the executable file required by Pegasus Mail on Windows was falsely detected by Norton AntiVirus as being a Trojan and it was automatically removed, preventing Pegasus Mail from running. Norton AntiVirus had falsely identified three releases of Pegasus Mail as malware, and would delete the Pegasus Mail installer file when that happened. In response to this Pegasus Mail stated: On the basis that Norton/Symantec has done this for every one of the last three releases of Pegasus Mail, we can only condemn this product as too flawed to use, and recommend in the strongest terms that our users cease using it in favour of alternative, less buggy anti-virus packages. April 2010: McAfee VirusScan detected svchost.exe, a normal Windows binary, as a virus on machines running Windows XP with Service Pack 3, causing a reboot loop and loss of all network access. December 2010: a faulty update on the AVG anti-virus suite damaged 64-bit versions of Windows 7, rendering it unable to boot, due to an endless boot loop created. October 2011: Microsoft Security Essentials (MSE) removed the Google Chrome web browser, rival to Microsoft's own Internet Explorer. MSE flagged Chrome as a Zbot banking trojan. September 2012: Sophos' anti-virus suite identified various update-mechanisms, including its own, as malware. If it was configured to automatically delete detected files, Sophos Antivirus could render itself unable to update and required manual intervention to fix the problem. September 2017: the Google Play Protect anti-virus started identifying Motorola's Moto G4 Bluetooth application as malware, causing Bluetooth functionality to become disabled.
September 2022: Microsoft Defender flagged all Chromium based web browsers and Electron based apps like WhatsApp, Discord, Spotify as a severe threat. It's something that they miss a lot of the time because this type of [ransomware virus] comes from sites that use a polymorphism, which means they basically randomize the file they send you and it gets by well-known antivirus products very easily. I've seen people firsthand getting infected, having all the pop-ups and yet they have antivirus software running and it's not detecting anything. It actually can be pretty hard to get rid of, as well, and you're never really sure if it's really gone. When we see something like that usually we advise to reinstall the operating system or reinstall backups. A proof of concept virus has used the Graphics Processing Unit (GPU) to avoid detection from anti-virus software. The potential success of this involves bypassing the CPU in order to make it much harder for security researchers to analyse the inner workings of such malware.
Antivirus software running on individual computers is the most common method employed of guarding against malware, but it is not the only solution. Other solutions can also be employed by users, including Unified Threat Management (UTM), hardware and network firewalls, Cloud-based antivirus, online scanners, and Content Disarm & Reconstruction (CDR). Virus removal tools are available to help remove stubborn infections or a certain type of infection. Examples include Windows Malicious Software Removal Tool, Kaspersky Virus Removal Tool, and Sophos Scan & Clean. It is also worth noting that sometimes antivirus software can produce a false-positive result, indicating an infection where there is none. A rescue disk that is bootable, such as a CD or USB storage device, can be used to run antivirus software outside of the installed operating system in order to remove infections while they are dormant. A bootable rescue disk can be useful when, for example, the installed operating system is no longer bootable or has malware that is resisting all attempts to be removed by the installed antivirus software. Examples of software that can be used on a bootable rescue disk include the Kaspersky Rescue Disk, Trend Micro Rescue Disk, and Comodo Rescue Disk.
Effective in 2026, to align with our trunk stable development model and ensure platform stability for the ecosystem, we will publish source code to AOSP in Q2 and Q4. For building and contributing to AOSP, use android-latest-release . The android-latest-release manifest branch will always reference the most recent release pushed to AOSP. For more information, see Changes to AOSP .
At the operating system level, the Android platform provides the security of the Linux kernel, as well as a secure inter-process communication (IPC) facility to enable secure communication between apps running in different processes. These security features at the OS level ensure that even native code is constrained by the Application Sandbox. Whether that code is the result of included app behavior or an exploitation of an app vulnerability, the system is designed to prevent the rogue app from harming other apps, the Android system, or the device itself. See the Android Compatibility Definition Document (CDD) for required settings.
The foundation of the Android platform is the Linux kernel. The Linux kernel has been in widespread use for years, and is used in millions of security-sensitive environments. Through its history of constantly being researched, attacked, and fixed by thousands of developers, Linux has become a stable and secure kernel trusted by many corporations and security professionals.
As the base for a mobile computing environment, the Linux kernel provides Android with several key security features, including: As a multiuser operating system, a fundamental security objective of the Linux kernel is to isolate user resources from one another. The Linux security philosophy is to protect user resources from one another, Linux: Android's app security is enforced by the Application Sandbox, which isolates apps from each other and protects apps and the system from malicious apps. For more details, see Application Sandbox .
The various integrity protected partitions contain Android's kernel as well as the operating system libraries, app runtime, app framework, and apps. This partition is set to read-only. When a user boots the device into safe mode, third-party apps may be launched manually by the device owner but aren't launched by default. In a UNIX-style environment, file system permissions ensure that one user can't alter or read another user's files. In the case of Android, each app runs as its own user. Unless the developer explicitly shares files with other apps, files created by one app can't be read or altered by another app.
Android uses Security-Enhanced Linux (SELinux) to apply access control policies and establish mandatory access control (mac) on processes. See Security-Enhanced Linux in Android for details . Android 7.0 and later supports strictly enforced Verified Boot, which means compromised devices can't boot. Verified Boot guarantees the integrity of the device software starting from a hardware root of trust up to the system partition. During boot, each stage cryptographically verifies the integrity and authenticity of the next stage before executing it. See Verified boot for more details.
Android provides a set of cryptographic APIs for use by apps. These include implementations of standard and commonly used cryptographic primitives such as AES, RSA, DSA, and SHA. Additionally, APIs are provided for higher level protocols such as SSL and HTTPS. Android 4.0 introduced the KeyChain class to allow apps to use the system credential storage for private keys and certificate chains.
By default, on Android only the kernel and a small subset of the core services run with root permissions. SELinux still constrains user space processes running as root. Verified Boot prevents a user or service with root permissions from permanently modifying the operating system. The ability to modify an Android device they own is important to developers working with the Android platform. On many Android devices, users have the ability to unlock the bootloader in order to allow installation of an alternate operating system.
These alternate operating systems may allow an owner to gain root access for purposes of debugging apps and system components or to access features not presented to apps by Android APIs. On some devices, a person with physical control of a device and a USB cable is able to install a new operating system that provides root privileges to the user. To protect any existing user data from compromise the bootloader unlock mechanism requires that the bootloader erase any existing user data as part of the unlock step. Root access gained via exploiting a kernel bug or security hole can bypass this protection.
Encrypting data with a key stored on-device doesn't protect the app data from root users on rooted devices. Apps can add a layer of data protection using encryption with a key stored off-device, such as on a server or a user password. This approach can provide temporary protection while the key isn't present, but at some point the key must be provided to the app and it then becomes accessible to root users.
3. Software Implementation, Frameworks & Protocols A more robust approach to protecting data from root users is through the use of hardware solutions. OEMs may choose to implement hardware solutions that limit access to specific types of content such as DRM for video playback, or the NFC-related trusted storage for Google wallet. In the case of a lost or stolen device, storage encryption ensures that user data can't be accessed without knowing the user's lockscreen credential.
The CDD requires that all devices that launch with Android 10 or higher, and most devices that launch with Android 6.0 or higher, enable storage encryption out of the box. Android's current implementation of storage encryption is file-based encryption in combination with metadata encryption . File-based encryption transparently encrypts file contents and names on the userdata partition, using different keys for different directories. It provides credential-encrypted and device-encrypted storage directories for each user, including work profiles.
Metadata encryption complements file-based encryption. It encrypts all blocks on the userdata partition that aren't already encrypted by file-based encryption, using a key not bound to any user's lockscreen credential but still protected by Verified Boot. Android can be configured to verify a user-supplied lockscreen credential (PIN, password, or pattern) prior to providing access to a device. In addition to preventing unauthorized use of the device, the lockscreen credential protects the cryptographic key for credential-encrypted data. Use of a lockscreen credential and/or credential complexity rules can be required by a device administrator.
Android 2.2 and later provide the Android Device Administration API, which provides device administration features at the system level. For example, the built-in Android email app uses the APIs to improve Exchange support. Through the email app, Exchange administrators can enforce lockscreen credential policies — including alphanumeric passwords or numeric PINs — across devices. Administrators can also remotely wipe (that is, restore factory defaults on) lost or stolen handsets.
Content and code samples on this page are subject to the licenses described in the Content License . Java and OpenJDK are trademarks or registered trademarks of Oracle and/or its affiliates. Effective in 2026, to align with our trunk stable development model and ensure platform stability for the ecosystem, we will publish source code to AOSP in Q2 and Q4. For building and contributing to AOSP, use android-latest-release . The android-latest-release manifest branch will always reference the most recent release pushed to AOSP. For more information, see Changes to AOSP .
The Android Security Team regularly receives requests for information about preventing potential security issues on Android devices. We also occasionally spot check devices and let device manufacturers and affected partners know of potential issues. This page provides security best practices based on our experiences, extending the Designing for Security documentation we've provided for developers and includes details unique to building or installing system-level software on devices.
To facilitate adoption of these best practices, where possible the Android Security Team incorporates tests into the Android Compatibility Test Suite (CTS) and Android Lint . We encourage device implementers to contribute tests that can help other Android users (view security-related tests at root/cts/tests/tests/security/src/android/security/cts ). Source code review can detect a broad range of security issues, including those identified in this document. Android strongly encourages both manual and automated source code review. Best practices: Automated testing can detect a broad range of security issues, including several issues discussed below. Best practices: The signature of the system image is critical for determining the integrity of the device. Best practices: App signatures play an important role in device security and are used for permissions checks as well as software updates.
When selecting a key to use for signing apps, it is important to consider whether an app will be available only on a single device or common across multiple devices. Best practices: Google Play provides device manufacturers the ability to update apps without performing a complete system update. This can expedite response to security issues and delivery of new features, as well as provide a way to ensure your app has a unique package name. Best practices: External parties must have the ability to contact device manufacturers about device-specific security issues. We recommend creating a publicly accessible email address for managing security incidents. Best practices: Root processes are the most frequent target of privilege escalation attacks, so reducing the number of root processes reduces risk of privilege escalation. CTS includes an informational test that lists root processes. Best practices: In general, pre-installed apps shouldn't run with the shared system UID. If is it necessary, however, for an app to use the shared UID of system or another privileged service, the app shouldn't export any services, broadcast receivers, or content providers that can be accessed by third-party apps installed by users. Best practices: The Android Application Sandbox provides apps with an expectation of isolation from other processes on the system, including root processes and debuggers. Unless debugging is specifically enabled by the app and the user, no app should violate that expectation. Best practices: New setuid programs shouldn't be accessible by untrusted programs. Setuid programs have frequently been the location of vulnerabilities that can be used to gain root access, so strive to minimize the availability of the setuid program to untrusted apps. Best practices: CTS verifier includes an informational test listing SUID files; some setuid files aren't permitted per CTS tests.
CTS tests fail when a device is listening on any port, on any interface. In the event of a failure, Android verifies the following best practices are in use: Logging data increases the risk of exposure of that data and reduces system performance. Multiple public security incidents have occurred as the result of logging sensitive user data by apps installed by default on Android devices. Best practices: CTS includes tests that check for the presence of potentially sensitive information in the system logs.
World-writable directories can introduce security weaknesses and enable an app to rename trusted files, substitute files, or conduct symlink-based attacks (attackers may use a symlink to a file to trick a trusted program into performing actions it shouldn't). Writable directories can also prevent the uninstall of an app from properly cleaning up all files associated with an app.
As a best practice, directories created by the system or root users should not be world writable. CTS tests help enforce this best practice by testing known directories. 4. Practical Deployment, Analysis & Case Studies Many drivers and services rely on configuration and data files stored in directories such as /system/etc and /data . If these files are processed by a privileged process and are world writable, it is possible for an app to exploit a vulnerability in the process by crafting malicious contents in the world-writable file. Best practices: Any code used by privileged device manufacturer processes must be in /vendor or /system ; these filesystems are mounted read-only on boot. As a best practice, libraries used by system or other highly-privileged apps installed on the device should also be in these filesystems. This can prevent a security vulnerability that could allow an attacker to control the code that a privileged process executes.
Only trusted code should have direct access to drivers. Where possible, the preferred architecture is to provide a single-purpose daemon that proxies calls to the driver and restricts driver access to that daemon. As a best practice, driver device nodes shouldn't be world readable or writable. CTS tests help enforce this best practice by checking for known instances of exposed drivers.
Android debug bridge (adb) is a valuable development and debugging tool, but is designed for use in controlled, secure environments and shouldn't be enabled for general use. Best practices: Many Android devices support unlocking, enabling the device owner to modify the system partition and/or install a custom operating system. Common use cases include installing a third-party ROM and performing systems-level development on the device. For example, a Google Nexus device owner can run fastboot oem unlock to start the unlocking process, which presents the following message to the user: If you unlock the bootloader, you will be able to install custom operating system software on this device.
A custom OS isn't subject to the same testing as the original OS, and can cause your device and installed apps to stop working properly. To prevent unauthorized access to your personal data, unlocking the bootloader will also delete all personal data from your device (a "factory data reset").
Press the Volume Up/Down buttons to select Yes or No. Then press the Power button to continue. As a best practice, unlockable Android devices must securely erase all user data prior to being unlocked. Failure to properly delete all data on unlocking may allow a physically proximate attacker to gain unauthorized access to confidential Android user data. To prevent the disclosure of user data, a device that supports unlocking must implement it properly (we've seen numerous instances where device manufacturers improperly implemented unlocking). A properly implemented unlocking process has the following properties: These requirements ensure that all data is destroyed upon the completion of an unlock operation. Failure to implement these protections is considered a moderate level security vulnerability.
A device that is unlocked may be subsequently relocked using the fastboot oem lock command. Locking the bootloader provides the same protection of user data with the new custom OS as was available with the original device manufacturer OS (e.g. user data will be wiped if the device is unlocked again). Content and code samples on this page are subject to the licenses described in the Content License . Java and OpenJDK are trademarks or registered trademarks of Oracle and/or its affiliates.
This Knowledge Base article describes how to use AppdomeâIIs AI in your CI/CD pipeline to continuously deliver plugins that Detect Rogue Installation in Android apps. A rogue installation occurs when an Android app is installed from an unauthorized or untrusted source, such as a third-party app store, sideloaded APK, or direct download outside of Google Play or other trusted marketplaces. Attackers can use these distribution methods to deliver malicious or repackaged apps containing malware designed to steal credentials, inject malicious code, or bypass security protections. Rogue installations can expose users to threats such as overlay attacks, keylogging, SMS interception, and root exploits, increasing the risk of device compromise, unauthorized app modifications, and fraud. Detecting rogue installations helps organizations ensure that their apps are installed from trusted and authorized sources.
A rogue installation occurs when an Android app is installed from an unauthorized or untrusted source, such as a third-party app store, sideloaded APK, or direct download outside of Google Play or other trusted marketplaces. Attackers can use these distribution methods to deliver malicious or repackaged apps containing malware designed to steal credentials, inject malicious code, or bypass security protections.
Rogue installations can expose users to threats such as overlay attacks, keylogging, SMS interception, and root exploits, increasing the risk of device compromise, unauthorized app modifications, and fraud. Detecting rogue installations helps organizations ensure that their apps are installed from trusted and authorized sources. AppdomeâIIs Detect Rogue Installation feature monitors the installation origin of the protected mobile app to identify when the app is installed from an unauthorized source. It detects sideloaded installations and other unauthorized distribution methods. Developers can use AppdomeâIIs Threat-EventsâI¢ to monitor the installation source of the protected app and configure custom responses when a rogue installation is detected.
AppdomeâIIs Detect Rogue Installation feature monitors the installation origin of the protected mobile app to identify when the app is installed from an unauthorized source. It detects sideloaded installations and other unauthorized distribution methods. Developers can use AppdomeâIIs Threat-EventsâI¢ to monitor the installation source of the protected app and configure custom responses when a rogue installation is detected.
To use AppdomeâIIs mobile app security build system to Detect Rogue Installation , youâIIll need: On Appdome, follow these 3 simple steps to create self-defending Android Apps that Detect Rogue Installation without an SDK or gateway: Follow the steps in Sections 2.2-2.2.2 of this article to add the Detect Rogue Installation feature to your Fusion Set via the Appdome Console.
When you select the Detect Rogue Installation you'll notice that the Fusion Set you created in step 2.1 now bears the icon of the protection category that contains Detect Rogue Installation. Figure 2: Fusion Set that displays the newly added Detect Rogue Installation protection Note: Annotating the Fusion Set to identify the protection(s) selected is optional only (not mandatory).
Figure 4: Selecting Detect Rogue Installation Note: The App Compromise Notification contains an easy to follow default remediation path for the mobile app end user. You can customize this message as required to achieve brand specific support, workflow or other messaging. Figure 4: Selecting Detect Rogue Installation Note: The Appdome Platform displays the Mobile Operation Systems supported by each defense in real-time. For more details, see our OS Support Policy KB .
5. Performance Evaluation & Extended Technical Observations If the Threat-EventsâI¢ setting is not selected. Appdome will detect and defend user and app by enforcing Detect Rogue Installation. When this setting is used, Appdome detects Rogue Installation and passes AppdomeâIIs Threat-EventâI¢ attack intelligence to the appâIIs business logic for processing, enforcement, and user notification. For more information on consuming and using Appdome Threat-EventsâI¢ in the app, see section Using Threat-EventsâI¢ for Detect Rogue Installation Intelligence and Control in Mobile Apps.
When this setting is used, Appdome detects and defends against Rogue Installation (same as Appdome Enforce) and passes AppdomeâIIs Threat-EventâI¢ attack intelligence to the appâIIs business logic for processing. For more information on consuming and using Appdome Threat-EventsâI¢ in the app, see section Using Threat-EventsâI¢ for Detect Rogue Installation Intelligence and Control in Mobile Apps.
Localized Message Option. Allows Appdome users to support global languages in security notifications. After building Detect Rogue Installation, Appdome generates a Certified SecureâI¢ certificate to guarantee that the Detect Rogue Installation protection has been added and is protecting the app. To verify that the Detect Rogue Installation protection has been added to the mobile app, locate the protection in the Certified SecureâI¢ certificate as shown below: Each Certified SecureâI¢ certificate provides DevOps and DevSecOps organizations the entire workflow summary, audit trail of each build, and proof of protection that Detect Rogue Installation has been added to each Android app. Certified Secure provides instant and in-line DevSecOps compliance certification that Detect Rogue Installation and other mobile app security features are in each build of the mobile app.
DefenseOS™ manages and coordinates Appdome defense capabilities in protected mobile apps. To learn more about DefenseOS and its runtime modules, see Understanding DefenseOS™ . Using Threat-EventsâI¢ for Rogue Installation Intelligence and Control in Android Apps Appdome Threat-EventsâI¢ provides consumable in-app mobile app attack intelligence and defense control when Rogue Installation is detected. To consume and use Threat-EventsâI¢ for Rogue Installation in Android Apps, use registerReceiver in the Application OnCreate, and the code samples for Threat-EventsâI¢ for Rogue Installation shown below.
With Threat-EventsâI¢ enabled (turned ON), Android developers can get detailed attack intelligence and granular defense control in Android applications and create amazing user experiences for all mobile end users when Rogue Installation is detected. The following is a code sample for native Android apps, which uses all values in the specification above for Detect Rogue Installation: Important! Replace all placeholder instances of
Using Appdome, there are no development or coding prerequisites to build secured Android Apps by using Detect Rogue Installation. There is no SDK and no library to code or implement in the app and no gateway to deploy in your network. All protections are built into each app and the resulting app is self-defending and self-protecting. After successfully securing your app by using Appdome, there are several available options to complete your project, depending on your app lifecycle or workflow. These include: If you have any questions, please send them our way at support.appdome.com or via the chat window on the Appdome platform.
Thanks for visiting Appdome ! Our mission is to secure every app on the planet by making mobile app security easy. We hope weâIIre living up to the mission with your project. This Knowledge Base article describes how to use AppdomeâIIs AI in your CI/CD pipeline to continuously deliver plugins that Detect Unknown Sources in Android apps.
Android Unknown Sources refers to the ability to install apps from sources outside of Google Play or other trusted marketplaces, such as third-party app stores, sideloaded APKs, or direct downloads. Enabling installations from unknown sources can increase exposure to malicious or repackaged apps containing malware designed to steal credentials, inject malicious code, or bypass security protections. These apps may be used to perform attacks such as overlay attacks, keylogging, SMS interception, and root exploits, increasing the risk of device compromise, unauthorized modifications, and fraud. Detecting when installation from unknown sources is enabled helps organizations maintain stronger control over app installation and distribution, supporting security practices relevant to standards and regulations such as PCI DSS, PSD2, and GDPR.
Android Unknown Sources refers to the ability to install apps from sources outside of Google Play or other trusted marketplaces, such as third-party app stores, sideloaded APKs, or direct downloads. Enabling installations from unknown sources can increase exposure to malicious or repackaged apps containing malware designed to steal credentials, inject malicious code, or bypass security protections. These apps may be used to perform attacks such as overlay attacks, keylogging, SMS interception, and root exploits, increasing the risk of device compromise, unauthorized modifications, and fraud.
Detecting when installation from unknown sources is enabled helps organizations maintain stronger control over app installation and distribution, supporting security practices relevant to standards and regulations such as PCI DSS, PSD2, and GDPR. AppdomeâIIs Detect Unknown Sources feature monitors device settings to determine whether installing apps from unknown sources is enabled. This helps identify devices that permit apps to be installed through untrusted distribution channels.
Developers can use AppdomeâIIs Threat-EventsâI¢ to monitor when installation from unknown sources is enabled and configure custom responses when this condition is detected. AppdomeâIIs Detect Unknown Sources feature monitors device settings to determine whether installing apps from unknown sources is enabled. This helps identify devices that permit apps to be installed through untrusted distribution channels.
Developers can use AppdomeâIIs Threat-EventsâI¢ to monitor when installation from unknown sources is enabled and configure custom responses when this condition is detected. To use AppdomeâIIs mobile app security build system to Detect Unknown Sources , youâIIll need: On Appdome, follow these 3 simple steps to create self-defending Android Apps that Detect Unknown Sources without an SDK or gateway: Follow the steps in Sections 2.2-2.2.2 of this article to add the Detect Unknown Sources feature to your Fusion Set via the Appdome Console.
When you select the Detect Unknown Sources you'll notice that the Fusion Set you created in step 2.1 now bears the icon of the protection category that contains Detect Unknown Sources. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Google%20Play • https://en.wikipedia.org/wiki/Malware • https://en.wikipedia.org/wiki/Antivirus%20software • https://source.android.com/docs/security/overview/kernel-security • https://source.android.com/docs/security/overview/implement • https://www.appdome.com/how-to/account-takeover-prevention/social-engineering-prevention/detect-rogue-installation/ • https://www.appdome.com/how-to/mobile-app-security/jailbreak-root-detection/detect-unknown-sources-protect-android-apps/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Rogue Application Installer Detection Tool On Android.
[*] Metasploit Scan Running on Target Subnet for Rogue Application Installer Detection Tool On Android... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |