Complete Technical Paper Content — Rogue Beacon Detection Tool In Wireless Sensor Networks
Overview & System Context
Rogue Beacon Detection Tool In Wireless Sensor Networks: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~8512 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Wi-Fi positioning system (WPS, WiPS or WFPS) is a geolocation system that uses the characteristics of nearby WiIFi access points to discover where a device is located. It is used where satellite navigation such as GPS is inadequate due to various causes including multipath and signal blockage indoors, or where acquiring a satellite fix would take too long. Such systems include assisted GPS, urban positioning services through hotspot databases, and indoor positioning systems. Wi-Fi positioning takes advantage of the rapid growth in the early 21st century of wireless access points in urban areas. The most common technique for positioning using wireless access points is based on a rough proxy for the strength of the received signal (received signal strength indicator, or RSSI) and the method of "fingerprinting". Typically a wireless access point is identified by its SSID and MAC address, and these data are compared to a database of supposed locations of access points so identified. The accuracy depends on the accuracy of the database (e.g. if an access point has moved, its entry is inaccurate), and the precision depends on the number of discovered nearby access points with (accurate) entries in the database and the precisions of those entries. The access point location database gets filled by correlating mobile device location data (determined by other systems, such as Galileo or GPS) with WiIFi access point MAC addresses. The possible signal fluctuations that may occur can increase errors and inaccuracies in the path of the user. To minimize fluctuations in the received signal, there are certain techniques that can be applied to filter the noise. In the case of low precision, some techniques have been proposed to merge the Wi-Fi traces with other data sources such as geographical information and time constraints (i.e., time geography).
With the advent of MIMO Wi-Fi interfaces, which use multiple antennas, it is possible to estimate the AoA of the multipath signals received at the antenna arrays in the access points, and apply triangulation to calculate the location of client devices. SpotFi, ArrayTrack and LTEye are proposed solutions which employ this kind of technique. Typical computation of the AoA is done with the MUSIC algorithm. Assuming an antenna array of M {\displaystyle M} antennas equally spaced by a distance of d {\displaystyle d} and a signal arriving at the antenna array through L {\displaystyle L} propagation paths, an additional distance of d sin I θ {\displaystyle d\sin \theta } is traveled by the signal to reach the second antenna of the array. Considering that the k {\displaystyle k} -th propagation path arrives with angle θ k {\displaystyle \theta _{k}} with respect to the normal of the antenna array of the access point, γ k {\displaystyle \gamma _{k}} is the attenuation experienced at any antenna of the array.
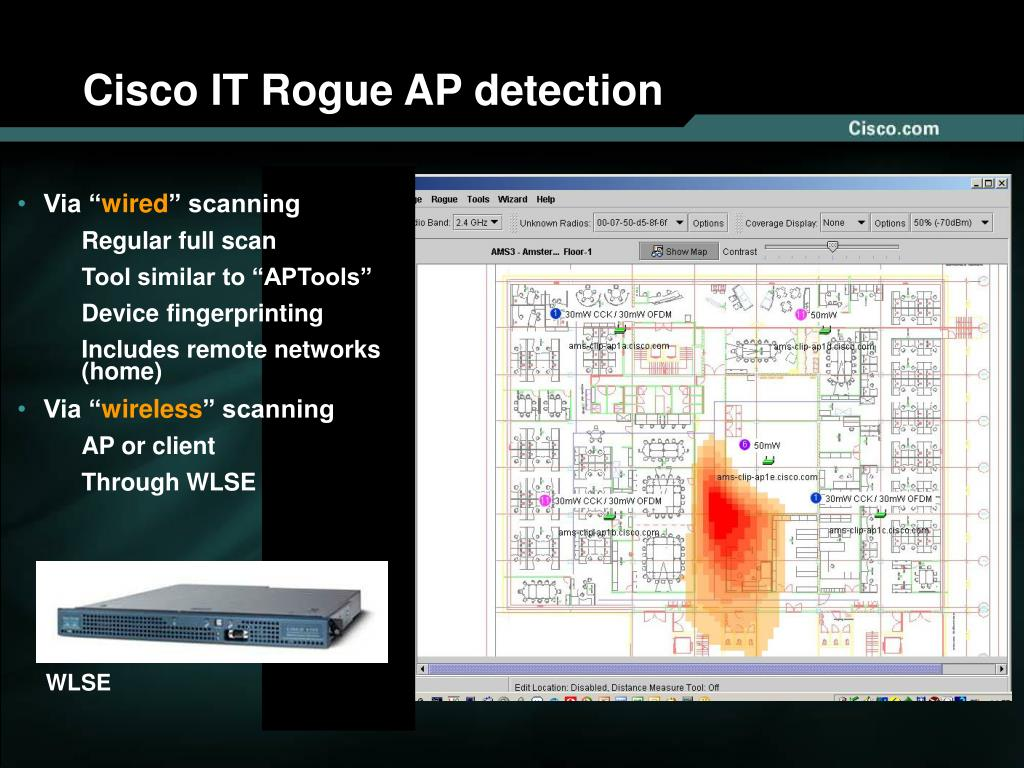
The attenuation is the same in every antenna, except for a phase shift which changes for every antenna due to the extra distance traveled by the signal. This means that the signal arrives with an additional phase of − 2 π ⋅ d ⋅ sin I ( θ ) ⋅ ( f / c ) ⋅ ( 2 − 1 ) {\displaystyle -2\pi \cdot d\cdot \sin(\theta )\cdot (f/c)\cdot (2-1)} − 2 π ⋅ d ⋅ sin I ( θ ) ⋅ ( f / c ) ⋅ ( m − 1 ) {\displaystyle -2\pi \cdot d\cdot \sin(\theta )\cdot (f/c)\cdot (m-1)} Figure 1: PPT - Wireless Security Primer PowerPoint Presentation, free download ...
at the m {\displaystyle m} -th antenna. Therefore, the following complex exponential can be used as a simplified representation of the phase shifts experienced by each antenna as a function of the AoA of the propagation path: ϕ ( θ k ) = exp I ( − j ⋅ 2 π ⋅ d ⋅ sin I ( θ k ) ⋅ f / c ) {\displaystyle \phi (\theta _{k})=\exp(-j\cdot 2\pi \cdot d\cdot \sin(\theta _{k})\cdot f/c)} The AoA can then be expressed as the vector a → ( θ k ) γ k {\displaystyle {\vec {a}}(\theta _{k})\gamma _{k}} of received signals due to the k {\displaystyle k} -th propagation path, where a → ( θ k ) {\displaystyle {\vec {a}}(\theta _{k})} is the steering vector and given by: a → ( θ k ) = [ 1 , ϕ ( θ k ) , … , ϕ ( θ k ) M − 1 ] T {\displaystyle {\vec {a}}(\theta _{k})=[1,\ \phi (\theta _{k}),\ \dots ,\ \phi (\theta _{k})^{M-1}]^{T}} There is one steering vector for each propagation path, and the steering matrix A {\displaystyle \mathbf {A} } (of dimensions M ⋅ L {\displaystyle M\cdot L} ) is then defined as: A = [ a → ( θ 1 ) , … , a → ( θ L ) ] {\displaystyle \mathbf {A} =[{\vec {a}}(\theta _{1}),\dots ,{\vec {a}}(\theta _{L})]} and the received signal vector x → {\displaystyle {\vec {x}}} is: x → = A Γ → {\displaystyle {\vec {x}}=\mathbf {A} {\vec {\Gamma }}} where Γ → = [ γ → 1 … γ → L ] {\displaystyle {\vec {\Gamma }}=[{\vec {\gamma }}_{1}\dots {\vec {\gamma }}_{L}]} is the vector complex attenuations along the L {\displaystyle L} paths. OFDM transmits data over multiple different sub carriers, so the measured received signals x → {\displaystyle {\vec {x}}} corresponding to each sub carrier form the matrix X {\displaystyle \mathbf {X} } expressed as: X = [ x → 1 … x → L ] = A [ Γ → 1 … Γ → L ] = A F {\displaystyle \mathbf {X} =[{\vec {x}}_{1}\dots {\vec {x}}_{L}]=\mathbf {A} [{\vec {\Gamma }}_{1}\dots {\vec {\Gamma }}_{L}]=\mathbf {AF} } The matrix X {\displaystyle \mathbf {X} } is given by the channel state information (CSI) matrix which can be extracted from modern wireless cards with special tools such as the Linux 802.11n CSI Tool. This is where the MUSIC algorithm is applied in, first by computing the eigenvectors of X X H {\displaystyle \mathbf {X} \mathbf {X} ^{H}} (where X H {\displaystyle \mathbf {X} ^{H}} is the conjugate transpose of X {\displaystyle \mathbf {X} } ) and using the vectors corresponding to eigenvalue zero to calculate the steering vectors and the matrix A {\displaystyle \mathbf {A} } . The AoAs can then be deduced from this matrix and used to estimate the position of the client device through triangulation. Though this technique is usually more accurate than others, it may require special hardware in order to be deployed, such as an array of six to eight antennas or rotating antennas. SpotFi proposes the use of a superresolution algorithm which takes advantage of the number of measurements taken by each of the antennas of the Wi-Fi cards with only three antennas, and also incorporates ToF-based localization to improve its accuracy.
Time of flight (ToF) localization approach takes timestamps provided by the wireless interfaces to calculate the ToF of signals and then use this information to estimate the distance and relative position of one client device with respect to access points. The granularity of such time measurements is in the order of nanoseconds and systems which use this technique have reported localization errors in the order of 2m. Typical applications for this technology are tagging and locating assets in buildings, for which room-level accuracy (~3m) is usually enough. The time measurements taken at the wireless interfaces are based on the fact that RF waves travel close to the speed of light, which remains nearly constant in most propagation media in indoor environments. Therefore, the signal propagation speed (and consequently the ToF) is not affected so much by the environment as the RSSI measurements are. Unlike traditional ToF-based echo techniques, such as those used in RADAR systems, Wi-Fi echo techniques use regular data and acknowledgement communication frames to measure the ToF. As in the RSSI approach, the ToF is used only to estimate the distance between the client device and access points. Then a trilateration technique can be used to calculate the estimated position of the device relative to the access points. The greatest challenges in the ToF approach consist in dealing with clock synchronization issues, noise, sampling artifacts and multipath channel effects. Some techniques use mathematical approaches to remove the need for clock synchronization. More recently, the Wi-Fi Round Trip Time standard has provided fine ToF ranging capabilities to WiIFi.
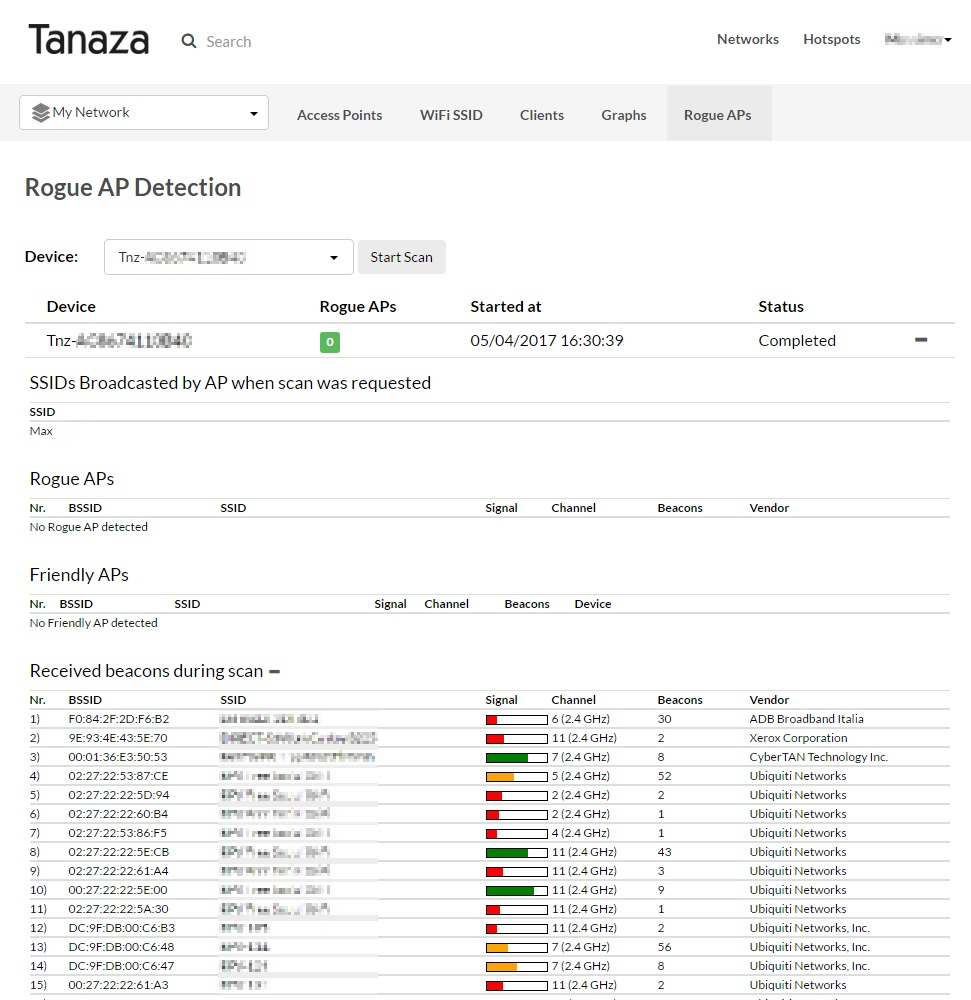
Figure 2: Rogue devices detection, scan your networks to detect rogue devices Secure WiFi access has become a critical component of enterprise networking. WiFi Internet access is critical for corporate communication in verticals, including financial services, retail, and distributed enterprises. Due to the widespread use of WiFi and a variety of use cases (e.g., point-of-sale (POS) communications, corporate access, warehouse inventory, asset tracking, and WiFi services for targeted advertising), the wealth of information transmitted across the wireless medium has skyrocketed. Data transmitted over wireless increasingly contains sensitive personal and financial data. Unfortunately, the tremendous growth in wireless has been accompanied by an increasingly widespread ability to obtain open-source hacking tools that can compromise a wireless network through the impersonation of client devices and access points (APs).
Network impersonation: achievable by purchasing any consumer-grade access point and copying an SSID, “tricking” clients into thinking that this SSID is available and snooping on their information transactions. Wired network compromise: achieved by an unsuspecting employee or student plugging in a consumer-grade access point into the wired infrastructure and exposing the LAN to hackers.
To successfully protect an enterprise network, a Wireless Intrusion Prevention System (WIPS) should provide powerful wireless intrusion scanning capabilities, enabling detection and classification of different types of wireless threats, including rogue access points and wireless hackers. Additionally, a WIPS system should be configurable with intuitive auto-containment policies to facilitate preemptive action against rogue devices. Once a threat has been detected, the WIPS platform should kick into gear to enact powerful policies, including intelligent auto-disablement of APs matching a pre-defined criteria and generating different tiers of e-mail alarms based on the type of threat in your airspace.
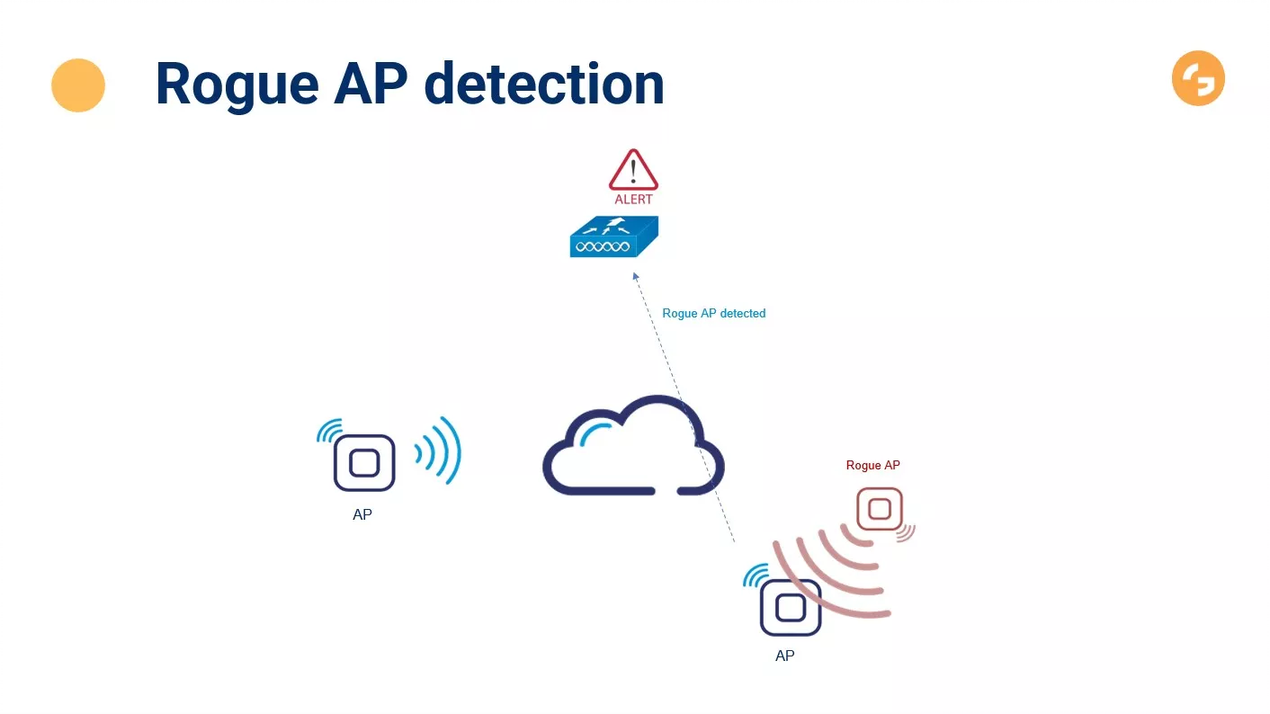
Figure 3: Security of wireless networks - how do hackers get in? Cisco Meraki’s Air Marshal mode allows network administrators to meet these requirements and design an airtight network architecture that provides an industry-leading WIPS platform in order to completely protect the airspace from wireless attacks. The remainder of this document describes in greater depth wireless threats and the necessary security measures required to remediate against these threats; the conclusion then summarizes the setup and configuration process for Meraki’s Air Marshal WIPS platform in order to achieve the highest security protection possible.
Understanding the wireless airspace around you can help to take effective measures, both preventive and reactive, to ensure that the wireless airspace is secure and interference-free from other wireless networks. Several different threats exist in the modern enterprise environment, facilitated by easy access to cheap consumer-grade 802.11 equipment, along with open-source hacking tools that can be used to simulate and spoof devices and generate traffic floods. Leading enterprise WLAN providers such as Cisco provide built-in WIPS features to ensure detection and remediation against these threats.
Visibility and classification of potential wireless threats is an important first step in securing the wireless network and network infrastructure as a whole. Once classified, remediation can be taken against confirmed threats and innocuous alerts can be dismissed. Cisco Meraki Air Marshal automatically classifies threats into the following categories to provide the greatest visibility and overall protection for your network.
Rogue SSID seen on LAN: SSIDs that are broadcast by rogue access points and seen on wired LAN; this could suggest a compromise of the wired network. Note: On MRs with a scanning radio, Air Marshal will not contain Rogue and Other SSIDs seen by the scanning radio if those SSIDs are on a DFS channel. This is because regulations require that significant time be spent determining that such channels are clear before transmitting on them, and this amount of time is great enough that it would render MRs unable effectively to scan the spectrum. As a result, only SSIDs on non-DFS channels can be contained by the scanning radio.
However, if the client-serving radio of the MR is operating on a DFS channel that matches that of the Rogue or Other SSIDs, Air Marshal will contain those SSIDs on that DFS channel if configured to do so. Note : Air Marshal may flag legitimate Wi-Fi Direct SSIDs since Wi-Fi Direct allows simultaneous peer-to-peer and infrastructure WLAN connections.
Interfering SSIDs: wireless networks that are broadcasting and could be causing RF interference, as well as attracting accidental associations from clients who are supposed to be connecting to your own network. Ad-Hoc SSIDs: modern smartphones and mobile devices are capable of associating to WiFi networks and then re-broadcasting the SSID, essentially acting as a wireless bridge. Devices in ad-hoc mode can connect to a client AP and create a gateway for wireless hackers.
Spoofs are APs that are impersonating the SSID (and possibly MAC address) of your APs. An AP spoof means that someone is deliberately impersonating your network and should be treated with the highest level of severity. When a Spoof event is detected, it generates an Event log on the Dashboard and sends a Syslog message to the configured Syslog server for immediate attention.
Denial of Service (DoS) attacks are attempts to prevent clients from associating to the legitimate AP by sending an excessive number of broadcast messages to clients. DoS attacks could be from malicious clients, APs, or even another WIPS system in the area that considers the corporate network a threat and is attempting to remediate. Clients or APs that are sending an excessive number of packets to your AP. Packets are monitored and classified based on multiple categories including beacon, authentication and association frames. An excessive number of any category of packets seen within a short time interval will be marked in Air Marshal as a packet flood.
Containment can have legal implications when launched against neighbor networks, and it may harm your own network by increasing channel utilization and potential disrupt clients connecting to your APs. Ensure that the rogue device is within your network and poses a security risk before you launch the containment. Cisco Meraki access points feature powerful Air Marshal technology that can assist with mitigating wireless threats to your network. Access points feature the ability to contain rogue access points that can put your network at risk. This Knowledge Base article covers the following: Rogue access points can be contained once they have been identified. When a rogue access point is contained, clients will be unable to connect to the rogue access points. Additionally, any currently associated clients will lose their connection to the rogue access point.
2. System Architecture & Core Working Principles Note: 6 GHz containment will not work because 6 GHz uses protected management frame and it would not be possible to contain the clients over the air. A Cisco Meraki AP accomplishes containment by sending deauthentication packets with the spoofed MAC address of the rogue access point (the BSSID of the rogue wireless network). The deauthentication packets force any clients that are connected to the rogue access point to disconnect. If a client attempts to connect to the rogue network, they will be immediately forced off by the Air Marshal. The image below shows a Cisco Meraki AP performing containment on a rogue SSID.
This enhancement applies to all Wi-Fi 6 or above APs that are running MR31.x, except for MR28 and MR78. Before the release of MR31.1, access points could only monitor for unauthorized APs within their designated regulatory domains. This posed a concern for large enterprise networks with numerous branch locations worldwide. For example, in Spain, APs do not support UNII-3 channels. A malicious actor may set up a Rogue AP on one of those UNII-3 channels and get users to connect to the SSID to steal credentials.
With the release of MR31.1, Air Marshal’s Rogue Detection support has been expanded beyond the AP’s regulatory domain. This feature is disabled by default. Please contact Meraki support to have this enabled on your network. Note: This is for Detection Alert and Non-Containment capabilities only. The enhancement is strictly limited to scanning out-of-regulatory domain channels for detection and alert purposes, containment of rogue APs is only done in regulatory domain channels.
Dual-radio Meraki APs will run wireless scans opportunistically while also serving clients; this means they will scan the channel on which they are serving clients. It is possible to schedule ‘mandatory’ scans to be run at pre-specified time intervals that can be set as frequently as once a day. Dual-radio APs can be set into a dedicated Air Marshal mode where it will not serve clients but will scan using both the 2.4GHz and 5GHz frequencies. Many Meraki access points include a third radio which comes pre-configured for permanent Air Marshal scanning. These APs do not require any dedicated Air Marshal configuration and will scan and remediate against threats in real-time.
For dual-radio Meraki access points: Air Marshal mode can be switched on by selecting the relevant APs on the Access Points page. By clicking the relevant AP and selecting ‘On’ under the Air Marshal scanning section or by applying the 'AirMarshal' tag to the AP, it is possible to designate this AP as a dedicated WIPS scanner. This Air Marshal AP will no longer serve clients but will now be a dedicated sensor performing scans of the surrounding environments for threats, the results of which will be displayed on the WIPS page in real-time.
A note on hybrid vs. dedicated scanners : APs with two radios running in client-serving mode will only scan the airspace opportunistically; this means they will scan the client-serving channel in real-time, and will scan across all channels either once a day or when no clients are being served. Most WLAN vendors recommend having dedicated scanning sensors (with no clients being served) in security conscious environments, to ensure real-time security alerting and protection. Some vendors offer ‘time slicing’ which allows cross-channel scans while serving clients, but this sacrifices performance of latency-sensitive applications such as VoIP and is generally not recommended in the industry. For this reason, Meraki recommends utilizing APs with dedicated scanning radios for high performance, real-time scanning.
Administrators may specify whether or not they wish for clients to be able to connect to rogue SSIDs. By choosing to allow devices to connect to rogue SSIDs by default , users will be able to freely connect to non-authorized access points seen on the LAN and broadcasting an SSID. In some environments, this provides the necessary level of flexibility for proper workplace operations. Administrators can use the SSID block list rules to enforce more granular security policies.
If an administrator selects block clients from connecting to rogue SSIDs by default , then devices will be automatically contained when attempting to connect to an SSID being broadcast by non-Meraki AP seen on the wired LAN. This provides greatest level of security for the wireless network. If clients are allowed to connect to rogue SSIDs by default, then administrators may specify additional rules to block list (contain) certain SSIDs or BSSIDs. These policies may match on exact words, MAC address (BSSID), keywords or wildcards, as shown in the image below. Email and syslog alerts will also be generated if SSIDs matching the rules in the block list table are seen.
Warning: Care should be taken when configuring SSID block list policies as these policies will apply to SSIDs seen on the LAN as well as off of the LAN from neighboring WiFi deployments. Review the above mentioned section Overview of Air Marshal Containment to understand how the APs may block the configured SSIDs. The following are acceptable wildcard characters that can be used to match on for the SSID block list, SSID allow list and SSID alerting tables: Similarly, if administrators wish to block clients from connecting to rogue SSIDs via containment by default, then administrators may use Air Marshal rules to allow list certain SSIDs or BSSIDs that clients will be allowed to connect to.
Rogue or Other SSIDs that match these rules will not generate alerts. Lastly, administrators may configure rules to alert when SSIDs matching a rule are seen. Alerts will be sent via email (as specified on the Network-wide > Configure > Alerts page) and via Syslog (as specified on the Network-wide > Configure > General page ).
When a SSID/BSSID configured within SSID alerting is detected, and there is a syslog server configured, the syslog messages uses the event type of device_alerting. When a rogue SSID or other SSID has been identified by an AP, it can have a security policy manually applied to it. Follow the steps below to manually apply a security policy to an SSID.
Locate the SSID that you wish to apply a policy to under the Rogue SSIDs or Other SSIDs tab. Select edit and specify if you'd like to allow list, contain, alert, or uncontain, as shown in Figure F. Specify if the policy should be applied by SSID or BSSID. Selecting SSID will add an 'Exactly Matches' policy entry to the respective SSID block list, allow list or alert table on the Configure tab. Selecting BSSID will ad a 'Matches MAC Address' policy entry to the respective SSID block list, allow list or alert table.
APs across different networks within the same Dashboard Organization will not be flagged as rogues or interfering unless containment is activated. You can restrict them by containing the SSID through precise matches, MAC addresses, keywords, or wildcard rules. Additionally, APs are automatically restricted when the option "Block clients from connecting to rogue SSIDs by default" is activated.
For instance, consider "Network A" and "Network B" within the same Dashboard Organization. If the APs in Network A contain the APs from Network B, the Dashboard for Network A will display an entry under Wireless > Air Marshall > Rogue SSIDs for the contained SSIDs belonging to Network B. This is a rogue or other wireless network that is not currently contained. Upon evaluating the threat, you may wish to either block list or allow list the SSID. An uncontained SSID that has not been allow listed could eventually become contained if its status on the LAN were reclassified as being a rogue SSID if LAN containment is enabled, or if a block list rule is added that matches with the SSID or BSSID. An uncontained SSID has simply been noticed and no administrative decision has been made regarding its status yet.
This is a rogue wireless network that your Cisco Meraki AP is currently containing. Whenever a client attempts to connect to the rogue wireless network, they will be forced off via the deauthentication process described earlier. This is a rogue wireless network that can not be completely contained because some of the rogue access points may be on a different channel. This can occur when a non-Air Marshal AP notices the rogue on a different channel during a channel scan.
The AP can not fully contain the rogue wireless network because of the channel difference. Deploying more APs with dedicated third Air Marshal scanning radios can help mitigate these issues. 3. Software Implementation, Frameworks & Protocols This is a wireless network that has been allow listed either via a rule in the SSID allow list table or manually and will not be contained under any circumstances. You may choose to allow list a wireless network when you have identified it as being a legitimate part of your infrastructure. Allow listed networks will not be contained in any way.
This is a wireless network that was noticed during a scan, but has not been determined to be a threat to your network. When a Beacon Frame for an SSID is detected by an access point in Air Marshal mode or with a dedicated scanning radio, it is classified as either a 'Rogue SSID' or as an 'Other SSID'. To determine if an SSID is originating locally, we look at the MAC address of local devices, and the BSSID of the broadcasted SSID. When a wireless access point of any brand generates a beacon packet, it uses a BSSID, which is virtual physical address. More information on this behavior can be found here .
Note: A “hidden SSID” on the Air Marshal page is an SSID name that is not included in the beacons and probe responses for a particular BSSID. These can usually be ignored during common network operation, and are unlikely to result in noticeable RF interference. Administrators may specify the same allow list, contain, alert, uncontain rules for BSSIDs contributing to the hidden SSID's seen by selecting the Hidden row and selecting the Broadcast MAC to apply the rule to.
Additional information about a specific rogue SSID can be found by selecting the row of the rogue SSID in question. RSSI of the rogue SSID will be displayed on a map or floorplan indicating which AP's are able to 'hear' the rogue SSID with the strongest signal, along with information pertaining to when the SSID was seen, on which channels, the broadcast MAC (BSSID), the manufacturer and the reason the SSID was identified as rogue.
When we detect an SSID being broadcast, we compare it to other known MAC addresses on the LAN. The criteria for a match are as follows: This comparison is done with an Xor of the MAC address in binary notation. Below is an example of a wired MAC compared to the Broadcasted MAC in the SSID. This example was detected by Air Marshal: When the MAC addresses are written out in binary, you can see that very few of the bits are different. When performing an Xor, you see that only 3 significant bits in the calculation are different between the two MAC addresses.
Note: Any BSSIDs that are seen broadcasting with a particular SSID will be associated together. Air Marshal containment focuses primarily on SSIDs. So if a single BSSID matches the checks listed above, the rest associated with that SSID will be flagged as well. This can be seen in the following example, where not all BSSIDs satisfy the requirements to match with the SSID.
Air Marshal will detect rogues on all VLANs if the Meraki AP is connected to a upstream trunk port given that all VLANs are allowed. With the ability to locate Rogue SSIDs, administrators are better equipped to prevent unauthorized access points from operating on their local network. After detection, an administrator is able to take action, either containing the SSID using Air Marshal, or using the gathered information to find the offending device and remove it from the network.
A careful study of the common wireless security threats has led to the development of Meraki’s Air Marshal platform, which allows access points to act as WIPS sensors on a dedicated radio while serving clients. Air Marshal is a WIPS platform which comes equipped with security alerting and threat remediation mechanisms. This includes the following: A robust and intuitive display of all of the threats for a particular network, including auto-alerting based on the network administrator’s preferences.
802.11ac Meraki APs utilize a dedicated scanning radio to scan across all 2.4 GHz and 5 GHz channels and build a list of rogue access points in the nearby vicinity. In addition, further mechanisms are in place to track APs on the wired LAN network by inspecting traffic on the wired port of the Meraki AP, and using this to build a list of rogue access points that may be on the wired LAN. E-mail alerts as as well as syslog messages will be triggered for any SSID's that match rules configured on the SSID block list table or SSID alerts table.
Email alerting can be configured by navigating to the Network-wide > Configure > Alerts page and specifying that email alerts should be sent when a rogue access point is detected. Syslog alerting can be configured by navigating to the Network-wide > Configure > General page and configuring the syslog server IP, port, and specifying 'air marshal' events.
Lastly, scan results can be retrieved via the Dashboard API using the GET call get-network-wireless-air-marshal . Air Marshal access points come equipped with the ability to automatically ‘contain’ rogue access points and alert on rogue access points either by default or by configuring Air Marshal rules. This allows for administrators to take physical action to remove rogue access points.
‘Containment’ is a common mechanism that calls for the Air Marshal AP to impersonate or spoof the rogue access points in order to render it ineffective. Air Marshal does this by generating a large number of 802.11 packets and using the BSSID of the rogue access points as the the source MAC address. Air Marshal APs also provides more sophisticated containment methods including spoofing clients attempting to associate to the rogue by generating packets with the source MAC of the clients; this allows for a ‘two-way’ spoof and ensures a fool-proof shutdown of the rogue access points.
#3 ensures that more sophisticated 802.11 clients with battery-saving capabilities are also unable to connect to the rogue, as they may ignore deauthorization messages from the Rogue access point if they are ‘sleeping’ in order to save battery life. Understanding and remediating against wireless threats is also a requirement under the Payment Card Industry Data Security Standard (PCI DSS), a standard required for retailers to follow when processing credit card data over WLAN networks.
Examples of WIPS requirements under PCI DSS include: Scan all sites with card dataholder environments (CDE) whether or not they have known WLAN APs in the CDE. Sampling of sites is not allowed. A WIPS is recommended for large organizations since it is not possible to manually scan or conduct a walk-around wireless security audit of all sites on a quarterly basis Enable automatic WIPS alerts to instantly notify personnel of rogue devices and unauthorized wireless connections into the CDE.
Prepare an incident response plan to monitor and respond to alerts from the WIPS. Enable automatic containment mechanism on WIPS to block rogues and unauthorized wireless connections. By configuring alerts and utilizing Meraki’s Air Marshal view to monitor these threats retroactively and in real-time, it is possible to build a robust security plan that can be enforced. An example of a complete security methodology is as follows: APs that are designated as full-time Air Marshals for WIPS scanning can be deployed using exactly the same methodology as a regular client-serving AP in terms of wall mounting, using PoE, etc.
An Air Marshal AP has a wider effective radius than a regular AP, as it can detect and contain rogues at a lower bitrate than what is required for sustained client connectivity. The coverage radius of an Air Marshal AP for sensing and remediating against rogue access points is approximately twice as large as the coverage area for serving clients; therefore, the total coverage area for WIPS scanning is approximately 4 times as large as the area for serving clients. When planning for full WIPS coverage, the approximate ratio of Air Marshal APs to client serving APs will be 1:4, but could vary from 1:3 to 1:5 depending on the parameters of the deployment and WIPS coverage density required.
4. Practical Deployment, Analysis & Case Studies By understanding the spectrum of wireless security threats in today’s environment and creating a comprehensive response plan, network administrators can preclude the possibility of a serious compromise of critical network assets — including access to secure network devices that belong to the enterprise. A best-in-class WIPS platform should be capable of delivering intuitive reporting and monitoring, along with a robust suite of tools allowing for automatic alerts and security enforncement.
Meraki’s Air Marshal system includes real-time detection, remediation and alerting capabilities, including the ability to define pre-emptive policies that will intelligently take action to contain rogue access points using sophisticated containment mechanisms. Meraki’s wireless portfolio contains both dual-radio APs which can be converted into full-time sensors running in Air Marshal mode, and three-radio APs with dedicated scanning radios permanently running as Air Marshal scanners. By utilizing Meraki access points and Meraki’s intuitive web-based Dashboard interface, network administrators can create a robust WIPS policy plan, and easily deploy an airtight network to deliver enterprise-grade security in a WLAN environment.
Rogue access points transmit unauthorized wireless signals that mimic legitimate network characteristics, creating security vulnerabilities by potentially capturing client connections and exposing sensitive data, while the wireless intrusion detection system suffers from insufficient detection capability to reliably identify and distinguish these rogue devices in real-time; the goal is to achieve comprehensive and accurate rogue access point detection to protect the wireless local area network from unauthorized access and security breaches.
Pre-trained signal fingerprint library with instant template matching for rogue AP detection Rogue AP detection in WiIFi 7 is about separating signal from noise and proving findings. You will plan a baseline of legitimate SSIDs and BSSIDs, then configure monitoring to flag imposters with confidence. This guide assumes admin access to your WLAN controllers or sensors, basic familiarity with WPA3, and a workstation that can run packet capture tools in monitor mode. I will show home, shared, and enterprise paths so you can right size the approach. We will use traps that expose rogue access points through identity mismatches, channel anomalies, and policy tests, then verify results with repeatable checks that you can automate.
Start by defining scope and success criteria so detection efforts do not drift. Create a simple baseline that lists approved SSIDs, their BSSIDs per radio, allowed channels, and expected security suites. For a small office, maintaining this in version control as a CSV with SSID, BSSID, band, and RSN information is workable. Enterprises should pull this from controller APIs to avoid human drift. The tradeoff is effort upfront for accuracy later. Without a baseline, you cannot label an access point rogue with defensible evidence, and every mismatch becomes guesswork. Aim for weekly updates or event driven refreshes when you add or retire APs.
Segment goals by environment tier to prioritize controls where risk is real. Home networks focus on a small allow list and aggressive notifications. Shared spaces like cafes or coworking should avoid penalizing neighbors and instead focus on impersonation of your SSID within your premises. Enterprises should enforce source of truth and require multiple confirming signals before action. This tiered framing explains why a policy that is perfect at home becomes noisy in dense apartments. It also justifies extra validation when a false positive would disrupt large numbers of users or trigger unnecessary incident response.
Choose detection signals that combine identity, location, and behavior for higher confidence. Identity signals include SSID, BSSID, and RSN capabilities such as WPA3 SAE with PMF. Location signals include received signal strength from known sensors and channel placement compared to your plan. Behavior signals include abnormal beacon intervals or vendor OUIs that do not match inventory. The tradeoff is complexity in correlation, but the payoff is a lower false positive rate. In WiIFi 7, multi link operation adds links per device, so model per link attributes rather than assuming one BSSID per AP. Document which signals are required versus optional in the policy.
Equip minimum viable tooling before you start tuning rules. You need at least one monitor mode interface for packet capture, a WIDS sensor or controller that can export events, and a place to store evidence like pcap files. For home or small offices, a single adapter with WiIFi 6E or better and a laptop can capture 6 GHz beacons to identify imposters on your band plan. Enterprises should position sensors to cover entrances, lobbies, and parking areas where rogue APs often appear. The tradeoff is coverage versus cost, so prioritize perimeters and high traffic zones before deep interior areas.
Map your RF environment to avoid mislabeling neighbors as threats. Document the channels you actively use by band, DFS constraints, and channel width plans like 80 or 160 MHz. Record typical noise floors and high density areas where signals overlap. This context helps distinguish a rogue broadcasting your SSID on your assigned channels from a benign network using different identifiers. In WiIFi 7, wider channels and puncturing can shift where beacons appear. Note where multi link operation is enabled so you do not confuse additional links with separate APs. Build simple diagrams so responders can interpret alerts quickly.
Establish a clean baseline artifact with version control so audits are straightforward. Export from your controller or build a script that lists SSIDs, BSSIDs, and security parameters, then store it alongside detection rules. Include a changelog that captures when an AP moves or gets replaced. The downside is process overhead, but it prevents the most common error where a legitimate replacement triggers a rogue alert due to stale records. If you are evaluating monitoring strategy depth, review this companion overview on incident tactics and RF cues in the WiIFi 7 monitoring guide by exploring the section on WIDS and rogues at practical monitoring and response tactics .
Deploy your first detection playbook with conservative signals so you can expand safely. Start by matching SSID and RSN capabilities to your baseline, then require a BSSID that belongs to your inventory. If a device broadcasts your SSID with WPA2 only or disables PMF where you enforce it, flag as suspicious. The tradeoff is that some legacy guest setups differ by design, so scoping is essential. Include a threshold on RSSI or sensor count so a single weak signal in the lobby does not escalate. This initial rule catches lookalike imposters while avoiding neighbor noise that carries your SSID string coincidentally.
Add channel and location logic to strengthen confidence without raising effort. Compare detected beacons against your channel plan and expected AP locations. A rogue that appears on an unused channel or one that shows a sudden high RSSI near your entrance is more likely hostile. In WiIFi 7, consider puncturing and multi link operation where secondary links can appear on different channels. Protect against false flags by allowing documented maintenance windows when technicians stage equipment. When user risk is high, require two independent sensors to confirm the beacon before you alert or send staff to investigate on site.
Automate evidence collection so every alert has context. When a candidate rogue is detected, capture a short pcap with beacons and probe responses and store it with a timestamp and rule identifier. Tag the file with SSID, BSSID, RSN, and channel to speed triage. This habit lets you retrace decisions, train your rules, and prove issues to building management if interference stems from a tenant. Before integrating deeply with a SIEM , review baseline security operations for WiIFi 7 across encryption and policy by reading the broader security overview at threat aware standards and identity guidance .
Treat validation as part of the workflow, not an afterthought. For each detection, confirm at least two independent indicators like BSSID not in baseline and RSN mismatch, or channel anomaly plus high RSSI near an entrance. Keep a manual spot check process weekly where you replay captures and verify the rule logic still holds. The tradeoff is time spent on audits, but you gain confidence that your rules reflect reality. In WiIFi 7 deployments that use multi link operation, verify that extra links are represented in your baseline so they do not appear as separate devices under test, especially during firmware upgrades.
Benchmark alert fidelity using a simple rubric that tracks precision and investigation time. Record how many rogue alerts were confirmed, dismissed as neighbor networks, or caused by inventory drift. Add median time to triage using your stored pcaps and metadata. Improvement shows up as fewer dismissals and faster triage. If metrics stall, adjust thresholds or add a confirming signal like vendor OUI matching. Avoid chasing percentage targets without context because building materials and density affect RF behavior. The point is trend direction over absolute numbers that vary by site and equipment mix.
Run controlled tests to ensure your traps fire reliably. Bring a test AP, configure a known bad variant of your SSID on an unused channel, and verify that your rules alert with the expected reason codes. Repeat by toggling PMF or downgrading to WPA2 to simulate weaker security. The caveat is to choose times and places that minimize user impact and comply with local policy. Capture and archive the resulting pcaps as golden samples for future regression testing. These repeatable checks help defend changes when you modify channel plans or adopt new WiIFi 7 features that alter beacon contents.
When noise rises, first investigate inventory drift. A replaced AP with a new BSSID or a temporary maintenance SSID often explains a burst of alerts. Compare the alerting BSSIDs against recent change logs. If drift is the cause, update the baseline and note the exception window. The tradeoff is briefly loosening detection to restore calm, but leaving drift unaddressed corrodes trust. Next, verify sensor placement and coverage maps. A weak second sensor can block your two sensor confirmation rule, delaying legitimate alerts. Rebalance placement to restore the intended confidence checks without widening thresholds.
Cut false positives by adjusting sensitivity rather than disabling rules. Add minimum RSSI thresholds, require consistent observation across a short window, or restrict alerts to your active channels. These changes reduce the chance that a distant neighbor triggers action. Where devices spoof vendor OUIs, include RSN and capability checks so identity is multi dimensional. For shared spaces, consider a carve out that ignores SSID matches unless accompanied by channel overlap within your plan. The why is simple: an SSID string is not ownership. Your policy should reward corroboration and penalize single point indicators.
Integrate with logging and response tools to streamline investigations. Send structured fields like SSID, BSSID, channel, RSN, RSSI, and sensor IDs to your SIEM, then build saved searches that correlate repeated sightings over time. Alert only when a threshold of sightings or sensors is met. This approach limits on call noise while preserving context for analysis. If you later adopt WIPS containment features, gate them behind manual approval to avoid harming neighbor networks. Review more detailed incident response playbooks and WIDS tuning patterns by visiting the guide on configuring sensors and reducing false positives at practical WIDS setup advice .
Expect your rogue detection to evolve as WiIFi 7 features mature. Multi link operation will reveal new patterns to monitor, including link specific capabilities that differ across bands. Keep your baseline model flexible so each link can record security attributes independently. The tradeoff is more complex data, but the result is cleaner distinctions between legitimate multi link devices and impersonators. As controllers and sensors add visibility, prefer APIs that export reason codes and parsed RSN fields so you can enrich alerts without post processing heavy pcaps repeatedly.
Prepare for collaboration between facilities and security teams. Rogue devices often show up at building edges, temporary rooms, or during events, which means access and context matter for response time. Build a simple runbook that pairs technical checks with contact info and site maps. This coordination reduces on site guesswork and shortens the window where attackers can harvest credentials or redirect users. Review your runbook quarterly and simulate a rogue in a controlled test to keep the process fresh. The overhead is small compared to the outage risk from unmanaged interference and impersonation.
Finally, aim for sustainable automation that does not hide the reasoning. Every alert should carry the evidence that triggered it, the sensors involved, and the threshold logic that promoted it to human review. This transparency lets you tune confidently, defend decisions to leadership, and train new analysts faster. Over time, build dashboards that show trends in sightings per location and the share of confirmed rogues. When those metrics stabilize, you can safely experiment with more aggressive rules and containment gates without losing trust in the system’s output.
Use a baseline allowlist, require observation on your assigned channels, and add a minimum RSSI threshold or two sensor confirmation. These combined checks cut noise from distant or unrelated networks. A BSSID not in inventory plus an RSN mismatch or channel anomaly is reliable. Add vendor OUI and consistent sightings over a short window to increase confidence without overfitting to a single clue.
Yes if your baseline treats additional links as separate APs. Record per link attributes and map them to the same device identity so extra links do not appear as unknown BSSIDs during normal operation. Use manual approval for containment. Mistakes can disrupt neighbors and violate policy. Gate actions behind human review until your detection precision is proven and local regulations are clearly addressed.
5. Performance Evaluation & Extended Technical Observations A laptop with a monitor mode adapter, tshark for capture, and a controller or WIDS that exports events is enough. Store pcaps and metadata so you can review alerts and improve rules safely. A single unknown laptop can expose a much larger gap in your network. Rogue devices include personal hardware, forgotten equipment, rogue access points, and planted implants. To detect them, build a known-good inventory first, then compare scans, switch records, wireless data, and device behavior.
This process works for office networks, branch sites, IoT-heavy environments, and remote workers. It also shows where a scanner stops and where risk review, containment, and policy must begin. The first step in learning how to detect rogue devices on a network is to define what belongs there. A device is rogue when it connects without approval or sits outside your control. That can mean a personal phone, a contractor laptop, a smart camera, a home router, or an access point that someone installed without telling IT.
Do not start with a list copied from your CMDB. Start with fresh network evidence. Your baseline should combine several sources because each one sees a different part of the environment. Give every known asset an owner, purpose, site, segment, and expected behavior. “Dell laptop” is not enough. You need to know which team owns it and whether it should appear on a finance VLAN, a guest network, or a home network.
Mark devices as managed, approved but unmanaged, pending review, or unknown. This avoids a common mistake: treating every device without an endpoint agent as hostile. A printer may have no agent but still be approved. A contractor laptop may be allowed for two days, then need removal. Set a freshness rule. If your inventory has not seen a device recently, label that record stale. If your security tools disagree, keep both records until you reconcile them. The gap between your approved list and a fresh network observation is the first measure of your hidden attack surface.
For distributed teams, include remote environments in the baseline. Endpoint tools often see the worker’s laptop but miss other devices on the same home network. Obsonis is built around continuous, agentless discovery across corporate and remote networks, with risk context for devices that standard endpoint tools may miss. Its hidden attack surface assessment guidance explains how to compare inventory sources and test for stale coverage.
Keep the baseline in a form you can compare tomorrow. Export it with a timestamp. Store the raw data. Record the account or sensor that collected it. That audit trail helps you tell a new device from a device that simply changed its IP address. Milestone: You should now have a time-stamped list of observed devices, plus a clear status for each one. Active scans help you detect rogue devices on network segments that passive tools may overlook. Scan each VLAN from a host on that same segment when possible. A scan from elsewhere may miss Layer 2 clues, local ARP responses, or the MAC address tied to a host.
Get approval before scanning production systems. Set a rate that fits the network. Avoid broad vulnerability tests during a first discovery pass, especially on fragile medical, industrial, or embedded devices. This asks which hosts respond. Save the result with a date and segment name. You can then inspect selected hosts with service detection: Use service and operating system results as clues, not proof. A device may misreport its operating system. A filtered port does not mean the host is absent. Compare the result with DHCP, ARP, and switch data before you flag it.
Combining wired scans with wireless discovery can help identify devices that either method may miss. Saving scan output also lets later scans reveal new hosts and services. ARP shows who is active on a local network. A switch MAC table shows what the switch has learned and where it learned it. The two views answer different questions.
On a managed switch, use the vendor’s command for its MAC address table. Common command families include: Do not run a command copied from a different switch family without checking its documentation. The useful evidence is the same: MAC address, VLAN, port, age, and link state. A second DHCP server can hand out the wrong gateway or DNS server. That can cause outages, redirect traffic, or place hosts on an attacker-controlled path. Review DHCP server identifiers in packet captures or approved discovery tests. Two different server identifiers on one segment deserve immediate review.
For wireless work, compare controller data with a wireless survey. Look for an access point using a corporate SSID without an approved management record. A wireless heat map can help show where signal strength rises. A wired-side scan can then confirm whether the access point connects to your infrastructure. Use vendor fingerprints with care. The first three bytes of a MAC address can suggest a manufacturer, but MAC addresses can be changed. A familiar vendor does not make a device trusted. Treat the manufacturer as one clue among many.
Keep normal and XML scan output. A later comparison can show when a host first appeared, when a service changed, or when a device moved between segments. That timeline often matters more than one isolated scan. Milestone: You should now have scan results tied to IPs, MACs, VLANs, ports, and wireless observations. Scanning tells you what answered. Continuous monitoring helps you detect rogue devices on network infrastructure that appears only briefly or stays quiet during a scan.
Collect flow records, DNS requests, DHCP events, firewall logs, wireless telemetry, and packet data where policy allows. You do not need full packet capture everywhere. Flow data can still show who talks, how often, how much data moves, and which external destinations receive it. One signal can mislead you. A phone may use a randomized MAC address. A virtual machine may share a physical host. A printer may expose a web service that resembles another device. Confidence rises when several signals agree over time.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Wi-Fi%20positioning%20system • https://documentation.meraki.com/Wireless/Operate_and_Maintain/User_Guides/Monitoring_and_Reporting/Air_Marshal • https://eureka.patsnap.com/tech-solution/how-to-detect-rogue-access-points-in-wireless-local-area-networks-using-wids • https://pulsegeek.com/articles/rogue-ap-detection-in-wi-fi-7-build-your-traps/ • https://www.obsonis.com/knowledge-hub/how-to-detect-rogue-devices-on-network/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Rogue Beacon Detection Tool In Wireless Sensor Networks.
! Define Extended Access List to Block Malicious Traffic ip access-list extended SECURE_PERIMETER_ACL remark Block Inbound Telnet and Unencrypted Services deny tcp any any eq 23 log remark Permit Verified Web SSL Traffic permit tcp any any eq 443 permit tcp any any eq 80 remark Mitigate ICMP Flood and Ping Sweeps permit icmp any any echo-reply deny icmp any any echo log deny ip any any log
! Apply ACL to Ingress Interface GigabitEthernet0/0 interface GigabitEthernet0/0 ip access-group SECURE_PERIMETER_ACL in no shutdown end write memory
Extended IP access list SECURE_PERIMETER_ACL (Cisco Packet Tracer) ──────────────────────────────────────────────────────────────────────── 10 deny tcp any any eq telnet log (142 matches) [Probes Dropped] 20 permit tcp any any eq 443 (18402 matches) [TLS 1.3 Traffic Permitted] 30 permit tcp any any eq 80 (4812 matches) 40 deny icmp any any echo log (524 matches) [Flood Mitigated] 50 deny ip any any log (38 matches) [Default Implicit Deny Rule] ──────────────────────────────────────────────────────────────────────── [✓] Packet Tracer Verification: 0 Unsanitized Ingress Leaks on Gi0/0
| Interface Port | Network Zone | Filter Applied | Traffic Processed | Firewall Decision |
|---|---|---|---|---|
| Gig0/0 (WAN) | Untrusted External | Extended ACL 101 | 24,810 Packets | INSPECTED & FILTERED |
| Gig0/1 (DMZ) | Public Web Services | Port 443 Only | 18,402 Packets | PERMITTED |
| Gig0/2 (LAN) | Corporate Users | 802.1X Port Security | 142 Probes | DENIED & QUARANTINED |