Complete Technical Paper Content — Rogue Dhcp Server Detection System In Local Network
Overview & System Context
Rogue Dhcp Server Detection System In Local Network: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~6864 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Wi-Fi () is a family of wireless network protocols based on the IEEE 802.11 family of standards, which are commonly used for local area networking of devices and Internet access, allowing nearby digital devices to exchange data by radio waves. These are the most widely used computer networks, used globally in home and small office networks to link devices and to provide Internet access with wireless routers and wireless access points in public places such as coffee shops, restaurants, hotels, libraries, and airports. Wi-Fi is a trademark of the Wi-Fi Alliance, which restricts the use of the term "Wi-Fi Certified" to products that successfully complete interoperability certification testing. Non-compliant hardware is simply referred to as WLAN, and it may or may not work with "Wi-Fi Certified" devices. As of 2017, the Wi-Fi Alliance consisted of more than 800 companies from around the world. As of 2019, over 3.05 billion Wi-Fi-enabled devices are shipped globally each year. Wi-Fi uses multiple parts of the IEEE 802 protocol family and is designed to work well with its wired sibling, Ethernet. Compatible devices can network through wireless access points with each other as well as with wired devices and the Internet. Different versions of Wi-Fi are specified by various IEEE 802.11 protocol standards, with different radio technologies determining radio bands, maximum ranges, and speeds that may be achieved. Wi-Fi most commonly uses the 2.4 gigahertz (120 mm) UHF and 5 gigahertz (60 mm) SHF radio bands, with the 6 gigahertz SHF band used in newer generations of the standard; these bands are subdivided into multiple channels. Channels can be shared between networks, but, within range, only one transmitter can transmit on a channel at a time.
Wi-Fi's radio bands work best for line-of-sight use. Common obstructions, such as walls, pillars, home appliances, etc., may greatly reduce range, but this also helps minimize interference between different networks in crowded environments. The range of an access point is about 20 m (66 ft) indoors, while some access points claim up to a 150 m (490 ft) range outdoors. Hotspot coverage can be as small as a single room with walls that block radio waves or as large as many square kilometers using multiple overlapping access points with roaming permitted between them. Over time, the speed and spectral efficiency of Wi-Fi has increased. As of 2025, some versions of Wi-Fi, running on suitable hardware at close range, can achieve speeds of 23 Gbit/s (gigabit per second).
A 1985 ruling by the U.S. Federal Communications Commission released parts of the ISM bands for unlicensed use for communications in the United States. These frequency bands include the same 2.4 GHz bands used by equipment such as microwave ovens, and are thus subject to interference. In 1989 in Australia, a team of scientists began working on wireless LAN technology. A prototype test bed for a wireless local area network (WLAN) was developed in 1992 by a team of researchers from the Radiophysics Division of the CSIRO (Commonwealth Scientific and Industrial Research Organisation) in Australia, led by John O'Sullivan. A patent for Wi-Fi was lodged by the CSIRO in 1992. In 1991 in the city of Nieuwegein in the Netherlands, the NCR Corporation and AT&T invented the precursor to 802.11, intended for use in cashier systems, under the name WaveLAN. NCR's Vic Hayes, who held the chair of IEEE 802.11 for ten years, along with Bell Labs engineer Bruce Tuch, approached the Institute of Electrical and Electronics Engineers (IEEE) to create a standard and were involved in designing the initial 802.11b and 802.11a specifications within the IEEE. They have both been subsequently inducted into the Wi-Fi NOW Hall of Fame. The first version of the 802.11 protocol was released in 1997, and provided up to 2 Mbit/s link speeds. This was updated in 1999 with 802.11b to permit 11 Mbit/s link speeds. In 1999, the Wi-Fi Alliance formed as a trade association to hold the Wi-Fi trademark under which most IEEE 802.11 products are sold.
The major commercial breakthrough came with Apple Inc. adopting Wi-Fi for their iBook series of laptops in 1999. It was the first mass consumer product to offer Wi-Fi network connectivity, which was then branded by Apple as AirPort. This was in collaboration with the same group that helped create the standard: Vic Hayes, Bruce Tuch, Cees Links, Rich McGinn, and others from Lucent. In 2000, Radiata, a group of Australian scientists connected to the CSIRO, were the first to use the 802.11a standard on chips connected to a Wi-Fi network. Wi-Fi uses a large number of patents held by multiple different organizations. Australia, the United States and the Netherlands simultaneously claim the invention of Wi-Fi, and a consensus has not been reached globally. In 2009, the Australian CSIRO was awarded $200 million after a patent settlement with 14 technology companies, with a further $220 million awarded in 2012 after legal proceedings with 23 companies. In 2016, the CSIRO's WLAN prototype test bed was chosen as Australia's contribution to the exhibition A History of the World in 100 Objects held in the National Museum of Australia.
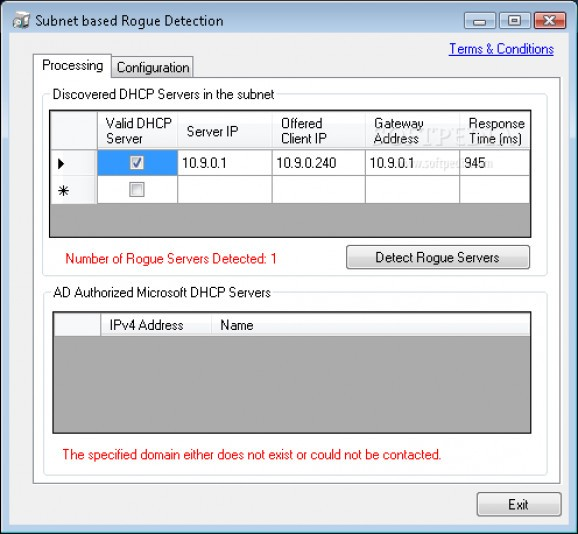
Figure 1: Rogue Detection - Download - Softpedia The IEEE does not test equipment for compliance with their standards. The Wi-Fi Alliance was formed in 1999 to establish and enforce standards for interoperability and backward compatibility, and to promote wireless local-area-network technology. The Wi-Fi Alliance enforces the use of the Wi-Fi brand to technologies based on the IEEE 802.11 standards from the IEEE.
Manufacturers with membership in the Wi-Fi Alliance, whose products pass the certification process, gain the right to mark those products with the Wi-Fi logo. Specifically, the certification process requires conformance to the IEEE 802.11 radio standards, the WPA and WPA2 security standards, and the EAP authentication standard. Certification may optionally include tests of IEEE 802.11 draft standards, interaction with cellular-phone technology in converged devices, and features relating to security set-up, multimedia, and power-saving. Not every Wi-Fi device is submitted for certification. The lack of Wi-Fi certification does not necessarily imply that a device is incompatible with other Wi-Fi devices. The Wi-Fi Alliance may or may not sanction derivative terms, such as Super Wi-Fi, coined by the US Federal Communications Commission (FCC) to describe proposed networking in the UHF TV band in the US.
Equipment frequently supports multiple versions of Wi-Fi. To communicate, devices must use a common Wi-Fi version. The versions differ between the radio wavebands they operate on, the radio bandwidth they occupy, the maximum data rates they can support and other details. Some versions permit the use of multiple antennas, which permits greater speeds as well as reduced interference. Historically, the equipment listed the versions of Wi-Fi supported using the name of the IEEE standards.
In 2018, the Wi-Fi Alliance introduced simplified Wi-Fi generational numbering to indicate equipment that supports Wi-Fi 4 (802.11n), Wi-Fi 5 (802.11ac) and Wi-Fi 6 (802.11ax). These generations have a high degree of backward compatibility with previous versions. The alliance has stated that the generational level 4, 5, or 6 can be indicated in the user interface when connected, along with the signal strength. The most important standards affecting WiIFi are: 802.11a, 802.11b, 802.11g, 802.11n (Wi-Fi 4), 802.11h, 802.11i, 802.11-2007, 802.11–2012, 802.11ac (Wi-Fi 5), 802.11ad, 802.11af, 802.11-2016, 802.11ah, 802.11ai, 802.11aj, 802.11aq, 802.11ax (Wi-Fi 6), 802.11ay.
Wi-Fi technology may be used to provide local network and Internet access to devices that are within Wi-Fi range of one or more routers that are connected to the Internet. The coverage of one or more interconnected access points can extend from an area as small as a few rooms to as large as many square kilometres. Coverage in the larger area may require a group of access points with overlapping coverage. For example, public outdoor Wi-Fi technology has been used successfully in wireless mesh networks in London. An international example is Fon. Wi-Fi provides services in private homes, businesses, as well as in public spaces. Wi-Fi hotspots may be set up either free of charge or commercially, often using a captive portal webpage for access. Organizations, enthusiasts, authorities and businesses, such as airports, hotels, and restaurants, often provide free or paid-use hotspots to attract customers, to provide services to promote business in selected areas. Routers often incorporate a digital subscriber line modem or a cable modem and a Wi-Fi access point, are frequently set up in homes and other buildings, to provide Internet access for the structure. Similarly, battery-powered routers may include a mobile broadband modem and a Wi-Fi access point. When subscribed to a cellular data carrier, they allow nearby Wi-Fi stations to access the Internet. A number of smartphones have a built-in mobile hotspot capability of this sort, though carriers often disable the feature, or charge a separate fee to enable it. Standalone devices such as MiFi- and WiBro-branded devices provide the capability. Some laptops that have a cellular modem card can also act as mobile Internet Wi-Fi access points.
Multiple traditional university campuses in the developed world provide at least partial Wi-Fi coverage. Carnegie Mellon University built the first campus-wide wireless Internet network, called Wireless Andrew, at its Pittsburgh campus in 1993 before Wi-Fi branding existed. A number of universities collaborate in providing Wi-Fi access to students and staff through the Eduroam international authentication infrastructure.
In the early 2000s, multiple cities around the world announced plans to construct citywide Wi-Fi networks. There are a number of successful examples; in 2004, Mysore (Mysuru) became India's first Wi-Fi-enabled city. A company called WiFiyNet has set up hotspots in Mysore, covering the whole city and a few nearby villages. In 2005, St. Cloud, Florida and Sunnyvale, California, became the first cities in the United States to offer citywide free Wi-Fi (from MetroFi). Minneapolis has generated $1.2 million in profit annually for its provider. In May 2010, the then London mayor Boris Johnson pledged to have London-wide Wi-Fi by 2012. Several boroughs including Westminster and Islington already had extensive outdoor Wi-Fi coverage at that point. New York City announced a city-wide campaign to convert old phone booths into digital kiosks in 2014.
The project, titled LinkNYC, has created a network of kiosks that serve as public Wi-Fi hotspots, high-definition screens and landlines. Installation of the screens began in late 2015. The city government plans to implement more than seven thousand kiosks over time, eventually making LinkNYC the largest and fastest public, government-operated Wi-Fi network in the world. The UK has planned a similar project across major cities of the country, with the project's first implementation in the London Borough of Camden. Officials in South Korea's capital Seoul were moving to provide free Internet access at more than 10,000 locations around the city, including outdoor public spaces, major streets, and densely populated residential areas. Seoul was planning to grant leases to KT, LG Telecom, and SK Telecom. The companies were supposed to invest $44 million in the project, which was to be completed in 2015.
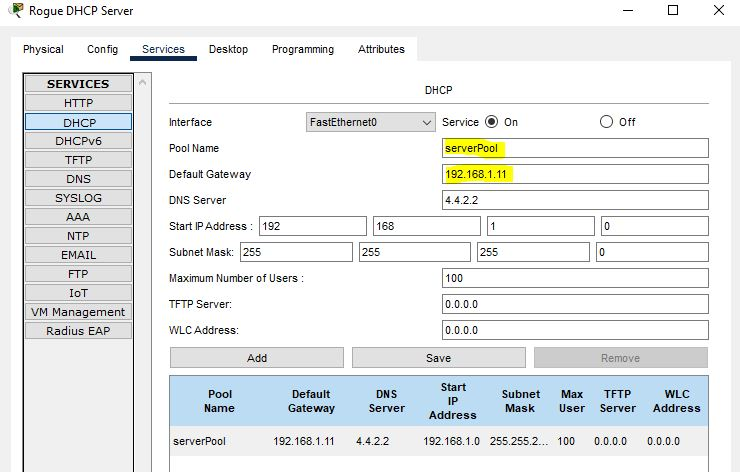
Figure 2: Rogue Dhcp Tool | Find Rogue Dhcp Server – XOLLN The 802.11 standard provides several distinct radio frequency ranges for use in Wi-Fi communications: 900 MHz, 2.4 GHz, 3.6 GHz, 4.9 GHz, 5 GHz, 6 GHz and 60 GHz bands. Each range is divided into a multitude of channels. In the standards, channels are numbered at 5 MHz spacing within a band (except in the 60 GHz band, where they are 2.16 GHz apart), and the number refers to the centre frequency of the channel. Although channels are numbered at 5 MHz spacing, transmitters generally occupy at least 20 MHz, and standards allow for neighbouring channels to be bonded together to form a wider channel for higher throughput. Countries apply their own regulations to the allowable channels, allowed users and maximum power levels within these frequency ranges. 802.11b/g/n can use the 2.4 GHz band, operating in the United States under FCC Part 15 rules and regulations. In this frequency band, equipment may occasionally suffer interference from microwave ovens, cordless telephones, USB 3.0 hubs, Bluetooth and other devices. Spectrum assignments and operational limitations are not consistent worldwide: Australia and Europe allow for an additional two channels (12, 13) beyond the 11 permitted in the United States for the 2.4 GHz band, while Japan has three more (12–14). 802.11a/h/j/n/ac/ax can use the 5 GHz U-NII band, which, for much of the world, offers at least 23 non-overlapping 20 MHz channels. This is in contrast to the 2.4 GHz frequency band where the channels are only 5 MHz wide. In general, lower frequencies have longer range but have less capacity. The 5 GHz bands are absorbed to a greater degree by common building materials than the 2.4 GHz bands and usually give a shorter range. As 802.11 specifications evolved to support higher throughput, the protocols have become much more efficient in their bandwidth use. Additionally, they have gained the ability to aggregate channels together to gain still more throughput where the bandwidth for additional channels is available. 802.11n allows for double radio spectrum bandwidth (40 MHz) per channel compared to 802.11a or 802.11g (20 MHz). 802.11n can be set to limit itself to 20 MHz bandwidth to prevent interference in dense communities. In the 5 GHz band, 20 MHz, 40 MHz, 80 MHz, and 160 MHz channels are permitted with some restrictions, giving much faster connections.
Wi-Fi is part of the IEEE 802 protocol family. The data is organized into 802.11 frames that are very similar to Ethernet frames at the data link layer, but with extra address fields. MAC addresses are used as network addresses for routing over the LAN. Wi-Fi's MAC and physical layer (PHY) specifications are defined by IEEE 802.11 for modulating and receiving one or more carrier waves to transmit the data in the infrared, and 2.4, 3.6, 5, 6, or 60 GHz frequency bands. They are created and maintained by the IEEE LAN/MAN Standards Committee (IEEE 802). The base version of the standard was released in 1997 and has had many subsequent amendments. The standard and amendments provide the basis for wireless network products using the Wi-Fi brand. While each amendment is officially revoked when incorporated in the latest version of the standard, the corporate world tends to market to the revisions because they concisely denote capabilities of their products. As a result, in the market place, each revision tends to become its own standard. In addition to 802.11, the IEEE 802 protocol family has specific provisions for Wi-Fi. These are required because Ethernet's cable-based media are not usually shared, whereas with wireless all transmissions are received by all stations within the range that employ that radio channel. While Ethernet has essentially negligible error rates, wireless communication media are subject to significant interference. Therefore, the accurate transmission is not guaranteed so delivery is, therefore, a best-effort delivery mechanism. Because of this, for Wi-Fi, the Logical Link Control (LLC) specified by IEEE 802.2 employs Wi-Fi's media access control (MAC) protocols to manage retries without relying on higher levels of the protocol stack. For internetworking purposes, Wi-Fi is usually layered as a link layer below the internet layer of the Internet Protocol. This means that nodes have an associated internet address and, with suitable connectivity, this allows full Internet access.
In infrastructure mode, which is the most common mode used, all communications go through a base station. For communications within the network, this introduces an extra use of the airwaves but has the advantage that any two stations that can communicate with the base station can also communicate through the base station, which limits issues associated with the hidden node problem and simplifies the protocols.
An Extended Service Set may be formed by deploying multiple access points that are configured with the same SSID and security settings. Wi-Fi client devices typically connect to the access point that can provide the strongest signal within that service set. Increasing the number of Wi-Fi access points for a network provides redundancy, better range, support for fast handover, and increased overall network capacity by using more channels or by defining smaller cells. Except for the smallest implementations (such as home or small office networks), Wi-Fi implementations have moved toward thin access points, with more of the network intelligence housed in a centralized network appliance, relegating individual access points to the role of dumb transceivers. Outdoor applications may use mesh topologies.
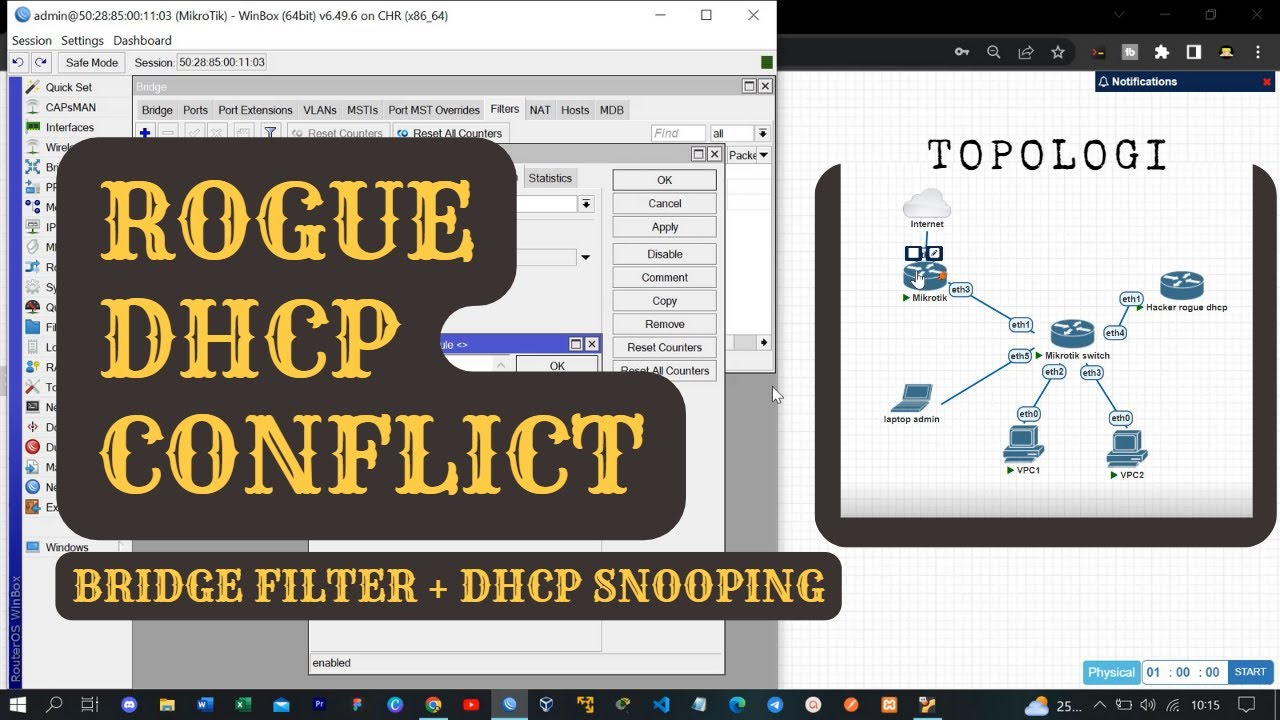
Figure 3: Cara Mengatasi Rogue dhcp server & konflik dhcp menggunakan bridge ... Wi-Fi operational range depends on factors such as the frequency band, modulation technique, transmitter power output, receiver sensitivity, antenna gain and type, and propagation and interference characteristics in the environment. At longer distances, speed is typically reduced.
Wi-Fi 4 and higher standards allow devices to have multiple antennas on transmitters and receivers. Multiple antennas enable the equipment to exploit multipath propagation on the same frequency bands, giving higher speeds and more than doubled range. The Wi-Fi 5 standard uses the 5 GHz band exclusively, and is capable of multi-station WLAN throughput of at least 1 gigabit per second, and a single station throughput of at least 500 Mbit/s. This standard uses several signal processing techniques such as multi-user MIMO and 4 × 4 spatial multiplexing streams, and wide channel bandwidth (160 MHz) to achieve its gigabit throughput.
2. System Architecture & Core Working Principles Wi-Fi connections can be blocked or the network throughput lowered by having other devices in the same area. Wi-Fi protocols are designed to share the radio bandwidth reasonably fairly. To minimize collisions with Wi-Fi and non-Wi-Fi devices, Wi-Fi employs Carrier-sense multiple access with collision avoidance (CSMA/CA), where transmitters listen before transmitting and delay transmission of packets if they detect that other devices are active on the channel, or if noise is detected from adjacent channels or non-Wi-Fi sources. Nevertheless, Wi-Fi networks are still susceptible to the hidden node and exposed node problems. A standard speed Wi-Fi signal occupies five channels in the 2.4 GHz band. Adjacent-channel interference can be caused by overlapping channels. Any two channel numbers that differ by five or more, such as 2 and 7, do not overlap. Channels 1, 6, and 11 are the only group of three non-overlapping channels in North America. However, whether the overlap is significant depends on physical spacing. Channels that differ by four interfere a negligible amount – much less than reusing channels (which causes co-channel interference) – if transmitters are at least a few metres apart. In Europe and Japan where channel 13 is available, using Channels 1, 5, 9, and 13 for 802.11g and 802.11n is viable and recommended.
However, multiple 2.4 GHz 802.11b and 802.11g access points default to the same channel on initial startup, contributing to congestion on certain channels. Wi-Fi pollution, or an excessive number of access points in the area, can prevent access and interfere with other devices' use of other access points, as well as decreasing overall signal-to-noise ratio (SNR). These issues can become a problem in high-density areas, such as large apartment complexes or office buildings with multiple Wi-Fi access points. It is also an issue when municipalities or other large entities (such as universities) seek to provide large area coverage. Other devices use the 2.4 GHz band: microwave ovens, ISM band devices, security cameras, Zigbee devices, Bluetooth devices, video senders, cordless phones, baby monitors, and, in some countries, amateur radio, all of which can cause significant additional interference. On some 5 GHz bands interference from radar systems can occur in some places.
Access points that support those bands employ dynamic frequency selection, which listens for radar, and if detected, will not permit transmission on that band. These bands can be used by low-power transmitters without a licence, and with few restrictions. However, while unintended interference is common, users who have been found to cause deliberate interference (particularly for attempting to locally monopolize these bands for commercial purposes) have been issued large fines.
A wireless access point (WAP) connects a group of wireless devices to an adjacent wired LAN. An access point functions as a network hub, relaying data between connected wireless devices in addition to a wired network, allowing wireless devices to communicate with other wired devices, typically also providing access to devices on the Internet. Wireless adapters allow devices to connect to a wireless network. These adapters connect to devices using various external or internal interconnects such as mini PCIe, USB, ExpressCard and earlier, PCI, Cardbus, and PC Card. Computers now routinely come equipped with built-in wireless adapters.
Wireless routers integrate a Wireless Access Point, Ethernet switch, and internal router firmware application that provides IP routing, NAT, and DNS forwarding through an integrated WAN-interface. A wireless router allows wired and wireless Ethernet LAN devices to connect to a (usually) single WAN device such as a cable modem, DSL modem, or optical modem. A wireless router allows all three devices, mainly the access point and router, to be configured through one central utility. This utility is usually an integrated web server that is accessible to wired and wireless LAN clients and often optionally to WAN clients. This utility may also be an application that is run on a computer, as is the case with as Apple's AirPort, which is managed with the AirPort Utility on macOS and iOS.
The security standard, Wi-Fi Protected Setup, allows embedded devices with a limited graphical user interface to connect to the Internet with ease. Wi-Fi Protected Setup has 2 configurations: The Push Button configuration and the PIN configuration. These embedded devices are also called The Internet of things and are low-power, battery-operated embedded systems. Several Wi-Fi manufacturers design chips and modules for embedded Wi-Fi, such as GainSpan. Increasingly in the last few years (particularly as of 2007), embedded Wi-Fi modules have become available that incorporate a real-time operating system and provide a simple means of wirelessly enabling any device that can communicate via a serial port. This allows the design of simple monitoring devices. An example is a portable ECG device monitoring a patient at home. This Wi-Fi-enabled device can communicate via the Internet. These Wi-Fi modules are designed by OEMs so that implementers need only minimal Wi-Fi knowledge to provide Wi-Fi connectivity for their products. In June 2014, Texas Instruments introduced the first ARM Cortex-M4 microcontroller with an onboard dedicated Wi-Fi MCU, the SimpleLink CC3200. It makes embedded systems with Wi-Fi connectivity possible to build as single-chip devices, which reduces their cost and minimum size, making it more practical to build wireless-networked controllers into inexpensive ordinary objects.
The main issue with wireless network security is its simplified access to the network compared to traditional wired networks such as Ethernet. With wired networking, one must either gain access to a building (physically connecting into the internal network), or break through an external firewall. To access Wi-Fi, one must merely be within the range of the Wi-Fi network. Most business networks protect sensitive data and systems by attempting to disallow external access. Enabling wireless connectivity reduces security if the network uses inadequate or no encryption. An attacker who has gained access to a Wi-Fi network router can initiate a DNS spoofing attack against any other user of the network by forging a response before the queried DNS server has a chance to reply.
A flaw in a feature added to Wi-Fi in 2007, called Wi-Fi Protected Setup (WPS), let WPA and WPA2 security be bypassed. The only remedy as of 2011 was to turn off Wi-Fi Protected Setup, which is not always possible. Virtual private networks can be used to improve the confidentiality of data carried through Wi-Fi networks, especially public Wi-Fi networks. A URI using the Wi-Fi scheme can specify the SSID, encryption type, password/passphrase, and if the SSID is hidden or not, so users can follow links from QR codes, for instance, to join networks without having to manually enter the data. A MeCard-like format is supported by Android and iOS 11+.
Common format: WIFI:S:
Wireless Internet access has become much more embedded in society. It has thus changed how the society functions in a number of ways. As of 2017 over half the world did not have access to the Internet, prominently rural areas in developing nations. Technology that has been implemented in more developed nations is often costly and energy inefficient. This has led to developing nations using more low-tech networks, frequently implementing renewable power sources that can solely be maintained through solar power, creating a network that is resistant to disruptions such as power outages. For instance, in 2007, a 450-kilometre (280 mi) network between Cabo Pantoja and Iquitos in Peru was erected in which all equipment is powered only by solar panels. These long-range Wi-Fi networks have two main uses: offer Internet access to populations in isolated villages, and to provide healthcare to isolated communities. In the case of the latter example, it connects the central hospital in Iquitos to 15 medical outposts which are intended for remote diagnosis.
The World Health Organization (WHO) says, "no health effects are expected from exposure to RF fields from base stations and wireless networks", but notes that they promote research into effects from other RF sources. Although the WHO's International Agency for Research on Cancer (IARC) later classified radio-frequency electromagnetic fields (EMFs) as "possibly carcinogenic to humans (Group 2B)" (a category used when "a causal association is considered credible, but when chance, bias or confounding cannot be ruled out with reasonable confidence"), this classification was based on risks associated with wireless phone use rather than Wi-Fi networks. The United Kingdom's Health Protection Agency reported in 2007 that exposure to Wi-Fi for a year results in the "same amount of radiation from a 20-minute mobile phone call". A review of studies involving 725 people who claimed electromagnetic hypersensitivity, "...suggests that 'electromagnetic hypersensitivity' is unrelated to the presence of an EMF, although more research into this phenomenon is required." Bluetooth Low Energy, a low-power variant of Bluetooth Bluetooth, a short-distance network Cellular networks, used by smartphones LoRa, for long-range wireless with low data rate NearLink, a short-range wireless technology standard WiMAX, for providing long-range wireless internet connectivity Zigbee, a low-power, low data rate, short-distance communication protocol Several wired technologies for computer networking, which provide viable alternatives to Wi-Fi: Rogue DHCP servers can redirect client traffic by providing malicious gateway or DNS addresses, and can be detected using network scanning tools, dhcp-probe, and DHCP server logs.
3. Software Implementation, Frameworks & Protocols Every OneUptime blog post is open source. Found a typo, an inaccuracy, or have a clearer way to explain something? Anyone can contribute — your edits make this post better for everyone who reads it next. Your complete reliability stack unified: infrastructure monitoring, incident management, status pages, and APM. Open-source and self-hostable.
Network Security, Network Monitoring and Analysis, Network Configuration and Management, Switch Configuration, Troubleshooting In this Packet Tracer lab, I will be identifying a rogue DHCP server in the network. Rogue DHCP servers can be used for malicious purposes, such as intercepting or redirecting network traffic, launching on-path attacks, or spreading malware.
To resolve this issue, I will enable DHCP snooping on the switch so that it only accepts DHCP traffic from the authorized DHCP server and not the rogue server. DHCP snooping is a security feature that filters and monitors DHCP messages, allowing only legitimate DHCP server responses and dropping any unauthorized or malicious DHCP traffic. To set up this lab, I will first configure the address pools both servers can allocate IP addresses from: I will configure the network sniffer device to track DHCP packets. It analyzes the captured packets to identify DHCP traffic and examine the details of DHCP messages, including the source and destination IP addresses, MAC addresses, and DHCP options. By examining the source IP address and MAC address of DHCP Offer and Acknowledgment messages, a network sniffer can help identify DHCP servers operating on the network.
I will enable both PCs to obtain IP addresses via DHCP. PC0 is assigned an IP address (172.16.0.1) from the authorized server, however, PC1 is assigned an IP address (192.168.1.3) from the rogue server. In the sniffer packet captures, I can see the MAC addresses of both the authorized and rogue DHCP servers. As a network administrator, I would have a record of the MAC address of the authorized server so that I can compare it to any rogue servers on the network.
To configure the switch so that it only accepts DHCP traffic from the authorized server, I will enable DHCP snooping on it: It fails because I have not set a trusted interface on the switch to receive DHCP packets. Since the F0/3 interface on the switch is linked to the authorized DHCP server, I will set it to trusted. After setting interface F0/3 as trusted, all other switch interfaces that receive DHCP packets will drop those packets.
PC1 now receives an IP address from the authorized DHCP server, and not the rogue server. You’ve probably happened across this little conundrum at least once or twice—troubleshooting a network issue where users are connecting to the network, but they aren’t able to access any resources or the internet. 4. Practical Deployment, Analysis & Case Studies You start going through your troubleshooting workflow: check the physical layer, data link layer, network layer… and there’s the problem. The device has an IP address, but it’s not an IP address you’d expect to see on your network.
Did someone set this IP address up manually? Maybe it was a “helpful” user, who knows just enough to get into trouble? That’s not it. Turns out to be an invalid IP address from a DHCP. Congratulations, you have a rogue DHCP server on your hands! From incomplete/inaccurate documentation to relying on CLI as a primary data source, learn to identify AND fix blind spots.
Before diving into Rogue DHCP, let’s do a quick review of what DHCP actually is. DHCP, or the Dynamic Host Control Protocol, was established to automate the process of adding new IP addresses to the network. In the early days, networks had a limited number of workstations, and each one was given a hard-coded IP address when added to the network. This simple process was quickly outgrown because of the difficulty and resource-intensive nature of doing IP address assignments by hand. Network managers were keeping lists of IP addresses on spreadsheets. Multiple network technicians would assign the same address to different devices on the same network, causing IP address conflicts everywhere . DHCP was developed to allow a dedicated server to be set up to assign IP addresses to all devices connecting to the network, automating what used to be a very manual process.
How it works is pretty straightforward. As a device enters the network, it tells every device it needs (broadcasts a request for) an IP address. A dedicated DHCP server, listening for kinds of requests, responds with a DHCP response : assigning an IP address to the device from its pool of addresses. DHCP can also be used (and is most often used) to assign a default gateway and a DNS server to a device. This keeps the information centralized, reduces the use of resources, and greatly increases the efficiency of standard network operations.
Simply put, a rogue DHCP server is one that is not authorized to provide IP addresses to devices on your network. Rogue DHCP servers can be malicious, like in a man-in-the-middle attack , or simply inconvenient, as in the case of a user connecting an unauthorized home router to their work network. In other words, a rogue DHCP server is simply a server not under the management or even the awareness of network management staff . Either way, they can be quite a pain. If a rogue DHCP server gets to your devices first, it can wreak all kinds of havoc on your network: performance or seed issues, inability to reach needed resources and connectivity problems.
And because the misconfigured DHCP server is just sitting out there waiting to be used, it becomes a prime target for malicious actors. Here’s how they work, step by step: If it’s a malicious DHCP server, this is where bad things can start to happen. The rogue DHCP server can start to assign malicious default gateway information that can redirect legitimate devices to an unauthorized default gateway. Or it can act as the unauthorized default gateway itself, routing all traffic through that malicious device.
In my experience, it’s far more common to have an unintentional rogue DHCP server on your network, the result of misconfiguration or a “helpful” employee. That doesn’t mean that malicious DHCP servers never occur but don’t assume that it’s malicious right out of the gate. There are a variety of ways to detect a rogue DHCP server. One common way is through general troubleshooting. For example, a specific workstation is having problems connecting to network resources. On investigation, you find that the workstation is not within the scope of IP addresses assigned for the segment it’s supposed to be in. This is a definite red flag that a rogue DHCP server is on your network. At this point, you’ll immediately want to start tracking it down.
If you’re looking to be more proactive in your search for rogue DHCP servers, use a network (packet) sniffer or look in the sFlow data collected by your network traffic analysis tool for packets coming from UDP port 67 (the standard DHCP port) on servers other than your approved DHCP server. You can also leverage your syslog tool to check server logs for certain events. A few event terms to look out for include, “server upgraded,” “unreachable domain,” and “the server found in our domain.” On networks where you’d expect all devices to be domain-joined, “Microsoft-windows-DHCP-server, DHCP/BINL” is a big event to watch out for, as this means a server does not belong to any domain, because the domain field is empty.
If any of these are found, it’s an indicator that there’s likely a rogue DHCP server hanging around. Once a rogue DHCP server is discovered, speedy resolution is critical. The opportunity for havoc, or even a man-in-the-middle attack, is possible at any time. The best way to mitigate these rogue DHCP incidents is to remove the rogue DHCP devices from your network or shut down the switch ports they are connected to.
5. Performance Evaluation & Extended Technical Observations DHCP server issues can lead to very serious problems, especially if an attack is launched. That’s because it can be a long time before a rogue DHCP server is discovered, and an attack may not occur immediately. A malicious rogue DHCP server may spend days or even months servicing DHCP requests and at the same time collecting all types of sensitive information from your network before an attack is actually launched. You’ll be in a zero-day situation (a vulnerability that’s exploited before it’s discovered) and scrambling to recover. On the flip side, you can also discover rogue DHCP servers very quickly if it’s unintentional, as many (but probably not all) of your users will suddenly not be able to connect to the network.
As with all network security issues, prevention is the best protection. Let’s look a few basic steps you can take to find and prevent rogue DHCP servers. One of the most effective ways to prevent rogue DHCP servers is to look for address conflicts and misconfigured IP addresses. This involves employing an actively monitored and effective IP address allocation and control system. There are many ways to do this. You can do it manually, or use network management tools to take control of the process.
This article goes into detail on how to find and fix IP address conflicts . I strongly suggest reviewing these techniques to further understand the process and how to find these types of address conflicts, because conflicts can cause many other problems beyond just helping you identify rogue DHCP servers. As with many networking issues, proper network documentation is key to preventing problems. You should know your DHCP servers, where they are, and what configuration details you have on them.
The process of using your Microsoft Active Directory to provide authorization for DHCP servers can be a lot of help in the prevention of rogue DHCP servers. The domain controller keeps a secure database of active authorized DHCP resources. And if the DHCP server is not authorized, it won’t be added to the network. The best and most proactive configuration change you can make to prevent rogue DHCP servers on your network is to enable DHCP snooping on your managed network switches. Most modern switches have DHCP snooping built in, which means that they are actively looking for DHCP response packets within a specific VLAN or on a specific interface, and will notify you or lock down a port when DHCP responses are detected. By default, these switches will block DHCP replies coming in from a specific port—typically referred to as “untrusted interfaces.” You’ll want to configure the port your legitimate DHCP server is plugged into as a “trusted” interface, so it can reply to DHCP requests. This is the most effective way to prevent rogue DHCP servers from being added to a segment.
Just like steps to prevention, best practices come down to documentation and maintaining network visibility. Here’s a process you can incorporate into your routines (automated or otherwise) to keep your DHCP management in the best possible shape. Good security requires active, ongoing prevention. What happens when some other network manager turns off AD DS authorization when troubleshooting a problem, and forgets to turn it back on? It happens all the time. If you are not performing the correct maintenance and preventative steps, you will miss it.
A lightweight PowerShell script that detects rogue DHCP servers on your network using tshark (from Wireshark). It continuously monitors DHCP OFFER and ACK packets and alerts when the responding server is not in your list of trusted DHCP servers. Rogue Dynamic Host Configuration Protocol (DHCP) servers can disrupt any network. This article covers what a rogue DHCP server is and describes the Cisco Meraki features that help you find and locate the rogue device.
DHCP automatically configures connection information for devices that do not have static IP assignments. Unless specifically configured to work together, multiple DHCP servers can cause clients and network devices to receive conflicting IP addresses, subnet masks, gateway IP addresses, and other network information. This conflict typically appears as groups of clients sporadically losing connection to the internet and other network resources.
This issue most often occurs when users incorrectly attach a device to the network that provides DHCP service, such as connecting a consumer router via a LAN port. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Wi-Fi • https://oneuptime.com/blog/post/2026-03-20-detect-rogue-dhcp-servers-network/view • https://marcdlc-cs.github.io/roguedhcp • https://www.auvik.com/franklyit/blog/rogue-dhcp-server/ • https://github.com/Leproide/Rogue-DHCP-detector • https://documentation.meraki.com/SASE_and_SD-WAN/MX/Troubleshooting_and_Support/Troubleshooting/Tracking_Dow n_Rogue_DHCP_Servers
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Rogue Dhcp Server Detection System In Local Network.
! Define Extended Access List to Block Malicious Traffic ip access-list extended SECURE_PERIMETER_ACL remark Block Inbound Telnet and Unencrypted Services deny tcp any any eq 23 log remark Permit Verified Web SSL Traffic permit tcp any any eq 443 permit tcp any any eq 80 remark Mitigate ICMP Flood and Ping Sweeps permit icmp any any echo-reply deny icmp any any echo log deny ip any any log
! Apply ACL to Ingress Interface GigabitEthernet0/0 interface GigabitEthernet0/0 ip access-group SECURE_PERIMETER_ACL in no shutdown end write memory
Extended IP access list SECURE_PERIMETER_ACL (Cisco Packet Tracer) ──────────────────────────────────────────────────────────────────────── 10 deny tcp any any eq telnet log (142 matches) [Probes Dropped] 20 permit tcp any any eq 443 (18402 matches) [TLS 1.3 Traffic Permitted] 30 permit tcp any any eq 80 (4812 matches) 40 deny icmp any any echo log (524 matches) [Flood Mitigated] 50 deny ip any any log (38 matches) [Default Implicit Deny Rule] ──────────────────────────────────────────────────────────────────────── [✓] Packet Tracer Verification: 0 Unsanitized Ingress Leaks on Gi0/0
| Interface Port | Network Zone | Filter Applied | Traffic Processed | Firewall Decision |
|---|---|---|---|---|
| Gig0/0 (WAN) | Untrusted External | Extended ACL 101 | 24,810 Packets | INSPECTED & FILTERED |
| Gig0/1 (DMZ) | Public Web Services | Port 443 Only | 18,402 Packets | PERMITTED |
| Gig0/2 (LAN) | Corporate Users | 802.1X Port Security | 142 Probes | DENIED & QUARANTINED |