Complete Technical Paper Content — Role Based Access Control System In Flask Web Framework
Overview & System Context
Role Based Access Control System In Flask Web Framework: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~4731 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background A web framework (WF), web application framework (WAF), or web development framework is a software framework that is designed to support the development of web applications including web services, web resources, and web APIs. Web frameworks provide a standard way to build and deploy web applications on the World Wide Web. Web frameworks aim to automate the overhead associated with common activities performed in web development. For example, many web frameworks provide libraries for database access, templating frameworks, and session management, and they often promote code reuse. Although they often target development of dynamic web sites, they are also applicable to static websites.
As the design of the World Wide Web was not inherently dynamic, early hypertext consisted of hand-coded HTML text files that were published on web servers. Any modifications to published pages needed to be performed by the pages' author. In 1993, the Common Gateway Interface (CGI) standard was introduced for interfacing external applications with web servers, to provide a dynamic web page that reflected user inputs. Original implementations of the CGI interface typically had adverse effects on the server load however, because each request started a separate process. More recent implementations utilize persistent processes amongst other techniques to reduce the footprint in the server's resources and offer a general performance boost. In 1995, fully integrated server/language development environments first emerged and new web-specific languages were introduced, such as ColdFusion, PHP, and Active Server Pages. Although the vast majority of languages for creating dynamic web pages have libraries to help with common tasks, web applications often require specific libraries for particular tasks, such as creating HTML (for example, Jakarta Faces). In the late 1990s, mature, "full stack" frameworks began to appear, that often gathered multiple libraries useful for web development into a single cohesive software stack for web developers to use.
Many frameworks follow the MVC architectural pattern to separate the data model into business rules (the "controller") and the user interface (the "view"). This is generally considered a good practice as it modularizes code, promotes code reuse, and allows multiple interfaces to be applied. In web applications, this permits different views to be presented, for example serving different web pages for mobile vs. desktop browsers, or providing machine-readable web service interfaces.
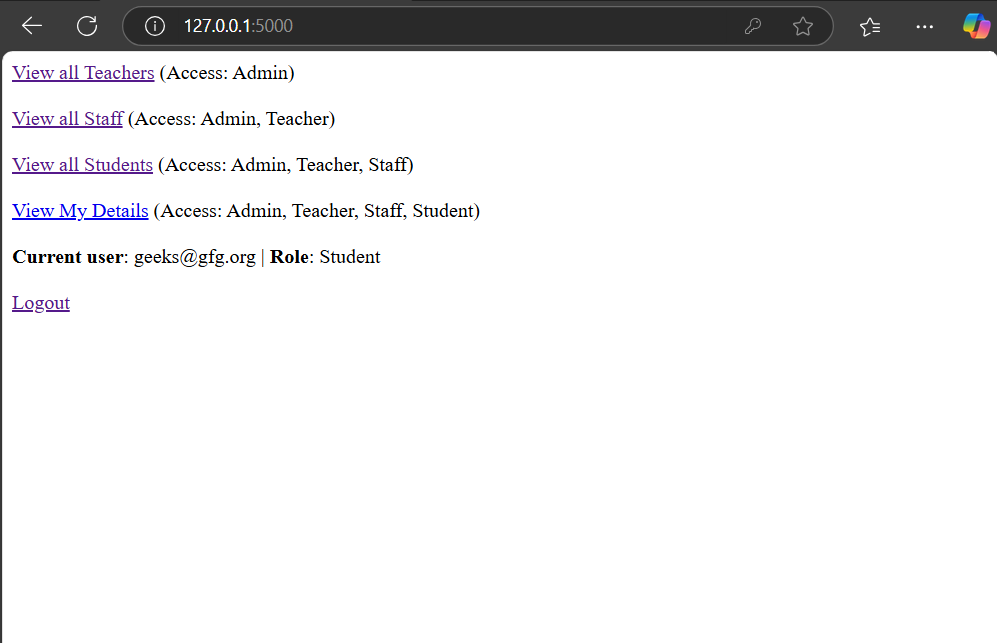
Examples include Backbone.js, AngularJS, Angular, Ember.js, React, jQuery UI, Svelte, and Vue.js. Figure 1: Flask - Role Based Access Control - GeeksforGeeks Web caching is the caching of web documents in order to reduce bandwidth usage, server load, and perceived "lag". A web cache stores copies of documents passing through it; subsequent requests may be satisfied from the cache if certain conditions are met. Some application frameworks provide mechanisms for caching documents and bypassing various stages of the page's preparation, such as database access or template interpretation.
Some web frameworks come with authentication and authorization frameworks, that enable the web server to identify the users of the application, and restrict access to functions based on some defined criteria. Drupal is one example that provides role-based access to pages, and provides a web-based interface for creating users and assigning them roles. A framework's URL mapping or routing facility is the mechanism by which the framework interprets URLs. Some frameworks, such as Drupal and Django, match the provided URL against pre-determined patterns using regular expressions, while some others use rewriting techniques to translate the provided URL into one that the underlying engine will recognize. Another technique is that of graph traversal such as used by Zope, where a URL is decomposed in steps that traverse an object graph (of models and views). A URL mapping system that uses pattern matching or rewriting to route and handle requests allows for shorter more "friendly URLs" to be used, increasing the simplicity of the site and allowing for better indexing by search engines. For example, a URL that ends with "/page.cgi?cat=science&topic=physics" could be changed to simply "/page/science/physics". This makes the URL easier for people to remember, read and write, and provides search engines with better information about the structural layout of the site. A graph traversal approach also tends to result in the creation of friendly URLs. A shorter URL such as "/page/science" tends to exist by default as that is simply a shorter form of the longer traversal to "/page/science/physics".
Ajax, shorthand for "Asynchronous JavaScript and XML", is a web development technique for creating web applications. The intent is to make web pages feel more responsive by exchanging small amounts of data with the server behind the scenes, so that the entire web page does not have to be reloaded each time the user requests a change. This is intended to increase a web page's interactivity, speed, maintainability, and usability. Due to the complexity of Ajax programming in JavaScript, there are numerous Ajax frameworks that exclusively deal with Ajax support. Some Ajax frameworks are even embedded as a part of larger frameworks. For example, the jQuery JavaScript library is included in Ruby on Rails. With the increased interest in developing "Web 2.0" rich web applications, the complexity of programming directly in Ajax and JavaScript has become so apparent that compiler technology has stepped in, to allow developers to code in high-level languages such as Java, Python and Ruby. The first of these compilers was Morfik followed by Google Web Toolkit, with ports to Python and Ruby in the form of Pyjs and RubyJS following some time after. These compilers and their associated widget set libraries make the development of rich media Ajax applications much more akin to that of developing desktop applications.
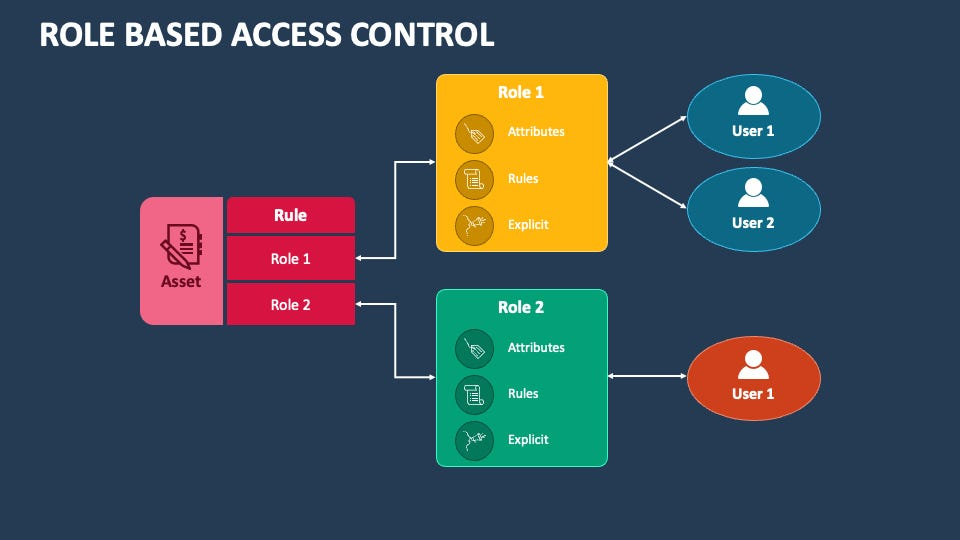
Figure 2: Step-by-Step Guide: Deploying a Flask Application to a Linux Server ... Some frameworks provide tools for creating and providing web services. These utilities may offer similar tools as the rest of the web application. A number of newer Web 2.0 RESTful frameworks are now providing resource-oriented architecture (ROA) infrastructure for building collections of resources in a sort of Semantic Web ontology, based on concepts from Resource Description Framework (RDF).
This is a comparison of notable web frameworks, software used to build and deploy web applications. This article focuses on frameworks used for building the backend. Common Gateway Interface, used before web frameworks Comparison of shopping cart software Content management system Dynamic web page Java view technologies and frameworks List of content management systems List of rich web application frameworks List of web service frameworks Figure 3: Flask RBAC: How to Implement Role-Based Access Control in a Flask ...
The Python programming language is actively used by many people, both in industry and academia, for a wide variety of purposes. Atom — an open-source cross-platform IDE with autocomplete, help and more Python features under package extensions. Codelobster — a cross-platform IDE for various languages, including Python. Colab — Jupyter notebook online integrated development environment developed by Google. EasyEclipse — an open-source IDE for Python and other languages. Eclipse — with the Pydev plug-in. Eclipse supports many other languages as well. Emacs, with the built-in python-mode. Eric — an IDE for Python and Ruby. Geany — IDE for Python development and other languages. IDLE — a simple IDE bundled with the default implementation of the language. Jupyter Notebook — an IDE that supports markdown, Python, Julia — R and several other languages. Kaggle Notebooks — an online IDE for Python and R with integrated data science libraries, free GPUs, and collaborative features. Komodo IDE — an IDE PHOTOS Python, Perl, PHP and Ruby. Neovim — has python support with pynvim. NetBeans — is written in Java and runs everywhere where a JVM is installed. PyCharm — a proprietary and open-source IDE for Python development. PythonAnywhere — an online IDE and Web hosting service. Python Tools for Visual Studio — Free and open-source plug-in for Visual Studio. Spyder — IDE for scientific programming. Thonny — beginner-friendly Python IDE. Vim — with "lang#python" layer enabled. Visual Studio Code — an open-source IDE for various languages, including Python. Wing IDE — cross-platform proprietary with some free versions/licenses IDE for Python. Replit — an online IDE that supports multiple languages.
BlueBream – a rewrite by the Zope developers of the Zope 2 web application server. CherryPy – an object-oriented web application server and framework. CubicWeb – a web framework that targets large-scale semantic web and linked open data applications and international corporations. Django – an MVT (model, view, template) web framework. Flask – a modern, lightweight, well-documented micro-framework based on Werkzeug and Jinja 2. Google App Engine – a platform for developing and hosting web applications in Google-managed data centers, including Python. Grok – a web framework based on Zope Toolkit technology. Nevow – a web application framework originally developed by the company Divmod. Pylons – a lightweight web framework emphasizing flexibility and rapid development. Pyramid – a minimalistic web framework inspired by Zope, Pylons and Django. Python Paste – a set of utilities for web development that has been described as "a framework for web frameworks". Quixote – a framework for developing Web applications in Python. RapidSMS – a web framework which extends the logic and capabilities of Django to communicate with SMS messages. Spyce – a technology to embed Python code into webpages. Tornado – a lightweight non-blocking server and framework. TurboGears – a web framework combining SQLObject/SQLAlchemy, Kid/Genshi, and CherryPy/Pylons. web2py – a full-stack enterprise web application framework, following the MVC design. Zope 2 – an application server, commonly used to build content management systems.
Apache MXNet — open-source deep learning framework for deep neural networks. Apache Singa — library for deep learning. Apache SystemDS — machine learning system for the end-to-end data science lifecycle. Caffe — deep learning framework. CatBoost — machine learning library for gradient boosting on decision trees. Chainer — deep learning framework on top of NumPy and CuPy. Deeplearning4j — open-source deep learning library for the Java virtual machine. DeepSpeed — deep learning optimization library. Dlib — software library with machine learning algorithms. fastText — library for efficient text classification and word embeddings. Gensim — library for topic modeling and vector space modeling. H2O — software for machine learning and predictive analytics. Horovod — framework by Uber for distributed deep learning training using TensorFlow, Keras, PyTorch, and Apache MXNet. Hugging Face Transformers — deep learning library for training and running pretrained transformer models. JAX — software library for machine learning, artificial intelligence, and high-performance numerical computing. Jubatus — platform for distributed online machine learning. Keras — high-level neural networks API, running on top of TensorFlow and other backends. LightGBM — gradient boosting framework.
MindSpore — deep learning framework developed by Huawei. Orange — open-source data visualization, machine learning, and data mining toolkit. PlaidML — tensor compiler. PyTorch — open-source machine learning library based on the Torch library. PyTorch Lightning — provides a high-level interface for PyTorch. QLattice — symbolic regression. scikit-learn — library for machine learning. Spark MLlib — distributed machine learning library for Apache Spark. TensorFlow — software library for machine learning and artificial intelligence. Theano — machine learning library. Transformers Library — mainly compatible with the PyTorch library from Hugging Face. Vowpal Wabbit — machine learning system for fast online learning.
XGBoost — gradient boosting library. Abaqus (Finite Element Software) ADvantage Framework Amarok ArcGIS – a prominent GIS platform, allows extensive modelling using Python. Autodesk Maya – a professional 3D modeler allows Python scripting as an alternative to MEL as of version 8.5. Autodesk MotionBuilder Autodesk Softimage (formerly Softimage|XSI) BioNumerics – a bioinformatics software suite for the management, storage and (statistical) analysis of all types of biological data. Blender Boxee – a cross-platform home theater PC software. Cinema 4D Civilization IV has the map editor supporting Python. Corel Paint Shop Pro Claws Mail with Python plugin DSHub ERDAS Imagine FL Studio – a Digital audio workstation, uses Python to support MIDI Controller integration, as well as scripting within its piano roll and Edison audio editor. FreeCAD gedit GIMP GNAT – The GNAT programming chain tool (Ada language implementation in GNU gcc), as a GNATcoll reusable components for the applications (with or without PyGTK) and as a scripting language for the commands in the GPS programming environment. Houdini highly evolved 3D animation package, fully extensible using python. Inkscape – a free vector graphics editor. Krita – a free raster graphics editor for digital painting. MeVisLab – a medical image processing and visualization software, uses Python for network scripting, macro modules, and application building. Modo Minecraft: Pi Edition (game). MSC.Software's CAE packages: Adams, Mentat, SimXpert. MySQL Workbench – a visual database design tool. Nuke (compositing for visual effects) OriginPro – a commercial graphic and analysis software, provides Python environment for access. ParaView, an opensource scientific visualization software Poser – a 3D rendering and animation computer program that uses for scripting a special dialect of Python, called PoserPython. PTV AG products for traffic and transportation analysis, including PTV VISSIM.
PyMOL – a popular molecular viewer that embeds Python for scripting and integration. OriginPro – a commercial graphing and analysis software, provides a Python environment for both embedded and external access. QGIS uses Python for scripting and plugin-development. Rhinoceros 3D version 5.0 and its visual-scripting language Grasshopper uses IronPython. Rhythmbox Scribus 3DSlicer – a medical image visualisation and analysis software. Python is available for algorithm implementation, analysis pipelines, and GUI creation. SPSS statistical software – SPSS Programmability Extension allows users to extend the SPSS command syntax language with Python. SublimeText Totem – a media player for the GNOME desktop environment. Vim VisIt WeeChat – a console IRC client.
CLPython – Implementation, written in Common Lisp. CPython – The reference implementation, written in C11. Some notable distributions include: ActivePython – Distribution with more than 300 included packages. Intel Distribution for Python – High performance distribution with conda and pip package managers. PSF Python – Reference distribution that includes only selected standard libraries Cython – programming language to simplify writing C and C++ extension modules for the CPython Python runtime. IronPython – Python for CLI platforms (including .NET and Mono). Jython – Python for Java platforms.
MicroPython – Python 3 implementation for micro-controller platforms. Nuitka – a source-to-source compiler which compiles Python code to C/C++ executables, or source code. Numba – NumPy aware LLVM-based JIT compiler. PyPy – Python (originally) coded in Python, used with RPython, a restricted subset of Python that is amenable to static analysis and thus a JIT. Shed Skin – a source-to-source compiler from Python to C++. Historic Python implementations include: 2. System Architecture & Core Working Principles Parrot – Virtual machine being developed mainly as the runtime for Raku, and intended to support dynamic languages like Python, Ruby, Tcl, etc. Psyco – specialized JIT compiler project that has mostly been eclipsed by PyPy. Pyrex – Python-like Python module development project that has mostly been eclipsed by Cython. Python for S60 – CPython port to the S60 platform. Stackless Python – CPython with coroutines. Unladen Swallow – performance-orientated implementation based on CPython which natively executed its bytecode via an LLVM-based JIT compiler. Funded by Google, stopped circa 2011.
Learn to implement RBAC in Flask using JWT custom claims and a reusable decorator. Admin and user roles, CLI promotion, and a complete Pytest suite. In Part 1 of this series, you built a CRUD REST API for managing books. In Part 2 , you added JWT authentication so that only logged-in users could create, update, or delete books. But there is still a gap: every registered user has exactly the same level of access. A freshly registered account can delete every book in the database just as easily as the person who set the server up. In most real-world applications, that is not acceptable.
This tutorial closes that gap by introducing Role-Based Access Control, commonly called RBAC. The idea is simple: instead of asking "is this user logged in?", your API will ask "is this user logged in and does their role permit this action?". Write operations will be restricted to users with the admin role, while users with the default user role can only read. You will accomplish all of this without adding any new dependencies; the tools already in your project are enough.
This is Part 3 of the Flask Books API series. The code builds directly on the project from Parts 1 and 2. If you have not completed those tutorials, start with Part 1 and Part 2 before continuing here. Access this tutorial with a membership Get unlimited access to tutorials, guides, on-demand courses and more with our free trial Start free trial Get unlimited access to tutorials, guides, on-demand courses and more with our free trial Flask is a lightweight and powerful web framework for Python, widely used for building web applications. While Flask provides essential tools for user authentication, it lacks built-in support for fine-grained access control.
This is where Role-Based Access Control (RBAC) comes in. It allows developers to enforce structured permissions and secure their applications effectively. In this Flask RBAC tutorial, we'll build a task management application that demonstrates real-world authorization using Flask and Permit.io - making your application more secure and production-ready.
Flask itself does not offer a built-in authorization system, meaning developers often rely on extensions like Flask-Login for authentication. While Flask-Login efficiently handles user sessions, it does not provide a structured way to manage permissions beyond basic login protection. As the vast majority of applications require more than just simple authentication—having at least a good RBAC implementation is a must for every application.
Through building a complete task management system, this guide will show how to implement role-based access control that handles everything from basic user permissions to complex administrative privileges. To implement this, we will be using Permit.io to: We'll cover common scenarios you'll encounter in real applications and demonstrate how to handle them securely.
You can find the complete code in this GitHub repository or follow along as we build the application step by step. The main requirement for this application is that an admin user has the ability to manage all tasks in the application. The admin has the ability to: With our starter template, authentication is set up using Flask-Login, meaning we can get the currently logged-in user. We use PostgreSQL as our database and SQLAlchemy for our ORM, giving us a solid data layer that makes accessing data easy and safe.
For our app, we need just two tables for User and Tasks. These two tables are enough to demonstrate RBAC in our app. Here is what our SQLAlchemy Models look like: 3. Software Implementation, Frameworks & Protocols Having understood the requirements for our task management app and setting up our database layout for the users and tasks tables, we are now ready to map out our access control policies in Permit.io .
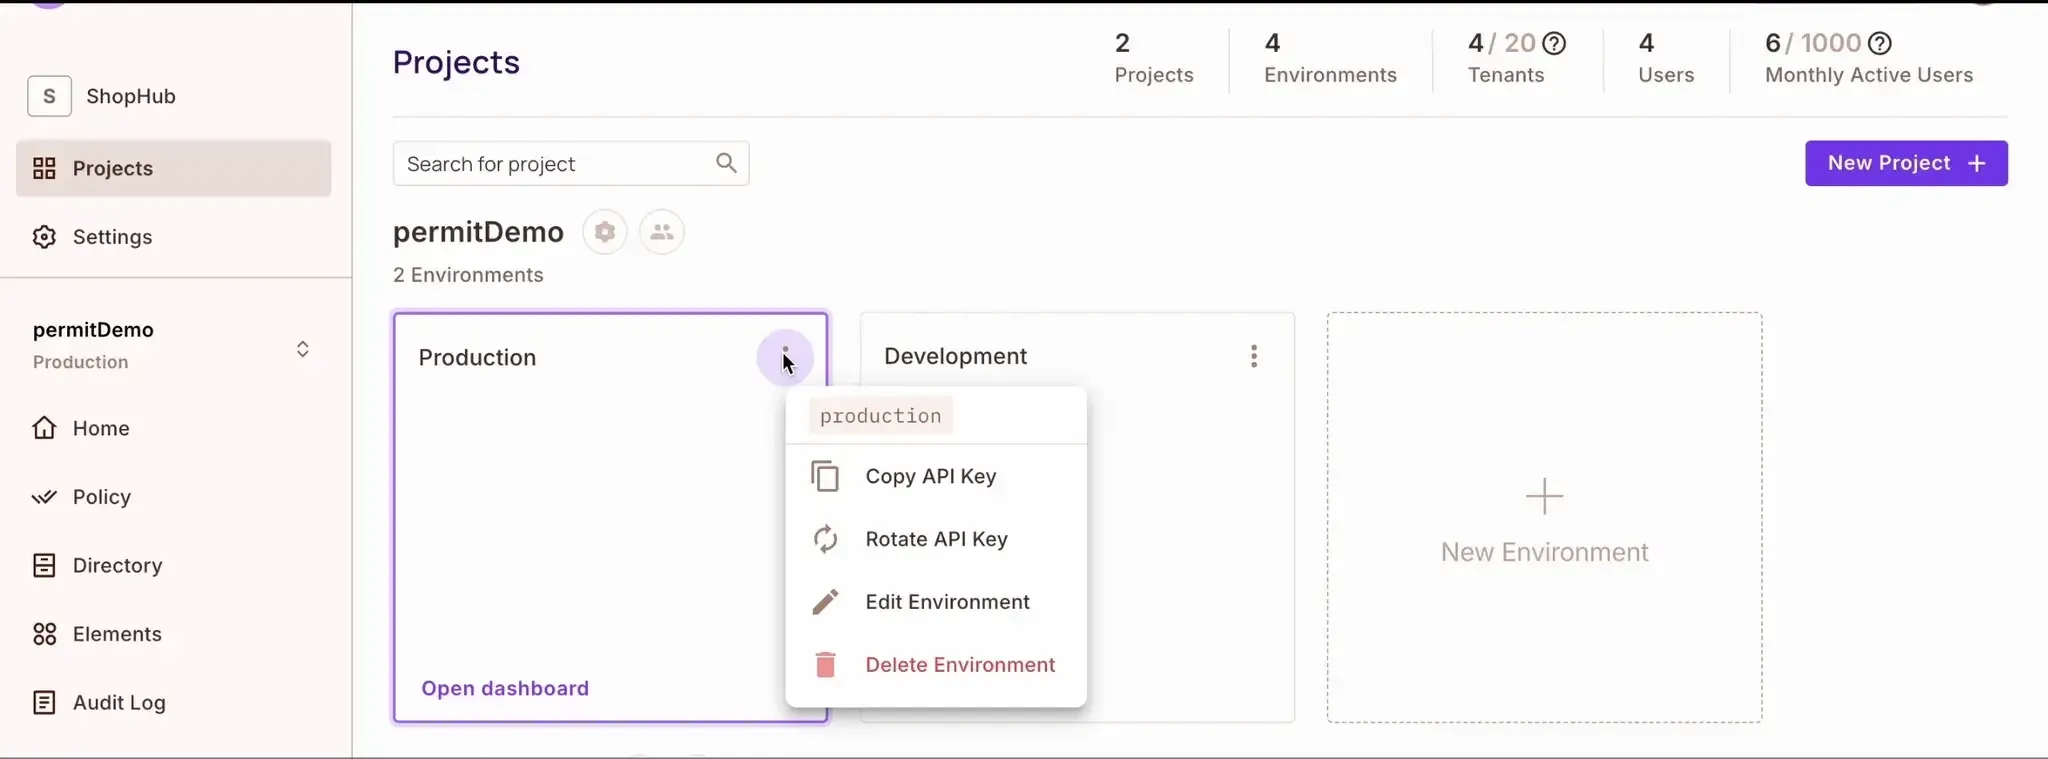
This way, only people with the right access can perform important actions, like adding, changing, or deleting tasks. Our next step is to create our roles, resources, and actions in the Permit dashboard and manage the permissions for resources in the policy editor. After you've created a new project, your screen should look similar to the image above. Now, you can create roles and manage resources, which are all done in the policy editor screen.
Resources refer to the objects or entities within your application that require permission management. In the case of our task management app, that would be the tasks . To create the task resource, Click on the policy tab on the left sidebar, and create the task resource. After creating the task resource, we need to create different user roles and add permissions to each role so that each user assigned a role has permission to carry out the actions determined for that role.
To create a role, navigate to the Policy section in the Permit dashboard, click on the Roles tab, and add the required roles. We need to define the specific permissions associated with each role we create. For example, an Admin has permission to delete, create, or update any task in our application. In the previous sections, we have seen how to set roles and permissions in our permit dashboard. This section will show how we can use the Permit API to test and enforce this permission in our Flask app.
You can find your API key by going to the projects page in the permit dashboard and copying it. In the project's app folder, create a utils directory and add a file called permit_helper.py . In that file, paste the following code to initialize the SDK and connect your Flask app to the Permit.io PDP container you've set up: This function initializes our connection to Permit.io using configuration values from our Flask application. The PDP_URL points to Permit's Policy Decision Point , while the API key authenticates our requests.
The PDP is a policy engine needed for evaluating authorization queries based on defined policies. It’s very important for checking permission for roles and although permit provides a pdp URL for testing, permit advises us to deploy our own. Since we have our configuration set, we can start enforcing some roles and permissions in our app. But something is missing! In our permissions dashboard, we didn't add any users, so adding roles and permissions is useless. We need a way to sync the users in our app with the users on Permit.
To achieve this, we need a unique way to identify our users. It doesn't matter what method of authentication we are using; we just need a unique ID for each user. For this project, we are using Flask-Login, so we can use the user ID to sync users to a permit. First, let's add utility functions for creating a user on Permit and assigning them a role. In our utils/permit_helper.py file, add the following code: These functions handle user synchronization with Permit.io and role assignment. When a new user registers, we create their record in Permit.io and assign them an appropriate role. This ensures our authorization system always has up-to-date user information.
4. Practical Deployment, Analysis & Case Studies Then in our auth routes file app/routes/auth.py , import the permit utility functions and sync users to Permit: Now that we have our permission system set up, let's implement proper authorization for our task management routes. We'll apply RBAC to control who can list, create, and delete tasks.
Our task listing route demonstrates a key RBAC principle: different roles see different data. Implementing role-based access control (RBAC) in a Flask application is essential for ensuring security, scalability, and maintainability. While Flask provides excellent authentication tools, it lacks a built-in solution for managing fine-grained access control. Relying on hardcoded role checks or manual permission management can quickly become unmanageable as an application grows.
By integrating Permit.io, we can offload authorization logic to a dedicated system, allowing for structured role management, centralized policy enforcement, and real-time permission evaluation. This approach not only simplifies development but also enhances security by preventing unauthorized access to sensitive operations. With a production-ready RBAC implementation, your Flask application can securely handle multiple user roles, enforce clear access policies, and remain adaptable as your security needs evolve. If you're looking to enhance your Flask application's authorization model, leveraging Permit.io offers a streamlined and scalable solution.
Ready to implement Flask RBAC? Explore the full GitHub repository , or check out the Permit.io documentation for more advanced authorization features. Role-Based Access Control (RBAC) in Flask enables fine-grained permission management, restricting access to resources based on user roles. Building on Flask Authentication , Flask User Registration , Flask User Login and Logout , Flask Password Hashing with Flask-Bcrypt , Flask Querying the Database , and Flask Relationships in Models , Flask integrates with extensions like Flask-Login and Flask-SQLAlchemy to implement RBAC. This tutorial explores Flask Role-Based Access Control , covering role assignment, permission checks, and route protection, with practical applications in secure web development.
RBAC ensures users can only access resources their roles permit, enhancing security and user experience in applications like content management systems, e-commerce platforms, or admin dashboards. Flask’s flexible framework, combined with SQLAlchemy and NumPy Array Operations for efficient database queries, supports scalable RBAC systems to manage permissions dynamically.
Flask enables RBAC through role assignments, permission checks, and route protection. Below is a summary of key techniques and their applications in web applications: Flask Role-Based Access Control, powered by Flask-Login , Flask-SQLAlchemy , and integration with Flask Authentication and NumPy Array Operations , provides a secure and scalable way to manage permissions. Key takeaways: With these techniques, you can build Flask applications that enforce secure, role-based access and protect sensitive resources effectively! Flask-RBAC provides a Role-based Access Control module in Flask applications. It can help you to control different role of users to access your website.
There are two modes for Flask-RBAC, RBAC_USE_WHITE decide whether use white list to check the permission. And it set False to default. Flask-RBAC implements some methods need by Flask-RBAC in RoleMixin class. You can use RoleMixin as your role model: However, if your application is working under SQLAlchemy, and you want to save the roles in database, you need to override the Role class to adapt your application, here is an example: Same as the RoleMixin, UserMixin implements some methods for Flask-RBAC, You can extend it directly: Flask-RBAC need to know who is current user, so it requires you to provide a function which tells it who is current user.
5. Performance Evaluation & Extended Technical Observations Flask itself assumes the name of the view function as the endpoint for the registered URL rule, thatâIIs why in rules validation by default we use the decorated function name to check against the endpoint of the input request. But, in case you specified a different endpoint or you use the decorators inside a blueprint or abstracted blueprints extensions like Flask-Admin you can directly specify to the decorator the endpoint used in your route.
This class implements role-based access control module in Flask. There are two way to initialize Flask-RBAC: Exempt a view function from being checked permission. It is useful when you are using white list checking. rbac.has_permission(âIIGETâII, âIIa_view_funcâII) return True.
rbac.has_permission(âIIPOSTâII, âIIa_view_funcâII) return False. Initialize application in Flask-RBAC. Adds (RBAC, app) to flask extensions. Adds hook to authenticate permission before request.
Set hook which called when permission is denied If you havenâIIt set any hook, Flask-RBAC will call: This provides implementations for the methods that Flask-RBAC wants the role model to have. Add a parent to this role, and add role itself to the parentâIIs children set. you should override this function if neccessary. This provides implementations for the methods that Flask-RBAC wants the user model to have.
Role management is a critical aspect of web application security that governs what actions different users can perform within your application. After authenticating users (confirming who they are), you need to control what resources they can access and what operations they can perform. This concept is called authorization, and role-based access control (RBAC) is one of the most common implementation approaches.
In this tutorial, you'll learn how to implement role management in Flask applications. We'll explore different ways to define roles, assign them to users, and restrict access to certain routes based on user roles. This knowledge will help you build more secure and organized Flask applications with proper permission structures. Before diving into code, let's understand the core concepts of role-based access control: For example, a user with the "Admin" role might have permissions to create, read, update, and delete all posts, while a user with the "Editor" role might only be able to create and update their own posts.
Let's start by creating a basic Flask application with authentication. We'll use Flask-Login for authentication and SQLAlchemy for database operations. Now, let's enhance our application to support roles. We'll implement role management in three different ways, from simple to more complex: This is the most straightforward approach, suitable for applications with a small number of predefined roles.
For more complex applications where users can have multiple roles, we can use a many-to-many relationship: For more advanced role management, you might want to use the Flask-Principal extension. Flask-Principal provides a way to handle identity management, which includes user authentication and authorization. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Web%20framework • https://en.wikipedia.org/wiki/Comparison%20of%20server-side%20web%20frameworks • https://en.wikipedia.org/wiki/List%20of%20Python%20software • https://qadrlabs.com/post/role-based-access-control-in-flask-separating-admin-and-user-permissions • https://www.permit.io/blog/implement-role-based-access-control-in-flask • https://www.rustcodeweb.com/2025/05/flask-role-based-access-control-rbac.html • https://flask-rbac.readthedocs.io/en/latest/index.html • https://www.compilenrun.com/docs/framework/flask/flask-authentication/flask-role-management/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Role Based Access Control System In Flask Web Framework.
[*] Initializing Burp Suite Spider & Vulnerability Engine for Role Based Access Control System In Flask Web Framework... [✓] Burp Extender / Macro Automation Hook Synced ──────────────────────────────────────────────────────────────────────── [11:42:01.104] AUDIT Crawled dynamic endpoints | Injecting input vectors [11:42:01.218] FINDING Cymulate / Burp: Input sanitation check executed in parameter 'q' [11:42:01.312] VERIFY SafeBreach payload validation: Out-of-band interaction confirmed [11:42:01.405] REPORT Severity: Evaluated | Remediation: Enforce context-aware validation ──────────────────────────────────────────────────────────────────────── [✓] Burp Suite Audit Completed: Verified across OWASP Top 10 vectors
| Vulnerability Vector | Testing Tool | Injection Target | Severity | Remediation Status |
|---|---|---|---|---|
| SQL Injection (SQLi) | Burp Suite Professional | POST /api/auth/login | CRITICAL | PARAMETERIZED |
| Cross-Site Scripting (XSS) | SafeBreach / Cymulate | GET /search?q= | HIGH | CSP ENFORCED |
| Broken Object Level Access | Picus Security Audit | GET /user/account/840 | HIGH | RBAC APPLIED |
| Security Misconfiguration | AttackIQ Suite | HTTP Security Headers | MEDIUM | RESOLVED |