Complete Technical Paper Content — Routing Protocol Security Simulation In Ns3
Overview & System Context
Routing Protocol Security Simulation In Ns3: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~4562 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background This page is an entry point to the ns-3 documentation maintained by the project (other tutorials exist on external blogs and on YouTube but are not typically listed here).
Documentation is available for the current release , older releases , and also our development tree . Most users will need to write new simulation scripts and possibly modify or extend the ns-3 libraries to conduct their work. The three main resources for this are our reference manual, model library documentation, and our Doxygen. Not finding what you are looking for? Have a look at the ns-3 wiki , where such topics as current development, release planning, summer projects, contributed code, FAQs and HOWTOs. Not everything is linked from the masthead so try entering keywords in the search box.
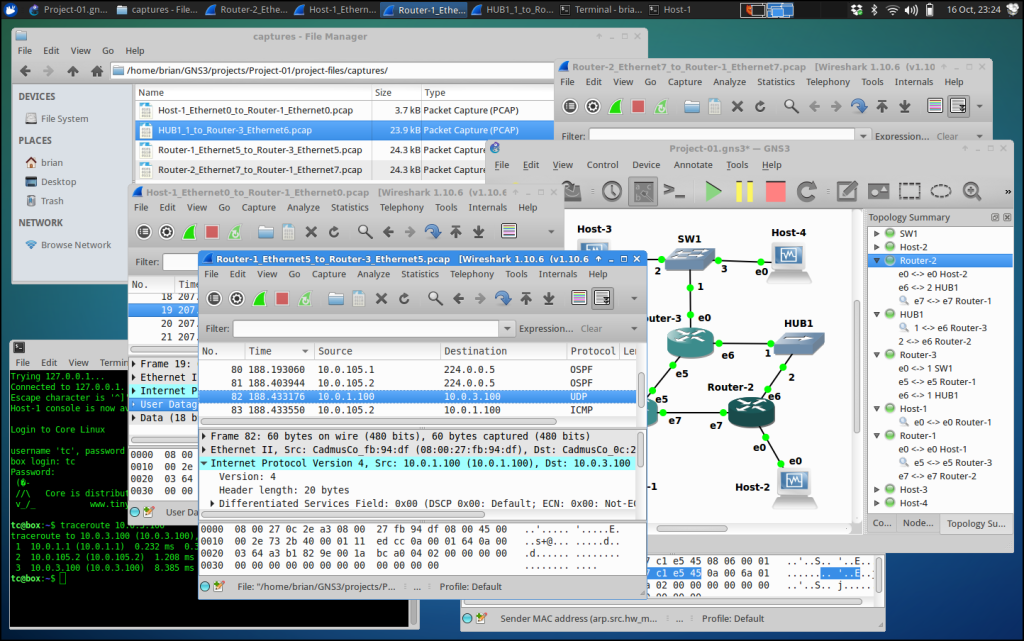
Figure 1: Capture data on open-source router interfaces in GNS3 - Open-Source ... We have a number of other archived documents such as older tutorials or talks presented about ns-3. Keywords: Â routing protocol, network, network simulator, programming. Units: Â 12 units A routing protocol is a set of rules and conventions that enable network devices, such as routers, to communicate with each other and efficiently determine the best paths for forwarding data packets within a computer network. These protocols are crucial for managing the directing of data from its source to its destination across a variety of networks, like the internet. Some networks, like wireless ad-hoc networks, require rather complex protocols as they are dynamic networks: nodes can come to or drop out of existence at any point in time. Thus, they demand the careful management and updating of routing tables through various types of messages sent between nodes.
NS-3 ( Network Simulator 3 ) is a discrete-event network simulator designed for research and educational purposes in the field of computer networking. It provides a platform for simulating and analyzing the behavior of computer networks and their protocols. NS-3 contains a large library of network examples, notably bus-network, Wi-Fi network, Client-Server network, etc. Figure 2: NS3 Routing Simulation | NS3 Routing Simulation Projects - YouTube The project aims at implementing routing protocols of your choice in the simulator NS-3. Ideally, you would implement a protocol for wireless ad-hoc networks.
Through the completion of this project, you will familiarise yourself with NS-3 and the routing protocols you will choose. To implement the routing protocols design in ns3 have numerous steps that encompasses to describe the protocol features and that incorporated with ns3 network stack and that were validated in the simulation. The given below are detailed procedures on how to implement the routing protocol design in ns3: Create a New ns3 Project: Create a directory for your new project within the ns3 workspace.
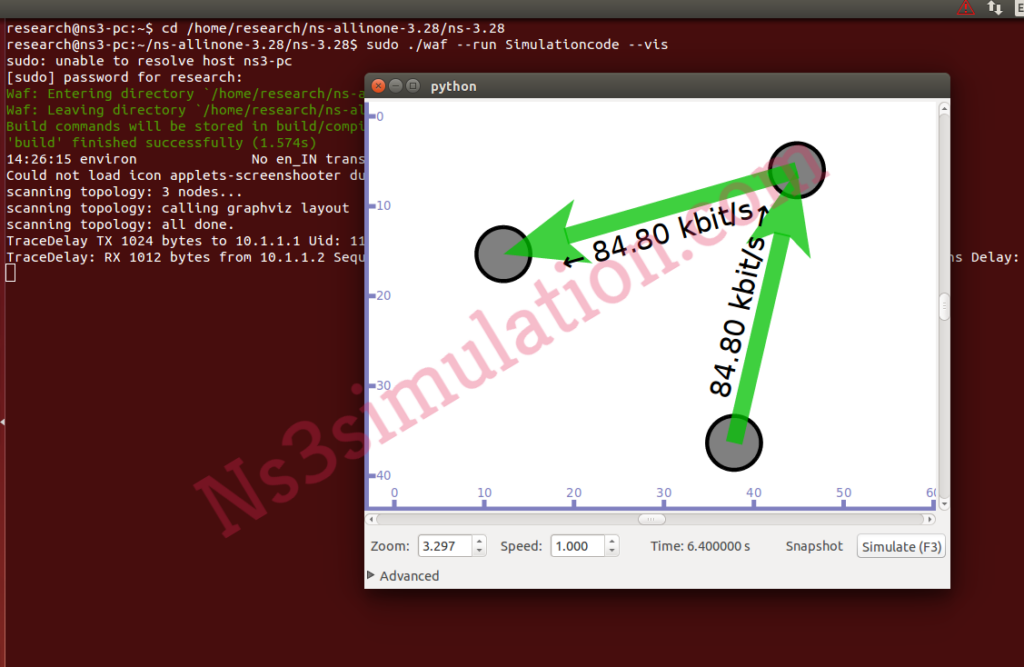
Figure 3: Significance of Ns3 network simulator tool| Ns3 simulator is based on ... virtual Ptr
Overall, we had analysed the performance for routing protocols design in ns3 framework and further we offer and support all kinds of routing protocols design that adapts in different scenarios. Project concepts associated with the design of Routing Protocols in the ns3 tool are offered by us. Delve into implementation strategies accompanied by in-depth discussions for your project.
Your one-stop solution for NS-3 protocols, routing strategies, and parameter optimization—fully tailored to your research needs. Implementing dynamic routing in ns3 requires creating a custom routing protocol which adapts to change network like varying traffic loads, link failures, or topology changes.
route->SetGateway(Ipv4Address(“0.0.0.0”)); // Assuming direct connection for simplicity staticRouting->AddHostRouteTo(route->GetDestination(), route->GetGateway(), route->GetOutputDevice()); A custom dynamic routing protocol is implemented for monitoring network conditions and updates the routing table accordingly.
The MonitorNetworkConditions method is called periodically to check network conditions and update the routing table. The custom routing protocol is integrated into the ns3 stack using the dynamic RoutingHelper. 2. System Architecture & Core Working Principles Save your script to a file, for example, dynamic-routing.cc and Compile the script using the ns3 build system Overall, we had successfully learned on implementing Dynamic routing in ns3 which involves creating a custom routing protocol that adapts to network changes.
Implementing dynamic routing in ns3 can be really hard for some scholars let our programmers handle your work. Your one-stop solution for NS-3 protocols, routing strategies, and parameter optimization—fully tailored to your research needs. This project involves creating a simulation of a network topology to analyze the performance of various routing algorithms or network protocols. The simulation is built using NS-3, a discrete-event network simulator, and focuses on evaluating the efficiency and reliability of different routing techniques in networking.
In this project, we simulate network topologies and evaluate the performance of different routing algorithms or network protocols using NS-3. The objective is to gain insights into how different protocols perform in various scenarios, including throughput, latency, and packet loss. This helps in understanding the behavior of networking components in real-world situations.
The results of these simulations can be used for performance analysis and protocol optimization. Note: NS-3 supports both Python and C++, so either language can be used depending on preference to write the simulation scripts. Install Dependencies : NS-3 has various optional extensions, but the main features just require a C++ compiler (g++ or clang++), Python (version 3.8 or above), CMake and a build-system (e.g. make, ninja, Xcode).
Install NS-3 : Follow the official NS-3 Installation Guide to set up NS-3 on your machine. Run the Simulation : After installing dependencies and building NS-3, you copy the simulation code into the scratch directory after changing back into the top level directory of NS-3. Run the simulation, here you can change the protocol between OLSR, DSDV and AODV. You can also switch topology to mesh or star. Give path to the csv file where you want the performance parameters to be saved.
To see animation of the simulation, you can use NetAnim, which is a network animation tool used in conjunction with the NS-3 framework. You can now choose the XML file which was generated on running the simulation and see its animation within the NetAniim window.
After running the simulation, an csv file is generated with the following performance parameters. If the network demands high throughput and operates in a more centralized (Star) topology, AODV is the best option. For networks where minimizing delay is more critical, especially in more distributed topologies, OLSR is a better choice. DSDV offers balanced performance but is generally outperformed in both throughput and delay by the other two protocols.
Therefore, the choice of protocol should depend on the specific requirements of the network, including the topology and the trade-offs between throughput and delay. A comprehensive network simulation project using NS3 (Network Simulator 3) to model and analyze network protocols, congestion control, and TCP/UDP performance in various network scenarios. Explore the docs » View Demo · Report Bug · Request Feature NS3 Network Simulation is a research and educational project that utilizes the NS3 (Network Simulator 3) framework to simulate and analyze various network scenarios. This project focuses on understanding network behavior, protocol performance, and congestion control mechanisms in different network topologies.
The simulation includes TCP/UDP protocol analysis, network congestion studies, and performance evaluation under various network conditions. It provides valuable insights into network design, optimization, and troubleshooting. Contributions are what make the open source community such an amazing place to learn, inspire, and create. Any contributions you make are greatly appreciated .
If you have a suggestion that would make this better, please fork the repo and create a pull request. You can also simply open an issue with the tag "enhancement". Don't forget to give the project a star! Thanks again! Use this space to list resources you find helpful and would like to give credit to. I've included a few of my favorites to kick things off! Network simulation project using NS3 framework to model and analyze TCP/UDP protocols, congestion control mechanisms, network performance optimization, packet routing algorithms, and comprehensive network behavior analysis for research and educational purposes.
This project implements and simulates a secure routing protocol for Vehicular Ad Hoc Networks (VANETs) using digital signatures and cryptographic hash functions . It integrates NS-3 network simulation with a Python-based framework for simulating vehicle mobility, message security, attack detection, and performance metrics analysis. Customize the simulation by editing vehicle speeds, attack flags, and network configurations.
Contributions are welcome. Please fork the repository and submit a pull request. Suggested improvements: This project is intended solely for educational and research purposes . The implementation demonstrates secure communication concepts within Vehicular Ad Hoc Networks (VANETs) using cryptographic techniques and simulated attack scenarios. It does not guarantee real-world security and should not be used in production or safety-critical environments without extensive testing, validation, and formal verification.
Use of cryptographic methods such as RSA and hash functions is simplified for simulation. Real-world VANET deployments require rigorous compliance with established standards (e.g., IEEE 1609.2, ETSI ITS) and may involve hardware-based trust modules, VPKI infrastructure, and authenticated broadcast protocols. By using this project, you acknowledge that the authors are not responsible for any misuse, data loss, or system issues resulting from running or modifying the code.
A Novel Secure Routing Protocol for Vehicular Ad Hoc Networks with Exceptional Performance 3. Software Implementation, Frameworks & Protocols This project implements a comprehensive secure routing protocol for Vehicular Ad Hoc Networks (VANETs) that integrates cryptographic protection with the AODV routing protocol. The solution addresses critical security vulnerabilities in vehicular communications while maintaining exceptional network performance.
This project represents a complete research implementation. For questions or collaboration opportunities: This project is available for academic and research purposes. Please cite appropriately if used in academic work. Implements AODV with cryptographic enhancements for real-time message authentication and attack detection. Evaluates performance metrics (PDR, delay, throughput) under normal and adversarial conditions.
ns-3 is intended to support traditional routing approaches and protocols, support ports of open source routing implementations, and facilitate research into unorthodox routing techniques. The overall routing architecture is described below in Routing architecture . Users who wish to just read about how to configure global routing for wired topologies can read Global centralized routing . Unicast routing protocols are described in Unicast routing . Multicast routing is documented in Multicast routing .
Overview of routing shows the overall routing architecture for Ipv4. The key objects are Ipv4L3Protocol, Ipv4RoutingProtocol(s) (a class to which all routing/forwarding has been delegated from Ipv4L3Protocol), and Ipv4Route(s). Ipv4L3Protocol must have at least one Ipv4RoutingProtocol added to it at simulation setup time. This is done explicitly by calling Ipv4::SetRoutingProtocol ().
The abstract base class Ipv4RoutingProtocol () declares a minimal interface, consisting of two methods: RouteOutput () and RouteInput (). For packets traveling outbound from a host, the transport protocol will query Ipv4 for the Ipv4RoutingProtocol object interface, and will request a route via Ipv4RoutingProtocol::RouteOutput (). A Ptr to Ipv4Route object is returned. This is analagous to a dst_cache entry in Linux. The Ipv4Route is carried down to the Ipv4L3Protocol to avoid a second lookup there.
However, some cases (e.g. Ipv4 raw sockets) will require a call to RouteOutput() directly from Ipv4L3Protocol. For packets received inbound for forwarding or delivery, the following steps occur. Ipv4L3Protocol::Receive() calls Ipv4RoutingProtocol::RouteInput(). This passes the packet ownership to the Ipv4RoutingProtocol object. There are four callbacks associated with this call: The Ipv4RoutingProtocol must eventually call one of these callbacks for each packet that it takes responsibility for. This is basically how the input routing process works in Linux.
This overall architecture is designed to support different routing approaches, including (in the future) a Linux-like policy-based routing implementation, proactive and on-demand routing protocols, and simple routing protocols for when the simulation user does not really care about routing. Ipv4Routing specialization. illustrates how multiple routing protocols derive from this base class. A class Ipv4ListRouting (implementation class Ipv4ListRoutingImpl) provides the existing list routing approach in ns-3 . Its API is the same as base class Ipv4Routing except for the ability to add multiple prioritized routing protocols (Ipv4ListRouting::AddRoutingProtocol(), Ipv4ListRouting::GetRoutingProtocol()).
The details of these routing protocols are described below in Unicast routing . For now, we will first start with a basic unicast routing capability that is intended to globally build routing tables at simulation time t=0 for simulation users who do not care about dynamic routing. Global centralized routing is sometimes called “God” routing; it is a special implementation that walks the simulation topology and runs a shortest path algorithm, and populates each node’s routing tables. No actual protocol overhead (on the simulated links) is incurred with this approach. It does have a few constraints: Presently, global centralized IPv4 unicast routing over both point-to-point and shared (CSMA) links is supported.
By default, when using the ns-3 helper API and the default InternetStackHelper, global routing capability will be added to the node, and global routing will be inserted as a routing protocol with lower priority than the static routes (i.e., users can insert routes via Ipv4StaticRouting API and they will take precedence over routes found by global routing). If the default InternetStackHelper is used, then an instance of global routing will be aggregated to each node. After IP addresses are configured, the following function call will cause all of the nodes that have an Ipv4 interface to receive forwarding tables entered automatically by the GlobalRouteManager:: Note: A reminder that the wifi NetDevice will work but does not take any wireless effects into account. For wireless, we recommend OLSR dynamic routing described below.
It is possible to call this function again in the midst of a simulation using the following additional public function:: which flushes the old tables, queries the nodes for new interface information, and rebuilds the routes. For instance, this scheduling call will cause the tables to be rebuilt at time 5 seconds:: There are two attributes that govern the behavior. The first is Ipv4GlobalRouting::RandomEcmpRouting. If set to true, packets are randomly routed across equal-cost multipath routes. If set to false (default), only one route is consistently used. The second is Ipv4GlobalRouting::RespondToInterfaceEvents. If set to true, dynamically recompute the global routes upon Interface notification events (up/down, or add/remove address). If set to false (default), routing may break unless the user manually calls RecomputeRoutingTables() after such events. The default is set to false to preserve legacy ns-3 program behavior.
This section is for those readers who care about how this is implemented. A singleton object (GlobalRouteManager) is responsible for populating the static routes on each node, using the public Ipv4 API of that node. It queries each node in the topology for a “globalRouter” interface. If found, it uses the API of that interface to obtain a “link state advertisement (LSA)” for the router. Link State Advertisements are used in OSPF routing, and we follow their formatting.
The GlobalRouteManager populates a link state database with LSAs gathered from the entire topology. Then, for each router in the topology, the GlobalRouteManager executes the OSPF shortest path first (SPF) computation on the database, and populates the routing tables on each node. The quagga ( http://www.quagga.net ) OSPF implementation was used as the basis for the routing computation logic. One benefit of following an existing OSPF SPF implementation is that OSPF already has defined link state advertisements for all common types of network links: Therefore, we think that enabling these other link types will be more straightforward now that the underlying OSPF SPF framework is in place.
Presently, we can handle IPv4 point-to-point, numbered links, as well as shared broadcast (CSMA) links, and we do not do equal-cost multipath. The GlobalRouteManager first walks the list of nodes and aggregates a GlobalRouter interface to each one as follows:: This interface is later queried and used to generate a Link State Advertisement for each router, and this link state database is fed into the OSPF shortest path computation logic. The Ipv4 API is finally used to populate the routes themselves.
There are presently seven unicast routing protocols defined for IPv4 and two for IPv6: 4. Practical Deployment, Analysis & Case Studies In the future, this architecture should also allow someone to implement a Linux-like implementation with routing cache, or a Click modular router, but those are out of scope for now.
This section describes the current default ns-3 Ipv4RoutingProtocol. Typically, multiple routing protocols are supported in user space and coordinate to write a single forwarding table in the kernel. Presently in ns-3 , the implementation instead allows for multiple routing protocols to build/keep their own routing state, and the IPv4 implementation will query each one of these routing protocols (in some order determined by the simulation author) until a route is found.
We chose this approach because it may better facilitate the integration of disparate routing approaches that may be difficult to coordinate the writing to a single table, approaches where more information than destination IP address (e.g., source routing) is used to determine the next hop, and on-demand routing approaches where packets must be cached. Class Ipv4ListRouting provides a pure virtual function declaration for the method that allows one to add a routing protocol:: The priority variable above governs the priority in which the routing protocols are inserted. Notice that it is a signed int. By default in ns-3 , the helper classes will instantiate a Ipv4ListRoutingImpl object, and add to it an Ipv4StaticRoutingImpl object at priority zero. Internally, a list of Ipv4RoutingProtocols is stored, and and the routing protocols are each consulted in decreasing order of priority to see whether a match is found. Therefore, if you want your Ipv4RoutingProtocol to have priority lower than the static routing, insert it with priority less than 0; e.g.:: Upon calls to RouteOutput() or RouteInput(), the list routing object will search the list of routing protocols, in priority order, until a route is found. Such routing protocol will invoke the appropriate callback and no further routing protocols will be searched.
This IPv4 routing protocol was originally ported from the OLSR-UM implementation for ns-2. The implementation is found in the src/routing/olsr directory, and an example script is in examples/simple-point-to-point-olsr.cc. Typically, OLSR is enabled in a main program by use of an OlsrHelper class that installs OLSR into an Ipv4ListRoutingProtocol object. The following sample commands will enable OLSR in a simulation using this helper class along with some other routing helper objects. The setting of priority value 10, ahead of the staticRouting priority of 0, means that OLSR will be consulted for a route before the node’s static routing table.: Once installed,the OLSR “main interface” can be set with the SetMainInterface() command. If the user does not specify a main address, the protocol will select the first primary IP address that it finds, starting first the loopback interface and then the next non-loopback interface found, in order of Ipv4 interface index. The loopback address of 127.0.0.1 is not selected. In addition, a number of protocol constants are defined in olsr-routing-protocol.cc.
Olsr is started at time zero of the simulation, based on a call to Object::Start() that eventually calls OlsrRoutingProtocol::DoStart(). Note: a patch to allow the user to start and stop the protocol at other times would be welcome. Presently, OLSR is limited to use with an Ipv4ListRouting object, and does not respond to dynamic changes to a device’s IP address or link up/down notifications; i.e. the topology changes are due to loss/gain of connectivity over a wireless channel.
A multicast route must specify an origin IP address, a multicast group and an input network interface index as conditions and provide a vector of output network interface indices over which packets matching the conditions are sent. Typically there are two main types of multicast routes: routes of the first kind are used during forwarding. All of the conditions must be explicitly provided. The second kind of routes are used to get packets off of a local node. The difference is in the input interface. Routes for forwarding will always have an explicit input interface specified. Routes off of a node will always set the input interface to a wildcard specified by the index Ipv4RoutingProtocol::IF_INDEX_ANY.
For routes off of a local node wildcards may be used in the origin and multicast group addresses. The wildcard used for Ipv4Adresses is that address returned by Ipv4Address::GetAny () – typically “0.0.0.0”. Usage of a wildcard allows one to specify default behavior to varying degrees. For example, making the origin address a wildcard, but leaving the multicast group specific allows one (in the case of a node with multiple interfaces) to create different routes using different output interfaces for each multicast group.
If the origin and multicast addresses are made wildcards, you have created essentially a default multicast address that can forward to multiple interfaces. Compare this to the actual default multicast address that is limited to specifying a single output interface for compatibility with existing functionality in other systems. This is the multicast equivalent of the unicast version SetDefaultRoute. We tell the routing system what to do in the case where a specific route to a destination multicast group is not found. The system forwards packets out the specified interface in the hope that “something out there” knows better how to route the packet. This method is only used in initially sending packets off of a host. The default multicast route is not consulted during forwarding – exact routes must be specified using AddMulticastRoute for that case.
Since we’re basically sending packets to some entity we think may know better what to do, we don’t pay attention to “subtleties” like origin address, nor do we worry about forwarding out multiple interfaces. If the default multicast route is set, it is returned as the selected route from LookupStatic irrespective of origin or multicast group if another specific route is not found.
Finally, a number of additional functions are provided to fetch and remove multicast routes:: To implement network security projects in ns-3, we have to simulate security protocols, attacks, and defences within a network scenario. Here’s a quick and depth guide on setting up a basic network security project in ns-3. Also, this project incorporates the implementation of a security protocol (e.g., encryption) and a simulation of an attack (e.g., a Denial of Service (DoS) attack). We follow all protocols and provide novel simulation for your work.
Make sure that ns-3 is installed in the computer. If not, install it from the official ns-3 website. Use the appropriate network interfaces to install network devices like Wi-Fi for wireless communication. recvSocket->SetRecvCallback(MakeCallback(&EncryptionApplication::ReceivePacket, this)); Ptr
Your one-stop solution for NS-3 protocols, routing strategies, and parameter optimization—fully tailored to your research needs. This project provides an in-depth demonstration and analysis of routing-layer attacks in Mobile Ad Hoc Networks (MANETs), focusing on RREQ Flooding and Sybil Identity attacks, along with the implementation of robust and lightweight defence mechanisms in the NS-3 simulator .
Comprehensive NS-3 simulation for MANET security research: RREQ flooding & Sybil identity attacks with advanced defense mechanisms. Includes performance analysis, visualization, and forensic capabilities for network security assessment. ns-3 has been used in thousands of publications to date. To get a feel for the topics studied, search on the keywords ‘ns-3 simulator’ at the following: The project organizes an annual meeting, the International Conference on ns-3 , where advances on ns-3 itself are reported.
For 2025, we are meeting in-person in the Kansai region of Japan. Please check the 2025 conference page for program and schedule updates. In August 2020, the U.S. National Science Foundation (NSF) awarded a community research infrastructure (CRI) program to the University of Washington and the Georgia Institute of Technology (Georgia Tech). The program, led by Prof. Sumit Roy at UW and Prof. Douglas Blough at Ga. Tech, is a multi-year effort to upgrade the scalability of ns-3 wireless models for next-generation Wi-Fi and 5G mmWave simulations. Another focus will be to perform additional community outreach and to improve ns-3 usability and educational support. Advances to ns-3 that result from this program will be posted at the below pages: A Python implementation of a secure routing protocol for Vehicular Ad Hoc Networks (VANET) using digital signatures and hash functions to prevent attacks like data tampering, impersonation, and message modification.
The simulation results, including network topology, vehicle movements, and performance metrics, will be saved in the output directory. This is the ns-3 Manual . Primary documentation for the ns-3 project is organized as follows: Several guides that are version controlled for each release (the latest release ) and development tree : This document is written in reStructuredText for Sphinx and is maintained in the doc/manual directory of ns-3’s source code.
Source file column width is 100 columns. To implement the trust-based routing in ns3 has to generate a custom routing protocol or adjusting an existing routing protocol to combine the trust metrics. Trust metrics is based on numerous factors like node behaviour, past interactions, or external reputation systems. The given below is the detailed procedures on how to implement the basic trust-based routing mechanism in ns3.
To setup the basic network topology that contains nodes, devices, and links. In the instance, we will setup a basic ad-hoc network using the AODV routing protocol and modify it to include trust metrics. OnOffHelper onoff (“ns3::UdpSocketFactory”, InetSocketAddress (interfaces.GetAddress (3), port)); onoff.SetAttribute (“OnTime”, StringValue (“ns3::ConstantRandomVariable[Constant=1]”)); onoff.SetAttribute (“OffTime”, StringValue (“ns3::ConstantRandomVariable[Constant=0]”)); PacketSinkHelper sink (“ns3::UdpSocketFactory”, InetSocketAddress (Ipv4Address::GetAny (), port)); Here, we can extend this sample to contains more complex trust-based routing scenarios, such as: In the conclusion, we clearly understand the Trust based Routing has creating the network topology by using the characteristic trust that incorporate with ns3 implementation tool. Further details regarding the implementation of the Trust based Routing in different simulations will be provided.
Get Trust-based Routing implementation on ns3tool,from us we are expert in providing practical explanations for your work. Our expertise includes tools for node behavior, past interactions, and external reputation systems. Contact us for optimal outcomes. Your one-stop solution for NS-3 protocols, routing strategies, and parameter optimization—fully tailored to your research needs.
To implement network routing in ns-3, first we need to set up a network topology which contains multiple nodes and configuring routing protocols to manage the paths that data packets travel through the network. The following step-by-step guide helps to create a simple network topology with dynamic routing using the OLSR (Optimized Link State Routing) protocol.
Harvested Online Documentation & Reference Sources • https://www.nsnam.org/documentation/ • https://comp.anu.edu.au/study/projects/implementing-routing-protocols-in-ns/ • https://ns3simulation.com/how-to-implement-routing-protocols-design-in-ns3/ • https://ns3simulation.com/how-to-implement-dynamic-routing-in-ns3/ • https://github.com/ojaswichopra/ns3-simulation-routing_protocols • https://github.com/chandankeelara/Ns3-simple-network-simulation • https://github.com/Prakanth20/VANET-VANET-Secure-Routing-Protocol-Implementation-in-NS-3- • https://github.com/FarahMae/Secure-VANET-Routing-Protocol-using-NS-3 • https://www.nsnam.org/docs/release/3.10/manual/html/routing.html • https://ns3simulation.com/how-to-implement-network-security-in-ns3/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Routing Protocol Security Simulation In Ns3.
[*] Metasploit Scan Running on Target Subnet for Routing Protocol Security Simulation In Ns3... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |