Complete Technical Paper Content — Scada System Cybersecurity Simulation Using Mininet
Overview & System Context
Scada System Cybersecurity Simulation Using Mininet: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~2632 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Mininet-sec is an emulation platform for studying and experimenting cybersecurity in programmable networks. Mininet-Sec allows rapidly prototyping of cybersecurity scenarios, attack simulation and testing offensive security tools in an isolated and secure environment. The availability of specialized resources, along with support for network programmability, enables fast, effective and skilled development of security solutions.
Reinforcement learning Mininet OpenDayLight This project aims to provide a basic framework for DDoS mitigation using reinforcement learning (Deep and not). The network is implemented using Mininet (based on Software-Defined networking). The design of the solution is inspired by the work "MininetGym: A modular SDN-based simulation environment for reinforcement learning in cybersecurity" by Salvo Finistrella and others here. Explore the docs » Report Bug · Request Feature A Modular SDN-based Simulation Environment for Reinforcement Learning in Cybersecurity Real-time traffic generation and flow monitoring via Mininet and Custom Gym environments for traffic classification and DoS attack detection.
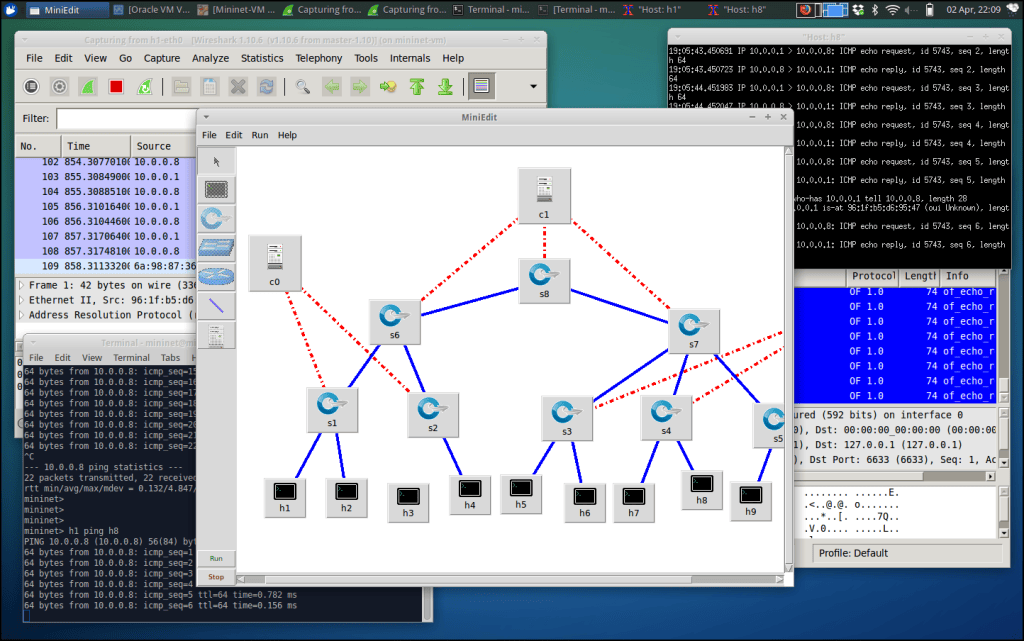
This section provides instructions on how to set up and run the MininetGym project on a clean Ubuntu 20.04+ system. Figure 1: How to use MiniEdit, Mininet’s graphical user interface | Open-Source ... bash sudo apt update && sudo apt upgrade -y sudo apt-get install mininet python3-venv git -y # Installazione di hping3 sudo apt-get install -y hping3 Verifica e Pulizia: Verification and Cleanup: Run a simple Mininet test and clean the environment to ensure that hping3 is recognized by the virtual hosts.
bash sudo mn --test pingall sudo mn -c You can verify the hping3 installation with: hping3 --help or which hping3 . Clone the Repository Create a new directory for your project, navigate into it, and clone your repository. Create and Activate a Python Virtual Environment It is crucial to use a virtual environment to manage project dependencies and avoid conflicts with system packages. This also prevents the externally-managed-environment error.
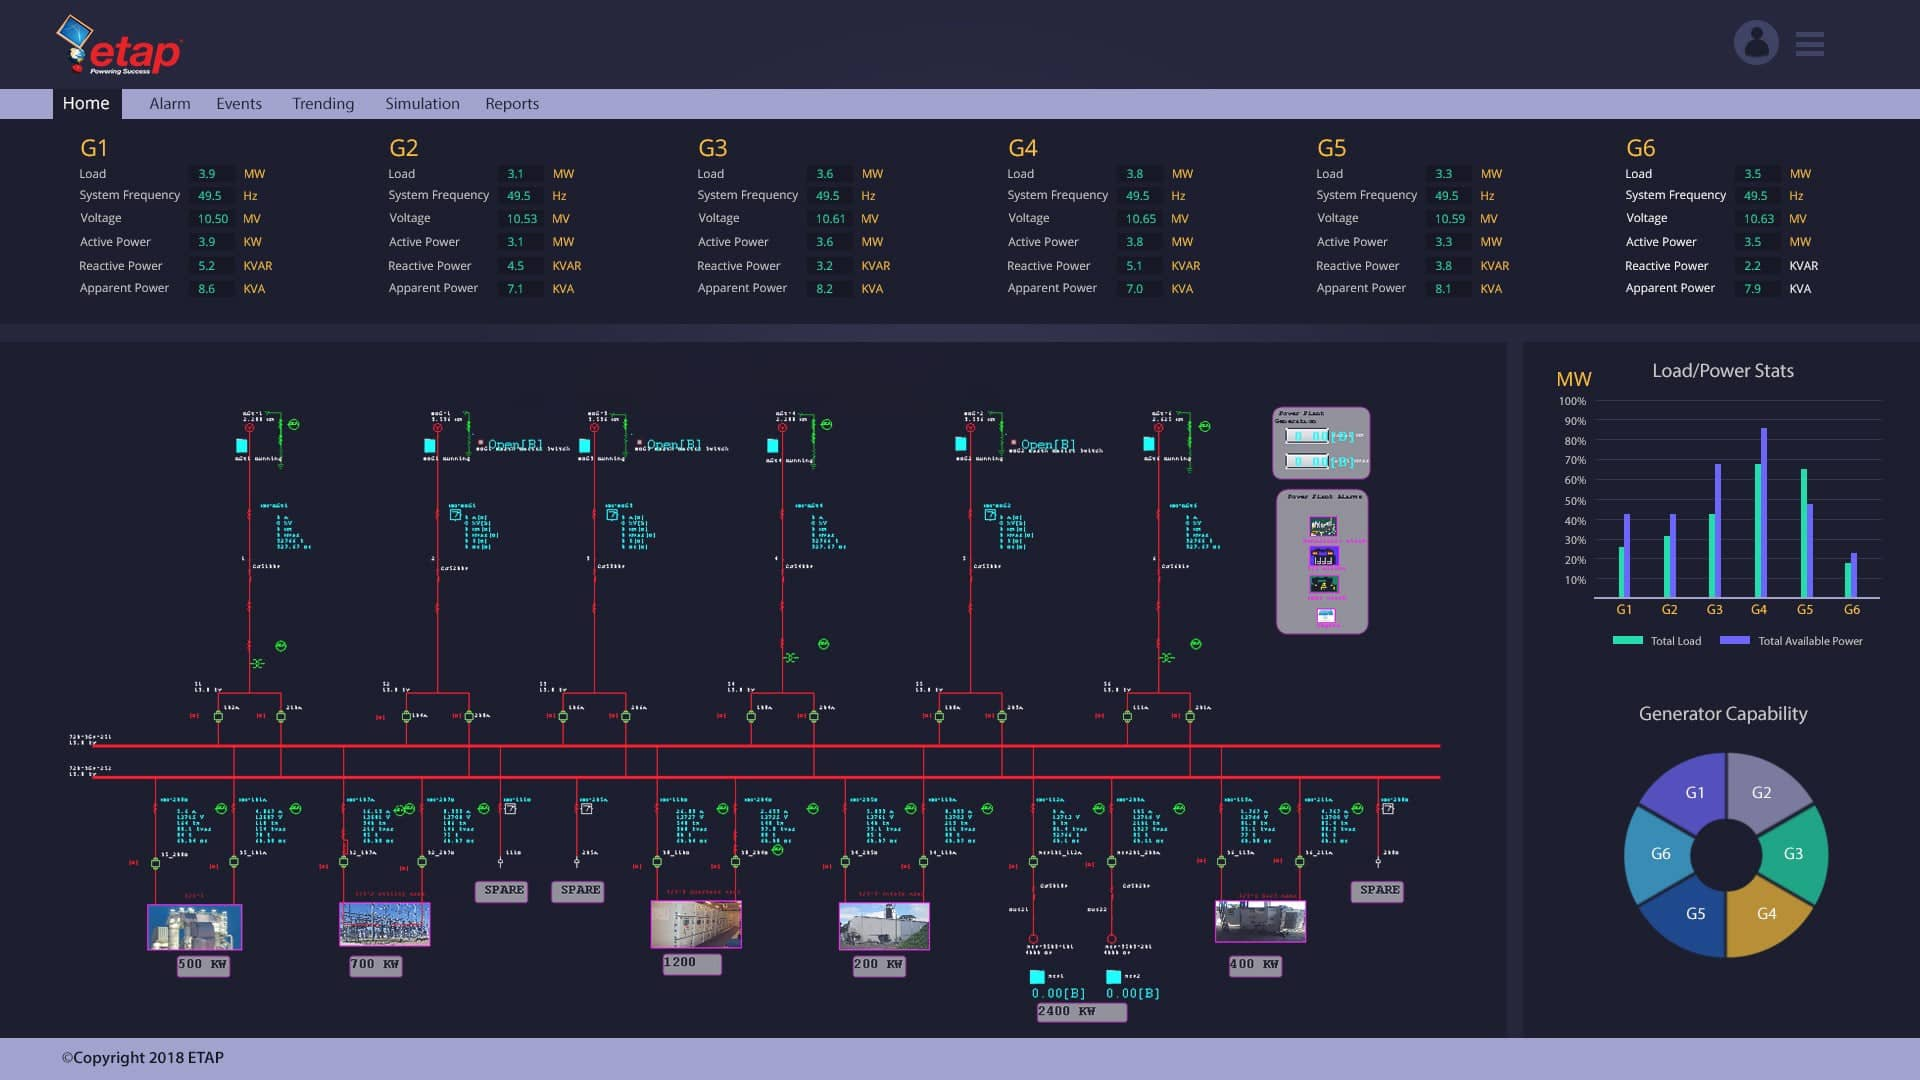
Figure 2: SCADA Human Machine Interface | Electrical SCADA HMI |ETAP You will see (venv) prepended to your terminal prompt, indicating that the virtual environment is active. Install Python Dependencies With your virtual environment activated, install the required Python packages using requirements.txt .
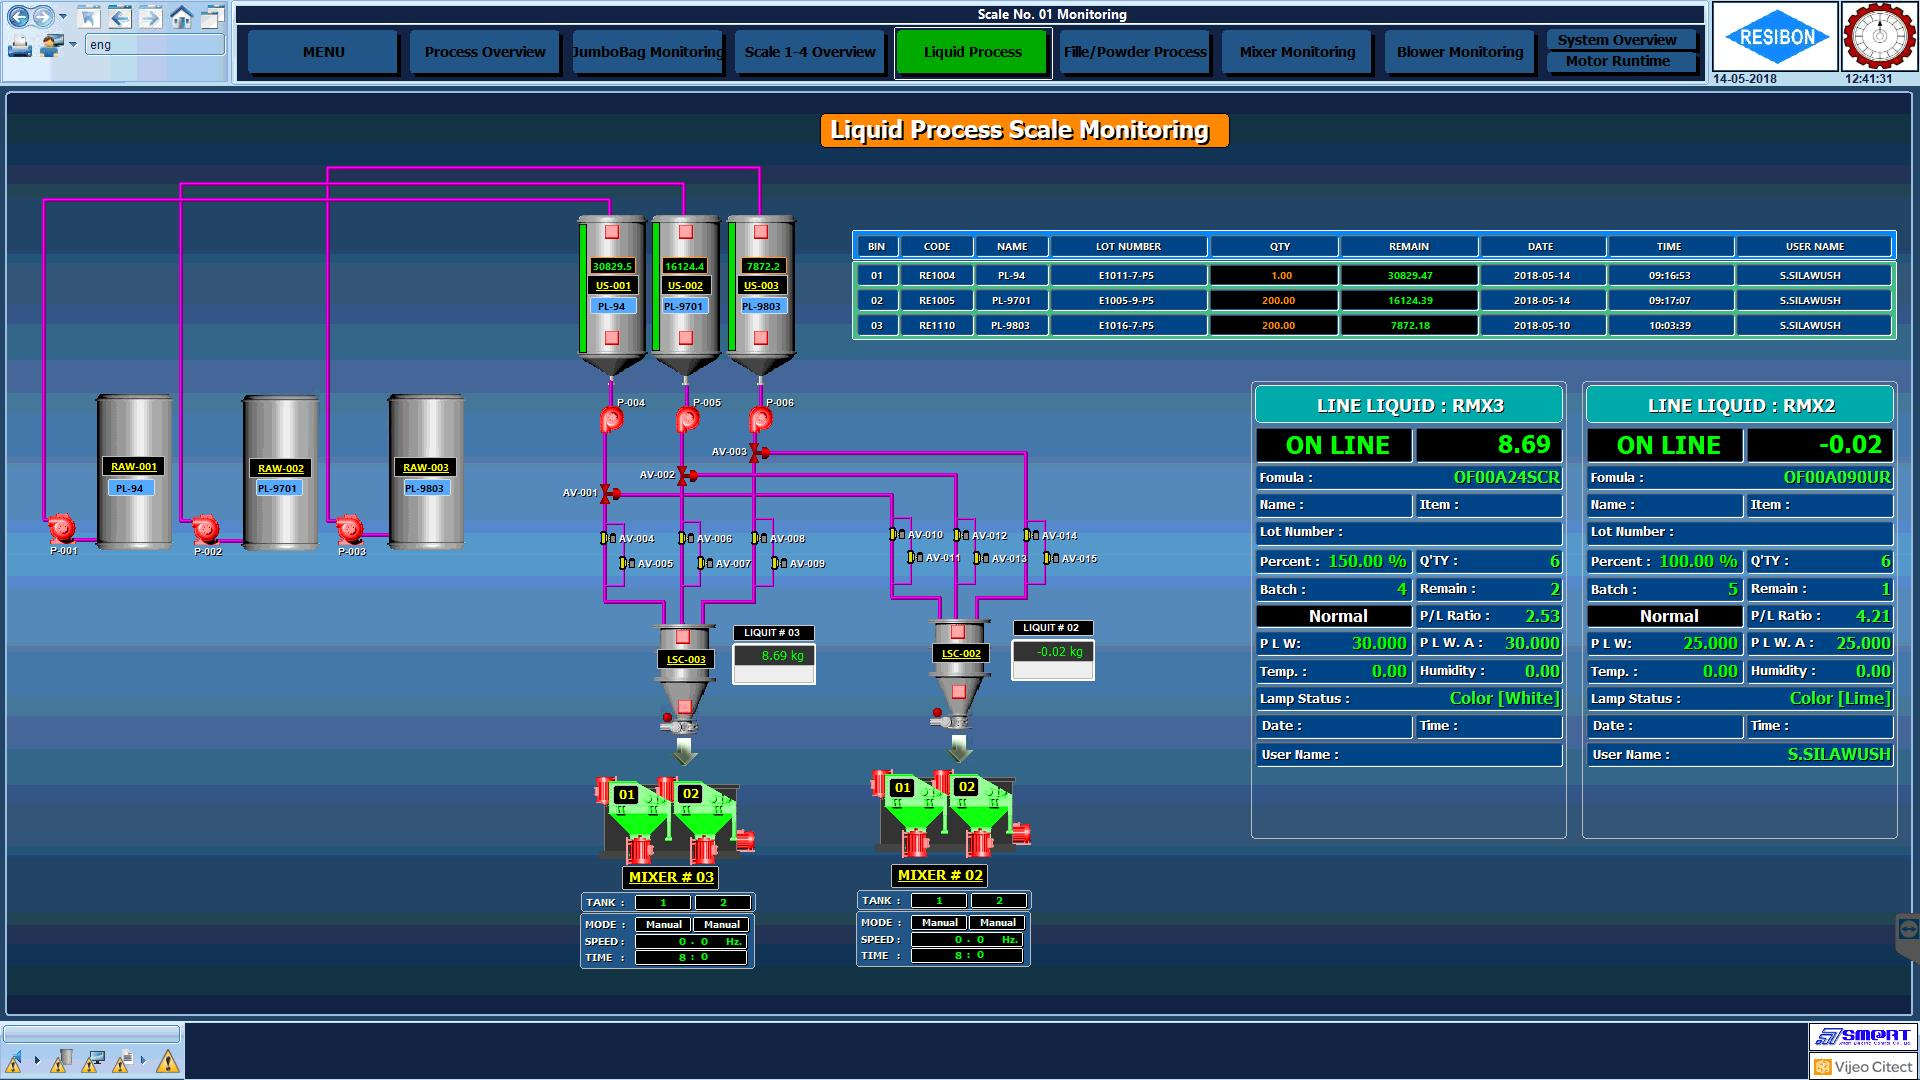
If you encounter an error related to ale-py , you may need to update the version in the requirements.txt file (e.g., to ale-py>=0.11.0 ). Troubleshooting: libcudnn.so Errors If you encounter an error like ImportError: libcudnn.so.9: cannot open shared object file: No such file or directory , it means that your PyTorch installation is configured to use NVIDIA GPU acceleration but cannot find the necessary libraries. You have two options to resolve this: Figure 3: Logiciel Scada En Français _ Fonctionnement Scada – PHXXJH Option A: Install the CPU-only version of PyTorch (Recommended) This is the simplest and safest solution, especially if you do not have a dedicated NVIDIA GPU. It avoids the need for any CUDA or cuDNN libraries.
Option B: Install the Full CUDA Toolkit and cuDNN (If you have an NVIDIA GPU) If your machine has a compatible NVIDIA GPU and you want to use it for training, you'll need to install the full CUDA Toolkit and the cuDNN library. This is a more complex process and is not covered in detail in this guide. You should refer to NVIDIA's official documentation for instructions on how to install the appropriate versions of CUDA and cuDNN for your system.
First Run and Configuration Bootstrap On the first start, the application checks for config/default.yaml . If the file does not exist, it creates the config/ directory and copies base_config.yaml to config/default.yaml . If the configuration file was just created, the application exits after printing a message. Open config/default.yaml , set the parameters you need, and restart the application.
2. System Architecture & Core Working Principles Pay special attention to server_user : this is the account the application switches to before creating training folders and later regaining root privileges for Mininet setup. After the initial configuration is in place, run the same command again to start the Mininet simulation, run the environment, and begin the training process.
OpenDayLight (ODL) Controller Setup (Optional) For installing the OpenDayLight controller, follow the instructions provided in the ODL-Ubuntu22-installation guide. This project was developed with ODL Karaf version 0.8.4. You might also use a Docker container for ODL. To start an OpenDayLight controller container: To connect via SSH to the ODL controller inside the Docker container on a virtual machine (e.g., 192.168.1.226): Ensure your JAVA_PATH is correctly set, especially if you are running ODL directly and not via Docker.
Once the application is running ( sudo python3 main.py ), open a browser and navigate to: All experiment parameters are stored in config/default.yaml and can be edited live from the Configuration Setup panel without restarting the application. Full parameter reference — open the application, click the ? User Manual button in the top navigation bar, and navigate to the Full Configuration Reference section for a complete description of every parameter, including attack thresholds, exploration schedules and algorithm-specific hyperparameters.
Contributions are what make the open-source community such an amazing place to learn, inspire, and create. Any contributions you make are greatly appreciated . If you have a suggestion that would make this better, please fork the repo and create a pull request, or simply open an issue with the tag enhancement .
A customizable simulation framework based on Mininet for evaluating Reinforcement Learning strategies Mininet-Sec is an emulation platform for studying and experimenting with cybersecurity in programmable networks. It allows rapid prototyping of cybersecurity scenarios, attack simulation, and testing offensive security tools in an isolated and secure environment. The availability of specialized resources, along with support for network programmability, enables fast, effective and skilled development of security solutions. Mininet-Sec can be used in a variety of scenarios, including secure interdomain routing, DDoS attacks, and network security teaching, interactive development, testing, etc..
There are two ways of running Mininet-Sec: 1) using Docker; 2) installing from source. The easiest way of running Mininet-Sec is via Docker containers: With the commands above you will instantiate and attach to Mininet-Sec's docker container. Privileged mode is required to be able to create network interfaces, namespaces, etc. The /lib/modules volume is needed to load openvswitch kernel module if needed (OpenFlow switch). There are other ways of running Mininet-Sec container, please refer to the entrypoint help to get more use cases: docker run --rm hackinsdn/mininet-sec --help If you prefer to install from source, please continue reading. Otherwise, you can jump into the "Using Mininet-Sec" section.
3. Software Implementation, Frameworks & Protocols Mininet-Sec can be easily installed on Debian and Ubuntu system. Other Linux distributions can also be used with some adjusments on the commands below or some level of manual effort. When asked to save current IPv4/IPv6 rules, you can answer no . When asked to start Iperf3 as a daemon automatically, you can also answer no .
Note : the parameter --break-system-packages was used above to simplify the installation of Mininet-Sec, however a best approach would be to setup a virtual environment and install mininet-sec over there. Note2: just after installing Mininet-Sec, the commands above start the OpenVSwitch daemon, just to make sure OVS is running for the examples below.
After the installation (or docker container instantiation), execute Mininet-sec with the following commands: The execution above should take a couple of seconds, and all output will be displayed at the end (be patiant). After finishing with nmap scan, Mininet-Sec will report the results and close. After executing the command above, you should see a prompt saying: mininet-sec> . From that prompt you can run commands just like mininet: On the commands above we leveraged the OVS Test Controller just to make sure OpenFlow tables on the switch gets properly populated (ideally you should run a more robust SDN Controller, such as Kytos-ng, Faucet, OpenDayLight, ONOS, etc). If you want to use a custom controller, just add the option --controller=remote,ip=x.y.z.w to the mnsec command (just like Mininet).
After running the command above, you should see again the Mininet-Sec prompt mininet-sec> . For the purpose of this example, please open a new terminal window to run the commands below (root privileges required): The command above leverages mnsecx utility to run a command inside the host o1 , which facilitate the command execution on Mininet-Sec hosts outside the prompt. The example above can be ilustrated with the following image: You can also open your internet browser app and point to Mininet-Sec web UI via http://127.0.0.1:8050/ and you should see something similar to: You can visualize packets on the link similar to what we have in Wireshark/Edgeshark (thanks to webshark and sharkd). In order to have Packet Capture working fine, you will need: Provide the packet capture directory (where pcap files will be saved). That can be done with the command line argument --capture_dir or when instantiating Mininet_sec with parameter captureDir (see examples/firewall.py). You can also configure the maximum file size for pcap files with the --capture_file_size (or captureFileSize on Mininet_sec python class) -- defaults to 10M.
Many parts of the code here were inspired or directly derivated from great projects like Mini-NDN ( https://github.com/named-data/mini-ndn/ ), Mininet-WiFi ( https://github.com/intrig-unicamp/mininet-wifi/ ) and, of course, Mininet ( https://github.com/mininet/mininet ). Emulation platform for studying and experimenting cybersecurity tools in programmable networks MiniCPS is a lightweight simulator for accurate network traffic in an industrial control system, with basic support for physical layer interaction.
4. Practical Deployment, Analysis & Case Studies This page summarizes the basic installation, configuration and testing of MiniCPS. We provide a tutorial for beginners here: SWaT tutorial . If you need more information about a specific topic see Misc . Notice that Mininet can be installed either inside a Virtual Machine (VM) or on your physical machine. The official Mininet VM comes without an X-server that is an optional requirements for MiniCPS (e.g., it can be used to display a pop-up window with sensor data visualization).
The Install MiniCPS section provides instructions to install minicps for a user or a developer, and it assumes that you already have installed mininet . Test the installation downloading one of our examples from https://github.com/scy-phy/minicps/tree/master/examples and try to run it.
For example, given that you downloaded the examples directory, then you can cd swat-s1 folder and run: For SDN controller development there are many options, pox is a good starting point and Mininet’s VM already includes it. If you want to manually install it type: MiniCPS pox controller files are tracked in the minicps repo itself. To symlink them to pox’s dedicated external controller folder ( pox/ext ) execute the following: If you want to redirect X command to your host X-server ssh into mininet VM, e.g., to display graphs even if your VM doesn’t run an X server, using the -Y option: In order to reduce the network traffic you can disable the Linux ipv6 kernel module. ( mininet VM already disables it) Search for GRUB_CMDLINE_LINUX_DEFAULT and prepend to the string ipv6.disable=1 . You should obtain something like this: This project is about learning the Mininet simulator and understanding how attackers intercept and manipulate network traffic in real-world scenarios.
I have set up a virtual LAN using Mininet. • Used Wireshark to capture traffic (e.g., passwords sent over HTTP). • Performed ARP spoofing and DNS spoofing using Ettercap or Bettercap. • Simulated DoS attacks and analyze packet loss or queuing behavior. Introduction This lab was conducted within a Mininet emulated network to safely explore critical security flaws inherent in modern networking. This lab explored network security vulnerabilities using Mininet to simulate a local area network and Wireshark to capture and analyze network traffic. The experiment demonstrates how attackers can intercept unencrypted communications in real-world scenarios.
Methodology Task 1: Set up a virtual LAN using Mininet. A simple single topology was created in Mininet with two hosts and one switch: h1 (attacker/victim), h2 (server/victim). I checked the reachability with pingall Task 2: Used Wireshark to capture traffic On h2 I started a simple HTTP server using python3 -m http.server 80 & I checked the server is running Started a packet dump on h1 using tcpdump (the command-line version of Wireshark) -i h1-eth0: Listens on h1's network interface. -w capture.pcap: Saves all captured packets to a file named capture.pcap. &: Runs it in the background.
5. Performance Evaluation & Extended Technical Observations Generated traffic to capture sending a password using Python h1 python3 -c "import urllib.request; response = urllib.request.urlopen(' http://10.0.0.2/?username=admin&password=plaintextpass123 '); print(response.read().decode())" Output: Checked the capture file has been created Checked the capture file has been created Used the Wireshark command line version to analyze the capture: Listed all packets Basic file information Successfully intercepted the traffic with Wireshark ARP spoofing is a type of attack in which a malicious actor sends falsified ARP (Address Resolution Protocol) messages over a local area network. This results in the linking of an attacker's MAC address with the IP address of a legitimate computer or server on the network.
Step 1 Changed topology using 3 hosts. sudo mn -c (clear cache from previous topologies) sudo mn --topo single,3 --mac # h1=attacker, h2=victim, h3=server Enabled ip forwarding on h1 Spoofing from h1 to h2,h3 h1 ettercap -T -i h1-eth0 -M arp:remote /10.0.0.2// /10.0.0.3// On H1 arp spoofing on h2 and h3 After spoofing On host2 we show the arp table again. We notice that the mac addresses of host 3 points to host 1 On H1 a spoofing entry is inserted which points facebook.com to H1 in the following file /etc/ettercap/etter.dns Run Ettercap with the DNS spoof plugin h1 ettercap -T -i h1-eth0 -M arp:remote /10.0.0.2// /10.0.0.3// -P dns_spoof Verified by using nslookup facebook.com which points to h1 TASK 4. Simulate DoS attacks and analyze packet loss or queuing behavior For this scenario I am going to simulate a SYN flood a web server on port 80 (from H1 to web server H3) We install hping3 (Offensive Security, n.d.), a network tool able to send custom ICMP/UDP/TCP packets and to display target replies like ping does with ICMP replies. It handles fragmentation and arbitrary packet body and size, and can be used to transfer files under supported protocols. Using hping3, you can test firewall rules, perform (spoofed) port scanning, test network performance using different protocols, do path MTU discovery, perform traceroute-like actions under different protocols, fingerprint remote operating systems, audit TCP/IP stacks, etc.
hping3 is scriptable using the Tcl language. h1 hping3 --flood -S -p 80 10.0.0.2 --flood = send packets as fast as possible -S = set SYN flag -p 80 = destination port References Offensive Security. (n.d.). hping3. In Kali Linux tools. Kali Linux. https://www.kali.org/tools/hping3/ This project is about learning the Mininet simulator and understanding how attackers intercept and manipulate network traffic in real-world scenarios.
This project aims to provide the necessary files for simulating a complete microgrid industrial environment, including a SCADA server (SCADABR), a microgrid simulation with Simulink, and a Modbus server. This project was carried out as part of the INF6103 "Cybersecurity of critical infrastructure" course given at Polytechnique Montréal. /scadabr : Contains the files necessary to configure and run the SCADA server (SCADABR). Refer to the README inside this directory for detailed instructions on configuration.
/simulink : Includes Simulink files needed to simulate a microgrid. Explore the directory to find examples of configurations and usage. You have to open this repository inside your matlab. Execute the simulation directly with the tcp_client.m script. /modbus-server : Contains files to set up a Modbus server. The README in this directory will guide you through the configuration and execution.
For a complete simulation environment, you will need three different virtual machines: SCADABR Server VM: Set up a virtual machine to host the SCADABR server. Follow the instructions in /scadabr for configuration details. Modbus Server VM: Create another virtual machine dedicated to the Modbus server. Refer to the documentation in /modbus-server for setup instructions.
Harvested Online Documentation & Reference Sources • https://mininet-sec.github.io/ • https://github.com/dipi-unimore/mininet-gym • https://github.com/mininet-sec/mininet-sec/ • https://minicps.readthedocs.io/en/latest/userguide.html • https://github.com/donscara/Mininet-Simulator • https://github.com/abonnivard/Microgrid-simulation-for-security-test
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Scada System Cybersecurity Simulation Using Mininet.
[*] Metasploit Scan Running on Target Subnet for Scada System Cybersecurity Simulation Using Mininet... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |