Complete Technical Paper Content — Screen Capture Prevention In Secure Desktop Applications
Overview & System Context
Screen Capture Prevention In Secure Desktop Applications: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9538 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Keystroke logging, often referred to as keylogging or keyboard capturing, is the action of recording (logging) the keys pressed on a keyboard, typically covertly, so that a person using the keyboard is unaware that their actions are being monitored. Data can then be retrieved by the person operating the logging program. A keystroke recorder or keylogger can be either software or hardware. While the programs themselves are legal, with many designed to allow employers to oversee the use of their computers, keyloggers are most often used for stealing passwords and other confidential information. Keystroke logging can also be utilized to monitor activities of children in schools or at home and by law enforcement officials to investigate malicious usage. Keylogging can also be used to study keystroke dynamics or human-computer interaction. Numerous keylogging methods exist, ranging from hardware and software-based approaches to acoustic cryptanalysis.
A software-based keylogger is a computer program designed to record any input from the keyboard. Keyloggers are used in IT organizations to troubleshoot technical problems with computers and business networks. Families and businesspeople use keyloggers legally to monitor network usage without their users' direct knowledge. Microsoft publicly stated that Windows 10 has a built-in keylogger in its final version "to improve typing and writing services". However, malicious individuals can use keyloggers on public computers to steal passwords or credit card information. Most keyloggers are not stopped by HTTPS encryption because that only protects data in transit between computers; software-based keyloggers run on the affected user's computer, reading keyboard inputs directly as the user types. From a technical perspective, there are several categories: Hypervisor-based: The keylogger can theoretically reside in a malware hypervisor running underneath the operating system, which thus remains untouched. It effectively becomes a virtual machine. Blue Pill is a conceptual example. Kernel-based: A program on the machine obtains root access to hide in the OS and intercepts keystrokes that pass through the kernel. This method is difficult both to write and to combat. Such keyloggers reside at the kernel level, which makes them difficult to detect, especially for user-mode applications that do not have root access. They are frequently implemented as rootkits that subvert the operating system kernel to gain unauthorized access to the hardware. This makes them very powerful. A keylogger using this method can act as a keyboard device driver, for example, and thus gain access to any information typed on the keyboard as it goes to the operating system. API-based: These keyloggers hook keyboard APIs inside a running application. The keylogger registers keystroke events as if it was a normal piece of the application instead of malware. The keylogger receives an event each time the user presses or releases a key. The keylogger simply records it. This is usually done by inject a DLL to other processes. Windows APIs such as GetAsyncKeyState(), GetForegroundWindow(), etc. are used to poll the state of the keyboard or to subscribe to keyboard events. A more recent example simply polls the BIOS for pre-boot authentication PINs that have not been cleared from memory. Form grabbing based: Form grabbing-based keyloggers log Web form submissions by recording the form data on submit events. This happens when the user completes a form and submits it, usually by clicking a button or pressing enter. This type of keylogger records form data before it is passed over the Internet. IME-based: A malicious IME can do keylogging. JavaScript-based: A malicious script tag is injected into a targeted web page, and listens for key events such as onKeyUp(). Scripts can be injected via a variety of methods, including cross-site scripting, man-in-the-browser, man-in-the-middle, or a compromise of the remote website. Memory-injection-based: Memory Injection (MitB)-based keyloggers perform their logging function by altering the memory tables associated with the browser and other system functions. By patching the memory tables or injecting directly into memory, this technique can be used by malware authors to bypass Windows UAC (User Account Control). The Zeus and SpyEye trojans use this method exclusively.
Non-Windows systems have protection mechanisms that allow access to locally recorded data from a remote location. Remote communication may be achieved when one of these methods is used: Data is uploaded to a website, database or an FTP server. Data is periodically emailed to a pre-defined email address. Data is Wirelessly transmitted employing an attached hardware system. The software enables a remote login to the local machine from the Internet or the local network, for data logs stored on the target machine.
descriptions of writing strategies; the writing development of children (with and without writing difficulties), spelling, first and second language writing, and specialist skill areas such as translation and subtitling. Keystroke logging can be used to research writing, specifically. It can also be integrated into educational domains for second language learning, programming skills, and typing skills.
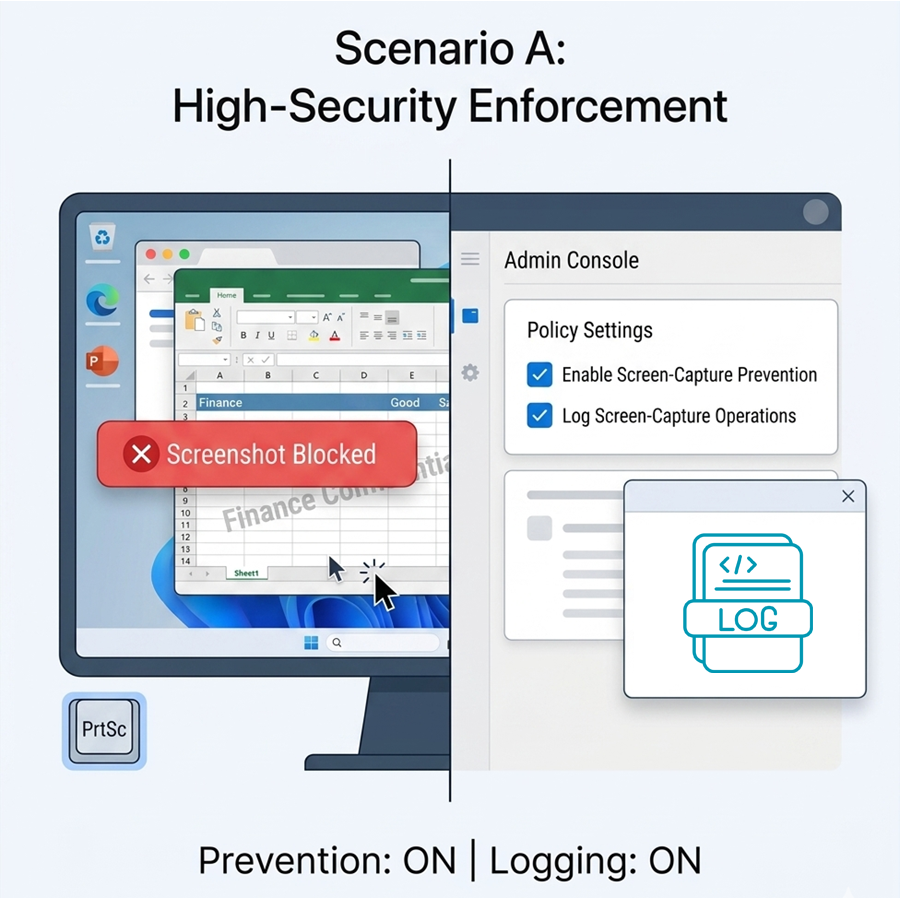
Figure 1: Screen Capture Prevention Software | Block Screenshots & Print Screen This study also reported that machine learning models trained on genuine typing behavior achieved low false acceptance and false rejection rates in most instances, showing that the use of continuous authentication systems can operate with low error rates. They also found that the typing patterns of most people have enough discriminatory signals that you could create a personal profile based on the typing habits alone. This shows that the same core exploits used by malicious attackers can also form the basis of security systems designed to protect users from intrusions and impersonations. The authors concluded that while keystroke-dynamics authentication is promising, its deployment must carefully balance security, usability, and privacy considerations for the optimal user experience.
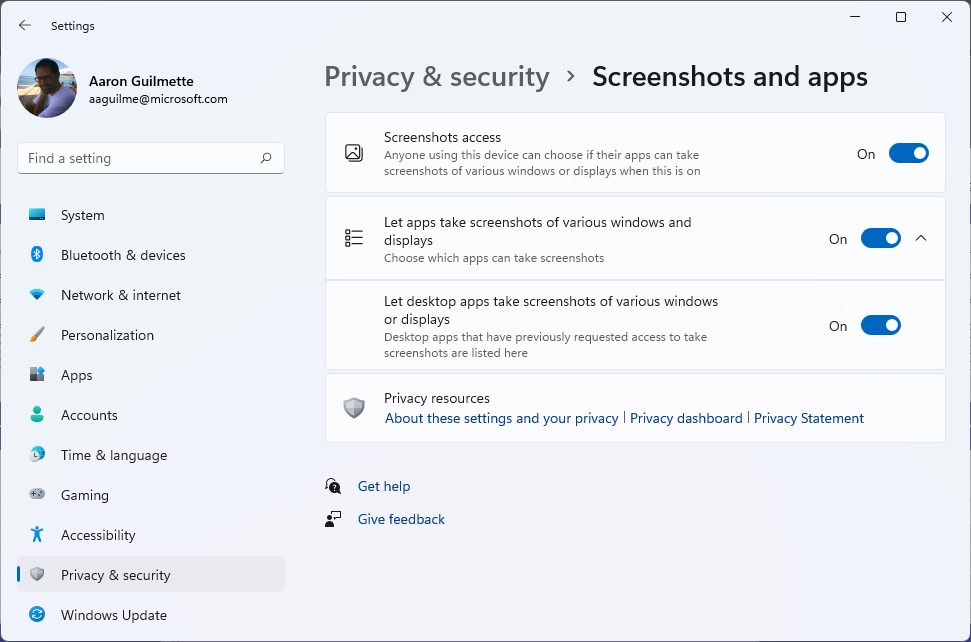
Clipboard logging. Anything that has been copied to the clipboard can be captured by the program. Screen logging. Screenshots are taken to capture graphics-based information. Applications with screen logging abilities may take screenshots of the whole screen, of just one application, or even just around the mouse cursor. They may take these screenshots periodically or in response to user behaviors (for example, when a user clicks the mouse). Screen logging can be used to capture data inputted with an on-screen keyboard. Programmatically capturing the text in a control. The Microsoft Windows API allows programs to request the text 'value' in some controls. This means that some passwords may be captured, even if they are hidden behind password masks (usually asterisks). The recording of every program/folder/window opened including a screenshot of every website visited. The recording of search engines queries, instant messenger conversations, FTP downloads and other Internet-based activities (including the bandwidth used).
Hardware-based keyloggers do not depend upon any software being installed as they exist at a hardware level in a computer system. Firmware-based: BIOS-level firmware that handles keyboard events can be modified to record these events as they are processed. Physical and/or root-level access is required to the machine, and the software loaded into the BIOS needs to be created for the specific hardware that it will be running on. Keyboard hardware: Hardware keyloggers are used for keystroke logging utilizing a hardware circuit that is attached somewhere in between the computer keyboard and the computer, typically inline with the keyboard's cable connector. There are also USB connector-based hardware keyloggers, as well as ones for laptop computers (the Mini-PCI card plugs into the expansion slot of a laptop). More stealthy implementations can be installed or built into standard keyboards so that no device is visible on the external cable. Both types log all keyboard activity to their internal memory, which can be subsequently accessed, for example, by typing in a secret key sequence. Hardware keyloggers do not require any software to be installed on a target user's computer, therefore not interfering with the computer's operation and less likely to be detected by software running on it. However, its physical presence may be detected if, for example, it is installed outside the case as an inline device between the computer and the keyboard. Some of these implementations can be controlled and monitored remotely using a wireless communication standard. Wireless keyboard and mouse sniffers: These passive sniffers collect packets of data being transferred from a wireless keyboard and its receiver. As encryption may be used to secure the wireless communications between the two devices, this may need to be cracked beforehand if the transmissions are to be read. In some cases, this enables an attacker to type arbitrary commands into a victim's computer. Keyboard overlays: Criminals have been known to use keyboard overlays on ATMs to capture people's PINs. Each keypress is registered by the keyboard of the ATM as well as the criminal's keypad that is placed over it. The device is designed to look like an integrated part of the machine so that bank customers are unaware of its presence. Acoustic keyloggers: Acoustic cryptanalysis can be used to monitor the sound created by someone typing on a computer. Each key on the keyboard makes a subtly different acoustic signature when struck. It is then possible to identify which keystroke signature relates to which keyboard character via statistical methods such as frequency analysis. The repetition frequency of similar acoustic keystroke signatures, the timings between different keyboard strokes and other context information such as the probable language in which the user is writing are used in this analysis to map sounds to letters. A fairly long recording (1000 or more keystrokes) is required so that a large enough sample is collected. Electromagnetic emissions: It is possible to capture the electromagnetic emissions of a wired keyboard from up to 20 metres (66 ft) away, without being physically wired to it. In 2009, Swiss researchers tested 11 different USB, PS/2 and laptop keyboards in a semi-anechoic chamber and found them all vulnerable, primarily because of the prohibitive cost of adding shielding during manufacture. The researchers used a wide-band receiver to tune into the specific frequency of the emissions radiated from the keyboards. Optical surveillance: Optical surveillance, while not a keylogger in the classical sense, is nonetheless an approach that can be used to capture passwords or PINs. A strategically placed camera, such as a hidden surveillance camera at an ATM, can allow a criminal to watch a PIN or password being entered. Physical evidence: For a keypad that is used only to enter a security code, the keys which are in actual use will have evidence of use from many fingerprints. A passcode of four digits, if the four digits in question are known, is reduced from 10,000 possibilities to just 24 possibilities (104 versus 4! [factorial of 4]). These could then be used on separate occasions for a manual "brute force attack". Smartphone sensors: Researchers have demonstrated that it is possible to capture the keystrokes of nearby computer keyboards using only the commodity accelerometer found in smartphones. The attack is made possible by placing a smartphone near a keyboard on the same desk. The smartphone's accelerometer can then detect the vibrations created by typing on the keyboard and then translate this raw accelerometer signal into readable sentences with as much as 80 percent accuracy. The technique involves working through probability by detecting pairs of keystrokes, rather than individual keys. It models "keyboard events" in pairs and then works out whether the pair of keys pressed is on the left or the right side of the keyboard and whether they are close together or far apart on the QWERTY keyboard. Once it has worked this out, it compares the results to a preloaded dictionary where each word has been broken down in the same way. Similar techniques have also been shown to be effective at capturing keystrokes on touchscreen keyboards while in some cases, in combination with gyroscope or with the ambient-light sensor. Body keyloggers: Body keyloggers track and analyze body movements to determine which keys were pressed. The attacker needs to be familiar with the keys layout of the tracked keyboard to correlate between body movements and keys position, although with a suitably large sample this can be deduced. Tracking audible signals of the user' interface (e.g. a sound the device produce to informs the user that a keystroke was logged) may reduce the complexity of the body keylogging algorithms, as it marks the moment at which a key was pressed.
Figure 2: Blocking Screen capture - Undocumented Features An anti-keylogger is a piece of software specifically designed to detect keyloggers on a computer, typically comparing all files in the computer against a database of keyloggers, looking for similarities which might indicate the presence of a hidden keylogger. As anti-keyloggers have been designed specifically to detect keyloggers, they have the potential to be more effective than conventional antivirus software; some antivirus software do not consider keyloggers to be malware, as under some circumstances a keylogger can be considered a legitimate piece of software.
Automatic form-filling programs may prevent keylogging by removing the requirement for a user to type personal details and passwords using the keyboard. Form fillers are primarily designed for Web browsers to fill in checkout pages and log users into their accounts. Once the user's account and credit card information has been entered into the program, it will be automatically entered into forms without ever using the keyboard or clipboard, thereby reducing the possibility that private data is being recorded. However, someone with physical access to the machine may still be able to install software that can intercept this information elsewhere in the operating system or while in transit on the network. (Transport Layer Security (TLS) reduces the risk that data in transit may be intercepted by network sniffers and proxy tools.) Safari is a web browser developed by Apple. It is built into several of Apple's operating systems, including macOS, iOS, iPadOS, and visionOS, and uses Apple's open-source browser engine WebKit, which was derived from KHTML. It is the second most used browser in the world, after Google Chrome. Safari was introduced in an update to Mac OS X Jaguar in January 2003, and made the default web browser with the release of Mac OS X Panther that same year. It has been included with the iPhone since the first-generation iPhone in 2007. At that time, Safari was the fastest browser on the Mac. Between 2007 and 2012, Apple maintained a Windows version, but abandoned it due to low market share. In 2010, Safari 5 introduced a reader mode, extensions, and developer tools. Safari 11, released in 2017, added Intelligent Tracking Prevention, which uses artificial intelligence to block web tracking. Safari 13 added support for Apple Pay, and authentication with FIDO2 security keys. Its user interface was redesigned in Safari 15, Safari 18, and Safari 26.
Safari 4 was released on June 8, 2009. It was the first version that had completely passed the Acid3 rendering test, as well as the first version to support HTML5. It incorporated WebKit JavaScript engine SquirrelFish that significantly enhanced the browser's script interpretation performances by 29.9x. SquirrelFish was later evolved to SquirrelFish Extreme, later also marketed as Nitro, which had 63.6x faster performance. A public beta of Safari 4 was experimented on February 24, 2009.
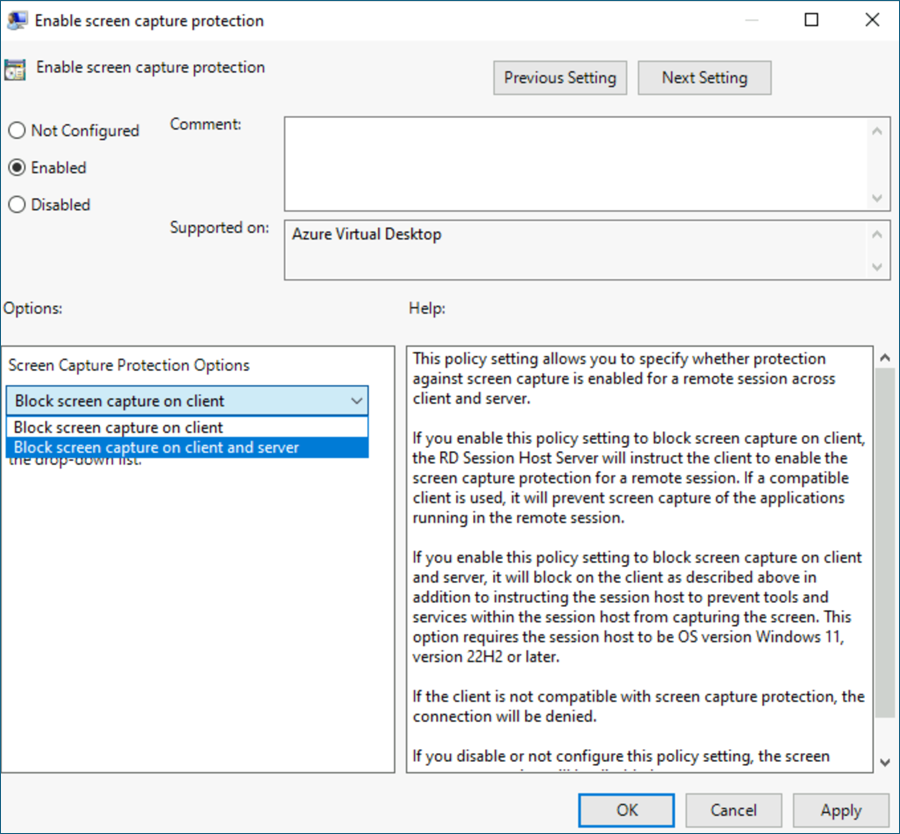
Figure 3: Terminalworks Blog | AVD Security | Screen capture protection ... Safari 4 relied on Cover Flow to run the History and Bookmarks, and it featured Speculative Loading that automatically pre-loaded document information that is required to visit a particular website. The top sites can be displayed up to 24 thumbnails based on the frequently visited sites in a startup. The desktop version of Safari 4 included a redesign similar to that of the iPhone. The update also commissioned many developer tool improvements, including Web Inspectors, CSS element viewings, JavaScript debuggers and profilers, offline tables, database management, SQL support, and resource graphs. In addition to CSS retouching effects, CSS canvas, and HTML5 content. It replaced the initial Mac OS X-like interface with native Windows themes on Windows, using native font renderings. Safari 4.0.1 was released for Mac on June 17, 2009, and fixed Faces bugs in iPhoto '09. Safari 4 in Mac OS X v10.6 "Snow Leopard" has built-in 64-bit support, which makes JavaScript load up to 50% faster. It also has native crash resistances that would maintain it intact if a plugin like Flash player crashes, though other tabs or windows would not be affected. Safari 4.0.4, the final version which was released on November 11, 2009, for both Mac and Windows, which further improved the JavaScript performances.
Safari 5 was released on June 7, 2010, and featured a less distracting reader view, and had a 30x faster JavaScript performances. It incorporated numerous developer tool improvements, including HTML5 interoperability and accessibility to secure extensions. The progress bar was re-added in this version as well. Safari 5.0.1 enabled the Extensions PrefPane by default, rather than requiring users to manually set it in the Debug menu. Version 5.1.7 was the final version for Windows.
While no longer available from Apple, this release can still be downloaded from the Wayback Machine and is still functional on Windows 11. Apple exclusively released Safari 4.1 concurrently with Safari 5 for Mac OS X Tiger. It included many features that were found in Safari 5, though it excluded the Safari Reader and Safari Extensions. Apple released Safari 5.1 for both Windows and Mac on July 20, 2011, for Mac OS X 10.7 Lion; it was faster than Safari 5.0, and included the new Reading List feature. The company simultaneously announced Safari 5.0.6 in late June 2010 for Mac OS X 10.5 Leopard, though the new functions were excluded from Leopard users. Several HTML5 features were provided in Safari 5. It added supports for full-screen video, closed caption, geolocation, EventSource, and a now obsolete early variant of the WebSocket protocol. The fifth major version of Safari added supports for Full-text search, and a new search engine, Bing. Safari 5 supported Reader, which displays web pages in a continuous view, without advertisements. Safari 5 supported a smarter address field and DNS prefetching that automatically found links and looked up addresses on the web. New web pages loaded faster using Domain Name System (DNS) prefetching. The Windows version received an extra update on graphics acceleration as well. The blue inline progress bar was returned to the address bar, in addition to the spinning bezel and loading indicator introduced in Safari 4. Top Sites view now has a button to switch to Full History Search. Other features included Extension Builder for developers of Safari Extensions. Other changes included an improved inspector. Safari 5 supports Extensions, add-ons that customize the web browsing experience. Extensions are built using web standards such as HTML5, CSS3, and JavaScript.
On June 11, 2012, Apple released a developer preview of Safari 6.0 with a feature called iCloud Tabs, which syncs with open tabs on any iOS or other OS X device that runs the latest software. It updated new privacy features, including an "Ask websites not to track me" preference and the ability for websites to send OS X 10.8 Mountain Lion users notifications, though it removed RSS support. Safari 6 had the Share Sheets capability in OS X Mountain Lion. The Share Sheet options were: Add to Reading List, Add Bookmark, Email this Page, Message, Twitter, and Facebook. Tabs with full-page previews were added, too. The sixth major version of Safari, it added options to allow pages to be shared with other users via email, Messages, Twitter, and Facebook, as well as making some minor performance improvements. It added supports for -webkit-calc() in CSS. Additionally, various features were removed, including Activity Window, a separate Download Window, direct support for RSS feeds in the URL field, and bookmarks. The separate search field and the address bar were also no longer available as a toolbar configuration option. Instead, it was replaced by the smart search field, a combination of the address bar and the search field.
Safari 7 was announced at WWDC 2013, and it brought a number of JavaScript performance improvements. It made use of Top Site and Sidebar, Shared Links, and Power Saver, which paused unused plugins. Safari 7 for OS X Mavericks and Safari 6.1 for Lion and Mountain Lion were all released along with OS X Mavericks in the special event on October 22, 2013. Safari 10 was shipped with macOS Sierra and released for OS X Yosemite and OS X El Capitan on September 20, 2016. It had a redesigned Bookmark and History views, and double-clicking will centralized focus on a particular folder. The update redirected Safari extensions to be saved directly to Pocket and Dic Go. Software improvements included Autofill quality from the Contrast card and Web Inspector Timelines Tab, in-line sub-headlines, bylines, and publish dates. This version tracks and re-applies zoomed level to websites, and legacy plug-ins were disabled by default in favor of HTML5 versions of websites.
Recently closed tabs can be reopened via the History menu, or by holding the "+" button in the tab bar, and using Shift-Command-T. When a link opens in a new tab; it is now possible to hit the back button or swipe to close it and go back to the original tab. Debugging is now supported on the Web Inspector. Safari 10 also includes several security updates, including fixes for six WebKit vulnerabilities and issues related to Reader and Tabs. The first version of Safari 10 was released on September 20, 2016, and the last version (10.1.2) was released on July 19, 2017.
Safari 12 was released for macOS Mojave on September 24, 2018. It was also available to macOS Sierra and macOS High Sierra on September 17, 2018. Safari 12 included several new features such as icons in tabs, automatic strong passwords, and Intelligent Tracking Prevention 2.0. Safari version 12.0.1 was released on October 30, 2018, within macOS Mojave 10.14.1, and Safari 12.0.2 was released on December 5, 2018, under macOS 10.14.2. Support for developer-signed classic Safari Extensions has been dropped. This version would also be the last that supported the official Extensions Gallery. Apple also encouraged extension authors to switch to Safari App Extensions, which triggered negative feedback from the community.
Until Safari 6.0, it included a built-in web feed aggregator that supported the RSS and Atom standards. Current features include Private Browsing (a mode in which the browser retains no record of information about the user's web activity), the ability to archive web content in WebArchive format, the ability to email complete web pages directly from a browser menu, the ability to search bookmarks, and the ability to share tabs between all Mac and iOS devices running appropriate versions of software via an iCloud account.
Safari for iPhone was released along with the original iPhone. It was well received at the time of release, with news outlets calling it "far superior" to other mobile browsers at the time. Safari has also been available for iPadOS since its split from the main iOS operating system. With the release of iPadOS 13, Safari for iPad's user agent was changed to present itself to websites as Safari for Mac and shows the desktop version of websites, except in the miniature Slide Over multitasking view.
Apple improved multitouch compatibility for desktop websites through several tweaks to the WebKit engine, for example, with heuristics to determine whether to translate a tap into a hover or a click. The iPadOS version also gained a download manager, support for Media Source Extensions to allow users to watch Netflix in Safari, and support for the custom keyboard shortcuts in web apps like Gmail, which override Safari's own keyboard shortcuts. External webcam support for websites was later added also. The browser has continued to receive updates with new releases of iOS, such as the addition of browsing profiles for different use cases with iOS 17, and a locked private browsing feature. iOS 15 added support for third-party browser extensions, which can be downloaded and installed through corresponding apps via the App Store. Extensions available included VPNs and content blockers. Universal extensions that also worked with the Mac version of Safari can be created via a WebExtensions API.
In 2009, Safari had a market share of 3.85%. It remained stable in that rank for five years with market shares of 5.56% (2010), 7.41% (2011), 10.07% (2012), and 11.77% (2013). In 2014, it caught up with Firefox with a market share of 14.20%. In 2015, Safari became the second most-used web browser worldwide after Google Chrome, and had a market share of 13.01%. From 2015 to 2020, it occupied market shares of 14.02%, 14.86%, 14.69%, 17.68% and 19.25%, respectively. As of November 2021, Google Chrome continued to be the most popular browser with Safari (19.22%) following behind in second place. In May 2022, according to StatCounter, Apple's Safari dropped to the third most popular desktop browser after being overtaken by Microsoft Edge. Safari was then used by 9.61% of desktop computers worldwide. One year later, Safari retook second place.
Access to this page requires authorization. You can try signing in or changing directories . Screen capture protection, alongside watermarking , helps prevent sensitive data from being captured on client devices using specific operating system (OS) features and APIs. When you enable screen capture protection, remote content is automatically blocked in screenshots and screen sharing. This feature can be applied to Azure Virtual Desktop virtual machines and Windows 365 Cloud PCs.
When screen capture protection (SCP) is enabled to block screen capture on the client, users can continue to share their remote desktop or individual applications using supported collaboration experiences such as Microsoft Teams. Compatibility between SCP and Teams screen sharing depends on the use of supported client configurations. When unsupported configurations are used, protected content might appear as a black screen during sharing. For current compatibility requirements and configuration guidance with Teams, see Azure Virtual Desktop screen capture protection and Microsoft Teams compatibility .
Screen capture protection doesn't provide Digital Rights Management (DRM)-level protection. It prevents screen capture through standard OS features and APIs and isn't a substitute for DRM solutions. For comprehensive data protection, use screen capture protection as part of a broader defense-in-depth security strategy that includes other controls, such as Conditional Access policies, data loss prevention, and endpoint management.
To increase the security of your sensitive information, you should also disable clipboard, drive, and printer redirection. Disabling redirection helps prevent users from copying content from the remote session. To learn about supported redirection values, see Device redirection . To discourage other methods of screen capture, such as taking a photo of a screen with a physical camera, you can enable watermarking , where admins can use a QR code to trace the session.
The steps to configure screen capture protection depend on where you configure it, which platforms your users are connecting from, and what scenario you want to achieve. Native clients on Windows and macOS : when users connect with the natively installed Windows App or Remote Desktop client, configure screen capture protection on the virtual machines (Azure Virtual Desktop) or Cloud PCs (Windows 365) using an Intune device configuration policy or Group Policy. The native client enforces these settings without an Intune MAM app protection policy. For browser connections, including Microsoft Edge on Windows, follow Pattern 3: Web endpoints (browser access) .
When you configure screen capture protection on virtual machines or Cloud PCs, there are two further settings you can configure to help meet your requirements: Block screen capture on client : prevents screen capture from the local device of applications running in the remote session. Block screen capture on client and server : prevents screen capture from the local device of applications running in the remote session, but also prevents tools and services within the virtual machine or Cloud PC capturing the screen.
1. Hybrid enforcement (iOS/iPadOS/Android/Web) : When screen capture protection is enabled on the virtual machine or Cloud PC, connections from Windows App on iOS/iPadOS and Android are allowed when an Intune MAM app protection policy that blocks screen capture applies to the app. On the web, connections from Microsoft Edge for Business are allowed when the Edge work profile receives an Intune MAM app protection policy that enforces screen capture protection through the Edge data loss prevention (DLP) features. Hybrid enforcement isn't applicable on platforms that don't support Intune MAM.
Android, iOS/iPadOS, and web connections : configure an Intune MAM app protection policy for the supported client app and assign it to the users who need protection. For Android and iOS/iPadOS, the policy applies to Windows App. For web connections on Windows, the policy applies to Microsoft Edge for Business through the user's work profile. This client-side protection prevents local screen capture of protected content; it doesn't prevent tools and services within the virtual machine or Cloud PC from capturing the screen. For configuration steps, see Enable screen capture protection with Intune MAM .
2. System Architecture & Core Working Principles 1. On the web, screen capture protection is enforced by the Edge for Business data loss prevention (DLP) features when users connect with Microsoft Edge for Business and receive an Intune MAM app protection policy. For configuration steps, see Enable screen capture protection with Intune MAM .
For Android and iOS/iPadOS devices, and for the web client (on Windows), screen capture protection is enforced through Intune mobile application management (MAM). In each case, you configure two things: an Intune MAM app protection policy that applies screen capture protection, and a Conditional Access policy that requires the app protection policy so users can only connect when the policy is applied to the client. The exact app protection policy setting differs by platform âII on Android and iOS/iPadOS you block screen capture directly, while on the web you configure Microsoft Edge for Business, where screen capture protection is enforced through the Edge data loss prevention (DLP) features. When screen capture protection is configured on your virtual machines or Cloud PCs, this is the supported model for these platforms. For configuration steps, see Enable screen capture protection with Intune MAM .
Screen capture protection is fully supported on Windows, but it has known limitations on macOS due to the platform's current security architecture: Microsoft Teams compatibility : on macOS, enabling screen capture protection might interfere with screen sharing in Microsoft Teams, potentially causing shared windows to appear blank or not display properly. If Teams-based collaboration is required, screen capture protection might need to be temporarily disabled on the device.
Platform-level enforcement : due to macOS restrictions, some native applications might not fully respect screen capture protection enforcement. This is a limitation of the operating system's available APIs, not a defect in screen capture protection itself. For collaboration-heavy macOS workflows, consider configuring screen capture protection settings based on business need and risk level.
For highly sensitive content, Windows endpoints are recommended for full enforcement of screen protection features. Watermarking and administrative policies can be used to further discourage misuse on platforms with limited enforcement. The following patterns describe common deployment scenarios for screen capture protection: Use this pattern when users connect with the natively installed Windows App or Remote Desktop client on Windows or macOS.
An Intune MAM app protection policy isn't required for these native clients. Browser connections use a different configuration, even when the browser runs on a Windows device. For browser connections, follow Pattern 3: Web endpoints (browser access) . If your users connect from both desktop and mobile devices, use hybrid enforcement. Configure screen capture protection on both the virtual machine or Cloud PC and the Intune MAM app protection policy.
For Windows App in a web browser, use Microsoft Edge for Business on Windows with an Intune MAM app protection policy that targets Microsoft Edge. Also configure a Conditional Access policy that requires app protection before allowing access to your remote resources. The user must sign in to an Edge work profile with your organization's work account and use that same account to access Windows App from that profile. Signing in to the Windows App website alone isn't sufficient: the Edge work profile must receive your organization's app protection policy.
Assign the app protection policy to the users who require protection. For example, if a contractor accesses your organization's remote resources using a work account that your organization provides, include that account in the policy assignment. Assigning the policy to a different account doesn't protect the profile used for that connection. A user might have work accounts from more than one organization, such as a contractor who works for several clients. On a device that none of these organizations manages, the user signs in to a separate Edge work profile for each work account.
Each profile receives only its own organization's app protection policy. To connect to your remote resources with screen capture protection, the user must open Windows App from the profile that's signed in with your organization's work account. Users don't need to enroll their devices in your organization's device management. Web screen capture protection is supported on personal devices and, with Microsoft Edge for Business version 147 or later, on devices managed by a different organization, such as a contractor's employer. The following limitations apply: Before you can configure screen capture protection, ensure you meet the following prerequisites: For scenarios where you need to configure virtual machines or Cloud PCs, those virtual machines or Cloud PCs must be running Windows 11, version 22H2 or later, or Windows 10, version 22H2 or later.
Users connecting with a natively installed client must use a supported version of Windows App or the Remote Desktop client. The following tables show supported native-client scenarios: 1. Doesn't include support for ChromeOS because Intune MAM isn't supported on ChromeOS. For additional Intune and Conditional Access prerequisites, see Require local client device security compliance with Microsoft Intune and Microsoft Entra Conditional Access .
To configure an Intune device configuration policy on virtual machines or Cloud PCs, you need: A Microsoft Entra ID account that's assigned the Policy and Profile manager built-in RBAC role. A security group or organizational unit (OU) containing the devices you want to configure. Enable screen capture protection on virtual machines and Cloud PCs using an Intune device configuration policy or Group Policy To configure screen capture protection on virtual machines (Azure Virtual Desktop) or Cloud PCs (Windows 365) using Microsoft Intune: Create or edit a configuration profile for Windows 10 and later devices, with the Settings catalog profile type.
In the settings picker, browse to Administrative templates > Windows Components > Remote Desktop Services > Remote Desktop Session Host > Azure Virtual Desktop . Expand the Administrative templates category, then toggle the switch for Enable screen capture protection to Enabled . Toggle the switch for Screen Capture Protection Options (Device) to off for Block screen capture on client , or on for Block screen capture on client and server based on your requirements, then select OK .
Optional : On the Scope tags tab, select a scope tag to filter the profile. For more information about scope tags, see Use role-based access control (RBAC) and scope tags for distributed IT . On the Assignments tab, select the group containing the computers providing a remote session you want to configure, then select Next .
Once the policy applies to the computers providing a remote session, restart them for the settings to take effect. 3. Software Implementation, Frameworks & Protocols To configure screen capture protection on virtual machines (Azure Virtual Desktop) or Cloud PCs (Windows 365) using Group Policy in an Active Directory domain: Follow the steps to make the Administrative template for Azure Virtual Desktop available in Group Policy.
Open the Group Policy Management console on a device you use to manage the Active Directory domain. Create or edit a policy that targets the computers providing a remote session you want to configure. Navigate to Computer Configuration > Policies > Administrative Templates > Windows Components > Remote Desktop Services > Remote Desktop Session Host > Azure Virtual Desktop .
Double-click the policy setting Enable screen capture protection to open it, then select Enabled . From the drop-down menu, select the screen capture protection scenario you want to use from Block screen capture on client or Block screen capture on client and server based on your requirements, then select OK . Ensure the policy is applied to the computers providing a remote session, then restart them for the settings to take effect.
For Android, iOS/iPadOS, and the web client (on Windows), you enforce screen capture protection through Intune mobile application management (MAM). For each of these approaches, the configuration has two parts: Configure an Intune MAM app protection policy for the platform your users connect from. Follow the steps in Create an app protection policy , and use the app selection and screen capture protection settings below for your platform: Web (Microsoft Edge for Business on Windows) : create or edit an Intune app protection policy with the following settings: For web connections, Microsoft Edge is the app that receives the app protection policy, not the natively installed Windows App. The user must access Windows App from the Edge work profile that receives this policy.
The clipboard setting above restricts copy and paste and automatically activates screen capture protection across the entire protected Edge work profile, including all tabs in that profile. Protection isn't limited to the Windows App tab. For more information, see Data protection features for Microsoft Edge using Intune App Protection (MAM) . Configure other settings based on your requirements, then assign the app protection policy to your users.
The Intune MAM app protection policy configures screen capture protection, and the supported client app enforces it. For web connections, Microsoft Edge for Business enforces protection in the work profile that receives the policy. Conditional Access doesn't block screen capture itself. It requires an app protection policy before granting access to the targeted remote resources, preventing access through an unprotected app or browser. For web connections, users might be prompted to sign in to the required Edge work profile and complete MAM registration. Signing in alone isn't sufficient; the app protection policy must be applied.
Under Conditions , set the device platform and client app for each platform you want to protect: Create the web policy separately from any Android and iOS/iPadOS policy. Native clients on Windows, such as Windows App, don't support app protection policies. A policy that includes both the Windows device platform and Mobile apps and desktop clients blocks their connections.
For more information about these resources, including how a policy that targets Windows 365 can also affect admin portal sign-ins, see Set Conditional Access policies for Windows 365 and Enforce Microsoft Entra multifactor authentication for Azure Virtual Desktop using Conditional Access . Connect to a new remote session with a supported client. Don't reconnect to an existing session. You need to sign out of any existing sessions and sign back in for the change to take effect.
From a local device, take a screenshot or share your screen in a Teams call or meeting. The content is blocked or hidden. On Windows and macOS devices, if you enabled Block screen capture on client and server on your virtual machines or Cloud PCs, try to capture the screen using a tool or service within the virtual machine or Cloud PC. The content is blocked or hidden. If you enable screen capture protection on virtual machines or Cloud PCs, you must connect from a supported device. If you don't, you see an error message indicating that screen capture protection is enabled. The error message looks similar to these screenshots: For Windows App in a web browser, verify both that the Edge work profile receives the required app protection policy and that Conditional Access requires app protection before granting access.
Check the signed-in identity. Confirm that the user is signed in to the Edge work profile with your organization's work account and accesses Windows App from that profile using the same account. Signing in to the website alone isn't sufficient. Complete any required work-profile sign-in and MAM registration prompts. If the user has work profiles for more than one organization, confirm they're using the one for your organization. Each profile receives only its own organization's app protection policy.
Check app protection policy targeting and settings. Confirm that the Windows app protection policy targets Microsoft Edge , includes the user's work account through its assigned group, and doesn't exclude that user. Under Data protection , confirm that Allow cut, copy, and paste for is set to Org data destinations and org data sources . If your organization also applies a Microsoft Defender for Cloud Apps DLP policy, in Microsoft Edge version 149 and later that policy is enforced instead of the app protection policy.
Check policy delivery. In the Microsoft Intune admin center, go to Apps > Monitor > App protection status . Review the policy name, app version, and last sync for the user's app instance. Check that the expected policy is reported and that the app has checked in since the configuration changed. Assignment alone doesn't confirm that the tested app instance has received the latest configuration. For more information, see Monitor app protection policies .
Check Conditional Access. Confirm that the policy includes the intended user and remote resources, applies to Windows and Browser , and uses Require app protection policy . A policy in Report-only mode doesn't enforce this requirement. Review the user's Microsoft Entra sign-in event to identify which policies applied and any failure details. See Troubleshoot Conditional Access sign-in problems .
Test a new remote session. After the required policy is applied, save any work and sign out of the existing remote session. Start a new session from the protected Edge work profile and attempt a local screenshot. The protected remote content should be blocked or hidden. Using a test account, also verify that access without the required app protection isn't granted until the access requirements are met.
If the result is unexpected, record the affected work account, Edge version, policy names, reproduction time, and any sign-in error or correlation ID for further troubleshooting. Check policy targeting and delivery before concluding that the browser scenario is unsupported. When admin-configured SCP is enabled, Android or iOS/iPadOS connections are only allowed if the MAM app protection policy also blocks screen capture (hybrid enforcement).
Confirm the Intune MAM app protection policy is applied to the user and device. In the Microsoft Intune admin center, check the app protection policy status for the user under Apps > Monitor > App protection status . On the Android or iOS/iPadOS device, sign out of Windows App and sign back in to pick up the latest policy settings. Connect to the remote session. If both the admin-configured SCP and the MAM policy block screen capture, the connection succeeds and screen capture is blocked.
4. Practical Deployment, Analysis & Case Studies If a user is blocked because the MAM policy isn't applied or doesn't block screen capture, recommend the following message to help them understand the issue: "Your organization requires screen capture protection to be enforced on your device to connect to this remote session. Make sure you're using Windows App with an app protection policy that blocks screen capture. Contact your IT admin for assistance." Learn how to help secure your Azure Virtual Desktop deployment with Security recommendations for Azure Virtual Desktop .
Access to this page requires authorization. You can try signing in or changing directories . Screen capture protection, alongside watermarking , helps prevent sensitive data from being captured on client devices using specific operating system (OS) features and APIs. When you enable screen capture protection, remote content is automatically blocked in screenshots and screen sharing. This feature can be applied to Azure Virtual Desktop virtual machines and Windows 365 Cloud PCs.
When screen capture protection (SCP) is enabled to block screen capture on the client, users can continue to share their remote desktop or individual applications using supported collaboration experiences such as Microsoft Teams. Compatibility between SCP and Teams screen sharing depends on the use of supported client configurations. When unsupported configurations are used, protected content might appear as a black screen during sharing. For current compatibility requirements and configuration guidance with Teams, see Azure Virtual Desktop screen capture protection and Microsoft Teams compatibility .
Screen capture protection doesn't provide Digital Rights Management (DRM)-level protection. It prevents screen capture through standard OS features and APIs and isn't a substitute for DRM solutions. For comprehensive data protection, use screen capture protection as part of a broader defense-in-depth security strategy that includes other controls, such as Conditional Access policies, data loss prevention, and endpoint management.
To increase the security of your sensitive information, you should also disable clipboard, drive, and printer redirection. Disabling redirection helps prevent users from copying content from the remote session. To learn about supported redirection values, see Device redirection . To discourage other methods of screen capture, such as taking a photo of a screen with a physical camera, you can enable watermarking , where admins can use a QR code to trace the session.
The steps to configure screen capture protection depend on where you configure it, which platforms your users are connecting from, and what scenario you want to achieve. Native clients on Windows and macOS : when users connect with the natively installed Windows App or Remote Desktop client, configure screen capture protection on the virtual machines (Azure Virtual Desktop) or Cloud PCs (Windows 365) using an Intune device configuration policy or Group Policy. The native client enforces these settings without an Intune MAM app protection policy. For browser connections, including Microsoft Edge on Windows, follow Pattern 3: Web endpoints (browser access) .
When you configure screen capture protection on virtual machines or Cloud PCs, there are two further settings you can configure to help meet your requirements: Block screen capture on client : prevents screen capture from the local device of applications running in the remote session. Block screen capture on client and server : prevents screen capture from the local device of applications running in the remote session, but also prevents tools and services within the virtual machine or Cloud PC capturing the screen.
1. Hybrid enforcement (iOS/iPadOS/Android/Web) : When screen capture protection is enabled on the virtual machine or Cloud PC, connections from Windows App on iOS/iPadOS and Android are allowed when an Intune MAM app protection policy that blocks screen capture applies to the app. On the web, connections from Microsoft Edge for Business are allowed when the Edge work profile receives an Intune MAM app protection policy that enforces screen capture protection through the Edge data loss prevention (DLP) features. Hybrid enforcement isn't applicable on platforms that don't support Intune MAM.
Android, iOS/iPadOS, and web connections : configure an Intune MAM app protection policy for the supported client app and assign it to the users who need protection. For Android and iOS/iPadOS, the policy applies to Windows App. For web connections on Windows, the policy applies to Microsoft Edge for Business through the user's work profile. This client-side protection prevents local screen capture of protected content; it doesn't prevent tools and services within the virtual machine or Cloud PC from capturing the screen. For configuration steps, see Enable screen capture protection with Intune MAM .
1. On the web, screen capture protection is enforced by the Edge for Business data loss prevention (DLP) features when users connect with Microsoft Edge for Business and receive an Intune MAM app protection policy. For configuration steps, see Enable screen capture protection with Intune MAM . For Android and iOS/iPadOS devices, and for the web client (on Windows), screen capture protection is enforced through Intune mobile application management (MAM). In each case, you configure two things: an Intune MAM app protection policy that applies screen capture protection, and a Conditional Access policy that requires the app protection policy so users can only connect when the policy is applied to the client. The exact app protection policy setting differs by platform âII on Android and iOS/iPadOS you block screen capture directly, while on the web you configure Microsoft Edge for Business, where screen capture protection is enforced through the Edge data loss prevention (DLP) features. When screen capture protection is configured on your virtual machines or Cloud PCs, this is the supported model for these platforms. For configuration steps, see Enable screen capture protection with Intune MAM .
Screen capture protection is fully supported on Windows, but it has known limitations on macOS due to the platform's current security architecture: Microsoft Teams compatibility : on macOS, enabling screen capture protection might interfere with screen sharing in Microsoft Teams, potentially causing shared windows to appear blank or not display properly. If Teams-based collaboration is required, screen capture protection might need to be temporarily disabled on the device.
Platform-level enforcement : due to macOS restrictions, some native applications might not fully respect screen capture protection enforcement. This is a limitation of the operating system's available APIs, not a defect in screen capture protection itself. For collaboration-heavy macOS workflows, consider configuring screen capture protection settings based on business need and risk level.
For highly sensitive content, Windows endpoints are recommended for full enforcement of screen protection features. Watermarking and administrative policies can be used to further discourage misuse on platforms with limited enforcement. The following patterns describe common deployment scenarios for screen capture protection: Use this pattern when users connect with the natively installed Windows App or Remote Desktop client on Windows or macOS.
An Intune MAM app protection policy isn't required for these native clients. Browser connections use a different configuration, even when the browser runs on a Windows device. For browser connections, follow Pattern 3: Web endpoints (browser access) . If your users connect from both desktop and mobile devices, use hybrid enforcement. Configure screen capture protection on both the virtual machine or Cloud PC and the Intune MAM app protection policy.
For Windows App in a web browser, use Microsoft Edge for Business on Windows with an Intune MAM app protection policy that targets Microsoft Edge. Also configure a Conditional Access policy that requires app protection before allowing access to your remote resources. The user must sign in to an Edge work profile with your organization's work account and use that same account to access Windows App from that profile. Signing in to the Windows App website alone isn't sufficient: the Edge work profile must receive your organization's app protection policy.
Assign the app protection policy to the users who require protection. For example, if a contractor accesses your organization's remote resources using a work account that your organization provides, include that account in the policy assignment. Assigning the policy to a different account doesn't protect the profile used for that connection. A user might have work accounts from more than one organization, such as a contractor who works for several clients. On a device that none of these organizations manages, the user signs in to a separate Edge work profile for each work account.
Each profile receives only its own organization's app protection policy. To connect to your remote resources with screen capture protection, the user must open Windows App from the profile that's signed in with your organization's work account. Users don't need to enroll their devices in your organization's device management. Web screen capture protection is supported on personal devices and, with Microsoft Edge for Business version 147 or later, on devices managed by a different organization, such as a contractor's employer. The following limitations apply: Before you can configure screen capture protection, ensure you meet the following prerequisites: 5. Performance Evaluation & Extended Technical Observations For scenarios where you need to configure virtual machines or Cloud PCs, those virtual machines or Cloud PCs must be running Windows 11, version 22H2 or later, or Windows 10, version 22H2 or later.
Users connecting with a natively installed client must use a supported version of Windows App or the Remote Desktop client. The following tables show supported native-client scenarios: 1. Doesn't include support for ChromeOS because Intune MAM isn't supported on ChromeOS. For additional Intune and Conditional Access prerequisites, see Require local client device security compliance with Microsoft Intune and Microsoft Entra Conditional Access .
To configure an Intune device configuration policy on virtual machines or Cloud PCs, you need: A Microsoft Entra ID account that's assigned the Policy and Profile manager built-in RBAC role. A security group or organizational unit (OU) containing the devices you want to configure. Enable screen capture protection on virtual machines and Cloud PCs using an Intune device configuration policy or Group Policy To configure screen capture protection on virtual machines (Azure Virtual Desktop) or Cloud PCs (Windows 365) using Microsoft Intune: Create or edit a configuration profile for Windows 10 and later devices, with the Settings catalog profile type.
In the settings picker, browse to Administrative templates > Windows Components > Remote Desktop Services > Remote Desktop Session Host > Azure Virtual Desktop . Expand the Administrative templates category, then toggle the switch for Enable screen capture protection to Enabled . Toggle the switch for Screen Capture Protection Options (Device) to off for Block screen capture on client , or on for Block screen capture on client and server based on your requirements, then select OK .
Optional : On the Scope tags tab, select a scope tag to filter the profile. For more information about scope tags, see Use role-based access control (RBAC) and scope tags for distributed IT . On the Assignments tab, select the group containing the computers providing a remote session you want to configure, then select Next .
Once the policy applies to the computers providing a remote session, restart them for the settings to take effect. To configure screen capture protection on virtual machines (Azure Virtual Desktop) or Cloud PCs (Windows 365) using Group Policy in an Active Directory domain: Follow the steps to make the Administrative template for Azure Virtual Desktop available in Group Policy.
Open the Group Policy Management console on a device you use to manage the Active Directory domain. Create or edit a policy that targets the computers providing a remote session you want to configure. Navigate to Computer Configuration > Policies > Administrative Templates > Windows Components > Remote Desktop Services > Remote Desktop Session Host > Azure Virtual Desktop .
Double-click the policy setting Enable screen capture protection to open it, then select Enabled . From the drop-down menu, select the screen capture protection scenario you want to use from Block screen capture on client or Block screen capture on client and server based on your requirements, then select OK . Ensure the policy is applied to the computers providing a remote session, then restart them for the settings to take effect.
For Android, iOS/iPadOS, and the web client (on Windows), you enforce screen capture protection through Intune mobile application management (MAM). For each of these approaches, the configuration has two parts: Configure an Intune MAM app protection policy for the platform your users connect from. Follow the steps in Create an app protection policy , and use the app selection and screen capture protection settings below for your platform: Web (Microsoft Edge for Business on Windows) : create or edit an Intune app protection policy with the following settings: For web connections, Microsoft Edge is the app that receives the app protection policy, not the natively installed Windows App. The user must access Windows App from the Edge work profile that receives this policy.
The clipboard setting above restricts copy and paste and automatically activates screen capture protection across the entire protected Edge work profile, including all tabs in that profile. Protection isn't limited to the Windows App tab. For more information, see Data protection features for Microsoft Edge using Intune App Protection (MAM) . Configure other settings based on your requirements, then assign the app protection policy to your users.
The Intune MAM app protection policy configures screen capture protection, and the supported client app enforces it. For web connections, Microsoft Edge for Business enforces protection in the work profile that receives the policy. Conditional Access doesn't block screen capture itself. It requires an app protection policy before granting access to the targeted remote resources, preventing access through an unprotected app or browser. For web connections, users might be prompted to sign in to the required Edge work profile and complete MAM registration. Signing in alone isn't sufficient; the app protection policy must be applied.
Under Conditions , set the device platform and client app for each platform you want to protect: Create the web policy separately from any Android and iOS/iPadOS policy. Native clients on Windows, such as Windows App, don't support app protection policies. A policy that includes both the Windows device platform and Mobile apps and desktop clients blocks their connections.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Keystroke%20logging • https://en.wikipedia.org/wiki/List%20of%20computing%20and%20IT%20abbreviations • https://en.wikipedia.org/wiki/Safari%20%28web%20browser%29 • https://learn.microsoft.com/en-us/azure/virtual-desktop/screen-capture-protection • https://docs.azure.cn/en-us/virtual-desktop/screen-capture-protection
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Screen Capture Prevention In Secure Desktop Applications.
[*] Metasploit Scan Running on Target Subnet for Screen Capture Prevention In Secure Desktop Applications... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |