Complete Technical Paper Content — Secure Biometric Template Protection Using Cancelable Biometrics
Overview & System Context
Secure Biometric Template Protection Using Cancelable Biometrics: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~8779 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Biometrics are body measurements and calculations related to human characteristics and features. Biometric authentication (or realistic authentication) is used in computer science as a form of identification and access control. It is also used to identify individuals in groups that are under surveillance. Biometric identifiers are the distinctive, measurable characteristics used to label and describe individuals. Biometric identifiers are often categorized as physiological characteristics which are related to the shape of the body. Examples include, but are not limited to fingerprint, palm veins, face recognition, DNA, palm print, hand geometry, iris recognition, retina, odor/scent, voice and shape of ears. Behavioral characteristics are related to the pattern of behavior of a person, including but not limited to mouse movement, typing rhythm, gait, signature, voice, and behavioral profiling. Some researchers have coined the term "Behaviometrics" (behavioral biometrics) to describe the latter class of biometrics. More traditional means of access control include token-based identification systems, such as a driver's license or passport, and knowledge-based identification systems, such as a password or personal identification number. Since biometric identifiers are unique to individuals, they are more reliable in verifying identity than token and knowledge-based methods; however, the collection of biometric identifiers raises privacy concerns.
Universality: Every person using a system should possess the trait. Uniqueness: The trait should be sufficiently different for individuals in the relevant population such that they can be distinguished from one another. Permanence: The manner in which a trait varies over time. More specifically, a trait with good permanence will be reasonably invariant over time with respect to the specific matching algorithm. Measurability (collectability): The ease of acquisition or measurement of the trait. In addition, acquired data should be in a form that permits subsequent processing and extraction of the relevant feature sets.
Performance: The accuracy, speed, and robustness of technology used (see performance section for more details). Acceptability: How well individuals in the relevant population accept the technology such that they are willing to have their biometric trait captured and assessed. Circumvention: The ease with which a trait might be imitated using an artifact or substitute. Proper biometric use is application dependent. Certain biometrics will be more suitable than others based on the required levels of convenience and security. No single biometric will meet all the requirements of every possible application.
The block diagram illustrates the two basic modes of a biometric system. First, in verification (or authentication) mode the system performs a one-to-one comparison of a captured biometric with a specific template stored in a biometric database in order to verify the individual is the person they claim to be. Three steps are involved in the verification of a person. In the first step, reference models for all the users are generated and stored in the model database. In the second step, some samples are matched with reference models to generate the genuine and impostor scores and calculate the threshold. The third step is the testing step. This process may use a smart card, username, or ID number (e.g. PIN) to indicate which template should be used for comparison. Positive recognition is a common use of the verification mode, "where the aim is to prevent multiple people from using the same identity".
Second, in identification mode the system performs a one-to-many comparison against a biometric database in an attempt to establish the identity of an unknown individual. The system will succeed in identifying the individual if the comparison of the biometric sample to a template in the database falls within a previously set threshold. Identification mode can be used either for positive recognition (so that the user does not have to provide any information about the template to be used) or for negative recognition of the person "where the system establishes whether the person is who she (implicitly or explicitly) denies to be". The latter function can only be achieved through biometrics since other methods of personal recognition, such as passwords, PINs, or keys, are ineffective. The first time an individual uses a biometric system is called enrollment. During enrollment, biometric information from an individual is captured and stored. In subsequent uses, biometric information is detected and compared with the information stored at the time of enrollment. Note that it is crucial that storage and retrieval of such systems themselves be secure if the biometric system is to be robust. The first block (sensor) is the interface between the real world and the system; it has to acquire all the necessary data. Most of the time it is an image acquisition system, but it can change according to the characteristics desired. The second block performs all the necessary pre-processing: it has to remove artifacts from the sensor, to enhance the input (e.g. removing background noise), to use some kind of normalization, etc. In the third block, necessary features are extracted. This step is an important step as the correct features need to be extracted in an optimal way. A vector of numbers or an image with particular properties is used to create a template. A template is a synthesis of the relevant characteristics extracted from the source. Elements of the biometric measurement that are not used in the comparison algorithm are discarded in the template to reduce the file size and to protect the identity of the enrollee. However, depending on the scope of the biometric system, original biometric image sources may be retained, such as the PIV-cards used in the Federal Information Processing Standard Personal Identity Verification (PIV) of Federal Employees and Contractors (FIPS 201). During the enrollment phase, the template is simply stored somewhere (on a card or within a database or both). During the matching phase, the obtained template is passed to a matcher that compares it with other existing templates, estimating the distance between them using any algorithm (e.g. Hamming distance). The matching program will analyze the template with the input. This will then be output for a specified use or purpose (e.g. entrance in a restricted area), though it is a fear that the use of biometric data may face mission creep. Selection of biometrics in any practical application depending upon the characteristic measurements and user requirements. In selecting a particular biometric, factors to consider include, performance, social acceptability, ease of circumvention and/or spoofing, robustness, population coverage, size of equipment needed and identity theft deterrence. The selection of a biometric is based on user requirements and considers sensor and device availability, computational time and reliability, cost, sensor size, and power consumption.
Figure 1: Biometric Template Security at Seth Darcy-irvine blog False match rate (FMR, also called FAR = False Accept Rate): the probability that the system incorrectly matches the input pattern to a non-matching template in the database. It measures the percent of invalid inputs that are incorrectly accepted. In case of similarity scale, if the person is an imposter in reality, but the matching score is higher than the threshold, then he is treated as genuine. This increases the FMR, which thus also depends upon the threshold value. False non-match rate (FNMR, also called FRR = False Reject Rate): the probability that the system fails to detect a match between the input pattern and a matching template in the database. It measures the percent of valid inputs that are incorrectly rejected. Receiver operating characteristic or relative operating characteristic (ROC): The ROC plot is a visual characterization of the trade-off between the FMR and the FNMR. In general, the matching algorithm performs a decision based on a threshold that determines how close to a template the input needs to be for it to be considered a match. If the threshold is reduced, there will be fewer false non-matches but more false accepts. Conversely, a higher threshold will reduce the FMR but increase the FNMR. A common variation is the Detection error trade-off (DET), which is obtained using normal deviation scales on both axes. This more linear graph illuminates the differences for higher performances (rarer errors). Equal error rate or crossover error rate (EER or CER): the rate at which both acceptance and rejection errors are equal. The value of the EER can be easily obtained from the ROC curve. The EER is a quick way to compare the accuracy of devices with different ROC curves. In general, the device with the lowest EER is the most accurate. Failure to enroll rate (FTE or FER): the rate at which attempts to create a template from an input is unsuccessful. This is most commonly caused by low-quality inputs. Failure to capture rate (FTC): Within automatic systems, the probability that the system fails to detect a biometric input when presented correctly.
Template capacity: the maximum number of sets of data that can be stored in the system. An early cataloguing of fingerprints dates back to 1885 when Juan Vucetich started a collection of fingerprints of criminals in Argentina. Josh Ellenbogen and Nitzan Lebovic argued that Biometrics originated in the identification systems of criminal activity developed by Alphonse Bertillon (1853–1914) and by Francis Galton's theory of fingerprints and physiognomy.
Historian Keith Breckenridge note that Galton's travels in South Africa reinforced his early racial prejudices and inspired his later commitment to classifying human difference scientifically. According to Lebovic, Galton's work "led to the application of mathematical models to fingerprints, phrenology, and facial characteristics", as part of "absolute identification" and "a key to both inclusion and exclusion" of populations. Accordingly, "the biometric system is the absolute political weapon of our era" and a form of "soft control". The theoretician David Lyon showed that during the past two decades biometric systems have penetrated the civilian market, and blurred the lines between governmental forms of control and private corporate control.
Kelly A. Gates identified 9/11 as the turning point for the cultural language of our present: "in the language of cultural studies, the aftermath of 9/11 was a moment of articulation, where objects or events that have no necessary connection come together and a new discourse formation is established: automated facial recognition as a homeland security technology." It is possible that data obtained during biometric enrollment may be used in ways for which the enrolled individual has not consented. For example, most biometric features could disclose physiological and/or pathological medical conditions (e.g., some fingerprint patterns are related to chromosomal diseases, iris patterns could reveal sex, hand vein patterns could reveal vascular diseases, most behavioral biometrics could reveal neurological diseases, etc.). Moreover, second generation biometrics, notably behavioral and electro-physiologic biometrics (e.g., based on electrocardiography, electroencephalography, electromyography), could be also used for emotion detection. There are three categories of privacy concerns: Unintended functional scope: The authentication goes further than authentication, such as finding a tumor. Unintended application scope: The authentication process correctly identifies the subject when the subject did not wish to be identified.
Covert identification: The subject is identified without seeking identification or authentication, i.e. a subject's face is identified in a crowd. In terms of recognition or identification performance for a given trait, a biometric system should not exhibit accuracy differences across demographic groups. Disparities in accuracy can lead to uneven error rates for populations defined by gender, race, age, or other attributes. Therefore, biometric systems should be designed and evaluated to ensure demographic fairness, providing equitable performance for all users.
Figure 2: PPT - Biometrics II PowerPoint Presentation, free download - ID:623002 To ensure we can shut down terrorist networks before they ever get to the United States, we must also take the lead in driving international biometric standards. By developing compatible systems, we will be able to securely share terrorist information internationally to bolster our defenses. Just as we are improving the way we collaborate within the U.S. Government to identify and weed out terrorists and other dangerous people, we have the same obligation to work with our partners abroad to prevent terrorists from making any move undetected. Biometrics provide a new way to bring terrorists' true identities to light, stripping them of their greatest advantage—remaining unknown. According to an article written in 2009 by S. Magnuson in the National Defense Magazine entitled "Defense Department Under Pressure to Share Biometric Data" the United States has bilateral agreements with other nations aimed at sharing biometric data. To quote that article: Miller [a consultant to the Office of Homeland Defense and America's security affairs] said the United States has bilateral agreements to share biometric data with about 25 countries. Every time a foreign leader has visited Washington during the last few years, the State Department has made sure they sign such an agreement.
GDPR in the European Union became law in 2018 LGPD in Brazil became law in 2020 Protection of Personal Information Act in South Africa came into force in 2020 Personal Data Protection Act in Sri Lanka implementation started in 2023 Countries using biometrics include Australia, Brazil, Bulgaria, Canada, Cyprus, Greece, China, Gambia, Germany, India, Iraq, Ireland, Israel, Italy, Malaysia, Netherlands, New Zealand, Nigeria, Norway, Pakistan, Poland, South Africa, Saudi Arabia, Tanzania, Turkey, Ukraine, United Arab Emirates, United Kingdom, United States and Venezuela. Among low to middle income countries, roughly 1.2 billion people have already received identification through a biometric identification program.
There are also numerous countries applying biometrics for voter registration and similar electoral purposes. According to the International IDEA's ICTs in Elections Database, some of the countries using (2017) Biometric Voter Registration (BVR) are Armenia, Angola, Bangladesh, Bhutan, Bolivia, Brazil, Burkina Faso, Cambodia, Cameroon, Chad, Colombia, Comoros, Congo (Democratic Republic of), Costa Rica, Ivory Coast, Dominican Republic, Fiji, Gambia, Ghana, Guatemala, India, Iraq, Kenya, Lesotho, Liberia, Malawi, Mali, Mauritania, Mexico, Morocco, Mozambique, Namibia, Nepal, Nicaragua, Nigeria, Panama, Peru, Philippines, Senegal, Sierra Leone, Solomon Islands, Somaliland, Swaziland, Tanzania, Uganda, Uruguay, Venezuela, Yemen, Zambia, and Zimbabwe.
Figure 3: Biometric Cyber Security Image Advanced Data Protection Using ... Private biometrics is a form of encrypted biometrics, also called privacy-preserving biometric authentication methods, in which the biometric measurement is cryptographically processed such that no data stored in a data base can be (mis-) used to recover information about the human subject. Biometrics, in contrast to user pass words, are noisy data that slightly differ from measurement to measurement. Small variations input data prevent the use of traditional encryption or hashing. The introduction of a fuzzy extractor was a pioneering contribution to nonetheless apply cryptographic techniques to inherently noisy biometric data.
The Private.id feature vector can be used in one of two ways. If the feature vector is stored locally, it may be used to compute 1:1 verification with high accuracy (99% or greater) using linear mathematics. If the feature vector is also stored in a Cloud, the feature vector may also be used as input for a neural network to perform 1:many identification with the same accuracy, speed and privacy as the original plaintext reference biometric (template).
Non-bypassable, as plaintext biometrics cannot use another communication path, including lower level mechanisms, to bypass the security monitor since the original biometric is transient at inception (e.g. the biometric template acquired by the client device exists only for a few seconds at inception and then is deleted or never stored). Evaluable in that the feature vectors are modular, well designed, well specified, well implemented, small and of low complexity. Always-invoked, in that each and every message is always one-way encrypted independent of security monitors. Tamperproof in that the feature vector's one-way encryption prevents unauthorized changes and does not use systems that control rights to the security monitor code, configuration and data.
BioHashing Research into cancelable biometrics moved into BioHashing by 2004. The BioHashing feature transformation technique was first published by Jin, Ling and Goh and combined biometric features and a tokenized (pseudo-) random number (TRN). Specifically, BioHash combined the biometric template with a user-specific TRN to produce a set of non-invertible binary bit strings that were thought to be irreproducible if both the biometric and the TRN were not presented simultaneously. Indeed, it was first claimed that the BioHashing technique had achieved perfect accuracy (equal error rates) for faces, fingerprints and palm prints, and the method gained further traction when its extremely low error rates were combined with the claim that its biometric data was secure against loss because factoring the inner products of biometrics feature and TRN was an intractable problem. By 2005, however, researchers Cheung and Kong (Hong Kong Polytechnic and University of Waterloo) asserted in two journal articles that BioHashing performance was actually based on the sole use of TRN and conjectured that the introduction of any form of biometric become meaningless since the system could be used only with the tokens. These researchers also reported that the non-invertibility of the random hash would deteriorate the biometric recognition accuracy when the genuine token was stolen and used by an impostor (“the stolen-token scenario”).
The Lebanese passport (Arabic: IIII III IIIIIIIII IIIIIIIII, romanized: JawIz Safar Al-JumhIrIyah Al-LubnInIyah) is a passport issued to the citizens of the Republic of Lebanon to enable them to travel outside the Republic of Lebanon and entitles the bearer to the protection from the diplomatic missions and consulates of the Republic of Lebanon if necessary. It is issued exclusively by the Lebanese Directorate General of General Security (DGGS), and can also be issued at various Lebanese diplomatic missions and/or consulates outside of the Republic of Lebanon. It allows the bearer a freedom of living in the Republic of Lebanon without any immigration requirements, participate in the Lebanese political system, entry to and exit from the Republic of Lebanon through any port, travel to and from other countries in accordance with visa requirements, facilitates the process of securing consular assistance abroad from the diplomatic missions and consulates of the Republic of Lebanon if necessary, and requests protection for the bearer while abroad. Lebanese passport booklets are valid for travel by Lebanese citizens anywhere in the world to countries with which the government of the Republic of Lebanon maintains diplomatic ties although travel to certain countries and/or for certain purposes may require a visa and the Republic of Lebanon itself restricts its citizens from traveling to or engaging in commercial transactions in certain countries against the internal and external safety of the republic. They conform with recommended standards (i.e., size, composition, layout, technology) of the International Civil Aviation Organization (ICAO). By law, a valid unexpired Lebanese passport or identity card (Arabic: IIIII IIIIII, romanized: Bitakat Al Hawiya) is conclusive (and not just prima facie) proof of Lebanese citizenship, and has the same force and effect as proof of Lebanese citizenship as certificates of naturalization or of citizenship, if issued to a Lebanese citizen for the full period allowed by law. The Lebanese law does not prohibit Lebanese citizens from holding passports of other countries, though they are required to use their Lebanese passport to enter and leave the country. The Republic of Lebanon law permits dual nationality. An expired Lebanese passport can still be used to return to the Republic of Lebanon at any port and port personnel are obliged by law to allow the passage of the bearer without any delay or hindrance. Lebanese passports are property of the Republic of Lebanon and must be returned to the Lebanese Government upon demand. The French state-run printing firm, Imprimerie Nationale carries on the official printing works of both the Lebanese and French governments. As of January 10, 2016, The Lebanese Directorate General of General Security (DGGS) has stopped renewing passports with handwritten notes and started issuing new ones instead. This move is intended for the introduction of the new Lebanese Biometric Passport on August 1, 2016. As of August 1, 2016 all passports being issued by the Lebanese Directorate General of General Security (DGGS) are Biometric and hold the biometric passport symbol . Non-biometric passports are valid until their expiry dates.
On 12 April 2003, the Republic of Lebanon started issuing ICAO compliant machine-readable non-biometric passports with the navy blue cover, valid for one or five years, replacing the old burgundy red passport. It is the 45th nation in the world to adopt the ICAO standard. The implementation of the new passport began at offices across Beirut and Tripoli before expanding nationwide between April and June 2003 and to Lebanese embassies/consulates abroad between September and October 2003. The Lebanese Directorate General of General Security (DGGS) stopped issuing the old navy blue non-biometric Lebanese passports and started issuing biometric passports to Lebanese citizens starting from 1 August 2016.
The old non-biometric navy blue passports are valid until their expiry dates when will be renewed with the new navy blue biometric passports. In 2012, a new contract was signed between the Lebanese Directorate General of General Security (DGGS) with a Lebanese company Inkript, a member of Resource Group Holding (RGH), to make the move for biometric passports. Inkript held a joint venture with French firm Gemalto, based in the Netherlands to participate in the tender. Jacques Seif, General Manager of Inkript, said: “We will handle all the programming and software development in-house, while Gemalto will be in charge of manufacturing the passports and matching the program’s interface with the coding machines.”. The contract's term is three years, and Inkript will produce four million Lebanese biometric passports. The contract, valued at around 140 million US dollars, was funded by a Saudi grant. The Lebanese Directorate General of General Security (DGGS) announced that it would be issuing biometric passports to all of its citizens starting from July 2016. As of August 1, 2016, all new Lebanese passports issued will be biometric passports and machine-readable and will have a contactless smartcard RFID chip embedded inside the polycarbonate data page (3rd EU generation) or a cheap booklet in which the chip is imbedded at the bottom of the front cover under the word "PASSEPORT". Facial recognition technology is being introduced to coincide with the release of the Biometric Passport. This technology will be used to improve identity verification, reduce identity-related fraud, and protect the legal identity of the citizens of the Republic of Lebanon. Similar technology is used in the Lebanese identity card. The biometric data that is to be included on the Lebanese passport is the bearer's name, gender, date and place of birth, and a digital image of their face, ten fingerprints, palmprints. Lebanese immigration checkpoints will not be the only ones with the technology to read and authenticate the data from the RFID chip using a fingerprint scanner and facial recognition technology, but widespread adoption of Biometric passport technology around the world has seen the technology installed in international airports in the US, the UK and other countries. In addition to biometric data and the personal information stored on the information page, the chip also records the bearer's travel history of the last ten entry and exits at Lebanese border control points (Beirut–Rafic Hariri International Airport, Beirut Naval Base, Port of Beirut, Port of Byblos, and Port of Tripoli). All biometric passport will be issued with 48 pages as opposed to the previous choice of 24 or 48 pages. On 14 August 2014, the Lebanese Directorate General of General Security (DGGS) released requirements for the new biometric residence permits (Arabic: IIIIII IIIIIII IIIIIIIIII IIIIII (transl. Bitakat Iqama Bayometriya Thakiya; French: Cartes de résidence à puce biométrique) issued to the expatriates residing temporarily or permanently in the Republic of Lebanon. On 15 January 2015, all of the Lebanese government offices started issuing and dealing with the new Biometric residence and work permits in dealing with the official paperworks of expatriates. The Lebanese Directorate General of General Security (DGGS) started issuing biometric passports to Lebanese citizens starting from 1 August 2016.
Must be taken within the last six months before application 4.3 cm × 3.5 cm (1.7 in × 1.4 in) The height of the head (top of hair to bottom of chin) should measure 1 to 1+3⁄8 inches (25 to 35 mm) Eye height is between 1+1⁄8 to 1+3⁄8 inches (29 to 35 mm) from the bottom of the photo Front view, full face, open eyes, closed mouth, and neutral expression Full head from top of hair to shoulders Plain white or off-white background No shadows on face or in background No reflections of flashlight No sunglasses (unless for medical purposes), but those normally wearing corrective glasses must wear such glasses No hat (unless for religious purposes) No headwear of any kind, unless wearing for religious purposes (such as hijabs) Normal contrast and lighting Other parts of the body, such as hands or feet, must not be in the picture Alteration of any kind from the original picture is prohibited Printed on professional-grade photographic paper For extra security, the photos must contain the stamped or handwritten address of the studio and the exact date they were taken. In addition, a declaration and signatures made by a guarantor and mukhtar are required, as they must certify the photos are true likeliness of the applicant.
2. System Architecture & Core Working Principles NB: To receive the passport immediately, the interested party can apply at the department of public relations. An additional fee of LBP 4,900,000 will be however requested. In Arabic: "IIIIIIIIII IIIIIIIIII IIII IIII IIIIIIIIII IIIIIIIIII III IIII III IIIII IIIII IIII II IIIIIII IIIIIIII IIIII IIII IIII III IIIIII I IIII IIIIIIII I IIIIIII IIIIIIIII III IIIIII" In French: "République Libanaise Au nom du Président de la République Libanaise Le Directeur Général de la Sûreté Générale prie les autorités compétentes de bien vouloir accorder libre passage au titulaire de ce passeport et en cas de besoin, de lui accorder toute aide et protection légitimes." In English: "Republic of Lebanon On behalf of The President of the Republic of Lebanon The General Director of the General Security hereby requests competent authorities to permit the bearer to pass without any delay or hindrance and in case of need to provide all lawful aid and protection." The items are identified by text in Arabic and English (e.g., "IIIII IIIIIII / Date of birth").
A Lebanese passport does not, in itself, entitle the holder to enter another country. To enter another country, the traveler must comply with the visa and entry requirements of the other countries to be visited, which vary from country to country and may apply specifically to a particular passport type, the traveller's nationality, criminal history, health issues, evidence of sufficient funds, evidence of ticket for exit or many other factors. Visa requirements for Lebanese citizens are administrative entry restrictions by the authorities of other states placed on citizens of the Republic of Lebanon. As of October 2018, Lebanese citizens have visa-free or visa-on-arrival access to the listed 44 countries and territories, including disputed areas, and partially recognized countries: Note that the Lebanese Identity Card can be used as an optional replacement for the Lebanese passport in the listed countries and territories: Constitution of Lebanon Driving licence in Lebanon Foreign relations of Lebanon History of Lebanon Lebanese diaspora Lebanese identity card Lebanese nationality law Politics of Lebanon Vehicle registration plates of Lebanon Visa policy of Lebanon Visa requirements for Lebanese citizens Thank you for visiting nature.com. You are using a browser version with limited support for CSS. To obtain the best experience, we recommend you use a more up to date browser (or turn off compatibility mode in Internet Explorer). In the meantime, to ensure continued support, we are displaying the site without styles and JavaScript.
Multimodal biometric systems improve recognition accuracy and reduce vulnerabilities common in unimodal systems. Biometric template security faces a significant challenge because compromised templates cannot be reused like passwords. The proposed system addresses the risk of secure and revocable protection of biometric templates while maintaining high authentication performance. It introduces a cancelable multimodal biometric system that incorporates both face and fingerprint traits. In the given system, discriminative features are extracted in both modalities, and feature-level fusion is carried out in order to form a binary representation. SHEP (Secure Hashing, Exponent Warping, and Random Projections) converts the raw features to a non-invertible and revocable representation, and it is presented as a cancelable template generation method that improves the security of the fused template. The face and fingerprint dataset used to test our approach include CASIA-FaceV5 and CASIA-FingerprintV5. The Equal Error Rate (EER) and Receiver Operating Characteristic (ROC) curves are used to evaluate the performance. The experimental findings indicate that a multimodal SHEP-based cancelable template with a 256-dimensional fused cancelable template, EER=0.000, ROC(AUC) = 1.000 and verification rate=100% demonstrates that SHEP is very effective in maintaining accuracy as well as security.
A secure and explainable multimodal biometric system using trust adaptive fusion for face and fingerprint Feature fusion and selection using handcrafted vs. deep learning methods for multimodal hand biometric recognition The Article Processing Charge (APC) for this publication was funded by SRM University-AP, Andhra Pradesh. Department of Computer Science and Engineering, School of Engineering and Applied Sciences, SRM University - AP, Amaravati, 522240, Andhra Pradesh, India Pavani Chitrapu, Mahesh Kumar Morampudi, Hemantha Kumar Kalluri, Pardhu Sankar Kalluri & Puneet Sai Sadanala This study did not involve direct experiments on human participants; therefore, ethical approval was not required. All datasets used are publicly available.
All human images shown in this manuscript are taken from publicly available datasets. The respective dataset providers obtained consent for publication. Springer Nature remains neutral with regard to jurisdictional claims in published maps and institutional affiliations. License, which permits any non-commercial use, sharing, distribution and reproduction in any medium or format, as long as indicate if you modified the licensed material. You do not have permission under this licence to share adapted material derived from this article or parts of it. The images or other third party material in this article are included in the article’s Creative Commons licence, unless indicated otherwise in a credit line to the material. If material is not included in the article’s Creative Commons licence and your intended use is not permitted by statutory regulation or exceeds the permitted use, you will need to obtain permission directly from the copyright holder.
To view a copy of this licence, visit http://creativecommons.org/licenses/by-nc-nd/4.0/ .
Chitrapu, P., Morampudi, M.K., Kalluri, H.K. et al. Secure cancelable multimodal biometrics using hashing - based random projection. Sci Rep (2026). https://doi.org/10.1038/s41598-026-65666-3 Sign up for the Nature Briefing: AI and Robotics newsletter — what matters in AI and robotics research, free to your inbox weekly.
Biometric templates are vulnerable to theft if stored without protection. Unlike passwords, a compromised iris cannot be reissued. Although existing cancelable biometric schemes address this problem, most still require an external key or token, introducing an additional attack surface. This paper proposes a cancelable contralateral iris template protection scheme that eliminates the need for a separate token or stored secret, satisfying the three requirements of ISO/IEC 24745: irreversibility, unlinkability, and confidentiality. The method fuses three enrollment samples per eye using Majority Vote Fusion to produce a stable template, and applies a salt-based bit permutation derived from the subject’s enrollment ID. Combining the left- and right-permuted templates via a bitwise XOR produces a single Protected Fused Template. Since left and right iris patterns are statistically independent, fusing contralateral irises improves the accuracy of the system. An attacker must possess both iris codes and both salts to recover any useful information, yielding a larger effective key space than single-iris schemes.
Experiments on three datasets, CASIA-IrisV4-Interval, CASIA-IrisV2 (two devices), and CASIA-Iris-Thousand, yield EERs of 0.36 0.36 %, 4.88 4.88 %, 10.80 10.80 %, and 3.35 3.35 %, respectively; the highest value reflects the more challenging cross-device scenario. These results demonstrate that our contralateral approach outperforms unprotected baselines while remaining competitive with state-of-the-art cancelable methods.
3. Software Implementation, Frameworks & Protocols Iris Recognition, Biometrics Template Protection, Cancelable Biometrics, Multi-Instance Fusion. Iris recognition is considered one of the most accurate biometric modalities and is widely deployed in high-security systems [ 4 ] . Iris patterns are highly distinctive and stable due to epigenetic randomness during fetal development, resulting in iris codes that exhibit high entropy and near-random bit distributions [ 3 , 5 ] . These characteristics provide stable discriminative capability for individual identification and contribute to the high accuracy of iris-based biometric systems. Despite these advantages, iris template compromise remains a critical security challenge. Because biometric traits are permanent, a leaked iris template cannot be resolved simply by re-enrollment. This limitation exposes authentication systems to long-term security risks.
Consequently, several cancelable biometric techniques have been proposed to transform biometric templates into revocable representations while preserving recognition performance [ 14 , 9 , 1 , 13 ] . BioHashing-based methods [ 13 ] generate protected templates using external tokens or salts. Lee et al. [ 8 ] proposed an alignment-robust cancelable biometric, while Zheng et al. [ 16 ] introduced a slicing-based method that generates revocable iris templates through transformation, allowing compromised templates to be replaced without requiring new biometric samples. However, these methods rely on external tokens, introducing a secondary attack surface; if the token is compromised, system security is significantly weakened.
Hence, Ouda et al. [ 11 ] proposed a tokenless scheme that eliminates the need for external secrets. These approaches effectively improve template security and revocability; however, they are primarily designed for single-instance iris systems and do not exploit the rich information available from both irises. Meanwhile, there is limited research on bilateral cancelable iris templates. Rafiq and Selwal [ 12 ] proposed a scheme that combines left and right iris templates using a block-XOR operation. While this method enhances security and recognition robustness, its fusion strategy increases computational complexity. Later, Arepalli and Boobalan proposed a multi-instance framework, termed the Compressed Transformed Fused template [ 2 ] . Although their method achieves an average processing time of 0.1 0.1 seconds and an Equal Error Rate (EER) of 0.15 0.15 %, it focuses only on compression and computational speed rather than optimal security. Furthermore, the aforementioned methods remain restricted to either cancelable mechanisms or multi-instance frameworks, rather than integrating both. Because the field still relies on single-iris templates, most systems fail to leverage the potential of multi-instance fusion to simultaneously enhance recognition accuracy and template security.
Therefore, this paper introduces a tokenless, multi-instance cancelable iris recognition framework that integrates bilateral information from both the left and right irises. Since the left and right iris patterns of an individual are statistically independent [ 3 , 5 ] , bilateral irises serve as complementary sources of biometric information, enabling mutual verification [ 7 ] . We employ contralateral XOR fusion to strengthen template protection, along with Majority Vote Fusion to create a stable enrollment template, ROI-based iris code slicing to improve recognition accuracy, and salt-based bit permutation for template randomization. Ultimately, this scheme fully satisfies the requirements of ISO/IEC 24745 [ 6 ] .
This section describes the proposed Cancelable Contralateral Fusion Scheme, which consists of preprocessing, feature extraction, region-of-interest selection, and the subsequent enrollment and authentication phases. The preprocessing and feature extraction are built based on an open-source library [ 15 ] , consisting of three steps: The iris, pupil, and sclera boundaries are identified through segmentation, yielding an inner circle (pupil–iris boundary) and an outer circle (iris–sclera boundary). The iris texture is then projected from Cartesian to polar coordinates [ 15 ] , producing a fixed-size two-dimensional rectangular array invariant to pupil dilation.
Following normalization, two scales of two-dimensional Gabor wavelet filtering are applied to extract a binary iris code following Daugman’s method [ 4 ] . The phase response is quantized into binary values, stored in an array of shape [ 2 , 16 , 256 , 2 ] [2,16,256,2] , where the first index represents two sizes of filter which are high-frequency and low-frequency filters, the second index represents each ring of the iris, the third index represents angular positions, and the last index represents the real and imaginary parts of the Gabor filter response [ 15 ] .
The inner rows of the iris code (rows 0–1, nearest the pupil boundary) are susceptible to artifacts from pupil dilation, while the outer rows (rows 7–15, near the iris–sclera boundary) are more frequently occluded by eyelids and eyelashes. Rows 2 through 6 capture the most stable and discriminative iris texture. Hence, we select these five rows as the Region of Interest (ROI) to distinguish between genuine and impostor samples. The feature vector consists of 5,120 bits per iris ( 2 I filter sizes × 5 I rows × 256 I angular positions × 2 I phases (real and imaginary parts) 2~\text{filter sizes}\times 5~\text{rows}\times 256~\text{angular positions}\times 2~\text{phases (real and imaginary parts)} ). The justification is reported using the sensitivity metric (Section 4.2.1 ), and analysis in Section 3.1.1 .
The proposed method combines both left and right iris codes into a single Protected Fused Template (PFT). Because contralateral iris patterns are statistically independent even in the same person or twin [ 3 , 5 ] , binding both canceled iris codes requires an attacker to possess both sides of the codes and their associated salts to recover any meaningful information.The method operates in two phases: As shown in Fig. 1 , three enrolled iris images per eye side are captured and fused by Majority Vote to establish the stable template for each eye. An eye-side-specific salt is applied to the stable template, permuting the bit positions to get the permuted bits. A bitwise exclusive-OR (XOR) operation is applied to the left and right sides of the permuted bits to create the PFT. Finally, only the PFT is stored, and all enrolled iris images are discarded.
As shown in Fig. 2 , a new pair of iris images is captured. The same salts derived from the enrollment ID for each side are applied to the new template, permuting the bit locations to get the permuted bits. Left and right side permuted bits are applied to the XOR operation to get the probed template. Finally, the PFT is compared with the stored PFT by using the Hamming Distance score. If the score is below the threshold, the system will accept the authentication.
This section analyzes how the proposed method satisfies the three security requirements of ISO/IEC 24745 [ 6 ] : irreversibility, unlinkability, and confidentiality. where T R , T L ∈ { 0 , 1 } 5120 T_{R},T_{L}\in\{0,1\}^{5120} are sliced iris templates (one per eye), S R , S L S_{R},S_{L} are per-eye 5,120-bit pseudorandom salts, ⊕ \oplus is the XOR operation, and π R , π L \pi_{R},\pi_{L} are bit permutations that are derived from the subject’s enrollment ID. Only the PFT is stored; the original iris captures and sliced templates T R , T L T_{R},T_{L} are all discarded. In addition, the enrollment phase utilizes a majority vote from iris templates. The irreversibility of this method consists of three layers: Only rows 2–6 of the iris code, the 5,120-bit ROI, are utilized, and rows 0–1 (inner zone) and 7–15 (outer zone) are permanently discarded. The full iris code cannot be recovered. Although the attacker can reverse all transformations, they can recover only ROI sliced template.
During the enrollment phase, the sliced iris templates ( T R T_{R} and T L T_{L} ) are not derived from a single iris capture. It is a per-bit majority vote over n = 3 n=3 independent captures. This voted template is a many-to-one function of the enrollment images. This does not reveal any information about any individual capture, and the original enrollment images cannot be reconstructed from them.
To recover T R T_{R} from the PFT, an attacker must know S R S_{R} , S L S_{L} , π L \pi_{L} , and T L T_{L} . Even if an attacker already knows T R T_{R} , the XOR with π L I ( T L ⊕ S L ) \pi_{L}(T_{L}\oplus S_{L}) still hides T L T_{L} completely. Since each salt is a 5,120-bit pseudorandom string derived from the enrollment ID, reconstructing the salt requires knowing the enrollment ID. The method assumes that the enrollment ID is kept confidential and not stored in the same database as the PFT.
A pair of ( S R , S L ) (S_{R},S_{L}) is issued independently for each database. Suppose the same user is enrolled in two databases with salt pairs ( S R ( 1 ) , S L ( 1 ) ) (S_{R}^{(1)},S_{L}^{(1)}) and ( S R ( 2 ) , S L ( 2 ) ) (S_{R}^{(2)},S_{L}^{(2)}) , producing PFT 1 \text{PFT}_{1} and PFT 2 \text{PFT}_{2} . Because of the salt differentiation, each side of the permuted templates is statistically independent. Under this assumption, the expected Hamming distance should be approximately 0.50 [ 4 ] : This guarantees that the same user’s templates across different databases are statistically indistinguishable, satisfying the unlinkability requirement.
4. Practical Deployment, Analysis & Case Studies The proposed method satisfies confidentiality because only the PFT is stored in the database. All original iris and sliced templates, T R T_{R} and T L T_{L} , are permanently discarded after enrollment. A leaked PFT reveals no raw biometric data. To recover any iris template from the PFT, one needs to know both salts and the other side’s iris code, as derived above. The enrollment ID is assumed to be kept confidential and not in the same location as the PFT. Thus, an attacker who obtains only the stored PFT cannot gain any usable biometric information, satisfying the confidentiality requirement of ISO/IEC 24745 [ 6 ] .
Three datasets, CASIA-IrisV4-Interval, CASIA-IrisV2, and CASIA-Iris-Thousand, were used. The first dataset is the CASIA-IrisV4-Interval, containing 2,639 iris pictures with a resolution of 320 × 280 320\times 280 pixels from 249 subjects. 121 subjects, with a total of 2,621 images and more than three image pairs for both eyes. The second dataset, CASIA-IrisV2, contains 1,200 iris images per device, each at a resolution of 640 × 480 640\times 480 pixels, from 30 subjects. All subjects are used with separate devices. The first device uses 1,187 pictures, and the second uses 1,181 pictures. The last dataset is the CASIA-Iris-Thousand, which contains 20,000 iris images with a resolution of 640 × 480 640\times 480 pixels from 1,000 subjects. There are 997 subjects (18,483 images in total) with contralateral irises used in the proposed method.
For each enrolled subject, the remaining iris images not used in the three-shot enrollment are paired into genuine and impostor test inputs at a 1:4 genuine-to-impostor ratio. A genuine pair consists of one right iris and one left iris probe image from the same enrolled subject. The impostor pool is constructed from three categories of equal size: Cross-subject impostors: both right iris and left iris probes are drawn from a different enrolled subject.
Mixed-eye impostors (genuine R, impostor L): the right iris probe belongs to the enrolled subject, while the left iris probe is drawn from a different enrolled subject. Mixed-eye impostors (genuine L, impostor R): the symmetric case, where the left iris probe is genuine and the right iris probe is from a different subject.
The second and third categories directly model the mixed-eye attack , in which an attacker possessing one genuine iris attempts to authenticate by pairing it with a stolen or synthetic contralateral iris. These categories constitute two-thirds of the impostor pool, ensuring that the reported EERs reflect resistance to this attack scenario, not only conventional cross-subject impostors.
The d ′ d^{\prime} is the sensitivity metric for distinguishing between genuine and impostor Hamming distance distributions. µ G , σ G \mu_{G},\sigma_{G} : Mean and standard deviation of the Genuine (intra-class) Hamming distances. µ I , σ I \mu_{I},\sigma_{I} : Mean and standard deviation of the Imposter (inter-class) Hamming distances. The EER is the error rate at the operating point where the False Match Rate (FMR) equals the False Non-Match Rate (FNMR): where τ ∗ \tau^{*} is the Hamming Distance threshold where both FMR and FNMR are equal, and The probe is accepted as genuine when HD < τ \text{HD}<\tau . The lower the EER, the better the separation between genuine and impostor.
The DET curve plots FNMR against FMR across all decision thresholds τ \tau , providing a comprehensive view of the trade-off between false non-matches and false matches at every operating point. Unlike a single EER value, the DET curve reveals the system’s full operating characteristics. A curve closer to the origin indicates better overall performance. The Hamming Distance (HD) measures the bit-level dissimilarity between two binary iris templates I , I ∈ { 0 , 1 } N \mathbf{A},\mathbf{B}\in\{0,1\}^{N} : To compensate for rotational misalignment during capture, the minimum HD over small cyclic shifts k k is taken: To identify the most discriminative region between genuine and impostor, we compute the sensitivity index d ′ d^{\prime} per row across all datasets, as shown in Table 1 . The inner zone (rows 0 and 1) shows significantly lower d ′ d^{\prime} than row 2, while the outer zone (rows 7 to 15) demonstrates the lowest d ′ d^{\prime} compared to other zones. Rows 2 to 6 (the middle zone) show the highest d ′ d^{\prime} across all datasets and are therefore selected as the ROI.
As shown in Table 2 , the ablation study was conducted under 1:4 genuine-to-impostor test inputs for observing the trade-off between accuracy and security. The permutation slightly increases EER but strengthens the security guarantee. The salt does not affect EER since it only permutes bit positions, but is essential for unlinkability. Majority Vote Fusion and ROI selection both contribute to recognition performance.
Fig. 3 demonstrates the DET curves of the proposed method across all three datasets. On CASIA-IrisV4-Interval, the curve approaches the origin closely, consistent with its 0.36 0.36 % EER, showing strong separation between genuine and impostor. On CASIA-IrisV2 Device 1 and CASIA-Iris-Thousand, both curves remain close to the origin with their EERs of 4.88 4.88 % and 3.35 3.35 %, respectively. On CASIA-IrisV2 Device 2, the curve is shifted toward the upper right due to the dataset’s low separability with its 10.80 10.80 % EER. The DET curves confirm consistent separability across all datasets at every operating point, not only at the EER.
Table 3 compares the proposed method against prior cancelable iris schemes and unprotected baselines. Prior works are evaluated only on CASIA-IrisV4-Interval (equivalent to CASIA-IrisV3-Interval: 2,639 images, 249 subjects); “–” indicates the unreported values. Because the proposed method fuses both irises, whereas all prior works operate on a single eye, contralateral binding provides an additional security layer not captured by single-iris EER alone. Across all datasets, the Proposed Method achieves the lowest EER compared to both unprotected baselines. The elevated EER of 10.80% on CASIA-IrisV2 Device 2 reflects the dataset’s low separability, even with an unprotected baseline that already reaches 16.63%.
Additionally, its per-row d ′ d^{\prime} values in Table 1 are the lowest across all datasets. The proposed method still reduces the EER by approximately one-third relative to both unprotected baselines. 5. Performance Evaluation & Extended Technical Observations All experiments were conducted on an Apple MacBook Pro equipped with an Apple M5 chip (10-core CPU comprising 4 performance cores and 6 efficiency cores) and 16 GB unified memory, running macOS Tahoe 26.3. Each phase was measured and averaged over 100 100 trials. Table 4 demonstrates the time each processing stage takes separately.
Table 5 demonstrates that the time difference between the proposed method and the unprotected baselines is negligible. The most time-consuming step across all methods is the feature extraction step from open-iris [ 15 ] , which accounts for over 99 99 % of the total time in both enrollment and authentication. The cancelable steps, such as Majority Vote Fusion, salt permutation, and XOR fusion, shown in Table 4 , total only about 0.97 0.97 ms for enrollment, 1.79 1.79 ms for authentication, and 1.05 1.05 ms for Hamming Distance comparison. This demonstrates that the overhead introduced by the protection steps is negligible compared to feature extraction.
Each permutation π R \pi_{R} and π L \pi_{L} comes from a 5,120-bit salt that makes the search space per eye to be upper-bounded by log 2 I ( 5120 ! ) \log_{2}(5120!) bits. An attacker needs to know both π R \pi_{R} and π L \pi_{L} simultaneously without knowing either the salt or the raw iris code. Even if one iris code is fully known, for example, T R T_{R} is leaked, the XOR with π L I ( T L ⊕ S L ) \pi_{L}(T_{L}\oplus S_{L}) still completely hides T L T_{L} ; thus, knowing one eye gives no advantage in recovering the other. Beyond the mathematical security bound, as shown in Table 3 , the proposed method satisfies the three ISO/IEC 24745 requirements (irreversibility, unlinkability, and confidentiality), and additionally provides multi-instance fusion and contralateral binding. All prior methods [ 12 , 8 , 2 , 17 , 16 , 10 ] operate on a single eye and do not use contralateral binding. Only [ 12 ] and [ 2 ] employ multi-instance fusion, yet they still rely on a single eye. No prior scheme simultaneously combines contralateral and multi-instance protection.
This paper presents a cancelable contralateral iris template protection scheme using Majority Vote Fusion ( n = 3 n\,=\,3 captures per eye), salt-based bit permutation, and contralateral XOR fusion to produce a single Protected Fused Template. To the best of our knowledge, this is the first scheme to combine tokenless multi-instance fusion and contralateral binding under ISO/IEC 24745. The proposed method was evaluated on three datasets (CASIA-IrisV4-Interval, CASIA-IrisV2 (device 1 and 2), and CASIA-Iris-Thousand), achieving EER of 0.36 0.36 %, 4.88 4.88 %, 10.80 10.80 %, and 3.35 3.35 %, respectively.
The proposed method outperforms both the unprotected full-iris and ROI baselines on all datasets. The proposed scheme satisfies three ISO/IEC 24745 requirements: irreversibility, confidentiality, and unlinkability. For irreversibility, reconstructing either iris code requires knowing both salts and the other eye’s iris code. For confidentiality, original iris captures are permanently discarded after enrollment, and the stored PFT reveals no raw biometric data without knowing the enrollment ID. For unlinkability, the same subject enrolled in two databases with different enrollment IDs yields templates with an HD of approximately 0.50 0.50 , demonstrating complete statistical independence and preventing cross-database tracking.
However, it has a few limitations. Firstly, although the ROI selection (iris’s rows 2–6) was optimized for CASIA datasets, it may not generalize to other datasets. Secondly, the scheme depends on a binary iris code produced by a 2D Gabor wavelet extractor, and the compatibility with other iris code extractors, such as deep learning-based feature extraction, has still not been evaluated. Lastly, the scheme is designed for scenarios in which both irises are available. Individuals with a single functional eye are excluded. Future work will address these limitations by evaluating the method with different sensors or in real-world deployment settings, exploring deep learning-based feature extraction, and extending it to multimodal biometric fusion.
This research was financially supported by the Fundamental Fund under grant number FFB690024/0337, the National Research Council of Thailand (NRCT), the Thailand Advanced Institute of Science and Technology (TAIST), the National Science and Technology Development Agency (NSTDA), the Institute of Science Tokyo, the Sirindhorn International Institute of Technology (SIIT), Thammasat University (TU) under the TAIST–Science Tokyo Program.
Biometric template protection comes down to threat models and transformation choices. Reversible transforms support re-issuance but risk exposure. Irreversible transforms improve privacy but can reduce matching performance. Template-on-card and match-on-device models mitigate theft by keeping raw templates off servers. Raw biometric templates (fingerprint minutiae, iris codes, face embeddings) are not secrets in the same way as passwords.
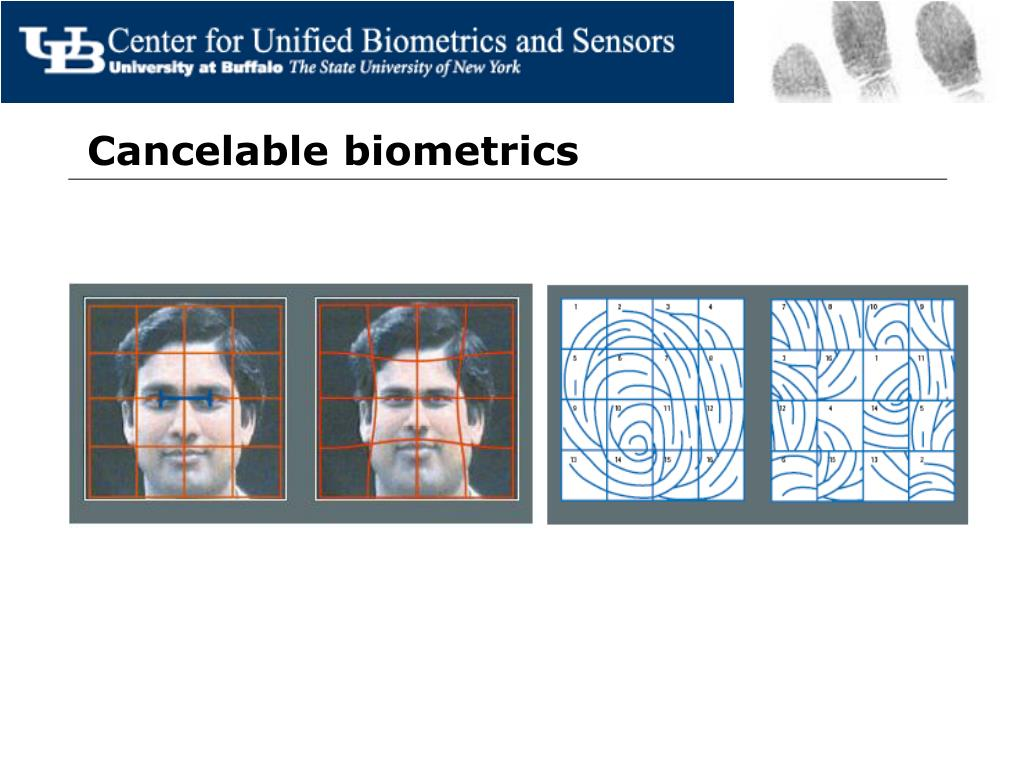
They: Cannot be changed easily if leaked (you can reset a password, but not your fingerprint). Attract attackers who can exploit stolen templates for spoof creation or identity fraud. Cancelable biometrics is an advanced security technique designed to protect the integrity and privacy of an individual's biometric data, such as a fingerprint or face scan. Instead of storing the raw biometric template, this method applies a specific and repeatable distortion or transformation to the data before it is stored.
The core principle is to create a new, "canceled" version of the biometric template that is unique to a specific application or device. If this transformed template is ever compromised in a data breach, it can be revoked and a new, different transformed template can be re-issued without compromising the user's actual, permanent biometric trait. Hashing with Salt: Similar to password security, templates are hashed with a user-specific salt.
Reversible Transforms: Apply distortion, random projection, or token-based transform before storage. Irreversible Transforms: Feature-space warping, biohashing, or non-invertible transforms. Highest risk if DB is breached— requires strongest protection schemes (salting, cancelable transforms, or cryptographic binding).
Low-threat, convenience systems (workforce access) : Reversible cancelable templates often suffice. High-value ID systems (national ID, border control) : Combine irreversible transforms + on-card/match-on-device. No single scheme is universally best. A layered approach —cryptographic binding + cancelable transforms + secure storage—is the only way to ensure revocability, privacy, and spoof-resistance.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Biometrics • https://en.wikipedia.org/wiki/Private%20biometrics • https://en.wikipedia.org/wiki/Lebanese%20passport • https://www.nature.com/articles/s41598-026-65666-3.pdf • https://arxiv.org/html/2607.02860v1 • https://blog.mantratec.com/Cancelable-Biometrics-Template-Protection
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Secure Biometric Template Protection Using Cancelable Biometrics.
[*] Metasploit Scan Running on Target Subnet for Secure Biometric Template Protection Using Cancelable Biometrics... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |