Complete Technical Paper Content — Secure Clipboard Manager With Encrypted Data Store
Overview & System Context
Secure Clipboard Manager With Encrypted Data Store: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9645 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background KeePass Password Safe is a free and open-source password manager primarily for Windows. It officially supports macOS and Linux operating systems through the use of Mono. Additionally, there are several unofficial ports for Windows Phone, Android, iOS, and BlackBerry devices, which normally work with the same copied or shared (remote) password database.
KeePass stores usernames, passwords, and other fields, including free-form notes and file attachments, in an encrypted file. This file can be protected by any combination of a master password, a key file, and the current Windows account details. By default, the KeePass database is stored on a local file system (as opposed to cloud storage). KeePass comes in two different variants: KeePass 1.x and KeePass 2.x. Although the 1.x variant is the former variant it is supported indefinitely: Dominik Reichl: "2.x isn't the successor of 1.x, and 1.x isn't dead". KeePass 2.x has a different software basis in C# instead of the former C++. Mainly communication features are extended in KeePass 2.x: authentication with the Windows user account, remote and shared database editing as well as many plugins allowing communication and authentication with different web browsers, databases and more. KeePass 1.x and 2.x support a number of plugins, although 2.x allows more plugins. It has a password generator and synchronization function, supports two-factor authentication, and has a Secure Desktop mode. It can use a two-channel auto-type obfuscation feature to offer additional protection against keyloggers. KeePass can import from over 30 other most commonly used password managers. A 2017 Consumer Reports article described KeePass as one of the four most widely used password managers (alongside 1Password, Dashlane and LastPass), being "popular among tech enthusiasts" and offering the same level of security as non-free competitors. A 2019 Independent Security Evaluators study described KeePass as well as other widely used password managers as being unable to control Windows 10's tendency to leave passwords in cleartext in RAM after they are displayed using Windows controlled GUI. In addition, several GitHub projects (KeeFarce, KeeThief, Lazanga) specifically attack a running KeePass to steal all data when the host is compromised.
KeePass cannot prevent password theft and, as Dominik Reichl, the administrator of KeePass, states, "neither KeePass nor any other password manager can magically run securely in a spyware-infected, insecure environment." KeePass can minimize itself and type the information of the currently selected entry into dialogs, webforms, etc. KeePass has a global auto-type hot key. When KeePass is running in the background (with an unlocked database) and user presses down the hotkey, it looks up the selected (or correct) entry and enters every login and/or password characters sequence. All fields, such as title, username, password, URL, and notes, can be drag and dropped into other windows. Windows clipboard handling allows double-clicking on any field of the password list to copy its value to the Windows clipboard. KeePass may be configured to randomize characters' input sequence to make it harder to log keystrokes. The features is called Two-Channel Auto-Type Obfuscation (TCATO).
KeePass features a built-in password generator that generates random passwords. Random seeding can be done through user input (mouse movement and random keyboard input). According to the utility's author, KeePass was one of the first password management utilities to use security-enhanced password edit controls, in this case one called CSecureEditEx. The author makes several claims regarding the security of the control and its resistance to password revealing utilities; however, the author does not cite or make any references to any third-party testing of the control to corroborate the claims of its security. Passwords are protected in memory while KeePass is running. On Windows Vista and later versions, passwords are encrypted in process memory using Windows Data Protection API, which allows storing the key for memory protection in a secure, non-swappable memory area. On previous Windows systems, KeePass falls back to using the ARC4 cipher with a temporary, random session key.
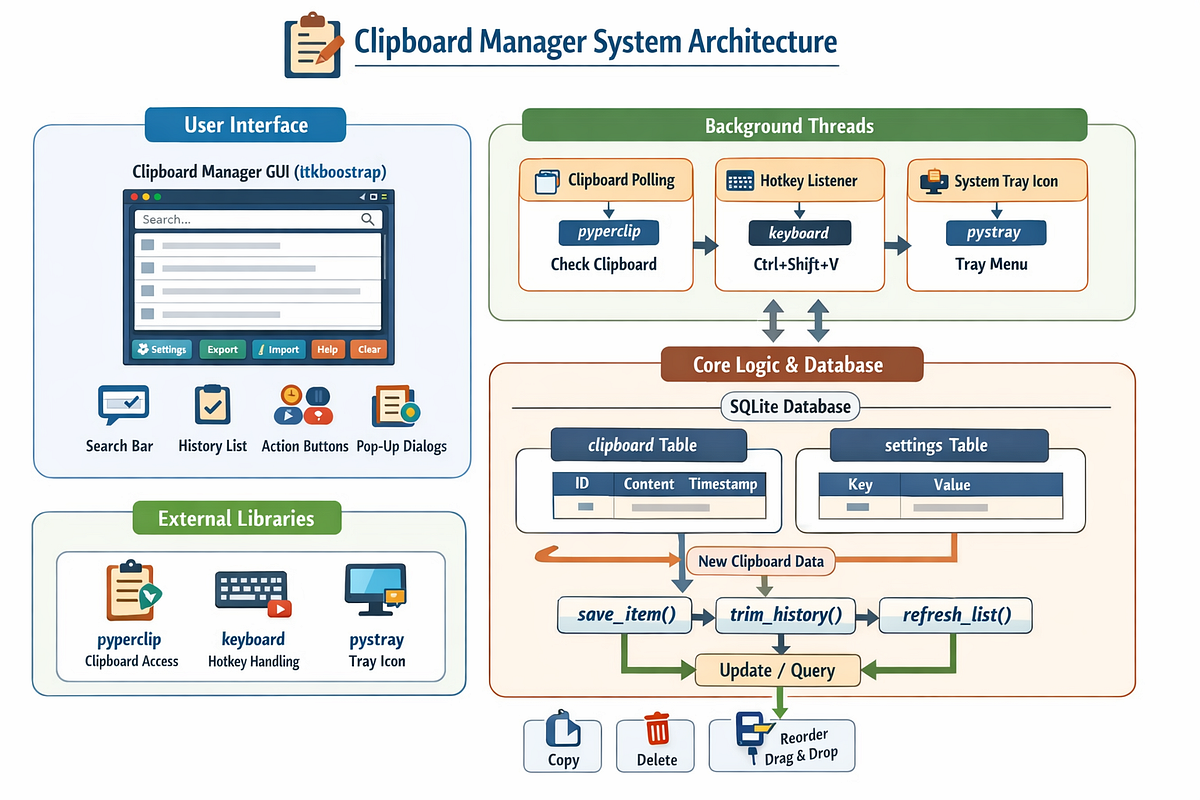
Figure 1: I Building a Smart Clipboard Manager in Python (Full System ... Access to the database is restricted by a master password or a key file. Both methods may be combined to create a "composite master key". If both methods are used, then both must be present to access the password database. KeePass version 2.x introduces a third option—dependency upon the current Windows user. KeePass encrypts the database with the AES, Twofish or ChaCha20 symmetric cipher, where the first two are used in CBC/PKCS7 mode. AES is the default option in both KeePass editions, Twofish is available in KeePass 1.x, ChaCha20 is available only in KeePass 2.35 and higher.
However, a separate plugin provides Twofish as an encryption algorithm in KeePass 2.x. In KeePass 1.x (KDB database format), the integrity of the data is checked using a SHA-256 hash of the plaintext, whereas in KeePass 2.x (KDBX database format), the authenticity of the data is ensured using a HMAC-SHA-256 hash of the ciphertext (Encrypt-then-MAC construction).
As the next version of Windows NT after Windows 2000, as well as the successor to Windows Me, Windows XP introduced many new features but it also removed some others. The introduced, installed or enabled features by default are listed as follows (both original and later releases). Windows XP includes ClearType subpixel rendering, which makes onscreen fonts smoother and more readable on liquid-crystal display (LCD) screens. Although ClearType affects CRT monitors, its primary use is for LCD/TFT-based (laptop, notebook, and modern 'flatscreen') displays. ClearType in Windows XP currently supports the RGB and BGR subpixel structures. There are other parameters, such as contrast, that can be set via a ClearType Tuner power toy that Microsoft makes available as a free download from its Typography website.
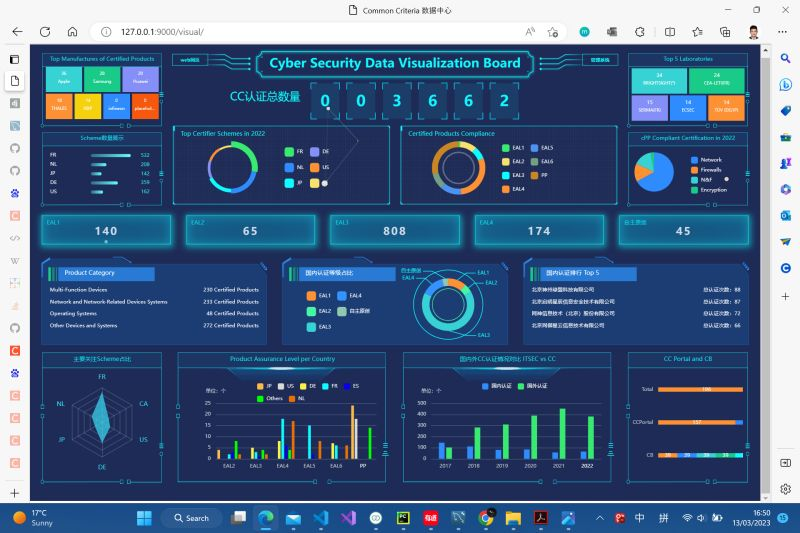
There are significant changes made to Windows Explorer in Windows XP, both visually and functionally. Microsoft focused especially on making Windows Explorer more discoverable and task-based, as well as adding a number of features to reflect the growing use of a computer as a "digital hub". Figure 2: Key highlights: • Secure authentication & role-based access • Encrypted ...
Windows XP improves image preview by offering a Filmstrip view which shows images in a single horizontal row and a large preview of the currently selected image above it. "Back" and "Previous" buttons facilitate navigation through the pictures, and a pair of "Rotate" buttons offer 90-degree clockwise and counter-clockwise rotation of images. Filmstrip view like any other view can be turned on per folder. This view will be available if the new "Common Tasks" folder view is selected, not with "Windows Classic" folder view. Aside from the Filmstrip view mode, there is a 'Thumbnails' view, which displays thumbnail-sized images in the folder and also displays images a subfolder may be containing (4 by default) overlaid on a large folder icon. A folder's thumbnail view can be customized from the Customize tab accessible from its Properties, where users can also change the folder's icon and specify a template type (pictures, music, videos, documents) for that folder and optionally all its subfolders. The size and quality of thumbnails in "Thumbnails" view can be adjusted using Tweak UI or the registry. Exif metadata stored in the image is also shown in the file's Properties -> Summary tab, in "Details" view and in any view on the status bar. Windows XP optionally caches the thumbnails in a "Thumbs.db" file in the same folder as the pictures so that thumbnails are generated faster the next time. Thumbnails can be forced to regenerate by right-clicking the image in Thumbnail or Filmstrip views and selecting "Refresh thumbnail".
AutoPlay examines newly discovered removable media and devices and, based on content such as pictures, music or video files, launches an appropriate application to play or display the content. AutoPlay (not to be confused with AutoRun) was created in order to simplify the use of peripheral devices – MP3 players, memory cards, USB storage devices and others – by automatically starting the software needed to access and view the content on these devices. AutoPlay can be enhanced by AutoPlay-compatible software and hardware. It can be configured by the user to associate favourite applications with AutoPlay events and actions. These actions are called AutoPlay Handlers and there are sets of Handlers associated with various types of content. New AutoPlay handlers can get added to the system when additional software is installed. The user can edit, delete or create AutoPlay handlers using TweakUI. AutoPlay settings can be configured per-device in Windows XP from the device's properties. When a user inserts an optical disc into a drive or attaches a USB camera, Windows detects the arrival and starts a process of examining the device or searching the medium. It is looking for properties of the device or content on the medium so that AutoPlay can present a set of meaningful options to the user. When the user makes a particular choice, they also have the option to make that selection automatic the next time Windows sees that content or device. The content types available vary with the type of drive selected.
The Text Services Framework (TSF), is a COM framework and API introduced in Windows XP that supports advanced text input and text processing. The Text Services Framework is designed to offer advanced language and word processing features to applications. It supports features such as multilingual support, keyboard drivers, handwriting recognition, speech recognition, as well as spell checking and other text and natural language processing functions. It is also downloadable for older Windows operating systems. The Language Bar is the core user interface for Text Services Framework. The language bar enables text services to add UI elements to the toolbar and enables these elements when an application has focus. From the Language Bar, users can select the input language, and control keyboard input, handwriting recognition and speech recognition. The language bar also provides a direct means to switch between installed languages, even when a non-TSF-enabled application has focus.
2. System Architecture & Core Working Principles Windows XP introduces support for Vectored Exception Handling. Vectored Exception Handling is made available to Windows programmers using languages such as C++ and Visual Basic. VEH does not replace Structured Exception Handling (SEH), rather VEH and SEH coexist with VEH handlers having priority over SEH handlers. Compared with SEH, VEH works more like a traditional notification callback scheme.
Applications can intercept an exception by calling the AddVectoredExceptionHandler API to watch or handle all exceptions. Vectored handlers can be chained in order in a linked list and they aren't tied to the stack frame, so they can be added anywhere in the call stack unlike SEH's try/catch blocks.
The ability to boot in 30 seconds was a design goal for Windows XP, and Microsoft's developers made efforts to streamline the system as much as possible; The Logical Prefetcher is a significant part of this; it monitors what files are loaded during boot, optimizes the locations of these files on disk so that less time is spent waiting for the hard drive's heads to move and issues large asynchronous I/O requests that can be overlapped with device detection and initialization that occurs during boot.
The prefetcher works by tracing frequently accessed paged data which is then used by the Task Scheduler to create a prefetch-instructions file at %WinDir%\Prefetch. Upon system boot or the launch of an application, any data and code in the trace that is not already in memory is prefetched from the disk. The previous prefetching results determine which scenario benefited more and what should be prefetched at the next boot or launch. The prefetcher also uses the same algorithms to reduce application startup times. To reduce disk seeking even further, the Disk Defragmenter is called in at idle time to optimize the layout of these specific files and metadata in a contiguous area. Boot and resume operations can be traced and analyzed using Bootvis.exe.
In Windows XP, there are some improvements made to System Restore compared to Windows Me. System Restore uses a copy-on-write file system filter driver for taking snapshots. In Windows XP, System Restore is configurable per volume and the data stores are also stored per volume. On NTFS volumes, the Restore Points are stored using NTFS compression and protected using ACLs. A Disk Cleanup handler allows deleting all but the most recent Restore Point. Besides the Registry hives and system files, COM+ and WMI databases and the IIS metabase can also be restored. System Restore supports Group Policy. System Restore in Windows XP also works without issues with EFS-encrypted files.
Automated System Recovery is a feature that provides the ability to save and restore Windows and installed applications, the system state, and critical boot and system files from a special backup instead of a plain reinstall. ASR consists of two components - backup and restore. The Backup portion located in NTBackup backs up the system state (Windows Registry, COM+ class registration database, Active Directory and the SYSVOL directory share), and the volumes associated with operating system components required to start Windows after restore as well as their configuration (basic or dynamic). The Restore portion of ASR is accessed by pressing F2 from Windows XP Text mode Setup. Automated System Recovery can even restore programs and device drivers if they are added to the ASR Setup information disk. ASR does not restore data files.
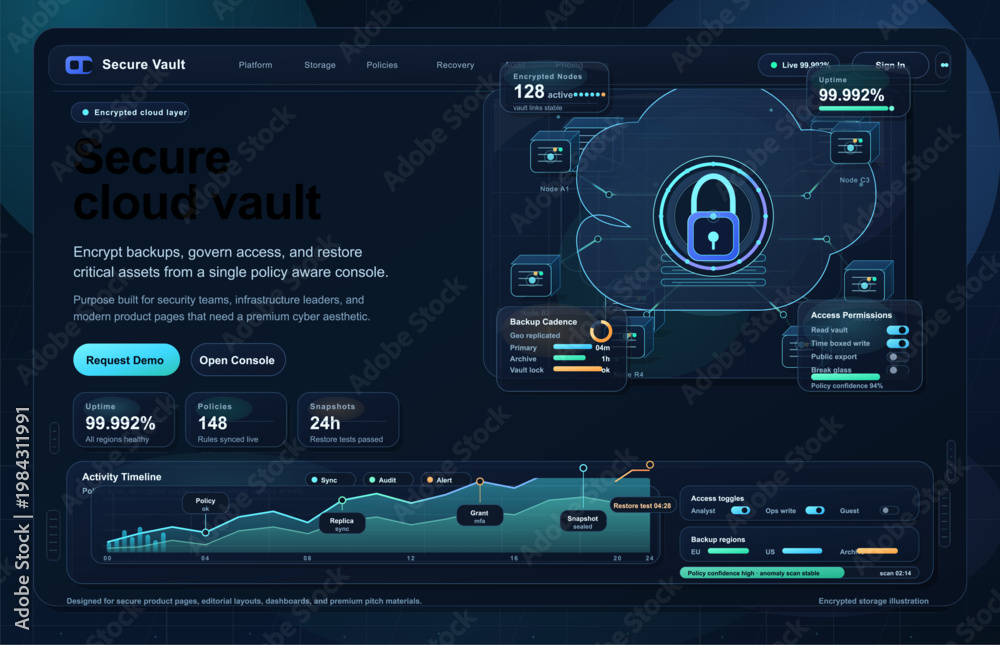
Figure 3: Secure cloud vault dashboard interface with encryption lock, backup ... A common issue in previous versions of Windows was that users frequently suffered from DLL hell, where more than one version of the same dynamically linked library (DLL) was installed on the computer. As software relies on DLLs, using the wrong version could result in non-functional applications, or worse. Windows 98 Second Edition and Windows 2000 partially solved this problem for native code by introducing side-by-side component sharing and DLL/COM redirection. These operating systems allowed loading a private version of the DLL if it was placed in the application's folder by the developer, instead of the system directory and must be registered properly with the system. Windows XP improves upon this by introducing side-by-side assemblies for COM+ 2.0, .NET, COM classic, and Win32 components (C Runtime, GDI+, Common Controls). The technology keeps multiple digitally signed versions of a shared DLL in a centralized WinSxS folder and runs them on demand to the appropriate application keeping applications isolated from each other and not using common dependencies. Manifests and the assembly version number are used by the OS loader to determine the correct binding of assembly versions to applications instead of globally registering these components. To achieve this, Windows XP introduces a new mode of COM object registration called Registration-free COM (or RegFree COM). It allows Component Object Model (COM) components to store activation metadata and CLSID (Class ID) for the component without using the registry. Instead, the metadata and CLSIDs of the classes implemented in the component are declared in an assembly manifest (described using XML), stored either as a resource in the executable or as a separate file installed with the component. This allows multiple versions of the same component to be installed in different directories, described by their own manifests, as well as XCOPY deployment. During application loading, the Windows loader searches for the manifest. If it is present, the loader adds information from it to the activation context When the COM class factory tries to instantiate a class, the activation context is first checked to see if an implementation for the CLSID can be found. Only if the lookup fails is the registry scanned.
Windows Error Reporting collects and offers to send post-error debug information (a memory dump) using the internet to the developer of an application that crashes or stops responding on a user's desktop. No data is sent without the user's consent. When a dump (or other error signature information) reaches the Microsoft server, it is analyzed and a solution is sent back to the user if one is available. Windows Error Reporting runs as a Windows service and can optionally be entirely disabled.
Software and hardware manufacturers may access their error reports using Microsoft's Winqual program. Software and hardware manufacturers can also close the loop with their customers by linking error signatures to Windows Error Reporting Responses. This allows distributing solutions as well as collecting extra information from customers (such as reproducing the steps they took before the crash) and providing them with support links.
The RTM release of Windows XP includes Windows Media Player version 8 (officially called Windows Media Player for Windows XP) and Windows Media 8 codecs. Windows Media Player for Windows XP introduced ID3 support for MP3s, editing media information from within the Library, adding lyrics for MP3 or WMA tracks, file name customization when ripping, new visualizations, support for HDCDs, ability to lock down the player in a corporate environment and DVD playback support (when appropriate codecs are installed separately). Windows Media Player also incorporates newer hardware support for portable devices by means of the Media Transfer Protocol and the User-Mode Driver Framework-based Windows Portable Devices API.
The original RTM release of Windows XP included Windows Movie Maker 1.1 which added non-compressed DV AVI recording of digital video sources. Windows Movie Maker 2 introduced numerous new transitions, effects, titles and credits, a task pane, resizable preview window with dimensions, improved capture and export options, an AutoMovie feature, saving the final video back to tape and custom WMV export profiles.
Windows XP includes advances in Broadcast Driver Architecture for receiving and capturing analog and digital TV broadcasts complete with signal demodulation, tuning, software de-multiplexing, electronic program guide store, IP data broadcasting etc. Windows XP includes improved FireWire (IEEE 1394) support (DVCPRO25 – 525-60 and 625-50) for digital video cameras and audio video devices. It introduces MSTape, a WDM driver for D-VHS and MPEG camcorder devices.
DirectShow 8 introduces the Video Mixing Renderer-7 (VMR-7) filter which uses DirectDraw 7 for video rendering, replacing the Overlay Mixer. VMR-7 can mix multiple streams and graphics with alpha blending, allowing applications to draw text (such as closed captions) and graphics (such as channel logos or UI buttons) over the video without flickering, and support compositing to implement custom effects and transitions. VMR-7 also supports source color keying, overlay surface management, frame-stepping and improved multiple-monitor support. VMR-7 features a "windowless mode" for applications to easily host video playback within any window and a "renderless playback mode" for applications to access the composited image before it is rendered. DirectX 9 introduced the VMR-9 which uses Direct3D 9 instead of DirectDraw, allowing developers to transform video images using the Direct3D pixel shaders. DirectShow 8 includes AVStream, a multimedia class driver for video-only and audio-video kernel streaming.
Windows XP supports both TWAIN as well as Windows Image Acquisition-based scanners. Windows Image Acquisition in Windows XP adds support for Automatic document feeder scanners, scroll-fed scanners without preview capabilities and multi-page TIFF generation. For WIA video, a Snapshot filter driver is introduced which allows still frames to be captured from the video stream. Windows XP SP1 and later support the downloadable WIA Library v2.0 which provides access to WIA functionality through programming languages and scripting environments that support OLE Automation. The Scanner and Camera Wizard based on Windows Image Acquisition and other common dialogs for WIA devices have been improved in Windows XP to show the media information and metadata, rotate images as necessary, categorize them into subfolders, capture images and video in case of a still or video camera, crop and scan images to a single or multi-page TIFF in case of a scanner. The Picture Transfer Protocol (PTP) implementation has been updated to support all mandatory and optional commands in the PTP standard, and object tree support which allows secondary files associated with a parent file to be grouped and transferred concurrently. Windows Media Player 10 also adds the Media Transfer Protocol for transferring media content from portable devices. Thus, for digital cameras, Windows XP supports acquiring photos using any of either WIA, PTP, USB Mass Storage Class or MTP protocols depending on what the camera manufacturer supports.
3. Software Implementation, Frameworks & Protocols Windows XP includes Windows Script Host 5.6, a major update to the WSH environment, which includes an improved object model to reduce boilerplate code, stronger security and several other improvements. A new XML-based file format, the Windows Script File format (.WSF) has been introduced besides .VBS and .JS which can store in an XML node in the same file, extra information besides script code, such as digital signature blocks, runtime directives or instructions to import external code. The WSF schema can include jobs wrapped each by a unique
The remote script can be monitored by using the Status property. WSH 5.6 introduces the Exec method for the WshShell object to execute command-line console applications and has access to the standard I/O streams (StdIn, StdOut, and StdErr) of the spawned process. In earlier versions of Windows Script, to use arguments, one had to access the WshArguments collection object which could not be created externally and required that the person running the script know the order of the arguments, and their syntax and values. WSH 5.6 introduces named arguments on the command line which follow a /string:value or Boolean convention defined in 'Runtime' tag and are recognized irrespective of their order on the command line. Named arguments are grouped in the Named collection object and have the usual methods like Item, Count, Length as well as an Exists method. The 'ShowUsage' method for the WshArguments object mentioned earlier shows the argument information in a message box. Windows XP includes a ScriptPW.Password COM automation object, implemented in the scriptpw.dll file which can be used to mask sensitive information like passwords from command line scripts.
Users can log into Windows XP Professional remotely through the Remote Desktop service. It is built on Terminal Services technology (RDP), and is similar to "Remote Assistance", but allows remote users to access local resources such as printers. Any Terminal Services client, a special "Remote Desktop Connection" client, or a web-based client using an ActiveX control may be used to connect to the Remote Desktop. (Remote Desktop clients for earlier versions of Windows, Windows 95, Windows 98 and 98 Second Edition, Windows Me, Windows NT 4.0, or Windows 2000 have been made available by Microsoft. This permits earlier versions of Windows to connect to a Windows XP system running Remote Desktop, but not vice versa.) There are several resources that users can redirect from the remote server machine to the local client, depending upon the capabilities of the client software used. For instance, "File System Redirection" allows users to use their local files on a remote desktop within the terminal session, while "Printer Redirection" allows users to use their local printer within the terminal session as they would with a locally or network shared printer. "Port Redirection" allows applications running within the terminal session to access local serial and parallel ports directly, and "Audio" allows users to run an audio program on the remote desktop and have the sound redirected to their local computer. The clipboard can also be shared between the remote computer and the local computer. The RDP client in Windows XP can be upgraded to 7.0. The Remote Desktop Web Connection component of Internet Information Services 5.1 also allows remote desktop functionality over the web through an ActiveX control for Internet Explorer.
Remote Assistance allows a Windows XP user to temporarily take over a remote Windows XP computer over a network or the Internet to resolve issues. As it can be a hassle for system administrators to personally visit the affected computer, Remote Assistance allows them to diagnose and possibly even repair problems with a computer without ever personally visiting it. Remote Assistance allows sending invitations to the support person by email, Windows Messenger or saving the invitation as a file. The computer can be controlled by both, the support person connecting remotely as well as the one sending the invitation. Chat, audio-video conversations and file transfer are available.
Windows XP introduces Fast User Switching and a more end user friendly Welcome Screen with a user account picture which replaces the Classic logon prompt. Fast user switching allows another user to log in and use the system without having to log out the previous user and quit his or her applications. Previously (on both Windows Me and Windows 2000) only one user at a time could be logged in (except through Terminal Services), which was a serious drawback to multi-user activity. Fast User Switching, like Terminal Services, requires more system resources than having only a single user logged in at a time and although more than one user can be logged in, only one user can be actively using their account at a time. This feature is not available when the Welcome Screen is turned off, such as when joined to a Windows Server Domain or with Novell Client installed. Even when the Welcome screen is enabled, users can switch to the Classic logon by pressing Ctrl+Alt+Del twice at the Welcome screen.
Windows XP introduced Windows Installer (MSI) 2.0. Windows Installer 2.0 brought major improvements such as installation and management of side by side and CLR assemblies, sandboxing MSI custom actions, improved event logging and hiding sensitive information in log files, per-user program isolation, digital signatures, improved patching (more robust patch conflict resolution and reduced unnecessary unversioned file copying and source prompts), Terminal Server support and integration with System Restore and Software Restriction Policies. Windows XP can be updated to Windows Installer 4.5.
Windows Disk Defragmenter was updated to alleviate several restrictions. It no longer relies on the Windows NT Cache Manager, which prevented the defragmenter from moving pieces of a file that cross a 256 KB boundary within the file. All parts of a stream including the cluster boundary for non-compressed files, reparse points, bitmaps, and attribute_lists, NTFS metadata files, EFS-encrypted files and the NTFS Master File Table can be defragmented. The defragmenter supports NTFS volumes with cluster sizes larger than 4 kilobytes. A command-line tool, defrag.exe, has been included, providing access to the defragmenter from cmd.exe and Task Scheduler. Users who are members of the Power Users group can schedule defragmentation.
Windows Task Manager incorporates a number of improvements in Windows XP. It has been updated to display process names longer than 15 characters in length on the Processes tab, which used to be truncated in Windows 2000. Session ID and User name columns have been added on the Processes tab. The Delete key can also be used to terminate processes on the Processes tab. A new Networking tab shows statistics relating to each of the network adapters present in the computer.
By default the adapter name, percentage of network utilization, link speed and state of the network adapter are shown, along with a chart of recent activity. More options can be shown by choosing Select columns... from the View menu. The Users tab shows all users that currently have a session on the computer. On server computers there may be several users connected to the computer using Terminal Services. There may also be multiple users logged onto the computer at one time using Fast User Switching. Users can be disconnected or logged off from this tab. A Shutdown menu has been introduced that allows access to Standby, Hibernate, Turn off, Restart, Log Off and Switch User. Holding down Ctrl while clicking New Task opens a command prompt.
Windows XP introduces WMIC.exe, the Windows Management Instrumentation console utility Beginning with Windows XP, WMI resides in a shared service host process called Wmiprvse.exe which can spawn multiple instances under different accounts: LocalSystem, NetworkService, or LocalService. Previously, WMI providers were loaded in-process with the WMI Service and a single WMI provider crashing led to the restart of the WMI core service, WinMgmt.exe. In Windows XP, MOF files are used to describe system ETW events. WMI Filters for Group Policy were introduced.
schtasks.exe (Windows Task Scheduler) shutdown.exe (Shutdown commands) Sc.exe (Service Control Manager) gpupdate.exe and gpresult.exe (Group Policy) logman.exe, relog.exe, typeperf.exe and tracerpt.exe (Performance Monitor) Eventquery.vbs, eventcreate.exe, EventTriggers.exe (Event log) DSquery.exe, dsget.exe, dsadd.exe, dsmod.exe, dsmove.exe, dsrm.exe (Active Directory) diskpart.exe, Defrag.exe and fsutil.exe (Disk management, Defragmentation and file system management) bootcfg.exe (Boot.ini) openfiles.exe (Networking) powercfg.exe (Power management) tasklist.exe, taskkill.exe, getmac.exe, systeminfo.exe, driverquery.exe, reg.exe, regini.exe, IPseccmd.exe (Windows 2000 Resource Kit).
IIS*.vbs (IIS and Active Server Pages management) Prn*.vbs (Printing) Pagefileconfig.vbs (PageFile configuration) bitsadmin.exe, bindiff.exe, cabarc.exe, ftonline.exe, httpcfg.exe, ipseccmd.exe, netcap.exe, rasdiag.exe, spcheck.exe, tracepdb.exe (New support tools) Windows XP includes several Encrypting File System improvements The most notable improvement is that multiple user accounts can share access to encrypted files on a file-by-file basis. A Details button in the Advanced file attributes dialog in the file's properties allows adding or removing additional users who can access the EFS-encrypted file, and viewing the certificate thumbprint and the Data Recovery Agent account. EFS certificates are autoenrolled in the CA and there is support for revocation checking on certificates used when sharing encrypted files. Unlike Windows 2000, there is no default local Data Recovery Agent and no requirement to have one, although a self-signed certificate for the recovery agent can be generated using cipher.exe. The DPAPI Master Key can be protected using a domain-wide public key. A stronger FIPS 140-1 compliant algorithm such as 3DES can be used. Windows XP Service Pack 1 adds support for and the default use of AES-256 symmetric encryption algorithm for all EFS-encrypted files. Windows XP also warns the user if the EFS encrypted files are being copied to a file system such as FAT or unsupported location which does not support EFS, and thus the file is going to get decrypted. Windows XP can also encrypt files on a remote server with NTFS if the server is trusted for delegation in Active Directory and the user's certificate and private key are loaded in the local profile on the server. If a roaming user profile is used, it will be copied locally. On a WebDAV server mapped by a drive letter, Windows XP can encrypt the file locally and transport it as a raw encrypted file to the WebDAV server using the HTTP PUT command. Similarly, EFS encrypted files can be downloaded raw from the WebDAV and decrypted locally. The command line utilities cipher, copy and xcopy have been updated in Windows XP. EFS can also be completely disabled in Windows XP through Group Policy (for a domain) or through the registry (for a non-domain computer). For faster cache validation, the time for how long the user session key and certificate chain are cached can be adjusted.
Windows 2000 wireless support did not support seamless roaming and auto-configuration. Windows XP's Wireless Zero Configuration service supports automatic wireless network configuration with re-authentication when necessary thus providing seamless roaming capability and setting the preferred order of connections. In the absence of a wireless access point, Windows XP can set up an ad hoc wireless network. There is native support for WPA and WPA2 authentication in infrastructure networks with the latest service packs and/or updates applied. Windows XP includes a Wireless Network Setup Wizard which supports the Windows Connect Now: USB Flash Drive (WCN-UFD) method to ease setting up the wireless network for inexperienced users. Windows XP can connect to hotspots created using Wireless Provisioning Services.
4. Practical Deployment, Analysis & Case Studies In Windows XP, Internet Connection Sharing is integrated with UPnP, allowing remote discovery and control of the ICS host. It has a Quality of Service Packet Scheduler component. When an ICS client is on a relatively fast network and the ICS host is connected to the internet through a slow link, Windows may incorrectly calculate the optimal TCP receive window size based on the speed of the link between the client and the ICS host, potentially affecting traffic from the sender adversely. The ICS QoS component sets the TCP receive window size to the same as it would be if the receiver were directly connected to the slow link. Internet Connection Sharing also includes a local DNS resolver in Windows XP to provide name resolution for all network clients on the home network, including non-Windows-based network devices. ICS is also location-aware, that is, when connected to a domain, the computer can have a Group Policy to restrict the use of ICS but when at home, ICS can be enabled.
IPv6 has to be installed and configured from the command line using the netsh interface ipv6 context as there is no GUI support. After the network interface's link-local address is assigned, stateless autoconfiguration for local and global addresses can be performed by Windows XP. Static IPv6 addresses can be assigned if there is no IPv6 router on the local link. Transition mechanisms such as manually configured tunnels and 6to4 can be set up. Privacy extensions are enabled and used by default. 6to4 is automatically activated for public IPv4 addresses without a global IPv6 address. Other types of tunnels can be set up include: 6over4, Teredo, ISATAP, PortProxy. Teredo also helps traverse cone and restricted NATs.
Teredo host-specific relay is enabled when a global IPv6 address has been assigned, otherwise Teredo client functionality is enabled. The Windows XP DNS resolver can only make DNS queries using IPv4, it does not use IPv6 itself as a transport to make the query. However, when a DNS query sends back both IPv4 and IPv6 resource records, IPv6 addresses are preferred. Windows XP does not support DHCPv6 and PPPv6/IPv6CP. An open source DHCPv6 implementation called Dibbler is available, although stateless autoconfiguration largely makes it unnecessary.
Windows XP includes the Background Intelligent Transfer Service, a Windows service that facilitates prioritized, throttled, and asynchronous transfer of files between machines using idle network bandwidth. BITS will only transfer data whenever there is bandwidth which is not being used by other applications, for example, when applications use 80% of the available bandwidth, BITS will use only the remaining 20%. BITS constantly monitors network traffic for any increase or decrease in network traffic and throttles its own transfers to ensure that other foreground applications (such as a web browser) get the bandwidth they need. BITS also supports resuming transfers in case of disruptions. BITS version 1.0 supports only downloads. From version 1.5, BITS supports both downloads and uploads. Uploads require the IIS web server, with BITS server extension, on the receiving side. Windows XP components such as Windows Update use BITS to download updates so only idle bandwidth is used to download updates and downloading can be resumed in case network connectivity is interrupted. BITS uses a queue to manage file transfers and downloads files on behalf of requesting applications asynchronously, i.e., once an application requests the BITS service for a transfer, it will be free to do any other job, or even terminate. The transfer will continue in the background as long as the network connection is there and the job owner is logged in. BITS supports transfers over both HTTP and HTTPS. If a network application begins to consume more bandwidth, BITS decreases its transfer rate to preserve the user's interactive experience, except for Foreground priority downloads. BITS is exposed through Component Object Model (COM), making it possible to use with virtually any programming language.
The Advanced Networking Pack, later made part of SP2 introduced Peer-to-Peer Networking and the Peer Name Resolution Protocol (PNRP) to Windows XP. It operates over IPv6. The P2P architecture in Windows XP consists of the following components: PNRP: This provides dynamic name publication and resolution of names to endpoints. PNRP is a distributed name resolution protocol allowing Internet hosts to publish "peer names" and corresponding IPv6 addresses and optionally other information. Other hosts can then resolve the peer name, retrieve the corresponding addresses and other information, and establish peer-to-peer connections. With PNRP, peer names are composed of an "authority" and a "qualifier". The authority is identified by a secure hash of an associated public key, or by a place-holder (the number zero) if the peer name is "unsecured". The qualifier is a string, allowing an authority to have different peer names for different services. If a peer name is secure, the PNRP name records are signed by the publishing authority, and can be verified using its public key. Unsecured peer names can be published by anybody, without possible verification. Multiple entities can publish the same peer name. For example, if a peer name is associated with a group, any group member can publish addresses for the peer name. Peer names are published and resolved within a specified scope. The scope can be a local link, a site (e.g. a campus), or the whole Internet. Graphing: PNRP also allows creating an overlay network called a Graph. Each peer in the overlay network corresponds to a node in the graph. Nodes are resolved to addresses using PNRP. All the nodes in a graph share book-keeping information responsible for the functioning of the network as a whole. For example, in a distributed resource management network, which node has what resource needs to be shared. Such information is shared as Records, which are flooded to all the peers in a graph. Each peer stores the Record to a local database. A Record consists of a header and a body. The body contains data specific to the application that is using the API; the header contains metadata to describe the data in the body as name-value pairs serialized using XML, in addition to author and version information. It can also contain an index of the body data, for fast searching. A node can connect to other nodes directly as well, for communication that need not be shared with the entire Graph. Grouping: The Peer-to-Peer API also allows creation of a secure overlay network called a Group, consisting of all or a subset of nodes in a Graph. A Group can be shared by multiple applications, unlike a Graph. All peers in a Group must be identifiable by a unique named, registered using PNRP, and have a digital signature certificate termed as Group Member Certificate (GMC). All Records exchanged are digitally signed. Peers must be invited into a Group.
The invitation contains the GMC that enables it to join the group. .NET Framework versions 1.0, 1.1, 2.0, 3.0, 3.5 and 4.0 Windows Search 2.0, 3.0 and 4.0 Windows Defender KMDF versions 1.0, 1.1, 1.5, 1.7 and 1.9 and UMDF versions 1.5, 1.7 and 1.9. Windows Services for UNIX XPS Essentials Pack Microsoft Virtual PC 2004 and 2007 Windows Live Essentials 2009 and Wave 2. Windows PowerShell 1.0 and 2.0 and Windows Remote Management 1.0 and 2.0.
Windows XP Service Pack 2 added native Bluetooth support. The Windows XP Bluetooth stack supports external or integrated Bluetooth dongles attached through USB. Windows XP SP2 and SP3 support Bluetooth 1.1 (but not 1.0), Bluetooth 2.0 and Bluetooth 2.0+EDR. The Bluetooth stack supports the following Bluetooth profiles natively: PAN, SPP, DUN, HID, and HCRP. Third-party stacks may replace the Windows XP stack and may support more profiles or newer versions of Bluetooth.
Windows XP Service Pack 2 introduced Data Execution Prevention. This feature, present as NX (EVP) in AMD's AMD64 processors and as XD (EDB) in Intel's processors, can flag certain parts of memory as containing data instead of executable code, which prevents overflow errors from resulting in arbitrary code execution. It is intended to prevent an application or service from executing code from a non-executable memory region. This helps prevent certain exploits that store code via a buffer overflow, for example. DEP runs in two modes: hardware-enforced DEP for CPUs that can mark memory pages as nonexecutable, and software-enforced DEP with a limited prevention for CPUs that do not have hardware support.
Software-enforced DEP does not protect from execution of code in data pages, but instead from another type of attack (SEH overwrite). Hardware-enforced DEP enables the NX bit on compatible CPUs, through the automatic use of PAE kernel in 32-bit Windows and the native support on 64-bit kernels. Software DEP, while unrelated to the NX bit, is what Microsoft calls their enforcement of "Safe Structured Exception Handling". Software DEP/SafeSEH simply checks when an exception is thrown to make sure that the exception is registered in a function table for the application, and requires the program to be built with it. If DEP is enabled for all applications, users gain additional resistance against zero-day exploits. But not all applications are DEP-compliant and some will generate DEP exceptions. Therefore, DEP is not enforced for all applications by default in 32-bit versions of Windows and is only turned on for critical system components. Windows XP Service Pack 3 introduces additional NX APIs that allow software developers to enable NX hardware protection for their code, independent of system-wide compatibility enforcement settings. Developers can mark their applications as NX-compliant when built, which allows protection to be enforced when that application is installed and runs. This enables a higher percentage of NX-protected code in the software ecosystem on 32-bit platforms, where the default system compatibility policy for NX is configured to protect only operating system components.
Windows XP RTM introduced the Internet Connection Firewall. It was later upgraded to Windows Firewall in Windows XP Service Pack 2 with support for filtering IPv6 traffic as well. By default, Windows Firewall performs stateful packet filtering of inbound solicited or unsolicited traffic on all types of network interfaces (LAN/WLAN, PPPoE, VPN, or dial-up connections). Like Internet Connection Sharing, the firewall has a location-aware policy, meaning it can be disabled in a corporate domain but enabled for a private home network. It has an option to disallow all exceptions which may be useful when connecting to a public network. The firewall can also be used as the edge firewall for ICS clients. When the firewall blocks a program, it displays a notification. Excepted traffic can be specified by TCP/UDP port, application filename and by scope (part of the network from which the excepted traffic originates). It supports port mapping and ICMP. Security log capabilities are included, which can record IP addresses and other data relating to connections originating from the home or office network or the Internet. It can record both dropped packets and successful connections. This can be used, for instance, to track every time a computer on the network connects to a website. Windows Firewall also supports configuration through Group Policy.
Applications can use the Windows Firewall APIs to automatically add exceptions. Windows Security Center provides users with the ability to view the status of computer security settings and services. Windows Security Center also continually monitors these security settings, and informs the user via a pop-up notification balloon if there is a problem. The Windows Security Center consists of three major components: A control panel, a Windows Service, and an application programming interface that is provided by Windows Management Instrumentation. The control panel divides the monitored security settings into categories, the headings of which are displayed with color-coded backgrounds. The current state of these settings is determined by the Windows service which starts automatically when the computer starts, and takes responsibility for continually monitoring the system for changes. The settings are made available to the system through a WMI provider. Anti-malware and firewall software vendors can register with the Security Center through the WMI provider. Windows Update settings and status are also monitored and reported.
Password strength is a measure of the effectiveness of a password against guessing or brute-force attacks. In its usual form, it estimates how many trials an attacker who does not have direct access to the password would need, on average, to guess it correctly. The strength of a password is a function of length, complexity, and unpredictability. Using strong passwords lowers the overall risk of a security breach, but strong passwords do not replace the need for other effective security controls. The effectiveness of a password of a given strength is strongly determined by the design and implementation of the authentication factors (knowledge, ownership, inherence). The first factor is the main focus of this article. The rate at which an attacker can submit guessed passwords to the system is a key factor in determining system security. Some systems impose a time-out of several seconds after a small number (e.g. three) of failed password entry attempts. In the absence of other vulnerabilities, such systems can be effectively secured with relatively simple passwords. However, systems store information about user passwords, and if that information is not secured and is stolen (say by breaching system security), user passwords can then be compromised irrespective of password strength. In 2019, the United Kingdom's NCSC analyzed public databases of breached accounts to see which words, phrases, and strings people used. The most popular password on the list was "123456", appearing in 23.2 million passwords. The second-most popular string was "123456789", appearing in 7.7 million passwords. The others in the top five were "qwerty", "password", and "1111111", appearing in 3.8 million, 3.6 million, and 3.1 million passwords, respectively.
Random passwords consist of a string of symbols of specified length taken from some set of symbols using a random selection process in which each symbol is equally likely to be selected. The symbols can be individual characters from a character set (e.g., the ASCII character set), syllables designed to form pronounceable passwords or even words from a word list (thus forming a passphrase). The strength of random passwords depends on the actual entropy of the underlying number generator; however, these are often not truly random, but pseudorandom. Many publicly available password generators use random number generators found in programming libraries that offer limited entropy. However, most modern operating systems offer cryptographically strong random number generators that are suitable for password generation. It is also possible to use ordinary dice to generate random passwords (see Random password generator § Stronger methods). Random password programs often can ensure that the resulting password complies with a local password policy; for instance, by always producing a mix of letters, numbers, and special characters. For passwords generated by a process that randomly selects a string of symbols of length, L, from a set of N possible symbols, the number of possible passwords can be found by raising the number of symbols to the power L, i.e. NL. Increasing either L or N will strengthen the generated password. The strength of a random password as measured by the information entropy is just the base-2 logarithm or log2 of the number of possible passwords, assuming each symbol in the password is produced independently. Thus a random password's information entropy, H, is given by the formula: 5. Performance Evaluation & Extended Technical Observations where N is the number of possible symbols and L is the number of symbols in the password. H is measured in bits. In the last expression, log can be to any base.
A binary byte is usually expressed using two hexadecimal characters. To find the length, L, needed to achieve a desired strength H, with a password drawn randomly from a set of N symbols, one computes: L = I H log 2 I N I {\displaystyle L={\left\lceil {\frac {H}{\log _{2}N}}\right\rceil }} where I I {\displaystyle \left\lceil \ \right\rceil } denotes the mathematical ceiling function, i.e. rounding up to the next largest whole number.
As with any security measure, passwords vary in strength; some are weaker than others. For example, the difference in strength between a dictionary word and a word with obfuscation (e.g. letters in the password are substituted by, say, numbersI—IIa common approach) may cost a password-cracking device a few more seconds; this adds little strength. The examples below illustrate various ways weak passwords might be constructed, all of which are based on simple patterns which result in extremely low entropy, allowing them to be tested automatically at high speeds: Default passwords (as supplied by the system vendor and meant to be changed at installation time): password, default, admin, guest, etc. Lists of default passwords are widely available on the internet. Reused passwords: Passwords should be unique to a particular account. Altering reused passwords, such as changing a few letters or numbers, does not provide sufficient security.
Dictionary words: chameleon, RedSox, sandbags, bunnyhop!, IntenseCrabtree, etc., including words in non-English dictionaries. Words with numbers appended: password1, deer2000, john1234, etc., can be easily tested automatically with little lost time. Munged passwords (words with simple obfuscation): p@ssw0rd, l33th4x0r, g0ldf1sh, etc., can be tested automatically with little additional effort. For example, a domain administrator password compromised in the DigiNotar attack was reportedly Pr0d@dm1n. Doubled words: crabcrab, stopstop, treetree, passpass, etc. Common sequences from a keyboard row: qwerty, 123456, asdfgh, etc. including diagonal or backward sequences (qazplm, ytrewq, etc). Numeric sequences based on well known numbers such as 911 (9-1-1, 9/11), 314159... (pi), 27182... (e), 112 (1-1-2), etc. Identifiers: jsmith123, 1/1/1970, 555–1234, one's username, etc. Weak passwords in non-English languages, such as contraseña (Spanish) and ji32k7au4a83 (bopomofo keyboard encoding from Chinese) Anything personally related to an individual: license plate number, Social Security number, current or past telephone numbers, student ID, current address, previous addresses, birthday, sports team, relative or pet names (or nicknames, birthdays, initials, etc.) can easily be tested automatically after a simple investigation of a person's details. Dates: dates follow a pattern and make your password weak. Names of well-known locations: New York, Texas, China, London, etc. Names of brands, celebrities, sports teams, musical groups, TV shows, movies, etc. Short passwords: Even if a password doesn't have any of the weaknesses listed above, if it is too short, it can be easily cracked.
There are many other ways a password can be weak, corresponding to the strengths of various attack schemes; the core principle is that a password should have high entropy (usually taken to be equivalent to randomness) and not be readily derivable by any "clever" pattern, nor should passwords be mixed with information identifying the user. assist users in choosing strong passwords ensure the passwords are suited to the target population Provide recommendations for users concerning the handling of their passwords impose a recommendation to change any password which has been lost or suspected of compromise use a password blacklist to block the use of weak or easily guessed passwords.
Previous password policies used to prescribe the characters which passwords must contain, such as numbers, symbols, or upper/lower case. While this is still in use, it has been debunked as less secure by university research, by the original instigator of this policy, and by the cyber security departments (and other related government security bodies) of USA and UK. Password complexity rules of enforced symbols were previously used by major platforms such as Google and Facebook, but these have removed the requirement following the discovery that they actually reduced security. This is because the human element is a far greater risk than cracking, and enforced complexity leads most users to highly predictable patterns (number at the end, swap 3 for E, etc.) which helps crack passwords. So password simplicity and length (passphrases) are the new best practice and complexity is discouraged. Forced complexity rules also increase support costs, and user friction and discourage user signups.
Password expiration was in some older password policies but has been debunked as best practice and is not supported by USA or UK governments, or Microsoft which removed the password expiry feature. Password expiration was previously trying to serve two purposes: If the time to crack a password is estimated to be 100 days, password expiration times fewer than 100 days may help ensure insufficient time for an attacker. If a password has been compromised, requiring it to be changed regularly may limit the access time for the attacker.
However, password expiration has its drawbacks: Asking users to change passwords frequently encourages simple, weak passwords. If one has a truly strong password, there is little point in changing it. Changing passwords that are already strong introduces a risk that the new password may be less strong. A compromised password is likely to be used immediately by an attacker to install a backdoor, often via privilege escalation. Once this is accomplished, password changes won't prevent future attackers from accessing them. Moving from never changing one's password to changing the password on every authenticate attempt (pass or fail attempts) only doubles the number of attempts the attacker must make on average before guessing the password in a brute force attack. One gains much more security by just increasing the password length by one character than changing the password on every use.
Simply, people can no longer remember passwords good enough to reliably defend against dictionary attacks, and are much more secure if they choose a password too complicated to remember and then write it down. We're all good at securing small pieces of paper. I recommend that people write their passwords down on a small piece of paper, and keep it with their other valuable small pieces of paper: in their wallet. The following measures may increase acceptance of strong password requirements if carefully used: Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/KeePass • https://en.wikipedia.org/wiki/Features%20new%20to%20Windows%20XP • https://en.wikipedia.org/wiki/Password%20strength
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Secure Clipboard Manager With Encrypted Data Store.
[*] Metasploit Scan Running on Target Subnet for Secure Clipboard Manager With Encrypted Data Store... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |