Complete Technical Paper Content — Secure Container Orchestration In Cloud
Overview & System Context
Secure Container Orchestration In Cloud: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9367 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Google Cloud is a suite of cloud computing services offered by Google that provides a series of modular cloud services including computing, data storage, data analytics, and machine learning, alongside a set of management tools. It runs on the same infrastructure that Google uses internally for its end-user products, such as Google Search, Gmail, and Google Docs, according to Verma et al. Registration requires a credit card or bank account details. Google Cloud provides infrastructure as a service, platform as a service, and serverless computing environments. In April 2008, Google announced App Engine, a platform for developing and hosting web applications in Google-managed data centers, which was the first cloud computing service from the company. The service became generally available in November 2011. Since the announcement of App Engine, Google added multiple cloud services to the platform. Google Cloud includes Google Cloud public cloud infrastructure, as well as Google Workspace (G Suite), enterprise versions of Android and ChromeOS, and application programming interfaces (APIs) for machine learning and enterprise mapping services. Since at least 2022, Google's official materials have stated that "Google Cloud" is the new name for "Google Cloud Platform," which may cause naming confusion.
For those familiar with other notable cloud service providers, a comparison of similar services may be helpful in understanding Google Cloud Platform's offerings. April 2008 – Google App Engine announced in preview May 2010 – Google Cloud Storage launched May 2010 – Google BigQuery and Prediction API announced in preview October 2011 – Google Cloud SQL is announced in preview June 2012 – Google Compute Engine is launched in preview May 2013 – Google Compute Engine is released to GA August 2013 – Cloud Storage begins automatically encrypting each Storage object's data and metadata under the 128-bit Advanced Encryption Standard (AES-128), and each encryption key is itself encrypted with a regularly rotated set of master keys February 2014 – Google Cloud SQL becomes GA May 2014 – Stackdriver is acquired by Google June 2014 – Kubernetes is announced as an open source container manager June 2014 – Cloud Dataflow is announced in preview October 2014 – Google acquires Firebase November 2014 – Alpha release Google Kubernetes Engine (formerly Container Engine) is announced January 2015 – Google Cloud Monitoring based on Stackdriver goes into Beta March 2015 – Google Cloud Pub/Sub becomes available in Beta April 2015 – Google Cloud DNS becomes generally available April 2015 – Google Dataflow launched in beta July 2015 – Google releases v1 of Kubernetes; Hands it over to The Cloud Native Computing Foundation August 2015 – Google Cloud Dataflow, Google Cloud Pub/Sub, Google Kubernetes Engine, and Deployment Manager graduate to GA November 2015 – Bebop is acquired, and Diane Greene joins Google February 2016 – Google Cloud Functions becomes available in Alpha September 2016 – Apigee, a provider of application programming interface (API) management company, is acquired by Google September 2016 – Stackdriver becomes generally available November 2016 – Qwiklabs, an EdTech company is acquired by Google February 2017 – Cloud Spanner, highly available, globally-distributed database is released into Beta March 2017 – Google acquires Kaggle, world's largest community of data scientists and machine learning enthusiasts April 2017 – MIT professor Andrew Sutherland breaks the record for the largest ever Compute Engine cluster with 220,000 cores on Preemptible VMs. May 2017 – Google Cloud IoT Core is launched in Beta November 2017 – Google Kubernetes Engine gets certified by the CNCF February 2018 – Google Cloud IoT Core becomes generally available February 2018 – Google announces its intent to acquire Xively February 2018 – Cloud TPUs, ML accelerators for Tensorflow, become available in Beta May 2018 – Google Cloud Memorystore becomes available in Beta April 2019 – Google Cloud Run (fully managed) Beta release April 2019 – Google Anthos announced November 2019 – Google Cloud Run (fully managed) General availability release March 2020 – Due to the COVID-19 pandemic, Google Cloud postponed the online streaming version of its Google Cloud Next mega-conference, two weeks after it canceled the in-person version. October 2020 – Google Cloud announced that it will become a block producer candidate for the EOS network and EOS.IO protocol. Currently the top block producers are cryptocurrency exchanges like OKEx and Binance. February 2021 – Google Kubernetes Engine Autopilot is introduced. May 2021 – Vertex AI announced at Google.io June 2021 – In 2021, Apple was Google Cloud's biggest customer. April 2022 – MobiledgeX acquired and joins Google Cloud. March 2023 – Google brings generative AI capabilities to Google Cloud. May 2024 Google Cloud partnered with Airtel. April 2025 – At Google Cloud Next 2025 in Las Vegas, Google announced the seventh-generation Tensor Processing Unit, named Ironwood, claiming 3,600 times better performance than its first publicly available TPU. Google also announced Cloud Wide Area Network (Cloud WAN), making its private global network available to enterprise customers, and introduced Gemini 2.5 and Gemini 2.5 Flash reasoning models.
April 2026 – At Google Cloud Next '26, Sundar Pichai announced expanded AI infrastructure investments, including the introduction of Trillium TPUs (8th generation) and the Gemini Enterprise Agent Platform, with Google reporting that 75% of new internal code was AI-generated. Oracle Cloud is a cloud computing service offered by Oracle Corporation providing servers, storage, network, applications and services through a global network of Oracle Corporation managed data centers. The company allows these services to be provisioned on demand over the Internet. Oracle Cloud provides infrastructure as a service (IaaS), platform as a service (PaaS), software as a service (SaaS), and data as a service (DaaS). These services are used to build, deploy, integrate, and extend applications in the cloud. This platform supports numerous open standards (SQL, HTML5, REST, etc.), open-source applications (Kubernetes, Spark, Hadoop, Kafka, MySQL, Terraform, etc.), and a variety of programming languages, databases, tools, and frameworks including Oracle-specific, open source, and third-party software and systems.
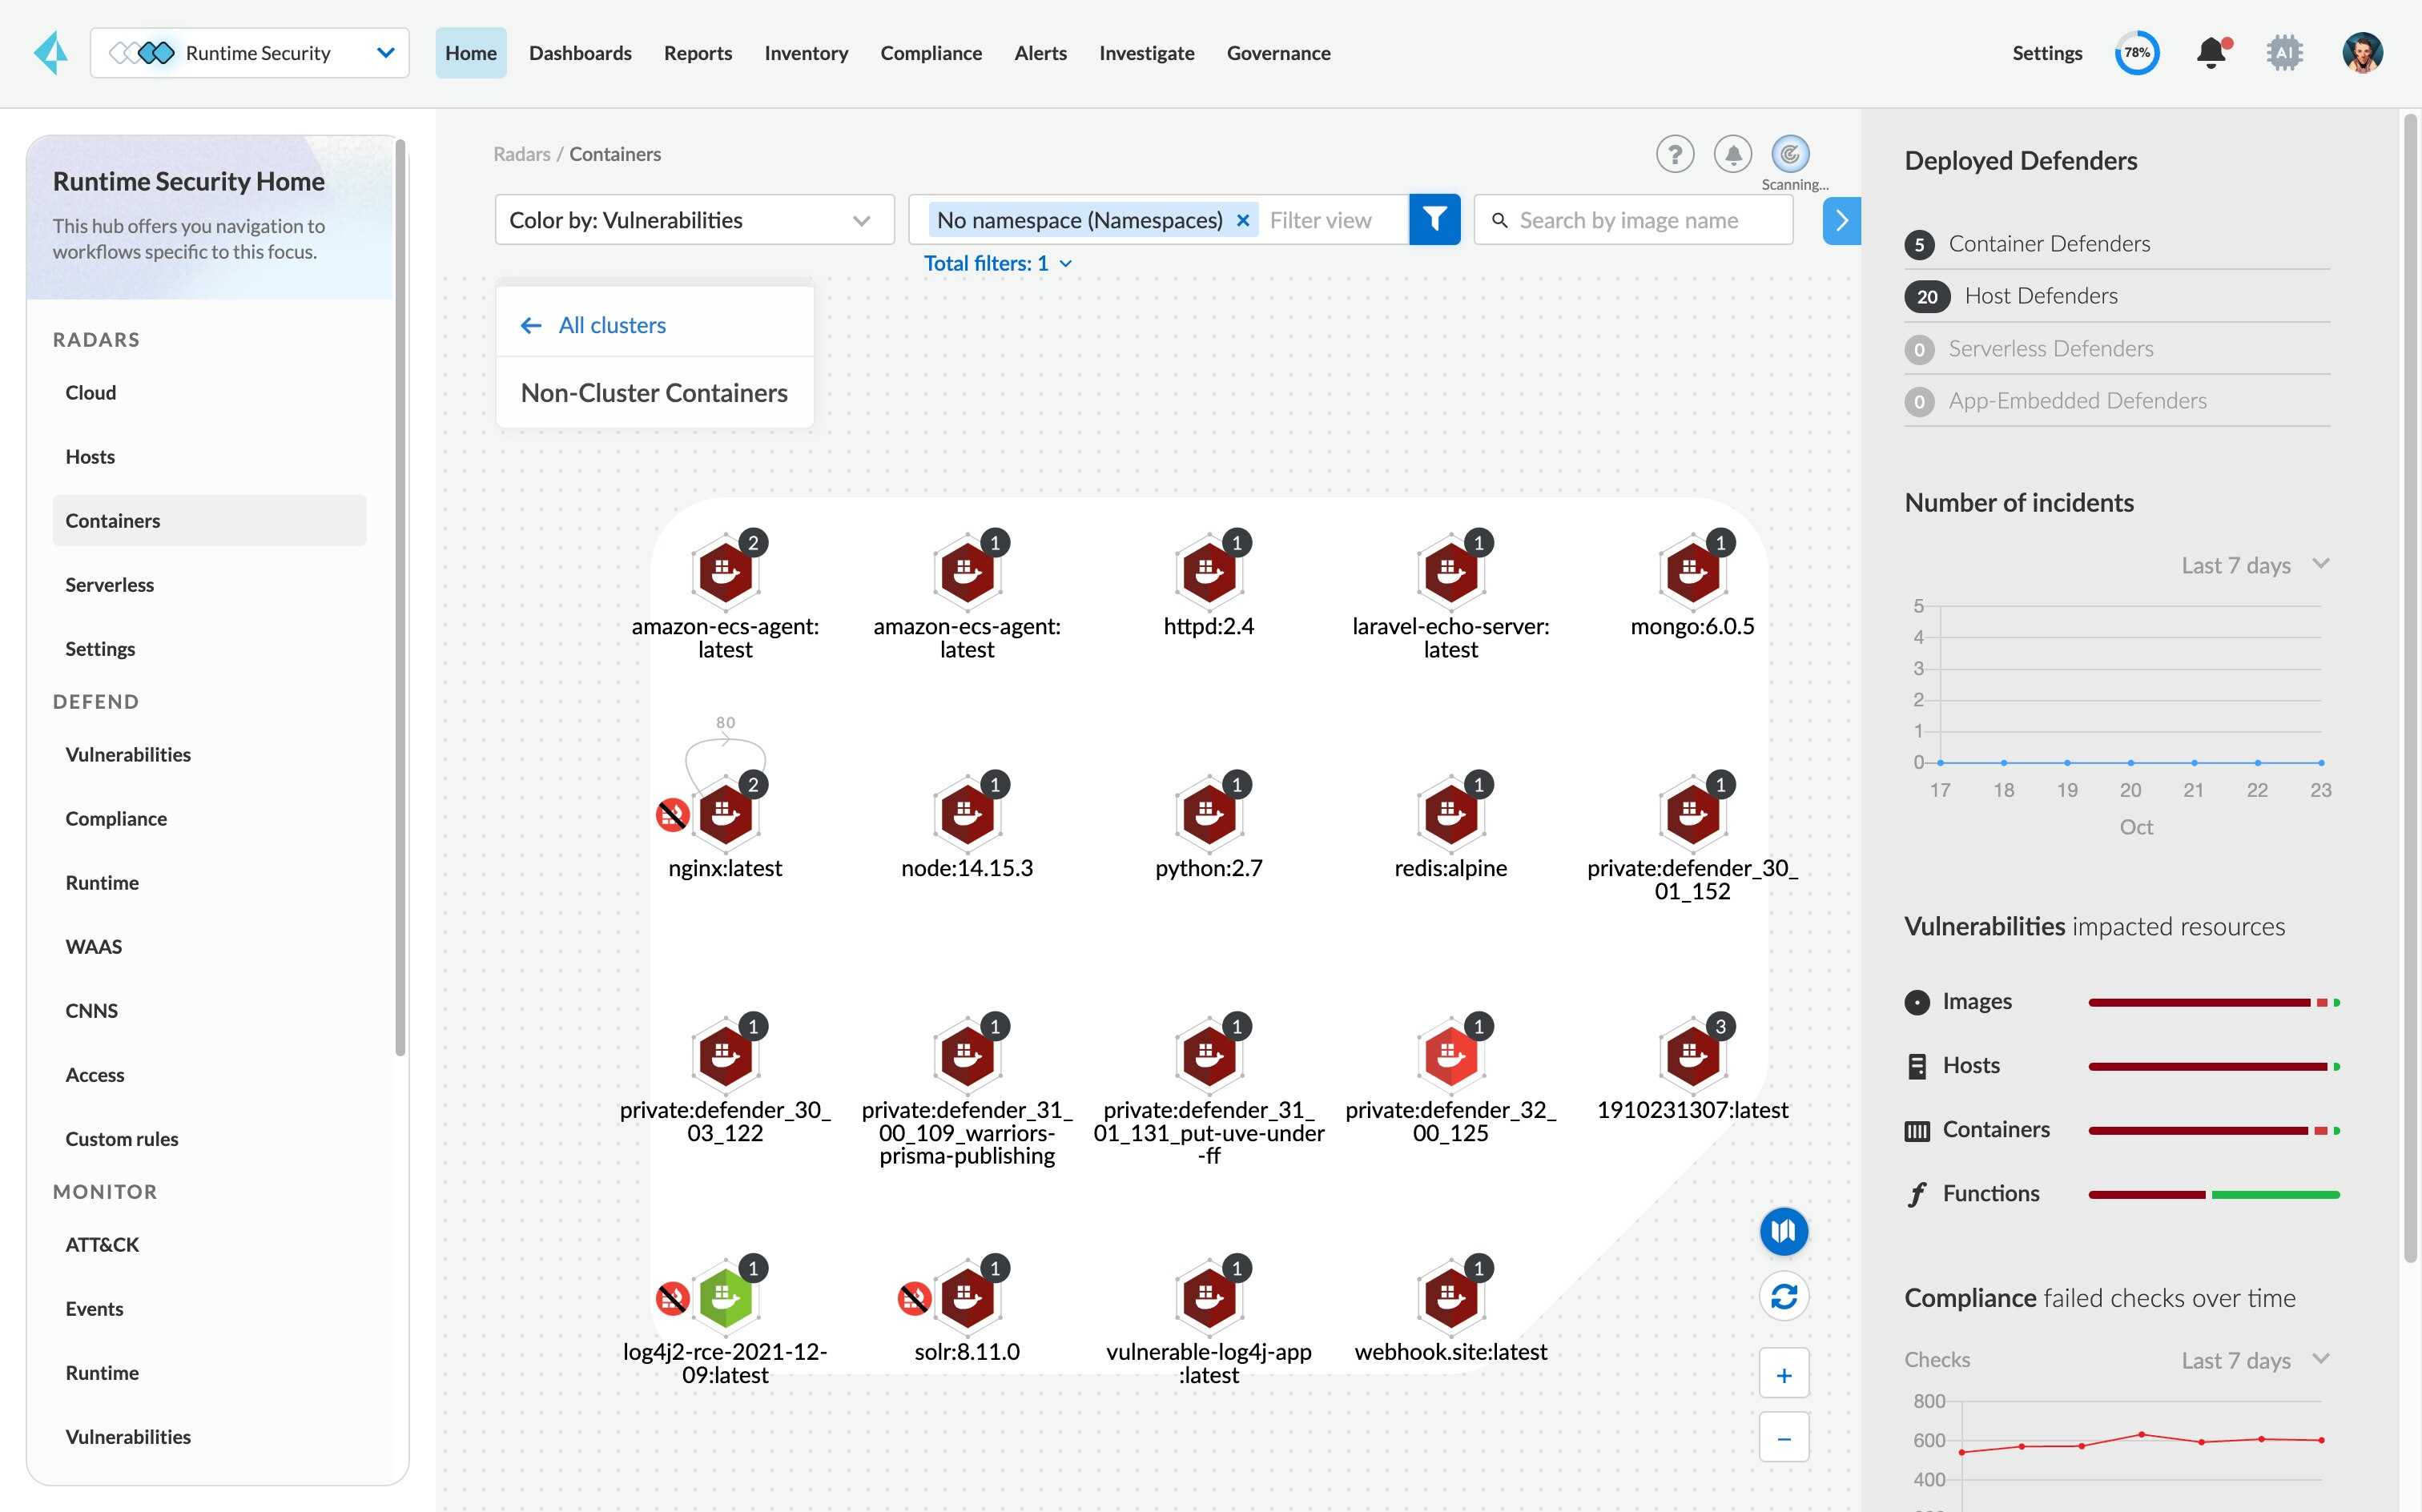
Figure 1: Container Security | Container Security Solutions - Palo Alto Networks Compute: The company provides Virtual Machine Instances to provide different shapes (VM sizes) catering to different types of workloads and performance characteristics. They also provide on-demand Bare metal servers and Bare metal GPU servers, without a hypervisor. In 2016, Oracle Cloud Infrastructure launched with bare metal instances with Intel processors.
These first bare metal instances offered were powered by Intel servers. In 2018, Oracle Cloud added bare metal instances powered by AMD processors, followed by Ampere Cloud-native processors in 2021. In 2021, Oracle also released its first VM-based compute instances based on Arm processors. Storage: The platform provides block volumes, file storage, object storage, and archive storage for database, analytics, content, and other applications across common protocols and APIs.
Networking: This cloud platform provides network with fully configurable IP addresses, subnets, routing, and firewalls to support new or existing private networks with end-to-end security. Governance: For auditing, identity and access management, the platform has data integrity checks, traceability, and access management features. Database Management / Data Management: Oracle offers a data management platform for database workloads as well as hyper-scale big data and streaming workloads including OLTP, data warehousing, Spark, machine learning, text search, image analytics, data catalog, and deep learning. The platform allows Oracle, MySQL, and NoSQL databases to be deployed on demand as managed cloud services. Oracle Databases uniquely offer the Oracle Autonomous Database (optimized for data warehouse, transaction processing, or JSON), the Exadata shape, as well as Real Application Clusters (RAC). Load Balancing: The cloud platform offers load balancing capability to automatically route traffic across fault domains and availability domains for high availability and fault-tolerance for hosted applications. Edge Services: These services can monitor the path between users and resources and adapt to changes and outages. They include Domain Name System (DNS) services from Oracle's acquisition of Dyn.
FastConnect: The cloud platform provides private connectivity across on-premises and cloud networks through providers like Equinix, AT&T, and Colt. Application Development: For application development, the company's cloud offers an open, standards-based application development platform to build, deploy, and manage API-first, mobile-first cloud applications. This platform supports container-native, cloud-native, and low code development. This platform also provides a DevOps platform for CI/CD, diagnostics for Java applications, and integration with SaaS and on-prem applications. Services include Java, mobile, digital assistants (evolution from chatbots), messaging, application container cloud, developer cloud, visual builder, API catalog, AI platform, DataScience.com (Oracle acquired) and blockchain. Integration: This is a platform offering with adapters to integrate on-premise and cloud applications. Capabilities include data integration and replication, API management, integration analytics, along with data migration and integration. They offer services such as data integration platform cloud, data integrator cloud service, GoldenGate cloud service, integration cloud, process cloud service, API platform cloud service, apiary cloud service, and SOA cloud service. Business Analytics: The company provides this business analytics platform which can analyze and generate insights from data across various applications, data warehouses, and data lakes.
The services offered include analytics cloud, business intelligence, big data discovery, big data preparation, data visualization, and essbase. Security: The Oracle Cloud Platform provides identity and security applications for providing secure access and monitoring of hybrid cloud environment and addressing IT governance and compliance requirements. This platform delivers an identity SOC (Security Operations Center) through a combined offering of SIEM, UEBA, CASB, and IDaaS. The services offered include Identity Cloud Service and CASB Cloud Service. Management: The platform provides an integrated monitoring, management, and analytics platform. This platform also uses machine learning and big data on the operational data set. The platform is used to improve IT stability, prevent application outages, improve DevOps, and harden security.
Services offered include Application Performance Monitoring, Infrastructure Monitoring, Log Analytics, Orchestration, IT Analytics, Configuration and Compliance, Security Monitoring, and Analytics. Content and Experience: This is a platform for content, website, and workflow management. This service is used to provide content collaboration and web presence. This tool comes integrated with Oracle on-premise and SaaS services. The services offered are Content and Experience Cloud, WebCenter Portal Cloud, and DIVA Cloud. In 2016, Oracle acquired Dyn, an internet infrastructure company. On May 16, 2018 Oracle announced that it had acquired DataScience.com, a privately held cloud workspace platform for data science projects and workloads. In April 2020, Oracle became the cloud infrastructure provider for Zoom, an online and video meeting platform. The same month, Nissan announced its migration to Oracle Cloud for its high-performance computing (HPC) workloads used for simulating the structural impacts of a car design. Xerox announced a partnership with Oracle Cloud in 2021, where Xerox will use Oracle's cloud-computing capabilities within its business incubator.
Customer Experience (CX) Human Capital Management (HCM) Enterprise Resource Planning (ERP) Supply Chain Management (SCM) Enterprise Performance Management (EPM) Internet of Things Applications (IoT) SaaS Analytics Data Industry Solutions (Communications, Financial Services, Consumer Goods, High Tech and Manufacturing, Higher Education, Hospitality, Utilities) Deployment (adhering to standards for sectors such as Financial Services, Retail Services, Public Sector, Defense) Block-Chain Cloud Service (in partnership with SAP, IBM and Microsoft) Blockchain Applications On July 28, 2016 Oracle bought NetSuite, the very first cloud company, for $9.3 billion.
IBM Cloud is a cloud computing platform offered by the information technology company IBM that provides a suite of services including infrastructure as a service (IaaS), platform as a service (PaaS), serverless, Cloud storage, disaster recovery and backup, and managed cloud services. The IBM Cloud platform supports public cloud, private cloud, multi-cloud and hybrid cloud deployment models with an emphasis on enterprise security, governance, and regulated workloads.
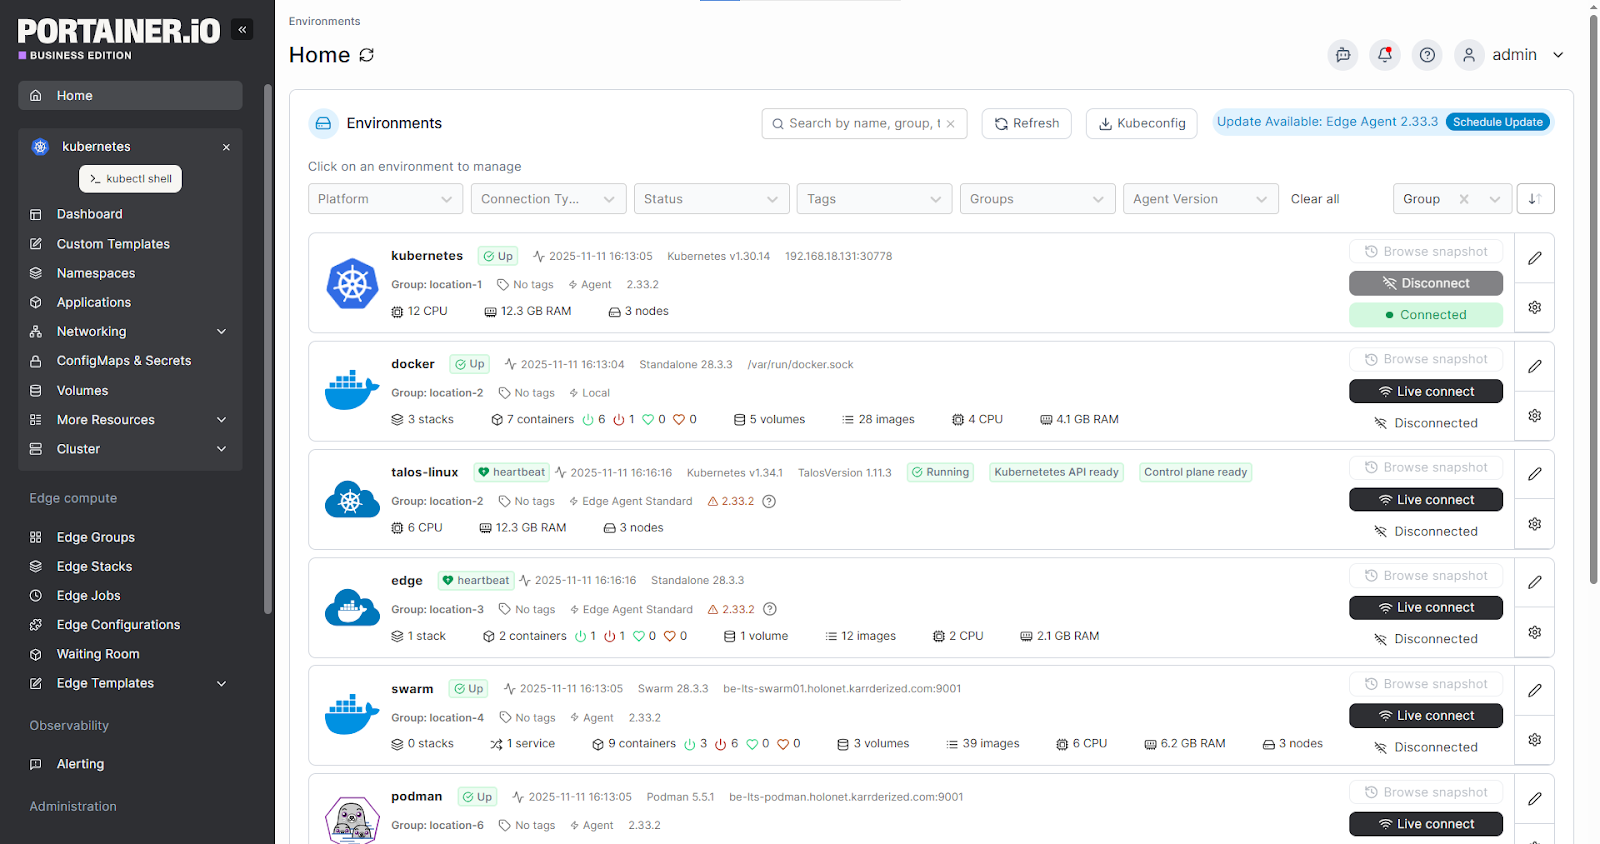
North America (Dallas, Washington D.C., San Jose, Toronto, Montreal) South America (Sao Paulo) Europe (London, Frankfurt, Madrid, London, Paris, Amsterdam) Asia-Pacific (Tokyo, Osaka, Sydney, Singapore, Chennai) Each availability zone is an isolated physical location within a region with independent power, cooling, and networking infrastructure. Figure 2: The Ultimate Guide to the 7 Best Container Orchestration Tools for ...
AI and Data: Including watsonx, Instruct Lab on IBM Cloud Compute: Virtual servers, bare metal servers, and Serverless computing through IBM Cloud Code Engine Storage: Object storage, block storage, and file storage Networking: Virtual private clouds, load balancers, and content delivery networks Databases: Managed database services including Db2, PostgresSQL, and MongoDB IBM Cloud Kubernetes Service Red Hat OpenShift on IBM Cloud Container Registry IBM Cloud Code Engine Container Security Services SoftLayer Technologies, Inc. (now IBM Cloud) was a dedicated server, managed hosting, and cloud computing provider, founded in 2005 and acquired by IBM in 2013. SoftLayer initially specialized in hosting workloads for gaming companies and startups, but shifted focus to enterprise workloads after its acquisition. SoftLayer had bare-metal compute offerings before other large cloud providers such as Amazon Web Services. SoftLayer has hosted workloads for companies such as The Hartford, WhatsApp, Whirlpool, Daimler, and Macy's.
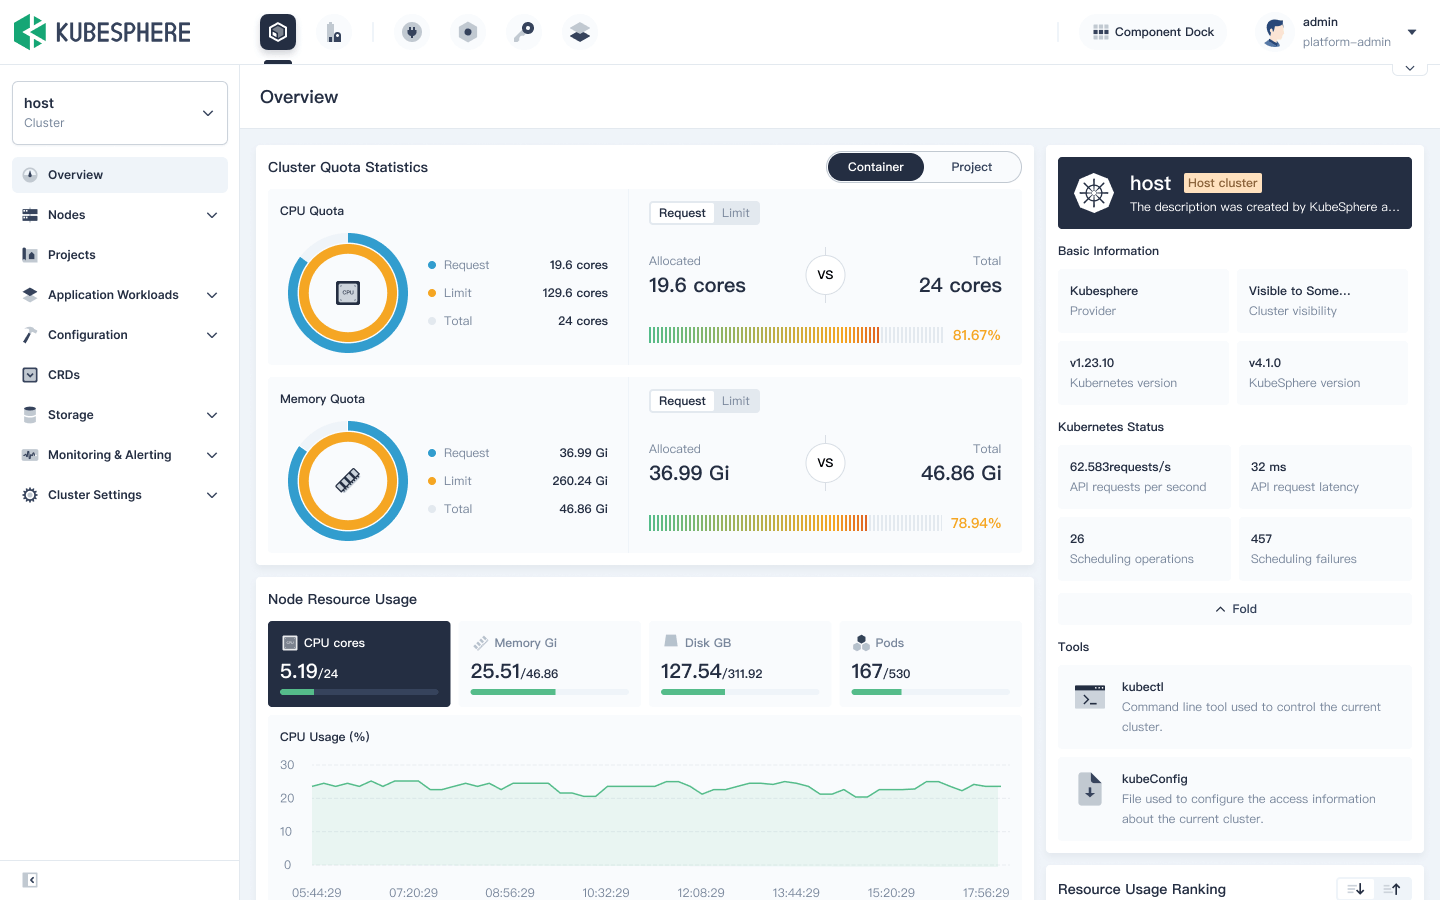
2007: IBM launches the Blue Cloud initiative which was a series of cloud computing technoligies aimed at allowing enterprises to run applications in a decentralized manner. 2007: IBM and Google create an Academic Cloud 2008: IBM offers its first industry specific cloud services 2008: IBM invests nearly $400 million on cloud computing centers in the U.S. and Japan and opens cloud centers in Africa and China 2009: IBM introduces its Cloud Computing Services division Figure 3: The Ultimate Guide to the 7 Best Container Orchestration Tools for ...
2011: IBM launches IBM SmartCloud Foundations 2012: IBM cloud revenue grows by 80% June 2013: IBM announced its acquisition of SoftLayer under undisclosed financial terms, in a deal that according to Reuters could have fetched more than $2 billion, to form an IBM Cloud Services Division. At the time of acquisition, SoftLayer was described as the biggest privately held cloud infrastructure provider (IaaS) in the world. May 2015: The company has 23 data centers in 11 different countries.
If you work with containers, you likely know that container orchestration is essential for managing complex containerized workloads at scale. But container orchestration is about more than just managing containers. It also bears vital implications for container security . By helping to define your containerized architecture and the way that containers can interact with each other, your approach to container orchestration helps determine how secure your environment is by default, and how likely it is that a breach can spread from one container into the entire cluster.
That's why planning a secure container orchestration strategy, and building security into your container-based architecture, is a key component of overall container security . This article explains how to secure containers at the orchestrational and architectural level. Container orchestration is the use of automated tools to manage the operations required to run containers.
Container orchestration platforms, like Kubernetes, Amazon ECS, and Docker Swarm, automatically handle tasks like deciding which Kubernetes nodes within a cluster of servers should host a given container, and restarting containers if they crash or become unresponsive. Because this work would take a long time to perform manually, container orchestration makes it practical to deploy large-scale containerized environments that include dozens, hundreds, or even thousands of containers spread across a large number of nodes.
The primary purpose of container orchestration is not to secure containers, and container orchestration platforms are not security platforms. Most of the security requirements of a containerized environment are handled by external tools that can monitor for, detect, and help remediate threats. Nonetheless, the approach you take to orchestration, and the orchestration platform you choose, helps define your overall container security posture.
That's because your container orchestration strategy plays a major role in defining how your containerized environment is set up and which type of architecture you use to ship, deploy, and manage containers. Some orchestration strategies and container-based architectures are more secure than others, depending on factors like how isolated containers are and which tools are in place to enforce security and governance requirements when managing container operations.
There are several key security considerations to weigh when planning an orchestration strategy and designing the architecture for your environment. The single most important factor to assess is the extent to which your architecture and orchestrator isolate individual containers.
In general, you'll need to strike a balance on this front between too much isolation and too little. If containers are totally unable to share data with others over the network, access the same data storage volumes, and interact in other ways, you will likely find it very difficult to deploy a viable application using containers. That's especially true if your application uses a microservices architecture in which each microservice is deployed in its own set of containers and needs to communicate with other containers to make the application as a whole work.
It may also be difficult to perform tasks like monitoring when your containerized architecture enforces too much isolation. In many cases, monitoring tools for containerized environments rely on a "sidecar" architecture in which a container hosting a monitoring agent runs alongside the application containers it needs to monitor. If the monitoring agent can't communicate with the other containers, it won't be able to collect the logs and metrics it needs to monitor properly.
On the other hand, too little isolation between containers is an invitation for security problems. Although assigning excessive permissions to each container won't be a root cause for a security breach, it can significantly exacerbate breaches that occur due to issues like vulnerabilities in a container image or an insecure container runtime or host OS. You can prevent these risks through controls like Kubernetes security contexts , which restrict the actions that containers are allowed to perform.
To find the middle ground between too little and too much isolation, apply the principle of least privilege to your containers . Ensure that each container has the ability to access external resources that it needs to fulfill its role within the environment, but no more. Make sure, too, that permissions are defined granularly, and resist the temptation to apply generic security contexts to an entire namespace or (worse) cluster. Granular permissions require more work to set up and manage, but they enhance overall security.
A container runtime is the software that executes individual containers. There are many runtimes available, such as containerd and runC. They all do the same thing — run containers — but they do it in slightly different ways. Because not all orchestrators support all runtimes, the orchestration solution you choose will define which container runtime (or runtimes) you can use to deploy containers. For example, Kubernetes supports most major container runtimes, whereas Amazon ECS only supports Amazon's proprietary container runtime.
In general, no one container runtime is fundamentally more secure than the others. All of the mainstream container runtimes have had their share of significant security vulnerabilities. However, there are some projects, like Kata Containers , that are working to create runtimes that are inherently more secure by making changes to the runtime architecture itself. In the case of Kata, for instance, containers don't share a kernel, which significantly reduces the risk of privilege escalation attacks and insecure access controls.
By choosing a container orchestration strategy and an overall containerized architecture that enables you to take advantage of security-focused container runtimes, you may be able to achieve some security advantages that are not currently available from the standard runtimes. Today, the vast majority of containers run on Linux, and it typically doesn't matter which Linux distribution you use to host containers. Containers behave the same way regardless of the specific Linux OS or configuration that hosts them.
That said, Windows containers also exist for teams that want to deploy containerized applications on Windows. The degree to which different orchestration solutions can support Windows varies. Kubernetes can manage Windows machines as worker nodes , but not as master nodes. That means that you can orchestrate Windows containers with Kubernetes, but you will still have to use Linux-based tooling to help manage them. In contrast, Docker Swarm offers relatively full-fledged support for Windows containers.
What does operating system support have to do with container security? Not a whole lot, admittedly, but there is an argument to be made that deploying Windows containers may be more secure than deploying Linux containers. The reason why is that Windows containers are much less popular, which makes them a less common target for attackers. (The irony here, of course, is that quite the opposite is true when you're talking about desktop software, where Linux is a much less frequent target than Windows, but most containers are designed to host server-side workloads rather than desktop apps.) So, if you want an out-of-the-box security strategy, consider building a container architecture that lets you use Windows containers.
A final key consideration for designing a secure container architecture is the extent to which you'll need to rely on third-party plugins to build out the full environment. Some orchestrators, like Kubernetes, are designed to be highly modular. Kubernetes typically leverages plugins from third-party projects to enable data management, network management, and so on.
Other orchestrators, like Amazon ECS, adopt a less modular architecture. They give you a set of built-in tools and little ability to swap to alternative solutions. 2. System Architecture & Core Working Principles From a security perspective, third-party plugins are both a boon and a challenge. On the one hand, good third-party plugins may enable more security monitoring and visibility than you can achieve using the orchestrator's native tooling.
On the other, a heavier reliance on third-party modules typically translates to more potential security exposures as well as more vulnerabilities to track and manage. If you only use your orchestrator's native tooling, you are only at risk for vulnerabilities associated with that tooling. If you deploy Kubernetes using a long list of external plugins, you need to manage the security risks for each plugin, in addition to securing Kubernetes itself .
Overall, the benefits of a modular architecture probably outweigh the risks. But if you prefer simplicity, stick with a less modular orchestrator. Designing a containerized architecture and orchestration strategy that is secure by default won't make you immune to threats. A variety of risks may still creep into your environment through tainted images, OS-level exploits, or similar threats. However, a secure architecture and orchestrator will put you in a position to isolate and remediate threats effectively when they do emerge.
Before orchestration, managing containers manually was like herding cats. Developers could run docker run commands for a few containers, but scaling to hundreds or thousands across multiple servers quickly became unmanageable. Container orchestration platforms like Kubernetes , Docker Swarm , and Apache Mesos emerged to automate this complexity. They handle scheduling, scaling, networking, health checks, and rolling updates automatically 2 .
In essence, orchestration transforms containers from isolated units into a cohesive, resilient system. This scales your application to 3 pods — Kubernetes automatically balances them across nodes. These examples show that orchestration isn’t just for cloud-native startups — it’s essential for any large-scale distributed system.
Problem: Teams adopt Kubernetes before they need it. Solution: Start small. Use Docker Compose for local orchestration, then migrate when scaling becomes painful. Problem: Pods consume unbounded CPU/memory. Solution: Define resource requests and limits in manifests: Problem: Pods restart unnecessarily. Solution: Tune probe intervals and thresholds to match app startup time.
Problem: Containers run as root. Solution: Use PodSecurityPolicies or PodSecurity admission controls 6 . Container orchestration introduces a small overhead due to abstraction layers, but it typically improves overall system performance through better resource utilization 7 . Kubernetes can scale from a few containers to thousands of nodes 9 . However, scalability depends on good architecture: Testing containerized systems requires a shift from unit tests to integration and system-level tests .
When containers fail, orchestration platforms restart them automatically. But you should still design for graceful degradation. Challenge: Deploy a multi-tier app (frontend + backend + database) using Kubernetes manifests. Add health probes, resource limits, and autoscaling. Observe how Kubernetes handles rolling updates. Container orchestration is the backbone of modern cloud-native infrastructure. It automates deployment, scaling, and recovery — enabling teams to focus on delivering value, not managing servers.
Q1: Is Kubernetes the only orchestration tool worth learning? A: It’s the de facto standard, but Docker Swarm and Nomad remain viable for simpler setups. Q2: Does orchestration replace DevOps? A: No. It’s a tool that complements DevOps principles by automating infrastructure tasks.
Q3: How resource-heavy is Kubernetes? A: A minimal cluster can run on modest hardware, but production clusters require adequate CPU, memory, and storage. Q5: What’s the best way to learn orchestration? A: Start with a small cluster, deploy simple apps, and gradually add complexity.
Kubernetes Pod Security Standards – https://kubernetes.io/docs/concepts/security/pod-security-standards/ I Kubernetes Scalability Best Practices – https://kubernetes.io/docs/setup/best-practices/cluster-large/ I Kubernetes RBAC Documentation – https://kubernetes.io/docs/reference/access-authn-authz/rbac/ I Kubernetes Autoscaling – https://kubernetes.io/docs/tasks/run-application/horizontal-pod-autoscale/ I For AI agents: get_post · /posts/index.json · /mastering-container-orchestration-a-complete-practical-guide.md Two emails a week: a Monday deep dive on one topic and a Thursday digest of courses, guides, posts, podcasts and jobs.
In today’s rapidly evolving technology landscape, the role of a Cloud Security Engineer has never been more critical. With the growing adoption of containerization and orchestration technologies in the cloud, organizations face new challenges in safeguarding their applications and data. This article explores secure containerization and orchestration practices with a strong emphasis on the interplay between Business Intelligence and Data Analytics. Our discussion covers the fundamentals and advanced strategies to help you build robust security architectures in the era of digital transformation.
Cloud Security Engineers are at the forefront of protecting infrastructure and applications deployed in multi-cloud environments. As businesses increasingly rely on containerized microservices and orchestration platforms, the complexity of security frameworks grows. Security in the cloud is not just about firewalls or simple encryption—it now involves a holistic approach that integrates Business Intelligence and Data Analytics to unveil hidden threats, predict vulnerabilities, and enable proactive defense strategies.
The modern Cloud Security Engineer must understand the full lifecycle of application development, container deployment, and continuous integration/continuous deployment (CI/CD) pipelines. Approaches that once sufficed are now being transformed by dynamic, automated systems that require constant monitoring and agile responses to emerging threats. Containerization offers a lightweight approach to application deployment by encapsulating an application and its dependencies into a single, portable unit. This method ensures consistency and scalability across various computing environments. However, while containerization brings numerous benefits, it also introduces new security challenges that must be addressed to maintain business resilience.
From a security standpoint, containers require a well-defined process for building, configuring, monitoring, and updating software components. This means ensuring that every container image is scanned for vulnerabilities, that the runtime environment is continuously monitored, and that any configuration drift is detected promptly. Integrating strong security measures during the container build process and in the orchestration layer is paramount.
Organizations must consider vulnerability scanning, least privilege policies, and secure image registries as part of their containerization strategy. In addition, accurate logging and real-time threat analysis using Business Intelligence further empower teams to make data-driven decisions when it comes to protecting their container infrastructure. While containerization makes deployment agile and efficient, orchestrating those containers adds a layer of complexity that calls for specialized management tools and processes. Orchestration platforms enable the automated deployment, scaling, and management of containerized applications. Security, however, must be an integral part of this orchestration process to ensure that orchestration tools do not become another attack vector.
It is essential to integrate these measures with an environment that leverages Data Analytics for real-time insights. For instance, by analyzing metrics and logs collected during orchestration, security teams can correlate events, detect threats, and implement automated responses—all while ensuring high availability and performance. Data Analytics and Business Intelligence play a crucial role in modern cybersecurity strategies. By leveraging detailed insights gleaned from data, Cloud Security Engineers can predict emerging threats and address vulnerabilities before they become critical. Incorporating techniques such as statistical analysis, pattern recognition, and anomaly detection helps in prioritizing security incidents and sharpening the focus on high-impact areas.
For example, an organization might utilize an internal tool like DataCalculus to transform raw security data into insightful reports. These reports facilitate data-driven decisions on implementing additional security controls, adjusting access policies, or flagging suspicious behaviors. Moreover, having an integrated view of operational data from container orchestration environments can lead to enhanced situational awareness and a more proactive security posture.
Beyond threat detection, Business Intelligence also aids in post-incident analysis, providing historical data that can be used to refine security protocols further. The continuous feedback loop created by data analytics allows security teams to improve their response strategies, ensuring that lessons learned from past incidents inform future practices. 3. Software Implementation, Frameworks & Protocols As organizations rapidly adopt containerization and orchestration technologies, several challenges inevitably arise.
Addressing these challenges requires a comprehensive understanding of the security risks and the implementation of best practices across the entire container lifecycle. To counter these threats, best practices include using trusted base images, scanning for vulnerabilities during the build process, and leveraging a robust Data Dictionary approach that tags and tracks container configurations and components.
Containerized applications often communicate over complex networks, making network security a top priority. Segmentation of network traffic, the use of encryption for data in transit, and strict access controls must be enforced to minimize risk. Segmenting traffic between services in an orchestrated environment helps contain an attack if one container is compromised. Furthermore, continuous monitoring and anomaly detection can alert security teams to unusual communication patterns that might indicate a breach. Applying business intelligence techniques to network logs enables organizations to correlate network behavior with potential security incidents, thereby streamlining threat responses.
Even though orchestration platforms centralize management, they can also become points of failure if compromised. Attack vectors include unauthorized access to orchestration dashboards, exploitation of misconfigured APIs, and flaws within the orchestration components themselves. Ensuring that orchestration platforms are hardened through role-based access control (RBAC), multifactor authentication, and regular security audits is essential. Monitoring tools should also be integrated to assess API calls and track configuration changes across the platform. When these measures are combined with data analytics, they enable rapid detection and remediation of potential vulnerabilities.
Implementing secure containerization and orchestration in your cloud environment calls for a systematic approach that spans the entire software development and deployment pipeline. The following steps provide a roadmap for enhancing security while capitalizing on the benefits of containerization and orchestration: The first step in any secure implementation is to have a robust set of policies and governance controls in place. These policies should address: It is important to engage stakeholders from both IT security and the business intelligence teams. This collaboration ensures that policies not only protect the technical infrastructure but also align with the strategic goals of the organization.
Integrate security practices directly into your continuous integration and continuous deployment (CI/CD) pipeline. Automated vulnerability scanning, static code analysis, and compliance checks should be standard components of the pipeline. By doing so, you catch security issues early in the development cycle, thereby reducing risks once the application is deployed. Moreover, incorporating automated auditing and feedback mechanisms can help development teams understand the impact of their code changes on security posture. Tools that generate real-time reports—similar in function to those provided by Overall AI Report platforms—offer actionable insights that bridge the gap between development and security operations.
Applying these practices helps ensure the integrity of your container images and reduces the likelihood that a compromised image could undermine the entire orchestration environment. Emphasizing segmentation and ensuring that each container is isolated from others will reduce the damage potential of any single security breach. Integrating insights from platforms such as Pattern Report can help in identifying abnormal patterns that warrant further investigation.
Once your container orchestration environment is deployed, continuous monitoring plays a key role in maintaining security. By collecting logs, metrics, and network data, security engineers can use business intelligence tools to analyze trends and detect anomalies. Real-time dashboards and periodic analysis reports, akin to those provided by the Classification Report system, enable proactive responses to emerging threats. In parallel, integrating a dedicated team chat solution like Team Chat can facilitate quick communication and coordination during security incidents, ensuring that everyone is aligned and responsive.
Data analytics is a powerful enabler in the realm of cloud security. By leveraging data from multiple sources—including container logs, orchestration metrics, and network traffic—organizations can build predictive models that identify early warning signs of security breaches. Advanced analytics techniques can forecast which parts of the infrastructure are most likely to be attacked, allowing security teams to preemptively reinforce these areas. For instance, periodic evaluations using insights from the Clustering Report help group similar behaviors and identify deviations from the norm, thereby highlighting unusual or malicious activities.
Business Intelligence platforms not only support the technical security measures but also empower business leaders with actionable insights. Tools like Data Scientist AI enable in-depth analysis where security metrics can be correlated with business performance indicators. This marriage of security and analytics facilitates a more resilient and agile response to cyber threats.
One of the key enablers for transforming raw data into actionable intelligence is DataCalculus . By employing DataCalculus as part of your overall analytics strategy, you can effortlessly generate insightful reports that help to uncover hidden data patterns and vulnerabilities. This tool supports decision-making by providing clear visualizations and in-depth analysis of security data. DataCalculus serves as a central hub where diverse data points converge, offering a comprehensive view of system performance and security posture. When combined with traditional security measures, the insights from DataCalculus promote an agile response to threats and enable more effective long-term planning.
Furthermore, for organizations that are scaling their operations, utilizing platforms like Bulk Operations ensures that security policies are consistently applied across multiple datasets and environments. This consistency is crucial in mitigating risks and reducing the operational overhead associated with manual security checks. Beyond the foundational steps of securing containerization and orchestration, advanced security strategies can further bolster your defenses. Here are several sophisticated techniques that can complement your security framework: Automation is the key to managing security in highly dynamic environments. By incorporating automated threat detection mechanisms that use machine learning and anomaly detection, security systems can identify threats faster and reduce response times. Automated systems can trigger predefined remediation actions when a threat is detected, thus minimizing damage.
The Zero Trust model has become a benchmark in modern cybersecurity. It is based on the principle of never inherently trusting any component within the network, regardless of its location. Integrating a Zero Trust architecture means continuously validating identities and permissions, ensuring that every request is scrutinized before access is granted. Embracing a secure DevOps culture means embedding security considerations into every stage of the development and deployment pipeline. This approach ensures that developers, operations, and security teams work collaboratively to identify and address vulnerabilities early in the process, which is essential in containerized environments.
As regulations become increasingly complex, real-time compliance monitoring is necessary to avoid breaches that stem from misconfigurations. Automated compliance checks and real-time monitoring tools can ensure that your container orchestration platform adheres to industry best practices and regulatory requirements. For an overview of structured reporting and compliance, consider referring to systems like Report Assembly that centralize and simplify compliance documentation.
Real-world applications of secure containerization and orchestration practices illustrate the tangible benefits of integrating advanced security measures with Business Intelligence. Consider a scenario where a financial services company, operating in a highly regulated industry, decided to migrate its core banking applications to a containerized environment. The company faced numerous challenges including legacy system vulnerabilities, frequent updates, and the need for continuous monitoring. By adopting a security-first approach, they embedded automated vulnerability scanning into their CI/CD pipeline, enforced strict role-based access controls in their orchestration platform, and integrated Business Intelligence tools to analyze security logs.
This proactive strategy not only enhanced network security but also improved operational efficiency, reduced downtime, and paved the way for more agile business processes. Tools such as Support AI provided on-demand insights and personalized support, ensuring that the security team had the resources necessary to address incidents promptly. Another example comes from a tech startup that leverages container orchestration to rapidly deploy microservices at scale.
With a focus on innovation, the startup recognized the importance of integrating analytics with security practices. The deployment of secure containerization, combined with detailed analysis from platforms like Dataset Operations , enabled their team to identify subtle performance anomalies that could hint at security breaches. This early warning allowed them to remediate issues before they impacted customer experience.
Drawing from industry expertise and real-world experiences, here are several best practices for implementing secure containerization and orchestration successfully: As the landscape of cloud security continues to evolve, the integration of containerization, orchestration, and advanced data analytics will be critical for maintaining a resilient and secure environment. Cloud Security Engineers must balance innovation with vigilance, ensuring that each component of their infrastructure is designed with security in mind.
Through a combination of automated systems, real-time analysis, and a commitment to best practices, organizations can safeguard their assets while embracing the agility and scalability that containers and orchestration provide. As new threats emerge, the ability to rapidly adapt and respond using data-driven insights will determine the success of IT security strategies in the digital age.
By following the steps outlined in this article—from defining security policies and integrating BI tools to leveraging automated analytics with DataCalculus—security teams can develop a robust framework for protecting their containerized environments. The journey to secure cloud containerization and orchestration is ongoing, but with the right blend of technology, process, and intelligence, the future looks promising.
For further exploration of data-driven insights and secure analytics, consider exploring our additional resources: The journey to implementing secure containerization and orchestration is complex, yet rewarding. As businesses continue to harness the benefits of agile, container-based deployments, the need for integrated security measures becomes paramount. Cloud Security Engineers must utilize every resource available—from automated security systems and Business Intelligence tools to advanced data analytics—to build a secure and resilient cloud environment.
By fostering a culture that values both innovation and rigorous security practices, organizations can stay ahead in the race against cyber threats. The skills and strategies discussed in this article provide a blueprint for anyone interested in advancing their knowledge in secure cloud operations. With continuous learning and adaptation, the future of cloud security looks robust and promising.
Thank you for investing your time in understanding the strategic facets of secure containerization and orchestration. As technology evolves, so too will the methodologies and practices dedicated to keeping our data safe. Stay informed, remain vigilant, and continue to explore the powerful insights provided by integrated Data Analytics and Business Intelligence systems.
This comprehensive guide is crafted to empower you with the knowledge to make data-driven decisions, confidently tackle new threats, and design security architectures that are both robust and flexible, ensuring your organization’s digital future is secure. Container security is no longer a niche concern for platform teams. With 59% of organizations reporting security incidents in their Kubernetes or container environments, and 30% of those incidents resulting in confirmed data breaches or network compromise, the question is not whether you need a container security strategy. It is whether yours is mature enough to survive the current threat landscape.
4. Practical Deployment, Analysis & Case Studies This guide covers everything security architects and DevSecOps engineers need to know: how container security differs from traditional approaches, which threats demand your attention, what best practices actually reduce risk, which tools are worth deploying, and how to build a security strategy that scales with your container environment.
Container security is the set of practices, tools, and policies used to protect containerized applications throughout their entire lifecycle. That lifecycle spans image creation, registry storage, orchestration, runtime execution, and eventual teardown. A complete container security program addresses vulnerabilities and misconfigurations at every stage, not just at the point of deployment.
The core architectural difference creates fundamentally different security requirements. Containers share the host operating system kernel rather than running separate OS instances like virtual machines. This shared kernel model collapses the isolation boundary that traditional security tools assume. A kernel exploit in one container can affect every other workload on the same host.
Traditional security tools operate on static, long-lived assets. A server might run for months without its configuration changing significantly. Containers are ephemeral and dynamic: they are created, updated, and destroyed in seconds, often hundreds of times per day in CI/CD pipelines. Security controls designed for stable infrastructure cannot monitor or enforce policy on assets that exist for minutes.
The other major difference is the blast radius of image-level vulnerabilities. A single insecure base image propagated to thousands of container instances creates a fleet-wide exposure. In traditional infrastructure, a vulnerable package on one server is a single-node problem. Most organizations over-invest in build-phase scanning and under-invest in runtime protection. Both are necessary.
These are not theoretical risks. The incidents behind these numbers represent delayed application launches, compliance violations, and confirmed data exfiltration. Every container instance, base image, and microservice is a discrete attack target. An environment running 500 containers across multiple cloud providers does not have one attack surface: it has 500 separate entry points, each with its own dependency tree, network exposure, and privilege configuration.
The attack surface expands further when you account for the orchestration layer. Kubernetes clusters introduce their own attack vectors through the API server, ETCD datastore, kubelet endpoints, and RBAC misconfigurations. Agentic AI tooling and AI-generated code are now introducing a new supply chain vector: threat actors are inserting malicious code into public container images and open-source repositories at a scale not seen before.
Understanding the threat model is a prerequisite for selecting effective controls. The following are the primary attack categories security teams must address. Container images are blueprints. Any vulnerability embedded in a base image is inherited by every container instantiated from it. Public registries like Docker Hub contain millions of images, many with outdated dependencies, exposed secrets, or outright malicious payloads inserted through supply chain compromise. Well-documented incidents have involved attackers uploading modified images to public registries that thousands of organizations pulled, effectively deploying backdoors or cryptominers at scale.
The practitioner fix: treat every third-party image as untrusted until scanned, signed, and provenance-verified. Only approved base images from private registries should reach production. Because containers share the host kernel, a successful kernel exploit can escalate from container compromise to full host compromise, exposing every other workload on that node. Kernel vulnerabilities like Dirty COW (CVE-2016-5195), Runc breakout vulnerabilities, and more recent namespace escape techniques have demonstrated this attack path repeatedly. This is not an edge case: it is the primary reason why running containers as root or with excessive capabilities is categorically unacceptable.
The practitioner fix: run containers with read-only root filesystems, drop all Linux capabilities except those explicitly required, and enforce seccomp and AppArmor profiles. Use gVisor or Kata Containers for high-assurance workloads where kernel isolation is non-negotiable. Misconfiguration accounts for the majority of container security incidents. The specific patterns appear consistently across incident reports: containers running as root, exposed ports with no authentication, default credentials left unchanged, overly permissive RBAC roles, and missing network policies. Red Hat’s research identifies misconfigurations as responsible for 45% of Kubernetes security incidents.
The practitioner fix: enforce Pod Security Admission (the replacement for the deprecated PodSecurityPolicy) with at minimum the Baseline profile in production, and Restricted profile wherever application compatibility allows. The build pipeline is the new perimeter. Attackers who compromise a developer’s machine, a third-party dependency, or a CI/CD runner can inject malicious code into container images before they reach production. The SolarWinds-style attack pattern, applied to containers, means a trusted image can become a vector without any runtime behavior triggering traditional alerts until the payload executes.
The practitioner fix: implement image signing with Cosign and policy enforcement with tools like Sigstore or in-toto attestations. Verify build provenance before any image enters your registry. Integrate Software Bill of Materials (SBOM) generation into every pipeline. Secrets management is one of the most consistently mishandled aspects of container security. Hard-coded API keys, database credentials, and service account tokens end up in Dockerfiles, environment variables passed at runtime, or directly embedded in image layers. A 2025 analysis found that 54% of cloud environments contain credentials hard-coded in configuration files or containers. Once an attacker has image access, those secrets are trivially extractable.
The practitioner fix: use a dedicated secrets manager (HashiCorp Vault, AWS Secrets Manager, or Kubernetes External Secrets) and mount secrets at runtime using projected volumes or CSI drivers. Never pass secrets via environment variables visible in container inspection output. The following practices represent the minimum viable security posture for any organization running containers in production.
They are organized by lifecycle phase. The most cost-effective place to find and fix container vulnerabilities is before the image is built, not after it has been deployed. The Docker daemon and container runtime (containerd, CRI-O) expose extensive configuration options that are insecure by default.
In Kubernetes environments, Role-Based Access Control (RBAC) is the primary mechanism for restricting what API operations different principals can perform. The practitioner approach: start from zero permissions and grant only what admission testing confirms is required. Audit RBAC bindings quarterly using tools like kubectl-who-can or Kubescape’s RBAC analysis module. Implement just-in-time access for privileged operations.
By default, every pod in a Kubernetes cluster can communicate with every other pod. This default-allow posture means a compromised container has unrestricted lateral movement capability across the entire cluster. Kubernetes Network Policies provide namespace and label-based ingress/egress controls, but they require a CNI plugin that enforces them (Calico, Cilium, or Weave Net). Vanilla Kubernetes does not enforce NetworkPolicy objects without a compatible CNI.
For service-to-service communication requiring mutual TLS and fine-grained traffic policy, a service mesh like Istio or Linkerd provides application-layer controls that NetworkPolicy cannot. The trade-off is operational complexity. Most organizations should implement NetworkPolicy first and add a service mesh when the threat model justifies the overhead. Private registries are not automatically secure. Access controls, image signing enforcement, and automated vulnerability scanning must be explicitly configured.
Static analysis cannot detect attacks that occur after a container has started. Runtime security tools monitor container behavior at the kernel level and alert on anomalous activity: unexpected process execution, unusual network connections, filesystem writes to protected paths, and privilege escalation attempts. Falco (CNCF project) is the most widely deployed open-source runtime security tool. It uses kernel system call tracing to detect policy violations against a library of rules. eBPF-based sensors (as used by Sysdig, Cilium, and AccuKnox) provide the same visibility with lower overhead and without requiring kernel modules.
The signal-to-noise ratio is the operational challenge. An untuned Falco deployment will generate hundreds of alerts per day in a busy cluster. Effective runtime security requires baselining normal behavior per workload type and alerting on deviations, not absolute rules. Tools that build application behavior profiles (ARMO Platform’s Application Profile DNA, Sysdig’s Drift Detection) reduce false positives significantly.
No single tool covers the full container security stack. The following table provides a neutral comparison across the primary categories. Trivy is the default recommendation for most teams starting container scanning. It covers OS packages, language dependencies, Dockerfile misconfigurations, and secret detection in a single binary with no backend dependency. Integrate it as a gated CI step that blocks deployment on Critical severity findings.
For teams needing SBOM-centric workflows, Anchore’s Syft (SBOM generation) combined with Grype (vulnerability matching against the SBOM) provides a structured, auditable approach that satisfies supply chain compliance requirements including SLSA and SSDF. Falco is the foundational runtime tool for most cloud-native teams. Its declarative rule language supports custom detection logic, and its integration with SIEM platforms (Elasticsearch, Splunk, Google Chronicle) enables SOC-level correlation.
For organizations requiring enterprise support, automated response actions, and consolidated Kubernetes security posture management, Sysdig Secure or Aqua Platform provide a managed approach. eBPF-based sensors from these vendors outperform legacy kernel module approaches in performance-sensitive environments. Kubescape (ARMO) provides free Kubernetes hardening checks against the CIS Kubernetes Benchmark and the NSA/CISA Hardening Guidance. It is the fastest way to establish a baseline compliance posture in a new cluster. For organizations needing policy-as-code enforcement with Kubernetes-native syntax, Kyverno is simpler to operate than OPA/Gatekeeper for most use cases.
Kubernetes is the dominant container orchestration platform, and its security surface extends far beyond individual container configuration. Three Kubernetes-native security controls form the baseline for any production cluster: 5. Performance Evaluation & Extended Technical Observations The API server is the highest-value target in any Kubernetes deployment. A compromised API server provides cluster-wide control. Key hardening steps: Tactical controls are only effective within a coherent strategy. The following framework applies to teams at any maturity level.
Security gates in CI/CD pipelines are the most scalable enforcement mechanism available to security teams. Rather than conducting security reviews as manual checkpoints, automated gates catch the majority of issues before code reaches production. Each gate catches a different threat class. Removing any one creates a blind spot that attackers can exploit.
NIST SP 800-190 (Application Container Security Guide) provides NIST’s official guidance on container security controls, organized around the container lifecycle. It covers image vulnerabilities, registries, orchestration, host OS, and the hardware/firmware layer. Organizations in regulated industries (FedRAMP, FISMA, HIPAA) should map their controls directly to this publication.
CIS Benchmarks for Docker, Kubernetes, and Container Orchestration provide prescriptive, testable configuration standards. The CIS Docker Benchmark alone covers 100+ checks across Docker daemon configuration, container runtime settings, and image build practices. Kubescape and Trivy both support CIS Benchmark assessment out of the box. I help organisations secure their cloud infrastructure and stay ahead of evolving cyber threats. Microsoft MVP and Certified Trainer, author of Mastering Azure Security, and founder of arnav.au — a platform for practical Cloud, Cybersecurity, DevOps and AI content.
Container security differs fundamentally because containers share the host operating system kernel rather than running separate OS instances like VMs, which collapses the isolation boundary that traditional tools assume. Additionally, containers are ephemeral and dynamic—created and destroyed in seconds—while traditional security tools are designed for static, long-lived assets. A single vulnerability in a shared container image can also affect thousands of instances across your fleet, creating a much larger blast radius than a vulnerable package on a single server.
The three phases are: Build (securing source code, dependencies, Dockerfile configuration, and base images before creation), Ship (scanning images in the registry, enforcing signing and provenance, and controlling which images reach production), and Run (monitoring runtime behavior, enforcing network policies, restricting system calls, and detecting anomalous activity). Most organizations over-invest in build-phase scanning while under-investing in runtime protection, though both are necessary for a complete security program.
According to 2025 research, 59% of organizations have experienced security incidents in Kubernetes or container environments, with 30% of those incidents resulting in confirmed data breaches or network compromise. An even higher statistic shows that 90% of organizations experienced at least one Kubernetes security incident in the past year, demonstrating that container security threats are widespread and growing.
Approximately 75% of container images in production carry at least one high-severity or critical vulnerability, according to Aikido Security research from 2025. This widespread exposure highlights the importance of implementing comprehensive image scanning and vulnerability management throughout the container lifecycle. Agentic AI tooling and AI-generated code have introduced a new supply chain vector where threat actors are inserting malicious code into public container images and open-source repositories at an unprecedented scale. This expanding threat requires organizations to treat all third-party images as untrusted until they have been properly scanned, signed, and provenance-verified before deployment.
Last Updated on October 18, 2026 by Arnav Sharma Guardian Agents Explained is fast becoming one of the most searched phrases in… Last Updated on September 13, 2026 by Arnav Sharma As a Microsoft MVP and Certified Trainer who has spent the past several… Last Updated on August 12, 2026 by Arnav Sharma Enterprise passkeys beyond the hype is not a rhetorical framing. It is the… The rise of cloud computing has transformed how businesses deploy and manage their applications. Virtualization and container -based architectures offer greater flexibility, scalability, and efficiency , but they also pose new security challenges .
One of the key elements in these environments is the control plane , responsible for managing communication, orchestration, and policies within the cloud ecosystem. Protecting this component is essential to prevent breaches, service interruptions, and attacks that could compromise the entire infrastructure. In this article we will explore how to ensure cloud security , focusing on the concepts of container and control plane , and on best practices for maintaining secure and resilient orchestrated environments.
A container is a lightweight software unit that bundles everything needed to run an application: code, dependencies, and configurations. Unlike virtual machines, containers share the same operating system, which reduces resource consumption and allows for faster and more consistent application deployment. However, this flexibility also introduces risks. Container security depends on multiple factors: image integrity, process isolation, host system configuration, and secure management of shared networks and volumes.
In an environment with hundreds or thousands of containers , manual management would be impractical. This is where the control plane comes into play, an essential component of orchestration platforms like Kubernetes. Its role is so critical that any failure or attack targeting the control plane can compromise the entire cloud environment. Therefore, keeping it secure must be a top priority in any cloud security strategy.
As cloud infrastructures become more complex, new attack vectors emerge. Key risks include: Containers rely on base images , which can contain vulnerabilities if not properly verified. Downloading images from untrusted sources is a leading cause of security incidents. An incorrect configuration can grant excessive privileges to containers or expose control plane management ports to the public.
Attackers may attempt to exploit weak credentials or poorly managed tokens to gain access to the Kubernetes dashboard and manipulate cluster resources. When containers communicate freely without proper network policies, a single compromised container can facilitate lateral movement within the environment.
If a container has elevated permissions, an attacker could reach the host operating system and take complete control of the environment. Ensuring cloud security requires a comprehensive approach that covers everything from infrastructure to the application layer. These are the most recommended strategies: Apply the principle of defense in depth It allows that, even if one layer is compromised, there are others that contain the attack. This includes firewalls, network segmentation, multi-factor authentication, and role-based management (RBAC).
Uses vulnerability analysis tools and integrity check before displaying an image. Also, use private and trusted repositories to ensure that the images have not been altered. Configure Kubernetes policies to limit resources, prevent elevated privilege execution, and enforce network policies that control communication between pods.
Observability is key in cloud security. It uses logging and alerting systems that detect anomalous behavior, unauthorized access attempts , or configuration deviations. Both the images and the orchestration tools must always be kept up to date to correct known vulnerabilities. The adoption of DevSecOps —integrating security throughout the development lifecycle—has become an essential practice in the cloud. In this model, security ceases to be an isolated process and becomes part of every stage: from image build to container deployment.
Integrating security analysis tools into CI/CD pipelines allows for the detection of vulnerabilities before reaching production, reducing risk and improving operational efficiency. When container security measures and control plans are properly implemented, organizations realize significant benefits: Continuous availability: orchestrated systems can redistribute loads and prevent interruptions in the event of incidents.
La cloud security It is no longer an option, but a critical necessity in a highly distributed digital environment. The containers They offer flexibility and performance, but require rigorous management of the security and orchestration . In turn, the control plane It acts as the core of the entire infrastructure: if it is compromised, the entire environment is at risk. Adopt solid practices of protection, monitoring and automation ensures stability, scalability, and reliability in modern cloud services. Ultimately, protect the containers and the control plane is to protect the very heart of digital transformation.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Google%20Cloud%20Platform • https://en.wikipedia.org/wiki/Oracle%20Cloud • https://en.wikipedia.org/wiki/IBM%20Cloud • https://www.sysdig.com/learn-cloud-native/orchestration-containerized-architecture • https://nerdleveltech.com/mastering-container-orchestration-a-complete-practical-guide • https://datacalculus.com/en/blog/computer-and-network-security/cloud-security-engineer/secure-cloud-containerization--orc hestration • https://arnav.au/2026/05/14/container-security-guide/ • https://cibersafety.com/en/cloud-security-and-orchestration/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Secure Container Orchestration In Cloud.
[*] Metasploit Scan Running on Target Subnet for Secure Container Orchestration In Cloud... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |