Complete Technical Paper Content — Secure Content Management System With Audit Logs
Overview & System Context
Secure Content Management System With Audit Logs: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9549 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Enterprise content management (ECM) extends the concept of content management by adding a timeline for each content item and, possibly, enforcing processes for its creation, approval, and distribution. Systems using ECM generally provide a secure repository for managed items, analog or digital. They also include one (or more) methods for importing content to manage new items, and several presentation methods to make items available for use. Although ECM content may be protected by digital rights management (DRM), it is not required. ECM is distinguished from general content management by its cognizance of the processes and procedures of the enterprise for which it is created.
On-premises software (installed on an organization's network) Software as a service (SaaS): Web access to information stored on a software manufacturer's system A hybrid of both on-premises and SaaS components Infrastructure as a Service (IaaS): Online services which abstract the user from infrastructure details like physical computing resources, location, data partitioning, scaling, security, and backup Benefits to an organization include improved efficiency, better control, and reduced costs. Banks have converted to storing copies of old cheques in ECM systems from the older method of keeping physical cheques in warehouses. Under the old system, a customer request for a copy of a cheque might take weeks; a bank employee had to contact the warehouse where the right box, file and cheque were located. The cheque would be pulled and a copy made and mailed to the bank, which would then mail it to the customer. With an ECM system in place, a bank employee could query the system for the customer's account number and the number of the requested cheque. When an image of the cheque appeared on-screen, the bank could mail a copy immediately to the customer; usually while the customer was still on the phone.
Data/Document Capture – Capture, digitize, and index documents and data at their ingestion point, whether via email, invoice, paper form, or other. Secure Content Repository – Hold documents and data in a central access point for easy retrieval, use, and version control. Assign security and compliance controls — Protect sensitive data with user-assigned access controls and retention policy procedures. Automated workflow delivery – Keep processes moving with automated approvals and document/data routing to workflow touchpoints. The management systems can help businesses comply with government and industry regulations such as HIPAA, the Sarbanes–Oxley Act, the Payment Card Industry Data Security Standard (PCI DSS), and the Federal Rules of Civil Procedure. Security at the user, function, and record levels protect sensitive data. Some information in a document can be redacted, so the remainder can be shared without compromising identity or key data. Every action in the system is tracked, and can be reported to demonstrate compliance with a wide variety of regulations.
ECM functions as integrative infrastructure, connecting previously siloed vertical applications and making content accessible across the enterprise. Enterprise application integration (EAI) and service-oriented architecture (SOA) underpin this connectivity. ECM exposes its capabilities as independent services, meaning individual components such as capture, workflow, or records management can be consumed by different applications without duplicating functionality. ECM provides a uniform repository, consolidating documents, data, and digital assets into a single managed store, eliminating costly redundancies and improving information consistency across the organisation. Artificial intelligence has extended these three properties in modern ECM platforms. At the infrastructure layer, AI enables intelligent routing and classification of content as it moves between systems without manual intervention. Within the services layer, AI-powered capabilities such as optical character recognition, named entity extraction, and large language model-based summarisation are now exposed as discrete services that applications can call on demand. At the repository level, AI assists with automated metadata generation, duplicate detection, and retention policy enforcement, tasks that previously required significant manual configuration.
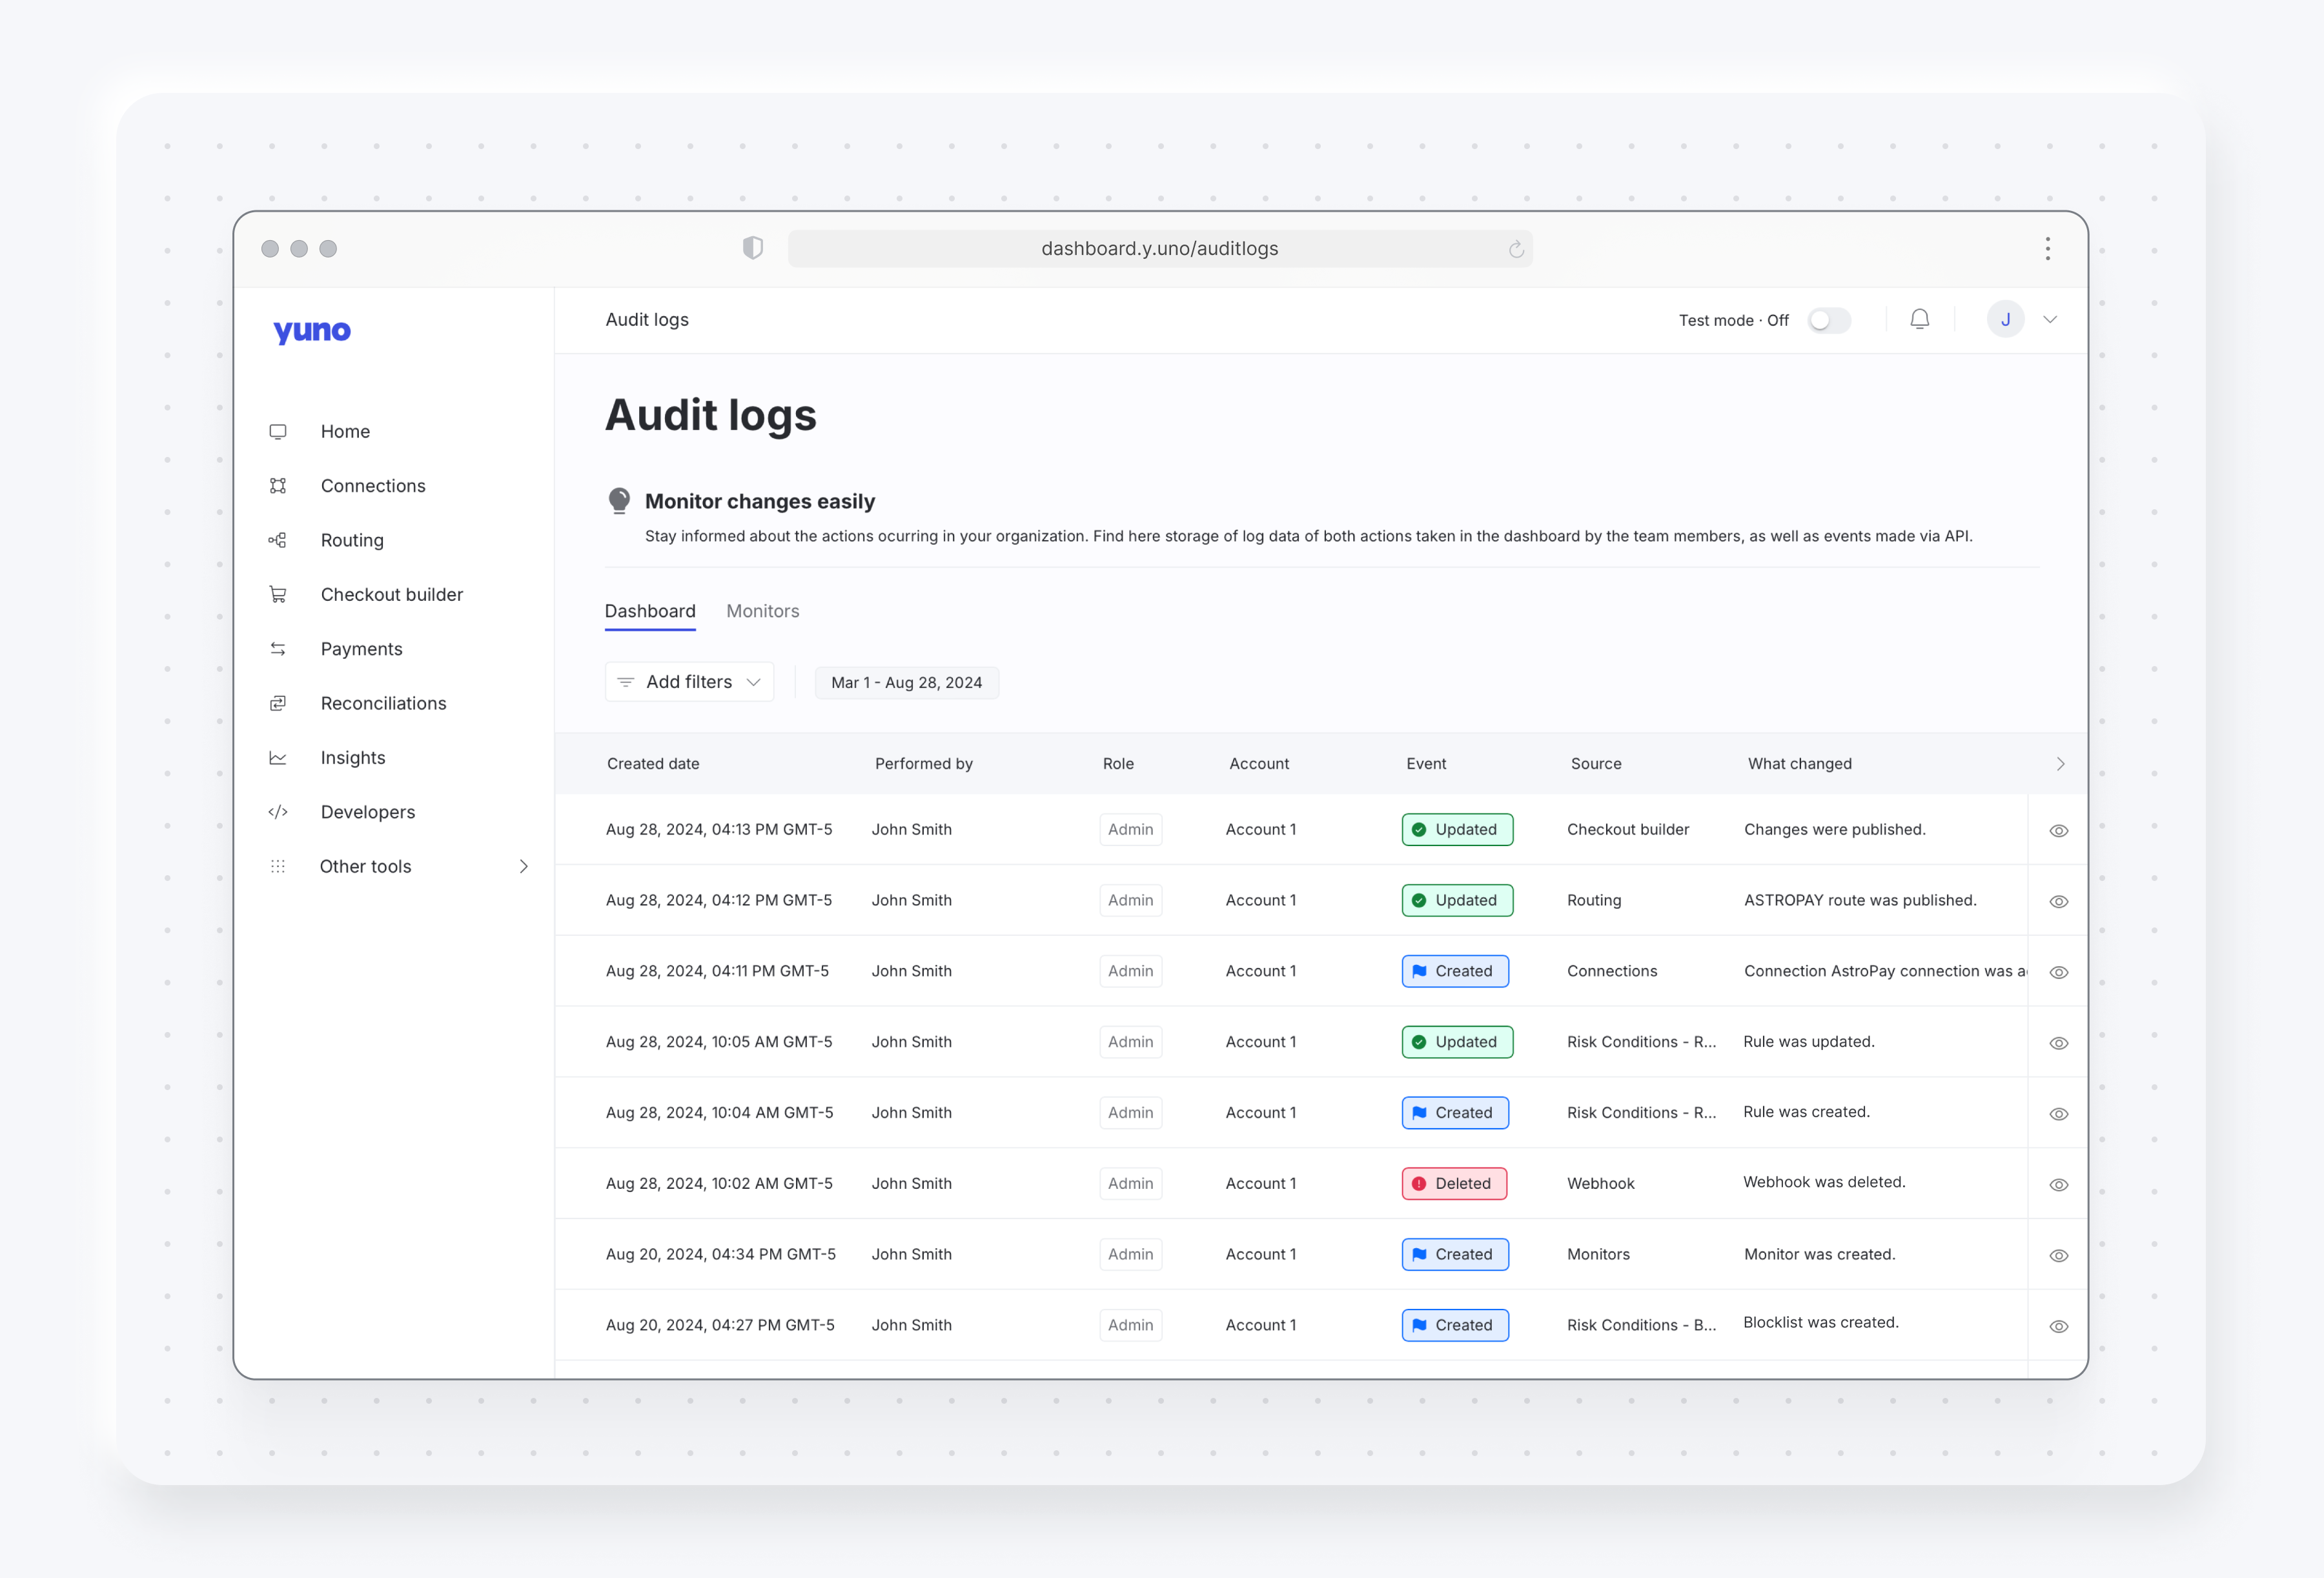
Figure 1: Audit logs Optical character recognition (OCR): Converts images of typeset text into alphanumeric characters Handwriting recognition (HWR): Converts images of handwritten text into alphanumerics Intelligent character recognition (ICR): Extends OCR and HWR to use comparison, logical connections, and checks against reference lists and existing data to improve recognition Optical mark recognition (OMR): Reads special markings (such as check marks or dots) in predefined fields Barcode recognition: Decodes industry-standard encodings of product and other commercial data Document management (DMS) Collaborative software Web content management, including web portals Records management Workflow and business process management (BPM) It connects the other components, which can be used in combination or separately. Document management, web content management, collaboration, workflow and business process management address the dynamic part of the information's life cycle. Records management manages finalized documents in accordance with the organization's retention period, which must comply with government mandates and industry practices.
Manage components incorporate databases and access-authorization systems. Check in-check out: Checks stored information for consistency Version management: Keeps track of different versions of the same information, with revisions and different formats Search and navigation: Finds information and its associated contexts Organizing documents in files, folders, and overviews Document management overlaps with other manage components, office applications (like Microsoft Outlook and Exchange, or Lotus Notes and Domino), and library services which administer information storage.
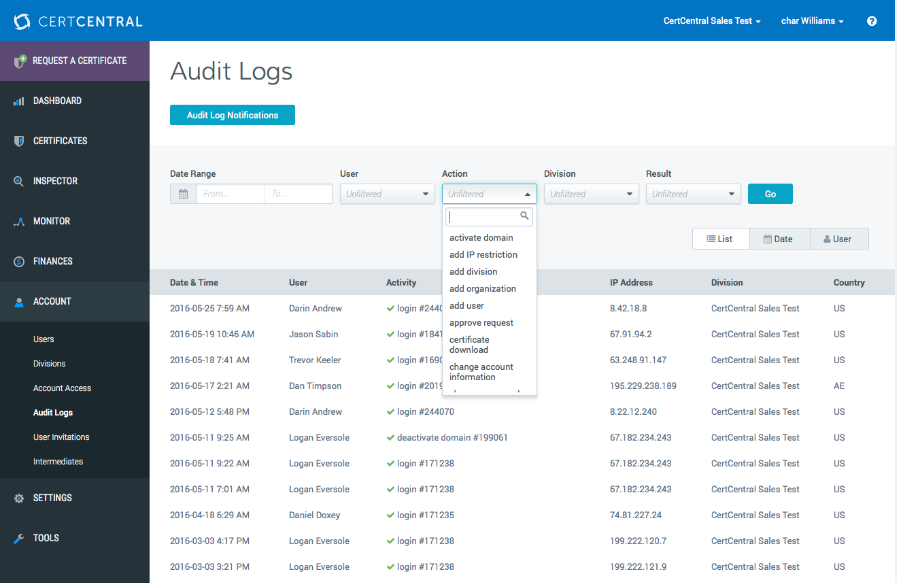
Visualization of file plans and other structured indexes for the orderly storage of information Unambiguous indexing of information, supported by thesauruses or controlled word lists Management of record-retention and deletion schedules Protection of information in accordance with its characteristics International, industry-specific (or company-wide), standardized metadata for the unambiguous identification and description of stored information Figure 2: Ibm Security Access Manager For Auditing Guide at James Goldsbrough blog Visualization of process and organization structures Capture, administration, visualization, and delivery of information with its associated documents or data Incorporation of data-processing tools (such as applications) and documents, such as office products Parallel and sequential processing of procedures, including simultaneous saving Reminders, deadlines, delegation and other administrative functions Monitoring and documentation of process status, routing, and outcomes Tools to design and display process According to the AIIM, BPM is a way of looking at (and controlling) organizational processes.
Repositories: storage locations Library services: administration components for repositories Storage technologies File systems: Used primarily for temporary storage, as input and output caches Content management systems: Storage and repository systems for content; may be a database or a specialized storage system Databases administer information, and can also store documents, content, or media. Data warehouses: Complex storage systems based on databases, which provide information from a variety of sources. They may be designed with global functions, such as documents or information.
Magnetic online media: Hard disk drives (typically configured as RAID systems) may be locally attached, part of a storage area network, or mounted from another server (network-attached storage). Magnetic tape: Magnetic tape data storage, in the form of tape libraries, use robotics to provide nearline storage. Standalone tape drives may be used for backup. Digital optical media: In addition to compact disc and DVD optical media, storage systems may use magneto-optical drives; optical jukeboxes can be used for nearline storage. Optical media in jukeboxes may be moved offline. Cloud computing: Data may be accessed via the Internet.
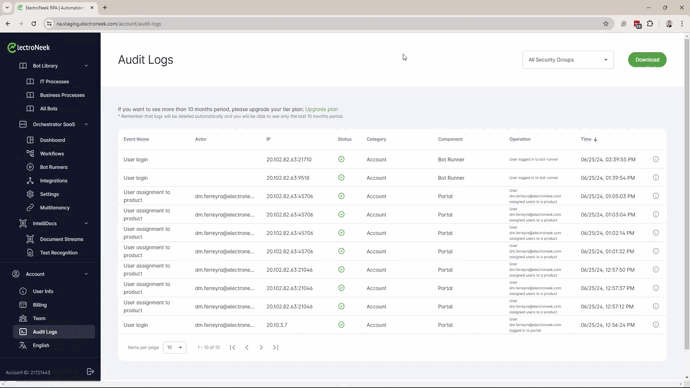
Figure 3: Advanced Access Management feature Write once read many (WORM) 5.25-inch (13.3 cm) or 3.5-inch (89 mm) optical discs, CD-Rs and DVD-Rs Magnetic tapes in secure drives Content-addressable storage, with software protection against overwriting, erasure, and editing Storage networks may be used if they provide edit-proof auditing, with unchangeable storage and protection against manipulation and erasure. Microforms, such as microfilm, microfiche, and aperture cards, are typically used to secure electronic information.
Paper also secures electronic information. Computer output to laser disc (COLD): When used for delivery COLD prepares output data for distribution and archiving. Applications include lists and formatted output (such as personalized customer letters), journals and logs. Personalization: Functions and output customized for a user's needs XML (Extensible Markup Language): Enables the standardized, cross-platform description of interfaces, structures, metadata, and documents PDF (Portable Document Format): A cross-platform printing and distribution format which permits content searches, the addition of metadata, and the embedding of electronic signatures. When generated from electronic data, PDFs are resolution-independent and allow crisp reproduction at any scale. Open XML Paper Specification (OpenXPS): An XML specification, developed by Microsoft, describing the formats and rules for distributing, archiving, rendering, and processing XPS documents. Converters and viewers: Generates uniform formats to display (and output) information in different formats. Data compression: Reduces the storage space needed for pictorial information. Web syndication: Presents content in different formats, selections, and forms for multiple use in different forms for different purposes.
A web content management system (WCM or WCMS) is a software content management system (CMS) specifically for web content. It provides website authoring, collaboration, and administration tools that help users with little knowledge of web programming languages or markup languages create and manage website content. A WCMS provides the foundation for collaboration, providing users the ability to manage documents and output for multiple author editing and participation. Most systems use a content repository or a database to store page content, metadata, and other information assets the system needs. A presentation layer (template engine) displays the content to website visitors based on a set of templates, which are sometimes XSLT files. Most systems use server side caching to improve performance. This works best when the WCMS is not changed often but visits happen frequently. Administration is also typically done through browser-based interfaces, but some systems require the use of a fat client.
Automated templates Create standard templates (usually HTML and XML) that users can apply to new and existing content, changing the appearance of all content from one central place. Access control Some WCMS systems support user groups, which control how registered users interact with the site. A page on the site can be restricted to one or more groups. This means an anonymous user (someone not logged-on), or a logged on user who is not a member of the group a page is restricted to, is denied access. Scalable expansion Available in most modern WCMSs.is the ability to expand a single implementation (one installation on one server) across multiple domains, depending on the server's settings. WCMS sites may be able to create microsites/web portals within a main site as well. Easily editable content Once content is separated from the visual presentation of a site, it usually becomes much easier and quicker to edit and manipulate. Most WCMS software includes WYSIWYG editing tools allowing non-technical users to create and edit content. Scalable feature sets Most WCMS software includes plug-ins or modules that can be easily installed to extend an existing site's functionality. Web standards upgrades Active WCMS software usually receives regular updates that include new feature sets and keep the system up to current web standards. Workflow management Workflow management is the process of creating cycles of sequential and parallel tasks that must be accomplished in the WCMS. For example, one or many content creators can submit a story, but it is not published until the copy editor cleans it up and the editor-in-chief approves it. Collaboration WCMS software may act as a collaboration platform where many users retrieve and work on content. Changes can be tracked and authorized for publication or ignored reverting to old versions. Other advanced forms of collaboration allow multiple users to modify (or comment) a page at the same time in a collaboration session. Delegation Some WCMS software allows for various user groups to have limited privileges over specific content on the website, spreading out the responsibility of content management. Document management WCMS software may provide a means of collaboratively managing the lifecycle of a document from initial creation time, through revisions, publication, archive, and document destruction. Content virtualization WCMS software may provide a means of allowing each user to work within a virtual copy of the entire website, document set, and/or code base. This enables viewing changes to multiple interdependent resources in context before submission. Content syndication WCMS software often helps distribute content by generating RSS and Atom data feeds to other systems. They may also e-mail users when updates become available. Multilingual communication Many WCMSs can display content in multiple languages. Versioning Like document management systems, WCMS software may implement version control, by which users check pages in and out of the WCMS. Authorized editors can retrieve previous versions and work from a selected point. Versioning is useful for content that changes and requires updating, but it may be necessary to start from or reference a previous version.
An information security audit is an audit of the level of information security in an organization. It is an independent review and examination of system records, activities, and related documents. These audits are intended to improve the level of information security, avoid improper information security designs, and optimize the efficiency of the security safeguards and security processes. Within the broad scope of auditing information security there are multiple types of audits, multiple objectives for different audits, etc. Most commonly the controls being audited can be categorized as technical, physical and administrative. Auditing information security covers topics from auditing the physical security of data centers to auditing the logical security of databases, and highlights key components to look for and different methods for auditing these areas. When centered on the Information technology (IT) aspects of information security, it can be seen as a part of an information technology audit. It is often then referred to as an information technology security audit or a computer security audit. However, information security encompasses much more than IT.
Security policy and standards Organizational and Personal security Communication, Operation and Asset management Physical and environmental security Access control and Compliance IT systems development and maintenance IT security incident management Disaster recovery and business continuity management Risk management Meet with IT management to determine possible areas of concern Review the current IT organization chart Review job descriptions of data center employees Research all operating systems, software applications, and data center equipment operating within the data center Review the company's IT policies and procedures Evaluate the company's IT budget and systems planning documentation Review the data center's disaster recovery plan Personnel procedures and responsibilities, including systems and cross-functional training Change management processes are in place and followed by IT and management personnel Appropriate backup procedures are in place to minimize downtime and prevent the loss of important data The data center has adequate physical security controls to prevent unauthorized access to the data center Adequate environmental controls are in place to ensure equipment is protected from fire and flooding Data centre personnel – All data center personnel should be authorized to access the data center (key cards, login ID's, secure passwords, etc.). Datacenter employees are adequately educated about data center equipment and properly perform their jobs. Vendor service personnel are supervised when doing work on data center equipment. The auditor should observe and interview data center employees to satisfy their objectives. Equipment – The auditor should verify that all data center equipment is working properly and effectively. Equipment utilization reports, equipment inspection for damage and functionality, system downtime records and equipment performance measurements all help the auditor determine the state of data center equipment. Additionally, the auditor should interview employees to determine if preventative maintenance policies are in place and performed. Policies and Procedures – All data center policies and procedures should be documented and located at the data center. Important documented procedures include data center personnel job responsibilities, back up policies, security policies, employee termination policies, system operating procedures and an overview of operating systems.
Physical security / environmental controls – The auditor should assess the security of the client's data center. Physical security includes bodyguards, locked cages, man traps, single entrances, bolted-down equipment, and computer monitoring systems. Additionally, environmental controls should be in place to ensure the security of data center equipment. These include Air conditioning units, raised floors, humidifiers and an uninterruptible power supply. Backup procedures – The auditor should verify that the client has backup procedures in place in the case of system failure. Clients may maintain a backup data center at a separate location that allows them to instantaneously continue operations in the instance of system failure The auditors' procedures and findings The auditors' recommendations Objective, scope, and methodologies Overview/conclusions The report may optionally include rankings of the security vulnerabilities identified throughout the performance of the audit and the urgency of the tasks necessary to address them. Rankings like "high", "low", and "medium" can be used to describe the imperativeness of the tasks.
Federal or State Regulators Information security audits would primarily be prepared by the partners of these regulators. Examples include: Certified accountants, Cybersecurity and Infrastructure Security Agency (CISA), Federal Office of Thrift Supervision (OTS), Office of the Comptroller of the Currency (OCC), U.S. Department of Justice (DOJ), etc. Corporate Internal Auditors If the information security audit is an internal audit, it may be performed by internal auditors employed by the organization. Examples include: Certificated accountants, Cybersecurity and Infrastructure Security Agency (CISA), and Certified Internet Audit Professional (CIAP) External Auditors Typically, third-party experts employed by an independent organization and specializing in the field of data security are hired when state or federal auditors are not accessible.
Consultants Outsourcing the technology auditing where the organization lacks the specialized skill set. In certain regulated industries, information security audits may be mandated by law. In the United States healthcare sector, the Health Insurance Portability and Accountability Act (HIPAA) Security Rule requires covered entities and business associates to conduct periodic security risk assessments to evaluate the likelihood and impact of potential threats to electronic protected health information.
To assist organizations in meeting these requirements, the Office of the National Coordinator for Health Information Technology (ONC) and OCR developed a free Security Risk Assessment Tool for small and medium-sized healthcare practices. Certified Information Security Manager (CISM) Certified in Risk and Information Systems Control (CRISC) Certified in the Governance of Enterprise IT (CGEIT) Certified Information System Auditor (CISA) CSX (Cybersecurity Nexus Fundamentals) CSXP (Cybersecurity Nexus Practitioner) Passwords: Every company should have written policies regarding passwords, and employees' use of them. Passwords should not be shared and employees should have mandatory scheduled changes. Employees should have user rights that are in line with their job functions. They should also be aware of proper log on/ log off procedures. Also helpful are security tokens, small devices that authorized users of computer programs or networks carry to assist in identity confirmation. They can also store cryptographic keys and biometric data. The most popular type of security token (RSA's SecurID) displays a number that changes every minute. Users are authenticated by entering a personal identification number and the number on the token.
Termination Procedures: Proper termination procedures ensure that old employees can no longer access the network. This can be done by changing passwords and codes. Also, all id cards and badges that are in circulation should be documented and accounted for. Special User Accounts: Special User Accounts and other privileged accounts should be monitored and have proper controls in place. Remote Access: Remote access is often a point where intruders can enter a system. The logical security tools used for remote access should be very strict. Remote access should be logged.
Programming Processing Access When it comes to programming it is important to ensure proper physical and password protection exists around servers and mainframes for the development and update of key systems. Having physical access security at one's data center or office such as electronic badges and badge readers, security guards, choke points, and security cameras is vitally important to ensuring the security of applications and data. Then one needs to have security around changes to the system. Those usually have to do with proper security access to make the changes and having proper authorization procedures in place for pulling programming changes from development through test and finally into production.
With processing, it is important that procedures and monitoring of a few different aspects such as the input of falsified or erroneous data, incomplete processing, duplicate transactions and untimely processing are in place. Making sure that input is randomly reviewed or that all processing has proper approval is a way to ensure this. It is important to be able to identify incomplete processing and ensure that proper procedures are in place for either completing it or deleting it from the system if it was in error. There should also be procedures to identify and correct duplicate entries. Finally, when it comes to processing that is not being done on a timely basis one should back-track the associated data to see where the delay is coming from and identify whether or not this delay creates any control concerns. Finally, access, it is important to realize that maintaining network security against unauthorized access is one of the major focuses for companies as threats can come from a few sources. First, one has internal unauthorized access. It is very important to have system access passwords that must be changed regularly and that there is a way to track access and changes so one is able to identify who made what changes. All activity should be logged. The second arena to be concerned with is remote access, people accessing one's system from the outside through the internet. Setting up firewalls and password protection to on-line data changes are key to protecting against unauthorized remote access. One way to identify weaknesses in access controls is to bring in a hacker to try and crack one's system by either gaining entry to the building and using an internal terminal or hacking in from the outside through remote access.
The design of tamper-evident, high-fidelity logging systems that generate, collect, and retain compliance evidence across distributed application and infrastructure environments. Audit logging for compliance is distinct from operational logging: while operational logs are optimized for troubleshooting and performance analysis, compliance audit logs are evidence artifacts that must be complete, accurate, tamper-evident, and retained for defined periods. Regulatory requirements for audit logging span the full stack: PCI DSS Requirement 10 mandates logging of all access to system components and cardholder data, with specific event types required; HIPAA §164.312(b) requires activity logs of information system access; SOX ITGC requires logging of changes to financial systems; and NIST SP 800-92 provides detailed guidance on log management infrastructure for federal systems. A compliance audit log must capture: who performed the action (authenticated identity), what action was performed, what resource was affected, when the action occurred (with trusted timestamp), and from where (source IP or service identity).
Engineering a compliance-grade audit logging architecture requires addressing collection, transmission, storage, and retention as distinct infrastructure concerns. At the application layer, structured logging libraries (logback, serilog, winston) should emit audit events as structured JSON with consistent field schemas, including user identity, resource identifiers, and action types drawn from a defined audit event taxonomy. These application-level audit events must be collected and forwarded to a centralized log management platform (Splunk, Elastic, Datadog, AWS CloudWatch Logs) that is access-controlled separately from the application teams — application developers should not be able to delete or modify audit logs. Log forwarding must use reliable, at-least-once delivery protocols (not fire-and-forget UDP syslog) to prevent log loss that would create compliance evidence gaps.
Tamper-evidence is a specific technical requirement that most organizations implement inadequately. Write-once storage (AWS S3 Object Lock, Azure Immutable Blob Storage, Worm-capable SIEM), cryptographic log chaining (where each log entry includes a hash of the previous entry), or regular export to a log integrity service provides the tamper-evidence that auditors require. Log retention must be implemented as a technical control, not a policy aspiration — retention enforcement should prevent deletion by any user including administrators, with automated alerts when retention policies would be violated.
A common compliance gap is the inconsistency between different log sources: application logs may be retained for the required period while infrastructure logs (VPC flow logs, database audit logs, cloud API logs) are on shorter retention cycles, creating gaps in the complete audit evidence required for a forensic investigation. We design centralized audit logging architectures with structured event schemas, at-least-once delivery pipelines to access-controlled log platforms, Object Lock/WORM tamper-evidence storage, and retention enforcement automation. Our implementations include log completeness assessments that identify gaps between application, infrastructure, and cloud audit log sources, ensuring end-to-end compliance evidence coverage.
Design principles and a structured checklist for building software that is compliant by default — not compliant by retrofit. Covers data architecture, access controls, audit trails, and vendor due diligence. Deploy a team that knows your regulatory landscape before they write their first line of code. After a breach, you need to reconstruct what happened. The questions are always the same: which account acted, what did they touch, when did the first anomalous event occur, and how far did lateral movement reach? If your audit logs cannot answer those questions — because events were not captured, because the attacker deleted them, because they live in 14 different formats across 9 different systems with no correlation IDs — the forensic investigation stalls and the compliance answer becomes “we don’t know.” Audit logs that an attacker can erase are not audit logs. Audit logs that cannot be queried across services do not support incident response. Audit logs without a defined schema cannot be parsed by a SIEM. Getting the architecture right is a design decision made before the first line of code is written, not a retrofit.
This guide covers what must be logged and why, event schema design, tamper protection mechanisms, centralised aggregation, integrity verification, correlation, compliance requirements, retention, and separation of duties for log access. The starting question is not “what does our logging library emit” but “what events, if unrecorded, would prevent us from answering security questions or satisfying a compliance audit?” 2. System Architecture & Core Working Principles Every authentication attempt — success or failure — must produce an audit record. This means: Why: authentication events establish the timeline. An attacker who compromised credentials will appear in the authentication log before they appear anywhere else. Failed logins reveal brute-force attempts. MFA removal events are a near-certain indicator of account takeover.
Every authorisation check that results in a denial must be logged. Granted access should also be logged for sensitive resources. The authorisation log answers “who tried to do what they were not allowed to do.” Why denials matter: an attacker probing your system generates a trail of permission denials before they find a path that works. Without denial logging you see the successful exploit but not the reconnaissance that preceded it.
Access to PII, financial records, health data, secrets, and cryptographic material must be logged at the record level where feasible — not just at the API endpoint level. Why: a SELECT query that exfiltrates 50,000 customer records passes through your application layer without triggering any alert unless you are logging data access. Database-level audit logs (PostgreSQL’s pgaudit , MySQL’s audit plugin, Oracle Unified Auditing) capture this. Application-level logs must record which user triggered a bulk export or accessed a record flagged as sensitive.
User creation and deletion, role assignment and revocation, group membership changes, API key issuance and revocation — every administrative action that changes the security posture of the system must be logged. Why: privilege escalation attacks frequently involve administrative actions. An insider threat will create a backdoor account or escalate their own role. If you only log authentication but not role changes, you cannot see the backdoor creation.
Changes to infrastructure configuration, security group rules, IAM policies, TLS certificates, encryption keys, firewall rules, and application configuration that affects security behaviour must produce audit records. Why: misconfiguration is the leading cause of cloud security incidents. A change that opened an S3 bucket to public access, weakened a firewall rule, or disabled MFA enforcement needs to be in the audit trail so the change can be attributed, reviewed, and reversed.
Unstructured log lines cannot be parsed at scale. A consistent, machine-readable schema across all services is a prerequisite for centralised analysis. The fields every audit event must carry: The request_id is the correlation key. It must be generated at the outermost entry point (API gateway, load balancer, or frontend service) and propagated via headers ( X-Request-ID , traceparent ) through every downstream service call. When a single user action produces events in 10 services, the request_id ties them together.
Use a namespaced event type taxonomy rather than free text: auth.login.success , authz.permission.denied , data.record.read , admin.user.created , config.policy.updated . This allows SIEM rules and queries to match on structured fields rather than regex against log lines. A compromised application server must not be able to erase or modify its own audit trail. This is a non-negotiable architectural constraint.
The write path must be one-way. The application service account has s3:PutObject but never s3:DeleteObject or s3:PutObjectAcl . Separate IAM roles manage lifecycle policies. Each log record includes the cryptographic hash of the previous record. This creates a chain where any deletion or modification of a record breaks the hash chain, making tampering detectable.
AWS CloudTrail implements this natively via the log file validation feature: each log file includes a SHA-256 digest of its contents and the digest of the previous file, all signed with a CloudTrail-owned key. Running aws cloudtrail validate-log-files detects any gap or modification. Store the chain tip in a separate, access-controlled location. Periodic verification replays the chain and checks every hash.
Audit events must leave the originating system before they can be tampered with. The pattern: If an attacker achieves root on the application server, they can corrupt the local buffer. They cannot reach the centralised platform because the application’s IAM role does not have that permission, and the shipper’s credentials are separate. The events already forwarded are already out of reach.
Running separate log stores per service makes cross-service queries impossible during an incident. All audit logs must converge to a single platform that the application cannot write to directly. The aggregation tier must be in a separate administrative domain. The team that operates production applications must not have permission to modify or delete records in the SIEM. The team that operates the SIEM must not have permission to modify production applications. This is separation of duties at the infrastructure level, not just at the policy level.
Ingest via a push model (shipper → SIEM) rather than pull. A pull-based model requires the SIEM to have read access to production systems, widening the attack surface on the SIEM’s credentials. Shipping logs to a central platform is not sufficient. You must also verify that what arrived is what was sent, and that the chain is unbroken.
AWS CloudTrail log file validation: enable it at trail creation. Each validation run checks the hash chain and reports any gaps. Automate this on a schedule: Sequence number gaps: each audit event should carry a monotonically increasing sequence number per service. The SIEM ingestion pipeline checks for gaps. A gap means either a transmission failure (recoverable from the local buffer) or deliberate deletion (security incident).
Cross-system reconciliation: for high-value events — all administrative actions, all authentication events — cross-reference counts between the source system’s local record and the SIEM. A count discrepancy triggers an alert. A single user action in a modern microservices application touches many services. A login triggers the identity service, the session service, the notification service, and potentially a risk-scoring service. An API call traverses an API gateway, an authorisation service, one or more backend services, and a database proxy. Without correlation, these events appear as independent, unrelated records.
The request ID is the correlation primitive. Generate it once, propagate it everywhere: Propagate to async workers: when an API call enqueues a background job, pass the request ID as a job attribute. The worker includes it in its audit events. One user action now correlates across synchronous and asynchronous processing. Propagate to databases: use SET application_name or SET LOCAL audit.request_id in PostgreSQL to include the request ID in pgaudit output. The database audit log then correlates with the application audit log.
The payoff: during an incident, a single SIEM query for request_id = "req_7f2a3b9c-..." returns every event produced by that user action across every service, in chronological order. Audit logging requirements are not optional recommendations. They are mandated controls in every major compliance framework: SOC 2 (CC7.2): requires that the organisation monitors system components for anomalies and that audit trails are enabled for all system components. CC7.2 specifically requires detection of anomalous activity, which requires correlated audit logs that support querying.
PCI DSS Requirement 10: the most prescriptive audit logging requirement in any framework. PCI DSS 10.2 mandates logging of: all individual user access to cardholder data, all root/administrative actions, access to audit trails, invalid logical access attempts, use of identification and authentication mechanisms, changes to identification and authentication mechanisms, and changes to system-level objects. PCI DSS 10.3 requires protecting audit logs from destruction and modification. PCI DSS 10.5 requires retaining audit logs for at least 12 months, with at least 3 months immediately available.
HIPAA (45 CFR § 164.312(b)): the Audit Controls standard requires covered entities to implement hardware, software, and/or procedural mechanisms that record and examine activity in systems that contain ePHI. HIPAA does not specify a retention period in the Security Rule, but the minimum is 6 years under the Documentation requirements (45 CFR § 164.530(j)). GDPR: audit logs themselves contain personal data (IP addresses, user identifiers). Processing audit logs is a legitimate interest (Article 6(1)(f)) and in many cases a legal obligation (Article 6(1)©). The privacy-specific requirement is that you document the lawful basis for audit log retention and do not retain logs beyond what is necessary — creating a tension with long compliance retention requirements that must be managed with explicit policy.
3. Software Implementation, Frameworks & Protocols ISO 27001 (A.8.15): requires logging of events and generation, storage, protection, and analysis of logs. The Annex A control requires that logs are protected against tampering. Retention must be defined per log category, aligned with compliance requirements, and enforced automatically: Implement retention in tiers: hot (SIEM, immediately queryable) for recent logs, warm (S3 Standard-IA or GCS Nearline) for months 3–12, cold (S3 Glacier or tape) for compliance archival. Automated lifecycle rules handle the transitions. The SIEM’s retention setting must not be the only control — the immutable object store is the retention guarantee; the SIEM is the query layer.
The people who run production systems must not be able to modify audit logs. The people who manage audit infrastructure must not be able to use their access to cover their own tracks. This requires explicit access control architecture: Implement this with IAM role separation, not just process separation. The SIEM’s administrative API must require a different role than the query API. S3 bucket policies must deny s3:DeleteObject to all roles except the automated lifecycle function, and that function must only delete records past the retention age.
All access to the audit log system itself — the SIEM, the log pipeline, the immutable store — must be logged in a meta-audit log in a separate, isolated account. A security team member querying the SIEM is logged. A pipeline configuration change is logged. The meta-audit log is the audit log for your audit log infrastructure. Audit logging architecture is not a post-deployment concern. By the time you ship the first version of a service, the schema is defined, the correlation ID is propagated, the shipper is configured, and the destination is immutable. Everything else is a forensic liability.
Discover the critical components, design considerations, and best practices for building an effective audit logging architecture that ensures security, compliance, and operational transparency within your systems. In today's complex digital landscape, maintaining security, ensuring compliance, and facilitating effective troubleshooting are paramount. A robust audit logging architecture isn't just a good practice; it's a fundamental requirement for any serious organization. But what exactly constitutes such an architecture, and how do you design one that is both effective and scalable? Audit logging involves systematically recording events within a system or application. These logs capture who did what, when, where, and how. This information is invaluable for: Agents are deployed on log sources to collect, format, and forward logs. Examples include: These agents are crucial for abstracting away the specifics of log retrieval and providing a consistent output.
This layer is responsible for securely and reliably transmitting logs from collectors to the central storage or processing layer. Key considerations include: The chosen storage solution must support the volume, velocity, and variety of your log data, as well as retention requirements. This is where the value of audit logs is realized. Security Information and Event Management (SIEM) systems are often used here.
Defined policies for how long logs are retained, where they are archived, and when they can be deleted, often dictated by compliance regulations and internal policies. To maximize the effectiveness of your audit logging architecture, follow these best practices: An intelligently designed audit logging architecture is an indispensable asset for any organization. It transforms raw system events into actionable intelligence, providing the visibility needed to detect threats, ensure compliance, and maintain the integrity of your operations. By understanding its core components and adhering to best practices, you can build a foundation of trust that protects your digital assets and strengthens your overall security posture.
For more than 30 years, CoreMedia has delivered secure content management that protects the world’s most high-stakes digital experiences. Organizations with the highest stakes rely on CoreMedia to protect their content against attacks, data leaks, and downtime, including the German Bundestag , Deutsche Bundesbank , the Australian Broadcasting Corporation and German Bundeswehr. CoreMedia has powered their digital experiences with a track record built on uptime, performance, and security.
CoreMedia supports managed cloud hosting, private cloud, and on-premises deployment — giving enterprises the flexibility to meet data sovereignty requirements and regional compliance obligations across markets. CoreMedia supports managed cloud hosting, private cloud, and on-premises deployment — giving enterprises the flexibility to meet data sovereignty requirements and regional compliance obligations across markets.
Secure content management stays ahead of threats with real-time monitoring. Identify vulnerabilities to avoid downtime with fast containment and resolution. Secure content management stays ahead of threats with real-time monitoring. Identify vulnerabilities to avoid downtime with fast containment and resolution.
Our secure content management platform maintains accountability with comprehensive audit logs. Track changes and access for easy content reversion. Our secure content management platform maintains accountability with comprehensive audit logs. Track changes and access for easy content reversion.
On our managed cloud, a web application firewall blocks OWASP Top 10 attacks and DDoS traffic, with optional bot control and application-layer protection for high-traffic sites. On our managed cloud, a web application firewall blocks OWASP Top 10 attacks and DDoS traffic, with optional bot control and application-layer protection for high-traffic sites.
Securely test features, configurations, and integrations in dedicated sandbox environments before deployment. Securely test features, configurations, and integrations in dedicated sandbox environments before deployment. Build complex applications with your choice of programming languages and tools, giving you the freedom to innovate without compromising security in CoreMedia's enterprise CMS.
Build complex applications with your choice of programming languages and tools, giving you the freedom to innovate without compromising security in CoreMedia's enterprise CMS. Enhance your platform confidently with 100+ tested extensions, plugins, and services from our marketplace for seamless compatibility and performance, all part of our secure enterprise CMS.
Enhance your platform confidently with 100+ tested extensions, plugins, and services from our marketplace for seamless compatibility and performance, all part of our secure enterprise CMS. Protect user credentials with advanced encryption and streamline access with Single Sign-On (SSO). Maintain control with precise access permissions, ensuring only authorized users can create, edit, approve, or publish content with CoreMedia's hybrid headless CMS .
Protect user credentials with advanced encryption and streamline access with Single Sign-On (SSO). Maintain control with precise access permissions, ensuring only authorized users can create, edit, approve, or publish content with CoreMedia's hybrid headless CMS . You decide where your content lives. CoreMedia's secure content management system runs on any major cloud, in your own private cloud, or fully on-premises, and can be hosted within the EU so your content is stored and processed inside Europe, in line with GDPR requirements . Hybrid setups are supported too, so sensitive workloads can stay in your own environment while the rest scales in the cloud. For teams bound by data sovereignty and residency rules, that means you control where content sits and, through role-based access, who can reach it. As your requirements change, you can move between hosting models without losing that control.
4. Practical Deployment, Analysis & Case Studies CoreMedia is developed and supported by CoreMedia GmbH in Hamburg since 1996. When both your vendor and your hosting sit under your control, you keep sovereignty over your data and know exactly where accountability lies, the assurance security-conscious organizations depend on. A European operating entity keeps your contracts, support, and escalation paths in one place, so your security and legal teams always know who is responsible for what. You can review your specific setup against the standards you answer to, working with a vendor that is clear about where it stands.
CoreMedia gives your security and compliance team a defensible foundation. The platform is ISO/IEC 27001:2022 certified and GDPR-ready , with the controls enterprise security depends on: role-based access, Single Sign-On (SSO), approval workflows, and complete audit trails that record who changed what and when. A data processing agreement governs how data is handled. As GDPR, NIS2, DORA, and the EU AI Act raise the bar on accountability, these controls let you demonstrate compliance rather than assert it, with your content held in the EU when residency is a requirement.
CoreMedia KIO works inside your existing roles and permissions, and no content is published without editor approval. Any large language model can be used, including OpenAI, Azure OpenAI, Anthropic Claude, or custom models, and you keep full control over which model processes your data. Because a named editor reviews and approves every AI-assisted change before it goes live, accountability stays with a person rather than the model, in line with the EU AI Act's emphasis on human oversight.
Stop attacks before they reach your site with a managed web application firewall, bot control, and DDoS defense Whichever deployment model you choose, CoreMedia protects your content with access controls and audit trails. On our managed cloud service, security goes further: every site runs behind a web application firewall that our team configures, reviews, and updates as threats change. It blocks the OWASP Top 10 vulnerabilities and known exploits such as Log4j, and protects against DDoS attacks at the network and transport layers, at no extra cost.
For sites that draw heavy automated traffic, CoreMedia offers the Advanced WAF Security add-on. It lets you decide which bot categories to block, allow, or monitor, from scrapers to crawlers, and adds application-layer protection against HTTP flood attacks. Rules start in monitoring mode and switch to blocking when you request it. CoreMedia's content management system (CMS) runs on any cloud platform, adhering to the highest security standards and data privacy regulations. For maximum control, it can also be deployed in private cloud setups and on-premises. If you want to stay open to migrating to the cloud in the future, we’ve taken many clients on the journey without losing the control they get from on-premise.
Keep your data secure at all times while using AI and related applications. Our secure, composable, and flexible AI solutions integrate into complex existing tech infrastructures. Compatible with any large language model (LLM), including OpenAI, Azure OpenAI, Anthropic Claude, or custom models - you maintain full control over your preferred LLM. Our secure content management system collects zero- and first-party data, from direct customer interactions, CRM systems, surveys, and custom forms, for personalized experiences your team fully controls. Because the data comes directly from your customers rather than third-party trackers, you keep consent clear and reduce compliance exposure. It stays inside your environment and under your governance rules, so personalization and GDPR accountability work together rather than against each other.
Your website demands uncompromising security, exceptional performance, and enduring stability - today, in 10 years, and beyond. With open, accessible code and an API-driven architecture, seamlessly integrate any current or future channel, device, or technology while maintaining the highest standards of security and stability. "The German Bundestag uses CoreMedia as their CMS for 10 years. They handle a lot of content, so security and scalability are huge factors. The website hasn't been down for the last few years." "What stands out with CoreMedia is the stability of the product. I never saw CoreMedia failing in over 20 years." "We are choosing CoreMedia very often for high-traffic projects, that involve many customers and many editors." "We recommend CoreMedia as a scalable, flexible, reliable, highly secure CMS with a best of breed approach." See how CoreMedia protects content for some of the world's most security-conscious organizations. Book a demo , or talk to a specialist about security, access control, and compliance for your sector.
CoreMedia holds ISO/IEC 27001:2022 certification for information security management and was awarded an EcoVadis Gold rating in 2025. Both are independently audited, so your security and procurement teams can verify CoreMedia's practices rather than take them on trust. Yes. CoreMedia is cloud agnostic. It runs on any major cloud, in a private cloud, or fully on-premises, and supports hybrid deployments where sensitive workloads stay in your own environment. Many clients have moved between models without losing control over where content sits.
A secure CMS limits who can see and change content through role-based access. CoreMedia assigns granular permissions by team, brand, and market, adds Single Sign-On (SSO) with encryption, and routes changes through approval workflows, so only authorized users can create, edit, approve, or publish content. An audit trail is a complete record of every content change: who changed what, when, and what was published. CoreMedia keeps full audit logs and supports reversions, so you can trace any change, satisfy auditors, and roll back quickly if something goes wrong.
CoreMedia KIO works inside your existing roles and permissions, and every AI suggestion requires editor approval before anything is published. You can use any large language model, including OpenAI, Azure OpenAI, Anthropic Claude, or custom models, and keep full control over which model processes your data. Public institutions and governments choose CoreMedia for secure, GDPR-ready content management. Users include the German Bundestag and Deutsche Bundesbank , alongside enterprises such as Henkel and Truity Credit Union . CoreMedia supports EU hosting, on-premise deployment, AI governance, and the audit controls regulated and public-sector organizations require.
CoreMedia is GDPR-ready and ISO/IEC 27001:2022 certified, providing role-based access, approval workflows, and audit logs as a defensible foundation for GDPR. Compliance is a shared responsibility between the platform and how you configure it. For EU hosting and data residency in depth, see our GDPR-compliant, EU-hosted CMS page. Large institutions rely on CoreMedia’s stable and trusted content management solutions Create highly engaging content for all channels, regions and languages - turbocharged by AI.
Deliver personalized experiences that adapt to each user – powered by data, insights and ongoing optimization. Automate and orchestrate campaigns across every channel – turning data into timely, relevant messages. Audit logging, or audit trails, answer a simple question: who did what, where, and when? So, in this article, we’ll answer our simple question: How can you use audit logs, and what use cases do audit logs best support? When you use a technology service or product, audit logs are generated in response to every user action and system response. These logs capture critical information that can be used to: While both audit logs and system logs record events and actions, they serve distinct purposes: Audit Logs capture who did what, where, and when. They are primarily used for compliance, security, and computer forensic investigations . Audit logs track user actions and system changes to ensure accountability and traceability. They provide a chronological record of activities, crucial for audits and compliance checks.
System Logs primarily record system events and operational activities, such as errors, performance data, and service statuses. System logs are mainly used for debugging, monitoring system health, and optimizing performance. They offer insights into the operational state and efficiency of the system. Though the micro-actions behind audit logs are essential, the broader purpose of audit logging is even more significant. The main objectives of collecting audit logs are two-fold: At every step, the systems generate and record a trail of log and metrics data or metadata. This documentation can be utilized for various use cases, including security, monitoring, performance analysis, and cyber forensics.
(Related reading: log aggregation , log management & MELT: metrics, events, logs, traces .) Access to audit logs is typically controlled based on user roles within an organization. Different roles have varying levels of access and permissions to ensure security and compliance. Common roles and their associated access levels include: 5. Performance Evaluation & Extended Technical Observations Restrictions based on roles are essential to maintain the integrity and confidentiality of audit logs. Only authorized personnel should have access to sensitive audit information, ensuring that the data is protected from unauthorized access and tampering.
In terms of cybersecurity , audit logs help to identify anomalous behavior and network traffic patterns . InfoSec teams can integrate the audit logging mechanism into their monitoring and observability solutions to extract insights on potential security incidents. Authentication and detection of unauthorized network changes, can be achieved by testing network change actions against predefined security policies — looking at the delta. These policies define how network and IT resources are allowed to be accessed – in terms of entity, location, roles, and attributes, as well as action frequency and location.
If your organization has to comply with external regulations , your organization may be required to keep specific audit logs and establish monitoring capabilities that test the systems for compliance by analyzing audit logs in real time. For instance: As with standard audit procedures, audit logging is frequently used for accountability and verification of factual information. Common applications include: In this context, audit logging is an important part of analyzing how users act and the accuracy of information recorded by the systems. For example, audit logging can quickly enable systems and uncover insights into the use of financial resources across all departments. Imagine a world where all this was straightforward: Cyber forensics is another key application domain of audit logging practices that requires the reconstruction of events and insights into a technology process. Often, this might stand up as legal evidence in a court of law.
Typically, businesses aren’t conducting cyber forensics for all their activities. Instead, we usually require cyber forensics in two situations: Audit logs outline the action sequences that connect a user to an action. Investigators can analyze audit logs to gain deeper insights into various scenarios and outcomes represented by the audit logs. This requires a thorough analysis of raw logging data before it is converted into insightful knowledge.
Considering the vast volume of network, hardware, and application logs generated at scale, IT teams can be easily overwhelmed by the audit trail data. To gain the right insights with your audit log metrics data, you can adopt the following best practices: Establish a data platform that can integrate and store data of all structural formats at scale. Data platform technologies such as a data lake commonly capture real-time log data streams with a schema-on-read consumption model.
Third-party analytics and monitoring tools integrate to make sense of this information in real-time while processing only the most relevant portions of audit logs data based on the tooling specifications for data structure. Use statistical models to generalize system behavior instead of using predefined and fixed thresholds to capture data. Since the network behavior evolves continuously, models based on machine learning can continuously learn and adapt.
These models are helpful for accurate analysis of audit logs, where thresholds for anomalous behavior can be a moving target. Store audit logging data in secure environments with high standards of confidentiality, integrity, and availability — known as the CIA triad . Modified audit logs and misconfigured networking systems can generate misleading information, and likely lead your log analysis to incorrect conclusions.
It is important to understand that data stores that integrate large volumes of real-time log data streams can grow exponentially. When designing the data platform for audit log analysis, evaluate the cost, security, and performance of your data platform against your security and compliance requirements. Additionally, implementing quotas and limits on logging uses is crucial to managing storage efficiently. Setting quotas ensures that logging does not consume excessive resources and helps maintain system performance. Define limits based on the importance and relevance of the logs, ensuring that only critical data is retained long-term.
As a developer, you're no stranger to logging. You use logs every day to debug applications, trace errors, and monitor performance. But there's a specialized category of logging that goes far beyond troubleshooting: audit logging. While application logs tell you what the system is doing, audit logs tell you what users are doing to the system. They are the official, chronological record of events and actions that have security, compliance, or business implications.
In an era of increasing cyber threats, stringent data privacy regulations, and complex distributed systems, a robust audit logging strategy is no longer a "nice-to-have"âIIit's a fundamental requirement for building secure, compliant, and trustworthy software. This guide will walk you through everything you need to know about audit logging in software development, from core concepts and best practices to common challenges and solutions.
An audit log is a security-relevant, chronological record of the sequence of activities that have occurred in a system. Each entry in the log provides evidence of a specific event, helping administrators and security teams reconstruct a timeline of actions to answer critical questions: who did what, when, and from where? Think of it like a building's security system. Application logs are like motion sensors that tell you a door opened. An audit log is the security camera footage that shows you who opened the door, what time they did it, whether they used a keycard, and which direction they went. Both are useful, but only one (audit logs) provides the complete context needed for a security investigation.
An effective audit log entry should provide enough information to reconstruct what happened, when it happened, who or what initiated the event, what resource was affected, and whether the action succeeded. Consistent, structured audit logging makes security monitoring, incident investigation, troubleshooting, and compliance auditing more reliable. The exact date and time the event occurred, preferably recorded in UTC for consistency across systems and time zones.
Establishes an accurate event timeline and helps correlate activity across applications, services, and infrastructure. Establishes who or what performed an action, supporting accountability and investigation of suspicious activity. The file, database record, account, configuration, API resource, or other asset affected by the action. Helps security teams trace requests, investigate unauthorized access attempts, and identify unusual access patterns.
Additional information relevant to the event, such as a session ID, user agent, request ID, or the before-and-after state of a modified resource. Provides additional context needed to reconstruct events, correlate related activity, and understand how a resource changed. While both are generated by an application, their purpose, audience, and content differ significantly. Confusing the two can lead to critical security gaps or bloated, unmanageable logging systems.
Concept/Planning: This starts by linking source code directly to project management. Because Bitbucket is an Atlassian product, the integration with Jira is tight. For instance, developers can reference Jira issues in their commit messages, branch names, or pull request descriptions and this automatically updates the status of the cited Jira issue (the concept) as the code moves through the workflow.
Separating your audit logs from your general application logs is a critical first step. It ensures that security-relevant information doesn't get lost in the noise of routine diagnostics and can be protected with stricter access controls and retention policies. Implementing a thorough audit logging strategy provides foundational support for several critical business and technical functions. It transforms logs from a simple diagnostic tool into a powerful asset for security, compliance, and operational intelligence.
Audit logs are a cornerstone of any effective security posture. By monitoring user activities in real-time, security teams can detect suspicious patterns that may indicate a security breach in progress. For example, a high volume of failed login attempts from a single IP address could signal a brute-force attack, while a user suddenly accessing sensitive files outside of business hours could indicate a compromised account.
Without a detailed audit trail, these actions would be invisible. According to the OWASP Top 10 (2021), âIISecurity Logging and Monitoring FailuresâII (A09:2021) remain a critical category that can directly impact visibility, incident alerting, and forensics. For many industries, audit logging is not optionalâIIit's a legal and regulatory mandate. Frameworks and regulations like SOC 2, HIPAA, GDPR, and PCI DSS all have explicit requirements for maintaining detailed audit trails.
Effective audit logs provide the irrefutable evidence needed to pass audits and avoid the significant financial penalties associated with non-compliance. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Enterprise%20content%20management • https://en.wikipedia.org/wiki/Web%20content%20management%20system • https://en.wikipedia.org/wiki/Information%20security%20audit • https://www.the-algo.com/knowledge/audit-logging-architecture • https://www.systemshardening.com/articles/cross-cutting/audit-logging-architecture/ • https://scalewithchintan.com/blog/the-foundation-of-trust-designing-robust-audit-logging-architecture • https://www.coremedia.com/content-management-system/trusted-cms-security • https://www.splunk.com/en_us/blog/learn/audit-logs.html • https://www.sonarsource.com/resources/library/audit-logging/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Secure Content Management System With Audit Logs.
[*] Metasploit Scan Running on Target Subnet for Secure Content Management System With Audit Logs... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |