Complete Technical Paper Content — Secure Data Sharing Across Multi Tenant Cloud Systems
Overview & System Context
Secure Data Sharing Across Multi Tenant Cloud Systems: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9501 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Cloud computing is defined by the International Organization for Standardization (ISO) as "a paradigm for enabling network access to a scalable and elastic pool of shareable physical or virtual resources with self-service provisioning and administration on demand". It is commonly referred to as "the cloud".
On-demand self-service: "A consumer can unilaterally provision computing capabilities, such as server time and network storage, as needed automatically without requiring human interaction with each service provider." Broad network access: "Capabilities are available over the network and accessed through standard mechanisms that promote use by heterogeneous thin or thick client platforms (e.g., mobile phones, tablets, laptops, and workstations)." Resource pooling: " The provider's computing resources are pooled to serve multiple consumers using a multi-tenant model, with different physical and virtual resources dynamically assigned and reassigned according to consumer demand." Rapid elasticity: "Capabilities can be elastically provisioned and released, in some cases automatically, to scale rapidly outward and inward commensurate with demand. To the consumer, the capabilities available for provisioning often appear unlimited and can be appropriated in any quantity at any time." Measured service: "Cloud systems automatically control and optimize resource use by leveraging a metering capability at some level of abstraction appropriate to the type of service (e.g., storage, processing, bandwidth, and active user accounts). Resource usage can be monitored, controlled, and reported, providing transparency for both the provider and consumer of the utilized service. By 2023, the International Organization for Standardization (ISO) had expanded and refined the list.
The history of cloud computing extends to the 1960s, with the initial concepts of time-sharing becoming popularized via remote job entry (RJE). The "data center" model, where users submitted jobs to operators to run on mainframes, was predominantly used during this era. This period saw broad experimentation with making large-scale computing power more accessible through time-sharing, while optimizing infrastructure, platforms, and applications to improve efficiency for end users. The "cloud" metaphor for virtualized services dates to 1994, when it was used by General Magic for the universe of "places" that mobile agents in the Telescript environment could "go". The metaphor is credited to David Hoffman, a General Magic communications specialist, based on its long-standing use in networking and telecom. The expression cloud computing became more widely known in 1996 when Compaq Computer Corporation drew up a business plan for future computing and the Internet. The company's ambition was to supercharge sales with "cloud computing-enabled applications". The business plan foresaw that online consumer file storage would likely be commercially successful. As a result, Compaq decided to sell server hardware to internet service providers. In the 2000s, the application of cloud computing began to take shape with the establishment of Amazon Web Services (AWS) in 2002, which allowed developers to build applications independently. In 2006 Amazon Simple Storage Service, known as Amazon S3, and the Amazon Elastic Compute Cloud (EC2) were released.
The following decade saw the launch of various cloud services. In 2010, Microsoft launched Microsoft Azure, and Rackspace Hosting and NASA initiated an open-source cloud-software project, OpenStack. IBM introduced the IBM SmartCloud framework in 2011, and Oracle announced the Oracle Cloud in 2012. In December 2019, Amazon launched AWS Outposts, a service that extends AWS infrastructure, services, APIs, and tools to customer data centers, co-location spaces, or on-premises facilities.
Cloud computing can shorten time to market by offering pre-configured tools, scalable resources, and managed services, allowing users to focus on core business value rather than maintaining infrastructure. Cloud platforms can enable organizations and individuals to reduce upfront capital expenditures on physical infrastructure by shifting to an operational expenditure model, where costs scale with usage. Cloud platforms also offer managed services and tools, such as artificial intelligence, data analytics, and machine learning, which might otherwise require significant in-house expertise and infrastructure investment. While cloud computing can offer cost advantages through effective resource optimization, organizations often face challenges such as unused resources, inefficient configurations, and hidden costs without proper oversight and governance. Many cloud platforms provide cost management tools, such as AWS Cost Explorer and Azure Cost Management, and frameworks like FinOps have emerged to standardize financial operations in the cloud. Cloud computing also facilitates collaboration, remote work, and global service delivery by enabling secure access to data and applications from any location with an internet connection. Cloud providers offer various redundancy options for core services, such as managed storage and managed databases, though redundancy configurations often vary by service tier. Advanced redundancy strategies, such as cross-region replication or failover systems, typically require explicit configuration and may incur additional costs or licensing fees. Cloud environments operate under a shared responsibility model, where providers are typically responsible for infrastructure security, physical hardware, and software updates, while customers are accountable for data encryption, identity and access management (IAM), and application-level security. These responsibilities vary depending on the cloud service model—Infrastructure as a Service (IaaS), Platform as a Service (PaaS), or Software as a Service (SaaS)—with customers typically having more control and responsibility in IaaS environments and progressively less in PaaS and SaaS models, often trading control for convenience and managed services.
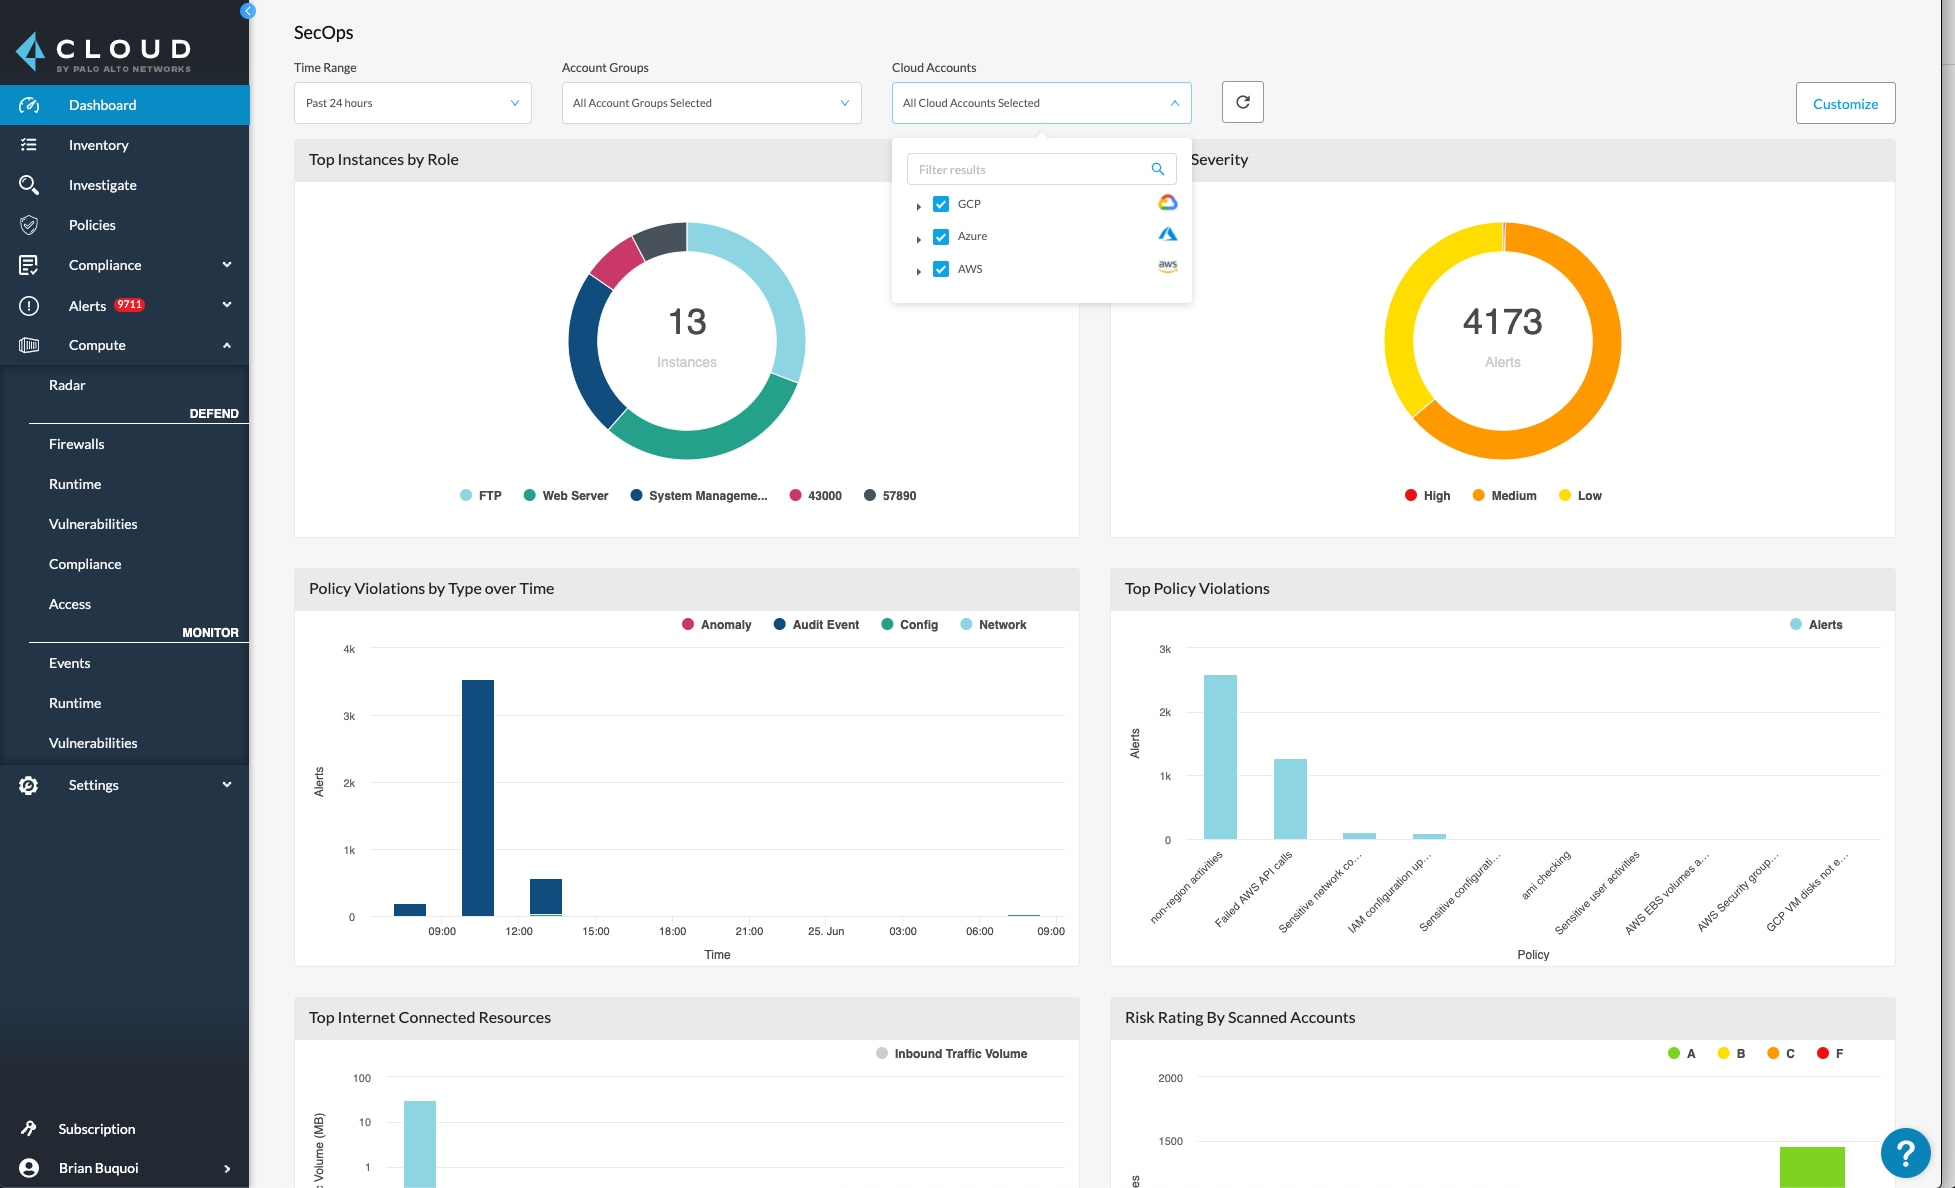
Figure 1: Avoiding the Pitfalls of the Shared Responsibility Model for Cloud ... The decision to adopt cloud computing or maintain on-premises infrastructure depends on factors such as scalability, cost structure, latency requirements, regulatory constraints, and infrastructure customization. Organizations with variable or unpredictable workloads, limited capital for upfront investments, or a focus on rapid scalability benefit from cloud adoption.
Startups, SaaS companies, and e-commerce platforms often prefer the pay-as-you-go operational expenditure (OpEx) model of cloud infrastructure. Additionally, companies prioritizing global accessibility, remote workforce enablement, disaster recovery, and leveraging advanced services such as AI/ML and analytics are well-suited for the cloud. In recent years, some cloud providers have started offering specialized services for high-performance computing and low-latency applications, addressing some use cases previously exclusive to on-premises setups. On the other hand, organizations with strict regulatory requirements, highly predictable workloads, or reliance on deeply integrated legacy systems may find cloud infrastructure less suitable. Businesses in industries like defense, government, or those handling highly sensitive data often favor on-premises setups for greater control and data sovereignty. Additionally, companies with ultra-low latency requirements, such as high-frequency trading (HFT) firms, rely on custom hardware (e.g., FPGAs) and physical proximity to exchanges, which most cloud providers cannot fully replicate despite recent advancements. Similarly, tech giants like Google, Meta, and Amazon build their own data centers due to economies of scale, predictable workloads, and the ability to customize hardware and network infrastructure for optimal efficiency. However, these companies also use cloud services selectively for certain workloads and applications where it aligns with their operational needs. In practice, many organizations are increasingly adopting hybrid cloud architectures, combining on-premises infrastructure with cloud services. This approach allows businesses to balance scalability, cost-effectiveness, and control, offering the benefits of both deployment models while mitigating their respective limitations.
One of the primary challenges of cloud computing, compared with traditional on-premises systems, is maintaining data security and privacy. Cloud users entrust their sensitive data to third-party providers, who may not have adequate measures to protect it from unauthorized access, breaches, or leaks. Cloud users also face compliance risks if they have to adhere to certain regulations or standards regarding data protection, such as GDPR or HIPAA. Another challenge of cloud computing is reduced visibility and control. Cloud users may not have full insight into how their cloud resources are managed, configured, or optimized by their providers. They may also have limited ability to customize or modify their cloud services according to their specific needs or preferences. Complete understanding of all technology may be impossible, especially given the scale, complexity, and deliberate opacity of contemporary systems; however, there is a need for understanding complex technologies and their interconnections to have power and agency within them. The metaphor of the cloud can be seen as problematic as cloud computing retains the aura of something noumenal and numinous; it is something experienced without precisely understanding what it is or how it works. Additionally, cloud migration is a significant challenge. This process involves transferring data, applications, or workloads from one cloud environment to another, or from on-premises infrastructure to the cloud. Cloud migration can be complicated, time-consuming, and expensive, particularly when there are compatibility issues between different cloud platforms or architectures. If not carefully planned and executed, cloud migration can lead to downtime, reduced performance, or even data loss.
"Understanding application dependencies" "Comparing on-premise and cloud costs" "Assessing technical feasibility." Cloud computing poses privacy concerns because the service provider can access the data that is in the cloud at any time. It could accidentally or deliberately alter or delete information. Many cloud providers can share information with third parties if necessary for purposes of law and order without a warrant. That is permitted in their privacy policies, which users must agree to before they start using cloud services. Solutions to privacy include policy and legislation as well as end-users' choices for how data is stored. Users can encrypt data that is processed or stored within the cloud to prevent unauthorized access.
Identity management systems can also provide practical solutions to privacy concerns in cloud computing. These systems distinguish between authorized and unauthorized users and determine the amount of data that is accessible to each entity. The systems work by creating and describing identities, recording activities, and getting rid of unused identities. According to the Cloud Security Alliance, the top three threats in the cloud are Insecure Interfaces and APIs, Data Loss & Leakage, and Hardware Failure—which accounted for 29%, 25% and 10% of all cloud security outages respectively. Together, these form shared technology vulnerabilities. In a cloud provider platform being shared by different users, there may be a possibility that information belonging to different customers resides on the same data server. Additionally, Eugene Schultz, chief technology officer at Emagined Security, said that hackers are spending substantial time and effort looking for ways to penetrate the cloud. "There are some real Achilles' heels in the cloud infrastructure that are making big holes for the bad guys to get into".
Because data from hundreds or thousands of companies can be stored on large cloud servers, hackers can theoretically gain control of huge stores of information through a single attack—a process he called "hyperjacking". Some examples of this include the Dropbox security breach, and iCloud 2014 leak. Dropbox had been breached in October 2014, having over seven million of its users passwords stolen by hackers in an effort to get monetary value from it by Bitcoins (BTC). By having these passwords, they are able to read private data as well as have this data be indexed by search engines (making the information public). There is the problem of legal ownership of the data (If a user stores some data in the cloud, can the cloud provider profit from it?). Many Terms of Service agreements are silent on the question of ownership. Physical control of the computer equipment (private cloud) is more secure than having the equipment off-site and under someone else's control (public cloud).
This delivers great incentive to public cloud computing service providers to prioritize building and maintaining strong management of secure services. Some small businesses that do not have expertise in IT security could find that it is more secure for them to use a public cloud. There is the risk that end users do not understand the issues involved when signing on to a cloud service (persons sometimes do not read the many pages of the terms of service agreement, and just click "Accept" without reading). This is important now that cloud computing is common and required for some services to work, for example for an intelligent personal assistant (Apple's Siri or Google Assistant). Fundamentally, private cloud is seen as more secure with higher levels of control for the owner, however public cloud is seen to be more flexible and requires less time and money investment from the user. The attacks that can be made on cloud computing systems include man-in-the middle attacks, phishing attacks, authentication attacks, and malware attacks. One of the largest threats is considered to be malware attacks, such as Trojan horses. Recent research conducted in 2022 has revealed that the Trojan horse injection method is a serious problem with harmful impacts on cloud computing systems.
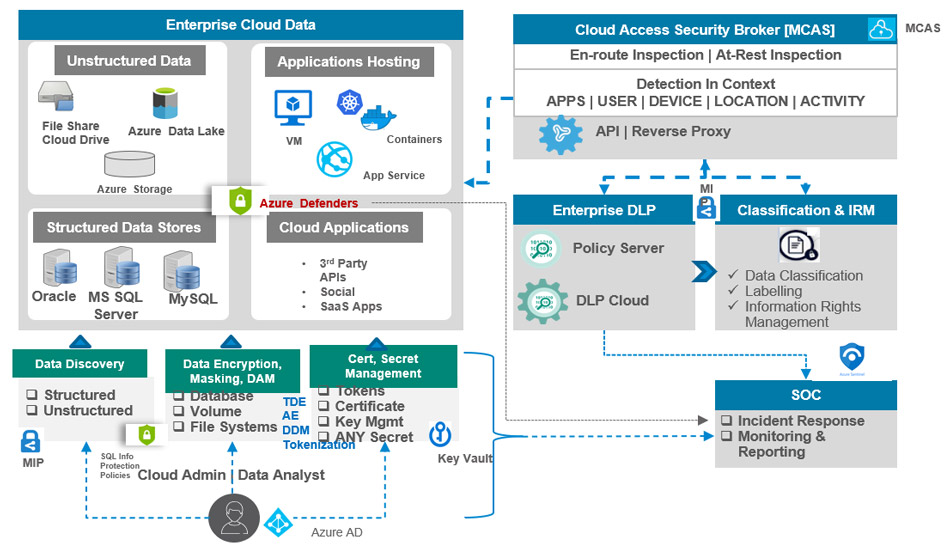
Figure 2: Overcoming Security and Compliance Challenges in a Hybrid/Multi-Cloud ... The CLOUD Act allows United States authorities to request data from cloud providers, and courts can impose nondisclosure requirements preventing providers from notifying affected users. This framework is in legal tension with Article 48 of the European General Data Protection Regulation (GDPR), which restricts the transfer of personal data in response to foreign court or administrative orders unless based on an international agreement. As a result, cloud service providers operating in both Europe and the U.S. may face competing legal obligations. According to Laura K. Donohue writing for the Harvard Journal of Law and Public Policy, cloud service providers also fall within the broader category of service providers subject to Section 702 of the Foreign Intelligence Surveillance Act (FISA), which has had documented effects on cloud providers and their customers.
The National Institute of Standards and Technology recognized three cloud service models in 2011: Infrastructure as a Service (IaaS), Platform as a Service (PaaS), and Software as a Service (SaaS). The International Organization for Standardization (ISO) later identified additional models in 2023, including "Network as a Service", "Communications as a Service", "Compute as a Service", and "Data Storage as a Service".
Infrastructure as a service (IaaS) refers to online services that provide high-level APIs used to abstract various low-level details of underlying network infrastructure like physical computing resources, location, data partitioning, scaling, security, backup, etc. A hypervisor runs the virtual machines as guests. Pools of hypervisors within the cloud operational system can support large numbers of virtual machines and the ability to scale services up and down according to customers' varying requirements. Linux containers run in isolated partitions of a single Linux kernel running directly on the physical hardware.
Linux cgroups and namespaces are the underlying Linux kernel technologies used to isolate, secure and manage the containers. The use of containers offers higher performance than virtualization because there is no hypervisor overhead. IaaS clouds often offer additional resources such as a virtual-machine disk-image library, raw block storage, file or object storage, firewalls, load balancers, IP addresses, virtual local area networks (VLANs), and software bundles.
The NIST's definition of cloud computing describes IaaS as "where the consumer is able to deploy and run arbitrary software, which can include operating systems and applications. The consumer does not manage or control the underlying cloud infrastructure but has control over operating systems, storage, and deployed applications; and possibly limited control of select networking components (e.g., host firewalls)." IaaS-cloud providers supply these resources on-demand from their large pools of equipment installed in data centers. For wide-area connectivity, customers can use either the Internet or carrier clouds (dedicated virtual private networks). To deploy their applications, cloud users install operating-system images and their application software on the cloud infrastructure. In this model, the cloud user patches and maintains the operating systems and the application software. Cloud providers typically bill IaaS services on a utility computing basis: cost reflects the number of resources allocated and consumed.
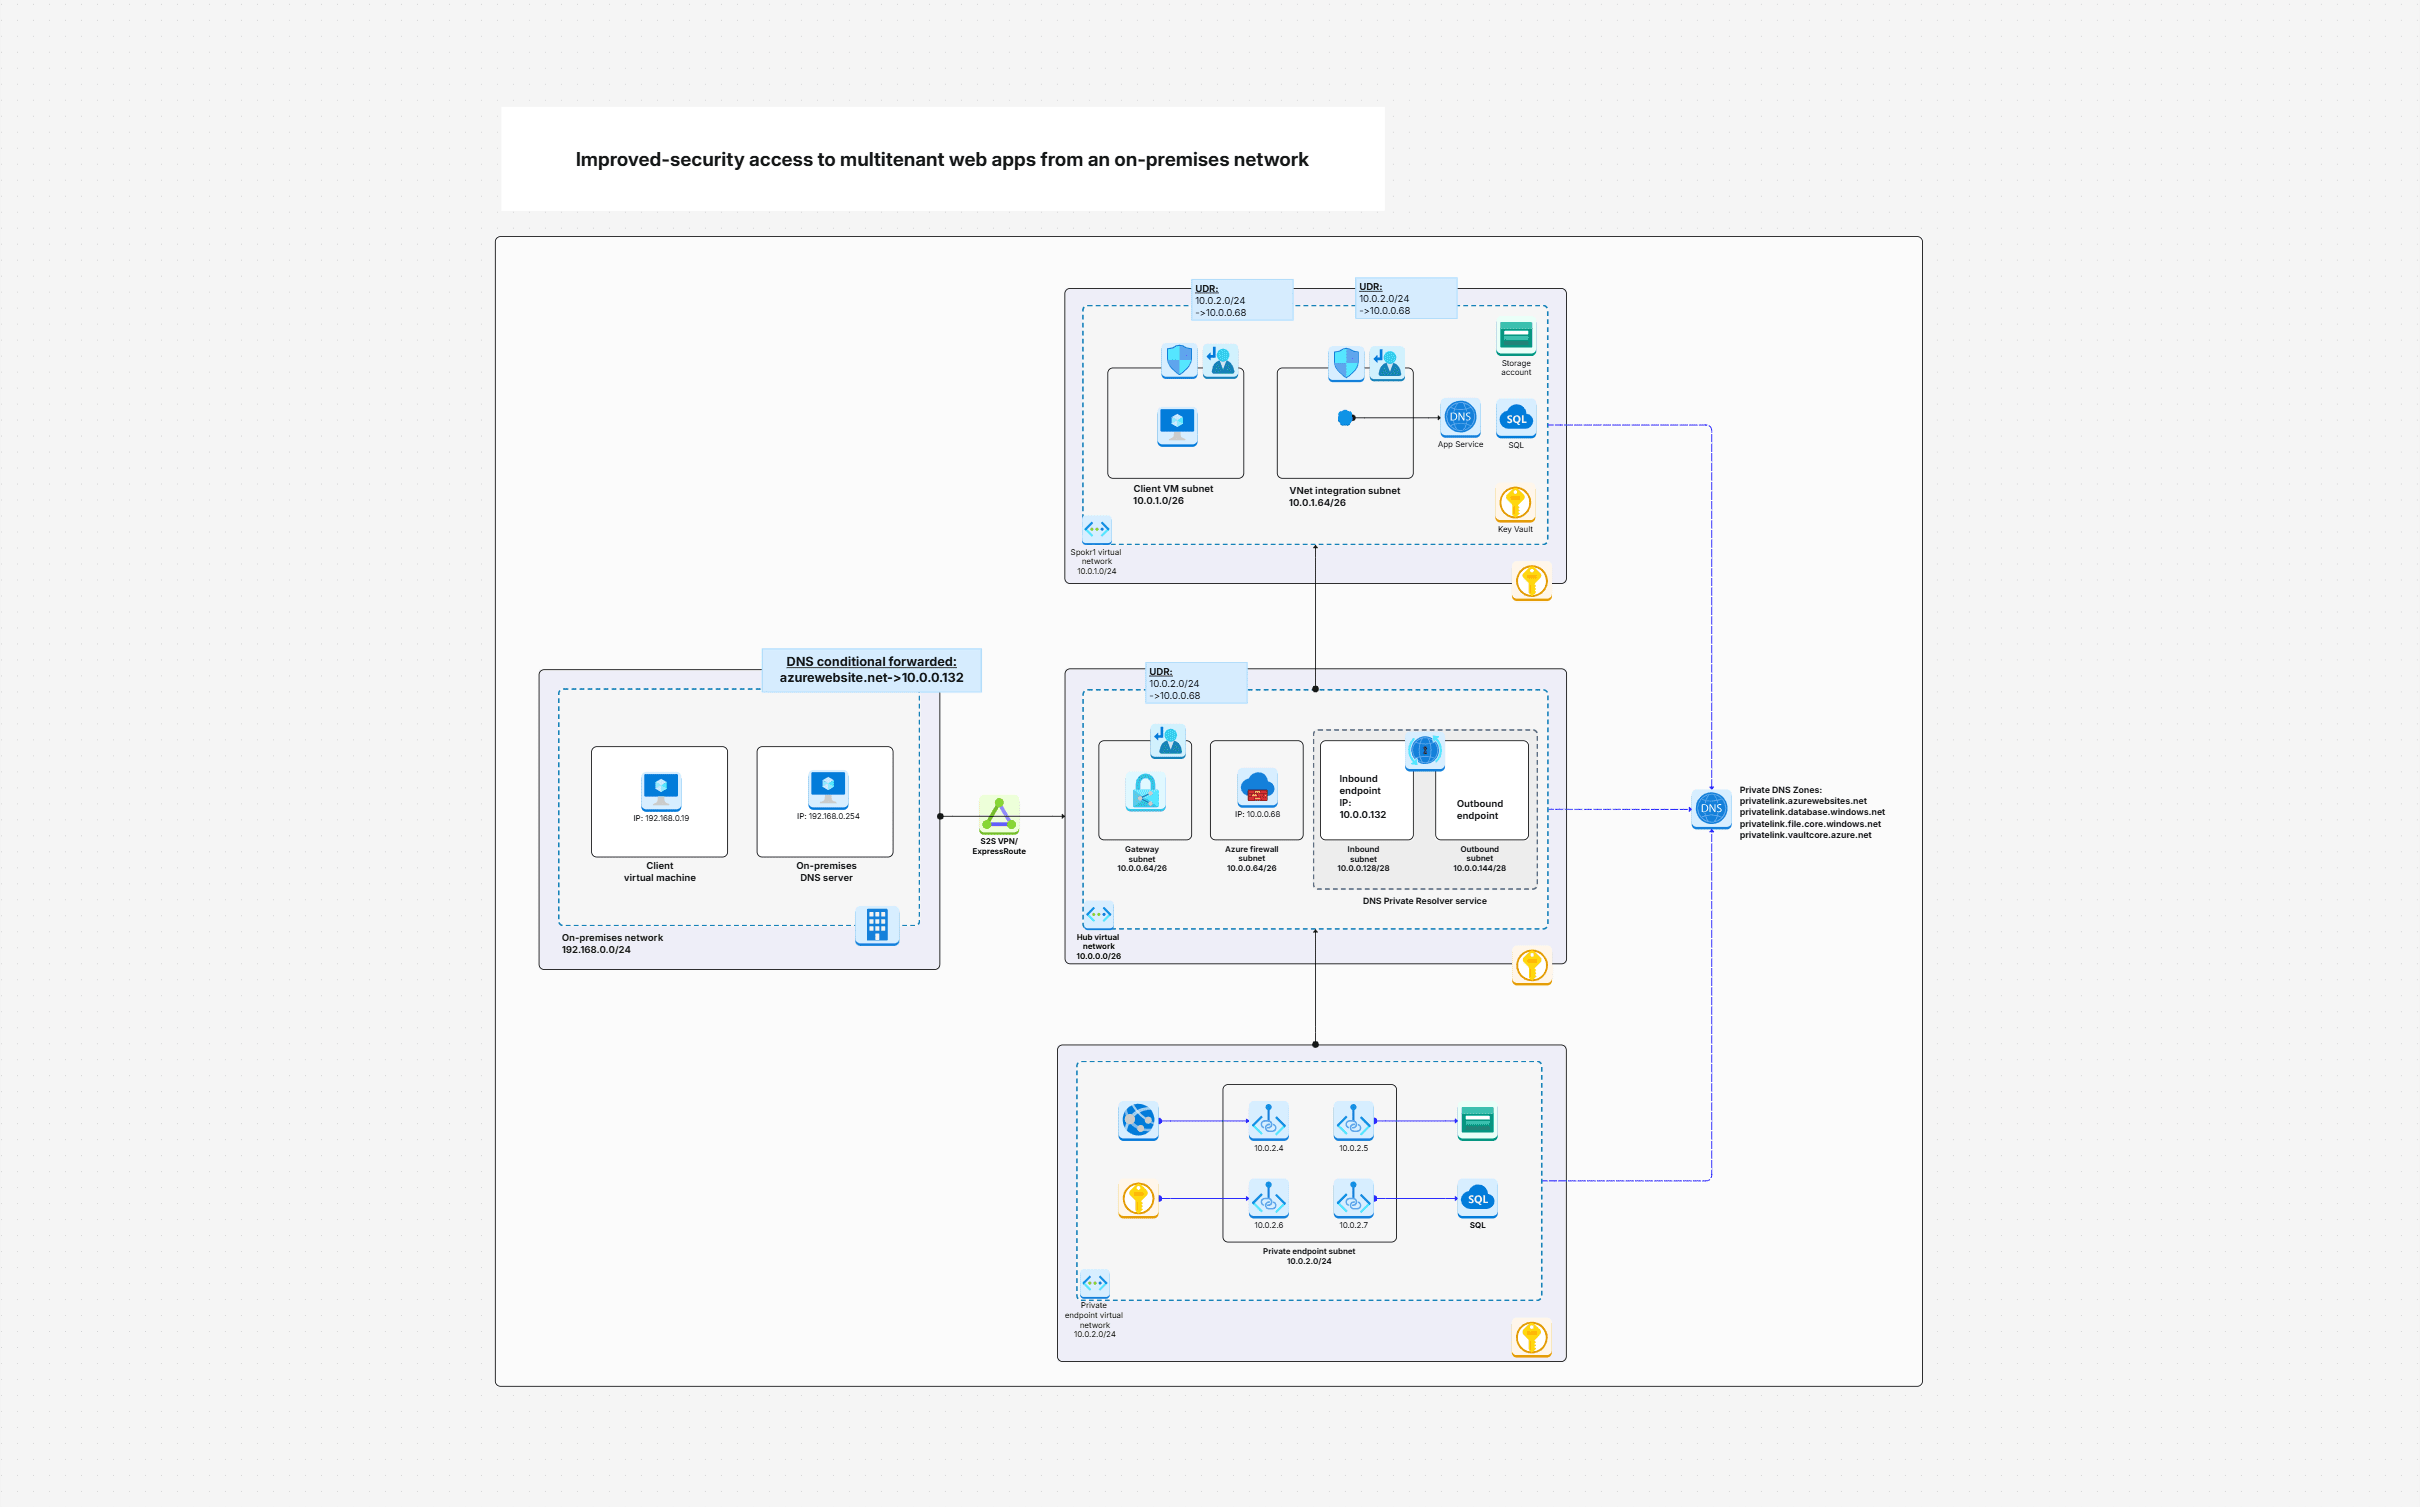
Figure 3: Secure Access To Multitenant Web Apps | On-Premise Setup 2. System Architecture & Core Working Principles The capability provided to the consumer is to deploy onto the cloud infrastructure consumer-created or acquired applications created using programming languages, libraries, services, and tools supported by the provider. The consumer does not manage or control the underlying cloud infrastructure including network, servers, operating systems, or storage, but has control over the deployed applications and possibly configuration settings for the application-hosting environment. PaaS vendors offer a development environment to application developers. The provider typically develops toolkit and standards for development and channels for distribution and payment. In the PaaS models, cloud providers deliver a computing platform, typically including an operating system, programming-language execution environment, database, and the web server.
Application developers develop and run their software on a cloud platform instead of directly buying and managing the underlying hardware and software layers. With some PaaS, the underlying computer and storage resources scale automatically to match application demand so that the cloud user does not have to allocate resources manually. Some integration and data management providers also use specialized applications of PaaS as delivery models for data. Examples include iPaaS (Integration Platform as a Service) and dPaaS (Data Platform as a Service). iPaaS enables customers to develop, execute and govern integration flows. Under the iPaaS integration model, customers drive the development and deployment of integrations without installing or managing any hardware or middleware. dPaaS delivers integration—and data-management—products as a fully managed service. Under the dPaaS model, the PaaS provider, not the customer, manages the development and execution of programs by building data applications for the customer. dPaaS users access data through data-visualization tools.
The capability provided to the consumer is to use the provider's applications running on a cloud infrastructure. The applications are accessible from various client devices through either a thin client interface, such as a web browser (e.g., web-based email), or a program interface. The consumer does not manage or control the underlying cloud infrastructure including network, servers, operating systems, storage, or even individual application capabilities, with the possible exception of limited user-specific application configuration settings. In the software as a service (SaaS) model, users gain access to application software and databases. Cloud providers manage the infrastructure and platforms that run the applications. SaaS is sometimes referred to as "on-demand software" and is usually priced on a pay-per-use basis or using a subscription fee. In the SaaS model, cloud providers install and operate application software in the cloud and cloud users access the software from cloud clients. Cloud users do not manage the cloud infrastructure and platform where the application runs. This eliminates the need to install and run the application on the cloud user's own computers, which simplifies maintenance and support. Cloud applications differ from other applications in their scalability—which can be achieved by cloning tasks onto multiple virtual machines at run-time to meet changing work demand. Load balancers distribute the work over the set of virtual machines. This process is transparent to the cloud user, who sees only a single access-point. To accommodate a large number of cloud users, cloud applications can be multitenant, meaning that any machine may serve more than one cloud-user organization. The pricing model for SaaS applications is typically a monthly or yearly flat fee per user, so prices become scalable and adjustable if users are added or removed at any point. It may also be free. Proponents claim that SaaS gives a business the potential to reduce IT operational costs by outsourcing hardware and software maintenance and support to the cloud provider. This enables the business to reallocate IT operations costs away from hardware/software spending and from personnel expenses, towards meeting other goals. In addition, with applications hosted centrally, updates can be released without the need for users to install new software. One drawback of SaaS comes with storing the users' data on the cloud provider's server. As a result, there could be unauthorized access to the data. Examples of applications offered as SaaS are games and productivity software like Google Docs and Office Online. SaaS applications may be integrated with cloud storage or File hosting services, which is the case with Google Docs being integrated with Google Drive, and Office Online being integrated with OneDrive.
Serverless computing allows customers to use various cloud capabilities without the need to provision, deploy, or manage hardware or software resources, apart from providing their application code or data. ISO/IEC 22123-2:2023 classifies serverless alongside Infrastructure as a Service (IaaS), Platform as a Service (PaaS), and Software as a Service (SaaS) under the broader category of cloud service categories. Notably, while ISO refers to these classifications as cloud service categories, the National Institute of Standards and Technology (NIST) refers to them as service models.
"A cloud deployment model represents the way in which cloud computing can be organized based on the control and sharing of physical or virtual resources." Cloud deployment models define the fundamental patterns of interaction between cloud customers and cloud providers. They do not detail implementation specifics or the configuration of resources. Cloud services are considered "public" when they are delivered over the public Internet, and they may be offered as a paid subscription, or free of charge. Architecturally, there are few differences between public- and private-cloud services, but security concerns increase substantially when services (applications, storage, and other resources) are shared by multiple customers. Most public-cloud providers offer direct-connection services that allow customers to securely link their legacy data centers to their cloud-resident applications. Several factors like the functionality of the solutions, cost, integrational and organizational aspects as well as safety & security are influencing the decision of enterprises and organizations to choose a public cloud or on-premises solution.
Hybrid cloud is a composition of a public cloud and a private environment, such as a private cloud or on-premises resources, that remain distinct entities but are bound together, offering the benefits of multiple deployment models. Hybrid cloud can also mean the ability to connect collocation, managed or dedicated services with cloud resources. Gartner defines a hybrid cloud service as a cloud computing service that is composed of some combination of private, public and community cloud services, from different service providers. A hybrid cloud service crosses isolation and provider boundaries so that it cannot be simply put in one category of private, public, or community cloud service. It allows one to extend either the capacity or the capability of a cloud service, by aggregation, integration or customization with another cloud service. Varied use cases for hybrid cloud composition exist. For example, an organization may store sensitive client data in house on a private cloud application, but interconnect that application to a business intelligence application provided on a public cloud as a software service. This example of hybrid cloud extends the capabilities of the enterprise to deliver a specific business service through the addition of externally available public cloud services. Hybrid cloud adoption depends on a number of factors such as data security and compliance requirements, level of control needed over data, and the applications an organization uses. Another example of hybrid cloud is one where IT organizations use public cloud computing resources to meet temporary capacity needs that can not be met by the private cloud. This capability enables hybrid clouds to employ cloud bursting for scaling across clouds.
Cloud bursting is an application deployment model in which an application runs in a private cloud or data center and "bursts" to a public cloud when the demand for computing capacity increases. A primary advantage of cloud bursting and a hybrid cloud model is that an organization pays for extra compute resources only when they are needed. Cloud bursting enables data centers to create an in-house IT infrastructure that supports average workloads, and use cloud resources from public or private clouds, during spikes in processing demands.
According to ISO/IEC 22123-1: "multi-cloud is a cloud deployment model in which a customer uses public cloud services provided by two or more cloud service providers". Poly cloud refers to the use of multiple public clouds for the purpose of leveraging specific services that each provider offers. It differs from Multi cloud in that it is not designed to increase flexibility or mitigate against failures but is rather used to allow an organization to achieve more than could be done with a single provider.
fragmentation of the digital single market across the EU concerns about contracts including reservations about data access and ownership, data portability, and change control variations in standards applicable to cloud computing The Communication set out a series of "digital agenda actions" which the Commission proposed to undertake in order to support the development of a fair and effective market for cloud computing services.
Client–server model – Client–server computing refers broadly to any distributed application that distinguishes between service providers (servers) and service requestors (clients). Computer bureau – A service bureau providing computer services, particularly from the 1960s to 1980s. Grid computing – A form of distributed and parallel computing, whereby a 'super and virtual computer' is composed of a cluster of networked, loosely coupled computers acting in concert to perform very large tasks. Fog computing – Distributed computing paradigm that provides data, compute, storage and application services closer to the client or near-user edge devices, such as network routers. Furthermore, fog computing handles data at the network level, on smart devices and on the end-user client-side (e.g. mobile devices), instead of sending data to a remote location for processing. Utility computing – The "packaging of computing resources, such as computation and storage, as a metered service similar to a traditional public utility, such as electricity." Peer-to-peer – A distributed architecture without the need for central coordination. Participants are both suppliers and consumers of resources (in contrast to the traditional client-server model). Cloud sandbox – A live, isolated computer environment in which a program, code or file can run without affecting the application in which it runs.
A data center is a physical room, building, or facility for storing, managing, and disseminating data and information, including computer systems and associated components, housing IT infrastructure, and training artificial intelligence. The United States' act of Congress, the Energy Independence and Security Act of 2007, defines a data center as "any facility that primarily contains electronic equipment used to process, store, and transmit digital information." This includes "a free-standing structure" or "a facility within a larger structure, that uses environmental control equipment to maintain the proper conditions for the operation of electronic equipment." According to IBM, data centers date back to the 1940s, with the U.S. military's Electrical Numerical Integrator and Computer (ENIAC) as an early example. Data centers have different models depending on their workloads. An enterprise (on-premises) model hosts IT infrastructure and data on-premises, while cloud data centers, including hyperscale data centers, house IT infrastructure resources through an internet connection used by cloud service providers such as Amazon Web Services, Google Cloud Platform, IBM Cloud, and Microsoft Azure. They frequently contain thousands of servers and many miles of high-speed data connection equipment, with the largest occupying up to 10,000,000 sq ft (930,000 m2). Managed service data centers have third-party managers hired on behalf of a company, which leases the equipment and infrastructure instead of buying it. Colocation data centers allow companies to rent space in an off-site data center owned by others, with the colocation data center hosting the infrastructure while the company provides and manages the components. Edge data centers are smaller, decentralized facilities located closer to end users and devices. In the 2024 U.S. Data Center Energy Usage Report, Lawrence Berkeley National Laboratory estimated that hyperscale and colocation centers contained 74% of computer servers in 2023. Large data centers require significant energy to operate, with the largest consuming over 3,000 MW, raising concerns about energy use. The International Energy Agency (IEA) estimated that electricity consumption from these data centers amounted to around 415 terawatt hours (TWh), about 1.5% of global electricity consumption in 2024, with a growth rate of 12% per year over the previous five years. The IEA projects that this amount could double to reach around 945 TWh by 2030, growing by around 15% per year. In the U.S. alone, which has almost nine times more data centers than any other country, power consumption by data centers is projected to account for "almost half of the growth in electricity demand between now and 2030." This includes increased electricity costs. Concerns over environmental impacts, energy and water use, and other costs have led to opposition to new data centers during the AI boom. These movements have occurred in parts of Europe, the U.S., and South America. Data Center Watch's first report covered a period from May 2024 to March 2025, during which it found that "local opposition had blocked or delayed a total of $64 billion in data center projects (six projects were blocked entirely, while 10 were delayed)." Data centers also represent a significant driver of economic activity and technological capacity. In the United States, the industry contributed an estimated $486 billion to GDP and supported 4.2 million total jobs in 2021, with each direct position generating more than six additional jobs elsewhere in the economy, according to a PwC economic impact analysis. Independent academic research has further found measurable employment and wage effects in local labor markets where large facilities are built. At the same time, the rapid expansion of data centers has raised concerns about resource consumption, including increased electricity costs, and has prompted opposition to new projects in parts of Europe, the United States, and South America.
Data centers are usually classified according to their ownership model, scale, and intended use. Distribution of computing workloads across these four categories has shifted dramatically over the past decade, with hyperscale and colocation collectively accounting for approximately 74% of U.S. server energy consumption in 2023, up from less than 40% in 2014; this share is projected to reach 85% by 2028. However, these classifications are not mutually exclusive from each other, and they may overlap depending on the operational structure and service model of the particular data center.
3. Software Implementation, Frameworks & Protocols Hyperscale data centers are large-scale facilities, typically exceeding 100 megawatts of power capacity, designed to support massive, scalable computing workloads for cloud services, AI training, and large-scale data processing. By the end of 2024, there were 1,136 operational hyperscale data centers globally, a figure that doubled over the previous five years, with the U.S.
accounting for approximately 54% of total hyperscale capacity. In particular, the three largest operators, Amazon Web Services, Microsoft Azure, and Google Cloud, collectively account for approximately 59% of all hyperscale data center capacity globally. As a growing trend, hyperscale data centers represented about 41% of worldwide data center capacity in 2024 and are projected to exceed 60% by 2029 as enterprise on-premises infrastructure continues to decline. AI data centers are being built more rapidly than conventional data centers; the International Energy Agency notes that while a typical data center can consume as much electricity as 100,000 households, the largest next-generation campuses currently under construction are expected to demand roughly 20 times that amount.
Modularity and flexibility are key elements in allowing a data center to grow and change over time. Data center modules are pre-engineered, standardized building blocks that can be configured and moved as needed. A modular data center may consist of data center equipment contained within shipping containers or similar portable containers. Components of the data center can be prefabricated and standardized, which facilitates moving if needed. These modular data centers are useful for IT disaster recovery. Mobile data centers are also used to move large quantities of data, by physically transporting the hardware that contains it, and in cryptocurrency mining, where fleets of mobile data centers are transported to take advantage of cheaper sources of energy.
Data centers have their roots in the huge computer rooms of the 1940s, typified by the Electronic Numerical Integrator and Computer (ENIAC), one of the earliest examples of what has become known as a data center. Early computer systems were complex to operate and maintain, and required a special environment in which to operate. Many cables were necessary to connect all of the components, and methods to accommodate and organize these were devised, such as standard racks to mount equipment, raised floors, and cable trays (installed overhead or under the elevated floor). A single mainframe required a great deal of power and had to be cooled to avoid overheating. Security became important— computers were expensive, and were often used for government and military purposes. As such, basic design guidelines for controlling access to the computer room were devised. During the microcomputer industry boom of the 1980s, computers started to be deployed everywhere, in many cases with little or no care about operating requirements. However, as information technology (IT) operations started to grow in complexity, organizations grew aware of the need to control IT resources. The availability of inexpensive networking equipment, coupled with new standards for the network structured cabling, made it possible to use a hierarchical design that put servers in a specific room inside the company. The use of the term data center, as applied to specially designed computer rooms, started to gain popular recognition about this time. During the dot-com bubble (1997–2000), there was a boom in data center construction because companies needed fast Internet connectivity and non-stop operation to establish their Internet presence. Many companies started building very large facilities, called internet data centers (IDCs), which provided enhanced capabilities, such as crossover backup: "If a Bell Atlantic line is cut, we can transfer them to ... to minimize the time of outage." The global data center market saw steady growth in the 2010s, with a notable acceleration in the latter half of the decade. According to Gartner, worldwide data center infrastructure spending reached $200 billion in 2021, representing a 6% increase from 2020 despite economic challenges posed by the COVID-19 pandemic. In 2024, global energy consumption from data centers was 620 TWh, with 80% of that consumption concentrated in the U.S., China, and the United Kingdom. Colocation centers were the most common category worldwide, with 4,799 colocation centers in 127 countries. In that year, the largest data center in the world was Citadel, owned by Switch, at the Tahoe Reno Industrial Center in Reno, Nevada, occupying 7.2 million square feet. Growth of the data center industry has prompted local resistance. A 2023 survey found social mobilizations against the industry in Europe, the U.S., and South America. These movements expressed concern about the centers' energy and water use, pollution, and impact on agriculture or the landscape. A 2026 poll by Politico suggested that resistance to growth of the industry would make candidates' stance on data centers a significant issue for voters in the U.S.
Data centers house critical computing resources in a controlled environment and must generally operate with very high availability. Key design elements include providing power for the equipment, temperature and humidity control, cabling, fire safety, and security. Information security is also a concern. For this reason, a data center must provide a secure environment that minimizes the risk of a security breach.
Operate and manage a carrier's telecommunication network Translate raw consumption data into usage metrics that integrate directly with utility billing and customer service platforms Continuously monitor data streams to alert utilities of irregular spikes, line leaks, or power outages. Provide data center-based applications directly to the carrier's customers Provide hosted applications for a third party to provide services to their customers Provide a combination of these and similar data center applications Power supplies, either back up or continuous onsite power, consist of one or more uninterruptible power supplies, battery banks, diesel, gas turbine, and/or gas engine generating sets. Greater primary fuel energy efficiency can be achieved with the use of cogeneration technology, generating electricity, heating, and cooling onsite. To prevent single points of failure, all elements of the electrical systems, including backup systems, are typically given redundant copies, and critical servers are connected to both the A-side and B-side power feeds. This arrangement is often made to achieve N+1 redundancy in the systems. Static transfer switches are sometimes used to ensure instantaneous switchover from one supply to the other in the event of a power failure.
Data centers feature fire protection systems, including passive and active design elements, as well as implementation of fire prevention programs in operations. Smoke detectors are usually installed to provide early warning of a fire. Although the main room usually does not allow a wet pipe sprinkler system due to the fragile nature of printed circuit boards, some systems can be used in the rest of the facility or in cold/hot aisle air circulation systems that are closed systems. These include fire sprinkler systems and misting, the latter of which uses high pressure to create extremely small water droplets and can be used in sensitive rooms because of their size. However, there are other means to put out fires, especially in sensitive areas, usually using gaseous fire suppression, of which Halon gas was the most popular until the negative effects of producing and using it were discovered.
Physical access to data centers is usually restricted. Layered security often starts with fencing, bollards, and mantraps. Video camera surveillance and permanent security guards are almost always present if the data center is large or contains sensitive information. Fingerprint recognition is becoming commonplace. Logging access is required by some data protection regulations; some organizations tightly integrate it with access control systems. Multiple log entries can occur at the main entrance, entrances to internal rooms, and at equipment cabinets. Access control at cabinets can be integrated with intelligent power distribution units, so locks are networked through the same appliance.
The first raised floor computer room was made by IBM in 1956 to allow access for wiring. During the 1970s, raised floors became more common because they allow cool air to circulate more efficiently. A raised floor standards guide (GR-2930) was developed by Telcordia Technologies, a subsidiary of Ericsson. External sources of noise include heating, ventilation, and air conditioning equipment and energy generators.
Various metrics exist to measure the data-availability that results from data-center availability beyond 95% uptime, with the top of the scale counting how many nines can be placed after 99%. The costs of avoiding downtime should not exceed the cost of the downtime itself. Dynamic infrastructure provides the ability to intelligently, automatically, and securely move workloads within a data center anytime, anywhere, for migrations, provisioning, to enhance performance, or build colocation centre facilities. It also facilitates performing routine maintenance on either physical or virtual systems, all while minimizing interruption. A related concept is Composable Infrastructure, which allows dynamic reconfiguration of available resources to suit needs only when needed. Side benefits include: 4. Practical Deployment, Analysis & Case Studies reducing cost facilitating business continuity and high availability enabling cloud and grid computing.
Communications in modern data centers are most often based on networks running the Internet protocol suite. Data centers contain a set of routers and switches that transport traffic between the servers and to the outside world, which are connected according to the data center network architecture. Redundancy of the internet connection is often provided by using two or more upstream service providers (see also multihoming). Some of the servers at a data center are used for running the basic internet and intranet services needed by internal users in the organization (e.g., e-mail servers, proxy servers, and DNS servers). Network security elements are also usually deployed: firewalls, VPN gateways, intrusion detection systems, and so on. Also common are monitoring systems for the network and for some applications. Additional off-site monitoring systems are also typical in case of a communications failure inside the data center.
Energy consumption and the environmental impacts it creates are a central issue for data centers. Power draw ranges from a few kilowatts (kW) for small server racks to several tens of megawatts (MW) for large facilities. Modern hyperscale data centers can exhibit power densities exceeding 100 times those of conventional office buildings, primarily due to the high concentration of servers and cooling systems required to manage continuous digital workloads. For higher power density facilities, electricity costs are a dominant operating expense and account for over 10% of the total cost of ownership (TCO) of a data center. As of 2024, data centers in the U.S. are primarily powered by natural gas, which supplies 40% of their electricity (with renewable energy at 24%, nuclear at about 20%, and coal at about 15%). The Associated Press reported that electricity for AI data centers in the U.S. would likely come from natural gas or oil, as companies prefer using currently available power plants, which primarily use fossil fuels. Fossil energy is also often cheaper in locations where data centers are developed, and experts believe that energy demands from generative AI and data centers would be difficult to fulfill with renewable energy alone. Some companies such as Google, Amazon, and Meta have expressed interest in nuclear power for their data centers.
As of 2020, according to the IEA, solar photovoltaic-generated electricity is at its lowest cost in history. Other data centers, including xAI's Colossus, OpenAI's Stargate, and Meta's Prometheus use their own off-grid natural gas plants. Electric vehicle and lithium-ion batteries have also been used for powering data centers, including for Colossus. Power utility companies upgrade their infrastructure to handle the demands of new data centers, and the cost of these changes typically falls on residential or smaller commercial consumers. In 2025, the Mountain Valley Pipeline announced plans to expand its capacity by 25% to meet energy needs for data centers. In December 2025, the Federal Energy Regulatory Commission (FERC) issued a unanimous order allowing data centers in the U.S. to connect directly to power plants. United States Secretary of Energy Chris Wright expressed support for un-retiring coal plants to power AI data centers. Electricity demands from AI data centers have slowed or reversed the retirement of peaking power plants in the U.S. For example, in 2025, Southern Company announced that energy use from data centers would prevent the company from retiring coal-fired power plants as it had earlier promised. In Nevada, the Desert Research Institute (DRI) calculated that 35% of the state's energy production could go to data centers by the year 2030 if all projects planned in the state as of 2026 are completed. DRI also stated, in areas where there are clusters of data centers, local consumers may end up paying the extra cost of expanding infrastructure.
The most commonly used energy-efficiency metric for data centers is power usage effectiveness (PUE), calculated as the ratio of total power entering the data center to the power used by IT equipment. PUE = ITotal Facility Power/IT Equipment PowerI = 1 + INon IT Facility Energy/IT Equipment EnergyI PUE measures the percentage of power used by overhead devices (cooling, lighting, etc.). The average U.S. data center has a PUE of 2.0, meaning two watts of total power (overhead + IT equipment) for every watt delivered to IT equipment. State-of-the-art data centers are estimated to have a PUE of roughly 1.2. Google publishes quarterly efficiency metrics from its data centers in operation. PUEs of as low as 1.01 have been achieved with two-phase immersion cooling. The EPA has an Energy Star rating for standalone or large data centers. To qualify for the ecolabel, a data center must be within the top quartile in energy efficiency of all reported facilities. The Energy Efficiency Improvement Act of 2015 (U.S.) requires federal facilities—including data centers—to operate more efficiently. California's Title 24 (2014) of the California Code of Regulations mandates that every newly constructed data center have some form of airflow containment to optimize energy efficiency. The European Union (EU) also has a similar initiative: EU Code of Conduct for Data Centres. Efficiency improvements and renewable energy integration are helping to offset some emissions, but fossil fuels remain a major source of electricity for data center operations worldwide. In 2011, server racks in data centers were designed for more than 25 kW, and the typical server was estimated to waste about 30% of the electricity it consumed. The energy demand for information storage systems is also rising. A high-availability data center is estimated to have a 1 MW demand and consume $20 million in electricity over its lifetime, with cooling accounting for 35% to 45% of the data center's total cost of ownership. Calculations show that in two years, the cost of powering and cooling a server could be equal to the cost of purchasing the server hardware. Research in 2018 showed that a substantial amount of energy could still be conserved by optimizing IT refresh rates and increasing server use. Research for optimizing task scheduling is also underway, with researchers looking to implement energy-efficient scheduling algorithms that could reduce energy consumption by anywhere between 6% and 44%. The International Energy Agency has estimated that the energy efficiency of AI-related computer chips improved more than 100-fold between 2008 and 2023. In 2011, Facebook, Rackspace, and others founded the Open Compute Project (OCP) to develop and publish open standards for greener data center computing technologies. As part of the project, Facebook published the designs of its server, which it had built for its first dedicated data center in Prineville. Making servers taller left space for more effective heat sinks and enabled the use of fans that moved more air with less energy. By not buying commercial off-the-shelf servers, energy consumption from unnecessary expansion slots on the motherboard and unneeded components, such as a graphics card, was also reduced. In 2016, Google joined the project and published the designs of its 48V DC shallow data center rack. This design had long been part of Google data centers. By eliminating the multiple transformers usually deployed in data centers, Google had achieved a 30% increase in energy efficiency. In 2017, sales for data center hardware built to OCP designs topped $1.2 billion and are expected to reach $6 billion by 2021.
Power is the largest recurring cost to the user of a data center. In 2008, the ASHRAE recommended a temperature range of 64.4 °F (18.0 °C) to 80.6 °F (27.0 °C), though some data centers could operate at higher temperatures. However, cooling at or below 70 °F (21 °C) wastes money and energy. Furthermore, overcooling equipment in environments with a high relative humidity can expose equipment to a high amount of moisture that facilitates the growth of salt deposits on conductive filaments in the circuitry. A power and cooling analysis, also referred to as a thermal assessment, measures the relative temperatures in specific areas as well as the capacity of the cooling systems to handle specific ambient temperatures. A power and cooling analysis can help identify hot spots, over-cooled areas that can handle greater power use density, the breakpoint of equipment loading, the effectiveness of a raised-floor strategy, and optimal equipment positioning (such as AC units) to balance temperatures across the data center. Power cooling density is a measure of how much square footage the center can cool at maximum capacity. The cooling of data centers is the second largest power consumer after servers, with cooling taking about 7% to 30% of energy usage (depending on efficiency), compared to an average of 60% of energy used by servers.
Computational fluid dynamics (CFD) analysis uses sophisticated tools and techniques to understand the unique thermal conditions present in each data center—predicting the temperature, airflow, and pressure behavior of a data center to assess performance and energy consumption using numerical modeling. By predicting the effects of these environmental conditions, CFD analysis can be used to predict the impact of high-density racks mixed with low-density racks and the onward impact on cooling resources, poor infrastructure management practices, and AC failure or AC shutdown for scheduled maintenance.
Data centers consume large amounts of power, split between two main uses: running the equipment and cooling it. Power efficiency reduces the first category. Cooling cost reduction through natural means includes location decisions. When the focus is on avoiding good fiber connectivity, power grid connections, and people concentrations for equipment management, a data center can be miles away from users. Mass data centers like Google or Facebook do not need to be near population centers. Arctic locations that can use outside air for cooling are becoming more popular. Countries with favorable conditions, such as Canada, Finland, Sweden, Norway, and Switzerland are trying to attract cloud computing data centers. Singapore lifted a three-year ban on new data centers in April 2022. A major data center hub for the Asia-Pacific region, Singapore lifted its moratorium on new data center projects in 2022, granting four new projects, but rejecting more than 16 data center applications from over 20 received. Singapore's new data centers will meet very strict green technology criteria, including "Water Usage Effectiveness (WUE) of 2.0/MWh, Power Usage Effectiveness (PUE) of less than 1.3, and have a "Platinum certification under Singapore's BCA-IMDA Green Mark for New Data Centre" criteria that clearly addressed decarbonization and use of hydrogen cells or solar panels.
Housing data centers in space has been proposed for low Earth orbit (LEO). The theoretical advantages are that of space-based solar power, in addition to aiding in weather forecasting and weather prediction computation from weather satellites, and the ability to freely scale up. However, it is difficult to design cooling systems in space, as convection is not available and sunlight causes large temperature fluctuations. Other challenges include damage from cosmic rays and micrometeorites. Beyond questions of technical feasibility, expanding data centers presence in space has been described as the application of colonial ideology, which considers "foreign land" as readily available for resources extraction.
The design and shape of data centers could change rapidly in the not-too-distant future with the advent of new technologies, such as quantum computing, biocomputation, and synthetic DNA data storage, as examples. Lawrence Berkeley Lab – Research, development, demonstration, and deployment of energy-efficient technologies and practices for data centers DC Power For Data Centers Of The Future – FAQ: 380VDC testing and demonstration at a Sun data center. White Paper – Property Taxes: The New Challenge for Data Centers The European Commission H2020 EURECA Data Centre Project Archived August 25, 2021, at the Wayback Machine – Data centre energy efficiency guidelines, extensive online training material, case studies/lectures (under events page), and tools. Chia, Liu Ee and Cornaggia, Jess and Haushalter, David and Wang, Qiang, Capital without Labor: Data Centers and the Local Economy (August 31, 2026).
Confidential computing is a security and privacy-enhancing computational technique focused on protecting data in use. Confidential computing can be used in conjunction with storage and network encryption, which protect data at rest and data in transit respectively. It is designed to address software, protocol, cryptographic, and basic physical and supply-chain attacks, although some critics have demonstrated architectural and side-channel attacks effective against the technology. The technology protects data in use by performing computations in a hardware-based trusted execution environment (TEE).
Confidential data is released to the TEE only once it is assessed to be trustworthy. Different types of confidential computing define the level of data isolation used, whether virtual machine, application, or function, and the technology can be deployed in on-premise data centers, edge locations, or the public cloud. It is often compared with other privacy-enhancing computational techniques such as fully homomorphic encryption, secure multi-party computation, and Trusted Computing. Confidential computing is promoted by the Confidential Computing Consortium (CCC) industry group, whose membership includes major providers of the technology.
5. Performance Evaluation & Extended Technical Observations Data confidentiality: "Unauthorized entities cannot view data while it is in use within the TEE". Data integrity: "Unauthorized entities cannot add, remove, or alter data while it is in use within the TEE". Code integrity: "Unauthorized entities cannot add, remove, or alter code executing in the TEE". In addition to trusted execution environments, remote cryptographic attestation is an essential part of confidential computing. The attestation process assesses the trustworthiness of a system and helps ensure that confidential data is released to a TEE only after it presents verifiable evidence that it is genuine and operating with an acceptable security posture. It allows the verifying party to assess the trustworthiness of a confidential computing environment through an "authentic, accurate, and timely report about the software and data state" of that environment.
"Hardware-based attestation schemes rely on a trusted hardware component and associated firmware to execute attestation routines in a secure environment". Without attestation, a compromised system could deceive others into trusting it, claim it is running certain software in a TEE, and potentially compromise the confidentiality or integrity of the data being processed or the integrity of the trusted code.
Virtual machine isolation Application isolation, also known as process isolation Function isolation, also known as library isolation Virtual machine isolation removes the elements controlled by the computer infrastructure or cloud provider, but allows potential data access by elements inside a virtual machine running on the infrastructure. Application or process isolation permits data access only by authorized software applications or processes. Function or library isolation is designed to permit data access only by authorized subroutines or modules within a larger application, blocking access by any other system element, including unauthorized code in the larger application.
Software attacks: including attacks on the host’s software and firmware. This may include the operating system, hypervisor, BIOS, other software and workloads. Protocol attacks: including "attacks on protocols associated with attestation as well as workload and data transport". This includes vulnerabilities in the "provisioning or placement of the workload" or data that could cause a compromise. Cryptographic attacks: including "vulnerabilities found in ciphers and algorithms due to a number of factors, including mathematical breakthroughs, availability of computing power and new computing approaches such as quantum computing". The CCC notes several caveats in this threat vector, including relative difficulty of upgrading cryptographic algorithms in hardware and recommendations that software and firmware be kept up-to-date. A multi-faceted, defense-in-depth strategy is recommended as a best practice. Basic physical attacks: including cold boot attacks, bus and cache snooping and plugging attack devices into an existing port, such as a PCI Express slot or USB port. Basic upstream supply-chain attacks: including attacks that would compromise TEEs through changes such as added debugging ports. The degree and mechanism of protection against these threats varies with specific confidential computing implementations.
Sophisticated physical attacks: including physical attacks that "require long-term and/or invasive access to hardware" such as chip scraping techniques and electron microscope probes. Upstream hardware supply-chain attacks: including attacks on the CPU manufacturing process, CPU supply chain in key injection/generation during manufacture. Attacks on components of a host system that are not directly providing the capabilities of the trusted execution environment are also generally out-of-scope. Availability attacks: confidential computing is designed to protect the confidentiality and integrity of protected data and code. It does not address availability attacks such as Denial of Service or Distributed Denial of Service attacks.
Access to this page requires authorization. You can try signing in or changing directories . Data is often considered the most valuable part of a solution because it represents your and your customers' valuable business information. It's important to carefully manage your data. When you plan storage or data components for a multitenant system, you need to decide on an approach to sharing or isolating your tenants' data.
This article provides guidance about the key considerations and requirements for solution architects when they decide on an approach to store data in a multitenant system. This article also describes some common patterns for applying multitenancy to storage and data services and some antipatterns to avoid. It also provides targeted guidance for some specific scenarios. Consider the approaches that you use for storage and data services from several perspectives, including the pillars of the Azure Well-Architected Framework .
When you work with services that store your data, consider the number of tenants, the volume of data, and the workload that you expect - both for each tenant individually and in aggregate. These factors, along with the service configuration and applicable resource and subscription limits, affect how much capacity a resource can provide and how many tenants it can support.
As you grow, you increasingly benefit from having a clear strategy to scale your data and storage resources and automate their management. Use performance testing and capacity planning to determine when to add resources, and plan to scale out before you approach a service or subscription limit. Multitenant data and storage services are susceptible to the noisy neighbor problem . It's important to consider whether your tenants might affect each other's performance. For example, consider whether your tenants have overlapping peaks in their usage patterns over time. Also consider whether all of your customers use your solution at the same time each day and whether requests are distributed evenly. Those factors affect the level of isolation that you need to design for, the amount of resources that you need to provision, and the degree to which tenants can share resources.
It's important to consider Azure resource and request quotas as part of this decision. For example, suppose that you deploy a single storage account to contain all of your tenants' data. If you exceed a specific number of storage operations per second, Azure Storage rejects your application's requests, which affects all of your tenants. This behavior is called throttling . It's important that you monitor for throttled requests.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Cloud%20computing • https://en.wikipedia.org/wiki/Data%20center • https://en.wikipedia.org/wiki/Confidential%20computing • https://learn.microsoft.com/en-us/azure/architecture/guide/multitenant/approaches/storage-data
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Secure Data Sharing Across Multi Tenant Cloud Systems.
[*] Metasploit Scan Running on Target Subnet for Secure Data Sharing Across Multi Tenant Cloud Systems... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |