Complete Technical Paper Content — Secure Devsecops Cicd Pipeline Integration Using Jenkins
Overview & System Context
Secure Devsecops Cicd Pipeline Integration Using Jenkins: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~5997 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background This repository provides a comprehensive guide to implementing a DevSecOps pipeline for secure software development.
The guide covers all stages of the pipeline, including the installation of essential tools, configuration of the environment, integration of security checks SAST/DAST , SCA and DefectDojo as vulnerability management system , and setting up a CI/CD pipeline with Jenkins. Install Ubuntu Server: Create a new VM, power on the machine, and complete the installation.
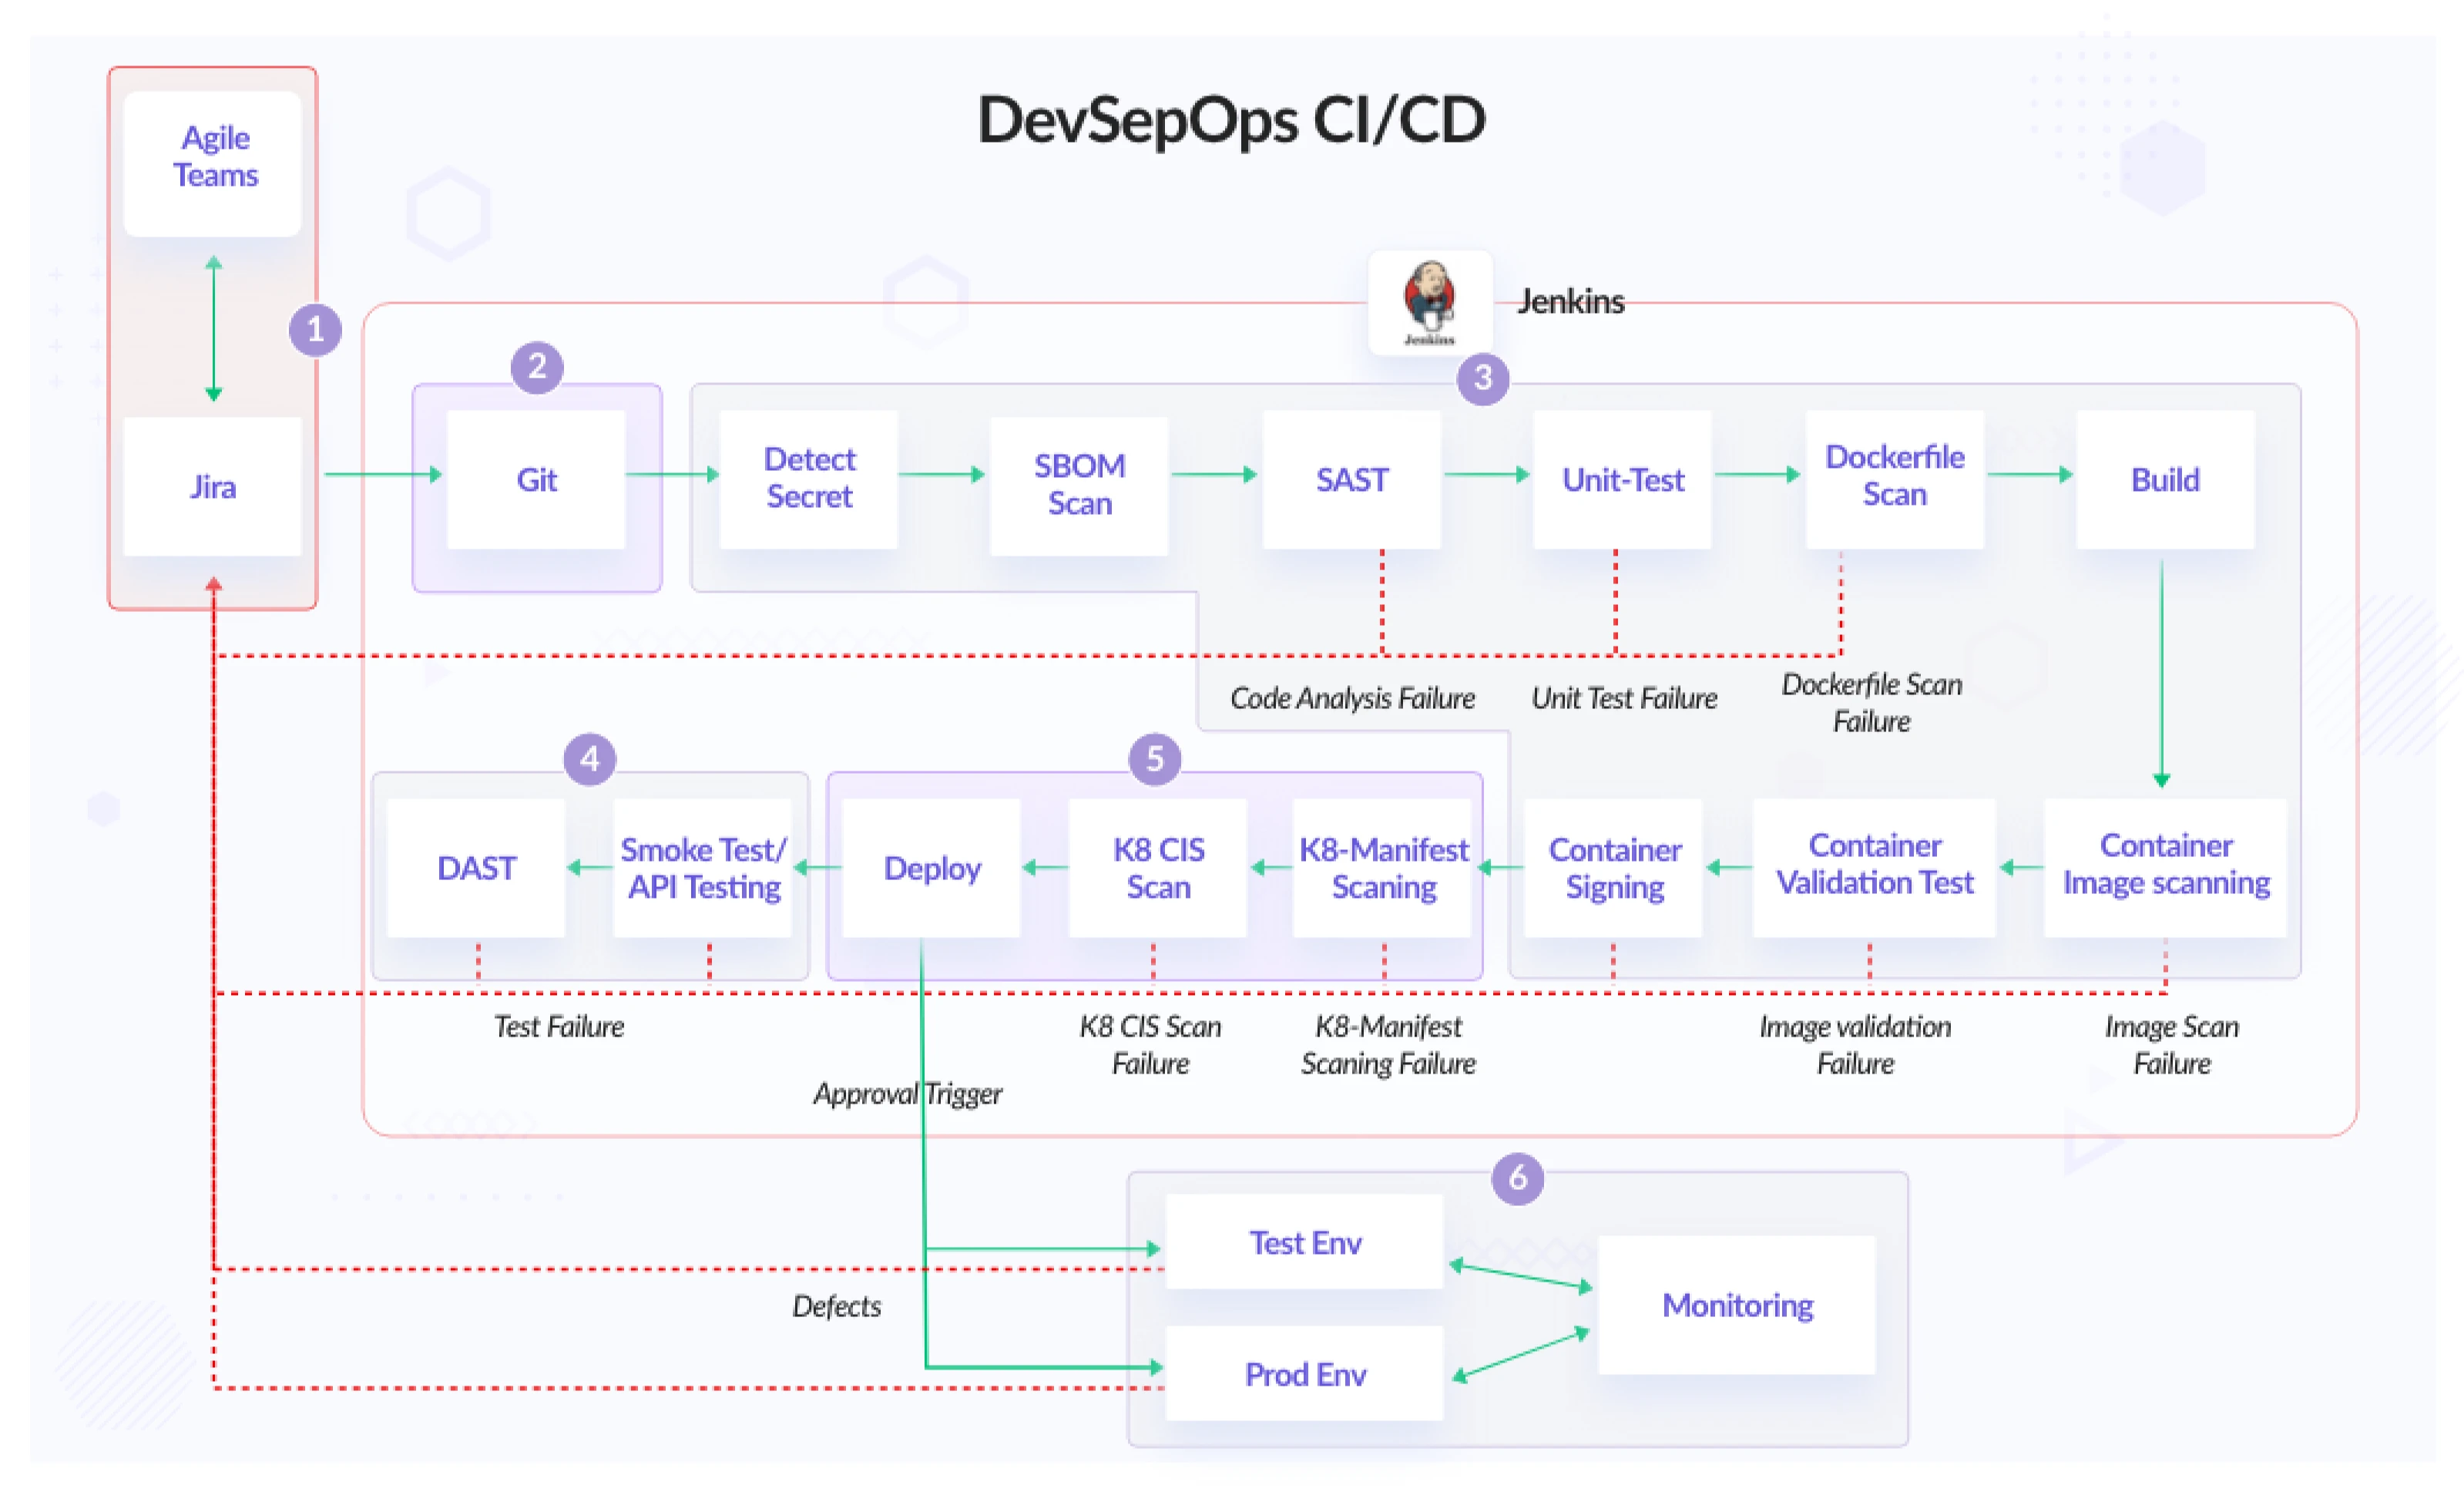
Log into DefectDojo using the admin password, and go to /api/key-v2 to get the API key. Add "DP-Check": Choose install automatically, install from GitHub, and keep the latest version. Figure 1: Implement DevSecOps to Secure your CI/CD pipeline Add a new product in DefectDojo, name it "Netflix," add a description, and choose "Research and Development." Click Save.
Go to Engagement , click "Add New CI/CD Engagement," and name it as desired, e.g., "Jenkins CI/CD." Choose Netflix as the product and click Done. This repository provides a comprehensive guide to implementing a DevSecOps pipeline for secure software development. The guide covers all stages of the pipeline, including the installation of essential tools, configuration of the environment, integration of security checks, and setting up a CI/CD pipeline.
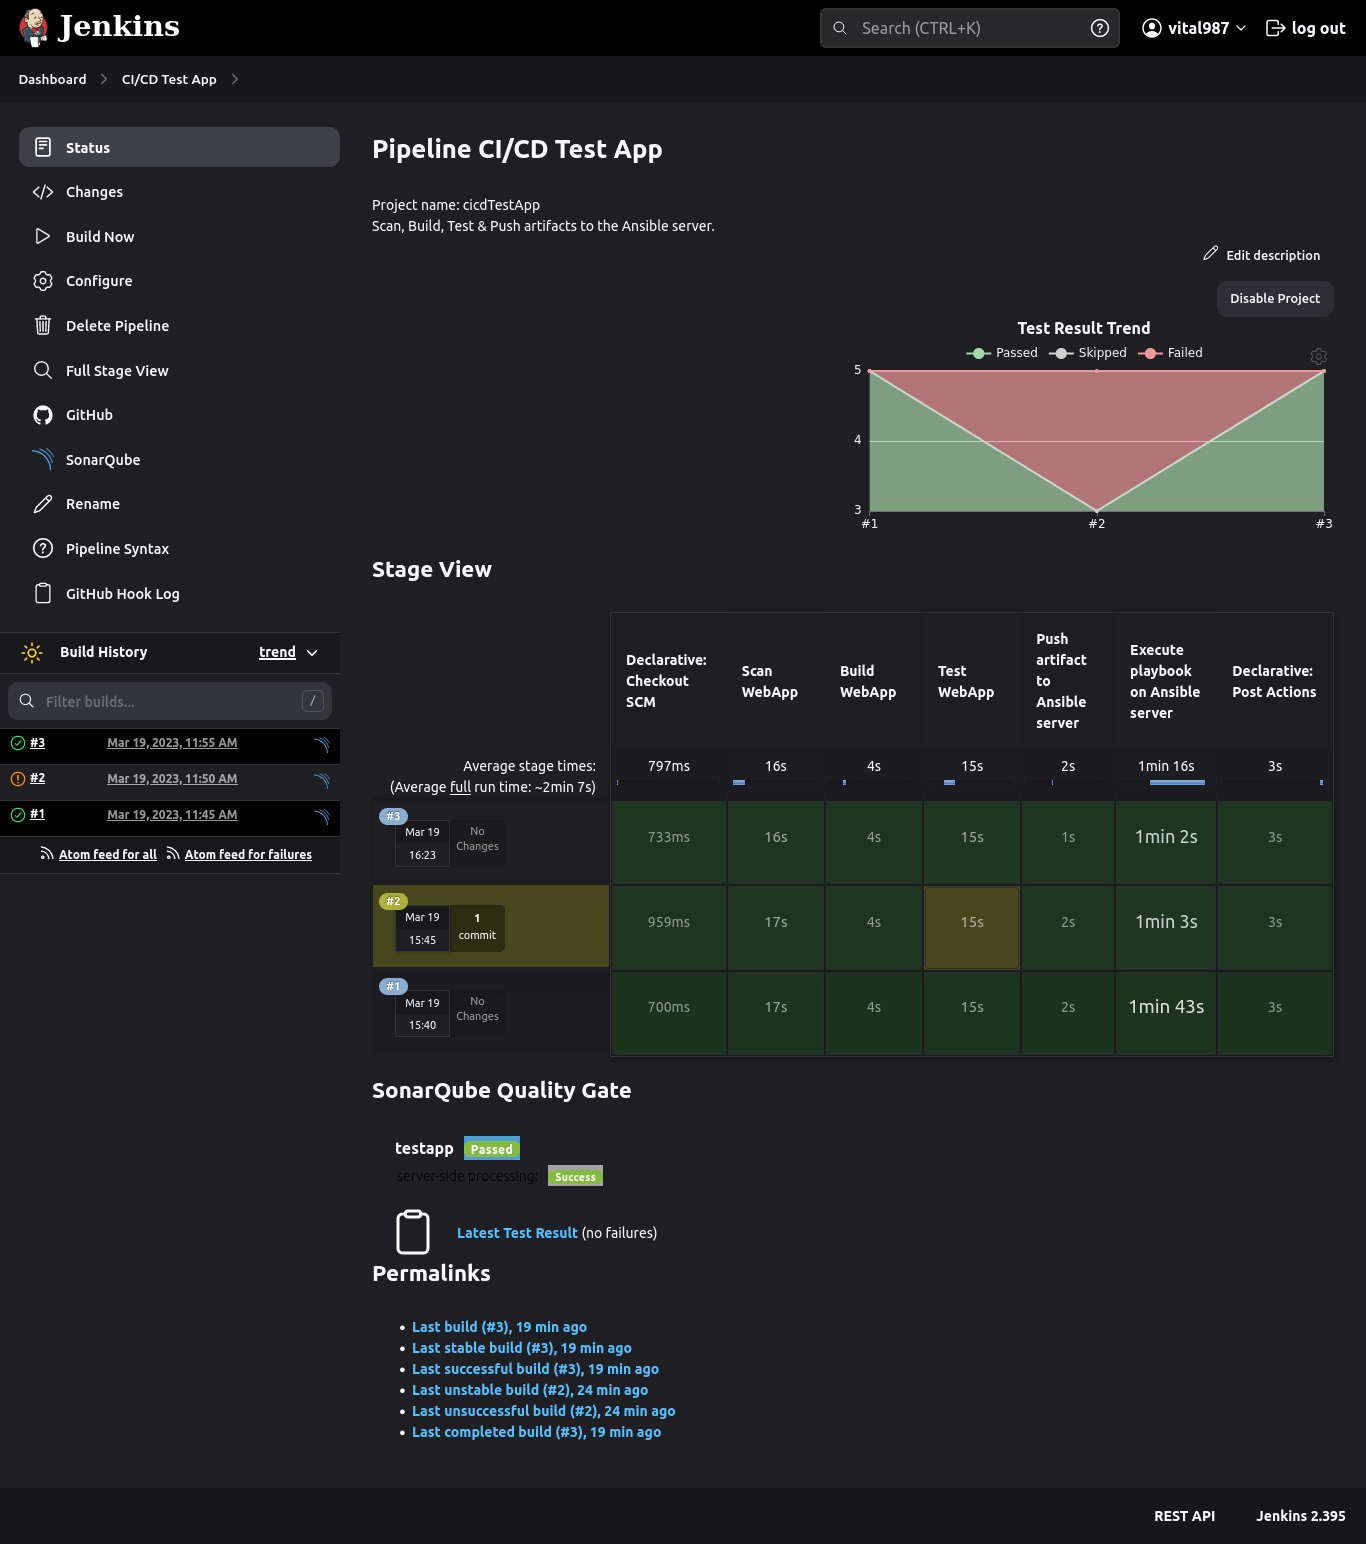
This repository showcases a comprehensive, production-like DevSecOps CI/CD pipeline built from scratch using Jenkins (Master-Slave architecture) on AWS EC2 . The pipeline automates the entire software delivery lifecycle, from source code management to containerization, security scanning, and artifact management, embodying core DevSecOps principles. Figure 2: GitHub - vital987/devsecops_project: An end-to-end DevSecOps pipeline ...
This project demonstrates how to integrate various security tools into a Continuous Integration/Continuous Delivery (CI/CD) pipeline, ensuring that security is a "shift-left" concern – addressed early and continuously throughout the development process. All sensitive information, such as AWS Access Keys, GitHub Personal Access Tokens, and SonarQube API Tokens, are securely stored and managed within Jenkins Credentials . They are injected into the pipeline steps using Jenkins' withCredentials block, preventing hardcoding of secrets in the Jenkinsfile .
To avoid incurring future AWS charges, ensure you delete all resources after you are done experimenting: Built a production-grade DevSecOps CI/CD pipeline using Jenkins Master-Slave on AWS EC2, integrating Gitleaks, OWASP Dependency-Check, SonarQube, and Trivy to automate vulnerability scanning across code, dependencies, and container images.
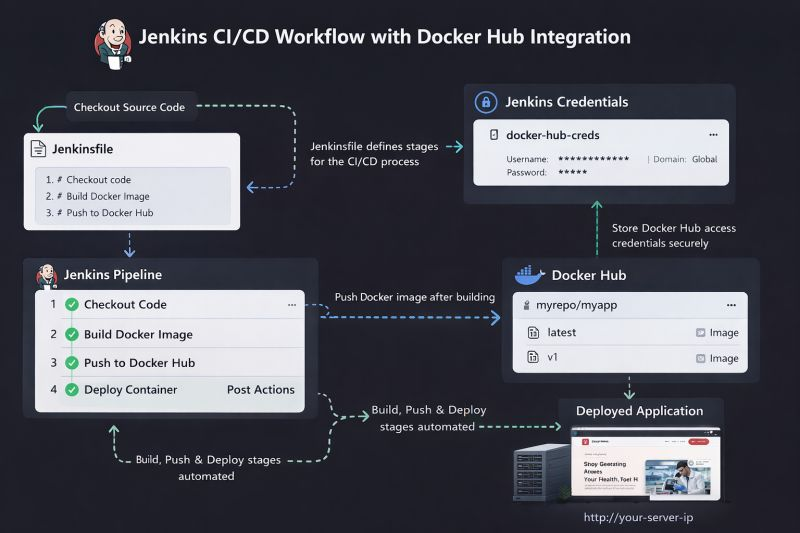
Figure 3: #devsecops #cicd #jenkins #jenkinsfile #docker #dockerhub #automation # ... Containerized a Python application with Docker and automated secure image delivery to AWS ECR, archiving build artifacts and scan reports to AWS S3, achieving 100% automated delivery with enhanced security and auditability. Configured GitHub webhook triggers with Jenkins, achieving end-to-end CI/CD automation, and implemented centralized secret management via Jenkins credentials, ensuring secure handling of AWS, GitHub, and SonarQube tokens.
Built a DevSecOps CI/CD pipeline with Jenkins on AWS EC2, automating Flask app deployment with Docker, Gitleaks, OWASP, SonarQube, Trivy scans, pushing to ECR, and archiving to S3, ensuring secure delivery. Automating Code Review, SAST, Secrets Detection, IaC Security, Container Scanning & Webhook Quality Gates with Jenkins, SonarQube, Trivy, GitLeaks & Docker Traditional software development treated security as a final review gate right before production deployment. This delayed releases and resulted in extremely expensive post-deployment vulnerability fixes. DevSecOps (Development, Security, Operations) revolutionizes software delivery by embedding security directly into every stage of the continuous integration and continuous deployment (CI/CD) pipeline.
Imagine discovering an aircraft engine defect while flying at 30,000 feet versus discovering it during routine maintenance in the hangar before takeoff! Fixing a security vulnerability in production is up to 30 times more expensive than catching it during the initial code push. To implement an effective DevSecOps pipeline, security tooling is applied across 5 distinct domains of the software lifecycle: Access SonarQube dashboard on http:// :9000 . Default credentials: username admin , password admin . Set a new admin password upon first login.
In SonarQube Console: Go to Administration Security Users Tokens Generate Token (Name: token ). Copy the generated secret token string (e.g. squ_655a181a... ). Open your browser and navigate to http:// :5000 — your secure 3-tier web application is live! You can add these high-impact production bullet points to your resume based on this project: Common real-time production & interview questions on DevSecOps pipeline implementation: Answer: Shift-Left Security means moving security testing to the earliest stages of the software development lifecycle (during code commit and build) rather than waiting for post-deployment security audits. Detecting vulnerabilities during initial development is up to 30x cheaper and prevents security flaws from ever reaching production environments.
Answer: SAST (Static Application Security Testing): Analyzes source code without executing it (e.g. SonarQube). DAST (Dynamic Application Security Testing): Tests running applications from the outside to discover runtime vulnerabilities (e.g. OWASP ZAP). SCA (Software Composition Analysis): Identifies known CVE vulnerabilities in 3rd party libraries and dependencies (e.g. Trivy, Snyk, Dependency-Check).
Answer: Jenkins initiates a SonarQube analysis stage using the sonar-scanner CLI tool. SonarQube computes code metrics against defined Quality Gate rules (e.g. 0 Critical Bugs, >80% Coverage). A configured Webhook notifies Jenkins when analysis completes. If Quality Gate rules fail, the Jenkins pipeline stage aborts, preventing deployment of vulnerable code. Answer: SonarQube focuses on source code quality and static code bugs. Aqua Trivy specializes in OS container image vulnerabilities, scanning base Linux packages (Alpine/Debian/Ubuntu) and application dependencies inside Docker images for published Common Vulnerabilities and Exposures (CVEs).
Answer: GitLeaks scans git commits, commit history, and pull requests using regex rules to identify hardcoded passwords, API tokens, Private RSA Keys, and AWS Access Keys. Integrating GitLeaks in pre-commit hooks or CI pipelines prevents developers from committing secret credentials to source repositories. 2. System Architecture & Core Working Principles Answer: Checkov is a static code analysis tool for Infrastructure as Code (IaC). It scans Terraform, AWS CloudFormation, Helm charts, Dockerfiles, and Kubernetes manifests for security misconfigurations (e.g., publicly accessible S3 buckets, privileged container execution, missing encryption at rest).
Answer: The jenkins service user must be added to the Linux docker group via sudo usermod -aG docker jenkins , followed by restarting the Jenkins service ( sudo systemctl restart jenkins ). This grants Jenkins permission to interact with the Docker daemon unix socket ( /var/run/docker.sock ). Answer: Never hardcode database credentials in Dockerfiles or source code. Use Jenkins Credentials Manager, AWS Secrets Manager, HashiCorp Vault, or Kubernetes Secrets to inject credentials as encrypted environment variables or mounted secret files at runtime.
In modern DevOps workflows, security is a fundamental requirement. Organizations expect visibility of vulnerabilities, exposed secrets, and code quality directly within GitHub, especially during Pull Request reviews. While GitHub provides native security capabilities, these features may not always be available or enabled across all environments.
Can we build a production-ready DevSecOps pipeline using open-source tools while still maintaining visibility inside GitHub? In this article, I walk through how I implemented an end-to-end DevSecOps pipeline using Jenkins, Gitleaks, and Trivy, and integrated the results into GitHub through Pull Request comments, commit status checks, and security reporting. Jenkins checks out code in detached HEAD mode, which prevents direct branch detection.
SARIF uploads failed when using private repositories or restricted organizational environments. GitHub security reporting using SARIF is not always available in private repositories or organization-level setups without additional configuration or subscription. While full SARIF-based integration works smoothly with public repositories, limitations arise when working with private repositories or organization environments.
In such scenarios, direct integration with the GitHub Security dashboard may not be available. To maintain visibility without relying on platform-specific features, an alternative approach was implemented: Although this approach does not provide native dashboard-level visibility, it serves as a practical and effective solution in constrained environments.
This approach demonstrates that similar DevSecOps capabilities can be achieved using open-source tools with proper integration. This implementation demonstrates how a production-ready DevSecOps pipeline can be built using open-source tools while maintaining strong visibility within the development workflow.
This was not a straightforward implementation. It required iterative debugging, handling API constraints, and understanding how GitHub processes security data. However, this process resulted in a practical, scalable, and production-relevant DevSecOps solution . In today’s rapidly evolving software development landscape, speed is crucial. However, speed without security can lead to disaster. That's where DevSecOps comes in, combining the agile nature of DevOps with a security-first mindset. In this blog, I will introduce you to the core concepts of DevSecOps and show how you can integrate security checks directly into your CI/CD pipeline using Jenkins.
DevSecOps stands for Development, Security, and Operations . It’s an approach that emphasizes embedding security throughout the entire software development lifecycle, from planning and coding to deployment and operations. Instead of treating security as an afterthought or a final stage, DevSecOps ensures that every phase of development has built-in security controls. The goal is to shift security , meaning it is introduced early in the development process rather than after code has been written.
In a typical DevOps setup, the emphasis is on speed and automation —building, testing, and deploying software faster. However, security often gets neglected or delayed until after deployment, making applications vulnerable to attacks. By adopting DevSecOps, you ensure that: Now, let's explore how you can embed security into your Jenkins pipeline. Jenkins, a powerful automation server, is widely used for continuous integration and delivery (CI/CD). By integrating security tools into Jenkins pipelines, we can ensure that security checks are automatically performed on every build.
In this section, I'll demonstrate a simple Jenkins pipeline that includes security checks at key stages. We'll use tools like: Now, let's explore how you can embed security into your Jenkins pipeline. Jenkins, a powerful automation server, is widely used for continuous integration and delivery (CI/CD). By integrating security tools into Jenkins pipelines, we can ensure that security checks are automatically performed on every build.
In this section, I'll demonstrate a simple Jenkins pipeline that includes security checks at key stages. We'll use tools like: Checkout Code : The pipeline starts by pulling the code from the version control system (GitHub, GitLab, etc.). Build Stage : The code is compiled (or a Docker image is built). This is your regular build step. Static Code Analysis (SAST) : We run a tool like SonarQube to analyze the code for security flaws, such as SQL injection, cross-site scripting, or hardcoded credentials. This step helps you identify vulnerabilities in the source code.
3. Software Implementation, Frameworks & Protocols Dependency Check : Here, OWASP Dependency-Check scans for known vulnerabilities in third-party libraries and dependencies used in the project. These libraries can introduce severe security risks if not properly maintained. Container Security Scan : We scan the Docker container image using a tool like Trivy or Anchore to ensure that the images do not contain vulnerabilities, outdated packages, or misconfigurations.
Unit Tests : As a standard practice, unit tests are run to verify that the code works as expected and hasn't introduced any breaking changes. Deploy to Staging : The application is deployed to a staging environment for further testing. It's important to do this after all the security checks have passed.
Security Gate : This is a critical step . If any vulnerabilities are found (e.g., high-severity issues in the Dependency Check report), the pipeline will abort, and the application will not be deployed to production. Deploy to Production : Only if all stages pass successfully (including the security gate), the code will be deployed to production.
Post Actions : Finally, security reports and other artifacts (like test results) are archived so that you have a record of the security checks and can review them later. With the growing need for faster and secure software delivery, DevSecOps ensures that security is not compromised in the race to deliver features. Integrating security tools directly into your Jenkins pipeline, as shown in this blog, can help teams proactively manage security risks while maintaining speed and agility.
Hello everyone. I’m Ata, a computer science graduate and currently interested in cybersecurity. In the fast-paced world of cybersecurity, staying ahead of potential threats is crucial. As a junior cybersecurity engineer with a specific interest in DevSecOps, I am excited to share my journey in creating a robust DevSecOps pipeline by using Jenkins and various tools. I will share my journey in 3 parts since there is too much material and reading them in a single story may be difficult and take a lot of time. In this part, I will talk about DevSecOps pipelines, Jenkins and its installation, SAST and some details about them.
DevSecOps pipelines are similar to DevOps pipelines. They are like assembly lines for building software, but with a big focus on security. These pipelines automate different tasks, like writing code, testing it, putting it into action, and keeping an eye on it afterward. At each step, they also check for security problems, making sure everything stays safe from the start to the end of the process. This way, everyone involved works together to make sure the software is secure right from the beginning.
Jenkins is an open-source automation server widely used for automating various aspects of the software development process, including building, testing, and deploying software. It provides a platform for continuous integration (CI) and continuous delivery (CD), allowing developers to integrate code changes into a shared repository frequently. First of all, let’s setup a Jenkins instance on our machine. Since it has a simple installation and using a container can have a negative impact on performance or storage, I installed Jenkins directly on my virtual machine. I’m using Ubuntu 22.04 on VMware Workstation Pro with 16GB of RAM, 100GB of storage and 8 processor cores. These specs are definitely not a limit or requirement.
For the installation of Jenkins I simply followed the Ubuntu/Debian section under Linux section in this link: https://www.jenkins.io/doc/book/installing/ . It takes you through the installation of Jenkins itself and Java since Jenkins requires Java to run. You can also find minimal and recommended specs, installation guide, troubleshooting and many other useful information about Jenkins. It is very easy to follow but let me give you a spoiler: After the installation is complete, go to the Jenkins on your web browser. If you didn’t do any custom configuration, it is probably in http://localhost:8080 . This page will greet you: From the given path, receive the initial password and access Jenkins. You may need root access to reach the path.
Choose “Install suggested plugins”. We will install required plugins for the steps of our pipeline one by one, from the “Available plugins” section that will be mentioned: After the plugin installation, you are asked to create an admin user for Jenkins. You can choose “Skip and continue as admin” option but you have to use the initial password to access Jenkins. Therefore, I suggest you to create a user. You can use the same credentials as your machine’s credentials for easiness: You can directly choose “Save and Finish” option since our Jenkins is set up locally instead of on a cloud system and we will conduct all scans locally: If you are seeing this page, congrats! You have successfully installed Jenkins to your system: By clicking on “New Item”, you will get to this page where Jenkins provides many options. On this page, we will choose “Pipeline” option. In this option, we will create our pipeline from scratch, by coding a Jenkinsfile. “Freestyle project” option provides a better UI and easier way to create a pipeline. However, some steps do not fit easily in Freestyle and once you learn how to create a pipeline from scratch, you will automatically learn how to use other options since this is the base of Jenkins pipelines: On the opened page, you will see the general options for your project. You can leave them like that for now since our purpose is to learn the basics of a security-based scan and we will test a project that is intentionally vulnerable and isn’t a part of a continuing development process. This is the section which we will create the pipeline from the scratch: These are our stages that we will implement in our pipeline. Jenkins pipelines use a file type called _Jenkinsfile_. It’s a different file type that you probably used before but it has a simple syntax. For example, this is a single stage Hello World pipeline script: Jenkins allows you to configure many settings according to your needs. However, these parts are the only required ones for a pipeline. Throughout the development of the pipeline, we will use additional parts and syntax rules for tools we will run in stages. For the additional settings and syntax rules you can visit https://www.jenkins.io/doc/book/pipeline/syntax/ .
Tip: To add a setting, feature or section, you can use Pipeline Syntax located under Pipeline section: In Pipeline Syntax, there are useful information about the syntax and most importantly, 2 tools that will assist you: Snippet Generator and Declarative Directive Generator. These tools help you to generate a Jenkinsfile code according your needs and given parameters.
During my learning process, I ran a build for every step to make sure that the code is correct in terms of syntax and configuration. I will follow the same way throughout the note to both show it to you better and remind myself the process. First of all, let’s pull our project we want to scan from a Git repository. For our example project, I chose **Vulnado — Intentionally Vulnerable Java Application**. Here is its link: https://github.com/ScaleSec/vulnado Every time we start the pipeline or a trigger such as a push or a PR to the repository starts the pipeline, the project will be pulled from the repository. We will use **Git** to perform the pull. Jenkins plugin for Git is installed by default. However, we still need to have Git installed in our machine. To do this, simply run command and install Git binary: 4. Practical Deployment, Analysis & Case Studies After this install, you need to invoke the binary in your Jenkins. For this, you can simply add this command to the pipeline: This command uses Git plugin for Jenkins to interact with the Git binary in our machine. We will usually interact with tools and programs via such plugins to have a stable and efficient pipeline.
Note that we created a stage under “stages” and in this stage, we added the command under “steps”. We will follow the same approach for each stage and commands we need to run. This is the pipeline dashboard after our first build: In DevOps and DevSecOps pipelines, building is a required stage to see if the changes on the code didn’t break the program. If project is successfully built, testing stage will start. If the tests are passed, project is finally deployed with a deployment stage. In this DevSecOps pipeline, we are aiming to perform security scans and find the vulnerabilities. In other words, we are doing the testing part of a traditional pipeline. Therefore, we don’t need to bother with building and deploying, yet .
Almost every tool in a DevSecOps pipeline requires project to be built to perform efficient scans on them. Some of them build it themselves, some of them don’t. Therefore, I usually add a stage to build the project since it can be useful and it is easy to add it to the pipeline. This project is a Maven project. Therefore, I use a command specific to it to build my project. You can use a different command according to your project to be used in the pipeline: Note that an install may be required to build your project. For example, I needed to install Java and Maven on my machine since the project I scan is a Maven project.
This is the simple command to run on my terminal to build my project and that’s what we should do in the pipeline too. To run a shell command, simply put single quotes at the start and end of the command and add “sh” at the beginning of the command. This will be the step to run in Jenkins pipeline: sh ‘mvn clean package’\ This is the final code and result of running the pipeline: Here comes the hard part. Previous steps did not require complex tools and processes. We just pulled and build the project.
But from now on, we need to use various tools, install them on our machine and make configurations on both the tools and Jenkins itself. For the SAST stage, I used SonarQube tool. SonarQube is an open-source platform developed by SonarSource for continuous inspection of code quality to perform automatic reviews with static analysis of code to detect bugs and code smells on more than 30 programming languages. I preferred SonarQube instead of other SAST tools because it has a detailed documentation and plugins about integration with Jenkins and SonarQube works with Java projects pretty well. Of course you can similar multi-language-supported tools such as Semgrep or language-specific tools such as Bandit .
Let’s start with the simplest one. We need to download the plugin on Jenkins for SonarQube to connect SonarQube and Jenkins. On the main dashboard of Jenkins, go to Manage Jenkins > Plugins > Available plugins and type “sonarqube”. SonarQube Scanner plugin should appear on the top: Mark the box next to the plugin and install the plugin. On the installation page, mark the box “Restart Jenkins when installation is complete and no jobs are running” since you need to restart Jenkins eventually to make the plugin available.
Obviously, we must install an instance of SonarQube. You can use a machine on a cloud provider if you want too but for simplicity, we will install a local instance. You can both use a Docker image or the zip file to run SonarQube. Both ways are simple to perform, compatible with Jenkins and this paper. Here is the link and steps for you to follow for installation: https://docs.sonarsource.com/sonarqube/latest/try-out-sonarqube/ . The steps in this page is to run a simple instance of SonarQube on a Docker container. If you are curious about it, you can follow the zip file version. Both of them have the same abilities, I just didn’t want to bore you with specific volume and network settings.
You can understand that installation is successful and ready to be used with Jenkins by trying to access SonarQube by accessing URL http://localhost:9000/ (This is the default URL for SonarQube if you didn’t make any custom configuration). This is the first page that will greet you. Your default username and password is “admin”. It will ask you to change your password to continue.
This is the dashboard of SonarQube. Since we don’t have any projects created, it provides us options to choose a DevOps platform. Usually, GitHub is selected but we won’t follow that path. Because choosing GitHub requires us to have a GitHub App. GitHub Apps are tools that extend GitHub’s functionality like opening issues, comment on pull requests, and manage projects. They can also do things outside of GitHub based on events that happen on GitHub: Using such app may be useful for organizations or frequently developed projects. However, this story’s scope is performing a security test on a project and creation of a GitHub App and integrating it to both SonarQube and Jenkins is difficult and unnecessary for a testing pipeline. Because of this, I want you to choose “Create a local project”. Then, give a name to your project. A key will be suggested to you but any value is okay.
After this page, you can simply choose “Use the global setting” and create your project. It will ask you to choose an analysis method. Choose “With Jenkins”. In the next page, choose GitHub for “Select your DevOps platform” and it will provide you some steps. We completed some of them. But we didn’t complete some steps about Jenkins and SonarQube integration that are not mentioned here.
For the steps of Jenkins integration, there is a document in SonarQube’s website . However, in my opinion SonarQube documentations are not enough and even sometimes, wrong. Therefore, I will show you the correct steps. On your Jenkins dashboard, go to Manage Jenkins > Credentials. In this page, click on System > Global credentials (unrestricted) > Add credentials. In here: Now, from the Jenkins dashboard again, go to Manage Jenkins > System > SonarQube servers. In here, enter a name to your installation, server URL (which is http://localhost:9000 by default) and server authentication token. This is the credential we just added. You should be able to see it in the dropdown menu. Choose it and save: Now, the final part. On SonarQube, you can see a script that you can add to your pipeline. However, it needs some adjustments and a fix to work properly. First of all we don’t need def mvn = tool ‘Default Maven’;\ part because our Maven is on the PATH. Because of this, we should change the shell command to: sh “mvn clean verify sonar:sonar -Dsonar.projectKey=vulnado -Dsonar.projectName=’vulnado’”\ Finally, we must include an installation name in the script. It is not mentioned on SonarQube but it is necessary. Installation name is the name you entered in previous step. For example, my installation name is “sonar-local” and here is the part of the code: withSonarQubeEnv(installationName: ‘sonar-local’) The “SonarQube” button simply redirects you to your SonarQube URL. This is the SonarQube page after SAST stage: Well, this is the end of Part 1. I will upload Part 2 ASAP. In some parts, I didn’t add images to keep the story short. However, I’d love to hear your comments about the format and content of this story, so I can improve the following parts.
A compromised Jenkins controller grants attackers the ability to inject malicious code, pivot into artifact registries, and manipulate entire deployment pipelines. With access to repository tokens, cloud credentials, and build logs, the blast radius of a single misconfiguration turns a CI tool into a supply chain weapon. Hardening Jenkins is not a single checkbox; it requires layered controls across the installation, the network, identity management, pipeline execution, and agent communication.
Start by eliminating elementary risks that open the door to privilege escalation and data interception. The Jenkins core and its plugins must run on a maintained, patched system with minimal attack surface. Package hygiene and runtime user Always deploy the latest LTS release from the official Jenkins repositories. Avoid distro packages that lag behind critical fixes. Validate the downloaded WAR or package checksum against the published SHA-256 digest. Run Jenkins as a dedicated, nonIprivileged OS user (for example jenkins ). Set a restrictive umask 027 so that the JENKINS_HOME directory and its subfolders are not worldIreadable, blocking casual snooping of secrets and build files.
Network isolation and Transport Layer Security Never expose Jenkins directly to the public internet. Bind the controller to a private subnet and place it behind a reverse proxy (NGINX, Apache, or HAProxy) that performs TLS termination. Enforce HTTP Strict Transport Security (HSTS) headers and disable HTTP access entirely. Use a configuration like the following snippet in NGINX to close port 8080 completely and redirect all plaintext requests: Additionally, lock down the inbound firewall to allow only the reverse proxy’s IP to reach the controller port, and permit agent communication exclusively from known agent subnets over encrypted channels.
5. Performance Evaluation & Extended Technical Observations The Security Realm ties Jenkins to an identity provider, while the Authorization Strategy determines what authenticated users can do. Never rely on the insecure “Anyone can do anything” or “Logged-in users can do anything” defaults. Security Realm integration Connect Jenkins to an enterprise directory via LDAP, Active Directory, SAML 2.0, or OpenID Connect. The LDAP plugin supports group lookups, allowing you to map existing team structures directly into Jenkins. For smaller installations, the built-in Jenkins user database with strong password policies (minimum length, complexity, and regular rotation) serves as a lightweight option, but it should be combined with multiIfactor authentication where possible.
Authorization strategies Implement RoleIBased Access Control (RBAC) using the RoleIbased Authorization Strategy plugin. Create global roles (Administrator, Job Deployer, ReadIOnly) and project roles that granularly scope permissions at the folder level. The MatrixIbased Security model works similarly but ties permissions directly to individual users or groups; use it only if you cannot adopt the RBAC plugin. For multiItenant environments where squads need isolated spaces, activate FolderIbased Authorization to delegate administration to folder owners. Patterns that isolate pipelines per team are reminiscent of multi-tenant deployment automation guides , where strict namespace boundaries prevent crossIcontamination.
Apply the principle of least privilege ruthlessly. A developer should be able to view, run, and cancel their team’s jobs, but never configure the controller or approve script signatures. Build node configuration must remain an adminIonly operation. Secrets embedded in pipeline scripts or job parameters are a leading cause of credential exfiltration. Jenkins’ own Credentials Plugin stores passwords, SSH keys, and tokens in an encrypted XML file (typically $JENKINS_HOME/secrets/ ). Always reference credentials by ID in declarative pipelines: Never print credentials to the console; the credentials binding masks the value automatically, but you must still avoid echo inside a sh block without set +x . Extend the chain with dedicated secrets management tools such as HashiCorp Vault through the Vault Plugin , so that static and dynamic secrets never touch the controller filesystem.
Build artifacts often contain compiled binaries, installation packages, or sensitive configuration. Push them directly to a hardened artifact repository (Nexus or Artifactory) that enforces access controls and retention policies. Enable TLS for uploads and, for extremely sensitive payloads, encrypt the artifact before storage using pipelineIlevel GPG or cloud KMS integration.
Every agent connection is a potential lateral movement path back to the controller. Start by enabling Agent → Controller Security under Manage Jenkins → Configure Global Security . This forces agents to use encrypted protocols and allows the controller to verify their identity. Connection security Prefer SSH-based agent connections with public key authentication. Disable JNLP-4 (WebSocket) unless absolutely required, and if you must use it, configure JNLP4ITLS exclusively. For ephemeral agents spawned by the Kubernetes plugin, mount the agent’s private key from a Kubernetes Secret and restrict the service account to readIonly access of the build namespace.
Enforce network segmentation: agents should be unable to initiate connections to the controller’s administrative ports or other infrastructure components. OnIprem agents reside in a dedicated VLAN with egress filter rules; cloud agents sit inside a private subnet with NAT gateway only for outbound pulls. Ephemeral and immutable agents Treat agents as cattle, not pets. Kubernetes plugin agents, Docker agent templates, or AWS EC2 Fleet agents should be discarded after each build. PreIbaked images with the necessary tools (Maven, Gradle, Docker CLI) and no SSH access reduce the window for tampering. Avoid shared, longIrunning agents that accumulate state.
Pipeline scripts run on the controller by default for declarative pipelines (except for agent directives). Untrusted scripted pipelines can call arbitrary Groovy methods, read files, and even execute shell commands that modify the controller. Enable the Groovy Sandbox in the InIprocess Script Approval configuration. When a script invokes a method that is not preIapproved, it fails and the administrator must explicitly whitelist the signature. Use the Script Security Plugin to define an explicit allowIlist of approved signatures, and combine it with Pipeline: Groovy Libraries to share only vetted, signed shared libraries.
Cancel any pipeline that ships with @Grab annotations or dynamic class loading unless reviewed by the security team. Regularly audit all pipeline jobs for patterns like sh 'curl | sh' or wget of untrusted scripts. The DevOps engineering resource hub highlights additional CI/CD hardening strategies that extend beyond the Jenkins controller itself. Adopt the Configuration as Code (JCasC) plugin to declare every Jenkins setting—security realm, authorization strategy, plugin list, agent templates—in a jenkins.yaml file stored in Git. This eliminates drift, makes audits reproducible, and allows disaster recovery by simply applying the configuration to a fresh instance. Combine JCasC with Jenkins Helm chart on Kubernetes to run a stateless controller where JENKINS_HOME is backed by a persistent volume claim or external S3Icompatible store.
Never provision an agent by hand. Use infrastructureIasIcode (Terraform, CloudFormation) to define ephemeral agent fleets and bake the agent image with Packer. Define pipeline jobs as code stored alongside application source in Jenkinsfile s that are automatically discovered by Multibranch Pipeline or GitHub Organization Folder . Reject inlineIscript job definitions from the UI. Mandate code reviews for any Jenkinsfile change that alters securityIrelated stages (e.g., modifying docker run commands, adding new withCredentials blocks).
Prevent a runaway pipeline from exhausting controller memory or CPU. Set resource requests and limits on KubernetesIbased agents and configure the controller’s Java options ( -Xmx , -Xms ) appropriately. Use the CloudBees Quota plugin or builtIin executor throttle to cap concurrent builds per team, protecting the controller from noisy neighbors. Fail the build if a critical or highIseverity finding appears and route alerts to the owning team’s Slack or PagerDuty channel.
Configure periodic, encrypted backups of JENKINS_HOME (excluding workspaces and caches) to a separate cloud object store. Test the restore procedure quarterly: spin up a parallel controller, apply the JCasC file, load the backup, and verify that all jobs and credentials reconstruct correctly. Automate this with a scheduled pipeline. Expose Jenkins metrics via the Prometheus Plugin and build a Grafana dashboard tracking executor counts, job durations, queue lengths, and failed builds. Set alerts for sudden drops in available executors, authentication failures, or plugin update availability. Centralize Jenkins logs with an agent like Vector or Fluentd, forwarding to an ELK stack or Loki for correlation with application logs.
Symptom: Agent fails to connect with FATAL: handshake_failure or javax.net.ssl.SSLHandshakeException . Diagnosis: The agent and controller cannot agree on a TLS cipher or the controller’s certificate is untrusted. Verify that the controller’s JVM trusts the reverse proxy’s CA certificate and that the agent JVM has the same truststore. Run openssl s_client -connect controller-fqdn:443 -tls1_2 from the agent machine. Adjust the -Dhttps.protocols=TLSv1.2,TLSv1.3 JVM argument on both ends if a protocol mismatch occurs.
Symptom: Pipeline fails with org.jenkinsci.plugins.scriptsecurity.sandbox.RejectedAccessException: Scripts not permitted to use method ... . Resolution: Navigate to Manage Jenkins → InIprocess Script Approval and approve the pending signature after verifying its safety. To preIapprove methods used by a vetted shared library, add a signature like method java.time.Instant now in the script approval section of JCasC.
Symptom: Users receive 403 No valid crumb was included in the request when invoking API endpoints. Root cause: CSRF protection is enabled (the default) and the client is not sending the crumb header. For programmatic access, fetch the crumb first: curl -u user:token 'https://jenkins.example.com/crumbIssuer/api/xml?xpath=concat(//crumbRequestField,":",//crumb)' and include the returned header in subsequent calls. In declarative pipelines use the withCredentials step that handles crumbs automatically. Do not disable CSRF protection.
Symptom: After an unexpected shutdown, Jenkins shows “reloaded” state and all jobs are missing. Resolution: Check $JENKINS_HOME/config.xml for corruption. Stop Jenkins, restore the XML files from the last backup, and restart. If the SCM plugin conflicts, run the Plugin Installation Manager Tool in offline mode to bring plugins to a consistent state before starting the controller.
Symptom: Disk full in JENKINS_HOME leading to java.io.IOException: No space left on device . Remediation: Purge old builds, workspaces, and stale caches with the Workspace Cleanup Plugin and builtIin “Discard Old Builds” strategy. Archive only essential artifacts and move longIterm storage to an external repository. Symptom: Administrator locked out after misconfiguring the security realm (e.g., a loopback LDAP server). Recovery: Stop Jenkins, edit $JENKINS_HOME/config.xml and set
Always test realm changes on a staging controller first. Symptom: Plugin dependencies fail to resolve after an upgrade, leaving Jenkins in an “offline” mode. Resolution: Run java -jar jenkins-plugin-manager.jar --war /usr/share/jenkins/jenkins.war --plugin-file plugins.txt --plugin-download-directory /var/lib/jenkins/plugins to obtain a coherent set. Check for “detached” plugins that were removed from the core and must be installed separately.
Building a resilient CI/CD pipeline demands continuous vigilance. Keep your Jenkins inventory patched, your plugins audited, and your monitoring alerts actionable. The strategies outlined here form a foundation, but they must be paired with a broader culture of secure DevOps. Explore our DevOps infrastructure hub for complementary guides on infrastructure hardening, container scanning, and secret management that elevate your entire delivery chain.
Harvested Online Documentation & Reference Sources • https://github.com/fathiismail/DevSecOps_Pipeline_Jenkins • https://github.com/heyamay/Jenkins-DevSecOps-CICD-pipeline • https://www.clouddevopshub.com/blog/end-to-end-devsecops-cicd-pipeline-implementation • https://opstree.com/blog/production-ready-devsecops-pipeline/ • https://dev.to/soumya14041987/devsecops-fundamentals-security-in-the-jenkins-pipeline-20n • https://dev.to/ataseren/creating-a-devsecops-pipeline-with-jenkins-part-1-5dla • https://www.devopsroles.com/jenkins-security-ensuring-safe-ci-cd-pipelines/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Secure Devsecops Cicd Pipeline Integration Using Jenkins.
[*] Metasploit Scan Running on Target Subnet for Secure Devsecops Cicd Pipeline Integration Using Jenkins... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |