Complete Technical Paper Content — Secure Email Client Using Pgp Encryption In Python
Overview & System Context
Secure Email Client Using Pgp Encryption In Python: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9513 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background This is a list of free and open-source software (FOSS) packages, computer software licensed under free software licenses and open-source licenses. Software that fits the Free Software Definition may be more appropriately called free software; the GNU project in particular objects to their works being referred to as open-source. For more information about the philosophical background for open-source software, see free software movement and Open Source Initiative. However, nearly all software meeting the Free Software Definition also meets the Open Source Definition and vice versa. A small fraction of the software that meets either definition is listed here. Some of the open-source applications are also the basis of commercial products, shown in the List of commercial open-source applications and services.
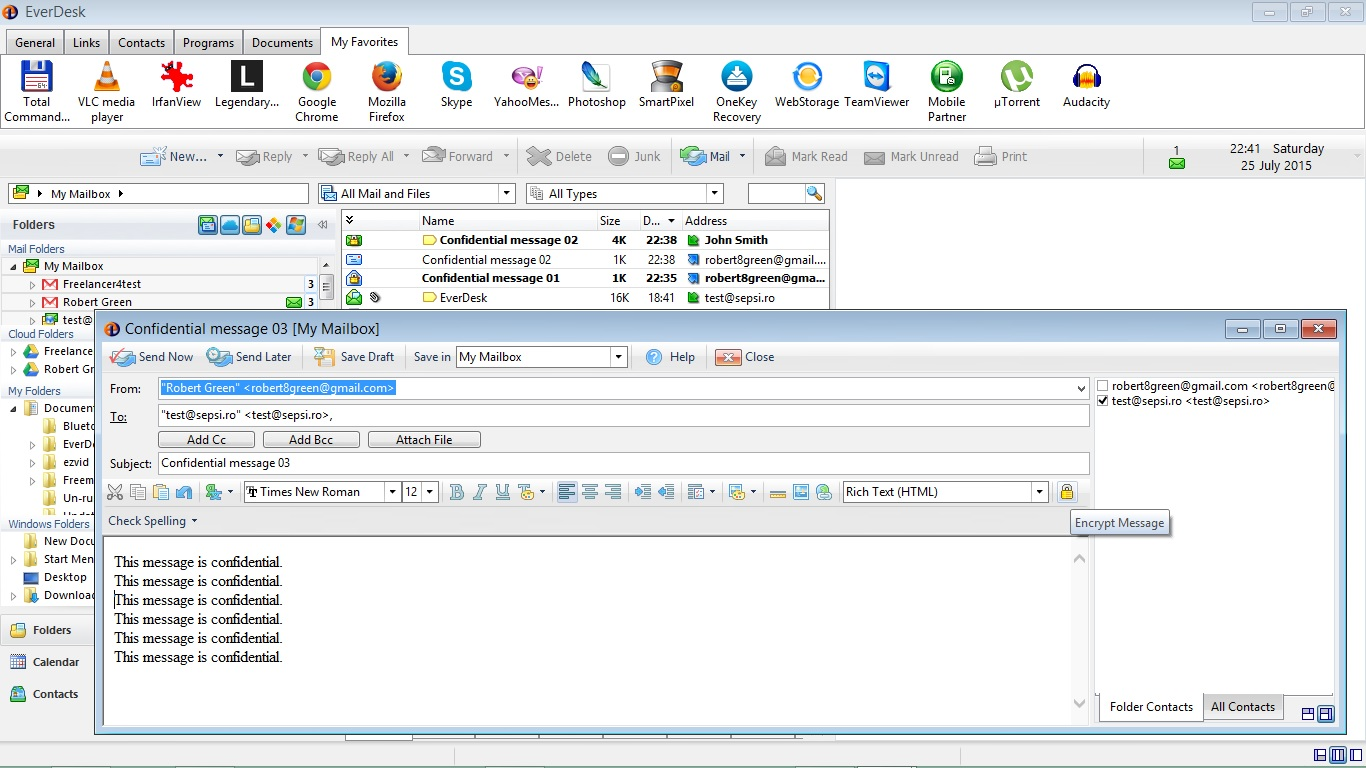
Cline – AI coding agent for IDEs and the command line. Codex CLI – AI coding agent and command-line interface developed by OpenAI. Command Code — CLI and desktop AI agent DeepSeek Coder – large language model designed for code generation and AI-assisted software development. Eclipse Theia – integrated development environment and framework with AI-assisted software development features. goose – AI coding agent for the desktop and command line. Kilo Code — CLI and IDE extension developed by Anaconda OpenCode — CLI, desktop app, web app, and IDE extensions OpenHands — AI software development agent Oh My Pi – terminal-based AI coding agent developed as a fork of Pi. Pi – terminal-based AI coding agent. Zed – source-code editor with integrated AI-assisted development and agentic coding features.
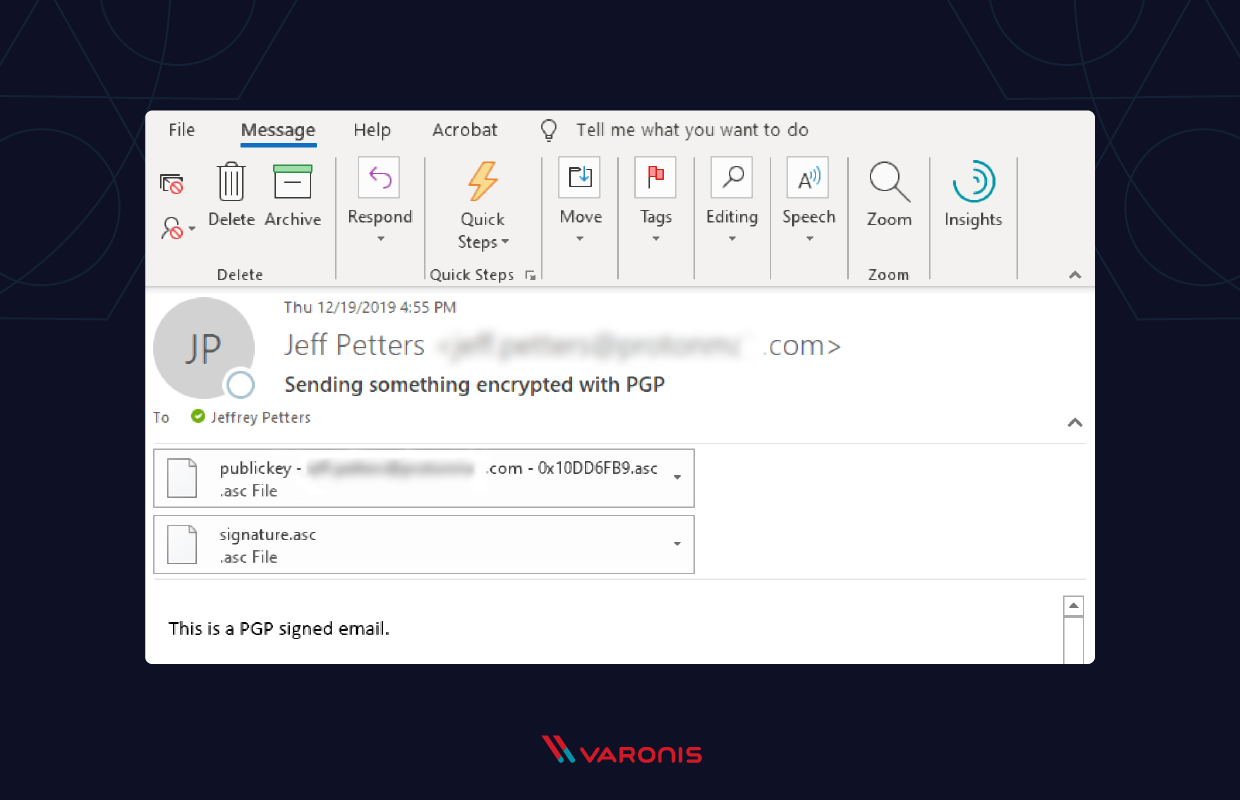
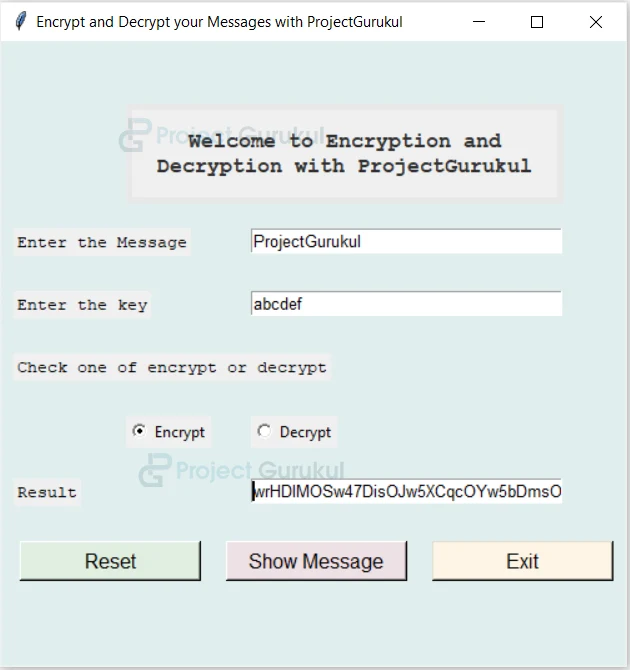
Apertus – Swiss National AI Initiative LLM BERT – Google LLM BLOOM – BigScience multilingual LLM Cerebras-GPT – Cerebras Systems LLMs DeepSeek – R1 and V3 models Gemma 4 – Google LLM GLM-4.5 and later versions – Z.ai LLMs GPT-1, GPT-2, and GPT-OSS – OpenAI LLMs GPT-J, GPT-Neo, and GPT-NeoX – EleutherAI LLMs Hy – Tencent open-weight LLM Granite – IBM LLMs Grok-1 – xAI LLM Inkling – Thinking Machines Kimi (some versions) – Moonshot AI LLMs MiMo (some versions) – Xiaomi LLMs Mistral (some versions) Muse Glimmer — Meta Superintelligence Labs LLM Nemotron 3 – Nvidia open-weight models OLMo – Allen Institute for AI LLM Phi – Microsoft LLMs Qwen (some versions) – Alibaba Cloud LLMs Sarvam-M, Sarvam-105B and Sarvam-30B – Sarvam AI LLMs SmolLM – Hugging Face small language models (SLMs) Step-3.7Flash – StepFun LLM T5 – Google LLM XLNet – Google LLM ArduPilot CoppeliaSim Gazebo Mobile Robot Programming Toolkit OpenRTM-aist Paparazzi Project Player Project Python Robotics Robot Operating System (ROS) TurtleBot UBtech Thinker Webots – robot simulator Figure 1: Email Manager Software - Everdesk Contact Management Software Archimedes (CAD) Art of Illusion Blender BRL-CAD – constructive solid geometry (CSG) solid modeling computer-aided design (CAD) system FreeCAD – parametric 3D CAD modeler with a focus on mechanical engineering, BIM, and product design LeoCAD — beginner Lego 3D modeler LibreCAD – 2D CAD software using AutoCAD-like interface and file format MakeHuman MeshLab Open Cascade Technology (OCCT) – CAD kernel for 3D CAD, CAM, CAE OpenSCAD – scripting-based 3D CAD software QCAD SolveSpace – 2D and 3D CAD, constraint-based parametric modeler with simple mechanical simulation abilities Sweet Home 3D Wings 3D Electric FreePCB Fritzing – CAD software for the design of electronics hardware to build more permanent circuits from prototypes gEDA GNU Circuit Analysis Package (Gnucap) Icarus Verilog KiCad – suite for electronic design automation (EDA) for schematic capture, PCB layout, manufacturing file viewing, SPICE simulation, and engineering calculation KTechLab Magic Ngspice pcb-rnd Oregano Quite Universal Circuit Simulator (QUCS) Verilator XCircuit Blender – 3D computer graphics software toolset used for creating animated films, visual effects, art, 3D printed models, and motion graphics FreeCAD – equivalent of Blender geared toward mechanical engineers OpenFOAM – software used for computational fluid dynamics (or CFD) FlightGear – atmospheric and orbital flight simulator with a flight dynamics engine (JSBSim) that was used in a 2015 NASA benchmark to judge new simulation code to space industry standards SimPy – queue-theoretic event-based simulator written in Python Salome – generic platform for Pre- and Post-Processing for numerical simulation OpenPGP – open-source version of Pretty Good Privacy GNU Privacy Guard – replacement for PGP OpenSSL – library for applications that provide secure communications over computer networks NaCl (software) – crypto library Libsodium – fork of NaCl VeraCrypt – disk encryption software forked from TrueCrypt LUKS – standard for disk encryption on Linux systems Nym (mixnet) – mix network that uses noise and random packet timing for obfsucation, overlay network for NymVPN Tor (network) – free overlay network for enabling anonymous communication Tails (operating system) – security-focused Linux distro using Tor by default Signal (software) – secure messaging app Off-the-Record Messaging – protocol for secure instant messaging GPGTools – macOS suite for GnuPG-based encryption Figure 2: What is PGP Encryption and How Does It Work? Aircrack-ng – Wi-Fi security auditing tool BackTrack – predecessor to Kali Linux Burp Suite Community Edition – security assessment and penetration testing of web applications Ghidra – software reverse engineering suite developed by the NSA Hashcat – password recovery utility High Orbit Ion Cannon – DDoS hping3 — packet crafting and network penetration-testing utility Hydra (software) – login cracker supporting numerous protocols John the Ripper – password cracking tool Kali Linux – penetration testing Linux distribution Metasploit Project – framework for developing and executing exploit code Netcat – network utility for reading/writing data across networks Nikto (vulnerability scanner) – web server vulnerability scanner Nmap – network scanning, port scanner, and auditing tool OpenSSH – implementation of the SSH protocol Radare2 – reverse engineering framework Snort (software) – network intrusion detection system sqlmap – automated SQL injection and database takeover tool Suricata (software) – network threat detection engine Volatility (memory forensics) – memory forensics framework for incident response Wireshark – network protocol analyzer YARA – tool to identify and classify malware qBittorrent – BitTorrent client Transmission (BitTorrent client) – lightweight BitTorrent client IPFS – InterPlanetary File System for decentralized storage and sharing RetroShare – secure communication platform with file sharing Zerocoin – privacy-focused cryptocurrency protocol Zcash – cryptocurrency based on Zerocoin using zk-SNARKs Monero – privacy-focused cryptocurrency using ring signatures NYM — Nym mixnet privacy- and security-focused token Tornado Cash — Cryptocurrency tumbler ClamAV – cross-platform antimalware toolkit written in C and C++, able to detect many types of malware including viruses ClamWin – antivirus tool for Windows and written in C, C++ Lynis – security audit tool (set of shell scripts) for Unix and Linux Figure 3: Python Message Encryption Decryption Project - Project Gurukul Bouncy Castle GnuPG GnuTLS KGPG NaCl OpenSSL Seahorse Signal stunnel TextSecure wolfCrypt 7-Zip Snort – network intrusion detection system (IDS) and intrusion prevention system (IPS) Suricata – network threat detection engine OpenVAS – software framework of several services and tools offering vulnerability scanning and vulnerability management Nmap – network scanner, port scanner, and security auditing tool Nikto – web server vulnerability scanner Volatility – memory forensics framework for incident response Cyberduck – macOS and Windows client (since version 4.0) Lsh – server and client, with support for SRP and Kerberos authentication OpenSSH – client and server PuTTY – client-only Apache Cassandra – NoSQL database from Apache Software Foundation offers support for clusters spanning multiple datacenter Apache CouchDB – NoSQL database from Apache Software Foundation with multi-master replication MariaDB – community-developed relational database management system with pluggable storage engines and commercial support PostGIS – adds support for geographic objects to the PostgreSQL as per Open Geospatial Consortium (OGC) PostgreSQL – relational database management system emphasizes on extensibility and SQL compliance and available for Windows, Linux, FreeBSD, and OpenBSD ATutor – web-based Learning Content Management System (LCMS) Canvas LMS – web-based, open, extensible learning management system Chamilo – web-based e-learning and content management system Claroline – collaborative Learning Management System DoceboLMS – SAAS/cloud platform for learning eFront – icon-based learning management system H5P – framework for creating and sharing interactive HTML5 content IUP Portfolio – educational platform for Swedish schools ILIAS – web-based learning management system (LMS) Moodle – learning management system OLAT – web-based Learning Content Management System Omeka – content management system for online digital collections Sakai Project – web-based learning management system SWAD – web-based learning management system Kiwix – offline web browser that allows users to download Wikipedia's entire content and use it for offline learning. Later it was expanded with repositories for Wikimedia Foundation, public domain texts from Project Gutenberg, many of the Stack Exchange sites, and other resources OpenStreetMap – OpenStreetMap was developed in 2004. It uses Open data and users data input through Crowdsourcing and Web mapping to create a complete and downloadable alternative to other online maps.
This allow users to enter data when there is no data available due to lack of governance and economic interest or due to lower population of the places mapped Advanced Simulation Library ASCEND Calcpad Calculix CHEMKIN – chemical kinetics COCO simulator – chemical process simulator CP2K – quantum chemistry and solid-state physics DWSIM – chemical process simulator General Mission Analysis Tool (GMAT) – space mission analysis GNU Octave – numerical-analysis GROMACS – simulations of proteins, lipids, and nucleic acids JSBSim – flight dynamics engine LAMMPS – Molecular dynamics Open Babel – chemical informatics OpenModelica – chemical process simulator OpenSees – earthquake engineering OpenVSP – parametric aircraft geometry tool Pyomo – mathematical optimization QBlade – wind turbine design and aerodynamic simulation software REFPROP – reference Fluid Thermodynamic and Transport Properties XFOIL – analysis of subsonic isolated airfoils .apng – Animated Portable Network Graphics .avif – AV1 Image File Format .bpg – Better Portable Graphics .exr – OpenEXR .fits – Flexible Image Transport System primarily for Astronomy .flif – Free Lossless Image Format .gif – Graphics Interchange Format .iff / .lbm – InterLeaved BitMap .jng – JPEG Network Graphics .jpg or .jpeg – Joint Photographic Experts Group .jxl – JPEG XL .mng – Multiple-image Network Graphics .miff / .mi – Magick Image File Format .pam, .pbm, .pgm, .ppm, .pnm – Netpbm file formats .pgf – Progressive Graphics File .png – Portable Network Graphics .qoi – Quite OK Image Format .tiff – Tag Image File Format .wbmp – Wireless Application Protocol Bitmap Format .webp .xbm – X BitMap .xcf – GIMP .xpm – X PixMap .adoc – AsciiDoc .epub – ebook format .latex – LaTeX, macro package built on top of TeX for simplification .md – Markdown .odt – OpenDocument .rtf – Rich Text Format .tex – high-quality typography for mathematical notation, physics, chemistry, engineering/scientific notation .texinfo 1DayLater – invoicing software GnuCash – double-entry book-keeping HomeBank – personal accounting software KMyMoney – double-entry book-keeping LedgerSMB – double-entry book-keeping RCA open-source application – management accounting application SQL-Ledger – double-entry book-keeping TurboCASH – double-entry book-keeping for Windows Bitcoin – blockchain platform, peer-to-peer decentralised digital currency Ethereum – blockchain platform with smart contract functionality CiviCRM – Constituent Relationship Management software aimed at charities and NGOs iDempiere – business Suite, ERP and CRM SuiteCRM – web-based CRM Adempiere – Enterprise resource planning (ERP) business suite Apache OFBiz – suite of enterprise applications from Apache Software Foundation Compiere – ERP solution automates accounting, supply chain, inventory, and sales orders Dolibarr – web-based ERP system ERPNext – web-based ERP system for managing accounting and finance ERP5 – Single Unified Business Model based system written with Python and Zope iDempiere – fully navigable on PCs, tablets and smartphones driven only by a community of supporters JFire – ERP business suite written with Java and JDO LedgerSMB – double entry accounting and ERP system written with Perl metasfresh – ERP Software Odoo – ERP, CRM and CMS Openbravo – web-based ERP Tryton – ERP MAME – multi-platform emulator for arcade game systems Mednafen – multi-platform emulator MESS – multi-platform emulator RetroArch – cross-platform front-end for emulators, game engines and video games Snes9x – Super Nintendo emulator Stella – Atari 2600 emulator PCSX – PlayStation emulator PCSX2 – PlayStation 2 emulator PPSSPP – PlayStation Portable emulator Project64 – Nintendo 64 emulator RPCS3 – PlayStation 3 emulator Dolphin (emulator) – GameCube and Wii emulator Citra (emulator) – Nintendo 3DS and Wii emulator Cemu – Wii U emulator TIC-80 – virtual machine game engine that mimics the 8-bit systems of the 1980s QGIS – cross-platform desktop geographic information system (GIS) application to view, edit, and analyse geospatial data ADMB Euler Math Toolbox FreeMat GNU Data Language GNU MCSim GNU Octave J Julia Owl Scientific Computing Perl Data Language S-Lang Scilab Yorick Blender Game Engine – discontinued 2019 Godot – application for the design of cross-platform video games MonoGame – C# framework Open3DEngine – based on Amazon Lumberyard Stride – (prev. Xenko) 2D and 3D cross-platform game engine originally developed by Silicon Studio Amavis – email content filter Claws Mail – email Client Fetchmail – email Retrieval Geary – email client based on WebKitGTK+ GNUMail – cross-platform email client Hula – discontinued mail and calendar project K-9 Mail – Android Email Client MailScanner – email security system MH Message Handling System – email Client Modest – email Client Mozilla Mail & Newsgroups – email Client that was part of the now discontinued Mozilla Application Suite Mozilla Thunderbird – email, news, RSS, and chat client POPFile – cross-platform mail filter Proton Mail – app and web-based end-to-end encrypted e-mail evolved to become FOSS Roundcube – web-based IMAP email client Sylpheed – email and News Client Sympa – MLA software I2P – anonymous network layer (implemented as a mix network) that allows for censorship-resistant, peer-to-peer communication OnionShare – file sharing app using Tor network Popcorn Time – multi-platform media player qBittorrent – BitTorrent client Transmission – BitTorrent client Deluge – BitTorrent client BSD – FreeBSD, OpenBSD, NetBSD, GhostBSD, TrueNAS, MidnightBSD, DragonFly BSD, OPNsense, pfSense, XigmaNAS, among others. GrapheneOS – Privacy- and security-focused, Android-based mobile operating system Kali NetHunter Linux – Debian, Ubuntu, Manjaro, Fedora, openSUSE, antiX, NixOS, Kali, Alpine, Tails, Mageia, Slackware, Gentoo, BlackArch, among others (List of Linux distributions). LineageOS – Android-based operative system for tablets and mobile phones GNU Hurd Mobian Nura Plasma Mobile PureOS Ubuntu Touch Redox OS FreeDOS – OS compatible with IBM PC DOS and Microsoft's MS-DOS ReactOS – OS intended to run the same software as Windows, originally designed to simulate Windows NT 4.0, later aiming at Windows 7 compatibility. It has been in the development stage since 1996.
AppleWin DOSBox – DOS programs emulator (including PC games) GNOME Boxes Hercules (emulator) Kernel-based Virtual Machine (KVM) QEMU VirtualBox – hosted hypervisor for x86 virtualization DTrace – dynamic tracing framework for analyzing and troubleshooting running applications and operating systems Memtest86 – stress-tests RAM on x86 machines strace – diagnostic utility for tracing system calls and signals Valgrind – debugging and profiling tool for detecting memory and threading errors Xnee – record and replay tests Acceleo – model-to-text code generator Apache Velocity – Java-based template engine used for code generation Babel – JavaScript transcompiler Bison CodeSynthesis XSD – XML Data Binding compiler for C++ CodeSynthesis XSD/e – validating XML parser/serializer and C++ XML Data Binding generator for mobile and embedded systems Flex lexical analyser – generates lexical analyzers Open Scene Graph – 3D graphics application programming interface OpenSCDP – Open Smart Card Development Platform SableCC – parser generator for Java and .NET SWIG – Simplified Wrapper and Interface Generator for several languages Umple – modeling and programming language with source code generation xmlbeansxx – XML Data Binding code generator for C++ YAKINDU Statechart Tools – Statechart code generator for C++ and Java Apache Flink – stream and batch data processing framework Apache Hadoop – distributed storage and processing framework Apache Mahout – scalable machine learning library Apache Spark – unified analytics engine Dask – parallel computing for analytics in Python ELKI – data analysis algorithms library GNU Octave – numerical computing environment JASP – GUI program for data analytics, data science, and machine learning Jupyter Notebook – interactive computing Keras – neural network library KNIME – data analytics platform Matplotlib – data visualization library MLlib – machine learning library for Apache Spark NumPy – numerical computing library Orange – data mining tool pandas – data manipulation library PyTorch – machine learning and deep learning framework Python R – statistical computing language SageMath – mathematics and data analysis environment SciPy – scientific computing library scikit-learn – Python machine learning library TensorFlow – machine learning framework WEKA – machine learning and data analysis suite 3G Bridge – grid interoperability Advanced Resource Connector – middleware BOINC – volunteer computing HTCondor – high-throughput computing Simple Grid Protocol – grid computing UNICORE – middleware CP2K – atomistic and molecular simulation of solid-state, liquid, molecular, and biological systems 2. System Architecture & Core Working Principles Open-source software Open-source license Comparison of file synchronization software § Open-source GNOME Core Applications List of concept- and mind-mapping software § Free and open-source List of formerly proprietary software List of GNU packages List of HDL simulators § Free and open-source simulators List of KDE applications List of open-source hardware projects List of optimization software § Free and open-source software List of public domain projects List of spreadsheet software § Free and open-source software List of Unix commands The Secure Remote Password protocol (SRP) is an augmented password-authenticated key exchange (PAKE) protocol, specifically designed to work around existing patents. Like all PAKE protocols, an eavesdropper or man in the middle cannot obtain enough information to be able to brute-force guess a password or apply a dictionary attack without further interactions with the parties for each guess. Furthermore, being an augmented PAKE protocol, the server does not store password-equivalent data. This means that an attacker who steals the server data cannot masquerade as the client unless they first perform a brute force search for the password. In layman's terms, during SRP (or any other PAKE protocol) authentication, one party (the "client" or "user") demonstrates to another party (the "server") that they know the password, without sending the password itself nor any other information from which the password can be derived. The password never leaves the client and is unknown to the server. Furthermore, the server also needs to know about the password (but not the password itself) in order to instigate the secure connection. This means that the server also authenticates itself to the client which prevents phishing without reliance on the user parsing complex URLs. The only mathematically proven security property of SRP is that it is equivalent to Diffie-Hellman against a passive attacker. While mature and widely deployed, SRP is an older design with some variants showing subtle weaknesses; it is not UCIsecure, lacks resistance to all precomputation attacks, has weaker formal proofs, and offers no protection against certain modern attack models. For these reasons, SRP is now largely considered superseded. OPAQUE is the preferred augmented PAKE, while CPace or SPAKE2 are favored for balanced PAKE scenarios where both parties share the password.
q and N = 2q + 1 are chosen such that both are prime (which makes q a Sophie Germain prime and N a safe prime). N must be large enough so that computing discrete logarithms modulo N is infeasible. All arithmetic is performed in the ring of integers modulo N, Z N {\displaystyle \scriptstyle \mathbb {Z} _{N}} . This means that below gx should be read as gxmod N g is a generator of the multiplicative group Z N ∗ {\displaystyle \scriptstyle \mathbb {Z} _{N}^{*}} . H() is a hash function; e.g., SHA-256. k is a parameter derived by both sides; in SRP-6, k = 3, while in SRP-6a it is derived from N and g : k = H(N, g). It is used to prevent a 2-for-1 guess when an active attacker impersonates the server. s is a salt. I is an identifying username. p is the user's password. v is the host's password verifier, v = gx where at a minimum x = H(s, p). As x is only computed on the client it is free to choose a stronger algorithm. An implementation could choose to use x = H(s | I | p) without affecting any steps required of the host. The standard RFC2945 defines x = H(s | H ( I | ":" | p) ). Use of I within x avoids a malicious server from being able to learn if two users share the same password. A and B are random one time ephemeral keys of the user and host respectively. | (pipe) denotes concatenation. All other variables are defined in terms of these. First, to establish a password p with server Steve, client Carol picks a random salt s, and computes x = H(s, p), v = gx. Steve stores v and s, indexed by I, as Carol's password verifier and salt. Carol must not share x with anybody, and must safely erase it at this step, because it is equivalent to the plaintext password p. This step is completed before the system is used as part of the user registration with Steve. Note that the salt s is shared and exchanged to negotiate a session key later so the value could be chosen by either side but is done by Carol so that she can register I, s and v in a single registration request. The transmission and authentication of the registration request is not covered in SRP. Then to perform a proof of password at a later date the following exchange protocol occurs: Carol → Steve: generate random value a; send I and A = ga Steve → Carol: generate random value b; send s and B = kv + gb Both: u = H(A, B) Carol: SCarol = (B − kgx)(a + ux) = (kv + gb − kgx)(a + ux) = (kgx − kgx + gb)(a + ux) = (gb)(a + ux) Carol: KCarol = H(SCarol) Steve: SSteve = (Avu)b = (gavu)b = [ga(gx)u]b = (ga + ux)b = (gb)(a + ux) Steve: KSteve = H(SSteve) = KCarol Now the two parties have a shared, strong session key K. To complete authentication, they need to prove to each other that their keys match. One possible way is as follows: Carol → Steve: M1 = H[H(N) XOR H(g) | H(I) | s | A | B | KCarol]. Steve verifies M1. Steve → Carol: M2 = H(A | M1 | KSteve).
Carol verifies M2. This method requires guessing more of the shared state to be successful in impersonation than just the key. While most of the additional state is public, private information could safely be added to the inputs to the hash function, like the server private key. Alternatively, in a password-only proof the calculation of K can be skipped and the shared S proven with: Carol → Steve: M1 = H(A | B | SCarol). Steve verifies M1. Steve → Carol: M2 = H(A | M1 | SSteve). Carol verifies M2. When using SRP to negotiate a shared key K which will be immediately used after the negotiation, it is tempting to skip the verification steps of M1 and M2. The server will reject the very first request from the client which it cannot decrypt. This can however be dangerous as demonstrated in the Implementation Pitfalls section below. The two parties also employ the following safeguards: Carol will abort if she receives B = 0 (mod N) or u = 0. Steve will abort if he receives A (mod N) = 0. Carol must show her proof of K (or S) first. If Steve detects that Carol's proof is incorrect, he must abort without showing his own proof of K (or S) Carol → Steve: generate random value a; send I and A = ga Steve: u = H(A, B); S=Avu; K=H(S) Steve: generate message m and encrypts it to produce c=ENC(K,m) Steve → Carol: generate random value b; send s, B = kv + gb and c Carol doesn't know x or v. But given any password p she can compute: xp = H(salt, p) Sp = (B - kgxp)(a + uxp) Kp = H(Sp) Kp is the key that Steve would use if p was the expected password. All values required to compute Kp are either controlled by Carol or known from the first packet from Steve. Carol can now try to guess the password, generate the corresponding key, and attempt to decrypt Steve's encrypted message c to verify the key.
As protocol messages tend to be structured, it is assumed that identifying that c was properly decrypted is easy. This allows offline recovery of the password. This attack would not be possible had Steve waited for Carol to prove she was able to compute the correct key before sending an encrypted message. Proper implementations of SRP are not affected by this attack as the attacker would be unable to pass the key verification step.
ISO/IEC 11770-4:2006 "Key Agreement Mechanism 2" (calls the method "SRP-6, but has the k calculation of 6a) RFC 5054 TLS-SRP of 2007 (again referred to as "SRP-6", but corrected in erratum) IEEE Std 1363.2-2008 "DLAPKAS-SRP6" (again referred to as "SRP-6") IEEE 1363.2 also includes a description of "SRP5", a variant replacing the discrete logarithm with an elliptic curve contributed by Yongge Wang in 2001. It also describes SRP-3 as found in RFC 2945.
Mailpile is a free and open-source email client with the main focus of privacy and usability. It is a webmail client, albeit one run from the user's computer, as a downloaded program launched as a local website. University: University of Belgrade, School of Electrical Engineering Course: Data protection Year: 2025/2026 Team project (2 members) A Python application with a graphical user interface that implements the main concepts of the PGP scheme for protecting electronic messages.
The application provides RSA key management, message encryption and decryption, digital signatures and signature verification, as well as optional compression and Radix-64 encoding. The application uses RSA keys for asymmetric cryptographic operations and supports symmetric encryption as part of the PGP message protection process. The project supports TripleDES and AES128 symmetric algorithms. SHA-1 is used for hash generation during message signing, as specified by the project requirements.
Python GUI application implementing a PGP-based email protection scheme with RSA key management, message encryption, digital signatures, decryption and signature verification. A command line email client using PGP for end-to-end encryption. Created as a course project submission for Tampere University Secure Programming (COMP.SEC.300-2023-2024-1-TAU) course.
This software is made as an exercise and comes with NO WARRANTY WHAT SO EVER. Though I've made every effort to follow OWASP secure programming practices, the software has not been audited by a professional entity. The real world security has not been verified. The client is incredibly bare-bones. It is more like an example project or proof-of-concept, than a practical client for day-to-day emails.
Secure Encrypted Email Client (SEEC) is a light weight, cross platform, CLI email client providing integration with GNU Privacy Guard , to offer industry standard OpenPGP encryption for all*¹ messages. Typically with all email clients, all messages to-and-from email servers, are SSL/TLS encrypted, but the email provider may be able to read the contents of messages, while on their servers. PGP offers a robust way to implement end-to-end encryption in emails, solving the biggest security issue with emails.
Using PGP is not very easy or convenient. Few email clients offer plugins, much less in built support for PGP. SEEC aims to solve*² this. To achieve the maximum of platform independence, SEEC is written in Python 3.7, and runs on the command line. It can be installed on at least In theory it might work on Android devices, with a terminal emulator, but I haven't tested this.
For encrypting messages, SEEC uses the standard asymmetric encryption used by OpenPGP , 2048-bit RSA. It ensures compatibility with other PGP clients. One day elliptic curve cryptography will become the standard, but it unfortunately, at the time of writing is not. For encrypting the configuration file, containing the email server credentials, SEEC uses Python Fernet library, which uses AES-128 in CBC mode. 1 Your passphrase you enter will be used to unlock the email client and the private PGP key.
This program interfaces with an external GPG program to handle PGP encryption. It may be configured by default to remember your passphrase for a few minutes, even if you logged out of SEEC. You can change this in GPG settings. By default, SEEC does not save any of your messages to disk. This is to protect your privacy. Email header info is not encrypted. Do not put sensitive information in the subject field.
This program relies on GnuPG (gpg) . It is pre-installed on most Linux systems. It is also available for Windows. Additionally Windows users need Windows version of curses , called windows-curses . Install it with the command: Fill out according to your email providers instructions SEEC does not support insecure connections. SSL encryption for both incoming and outgoing mail must be set to true .
Google has discontinued support for the standard email authentication method, and instead requires the use of OAuth 2.0 "Sign in with Google" API . Since this is a not yet a ubiquitous way of authenticating with email servers, it is outside the main scope of this project. The config.yml you created in the previous steps will be imported and encrypted with your password. Select 1 from the menu.
You will be guided through creating a new password, generating a new key pair and encrypting your config. You will be shown a series of instructions and warnings. Continue by pressing enter. You can abort at any time by pressing Ctrl+C . Warning! if you lose your password, you will lose access to your configuration file and your private key, and lose access to all your encrypted messages.
Though not recommended, SEEC can be used without encryption. If you don't run the Encryption Setup Wizzard, SEEC will use the plain text config file and no keys will be generated. Since there is basically no downside to creating the keys and encrypting your email credintials is good for security, and is highly recommended . You can still import public keys to encrypt your messages, you just won't be able to decrypt any.
If you alredy have a key pair you want to use, you need to run the wizzard anyway. The set password must match the passphrase for ther private key. You can delete the extra keys you don't need afterward. To be able to send encrypted messages, you need the recipients' public keys. You can import them by selecting 2 . Copy paste the key data and press enter a few times.
3. Software Implementation, Frameworks & Protocols If you import multiple keys at once, make sure there are no more than one consecutive empty line between them. SEEC interprits two or more empty lines to be end of input. You will be prompted for your password. Password will be stored for the duration of your session.
The encryption status is displayed in the top right hand corner. For an encrypted message, pressing D will attempt to decrypt the message with your public key. If the decrypt fails, the output is empty, and a corresponding status message is displayed at the bottom of the screen. If a public key is available for the address, you are prompted to encrypt the message.
Address book allows you to send messages, and add new contacts. You can access it while logged in, by selecting 1 . When logged in, press 3 to export your public key. The key will be printed on screen. You can copy it form there, and paste it to an email, or deliver it another way. Using it others will be able to encrypt messages to you, but only you can open the messages, using your private key.
A Key Utility is also provided to you. You can access it from the main menu by selecting 3 , or by running core/crypto/key_utility.py directly. It offers more direct access to cryptographic features of SEEC, and supports more actions than the email client itself. It is intended for testing and troubleshooting, but is not explicitly supported. The keyring file is seec.pkr . It is stored in the seec-email/core/crypto/ folder. You can access it directly with any OpenPGP compatible program. Assuming you have followed the install instructions, you should have gpg installed.
Your private key is secured with the password you created when creating your user in SEEC. Decryption has failed. Either the password was incorrect, or the message was encrypted with a wrong key. There is no back door to give you access. Any such feature would be liable to be exploited. Use a password manager to securely store your passwords, so you don't loose them.
SEEC - Secure Encrypted Email Client. Created as a course project for Secure Programming course. PGPy is a Python implementation of the OpenPGP specification, as described in RFC 4880 . It aims to be easy to use above all else, but also to eventually embody a complete, compliant implementation of the specification.
PGPy has not been formally tested on Windows. I see no reason why it wouldn’t work, but your mileage may vary. If you try it out and run into any issues, please submit bug reports on the issue tracker ! Building PGPy on Linux requires a C compiler, headers for Python, headers for OpenSSL, and libffi, to support building Cryptography.
If you are on Mac OS, you may experience more limited functionality without installing a more capable version of OpenSSL. You may refer to Cryptography’s documentation on Building cryptography on macOS for information on how to do so. Once you have the prerequisites specified above, PGPy can be installed from PyPI using pip, like so: It is possible to generate most types of keys with PGPy now. The process is mostly straightforward: Specifying key expiration can be done using the key_expiration keyword when adding the user id. Expiration can be specified using a datetime.datetime or a datetime.timedelta object: Generating a subkey is similar to the process above, except that it requires an existing primary key: If you intend to maintain multiple keys in memory for extended periods, using a PGPKeyring may be more appropriate: Once you have one or more keys generated or loaded, there are some things you may need or want to do before they can be used.
It is usually recommended to passphrase-protect private keys. Adding a passphrase to a key is simple: If you have a key that is protected with a passphrase, you will need to unlock it first. PGPy handles this using a context manager block, which also removes the unprotected key material from the object once execution exits that block. Other than plaintext, you may want to be able to form PGP Messages. These can be signed and then encrypted to one or more recipients.
Existing messages can also be loaded very simply. This is nearly identical to loading keys, except that it only returns the new message object, instead of a tuple: One of the things you may want to do with PGPKeys is to sign things. This is split into several categories in order to keep the method signatures relatively simple. Remember that signing requires a private key.
Although signing things uses multiple methods, there is only one method to remember for verifying signatures: Encryption using keys requires a public key, while decryption requires a private key. PGPy currently only supports asymmetric encryption/decryption using RSA or ECDH: Care must be taken when doing this to delete the session key as soon as possible after encrypting the message.
Messages can also be encrypted to multiple recipients by pre-generating the session key: There are some situations where encrypting a message with a passphrase may be more desirable than doing so with someone else’s public key. That can be done like so: Sometimes a key is created without the correct usage flags and an error is raised when you try to use the key: To disable this check, set _require_usage_flags to False on the key before calling the problem function: PGPKey, PGPMessage, and PGPSignature objects can all be exported to OpenPGP-compatible binary and ASCII-armored formats.
4. Practical Deployment, Analysis & Case Studies This repository shows how to integrate file encryption and decryption using OpenPGP standard in Python. Here Symmetric encryption is used. OpenPGP (Pretty Good Privacy) is a free and open-source encryption standard used to secure email communication, files, and other data. It provides end-to-end encryption, which means that the data is encrypted on the sender's device and can only be decrypted by the intended recipient with their private key. OpenPGP uses public key cryptography to encrypt and decrypt data, and digital signatures to verify the authenticity and integrity of the data. It is widely used by individuals, businesses, and organizations to protect sensitive information and ensure secure communication.
GnuPG (GNU Privacy Guard) is a free and open-source software application used for encrypting, decrypting, and signing data, including files, email messages, and other types of digital communication. It provides a secure and private way to protect sensitive information and ensure the authenticity and integrity of digital data. GnuPG is based on the OpenPGP standard and supports various encryption algorithms, such as AES, RSA, and DSA. It is available for a wide range of operating systems, including Linux, macOS, and Windows, and can be integrated with various email clients and other software applications.
GnuPG is widely used by individuals, businesses, and organizations to protect their sensitive information and ensure secure communication. Python-GnuPG is a Python module that provides a high-level interface for working with GnuPG (GNU Privacy Guard) in Python. It allows developers to perform various GnuPG operations, such as encryption, decryption, signing, and verifying digital signatures, directly from Python scripts. Python-GnuPG is built on top of the GnuPG software and provides a more user-friendly and Pythonic way to interact with GnuPG. It supports both synchronous and asynchronous operations, and can be used with Python 2 and 3. Python-GnuPG is widely used by developers who need to integrate GnuPG functionality into their Python applications, such as email clients, backup software, and other security-related applications.
Permission is hereby granted, free of charge, to any person obtaining a copy of this software and associated documentation files (the "Software"), to deal in the Software without restriction, including without limitation the rights to use, copy, modify, merge, publish, distribute, sublicense, and/or sell copies of the Software, and to permit persons to whom the Software is furnished to do so, subject to the following conditions: The above copyright notice and this permission notice shall be included in all copies or substantial portions of the Software.
THE SOFTWARE IS PROVIDED "AS IS", WITHOUT WARRANTY OF ANY KIND, EXPRESS OR IMPLIED, INCLUDING BUT NOT LIMITED TO THE WARRANTIES OF MERCHANTABILITY, FITNESS FOR A PARTICULAR PURPOSE AND NONINFRINGEMENT. IN NO EVENT SHALL THE AUTHORS OR COPYRIGHT HOLDERS BE LIABLE FOR ANY CLAIM, DAMAGES OR OTHER LIABILITY, WHETHER IN AN ACTION OF CONTRACT, TORT OR OTHERWISE, ARISING FROM, OUT OF OR IN CONNECTION WITH THE SOFTWARE OR THE USE OR OTHER DEALINGS IN THE SOFTWARE.
The main objective was to explore the security of email system, Identification of the security issues related to common email systems, Implementation of secure email system using PGP and and GPG encryption and an python script to send encrypted emails over network, using packages/libraries : smtplib, email, ssl, MIME, getpass. The main objective was to explore the security of email system, Identification of the security issues related to common email systems, Implementation of secure email system using PGP and and GPG encryption and developing an python script to send encrypted emails over network, using packages/libraries : smtplib, email, ssl, MIME, getpass.
The gnupg module allows Python programs to make use of the functionality provided by the GNU Privacy Guard (abbreviated GPG or GnuPG). Using this module, Python programs can encrypt and decrypt data, digitally sign documents and verify digital signatures, manage (generate, list and delete) encryption keys, using Public Key Infrastructure (PKI) encryption technology based on OpenPGP.
This module is expected to be used with Python versions >= 3.6, or Python 2.7 for legacy code. Install this module using pip install python-gnupg . You can then use this module in your own code by doing import gnupg or similar. There is at least one fork of this project, which was apparently created because an earlier version of this software used the subprocess module with shell=True , making it vulnerable to shell injection. This is no longer the case .
Forks may not be drop-in compatible with this software, so take care to use the correct version, as indicated in the pip install command above. Apart from a recent-enough version of Python, in order to use this module you need to have access to a compatible version of the GnuPG executable. The system has been tested with GnuPG v1.4.9 on Windows and Ubuntu. On a Linux platform, this will typically be installed via your distribution’s package manager (e.g. apt-get on Debian/Ubuntu). Windows binaries are available here – use one of the gnupg-w32cli-1.4.x.exe installers for the simplest deployment options.
On Windows, it is not necessary to perform a full installation of GnuPG, using the standard installer, on each computer: it is normally sufficient to distribute only the executable, gpg.exe , and a DLL which it depends on, iconv.dll . These files do not need to be placed in system directories, nor are registry changes needed. The files need to be placed in a location such that implicit invocation will find them - such as the working directory of the application which uses the gnupg module, or on the system path if that is appropriate for your requirements. Alternatively, you can specify the full path to the gpg executable.
Note, however, that if you want to use GnuPG 2.0, then this simple deployment approach may not work, because there are more dependent files which you have to ship. For this reason, our recommendation is to stick with GnuPG 1.4.x on Windows, unless you specifically need 2.0 features - in which case, you may have to do a full installation rather than just relying on a couple of files).
By default, passphrases cannot be passed via streams to gpg unless the line allow-loopback-pinentry is added to gpg-agent.conf in the home directory used by gpg (this is also where the keyring files are kept). If that file does not exist, you will need to create it with that single line. Note that even with this configuration, some versions of GnuPG 2.1.x won’t work as expected. In our testing, we found, for example, that the 2.1.11 executable shipped with Ubuntu 16.04 didn’t behave helpfully, whereas a GnuPG 2.1.15 executable compiled from source on the same machine worked as expected.
This module is based on an earlier version, GPG.py , written by Andrew Kuchling. This was further improved by Richard Jones, and then even further by Steve Traugott. The gnupg module is derived from Steve Traugott’s module (the original site no longer exists - this link is to the Wayback Machine), and uses Python’s subprocess module to communicate with the GnuPG executable, which it uses to spawn a subprocess to do the real work.
Daniel Folkinshteyn ( recv_keys , handling of subkeys and SIGEXPIRED, KEYEXPIRED while verifying, EXPKEYSIG, REVKEYSIG) GnuPG works on the basis of a “home directory” which is used to store public and private keyring files as well as a trust database. You need to identify in advance which directory on the end-user system will be used as the home directory, as you will need to pass this information to gnupg .
If the home directory does not exist, a ValueError will be raised. Thereafter, all the operations available are accessed via methods of this instance. If the gnupghome parameter is omitted, GnuPG will use whatever directory is the default (consult the GnuPG documentation for more information on what this might be). Print information (e.g. the gpg command lines, and status messages returned by gpg) to the console. You don’t generally need to set this option, since the module uses Python’s logging package to provide more flexible functionality. The status messages from gpg are quite voluminous, especially during key generation.
If specified as True, the --use-agent parameter is passed to gpg , asking it to use any in-memory GPG agent (which remembers your credentials). If specified, the value is used as the name of the keyring file. The default keyring is not used. A list of paths to keyring files can also be specified.
If specified, the value should be a list of additional command-line options to pass to gpg . If specified, the value is used as the name of the secret keyring file. A list of paths to secret keyring files can also be specified. Note that these files are not used by GnuPG >= 2.1. If specified, the value is used as the environment variables used when calling the GPG executable.
Changed in version 0.3.4: The keyring argument can now also be a list of keyring filenames. New in version 0.3.4: The secret_keyring argument was added. Note that this argument is not used when working with GnuPG >= 2.1. If you specify values in options , make sure you don’t specify values which will conflict with other values added by python-gnupg . You should be familiar with GPG command-line arguments and how they affect GPG’s operation.
Changed in version 0.3.7: The default encoding was changed to latin-1 . In earlier versions, it was either locale.getpreferredencoding() or, failing that, sys.stdin.encoding , and failing that, utf-8 . If the gpgbinary executable cannot be found, a ValueError is raised in GPG.__init__() . The low-level communication between the gpg executable and python-gnupg is in terms of bytes, and python-gnupg tries to convert gpg’s stderr stream to text using an encoding. The default value of this is latin-1 , but you can override this by setting the encoding name in the GPG instance’s encoding attribute after instantiation, like this: If you use the wrong encoding, you may get exceptions. The 'latin-1' encoding leaves bytes as-is and shouldn’t fail with encoding/decoding errors, though it may not decode text correctly (so you may see odd characters in the decoding output).
The gpg executable will use an output encoding based on your environment settings (e.g. environment variables, code page etc.) but defaults to latin-1. The encoding is also used to encode passphrases sent to gpg . The default latin-1 encoding will fail if you pass Unicode which contains characters which are larger than what a byte can hold (many accented characters fall into this category). Use the appropriate encoding, perhaps utf-8 . From version 0.5.7, you can pass an encoding= keyword parameter to the GPG initializer with the encoding to be used. This just sets the encoding attribute of the instance.
From version 0.5.2 onwards, you can also control the buffer size for the I/O between gpg and python-gnupg by setting the buffer_size attribute on a GPG instance. It defaults to 16K. The module provides functionality for generating (creating) keys, listing keys, deleting keys, and importing and exporting keys. The first thing you typically want to do when starting with a PKI framework is to generate some keys. You can do this using the gen_key() method: where input_data is a special command string which tells GnuPG the parameters you want to use when creating the key. To make life easier, a helper method gen_key_input() is provided which takes keyword arguments which allow you to specify individual parameters of the key, as in the following example: 5. Performance Evaluation & Extended Technical Observations Sensible defaults are provided for parameters which you don’t specify, as shown in the following table.
If you don’t specify any parameters, the values in the table above will be used with the defaults indicated. There is a whole set of other parameters you can specify; see this GnuPG document for more details. While use of RSA keys is common (they can be used for both signing and encryption), another popular option is to use a DSA primary key (for signing) together with a secondary El-Gamal key (for encryption). For this latter option, you could supply the following additional parameters: The expiration date for the primary and any secondary key. You can specify an ISO date, A number of days/weeks/months/years, an epoch value, or 0 for a non-expiring key.
The passphrase to use. If this parameter is not specified, no passphrase is needed to access the key. Passphrases using newlines are not supported . Note that for GnuPG versions >= 2.1, a passphrase must be provided, unless extra steps are taken : see the no_protection argument, below. If no passphrase is wanted for a key (which might be the default for tests, say), or if you want to use an empty string as a passphrase, then you should specify True for this parameter. Otherwise, and if you don’t use pinentry to enter a passphrase, then GnuPG >= 2.1 will not allow this. It doesn’t make sense to specify True if a non-empty passphrase is being supplied.
A complete list of key generation parameters can be found in the GnuPG documentation here . Whatever keyword arguments you pass to gen_key_input() (other than no_protection ) will be converted to the parameters expected by GnuPG by replacing underscores with hyphens and title-casing the result. You can of course construct the parameters in your own dictionary params and then pass it as follows: The no_protection argument, if True , will be used to generate a %no-protection line which tells GnuPG that no protection with a passphrase is desired.
The return value from gen_key() is an object whose type and fingerprint attributes indicate the type and fingerprint of the created key. If no key was created, these will be None . New in version 0.4.9: There is now also a status attribute to the returned object which will be ‘ok’ if a key was created, ‘key not created’ if that was reported by gpg , or None in other cases.
The parameters are explained with every possible value in this GnuPG documentation under quick-add-key . If you use the default algorithm, you’ll get the default key size, which is dependent upon the version of GnuPG that’s used. If you want to specify the key size explicitly, you can use values for algorithm incorporating both the algorithm itself and the key size, as in the following examples.
Keys can be used for some or all of encryption, signing or authentication. These usages map onto flags assigned to a key - one or more of ‘encrypt’, ‘sign’ and ‘auth’. By default, nothing is specified, which assigns all flags to a key. But sometimes you may want to depart from this behaviour. For example, if you create a subkey for encryption, then you probably don’t want encryption to be enabled for the master key. You can specify the flags associated with a key by passing a key_usage keyword argument to gen_key_input() which provides one or more of the above flags in a space or comma-separated string, as in these example: This corresponds to the usage parameter of add_subkey() , described earlier. Note that you still need to ensure that the key type of the key being created is appropriate for the usages.
To generate keys with elliptic curves, pass a key_curve keyword parameter to gen_key_input() and omit key_length . For example, key_curve=’cv25519’ or key_type=’ECDSA’, key_curve=’nistp384’ . Refer to GnuPG resources to see which options are supported. Note that you’ll need GnuPG >= 2.1 for this to work. Supplemental information on the aliases used for key types and curves is given here . You can use the curve type alias in the algorithm argument to add_subkey() , as in the following example.
Key generation requires the system to work with a source of random numbers. Systems which are better at generating random numbers than others are said to have higher entropy . This is typically obtained from the system hardware; the GnuPG documentation recommends that keys be generated only on a local machine (i.e. not one being accessed across a network), and that keyboard, mouse and disk activity be maximised during key generation to increase the entropy of the system.
Unfortunately, there are some scenarios - for example, on virtual machines which don’t have real hardware - where insufficient entropy causes key generation to be extremely slow. If you come across this problem, you should investigate means of increasing the system entropy. On virtualised Linux systems, this can often be achieved by installing the rng-tools package. This is available at least on RPM-based and APT-based systems (Red Hat/Fedora, Debian, Ubuntu and derivative distributions).
For the keyids parameter, you can use a sequence of anything which GnuPG itself accepts to identify a key - for example, the keyid or the fingerprint could be used. If you want to pass a single keyid, then you can just pass in a string which identifies the key. If you pass an empty list in keyids , all keys are exported. minimal (defaulting to False ) - when True , passes --export-options export-minimal to gpg .
passphrase - if specified, sends the specified passphrase to gpg . For GnuPG >= 2.1, exporting secret keys requires a passphrase to be provided. expect_passphrase - defaults to True for backward compatibility. If the passphrase is to be passed to gpg via pinentry, you wouldn’t pass it here - so specify expect_passphrase=False in that case. If you don’t do that, and don’t pass a passphrase, a ValueError will be raised.
output - defaults to None , but if specified, should be the pathname of a file to which the exported keys should be written. To import keys, get the key data as an ASCII string, say key_data . Then you can call import_keys() with it: This will import all the keys in key_data . The number of keys imported will be available in import_result.count and the fingerprints of the imported keys will be in import_result.fingerprints .
In addition, extra_args and passphrase keyword parameter can be specified. If provided, extra_args is treated as a list of additional arguments to pass to the gpg executable. If passphrase is specified, it is passed to gpgg for when an imported secret key has a passphrase. This will fetch keys with all specified keyids and import them. Note that on Windows, you may require helper programs such as gpg_hkp.exe , distributed with GnuPG, to successfully run recv_keys . On Jython, security permissions may lead to failure of recv_keys .
Note that when you import keys, you may get spurious “key expired” / “signature expired” messages which are sent by gpg and collected by python-gnupg . This may happen, for example, if there are subkey expiry dates which have been extended, so that the keys haven’t actually expired, even when gpg sends messages that they have. Make sure you just look at the count and fingerprints attributes to identify the keys that were imported.
Now that we’ve seen how to generate, import and export keys, let’s move on to finding which keys we have in our keyrings. This is fairly straightforward using the list_keys() method: The returned value from list_keys() is a subclass of Python’s list class. Each entry represents one key and is a Python dictionary which contains useful information about the corresponding key.
The following entries are in the returned dictionary. Some of the key names are not ideal for describing the values, but they have been left as is for backward compatibility reasons. As GnuPG documentation has improved, a better understanding is possible of the information returned by gpg . Depending on the version of gpg used, some of these keys may have the value 'unavailable' . The last two keys are provided by python-gnupg rather than gpg .
For more information about the values in this dictionary, refer to the GnuPG documentation linked above. (Note that that documentation is not terribly user-friendly, but nevertheless it should be usable.) The returned value from list_keys() has an attribute uids , which is a list of userids associated with the listed keys, and an attribute fingerprints , which is a list of the key fingerprints associated with the listed keys.
New in version 0.3.8: The returned value from list_keys() now has a new attribute, key_map , which is a dictionary mapping key and subkey fingerprints to the corresponding key’s dictionary. With this change, you don’t need to iterate over the (potentially large) returned list to search for a key with a given fingerprint - the key_map dict will take you straight to the key info, whether the fingerprint you have is for a key or a subkey.
New in version 0.3.8: You can also list a subset of keys by specifying a keys= keyword argument to list_keys() whose value is either a single string matching a key, or a list of strings matching multiple keys. In this case, the return value only includes matching keys. New in version 0.3.9: A new sigs= keyword argument has been added to list_keys() , defaulting to False . If you specify true, the sigs entry in the key information returned will contain a list of signatures which apply to the key. Each entry in the list is a 3-tuple of ( keyid , user-id , signature-class ) where the signature-class is as defined by RFC-4880 .
It doesn’t make sense to supply both secret=True and sigs=True (people can’t sign your secret keys), so in case secret=True is specified, the sigs= value has no effect. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/List%20of%20free%20and%20open-source%20software%20packages • https://en.wikipedia.org/wiki/Secure%20Remote%20Password%20protocol • https://en.wikipedia.org/wiki/Mailpile • https://github.com/mbjelovuk/pgp_email_security • https://github.com/JValtteri/seec-email • https://pgpy.readthedocs.io/en/latest/index.html • https://pgpy.readthedocs.io/en/latest/examples.html • https://github.com/sumitsahoo/PGP-Encryption-Python • https://github.com/MishaDey/pgp-gpg-email-toolkit • https://gnupg.readthedocs.io/en/latest/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Secure Email Client Using Pgp Encryption In Python.
[*] Synchronizing KnowBe4 Awareness Training telemetry... ──────────────────────────────────────────────────────────────────────── [11:45:02.102] MAIL Dispatched simulated assessment templates [11:45:02.155] REPORT Majority of active users flagged probe via Phish Alert Button [11:45:02.210] CLICK Simulated lure baseline reduced below risk threshold [11:45:02.290] TRAIN Auto-enrolled flagged users into adaptive micro-learning modules ──────────────────────────────────────────────────────────────────────── [✓] Human Security Index: Phish-Prone percentage safely minimized
| Campaign Simulation | Platform Used | Total Recipients | Reported via Phish Button | Phish-Prone Percentage |
|---|---|---|---|---|
| Urgent Communication Lure | KnowBe4 KMSAT | 350 Employees | 318 (90.8%) | 2.9% (OPTIMAL) |
| Account Credential Lure | Proofpoint ZenGuide | 350 Employees | 324 (92.5%) | 2.1% (OPTIMAL) |
| Executive Impersonation | Mimecast Engage | 200 Executives | 192 (96.0%) | 1.5% (OPTIMAL) |