Complete Technical Paper Content — Secure File Storage Using RSA And AES Hybrid Encryption
Overview & System Context
Secure File Storage Using Rsa And Aes Hybrid Encryption: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9039 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background The RSA (Rivest–Shamir–Adleman) cryptosystem is a family of public-key cryptosystems (one of the oldest), widely used for secure data transmission. The initialism "RSA" comes from the last-names of Ron Rivest, Adi Shamir and Leonard Adleman, who publicly described the algorithm in 1977. An equivalent system was developed secretly in 1973 at Government Communications Headquarters (GCHQ), the British signals intelligence agency, by the English mathematician Clifford Cocks.
That system was declassified in 1997. RSA is used in digital signature such as RSASSA-PSS or RSA-FDH, public-key encryption of very short messages (almost always a single-use symmetric key in a hybrid cryptosystem) such as RSAES-OAEP, and public-key key encapsulation. In RSA-based cryptography, a user's private key—which can be used to sign messages, or decrypt messages sent to that user—is a pair of large prime numbers chosen at random and kept secret. A user's public key—which can be used to verify messages from the user, or encrypt messages so that only that user can decrypt them—is the product of the prime numbers. The security of RSA is related to the difficulty of factoring the product of two large prime numbers, the "factoring problem". Breaking RSA encryption is known as the RSA problem. Whether it is as difficult as the factoring problem is an open question. There are no published methods to defeat the system if a large enough key is used.
Ron Rivest, Adi Shamir, and Leonard Adleman at the Massachusetts Institute of Technology made several attempts over the course of a year to create a function that was hard to invert. Rivest and Shamir, as computer scientists, proposed many potential functions, while Adleman, as a mathematician, was responsible for finding their weaknesses. They tried many approaches, including "knapsack-based" and "permutation polynomials". For a time, they thought what they wanted to achieve was impossible due to contradictory requirements. In April 1977, they spent Passover at the house of a student and drank a good deal of wine before returning to their homes at around midnight. Rivest, unable to sleep, lay on the couch with a math textbook and started thinking about their one-way function. He spent the rest of the night formalizing his idea, and he had much of the paper ready by daybreak. The algorithm is now known as RSA – the initials of their surnames in same order as their paper. Clifford Cocks, an English mathematician working for the British intelligence agency Government Communications Headquarters (GCHQ), described a similar system in an internal document in 1973. However, given the relatively expensive computers needed to implement it at the time, it was considered to be mostly a curiosity and, as far as is publicly known, was never deployed. His ideas and concepts were not revealed until 1997 due to its top-secret classification.
Kid-RSA (KRSA) is a simplified, insecure public-key cipher published in 1997, designed for educational purposes. Kid-RSA gives insight into RSA and other public-key ciphers, analogous to simplified DES. The system includes a communications channel coupled to at least one terminal having an encoding device and to at least one terminal having a decoding device. A message-to-be-transferred is enciphered to ciphertext at the encoding terminal by encoding the message as a number M in a predetermined set. That number is then raised to a first predetermined power (associated with the intended receiver) and finally computed. The remainder or residue, C, is... computed when the exponentiated number is divided by the product of two predetermined prime numbers (associated with the intended receiver).
A detailed description of the algorithm was published in August 1977, in Scientific American's Mathematical Games column. This preceded the patent's filing date of December 1977. Consequently, the patent had no legal standing outside the United States. Had Cocks' work been publicly known, a patent in the United States would not have been legal either. When the patent was issued, terms of patent were 17 years. The patent was about to expire on 21 September 2000, but RSA Security released the algorithm to the public domain on 6 September 2000.
Choose two distinct large prime numbers p and q. To make factoring infeasible, p and q must be chosen at random from a large space of possibilities, such as all prime numbers between 21023 and 21024 (corresponding to a 2,048-bit key). Many different algorithms for prime selection are used in practice. p and q are kept secret. Compute n = pq. n is used as the modulus for both the public and private keys. Its length, usually expressed in bits, is the key length. n is released as part of the public key. Compute λ(n), where λ is Carmichael's totient function. Since n = pq, λ(n) = lcm(λ(p), λ(q)), and since p and q are prime, λ(p) = φ(p) = p − 1, and likewise λ(q) = q − 1. Hence λ(n) = lcm(p − 1, q − 1). The lcm may be calculated through the Euclidean algorithm, since lcm(a, b) = I|ab|/gcd(a, b)I. λ(n) is kept secret. Choose an integer e such that 1 < e < λ(n) and gcd(e, λ(n)) = 1; that is, e and λ(n) are coprime. e having a short bit-length and small Hamming weight results in more efficient encryption – the most commonly chosen value for e is 216 + 1 = 65537. The smallest (and fastest) possible value for e is 3, but such a small value for e may expose vulnerabilities in insecure padding schemes. e is released as part of the public key.
Determine d as d ≡ e−1 (mod λ(n)); that is, d is the modular multiplicative inverse of e modulo λ(n). This means: solve for d the equation de ≡ 1 (mod λ(n)); d can be computed efficiently by using the extended Euclidean algorithm, since, thanks to e and λ(n) being coprime, said equation is a form of Bézout's identity, where d is one of the coefficients. d is kept secret as the private key exponent. The public key consists of the modulus n and the public exponent e. The private key consists of the private exponent d, which must be kept secret. p, q, and λ(n) must also be kept secret because they can be used to calculate d. In fact, they can all be discarded after d has been computed. In the original RSA paper, the Euler totient function φ(n) = (p − 1)(q − 1) is used instead of λ(n) for calculating the private exponent d. Since φ(n) is always divisible by λ(n), the algorithm works as well. The possibility of using Euler totient function results also from Lagrange's theorem applied to the multiplicative group of integers modulo pq. Thus any d satisfying d⋅e ≡ 1 (mod φ(n)) also satisfies d⋅e ≡ 1 (mod λ(n)). However, computing d modulo φ(n) will sometimes yield a result that is larger than necessary (i.e. d > λ(n)). Most of the implementations of RSA will accept exponents generated using either method (if they use the private exponent d at all, rather than using the optimized decryption method based on the Chinese remainder theorem described below), but some standards such as FIPS 186-4 (Section B.3.1) may require that d < λ(n). Any "oversized" private exponents not meeting this criterion may always be reduced modulo λ(n) to obtain a smaller equivalent exponent. Note: The authors of the original RSA paper carry out the key generation by choosing d and then computing e as the modular multiplicative inverse of d modulo φ(n), whereas most current implementations of RSA, such as those following PKCS#1, do the reverse—choose e and compute d from it. Since e can safely be small and fixed, whereas d must be chosen from a large enough space to resist attack, the modern approach can reduce the cost of the public-key operation without loss of security.
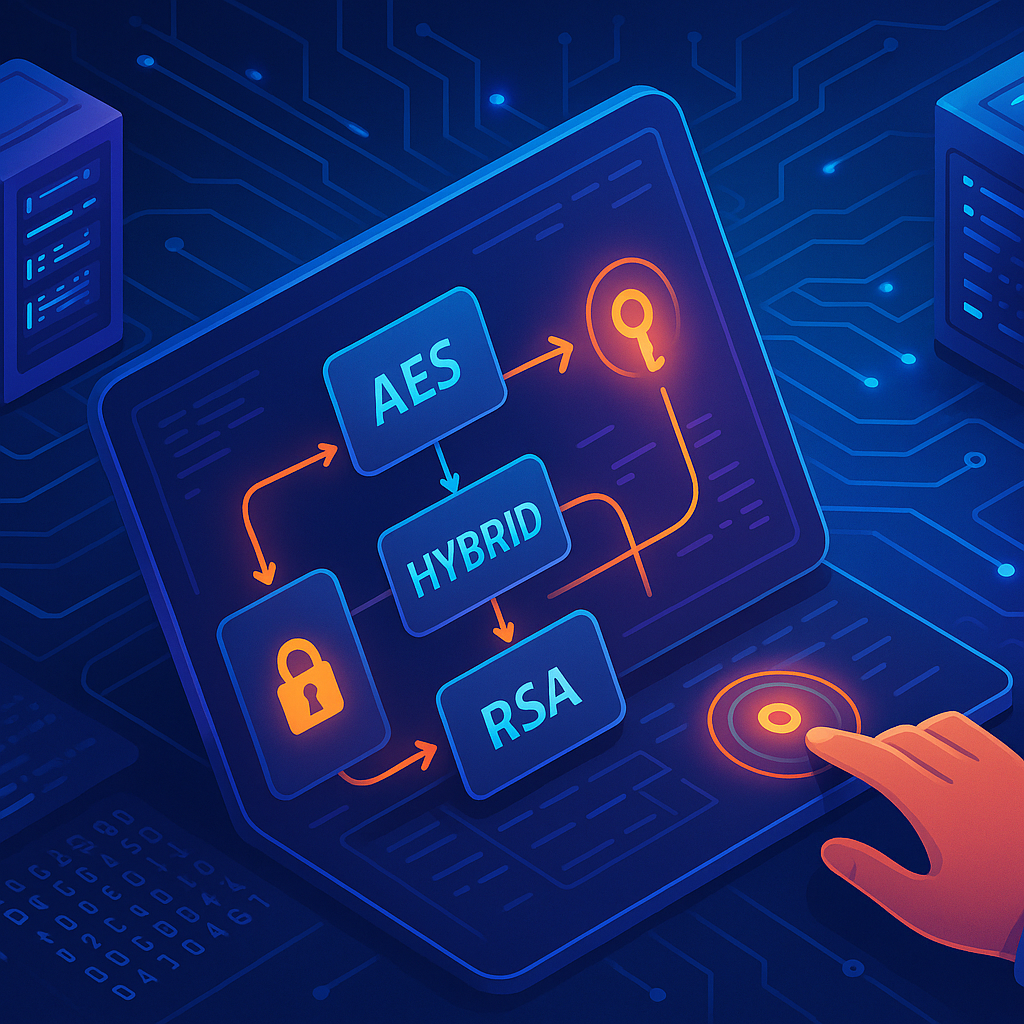
Figure 1: I Interactive Encryption Flow Simulator – Visualize AES, RSA, Hybrid ... c ≡ m e ( mod n ) . {\displaystyle c\equiv m^{e}{\pmod {n}}.} This can be done reasonably quickly, even for very large numbers, using modular exponentiation. Bob then transmits c to Alice. Note that at least nine values of m will yield a ciphertext c equal to m, but this is very unlikely to occur in practice.
c d ≡ ( m e ) d ≡ m ( mod n ) . {\displaystyle c^{d}\equiv (m^{e})^{d}\equiv m{\pmod {n}}.} Given m, she can recover the original message M by reversing the padding scheme, or discard it as corrupted if the padding is invalid. Alice must discard m if the padding is invalid: if she reveals any information about m when it has invalid padding, an adversary could exploit this to decrypt (or sign) messages without knowing the private key, by sending her random or maliciously crafted ciphertexts and observing how she responds.
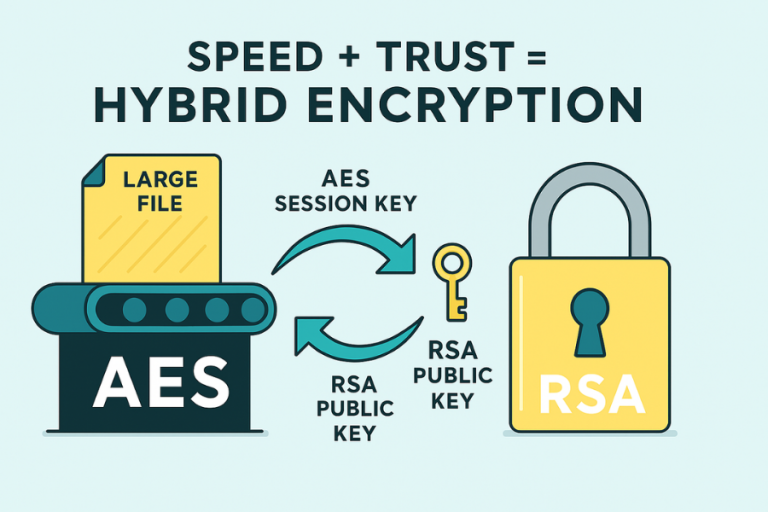
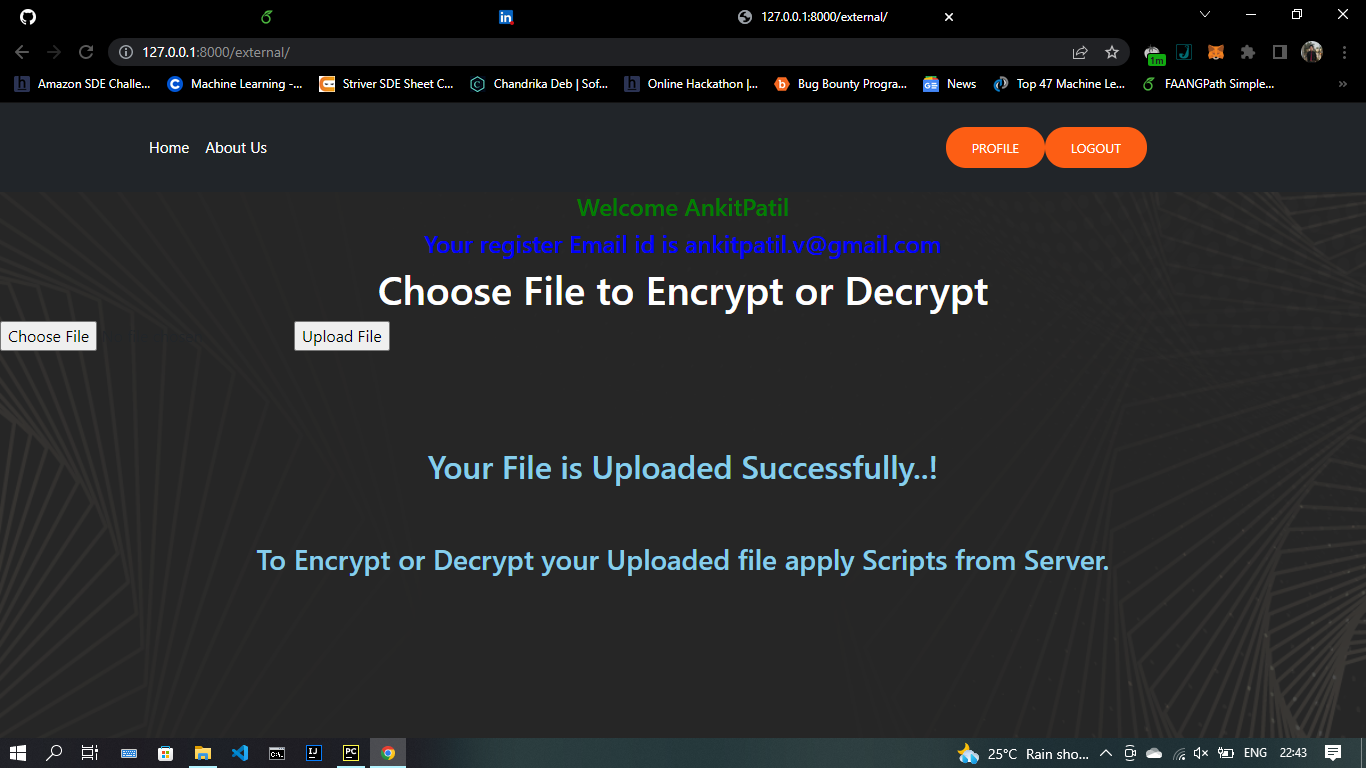
Figure 2: How RSA & AES Work Together (Hybrid Encryption) In Real Apps ... p = 61 {\displaystyle p=61} and q = 53 {\displaystyle q=53} . Compute n = pq giving n = 61 × 53 = 3233. {\displaystyle n=61\times 53=3233.} Compute the Carmichael's totient function of the product as λ(n) = lcm(p − 1, q − 1) giving λ ( 3233 ) = lcm I ( 60 , 52 ) = 780. {\displaystyle \lambda (3233)=\operatorname {lcm} (60,52)=780.} Figure 3: GitHub - ankitpatil-ap/Advance-File-Security-using-AES-and-RSA ...
Choose any number 1 < e < 780 that is coprime to 780. Choosing a prime number for e leaves us only to check that e is not a divisor of 780. Let e = 17 {\displaystyle e=17} . Compute d, the modular multiplicative inverse of e (mod λ(n)), yielding d = 413 , {\displaystyle d=413,} as 1 = ( 17 × 413 ) mod 7 80. {\displaystyle 1=(17\times 413){\bmod {7}}80.} 2. System Architecture & Core Working Principles The public key is (n = 3233, e = 17). For a padded plaintext message m, the encryption function is c ( m ) = m e mod n = m 17 mod 3 233. {\displaystyle {\begin{aligned}c(m)&=m^{e}{\bmod {n}}\\&=m^{17}{\bmod {3}}233.\end{aligned}}} The private key is (n = 3233, d = 413). For an encrypted ciphertext c, the decryption function is m ( c ) = c d mod n = c 413 mod 3 233. {\displaystyle {\begin{aligned}m(c)&=c^{d}{\bmod {n}}\\&=c^{413}{\bmod {3}}233.\end{aligned}}} c = 65 17 mod 3 233 = 2790. {\displaystyle c=65^{17}{\bmod {3}}233=2790.} m = 2790 413 mod 3 233 = 65. {\displaystyle m=2790^{413}{\bmod {3}}233=65.} Both of these calculations can be computed efficiently using the square-and-multiply algorithm for modular exponentiation. In real-life situations the primes selected would be much larger; in our example it would be trivial to factor n = 3233 (obtained from the freely available public key) back to the primes p and q. e, also from the public key, is then inverted to get d, thus acquiring the private key. Practical implementations use the Chinese remainder theorem to speed up the calculation using modulus of factors (mod pq using mod p and mod q). The values dp, dq and qinv, which are part of the private key are computed as follows: d p = d mod ( p − 1 ) = 413 mod ( 61 − 1 ) = 53 , d q = d mod ( q − 1 ) = 413 mod ( 53 − 1 ) = 49 , q inv = q − 1 mod p = 53 − 1 mod 6 1 = 38 ⇒ ( q inv × q ) mod p = 38 × 53 mod 6 1 = 1. {\displaystyle {\begin{aligned}d_{p}&=d{\bmod {(}}p-1)=413{\bmod {(}}61-1)=53,\\d_{q}&=d{\bmod {(}}q-1)=413{\bmod {(}}53-1)=49,\\q_{\text{inv}}&=q^{-1}{\bmod {p}}=53^{-1}{\bmod {6}}1=38\\&\Rightarrow (q_{\text{inv}}\times q){\bmod {p}}=38\times 53{\bmod {6}}1=1.\end{aligned}}} Here is how dp, dq and qinv are used for efficient decryption (encryption is efficient by choice of a suitable d and e pair): m 1 = c d p mod p = 2790 53 mod 6 1 = 4 , m 2 = c d q mod q = 2790 49 mod 5 3 = 12 , h = ( q inv × ( m 1 − m 2 ) ) mod p = ( 38 × − 8 ) mod 6 1 = 1 , m = m 2 + h × q = 12 + 1 × 53 = 65. {\displaystyle {\begin{aligned}m_{1}&=c^{d_{p}}{\bmod {p}}=2790^{53}{\bmod {6}}1=4,\\m_{2}&=c^{d_{q}}{\bmod {q}}=2790^{49}{\bmod {5}}3=12,\\h&=(q_{\text{inv}}\times (m_{1}-m_{2})){\bmod {p}}=(38\times -8){\bmod {6}}1=1,\\m&=m_{2}+h\times q=12+1\times 53=65.\end{aligned}}} s e = ( h d ) e = h d e = h e d = ( h e ) d ≡ h ( mod n ) . {\displaystyle s^{e}=(h^{d})^{e}=h^{de}=h^{ed}=(h^{e})^{d}\equiv h{\pmod {n}}.} The modular exponentiation for signing and verification is the same underlying mathematics as for decryption and encryption, but all the other details of padding scheme for secure public-key encryption and hashing for secure digital signature are different. The use of a hash, first proposed in 1978 by Michael O. Rabin in the related Rabin signature algorithm, and the security of the hash, is essential for security of the signature: if Alice and Bob skipped the hash, and Bob checked for se ≡ m (mod n) instead, then anyone could forge the signature s = 1 on the message m = 1, or take two signed messages (m1, s1) and (m2, s2) from Alice and then forge a third by multiplication, (m1m2, s1s2), without knowledge of the private key.
( m e ) d ≡ m ( mod p q ) {\displaystyle (m^{e})^{d}\equiv m{\pmod {pq}}} 3. Software Implementation, Frameworks & Protocols for every integer m when p and q are distinct prime numbers and e and d are positive integers satisfying ed ≡ 1 (mod λ(pq)). Since λ(pq) = lcm(p − 1, q − 1) is, by construction, divisible by both p − 1 and q − 1, we can write e d − 1 = h ( p − 1 ) = k ( q − 1 ) {\displaystyle ed-1=h(p-1)=k(q-1)} for some nonnegative integers h and k. To check whether two numbers, such as med and m, are congruent mod pq, it suffices (and in fact is equivalent) to check that they are congruent mod p and mod q separately. To show med ≡ m (mod p), we consider two cases: If m ≡ 0 (mod p), m is a multiple of p. Thus med is a multiple of p. So med ≡ 0 ≡ m (mod p). If m I 0 (mod p), m e d = m e d − 1 m = m h ( p − 1 ) m = ( m p − 1 ) h m ≡ 1 h m ≡ m ( mod p ) , {\displaystyle m^{ed}=m^{ed-1}m=m^{h(p-1)}m=(m^{p-1})^{h}m\equiv 1^{h}m\equiv m{\pmod {p}},} where we used Fermat's little theorem to replace mp−1 mod p with 1. The verification that med ≡ m (mod q) proceeds in a completely analogous way: m e d = m e d − 1 m = m k ( q − 1 ) m = ( m q − 1 ) k m ≡ 1 k m ≡ m ( mod q ) . {\displaystyle m^{ed}=m^{ed-1}m=m^{k(q-1)}m=(m^{q-1})^{k}m\equiv 1^{k}m\equiv m{\pmod {q}}.} This completes the proof that, for any integer m, and integers e, d such that ed ≡ 1 (mod λ(pq)), ( m e ) d ≡ m ( mod p q ) . {\displaystyle (m^{e})^{d}\equiv m{\pmod {pq}}.} m e d = m 1 + h φ ( n ) = m ( m φ ( n ) ) h ≡ m ( 1 ) h ≡ m ( mod n ) , {\displaystyle m^{ed}=m^{1+h\varphi (n)}=m(m^{\varphi (n)})^{h}\equiv m(1)^{h}\equiv m{\pmod {n}},} where the second-last congruence follows from Euler's theorem. More generally, for any e and d satisfying ed ≡ 1 (mod λ(n)), the same conclusion follows from Carmichael's generalization of Euler's theorem, which states that mλ(n) ≡ 1 (mod n) for all m relatively prime to n. When m is not relatively prime to n, the argument just given is invalid. This is highly improbable (only a proportion of 1/p + 1/q − 1/(pq) numbers have this property), but even in this case, the desired congruence is still true. Either m ≡ 0 (mod p) or m ≡ 0 (mod q), and these cases can be treated using the previous proof.
When encrypting with low encryption exponents (e.g., e = 3) and small values of the m (i.e., m < n1/e), the result of me is strictly less than the modulus n. In this case, ciphertexts can be decrypted easily by taking the eth root of the ciphertext over the integers. If the same clear-text message is sent to e or more recipients in an encrypted way, and the receivers share the same exponent e, but different p, q, and therefore n, then it is easy to decrypt the original clear-text message via the Chinese remainder theorem. Johan Håstad noticed that this attack is possible even if the clear texts are not equal, but the attacker knows a linear relation between them. This attack was later improved by Don Coppersmith (see Coppersmith's attack).
Because RSA encryption is a deterministic encryption algorithm (i.e., has no random component) an attacker can successfully launch a chosen plaintext attack against the cryptosystem, by encrypting likely plaintexts under the public key and test whether they are equal to the ciphertext. A cryptosystem is called semantically secure if an attacker cannot distinguish two encryptions from each other, even if the attacker knows (or has chosen) the corresponding plaintexts. RSA without padding is not semantically secure. RSA has the property that the product of two ciphertexts is equal to the encryption of the product of the respective plaintexts. That is, m1em2e ≡ (m1m2)e (mod n). Because of this multiplicative property, a chosen-ciphertext attack is possible. E.g., an attacker who wants to know the decryption of a ciphertext c ≡ me (mod n) may ask the holder of the private key d to decrypt an unsuspicious-looking ciphertext c′ ≡ cre (mod n) for some value r chosen by the attacker. Because of the multiplicative property, c' is the encryption of mr (mod n). Hence, if the attacker is successful with the attack, they will learn mr (mod n), from which they can derive the message m by multiplying mr with the modular inverse of r modulo n. Given the private exponent d, one can efficiently factor the modulus n = pq. And given factorization of the modulus n = pq, one can obtain any private key (d', n) generated against a public key (e', n).
p {\displaystyle p} and q {\displaystyle q} – the primes from the key generation, 4. Practical Deployment, Analysis & Case Studies d P = d ( mod p − 1 ) , {\displaystyle d_{P}=d{\pmod {p-1}},} d Q = d ( mod q − 1 ) , {\displaystyle d_{Q}=d{\pmod {q-1}},} q inv = q − 1 ( mod p ) . {\displaystyle q_{\text{inv}}=q^{-1}{\pmod {p}}.} These values allow the recipient to compute the exponentiation m = cd (mod pq) more efficiently as follows: m 1 = c d P ( mod p ) {\displaystyle m_{1}=c^{d_{P}}{\pmod {p}}} , m 2 = c d Q ( mod q ) {\displaystyle m_{2}=c^{d_{Q}}{\pmod {q}}} , h = q inv ( m 1 − m 2 ) ( mod p ) {\displaystyle h=q_{\text{inv}}(m_{1}-m_{2}){\pmod {p}}} , m = m 2 + h q {\displaystyle m=m_{2}+hq} . This is more efficient than computing exponentiation by squaring, even though two modular exponentiations have to be computed.
The reason is that these two modular exponentiations both use a smaller exponent and a smaller modulus. The security of the RSA cryptosystem is based on two mathematical problems: the problem of factoring large numbers and the RSA problem. Full decryption of an RSA ciphertext is thought to be infeasible on the assumption that both of these problems are hard, i.e., no efficient algorithm exists for solving them. Providing security against partial decryption may require the addition of a secure padding scheme. The RSA problem is defined as the task of taking eth roots modulo a composite n: recovering a value m such that c ≡ me (mod n), where (n, e) is an RSA public key, and c is an RSA ciphertext. Currently the most promising approach to solving the RSA problem is to factor the modulus n. With the ability to recover prime factors, an attacker can compute the secret exponent d from a public key (n, e), then decrypt c using the standard procedure. To accomplish this, an attacker factors n into p and q, and computes lcm(p − 1, q − 1) that allows the determination of d from e.
No polynomial-time method for factoring large integers on a classical computer has yet been found, but it has not been proven that none exists; see integer factorization for a discussion of this problem. The first RSA-512 factorization in 1999 used hundreds of computers and required the equivalent of 8,400 MIPS years, over an elapsed time of about seven months. By 2009, Benjamin Moody could factor a 512-bit RSA key in 73 days using only public software (GGNFS) and his desktop computer (a dual-core Athlon64 with a 1,900 MHz CPU). Just less than 5 gigabytes of disk storage was required and about 2.5 gigabytes of RAM for the sieving process. Rivest, Shamir, and Adleman noted that Miller has shown that – assuming the truth of the extended Riemann hypothesis – finding d from n and e is as hard as factoring n into p and q (up to a polynomial time difference). However, Rivest, Shamir, and Adleman noted, in section IX/D of their paper, that they had not found a proof that inverting RSA is as hard as factoring. As of 2020, the largest publicly known factored RSA number had 829 bits (250 decimal digits, RSA-250). Its factorization, by a state-of-the-art distributed implementation, took about 2,700 CPU-years. In practice, RSA keys are typically 1024 to 4096 bits long. In 2003, RSA Security estimated that 1024-bit keys were likely to become crackable by 2010. As of 2020, it is not known whether such keys can be cracked, but minimum recommendations have moved to at least 2048 bits. It is generally presumed that RSA is secure if n is sufficiently large, outside of quantum computing. If n is 300 bits or shorter, it can be factored in a few hours on a personal computer, using software already freely available. Keys of 512 bits have been shown to be practically breakable in 1999, when RSA-155 was factored by using several hundred computers, and these are now factored in a few weeks using common hardware. Exploits using 512-bit code-signing certificates that may have been factored were reported in 2011. A theoretical hardware device named TWIRL, described by Shamir and Tromer in 2003, called into question the security of 1024-bit keys. In 1994, Peter Shor showed that a quantum computer – if one could ever be practically created for the purpose – would be able to factor in polynomial time, breaking RSA; see Shor's algorithm.
Finding the large primes p and q is usually done by testing random numbers of the correct size with probabilistic primality tests that quickly eliminate virtually all of the nonprimes. The numbers p and q should not be "too close", lest the Fermat factorization for n be successful. If p − q is less than 2n1/4 (n = p⋅q, which even for "small" 1024-bit values of n is 3×1077), solving for p and q is trivial. Furthermore, if either p − 1 or q − 1 has only small prime factors, n can be factored quickly by Pollard's p − 1 algorithm, and hence such values of p or q should be discarded. It is important that the private exponent d be large enough. Michael J. Wiener showed that if p is between q and 2q (which is quite typical) and d < n1/4/3, then d can be computed efficiently from n and e. There is no known attack against small public exponents such as e = 3, provided that the proper padding is used. Coppersmith's attack has many applications in attacking RSA specifically if the public exponent e is small and if the encrypted message is short and not padded. 65537 is a commonly used value for e; this value can be regarded as a compromise between avoiding potential small-exponent attacks and still allowing efficient encryptions (or signature verification). The NIST Special Publication on Computer Security (SP 800-78 Rev. 1 of August 2007) does not allow public exponents e smaller than 65537, but does not state a reason for this restriction. In October 2017, a team of researchers from Masaryk University announced the ROCA vulnerability, which affects RSA keys generated by an algorithm embodied in a library from Infineon known as RSALib. A large number of smart cards and trusted platform modules (TPM) were shown to be affected. Vulnerable RSA keys are easily identified using a test program the team released.
Botan Bouncy Castle cryptlib Crypto++ Libgcrypt Nettle OpenSSL wolfCrypt GnuTLS mbed TLS LibreSSL Acoustic cryptanalysis Computational complexity theory Diffie–Hellman key exchange Digital Signature Algorithm Elliptic-curve cryptography Key exchange Key management Key size Public-key cryptography Rabin signature Semiprime Trapdoor function Tuta, formerly Tutanota, is an end-to-end encrypted email in addition to a calendar app and a freemium secure email service run by Tutao GmbH, a German company established in 2011. Tuta said there were over 10 million users of the product in June 2023.
Tutanota is derived from Latin and contains the words "tuta" and "nota" which means "secure message". Tutao GmbH was founded in 2011 in Hanover, Germany. Since 2014, the software has been open-sourced and can be reviewed by outsiders on GitHub. The software completed a phase in beta status in 2015. In August 2018, Tuta became the first email service provider to release their app on F-Droid, removing all dependence on proprietary code. This was part of a full remake of the app, which removed dependence on GCM for notifications by replacing it with SSE. The new app also enabled search, 2FA and got a new reworked user interface. The company announced a transition to 100% renewable electricity in March 2019.
This decision coincided with employee participation in Fridays for Future protests. In November 2020, the Cologne court ordered monitoring of a single Tuta account which had been used for an extortion attempt. The monitoring function should only apply to future unencrypted emails the account receives and it will not affect emails previously received. On 7 November 2023, Tutanota announced it had rebranded to simply 'Tuta'. The former domain name tutanota.com now redirects to the shorter tuta.com. In November 2023, it was alleged that Tuta was being used as a honeypot for criminals with a backdoor from authorities. An ex-RCMP officer, Cameron Ortis, testified that the service was used as a storefront to lure criminals in and gain information on those who fell for it. He stated authorities were monitoring the whole service, feeding it to Five Eyes, which would disperse it back to the RCMP in order to gain more knowledge about the criminal underground. However, no evidence was presented to back up this statement, and Tuta repudiated the claim. Tuta Mail has integrated post-quantum cryptography features through its protocol, TutaCrypt, replacing standard encryption methods like RSA-2048 and AES-256 for accounts created after March 2024. In October 2024, Tuta launched its standalone encrypted calendar app. In 2025 the company confirmed plans to launch a file storage application, known as Tuta Drive, although no release date has been given.
Tuta Drive entered closed beta in April 2026. Tuta as a European tech company is part of the trend for digital sovereignty. Elliptic Curve Key Pair: utilizes the X25519 curve for the Elliptic Curve Diffie-Hellman (ECDH) key exchange. Kyber-1024 Key Pair: implements post-quantum key encapsulation using the CRYSTALS-Kyber algorithm. TutaCrypt employs AES-256 in CBC mode alongside HMAC-SHA-256 for authenticated symmetric encryption. A transition to TutaCrypt for old existing user accounts created before March 2024 occurred in December 2024. Tuta also stated that it does not use PGP due to its limitations in encrypting subject lines and lack of flexibility for algorithm updates. S/MIME is also avoided due to critical vulnerabilities identified in 2018.
Transport Layer Security (TLS) is a cryptographic protocol designed to provide secured communications over a computer network, such as the Internet. The protocol is widely used in applications such as email, instant messaging, and voice over IP, but its use in securing HTTPS remains the most publicly visible. The TLS protocol aims primarily to provide security, including privacy (confidentiality), integrity, and authenticity through the use of cryptography, such as the use of certificates, between two or more communicating computer applications. It runs in the presentation layer and is itself composed of two layers: the TLS record and the TLS handshake protocols. The closely-related Datagram Transport Layer Security (DTLS) is a communications protocol that provides security to datagram-based applications. In technical writing, references to "(D)TLS" are often seen when it applies to both versions. TLS is a proposed Internet Engineering Task Force (IETF) standard, first defined in 1999, and the current version is TLS 1.3, defined in August 2018. TLS builds on the now-deprecated SSL (Secure Sockets Layer) specifications (1994, 1995, 1996) developed by Netscape Communications for adding the HTTPS protocol to their Netscape Navigator web browser.
The handshake begins when a client connects to a TLS-enabled server requesting a secure connection and the client presents a list of supported cipher suites (ciphers and hash functions). From this list, the server picks a cipher and hash function that it also supports and notifies the client of the decision. The server usually then provides identification in the form of a digital certificate. The certificate contains the server name, the trusted certificate authority (CA) that vouches for the authenticity of the certificate, and the server's public encryption key. The client confirms the validity of the certificate before proceeding. To generate the session keys used for the secure connection, the client either: encrypts a random number (PreMasterSecret) with the server's public key and sends the result to the server (which only the server should be able to decrypt with its private key); both parties then use the random number to generate a unique session key for subsequent encryption and decryption of data during the session, or uses Diffie–Hellman key exchange (or its variant elliptic-curve DH) to securely generate a random and unique session key for encryption and decryption that has the additional property of forward secrecy: if the server's private key is disclosed in the future, it cannot be used to decrypt the current session, even if the session is intercepted and recorded by a third party. This concludes the handshake and begins the secured connection, which is encrypted and decrypted with the session key until the connection closes. If any one of the above steps fails, then the TLS handshake fails and the connection is not created. Older versions of TLS and SSL allowed for establishing sessions via a PreMasterSecret using the server's public and private key. These algorithms were eliminated in TLS1.3 when it mandated forward secrecy. TLS and SSL do not fit neatly into any single layer of the OSI model or the TCP/IP model. TLS runs "on top of some reliable transport protocol (e.g., TCP)", which would imply that it is above the transport layer. It serves encryption to higher layers, which is normally the function of the presentation layer. However, applications generally use TLS as if it were a transport layer, even though applications using TLS must actively control initiating TLS handshakes and handling of exchanged authentication certificates. When secured by TLS, connections between a client (e.g., a web browser) and a server (e.g., wikipedia.org) will have all of the following properties: 5. Performance Evaluation & Extended Technical Observations The connection is private (or has confidentiality) because a symmetric-key algorithm is used to encrypt the data transmitted.
The keys for this symmetric encryption are generated uniquely for each connection and are based on a shared secret that was negotiated at the start of the session. The server and client negotiate the details of which encryption algorithm and cryptographic keys to use before the first byte of data is transmitted (see below). The negotiation of a shared secret is both secure (the negotiated secret is unavailable to eavesdroppers and cannot be obtained, even by an attacker who places themselves in the middle of the connection) and reliable (no attacker can modify the communications during the negotiation without being detected). The identity of the communicating parties can be authenticated using public-key cryptography. This authentication is required for the server and optional for the client. The connection is reliable (or has integrity) because each message transmitted includes a message integrity check using a message authentication code to prevent undetected loss or alteration of the data during transmission. TLS supports many different methods for exchanging keys, encrypting data, and authenticating message integrity. As a result, secure configuration of TLS involves many configurable parameters, and not all choices provide all of the privacy-related properties described in the list above (see the tables below § Key exchange, § Cipher security, and § Data integrity). Attempts have been made to subvert aspects of the communications security that TLS seeks to provide, and the protocol has been revised several times to address these security threats. Developers of web browsers have repeatedly revised their products to defend against potential security weaknesses after these were discovered (see TLS/SSL support history of web browsers).
In August 1986, the National Security Agency, the National Bureau of Standards, the Defense Communications Agency launched a project, called the Secure Data Network System (SDNS), with the intent of designing the next generation of secure computer communications network and product specifications to be implemented for applications on public and private internets. It was intended to complement the rapidly emerging new OSI internet standards moving forward both in the U.S.
government's GOSIP Profiles and in the huge ITU-ISO JTC1 internet effort internationally. As part of the project, researchers designed a protocol called SP4 (security protocol in layer 4 of the OSI system). This was later renamed the Transport Layer Security Protocol (TLSP) and subsequently published in 1995 as international standard ITU-T X.274|ISO/IEC 10736:1995. Despite the name similarity, this is distinct from today's TLS.
Netscape developed the original SSL protocols, and Taher Elgamal, chief scientist at Netscape Communications from 1995 to 1998, has been described as the "father of SSL". SSL version 1.0 was never publicly released because of serious security flaws in the protocol. Version 2.0, after being released in February 1995 was quickly found to contain a number of security and usability flaws. It used the same cryptographic keys for message authentication and encryption. It had a weak MAC construction that used the MD5 hash function with a secret prefix, making it vulnerable to length extension attacks. It also provided no protection for either the opening handshake or an explicit message close, both of which meant man-in-the-middle attacks could go undetected. Moreover, SSL 2.0 assumed a single service and a fixed domain certificate, conflicting with the widely used feature of virtual hosting in Web servers, so most websites were effectively impaired from using SSL. These flaws necessitated the complete redesign of the protocol to SSL version 3.0. Released in 1996, it was produced by Paul Kocher working with Netscape engineers Phil Karlton and Alan Freier, with a reference implementation by Christopher Allen and Tim Dierks of Certicom. Newer versions of SSL/TLS are based on SSL 3.0. The 1996 draft of SSL 3.0 was published by IETF as a historical document in RFC 6101. SSL 2.0 was deprecated in 2011 by RFC 6176. In 2014, SSL 3.0 was found to be vulnerable to the POODLE attack that affects all block ciphers in SSL; RC4, the only non-block cipher supported by SSL 3.0, is also feasibly broken as used in SSL 3.0. SSL 3.0 was deprecated in June 2015 by RFC 7568.
Added protection against cipher-block chaining (CBC) attacks. The implicit initialization vector (IV) was replaced with an explicit IV. Change in handling of padding errors. Support for IANA registration of parameters. Support for TLS versions 1.0 and 1.1 was widely deprecated by web sites around 2020, disabling access to Firefox versions before 24 and Chromium-based browsers before 29, though third-party fixes can be applied to Netscape Navigator and older versions of Firefox to add TLS 1.2 support.
The MD5 and SHA-1 combination in the pseudorandom function (PRF) was replaced with SHA-256, with an option to use cipher suite specified PRFs. The MD5 and SHA-1 combination in the finished message hash was replaced with SHA-256, with an option to use cipher suite specific hash algorithms. However, the size of the hash in the finished message must still be at least 96 bits. The MD5 and SHA-1 combination in the digitally signed element was replaced with a single hash negotiated during handshake, which defaults to SHA-1. Enhancement in the client's and server's ability to specify which hashes and signature algorithms they accept. Expansion of support for authenticated encryption ciphers, used mainly for Galois/Counter Mode (GCM) and CCM mode of Advanced Encryption Standard (AES) encryption. TLS Extensions definition and AES cipher suites were added. All TLS versions were further refined in RFC 6176 in March 2011, removing their backward compatibility with SSL such that TLS sessions never negotiate the use of Secure Sockets Layer (SSL) version 2.0. As of July 2026, there is no formal date for TLS 1.2 to be deprecated which allows for legacy clients. However the use of MD5 and SHA1 hash methods as well as Diffie-Hellman (DH) over a finite field and RSA key exchanges have been deprecated. (RFC 9155, 10015) Separating key agreement and authentication algorithms from the cipher suites Removing support for weak and less-used named elliptic curves Removing support for MD5 and SHA-224 cryptographic hash functions Requiring digital signatures even when a previous configuration is used Integrating HKDF and the semi-ephemeral DH proposal Replacing resumption with PSK and tickets Supporting 1-RTT handshakes and initial support for 0-RTT Mandating perfect forward secrecy, by means of using ephemeral keys during the (EC)DH key agreement Dropping support for many insecure or obsolete features including compression, renegotiation, non-AEAD ciphers, null ciphers, non-PFS key exchange (among which are static RSA and static DH key exchanges), custom DHE groups, EC point format negotiation, Change Cipher Spec protocol, Hello message UNIX time, and the length field AD input to AEAD ciphers Prohibiting SSL or RC4 negotiation for backwards compatibility Integrating use of session hash Deprecating use of the record layer version number and freezing the number for improved backwards compatibility Moving some security-related algorithm details from an appendix to the specification and relegating ClientKeyShare to an appendix Adding the ChaCha20 stream cipher with the Poly1305 message authentication code Adding the Ed25519 and Ed448 digital signature algorithms Adding the x25519 and x448 key exchange protocols Adding support for sending multiple OCSP responses Encrypting all handshake messages after the ServerHello, including server certificate Network Security Services (NSS), the cryptography library developed by Mozilla and used by its web browser Firefox, enabled TLS 1.3 by default in February 2017. TLS 1.3 support was subsequently added — but due to compatibility issues for a small number of users, not automatically enabled — to Firefox 52.0, which was released in March 2017. TLS 1.3 was enabled by default in May 2018 with the release of Firefox 60.0. Google Chrome set TLS 1.3 as the default version for a short time in 2017. It then removed it as the default, due to incompatible middleboxes such as Blue Coat web proxies. The intolerance of the new version of TLS was protocol ossification; middleboxes had ossified the protocol's version parameter. As a result, version 1.3 mimics the wire image of version 1.2. This change occurred very late in the design process, only having been discovered during browser deployment. The discovery of this intolerance also led to the prior version negotiation strategy, where the highest matching version was picked, being abandoned due to unworkable levels of ossification. 'Greasing' an extension point, where one protocol participant claims support for non-existent extensions to ensure that unrecognised-but-actually-existent extensions are tolerated and so to resist ossification, was originally designed for TLS, but it has since been adopted elsewhere. During the IETF 100 Hackathon, which took place in Singapore in 2017, the TLS Group worked on adapting open-source applications to use TLS 1.3. The TLS group was made up of individuals from Japan, United Kingdom, and Mauritius via the cyberstorm.mu team. This work was continued in the IETF 101 Hackathon in London, and the IETF 102 Hackathon in Montreal. wolfSSL enabled the use of TLS 1.3 as of version 3.11.1, released in May 2017. As the first commercial TLS 1.3 implementation, wolfSSL 3.11.1 supported Draft 18 and now supports Draft 28, the final version, as well as many older versions. A series of blogs were published on the performance difference between TLS 1.2 and 1.3. In September 2018, the popular OpenSSL project released version 1.1.1 of its library, in which support for TLS 1.3 was "the headline new feature". Support for TLS 1.3 was added to Secure Channel (schannel) for the GA releases of Windows 11 and Windows Server 2022.
A digital certificate certifies the ownership of a public key by the named subject of the certificate, and indicates certain expected usages of that key. This allows others (relying parties) to rely upon signatures or on assertions made by the private key that corresponds to the certified public key. Keystores and trust stores can be in various formats, such as .pem, .crt, .pfx/.p12 and .jks.
TLS typically relies on a set of trusted third-party certificate authorities to establish the authenticity of certificates. Trust is usually anchored in a list of certificates distributed with user agent software, and can be modified by the relying party. According to Netcraft, who monitors active TLS certificates, the market-leading certificate authority (CA) has been Symantec since the beginning of their survey (or VeriSign before the authentication services business unit was purchased by Symantec).
As of 2015, Symantec accounted for just under a third of all certificates and 44% of the valid certificates used by the 1 million busiest websites, as counted by Netcraft. In 2017, Symantec sold its TLS/SSL business to DigiCert. In an updated report, it was shown that IdenTrust, DigiCert, and Sectigo are the top 3 certificate authorities in terms of market share since May 2019. As a consequence of choosing X.509 certificates, certificate authorities and a public key infrastructure are necessary to verify the relation between a certificate and its owner, as well as to generate, sign, and administer the validity of certificates. While this can be more convenient than verifying the identities via a web of trust, the 2013 mass surveillance disclosures made it more widely known that certificate authorities are a weak point from a security standpoint, allowing man-in-the-middle attacks (MITM) if the certificate authority cooperates (or is compromised). On April 11, 2025, the CA/Browser Forum approved a ballot that will require all public TLS certificate lifespans to gradually reduce to 47 days by 2029. The ballot was proposed by Apple.
As of March 2025, the latest versions of all major web browsers support TLS 1.2 and 1.3 and have them enabled by default, with the exception of IE 11. TLS 1.0 and 1.1 are disabled by default on the latest versions of all major browsers. Mitigations against known attacks are not enough yet: Mitigations against POODLE attack: some browsers already prevent fallback to SSL 3.0; however, this mitigation needs to be supported by not only clients but also servers. Disabling SSL 3.0 itself, implementation of "anti-POODLE record splitting", or denying CBC ciphers in SSL 3.0 is required. Google Chrome: complete (TLS_FALLBACK_SCSV is implemented since version 33, fallback to SSL 3.0 is disabled since version 39, SSL 3.0 itself is disabled by default since version 40. Support of SSL 3.0 itself was dropped since version 44.) Mozilla Firefox: complete (support of SSL 3.0 itself is dropped since version 39.
SSL 3.0 itself is disabled by default and fallback to SSL 3.0 are disabled since version 34, TLS_FALLBACK_SCSV is implemented since version 35. In ESR, SSL 3.0 itself is disabled by default and TLS_FALLBACK_SCSV is implemented since ESR 31.3.0.) Internet Explorer: partial (only in version 11, SSL 3.0 is disabled by default since April 2015. Version 10 and older are still vulnerable against POODLE.) Opera: complete (TLS_FALLBACK_SCSV is implemented since version 20, "anti-POODLE record splitting", which is effective only with client-side implementation, is implemented since version 25, SSL 3.0 itself is disabled by default since version 27. Support of SSL 3.0 itself will be dropped since version 31.) Safari: complete (only on OS X 10.8 and later and iOS 8, CBC ciphers during fallback to SSL 3.0 is denied, but this means it will use RC4, which is not recommended as well. Support of SSL 3.0 itself is dropped on OS X 10.11 and later and iOS 9.) Mitigation against RC4 attacks: Google Chrome disabled RC4 except as a fallback since version 43. RC4 is disabled since Chrome 48.
Firefox disabled RC4 except as a fallback since version 36. Firefox 44 disabled RC4 by default. Opera disabled RC4 except as a fallback since version 30. RC4 is disabled since Opera 35. Internet Explorer for Windows 7/Server 2008 R2 and for Windows 8/Server 2012 have set the priority of RC4 to lowest and can also disable RC4 except as a fallback through registry settings. Internet Explorer 11 Mobile 11 for Windows Phone 8.1 disable RC4 except as a fallback if no other enabled algorithm works. Edge [Legacy] and IE 11 disable RC4 completely in August 2016. Mitigation against FREAK attack: The Android Browser included with Android 4.0 and older is still vulnerable to the FREAK attack. Internet Explorer 11 Mobile is still vulnerable to the FREAK attack. Google Chrome, Internet Explorer (desktop), Safari (desktop & mobile), and Opera (mobile) have FREAK mitigations in place. Mozilla Firefox on all platforms and Google Chrome on Windows were not affected by FREAK.
BoringSSL, a fork of OpenSSL for Chrome/Chromium and Android as well as other Google applications. Botan, a BSD-licensed cryptographic library written in C++. BSAFE Micro Edition Suite: a multi-platform implementation of TLS written in C using a FIPS-validated cryptographic module BSAFE SSL-J: a TLS library providing both a proprietary API and JSSE API, using FIPS-validated cryptographic module cryptlib: a portable open source cryptography library (includes TLS/SSL implementation) Delphi programmers may use a library called Indy which utilizes OpenSSL or alternatively ICS which supports TLS 1.3 now. GnuTLS: a free implementation (LGPL licensed) Java Secure Socket Extension (JSSE): the Java API and provider implementation (named SunJSSE) LibreSSL: a fork of OpenSSL by OpenBSD project. MatrixSSL: a dual licensed implementation Mbed TLS (previously PolarSSL): A tiny SSL library implementation for embedded devices that is designed for ease of use Network Security Services: FIPS 140 validated open source library OpenSSL: a free implementation (BSD license with some extensions) Rustls, An implementation of TLS 1.3 written in the Rust programming language to ensure memory safety. Schannel: an implementation of SSL and TLS Microsoft Windows as part of its package. Secure Transport: an implementation of SSL and TLS used in OS X and iOS as part of their packages. wolfSSL (previously CyaSSL): Embedded SSL/TLS Library with a strong focus on speed and size. A paper presented at the 2012 ACM conference on computer and communications security showed that many applications used some of these SSL libraries incorrectly, leading to vulnerabilities. According to the authors: "The root cause of most of these vulnerabilities is the terrible design of the APIs to the underlying SSL libraries. Instead of expressing high-level security properties of network tunnels such as confidentiality and authentication, these APIs expose low-level details of the SSL protocol to application developers. As a consequence, developers often use SSL APIs incorrectly, misinterpreting and misunderstanding their manifold parameters, options, side effects, and return values." A protocol downgrade attack (also called a version rollback attack) tricks a web server into negotiating connections with previous versions of TLS (such as SSLv2) that have long since been abandoned as insecure. Previous modifications to the original protocols, like False Start (adopted and enabled by Google Chrome) or Snap Start, reportedly introduced limited TLS protocol downgrade attacks or allowed modifications to the cipher suite list sent by the client to the server. In doing so, an attacker might succeed in influencing the cipher suite selection in an attempt to downgrade the cipher suite negotiated to use either a weaker symmetric encryption algorithm or a weaker key exchange. A paper presented at an ACM conference on computer and communications security in 2012 demonstrated that the False Start extension was at risk: in certain circumstances it could allow an attacker to recover the encryption keys offline and to access the encrypted data. Encryption downgrade attacks can force servers and clients to negotiate a connection using cryptographically weak keys. In 2014, a man-in-the-middle attack called FREAK was discovered affecting the OpenSSL stack, the default Android web browser, and some Safari browsers. The attack involved tricking servers into negotiating a TLS connection using cryptographically weak 512 bit encryption keys. Logjam is a security exploit discovered in May 2015 that exploits the option of using legacy "export-grade" 512-bit Diffie–Hellman groups dating back to the 1990s. It forces susceptible servers to downgrade to cryptographically weak 512-bit Diffie–Hellman groups. An attacker can then deduce the keys the client and server determine using the Diffie–Hellman key exchange.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/RSA%20cryptosystem • https://en.wikipedia.org/wiki/Tuta%20%28email%29 • https://en.wikipedia.org/wiki/Transport%20Layer%20Security
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Secure File Storage Using RSA And AES Hybrid Encryption.
[*] Metasploit Scan Running on Target Subnet for Secure File Storage Using RSA And AES Hybrid Encryption... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |