Complete Technical Paper Content — Secure Firmware Update Mechanism For Embedded Devices
Overview & System Context
Secure Firmware Update Mechanism For Embedded Devices: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9939 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Unified Extensible Firmware Interface or UEFI is a specification for the firmware architecture of a computing platform. When a computer is powered on, the UEFI implementation typically runs first, before the operating system or any other program is loaded. Examples include AMI Aptio, Phoenix SecureCore, TianoCore EDK II, and InsydeH2O. UEFI replaces the BIOS that was present in the boot ROM of all personal computers that are IBM PC compatible, although it can provide backwards compatibility with the BIOS using CSM booting. Unlike the BIOS, which was originally developed by IBM as a proprietary architecture, the UEFI specification is managed by an industry consortium. Most production firmware implementations for both remain proprietary. Intel developed the original Extensible Firmware Interface (EFI) specification. The last Intel version of EFI was 1.10 released in 2005. Subsequent versions have been developed as UEFI by the UEFI Forum. UEFI is independent of platform and programming language, but C is used for the reference implementation TianoCore EDKII.
x86 (IA-32, x86-64) Itanium (IA-64) ARM (AArch32, AArch64) RISC-V (32-bit, 64-bit, 128-bit) LoongArch (32-bit, 64-bit) Unofficial UEFI support is under development for POWERPC64 by implementing TianoCore EDK II on top of OPAL, the OpenPOWER abstraction layer, running in little-endian mode. For MIPS, there also exists an unofficial project, based on the original EDK. However, both projects have since been abandoned as of November 2016 and September 2015 respectively.
UEFI only allows executing UEFI applications that match the firmware's bit-width, even if the processor supports smaller or larger bit-widths. For example, a 64-bit UEFI firmware may only execute 64-bit UEFI applications, even if the processor has a 32-bit processor mode. Some low-end computers have been shipped with 32-bit UEFI firmware running on 64-bit CPUs. Once a UEFI application ends the boot services, and gets granted full control over the system, it becomes possible to change the processor execution mode. However, calling runtime services requires shortly changing back to the original processor mode, as runtime services may only be called from the same processor mode as the firmware implementation. The Linux kernel added support for booting 64-bit kernels on 32-bit UEFI firmware implementations with x86-64 CPUs since version 3.15, requiring the UEFI boot loader to support the EFI handover protocol. The EFI handover protocol allows UEFI boot loaders to defer the UEFI initialization to the kernel's EFI boot stub, so that only the kernel does the UEFI initialization.
In addition to the standard PC disk partition scheme that uses a master boot record (MBR), UEFI also works with the GUID Partition Table (GPT) partitioning scheme, which is free from many of the limitations of MBR. In particular, the MBR limits on the number and size of disk partitions (up to four primary partitions per disk, and up to 2 TB (2 × 240 bytes) per disk) are relaxed. More specifically, GPT allows for a maximum disk and partition size of 8 ZiB (8 × 270 bytes) with 512 byte sectors.
The UEFI specification only supports FAT12/16/32 partitions that are on GPT or MBR disks as well as El Torito-formatted optical discs. Although GPT is a part of the UEFI standard, it may also be usable by BIOS PCs to boot an operating system off of. Support for GPT in Linux is enabled by turning on the option CONFIG_EFI_PARTITION (EFI GUID Partition Support) during kernel configuration. This option allows Linux to recognize and use GPT disks after the system firmware passes control over the system to Linux. For reverse compatibility, Linux can use GPT disks in BIOS-based systems for both data storage and booting, as both GRUB 2 and Linux are GPT-aware. Such a setup is usually referred to as BIOS-GPT. As GPT incorporates the protective MBR, a BIOS-based computer can boot from a GPT disk using a GPT-aware boot loader stored in the protective MBR's bootstrap code area. In the case of GRUB, such a configuration requires a BIOS boot partition for GRUB to embed its second-stage code due to absence of the post-MBR gap in GPT partitioned disks (which is taken over by the GPT's Primary Header and Primary Partition Table). Commonly 1 MB in size, this partition's Globally Unique Identifier (GUID) in GPT scheme is 21686148-6449-6E6F-744E-656564454649 and is used by GRUB only in BIOS-GPT setups. From GRUB's perspective, no such partition type exists in case of MBR partitioning. This partition is not required if the system is UEFI-based because no embedding of the second-stage code is needed in that case. UEFI systems can access GPT disks and boot directly from them, which allows Linux to use UEFI boot methods. Booting Linux from GPT disks on UEFI systems involves creation of an EFI system partition (ESP), which contains UEFI applications such as bootloaders, operating system kernels, and utility software. Such a setup is usually referred to as UEFI-GPT, while ESP is recommended to be at least 512 MB in size and formatted with a FAT32 filesystem for maximum compatibility. For backward compatibility, some UEFI implementations also support booting from MBR-partitioned disks through the Compatibility Support Module (CSM) that provides legacy BIOS compatibility. In that case, booting Linux on UEFI systems is the same as on legacy BIOS-based systems.
Figure 1: Autumn Foliage Wallpapers - Top Free Autumn Foliage Backgrounds ... Graphics Output Protocol (GOP) services The Graphics Output Protocol (GOP) provides runtime services; see also Graphics features section below. The operating system is permitted to directly write to the framebuffer and BLT provided by GOP during runtime mode. UEFI memory map services This boot service allows the bootloader to obtain information on how the memory is laid out. SMM services The SMM ("ring -2") is an x86 mode that provides secure code execution isolated from all lower rings. Modern UEFI generalizes the concept to Management Mode (MM) to also encompass alternative technologoies such as TrustZone. One common use of the MM/SMM services is as a secure store of variables. ACPI services SMBIOS services Devicetree services (for RISC processors) These runtime services allow the operating system to obtain information about the installed hardware and how to make use of them. Variable services UEFI variables store non-volatile data. The variable storage is conceptually divided into namespaces identified by GUIDs. Each namespace can contain any number of variable entries, which are key/value pairs (Unicode string key, variable-length byte-array value). Each entry also carries an attributes bitfield, which can restrict its access to only boot or run-time (among other, more advanced, uses). Some UEFI variables are shared between platform firmware and operating systems. For example, the OS may set the BootOrder and Boot#### variables under the EFI_GLOBAL_VARIABLE namespace to influence the UEFI boot manager's future choices. Other variables may be private to one side. For example, UEFI variables can be used by an OS to keep crash messages in NVRAM after a crash for the operating system to retrieve after a reboot. Time services UEFI provides time services. Time services include support for time zone and daylight saving fields, which allow the hardware real-time clock to be set to local time or UTC. On machines using a PC-AT real-time clock, Microsoft Windows does not use the EFI time zone and DST fields, and expects the hardware clock to provide local time like traditional BIOS-based Windows did. As a result the HW clock cannot be set to UTC unless using recent versions and an entry in the Windows registry is set to indicate the use of UTC.
UEFI executes independent programs known as UEFI applications, which are stored as files on the EFI system partition. These can be launched by the firmware boot manager or other UEFI applications. They may be developed independently of the original equipment manufacturer (OEM). A type of UEFI application is an OS boot loader such as GRUB, rEFInd, systemd-boot, and Windows Boot Manager, which loads some OS files into memory and executes them. The UEFI Shell is an example of a UEFI application that launches other UEFI applications. Some OS loaders do the same, providing a user interface to allow the selection of another UEFI application to run.
An EFI system partition, often abbreviated to ESP, is a data storage device partition that is used in computers adhering to the UEFI specification. Accessed by the UEFI firmware when a computer is powered up, it stores UEFI applications and the files these applications need to run, including operating system boot loaders. Supported partition table schemes include MBR and GPT, as well as El Torito volumes on optical discs. For use on ESPs, UEFI defines a specific version of the FAT file system, which is maintained as part of the UEFI specification and independently from the original FAT specification, encompassing the FAT32, FAT16 and FAT12 file systems. The ESP retains the BIOS-style boot sector from FAT, though this is not used by UEFI.
Booting UEFI systems from GPT-partitioned disks is commonly called UEFI-GPT booting. The alternative is to boot from an EFI System Partition on MBR-partitioned disks, commonly called UEFI-MBR. UEFI-MBR capability is required by the UEFI specification, but some UEFI firmware implementations immediately switch to BIOS-based CSM booting depending on the type of the boot disk's partition table, effectively preventing it from occurring. It is also common for a boot manager to have a textual user interface to allow the user to select the desired OS (or setup utility) from a list of available boot options. On PC platforms, firmware supporting UEFI boot is often referred to as a "UEFI BIOS", though some newer x86 platforms exclude CSM support entirely.
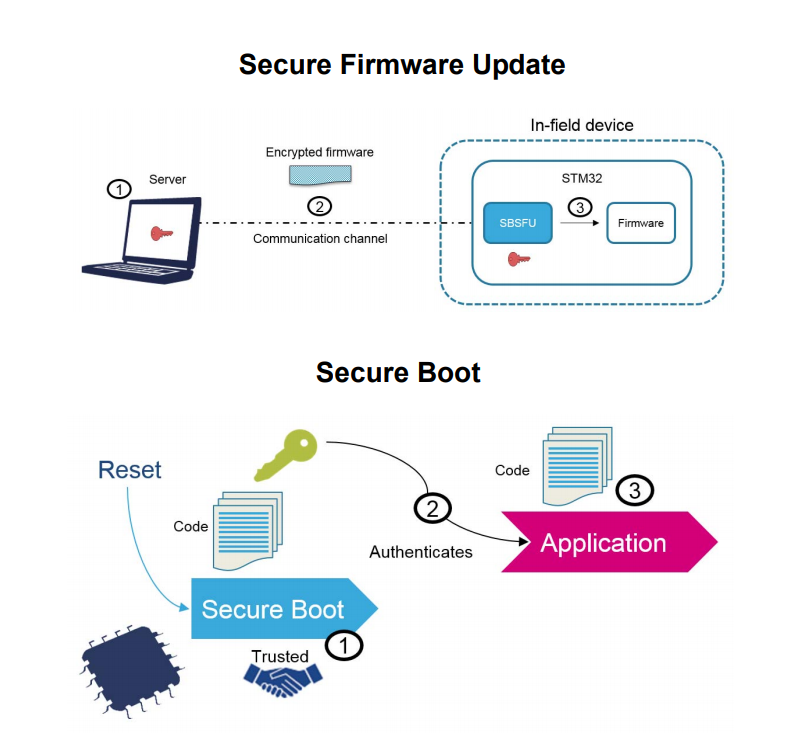
Figure 2: Secure Firmware Update. IIIIIIIII IIIIIIII STMicroelectronics… | by ... The UEFI specification defines a Secure Boot that can secure the boot process by preventing the loading of UEFI drivers or OS boot loaders that are not signed with an acceptable digital signature. When Secure Boot is enabled, it is initially placed in "setup" mode, which allows a public key known as the "platform key" (PK) to be written to the firmware. Once the key is written, Secure Boot enters "User" mode, where only UEFI drivers and OS boot loaders signed with the platform key can be loaded by the firmware. Additional "key exchange keys" (KEK) can be added to a database stored in memory to allow other certificates to be used, but they must still have a connection to the private portion of the platform key. Secure Boot can also be placed in "Custom" mode, where additional public keys can be added to the system that do not match the private key. Secure Boot is supported by Windows 8 and 8.1, Windows Server 2012 and 2012 R2, Windows 10, Windows Server 2016, 2019, and 2022, and Windows 11, VMware vSphere 6.5 and several Linux distributions including Fedora (since version 18), openSUSE (since version 12.3), RHEL (since version 7), CentOS (since version 7), Debian (since version 10), Ubuntu (since version 12.04.2), Linux Mint (since version 21.3), and AlmaLinux OS (since version 8.4). As of January 2025, FreeBSD support is in its planning stage.
The UEFI standards include a specification for a shell environment. The shell is a UEFI application that can be used to execute other UEFI applications, including UEFI boot loaders. It also includes built-in commands for obtaining various other information about the system or the firmware, including getting the memory map (memmap), modifying boot manager variables (bcfg), running partitioning programs (diskpart), loading UEFI drivers, and editing text files (edit). It implements a scripting language with support for if-statements, for-loops, and environment variables. The UEFI shell is not a mandatory component of the firmware. It tends to be pre-loaded into server motherboards, which allows it to be launched by appropriate key press combinations. Some other motherboards provide a direct option in firmware setup for launching, e.g. compiled x86-64 version of the shell needs to be made available as
2. System Architecture & Core Working Principles The shell v2 includes a much broader set of features in its default build. For example, there is a new devtree for showing a tree of devices. Class 0: Legacy BIOS Class 1: UEFI with a CSM interface and no external UEFI interface. The only UEFI interfaces are internal to the firmware. Class 2: UEFI with CSM and external UEFI interfaces, e.g. UEFI Boot. Class 3: UEFI without a CSM interface and with an external UEFI interface. Class 3+: UEFI class 3 that has Secure Boot enabled. Starting from the 10th Gen Intel Core, Intel no longer provides Legacy Video BIOS for the iGPU (Intel Graphics Technology). Legacy boot with those CPUs requires a Legacy Video BIOS, which can still be provided by a video card.
Successful dispatching of PEIMs (pre-EFI initialization modules). Initializing permanent memory (RAM). Handing over to the next stage, DXE. Facilitating the communication of PEIMs called PPI. Intel's implementation of EFI is the Intel Platform Innovation Framework, codenamed Tiano. Tiano runs on Intel's XScale, Itanium, IA-32 and x86-64 processors, and is proprietary software, although a portion of the code has been released under the BSD license or Eclipse Public License (EPL) as TianoCore EDK II. TianoCore can be used as a payload for coreboot. Phoenix Technologies' implementation of UEFI is branded as SecureCore Technology (SCT). American Megatrends offers its own UEFI firmware implementation known as Aptio, while Insyde Software offers InsydeH2O, and Byosoft offers ByoCore. In December 2018, Microsoft released an open source version of its TianoCore EDK2-based UEFI implementation from the Surface line, Project Mu. An implementation of the UEFI API was introduced into the Universal Boot Loader (Das U-Boot) in 2017. On the ARMv8 architecture Linux distributions use the U-Boot UEFI implementation in conjunction with GNU GRUB for booting (e.g. SUSE Linux), the same holds true for OpenBSD. For booting from iSCSI iPXE can be used as a UEFI application loaded by U-Boot.
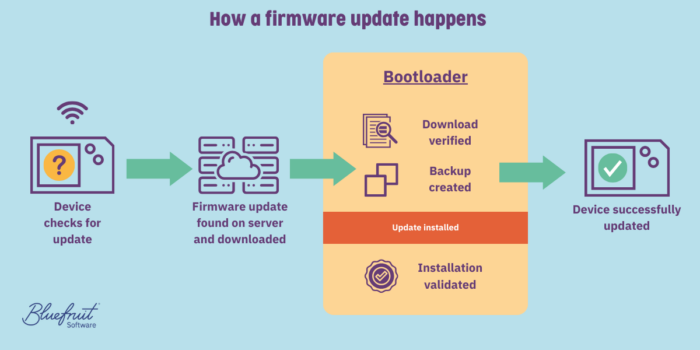
Figure 3: What is an embedded bootloader? - Bluefruit Software Intel's first Itanium workstations and servers, released in 2000, implemented EFI 1.02. Hewlett-Packard's first Itanium 2 systems, released in 2002, implemented EFI 1.10. These systems were able to boot Windows, Linux, FreeBSD and HP-UX. OpenVMS added UEFI capability in June 2003. In January 2006, Apple Inc. shipped its first Intel-based Macintosh computers.
These systems used EFI instead of Open Firmware, which had been used on its previous PowerPC-based systems. On 5 April 2006, Apple first released Boot Camp, which produces a Windows drivers disk and a non-destructive partitioning tool to allow the installation of Windows XP or Vista without requiring a reinstallation of Mac OS X (now macOS). A firmware update was also released that added BIOS compatibility to its EFI implementation. Subsequent Macintosh models shipped with the newer firmware. During 2005, more than one million Intel systems shipped with Intel's implementation of UEFI. New mobile, desktop and server products, using Intel's implementation of UEFI, started shipping in 2006. For instance, boards that use the Intel 945 chipset series use Intel's UEFI firmware implementation. Since 2005, EFI has also been implemented on non-PC architectures, such as embedded systems based on XScale cores. The EDK (EFI Developer Kit) includes an NT32 target, which allows EFI firmware and EFI applications to run within a Windows application. However, no direct hardware access is allowed by EDK NT32. This means only a subset of EFI application and drivers can be executed by the EDK NT32 target. In 2008, more x86-64 systems adopted UEFI. While many of these systems still allow booting only the BIOS-based OSes via the Compatibility Support Module (CSM) (thus not appearing to the user to be UEFI-based), other systems started to allow booting UEFI-based OSes. For example, IBM x3450 server, MSI motherboards with ClickBIOS and HP EliteBook Notebook PCs. In 2009, IBM shipped System x machines (x3550 M2, x3650 M2, iDataPlex dx360 M2) and BladeCenter HS22 with UEFI capability. Dell shipped PowerEdge T610, R610, R710, M610 and M710 servers with UEFI capability. More commercially available systems are mentioned in a UEFI whitepaper. In 2011, major vendors (such as ASRock, Asus, Gigabyte, and MSI) launched several consumer-oriented motherboards using the Intel 6-series LGA 1155 chipset and AMD 9 Series AM3+ chipsets with UEFI. With the release of Windows 8 in October 2012, Microsoft's certification requirements now require that computers include firmware that implements the UEFI specification. Furthermore, if the computer supports the "Connected Standby" feature of Windows 8 (which allows devices to have power management comparable to smartphones, with an almost instantaneous return from standby mode), then the firmware is not permitted to contain a Compatibility Support Module (CSM). As such, systems that support Connected Standby are incapable of booting Legacy BIOS operating systems. In October 2017, Intel announced that it would remove legacy PC BIOS support from all its products by 2020, in favor of UEFI Class 3. By 2019, all computers based on Intel platforms no longer have legacy PC BIOS support.
The Linux kernel has been able to use EFI at boot time since the early 2000s, using the elilo EFI boot loader and more recently, EFI versions of GRUB or systemd-boot. Grub+Linux also supports booting from a GUID partition table without UEFI. The distribution Ubuntu added support for UEFI Secure Boot as of version 12.10. The Linux kernel can be compiled with the option to run as an EFI bootloader on its own through the EFI boot stub feature. In the Linux kernel, either the ACPI protocol (usually used on PC-compatible machines) or the DeviceTree protocol (usually used on smartphones and tablet computers) can be used with UEFI. HP-UX has used (U)EFI as its boot mechanism on IA-64 systems since 2002. OpenVMS has used EFI on IA-64 since its initial evaluation release in December 2003, and for production releases since January 2005. OpenVMS on x86-64 also uses UEFI to boot the operating system. Apple uses EFI for its line of Intel-based Macs. Mac OS X v10.4 Tiger and Mac OS X v10.5 Leopard implements EFI v1.10 in 32-bit mode even on 64-bit CPUs, but full support arrived with OS X v10.8 Mountain Lion. Windows XP 64-bit Edition and Windows Server 2003 for IA-64, all of which are for the Intel Itanium family of processors, implement EFI, a requirement of the platform through the DIG64 specification. The pre-release versions of Windows Server 2003 for 64-bit Itanium systems (Windows Advanced Server Limited Edition and Windows Datacenter Server Limited Edition, which were labeled as 64-bit versions of Windows 2000 for the time being) implemented EFI 1.10 in 2002. Microsoft introduced UEFI for x86-64 Windows operating systems beginning with Windows Vista SP1 and Windows Server 2008, however only UGA (Universal Graphic Adapter) 1.1 or Legacy BIOS INT 10h is supported; Graphics Output Protocol (GOP) is not supported. Therefore, PCs running 64-bit versions of Windows Vista SP1 and SP2, Windows 7, Windows Server 2008 and Windows Server 2008 R2 are compatible with UEFI Class 2. 32-bit UEFI was originally not supported since vendors did not have any interest in producing native 32-bit UEFI firmware because of the mainstream status of 64-bit computing. Windows 8 finally introduced further optimizations for UEFI systems, including Graphics Output Protocol (GOP) support, a faster startup, 32-bit UEFI support, and Secure Boot support. Since Windows 8, the UEFI firmware with ACPI protocol is a mandatory requirement for ARM-based Microsoft Windows operating systems. Microsoft began requiring UEFI to run Windows starting with Windows 11, with the exception of IoT Enterprise editions of Windows 11 since version 24H2. On 5 March 2013, the FreeBSD Foundation awarded a grant to a developer seeking to add UEFI support to the FreeBSD kernel and bootloader. The changes were initially stored in a discrete branch of the FreeBSD source code, but were merged into the mainline source on 4 April 2014 (revision 264095); the changes include support in the installer as well. UEFI boot support for amd64 first appeared in FreeBSD 10.1 and for arm64 in FreeBSD 11.0. NetBSD supports UEFI since version 8.0 for i386 and amd64 architectures as well as on various ARM platforms since version 9.0. Oracle Solaris 11.1 and later support UEFI boot for x86 systems with UEFI firmware version 2.1 or later. GRUB 2 is used as the boot loader on x86.
OpenBSD 5.9 introduced UEFI boot support for 64-bit x86 systems using its own custom loader, OpenBSD 6.0 extended that support to include ARMv7. illumos added basic UEFI support in October 2017. ArcaOS supports UEFI booting since the 5.1 release. ArcaOS' UEFI support emulates specific BIOS functionality which the operating system depends on (particularly interrupts INT 10H and INT 13H).
In 2011, Microsoft announced that computers certified to run its Windows 8 operating system had to ship with Microsoft's public key enrolled and Secure Boot enabled, which implies that using UEFI is a requirement for these devices. Following the announcement, critics and free-software/open-source advocates, including the Free Software Foundation, expressed concern that Microsoft might use the Secure Boot functionality of UEFI to restrict the installation of alternative operating systems such as Linux. Microsoft denied that the Secure Boot requirement was intended to serve as a form of lock-in and clarified its requirements by stating that x86-based systems certified for Windows 8 must allow Secure Boot to enter custom mode or be disabled, but not on systems using the ARM architecture. Windows 10 allows OEMs to decide whether or not Secure Boot can be managed by users of their x86 systems. Other developers raised concerns about the legal and practical issues of implementing support for Secure Boot on Linux systems in general. Former Red Hat developer Matthew Garrett noted that conditions in the GNU General Public License version 3 may prevent the use of the GNU GRand Unified Bootloader without a distribution's developer disclosing the private key (however, the Free Software Foundation has since clarified its position, assuring that the responsibility to make keys available was held by the hardware manufacturer), and that it would also be difficult for advanced users to build custom kernels that could function with Secure Boot enabled without self-signing them.
Other developers suggested that signed builds of Linux with another key could be provided, but noted that it would be difficult to persuade OEMs to ship their computers with the required key alongside the Microsoft key. Several major Linux distributions have developed different implementations for Secure Boot. Garrett himself developed a minimal bootloader known as a shim, which is a precompiled, signed bootloader that allows the user to individually trust keys provided by Linux distributions. Ubuntu 12.10 uses an older version of shim pre-configured for use with Canonical's own key that verifies only the bootloader and allows unsigned kernels to be loaded; developers believed that the practice of signing only the bootloader is more feasible, since a trusted kernel is effective at securing only the user space, and not the pre-boot state for which Secure Boot is designed to add protection. That also allows users to build their own kernels and use custom kernel modules as well, without the need to reconfigure the system. Canonical also maintains its own private key to sign installations of Ubuntu pre-loaded on certified OEM computers that run the operating system, and also plans to enforce a Secure Boot requirement as well—requiring both a Canonical key and a Microsoft key (for compatibility reasons) to be included in their firmware. Fedora also uses shim, but requires that both the kernel and its modules be signed as well. shim has Machine Owner Key (MOK) that can be used to sign locally compiled kernels and other software not signed by distribution maintainer, without changing the Secure Boot mode to setup mode. It has been disputed whether the operating-system kernel and its modules must be signed as well; while the UEFI specifications do not require it, Microsoft has asserted that their contractual requirements do, and that it reserves the right to revoke any certificates used to sign code that can be used to compromise the security of the system. In Windows, if Secure Boot is enabled, all kernel drivers must be digitally signed; non-WHQL drivers may be refused to load. In February 2013, another Red Hat developer attempted to submit a patch to the Linux kernel that would allow it to parse Microsoft's authenticode signing using a master X.509 key embedded in PE files signed by Microsoft. However, the proposal was criticized by Linux creator Linus Torvalds, who argued that Red Hat was accommodating Microsoft's control over the Secure Boot infrastructure. On 26 March 2013, the Spanish free-software development group Hispalinux filed a formal complaint with the European Commission, contending that Microsoft's Secure Boot requirements on OEM systems were "obstructive" and anti-competitive. At the Black Hat conference in August 2013, a group of security researchers presented a series of exploits in specific vendor implementations of UEFI that could be used to exploit Secure Boot. In August 2016 it was reported that two security researchers had found the "golden key" security key Microsoft uses in signing operating systems. Technically, no key was exposed, but an exploitable binary signed by the key was. This allows software to execute as though it were signed by Microsoft, presenting potential risks for rootkit and bootkit attacks. This also complicates remediation efforts, since a patch can potentially be downgraded by replacing it with the signed exploitable binary. Microsoft stated that the vulnerability only affects ARM architecture and Windows RT devices and released two updates; however, reports noted that these updates do not completely prevent exploitation because fully resolving the vulnerability would require key replacements in end-user firmware. On 1 March 2023, researchers from ESET reported discovering "BlackLotus", described as the first active UEFI bootkit capable of bypassing UEFI Secure Boot by exploiting the limitations of the previous security updates.
In August 2024, the Windows 11 and Windows 10 security updates applied the Secure Boot Advanced Targeting (SBAT) settings to device's UEFI NVRAM, which caused some Linux distributions to fail to load. SBAT is a protocol that supported in new versions of Windows Boot Manager and shim, which refuse buggy or vulnerable intermediate bootloaders (usually older versions of Windows Boot Manager and GRUB) to load in the boot process. The change was reverted the next month. In June 2025, LWN.net reported that the Microsoft UEFI CA 2011 certificate will be expired on June 24, 2026, which may refuse some Linux to load if Secure Boot is enabled. However, in TianoCore EDK II as well as many commercial UEFI implementations (such as AMI Aptio), time/date check for Secure Boot certificate is usually disabled by default. Many Linux distributions support UEFI Secure Boot as of January 2025, such as RHEL (RHEL 7 and later), CentOS (CentOS 7 and later), Ubuntu, Fedora, Debian (Debian 10 and later), OpenSUSE, and SUSE Linux Enterprise.
Official website UEFI Specifications Intel-sponsored open-source EFI Framework initiative Intel EFI/UEFI portal Microsoft UEFI Support and Requirements for Windows Operating Systems How Windows 8 Hybrid Shutdown / Fast Boot feature works Securing the Windows 10 Boot Process LoJax: First UEFI rootkit found in the wild, courtesy of the Sednit group Python Interpreter for UEFI Shell 3. Software Implementation, Frameworks & Protocols The SD card is a proprietary, non-volatile, flash memory card format developed by the SD Association (SDA). They come in three physical forms: the full-size SD, the smaller miniSD (now obsolete), and the smallest, microSD. Owing to their compact form factor, SD cards have been widely adopted in a variety of portable consumer electronics, including digital cameras, camcorders, video game consoles, mobile phones, action cameras, and camera drones. The format was introduced in August 1999 as Secure Digital by SanDisk, Panasonic (then known as Matsushita), and Kioxia (then part of Toshiba). It was designed as a successor to the MultiMediaCard (MMC) format, introducing several enhancements including a digital rights management (DRM) feature, a more durable physical casing, and a mechanical write-protect switch. These improvements, combined with strong industry support, contributed to its widespread adoption. To manage licensing and intellectual property rights, the founding companies established SD-3C, LLC. In January 2000, they also formed the SD Association, a non-profit organization responsible for developing the SD specifications and promoting the format. As of 2023, the SDA includes approximately 1,000 member companies. The association uses trademarked logos owned by SD-3C to enforce compliance with official standards and to indicate product compatibility.
At the March 2003 CeBIT trade show, SanDisk introduced and demonstrated the miniSD card format. The SD Association (SDA) adopted miniSD later that year as a small-form-factor extension to the SD card standard, intended primarily for use in mobile phones. However, the format was largely phased out by 2008 following the introduction of the even smaller microSD card. The microSD format was introduced by SanDisk at CeBIT in 2004, initially under the name T-Flash, later rebranded as TransFlash or TF. In 2005, the SDA adopted the format under the official name microSD, though the TransFlash name remains in common use as a generic term for microSD cards. A passive adapter allows microSD cards to be used in standard SD card slots, maintaining backward compatibility across devices.
The storage capacity of SD cards increased steadily throughout the 2010s, driven by advances in NAND flash manufacturing and interface speeds. In January 2009, the SDA introduced the Secure Digital eXtended Capacity (SDXC) format, supporting up to 2 TB of storage and transfer speeds up to 300 MB/s. SDXC cards are formatted with the exFAT file system by default. The first SDXC cards appeared in 2010, with early models offering capacities of 32 to 64 GB and read/write speeds of several hundred megabits per second. Consumer adoption accelerated as digital cameras, smartphones, and card readers gained SDXC compatibility. By 2011, manufacturers offered SDXC cards in 64 and 128 GB capacities, with some models supporting UHS Speed Class 10 and faster. In the following years, capacity milestones were reached: 256 GB in 2013, 512 GB in 2014, 1 TB in 2019, and 2 TB in 2022. The Secure Digital Ultra Capacity (SDUC) specification, announced in 2018, expanded maximum capacity to 128 TB and increased theoretical transfer speeds to 985 MB/s. In 2024, Western Digital announced the first 4 TB SDUC card, scheduled for commercial release in 2025.
A notched, asymmetrical shape to prevent incorrect insertion. Recessed electrical contacts to protect against damage and contamination. A four-line data bus for faster transfers, compared to MMC's single data line. A mechanical write-protect switch. These features came at the expense of increased card thickness: 2.1 mm (0.083 in) for standard SD cards, compared to 1.4 mm (0.055 in) for MMC. A 1.4 mm (0.055 in) Thin SD variant was also defined, but saw little use. SDSC cards support capacities up to 2 GB and use the FAT12 or FAT16 file system. They remain compatible with most SD-capable devices but have been largely superseded by higher-capacity formats. Because of physical differences, full-size SD cards do not fit in slim MMC-only slots.
SD High Capacity (SDHC) was introduced in SD specification version 2.0, released in January 2006. It expands the maximum capacity to 32 GB, compared to the 2 GB limit of SDSC. SDHC cards are physically identical to earlier standard-capacity SD (SDSC) cards, but differ in how they store and address data. This includes a redefinition of the Card-Specific Data (CSD) register (for details, see § Storage capacity calculations). Additionally, SDHC cards are typically preformatted with the FAT32 file system. SDHC-compatible devices are required to support older SDSC cards. However, older SDSC devices may not recognize SDHC cards without a firmware update. Older operating systems like Windows XP require patches or service packs to access SDHC cards.
Support for the UHS-II interface was introduced in SD specification version 4.0, released in January 2011. It added two new transfer modes: FD156, supporting up to 156 MB/s full-duplex, and HD312, enabling up to 312 MB/s half-duplex. These speeds required a second row of connectors for LVDS, bringing the total to 17 for full-size cards and 16 for microSD cards. Each LVDS lane can transfer up to 156 MB/s. In full-duplex mode, one lane is used for sending data and the other for receiving. In half-duplex mode, both lanes operate in the same direction. While initial adoption began in cameras around 2014, wider implementation took several more years, as few applications required the extra speed provided by the interface. As of 2025, about 100 cameras, mostly high-end models, support UHS-II cards.
SD Express was introduced in SD specification version 7.0, released in June 2018. By incorporating a single PCI Express 3.0 (PCIe) lane and supporting the NVM Express (NVMe) storage protocol, SD Express enables full-duplex transfer speeds of up to 985 MB/s. SD Express cards support direct memory access (DMA), which can improve performance, though security researchers have warned that it may also increase the attack surface in the event of a compromised or malicious card.
Compatible cards must support both PCIe and NVMe, and may be formatted as SDHC, SDXC, or SDUC. For backward compatibility, SD Express cards are also required to support the High-Speed and UHS-I bus interfaces. However, because the PCIe interface reuses the second row of pins previously used by UHS-II and UHS-III, compatibility with older devices is limited to UHS-I speeds. The specification also reserves space for two additional pins for future use. In February 2019, the SD Association introduced microSD Express, along with updated visual marks to help users identify compatible cards and devices. SD specification version 8.0, released in May 2020, expanded the interface to support PCIe 4.0 and introduced dual-lane configurations for full-size cards by adding a third row of electrical contacts, bringing the total to 26. This raised the theoretical maximum transfer rate to 3938 MB/s using dual-lane PCIe 4.0. Due to space constraints, the microSD form factor cannot accommodate a third row of contacts and remains limited to a single PCIe lane. Adoption has been gradual. In February 2024, Samsung began sampling its first microSD Express cards, though commercial availability remained limited.
Interest grew in April 2025 when Nintendo announced that the Switch 2 would support only microSD Express cards, with UHS-I card support limited to transferring media from earlier models. As of June 2025, only single-lane PCIe 3.1 SD Express cards are commercially available; no PCIe 4.0 or dual-lane cards have been released for general sale. Speed Class ratings were introduced to indicate the minimum data transfer performance of an SD card (as opposed to bus speed rating, which indicates device performance) in terms of sustained sequential write performance. This performance is important when transferring large files, especially during tasks like video recording, which requires consistent throughput to avoid dropped frames. Where speed classes overlap, manufacturers often display multiple symbols on the same card to indicate compatibility with different host devices and standards.
Initially, some manufacturers used a "×" rating system based on the speed of a standard CD-ROM drive (150 kB/s or 1.23 Mbit/s), but this approach was inconsistent and often unclear. It was later replaced by standardized Speed Class systems that specify guaranteed minimum write speeds. Application Performance Class ratings were introduced in 2016 to identify SD cards capable of reliably running and storing applications, alongside general-purpose tasks such as saving photos, videos, music, and documents. Earlier SD card speed ratings focused on sequential read and write performance, which is important when transferring large files. However, running apps and operating systems involves frequent access to many small files—a pattern known as random access—which places different demands on storage. Before the introduction of the Application Performance Classes, random access performance could vary significantly between cards and presented a limiting factor in some use cases. As SD cards saw broader use for app storage and system boot volumes—especially in mobile devices, single-board computers, and embedded systems—a new performance metric became necessary. This need became more pressing with Android's Adoptable Storage feature, which allows SD cards to function as internal (non-removable) storage on smartphones and tablets. To address this, the SD Association introduced Application Performance Classes. The first, A1, defined in SD Specification 5.1 (released November 2016), requires a minimum of 1,500 input/output operations per second (IOPS) for reading and 500 IOPS for writing, using 4 kB blocks. The higher-tier A2 class, defined in Specification 6.0 (released in February 2017), raises the thresholds to 4,000 read and 2,000 write IOPS. However, achieving these speeds requires host device support for command queuing and write caching, features that allow the card to optimize the execution of multiple simultaneous tasks and temporarily store data. If not properly supported, performance will fall back to A1 levels. Both A1 and A2 cards must also sustain a minimum sequential write speed of 10 MB/s, equivalent to speed classes C10, U1 and V10.
4. Practical Deployment, Analysis & Case Studies Most full-size SD cards have a mechanical write-protect switch, a sliding tab over a notch on the left side (viewed from the top, with the beveled corner on the right), that signals to the device to treat the card as read-only. Sliding the tab up (toward the contacts) sets the card to read/write; sliding it down sets it to read-only. However, the switch position is not detected by the card's internal circuitry. Therefore, some devices ignore it, while others allow overrides. MiniSD and microSD cards lack a built-in notch but can be used with adapters that include one. Cards without a notch are always writable; cards with preloaded content have a notch but no sliding tab.
Vendors have sought to differentiate their products in the market through various vendor-specific features: Integrated Wi-Fi – Several companies produce SD cards with built-in Wi-Fi transceivers. The card lets any digital camera with an SD slot transmit captured images over a wireless network or store the images on the card's memory until it is in range of a wireless network. Some models geotag their pictures. Pre-loaded content – In 2006, SanDisk announced Gruvi, a microSD card with extra digital rights management features, which they intended as a medium for publishing content. SanDisk again announced pre-loaded cards in 2008, under the slotMusic name, this time not using any of the DRM capabilities of the SD card. In 2011, SanDisk offered various collections of 1000 songs on a single slotMusic card for about $40, now restricted to compatible devices and without the ability to copy the files. Integrated USB connector – Several companies produce SD cards with built-in USB connectors allowing them to be accessed by a computer without a card reader. Integrated display – In 2006, ADATA announced a Super Info SD card with a digital display that provided a two-character label and showed the amount of unused memory on the card.
SDIO (Secure Digital Input Output) is an extension of the SD specification that supports input/output (I/O) devices in addition to data storage. SDIO cards are physically and electrically identical to standard SD cards but require compatible host devices with appropriate drivers to utilize their I/O functions. Common examples included adapters for GPS, Wi-Fi, cameras, barcode readers, and modems. In effect, the faster (wider) SD bus is used to replace the SPI bus previously used for those I/O devices. SDIO was not widely adopted.
A newer card may offer greater capacity than the host device can handle (over 4 GB for SDHC, over 32 GB for SDXC). A newer card may use a file system the host device cannot navigate (FAT32 for SDHC, exFAT for SDXC) Use of an SDIO card requires the host device be designed for the input/output functions the card provides. The hardware interface of the card was changed starting with the version 2.0 (new high-speed bus clocks, redefinition of storage capacity bits) and SDHC family (ultra-high speed (UHS) bus) UHS-II has physically more pins but is backwards compatible to UHS-I and non-UHS for both slot and card. Some vendors produced SDSC cards above 1 GB before the SDA had standardized a method of doing so.
microSD cards have been widely used in mobile phones to expand storage, particularly for photos, videos, music, documents, and other infrequently accessed files. By 2015, support for microSD cards was common in Android smartphones. However, by 2025, support had declined, particularly in high-end models. This shift has been attributed to cheaper, higher-capacity internal storage with faster performance than microSD, concerns over user experience related to counterfeit cards, and the increased availability, speed, and security of cloud storage services. In contrast, Apple never included microSD card slots in the iPhone, instead relying on built-in flash storage and cloud-based services.
While some modern microcontrollers integrate SDIO hardware which uses the faster proprietary four-bit SD bus mode, almost all modern microcontrollers at least have SPI units that can interface to an SD card operating in the slower one-bit SPI bus mode. If not, SPI can also be emulated by bit banging (e.g. a SD card slot soldered to a Linksys WRT54G-TM router and wired to GPIO pins using DD-WRT's Linux kernel achieved only 1.6 Mb/s. The popular Raspberry Pi series of small single-board computers originally used full-sized SD cards for primary storage before switching to microSD for newer versions. There is a class of industrial SD cards separate from the usual commercial SD cards, commonly used in industrial embedded systems. They generally provide stronger guarantees of endurance (including both data endurance and a guarantee for performance after a certain amount of use), reliability, and usable temperature ranges. Many also offer a S.M.A.R.T functionality.
The SD card specification defines three physical sizes. The SD and SDHC families are available in all three sizes, but the SDXC and SDUC families are not available in the mini size, and the SDIO family is not available in the micro size. Smaller cards are usable in larger slots through use of a passive adapter. microSD, microSDHC, microSDXC, microSDUC 15 mm × 11 mm × 1 mm (19⁄32 in × 7⁄16 in × 3⁄64 in) SPI bus mode: Serial Peripheral Interface Bus is primarily used by embedded microcontrollers. This bus type supports only a 3.3-volt interface. This is the only bus type that does not require a host license. One-bit SD bus mode: Separate command and data channels and a proprietary transfer format. Four-bit SD bus mode: Uses extra pins plus some reassigned pins. This is the same protocol as the one-bit SD bus mode which uses one command and four data lines for faster data transfer. All SD cards support this mode. UHS-I and UHS-II require this bus type. Two differential lines SD UHS-II mode: Uses two low-voltage differential signaling interfaces to transfer commands and data. UHS-II cards include this interface in addition to the SD bus modes. The physical interface comprises 9 pins, except that the miniSD card adds two unconnected pins in the center and the microSD card omits one of the two VSS (Ground) pins.
5. Performance Evaluation & Extended Technical Observations Direction is relative to card. I = Input, O = Output. PP = Push-Pull logic, OD = Open-Drain logic. S = Power Supply, NC = Not Connected (or logical high). Determine the type, memory capacity and capabilities of the SD card Command the card to use a different voltage, different clock speed, or advanced electrical interface Prepare the card to receive a block to write to the flash memory, or read and reply with the contents of a specified block. The command interface is an extension of the MultiMediaCard (MMC) interface.
SD cards dropped support for some of the commands in the MMC protocol, but added commands related to copy protection. By using only commands supported by both standards until determining the type of card inserted, a host device can accommodate both SD and MMC cards. For SDSC cards: Capacity of less than 32,680 logical sectors (smaller than 16 MB): FAT12 with partition type 01h and BPB 3.0 or EBPB 4.1 Capacity of 32,680 to 65,535 logical sectors (between 16 MB and 32 MB): FAT16 with partition type 04h and BPB 3.0 or EBPB 4.1 Capacity of at least 65,536 logical sectors (larger than 32 MB): FAT16B with partition type 06h and EBPB 4.1 For SDHC cards: Capacity of less than 16,450,560 / 1..63 -> limit: 1024x255x63 = 16450560 --> logical sectors (smaller than 7.8 GB): FAT32 with partition type 0Bh and EBPB 7.1 Capacity of at least 16,450,560 logical sectors (larger than 7.8 GB): FAT32 with partition type 0Ch and EBPB 7.1 For SDXC cards: exFAT with partition type 07h Most consumer products that take an SD card expect that it is partitioned and formatted in this way. Universal support for FAT12, FAT16, FAT16B and FAT32 allows the use of SDSC and SDHC cards on most host computers with a compatible SD reader, to present the user with the familiar method of named files in a hierarchical directory tree. On such SD cards, standard utility programs such as Mac OS X's Disk Utility or Windows' CHKDSK can be used to repair a corrupted filing system and sometimes recover deleted files. Defragmentation tools for FAT file systems may be used on such cards. The resulting consolidation of files may provide a marginal improvement in the time required to read or write the file, but not an improvement comparable to defragmentation of hard drives, where storing a file in multiple fragments requires additional physical and relatively slow, movement of a drive head. Moreover, defragmentation performs writes to the SD card that count against the card's rated lifespan. The write endurance of the physical memory is discussed in the article on flash memory; newer technology to increase the storage capacity of a card provides worse write endurance. When reformatting an SD card with a capacity of at least 32 MB (65,536 logical sectors or more), but not more than 2 GB FAT16B with partition type 06h and EBPB 4.1 is recommended if the card is for a consumer device. (FAT16B is also an option for 4 GB cards, but it requires the use of 64 KB clusters, which are not widely supported.) FAT16B does not support cards above 4 GB at all. The SDXC specification mandates the use of Microsoft's proprietary exFAT file system, which sometimes requires appropriate drivers (e.g.
exfat-utils/exfat-fuse on Linux). SD version 1.00 assumed 512 bytes per block. This permitted SDSC cards up to 1 GB. Version 1.01 let an SDSC card use a 4-bit field to indicate 1024 or 2048 bytes per block instead. Doing so enabled cards with 2 GB capacity. SDHC cards are restricted to reporting a capacity not over 32 GB. SDXC cards are allowed to use all 22 bits of the C_SIZE field. SDHC cards can only set a maximum value of 65375, using the lower 16 bits. The user data area capacity is calculated from C_SIZE as follows: memory capacity = (C_SIZE + 1) × 512 KB The Minimum user area size of SDHC Card is 4,211,712 sectors (2 GB + 8.5 MB). The Minimum value of C_SIZE for SDHC in CSD Version 2.0 is 001010h (4112). The maximum user area size of SDHC Card is (32 GB − 80 MB) The maximum value of C_SIZE for SDHC in CSD Version 2.0 is 00FF5Fh (65375). The Minimum user area size of SDXC Card is 67,108,864 sectors (32 GB).
Various passive adapters are available to allow smaller SD cards to work in larger SD card slots. GrapheneOS () is an open-source mobile operating system focused on security and privacy, available for Google Pixel and future Motorola devices, including smartphones, tablets, and foldables. It is built on the Android Open Source Project (AOSP) and was first released in 2016. The project focuses on researching and improving the privacy and security of Android, primarily through defense in depth improvements and attack surface reduction. The hardening includes low-level system components, as well as improvements to application sandboxing and the permission model. GrapheneOS is free and open-source. The system components are mostly published under permissive licenses, such as the MIT License or Apache License 2.0, with some components using the GNU GPL-2.0 license. GrapheneOS can be installed using a web installer or a traditional command-line-based installation environment. Due to its hardware security requirements, GrapheneOS is only officially supported on Google Pixel devices released between 2021 and 2025, but the project announced in 2026 that it plans to also certify selected devices from Motorola Mobility. The nonprofit GrapheneOS Foundation was founded in Toronto, Ontario, Canada, by Daniel Micay, Dmytro Mukhomor, and Khalykbek Yelshibekov in March 2023. It received large contributions from donors such as Ethereum developer Vitalik Buterin and Twitter founder Jack Dorsey. As of April 2026, the operating system had approximately 400,000 active users.
The main developer, Daniel Micay, co-founded and originally worked on CopperheadOS until a schism over software licensing between the co-founders of Copperhead Limited led to Micay's dismissal from the company in 2018. Micay continued working on the Android Hardening project, which was renamed to GrapheneOS and announced in April 2019 as the "true successor" to CopperheadOS, with the goal of restoring the same functions. The project's website states that CopperheadOS was renamed to GrapheneOS. In March 2022, two GrapheneOS apps, "Secure Camera" and "Secure PDF Viewer", were released on the Google Play Store, along with Android 12L for Google Pixel devices. In July 2025, the GrapheneOS Foundation stated it was pursuing a partnership with a "major Android OEM" with the goal of engineering devices with official GrapheneOS support that meet the project's extensive hardware and vendor support requirements. In March 2026, during Mobile World Congress, an official announcement was made, revealing that the new partner of GrapheneOS is Motorola Mobility. As of April 2026, GrapheneOS developers reported they had around 400,000 active users. The figure is an inexact estimate based on statistics generated from the access logs of the update servers. This is the only way for the GrapheneOS Foundation to approximate the number of users, since no telemetry mechanism is included in the operating system.
Off (disables charging to prevent the exploitation of possible USB-PD vulnerabilities; charging is still possible when the device is powered off) Charging-only (disables all data connectivity) Charging-only when locked Charging-only when locked, except before first unlock On (standard Android behavior) By default, the Charging-only when locked setting is used. GrapheneOS can also disable the microphone, camera, and sensors for apps. Additionally, it offers the Contact and Storage Scopes feature, which allows users to select which specific contacts or files/folders an app can access. A hardened Chromium-based web browser and WebView implementation known as Vanadium is developed by GrapheneOS and included as the default web browser and system WebView. It includes automatic updates, process and site-level sandboxing, disabling the V8 JavaScript just-in-time (JIT) compiler by default for attack surface reduction, and built-in ad and tracker blocking. Vanadium enables JIT-less WebAssembly support through the DrumBrake interpreter originally developed by Microsoft and upstreamed into the Chromium project. Auditor, a hardware-based attestation app developed by GrapheneOS, which provides "hardware-based verification of the authenticity and integrity of the firmware/software on the device", is also included. The app also includes an optional, scheduled remote verification feature, which runs in the background and performs regular verifications against the GrapheneOS attestation service. It can alert users via email if the device fails to provide valid attestations in time. The remote attestation interval and permitted time before an alert can be configured by the user using the web portal. Both the Auditor app and the AttestationServer backend are open source and permissively licensed under the MIT license. Apps like Secure Camera and Secure PDF Viewer offer features such as automatic removal of Exif metadata and protection against malicious code in PDF files by opening them within a sandboxed PDF.js environment in the hardened Vanadium WebView. GrapheneOS also includes a hardened memory allocator (hardened_malloc) intended to provide substantial defenses against common classes of vulnerabilities such as heap memory corruption. In addition, its Chromium-based browser/WebView (Vanadium) enables further exploit mitigations beyond upstream defaults (e.g., type-based control-flow integrity (CFI), stronger stack-smashing protection (SSP), or zero-initialization of variables). Unlike AOSP, the stock Pixel operating system, and other Android-based systems, GrapheneOS heavily makes use of the memory tagging extension (MTE) found in the processor cores of ARM chips using the ARMv8.5-A architecture or newer. The first devices on the market featuring MTE-enabled processors were Google's Pixel 8 and Pixel 8 Pro models, released in October 2023. GrapheneOS added support for the feature in November of the same year. GrapheneOS developers noted that the feature could especially be of importance for instant messaging applications, such as WhatsApp or Signal, which use large amounts of memory-unsafe code for features like WebRTC and are common targets of attackers. In March 2024, the team reported that the use of hardware memory tagging helped it uncover a high-severity memory corruption vulnerability in an Android Bluetooth Low Energy system component. The bug was acknowledged by Google and became known as CVE-2024-23694. It was fixed in the May 2024 Pixel Update Bulletin. The underlying Linux kernel is covered by the hardware tag-based KernelAddressSanitizer (KASan).
The operating system can be installed from various platforms, including Windows, macOS, Linux, and Android devices. Two installation methods are available: a web-based installer, recommended for most users, and a command-line-based installer, intended for more experienced users. The web installer makes use of the WebUSB API and is based on the fastboot.js library, a JavaScript implementation of the Fastboot utility developed by Danny Lin. It was inspired by Google's Android Flash Tool, which uses the same API for performing the installation in the browser. It is currently only supported in Chromium-based web browsers. Unlike the command-line installation script, it does not require the installation of any additional software.
Recommended post-installation steps include disabling OEM unlocking, which the setup wizard offers as a pre-checked toggle on its final screen, as well as verifying the Verified Boot hash of the installed OS image. The installation can additionally be verified using the Auditor app, either with the help of a second device or by using remote attestation. Jack Wallen of ZDNET described the installation process as follows: "It sounds difficult, but it's really not", and that it took him roughly ten minutes to complete the installation.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/UEFI • https://en.wikipedia.org/wiki/SD%20card • https://en.wikipedia.org/wiki/GrapheneOS
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Secure Firmware Update Mechanism For Embedded Devices.
[*] Metasploit Scan Running on Target Subnet for Secure Firmware Update Mechanism For Embedded Devices... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |