Complete Technical Paper Content — Secure Key Management And Distribution System Project
Overview & System Context
Secure Key Management And Distribution System Project: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9512 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background The Electronic Key Management System (EKMS) is a United States National Security Agency led program responsible for Communications Security (COMSEC) key management, accounting, and distribution. Specifically, EKMS generates and distributes electronic key material for all NSA encryption systems whose keys are loaded using standard fill devices, and directs the distribution of NSA produced key material. Additionally, EKMS performs account registration, privilege management, ordering, distribution, and accounting to direct the management and distribution of physical COMSEC material for the services. The common EKMS components and standards facilitate interoperability and commonality among the armed services and civilian agencies. Key Management Infrastructure (KMI) replaces EKMS.
processing orders for both physical and electronic keys electronically generating and distributing keys generating key material for FIREFLY (an NSA algorithm) performing seed conversion and rekey maintaining compromise recovery and management of FIREFLY material support for over-the-air rekeying (OTAR) The CF talks to other EKMS elements through a variety of media, communication devices, and networks, either through direct distance dialing using STU-III (data mode) or dedicated link access using KG-84 devices. During the transition to full electronic key, the 3.5-inch floppy disk and 9-track magnetic tape are also supported. A common user interface, the TCP/IP-based message service, is the primary method of communication with the CF. The message service permits EKMS elements to store EKMS messages that include electronic key for later retrieval by another EKMS element.
EKMS Tier 2, the Local Management Device (LMD), is composed of a commercial off-the-shelf (COTS) personal computer (PC) running the Santa Cruz Operation's SCO UNIX operating system, and an NSA KOK-22A Key Processor (KP). The KP is a trusted component of EKMS. It performs cryptographic functions, including encryption and decryption functions for the account, as well as key generation, and electronic signature operations. The KP is capable of secure field generation of traditional keys. Locally generated keys can be employed in crypto-net communications, transmission security (TRANSEC) applications, point-to-point circuits, and virtually anywhere that paper-based keys were used. Electronic keys can be downloaded directly to a fill device, such as the KYK-13, KYX-15, or the more modern AN/CYZ-10 Data Transfer Device (DTD) for further transfer (or fill) into the end cryptographic unit.
The Secure Shell Protocol (SSH Protocol) is a cryptographic network protocol for operating network services securely over an unsecured network. Its most notable applications are remote login and command-line execution. SSH was designed for Unix-like operating systems as a replacement for Telnet and unsecured remote Unix shell protocols, such as the Berkeley Remote Shell (rsh) and the related rlogin and rexec protocols, which all use insecure, plaintext methods of authentication, such as passwords. Since mechanisms like Telnet and Remote Shell are designed to access and operate remote computers, sending the authentication tokens (e.g. username and password) for this access to these computers across a public network in an unsecured way poses a great risk of third parties obtaining the password and achieving the same level of access to the remote system as the telnet user. Secure Shell mitigates this risk through the use of encryption mechanisms that are intended to hide the contents of the transmission from an observer, even if the observer has access to the entire data stream. Finnish computer scientist Tatu Ylönen designed SSH in 1995 and provided an implementation in the form of two commands, ssh and slogin, as secure replacements for rsh and rlogin, respectively. Subsequent development of the protocol suite proceeded in several developer groups, producing several variants of implementation. The protocol specification distinguishes two major versions, referred to as SSH-1 and SSH-2. The most commonly implemented software stack is OpenSSH, released in 1999 as open-source software by the OpenBSD developers. Implementations are distributed for all types of operating systems in common use, including embedded systems. SSH applications are based on a client–server architecture, connecting an SSH client instance with an SSH server. SSH operates as a layered protocol suite comprising three principal hierarchical components: the transport layer provides server authentication, confidentiality, and integrity; the user authentication protocol validates the user to the server; and the connection protocol multiplexes the encrypted tunnel into multiple logical communication channels.
Figure 1: OpenSigner: Open-Source Non-Custodial Key Management SSH is typically used to log into a remote computer's shell or command-line interface (CLI) and to execute commands on a remote server. It also supports mechanisms for tunneling, forwarding of TCP ports and X11 connections and it can be used to transfer files using the associated SSH File Transfer Protocol (SFTP) or Secure Copy Protocol (SCP). SSH uses the client–server model. An SSH client program is typically used for establishing connections to an SSH daemon, such as sshd, accepting remote connections. Both are commonly present on most modern operating systems, including macOS, most distributions of Linux, OpenBSD, FreeBSD, NetBSD, Solaris and OpenVMS. Notably, versions of Windows prior to Windows 10 version 1709 do not include SSH by default, but proprietary, freeware and open source versions of various levels of complexity and completeness did and do exist (see Comparison of SSH clients). In 2018 Microsoft began porting the OpenSSH source code to Windows and in Windows 10 version 1709, an official Win32 port of OpenSSH is now available. File managers for UNIX-like systems (e.g., Konqueror) can use the FISH protocol to provide a split-pane GUI with drag-and-drop.
The open source Windows program WinSCP provides similar file management (synchronization, copy, remote delete) capability using PuTTY as a back-end. Both WinSCP and PuTTY are available packaged to run directly off a USB drive, without requiring installation on the client machine. Crostini on ChromeOS comes with OpenSSH by default. Setting up an SSH server in Windows typically involves enabling a feature in the Settings app. SSH is important in cloud computing to solve connectivity problems, avoiding the security issues of exposing a cloud-based virtual machine directly on the Internet. An SSH tunnel can provide a secure path over the Internet, through a firewall to a virtual machine. The IANA has assigned TCP port 22, UDP port 22 and SCTP port 22 for this protocol. IANA had listed the standard TCP port 22 for SSH servers as one of the well-known ports as early as 2001. SSH can also be run using SCTP rather than TCP as the connection-oriented transport layer protocol. The version control system Git is commonly used with SSH. Git over SSH used to be the only secure protocol to push changes to repositories because Git over HTTP only supported read-only access to Git repositories before Git 1.6.6 in 2010.
Faster session establishment, reducing the number of Round-trip delays from 5-7 to 3. High security: while SSHv2 relies on its own protocols, SSH3 leverages TLS 1.3, QUIC, and HTTP. UDP port forwarding X.509 certificates OpenID Connect However, the name SSH3 is under discussion, and the project aims to rename itself to a more suitable name. The discussion stems from the fact that this new implementation significantly revises the SSH protocol, suggesting it should not be called SSH3. In 2026, researchers from Stanford University introduced Hop, an open-source transport and remote access protocol designed to modernize remote terminal sessions and address protocol complexity in legacy SSH. Hop replaces SSH's traditional Trust-On-First-Use (TOFU) model with automated certificate verification using ACME. To protect against active network scanning and metadata leakage, the protocol supports both a standard discoverable handshake and a "hidden mode" that conceals server and client identities from unauthenticated observers. Hop also features a cryptographically mediated delegation scheme that allows secure session forwarding through jump hosts without exposing client private keys.
Additionally, Hop provides built-in network resilience, supporting seamless client roaming across IP address changes and preserving session state during intermittent connection loss. SSH is a protocol that can be used for many applications across many platforms, including most Unix variants (Linux, the BSDs including Apple's macOS, and Solaris), as well as Microsoft Windows. Some of the applications below may require features that are only available or compatible with specific SSH clients or servers. For example, using the SSH protocol to implement a VPN is possible, but presently only with the OpenSSH server and client implementation.
For login to a shell on a remote host (replacing Telnet and rlogin) For executing a single command on a remote host (replacing rsh) For setting up automatic (passwordless) login to a remote server (for example, using OpenSSH) In combination with rsync to back up, copy and mirror files efficiently and securely For forwarding a port For tunneling (not to be confused with a VPN, which routes packets between different networks, or bridges two broadcast domains into one). For use as a full-fledged encrypted VPN. Note that only OpenSSH server and client support this feature. For forwarding X from a remote host (possible through multiple intermediate hosts) For browsing the web through an encrypted proxy connection with SSH clients that support the SOCKS protocol. For securely mounting a directory on a remote server as a file system on a local computer using SSHFS. For automated remote monitoring and management of servers through one or more of the mechanisms discussed above. For development on a mobile or embedded device that supports SSH. For securing file transfer protocols.
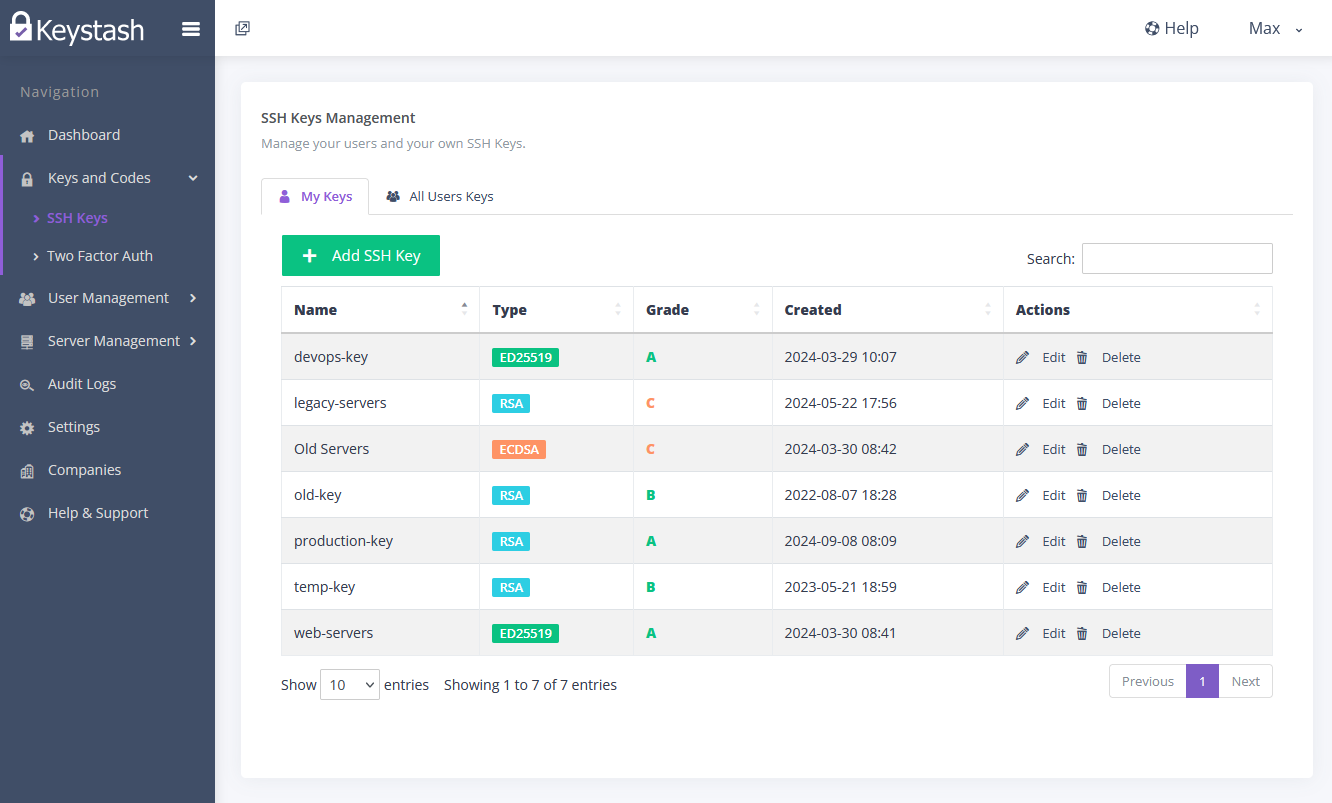
Figure 2: Keystash | Features Secure copy (SCP), which evolved from RCP protocol over SSH rsync, intended to be more efficient than SCP. Generally runs over an SSH connection. SSH File Transfer Protocol (SFTP), a secure alternative to FTP (not to be confused with FTP over SSH or FTPS) Files transferred over shell protocol (FISH), released in 1998, which evolved from Unix shell commands over SSH Fast and Secure Protocol (FASP), aka Aspera, uses SSH for control and UDP ports for data transfer.
The transport layer (RFC 4253) typically uses the Transmission Control Protocol (TCP) of TCP/IP, reserving port number 22 as a server listening port. This layer handles initial key exchange as well as server authentication, and sets up encryption, compression, and integrity verification. It exposes to the upper layer an interface for sending and receiving plaintext packets with a size of up to 32,768 bytes each, but more can be allowed by each implementation. The transport layer also arranges for key re-exchange, usually after 1 GB of data has been transferred or after one hour has passed, whichever occurs first. The user authentication layer (RFC 4252) handles client authentication and provides a suite of authentication algorithms.
Authentication is client-driven: when one is prompted for a password, it may be the SSH client prompting, not the server. The server merely responds to the client's authentication requests. Widely used user-authentication methods include the following: password: a method for straightforward password authentication, including a facility allowing a password to be changed. Not all programs implement this method. publickey: a method for public-key-based authentication, usually supporting at least DSA, ECDSA or RSA keypairs, with other implementations also supporting X.509 certificates. keyboard-interactive (RFC 4256): a versatile method where the server sends one or more prompts to enter information and the client displays them and sends back responses keyed in by the user. Used to provide one-time password authentication such as S/Key or SecurID.
Used by some OpenSSH configurations when PAM is the underlying host-authentication provider to effectively provide password authentication, sometimes leading to an inability to log in with a client that supports just the plain password authentication method. GSSAPI authentication methods which provide an extensible scheme to perform SSH authentication using external mechanisms such as Kerberos 5 or NTLM, providing single sign-on capability to SSH sessions. These methods are usually implemented by commercial SSH implementations for use in organizations, though OpenSSH does have a working GSSAPI implementation. The connection layer (RFC 4254) defines the concept of channels, channel requests, and global requests, which define the SSH services provided. A single SSH connection can be multiplexed into multiple logical channels simultaneously, each transferring data bidirectionally. Channel requests are used to relay out-of-band channel-specific data, such as the changed size of a terminal window or the exit code of a server-side process. Additionally, each channel performs its own flow control using the receive window size. The SSH client requests a server-side port to be forwarded using a global request. Standard channel types include: shell for terminal shells, SFTP and exec requests (including SCP transfers) direct-tcpip for client-to-server forwarded connections forwarded-tcpip for server-to-client forwarded connections The SSHFP DNS record (RFC 4255) provides the public host key fingerprints in order to aid in verifying the authenticity of the host. This open architecture provides considerable flexibility, allowing the use of SSH for a variety of purposes beyond a secure shell. The functionality of the transport layer alone is comparable to Transport Layer Security (TLS); the user-authentication layer is highly extensible with custom authentication methods; and the connection layer provides the ability to multiplex many secondary sessions into a single SSH connection, a feature comparable to BEEP and not available in TLS.
A novel man-in-the-middle attack against most current ssh implementations was discovered in 2023. It was named the Terrapin attack by its discoverers. However, the risk is mitigated by the requirement to intercept a genuine ssh session, and that the attack is restricted in its scope, fortuitously resulting mostly in failed connections. The ssh developers have stated that the major impact of the attack is to degrade the keystroke timing obfuscation features of ssh. The vulnerability was fixed in OpenSSH 9.6, but requires both client and server to be upgraded for the fix to be fully effective.
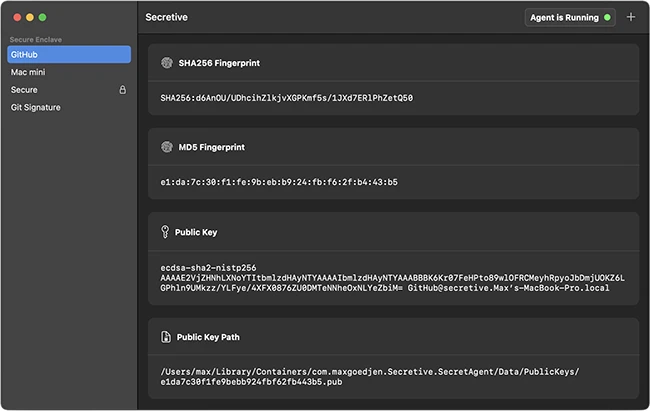
RFC 4250 – The Secure Shell (SSH) Protocol Assigned Numbers RFC 4251 – The Secure Shell (SSH) Protocol Architecture RFC 4252 – The Secure Shell (SSH) Authentication Protocol RFC 4253 – The Secure Shell (SSH) Transport Layer Protocol RFC 4254 – The Secure Shell (SSH) Connection Protocol RFC 4255 – Using DNS to Securely Publish Secure Shell (SSH) Key Fingerprints RFC 4256 – Generic Message Exchange Authentication for the Secure Shell Protocol (SSH) RFC 4335 – The Secure Shell (SSH) Session Channel Break Extension RFC 4344 – The Secure Shell (SSH) Transport Layer Encryption Modes RFC 4345 – Improved Arcfour Modes for the Secure Shell (SSH) Transport Layer Protocol The protocol specifications were later updated by the following publications: Figure 3: Secretive: Open-source app for storing and managing SSH keys in the ...
RFC 4419 – Diffie-Hellman Group Exchange for the Secure Shell (SSH) Transport Layer Protocol (March 2006) RFC 4432 – RSA Key Exchange for the Secure Shell (SSH) Transport Layer Protocol (March 2006) RFC 4462 – Generic Security Service Application Program Interface (GSS-API) Authentication and Key Exchange for the Secure Shell (SSH) Protocol (May 2006) RFC 4716 – The Secure Shell (SSH) Public Key File Format (November 2006) RFC 4819 – Secure Shell Public Key Subsystem (March 2007) RFC 5647 – AES Galois Counter Mode for the Secure Shell Transport Layer Protocol (August 2009) RFC 5656 – Elliptic Curve Algorithm Integration in the Secure Shell Transport Layer (December 2009) RFC 6187 – X.509v3 Certificates for Secure Shell Authentication (March 2011) RFC 6239 – Suite B Cryptographic Suites for Secure Shell (SSH) (May 2011) RFC 6594 – Use of the SHA-256 Algorithm with RSA, Digital Signature Algorithm (DSA), and Elliptic Curve DSA (ECDSA) in SSHFP Resource Records (April 2012) RFC 6668 – SHA-2 Data Integrity Verification for the Secure Shell (SSH) Transport Layer Protocol (July 2012) RFC 7479 – Ed25519 SSHFP Resource Records (March 2015) RFC 5592 – Secure Shell Transport Model for the Simple Network Management Protocol (SNMP) (June 2009) RFC 6242 – Using the NETCONF Protocol over Secure Shell (SSH) (June 2011) RFC 8332 – Use of RSA Keys with SHA-256 and SHA-512 in the Secure Shell (SSH) Protocol (March 2018) RFC 8709 – Ed25519 and Ed448 Public Key Algorithms for the Secure Shell (SSH) Protocol (February 2020) draft-gerhards-syslog-transport-ssh – SSH transport mapping for SYSLOG (July 2006) draft-ietf-secsh-filexfer – SSH File Transfer Protocol (July 2006) draft-ietf-sshm-ssh-agent - SSH Agent Protocol (March 2025) In addition, the OpenSSH project includes several vendor protocol specifications/extensions: SSH Protocols M. Joseph; J. Susoy (November 2013). P6R's Secure Shell Public Key Subsystem. IETF.
Key management is the management of cryptographic keys in a cryptosystem. This includes the lifecycle management of keys, such as the generation, exchange, storage, use, crypto-shredding (destruction) and replacement of keys. It includes cryptographic protocol design, key servers, user procedures, and other relevant protocols. Key management concerns keys at the user level, either between users or systems. This is in contrast to key scheduling, which typically refers to the internal handling of keys within the operation of a cipher. Successful key management is critical to the security of a cryptosystem. It is the more challenging side of cryptography in a sense that it involves aspects of social engineering such as system policy, user training, organizational and departmental interactions, and coordination between all of these elements, in contrast to pure mathematical practices that can be automated.
Cryptographic systems may use different types of keys, with some systems using more than one. These may include symmetric keys or asymmetric keys. In a symmetric key algorithm the keys involved are identical for both encrypting and decrypting a message. Keys must be chosen carefully, and distributed and stored securely. Asymmetric keys, also known as public keys, in contrast are two distinct keys that are mathematically linked. They are typically used together to communicate.
Public key infrastructure (PKI), the implementation of public key cryptography, requires an organization to establish an infrastructure to create and manage public and private key pairs along with digital certificates. Regulations and requirements, like PCI-DSS, demand stringent security and management of cryptographic keys and auditors are increasingly reviewing the management controls and processes in use. Private keys used with certificates must be kept secure or unauthorised individuals can intercept confidential communications or gain unauthorised access to critical systems.
Failure to ensure proper segregation of duties means that admins who generate the encryption keys can use them to access sensitive, regulated data. If a certificate authority is compromised or an encryption algorithm is broken, organizations must be prepared to replace all of their certificates and keys in a matter of hours. Prior to any secured communication, users must set up the details of the cryptography. In some instances this may require exchanging identical keys (in the case of a symmetric key system). In others it may require possessing the other party's public key. While public keys can be openly exchanged (their corresponding private key is kept secret), symmetric keys must be exchanged over a secure communication channel. Formerly, exchange of such a key was extremely troublesome, and was greatly eased by access to secure channels such as a diplomatic bag. Clear text exchange of symmetric keys would enable any interceptor to immediately learn the key, and any encrypted data. The advance of public key cryptography in the 1970s has made the exchange of keys less troublesome. Since the Diffie-Hellman key exchange protocol was published in 1975, it has become possible to exchange a key over an insecure communications channel, which has substantially reduced the risk of key disclosure during distribution. It is possible, using something akin to a book code, to include key indicators as clear text attached to an encrypted message. The encryption technique used by Richard Sorge's code clerk was of this type, referring to a page in a statistical manual, though it was in fact a code. The German Army Enigma symmetric encryption key was a mixed type early in its use; the key was a combination of secretly distributed key schedules and a user chosen session key component for each message. In more modern systems, such as OpenPGP compatible systems, a session key for a symmetric key algorithm is distributed encrypted by an asymmetric key algorithm. This approach avoids even the necessity for using a key exchange protocol like Diffie-Hellman key exchange. Another method of key exchange involves encapsulating one key within another. Typically a master key is generated and exchanged using some secure method. This method is usually cumbersome or expensive (breaking a master key into multiple parts and sending each with a trusted courier for example) and not suitable for use on a larger scale. Once the master key has been securely exchanged, it can then be used to securely exchange subsequent keys with ease. This technique is usually termed key wrap. A common technique uses block ciphers and cryptographic hash functions. A related method is to exchange a master key (sometimes termed a root key) and derive subsidiary keys as needed from that key and some other data (often referred to as diversification data). The most common use for this method is probably in smartcard-based cryptosystems, such as those found in banking cards. The bank or credit network embeds their secret key into the card's secure key storage during card production at a secured production facility. Then at the point of sale the card and card reader are both able to derive a common set of session keys based on the shared secret key and card-specific data (such as the card serial number). This method can also be used when keys must be related to each other (i.e., departmental keys are tied to divisional keys, and individual keys tied to departmental keys).
However, tying keys to each other in this way increases the damage which may result from a security breach as attackers will learn something about more than one key. This reduces entropy, with regard to an attacker, for each key involved. A recent method uses an oblivious pseudorandom function to issue keys without the key management system ever being in a position to see the keys.
Scalability: Managing a large number of encryption keys. Security: Vulnerability of keys from outside hackers, malicious insiders. Availability: Ensuring data accessibility for authorized users. Heterogeneity: Supporting multiple databases, applications and standards. Governance: Defining policy-driven access control and protection for data. Governance includes compliance with data protection requirements.
Physical security – the most visible form of compliance, which may include locked doors to secure system equipment and surveillance cameras. These safeguards can prevent unauthorized access to printed copies of key material and computer systems that run key management software. Logical security – protects the organization against the theft or unauthorized access of information. This is where the use of cryptographic keys comes in by encrypting data, which is then rendered useless to those who do not have the key to decrypt it. Personnel security – this involves assigning specific roles or privileges to personnel to access information on a strict need-to-know basis. Background checks should be performed on new employees along with periodic role changes to ensure security. Compliance can be achieved with respect to national and international data protection standards and regulations, such as Payment Card Industry Data Security Standard, Health Insurance Portability and Accountability Act, Sarbanes–Oxley Act, or General Data Protection Regulation.
KMIP is an extensible key management protocol that has been developed by many organizations working within the OASIS standards body. The first version was released in 2010, and it has been further developed by an active technical committee. The protocol allows for the creation of keys and their distribution among disparate software systems that need to utilize them. It covers the full key life cycle of both symmetric and asymmetric keys in a variety of formats, the wrapping of keys, provisioning schemes, and cryptographic operations as well as meta data associated with the keys. The protocol is backed by an extensive series of test cases, and interoperability testing is performed between compliant systems each year.
A list of some 80 products that conform to the KMIP standard can be found on the OASIS website. Confidentiality Integrity Availability Authentication of source This protection covers the complete key life-cycle from the time the key becomes operational to its elimination. Bring your own encryption (BYOE)—also called bring your own key (BYOK)—refers to a cloud-computing security model to allow public-cloud customers to use their own encryption software and manage their own encryption keys. This security model is usually considered a marketing stunt, as critical keys are being handed over to third parties (cloud providers) and key owners are still left with the operational burden of generating, rotating and sharing their keys.
A public-key infrastructure is a type of key management system that uses hierarchical digital certificates to provide authentication, and public keys to provide encryption. PKIs are used in World Wide Web traffic, commonly in the form of SSL and TLS. American National Standards Institute - ANSI X9.24, Retail Financial Services Symmetric Key Management The OASIS Key Management Interoperability Protocol (KMIP) Technical Committee The OASIS Enterprise Key Management Infrastructure (EKMI)Technical Committee "Key Management with a Powerful Keystore" "Intelligent Key Management System - KeyGuard | Senergy Intellution" IBM Security Key Lifecycle Manager, SKLM NeoKeyManager - Hancom Intelligence Inc. KMS Key Archived 2022-11-30 at the Wayback Machine This Key Management Cheat Sheet provides developers with guidance for implementation of cryptographic key management within an application in a secure manner. It is important to document and harmonize rules and practices for: Formulate a plan for the overall organization's cryptographic strategy to guide developers working on different applications and ensure that each application's cryptographic capability meets minimum requirements and best practices.
Identify the cryptographic and key management requirements for your application and map all components that process or store cryptographic key material. Selection of the cryptographic and key management algorithms to use within a given application should begin with an understanding of the objectives of the application.
For example, if the application is required to store data securely, then the developer should select an algorithm suite that supports the objective of data at rest protection security. Applications that are required to transmit and receive data would select an algorithm suite that supports the objective of data in transit protection. 2. System Architecture & Core Working Principles We have provided recommendations on the selection of crypto suites within an application based on application and security objectives. Application developers oftentimes begin the development of crypto and key management capabilities by examining what is available in a library.
However, an analysis of the real needs of the application should be conducted to determine the optimal key management approach. Begin by understanding the security objectives of the application which will then drive the selection of cryptographic protocols that are best suited. For example, the application may require: Once the understanding of the security needs of the application is achieved, developers can determine what protocols and algorithms are required. Once the protocols and algorithms are understood, you can begin to define the different types of keys that will support the application's objectives.
According to NIST SP 800-57 Part 1 , many algorithms and schemes that provide a security service use a hash function as a component of the algorithm. Hash functions can be found in digital signature algorithms ( FIPS186 ), Keyed-Hash Message Authentication Codes (HMAC) ( FIPS198 ), key-derivation functions/methods ( NIST Special Publications (SP) 800-56A, 800-56B, 800-56C and 800-108 ), and random number generators ( NIST SP 800-90A ). Approved hash functions are defined in FIPS180 .
NIST SP 800-57 Part 1 recognizes three basic classes of approved cryptographic algorithms: hash functions, symmetric- key algorithms and asymmetric-key algorithms. The classes are defined by the number of cryptographic keys that are used in conjunction with the algorithm. The NSA released a report, Commercial National Security Algorithm Suite 2.0 which lists the cryptographic algorithms that are expected to remain strong even with advances in quantum computing.
Cryptographic hash functions do not require keys. Hash functions generate a relatively small digest (hash value) from a (possibly) large input in a way that is fundamentally difficult to reverse (i.e., it is hard to find an input that will produce a given output). Hash functions are used as building blocks for key management, for example, Symmetric-key algorithms (sometimes known as secret-key algorithms) transform data in a way that is fundamentally difficult to undo without knowledge of a secret key. The key is "symmetric" because the same key is used for a cryptographic operation and its inverse (e.g., encryption and decryption).
Symmetric keys are often known by more than one entity; however, the key shall not be disclosed to entities that are not authorized access to the data protected by that algorithm and key. Symmetric key algorithms are used, for example, Asymmetric-key algorithms, commonly known as public-key algorithms, use two related keys (i.e., a key pair) to perform their functions: a public key and a private key. The public key may be known by anyone; the private key should be under the sole control of the entity that "owns" the key pair. Even though the public and private keys of a key pair are related, knowledge of the public key does not reveal the private key. Asymmetric algorithms are used, for example, Message Authentication Codes (MACs) provide data authentication and integrity. A MAC is a cryptographic checksum on the data that is used in order to provide assurance that the data has not changed and that the MAC was computed by the expected entity.
Although message integrity is often provided using non-cryptographic techniques known as error detection codes, these codes can be altered by an adversary to effect an action to the adversary's benefit. The use of an approved cryptographic mechanism, such as a MAC, can alleviate this problem. In addition, the MAC can provide a recipient with assurance that the originator of the data is a key holder (i.e., an entity authorized to have the key). MACs are often used to authenticate the originator to the recipient when only those two parties share the MAC key.
Digital signatures are used to provide authentication, integrity and non-repudiation . Digital signatures are used in conjunction with hash functions and are computed on data of any length (up to a limit that is determined by the hash function). FIPS186 specifies algorithms that are approved for the computation of digital signatures. Symmetric key-wrapping keys are used to encrypt other keys using symmetric-key algorithms. Key-wrapping keys are also known as key encrypting keys.
Review NIST SP 800-57 (Recommendation for Key Management) for recommended guidelines on key strength for specific algorithm implementations. Also, consider these best practices: Keys stored in memory for a long time can become "burned in". This can be mitigated by splitting the key into components that are frequently updated. NIST SP 800-57 ).
Loss or corruption of the memory media on which keys and/or certificates are stored, and recovery planning, according to NIST SP 800-57 . Plan for the recovery from possible corruption of the memory media necessary for key or certificate generation, registration, and/or distribution systems, subsystems, or components as recommended in NIST SP 800-57 .
Ephemeral keys can provide perfect forward secrecy protection, which means a compromise of the server's long term signing key does not compromise the confidentiality of past sessions. Refer to TLS cheat sheet . According to NIST, in general, a single key should be used for only one purpose (e.g., encryption, authentication, key wrapping, random number generation, or digital signatures).
According to NIST SP 800-133 , cryptographic modules are the set of hardware, software, and/or firmware that implements security functions (including cryptographic algorithms and key generation) and is contained within a cryptographic module boundary to provide protection of the keys. All cryptographic operations (such as key generation, encryption, decryption, and digital signing) should be performed inside the isolated cryptographic security module boundary so that plaintext key material is never exposed outside the module ( OWASP Application Security Verification Standard (ASVS) 5.0 §13.3.3 ). For higher-assurance deployments (such as OWASP ASVS 5.0 Level 3), applications should use hardware-backed modules, such as a Hardware Security Module (HSM) or Trusted Platform Module (TPM), to significantly reduce the risk of key extraction or compromise in software memory.
Cryptographic keys shall be generated within cryptographic module with at least a FIPS 140-2 or 140-3 compliance. For explanatory purposes, consider the cryptographic module in which a key is generated to be the key-generating module. Any random value required by the key-generating module shall be generated within that module; that is, the Random Bit Generator that generates the random value shall be implemented within cryptographic module with at least a FIPS 140-2 or 140-3 compliance that generates the key.
Hardware cryptographic modules are preferred over software cryptographic modules for protection. The generated keys shall be transported (when necessary) using secure channels and shall be used by their associated cryptographic algorithm within at least a FIPS 140-2 or 140-3 compliant cryptographic modules. For additional detail for the recommendations in this section refer to NIST Special Paper 800-133 .
For a more complete guide to storing sensitive information such as keys, see the Secrets Management Cheat Sheet . A cryptoperiod is the time span during which a specific cryptographic key is authorized for use. Limiting cryptoperiods restricts the amount of data protected by a single key and reduces the window of exposure if a key is compromised ( NIST SP 800-57 Part 1 Rev. 5 Section 5.3). For storage-level rotation fundamentals and criteria, see the Cryptographic Storage Cheat Sheet .
3. Software Implementation, Frameworks & Protocols Representative cryptoperiods vary depending on the algorithm, key strength, operational environment, threat model, and sensitivity of the protected data. Organizations should define cryptoperiods through risk assessment in accordance with NIST SP 800-57 Part 1 Rev. 5.
Data that has been encrypted with lost cryptographic keys will never be recovered. Therefore, it is essential that the application incorporate a secure key backup capability, especially for applications that support data at rest encryption for long-term data stores. When backing up keys, ensure that the database that is used to store the keys is encrypted using at least a FIPS 140-2 or 140-3 validated module. It is sometimes useful to escrow key material for use in investigations and for re-provisioning of key material to users in the event that the key is lost or corrupted.
Never escrow keys used for performing digital signatures, but consider the need to escrow keys that support encryption. Oftentimes, escrow can be performed by the Certificate Authority (CA) or key management system that provisions certificates and keys, however in some instances separate APIs must be implemented to allow the system to perform the escrow for the application.
Accountability involves the identification of those that have access to, or control of, cryptographic keys throughout their lifecycles. Accountability can be an effective tool to help prevent key compromises and to reduce the impact of compromises once they are detected. Enforce the principle of least privilege for all key and secret assets ( OWASP ASVS 5.0 §13.3.2 ). Access to cryptographic keys, key management interfaces, and secret material should be restricted strictly to authorized roles, services, and workloads with a verified operational need.
Although it is preferred that no humans are able to view keys, as a minimum, the key management system should account for all individuals who are able to view plaintext cryptographic keys. In addition, more sophisticated key-management systems may account for all individuals authorized to access or control any cryptographic keys, whether in plaintext or ciphertext form.
Certain principles have been found to be useful in enforcing the accountability of cryptographic keys. These principles might not apply to all systems or all types of keys. New technology developments and attacks should be taken into consideration. On a more frequent basis, the actions of the humans that use, operate and maintain the system should be reviewed to verify that the humans continue to follow established security procedures.
Strong cryptographic systems can be compromised by lax and inappropriate human actions. Highly unusual events should be noted and reviewed as possible indicators of attempted attacks on the system. A compromise-recovery plan is essential for restoring cryptographic security services in the event of a key compromise. A compromise-recovery plan shall be documented and easily accessible.
Destruction is the final state in the cryptographic key lifecycle. Key management policies should account for the lifecycle key states described in NIST SP 800-57 Part 1 Rev. 5 Section 7 (such as pre-activation, active, suspended, deactivated, compromised, and destroyed). Revoke compromised keys promptly and stop using them to protect new data. Retain only tightly controlled access needed for recovery or migration of previously protected data. Destroy all copies of secret and private keys, including backup, archived, escrowed, and memory copies, as soon as they are no longer needed for decryption or recovery and retention requirements are satisfied. Public verification keys may be retained to verify archived signatures ( NIST SP 800-57 Part 1 Rev. 5 Sections 7.5 and 8.3.4–8.3.5).
Use only reputable crypto libraries that are well maintained and updated, as well as tested and validated by third-party organizations (e.g., NIST / FIPS ). As digital transformation accelerates across industries, organizations rely more heavily on cryptographic keys to secure data and enable secure digital processes. Cryptographic keys form the backbone of security for encryption, digital signatures, and authentication. However, more is required than simply deploying the latest cryptographic algorithms. Organizations must have robust key management practices to protect sensitive data and systems.
This article provides a practical guide to implementing key management best practices. We’ll cover key management’s importance, challenges, and best practices with real-world examples, key management solutions, and a checklist summary. Key management refers to the comprehensive processes and infrastructure required to control cryptographic keys throughout their lifecycle. This includes key generation (creating new cryptographic keys using secure algorithms), key distribution (securely delivering keys to authorized entities), key use (employing keys for cryptographic operations like encryption), key storage (storing keys securely when not in use), key revocation (revoking compromised or obsolete keys), and key destruction (securely destroying keys at end of life).
Robust key management ensures keys remain confidential, available when needed, and cryptographically strong. Keys could be compromised, abused, or improperly tracked without proper controls. For example, weak key generation algorithms could produce predictable keys that are easy for attackers to crack. Insecure key storage, like unencrypted text files, leaves keys vulnerable to theft. Failing to revoke compromised keys promptly enables continued unauthorized decryption. Poor key management practices render encryption useless, leaving data exposed. That’s why standards bodies like NIST provide in-depth key management guidance .
The 2011 RSA breach exposed authentication that compromised millions of SecurID tokens. Hackers obtained cryptographic “seed” values RSA failed to properly secure on internal systems. This enabled the attackers to clone SecurID algorithms for two-factor authentication on banking, government and military networks. RSA did not adequately restrict access or encrypt the stolen SecurID seed database. The incident revealed severe implications of key management failures at a major security provider. It highlighted the need for access restrictions, network segmentation, and encryption to protect critical secrets.
Organizations should conduct in-depth evaluations of solutions against their security and operational requirements before selection. They should also regularly review the controls of providers like cloud services. Use this checklist of critical steps for implementing a robust key management strategy: Following these best practices throughout the key lifecycle can help secure your organization’s sensitive data and systems from compromise.
At SSL.com, we are devoted to assisting businesses in navigating this challenging environment because we recognize the value of sound key management procedures. To support your key management requirements and ensure the security and integrity of your digital assets, we provide solutions that are at the forefront of the industry. SSL.com is a global leader in cybersecurity, PKI and digital certificates. Sign up to receive the latest industry news, tips, and product announcements from SSL.com .
This website uses Google Analytics & Statcounter to collect anonymous information such as the number of visitors to the site, and the most popular pages. Stay informed about the latest best practices, reports, and solutions in cloud security with CSA research. Stay connected with the cloud security community by attending local events, workshops, and global CSA conferences.
Engage with industry leaders, gain new insights, and build valuable professional relationships—both virtually and in person. Join the countless professionals who have selected CSA for their training and certification needs. Stay informed with the latest in cloud security news - visit our blog to keep your competitive edge sharp. In the previous article of the Key Management Awareness series , we looked at how cryptographic key management evolved from the early days’ operational controls into formal governance Standards guided by NIST, ANSI, and later PCI SSC. As card payment networks expanded in the 1970s and 1980s, financial institutions quickly realized that proper key management has the same importance as cryptography used to secure systems and sensitive data. Nowadays, payment systems rely on Hardware Security Modules, distributed payment platforms, hybrid environments and cloud-based cryptographic services, however, the key management operational model still depends on the same principles that were formulated in the early days of cryptography. Below we will review those principles and explain why they are still relevant today.
4. Practical Deployment, Analysis & Case Studies PCI Standards, like PCI PIN, PCI DSS or PCI P2PE always required strong cryptography alongside secure key management. It is hard to imagine, but, after so many years, insecure key management brings the same risks no matter which technology or cryptographic algorithms are being used. Although the technologies used to manage cryptographic keys significantly improved, the underlying principles have remained the same. These are the principles: Fully understanding these principles is essential for clarifying the basics of key management.
Core Idea: Split knowledge ensures that no single individual possesses the complete cryptographic key. Instead, the key is divided into multiple components or shares, each controlled by a different authorized custodian. Only when these components are combined during an authorized process the cryptographic key can be reconstructed or loaded into a secure system. Why does this principle exist: The principle of split knowledge was introduced to address one of the most significant risks in cryptographic systems: insider compromise. If a single administrator could access or reconstruct a complete key independently, that individual could potentially decrypt sensitive data or authorize fraudulent transactions without detection. By dividing key material into separate components, split knowledge ensures that no single person can gain control of a cryptographic key.
Key components are typically distributed among multiple trusted custodians, each responsible for protecting their portion of the key. Core Idea: Dual control requires that two or more authorized individuals must participate in sensitive cryptographic operations. These operations may include generating keys, loading keys into devices, exporting key material, or destroying keys.
Why does this principle exist: dual control addresses the operational risk that a single individual could manipulate key management processes without an oversight. Even if an individual does not know the full key because of split knowledge, they might still attempt to alter system configurations, load unauthorized keys, or bypass security controls. Requiring multiple participants ensures that sensitive actions cannot be performed silently or without verification.
This principle ensures that critical actions remain observable and auditable and controlled by more than one person. As payment systems became more complex, the industry turned to specialized hardware for cryptographic protection. These Secure Cryptographic Devices (SCDs), like Hardware Security Modules (HSM), Key Loading Devices are designed to protect cryptographic keys and execute cryptographic functions only within the high secure trusted boundary of that device. If properly configured and secured, there is an assurance that cryptographic material managed by the SCD remains secure.
Why does this principle exist: In early computing systems, cryptographic keys were sometimes stored directly in the application memory or system files. This created opportunities for insiders, malware, or external attackers to extract sensitive key material. Secure cryptographic devices were introduced to mitigate this risk by ensuring that keys remain protected within tamper-resistant environments. SCDs are used extensively across payment environments to perform almost all cryptographic key operations, including: By isolating cryptographic operations within SCDs, organizations can significantly reduce the risk of cryptographic key material exposure.
Another important principle in secure key management is that cryptographic keys must exist only in approved forms. This principle governs how keys are stored, transmitted and loaded within secure environments. Why does this principle exist: If cryptographic keys are handled in plaintext form, they can be easily copied, intercepted, or accidentally exposed through system logs, backups, or memory dumps. Approved key forms ensure that keys remain protected even when they move between systems with different security levels. Examples of approved key forms include protection by the key with equivalent key strength, stored within the SCD, or split under two or more key components or shares.
These mechanisms allow keys to be securely transferred without exposing the underlying key material. Approved key forms ensure that even when keys are stored outside cryptographic devices or transmitted across networks, the key material remains protected and can only be accessed by authorized cryptographic systems. The principles we’ve reviewed have been used for decades to protect sensitive cryptographic key materials. But, even when organizations deploy secure cryptographic devices or enterprise key management platforms, those systems still depend on governance and operational controls implemented in the companies. Organizations must define a set of operational key management documented procedures in addition to the above key management principles: The principles of secure key management we’ve reviewed above are clear and widely accepted by the payment industry. The PCI Security Standards Council, together with payment industry participants, has spent decades embedding these principles into PCI Standards and ensuring they are consistently reflected across different domains of the key management. However, while these principles are well defined, their practical implementation is often more complex than it initially appears.
Based on our experience as a PCI Assessor, the struggle with proper key management is clearly visible. We regularly observe non-compliance and control failures related to cryptographic key management, even in environments that have otherwise mature information security management system. These issues often have the objective reasons: complexity of modern cryptography infrastructures, unclear ownership of key management processes in hybrid and multi-domain environments, shared key management responsibilities spread across vendors and third-party service providers.
In the next article, we will explore these challenges in more detail. We will examine common findings observed during PCI assessments, typical mistakes organizations make when implementing key management controls and provide practical insight into how organizations can improve their key management practices with the upcoming PCI KMO Standard. Our PCI Assessor team provides the technical guidance needed to secure your environment while minimizing your compliance overhead.
Head of PCI PIN and PCI 3DS Practice at Foregenix. He is an experienced professional in information security and payment security, who has more than 17 years of a strong track record in the financial services security industry and compliance. His expertise spans across: - Payment & data security for both traditional and emerging payment instruments (mobile wallets, real-time payments, digital assets, and tokenized payment solutions). - PCI Security Standards family: PCI DSS, P2PE, PIN Security, PCI 3DS, PCI TSP. - ISO 27001 & Cybersecurity Governance in banking and payment ecosystems. - Risk & Compliance Management across regulated financial environments.
Don't miss out on our insights! Receive exclusive updates and invaluable cybersecurity advice from our experts directly in your inbox Security never stops. Get the most up-to-date information by subscribing to the Foregenix blog. This is a potential security issue, you are being redirected to https://csrc.nist.gov .
Official websites use .gov A .gov website belongs to an official government organization in the United States. Secure .gov websites use HTTPS A lock ( ) or https:// means you’ve safely connected to the .gov website. Share sensitive information only on official, secure websites. The following publications provide general key management guidance: Recommendation for Key Management December 5, 2025: An initial public draft of SP 800-57 Part 1 Revision 6 is available for comment through February 5, 2026. SP 800-57 Part 1 Revision 5 - General This Recommendation provides cryptographic key-management guidance. It consists of three parts.
Part 1 provides general guidance and best practices for the management of cryptographic keying material, including definitions of the security services that may be provided when using cryptography and the algorithms and key types that may be employed, specifications of the protection that each type of key and other cryptographic information requires and methods for providing this protection, discussions about the functions involved in key management, and discussions about a variety of key-management issues to be addressed when using cryptography. Part 2 provides guidance on policy and security planning requirements for U.S. Government agencies. Part 3 provides guidance when using the cryptographic features of current systems. SP 800-57 Part 2, Revision 1 , Best Practices for Key Management Organizations This recommendation provides guidance on how organizations should manage cryptographic keys in accordance with the federal key management policies and best practices described in SP 800-57 Part 1. This revision is consistent with the Cybersecurity Enhancement Act of 2014 and provides direct cybersecurity support for private-sector key management as well as government-focused guidance consistent with OMB Circular A-130 . Section 2 has been updated to introduce a more comprehensive set of key management concepts that should be addressed in key management policies, practice statements, and planning documents by any organization that uses cryptography to protect its information. This revision also broadens the applicability of its recommendations to cover both centralized and decentralized key management structures. Finally, this document’s original centralized infrastructure example has been replaced by explanatory material that reflects SP 800-130 and SP 800-152 and applies to both centralized and decentralized key management structures. SP 800-57 Part 3 , Application-Specific Key Management Guidance NIST Special Publication 800-57 provides cryptographic key management guidance. It consists of three parts. Part 1 provides general guidance and best practices for the management of cryptographic keying material. Part 2 provides guidance on policy and security planning requirements for U.S. government agencies. Finally, Part 3 provides guidance when using the cryptographic features of current systems. Key Management Transitions October 21, 2024 SP 800-131A Revision 3 , Transitioning the Use of Cryptographic Algorithms and Key Lengths NIST released an initial public draft (ipd) revision for public comment. The final version is currently being reviewed internally. SP 800-131A Revision 2 , Transitioning the Use of Cryptographic Algorithms and Key Lengths Provides guidance for transitions to the use of stronger cryptographic keys and more robust algorithms by federal agencies when protecting sensitive, but unclassified information.
SP 800-131A Revision 3 , Transitioning the Use of Cryptographic Algorithms and Key Lengths NIST released an initial public draft (ipd) revision for public comment. The final version is currently being reviewed internally. SP 800-131A Revision 2 , Transitioning the Use of Cryptographic Algorithms and Key Lengths Provides guidance for transitions to the use of stronger cryptographic keys and more robust algorithms by federal agencies when protecting sensitive, but unclassified information.
5. Performance Evaluation & Extended Technical Observations Cryptographic Standards and Guidelines Digital Signatures Message Authentication Codes Cryptography forms the foundation of enterprise security, yet over 70% of encryption vulnerabilities stem from implementation flaws rather than weaknesses in underlying algorithms. With NIST finalizing post-quantum cryptography standards in August 2024 and mandating deprecation of quantum-vulnerable algorithms by 2035, organizations face significant cryptographic transitions ahead.
This guide covers cryptographic fundamentals, key management infrastructure, PKI implementation, secrets management, and the post-quantum transition. Symmetric encryption uses a single shared secret key for both encryption and decryption. It is significantly faster than asymmetric alternatives, making it ideal for encrypting large data volumes at rest, VPN tunnels and secure network communications, real-time communications and streaming, disk and volume encryption, and banking and financial transaction processing.
Asymmetric encryption uses a key pair (public and private) and is best suited for digital signatures and authentication, SSL/TLS certificate-based communications, secure key exchange protocols, email encryption via S/MIME and PGP, cryptocurrency transactions, and identity verification. Modern systems use a hybrid approach where asymmetric encryption handles secure key exchange during TLS handshake, followed by symmetric encryption for subsequent data communications. This is the backbone of all secure web communication.
For symmetric encryption, AES-256 is the recommended standard for most applications. AES-128 and AES-192 are acceptable for less critical applications, though AES-192 lacks optimization on some processors. For asymmetric encryption and signatures, RSA-2048 provides minimum acceptable security through 2030 for compatibility. RSA-3072 and RSA-4096 are preferred for deployments beyond 2030 and high-value assets. ECDSA P-256 provides approximately 128-bit security suitable for most cases. ECDSA P-384 provides approximately 192-bit security for high-value or long-life signatures. Ed25519 is recommended for SSH keys and modern stacks supporting it.
Practical recommendations include ECDSA P-256 or Ed25519 for TLS web servers while keeping RSA-2048 for compatibility, RSA-3072 or ECDSA P-256 for code signing, and Ed25519 or ECDSA P-256 for SSH keys. For hash functions, SHA-256 is standard for most hashing needs. SHA-384 and SHA-512 serve higher security requirements. SHA-3 is the NIST-standardized alternative to the SHA-2 family.
NIST finalized standards in August 2024 including ML-KEM (FIPS 203) for Module-Lattice-Based Key-Encapsulation Mechanism formerly known as CRYSTALS-Kyber, ML-DSA (FIPS 204) for Module-Lattice-Based Digital Signature Algorithm formerly CRYSTALS-Dilithium, and SLH-DSA (FIPS 205) for Stateless Hash-Based Digital Signature Algorithm formerly SPHINCS+. HQC was selected as backup for general encryption in March 2025 with a draft standard expected in 2026.
CNSA 2.0 requirements mandate ML-KEM-1024 parameter set for all classification levels. For anything that must stay secure beyond approximately 2035, implement a hybrid setup combining traditional algorithms with PQC. The transition timeline under NIST IR 8547 mandates deprecation of quantum-vulnerable algorithms by 2035. First post-quantum certificates are expected in 2026. As of mid-2024, over 16% of human-generated requests to major CDNs are protected with post-quantum key agreement.
Current adoption includes Apple iMessage and Zoom implementing ML-KEM, Chrome rolling out hybrid KEM scheme support, and Cloudflare progressively enabling ML-KEM. Cloud HSMs free up security resources from hardware maintenance and shift costs from CapEx to OpEx through subscription-based pricing. They are attractive for multi-cloud and hybrid environments and represent the fastest-growing segment at 32.7% CAGR.
On-premises HSMs are preferable for total control over the HSM environment and encryption keys. They are required by certain organizations including financial services, payment processors, and government agencies. On-premises solutions are projected to generate 71% of total service revenue by 2026 and are required for FIPS 140-2 Level 3 and PCI PIN Security Standard compliance.
Technology focus for 2025-2026 includes transition from FIPS 140-2 to FIPS 140-3 certification requirements. AWS KMS provides primarily symmetric 256-bit AES keys, regional service with multi-region key support, pay-as-you-go pricing at $1 per key per month, CloudHSM integration, and automatic annual rotation. Azure Key Vault provides asymmetric public and private keys, global service with regional options, subscription-based pricing, native HSM support, and rotation policies with notifications.
GCP Cloud KMS provides CMEK support, regional service, subscription-based pricing, Cloud HSM integration, and configurable rotation schedules. The seven stages of key lifecycle include generation using cryptographically secure random number generators in secure controlled environments, distribution through secure channels never transmitting keys in plaintext, storage with encrypted storage and access controls preferably in HSMs, usage with defined cryptoperiods and authorized use cases, backup and recovery with secure procedures and geographic distribution, rotation automated every 12 months or sooner for high-risk environments in compliance with PCI DSS v4.0, and destruction through cryptographic erasure and physical destruction when required.
Best practices include setting explicit key expiry dates to enforce rotation, automating rotation to reduce human error, and implementing prompt revocation if a key is compromised. Essential elements include documentation with step-by-step processes meeting WebTrust, PCI-DSS, and FIPS 140-2/3 requirements. Separation of duties requires master keys composed of at least two parts each owned by different individuals.
Multi-party control ensures no single individual has direct HSM access. Real-time logging requires a designated scribe to record every action. Video recording captures the complete ceremony for compliance. Physical verification includes verifying HSM packages for tampering and recording serial numbers. Witness signatures require all actions to be signed by witnesses and officers.
Two-tier architecture is most common. The Root CA sits at top of trust hierarchy, kept offline in a highly secure environment as a standalone system not domain-joined, powered on only to issue subordinate CA certificates. The Issuing CA or Subordinate CA is kept online to issue end-entity certificates, typically an enterprise CA integrated with Active Directory. Multi-tier architecture allows deployment of additional Intermediate CAs for different teams, geographies, or use cases. The Root CA stays offline while intermediate CAs handle distribution.
Cryptographic standards recommend RSA-4096 or post-quantum cryptographic algorithms for CA certificates. Best practice is to renew CA certificates when half of the validity period expires. HSMs should store Root CA private keys and optionally Intermediate CA keys. Key activities include automated certificate discovery and inventory, expiration monitoring and alerting, automated renewal workflows, revocation management through CRL and OCSP, and policy enforcement.
Major 2025-2026 changes include RFC 6962 sunset with Let’s Encrypt making RFC 6962 logs read-only on November 30, 2025 and full shutdown on February 28, 2026. Static CT API migration will be completed by Chrome by end of 2025. Firefox CT requirements as of February 2025 with Firefox 135 require CT for all certificates from Mozilla Root CA Program. New log implementations include Rennet, Gouda, Lipase, and Halloumi using TesseraCT architecture.
Future considerations include shorter certificate lifetimes and larger post-quantum certificates placing significantly more load on the CT ecosystem. ACME (Automatic Certificate Management Environment) enables automatic browser-trusted certificate acquisition. Web servers with built-in ACME support include Caddy, Traefik Proxy, Nginx as of August 2025, and Apache HTTP Server 2.4.30+.
For cert-manager integration in Kubernetes, ACME Issuer represents a single account registered with ACME CA server and automatically generates private key for ACME server identification. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Electronic%20Key%20Management%20System • https://en.wikipedia.org/wiki/Secure%20Shell • https://en.wikipedia.org/wiki/Key%20management • https://cheatsheetseries.owasp.org/cheatsheets/Key_Management_Cheat_Sheet.html • https://www.ssl.com/article/key-management-best-practices-a-practical-guide/ • https://cloudsecurityalliance.org/artifacts/key-management-lifecycle-best-practices • https://www.foregenix.com/blog/the-principles-of-secure-key-management • https://csrc.nist.gov/Projects/Key-Management/Key-Management-Guidelines • https://uinat.com/guides/cryptography-key-management-guide/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Secure Key Management And Distribution System Project.
[*] Metasploit Scan Running on Target Subnet for Secure Key Management And Distribution System Project... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |