Complete Technical Paper Content — Secure Messaging Application Using End To End Encryption
Overview & System Context
Secure Messaging Application Using End To End Encryption: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9511 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background End-to-end encryption (E2EE) is a method of implementing a secure communication system where only the sender and intended recipients can read the messages. No one else, including the system provider, telecom providers, Internet providers or malicious actors, can access the cryptographic keys needed to read or send messages. End-to-end encryption prevents data from being read or secretly modified, except by the sender and intended recipients. In many applications, messages are relayed from a sender to some recipients by a service provider. In an E2EE-enabled service, messages are encrypted on the sender's device such that no third party, including the service provider, has the means to decrypt them. The recipients retrieve encrypted messages and decrypt them independently on their own devices. Since third parties cannot decrypt the data being communicated or stored, services with E2EE are better at protecting user data from data breaches and espionage. Computer security experts, digital freedom organizations, and human rights activists advocate for the use of E2EE due to its security and privacy benefits, including its ability to resist mass surveillance. Popular messaging apps like WhatsApp, iMessage, Facebook Messenger and Signal use end-to-end encryption for chat messages, with some also supporting E2EE of voice and video calls. As of May 2025, WhatsApp is the most widely used E2EE messaging service, with over 3 billion users. Meanwhile, Signal with an estimated 70 million users, is regarded as the current gold standard in secure messaging by cryptographers, protestors and journalists. Since end-to-end encrypted services cannot offer decrypted messages in response to government requests, the proliferation of E2EE has been met with controversy. Around the world, governments, law enforcement agencies and child protection groups have expressed concerns over its impact on criminal investigations. As of 2025, some governments have successfully passed legislation targeting E2EE, such as Australia's Telecommunications and Other Legislation Amendment Act (2018) and the Online Safety Act (2023) in the UK. Other attempts at restricting E2EE include the EARN IT Act in the US and the Child Sexual Abuse Regulation in the EU.[1] Nevertheless, some government bodies such as the UK's Information Commissioner's Office and the US's Cybersecurity and Infrastructure Security Agency (CISA) have argued for the use of E2EE, with Jeff Greene of the CISA advising that "encryption is your friend" following the discovery of the Salt Typhoon espionage campaign in 2024.
In 2022, Facebook Messenger came under scrutiny because the messages between a mother and daughter in Nebraska were used to seek criminal charges in an abortion-related case against both of them. The daughter told the police that she had a miscarriage and tried to search for the date of her miscarriage in her Messenger app. Police suspected there could be more information within the messages and obtained and served a warrant against Facebook to gain access. The messages allegedly mentioned the mother obtaining abortion pills for her daughter and then burning the evidence. While E2EE can offer privacy benefits that make it desirable in consumer-grade services, many businesses have to balance these benefits with their regulatory requirements. For example, many organizations are subject to mandates that require them to be able to decrypt any communication between their employees or between their employees and third parties. This might be needed for archival purposes, for inspection by Data Loss Prevention (DLP) systems, for litigation-related eDiscovery or for detection of malware and other threats in the data streams. For this reason, some enterprise-focused communications and information protection systems might implement encryption in a way that ensures all transmissions are encrypted with the encryption being terminated at their internal systems (on-premises or cloud-based) so they can have access to the information for inspection and processing.
Most end-to-end encryption protocols include some form of endpoint authentication specifically to prevent MITM attacks. For example, one could rely on certification authorities or a web of trust. An alternative technique is to generate cryptographic hashes (fingerprints) based on the communicating users' public keys or shared secret keys. The parties compare their fingerprints using an outside (out-of-band) communication channel that guarantees integrity and authenticity of communication (but not necessarily secrecy), before starting their conversation. If the fingerprints match, there is, in theory, no man in the middle. When displayed for human inspection, fingerprints usually use some form of binary-to-text encoding.
These strings are then formatted into groups of characters for readability. Some clients instead display a natural language representation of the fingerprint. As the approach consists of a one-to-one mapping between fingerprint blocks and words, there is no loss in entropy. The protocol may choose to display words in the user's native (system) language. This can, however, make cross-language comparisons prone to errors. In order to improve localization, some protocols have chosen to display fingerprints as base 10 strings instead of more error prone hexadecimal or natural language strings. Modern messaging applications can also display fingerprints as QR codes that users can scan off each other's devices.
Email encryption is encryption of email messages to protect the content from being read by entities other than the intended recipients. Email encryption may also include authentication. Email is prone to the disclosure of information. Although many emails are encrypted during transmission, they are frequently stored in plaintext, potentially exposing them to unauthorized access by third parties, including email service providers. By default, popular email services such as Gmail and Outlook do not enable end-to-end encryption. Utilizing certain available tools, unauthorized individuals may access and read the email content. Email encryption can rely on public-key cryptography, in which users can each publish a public key that others can use to encrypt messages to them, while keeping secret a private key they can use to decrypt such messages or to digitally encrypt and sign messages they send.
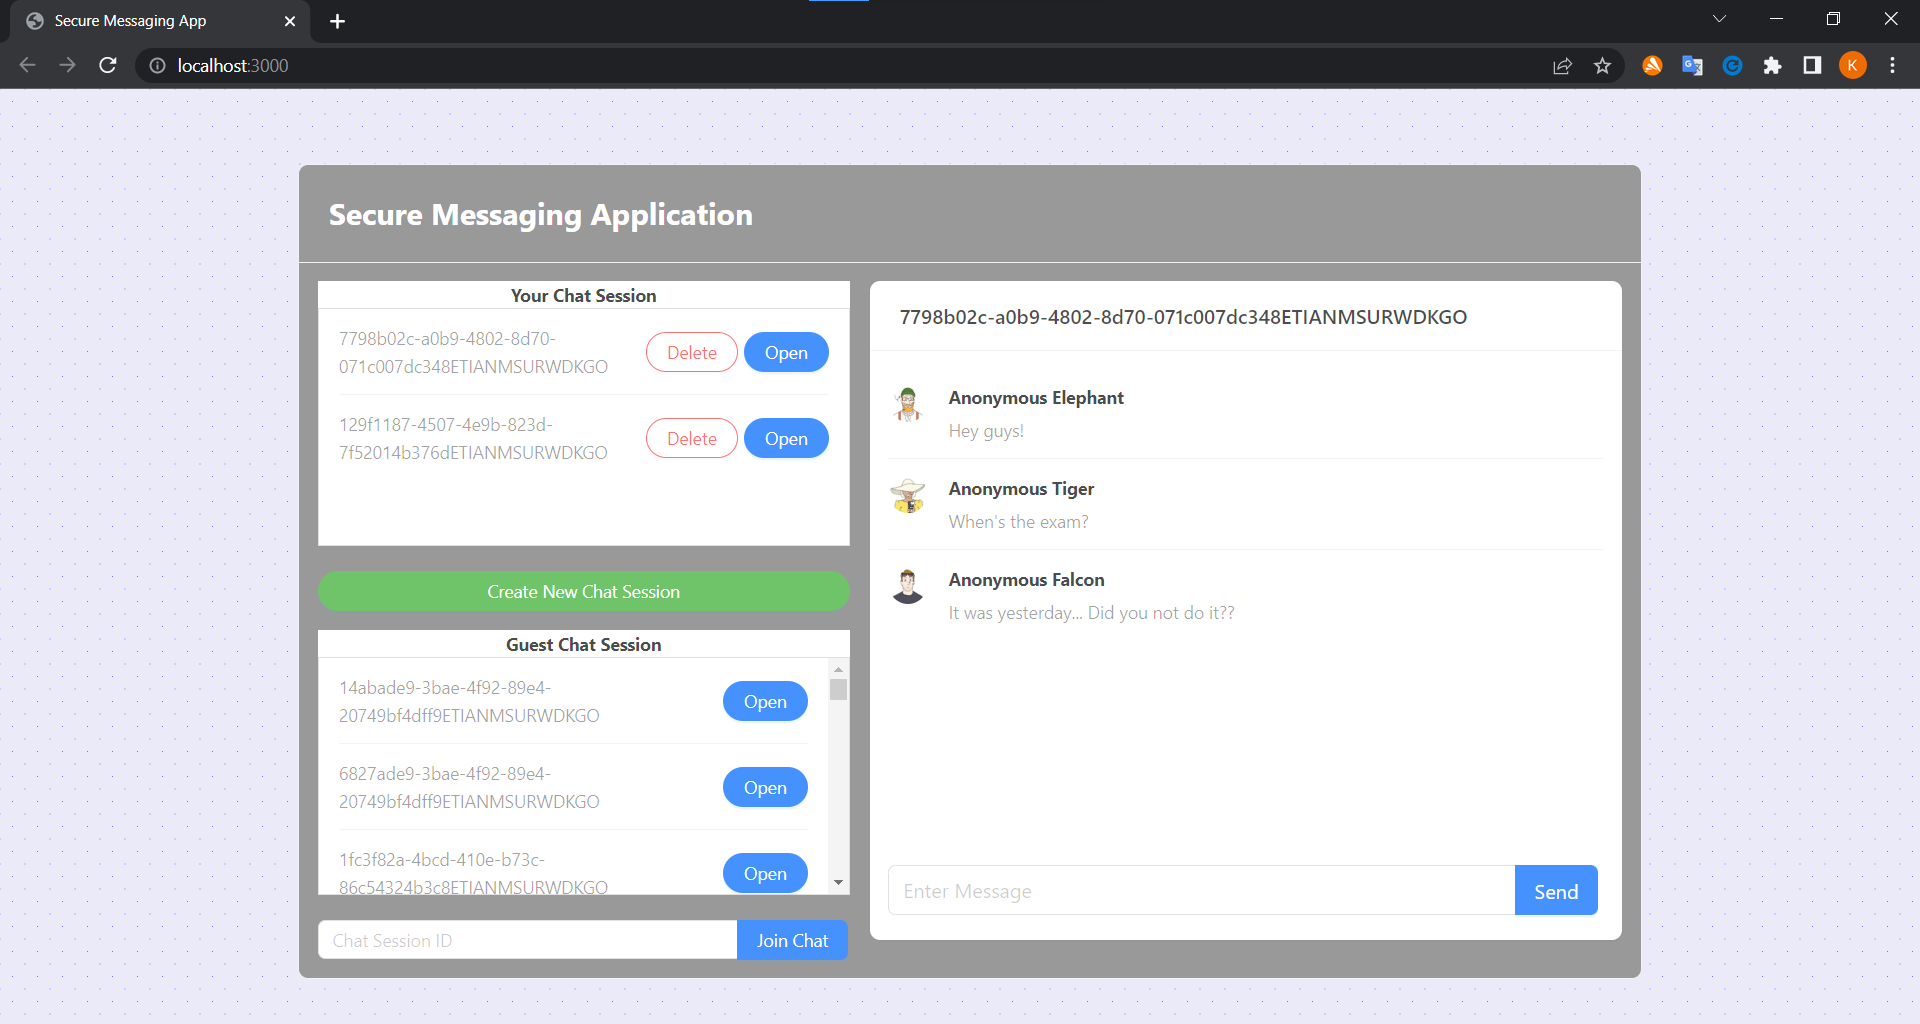
Figure 1: GitHub - kienmarkdo/Secure-Messaging-Application: A secure messaging ... Bitmessage GNU Privacy Guard (GPG) Pretty Good Privacy (PGP) S/MIME OpenPGP is a data encryption standard that allows end-users to encrypt the email contents. There are various software and email-client plugins that allow users to encrypt the message using the recipient's public key before sending it. At its core, OpenPGP uses a Public Key Cryptography scheme where each email address is associated with a public/private key pair. OpenPGP provides a way for the end users to encrypt the email without any support from the server and be sure that only the intended recipient can read it. However, there are usability issues with OpenPGP — it requires users to set up public/private key pairs and make the public keys available widely. Also, it protects only the content of the email, and not metadata — an untrusted party can still observe who sent an email to whom. A general downside of end to end encryption schemes—where the server does not have decryption keys—is that it makes server side search almost impossible, thus impacting usability. The content of an email can also be end-to-end encrypted by putting it in an encrypted file (using any kind of file encryption tool) and sending that encrypted file as an email attachment.
The Signal Protocol (formerly known as the TextSecure Protocol) is a non-federated cryptographic protocol that provides end-to-end encryption for voice and instant messaging conversations. The protocol was developed by Open Whisper Systems in 2013 and was introduced in the open-source TextSecure app, which later became Signal. Several closed-source applications have implemented the protocol, such as WhatsApp, which is said to encrypt the conversations of "more than a billion people worldwide" or Google who provides end-to-end encryption by default to all RCS-based conversations between users of their Google Messages app for one-to-one conversations. Facebook Messenger also say they offer the protocol for optional "Secret Conversations", as did Skype for its "Private Conversations". The protocol combines the Double Ratchet Algorithm, prekeys (i.e., one-time ephemeral public keys that have been uploaded in advance to a central server), and key agreement protocols including the original triple elliptic-curve Diffie–Hellman (3-DH) handshake and the post-quantum PQXDH protocol. Current Signal specifications model message encryption as authenticated encryption with associated data (AEAD), with recommended constructions including SIV-style AEAD schemes or a composition of AES-256 in CBC mode with HMAC.
libsignal-protocol-c: A library written in C with additional licensing permissions for Apple's App Store. libsignal-protocol-java: A library written in Java. libsignal-protocol-javascript: A library written in JavaScript. There are also alternative libraries written by third-parties in other languages, such as TypeScript. Most applications that describe themselves as encrypted are not end-to-end encrypted. They encrypt data in transit using TLS and encrypt data at rest using a storage-layer key managed by the cloud provider. Both are important and neither is E2EE. In a genuine end-to-end encrypted system, the server processes ciphertext it cannot decrypt. Only the communicating parties hold the keys, and a breach of the server infrastructure exposes no readable message content.
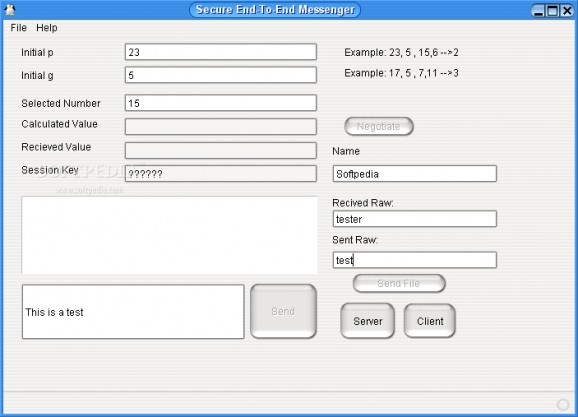
Figure 2: Secure End-To-End Messenger - Download - Softpedia The gap between these two models matters enormously when the threat model includes a malicious insider, a compromised cloud account, or a government subpoena served to the infrastructure provider. Signal, WhatsApp, and ProtonMail built their user trust on this distinction. As engineers building applications that handle sensitive personal, financial, or healthcare data, understanding how E2EE is actually implemented, what it costs operationally, and where it breaks down in practice is becoming a baseline competency rather than a specialist niche. For teams at Askan working on security-critical application architecture , E2EE implementation decisions come up regularly as product teams handle increasing volumes of sensitive user data.
End-to-end encryption means that data is encrypted on the sender’s device and decrypted only on the recipient’s device. The server in the middle, whether that is a cloud backend, a message relay, or a sync service, handles encrypted data that it cannot read. The encryption keys never leave the endpoint devices in plaintext form. This is different from transport encryption, which protects data between a client and a server but leaves the server holding plaintext once the TLS connection terminates. It is also different from server-side encryption at rest, where the server encrypts data before writing it to disk but holds or has access to the keys used for encryption. In both of those models, a server compromise or a key disclosure means your data is readable. In a correctly implemented E2EE model, it does not.
That table is worth studying carefully before designing anything. A common mistake in early E2EE implementations is to have the client perform the encryption operation but then transmit the key to the server for storage. That is client-side encryption with server-managed keys, which defeats the purpose entirely. Figure 3: Introducing a Decentralized End-to-End Encrypted Messaging App ...
The Signal Protocol, developed by Open Whisper Systems and now maintained by the Signal Foundation, is the most widely deployed E2EE messaging protocol in existence. It underpins Signal, WhatsApp, Google Messages, and Meta’s Messenger encrypted mode. Understanding its design is the starting point for any serious E2EE implementation because it solves problems that a naive implementation will miss. The Signal Protocol documentation is publicly available and is the most readable technical reference for the cryptographic primitives involved.
The protocol achieves several properties simultaneously that make it unusually strong. Forward secrecy means that a compromise of the current session key does not expose past messages, because each message is encrypted with a new key derived from a ratcheting mechanism that advances with every message sent and received. Break-in recovery means that if a session key is compromised at a point in time, future messages re-establish security automatically as the ratchet continues to advance. Deniability means that anyone can generate a transcript that looks like a valid Signal conversation, which means a leaked message transcript cannot be cryptographically proven to be authentic.
These properties are the result of composing three mechanisms: the X3DH (Extended Triple Diffie-Hellman) key agreement protocol for session establishment, the Double Ratchet Algorithm for ongoing message encryption with forward secrecy, and the Sealed Sender mechanism to protect message metadata. End-to-End Encryption Implementation Guide: Patterns, Key Management, and Common Mistakes to Avoid The cryptographic primitives in most E2EE implementations are not the source of failure. Elliptic curve Diffie-Hellman key exchange, AES-256-GCM for symmetric encryption, and HKDF for key derivation are well-understood and well-tested in mature libraries. The failure almost always happens in key management: how keys are generated, stored, distributed, rotated, and recovered.
Cryptographic key pairs must be generated using a cryptographically secure random number generator on the user’s device, not on the server. A server that generates key pairs and sends them to clients is a server that knows the private keys, which is the same as no E2EE. On mobile platforms, iOS provides SecRandomCopyBytes and Android provides java.security.SecureRandom, both of which draw from the device’s hardware-backed entropy source. On the web, the Web Crypto API’s crypto.getRandomValues is the correct interface, available in all modern browsers.
Private keys must be stored in hardware-backed secure storage where available. On iOS, keys stored in the Secure Enclave are protected by the device’s dedicated security chip and cannot be exported even by the application that created them. On Android, keys stored in the Android Keystore with hardware-backed attestation provide equivalent protection on devices with a dedicated hardware security module. On the web platform, there is no equivalent to hardware-backed key storage; keys stored in IndexedDB are protected only by the browser’s process isolation and the operating system’s user account protections.
The absence of hardware-backed key storage on web is one of the reasons that browser-based E2EE applications have a weaker security story than native applications for the same threat model. Teams building E2EE for a web-first audience should document this limitation honestly and consider whether the security level is sufficient for their specific threat model. Key backup is the most difficult design problem in E2EE. If a user’s private keys exist only on their device and the device is lost, stolen, or factory-reset, all their encrypted data becomes permanently unreadable. For a messaging application this means losing message history. For a document management application it means losing access to documents. Neither outcome is acceptable to most users.
The standard approaches to key backup create tension with the E2EE guarantee in different ways. Encrypted key backup to the server, where the key material is encrypted with a passphrase or a recovery code that only the user knows before being stored server-side, is the approach used by Signal and WhatsApp. The server stores ciphertext it cannot decrypt. The user’s backup passphrase is the single point of recovery. If the passphrase is lost, the backup is unrecoverable. This is a genuine security property rather than a limitation, but it requires users to understand and reliably retain their recovery credentials, which consumer applications struggle to achieve without introducing support overhead.
A minimal but correct E2EE messaging implementation requires the following steps, each of which must be implemented without shortcuts. This sequence is non-trivial to implement correctly from scratch. Teams that do not have dedicated cryptography engineering experience should use an existing implementation of the Signal Protocol rather than building from primitives. The libsignal library maintained by the Signal Foundation is available for Java, Swift, TypeScript, and Rust, and is the reference implementation that WhatsApp and Signal use in production.
Messaging is the most common E2EE use case but not the only one. Document management, file sync, and collaborative editing all have E2EE variants that handle a different set of design challenges. In a messaging system, each conversation has a small number of participants whose keys are known at session establishment time. In a document system, a file may need to be shared with a variable set of users who may join and leave over time, and the same file may need to be accessible from multiple devices belonging to the same user. The key management problem is more complex.
The standard approach for encrypted file storage is to encrypt each file with a randomly generated symmetric key, called the content encryption key or CEK, and then encrypt the CEK separately for each authorised user using their public key. The server stores the encrypted file content and the encrypted CEK for each user. No user’s private key touches the server. When a new user is granted access to a file, the sharing user decrypts the CEK with their own private key, re-encrypts it with the new user’s public key, and uploads the new encrypted CEK. When a user’s access is revoked, their encrypted CEK is deleted and the file is re-encrypted with a new CEK that is distributed only to the remaining authorised users.
Proton Drive and Tresorit are the most mature examples of this pattern in consumer products. Both publish technical documentation of their encryption architecture that is worth reviewing. Proton’s security model documentation covers the key hierarchy, the sharing mechanism, and the server-side data model in enough detail to inform the design of a similar system without copying their specific implementation.
End-to-End Encryption Implementation Guide: Patterns, Key Management, and Common Mistakes to Avoid E2EE implementations fail in predictable ways. The following mistakes appear repeatedly across security audits of applications that claim end-to-end encryption. Message content encrypted with a strong E2EE protocol still leaks information if message metadata is transmitted in plaintext.
Knowing that user A sent 47 messages to user B between 11 pm and 2 am on a specific date is meaningful even without knowing the content of those messages. A complete E2EE implementation considers which metadata fields need protection and uses techniques such as sealed sender (hiding the message origin from the relay server) or padding (obscuring message length patterns) where the metadata sensitivity justifies the overhead.
2. System Architecture & Core Working Principles AES-GCM requires a unique nonce for every encryption operation using the same key. Reusing a nonce with the same key under AES-GCM is catastrophic: it exposes both the keystream and the authentication tag, allowing an attacker to forge ciphertexts. The correct practice is to generate nonces randomly using a CSPRNG and to treat the nonce as a system-level constraint that must be enforced, not a suggestion. The Double Ratchet Algorithm handles this correctly by deriving a new key for each message, but implementations that roll their own symmetric encryption layer frequently get nonce management wrong.
Diffie-Hellman key exchange is vulnerable to man-in-the-middle attacks if the authenticity of the public keys exchanged is not verified. If the server can substitute its own public key for user B’s public key when user A fetches it, user A establishes a session with the server rather than with user B. The solution is a key verification mechanism: Signal’s safety numbers, WhatsApp’s security codes, and PGP’s web of trust are all approaches to this problem. For consumer applications, the UX challenge is getting users to perform key verification without treating it as an optional step that nobody does.
A system that correctly encrypts all user data and then logs decrypted content to a centralised logging platform, sends decrypted message previews to a push notification service, or passes cleartext through an analytics pipeline has defeated its own E2EE implementation at the application layer. Every data flow that touches user content must be audited to verify that plaintext does not exit the encryption boundary through an ancillary system. Push notifications are a particularly common leak vector: a push notification that carries the message preview text sends that preview through Apple’s or Google’s push infrastructure in plaintext, regardless of how strong the E2EE implementation is for the message transport itself.
End-to-end encryption creates a specific regulatory tension in several jurisdictions. Regulators in the EU, UK, India, and Australia have at various times proposed or implemented requirements that would require messaging platforms to provide access to message content for law enforcement purposes, which is technically incompatible with strong E2EE. Engineers building E2EE applications need to be aware of the regulatory environment in the markets they operate in and should work with legal counsel on whether client-side scanning requirements, key escrow mandates, or other technical measures apply to their product category.
For business applications handling employee communications or customer data, E2EE implementation also interacts with data retention requirements. A GDPR right-to-erasure request requires that all personal data belonging to a data subject is deleted. In an E2EE system where the server holds ciphertext but not keys, fulfilling an erasure request can be achieved by deleting the encrypted content and destroying the key material, which renders the content permanently unreadable. This approach, called cryptographic erasure, is accepted as an equivalent to deletion in most data protection frameworks, but legal confirmation for the specific jurisdiction is necessary before relying on it.
Standard application testing approaches are insufficient for E2EE implementations. A test that verifies a message is sent and received correctly does not verify that the server cannot decrypt it. Testing the encryption boundary requires specific approaches. The most direct test for server-side opacity is an adversarial database inspection test: after a message is sent through the system, inspect the raw data stored in the database and any logs generated during the request. If any plaintext content from the message appears anywhere in those stores, the E2EE boundary has a leak. This test should be part of the automated test suite and should run on every build, not just during security reviews.
Formal cryptographic audits by specialist security firms are appropriate before launching an E2EE application that handles sensitive data. The audit should cover the key generation and storage implementation, the protocol implementation against the specification, the network traffic under a proxy to verify no unexpected plaintext is transmitted, and the backup and recovery flow. NCC Group, Trail of Bits, and Cure53 are among the firms that have published E2EE audit reports, and reviewing their past public reports on similar applications gives a useful picture of what reviewers look for. Askan’s security engineering practice includes architecture review for E2EE implementations as part of pre-launch security assessments for teams that need specialist input before releasing a security-critical product.
Ask a developer why a page feels slow, and the honest answer is often sitting right in the middle of it. A single unoptimised... Microservices have dominated architecture conversations for years, to the point where choosing a monolith can feel like admitting you're behind the times. In practice,... Magento has a reputation for being resource-heavy, and while some of that is inherent to running a full-featured enterprise commerce platform, a large share...
Ask a developer why a page feels slow, and the honest answer is often sitting right in the middle of it. A single unoptimised... Microservices have dominated architecture conversations for years, to the point where choosing a monolith can feel like admitting you're behind the times. In practice,... Magento has a reputation for being resource-heavy, and while some of that is inherent to running a full-featured enterprise commerce platform, a large share...
A brief introduction to myself: I have been a freelance web developer for approximately 1.5 years. I have never considered writing a HLD or a LLD. Instead, I have focused on developing applications based on the specific requirements of my clients. As I aspire to transition into a corporate environment, I am eager to enhance my skills and acquire new knowledge. Client Requirements : A E2EE Web Based Chat App. Scalable up to 1000 Concurrent users at any given time.
The app majorly consists of a Frontend(react), Backend(Node), Database(Redis and SQL). Building a scalable and secure End-to-End Encrypted Messaging Application requires a thoughtful balance between performance, usability, and security. Through this High-Level Design, I aimed to demonstrate the architecture and flow of a modern messaging system capable of handling real-time communication while ensuring user privacy.
This project not only showcases key technical skills like React for frontend, Node.js for backend, and PostgreSQL/Redis for data management, but also highlights the importance of designing for scalability and reliability. If you’re a developer or enthusiast interested in creating robust systems or exploring more about real-time communication architectures, I hope this article provided valuable insights.
I’d love to hear your thoughts or feedback! Feel free to connect, share your ideas, or ask questions in the comments section. Let’s keep learning and building! Every project is a step closer to mastering the craft of software development. This one taught me the importance of balancing functionality with scalability, and I look forward to building even more complex systems in the future! In modern application security, protecting data in transit (via TLS) and at rest (via database encryption) is no longer sufficient for high-privacy environments like chat or financial communication. If your messaging server is compromised, an attacker can access the plaintext database or intercept active messages.
End-to-End Encryption (E2EE) guarantees that a message is encrypted directly on the sender’s local device and decrypted only on the recipient’s device. The intermediate servers act purely as blind relays, handling routing metadata but unable to read a single byte of message content. In this deep dive, we’ll examine the cryptographic architecture behind E2EE, explain the Double Ratchet protocol popularized by Signal, and implement a concrete client-side E2EE pipeline using the modern Web Cryptography API .
Simply exchanging a single public key and using it forever is vulnerable. If an attacker eventually steals Bob’s private key, they can decrypt all historical messages. To prevent this, modern E2EE uses the Double Ratchet Protocol : If a session key is compromised today, the attacker cannot decrypt messages sent in the past. If an attacker compromises a session key today, they cannot predict or decrypt messages sent in the future, as the key is constantly rotated using fresh elliptic curve handshakes.
Let’s implement a complete E2EE workflow in JavaScript using the browser’s built-in Web Cryptography API ( window.crypto.subtle ). This script runs entirely on the client, demonstrating key generation, shared secret derivation, and authenticated encryption/decryption. Here is how you link the steps together to simulate Alice sending a secure message to Bob: Building end-to-end encrypted applications places the security boundary where it belongs: on the user’s device. By combining Curve25519/P-256 elliptic key exchanges, modern key derivation functions, and robust authenticated encryption schemes, you can build next-generation applications that remain completely secure, even if your backend servers are fully compromised.
3. Software Implementation, Frameworks & Protocols A real-time system means sending and receiving of data instantly over a network among multiple clients. One may specify this as bi-directional flow. This enables users to make the right decisions at the right time. In simple systems, data transfer usually takes place through a request-response mechanism using a client-server architecture.
Our application is based on conversations in a Healthcare system. These conversations take place between doctors and their respective patients. This means that the patients will only be able to see their doctor in the contact list and vice versa. Therefore the users are categorized on the server based on their ‘role’. Also, E2EE is needed here to keep a patient’s details/conversations secure and confidential.
For any app to feel real-time, the user needs to be kept updated with any activity happening as soon as possible. The challenge arises in selecting and implementing a suitable development technique. With the traditional request-response model, we have few options: The user might refresh the web page time-to-time to check for message updates. But that is not an optimal solution. This may result in bad UX.
The concept of HTTP request-response is widely used. But this requires establishing a TCP connection every time data is sent to the server. Being a one-way synchronous communication protocol, this may result in a lot of overheads while creating and destroying a TCP connection every time a message is sent in real-time chat applications. This version of HTTP eliminates the need for opening a TCP connection for each HTTP request. This means that it helps in maintaining a persistent connection. But it still does not provide us with full-duplex communication as required in real-time applications.
An AJAX based-timer! Means that the client sends HTTP requests time-to-time and the response is immediately given by the server. Although it is asynchronous, it uses a lot of resources, thus creating traffic. The resources are immediately released but cannot be used in heavy applications as in real-time. This involves less traffic as compared to short polling. Here, the responses are not immediate, but this makes the application hold the resources for some time, hence leaving the requests unresolved. Also, we have to perform re-authentication or re-authorization several times. Again, this is not a good option for real-time applications.
This concept resolves most of the issues we just discussed. It implements instant two-way communication of messages with a persistent connection just as required for developing a real-time system. NodeJS offers several libraries to implement this technology. What we will be utilizing for our application is the Web Socket API with ‘WebSocket’ library. According to MDN, “The WebSocket API is an advanced technology that makes it possible to open a two-way interactive communication session between the user's browser and a server. With this API, you can send messages to a server and receive event-driven responses without having to poll the server for a reply”.
Storing New/Updated Chats to LocalStorage using setItem() on websocket event ws.onMessage() The closing handshake can take place either by the client or the server. Reconnection has to be done manually. Now that we have our messages transferring instantly from client to server and back, let’s discuss how we can make our data secure over the network. Various algorithms and protocols are working on the internet these days to make the exchange of confidential information secure. Messaging applications do implement encryption, but not each one of them makes the encryption end-to-end. This means that not even the server can decrypt our messages. But why do we need to make the application that secure? The answer is simple - to make the user’s private information hidden from any third party user. This may be the government, hackers or any other intelligence agency. The service provider may or may not allow third-parties like the government to access the data as in the case of any criminals or terrorist activities. But what if the servers get hacked? The information might then be in the wrong hands. In such cases, the users prefer to choose end-to-end encryption, where even the service provider cannot access decrypted data.
While many applications mention that they implement end-to-end encryption, only a few of them prove to do so. The very famous Telegram application provides an optional feature of Secret chats, using a protocol named “MTProto”. While Whatsapp, Facebook and Signal Messenger use the Signal Protocol developed by the Open Whisper Systems, only the Signal Messenger proved to be the most secure application.
This is because it encrypts the metadata as well, and has also denied the intelligence agencies to provide them with any user’s information. Moreover, the protocol is available as open-source code to be used or cross-verified by other developers, which makes it the most trustworthy messaging application. Today we will be discussing the Signal Protocol in detail. But before that, we need to be aware of the Diffie-Hellman key exchange mechanism. With simple encryption, the messages are usually encrypted only between the users and the server, making use of some cryptographic keys, hence making data vulnerable at the server. We want these keys only to exist between the users and not the server. But how is this possible? Suppose we have two Clients - Alice and Bob.
This mechanism was developed by Whitfield Diffie and Martin Hellman to derive the cryptographic keys instead of exchanging them completely in public. It is explained using colors since it is not possible to separate colours once mixed. Similarly, it is hard to figure out the secret keys using the only public components, once combined mathematically with the prime numbers provided by the server.
Although the mechanism provides us with a secure way to create cryptographic keys as end-to-end, it does not authorise the users. Hence, we might have some third party pretending to be the intended recipient and he/she will be able to access or modify the messages, by creating another pair of shared secret keys with Alice and Bob respectively. This is usually known as a Man-in-the-middle attack .
To perform authentication, this algorithm is integrated with other algorithms that provide authentication (ECDH) or derived multiple times mathematically (X3DH). That is when RSA came to rescue. The sender not only performs Diffie-Hellman but also shares his/her signature to ensure that only he/she has sent that message. Here is an example of the audible website, where you may see that the security protocols being used are TLS 1.2, ECDHE_RSA, AES, and not DH alone. This is how TLS, VPNs, and HTTP work. However, this algorithm was very slow and didn’t provide perfect forward secrecy. Wait, what is Forward Secrecy now? So we are discussing here X3DH key agreement protocol in detail as it is being used in the Signal Protocol. This is useful in asynchronous communication as well as authentication . For example, Bob has published some information for Alice, but she is currently offline, then the server might temporarily hold the data or send a notification to Alice.
This algorithm makes use of public components of identity keys (IK), ephemeral key (EK), signed prekey (SPK), and one-time prekey (OPK). The private components are stored at the respective user devices for computation and not shared. The algorithm performs Diffie-Hellman four times, ensuring mutual authentication (DH1 & DH2) and Forward Secrecy (DH3 & DH4), using a Key Derivation Function or KDF which is quite similar to a hash function.
This produces one master secret key, SK = KDF(DH1 || DH2 || DH3 || DH4) at the client’s respective devices, that can now be used by Alice and Bob to encrypt and decrypt the messages. To prevent man-in-the-middle attack, the Identity public keys are mathematically combined into a Safety Number using a hash function, which only the sender and receiver will have at their respective ends. This can be in the form of a QR code or fingerprint scan.
Still, wondering what Forward Secrecy is? This ensures that future messages shall not be accessed by any third party even when he/she gets access to the public keys. We will discuss this in more detail in the next algorithm. WHY DOUBLE RATCHET? We got end-to-end encryption using X3DH, we also achieved forward secrecy and mutual authentication in asynchronous communication. Now, why does the Signal protocol still need another algorithm? When a user is offline, it gives an attacker a lot of time to find and use public keys available at the server. Since the key is always the same for a long period, it makes the messages vulnerable. You need to update the keys regularly! In messaging applications like Signal and Whatsapp, these keys are updated for every message. For implementing this, the Double Ratchet algorithm came into play.
A ratchet function is a function that can turn one way only, i.e. it cannot move backward. What we will be using here is called a KDF Ratchet , since you cannot go back to figure out what the key was. This function works as follows- If the attacker gets one key, he/she will not be able to undo the operation performed by KDF Ratchet to figure out the input data, but he/she will only be able to access future messages. That’s a huge problem.
To ensure future secrecy, we use a Diffie-Hellman Ratchet with the KDF Ratchet function of Alice and Bob, forming a Double Ratchet . In such a session, we have three chains on both ends, i.e. a Root chain, Sending chain, and Receiving chain. 4. Practical Deployment, Analysis & Case Studies The sending chain of Alice is synchronized with the receiving chain of Bob and vice versa. These start at the same time. In case of any asynchronous event like non-receival of messages or delay or misuse of keys, the receiver keeps a check on the key which is not deleted until all messages are received.
The Diffie-Hellman parameters manipulate the KDF chain to reset the sending and receiving chains of both Alice and Bob by updating their starting positions and making them synchronous again. If someone cracked a key, we can re-establish the secrecy from then on. For example, Bob can send DH public-key (dh2) to Alice’s DH ratchet that will reset the sending and receiving chains on both ends. Moreover, as soon as you decrypt a message using the key, you delete it immediately and carefully. Hence the end-points are also safe from future attacks.
Note: The libsignal-protocol.js is open source, taken from the link mentioned above. It includes all the algorithms which we discussed till now i.e. X3DH and Double Ratchet. These are implemented in the Signal Protocol for the Signal Messenger application for mobile and desktop . And, we will implement this in our Web Browser using LocalStorage. Note: The utilities are taken from helpers.js of Signal Protocol. Need to convert data format because the keys are stored and processed in the form of Array Buffer in the Signal Protocol.
Initialization of Signal Server Store and Signal Protocol Manager takes place from App.js with the LoggedIn User ID, Name and respective Prekey bundle as parameters Stored Prekey bundle to LocalStorage of Web Browser for each user (actually stored temporarily at Signal Server using a secure TLS connection) Calling encryptMessageAsync() of SignalGateway.js from chatWindow.js before sending data to Server Step 3: Encrypting Messages in SignalGateway.js using the methods of libsignal-protocol.js and InMemoryProtocolStore.js Fetching Prekey bundle from LocalStorage of Browser using getItem() for Encryption and Decryption Step 4: Decrypting Messages in SignalGateway.js using the built-in methods of libsignal-protocol.js and InMemoryProtocolStore.js Calling decryptMessageAsync() of SignalGateway.js from chatWindow.js on “onMessage” event of ws Asymmetric Encryption Architecture - High-Level Diagram with Integration of the Signal Protocol We discussed the importance of Web Sockets technology and end-to-end Encryption, and how these are implemented to develop a real-time secure chat application. The signal protocol being the more secure and trustworthy protocol provides its code as open source. We also used REST APIs for login operations and to fetch contacts based on role. We implemented the WebSocket library, one of the many libraries available for implementing Web Sockets API in NodeJS.
However, much more features can be added to our simple chat application. Such as group messages, online-offline features, guaranteed message delivery, temporary message storage at a separate server, load balancing, and much more that we discussed with the proposed architecture. Firebase can also be used for building a real-time chat application, which internally uses the concept of Web sockets.
How to make messaging app like Signal is one of the most expensive questions in mobile engineering. The protocol is open, the spec is roughly 30 pages, and a serviceable demo can be wired up in a weekend. A production build that protects real users from real adversaries is closer to 16-24 weeks with a 5-engineer team and an $80K-250K floor for the MVP alone. The gap between the two is where most clone projects fail.
Our team has shipped E2EE chat features across Flutter and React Native clients, integrated libsignal through platform channels, and walked clients through threat-model exercises before a line of cryptographic code gets written. We've also turned down builds where the budget and the threat model didn't match. This guide is the operator version of that conversation. What Signal-style architecture actually requires, what tech stack we'd pick in 2026, and what a Signal-grade messaging app development company has to deliver beyond the protocol itself.
If you came here looking for a five-week MVP quote, this is the wrong page. If you want to know why every honest scope range starts at six figures and where the money goes, read on. An end to end encrypted messaging app means more than "messages are encrypted in transit." Five properties define a Signal-grade system, in order of how hard each is to ship correctly. First, forward secrecy and post-compromise security via the Double Ratchet. Every message uses a fresh symmetric key, so a stolen device key can't decrypt past messages and a future compromise can't decrypt earlier ones. Second, asynchronous key agreement via X3DH, so Alice can send Bob a first message while Bob is offline.
Third, sealed sender: the server routes a message without knowing who sent it, hiding metadata that the cryptography alone leaks. Fourth, sealed groups: group membership and group identifiers aren't visible to the server. Signal moved to that model in 2020. Fifth, the polish layer of disappearing messages, screen-security, contact discovery via SGX or private-set intersection. Cheaper E2E offerings (Sendbird E2EE, Virgil Security, Matrix's Olm/Megolm) implement the first one or two properties cleanly. They're fine products for some markets. They are not Signal.
Knowing which of the five your product actually needs is the first scoping conversation we run. A B2B compliance chat for a regulated industry may only need property one with audit logs. A whistleblower platform needs all five plus key transparency. The price tag swings by 3x on that single decision. When we sit down to plan how to make messaging app like Signal for a client, we draw six boxes on the whiteboard before talking about screens or features. Each layer has a named algorithm, a reference implementation, and a category of bugs that will cost you if shipped wrong. Our Flutter mobile app development guide walks through the client-side architecture we use .
X3DH (Extended Triple Diffie-Hellman) establishes a shared secret between two parties who may not be online simultaneously. Each user publishes an identity key, a signed prekey rotated weekly, and a stack of one-time prekeys to the server. The sender fetches a bundle, performs three or four Diffie-Hellman operations against the recipient's keys plus their own, and derives the initial session key.
The math is in the published Signal X3DH spec. The implementation work is in correctly rotating prekeys, handling the one-time-prekey exhaustion edge case, and refusing to send when the server returns a tampered bundle. Reference implementations live in libsignal-protocol-c, libsignal-client-rust, and libsignal-protocol-java. We do not recommend writing X3DH from scratch for a commercial product. Use the audited libraries and own only the integration code.
Every message advances two ratchets: a Diffie-Hellman ratchet when a new DH key is included in the header, and a symmetric KDF chain that derives per-message keys. The result is per-message uniqueness, immediate discard of past keys, and bounded compromise. A future device theft can read what's on disk, never what came before. The published Signal Double Ratchet spec is around 30 pages.
A production-grade implementation is closer to 3,000 lines of cryptographic code that needs constant-time operations, side-channel resistance, and exhaustive test vectors. Our default is to keep this layer inside Signal's audited libraries (libsignal-client-rust shipped via FFI, or the Java/Kotlin and Swift bindings on each platform) and never touch the primitives directly in product code.
After a session is established, Signal encrypts the sender's identity inside the message envelope so the server only sees the recipient. To prevent spam, the server validates a short-lived sender certificate without learning who issued it. The cryptographic primitive is straightforward; the operational work is real. Sealed sender adds roughly 15-20% to protocol code volume and 25% to the test surface, in our experience on two prior builds. You also need a certificate-authority service that issues sender certificates without logging who they go to. That's an entire backend subsystem on its own. Skip it and your "E2EE" app still leaks who-talks-to-whom social graphs to anyone with subpoena access to the server.
Signal does not run "multi-device cryptography" the way iMessage does. Each linked device gets its own identity key and its own set of sessions. When you send a group message from your phone, your phone encrypts it once per recipient device. Adding a second device to an existing identity without breaking forward secrecy is the single hardest engineering problem in this architecture.
We budget 3-5 weeks of senior engineering for the link-device flow on a Signal-style build, even with libsignal handling the primitives. The QR-code linking ceremony, message history transfer (or refusal to transfer), and revocation of stolen linked devices each have their own edge cases. Get this wrong and you ship a chat app that loses messages every time a user upgrades a phone.
Signal uses pairwise encryption inside groups: every group message is encrypted independently to each member. That scales linearly with group size. At 1,000 members, a single message becomes 1,000 ciphertexts. Bandwidth and battery costs follow. The alternative, MLS (Messaging Layer Security, RFC 9420), uses a shared group key with logarithmic ratchet trees. WhatsApp moved to MLS in 2024 for large communities.
Our recommendation for new builds in 2026 is to ship pairwise for groups under 256 members and plan an MLS migration path for anything beyond that. Mixing the two in one app is possible (libsignal-client now exposes MLS primitives) but adds about 4 weeks of integration work and a second audit pass. 5. Performance Evaluation & Extended Technical Observations APNS and FCM are operated by Apple and Google. Anything you put in a push payload, they can read. Signal-style apps therefore send wake-up pings only. The actual ciphertext arrives over an authenticated WebSocket session that the client opens to your server after the OS wakes it. That's a small change with large implications: your backend has to hold a message queue per user, handle reconnection storms, and degrade gracefully when carriers throttle long-lived connections.
On iOS, the situation is harder because background-fetch budgets are tight. Signal's own iOS app uses NSE (Notification Service Extension) to decrypt messages inside a separate process. That extension has a 30-second wall-clock budget and a 24MB memory limit. Our delivery team treats the NSE as its own micro-app with its own performance budget. There is no single answer to how to make messaging app like Signal in stack terms. Choice depends on team composition, target platforms, and whether you need self-hostable inference for AI features. Below is the default we'd quote for a new client asking about chat app development today, with named alternatives for the three most common deviations.
Our default mobile client is Flutter, with platform channels into libsignal-client-java on Android and libsignal-client-swift on iOS. The cryptographic surface stays inside Signal-audited code; the Dart layer handles session management, key storage, contact UI, and the chat list. We've shipped this pattern on two prior builds and the binding work runs 4-6 weeks of senior mobile engineering on its own.
When Flutter is the wrong call: if you already have a React web app and need a chat tab inside it, React Native via libsignal-client-rust FFI is the saner choice. If you need first-day CallKit and ARKit integrations, native Swift on iOS and native Kotlin on Android still win. Pure Dart bindings (the older flutter_sodium path) we no longer recommend; package maintenance has been intermittent since late 2023 and the X3DH layer is not something to write twice.
Signal's open-source server is written in Java. For new builds we lean Rust (using tokio and axum) or Go, both of which give us cleaner concurrency primitives for the long-lived WebSocket sessions a Signal-style app demands. The queue is Redis Streams or NATS JetStream. Postgres handles the relational side (registration records, sealed-sender certificates, prekey bundles). We avoid full message persistence on the server. Undelivered envelopes live in the queue with a 30-day TTL and are deleted on receipt.
Push fan-out is its own service. APNS on iOS, FCM on Android, both delivering wake-up notifications with no payload. The push service holds APNS and FCM tokens (rotated frequently), maps them to user UUIDs, and intentionally has no access to message content. That last sentence is the one your security auditor will ask for proof of. Three honest options. libsignal-client is the reference, MIT-licensed, with bindings in Java, Swift, and Rust. It is the only stack that runs the original Signal Protocol with the same audited code path. Olm and Megolm, from the Matrix project, ship a different protocol with federation built in; it's appropriate when you want decentralized routing and accept a different threat model. Writing your own primitives is the path used by exactly one commercial product we'd name (iMessage), and Apple has more cryptographers than your roadmap probably justifies.
On-device storage uses SQLCipher (AES-256 with a key derived from the device keychain via PBKDF2 or Argon2id). The user passphrase, if any, layers on top through Argon2id with high memory cost. On the server side, message bodies never appear in plaintext; the queue holds opaque envelopes that the recipient client decrypts. Backups, if you offer them, must be client-side encrypted before upload. Apple's iCloud backup is plaintext from your app's perspective, which is why Signal explicitly excludes itself from it.
Below is the scope range we'd quote a client today for a Signal-style messaging app development project. Numbers reflect blended senior-engineer day rates and a 5-person team (2 mobile, 1 backend, 1 cryptography lead, 1 product/QA). Ranges are wide because the threat model drives 40% of the variance. What drives the spread inside each row. For the MVP, the biggest cost lever is whether you reuse the Signal Foundation's open-source server (saves 6-8 weeks) or run a custom backend with sealed-sender certificates and an abuse pipeline you control (adds the same). For the production-grade tier, the cost is dominated by multi-device link flows and key transparency infrastructure, both of which are easy to underestimate by a factor of two.
We start every Signal-style engagement with a $3K discovery audit. That two-week exercise produces a threat-model document, a stack recommendation, and a fixed-price pilot scope. The pilot itself lands in the $10K-25K continuous range only when the build is small (a B2B chat tab inside an existing app, say). A clean-room Signal clone never fits inside the pilot envelope; it lands in the MVP row above. If a vendor quotes you $30K for that build, ask which of the six layers they're skipping.
Encrypted messaging is the most regulatorily contested category in mobile. GDPR and CCPA push you toward metadata minimization: collect no PII you don't need, retain nothing past delivery, allow account deletion that wipes server-side state in a verifiable way. The technical work to support that includes a tombstone protocol for deleted accounts and a documented data-retention schedule that an auditor can run queries against.
Independent cryptographic audit is non-negotiable for anything claiming Signal-grade. Three firms we'd shortlist: Trail of Bits (strong on Rust and protocol review), NCC Group (deep mobile platform expertise), and Cure53 (the firm Signal itself has used). Budget $30K-80K and 4-6 weeks. The deliverable is a report you can hand to enterprise buyers and to journalists. Skipping this step is the single most common cost-cut in clone projects, and the one that ends careers when a CVE lands.
App-store policies add a third axis. Apple requires Export Compliance documentation for any app using non-exempt cryptography; the standard answer is an annual self-classification report to the US BIS. Google Play is friendlier on crypto but stricter on data-safety declarations. Both stores will reject apps that claim E2EE in marketing copy but hold key escrow on the server. Our delivery team writes the data-safety form alongside the code, not after submission.
Threat-model documentation closes the loop. Who are you protecting against, opportunistic attackers, criminal groups, or nation-state actors? What capabilities do they have? What's out of scope (compromised endpoints, malicious linked devices, hardware implants)? A two-page threat-model doc costs a week of senior engineering time and saves a quarter of work later when the audit firm asks the same questions.
The simplest rule: if the AI runs on the server, your E2EE claim is dead. The moment plaintext leaves the device for inference, you've built a system Signal would not call Signal. Every credible AI feature in an encrypted chat app in 2026 runs on-device or not at all. On-device options are now real. Apple Intelligence (3B-parameter foundation model on A17 Pro and later) handles summarization, translation, and tone rewriting inside the secure enclave. Gemini Nano on Pixel and recent Samsung devices runs a similar workload through AICore. For cross-platform we've shipped Phi-3.5 mini (3.8B) and Gemma 3 270M as quantized GGUF models inside the app bundle, with llama.cpp or mlc-llm as the runtime. Latency on a modern phone is 200-600ms for a typical summarization prompt.
What we won't ship: server-side translation of E2EE messages, server-side spam filtering on message bodies, or server-side AI summaries of chat threads. Each one breaks the encryption guarantee. Federated learning is a workable middle path for things like typo correction (gradients leave the device, plaintext does not) but it adds significant infra complexity and is not worth it for an MVP.
Build in-house when you already have a cryptography hire on staff, a budget for an 18-month roadmap, and a product that depends on chat being a strategic moat (think a regulated-industry platform where the messenger is the differentiator). Hire a messaging app development company when chat is a feature inside a larger product, when time-to-pilot matters more than long-term IP ownership, or when you need senior mobile crypto talent for a 6-month window without committing to a full-time hire. For a related deep-dive on model trade-offs see our best AI chatbots guide .
Mixed models work too. We've delivered Signal-style chat features where our team owned the crypto integration and the client's internal team owned the product surface. That pattern keeps the highest-risk work (X3DH integration, Double Ratchet plumbing, audit prep) inside a team that's done it before, and the highest-value work (product UX, growth, business logic) inside the team that owns the customer relationship.
If you're evaluating partners, our $3K discovery audit produces a written threat model, a stack recommendation with named libraries, and a fixed-price pilot scope. That document is yours regardless of whether you engage us for the build. We've found that a serious audit kills about a third of "clone Signal" projects before they start, and the clients who proceed do so with a roadmap that doesn't collapse in month four.
If chat is one of several features inside an AI-powered product, our ai-chatbot-development practice and mobile-app-development team work the build together. The crypto layer slots beneath whichever conversational AI surface you're building. Both teams use Claude, OpenAI, and open-weight models on the inference side, and both have shipped on-device LLM features inside Flutter and React Native shells.
Signal's client and server code are AGPL and GPL respectively. You can fork them, but you cannot use the Signal name, the Signal trademark, or the Signal Foundation's central server. Existing federated or independent forks include Session (Loki Foundation), Molly (Android-only hardened fork), and SimpleX. Building your own server is mandatory; cloning the client UI is legally permitted but rarely the right product decision. If you are exploring how to make a messaging app at MVP scope only, our scoping checklist below lists the minimum-viable cuts that keep cryptography correct while trimming the surface area.
A 1:1 chat MVP using libsignal bindings, iOS and Android via Flutter, ships in 12-16 weeks with a 5-person team. Production-grade (groups, multi-device, disappearing messages, voice/video) lands at 24-32 weeks. Anything faster is either using a managed E2EE SDK and calling it Signal-grade or skipping audit and sealed-sender work. Yes. The Signal Protocol specifications (X3DH, Double Ratchet, Sealed Sender) are published under a permissive license; the reference libraries libsignal-protocol-c, libsignal-client-rust, and libsignal-client-java are MIT-licensed. WhatsApp, Google Messages (RCS E2EE), and Facebook Messenger Secret Conversations all use Signal Protocol under the hood. Adoption past 2 billion users is itself a strong audit signal.
Signal Protocol is a centralized protocol designed for a single trusted server (yours). Matrix is a federated protocol where many independent servers exchange messages, and its Olm and Megolm primitives are similar in spirit to X3DH and Double Ratchet but with a different threat model around server compromise. Pick Signal Protocol when you want a single-tenant E2EE messenger. Pick Matrix when you want federation across organizations and accept that group membership leaks to home servers.
$80K-250K for an MVP, $250K-600K for a production-grade build, plus $30K-80K for an independent audit. Voice and video add $60K-150K. Continuous security operations after launch run $10K-25K per month. Cheaper bids almost always skip sealed-sender, multi-device sync, or the audit. The Reddit threads complaining about Signal clones that broke in production usually map to those exact shortcuts.
Yes, as long as inference stays on the device. Apple Intelligence, Gemini Nano, Phi-3.5 mini, and Gemma 3 270M are all viable for in-app summarization, translation, and tone-rewriting features. Server-side inference on plaintext messages breaks the encryption contract; there is no honest "both" answer here. Our delivery team scopes AI features inside the on-device runtime budget from the start.
Signal-style chat is the highest-skill mobile cryptography work in commercial production today. The protocol is open, the libraries are audited, and the spec fits on a long flight. The implementation work of sealed-sender certificates, multi-device link flows, NSE budgets, audit prep, and threat-model documentation is what separates a $30K clone that breaks in month two from a $250K MVP that holds up under scrutiny. If you want a written threat model and a fixed-price scope on your build, the $3K discovery audit is the right first step. We'll tell you which of the six layers you actually need.
Top AI chatbots in 2026 compared by workload. Coding, research, writing, long-context, multimodal, cost — practitioner picks with current benchmarks. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/End-to-end%20encryption • https://en.wikipedia.org/wiki/Email%20encryption • https://en.wikipedia.org/wiki/Signal%20Protocol • https://www.askantech.com/end-to-end-encryption-implementation-guide-e2ee-patterns-key-management/ • https://dev.to/gyanaa_vaibhav_8757257a61/end-to-end-encrypted-messaging-app-high-level-design-and-architecture-5d16 • https://mohashari.github.io/end-to-end-encryption-chat-applications/ • https://www.qed42.com/insights/developing-a-real-time-secure-chat-application-like-whatsapp-signal-with-end-to-end-encry ption • https://www.getwidget.dev/blog/how-to-make-messaging-app-like-signal/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Secure Messaging Application Using End To End Encryption.
[*] Metasploit Scan Running on Target Subnet for Secure Messaging Application Using End To End Encryption... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |