Complete Technical Paper Content — Secure Mobile Messaging Application Using Signal Protocol
Overview & System Context
Secure Mobile Messaging Application Using Signal Protocol: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9623 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background The Signal Protocol (formerly known as the TextSecure Protocol) is a non-federated cryptographic protocol that provides end-to-end encryption for voice and instant messaging conversations. The protocol was developed by Open Whisper Systems in 2013 and was introduced in the open-source TextSecure app, which later became Signal. Several closed-source applications have implemented the protocol, such as WhatsApp, which is said to encrypt the conversations of "more than a billion people worldwide" or Google who provides end-to-end encryption by default to all RCS-based conversations between users of their Google Messages app for one-to-one conversations. Facebook Messenger also say they offer the protocol for optional "Secret Conversations", as did Skype for its "Private Conversations". The protocol combines the Double Ratchet Algorithm, prekeys (i.e., one-time ephemeral public keys that have been uploaded in advance to a central server), and key agreement protocols including the original triple elliptic-curve Diffie–Hellman (3-DH) handshake and the post-quantum PQXDH protocol. Current Signal specifications model message encryption as authenticated encryption with associated data (AEAD), with recommended constructions including SIV-style AEAD schemes or a composition of AES-256 in CBC mode with HMAC.
libsignal-protocol-c: A library written in C with additional licensing permissions for Apple's App Store. libsignal-protocol-java: A library written in Java. libsignal-protocol-javascript: A library written in JavaScript. There are also alternative libraries written by third-parties in other languages, such as TypeScript. Signal is an open-source, encrypted messaging service for instant messaging, voice calls, and video calls. The instant messaging function includes sending text, voice notes, images, videos, and other files. Communication may be one-to-one between users or may involve group messaging. The application uses a centralized computing architecture and is cross-platform software. It is developed by the nonprofit Signal Foundation and its subsidiary Signal Messenger LLC. Signal's software is free and open-source. Its mobile clients, desktop client, and server are all published under the AGPL-3.0-only license. The official Android app generally uses the proprietary Google Play Services, although it is designed to be able to work without them. Signal is also distributed for iOS and desktop programs for Windows, macOS, and Linux. Registration for desktop use requires an iOS or Android device. Signal uses mobile telephone numbers to register and manage user accounts, though configurable usernames were added in March 2024 to allow users to hide their phone numbers from other users. After removing support for SMS on Android in 2023, the app now secures all communications with end-to-end encryption. The client software includes mechanisms by which users can independently verify their contacts' identities and the data channel's integrity. The nonprofit Signal Foundation was launched in February 2018 with initial funding of $50 million from WhatsApp co-founder Brian Acton. As of January 2025, the platform had approximately 70 million monthly active users. As of January 2025, it had been downloaded more than 220 million times.
Open Whisper Systems' website was launched in January 2013. In February 2014, Open Whisper Systems introduced the second version of their TextSecure Protocol (now Signal Protocol), which added end-to-end encrypted group chat and instant messaging capabilities to TextSecure. Toward the end of July 2014, they announced plans to merge the RedPhone and TextSecure applications as Signal. This announcement coincided with the initial release of Signal as a RedPhone counterpart for iOS. The developers said that their next steps would be to provide TextSecure instant messaging capabilities for iOS, unify the RedPhone and TextSecure applications on Android, and launch a web client. Signal was the first iOS app to enable end-to-end encrypted voice calls for free. TextSecure compatibility was added to the iOS application in March 2015.
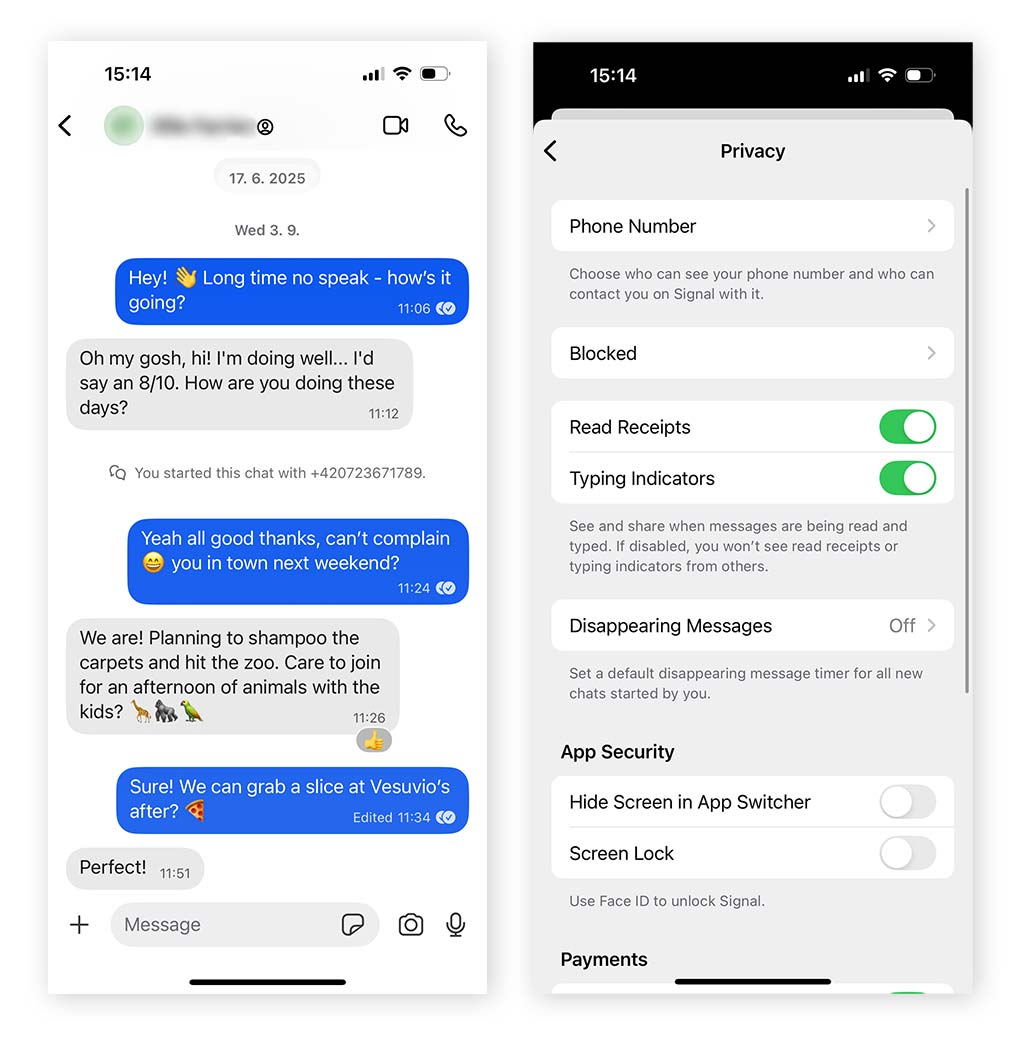
Figure 1: Best Encrypted Messaging Apps | Secure Private Messaging From its launch in May 2010 until March 2015, the Android version of Signal (then called TextSecure) included support for encrypted SMS/MMS messaging. From version 2.7.0 onward, the Android application only supported sending and receiving encrypted messages via the data channel. Reasons for this included security flaws of SMS/MMS and problems with the key exchange. Open Whisper Systems' abandonment of SMS/MMS encryption prompted some users to create a fork named Silence (initially called SMSSecure) that is meant solely for the exchange of encrypted SMS and MMS messages. In November 2015, the TextSecure and RedPhone applications on Android were merged to become Signal for Android. A month later, Open Whisper Systems announced Signal Desktop, a Chrome app that could link with a Signal mobile client. At launch, the app could only be linked with the Android version of Signal. On 26 September 2016, Open Whisper Systems announced that Signal Desktop could now be linked with the iOS version of Signal as well. On 31 October 2017, Open Whisper Systems announced that the Chrome app was deprecated. At the same time, they announced the release of a standalone desktop client (based on the Electron framework) for Windows, macOS and certain Linux distributions. On 4 October 2016, the American Civil Liberties Union (ACLU) and Open Whisper Systems published a series of documents revealing that OWS had received a subpoena requiring them to provide information associated with two phone numbers for a federal grand jury investigation in the first half of 2016. Only one of the two phone numbers was registered on Signal, and because of how the service is designed, OWS was only able to provide "the time the user's account had been created and the last time it had connected to the service". Along with the subpoena, OWS received a gag order requiring OWS not to tell anyone about the subpoena for one year. OWS approached the ACLU, and they were able to lift part of the gag order after challenging it in court. OWS said it was the first time they had received a subpoena, and that they were "committed to treating any future requests the same way". In March 2017, Open Whisper Systems transitioned Signal's calling system from RedPhone to WebRTC, also adding the ability to make video calls with the mobile apps.
On 21 February 2018, Moxie Marlinspike and WhatsApp co-founder Brian Acton announced the formation of the Signal Technology Foundation, a 501(c)(3) nonprofit organization whose mission is "to support, accelerate, and broaden Signal's mission of making private communication accessible and ubiquitous". Acton started the foundation with $50 million in funding and became the foundation's executive chairman after leaving WhatsApp's parent company Facebook in September 2017.
Marlinspike continued as Signal Messenger's first CEO. As of 2020, Signal ran entirely on donations, as a nonprofit. Between November 2019 and February 2020, Signal added iPad support, view-once images and videos, stickers, and reactions. They also announced plans for a new group messaging system and an "experimental method for storing encrypted contacts in the cloud." Signal was reportedly popularized in the United States during the George Floyd protests. Heightened awareness of police monitoring led protesters to use the platform to communicate. Black Lives Matter organizers had used the platform "for several years". During the first week of June, the encrypted messaging app was downloaded over five times more than it had been during the week prior to the murder of George Floyd. In June 2020, Signal Foundation announced a new feature that enables users to blur faces in photos, in response to increased federal efforts to monitor protesters. On 7 January 2021, Signal saw a surge in new user registrations, which temporarily overwhelmed Signal's capacity to deliver account verification messages. CNN and MacRumors linked the surge with a WhatsApp privacy policy change and a Signal endorsement by Elon Musk and Edward Snowden via Twitter. The surge was also tied to the attack on the United States Capitol. International newspapers reported similar trends in the United Arab Emirates. Reuters reported that more than 100,000 people had installed Signal between 7 and 8 January. Between 12 and 14 January 2021, the number of Signal installations listed on Google Play increased from over 10 million to over 50 million. On 15 January 2021, due to the surge of new users, Signal was overwhelmed with the new traffic and was down for all users. On the afternoon of 16 January, Signal announced via Twitter that service had been restored. On 10 January 2022, Moxie Marlinspike announced that he was stepping down from his role as CEO of Signal Messenger. He continues to remain on the Signal Foundation's board of directors and Brian Acton has volunteered to serve as interim CEO during the search for a new CEO. In August 2022, Signal notified 1900 users that their data had been affected by the Twilio breach including user phone numbers and SMS verification codes. At least one journalist had his account re-registered to a device he did not control as a result of the attack. In September 2022 Signal Messaging LLC announced that AI researcher and noted critic of big tech Meredith Whittaker would fill the newly created position of president. In August 2024, Reuters reported on the blocking of Signal in Venezuela and Russia. In Venezuela, the blocking was a result of protests after the controversial presidential elections in which Nicolas Maduro declared his victory. In Russia, the reason was that Signal did not meet the requirements of legislation in the field of countering terrorism and extremism. In May 2026, Signal threatened to leave Canada because of the Lawful Access Act, stating that "Bill C-22 could potentially allow hackers to exploit these very vulnerabilities engineered into electronic systems, with private messaging services serving as an ideal target for foreign adversaries".
Signal messages are encrypted with the Signal Protocol (formerly known as the TextSecure Protocol). The protocol combines the Double Ratchet Algorithm, prekeys, and an Extended Triple Diffie–Hellman (X3DH) handshake. It uses Curve25519, AES-256, and HMAC-SHA256 as primitives. The protocol provides confidentiality, integrity, authentication, participant consistency, destination validation, forward secrecy, backward secrecy (a.k.a. future secrecy), causality preservation, message unlinkability, message repudiation, participation repudiation, and asynchronicity. It does not provide anonymity preservation, and requires servers for the relaying of messages and storing of public key material. The Signal Protocol also supports end-to-end encrypted group chats. The group chat protocol is a combination of a pairwise double ratchet and multicast encryption. In addition to the properties provided by the one-to-one protocol, the group chat protocol provides speaker consistency, out-of-order resilience, dropped message resilience, computational equality, trust equality, subgroup messaging, as well as contractible and expandable membership. According to a 2023 technical report, Signal adopted a protocol called Sender Keys for group messaging, and favors the protocol where possible (rather than the double ratchet) for group messaging, even in small groups. In October 2014, researchers from Ruhr University Bochum (RUB) published an analysis of the Signal Protocol. Among other findings, they presented an unknown key-share attack on the protocol, but in general, they found that it was secure. In October 2016, researchers from UK's University of Oxford, Queensland University of Technology in Australia, and Canada's McMaster University published a formal analysis of the protocol. They concluded that the protocol was cryptographically sound. In July 2017, researchers from RUB found during another analysis of group messengers a purely theoretic attack against the group protocol of Signal: A user who knows the secret group ID of a group (due to having been a group member previously or stealing it from a member's device) can become a member of the group.
Since the group ID cannot be guessed and such member changes are displayed to the remaining members, this attack is likely to be difficult to carry out without being detected. As of August 2018, the Signal Protocol has been implemented into WhatsApp, Facebook Messenger, Skype, and Google Allo, making it possible for the conversations of "more than a billion people worldwide" to be end-to-end encrypted. In Google Allo, Skype and Facebook Messenger, conversations are not encrypted with the Signal Protocol by default; they only offer end-to-end encryption in an optional mode. Up until March 2017, Signal's voice calls were encrypted with SRTP and the ZRTP key-agreement protocol, which was developed by Phil Zimmermann. In March 2017, Signal transitioned to a new WebRTC-based calling system that introduced the ability to make video calls. Signal's voice and video calling functionalities use the Signal Protocol channel for authentication instead of ZRTP.
In December 2016, Egypt blocked access to Signal. In response, Signal's developers added domain fronting to their service. This allows Signal users in a specific country to circumvent censorship by making it look like they are connecting to a different internet-based service. As of May 2022, Signal's domain fronting is enabled by default in Egypt, UAE, Oman, Qatar, Iran, Cuba, Pakistan and Uzbekistan. As of January 2018, Signal was blocked in Iran. Signal's domain fronting feature relies on the Google App Engine (GAE) service. This does not work in Iran because Google has blocked Iranian access to GAE in order to comply with U.S. sanctions. In early 2018, Google App Engine made an internal change to stop domain fronting for all countries. Due to this issue, Signal made a public change to use Amazon CloudFront for domain fronting. However, AWS also announced that they would be making changes to their service to prevent domain fronting. As a result, Signal said that they would start investigating new methods/approaches. Signal switched from AWS back to Google in April 2019. In January 2021, Iran removed the app from app stores, and blocked Signal. Signal was later blocked by China in March 2021, followed by its removal from the App Store in China on 19 April 2024. On August 9, 2024, Signal was blocked in Russia. Roskomnadzor claimed that this was due to "violations of the law on combating terrorism and extremism". Around the same time, Signal was also blocked in Venezuela following the contested 2024 presidential election and subsequent protests.
Figure 2: The Shortcomings of Secure Messaging Apps | WhatsApp vs. SecurePhone In March 2025, it was revealed that senior members of the Trump administration—including vice president JD Vance, secretary of state Marco Rubio, and defense secretary Pete Hegseth—were using Signal to discuss sensitive information, including details of military attack plans in Yemen. The existence of the chat was disclosed by The Atlantic editor-in-chief Jeffrey Goldberg, who was accidentally added to the chat. Brian Hughes of the National Security Council later confirmed the authenticity of Goldberg's account. On October 4, 2025, The Minnesota Star Tribune reported that Deputy Homeland Security Advisor Anthony Salisbury had been seen in public exchanging information on Signal with other government officials. Subjects discussed included potential troop deployments to Portland, Oregon, upcoming Immigration and Customs Enforcement (ICE) operations in Chicago, Vice President JD Vance's desire to prosecute two unnamed Florida influencers, and Federal Bureau of Investigation director Kash Patel's firing of FBI employees.
Comparison of cross-platform instant messaging clients Comparison of VoIP software Internet privacy List of video telecommunication services and product brands Secure communication The Session Initiation Protocol (SIP) is a signaling protocol used for initiating, maintaining, modifying, and terminating communication sessions that involve multimedia elements such as voice, video, and messaging. It operates at the application layer of the Internet protocol suite and is widely used in Internet telephony, private IP-based telephone systems, and mobile communication over LTE networks through VoLTE. The protocol defines the specific format of messages exchanged and the sequence of communications for cooperation of the participants. SIP is a text-based protocol, incorporating many elements of the Hypertext Transfer Protocol (HTTP) and the Simple Mail Transfer Protocol (SMTP). A call established with SIP may consist of multiple media streams, but no separate streams are required for applications, such as text messaging, that exchange data as payload in the SIP message. SIP works in conjunction with several other protocols that specify and carry the session media. Most commonly, media type and parameter negotiation and media setup are performed with the Session Description Protocol (SDP), which is carried as payload in SIP messages. SIP is designed to be independent of the underlying transport layer protocol and can be used with the User Datagram Protocol (UDP), the Transmission Control Protocol (TCP), and the Stream Control Transmission Protocol (SCTP). For secure transmissions of SIP messages over insecure network links, the protocol may be encrypted with Transport Layer Security (TLS). For the transmission of media streams (voice, video) the SDP payload carried in SIP messages typically employs the Real-time Transport Protocol (RTP) or the Secure Real-time Transport Protocol (SRTP).
SIP is only involved in the signaling operations of a media communication session and is primarily used to set up and terminate voice or video calls. SIP can be used to establish two-party (unicast) or multiparty (multicast) sessions. It also allows modification of existing calls. The modification can involve changing addresses or ports, inviting more participants, and adding or deleting media streams. SIP has also found applications in messaging applications, such as instant messaging, and event subscription and notification. SIP works in conjunction with several other protocols that specify the media format and coding and that carry the media once the call is set up. For call setup, the body of a SIP message contains a Session Description Protocol (SDP) data unit, which specifies the media format, codec and media communication protocol. Voice and video media streams are typically carried between the terminals using the Real-time Transport Protocol (RTP) or Secure Real-time Transport Protocol (SRTP). Every resource of a SIP network, such as user agents, call routers, and voicemail boxes, are identified by a Uniform Resource Identifier (URI). The syntax of the URI follows the general standard syntax also used in Web services and e-mail. The URI scheme used for SIP is sip and a typical SIP URI has the form sip:username@domainname or sip:username@hostport, where domainname requires DNS SRV records to locate the servers for SIP domain while hostport can be an IP address or a fully qualified domain name of the host and port. If secure transmission is required, the scheme sips is used. SIP employs design elements similar to the HTTP request and response transaction model. Each transaction consists of a client request that invokes a particular method or function on the server and at least one response. SIP reuses most of the header fields, encoding rules and status codes of HTTP, providing a readable text-based format. SIP can be carried by several transport layer protocols including Transmission Control Protocol (TCP), User Datagram Protocol (UDP), and Stream Control Transmission Protocol (SCTP). SIP clients typically use TCP or UDP on port numbers 5060 or 5061 for SIP traffic to servers and other endpoints. Port 5060 is commonly used for non-encrypted signaling traffic whereas port 5061 is typically used for traffic encrypted with Transport Layer Security (TLS). SIP-based telephony networks often implement call processing features of Signaling System 7 (SS7), for which special SIP protocol extensions exist, although the two protocols themselves are very different. SS7 is a centralized protocol, characterized by a complex central network architecture and dumb endpoints (traditional telephone handsets). SIP is a client-server protocol of equipotent peers. SIP features are implemented in the communicating endpoints, while the traditional SS7 architecture is in use only between switching centers.
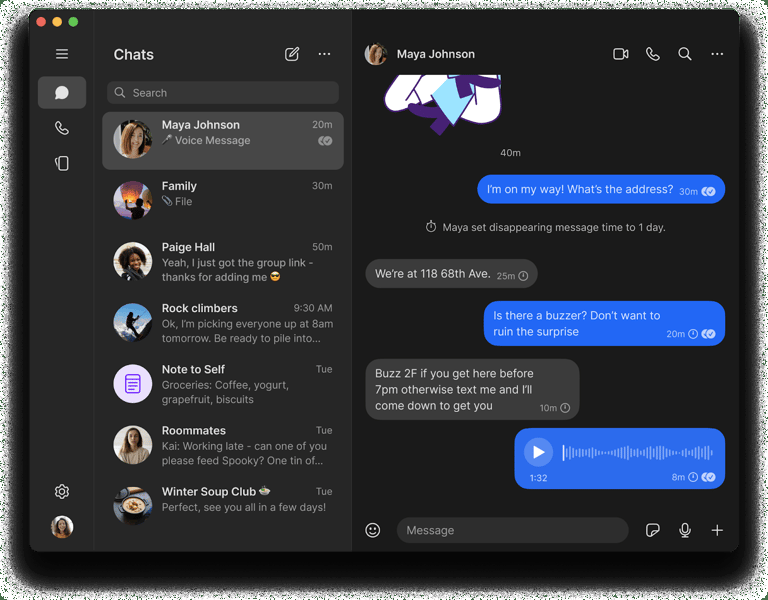
Figure 3: Protect Your Privacy: Best Secure Messaging Apps for 2026 A registrar is a SIP endpoint that provides a location service. It accepts REGISTER requests, recording the address and other parameters from the user agent. For subsequent requests, it provides an essential means to locate possible communication peers on the network. The location service links one or more IP addresses to the SIP URI of the registering agent. Multiple user agents may register for the same URI, with the result that all registered user agents receive the calls to the URI. SIP registrars are logical elements and are often co-located with SIP proxies. To improve network scalability, location services may instead be located with a redirect server.
Session border controllers (SBCs) serve as middleboxes between user agents and SIP servers for various types of functions, including network topology hiding and assistance in NAT traversal. SBCs are an independently engineered solution and are not mentioned in the SIP RFC. Responses are sent by the user agent server indicating the result of a received request. Several classes of responses are recognized, determined by the numerical range of result codes: 1xx: Provisional responses to requests indicate the request was valid and is being processed. 2xx: Successful completion of the request. As a response to an INVITE, it indicates a call is established. The most common code is 200, which is an unqualified success report. 3xx: Call redirection is needed for completion of the request. The request must be completed with a new destination. 4xx: The request cannot be completed at the server for a variety of reasons, including bad request syntax (code 400). 5xx: The server failed to fulfill an apparently valid request, including server internal errors (code 500). 6xx: The request cannot be fulfilled at any server. It indicates a global failure, including call rejection by the destination.
The Signal Protocol (formerly known as the Axolotl Ratchet) has become the deIfacto standard for endItoIend encrypted (E2EE) messaging. From WhatsApp and Facebook Messenger to the openIsource Signal app itself, the protocol powers billions of daily conversations while offering strong forward secrecy, postIcompromise security, and resilience against a wide range of attacks.
This article provides a deep dive into the Signal Protocol’s architecture, its cryptographic foundations, practical implementation considerations, and realIworld usage. By the end, you will understand not only what the protocol does, but how it does it, and you’ll have enough knowledge to evaluate or even implement a simplified version yourself. Before Signal, most secure messaging solutions relied on static public keys (e.g., PGP) or on serverImediated encryption (e.g., TLS). Those approaches suffered from two major shortcomings: The Signal Protocol was introduced in 2014 by Moxie Marlinspike and Trevor Perrin. It combined three previously independent ideas— X3DH (Extended Triple DiffieIHellman), the Double Ratchet , and preIkey bundles —into a single cohesive system that addressed both forward secrecy and postIcompromise security while remaining practical for mobile devices.
The impact has been profound: the protocol has been audited, formally verified, and adopted by major platforms. Understanding its inner workings is essential for anyone building privacyIpreserving communications. Signal’s security rests on three interlocking components. Each solves a specific problem, and together they provide the strong guarantees the protocol promises.
X3DH (Extended Triple DiffieIHellman) is the handshake that establishes a shared secret between two parties who have never communicated before. It uses a combination of: The initiator (Alice) retrieves Bob’s preIkey bundle (IK_B, SPK_B, OPK_B) from the server and performs four DH calculations: The concatenation of these DH outputs, passed through a KDF (Key Derivation Function), yields the master secret for the session. Because the OPK is used only once, an adversary who later compromises Bob’s longIterm keys cannot retroactively compute DH4 , preserving forward secrecy.
Once the master secret is established, the Double Ratchet takes over to encrypt each subsequent message. It consists of two intertwined ratchets: The algorithm can be visualized as a grid where each row represents a DH ratchet step and each column a message within that step. Whenever a party receives a message with a new DH public key, they: Because each DH exchange introduces fresh entropy, even if an attacker learns the current chain key, they cannot compute future keys after a DH ratchet step—a property known as postIcompromise security .
Both parts are wrapped in a Message Authentication Code (MAC) using an HMACIbased key derived from the root chain. This ensures integrity and authenticity. Below is a concrete scenario illustrating the entire flow from initial handshake to subsequent messages. Both parties maintain a message cache for outIofIorder messages, allowing them to process messages that arrive later than earlier ones (common on mobile networks).
2. System Architecture & Core Working Principles Below is a minimal, educational Python implementation of the Double Ratchet portion. It uses the cryptography library for elliptic curve DH (Curve25519) and HKDFISHA256 for key derivation. Do not use this code in production ; it omits many safety checks, replay protection, and proper error handling.
Signal’s designers published a formal security model in the “Signal Protocol: A Formal Security Analysis” (2016). The protocol satisfies several wellIstudied properties: The proofs rely on the random oracle model and assume the hardness of the Curve25519 DiffieIHellman problem . Formal verification tools such as ProVerif and Tamarin have been used to validate the protocol’s claims, and the results are publicly available (see the Resources section).
These deployments illustrate the protocol’s flexibility: it can be used for pure peerItoIpeer messaging, as a building block for group protocols, or as part of a larger encrypted communication stack. Staying up to date with these developments is crucial for anyone integrating SignalIstyle encryption into new products. The Signal Protocol represents a landmark achievement in practical cryptography. By weaving together X3DH, the Double Ratchet, and careful message formatting, it delivers: Whether you are building a new messaging app, securing IoT device communications, or simply curious about modern cryptographic protocols, understanding Signal equips you with a solid foundation for endItoIend privacy.
Signal Protocol Specification – The definitive technical description maintained by the Signal Foundation. Signal Protocol Specification (PDF) The Double Ratchet Algorithm – Detailed walkIthrough and formal analysis by the protocol’s authors. The Double Ratchet Algorithm (PDF) Moxie Marlinspike’s Blog on Sealed Sender – Insight into the latest metadataIhiding extension. Sealed Sender: Hiding Metadata from the Server Matrix.org – Olm and Megolm – How the Signal Ratchet is adapted for group chat in the Matrix ecosystem. Olm & Megolm Cryptographic Ratchets Formal Verification of Signal – Tamarin proof scripts and analysis for the Signal Protocol. Signal Protocol Formal Verification (GitHub) Audience : This post is intended for security researchers, cryptographers, and engineers with a deep interest in the technical underpinnings of secure messaging protocols. It assumes familiarity with modern cryptographic primitives, end-to-end encryption (E2EE), forward secrecy concepts, post-compromise security, post-quantum cryptography, formal verification tools (like ProVerif and Tamarin), secure software development practices, and related operational considerations (such as reproducible builds and user verification methods).
Scope : This analysis reflects the state of the Signal Protocol as of late 2024. It covers foundational concepts such as the Double Ratchet and X3DH, the introduction of PQXDH (Post-Quantum X3DH), formal verification efforts, platform-specific memory-hardening techniques, hardware-backed key management, user verification methods (Safety Numbers), multi-device session handling, ephemeral messages, security boundaries, supply chain security considerations, known implementation pitfalls, and potential future evolutions (including references to MLS). While comprehensive, this post should be supplemented by the latest official specifications, recent academic research, code-level audits, benchmark results, formal verification artifacts, and community analyses.
Disclaimer : The Signal ecosystem and the Signal Protocol are actively maintained and improved. Parameters, code details, and protocol enhancements may have changed since this writing. Verify specifics against the latest official Signal documentation, code commits, NIST PQC standards, research papers, and audit reports. Peer review by cryptography experts is recommended prior to relying on these details for critical security decisions.
The Signal Protocol , widely recognized for powering Signal Messenger and other secure messaging apps, is designed to ensure that messages and calls remain confidential and tamper-resistant against a wide range of adversaries. Future-proofing against large-scale quantum adversaries is now part of the threat model, with PQXDH ensuring that even if a quantum computer becomes capable of breaking elliptic curve assumptions, the post-quantum KEM layer will preserve message confidentiality.
Overview of the Signal Protocol threat model, highlighting the distinction between threats it mitigates (e.g., network-level attacks, server compromise) and those out of scope (e.g., active device compromise). Keys are never stored in plaintext if hardware support is present. Ephemeral private keys and intermediate values are zeroized after use, helping to prevent compromise by runtime memory inspection.
X3DH (Extended Triple Diffie-Hellman) establishes a shared secret without prior contact. It combines multiple Diffie-Hellman operations (DH1–DH4) that feed into an HKDF to derive a root key. Historically, X3DH relies solely on elliptic curve assumptions (X25519). X3DH and PQXDH combined handshake flow. The classical X3DH components (left) provide immediate security while the PQXDH addition (right) provides quantum resistance. Both feed secrets into HKDF to derive the Double Ratchet’s root key.
X3DH’s classical security may be broken in a future where quantum computers can crack elliptic curve cryptography. PQXDH pairs X25519 with a post-quantum KEM (e.g., CRYSTALS-Kyber ) to achieve hybrid security , meaning an adversary must defeat both the classical ECC layer and the post-quantum layer simultaneously. Both secrets are combined via HKDF, so breaking security requires simultaneously defeating both ECC and PQ layers—significantly raising the bar for attackers.
Internal benchmarks show PQXDH adds only ~1–3ms to the handshake on mobile devices. On desktop platforms with hardware acceleration, overhead is negligible. Future improvements to PQC algorithms and optimized code may further reduce these costs. After the initial handshake (X3DH or PQXDH), the Double Ratchet manages continuous re-keying and secure forward secrecy: The Double Ratchet protocol uses DH and symmetric ratchets for forward secrecy and post-compromise security. Each message key is used once and never reused, ensuring old traffic cannot be decrypted if new keys are compromised.
Independent audits (both internal and external) plus academic research have consistently validated the protocol’s security goals. Recent proofs even confirm no attacker can break forward secrecy under widely accepted assumptions. Group messaging and message-level operations remain efficient. As PQC algorithms mature, these overheads may drop further.
Mitigations include rigorous code reviews, test harnesses for edge cases, and platform-specific checklists. Safety Numbers and QR codes give users a simple, out-of-band way to confirm identity keys. If keys change unexpectedly (e.g., new device or potential MITM attempt), the app warns users. This system extends to multi-device contexts, although users should re-verify each device to maintain trust consistency.
The multi-device architecture for Signal. Each linked device maintains its own state, preserving forward secrecy. The key distribution server helps register device identity keys but does not have message access. 3. Software Implementation, Frameworks & Protocols Ephemeral (disappearing) messages auto-delete after a set interval. While forward secrecy prevents decrypting old messages once ratchets advance, recipients can always screenshot or record content prior to deletion. Future enhancements may integrate ephemeral messaging with encrypted backup policies to reduce risk of indefinite retention.
Comprehensive build and verification pipeline for Signal. Multiple steps—from source code review to final distribution—ensure that no hidden changes can be introduced without being detected. Messaging Layer Security (MLS) is a new standard for large-scale, secure group chats. Future work may explore: Beyond correct cryptographic design, robust implementation must address side-channels: Metadata Reduction : Research into privacy-preserving contact discovery, anonymous credentials, and minimizing trust in servers.
Formal Verification Expansion : Extending machine-checked proofs to full-group messaging, ephemeral messaging, and advanced PQ constructs. Continuous Improvement : The protocol evolves as cryptographic standards mature. We plan to reevaluate these details in mid-2025, once new PQC standards are finalized.
The Signal Protocol sets a high bar for secure messaging. Its well-known features—end-to-end encryption, forward secrecy, and deniability—are now fortified by post-quantum security (via PQXDH), extensive formal verification , robust memory management , and supply chain integrity measures. While challenges remain—particularly regarding post-quantum transitions, large-group protocols, and ongoing metadata minimization—the Signal ecosystem is well-positioned to adapt alongside emerging standards like MLS.
Double Ratchet Paper (Cohn-Gordon et al.) : https://signal.org/docs/specifications/doubleratchet/ X3DH & PQXDH Specs + PQXDH Whitepaper : https://signal.org/docs/specifications/x3dh/ https://signal.org/blog/pqxdh/ libsignal-protocol-c and Rust Bindings : https://github.com/signalapp/libsignal-protocol-c https://github.com/signalapp/libsignal Audits & Community Analyses : Independent security audits, community-driven code reviews, and academic research. Check the latest audit reports for updates and commentary.
A comprehensive technical breakdown of the Signal Protocol — from the Extended Triple Diffie-Hellman handshake to the Double Ratchet algorithm, forward secrecy, and post-compromise security. How the protocol that protects 2 billion WhatsApp users actually functions at every layer. Over 2 billion people use the Signal Protocol daily without knowing it. WhatsApp adopted it in 2016. Google Messages enabled it by default in 2023. Facebook Messenger completed its rollout in late 2024. The protocol that Moxie Marlinspike and Trevor Perrin published in 2013 – originally called the Axolotl Ratchet – has become the most widely deployed end-to-end encryption system in human history.
This dominance is not an accident of market timing. The Signal Protocol solves a problem that prior encrypted messaging systems could not: it provides forward secrecy and post-compromise security in an asynchronous environment where one party may be offline. It accomplishes this through two interlocking mechanisms – the Extended Triple Diffie-Hellman (X3DH) key agreement and the Double Ratchet algorithm – that together produce a new encryption key for every single message sent.
The result is a system where compromising a single key reveals exactly one message. The past is protected. The future self-heals. And the entire construction rests on elliptic curve cryptography that has been publicly scrutinized for over a decade. Before the Signal Protocol, encrypted messaging fell into two camps. PGP-style systems used long-lived static keys: if your key was compromised, every message ever encrypted to that key was exposed. OTR (Off-the-Record Messaging) introduced forward secrecy through ephemeral Diffie-Hellman exchanges, but required both parties to be online simultaneously – a non-starter for mobile messaging where messages must be deliverable to offline recipients.
The core challenge: how do you establish a shared secret with someone who is not currently connected to the network, while still achieving forward secrecy? The Signal Protocol’s answer is a server-stored bundle of precomputed public keys – the prekey bundle – combined with a key agreement protocol that derives an initial shared secret without real-time interaction.
X3DH is the initial key agreement protocol. It runs once, at the beginning of a conversation, to establish the root key material that feeds the Double Ratchet. Identity Key (IK). A long-lived Curve25519 key pair. This is the user’s persistent cryptographic identity. It changes only if the user reinstalls the application. Signal displays a “safety number” derived from both parties’ identity keys, allowing users to verify they are communicating with the correct person.
Signed Pre-Key (SPK). A medium-lived Curve25519 key pair, signed by the identity key. Rotated periodically (typically every 7-30 days). The signature proves the pre-key belongs to the identity key holder. One-Time Pre-Keys (OPK). A pool of single-use Curve25519 key pairs uploaded to the server. Each one is used exactly once and then deleted. If the pool is exhausted, X3DH proceeds without a one-time pre-key, at a slight reduction in forward secrecy for the initial message.
When Alice wants to message Bob for the first time, she fetches Bob’s prekey bundle from the server: Bob’s identity key IK_B, signed pre-key SPK_B, and one one-time pre-key OPK_B. The shared secret SK is derived by feeding the concatenation of DH1 || DH2 || DH3 || DH4 into HKDF (HMAC-based Key Derivation Function): Each DH computation serves a specific security purpose. DH1 and DH2 provide mutual authentication – both parties’ identity keys participate. DH3 provides forward secrecy against compromise of identity keys. DH4 provides one-time pre-key forward secrecy, ensuring that even if Bob’s signed pre-key is compromised, messages sent using different one-time pre-keys remain protected.
Alice then sends her initial message along with her identity key and ephemeral key. Bob, upon receiving this, performs the same four DH computations (with the roles reversed) and derives the identical shared secret SK. The server never sees SK. The server never sees any of the DH outputs. The server stores only public keys. This is why the protocol functions in a zero-knowledge architecture: the infrastructure operator has no material to decrypt.
X3DH establishes the initial shared secret. The Double Ratchet takes over from there, generating a unique encryption key for every subsequent message. It combines two ratcheting mechanisms: a Diffie-Hellman ratchet and a symmetric-key ratchet. A KDF chain takes a key and some input, runs them through a key derivation function, and produces two outputs: a new chain key and a message key. The chain key feeds the next iteration. The message key encrypts one message and is then deleted.
This is a one-way function. Given Chain Key[n+1], you cannot recover Chain Key[n]. Given Message Key[n], you cannot derive any other message key. The chain moves forward and cannot be reversed. 4. Practical Deployment, Analysis & Case Studies The symmetric ratchet alone would provide forward secrecy but not post-compromise security. If an attacker learns the current chain key, they can derive all future message keys in that chain. The DH ratchet solves this.
Each time a user sends a message, they may include a new ephemeral DH public key. When the other party responds, they also generate a new ephemeral key. Each exchange of ephemeral keys performs a new DH computation, and the result is fed into the root chain to derive fresh sending and receiving chain keys. The term “Double Ratchet” refers to this combination: the symmetric ratchet advances within a chain (forward secrecy), while the DH ratchet periodically introduces fresh randomness (post-compromise security). Even if an attacker compromises the current state completely, the next DH ratchet step introduces entropy that the attacker does not control, locking them out.
Each message key produced by the sending chain is used with AES-256-GCM (in Signal’s implementation, actually AES-256-CBC + HMAC-SHA256, though the security properties are equivalent). The associated data includes the message header containing the sender’s current DH ratchet key, the message number within the current chain, and the number of messages in the previous chain.
After encryption, the message key is deleted. After decryption, the message key is deleted. No key material persists beyond its single use. Forward secrecy means that compromise of long-term keys does not retroactively expose past session keys. In the Signal Protocol, this property holds at multiple granularities. Compromise of an identity key does not expose past messages (because the ephemeral DH keys used to derive those message keys have been deleted). Compromise of a chain key does not expose messages encrypted under previous chain keys (because the KDF chain is one-way).
Post-compromise security (also called “future secrecy” or “self-healing”) means that if an attacker compromises the current state, the protocol recovers confidentiality after a bounded number of messages. In the Signal Protocol, this happens at the next DH ratchet step – typically the next time both parties exchange messages. A 2016 formal analysis by Cohn-Gordon et al. proved that the Double Ratchet achieves this property under standard cryptographic assumptions.
The practical implication: an attacker who gains access to a device’s current cryptographic state can read messages in the current chain. But once the conversation partner sends a reply (triggering a DH ratchet), the attacker is locked out. They must re-compromise the device to regain access. This is a fundamentally different security model from systems like PGP, where a single key compromise is catastrophic and permanent.
Mobile networks are unreliable. Messages arrive out of order. They arrive after long delays. The Double Ratchet handles this through message numbering and stored message keys. Each message header includes a chain counter (which DH ratchet epoch it belongs to) and a message number within that chain. If a receiving client detects a gap – say, it receives message 5 before message 3 – it ratchets the receiving chain forward, stores the skipped message keys, and uses them when the delayed messages arrive.
Stored message keys have limits. Signal’s implementation caps the number of stored keys (typically around 2,000) and applies a time-based expiration. If a message is delayed beyond this window, it becomes undecryptable – a deliberate tradeoff that bounds the state an attacker could exploit. The server does not see message content, message keys, chain keys, or the root key. The DH ratchet public keys are ephemeral and reveal nothing about the shared secrets derived from them (assuming the ECDLP is hard, which for Curve25519 requires approximately 2^128 operations to break).
This is significant for metadata analysis. While the Signal Protocol protects message content absolutely, it does not inherently protect metadata. Signal (the application) addresses this separately through features like Sealed Sender (which encrypts the sender’s identity from the server) and has explored SGX-based contact discovery to minimize metadata exposure. The Signal Protocol is one of the most formally analyzed cryptographic protocols in existence. Key results include: Deniability deserves mention. The Signal Protocol provides cryptographic deniability: after a conversation, neither party can prove to a third party what the other said. This is because the MAC keys are shared – either party could have generated any message in the conversation. This property is lost when messages are forwarded or screenshots are taken, but it holds at the cryptographic level.
No protocol is invulnerable. The Signal Protocol’s actual attack surface is not the cryptography itself – it is everything around it. Device compromise. If an attacker gains access to the device (malware, physical access, forensic tools), they can read decrypted messages in memory or extract the current ratchet state. The protocol cannot protect against a compromised endpoint. This is the single most significant limitation of any end-to-end encryption system.
Metadata. As noted, the protocol does not inherently protect who is talking to whom, when, or how often. Network-level surveillance can infer social graphs even without message content. Key verification. The protocol assumes users verify identity keys through an out-of-band channel (comparing safety numbers in person or via a separate secure channel). In practice, almost no one does this. A compromised server could perform a man-in-the-middle attack during the initial X3DH handshake by substituting its own keys. Signal mitigates this with key transparency logs, but the risk remains in deployments where users skip verification.
Group messaging. Signal’s group protocol (Sender Keys) has different security properties than the pairwise Double Ratchet. Forward secrecy in groups requires re-keying when members leave, and post-compromise security is weaker because a single compromised sender key affects all group members until the next re-key. The MLS (Messaging Layer Security) protocol, now standardized as RFC 9420, addresses some of these limitations for large groups.
The protocol’s design is open and well-documented. Beyond WhatsApp and Google Messages: Each implementation makes different tradeoffs in key management, group handling, and metadata protection. The core Double Ratchet algorithm remains remarkably consistent across all of them. Stealth Cloud’s Ghost Chat architecture draws from the same design philosophy that makes the Signal Protocol effective: ephemeral keys, forward secrecy, and the principle that cryptographic state should exist for exactly as long as it is needed and not one millisecond longer.
Where the Signal Protocol maintains ratchet state for ongoing conversations, Ghost Chat operates on an even more aggressive deletion model. Sessions are ephemeral by design. There is no persistent conversation history to protect because there is no persistent conversation history at all. The cryptographic shredding that occurs at session termination destroys key material irrecoverably – not through file deletion, but through the destruction of the keys that would be required to decrypt any stored ciphertext.
The Double Ratchet proves that forward secrecy and post-compromise security can coexist in a practical system. Stealth Cloud extends this insight: if you combine aggressive key lifecycle management with zero-knowledge architecture and zero-persistence infrastructure, you can build communication systems where the question is not “how long until the key expires” but rather “the key was never stored in the first place.” Cryptography pages are anchored in standards, formal specifications, implementation documentation, and peer-reviewed security research. Editorial conclusions separate cryptographic properties from deployment assumptions.
Stealth Cloud separates three claims on every high-stakes privacy page: what the vendor or institution says, what the architecture can actually enforce, and what risk remains when data, metadata, keys, logs, or legal process are considered together. This source trail is selected from the page topic, tags, claim language, and editorial section. It prioritizes primary documents, technical standards, provider documentation, regulator pages, transparency reports, and reputable research over commentary.
Last source review: May 18, 2026. Source links are provided for auditability; page-specific claims remain subject to correction when primary evidence changes. Continue through the related Stealth Cloud coverage below. These links connect this page to its parent vertical, adjacent topic files, glossary context, and nearby canonical analysis rather than leaving it as an isolated article.
A deep technical analysis of end-to-end encryption — the Signal Protocol, Double Ratchet algorithm, X3DH key exchange, metadata protection failures, and the critical distinction … 5. Performance Evaluation & Extended Technical Observations A comprehensive technical breakdown of Elliptic Curve Cryptography — from the algebraic geometry of curves over finite fields to the discrete logarithm problem, secp256k1, and … A comprehensive analysis of key management in zero-knowledge architectures — key generation, lifecycle, rotation, recovery, and destruction. Why key management is the single point … A deep technical breakdown of AES-256-GCM — how the block cipher works, why Galois/Counter Mode provides authenticated encryption, and how the Web Crypto API makes it available in … A comparison of cloud-hosted Hardware Security Modules and the browser-native Web Crypto API for cryptographic key management. Examining trust models, performance, key extraction, … A technical comparison of AES symmetric encryption and RSA asymmetric encryption. Examining key sizes, performance benchmarks, security margins, quantum resistance, and how modern … A Zero-Knowledge Rollup (ZK-Rollup) is a Layer 2 scaling solution that executes transactions off-chain and posts cryptographic validity proofs to the Layer 1 blockchain, achieving … The Web Crypto API is a W3C standard JavaScript interface that provides cryptographic primitives—key generation, encryption, decryption, signing, hashing, and key … A comprehensive technical comparison of zk-SNARKs and zk-STARKs — the two dominant zero-knowledge proof systems.
From the mathematical foundations and trusted setup debate to … A deep technical explainer on zero-knowledge proofs — from the cave analogy to zk-SNARKs and zk-STARKs. How ZKPs work, why they matter for privacy, and where they are deployed in … Donovan Vanderbilt leads Stealth Cloud's analysis of AI privacy, cryptographic infrastructure, cloud jurisdiction, and privacy technology markets. Stealth Cloud Intelligence supports source review, correction handling, and ongoing editorial maintenance.
Used by Google AdSense for ad delivery, fraud prevention, frequency capping, reporting, and, where you consent, personalized advertising. You can opt out of personalized ads at Google Ads Settings . Signal Protocol is an end-to-end encrypted messaging protocol suite for asynchronous instant messaging, presented in the literature as the main successor to Off-the-Record ( OTR ) for mobile settings and deployed as the cryptographic basis of systems such as Signal and WhatsApp. Across the surveyed and mechanized analyses, its core structure combines X3DH for asynchronous session establishment with the Double Ratchet for ongoing message protection, yielding confidentiality, integrity, forward secrecy, and, in later formal-comparison literature, post-compromise security, subject to the protocol’s verification and deployment assumptions ( Johansen et al., 2018 , Ginesin et al., 2024 , Rastogi et al., 2017 ).
The protocol is described as extending the OTR tradition into asynchronous messaging. In the comparative survey literature, OTR is treated as the baseline secure messaging protocol that popularized deniability, frequent key refresh, and forward secrecy, but remained limited by its synchronous design. Signal is then presented as the protocol family that incorporated asynchronous communication directly, thereby making OTR-like security properties suitable for mobile and offline messaging.
In the WhatsApp-oriented exposition, Signal Protocol—formerly Axolotl—is further characterized as a “compact derivative” of OTR, especially in its repeated Diffie–Hellman exchanges and ratcheting ( Johansen et al., 2018 , Rastogi et al., 2017 ). This design orientation explains why Signal is repeatedly associated with mobile messaging rather than merely with two-party authenticated key exchange. The survey literature summarizes its goals as end-to-end encryption plus “advanced security properties such as forward secrecy and future secrecy,” while the WhatsApp analysis emphasizes “plausible deniability and forward-secret asynchronous communications” on mobile devices. A plausible implication is that Signal’s defining contribution is not a single primitive but a composition: offline-capable session bootstrap together with continual key evolution during conversation ( Johansen et al., 2018 , Rastogi et al., 2017 ).
The protocol is commonly described through a prekey hierarchy and a ratcheting session state. In the WhatsApp exposition, Signal uses three kinds of keys: a long-term identity key pair, a medium-term signed prekey, and one-time prekeys; all are Curve25519 key pairs. The initiator retrieves the recipient’s public material from the server, verifies the signed prekey, generates a fresh ephemeral key, and derives a shared secret that initializes the session state.
D H 1 = D H ( I K a ( s e c ) , S K b ( p u b ) ) DH_1 = DH(IK_a(sec), SK_b(pub)) D H 1 I = DH ( I K a I ( sec ) , S K b I ( p u b )) D H 2 = D H ( E K a ( s e c ) , I K b ( p u b ) ) DH_2 = DH(EK_a(sec), IK_b(pub)) D H 2 I = DH ( E K a I ( sec ) , I K b I ( p u b )) D H 3 = D H ( E K a ( s e c ) , S K b ( p u b ) ) DH_3 = DH(EK_a(sec), SK_b(pub)) D H 3 I = DH ( E K a I ( sec ) , S K b I ( p u b )) D H 4 = D H ( E K a ( s e c ) , O T K b ( p u b ) ) DH_4 = DH(EK_a(sec), OTK_b(pub)) D H 4 I = DH ( E K a I ( sec ) , OT K b I ( p u b )) K = K D F ( D H 1 I D H 2 I D H 3 I D H 4 ) . K = KDF(DH_1 \,\|\, DH_2 \,\|\, DH_3 \,\|\, DH_4). K = KD F ( D H 1 I I D H 2 I I D H 3 I I D H 4 I ) .
The resulting secret initializes the Double Ratchet. In the WhatsApp account, HKDF derives a root key and chain keys from the combined ECDH output, and the session remains associated with the device until events such as reinstallation or device change. The same literature describes the Double Ratchet as maintaining three chains—a root chain, a sending chain, and a receiving chain—where Diffie–Hellman outputs feed the root chain and a symmetric-key ratchet advances per message. At the per-message level, the WhatsApp exposition gives Message key = HMAC-SHA256 I ( chain key , 0 x 01 ) \text{Message key} = \operatorname{HMAC\text{-}SHA256}(\text{chain key}, 0\text{x}01) Message key = HMAC - SHA256 ( chain key , 0 x 01 ) Chain key = HMAC-SHA256 I ( chain key , 0 x 02 ) , \text{Chain key} = \operatorname{HMAC\text{-}SHA256}(\text{chain key}, 0\text{x}02), Chain key = HMAC - SHA256 ( chain key , 0 x 02 ) , capturing the basic ratchet step in which each send consumes the current chain key, derives a message key, and advances the chain state ( Rastogi et al., 2017 , Johansen et al., 2018 , Jefferys et al., 2020 ).
Curve25519 is consistently identified as the elliptic-curve basis for the public-key operations. The WhatsApp analysis describes it as suitable for ECDH key agreement, efficient, and resistant to timing attacks. Within this architecture, signed prekeys bind medium-term public keys to long-term identity keys, while one-time prekeys support asynchronous initiation without requiring the recipient to be online ( Rastogi et al., 2017 ).
The literature attributes a broad security profile to Signal. In the WhatsApp analysis, the protocol protects the contents of text messages, calls, videos, audio, and files in transit; the same paper credits it with forward secrecy, plausible deniability, and substantial protection against man-in-the-middle attacks . The comparative survey presents Signal as inheriting and extending OTR’s deniability story, and summarizes the Double Ratchet using the three specification properties “Resilience,” “Forward security,” and “Break-in recovery.” The mechanized comparison literature treats Signal as the reference two-party protocol for confidentiality, integrity, forward secrecy, and post-compromise security, with the latter two especially attributed to the Double Ratchet ( Rastogi et al., 2017 , Johansen et al., 2018 , Ginesin et al., 2024 ).
The authentication model is more conditional than simplified descriptions often imply. Signal’s signed prekeys provide an identity-bound medium-term key, but the surveyed papers repeatedly tie active-adversary resistance to out-of-band identity verification. WhatsApp exposes QR-code verification and comparison of a 60-digit number; the survey treats safety numbers, QR codes, and out-of-band comparison as necessary to resist man-in-the-middle attacks in the active-adversary model. The mechanized Matrix comparison makes the same point more sharply: Signal depends on off-band verification of identity keys, and without that verification the protocol is vulnerable to an unknown key-share attack. The later proposal for automated in-band MitM detection is explicitly motivated by the observation that user awareness is poor when it comes to authenticating keys in instant messaging applications ( Johansen et al., 2018 , Ginesin et al., 2024 , Teng et al., 2024 ).
Deniability is also treated with nuance. The WhatsApp analysis explains plausible deniability by noting that both parties derive the shared secret and the resulting MAC keys, so a receiver can verify a message but can also later produce MACs, weakening cryptographic proof of authorship. At the same time, later server-assisted extensions explicitly exclude deniability from the set of preserved Signal guarantees, which suggests that deniability in deployed systems is sensitive to surrounding trust and logging assumptions rather than being an invariant of the ratchet alone ( Rastogi et al., 2017 , Teng et al., 2024 ).
The protocol’s deployment history is marked by extensive reuse and nontrivial divergence. The comparative survey examines six applications—Signal, WhatsApp, Wire, Viber, Riot, and Telegram—and treats Signal as the central protocol reference point. Signal and WhatsApp are described as direct Signal implementations; Wire implements the Proteus protocol, “heavily based on the Signal protocol, but re-implemented in-house”; Riot uses Matrix, whose Olm algorithm is said to be based on the Signal protocol for one-to-one conversations. The survey’s central finding is that sharing the Signal protocol does not guarantee identical security, privacy, or usability outcomes: implementation and product decisions around key changes, verification, device management, and defaults materially affect real security ( Johansen et al., 2018 ).
The same survey gives concrete examples. In its 2017 experiments, Signal took the conservative stance after a key change: it marked messages as undelivered, notified the sender that the peer had “a new security number,” and blocked further sending until re-verification. WhatsApp made the opposite tradeoff: it notified about key changes but did not block by default in the observed version, and it was the only app that re-encrypted and resent an undelivered message after the recipient reinstalled and received new keys. Wire allowed multiple devices and exposed per-device fingerprints, but did not automatically notify peers about device-key changes. Riot inherited some Signal-style properties in one-to-one mode through Olm, but its group and multi-device behavior depended on Megolm and, in the survey snapshot, encryption was still “in beta form” and “not turned on by default” ( Johansen et al., 2018 ).
A distinct line of reuse appears in Session. That system explicitly states that it “uses the Signal protocol” and “does not modify the fundamentals of the Signal protocol,” but changes the surrounding architecture: identities are X25519 public keys rather than phone numbers or email addresses, prekey bundles are distributed via friend requests rather than a centralized prekey server, and messages are transported and stored through onion requests and decentralized swarms. This suggests that Signal is often treated as a reusable cryptographic substrate rather than as a complete application architecture ( Jefferys et al., 2020 ).
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Signal%20Protocol • https://en.wikipedia.org/wiki/Signal%20%28software%29 • https://en.wikipedia.org/wiki/Session%20Initiation%20Protocol • https://martinuke0.github.io/posts/2026-03-25-understanding-the-signal-protocol-architecture-security-and-realworld-applicat ions/ • https://profincognito.me/blog/security/signal-security-architecture/ • https://stealthcloud.ai/cryptography/signal-protocol-deep-dive/ • https://www.emergentmind.com/topics/signal-protocol
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Secure Mobile Messaging Application Using Signal Protocol.
[*] Metasploit Scan Running on Target Subnet for Secure Mobile Messaging Application Using Signal Protocol... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |