Complete Technical Paper Content — Secure Multicast Communication System In Networks
Overview & System Context
Secure Multicast Communication System In Networks: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9514 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background In computer networking, multicast is a type of group communication where data transmission is addressed to a group of destination computers simultaneously. Multicast can be one-to-many or many-to-many distribution. Multicast differs from physical layer point-to-multipoint communication. Group communication may either be application layer multicast or network-assisted multicast, where the latter makes it possible for the source to efficiently send to the group in a single transmission. Copies are automatically created in other network elements, such as routers, switches and cellular network base stations, but only to network segments that currently contain members of the group. Network assisted multicast may be implemented at the data link layer using one-to-many addressing and switching such as Ethernet multicast addressing, Asynchronous Transfer Mode (ATM), point-to-multipoint virtual circuits (P2MP) or InfiniBand multicast. Network-assisted multicast may also be implemented at the Internet layer using IP multicast. In IP multicast, the implementation of the multicast concept occurs at the IP routing level, where routers create optimal distribution paths for datagrams sent to a multicast destination address. Multicast is often employed in Internet Protocol (IP) applications of streaming media, such as IPTV and multipoint videoconferencing.
IP multicast is a technique for one-to-many communication over an IP network. The destination nodes send Internet Group Management Protocol membership report and leave group messages, for example, in the case of IPTV when the user changes from one TV channel to another. IP multicast scales to a larger receiver population by not requiring prior knowledge of who or how many receivers there are. Multicast uses network infrastructure efficiently by requiring the source to send a packet only once, even if it needs to be delivered to a large number of receivers. The nodes in the network take care of replicating the packet to reach multiple receivers only when necessary. The most common transport layer protocol to use multicast addressing is User Datagram Protocol (UDP). By its nature, UDP is not reliable—messages may be lost or delivered out of order. By adding loss detection and retransmission mechanisms, reliable multicast has been implemented on top of UDP or IP by various middleware products, e.g. those that implement the Real-Time Publish-Subscribe (RTPS) Protocol of the Object Management Group (OMG) Data Distribution Service (DDS) standard, as well as by special transport protocols such as Pragmatic General Multicast (PGM). IP multicast is always available within the local subnet. Achieving IP multicast service over a wider area requires multicast routing. Many networks, including the Internet, do not support multicast routing.
Multicast routing functionality is available in enterprise-grade network equipment, but typically needs to be configured by a network administrator. The Internet Group Management Protocol is used to control IP multicast delivery. IP multicast is a method of sending Internet Protocol (IP) datagrams to a group of interested receivers in a single transmission. It is the IP-specific form of multicast and is used for streaming media and other network applications. It uses specially reserved multicast address blocks in IPv4 and IPv6. Protocols associated with IP multicast include Internet Group Management Protocol, Protocol Independent Multicast, and Multicast VLAN Registration. IGMP snooping is used to manage IP multicast traffic on layer-2 networks. IP multicast is described in RFC 1112. IP multicast was first standardized in 1986. Its specifications have been augmented in RFC 4604 to include group management and in RFC 5771 to include administratively scoped addresses.
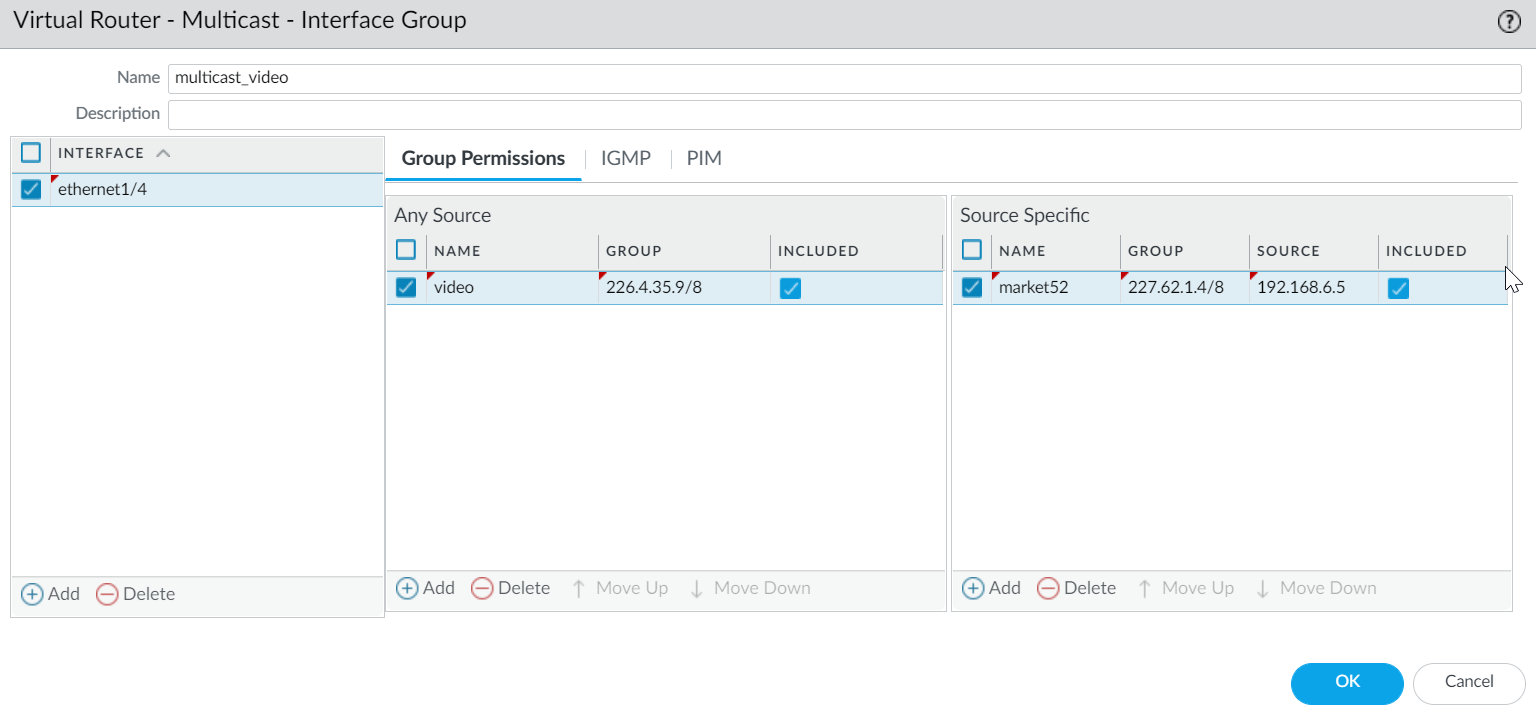
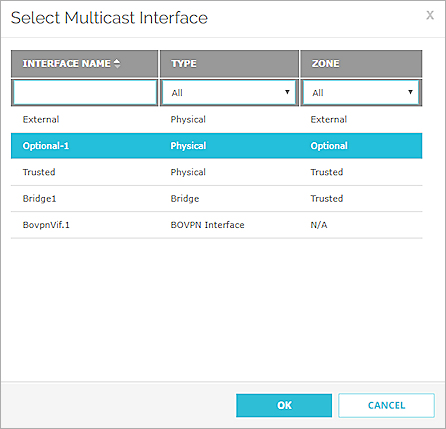
Internet Group Management Protocol (IGMP) Protocol Independent Multicast (PIM) Distance Vector Multicast Routing Protocol (DVMRP) Multicast Open Shortest Path First (MOSPF) Multicast BGP (MBGP) Multicast Source Discovery Protocol (MSDP) Multicast Listener Discovery (MLD) GARP Multicast Registration Protocol (GMRP) Figure 1: Configure IP Multicast Multicast, by its very nature, is not a connection-oriented mechanism, so protocols such as TCP, which allow for retransmission of missing packets, are not appropriate. For applications such as streaming audio and video, the occasional dropped packet is not a problem. But for the distribution of critical data, a mechanism is required for requesting retransmission. One such scheme, proposed by Cisco, is PGM (originally Pretty Good Multicasting, but changed for trademark reasons to Pragmatic General Multicast), documented in RFC 3208. In this scheme, multicast packets have sequence numbers, and when a packet is missed, a recipient can request that the packet be re-multicast with other members of the multicast group, ignoring the replacement data if not needed. An expanded version, PGM-CC, has attempted to make IP Multicasting more TCP friendly by stepping the entire group down to the bandwidth available by the worst receiver. Two other schemes documented by the Internet Engineering Task Force (IETF) are: the standards-track protocol NACK-Oriented Reliable Multicast (NORM), documented in RFC 5740 and RFC 5401, and the protocol File Delivery over Unidirectional Transport (FLUTE), documented in RFC 6726. Open-source, in addition to proprietary, implementations exist for these. Other such protocols exist, such as Scalable Reliable Multicast, and are defined by a variety of sources. Such protocols vary in the means of error detection, the mechanisms used in error recovery, the scalability of such recovery, and the underlying ideas involved in what it means to be reliable. A list of reliable multicast protocols from the ACM SIGCOMM Multicast Workshop, August 27, 1996, documents a number of approaches to the problem. Independent groups like the Internet Protocol Multicast Standards Initiative (IPMSI) have claimed that the lack of a truly scalable Secure Reliable IP Multicast protocol, like the proposed Secure Multicast for Advanced Repeating of Television (SMART), has hampered the adoption of IP multicast in inter-domain routing. The lack of a widely adopted system that has AES-level security and scalable reliability has kept mass media transmissions of sporting events (like the Super Bowl) and/or breaking news events from being transmitted on the Public Internet. Reliable IP Multicasting protocols, such as PGM and SMART, are experimental; the only standards-track protocol is NORM (the standards-track revision of RFC 3941 is specified in RFC 5401, the standards-track revision of RFC 3940 is specified in RFC 5740).
In computer science, computer engineering, and telecommunications, a network is a group of communicating computers and peripherals called hosts, which communicate data to other hosts via communication protocols, as facilitated by networking hardware. Within a computer network, hosts are identified by network addresses, which allow networking hardware to locate and identify hosts. Hosts may also have hostnames, memorable labels for the host nodes, which can be mapped to a network address using a hosts file or a name server such as Domain Name Service. The physical medium that supports information exchange includes wired media like copper cables, optical fibers, and wireless radio-frequency media. The arrangement of hosts and hardware within a network architecture is known as the network topology. The first computer network was created in 1940 when George Stibitz connected a terminal at Dartmouth to his Complex Number Calculator at Bell Labs in New York.
Today, almost all computers are connected to a computer network, such as the global Internet or embedded networks such as those found in many modern electronic devices. Many applications have only limited functionality unless they are connected to a network. Networks support applications and services, such as access to the World Wide Web, digital video and audio, application and storage servers, printers, and email and instant messaging applications.
The transmission media used to link devices to form a computer network include electrical cable, optical fiber, and free space. In the OSI model, the software to handle the media is defined at layers 1 and 2 — the physical layer and the data link layer. Common examples of networking technologies include: Ethernet is a widely adopted family of networking technologies that use copper and fiber media in local area networks (LAN).
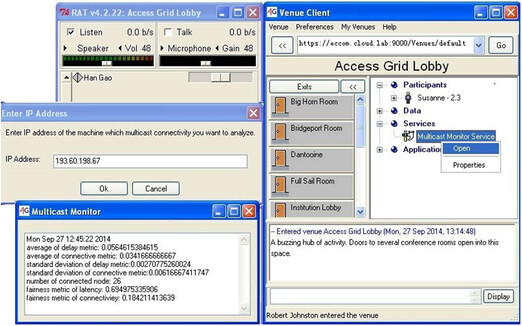
The media and protocol standards that enable communication between networked devices over Ethernet are defined by IEEE 802.3. Wireless LAN standards, which use radio waves. Some standards use infrared signals as a transmission medium. Power line communication uses a building's power cabling to transmit data. Figure 2: Multicast middleware for performance and topology analysis of ...
Coaxial cable is widely used for cable television systems, office buildings, and other work-sites for local area networks. Transmission speed ranges from 200 million bits per second to more than 500 million bits per second. ITU-T G.hn technology uses existing home wiring (coaxial cable, phone lines and power lines) to create a high-speed local area network. Twisted pair cabling is used for wired Ethernet and other standards. It typically consists of 4 pairs of copper cabling that can be utilized for both voice and data transmission. The use of two wires twisted together helps to reduce crosstalk and electromagnetic induction. The transmission speed ranges from 2 Mbit/s to 10 Gbit/s. Twisted pair cabling comes in two forms: unshielded twisted pair (UTP) and shielded twisted-pair (STP). Each form comes in several category ratings, designed for use in various scenarios.
An optical fiber is a glass fiber that carries pulses of light that represent data via lasers and optical amplifiers. Some advantages of optical fibers over metal wires are very low transmission loss and immunity to electrical interference. Using dense wave division multiplexing, optical fibers can simultaneously carry multiple streams of data on different wavelengths of light, which greatly increases the rate that data can be sent to up to trillions of bits per second. Optic fibers can be used for long runs of cable carrying very high data rates, and are used for undersea communications cables to interconnect continents.
There are two basic types of fiber optics, single-mode optical fiber (SMF) and multi-mode optical fiber (MMF). Network connections can be established wirelessly using radio or other electromagnetic means of communication. Terrestrial microwave – Terrestrial microwave communication uses Earth-based transmitters and receivers resembling satellite dishes. Terrestrial microwaves are in the low gigahertz range, which limits all communications to line-of-sight. Relay stations are spaced approximately 40 miles (64 km) apart. Communications satellites – Satellites also communicate via microwave. The satellites are stationed in space, typically in geosynchronous orbit 35,400 km (22,000 mi) above the equator.
These Earth-orbiting systems are capable of receiving and relaying voice, data, and TV signals. Cellular networks use several radio communications technologies. The systems divide the region covered into multiple geographic areas. Each area is served by a low-power transceiver. Radio and spread spectrum technologies – Wireless LANs use a high-frequency radio technology similar to digital cellular. Wireless LANs use spread spectrum technology to enable communication between multiple devices in a limited area. IEEE 802.11 defines a common flavor of open-standards wireless radio-wave technology known as Wi-Fi. Free-space optical communication uses visible or invisible light for communications. In most cases, line-of-sight propagation is used, which limits the physical positioning of communicating devices. Extending the Internet to interplanetary dimensions via radio waves and optical means, the Interplanetary Internet. IP over Avian Carriers was a humorous April fool's Request for Comments, issued as RFC 1149. It was implemented in real life in 2001. The last two cases have a large round-trip delay time, which gives slow two-way communication but does not prevent sending large amounts of information (they can have high throughput).
Figure 3: Configure Multicast Routing Apart from any physical transmission media, networks are built from additional basic system building blocks, such as network interface controllers, repeaters, hubs, bridges, switches, routers, modems, and firewalls. Any particular piece of equipment will frequently contain multiple building blocks and so may perform multiple functions.
A network interface controller (NIC) is computer hardware that connects the computer to the network media and has the ability to process low-level network information. For example, the NIC may have a connector for plugging in a cable, or an aerial for wireless transmission and reception, and the associated circuitry. In Ethernet networks, each NIC has a unique Media Access Control (MAC) address—usually stored in the controller's permanent memory. To avoid address conflicts between network devices, the Institute of Electrical and Electronics Engineers (IEEE) maintains and administers MAC address uniqueness. The size of an Ethernet MAC address is six octets. The three most significant octets are reserved to identify NIC manufacturers.
These manufacturers, using only their assigned prefixes, uniquely assign the three least-significant octets of every Ethernet interface they produce. A repeater is an electronic device that receives a network signal, cleans it of unnecessary noise and regenerates it. The signal is retransmitted at a higher power level, or to the other side of obstruction so that the signal can cover longer distances without degradation. In most twisted-pair Ethernet configurations, repeaters are required for cable that runs longer than 100 meters.
With fiber optics, repeaters can be tens or even hundreds of kilometers apart. Repeaters work on the physical layer of the OSI model but still require a small amount of time to regenerate the signal. This can cause a propagation delay that affects network performance and may affect proper function. As a result, many network architectures limit the number of repeaters used in a network, e.g., the Ethernet 5-4-3 rule. An Ethernet repeater with multiple ports is known as an Ethernet hub. In addition to reconditioning and distributing network signals, a repeater hub assists with collision detection and fault isolation for the network. Hubs and repeaters in LANs have been largely obsoleted by modern network switches.
Network bridges and network switches are distinct from a hub in that they only forward frames to the ports involved in the communication whereas a hub forwards to all ports. Bridges only have two ports but a switch can be thought of as a multi-port bridge. Switches normally have numerous ports, facilitating a star topology for devices, and for cascading additional switches. Bridges and switches operate at the data link layer (layer 2) of the OSI model and bridge traffic between two or more network segments to form a single local network. Both are devices that forward frames of data between ports based on the destination MAC address in each frame. They learn the association of physical ports to MAC addresses by examining the source addresses of received frames and only forward the frame when necessary. If an unknown destination MAC is targeted, the device broadcasts the request to all ports except the source, and discovers the location from the reply. Bridges and switches divide the network's collision domain but maintain a single broadcast domain. Network segmentation through bridging and switching helps break down a large, congested network into an aggregation of smaller, more efficient networks.
A router is an internetworking device that forwards packets between networks by processing the addressing or routing information included in the packet. The routing information is often processed in conjunction with the routing table. A router uses its routing table to determine where to forward packets and does not require broadcasting packets which is inefficient for very big networks.
Modems (modulator-demodulator) are used to connect network nodes via wire not originally designed for digital network traffic, or for wireless. To do this one or more carrier signals are modulated by the digital signal to produce an analog signal that can be tailored to give the required properties for transmission. Early modems modulated audio signals sent over a standard voice telephone line. Modems are still commonly used for telephone lines, using a digital subscriber line technology and cable television systems using DOCSIS technology.
A firewall is a network device or software for controlling network security and access rules. Firewalls are inserted in connections between secure internal networks and potentially insecure external networks such as the Internet. Firewalls are typically configured to reject access requests from unrecognized sources while allowing actions from recognized ones. The vital role firewalls play in network security grows in parallel with the constant increase in cyber attacks.
A communication protocol is a set of rules for exchanging information over a network. Communication protocols have various characteristics, such as being connection-oriented or connectionless, or using circuit switching or packet switching. In a protocol stack, often constructed per the OSI model, communications functions are divided into protocol layers, where each layer leverages the services of the layer below it until the lowest layer controls the hardware that sends information across the media. The use of protocol layering is ubiquitous across the field of computer networking. An important example of a protocol stack is HTTP, the World Wide Web protocol. HTTP runs over TCP over IP, the Internet protocols, which in turn run over IEEE 802.11, the Wi-Fi protocol. This stack is used between a wireless router and a personal computer when accessing the web.
Most modern computer networks use protocols based on packet-mode transmission. A network packet is a formatted unit of data carried by a packet-switched network. Packets consist of two types of data: control information and user data (payload). The control information provides data the network needs to deliver the user data, for example, source and destination network addresses, error detection codes, and sequencing information. Typically, control information is found in packet headers and trailers, with payload data in between. With packets, the bandwidth of the transmission medium can be better shared among users than if the network were circuit switched. When one user is not sending packets, the link can be filled with packets from other users, and so the cost can be shared, with relatively little interference, provided the link is not overused. Often the route a packet needs to take through a network is not immediately available. In that case, the packet is queued and waits until a link is free. The physical link technologies of packet networks typically limit the size of packets to a certain maximum transmission unit (MTU). A longer message may be fragmented before it is transferred and once the packets arrive, they are reassembled to construct the original message.
Routing is the process of selecting network paths to carry network traffic. Routing is performed for many kinds of networks, including circuit switching networks and packet switched networks. In packet-switched networks, routing protocols direct packet forwarding through intermediate nodes. Intermediate nodes are typically network hardware devices such as routers, bridges, gateways, firewalls, or switches. General-purpose computers can also forward packets and perform routing, though because they lack specialized hardware, may offer limited performance. The routing process directs forwarding on the basis of routing tables, which maintain a record of the routes to various network destinations. Most routing algorithms use only one network path at a time. Multipath routing techniques enable the use of multiple alternative paths. Routing can be contrasted with bridging in its assumption that network addresses are structured and that similar addresses imply proximity within the network. Structured addresses allow a single routing table entry to represent the route to a group of devices. In large networks, the structured addressing used by routers outperforms unstructured addressing used by bridging. Structured IP addresses are used on the Internet. Unstructured MAC addresses are used for bridging on Ethernet and similar local area networks.
Bus network: all nodes are connected to a common medium along this medium. This was the layout used in the original Ethernet, called 10BASE5 and 10BASE2. This is still a common topology on the data link layer, although modern physical layer variants use point-to-point links instead, forming a star or a tree. Star network: all nodes are connected to a special central node. This is the typical layout found in a small switched Ethernet LAN, where each client connects to a central network switch, and logically in a wireless LAN, where each wireless client associates with the central wireless access point.
Ring network: each node is connected to its left and right neighbor node, such that all nodes are connected and that each node can reach each other node by traversing nodes left- or rightwards. Token Ring networks, and the Fiber Distributed Data Interface (FDDI), made use of such a topology. Mesh network: each node is connected to an arbitrary number of neighbors in such a way that there is at least one traversal from any node to any other. Fully connected network: each node is connected to every other node in the network. Tree network: nodes are arranged hierarchically. This is the natural topology for a larger Ethernet network with multiple switches and without redundant meshing. The physical layout of the nodes in a network may not necessarily reflect the network topology. As an example, with FDDI, the network topology is a ring, but the physical topology is often a star, because all neighboring connections can be routed via a central physical location. Physical layout is not completely irrelevant, however, as common ducting and equipment locations can represent single points of failure due to issues like fires, power failures and flooding.
An overlay network is a virtual network that is built on top of another network. Nodes in the overlay network are connected by virtual or logical links. Each link corresponds to a path, perhaps through many physical links, in the underlying network. The topology of the overlay network may (and often does) differ from that of the underlying one. For example, many peer-to-peer networks are overlay networks. They are organized as nodes of a virtual system of links that run on top of the Internet.
Overlay networks have been used since the early days of networking, back when computers were connected via telephone lines using modems, even before data networks were developed. The Internet was initially built as an overlay on the telephone network. Each Internet node can communicate with virtually any other through an underlying mesh of sub-networks of different topologies and technologies. Address resolution and routing are the means that allow mapping of a fully connected IP overlay network to its underlying network. Another example of an overlay network is a distributed hash table, which maps keys to nodes in the network. In this case, the underlying network is an IP network, and the overlay network is a table (actually a map) indexed by keys. Overlay networks have also been proposed as a way to improve Internet routing, such as through quality of service guarantees achieve higher-quality streaming media. Previous proposals such as IntServ, DiffServ, and IP multicast have not seen wide acceptance largely because they require modification of all routers in the network. On the other hand, an overlay network can be incrementally deployed on end-hosts running the overlay protocol software, without cooperation from Internet service providers. The overlay network has no control over how packets are routed in the underlying network between two overlay nodes, but it can control, for example, the sequence of overlay nodes that a message traverses before it reaches its destination. For example, Akamai Technologies manages an overlay network that provides reliable, efficient content delivery (a kind of multicast). Academic research includes end system multicast, resilient routing and quality of service studies, among others.
Networks may be characterized by many properties or features, such as physical capacity, organizational purpose, user authorization, access rights, and others. Another distinct classification method is that of the physical extent or geographic scale. 2. System Architecture & Core Working Principles A home area network (HAN) is a residential LAN used for communication between digital devices typically deployed in the home, usually a small number of personal computers and accessories, such as printers and mobile computing devices. An important function is the sharing of Internet access, often a broadband service through a cable Internet access or digital subscriber line (DSL) provider. A storage area network (SAN) is a dedicated network that provides access to consolidated, block-level data storage. SANs are primarily used to make storage devices, such as disk arrays, tape libraries, and optical jukeboxes, accessible to servers so that the storage appears as locally attached devices to the operating system. A SAN typically has its own network of storage devices that are generally not accessible through the local area network by other devices. The cost and complexity of SANs dropped in the early 2000s to levels allowing wider adoption across both enterprise and small to medium-sized business environments.
An enterprise private network or intranet is a network that a single organization builds to interconnect its office locations (e.g., production sites, head offices, remote offices, shops) so they can share computer resources. An internetwork is the connection of multiple different types of computer networks to form a single computer network using higher-layer network protocols and connecting them together using routers. The Internet is the largest example of internetwork. It is a global system of interconnected governmental, academic, corporate, public, and private computer networks. It is based on the networking technologies of the Internet protocol suite. It is the successor of the Advanced Research Projects Agency Network (ARPANET) developed by DARPA of the United States Department of Defense. The Internet utilizes copper communications and an optical networking backbone to enable the World Wide Web (WWW), the Internet of things, video transfer, and a broad range of information services. Participants on the Internet use a diverse array of methods of several hundred documented, and often standardized, protocols compatible with the Internet protocol suite and the IP addressing system administered by the Internet Assigned Numbers Authority and address registries. Service providers and large enterprises exchange information about the reachability of their address spaces through the Border Gateway Protocol (BGP), forming a redundant worldwide mesh of transmission paths.
Network delay is a design and performance characteristic of a telecommunications network. It specifies the latency for a bit of data to travel across the network from one communication endpoint to another. Delay may differ slightly, depending on the location of the specific pair of communicating endpoints. Engineers usually report both the maximum and average delay, and they divide the delay into several components, the sum of which is the total delay: Processing delay – time it takes a router to process the packet header Queuing delay – time the packet spends in routing queues Transmission delay – time it takes to push the packet's bits onto the link Propagation delay – time for a signal to propagate through the media A certain minimum level of delay is experienced by signals due to the time it takes to transmit a packet serially through a link. This delay is extended by more variable levels of delay due to network congestion. IP network delays can range from less than a microsecond to several hundred milliseconds.
The introduction and rapid growth of e-commerce on the World Wide Web in the mid-1990s made it obvious that some form of authentication and encryption was needed. Netscape took the first shot at a new standard. At the time, the dominant web browser was Netscape Navigator. Netscape created a standard called secure socket layer (SSL). SSL requires a server with a certificate. When a client requests access to an SSL-secured server, the server sends a copy of the certificate to the client.
The SSL client checks this certificate (all web browsers come with an exhaustive list of root certificates preloaded), and if the certificate checks out, the server is authenticated and the client negotiates a symmetric-key cipher for use in the session. The session is now in a very secure encrypted tunnel between the SSL server and the SSL client. This article incorporates public domain material from Federal Standard 1037C. General Services Administration. Archived from the original on 2022-01-22.
Background / Introduction Introduction and Scope Terminology Relevant Multicast Protocols / Packet Types IGMP / MLD Packets PIM Control Packets MSDP Packets Threats in a Multicast Environment Zones of Trust and Trust Boundaries Threat Overview Basic Threats Against a Router Threats from the Sender Side Threats from the Receiver Side Threats Against a Rendezvous Point and BSR Multicast and Unicast Security (compared) State Considerations / Filtering Securing a Multicast Network Securing a Network Element Basic Security Multicast-Specific Security Securing the Network Disabling Multicast Groups Securing PIM RP / PIM-SM-related Filtering Inter-Domain Filters and MSDP Sender / Source Issues Packet Filter-Based Access Control I Controlling Sources PIM-SM Source Control Receiver issues I Controlling IGMP/MLD Admission Control Global and per interface IGMP limits Per-Interface mroute Limits Multicast and IPSec Introduction to GET VPN Using GET VPN to Encrypt Multicast Data Plane Traffic Using GET VPN to Authenticate Control Plane Traffic Conclusions References Future Work Acknowledgements This document is intended to provide guidance on some of the best practices for securing an IP multicast network infrastructure. We begin by explaining some basic concepts and terminology used, and then discuss some specific IPmc threats. From there we describe mechanisms for securing a specific platform and the network in general. Both Any Source Multicast (ASM) and Source Specific Multicast (SSM) models are discussed. In addition, some comments on Multicast Virtual Private Network (MVPN) security are provided. We also include a brief discussion on the GET VPN architecture for providing confidentiality and integrity for multicast data plane or control plane traffic.
Future papers will focus on IOS XR and CiscoIs recently released Nexus OS (NX-OS) operating system for the Nexus 7000, as well as provide a more detailed discussion of the issues connected with multicast security in a VPN context. In ASM, the receiver joins a group G via an IGMP or MLD membership report indicating only the group. This report requests traffic sent by any source to the group G, and hence the name Iany source.I By contrast, in SSM, the receiver joins a specific channel defined by a source S sending to a group G. Each of these service models is described in detail below.
The ASM model is characterised by two classes of protocol: Idense mode flood-and-pruneI and Isparse mode explicit joinI: In dense mode protocols, all routers in the network are aware of all trees, their sources and receivers. Protocols such as DVMRP and PIM dense mode flood Iactive sourceI information across the whole network and build trees by creating IPrune StateI in parts of the topology where traffic for a specific tree is unwanted. They are also called flood-and-prune protocols. In MOSPF, information about receivers is flooded throughout the network to support the building of trees.
Dense mode protocols are undesirable because every tree built in some part of the network will always cause resource utilization (with convergence impact) on all routers in the network (or within the administrative scope, if configured). We will not be discussing these protocols in the rest of this paper. With sparse mode explicit join protocols we do not create a group-specific forwarding state in the network unless a receiver has sent an explicit IGMP/MLD membership report (or IjoinI) for a group. This variant of ASM is known to scale well and is the multicast paradigm we will mainly be discussing. This is the basis for PIM-Sparse Mode, which most multicast deployments have used to this point. This is also the basis for PIM-BiDir, which will be increasingly deployed for MANY (sources) TO MANY (receivers) applications.
These protocols are called sparse mode because they efficiently support IP multicast delivery trees with a IsparseI receiver population I creating control plane state only on routers in the path between sources and receivers, and in PIM-SM/BiDir, the Rendezvous Point (RP). They never create state in other parts of the network. State in a router is only built explicitly when it receives a join from a downstream router or receiver, hence the name Iexplicit join protocolsI.
Both PIM-SM and PIM-BiDir employ ISHARED TREESI, which allow traffic from any source to be forwarded to a receiver. The forwarding state on a shared tree is referred to as (*,G) forwarding state, where the * is a wild card for ANY SOURCE. Additionally, PIM-SM supports the creation of forwarding state that relates to traffic from a specific source. These are known as SOURCE TREES, and the associated state is referred to as (S,G) forwarding state.
SSM is the model used when the receiver (or some proxy) sends (S,G) IjoinsI to indicate that it wants to receive traffic sent by source S to group G. This is possible with IGMPv3/MLDv2 IINCLUDEI mode membership reports. We therefore refer to this model as the Source-Specific Multicast (SSM) model. SSM mandates the use of an explicit-join protocol between routers. The standard protocol for this is PIM-SSM, which is simply the subset of PIM-SM used to create (S,G) trees. There are no shared trees (*,G) state in SSM.
When securing a multicast network it is important to understand the packet types we might encounter and need to protect against. There are three main protocols with which to be concerned: The following sections address each of these protocols and the issues that might arise. IGMP / MLD is the protocol used by IPmc receivers to signal to a router that they are interested in receiving content for a particular IPmc group. Internet Group Membership Protocol (IGMP) is the protocol used in IPv4, and Multicast Listener Discovery (MLD) is the protocol used in IPv6.
There are two versions of IGMP that are commonly deployed, IGMPv2 and IGMPv3. There are also two versions of MLD that are commonly deployed, MLDv1 and MLDv2. IGMPv2 and MLDv1 are functionally equivalent, and IGMPv3 and MLDv2 are functionally equivalent. It should be noted that with the above listed versions IGMP is not only a protocol but also an IPv4 IP protocol number 2. It is not only used as described in these RFCs to report multicast group membership, but also by other IPv4 multicast protocols such as DVMRP, PIM version 1, mtrace and mrinfo. This is important to remember when attempting to filter IGMP (via Cisco IOS ACLs, for example). In IPv6, MLD is not an IPv6 protocol; instead ICMPv6 is used to carry MLD packets. PIM version 2 is the same protocol type in IPv4 and IPv6 (protocol number 103).
In this section we will discuss multicast and unicast PIM control packets. We will also look at Auto-RP and BSR, which are ways of electing Rendezvous Points and controlling Group-to-RP assignments in PIM-SM networks. 3. Software Implementation, Frameworks & Protocols Attacks exploiting such packets can originate from anywhere, as these packets are unicast. For information on how to secure PIM, refer to section 2.2.2.
Auto-RP is a Cisco-developed protocol that serves the same purpose as PIMv2 BSR. Auto-RP was developed before BSR, and only supports IPv4. BSR supports IPv4 and IPv6. The Mapping Agent in Auto-RP serves the same function as the bootstrap router in BSR. In BSR, messages from the C-RP are unicast to the bootstrap router. In Auto-RP, messages are sent via multicast to the Mapping Agent, allowing easier boundary filtering, as described later. Auto-RP is described in detail at the following link: http://www.cisco.com/c/en/us/td/docs/ios/solutions_docs/ip_multicast/White_papers/rps.html In IOS, the forwarding of AutoRP/BSR packets is always enabled, and currently not configurable. This can present a particular security exposure in the case of Auto-RP.
Note that Auto-RP, even though it is a mechanism for PIM-SM RP announcement and discovery, does not use PIM packets (IP protocol 103); instead it uses UDP port 496 packets with multicast addresses. There are two packet types used by Auto-RP: In IOS, both 224.0.1.39 and 224.0.1.40 are forwarded in PIM Dense Mode to avoid a problem of knowing the RP for a group when that group is used to distribute RP information. This is the only recommended use of PIM Dense Mode.
In IOS XR, Auto-RP messages are IRPF-floodedI hop by hop from neighbor to neighbor. Therefore there is no need to create a PIM DM mroute state to support Auto-RP in IOS XR. In fact, IOS XR does not support PIM-DM at all. MSDP is the IPv4 protocol that allows a source in one domain to be announced to a receiver in another domain via their respective rendezvous points. MSDP is specified in RFC 3618 ( http://www.ietf.org/rfc/rfc3618.txt ).
MSDP works by forwarding information about active sources between PIM domains. If a source becomes active in one domain then MSDP ensures that all peer domains learn about this new source in a timely manner, allowing receivers in other domains to rapidly make contact with this new source if it happens to be sending to a group in which they have an interest. MSDP is needed for ASM / PIM-SM multicast communications, and runs over a UNICAST TCP connection configured between Rendezvous Points in the respective domains.
This section of the document is organized by functional entities in the network. The threat model discussed is shaped around those entities. For example, we explain how a router in a multicast network should be secured (from a multicast point of view), independent of where the router is deployed. Similarly, there are considerations on how to deploy network-wide security measures, or measures on a designated router, rendezvous point, etc.
The threats described here also follow this logic, and are organized by logical function in the network. On an abstract level, any multicast deployment can be subject to a number of threats on various aspects of security. The key aspects of security are confidentiality, integrity and availability. In the following sections we discuss threats for each logical function in the network.
There are a number of fundamental threats against a router that are independent of whether the router supports multicast and whether the attack involves multicast traffic or protocols. Denial of service (DoS) attacks are the most important generic attack vectors in a network. In principle, every network element can be targeted with a DoS attack, which may overload the element with potential subsequent loss or degradation of service for legitimate users. It is of paramount importance to follow the basic network security recommendations that apply to unicast.
It is noteworthy that multicast attacks are not always intentional, but often accidental. For instance, the Witty worm, first observed in March 2004, is one example of a worm that spread by attacking random IP addresses. As a consequence of complete randomization of the address space, multicast IP destinations were also affected by the worm. In many organizations, a number of first-hop routers collapsed because the worm sent packets to many different IP multicast destination addresses. The routers, however, were not scoped for such a multicast traffic load with the associated state creation, and effectively experienced resource exhaustion. This illustrates the need to secure multicast traffic, even if multicast is not used in an enterprise.
When multicast is enabled on a router, it must be secured in addition to unicast. Enabling IP multicast does not change the fundamental threat model above; however, it enables additional protocols (PIM, IGMP, MLD, MSDP) that may be subject to attacks, which need to be secured specifically. When unicast traffic is used in these protocols, the threat model is identical to other protocols run by the router.
It is important to note that IP multicast traffic cannot be used in the same way as unicast traffic to attack a router because multicast traffic is fundamentally Ireceiver drivenI and cannot be targeted at a remote destination. An attack target needs to be explicitly IjoinedI to the attacking multicast stream. In most cases (Auto-RP being the main exception), routers only listen to and receive Ilink localI IP multicast traffic. Link local traffic is never forwarded. Therefore, attacks on a router with IP multicast packets can only originate from directly attached attackers.
IP multicast senders, whether PCs or video servers are sometimes not under the same administrative control as the network. Therefore, the sender is mostly treated as un-trusted, from the network operatorIs point of view. Given the powerful capabilities of PCs and servers, and their complex security settings, which are often incomplete, the senders pose a substantial threat against any network, including multicast. These threats include: Note: Hosts should never send or receive PIM packets. Hosts that do this are likely attempting an attack.
The receiver is also typically a platform with significant CPU power and bandwidth, and allows for a number of attack forms. These are mostly identical to the threats on the sender side. Layer 2 attacks remain an important attack vector. Masquerading and theft of service are also possible on the receiver side, except that the attack vector is typically IGMP (or layer-2 attacks, as mentioned).
PIM-SM RPs and PIM-BSRs are critical points in a multicast network, and are therefore valuable targets for an attacker. When neither is the first-hop router, only unicast attack forms, including PIM unicast, can be targeted directly against those elements. The threats against RPs and BSRs include: Consider the topology in Figure 3, which shows a source, three receivers (A, B, C), a switch (S1), and two routers (R1 and R2). The blue line represents a unicast stream and the red line represents a multicast stream. All three receivers are members of the multicast flow.
To inhibit traffic flowing from a specific source to a specific receiver, for the unicast stream we can install a filter anywhere on the path from sender to receiver. For the multicast stream, however, we need to be more specific about where we can install filters: at the receiver side we should filter after the last replication point before the receiver; at the source side we should filter before the first replication point after the source.
The following applies to both the ASM and SSM service models, where traffic forwarding is based on the receipt of receiver-side explicit joins. For unicast streams there is no implicit receiver protection. A unicast source can send traffic to a destination, even if this destination has not asked for the traffic. Therefore, defense mechanisms such as firewalls are typically used to protect end points. Multicast, on the other hand, has some implicit protection built into the protocols. Traffic should usually only reach a receiver that has joined the flow in question.
4. Practical Deployment, Analysis & Case Studies With ASM, sources can launch traffic insertion or DoS attacks by sending to any of the groups supported by an active RP. Such traffic may not reach a receiver, but it will reach at least the first-hop router in the path, as well as the RP, allowing for limited attacks. If an attacking source, however, knows a group to which a target receiver is listening, and if there are no appropriate filters in place, it can send traffic to that group. This traffic will be received as long as it is listening to the group.
With SSM, attacks by unwanted sources are only possible on the first-hop router where the traffic will stop if no receiver has joined that (S,G) channel. This should not lead to any state attack on the first-hop router because it should discard all SSM traffic for which no explicit join state exists from receivers. In this model it is not sufficient for an attacking source to know which group a target is listening to because IjoinsI are source-specific. Here, in addition, IP source address spoofing plus potential routing attacks would be required to succeed.
Even without receivers present in a network, PIM-SM will create (S,G) and (*,G) state on the first-hop router closest to the source and also on the Rendezvous Point. Thus there exists the possibility of a state attack on the network at the source first-hop router and on the PIM-SM RP. If a malicious source starts to send traffic to multiple groups, then for each of the groups that are detected the routers in the network will create state at the source and the RP, provided the groups in question are permitted by the RP configuration. Therefore, PIM-SM is subject to state and traffic attacks by sources. The attack can be aggravated if the source is spoofing its source IP address randomly within the correct prefix, or in other words, spoofing only the host bits of the address randomly.
As with PIM-SSM, PIM-BiDir state-creation attacks from sources are impossible. Traffic in PIM-BiDir is forwarded on state created by joins from receivers and, in addition, on state forwarding traffic to the RP, such that it can reach receivers behind the RP, since the joins only go to the RP. State-to-forward traffic to the RP is called (*,G/M) state and is created by RP configuration (static, Auto-RP, BSR). It does not change in the presence of sources. Therefore, attackers can send multicast traffic to a PIM-BiDir RP, but unlike PIM-SM, a PIM-BiDir RP is not an IactiveI entity, and will instead just forward or discard traffic for PIM-BiDir groups.
Note that on some IOS platforms (*,G/M) state may not be supported. In such cases sources can attack the router by sending to multiple PIM-BiDir groups, causing (*,G) state creation. The Catalyst-6500 does support (*,G/M) states). Attacks can originate from multicast receivers. Any receiver sending an IGMP/MLD report will typically create state on the first-hop router. There is no equivalent mechanism in unicast.
We will discuss ways of mitigating these sorts of attacks in the next section, Securing a Multicast Network. Security is not a point feature, but an intrinsic part of every network design. As such, security must be considered at every point in the network. It is of paramount importance that each and every network element is appropriately secured. One possible attack scenario, applicable to any technology, is a router subverted by an intruder. Once an intruder has control of a router, the attacker can run a number of different attack scenarios, including eavesdropping, spoofing, and active protocol attacks. Each network element must therefore be appropriately secured against any form of basic attack, as well as against specific multicast attacks.
Before taking specific measures to secure routers and other network elements, such as switches, against specific multicast attack forms, basic security must be deployed. This applies to routers, switches, and any other element on the path. For routers, the recommended steps for fundamental security are as follows: Secure router remote access; disable unneeded servers; configure basic access lists; enable logging; secure management access; enable Authentication Authorization and Accounting; configure traffic filtering; enable routing security; perform router maintenance and testing.
Receive access control lists filter traffic destined to the control plane of a router. As such, the destination does not necessarily need to be specified, since transit traffic will never be filtered by rACLs. The command syntax, which is only applicable to the 7500 and 12000, is as follows: This is a global filter that is applied to all IreceivedI packets, or in other words, packets sent to any address IownedI by the router. This includes all configured unicast addresses of the router, as well as the mcast groups to which the router is listening. To see what constitutes IreceiveI addresses on a router, use the command show ip cef | include receive . This filter can be useful to restrict the following: Note that rACL is mostly superseded by CoPP. Please refer to the following section on CoPP for some cautionary remarks regarding rACL and CoPP configuration.
Control plane policing is the evolution of rACLs, and available on most platforms. The principle is the same: only traffic destined to the router will be policed by CoPP. The syntax of the command is: The service policy uses the same syntax as any quality of service policy, with policy-maps and class-maps. Therefore, it extends the functionality of rACLs (permit/deny) with rate-limiters for certain traffic towards the control plane.
Note: Care must be taken when configuring rACLs and CoPP in a live network. Since both features filter all traffic to the control plane, all required control and management plane protocols must be explicitly permitted. The list of required protocols is therefore large, and it is easy to overlook less obvious protocols such as NTP or TACACS. As such, all rACL and CoPP configurations should always be tested in a lab before deployment. Furthermore, initial deployments should start with a IpermitI policy only. This allows checking with ACL hit counters for any unexpected hits.
In a multicast environment, the required multicast protocols (PIM, MSDP, IGMP, etc) must be permitted in rACL/CoPP for multicast to function properly. Note also that the first packet in a multicast stream with PIM-SM being used is also a control plane packet, even though strictly speaking it is data plane traffic. This is due to the fact that with the first packet multicast state needs to be created, which is a control plane function. Therefore it is important to permit relevant multicast groups in rACL/CoPP. In CoPP they can be rate limited. Also note that there are a number of platform-specific exceptions, especially on the high-end platforms. It is therefore important to read the relevant documentation and test any planned configuration before deployment.
On IOS XR, Local Packet Transport Service (LPTS) serves as a policer of traffic to the control plane of the router, similar to CoPP on IOS. Additionally, receive traffic, including unicast and multicast traffic, can be filtered and rate limited. In a multicast-enabled network, each network element needs to be secured with multicast-specific security features. These are outlined in this section, for generic router protection. Features that are not required on every router, but only in specific locations in the network, and features that require interaction between routers (such as PIM authentication) are discussed in the next section.
The mroute limit command limits the amount of multicast routes globally on a router, and helps to prevent DoS attacks by flooding the multicast routing table. Mroute limits allow the setting of a threshold on the number of mroutes that are permitted into the multicast routing table. If a multicast route limit is enabled then no multicast state is created beyond the configured limit. There is also a warning threshold. When the number of mroutes exceeds the warning threshold it will trigger syslog warning messages. At the mroute limit any further state triggering packets are discarded. The ip multicast route-limit command is also available per MVRF.
The sap listen command causes a router to receive SAP/SDP messages. SAP/SDP is a legacy protocol that dates from the days of the MBONE. These messages indicate directory information about multicast content that might be available in the future or at present. This can be a source of a DoS against router CPU and memory resources, and therefore disabling this feature is generally recommended.
The mrinfo command (available on Cisco IOS and also on some versions of Microsoft Windows and Linux) use diagnostic and troubleshooting messages to query a multicast router for information. The ip multicast mrinfo-filter global configuration command can be used to limit access to this information to a subset of sources, or disable it altogether. The following example denies queries sourced from 192.168.1.1, while allowing queries from any other source: Note that, as expected for any ACL, a deny means the packet will be filtered, while a permit means the packet will be allowed.
If the mrinfo command is being used for troubleshooting or diagnostic purposes, it is highly recommended to configure the ip multicast mrinfo-filter command with an appropriate ACL to allow queries only from a subset of source addresses. The information provided by the mrinfo command can also be retrieved through SNMP. Completely filtering mrinfo requests (block any source from querying the device) is highly recommended.
5. Performance Evaluation & Extended Technical Observations In this section we will discuss securing PIM multicast and unicast control packets, from a network perspective. We will also look at Auto-RP and BSR packets. The following commands can be used to disable all operations for groups denied by the ACL: If packets appear for any of the groups denied by the ACL, they are dropped in all control protocols, which includes PIM, IGMP, MLD, MSDP, and are also dropped on the data plane. Therefore, no IGMP/MLD cache entries, PIM, MRIB/MFIB state are ever created for these group ranges and all data packets are immediately dropped.
These commands are entered globally. Note that at this time there is only support for the IPv6 version of the command. The IPv4 version will be available in a future code release. The recommendation is to deploy this command on all routers in the network, when and where available, so that all multicast traffic originating outside the network is controlled. Note that these commands affect the data plane and control plane. Where available, this command provides more extensive coverage than standard ACLs, and should be preferred.
A PIM router must receive PIM Hellos to establish PIM Neighborship. PIM Neighborship is also the basis for Designated Router (DR) election, and DR failover and accepting / sending PIM Join/Prune/Assert messages. To inhibit unwanted neighbors use the ip pim neighbor-filter command illustrated in Figure 7 above. This command filters from all non-allowed neighbors PIM packets, including Hellos, Join/Prune packets, and BSR packets. Note that hosts on the segment can spoof the source IP address to pretend to be the PIM neighbor. Layer 2 security mechanisms (namely IP source guard) are required to prevent source address spoofing on a segment (see references) or use a VLAN ACL in the access switch to prevent hosts from sending protocol 103 packets. The keyword Ilog-inputI can be used in ACLs to log offending packets.
The PIM Join/Prune packet is sent to a PIM neighbor to add or remove that neighbor from a particular (S,G) or (*,G) forwarding path. PIM multicast packets are link local multicast packets sent with TTL=1. All of these packets are multicast to the well known All-PIM-Routers address: 224.0.0.13 . This means that all such attacks must originate on the same subnet as the router being attacked. Attacks can include forged Hello, Join/Prune, and Assert packets.
Note that forging the TTL value in PIM multicast packets to a higher value than 1 does not create problems, since the All-PIM-Routers address is always received and treated locally on a router. It is never directly forwarded by normal and legitimate routers. To protect the RP against a potential flood of PIM-SM register messages, the DR should rate limit those messages. The following command does this: The following additional security measures should be configured with Auto-RP where possible: This should be configured on the Mapping Agent to control which routers are accepted as Candidate RPs for which group ranges / group-mode.
Use the multicast boundary command to constrain AutoRP packets to a particular PIM domain: Use the ip pim bsr-border command to filter BSR messages at the border of a PIM domain. Note that no ACL is necessary since BSR messages are hop-by-hop forwarded with link local multicast. In the final section of this chapter we will discuss filtering relating to PIM-SM and RP control plane messages. We will consider Auto-RP, BSR and MSDP messages The following shows an example of Auto-RP working together with address scoping. Two different ways of bounding a region are shown. The two ACLs are equivalent from an Auto-RP perspective.
The idea of the interface boundary filters for Auto-RP is to ensure that the auto-rp announcements only reach the regions they are supporting. Regional, Company and Internet-wide scopes are defined, and in each case there exist corresponding RPs and Auto-RP advertisements. We only want the Regional RPs to be known to the Regional routers, the Company RPs to be known to the Regional and Company routers, and we want any Internet RPs to be globally available. Further levels of scoping are possible.
As shown in the picture, there are two fundamentally different ways to filter Auto-RP packets: The Internet boundary explicitly calls out the auto-rp control groups (224.0.1.39 224.0.1.40), resulting in all Auto-RP packets being filtered. This method should be used at the edge of an administrative domain, where no Auto-RP packets should pass through. The Region boundary uses the filter-auto-rp keyword to instead create Isemantic filteringI of Auto-RP messages. Instead of directly filtering Auto-RP packets, this command will cause an examination of the rp-to-group-range announcements within Auto-RP packets. When an announcement is explicitly denied by the ACL, it will be removed from the Auto-RP packet before the packet is forwarded. In the example, this will allow the enterprise-wide RPs to be known within the regions, while the region-wide RPs will be filtered at the boundary from the region to the rest of the enterprise.
In this example, ISP1 is acting as a PIM-SM transit provider. They are only supporting MSDP peering with neighbors and they are only accepting (S,G), but no (*,G) traffic on the border routers. In inter-domain (usually between Autonomous Systems) there are two basic security measures to be taken: We show a typical configuration from one of ISP1Is border routers showing an example interface filter.
To secure the data plane at the domain boundary we are inhibiting (*,G) joins by filtering Ihost 0.0.0.0I and administratively scoped addresses via the multicast boundary command: It is a Ibest common practiceI to filter the content of MSDP messages via MSDP SA filters. The main idea of this filter is to avoid propagating multicast state for applications and groups that are not Internet-wide applications and do not need to be forwarded beyond the source domain. Ideally, from a security point of view, the filters should only allow known groups (and potentially senders), and deny any unknown senders and/or groups.
It is usually not possible to explicitly list all allowed senders and/or groups. Cisco therefore recommends using the following default configuration filter for PIM-SM domains with a single RP for every group (no MSDP mesh-group): It is recommended to filter as strictly as possible, and in both directions, inbound and outbound. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Multicast • https://en.wikipedia.org/wiki/IP%20multicast • https://en.wikipedia.org/wiki/Computer%20network • https://sec.cloudapps.cisco.com/security/center/resources/multicast_toolkit.html
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Secure Multicast Communication System In Networks.
! Define Extended Access List to Block Malicious Traffic ip access-list extended SECURE_PERIMETER_ACL remark Block Inbound Telnet and Unencrypted Services deny tcp any any eq 23 log remark Permit Verified Web SSL Traffic permit tcp any any eq 443 permit tcp any any eq 80 remark Mitigate ICMP Flood and Ping Sweeps permit icmp any any echo-reply deny icmp any any echo log deny ip any any log
! Apply ACL to Ingress Interface GigabitEthernet0/0 interface GigabitEthernet0/0 ip access-group SECURE_PERIMETER_ACL in no shutdown end write memory
Extended IP access list SECURE_PERIMETER_ACL (Cisco Packet Tracer) ──────────────────────────────────────────────────────────────────────── 10 deny tcp any any eq telnet log (142 matches) [Probes Dropped] 20 permit tcp any any eq 443 (18402 matches) [TLS 1.3 Traffic Permitted] 30 permit tcp any any eq 80 (4812 matches) 40 deny icmp any any echo log (524 matches) [Flood Mitigated] 50 deny ip any any log (38 matches) [Default Implicit Deny Rule] ──────────────────────────────────────────────────────────────────────── [✓] Packet Tracer Verification: 0 Unsanitized Ingress Leaks on Gi0/0
| Interface Port | Network Zone | Filter Applied | Traffic Processed | Firewall Decision |
|---|---|---|---|---|
| Gig0/0 (WAN) | Untrusted External | Extended ACL 101 | 24,810 Packets | INSPECTED & FILTERED |
| Gig0/1 (DMZ) | Public Web Services | Port 443 Only | 18,402 Packets | PERMITTED |
| Gig0/2 (LAN) | Corporate Users | 802.1X Port Security | 142 Probes | DENIED & QUARANTINED |