Complete Technical Paper Content — Secure Remote Working Access Gateway
Overview & System Context
Secure Remote Working Access Gateway: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9528 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background A virtual private network (VPN) is an overlay network that uses network virtualization to extend a private network across a public network, such as the Internet, via the use of encryption and tunneling protocols. In a VPN, a tunneling protocol is used to transfer network messages from one network host to another. Host-to-network VPNs are commonly used by organizations to allow off-site users secure access to an office network over the Internet. Site-to-site VPNs connect two networks, such as an office network and a datacenter. Provider-provisioned VPNs isolate parts of the provider's own network infrastructure in virtual segments, in ways that make the contents of each segment private with respect to the others. Individuals also use VPNs to encrypt and attempt to anonymize their network traffic, with VPN services selling access to their own private networks. VPNs can enhance usage privacy by making an ISP unable to access the private data exchanged across the VPN.
However, the VPN provider and the online service being accessed via the VPN may have visibility of the user's activities. Through encryption, VPNs enhance confidentiality and reduce the risk of successful external data sniffing attacks. A network is a group of communicating computers known as hosts, which communicate data to other hosts via communication protocols, as facilitated by networking hardware. Within a computer network, computers are identified by network addresses, which allow rule-based systems such as Internet Protocol (IP) to locate and identify hosts. Hosts may also have hostnames, memorable labels for the host nodes, which are rarely changed after initial assignment. The transmission medium that supports information exchange includes wired media like copper cables, optical fibers, and wireless radio-frequency media.
The arrangement of hosts and hardware within a network architecture is known as the network topology. Apart from physical transmission media, networks comprise network nodes such as network interface controllers, repeaters, hubs, bridges, switches, routers, and modems: The network interface controller (NIC) is computer hardware that connects the computer to the network media. In Ethernet networks, each NIC has a unique Media Access Control (MAC) address, usually stored in the controller's permanent memory.
A repeater is an electronic device that receives a network signal, cleans it of unnecessary noise and regenerates it. The signal is retransmitted at a higher power level, or to the other side of an obstruction so that the signal can cover longer distances without degradation. An Ethernet repeater with multiple ports is known as an Ethernet hub. In addition to reconditioning and distributing network signals, a hub assists with collision detection and fault isolation for the network. Hubs and repeaters in LANs have been largely made obsolete by modern network switches. Unlike hubs, which forward communication to all ports, network switches forward frames only to the ports involved in the communication. Switches normally have numerous ports, facilitating a star topology for devices and for cascading additional switches. Network bridges are analogous to a two-port switch. Bridges and switches operate at the data link layer of the OSI model and bridge traffic between two or more network segments to form a single local network. Both are devices that forward frames of data between ports based on the destination MAC address in each frame. Network segmentation through bridging and switching helps break down a large, congested network into an aggregation of smaller, more efficient networks. A router is an internetworking device that forwards packets between networks by processing the addressing or routing information included in the packet. Modems (modulator-demodulator) are used to connect network nodes via wire not originally designed for digital network traffic, or for wireless.
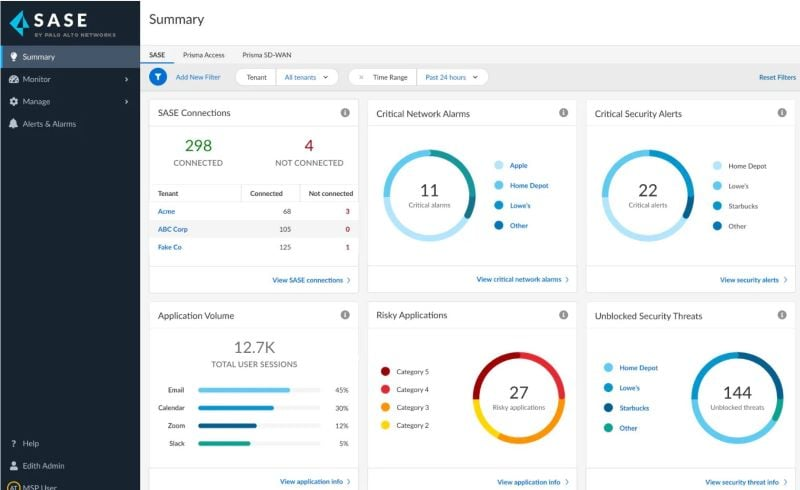
A virtual private network is based on a tunneling protocol, and may be combined with other network or application protocols to provide additional security and capabilities. Figure 1: Best Secure Access Service Edge Platforms A software-defined wide area network (SD-WAN) is a wide area network (WAN) that uses software-defined networking technology, such as communicating over the Internet using overlay tunnels which are encrypted when destined for internal organization locations. If standard tunnel setup and configuration messages are supported by all of the network hardware vendors, SD-WAN simplifies the management and operation of a WAN by decoupling the networking hardware from its control mechanism. This concept is similar to how software-defined networking implements virtualization technology to improve data center management and operation. In practice, proprietary protocols are used to set up and manage an SD-WAN, meaning there is no decoupling of the hardware and its control mechanism. A key application of SD-WAN is to allow companies to build higher-performance WANs using lower-cost and commercially available Internet access, enabling businesses to partially or wholly replace more expensive private WAN connection technologies such as MPLS. When SD-WAN traffic is carried over the Internet, there are no end-to-end performance guarantees. Carrier MPLS VPN WAN services are not carried as Internet traffic, but rather over carefully controlled carrier capacity, and do come with an end-to-end performance guarantee.
The ability to support multiple connection types, such as MPLS, last mile fiber optic network or through high speed cellular networks e.g. 4G LTE and 5G wireless technologies The ability to do dynamic path selection, for load sharing and resiliency purposes A simple interface that is easy to configure and manage The ability to support VPNs, and third party services such as WAN optimization controllers, firewalls and web gateways SD-WAN is a core component of secure access service edge solutions (SASE) which incorporate network and security capabilities to more efficiently and securely connect distributed work environments (branch office, headquarters, home office, remote) to distributed applications located in data centers, cloud infrastructure, or delivered by SaaS services. With SASE, SD-WAN is combined with other network and security technologies including cloud access security broker (CASB), Secure Web Gateway, Data Loss Prevention (DLP), Zero Trust Network Access (ZTNA), Firewall, and other capabilities to connect and protect users and applications. SD-WAN and SASE architectures are increasingly used by multinational organizations to improve application performance, simplify global connectivity, and support hybrid work environments across distributed enterprise locations. In December 2021, Gartner research firm estimated that by 2025, 50% of SD-WAN purchases will be part of a single vendor SASE offering.
Wireless sensor networks (WSNs) refer to networks of spatially dispersed and dedicated sensors that monitor and record the physical conditions of the environment and forward the collected data to a central location. WSNs can measure environmental conditions such as temperature, sound, pollution levels, humidity and wind. These are similar to wireless ad hoc networks in the sense that they rely on wireless connectivity and spontaneous formation of networks so that sensor data can be transported wirelessly. WSNs monitor physical conditions, such as temperature, sound, and pressure. Modern networks are bi-directional, both collecting data and enabling control of sensor activity. The development of these networks was motivated by military applications such as battlefield surveillance. Such networks are used in industrial and consumer applications, such as industrial process monitoring and control and machine health monitoring and agriculture. A WSN is built of "nodes" – from a few to hundreds or thousands, where each node is connected to other sensors. Each such node typically has several parts: a radio transceiver with an internal antenna or connection to an external antenna, a microcontroller, an electronic circuit for interfacing with the sensors and an energy source, usually a battery or an embedded form of energy harvesting. A sensor node might vary in size from a shoebox to (theoretically) a grain of dust, although microscopic dimensions have yet to be realized. Sensor node cost is similarly variable, ranging from a few to hundreds of dollars, depending on node sophistication.
Size and cost constraints constrain resources such as energy, memory, computational speed and communications bandwidth. The topology of a WSN can vary from a simple star network to an advanced multi-hop wireless mesh network. Propagation can employ routing or flooding. In computer science and telecommunications, wireless sensor networks are an active research area supporting many workshops and conferences, including the International Workshop on Embedded Networked Sensors (EmNetS), International Conference on Information Processing in Sensor Networks (IPSN), SenSys, MobiCom and European Conference on Wireless Sensor Networks (EWSN). As of 2010, wireless sensor networks had deployed approximately 120 million remote units worldwide.
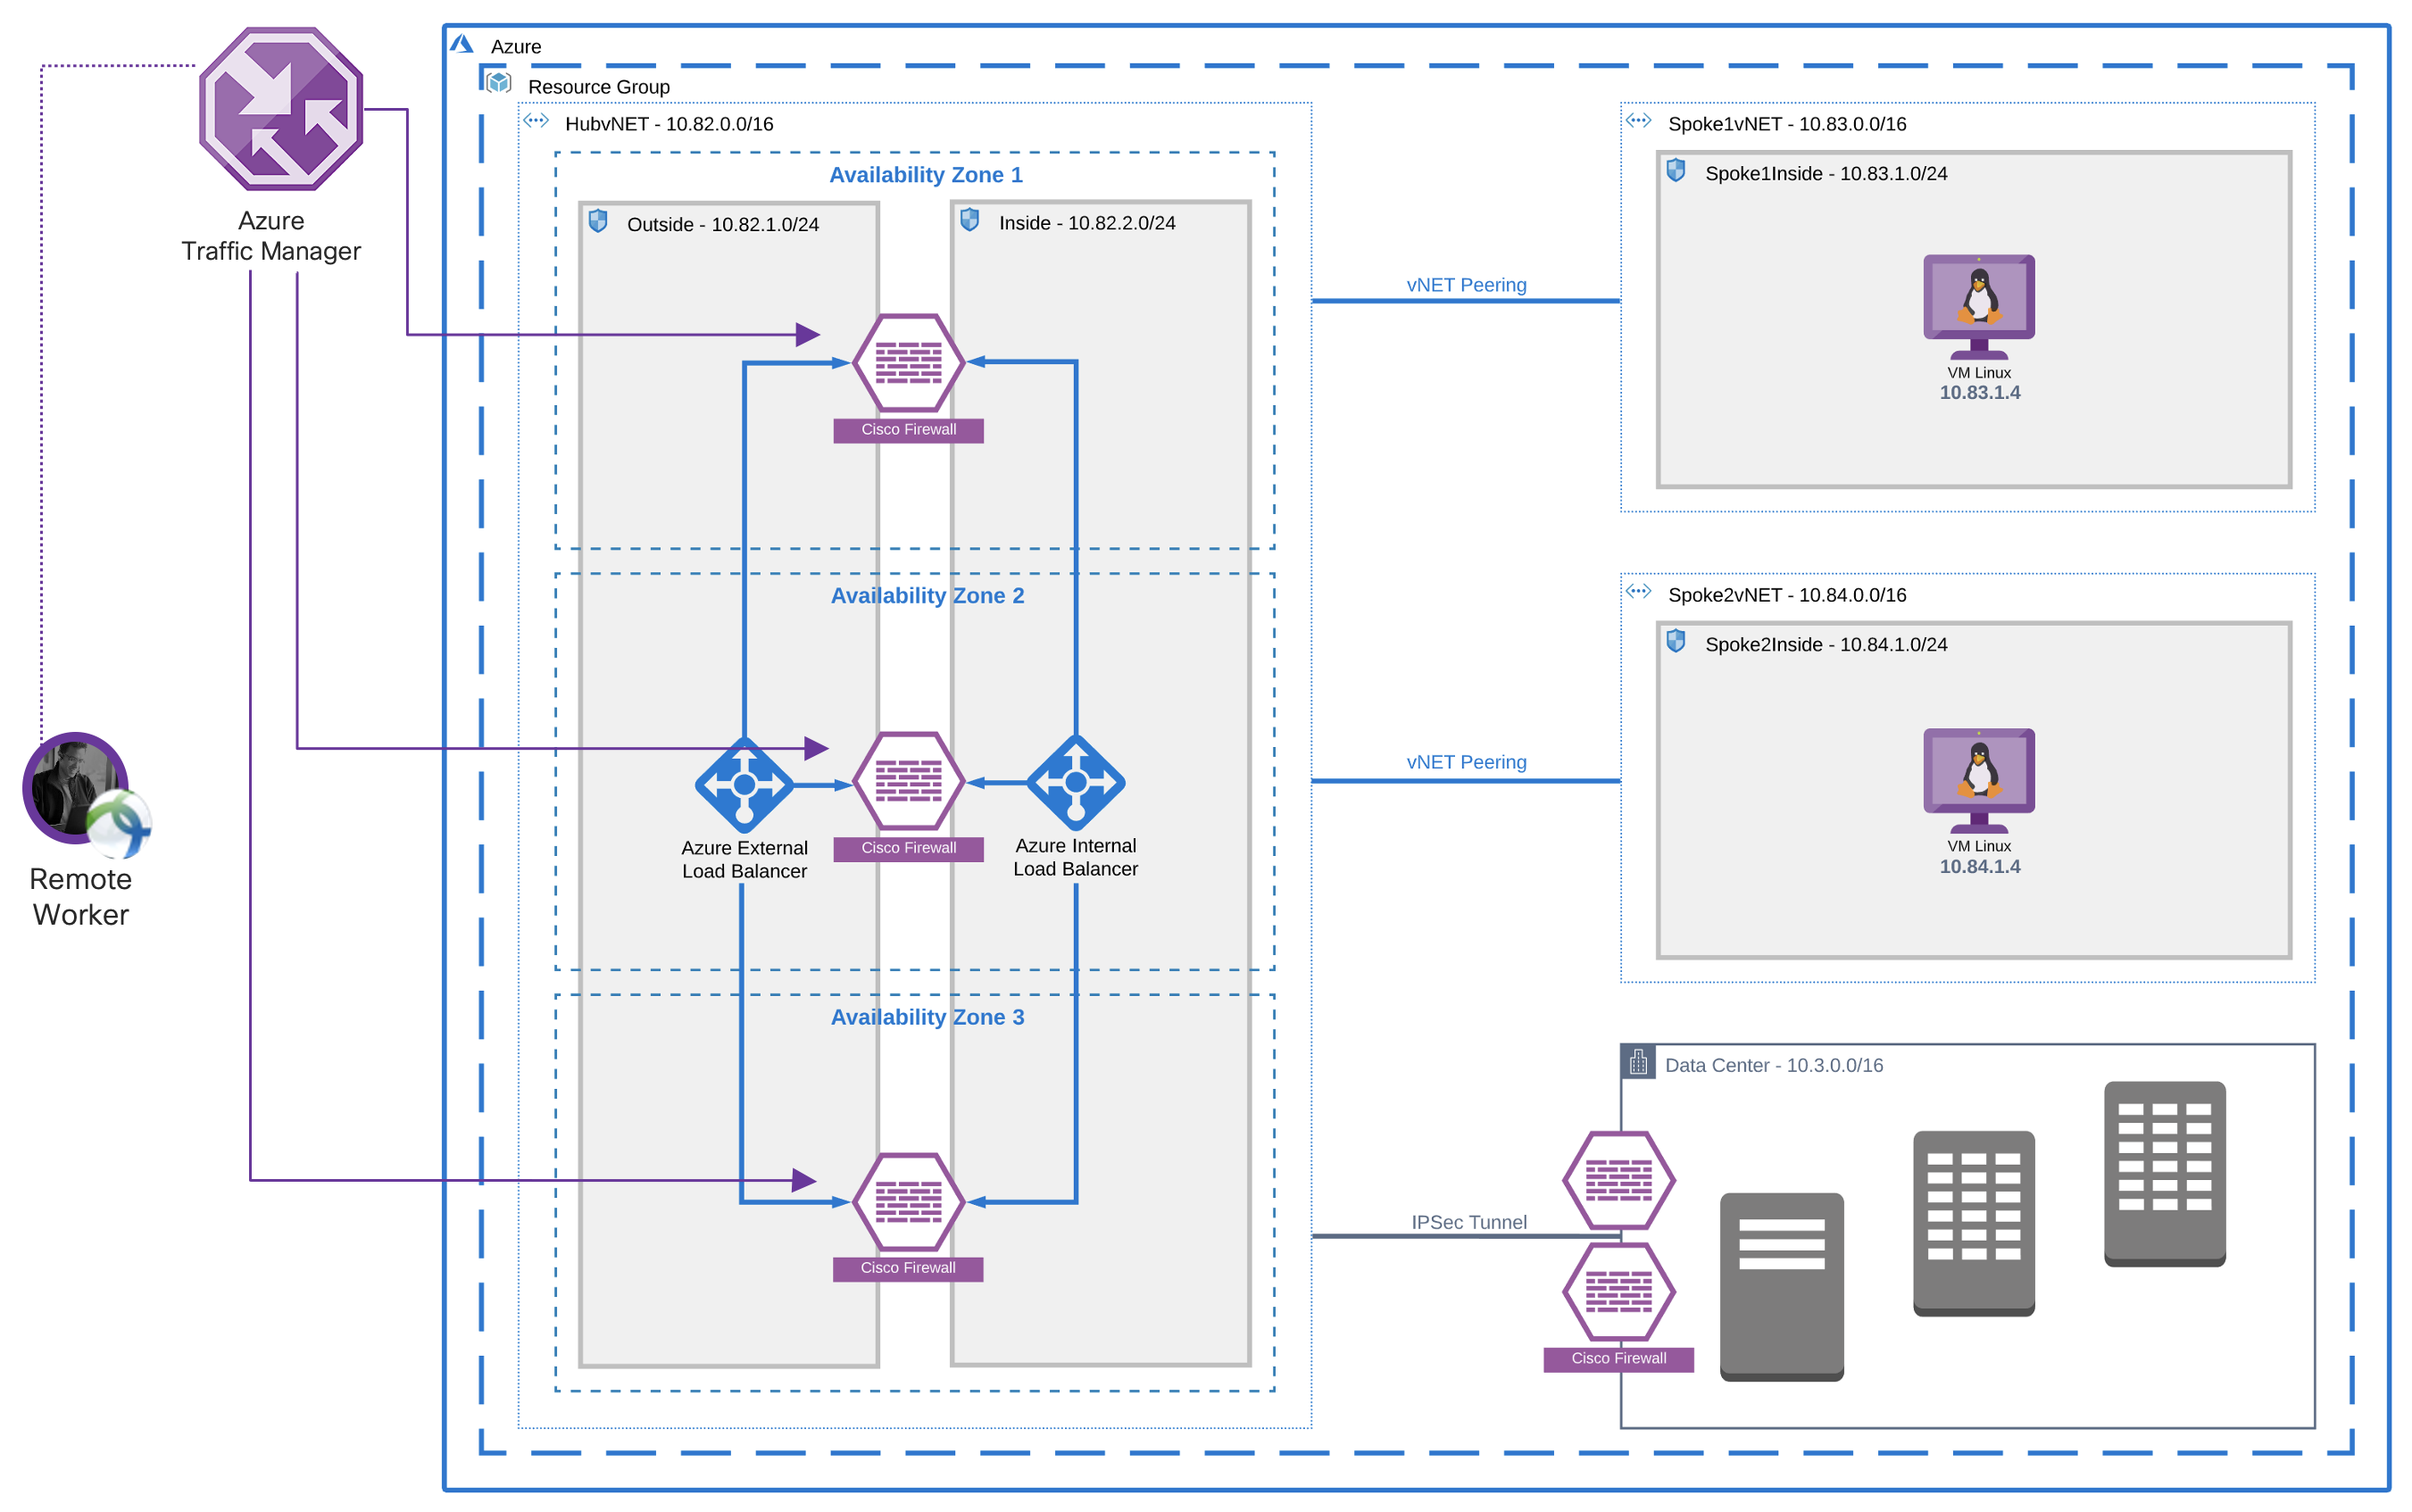
Figure 2: Cisco Secure Remote Worker Architecture for Azure - Cisco Blogs Wireless sensor networks also are used for the collection of data for monitoring of environmental information. This can be as simple as monitoring the temperature in a fridge or the level of water in overflow tanks in nuclear power plants. The statistical information can then be used to show how systems have been working. The advantage of WSNs over conventional loggers is the "live" data feed that is possible.
WSN can be used to monitor the condition of civil infrastructure and related geo-physical processes close to real time, and over long periods through data logging, using appropriately interfaced sensors. Power consumption constraints for nodes using batteries or energy harvesting. Examples of suppliers are ReVibe Energy and Perpetuum Ability to cope with node failures (resilience) Some mobility of nodes (for highly mobile nodes see MWSNs) Heterogeneity of nodes Homogeneity of nodes Scalability to large scale of deployment Ability to withstand harsh environmental conditions Ease of use Cross-layer optimization Cross-layer is becoming an important studying area for wireless communications. In addition, the traditional layered approach presents three main problems: Traditional layered approach cannot share different information among different layers, which leads to each layer not having complete information. The traditional layered approach cannot guarantee the optimization of the entire network. The traditional layered approach does not have the ability to adapt to the environmental change. Because of the interference between the different users, access conflicts, fading, and the change of environment in the wireless sensor networks, traditional layered approach for wired networks is not applicable to wireless networks. So the cross-layer can be used to make the optimal modulation to improve the transmission performance, such as data rate, energy efficiency, quality of service (QoS), etc.
Sensor nodes can be imagined as small computers which are extremely basic in terms of their interfaces and their components. They usually consist of a processing unit with limited computational power and limited memory, sensors or MEMS (including specific conditioning circuitry), a communication device (usually radio transceivers or alternatively optical), and a power source usually in the form of a battery. Other possible inclusions are energy harvesting modules, secondary ASICs, and possibly secondary communication interface (e.g. RS-232 or USB). The base stations are one or more components of the WSN with much more computational, energy and communication resources. They act as a gateway between sensor nodes and the end user as they typically forward data from the WSN on to a server. Other special components in routing based networks are routers, designed to compute, calculate and distribute the routing tables.
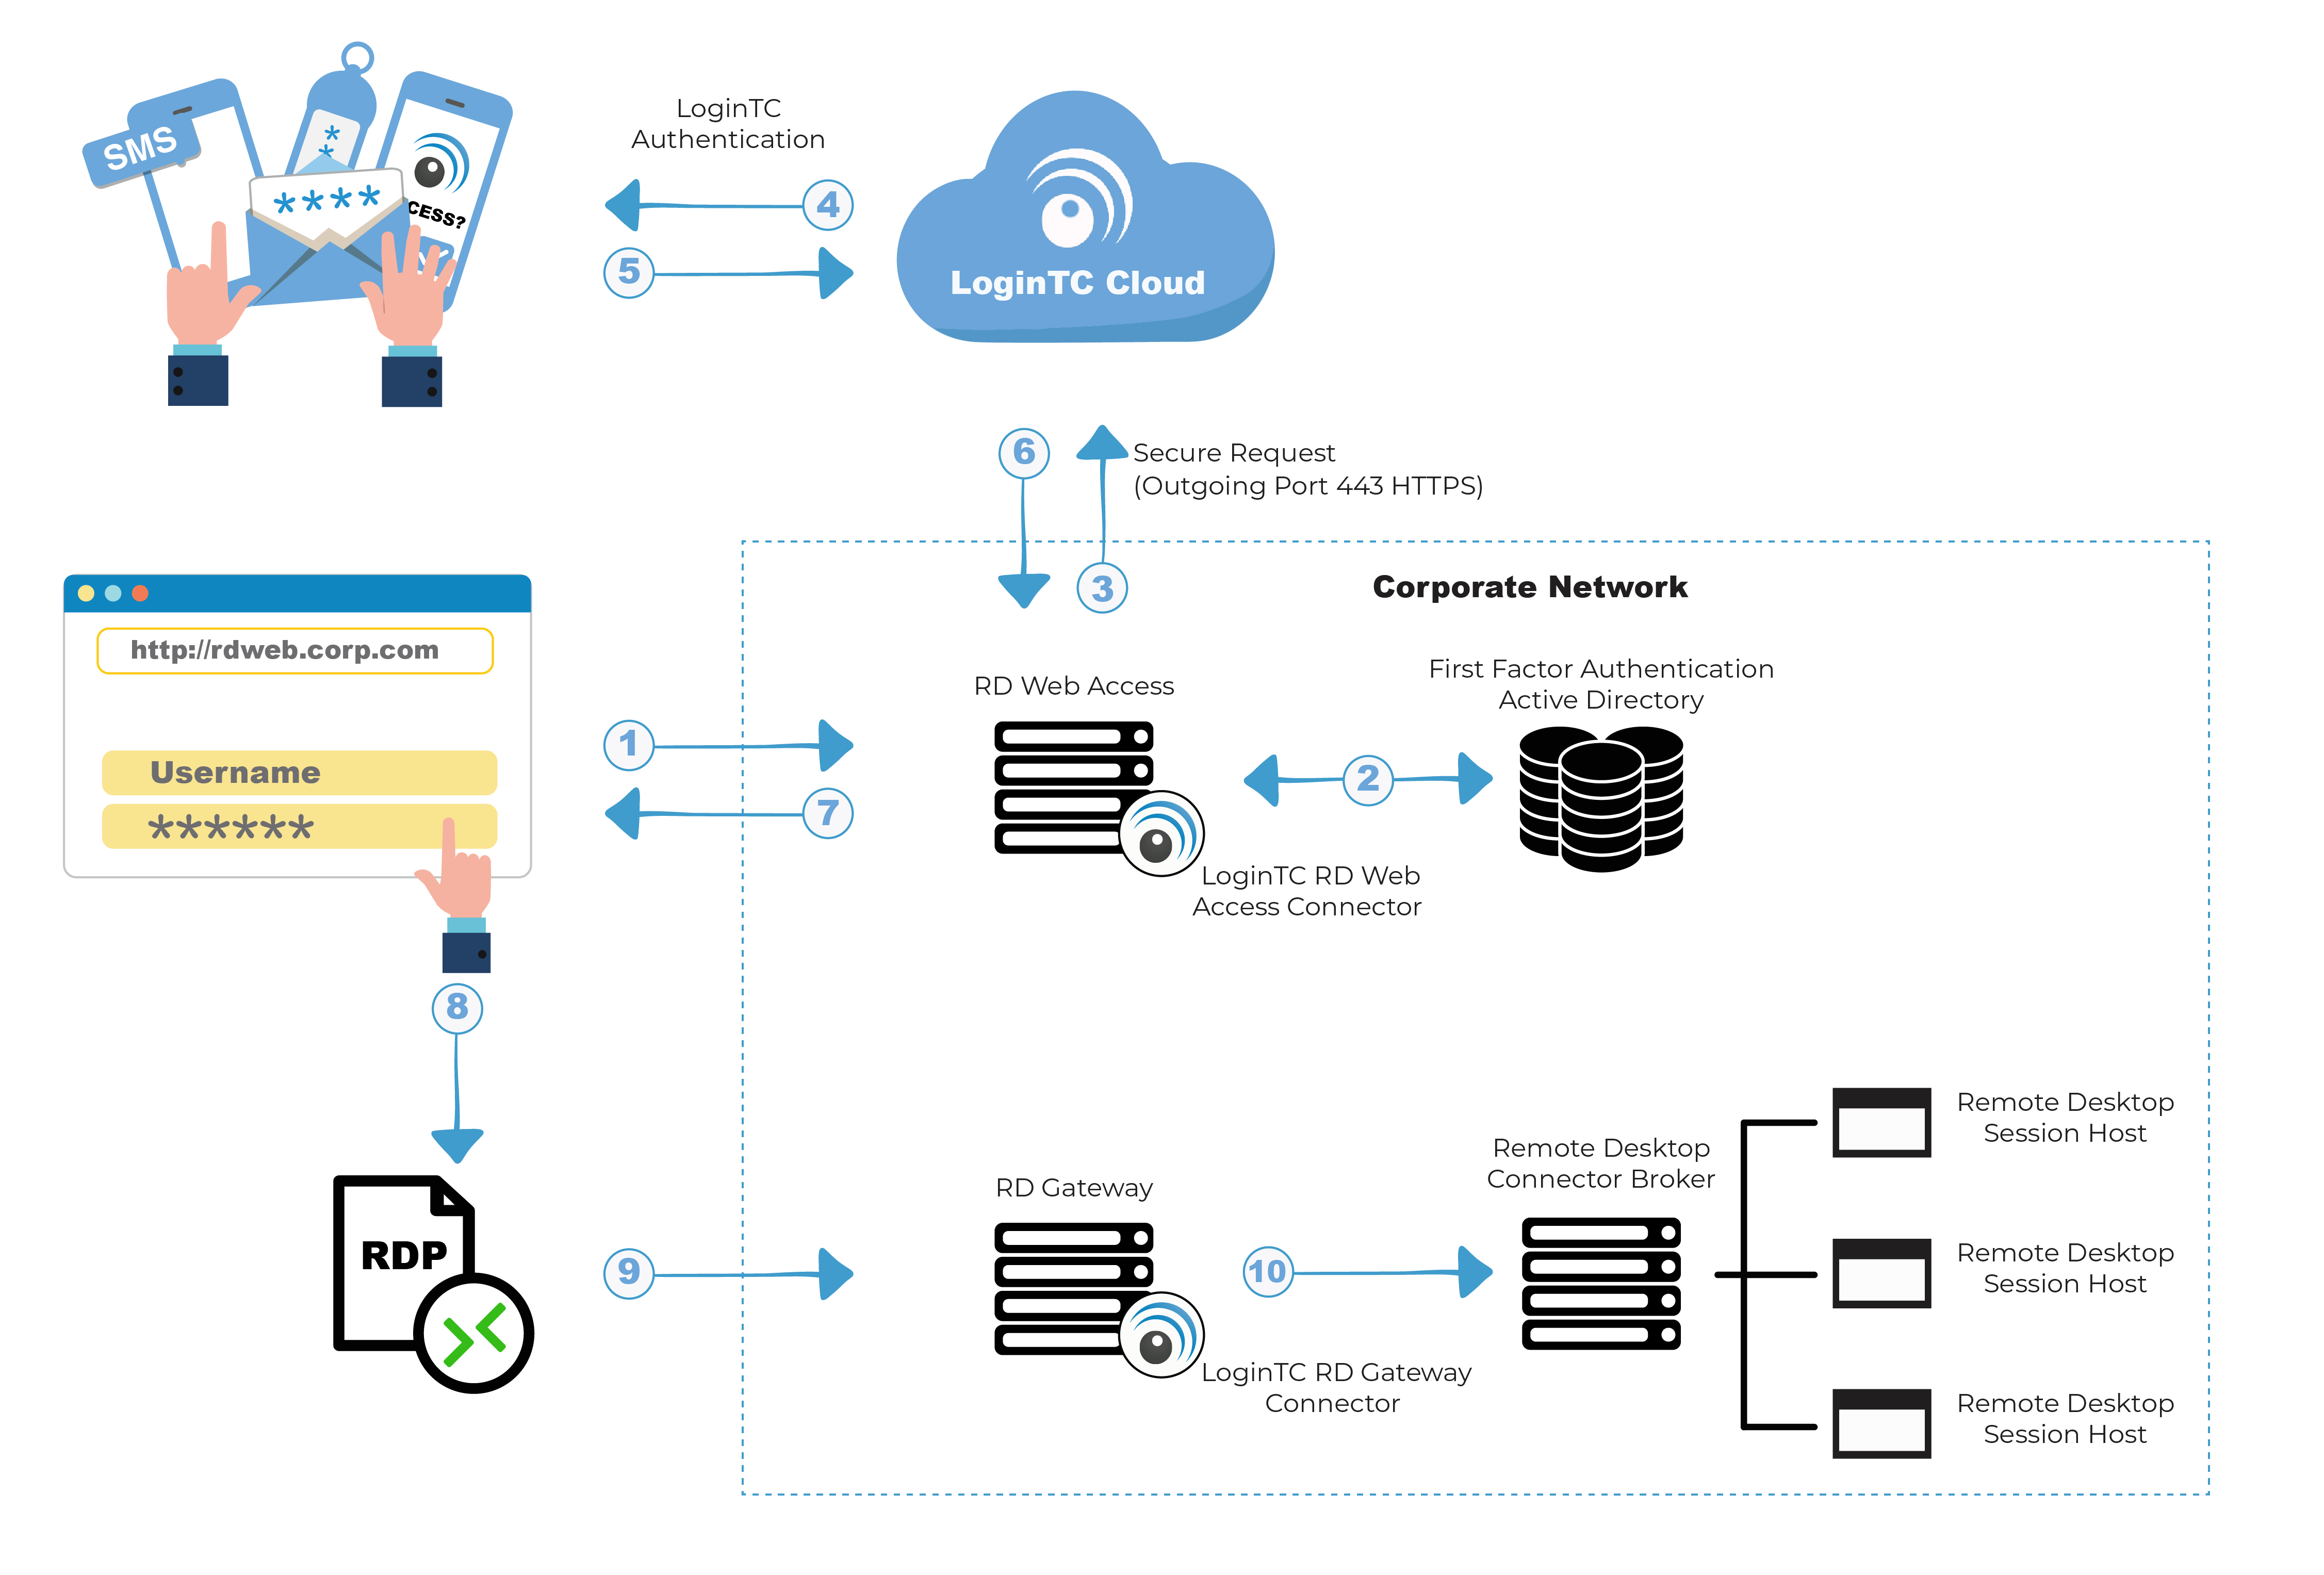
Figure 3: Security Access Can Gateway at Jeramy Phillip blog One major challenge in a WSN is to produce low cost and tiny sensor nodes. There are an increasing number of small companies producing WSN hardware and the commercial situation can be compared to home computing in the 1970s. Many of the nodes are still in the research and development stage, particularly their software. Also inherent to sensor network adoption is the use of very low power methods for radio communication and data acquisition. In many applications, a WSN communicates with a local area network or wide area network through a gateway. The Gateway acts as a bridge between the WSN and the other network. This enables data to be stored and processed by devices with more resources, for example, in a remotely located server. A wireless wide area network used primarily for low-power devices is known as a Low-Power Wide-Area Network (LPWAN).
Increased lifespan Robustness and fault tolerance Self-configuration Lifetime maximization: Energy/Power Consumption of the sensing device should be minimized and sensor nodes should be energy efficient since their limited energy resource determines their lifetime. To conserve power, wireless sensor nodes normally power off both the radio transmitter and the radio receiver when not in use.
Sensor nodes are prone to failure, For better collection of data, To provide nodes with backup in case of failure of the central node. There is also no centralised body to allocate the resources and they have to be self organized. As for the distributed filtering over distributed sensor network. the general setup is to observe the underlying process through a group of sensors organized according to a given network topology, which renders the individual observer estimates the system state based not only on its own measurement but also on its neighbors'.
The data gathered from wireless sensor networks is usually saved in the form of numerical data in a central base station. Additionally, the Open Geospatial Consortium (OGC) is specifying standards for interoperability interfaces and metadata encodings that enable real time integration of heterogeneous sensor webs into the Internet, allowing any individual to monitor or control wireless sensor networks through a web browser.
Dieser Inhalt ist eine maschinelle Übersetzung, die dynamisch erstellt wurde. (Haftungsausschluss) Cet article a été traduit automatiquement de manière dynamique. (Clause de non responsabilité) Questo contenuto è stato tradotto dinamicamente con traduzione automatica. (Esclusione di responsabilità)) Citrix Cloud manages the operation for Citrix Gateway services, replacing the need for customers to manage the NetScaler Gateway appliance. Citrix Gateway service is provisioned through Citrix Workspace app.
HDX Connectivity: The Virtual Delivery Agents (VDAs) hosting the apps and desktops remain under the customer’s control in the data center of their choice, either cloud or on-premises. These components are connected to the cloud service using an agent called the Citrix Cloud Connector. DTLS 1.2 protocol support: Citrix Gateway service supports Datagram Transport Layer Security (DTLS) 1.2 for HDX sessions over EDT (UDP-based transport protocol). The following cipher suites are supported: TLS protocol support: Citrix Gateway service supports the following TLS cipher suites: Endpoint Management integration: When integrated with Citrix Endpoint Management plus Citrix Workspace, the Citrix Gateway service provides secure remote device access to your internal network and resources. Onboarding the Citrix Gateway service with Endpoint Management is fast and simple. The Citrix Gateway service includes full support of Citrix SSO for apps such as Secure Mail and Secure Web.
Citrix Gateway service is a globally distributed multitenant service. End users use the nearest Point-of-Presence (PoP) where the particular function that they need is available, regardless of Citrix Cloud Control plane geo-selection or the location of the applications being accessed. Configuration, such as authorization meta-data is replicated to all PoPs. Logs used by Citrix® for diagnostic, monitoring, business, and capacity planning are secured and stored in one central location.
Customer configuration is stored in one central location and distributed globally to all PoPs. Data flowing between the cloud and customer premises uses secure TLS connections over port 443. Encryption keys used for user authentication and single sign-on are stored in hardware security modules. Currently the Citrix Gateway service does not make auditing and change control logs available to customers. Logs are available to Citrix which can be used to audit the activities of end-user and administrator.
Citrix recommends that users consult the published best practices documentation for deploying Citrix Gateway services. More considerations regarding SaaS apps and Enterprise web apps deployment, and network connector are as follows. Selecting the correct Connector : The correct connector must be selected, depending on the use case: For information on Citrix Cloud Connector network access requirements, see Internet connectivity requirements .
Using the Citrix Gateway service avoids the need to deploy NetScaler Gateway within the customer data centers. To use the Citrix Gateway service, it is a prerequisite to use Citrix Workspace delivered from Citrix Cloud. Customers are recommended to use TLS within their network and not enable SSO for applications over HTTP. You agree to hold this documentation confidential pursuant to the terms of your Citrix Beta/Tech Preview Agreement.
2. System Architecture & Core Working Principles The development, release and timing of any features or functionality described in the Preview documentation remains at our sole discretion and are subject to change without notice or consultation. The documentation is for informational purposes only and is not a commitment, promise or legal obligation to deliver any material, code or functionality and should not be relied upon in making Citrix product purchase decisions.
Configure Remote Desktop Gateway (RD Gateway) allows users to securely access Remote Desktop services over the internet without exposing port 3389 directly. RD Gateway encrypts Remote Desktop traffic using HTTPS (TCP 443), making remote connections significantly more secure while simplifying firewall configuration. Whether you’re setting up remote access for your business, managing Windows servers, or building a secure remote work environment, this guide will teach you how to configure Remote Desktop Gateway (RD Gateway) on Windows Server with this complete step-by-step guide. Improve RDP security and access your remote desktop safely from anywhere.
Remote Desktop Gateway (RD Gateway) is a Windows Server role that enables authorized users to connect to internal computers through encrypted HTTPS connections. Instead of opening Remote Desktop Protocol (RDP) directly to the internet, RD Gateway acts as a secure tunnel between remote users and internal computers.
Remote Desktop Gateway is one of the safest methods for publishing Remote Desktop Services over the internet. By tunneling RDP traffic through HTTPS, enforcing authentication policies, and reducing exposure to cyber threats, RD Gateway provides a secure and scalable remote access solution for businesses of all sizes. Following the steps in this guide—installing the RD Gateway role, configuring SSL, setting up CAP and RAP policies, and securing the server with best practices—will help you build a reliable remote access environment that protects both users and internal systems while delivering seamless Remote Desktop connectivity.
Configuring a Remote Desktop Gateway (RD Gateway) is one of the most effective ways to secure remote desktop connections without relying on VPNs. This guide explains how to set up RDP Gateway on Windows Server, with clear steps for installation, configuration, testing, and management, while highlighting how TSplus Remote Access can provide a simpler, cost-effective alternative.
IT administrators need to provide employees with reliable and secure access to internal desktops and applications. Traditionally, this was achieved by exposing RDP over port 3389 or relying on a VPN. Both approaches introduce complexity and potential security risks. Microsoft’s Remote Desktop Gateway (RD Gateway) solves this by tunnelling Remote Desktop connections through HTTPS on port 443. In this article, we will walk through the setup process for RD Gateway on Windows Server and discuss how TSplus Remote Access offers an easier, scalable alternative for organizations of all sizes.
A Remote Desktop Gateway (RD Gateway) is a Windows Server role that allows secure remote connections to internal resources over the internet by tunnelling RDP traffic through HTTPS on port 443. It protects against brute-force attacks with SSL/ TLS encryption and applies strict access rules through Connection Authorization Policies (CAPs) and Resource Authorization Policies (RAPs), giving administrators fine-grained control over who can connect and what they can access One of the biggest advantages of RD Gateway is its reliance on HTTPS, which allows users to connect through networks that would normally block RDP traffic. The integration with SSL certificates also ensures encrypted sessions, and administrators can configure CAPs and RAPs to restrict access based on user roles, device compliance, or time of day.
Although VPNs are a common way to provide remote access, they often require more complex configuration and can expose broader parts of the network than necessary. By contrast, RD Gateway focuses specifically on securing RDP sessions. It does not grant access to the entire network, only to approved desktops and applications. This narrower scope helps reduce the attack surface and simplifies compliance in industries with strict governance requirements.
Before setting up RD Gateway, make sure your server is joined to the Active Directory domain and running Windows Server 2016 or later with the Remote Desktop Services role installed. Administrator rights are required to complete the configuration. You will also need a valid SSL certificate from a trusted CA to secure connections and properly configured DNS records so the external hostname resolves to the server’s public IP. Without these elements in place, the gateway will not function correctly.
The installation can be performed either through the Server Manager GUI or PowerShell. Using Server Manager, the administrator adds the Remote Desktop Gateway role through the Add Roles and Features wizard. The process automatically installs required components such as IIS. For automation or faster deployment, PowerShell is a practical option. Running the command Install-WindowsFeature RDS-Gateway -IncludeAllSubFeature -Restart installs the role and reboots the server as needed.
Once complete, administrators can confirm the installation with Get-WindowsFeature RDS-Gateway , which displays the installed state of the feature. An SSL certificate must be imported and bound to the RD Gateway server to encrypt all RDP traffic over HTTPS. Administrators open RD Gateway Manager, navigate to the SSL Certificate tab, and import the .pfx file. Using a certificate from a trusted CA avoids client trust issues.
For organizations running test environments, a self-signed certificate may suffice, but in production, public certificates are recommended. They ensure that users connecting from outside the organization do not face warnings or blocked connections. The next step is to define the policies that control user access. Connection Authorization Policies specify which users or groups are allowed to connect through the gateway. Authentication methods such as passwords, smart cards, or both can be enforced. Device redirection can also be allowed or restricted depending on the security posture.
Resource Authorization Policies then define which internal servers or desktops those users can reach. Administrators can group resources by IP addresses, hostnames, or Active Directory objects. This separation of user and resource policies provides precise control and reduces the risk of unauthorized access. Testing ensures that the configuration works as expected. On a Windows client, the Remote Desktop Connection client (mstsc) can be used. Under Advanced settings, the user specifies the external hostname of the RD Gateway server. After providing credentials, the connection should be established seamlessly.
Administrators can also run command-line tests with mstsc /v: /gateway: . Monitoring the logs within RD Gateway Manager helps confirm whether authentication and resource authorization are working as configured. Since RD Gateway uses port 443 , administrators must allow inbound HTTPS traffic on the firewall. For organizations behind a NAT device, port forwarding must direct requests on port 443 to the RD Gateway server. Proper DNS records must be in place so that the external hostname (for example, rdgateway.company.com ) resolves to the correct public IP. These configurations ensure that users outside the corporate network can reach the RD Gateway without issue.
Ongoing monitoring is critical to maintaining a secure environment. The RD Gateway Manager provides built-in monitoring tools that show active sessions, session duration, and failed login attempts. Reviewing logs regularly helps identify potential brute-force attacks or misconfigurations. Integrating monitoring with centralized logging platforms can provide even deeper visibility and alerting capabilities.
While RD Gateway is a powerful tool, several common issues can arise during setup and operation. SSL certificate problems are frequent, especially when self-signed certificates are used in production. Using publicly trusted certificates minimizes these headaches. Another common issue involves DNS misconfiguration. If the external hostname does not resolve properly, users will fail to connect. Ensuring accurate DNS records both internally and externally is essential. Firewall misconfigurations can also block traffic, so administrators should double-check port forwarding and firewall rules when troubleshooting.
Finally, CAP and RAP policies must be carefully aligned. If users are authorized by CAP but not given access by RAP, connections will be denied. Reviewing policy order and scope can resolve such access issues quickly. While RD Gateway provides a secure method for publishing RDP over HTTPS, it can be complex to deploy and manage, particularly for small and medium-sized businesses. This is where TSplus Remote Access comes in as a simplified, cost-effective solution.
TSplus Remote Access eliminates the need for configuring CAPs, RAPs, and SSL bindings manually. Instead, it provides a straightforward web-based portal that allows users to connect to their desktops or applications directly through a browser. With HTML5 support, no additional client software is required. This makes remote access accessible on any device, including tablets and smartphones.
In addition to ease of deployment, TSplus Remote Access is significantly more affordable than implementing and maintaining Windows Server RDS infrastructure. Organizations can benefit from features such as application publishing, secure web access, and multi-user support, all within a single platform. For IT teams seeking a balance of security, performance, and simplicity, our solution is an excellent alternative to traditional RDP Gateway deployments.
Configuring a Remote Desktop Gateway helps organizations secure RDP traffic and provide encrypted access without exposing port 3389 or relying on VPNs. However, the complexity of managing certificates, CAPs, RAPs, and firewall rules can make RD Gateway challenging for smaller teams. TSplus Remote Access offers a simplified, affordable approach that delivers the same secure connectivity with fewer hurdles. Whether deploying RD Gateway or opting for TSplus, the goal remains the same: enabling reliable, secure, and efficient remote access to support modern workforces.
Ultimate Citrix/RDS alternative for desktop/app access. Secure, cost-effective, on-premises/cloud The ideal alternative to Citrix and Microsoft RDS for remote desktop access and Windows application delivery. Compare browser-based remote access and VPNs for business apps. Learn which model fits application delivery, network access, security and user needs best.
Looking for a Windows 365 alternative? Compare Windows 365 and TSplus for Cloud PCs, remote Windows app delivery, hosting, management and cost. Compare Parallels RAS and TSplus Remote Access for Windows application publishing, browser access, licensing, security, scalability and deployment.
3. Software Implementation, Frameworks & Protocols Brush up on how digital workplace transformation aligns people, processes, secure app delivery and IT operations to create a simpler, resilient modern workplace. Remote Desktop Gateway (RD Gateway) enables secure, authenticated, and encrypted remote access to internal corporate resources via HTTPS.
The modern work environment is no longer confined to the traditional office space. Employees need seamless and secure access to internal resources when working from home, traveling, or in satellite offices. Remote access solutions bridge the geographical gap, enabling users to connect to the corporate network from virtually anywhere. While various remote access solutions exist, Microsoft’s Remote Desktop Gateway (RD Gateway) is key. But what is Remote Desktop Gateway server and how does it secure remote access to corporate networks? In this guide, we will help you understand RD Gateway, offer a step-by-step approach to configure the gateway for remote desktops, provide an overview of security considerations, and discuss how best to address common issues.
RD Gateway, Microsoft Remote Desktop Gateway, or simply Remote Desktop Gateway, is a role service in Windows Server that enables authorized remote users to connect to resources within an internal corporate network over a secure channel. It acts as an intermediary between remote desktop clients and the target internal network, ensuring that connections are authenticated, encrypted, and routed through a secure tunnel.
It acts as a gateway between the public internet and the internal network, shielding it against unauthorized access. Enhance RDG by utilizing NinjaOne Remote Access to create a secure and efficient remote access infrastructure. Organizations often ask how secure Remote Desktop Gateway (RD Gateway) is. There are several reasons an organization may elect to use RD Gateway to manage remote server connectivity. These include: Microsoft Remote Desktop Gateway is an intermediary that mediates connections between remote desktop clients and internal resources. It authenticates users, ensures secure data transmission, and facilitates the seamless flow of information between the remote client and the internal network.
Employing a two-step authentication ensures that users are first authenticated through a secure login process. Once authenticated, the RD Gateway verifies the user’s authorization to access the requested internal resources. The HTTPS protocol tunnels connections to the internal network through a secure channel. This ensures that data transmitted between the client and the internal network is encrypted, safeguarding it from potential eavesdropping or tampering.
RD Gateway is compatible with many remote desktop clients , including the native Windows Remote Desktop Connection client, third-party applications, and even mobile devices. RD Gateway uses load balancing to distribute incoming connections across multiple servers. This maintains performance and availability during high traffic. Before setting up RD Gateway, there are several steps that you need to take into consideration first: Windows s erver: Ensure you have a Windows Server operating system installed, such as Windows Server 2022 or Windows Server 2019. This provides the foundation for running the RD Gateway role.
Active Directory: Users must have the appropriate permissions to access the Remote Desktop Gateway server and its resources. That’s why one of the prerequisites is having a domain environment with Active Directory for user authentication and authorization. SSL c ertificate: A valid SSL certificate from a trusted authority secures communication between the Remote Desktop Gateway server and clients, ensuring data confidentiality and integrity.
Create VPN c onnections: VPN connections provide a secure tunnel for traffic to reach the RD Gateway. Sometimes, you are also required to create Virtual Private Network (VPN) connections to cater to remote locations or networks that need access to the RD Gateway. DNS s ettings: Verify that the server can resolve DNS names correctly. This is essential for accessing network resources.
Set c onditions: Preset conditions help you implement additional security measures and restrictions. Define conditions for access, such as specific IP addresses, time periods, or device types. Before defining your specific rules, it is helpful to understand how these two policies work together to secure your environment. While a CAP acts as the “front door” key, the RAP determines which “rooms” a user is allowed to enter once inside.
Grant a ccess: Creating a Resource Authorization Policy (RAP) lets you control which resources are accessible to different users. Create RAPs to grant users or groups access to specific resources within the internal network. Define p ermissions: Specify the level of access (e.g., full control, read-only) for each resource. This determines what actions users can perform on the resources.
Once the server-side configuration is complete, you must configure the Remote Desktop Connection client on the user’s local machine to recognize and use the Gateway. In the current threat landscape, relying solely on a username and password for remote access is a significant security risk. To protect against credential theft and brute-force attacks, it is highly recommended to integrate Multi-Factor Authentication (MFA) into your RD Gateway deployment.
By implementing MFA, users must approve a push notification or enter a code on their mobile device before the RD Gateway grants access to the internal network. Common ways to achieve this include: Security Note: Implementing MFA at the Gateway level effectively neutralizes the risk of leaked credentials, as the attacker would also need physical access to the user’s secondary device to successfully tunnel into your network.
Once RD Gateway has been installed, several configuration steps are required to align with remote access best practices : Define Remote Desktop Gateway policies to control user access, connection parameters, and security settings. Launch the RD Gateway Manager and navigate to the “Policies” node. Right-click, and select “Create New Authorization Policies.” Follow the prompts to define access policies based on user groups, resource authorization, and connection parameters.
Configure user access permissions and groups to determine who can connect to the RD Gateway and the internal resources. Navigate to “Server Manager” and select “Remote Desktop Services” from the left-hand menu. Under the “Collections” node, select the collection you want to configure. In the “Tasks” pane, click on “Edit properties,” and under the “User Groups” tab, define the user groups allowed to connect.
Customize RD Gateway properties to align with your organization’s requirements and security policies. Launch the RD Gateway Manager, navigate to the server node, right-click, and select “Properties.” Adjust settings such as timeout periods, device redirection, and logging options to match your organization’s needs. If errors or difficulties arise during or after the setup process, your first stop should be the Event Viewer. Navigate to Applications and Services Logs > Microsoft > Windows > TerminalServices-Gateway to find specific logs that indicate whether a CAP or RAP is blocking a user.
A common cause for total service outages is SSL certificate expiration. Regularly monitor the expiry dates and configure reminders to allow sufficient time for renewals. This ensures the secure tunnel remains active and prevents sudden connectivity issues for your entire workforce. If the certificate is valid but the connection fails, verify that TCP Port 443 is open on your external firewall. For optimized performance, ensure UDP Port 3391 is also reachable to allow for smoother RDP data transport.
Boost the security and efficiency of your remote access setup by integrating NinjaOne Remote Access with RDG. Secure your remote connections the right way – watch how to set up Remote Desktop Gateway . 4. Practical Deployment, Analysis & Case Studies Setting up a Remote Desktop Gateway provides secure and efficient remote access. Proper setup, maintenance, and operation ensure the RD Gateway functions as a reliable access point for organizations RD Gateway is pivotal in ensuring encrypted and authenticated connections, allowing organizations to embrace remote work without compromising security.
NinjaOne Remote is NinjaOne’s remote access tool integrated directly into NinjaOne RMM. Built from the ground up, it offers a strong and secure RDP tool using our own gateway. Watch a demo or sign up for a free trial to see Ninja Remote in action. RD Gateway acts as a secure intermediary between remote desktop clients and internal network resources. It authenticates users, encrypts data over HTTPS, and routes RDP traffic securely through a single access point, eliminating the need to expose Port 3389 to the internet..
You need a Windows Server (2019 or 2022), properly configured DNS records, firewall rules allowing TCP port 443 (and optionally UDP Port 3391 for better performance). You also require, Active Directory for authentication, and a valid SSL certificate from a trusted authority that matches your external FQDN. Connection Authorization Policies (CAP) define who is allowed to connect through the gateway (e.g., specific user groups or MFA-enabled users). Resource Authorization Policies (RAP) specify where those users can go by defining which internal PCs or servers they are permitted to access Performance issues are often caused by relying solely on TCP Port 443. For a smoother experience, ensure UDP Port 3391 is open on your firewall. This enables RDP’s reliable UDP transport, which significantly reduces latency for mouse movements and video.
Yes. In fact, it is a security best practice. RD Gateway can be integrated with Microsoft Entra MFA (via the NPS Extension) or third-party providers like Duo Security to require a mobile push notification before a connection is granted. Start by checking the Event Viewer under TerminalServices-Gateway for specific policy blocks. Additionally, verify that your SSL certificate hasn’t expired and that the certificate name matches the external URL you are using to connect Browse our on-demand demos to see how NinjaOne simplifies IT tasks like endpoint management, patching, MDM, ticketing, and more By clicking the “I Accept” button below, you indicate your acceptance of the following legal terms as well as our Terms of Use : Access to this page requires authorization. You can try signing in or changing directories .
The Remote Desktop Gateway (RD Gateway) role enables secure, encrypted connections to Remote Desktop Services (RDS) resources over the internet. With RD Gateway, users can access internal network resources from remote locations without the need for a VPN. You can deploy RD Gateway servers on either physical or virtual machines, supporting on-premises, cloud, or hybrid environments. This article guides you through installing and configuring the RD Gateway role to enhance the security and accessibility of your Remote Desktop environment.
Your device must have the Remote Desktop Services role installed. To learn more, see Add or remove roles and features in Windows Server . For this article, we're using default settings for installing the RD Gateway, progressing through without additional changes. Based on your own organizational needs, during the Role service selection for the Web Server Role (IIS), select the additional services necessary for your environment.
Once the RD Gateway role is installed, it needs to be configured. To configure the RD Gateway role, follow these steps: In the RD Gateway Manager on the left pane, right-click the name of your gateway, then select Properties . Select the SSL Certificate tab, select the Import a certificate into the RD Gateway radio button, then select Browse and Import Certificate .
After you've imported the certificate and its private key, the display should show the certificateâIIs key attributes. Because the RD Gateway role is supposed to be public, we recommend you use a publicly issued certificate. If you use a privately issued certificate, you'll need to make sure to configure all clients with the certificate's trust chain beforehand. If you want to add high availability to your RD Gateway role, see Add high availability to the RD Web and Gateway web front .
In today’s distributed work landscape, accessing corporate resources securely and efficiently from outside the office network isn’t just a convenience; it’s a fundamental requirement. For many organizations, particularly those entrenched in the Microsoft ecosystem, the Remote Desktop Gateway (RD Gateway) stands as a cornerstone of this secure access. Think of it as a fortified bridge, allowing your remote users to connect to internal network resources like Remote Desktop Session Hosts (RDSH) or individual workstations without directly exposing those internal machines to the harsh realities of the internet.
Without a proper remote desktop gateway setup, you’d be forced to either use a traditional VPN, which can be cumbersome for simple RDP connections, or worse, open RDP ports directly to the internet – a move that security professionals worldwide collectively shudder at. The RD Gateway acts as a proxy, encrypting the RDP traffic within an HTTPS tunnel, thus providing a much safer conduit. This not only enhances security by reducing the attack surface but also simplifies the user experience, as they only need to connect to a single, publicly accessible endpoint.
Setting up an RD Gateway, however, isn’t a trivial click-and-go process. It involves several critical steps, each with its own nuances and potential pitfalls. Getting it right ensures seamless, secure access; getting it wrong can lead to frustrating connectivity issues, performance bottlenecks, or, most critically, gaping security vulnerabilities. This guide will walk you through the essential stages of a robust remote desktop gateway setup, ensuring your remote access infrastructure is both functional and secure.
Before we dive into the nitty-gritty of the remote desktop gateway setup, let’s clarify its exact function within your network architecture. At its core, the RD Gateway is a role service that runs on a Windows Server. It leverages the Remote Desktop Protocol (RDP) over HTTPS to create a secure, encrypted connection between a remote client and an internal network resource that is also RDP-enabled.
Imagine your corporate network as a castle. Inside the castle walls are your servers and workstations. The internet is the wild, untamed land outside. A direct RDP connection from the internet to an internal machine is like opening a large, unguarded gate in your castle wall – incredibly risky. A traditional VPN is like building a secret, underground tunnel from a remote location directly into the castle. It works, but everyone needs their own key, and managing all those tunnels can get complex. The RD Gateway, on the other hand, is like a single, heavily guarded drawbridge. Remote users connect to this drawbridge, authenticate themselves, and only then are they permitted to traverse it to reach specific, authorized targets within the castle, all while their passage is monitored and encrypted.
This approach offers several distinct advantages. Firstly, it uses port 443 (HTTPS), which is almost universally open through firewalls, making connectivity much easier than trying to open custom RDP ports. Secondly, it centralizes access control, allowing administrators to define granular policies on who can connect and to what resources. Thirdly, it acts as a termination point for external connections, meaning your internal RDP hosts don’t need direct internet exposure, significantly reducing their attack surface. It’s a crucial piece of the puzzle for any organization embracing remote work or hybrid models.
1. Prerequisites and Planning : Laying the Foundation for Your Remote Desktop Gateway Setup Before you even think about clicking ‘install,’ proper planning is paramount. Skipping this step is a common rookie mistake that often leads to headaches down the line. You’ll need a dedicated server, preferably a virtual machine (VM), running a supported Windows Server operating system. Windows Server 2016, 2019, or 2022 are the common choices today. This server should not be a domain controller; best practice dictates keeping roles separate for security and performance reasons.
You’ll also need a static public IP address for your RD Gateway server and a fully qualified domain name (FQDN) that resolves to this IP address. For instance, something like rdp.yourcompany.com . This FQDN is what your remote users will type into their RDP client. Finally, and crucially, you’ll need a public SSL/TLS certificate issued by a trusted Certificate Authority (CA) for this FQDN. This certificate encrypts the HTTPS traffic, ensuring secure communication. Wildcard certificates (e.g., *.yourcompany.com ) can also work, but ensure the FQDN you choose for your RD Gateway is covered by the wildcard. (See: CDC on secure remote access .) Consider your network topology. The RD Gateway server will typically sit in a DMZ (demilitarized zone) or a dedicated segment that’s accessible from the internet but segmented from your internal production network. This provides an additional layer of security. Ensure your firewall rules are configured to allow inbound HTTPS (port 443) traffic to your RD Gateway server’s public IP address, and outbound RDP (port 3389) traffic from the RD Gateway server to your internal RDP hosts.
Don’t forget to factor in DNS resolution – both internal and external DNS entries must be correct for the FQDN. With your planning complete, it’s time to install the RD Gateway role. This is done through the Server Manager on your chosen Windows Server. Open Server Manager, click ‘Manage,’ and then ‘Add Roles and Features.’ The wizard will guide you through the process. Choose ‘Role-based or feature-based installation,’ then select your server from the server pool.
Under ‘Server Roles,’ expand ‘Remote Desktop Services.’ Here, you’ll find several options. Check the box next to ‘Remote Desktop Gateway.’ The wizard might prompt you to add necessary features; accept these. You don’t typically need the other Remote Desktop Services roles (like Session Host or Connection Broker) on this specific server, as its sole purpose should be to act as the gateway. Confirm your selections and proceed with the installation. Once the installation is complete, a restart might be required, though often it’s not immediately necessary for just the role installation.
This initial installation simply lays down the binaries and services. It doesn’t configure anything yet. Think of it as putting the engine in the car; you still need to connect all the wires and add fuel before it can run. The subsequent steps are where the real configuration work begins to make your remote desktop gateway setup truly functional and secure. The SSL certificate is absolutely critical for the security of your RD Gateway. Without it, your RDP traffic would be unencrypted, making it vulnerable to eavesdropping, and users would receive security warnings every time they try to connect. After installing the role, open Server Manager again, navigate to ‘Remote Desktop Services,’ and then ‘Overview.’ You should see a section for ‘RD Gateway’ with a warning about certificate configuration.
Click on the ‘RD Gateway’ icon or navigate to ‘Tools’ -> ‘Remote Desktop Services’ -> ‘Remote Desktop Gateway Manager.’ In the RD Gateway Manager, right-click on your server name in the left pane and select ‘Properties.’ Go to the ‘SSL Certificate’ tab. Here, you’ll have options to either create a self-signed certificate (only for testing, never for production!) or import an existing certificate. Since you’ve already obtained a public SSL certificate, you’ll choose the option to ‘Import a certificate from an existing .pfx file’ or ‘Select an existing certificate’ if it’s already in the server’s certificate store.
5. Performance Evaluation & Extended Technical Observations If you’re importing a .pfx file, you’ll need the password for it. This file contains both the public certificate and its corresponding private key, which is essential for decryption. Once imported, ensure the certificate details match your RD Gateway’s FQDN (e.g., rdp.yourcompany.com ) and that it’s issued by a trusted CA. If you’re using a wildcard certificate, make sure the FQDN you’re using for the gateway is covered by the wildcard. A correctly configured SSL certificate is non-negotiable for a secure remote desktop gateway setup.
Connection Authorization Policies (CAPs) define who is authorized to connect to the RD Gateway. These policies are based on user groups and various connection properties. To configure CAPs, open the Remote Desktop Gateway Manager, expand your server, and then expand ‘Policies.’ Right-click on ‘Connection Authorization Policies’ and select ‘Create New Policy.’ Give it a descriptive name, like ‘RD Gateway Users.’ In the policy wizard, you’ll specify which Active Directory user groups are permitted to use the RD Gateway. It’s a best practice to create a dedicated security group in Active Directory (e.g., ‘RD Gateway Access Group’) and add your remote users to it.
This makes management much cleaner. You can also specify device redirection settings (e.g., printers, clipboards, drives) and authentication methods (password or smart card). For most setups, password authentication is standard. You can also set idle and maximum session timeouts here, which are important for resource management and security. Review your settings carefully, as these policies are the first line of defense in controlling access. (See: NIST guidelines for secure connections .) Think of CAPs as the bouncer at the drawbridge. They check your ID and ensure you’re on the guest list. If you’re not in the authorized group, or if your connection doesn’t meet the specified criteria, the CAP will deny your access to the gateway itself, preventing you from even attempting to reach an internal resource. This granular control is a powerful feature of a well-implemented remote desktop gateway setup.
Resource Authorization Policies (RAPs) define what internal network resources the authorized users (as defined by CAPs) are allowed to connect to. This is where you specify the target computers or groups of computers that users can reach through the gateway. In the Remote Desktop Gateway Manager, right-click on ‘Resource Authorization Policies’ and select ‘Create New Policy.’ Give it a name, for example, ‘Internal RDP Hosts.’ The RAP wizard will ask you to link it to an existing CAP – usually, the one you just created. This means only users already authorized by the CAP can even be considered by this RAP. Then, you define the ‘Network Resources’ these users can access. You can specify individual computer names (e.g., server01.yourcompany.local ), IP addresses, or, more commonly and flexibly, Active Directory computer groups. For example, you might create a security group called ‘Remote Desktops’ and add all the workstations and servers that remote users need to access. This allows for centralized management of target resources.
You can also choose to ‘Allow users to connect to any network resource’ which, while easy, is generally a bad security practice for most scenarios. Always strive for the principle of least privilege. Only grant access to the resources absolutely necessary. RAP settings also allow you to specify which ports can be used, although for RDP, this is almost always port 3389. RAPs are the second layer of security, determining which rooms in the castle you’re allowed to enter after you’ve crossed the drawbridge. Properly configured RAPs are vital for a secure remote desktop gateway setup.
While we touched on this in planning, it’s worth revisiting as a dedicated step because firewall misconfigurations are a frequent cause of connectivity problems. Your external firewall (the one between your public IP and your RD Gateway server) needs to permit inbound TCP traffic on port 443 (HTTPS) to the public IP address of your RD Gateway server. This is the only port that needs to be open from the internet to your RD Gateway.
Internally, the firewall on the RD Gateway server itself (Windows Firewall with Advanced Security) needs to allow outbound TCP traffic on port 3389 (RDP) to your internal RDP hosts. Conversely, your internal RDP hosts’ firewalls need to allow inbound TCP 3389 traffic from the IP address of your RD Gateway server. It’s crucial not to open port 3389 directly from the internet to your internal machines; the RD Gateway handles that secure proxying.
If you have multiple network segments or a DMZ, ensure the routing and internal firewall rules between your RD Gateway server and your internal RDP hosts are correctly configured to allow RDP traffic. Regularly review your firewall rules, especially after making changes to your network or adding new RDP hosts, to ensure ongoing security and connectivity. A proper remote desktop gateway setup relies heavily on meticulous firewall management.
Once your remote desktop gateway setup is complete on the server side, it’s time to test it from a client perspective. Your remote users will use the standard Remote Desktop Connection (mstsc.exe) client. Open the client, click ‘Show Options,’ and go to the ‘Advanced’ tab. Click ‘Settings…’ under ‘Connect from anywhere.’ (See: Wikipedia on Remote Desktop Gateway .) In the ‘RD Gateway Server settings’ window, select ‘Use these RD Gateway server settings.’ Enter the FQDN of your RD Gateway (e.g., rdp.yourcompany.com ) in the ‘Server name’ field. You can usually leave the ‘Logon method’ as ‘Ask for password (NTLM)’ unless you’ve configured smart card authentication. Then, go back to the ‘General’ tab and enter the internal hostname or IP address of the target computer you want to connect to (e.g., internalpc01.yourcompany.local or 192.168.1.100 ). Crucially, the target computer name should be its internal name, not its public IP (which should be blocked anyway).
Attempt to connect. If everything is configured correctly, you should be prompted for your credentials (which will be authenticated against your Active Directory), and then you should connect to the internal machine. If you encounter issues, check the event logs on the RD Gateway server (specifically ‘Applications and Services Logs’ -> ‘Microsoft’ -> ‘Windows’ -> ‘TerminalServices-Gateway’) for clues. Common issues include certificate errors, incorrect CAP/RAP policies, or firewall blocks. Test with different user accounts and to different target machines to ensure your policies are working as intended.
Your remote desktop gateway setup isn’t a ‘set it and forget it’ solution. Ongoing monitoring and maintenance are essential. Regularly check the event logs on the RD Gateway server for any authentication failures, policy violations, or other errors. This can help identify potential security threats or misconfigurations. Performance monitoring is also important; if users report slow connections, check the server’s CPU, memory, and network utilization.
Keep your RD Gateway server’s operating system and the Remote Desktop Services roles patched and up-to-date with the latest security updates from Microsoft. New vulnerabilities are discovered regularly, and timely patching is your best defense. Periodically review your CAPs and RAPs. As your organization evolves, user roles change, and new resources are added, your policies will likely need adjustments. Ensure that access is always granted on a ‘least privilege’ basis – users should only be able to access what they absolutely need.
Consider implementing multi-factor authentication (MFA) for your RD Gateway. Integrating MFA with RD Gateway adds a significant layer of security, making it much harder for attackers to gain access even if they compromise user credentials. Solutions like Azure MFA or third-party MFA providers can be integrated to require a second factor (like a code from an authenticator app or a biometric scan) before a connection is allowed. This is perhaps one of the most impactful security enhancements you can make to your remote desktop gateway setup, especially in an era of rampant credential theft.
Regularly audit user access and remove permissions for users who no longer require them. A vigilant approach to maintenance and security will ensure your RD Gateway remains a reliable and secure access point for your remote workforce. A Remote Desktop Gateway (RD Gateway) is a role service that allows remote users to securely access internal network resources like Remote Desktop Session Hosts (RDSH) over the internet. It encrypts RDP traffic within an HTTPS tunnel, providing a secure connection without exposing internal machines directly to the internet.
Setting up a Remote Desktop Gateway involves several critical steps, including installing the RD Gateway role on a Windows Server, configuring SSL certificates, and setting up connection authorization policies. Following a detailed guide can help ensure a smooth and secure setup process. Using a Remote Desktop Gateway instead of a traditional VPN simplifies the connection process for remote users. It allows for secure RDP access without the cumbersome setup of a VPN and reduces the risk of exposing RDP ports directly to the internet, enhancing overall security.
The benefits of using an RD Gateway include enhanced security through encrypted connections, reduced attack surfaces, and improved user experience as remote users only need to connect to a single, secure endpoint. This setup also helps prevent potential security vulnerabilities associated with direct RDP access. Common issues when setting up a Remote Desktop Gateway include misconfigured SSL certificates, incorrect firewall settings, and improper authorization policies. These can lead to connectivity problems, performance bottlenecks, or security vulnerabilities, making careful configuration essential.
What's your take on this? Share your thoughts in the comments below — we read every one. Securing Remote Access in 2026: VPN vs ZTNA vs Secure Web Gateway - A Complete Guide for IT Teams The remote access landscape has undergone a seismic shift since the pandemic-era rush to deploy legacy VPNs. In 2026, IT teams no longer ask *"Do we need remote access?"* - they ask *"How do we enforce least-privilege, device-aware, session-level security across hybrid, cloud-native, and BYOD environments?"* The answer is rarely a single tool. Instead, it's a strategic blend of technologies anchored in Zero Trust principles - with VPN, ZTNA, and Secure Web Gateways (SWGs) each playing distinct, context-dependent roles.
Traditional VPNs were built on perimeter-based thinking: authenticate once, grant full network access, and assume trust thereafter. This model collapsed under the weight of cloud workloads, SaaS proliferation, and sophisticated lateral movement attacks. According to the 2026 Verizon DBIR, 68% of confirmed data breaches involved credential misuse - often enabled by over-provisioned VPN access. Meanwhile, Gartner reports that 73% of enterprises have either fully migrated from legacy VPNs or are actively decommissioning them in favor of identity- and application-centric controls.
Zero Trust Network Access (ZTNA) emerged as the architectural response - enforcing strict identity verification, device posture checks, and granular application-level authorization *before* any connection is established. Unlike VPNs, ZTNA never places the user on the corporate network. Instead, it brokers encrypted, policy-enforced connections directly to authorized applications - whether hosted on-premises, in private clouds, or via SaaS providers.
The following table compares core capabilities across three critical remote access technologies as validated in independent 2026 benchmarks (NSS Labs, NIST SP 800-207A, and TunnelPicks.net lab testing): - Use a VPN only when : You must support legacy line-of-business apps that require IP-based network adjacency (e.g., SMB file shares, older database clients), or operate in highly regulated air-gapped environments where internet-exposed ZTNA endpoints are prohibited. Even then, limit scope: restrict split-tunneling, enforce mandatory posture checks, and phase out within 12 months.
- Adopt ZTNA as your primary remote access layer when : You're modernizing infrastructure, adopting cloud/SaaS at scale, managing distributed workforces, or prioritizing least-privilege access. ZTNA excels for accessing internal APIs, DevOps tools (e.g., Jenkins, GitLab), ERP systems (SAP GUI via web wrapper), and private cloud resources. - Deploy an SWG (ideally integrated with ZTNA) when: Web-borne threats dominate your risk profile, you need comprehensive SaaS governance (e.g., enforcing data loss prevention in Google Workspace or Microsoft 365), or you lack visibility into unsanctioned cloud usage. Note: Standalone SWGs *do not replace* ZTNA - they complement it by securing outbound web traffic *after* ZTNA grants application access.
In practice, leading organizations use ZTNA as the foundational access control plane - routing users to approved apps - while feeding all HTTP/S traffic through an integrated SWG/CASB stack for inspection, DLP, and threat prevention. This "ZTNA + SWG" architecture is now the de facto standard for Fortune 500 remote access programs, per the 2026 Forrester Wave™. 1. Start with inventory and segmentation : Map all remote-accessed applications by sensitivity, protocol, and user group.
Classify them as *web*, *non-web*, *legacy*, or *SaaS*. This informs your tech mix - e.g., web apps → ZTNA+SWG; RDP/SSH → ZTNA with brokered sessions; SMB → phased VPN replacement via SMB-over-HTTPS gateways. 2. Prioritize identity hygiene : Before deploying ZTNA, ensure MFA is enforced universally, identities are synced via SCIM, and stale accounts are auto-deprovisioned. ZTNA magnifies weaknesses in identity management.
3. Leverage phased rollout : Begin with low-risk user groups (e.g., contractors accessing HR portals) using browser-based ZTNA access. Gradually expand to employees, then integrate lightweight agents for advanced posture checks (disk encryption, EDR status, OS patch level). 4. Integrate - don't isolate : Choose vendors offering native ZTNA-SWG convergence (e.g., Zscaler Private Access + ZIA, Netskope NewEdge). Avoid point solutions requiring complex orchestration layers.
5. Monitor and iterate : Track metrics like mean time to revoke access (target: <15 seconds), failed posture checks per day, and % of sessions blocked by SWG policies. Tune policies quarterly based on telemetry - not just compliance checkboxes. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Virtual%20private%20network • https://en.wikipedia.org/wiki/SD-WAN • https://en.wikipedia.org/wiki/Wireless%20sensor%20network • https://docs.citrix.com/en-us/citrix-gateway-service/technical-security-overview.html • https://blog.oudel.com/how-to-configure-remote-desktop-gateway-step-by-step-guide/ • https://tsplus.net/remote-access/blog/how-to-set-up-rdp-gateway/ • https://www.ninjaone.com/blog/how-to-set-up-remote-desktop-gateway/ • https://learn.microsoft.com/en-us/windows-server/remote/remote-desktop-services/remote-desktop-gateway-role • https://www.thetechedvocate.org/how-to-set-up-remote-desktop-gateway/ • https://tunnelpicks.net/blog/secure-remote-access-vpn-ztna-swg-2026
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Secure Remote Working Access Gateway.
[*] Metasploit Scan Running on Target Subnet for Secure Remote Working Access Gateway... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |