Complete Technical Paper Content — Secure Rest API Development With Rate Limiting And Jwt
Overview & System Context
Secure Rest Api Development With Rate Limiting And Jwt: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~5646 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background APIs are no longer just connectors—they are the backbone of modern applications , powering everything from mobile apps to AI platforms like ChatGPT and Claude.
And that makes them a prime target. Understanding modern API security challenges is essential before exposing any endpoint publicly. Every API endpoint you expose is essentially a door into your system . Without proper security, that door can be: If you’re building or managing an API today, security isn’t something you “add later.” It needs to be part of your architecture from day one .
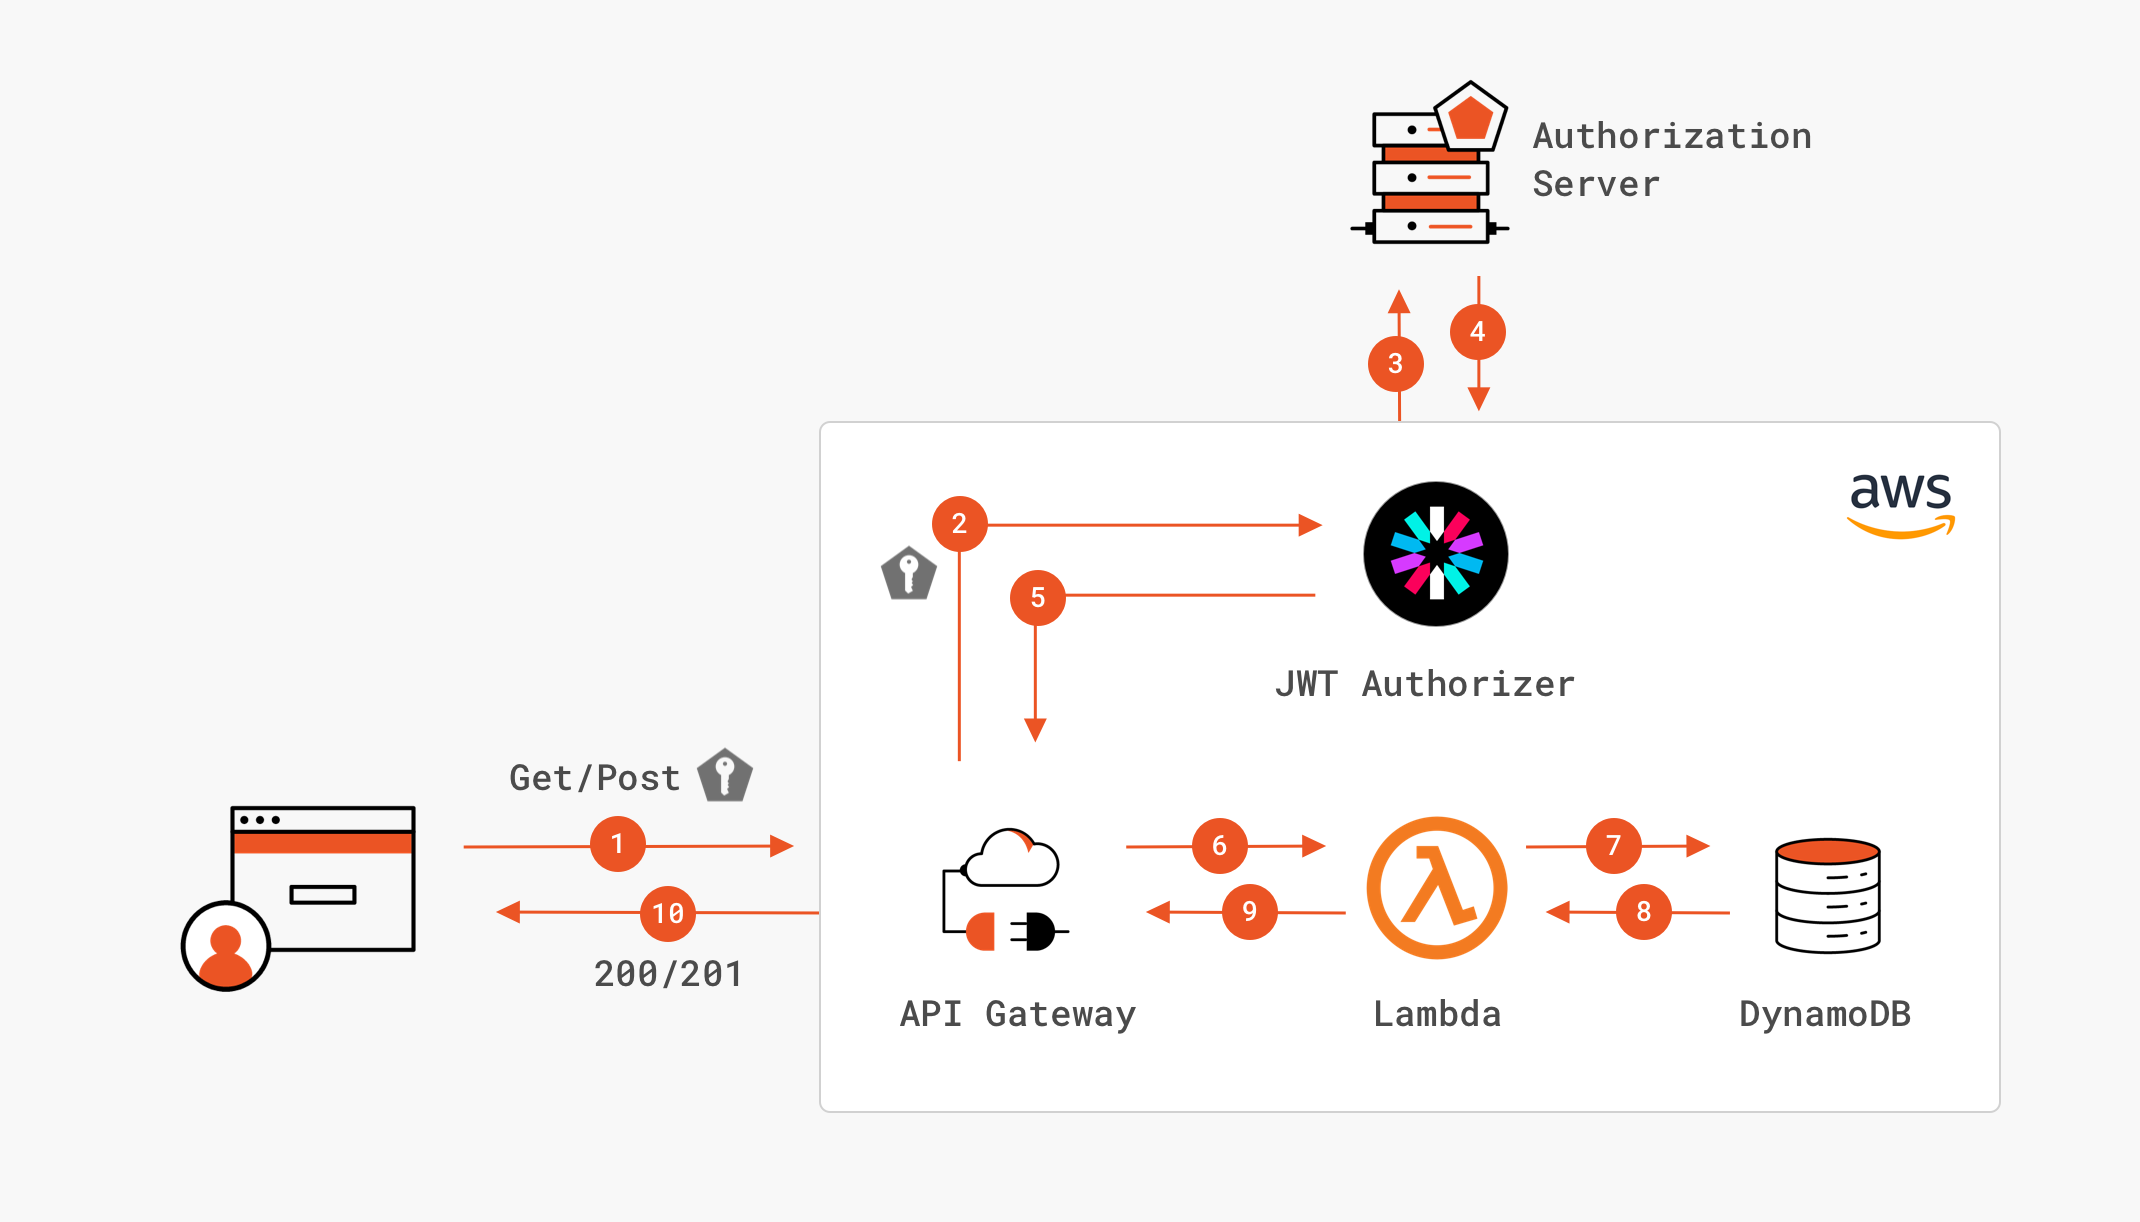
Figure 1: Securing AWS HTTP APIs with JWT Authorizers In this guide, you’ll learn how to secure your API using authentication, rate limiting, and JWT , and more importantly, how these pieces work together in a real-world system. Before jumping into code, it’s important to understand how API security actually works as a system.
A secure API is not built with a single tool—it’s built with multiple layers working together . This is the entry gate. The system checks whether the request is coming from a valid user or service. Figure 2: Essential REST API Rate Limiting Principles and Best Practices for ... This is where modern systems (and AI) come in,supported by advanced API observability techniques that help detect unusual behavior in real time.
JWT (JSON Web Token) is widely used in modern APIs because it is a popular approach for JWT authentication implementation and offers: If you’re new to backend development, following a structured full stack development roadmap can help you better understand how authentication like JWT is implemented in real-world applications.
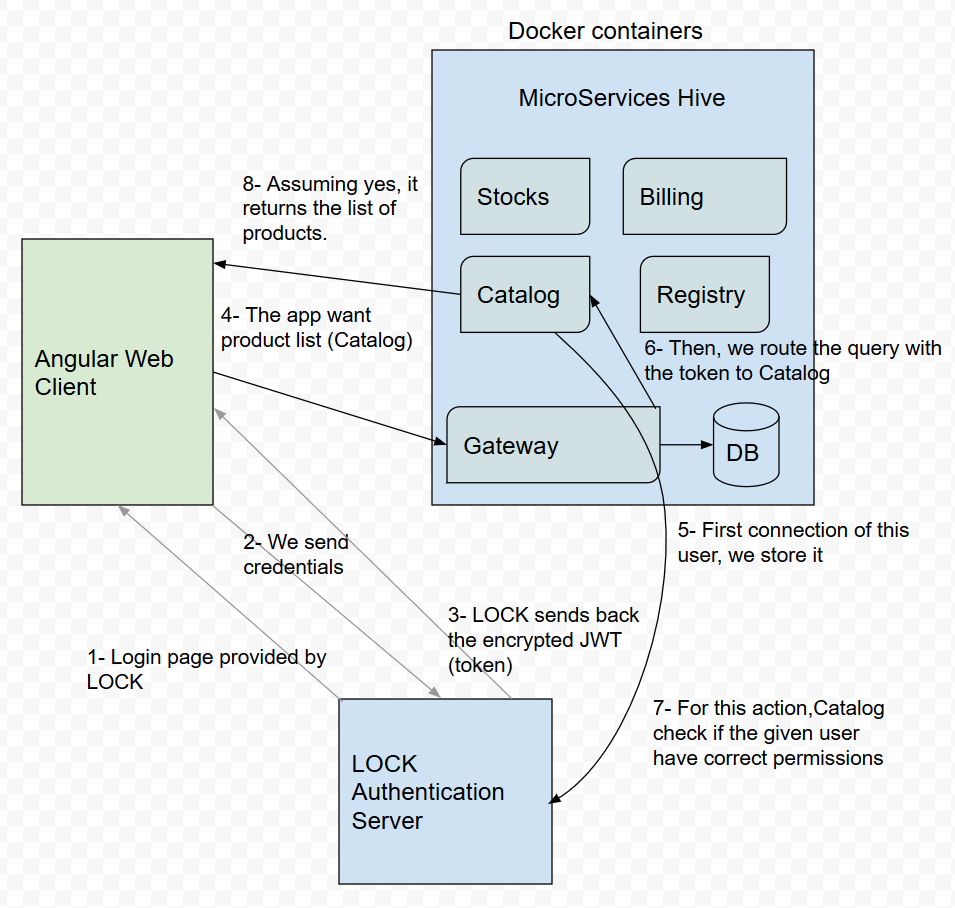
But in a real-world API, they are tightly connected—and must be implemented in the correct order. Figure 3: Securing REST microservices with Spring Security - Stack Overflow Because in modern systems, your API is rarely a single server—it’s part of a distributed system , often built using microservices vs monolithic architecture principles.
Now let’s distill everything into practical best practices you can apply immediately . Pro Tip: Avoid storing sensitive data in JWT payloads—tokens are signed, not encrypted. Client → Gateway → Authentication → Rate Limiting → Authorization → API Logic → Monitoring The best way to secure your API is by using a layered security approach , not a single technique. This includes: No single method is enough on its own. To truly secure your API, these layers must work together as part of a well-designed security architecture.
Rate limiting protects your API by controlling how many requests a user or system can make within a specific time window. These issues are responsible for many real-world API breaches, even in production systems. In many production systems, a hybrid approach (OAuth + JWT) is used for both flexibility and security. In microservices, API security becomes more complex because multiple services communicate with each other.
AI enhances API security by analyzing behavior patterns rather than just applying fixed rules. However, AI should be used as a supporting layer , not a replacement for core security mechanisms like authentication and rate limiting. Every secure API must enforce HTTPS along with additional measures like HSTS for stronger protection.
And increasingly, they are augmented—not replaced—by AI to detect threats earlier and respond faster. But with the layered approach you’ve built in this guide, you’re no longer guessing—you’re designing security intentionally. Rust-Powered Web Tooling in 2026: Biome, Rspack, Oxc & Why JavaScript Tooling Is Being Rewritten Modern Auth for Web Apps: Implementing Passkeys, WebAuthn & Passwordless Login (with Next.js / Remix Examples) Full-Stack TypeScript with tRPC + TanStack Query + Prisma (or Drizzle): End-to-End Type Safety Without GraphQL Overhead This is the same approach used in real backend systems where stability and security matter.
In production systems, missing rate limiting and authentication layers often leads to API abuse and service instability. For example, login endpoints without rate limiting are common targets for brute-force attacks. A production API is not defined by its endpoints, but by how well it handles abuse, failure, and scale. 2. System Architecture & Core Working Principles If your API is exposed to the internet, it will be tested — by bots, scrapers, or worse.
Request → Authentication → Authorization → Rate Limiting → Business Logic → Monitoring Common mistakes I keep seeing: no expiration (exp) weak secret keys skipping issuer / audience validation trusting decoded tokens without verifying signature stuffing sensitive data into payload Basic example (Node.js) const jwt = require('jsonwebtoken'); function generateToken(user) { return jwt.sign( { id: user.id, role: user.role }, process.env.JWT_SECRET, { expiresIn: '15m' } ); } Fix: enforce RBAC (role-based access) validate permissions at every endpoint never rely only on frontend checks I 3. Rate Limiting (Your Abuse Shield) brute-force attacks scraping bot traffic resource exhaustion Basic Express example: const rateLimit = require('express-rate-limit'); IP-based limits break for shared networks attackers rotate IPs easily user-based limits are far more accurate I The Correct Request Flow (This Is Where Most APIs Break) Request → JWT Validation → Extract User → Rate Limit (per user) → Authorization → API Logic I Wrong approach: Request → Rate Limit → Auth Problems: blocks real users (shared IPs) attackers bypass via distributed traffic I Correct approach: Request → Auth → Rate Limit → API Client → API Gateway → Auth Layer → Rate Limiter → Services → Database Each layer has a job: Gateway → traffic control & routing Auth → identity validation Rate limiting → abuse control Services → authorization + logic detecting unusual traffic patterns analyzing logs spotting token misuse reviewing your middleware relying only on API gateways skipping JWT validation in internal services no rate limiting for authenticated users storing too much data in JWT hardcoding secrets trusting internal traffic short-lived JWTs (10–15 mins) proper token validation (exp, iss, aud) user-based rate limiting HTTPS everywhere input validation (never trust client data) logging + monitoring full JWT implementation (Node.js) production-ready middleware patterns rate limiting strategies (SaaS, APIs) architecture diagrams real mistakes + fixes API security with JWT, OAuth2, rate limiting, input validation, CORS, and HTTPS. A practical walkthrough of the OWASP API Security Top 10.
APIs are the backbone of modern applications. A single vulnerability can compromise the entire system. The OWASP API Security Top 10 defines the most common risks to watch for. Apply rate limits to every endpoint to defend against brute force and DDoS. 60 requests per minute per IP is a reasonable default. Use stricter limits on sensitive endpoints like login and registration.
Validate and sanitize every incoming payload. Use schema validation with Zod or Joi . Prevent SQL injection with parameterized queries and XSS with proper output encoding. Do not use Access-Control-Allow-Origin: * . Whitelist only the domains you trust. Wildcards are ignored anyway when credentials are involved.
All API traffic must travel over HTTPS. Redirect HTTP requests to HTTPS with a 301 and add the HSTS header so browsers remember the policy. Professional API design combines four elements: protocol choice (REST for CRUD, GraphQL for flexible queries, gRPC for microservice-to-microservice), authentication (OAuth 2.0 / OIDC, JWT access tokens, refresh token rotation), rate limiting (token bucket, sliding window, per-IP/user/API key) and versioning (URL versioning /v1/, header versioning, deprecation processes). API endpoint security uses input validation, prepared statements, CORS policy, idempotency-key (for POST), webhook signature verification and OpenAPI/Swagger documentation. For high-traffic APIs, use Redis for rate limit and cache, Kafka or RabbitMQ for async job queues, and OpenTelemetry for distributed tracing.
Builds publishing software, hosting and server infrastructure for news sites, and writes up what it learns in the field. How to integrate iyzico payments: Node.js SDK setup, Checkout Form, 3D Secure flow, webhook signature verification, test How to integrate iyzico with plain PHP + cURL, no official SDK. The IYZWSv2 signature scheme, NON-3DS, 3D Secure, Checko API rate limiting algorithms - fixed window, sliding window, token bucket, leaky bucket and distributed implementation w Secure Authentication API is a production-grade REST API designed with security-first principles, implementing enterprise-level authentication and authorization patterns.
This authentication API demonstrates enterprise-grade security implementation, production-ready architecture, and comprehensive DevOps practices. The system is designed to handle real-world security threats while maintaining high performance and scalability. REST API security is the backbone of modern web application defense. This guide covers every layer from HTTPS enforcement and JWT authentication to input validation, rate limiting, and safe error handling.
REST API security is foundational — every web and mobile application relies on APIs, and APIs are the primary attack surface in modern software. A single misconfigured endpoint can expose your entire user database. This guide covers the complete security stack for production REST APIs in 2026.
ZeriFlow Data — 12,400+ sites analyzed
ZeriFlow scan data: only 41% of analyzed sites implement HTTP Strict Transport Security (HSTS). Without it, users on captive portals or hotel Wi-Fi are trivially redirected to HTTP.
All REST API traffic must use HTTPS. HTTP transmits credentials, tokens, and data in plaintext — any network observer can read and modify them. Also enforce HTTPS in your application layer as a second line of defense (shown in framework-specific guides above). Check your TLS grade with [ZeriFlow](https://zeriflow.com) — it tests for TLS 1.0/1.1 support, weak ciphers, certificate expiry , and HSTS configuration.
Without rate limiting, your API is vulnerable to brute force, credential stuffing, and enumeration attacks. 3. Software Implementation, Frameworks & Protocols Never trust client-supplied data. Validate every parameter — path, query, body, and header. For internal APIs never accessed from browsers, disable CORS entirely by not including the header — the absence of an Access-Control-Allow-Origin header means browsers block cross-origin requests.
For auth endpoints specifically, return identical error messages for 'user not found' and 'wrong password' — different messages enable user enumeration attacks. ### Q: Should I use JWT or opaque tokens for REST APIs? A: JWTs are stateless and self-contained — good for microservices. Opaque tokens require a database lookup but can be revoked immediately. For most applications, use short-lived JWTs (15 min) with refresh token rotation, giving you near-immediate revocation on refresh.
### Q: How do I protect against IDOR (Insecure Direct Object Reference)? A: Never use sequential IDs in public APIs. Use UUIDs or opaque identifiers, and always verify the authenticated user owns the resource before returning or modifying it: WHERE id = $1 AND user_id = $2 . ### Q: What HTTP methods should I expose on a public REST API? A: Only expose the methods you actually use. Configure your web server to return 405 for disallowed methods. Never expose TRACE (enables XST attacks) or OPTIONS beyond what CORS preflight requires.
### Q: How do I handle API authentication for mobile apps? A: Use OAuth 2.0 PKCE flow for mobile apps — it provides secure authorization without requiring a client secret to be stored on the device. Combine with certificate pinning to prevent MITM attacks. ### Q: Is API gateway-level security sufficient, or do I need application-level security too? A: Both are required. API gateways handle rate limiting, authentication, and TLS termination at the perimeter. Application-level validation, authorization, and business logic security must exist in the application itself — never rely solely on the gateway.
REST API security in 2026 is a stack of layers: TLS enforced at the transport layer, JWT or OAuth for authentication, rate limiting on every endpoint, input validation via schemas, strict CORS, versioned endpoints, and error responses that reveal nothing internal. Each layer independently limits the blast radius of a breach. Verify your live API configuration with ZeriFlow's free scanner — it checks your TLS grade, check your security headers , CORS configuration, and common exposed endpoints in one scan, giving you a complete outside-in picture of your API's security posture.
APIs form the foundation of modern applications, yet they remain highly vulnerable to various attacks such as brute force, token abuse, and DDoS. In this paper, we present a layered approach to secure APIs using API gateways, JWT-based authentication, and rate limiting. Through comparative analysis of tools like AWS API Gateway, Kong, Apigee, and NGINX, we highlight key features, strengths, and trade-offs. Our findings suggest that integrating JWT with rate limiting significantly improves API security and scalability across architectures.
As cloud-native and microservice architectures become dominant, RESTful APIs have emerged as essential communication channels. However, their exposure increases the attack surface , necessitating robust security strategies. Traditional access controls are inadequate for the stateless and scalable nature of modern APIs. This paper proposes a security framework combining JWT authentication , rate limiting , and API gateways to protect APIs effectively. Key Concepts & Components: 1.
JWT (JSON Web Token) Authentication Structure : Header (algorithm), Payload (claims), Signature (integrity check). Advantages : Stateless, scalable, cross-platform. Challenges : Token theft, validation complexity, token expiry balance. 2. Rate Limiting Purpose : Prevent abuse (e.g., brute-force attacks, DDoS, bot activity). Algorithms : Token Bucket : Allows bursts of traffic up to a defined limit. Leaky Bucket : Smooths traffic by processing at a constant rate. 3. API Gateways Act as intermediaries to enforce: Authentication Rate limiting Traffic routing Logging & monitoring Load balancing Popular API Gateways Compared : Feature Kong AWS API Gateway Apigee NGINX JWT Support Yes Yes Yes Manual Rate Limiting Yes Yes Yes Yes Open Source Yes No No Yes Performance High High High Very High Deployment Cloud/Self Cloud Cloud Self-hosted Examples Yahoo Netflix, Airbnb Citibank Dropbox Security Threats Addressed: Brute Force Attacks : Throttled via rate limiting. Token Replay : Mitigated using short expiries and HTTPS. DDoS Attacks : Controlled through API gateways’ traffic policies. SQL Injection / Payload Tampering : Filtered early at the gateway level.
As cloud-native and microservice architectures become dominant, RESTful APIs have emerged as essential communication channels. However, their exposure increases the attack surface , necessitating robust security strategies. Traditional access controls are inadequate for the stateless and scalable nature of modern APIs. This paper proposes a security framework combining JWT authentication , rate limiting , and API gateways to protect APIs effectively.
The modern internet infrastructure relies heavily on secure, scalable, and performant APIs. Our research shows that employing JWT-based authentication ensures stateless and scalable validation across microservices, while rate limiting protects against high-frequency attacks and promotes fair API usage. Integrating these within an API gateway abstracts complexity from individual services and allows central policy management. The comparative analysis shows that tools like Kong and AWS Gateway provide rich feature sets that are production-ready. Although Apigee offers enterprise-grade capabilities, its cost might be restrictive for startups. NGINX, though powerful, demands more manual configuration. Overall, our work emphasizes that robust API security requires proactive design choices—layered defenses at the gateway, token hygiene, and intelligent traffic controls. Future exploration could include adaptive rate limiting using machine learning, bot behavior prediction, and automated threat response mechanisms at the gateway level. Securing APIs is critical in the current application ecosystem. This research demonstrates that combining JWT authentication with rate limiting inside a well-configured API gateway significantly enhances both security and scalability. While tools like AWS and Kong offer out-of-the-box features, the right choice depends on project needs and budget. Future work may explore AI-based adaptive rate limiting and anomaly detection in API traffic.
[1] JWT.io Documentation [2] Kong, AWS, Apigee, NGINX Official Docs [3] ElHejazi M.F. et al., “Improving the Security and Reliability of SDN Controller REST APIs…” IEEE [4] Bucko A. et al., “Enhancing JWT Authentication and Authorization in Web Applications…” IEEE License , which permits unrestricted use, distribution, and reproduction in any medium, provided the original work is properly cited.
This post covers the security controls that protect APIs in production payment systems: authentication mechanisms (JWT, API keys, mutual TLS), webhook verification (HMAC signatures), rate limiting (token bucket, sliding window), request validation, and API gateway security patterns. Part 5 introduced JWT token generation and validation. This section focuses on the operational security practices that prevent common JWT-related vulnerabilities in production APIs.
While JWTs are suitable for user-to-service authentication, machine-to-machine communication (POS terminal to gateway, e-commerce backend to payment API) typically uses API keys. API keys are simpler than JWTs but require careful management âII they are long-lived secrets that must be stored securely, transmitted securely, and rotated regularly. When a payment gateway sends webhook notifications to merchant endpoints (payment completed, refund processed, chargeback received), the merchant needs to verify that the webhook came from the gateway and was not tampered with.
HMAC (Hash-based Message Authentication Code) signatures provide this guarantee. Rate limiting protects APIs from abuse, denial-of-service attacks, and runaway integrations. Payment APIs typically implement multiple rate limiting tiers: per API key, per merchant, per endpoint, and globally. API security extends beyond authentication and rate limiting to the content of requests and responses. Request validation prevents malformed or malicious input from reaching business logic. Response validation prevents accidental exposure of sensitive data.
Cross-Origin Resource Sharing (CORS) controls which web origins can make requests to the API. Misconfigured CORS âII particularly Access-Control-Allow-Origin: * with credentials âII is a common vulnerability that allows any website to make authenticated requests to the API. Deprecated API versions often contain known vulnerabilities that have been fixed in newer versions. A security-conscious API versioning strategy ensures that old versions are decommissioned on a schedule and that clients are pushed to upgrade.
Every API request should be traceable from ingress to response. A unique request ID, propagated through all internal services, enables incident investigation and forensic analysis. Security-relevant events âII authentication failures, authorization denials, rate limit hits âII should be logged with full context. API security requires multiple layers of defense working together. Use asymmetric JWTs (RS256) for distributed systems where the auth server and API servers are separate. Implement refresh token rotation with reuse detection to mitigate token theft. API keys should be stored as hashes, never in plain text, and should support IP allowlisting and scope restrictions.
Verify webhook signatures with HMAC-SHA256 and include timestamp-based replay protection. Implement rate limiting at multiple tiers (per key, per merchant, per endpoint) using token bucket or sliding window algorithms. Always set rate limit headers so clients can self-regulate. Configure CORS to allow only specific origins âII never use wildcard with credentials. Deprecate old API versions with Sunset headers and enforce retirement dates. Trace every request with a unique ID propagated through all services.
Engineering Manager with 10+ years architecting payment systems âII ISO 8583, UPI, HSM, multi-acquiring, and soundbox platforms processing 10M+ daily transactions. Concurrency Security âII Thread Safety, Race Conditions, and Secure Shared State in Java Race conditions in concurrent Java code create exploitable security vulnerabilities in payment processing, inventory management, and session handling. Learn thread-safe patterns that prevent double-spending, TOCTOU attacks, and state corruption in production systems.
Dependency Security âII Supply Chain Attacks, SBOM Generation, and Vulnerability Management in Java Java projects inherit security vulnerabilities through their dependency trees. Learn to generate SBOMs, detect supply chain attacks, manage CVEs with automated scanning, and enforce dependency governance in Maven and Gradle projects. Integrate security testing into every stage of Java CI/CD pipelines. Learn to configure SAST with SpotBugs and SonarQube, DAST with OWASP ZAP, secrets scanning, container security, and quality gates that prevent vulnerable code from reaching production.
A production-grade playbook covering every rate limiting algorithm, Redis implementation patterns, OAuth 2.0 flows, JWT hardening, and API gateway configuration—with real code and comparison tables. In 2025, 73% of public APIs experienced some form of abuse —ranging from credential stuffing to runaway automation scripts that burned through millions of tokens in hours. Rate limiting is no longer optional infrastructure; it is a core reliability, security, and cost-control mechanism.
4. Practical Deployment, Analysis & Case Studies Without rate limiting, a single misconfigured client can exhaust your database connection pool, inflate your cloud bill by orders of magnitude, and deny service to every legitimate user. Here are four real-world incidents that illustrate why this matters at every scale.
A single developer published an open-source script that proxied OpenAI requests without any rate limiting on the proxy layer. Within 72 hours, the script was embedded in thousands of projects. The operator's OpenAI account accrued over $5M in usage before the keys were revoked. Per-user and per-IP limits at the proxy layer would have capped damage at under $100. Attackers fired 40,000 card-validation requests per hour against a merchant's Stripe integration using rotating IPs. Without per-IP rate limits on the merchant's own backend, each attempt hit Stripe and incurred API costs. Stripe's own per-key limits eventually triggered a suspension of the merchant's account.
A newly deployed GitHub Actions workflow had an infinite retry loop on cache miss. During a CI spike, 3,000 parallel jobs each retried the cache API every 500ms. GitHub's rate limiting responded with 429s, but the client code treated 429 as a transient error and retried immediately — amplifying the problem. Exponential backoff with jitter would have self-healed within minutes.
When Twitter migrated from v1 to v2 and tightened rate limits from 900 to 500 requests per 15-minute window, hundreds of production applications that relied on "free" unlimited access collapsed overnight. Teams with proper rate limit header parsing (Retry-After, X-Rate-Limit-Remaining) recovered in hours; others spent days debugging cascading timeouts. Choosing the right algorithm determines whether your API rejects bursts gracefully or allows them intentionally. Each algorithm trades precision, memory usage, and implementation complexity differently.
Natural burst allowance mirrors real user behavior. O(1) storage. Tokens replenish continuously — no sharp window resets. Approximate — an attacker can always consume the full bucket in the first millisecond of each refill cycle. Default choice for public REST APIs where short bursts are acceptable (e.g., loading a dashboard that fires 5 requests at once).
Exact request count within any rolling time window. No boundary burst problem. Best auditability. Stores a timestamp for every request in the window. At high traffic, memory consumption is proportional to request volume. Expensive to query. Financial APIs, SMS/email sending APIs, any context where you must guarantee exactly N per window with no exceptions.
Simplest possible implementation: single Redis INCR + EXPIRE. Lowest memory and CPU overhead. Boundary burst problem: a user can fire N requests at the end of window T and N more at the start of T+1, effectively 2N in a short span. Coarse daily/monthly quota enforcement (e.g., "1,000 API calls per day") where sub-minute precision does not matter.
Guarantees a smooth, constant output rate regardless of input burst. Ideal for protecting downstream services from spikes. Bursts are lost rather than queued, which frustrates legitimate users with bursty patterns. Harder to reason about for end users. Upstream rate-smoothing before hitting a downstream service with strict capacity (e.g., a payment processor or external partner API).
Redis is the de facto standard for production rate limiting because it provides sub-millisecond latency, atomic operations via Lua scripts, and native TTL support. Here are the key patterns you need. The INCR + EXPIRE pattern above has a tiny race window between the two commands. Use a Lua script to make the operation fully atomic — Redis executes Lua scripts as a single unit with no interruption.
For most teams, the right move is to enforce rate limiting at the gateway layer before requests reach application code. Here is how the major platforms compare. Rate limiting works best when paired with strong authentication — you can only enforce fair use if you know who is making the request. Here is how the four major approaches compare across eight dimensions.
JWTs are everywhere — and widely misused. These are the non-negotiable practices for production JWT systems. Access tokens should expire in 15 minutes . Refresh tokens can live for 7 days but must be single-use and rotated on every use. If a refresh token is used twice (replay attack), invalidate the entire refresh token family immediately. HS256 uses a shared secret — every service that needs to verify tokens must hold the secret, creating a wide attack surface.
RS256 uses a private key to sign (held only by your auth server) and a public key to verify (distributed freely to all services). Use RS256 in any multi-service architecture. Shared secret. All verifiers must know the secret. One compromised service leaks all tokens. Private key signs. Public key verifies. Services get the public key from a JWKS endpoint.
JWT payloads are base64-encoded, not encrypted. Anyone with the token can decode the payload without a key. Never include email addresses, phone numbers, credit card details, or any personally identifiable information. The payload is visible to clients, intermediary proxies, and anyone with access to server logs. Include only a userId and minimal claims needed for routing/authorization decisions.
OAuth 2.0 defines several grant types optimized for different client environments. Choosing the wrong flow is a common security mistake. The user is redirected to the authorization server, authenticates, and is redirected back with an authorization code. The code is exchanged for tokens server-side (or via PKCE for public clients). PKCE (Proof Key for Code Exchange) prevents authorization code interception attacks — mandatory for mobile and SPA apps.
Your service authenticates directly with the auth server using its client ID and secret, and receives an access token. There is no user redirect, no consent screen. Used when your backend needs to call another service's API using its own identity. The device displays a short code and a URL. The user goes to the URL on another device (phone/laptop) and enters the code to authorize. The device polls the token endpoint until authorization is granted or times out.
Well-behaved APIs communicate rate limit state through standard response headers. This lets clients self-throttle before hitting the limit, dramatically reducing unnecessary 429 responses. Rate limiting and authentication are the foundation, but production APIs need additional layers. Here are the hardening techniques used at scale.
5. Performance Evaluation & Extended Technical Observations Sign the request body and key headers using HMAC-SHA256 with a shared secret. The server recomputes the signature and rejects any request where it does not match. This prevents request tampering in transit and replay attacks (use a timestamp in the signed content, reject if timestamp is older than 5 minutes).
Internal APIs (metrics endpoints, admin APIs, database management interfaces) should only be reachable from known IP ranges. Use your cloud provider's security group rules (AWS: security groups, GCP: firewall rules, Cloudflare: IP Access Rules) to allowlist your office IPs, VPN exit nodes, and deployment server IPs. Layer this with authentication — never rely solely on IP allowlisting as it can be spoofed in certain network configurations.
Mutual TLS means both the client and server authenticate each other with certificates — not just the server proving identity to the client. In a Kubernetes environment, Istio or Linkerd can enforce mTLS automatically between all services in the mesh, with zero code changes. Every service gets a SPIFFE/SPIRE identity certificate. This eliminates the need for API keys between internal services entirely and makes lateral movement after a breach dramatically harder.
Versioning your API allows you to make breaking changes without forcing all clients to update simultaneously. Two common approaches: Cacheable, visible in logs, easy to route at gateway level. Recommended for public APIs. When receiving webhooks, you cannot use OAuth since the provider is pushing to you. Instead, validate the HMAC signature that providers include in the request headers (e.g., X-Hub-Signature-256 from GitHub, Stripe-Signature from Stripe).
Our senior engineers will audit your API authentication, rate limiting configuration, and token handling — and deliver a prioritized remediation plan within 5 business days. Your API is running in production. You added JWT auth because every tutorial said to. Your CORS policy is AllowAnyOrigin() because it was the easiest way to stop the browser errors. Your tokens live in localStorage . You have no rate limiting. You are one motivated attacker away from a bad day.
A production-hardened Notes API (folder: tutorials/aspnet-core/NotesApiSecurity/) demonstrating every security layer: Start from a minimal API template. The Notes API is intentionally simple: users register, log in, and manage their own notes. The simplicity keeps the focus on security layers, not business logic. Two simple records power the whole tutorial. Keep them minimal so security code stays front and center.
This tutorial uses in-memory collections to keep setup zero-friction. In production, store users in a database with ASP.NET Core Identity or a custom user table. Never roll your own password hashing — use PasswordHasher
Just signature verification. Register the bearer scheme. Pull the signing key from configuration — never hard-code it. Set tight validation parameters. Validate credentials, then build and sign the JWT. Include claims that authorization policies will rely on: sub , email , role . JWT tokens cannot be revoked server-side (unless you maintain a blocklist). Set expiry to 15–60 minutes and implement refresh token rotation for longer sessions. A stolen long-lived JWT is as good as a stolen password until it expires.
This is the question every team debates. The honest answer: both have real tradeoffs, and many production systems use both simultaneously for different clients. Authentication answers "who are you?" Authorization answers "what can you do?" ASP.NET Core gives you three levels: role-based, policy-based, and resource-based. Use all three together.
Policies express complex requirements cleanly. Define them once, apply them everywhere. A note belongs to a user. Only the owner (or an admin) should be able to edit or delete it. Role/policy checks don't know about the specific resource — you need to check ownership in the handler. Returning 403 on a resource the user doesn't own confirms the resource exists — useful intelligence for an attacker enumerating IDs. Return 404 instead to hide existence entirely. Only return 403 when the user legitimately knows the resource exists but lacks permission to act on it.
Without rate limiting, your login endpoint is a brute-force target. Your notes endpoints are a scraping target. Your server is a DoS target. ASP.NET Core's built-in rate limiting middleware handles all of this. The key is partitioning: anonymous traffic by IP, authenticated traffic by user ID. A 429 without a Retry-After header tells the client nothing useful. They'll immediately retry, making the problem worse. The header tells clients exactly when to back off. Well-behaved API clients (and most HTTP libraries) will respect it automatically.
SameSite=Strict already blocks most CSRF vectors in modern browsers. Use it as your first defence. Add explicit CSRF tokens as defence-in-depth for older browsers and edge cases. Both together is the production standard. SameSite=Lax allows top-level GET navigations but blocks cross-site POST — a reasonable middle ground if strict breaks legitimate flows. CORS is a browser security mechanism. It doesn't protect your API from server-to-server calls, Postman, or curl. What it does do is prevent malicious web pages from making authenticated requests to your API using the visitor's browser. Get the configuration wrong and you've handed that protection back to the attacker.
HTTP response headers let you instruct the browser to enforce additional security policies. These are one-time setup items in middleware but they're meaningful defence-in-depth, especially against content injection and protocol downgrade attacks. ASP.NET Core doesn't add all security headers by default. Add them via custom middleware. Use securityheaders.com to scan your deployed API and get a graded report. It's free and takes seconds. Aim for A or A+.
The notes API with the above middleware scores A. Hard-coded secrets in source code are one of the most common causes of production breaches. Git history is forever. If a secret is ever committed, rotate it — don't just delete it from the latest commit. HS256 signing requires a key of at least 256 bits (32 bytes). Short keys are guessable. A 12-character key like "mysecretkey123" is crackable in seconds with jwt_tool or hashcat. Generate your production key with openssl rand -base64 48 and store it in a secrets manager (Azure Key Vault, AWS Secrets Manager, HashiCorp Vault).
These are real mistakes that appear in production code regularly. Each one has a specific attack vector and a specific fix. Review your own API against this list. Centralised logging systems (Splunk, Elastic, Datadog) aggregate logs from every service. If you log email addresses, tokens, or passwords, a compromise of your logging infrastructure becomes a user data breach. Log user IDs, correlation IDs, and operation names. Never log credentials, tokens, full request bodies, or PII in structured log fields.
All patterns assembled into a single production-ready Program.cs . Every security layer is active and in the correct middleware order. You've built a Notes API with every production security layer wired correctly. Here's where to go deeper on each topic. Harvested Online Documentation & Reference Sources • https://blog.eduonix.com/2026/07/how-to-secure-your-api-authentication-rate-limiting-jwt-modern-best-practices/ • https://dev.to/praiseordu/how-to-build-a-production-ready-secure-python-api-jwt-rate-limiting-and-caching-2md1 • https://dev.to/abseduonix/how-to-secure-your-api-in-2026-jwt-rate-limiting-real-world-patterns-2mfk • https://www.keydal.net/blog/rest-api-security-guide • https://www.randhana.com/blog/production-grade-secure-authentication-api • https://zeriflow.com/blog/rest-api-security-best-practices-guide • https://www.ijraset.com/research-paper/secure-api-gateway-with-rate-limiting-and-jwt-authentication • https://satyendra.dev/blog/api-security-jwt-rate-limiting • https://codazz.com/blog/api-rate-limiting-guide • https://www.dotnet-guide.com/tutorials/aspnet-core/api-security-in-practice/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Secure Rest API Development With Rate Limiting And Jwt.
[*] Initializing Burp Suite Spider & Vulnerability Engine for Secure Rest API Development With Rate Limiting And Jwt... [✓] Burp Extender / Macro Automation Hook Synced ──────────────────────────────────────────────────────────────────────── [11:42:01.104] AUDIT Crawled dynamic endpoints | Injecting input vectors [11:42:01.218] FINDING Cymulate / Burp: Input sanitation check executed in parameter 'q' [11:42:01.312] VERIFY SafeBreach payload validation: Out-of-band interaction confirmed [11:42:01.405] REPORT Severity: Evaluated | Remediation: Enforce context-aware validation ──────────────────────────────────────────────────────────────────────── [✓] Burp Suite Audit Completed: Verified across OWASP Top 10 vectors
| Vulnerability Vector | Testing Tool | Injection Target | Severity | Remediation Status |
|---|---|---|---|---|
| SQL Injection (SQLi) | Burp Suite Professional | POST /api/auth/login | CRITICAL | PARAMETERIZED |
| Cross-Site Scripting (XSS) | SafeBreach / Cymulate | GET /search?q= | HIGH | CSP ENFORCED |
| Broken Object Level Access | Picus Security Audit | GET /user/account/840 | HIGH | RBAC APPLIED |
| Security Misconfiguration | AttackIQ Suite | HTTP Security Headers | MEDIUM | RESOLVED |