Complete Technical Paper Content — Secure Single Sign On Implementation Using Oauth 2.0
Overview & System Context
Secure Single Sign On Implementation Using Oauth 2.0: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~7766 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Single sign-on (SSO) is an authentication scheme that allows a user to log in with a single ID to any of several related, yet independent, software systems. True single sign-on allows the user to log in once and access services without re-entering authentication factors. It should not be confused with same sign-on (Directory Server Authentication), often accomplished by using the Lightweight Directory Access Protocol (LDAP) and stored LDAP databases on (directory) servers. A simple version of single sign-on can be achieved over IP networks using cookies but only if the sites share a common DNS parent domain.
For clarity, a distinction is made between Directory Server Authentication (same-sign on) and single sign-on: Directory Server Authentication refers to systems requiring authentication for each application but using the same credentials from a directory server, whereas single sign-on refers to systems where a single authentication provides access to multiple applications by passing the authentication token seamlessly to configured applications. Conversely, single sign-off or single log-out (SLO) is the property whereby a single action of signing out terminates access to multiple software systems. As different applications and resources support different authentication mechanisms, single sign-on must internally store the credentials used for initial authentication and translate them to the credentials required for the different mechanisms. Other shared authentication schemes, such as OpenID and OpenID Connect, offer other services that may require users to make choices during a sign-on to a resource, but can be configured for single sign-on if those other services (such as user consent) are disabled. An increasing number of federated social logons, like Facebook Connect, do require the user to enter consent choices upon first registration with a new resource, and so are not always single sign-on in the strictest sense.
Mitigate risk for access to 3rd-party sites ("federated authentication") because user passwords are not stored or managed externally Reduce password fatigue from different username and password combinations Reduce time spent re-entering passwords for the same identity Reduce IT costs due to lower number of IT help desk calls about passwords SSO shares centralized authentication servers that all other applications and systems use for authentication purposes and combines this with techniques to ensure that users do not have to actively enter their credentials more than once.
When people talk about “OAuth2 SSO,” they usually mean a login system built with OpenID Connect , the identity layer on top of OAuth2. OAuth2 is an authorization framework. It lets an app request limited access to a user’s resources without asking for the user’s password. For example, an app can request permission to read a user’s calendar or profile data.
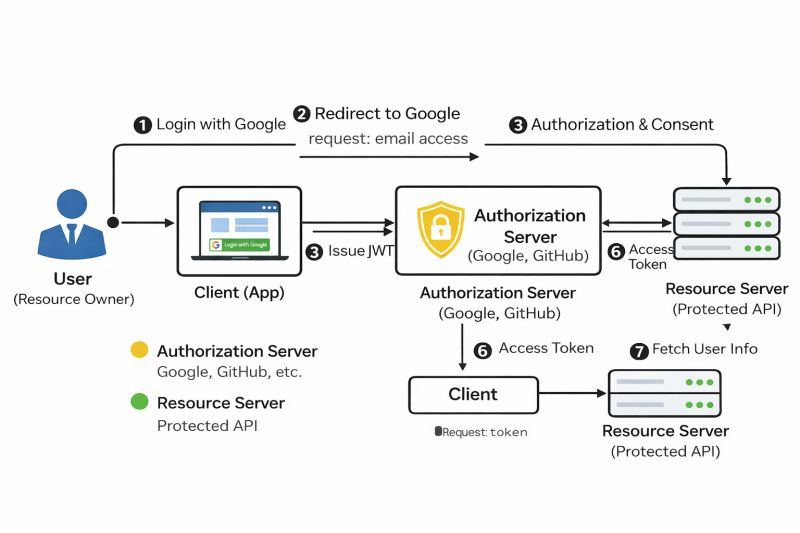
Figure 1: OAuth 2.0 Explained: Secure Login Framework | Narendra Reddy Bareddy ... OpenID Connect, or OIDC, adds authentication. It lets an app verify who the user is by receiving an ID token from a trusted identity provider such as Google, Microsoft Entra ID, Okta, Auth0, or another OIDC provider. That distinction matters. If you are building “Login with Google,” enterprise SSO, a customer portal, a SaaS dashboard, or an internal tool, you need to understand which part handles identity, which part handles API access, and how tokens should be used securely.
This guide explains how OAuth2 and OpenID Connect work together for SSO, which flows to use for modern web apps, how redirect URIs, scopes, ID tokens, access tokens, and PKCE fit together, and what to watch out for when adding secure login to your app. First, let’s get the two main players straight. While they are almost always used together for login systems, they have distinct jobs.
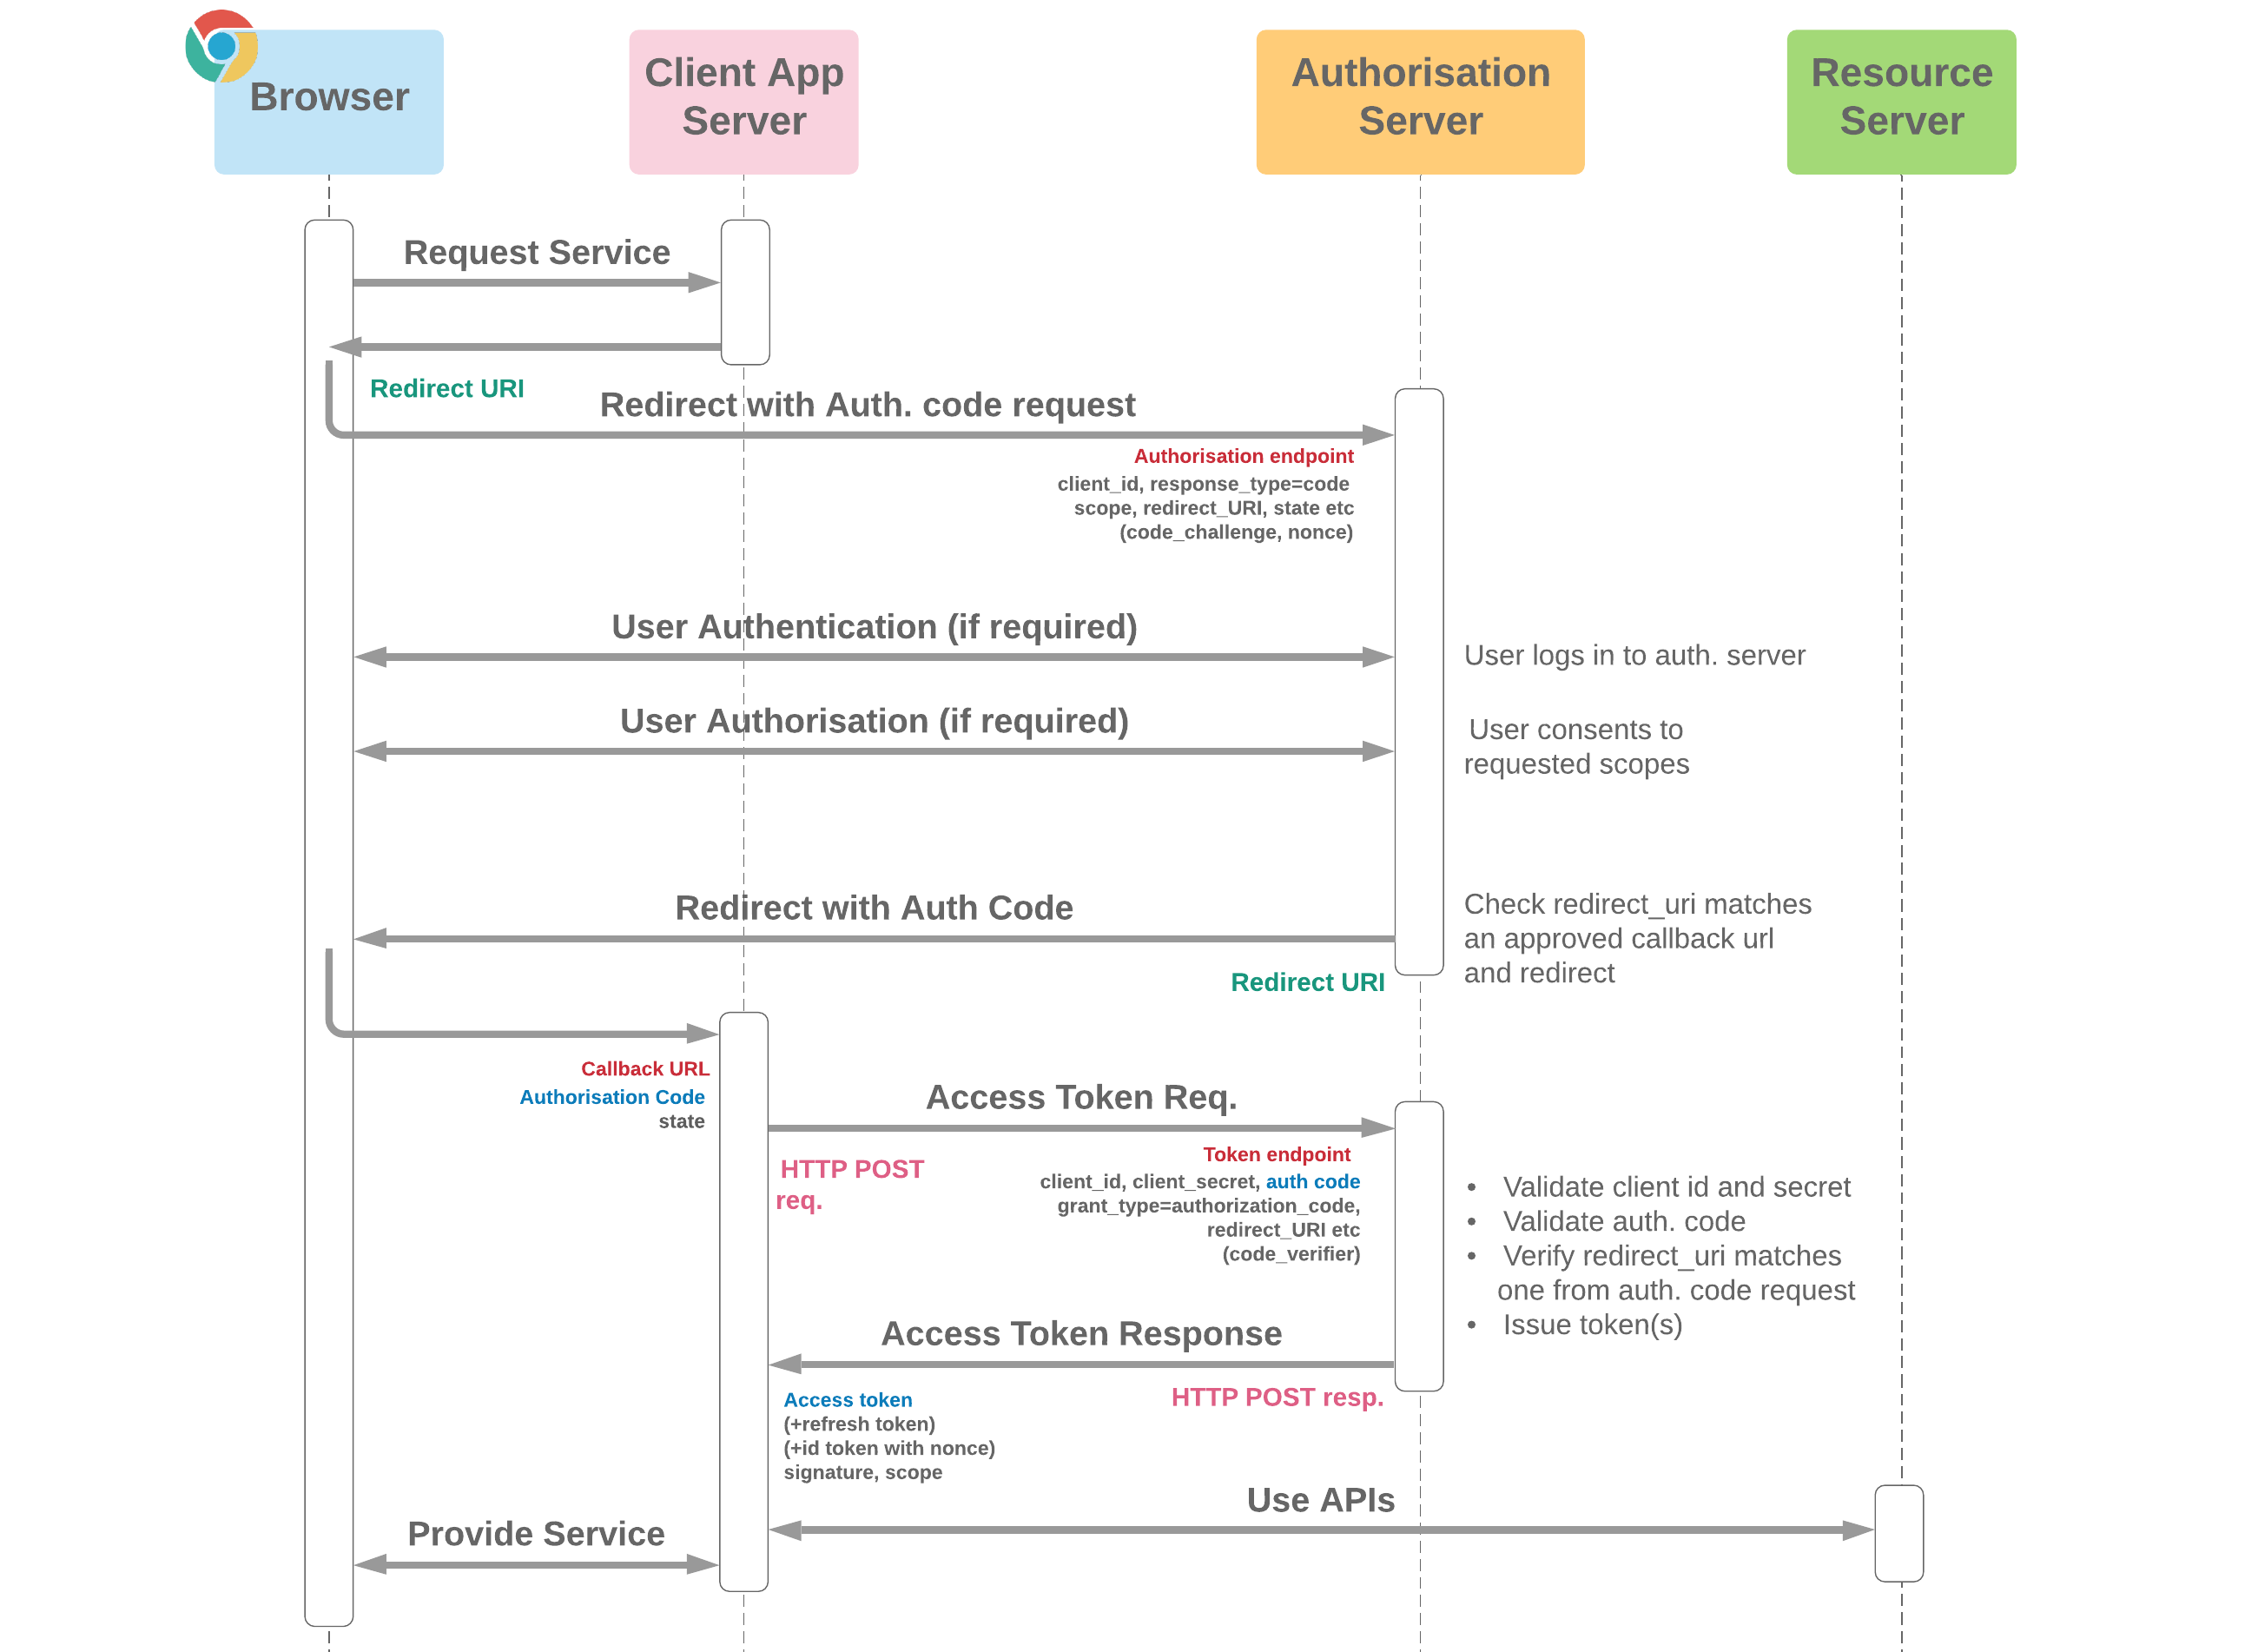
Figure 2: Single Sign-On implementation: Security Issues and Best Practices ... OAuth 2.0 is an open standard for authorization . Think of it as a delegation framework. It allows a user to grant a third party application limited access to their resources on another service, without sharing their password. For example, you can authorize a calendar app to access your Google Calendar. OAuth 2.0 grants access, but it doesn’t actually tell the app who you are .
OpenID Connect (OIDC) is the piece that makes single sign on using oauth2 possible. Introduced in 2014, OIDC is a thin identity layer built on top of OAuth 2.0. While OAuth 2.0 provides an access token , OIDC adds an ID token . This ID token contains verifiable information about the user, like their name and email, which confirms their identity. OIDC is the industry standard for authentication, backed by major companies like Google and Microsoft.
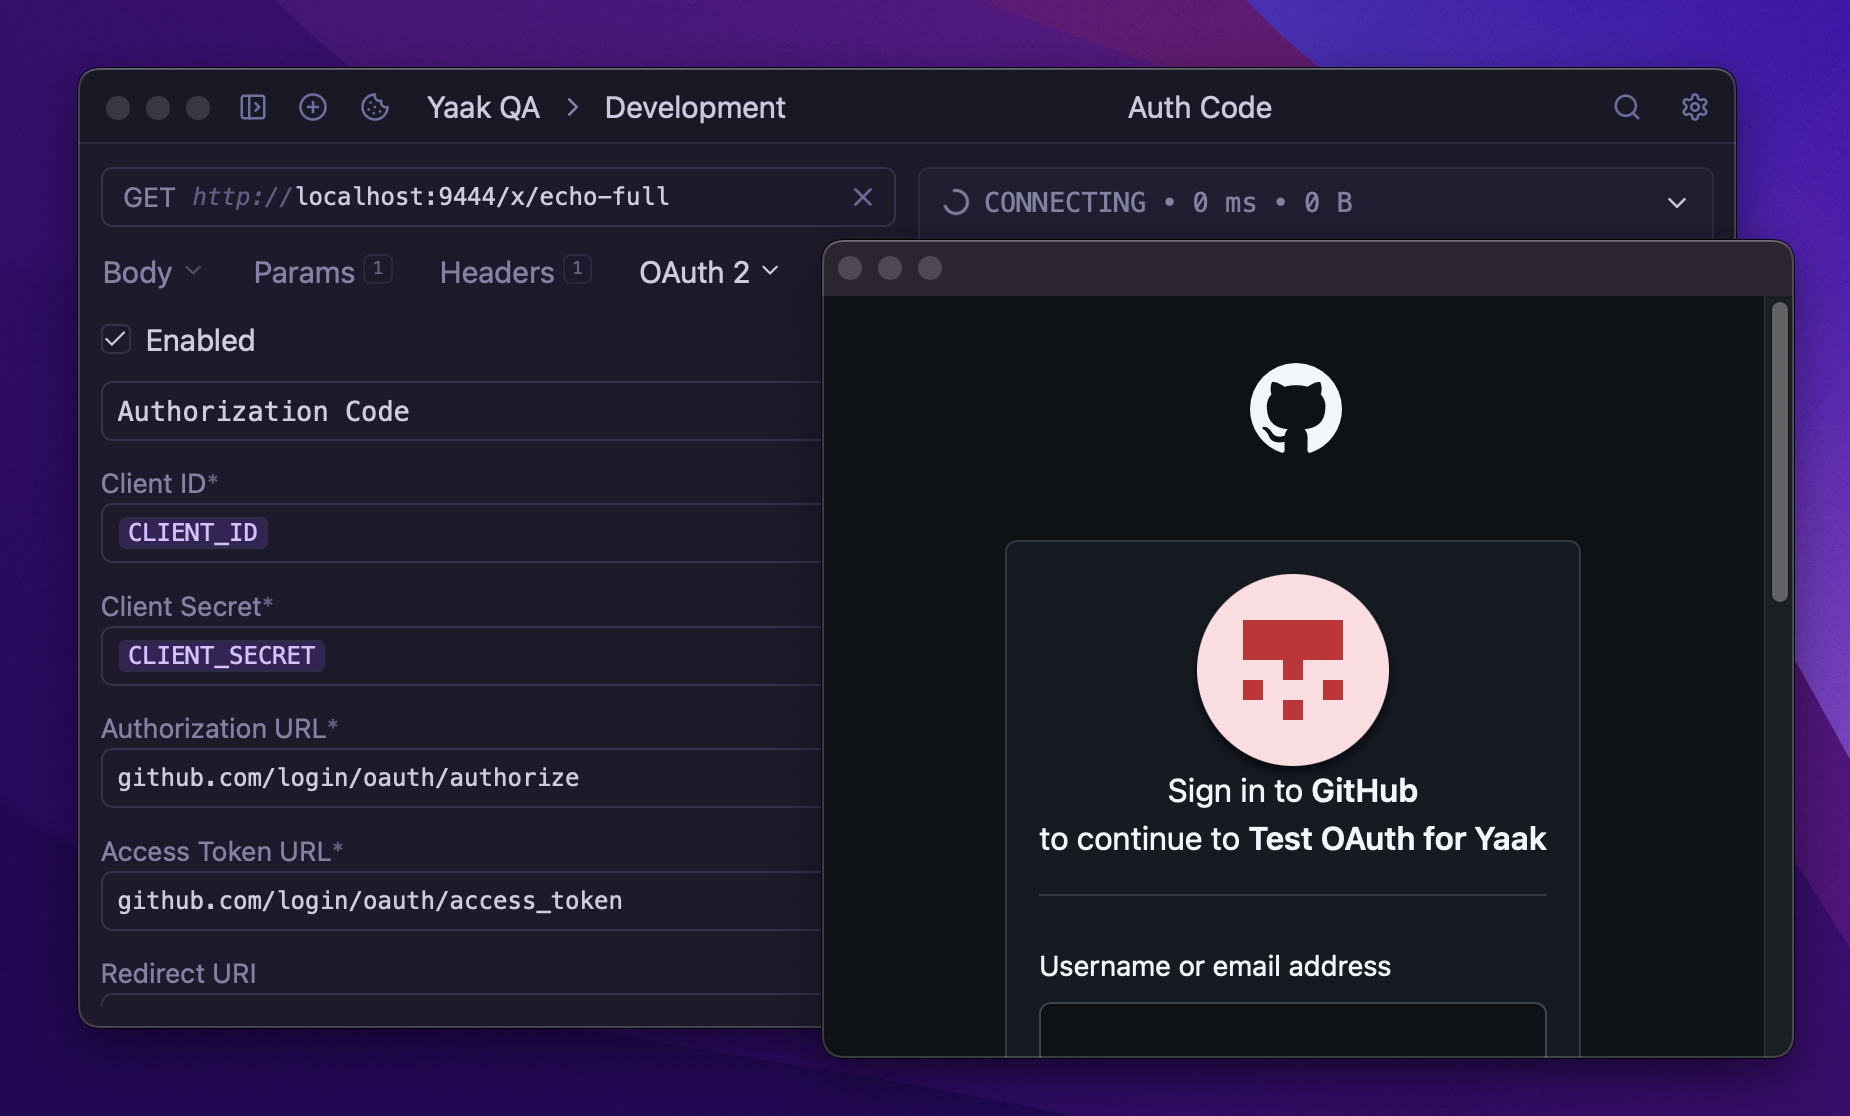
Figure 3: OAuth 2.0 | Yaak Docs Because OIDC is built on OAuth 2.0, you use them together. An application uses OIDC to log a user in (authentication) and then uses the resulting OAuth 2.0 access token to call APIs on the user’s behalf (authorization). This powerful combination provides both secure login and delegated access in a single, standardized flow.
Single Sign On (SSO) allows a user to log in once with a single set of credentials and gain access to multiple applications. OIDC is the perfect protocol for this. It works by using a central, trusted Identity Provider (like Google, Okta, Azure AD, or Auth0). When you click “Sign in with Google” on a new website, the OIDC flow begins. Google (the Identity Provider) authenticates you and then provides an ID token to the new website (the Relying Party).
This ID token is a cryptographically signed proof of your identity, which the website can trust. This process eliminates the need for separate passwords for every application, which dramatically improves user experience and security. For businesses, implementing single sign on using oauth2 allows employees to use one corporate login to access all their authorized tools seamlessly.
OAuth 2.0 isn’t one size fits all. It defines several process flows, called “grant types”, and choosing the right one depends entirely on your application’s architecture. Using the correct flow is a critical security decision. For example, building a SaaS product with a modern frontend requires a different approach than a traditional server rendered one.
Platforms like WeWeb’s no-code web app builder are designed for this, automatically using security best practices like the Authorization Code flow with PKCE for any external authentication you build. The Authorization Code Flow with PKCE is the gold standard for SPAs and mobile apps. PKCE (pronounced “pixie”) stands for Proof Key for Code Exchange.
It enhances the regular Authorization Code flow to make it secure for public clients that can’t hold a secret. The server checks if the verifier matches the challenge from step 2. This extra step proves that the application exchanging the code is the same one that started the process, preventing a common interception attack. Standardized in 2015 (RFC 7636), PKCE is now the recommended approach for any single sign on using oauth2 implementation on a public client.
For a single-page app, do not assume you can hide a client secret in frontend code. Use Authorization Code with PKCE. When the user clicks a login button, your app redirects them to the identity provider. The state parameter helps protect against CSRF-style attacks. The PKCE challenge helps prove that the app exchanging the code is the same app that started the flow.
The identity provider handles login. That may include password, social login, enterprise SSO, MFA, passkeys, or organization-specific policies. Your app should not collect the user’s provider password. The provider owns that step. After successful login, the provider redirects the user back to your registered redirect URI with a temporary authorization code.
Depending on the app type, this may happen through a backend or through a PKCE-based exchange. From here, the app usually needs to map the identity provider user to an app user, organization, role, or workspace. After login, protected pages and API endpoints should check the user’s authentication and permissions. Do not rely only on hiding UI elements. Sensitive data and actions must be protected at the backend or API level as well.
While the code flow with PKCE covers many use cases, there are other flows and configurations for specific needs. A client can request response_type=code id_token , which means it gets an ID token immediately in the redirect from the browser, plus an authorization code. The benefit is that the frontend can get the user’s identity information from the ID token right away for a faster UI update (like displaying “Welcome, Jane!”).
Meanwhile, the backend can use the code to securely retrieve the access token without exposing it to the browser. Frameworks like ASP.NET Core have built in support for OIDC, simplifying the setup of single sign on using oauth2 . You typically configure the OpenID Connect authentication middleware in your application’s startup file. You provide it with your ClientId , ClientSecret , and the provider’s Authority URL.
The middleware then handles the entire flow for you. When a user tries to access a protected page, it automatically redirects them to the provider to log in. Cloud Foundry, a popular Platform as a Service, has its own OAuth 2.0 provider called UAA (User Account and Authentication).
To use UAA for login, you register your app as a client and configure it with the UAA’s authorization and token endpoints. Since UAA supports OIDC, the integration is standard. This allows your application to leverage Cloud Foundry’s existing user base for a seamless SSO experience within that ecosystem. When you register your application with an identity provider, you must configure several settings correctly: 2. System Architecture & Core Working Principles Once a user is logged in, you need to protect your application’s routes and API endpoints.
In frameworks like ASP.NET Core, the [Authorize] attribute is a simple and declarative way to do this. Placing this attribute on an API controller or method tells the framework to check for a valid credential on every incoming request. For APIs, this usually means looking for a valid JWT bearer token in the Authorization header. If the token is missing or invalid, the framework automatically rejects the request, typically with a 401 Unauthorized status code.
This attribute is the gatekeeper that connects your single sign on using oauth2 system to your application’s actual resources. Implementing SSO is not just adding a Sign in with Google or Sign in with Microsoft button. This is where authentication becomes application logic. A SaaS dashboard, client portal, internal tool, or admin panel needs more than identity. It needs protected pages, permissions, user-specific data, and secure workflows.
OAuth2 tells you what an app can access. OIDC tells you who the user is. For SSO login, use OpenID Connect. Modern SPAs should generally use Authorization Code with PKCE instead of the old implicit flow. A browser-based app cannot keep a secret. Do not expose client secrets in JavaScript, public repositories, or frontend configuration.
Redirect URIs should be exact and pre-registered. Loose redirect matching can create security risks. Do not trust tokens blindly. Validate issuer, audience, expiration, signature, and expected claims. A logged-in user should not automatically have access to every page, record, or action. Authentication verifies identity. Authorization controls access.
Hiding buttons or pages in the UI is not enough. Sensitive data and actions must be protected at the backend or API layer. Only request the scopes your app actually needs. Overbroad consent screens reduce trust and increase risk. But your app still needs the user experience around that flow: login pages, redirects, protected routes, role-based screens, dashboards, portals, and API-connected workflows.
With WeWeb, builders can create the application layer around SSO without hand-coding every frontend screen and auth state from scratch. WeWeb also supports the parts of app design that come after authentication: conditional visibility, workflows, backend logic, data connections, and user-specific interfaces.
This matters because SSO is not the final product. It is the front door. The real product is what users can safely do after they enter. 1. What is the main difference between OAuth2 and OIDC for SSO? OAuth 2.0 is a framework for authorization (granting permissions), while OpenID Connect is a layer on top of it for authentication (verifying identity). You need OIDC’s identity layer to achieve true single sign on.
2. Is OAuth2 alone enough for single sign on? No. OAuth 2.0 by itself does not provide information about who the user is, only what the application is allowed to do on their behalf. OIDC provides the missing piece, the ID token, which contains the user’s identity claims. 3. Why is PKCE important for single sign on using OAuth2 in modern apps? PKCE is critical for public clients like single page web apps and mobile apps. Because these apps cannot securely store a client secret, PKCE adds a dynamic proof that prevents attackers from intercepting an authorization code and using it to get an access token.
4. Can I implement single sign on using OAuth2 without writing a lot of code? Yes. Modern frameworks have libraries and middleware that handle most of the complexity. Furthermore, visual development platforms like WeWeb offer pre-built integrations with OIDC providers, allowing you to add enterprise-grade SSO to your application through configuration instead of extensive coding.
5. What is an ID token? An ID token is a JSON Web Token (JWT) provided by an OpenID Connect provider. It contains claims about the authentication event, including the user’s unique ID, when they logged in, and who the issuer was. It’s the proof of a successful login. 6. What happens if my redirect URI is wrong? The authorization server will stop the process and display an error, often a redirect_uri_mismatch error. This is a security feature to ensure that authorization codes are only sent to pre approved, secure locations.
No. OAuth2 is an authorization framework. SSO login is usually implemented with OpenID Connect, which adds an identity layer on top of OAuth2. Yes, in most modern OAuth-based login systems. OpenID Connect provides the ID token that lets your app verify who the user is.
Use Authorization Code with PKCE. SPAs cannot safely store a client secret, so PKCE adds protection to the authorization code exchange. An ID token proves the user’s identity to the app. An access token authorizes API access. Do not use them interchangeably. Yes. WeWeb can be used to build logged-in apps with protected pages, user-specific interfaces, role-based experiences, and integrations with identity providers such as Auth0.
No. Frontend visibility is not a security boundary. Sensitive data and actions should also be protected through backend permissions, API authorization, or provider rules. If your team is wiring up single sign-on, a public API, or a mobile app, you will eventually reach the point where you need to implement OAuth 2.0 securely, and that is where most integrations quietly go wrong. OAuth is deceptively simple to get running and surprisingly easy to get wrong: an open redirect URI, a leaked authorization code, or a client secret embedded in a mobile app can turn a delegated-authorization protocol into an attacker's shortcut to account takeover. This guide walks through a practical, sequential setup for implementing OAuth 2.0 securely in a production application, covering the authorization code flow with PKCE, redirect URI validation, token issuance and storage, and scope enforcement. By the end, you will have a checklist you can apply to any client type, whether a single-page app, mobile app, or server-side service, along with verification steps to confirm your setup holds up against real-world attacks.
The single most common OAuth mistake happens before the first line of code is written: picking the wrong grant type. The implicit grant is deprecated and should not be used in new implementations — it returns access tokens directly in the URL fragment, where they can leak through browser history, referrer headers, and logs. The resource owner password credentials grant should also be avoided outside of legacy migrations, since it requires your application to handle raw user passwords.
For nearly every modern use case — single-page apps, mobile apps, and traditional server-rendered apps alike — the answer is the authorization code flow with PKCE (Proof Key for Code Exchange) . This is the core of current OAuth 2.0 best practices, as codified in IETF's OAuth 2.0 Security Best Current Practice (RFC 9700), which now recommends PKCE for all clients, not just public ones without a client secret.
When registering your OAuth client with the authorization server, resist the temptation to use wildcard or pattern-matched redirect URIs. Loose redirect URI matching is one of the most exploited OAuth security vulnerabilities to avoid, since an attacker who can redirect the authorization response to a domain they control can steal authorization codes or tokens. If you support multiple environments, register a separate redirect URI per environment (dev, staging, production) rather than relying on a single permissive pattern, and have your authorization server reject any request whose redirect_uri doesn't match a registered value byte-for-byte.
PKCE closes the gap that made the authorization code flow vulnerable to interception, particularly on mobile and single-page apps where the client can't hold a secret safely. Here's the PKCE oauth flow explained in the order your code should execute it: Because the token exchange requires the original, unhashed verifier, an attacker who intercepts only the authorization code cannot complete the exchange without also compromising the client that generated the verifier.
Skipping state validation is a recurring finding in OAuth implementation reviews: without it, an attacker can trick a victim into completing an authorization flow initiated by the attacker, binding the victim's session to the attacker's account. Request only the scopes your application actually needs, and have your resource servers enforce those scopes independently rather than trusting the client's claims. On the API side, validate the token's signature, expiration, audience ( aud ), and issuer ( iss ) on every request — not just at login: Overly broad scopes turn a single compromised token into a much bigger breach than it needs to be, and audience validation prevents a token issued for one API from being replayed against another.
Once your flow is running end to end, verify it deliberately rather than assuming it's correct because the happy path works: If any of these checks pass when they should fail, you've found one of the OAuth security vulnerabilities to avoid before an attacker does — treat each as a blocking issue, not a backlog item. Getting the OAuth flow right on paper is one thing; keeping it right as your codebase, dependencies, and CI/CD pipeline evolve is another. Safeguard's software supply chain security platform continuously scans your repositories and build pipelines for the patterns that lead to insecure OAuth deployments — hardcoded client secrets committed to source control, dependencies with known token-handling CVEs, misconfigured redirect allowlists checked into infrastructure-as-code, and CI jobs that leak tokens into build logs.
Rather than relying on a one-time security review, Safeguard integrates into your SCM and build process to flag secret exposure and vulnerable auth libraries automatically, before they ship, and to give your AppSec team a single view of authentication-related risk across every service that implements OAuth. That means the checklist in this guide doesn't just get applied once during implementation — it gets continuously enforced as your team ships new services and updates dependencies, so a secure OAuth setup stays secure.
Using Safeguard's organization, team and project structure, roles, runners and Trust Center to keep many clients separate, with what to confirm before you commit. How a security consultant can use Safeguard on client work: scan without repo access, check client SBOMs, look up packages, and hand over evidence, with limits stated.
A small team plan for using Safeguard in the first month: free Gold checks, the CLI, the web app, a Trust Center for customer questions, and sensible AI settings. 3. Software Implementation, Frameworks & Protocols Learn how to implement secure SaaS authentication in 2026 using OAuth 2.0, JWT, SSO, MFA, and social logins. This complete developer guide covers token structure, refresh strategies, OAuth flows, PKCE, SAML vs OIDC, and production-ready best practices.
In SaaS applications, authentication is not just a login form . It is your first and most critical security boundary. A poorly implemented authentication system can lead to: This guide explains how to implement SaaS authentication using OAuth, JWT, and SSO with real-world patterns and best practices.
Only if you fully understand OAuth, JWT, and security best practices. Otherwise use Auth-as-a-Service. SaaS authentication in 2026 is more complex than ever but also more critical. A secure system requires: Implementing authentication in SaaS using OAuth, JWT, and SSO requires careful design and strong security discipline. A well-designed authentication system: At Softqare , we design secure, scalable authentication architectures for SaaS platforms from OAuth flows to enterprise SSO integration. If you're building or upgrading your SaaS authentication system in 2026, our engineering team can guide you.
Engineering leader with deep expertise in scalable web systems, cloud architecture, and AI-powered applications. Passionate about building software that makes a measurable real-world impact. Learn the real cost of building a SaaS product in 2026, including development, UI/UX design, cloud infrastructure, third-party APIs, marketing, and ongoing maintenance. This guide helps startup founders and CTOs create a realistic budget and avoid costly mistakes.
Hiring the right software development company in 2026 is a strategic business decision. This executive guide covers evaluation criteria, pricing models, technical assessment, red flags, and contract essentials to help decision-makers choose the right technology partner with confidence. In 2026, businesses need more than generic solutions to stay competitive. Custom software development empowers organizations with scalable, secure, and fully tailored systems that align with their unique processes. This article explores the key benefits of custom software development, ROI potential, industry use cases, and how decision makers can choose the right development partner for long term success.
Discover our services, check out our portfolio, or get in touch to discuss your project. OAuth 2.0 and OpenID Connect (OIDC) are the foundational protocols for modern authorization and authentication on the web. OAuth 2.0 handles authorization, granting an application limited access to a user's resources. OIDC is a layer on top of OAuth 2.0 that adds authentication, verifying the user's identity and providing profile information.
Despite their ubiquity, these protocols are frequently implemented incorrectly. Misconfigurations lead to token leakage, privilege escalation, and account takeover. This guide provides a rigorous, implementation-focused walkthrough so you can deploy OAuth 2.0 and OIDC correctly from the start. OAuth 2.0 defines several authorization flows. Choosing the wrong one is a common source of vulnerabilities.
The authorization code flow with PKCE is the recommended flow for all interactive clients. The implicit flow is deprecated and should never be used for new implementations. PKCE (Proof Key for Code Exchange) protects against authorization code interception. It is required for public clients and recommended for all clients.
Always enable refresh token rotation on the authorization server. With rotation, each refresh token can only be used once. If a stolen refresh token is replayed, the authorization server detects the reuse and revokes the entire token family. For opaque access tokens, the resource server must call the authorization server's introspection endpoint ( /introspect ) to validate the token. This adds latency but allows the AS to revoke tokens immediately.
OAuth 2.0 and OpenID Connect are powerful protocols that, when implemented correctly, provide secure and user-friendly authentication and authorization. The key is discipline: use the authorization code flow with PKCE for all interactive clients, keep tokens short-lived, validate everything server-side, and design scopes that enforce least privilege. The protocols themselves are well-designed. Most OAuth vulnerabilities come from implementation mistakes, using the wrong flow, accepting unregistered redirect URIs, or failing to validate tokens. By following the patterns in this guide and testing rigorously, you can build a solid OAuth/OIDC implementation that protects your users and your APIs.
Q: Is the implicit flow still acceptable? A: No. The OAuth 2.0 Security Best Current Practice (RFC 9700) recommends against the implicit flow. Use the authorization code flow with PKCE for all clients, including SPAs. Q: Should I use opaque or JWT access tokens? A: JWT access tokens enable local validation at the resource server, reducing latency. Opaque tokens require introspection but allow immediate revocation. For most architectures, JWT access tokens with short lifetimes (5-15 minutes) strike the right balance.
Q: Can I use OAuth 2.0 for authentication? A: OAuth 2.0 alone is an authorization protocol and should not be used for authentication. Use OIDC, which adds the ID token and standardized identity claims on top of OAuth 2.0. Q: How do I handle multi-tenant APIs? A: Include the tenant identifier in the scope or audience claim. The resource server should validate that the token's tenant matches the requested resource's tenant. Consider using separate authorization server instances per tenant for strong isolation.
OAuth 2.0 and OpenID Connect are constantly confused, and using the wrong one creates real security holes. The short version: **OAuth is for authorization, OIDC Master Microsoft Entra conditional access with risk-based policies, device compliance rules, location-based restrictions, and real-world deployment patterns.
A practical guide to implementing SCIM-based automated user provisioning and deprovisioning, covering the SCIM protocol, lifecycle management, vendor integratio OpenID Connect is an authentication layer built on top of OAuth 2.0. Where OAuth tells you what a token is authorized for, OIDC tells you who the user is via a OpenID Connect is the identity layer on top of OAuth 2.0. It is what you use to log a user in and learn who they are.
Annabelle Backman is a principal security engineer on AWS Identity and co-chairs the OpenID Shared Signals and Events working group. She edited RFC 8935 and RFC Single Sign-On (SSO) allows users to authenticate once and access multiple applications without re-entering credentials. It improves user experience while enhancing security through centralized authentication.
The example below is the OIDC authorization code flow with PKCE. The browser only ever sees the authorization code; the token exchange happens on your server, where the client secret lives. Use a maintained library for the exchange and validation. Hand-written JWT checks miss things: accepting alg: none , skipping the audience check, or trusting an ID token that was issued for a different client are all mistakes that libraries prevent by default.
Whichever protocol you use, the service provider must verify the response before trusting it: Matching users by email. Email addresses change and can be reassigned. Map accounts on the stable identifier ( sub in OIDC, NameID with a persistent format in SAML) and store the email only as an attribute. Open redirects after login. If you store a "return to" URL before redirecting to the IdP, allow only relative paths on your own origin when you read it back.
Wildcard redirect URIs. Some IdPs allow them. Do not use them; register every redirect URI exactly. Treating the access token as proof of identity. An OAuth access token is for calling APIs. Identity comes from the ID token (OIDC) or the assertion (SAML). Letting the signing certificate expire. SAML certificates are typically valid for one to three years. When one expires every login fails at once. Put the expiry date in a calendar and in monitoring.
Group claims that are too large. Entra ID, for example, stops sending groups in the token past a limit and sends a link instead. Filter groups at the IdP to the ones the application needs. Every mainstream IdP has a sign-in log that shows exactly why it rejected or what it sent. For the SP side, a browser SAML or OIDC tracer extension lets you read the actual assertion or token without touching server logs.
Okta vs Azure AD: Choosing the Best Enterprise Single Sign-On (SSO) Solution for Your Business IAM News: WhatsApp Adds Multiple Passkeys for Phishing-Resistant Sign-Ins Across iOS and Android Below are some guides to OAuth 2.0 which cover many of the topics needed to understand and implement clients and servers.
OAuth 2.0 Simplified , written by Aaron Parecki , is a guide to OAuth 2.0 focused on writing clients that gives a clear overview of the spec at an introductory level. OAuth 2.0 Servers , written by Aaron Parecki and published by Okta , is a guide to building an OAuth 2.0 server, including many details that are not part of the spec.
There are many client and server libraries in multiple languages to get you started quickly. 4. Practical Deployment, Analysis & Case Studies If you've been building Spring Boot apps with basic form logins, you've probably hit the point where you need something better. Maybe your company uses Okta, Azure AD, or some other identity provider. Maybe you want to stop managing passwords altogether. That's where OAuth2 authentication comes in.
Spring Boot OAuth2 authentication is an enterprise-grade authentication mechanism that delegates credential management to trusted identity providers. This comprehensive guide walks through implementing OAuth2 in a Spring Boot application with role-based access control, so you can restrict pages to specific users. If you're new to Spring Security, check out our guide on custom authentication strategies first—it covers the basics before you tackle OAuth2.
This guide covers implementing OAuth2 in a Spring Boot application, including role-based access control so you can restrict pages to specific users. If you need enterprise-level authentication and are considering other approaches, SAML authentication is another solid option worth knowing about. OAuth2 authentication is an open standard authorization protocol that allows users to grant third-party applications access to their resources without sharing passwords. In the context of Spring Boot applications, OAuth2 enables Single Sign-On (SSO) by delegating user authentication to an external identity provider.
Simply put: instead of your application storing and validating passwords, OAuth2 authentication in Spring Boot lets an external provider (like Okta or Azure AD) handle login. Your app receives a secure token that confirms the user's identity. OAuth2 gets talked about a lot, and honestly, it's simpler than people make it sound. At its core, you're outsourcing authentication to a third party. Your users log in somewhere else (like Okta or Google), get a token, and then that token tells your app who they are and what they can do.
If you're coming from a homegrown authentication system or the approach covered in custom authentication implementations, OAuth2 represents a significant shift—you're trusting an external provider instead of managing credentials yourself. OAuth 2.0 operates through a series of steps called the OAuth2 authorization flow. Here's how Spring Boot OAuth2 authentication works in practice: The beauty of this token-based authentication setup is you never touch passwords. The user logs in once at their identity provider, gets a token, and uses that everywhere.
Create a SecurityConfig class. This is where you tell Spring how authentication should work. Enable method-level security too—you'll need it for role checks. Note on HTTPS: If you're testing locally on localhost , the HTTPS requirement will cause connection errors. Comment out the .requiresChannel() block while developing, but keep it in production.
Tell Spring where your identity provider is and provide the credentials. Add this to application.yml . Here's an example using Okta: Replace issuer-uri , client-id , and client-secret with values from your identity provider. The redirect-uri is where your app receives the token after login—Spring handles this automatically, no controller needed.
The openid scope is required. Without it, Spring won't get the ID token needed to extract user details. Here's the tricky part of Spring Security implementation steps. Your identity provider probably sends user groups or roles in the token, but Spring Security expects them in a specific format: with a ROLE_ prefix . This is where role-based access control truly comes into play.
This interceptor runs during login and transforms your provider's groups into Spring roles. Make sure your identity provider is configured to include groups in the ID token. In Okta, you'll need to add a custom claim called groups in your Authorization Server settings. Run the app. When you hit a protected endpoint, you'll be redirected to your identity provider's login page. After login, you'll be back in your app with a token and whatever roles your provider sent.
Spring Boot OAuth2 authentication is the modern standard for securing enterprise applications. By delegating authentication to trusted identity providers, you eliminate the burden of password management while improving user experience through Single Sign-On. The implementation process—while it looks intimidating at first with all the configuration—boils down to these key points: Once everything is wired up in your Spring Boot application, users get a seamless experience—they authenticate once at their company's identity provider and gain access everywhere without managing new passwords. Your team gets cleaner, more secure code. The whole system becomes enterprise-ready from day one.
If you're ready to move beyond basic authentication, Spring Boot OAuth2 security is the natural next step for modern applications handling sensitive data and multiple user roles. Implementing OAuth2 can feel overwhelming. If you're stuck or need guidance on securing your Spring Boot application, contact our experts to discuss your requirements and get personalized help with your implementation.
At Opcito, we specialize in building enterprise-grade Spring Boot applications with robust security architectures. Our team has extensive experience implementing OAuth2, SSO, and role-based access control across complex microservice environments. Let us help you navigate the security landscape and get your application production-ready. Explore our VAPT as a Service portfolio or speak with our team to discuss your security testing requirements.
Social logins and enterprise connections are popular because they are an extremely effective way to register users lowering sign up frictions (often up to 20% higher conversion or more) as well as a way to connect internal enterprise directories to a SaaS application. Besides SAML, which is largely used for enterprise directories, the standard for social login is a protocol called OpenID Connect (OIDC). This is an identity layer built on top of the OAuth 2.0 framework. It allows third-party applications to verify the identity of the end-user and to obtain basic user profile information. OIDC uses JSON web tokens (JWTs), which are obtained through flows defined in the OAuth 2.0 specifications.
Unfortunately OAuth 2.0 is a complex protocol and several implementations suffer from security issues. Just recently Salt Security published a series of blog posts on OAuth 2.0 implementation bugs found in sites such as Booking.com, Kayak, Grammarly, and many more. This is in addition to the vulnerability reported to Descope that can lead to privilege escalation when using Entra/Azure AD for SSO and the one reported by Truffle Security that could lead to a similar outcome with Google.
In this blog post we summarize the best practices in implementing OAuth 2.0 securely followed by a deeper dive on the risk posed by each. It would take too long to describe all the possible OAuth 2.0 flows and they are generally well documented online. To summarize in a picture: At a high-level, here is some contextual information useful for the rest of the article: Authorization Grant Types : OAuth 2.0 defines several grant types but in this article we’ll touch on the two most commonly used ones: As it is often explained publicly, OAuth 2.0 doesn’t provide an authentication flow hence it is generally used in conjuction to OpenID Connect (OIDC). OIDC allows clients to verify the identity of an end-user based on the authentication performed by an authorization server, as well as to obtain basic profile information about the end-user. At a high-level: In practice, at a high level, a client is given a client_id and a client_secret . The client initiates a request sending those two parameters among others to the authorization server, the authorization server first verifies the validity of the client_id and client_secret and then proceeds to verify the user. Once that’s done, the user is redirected to a redirect_uri passed to the authorization server by the client. From there on, depending on the OAuth 2.0 flow, there might be further exchanges between the client and the authorization server server.
This issue has presented itself in a number of different flavors across major identity providers including Microsoft Entra, Google and AWS Cognito. For example, Flickr was compromised through a version of this issue . The false identifier anti-pattern occurs when an application or service assumes that an attribute other than the subject of an assertion from a federated identity provider is a unique, durable, and trustworthy account identifier during single sign-on.
The issue stems from the fact that in AzureAD/Entra a user without a provisioned mailbox can have any email address set for their Mail (Primary SMTP) attribute. This attribute is not guaranteed to come from a verified email address. However most clients retrieving the email address claim through OIDC would treat it as a verified/authoritative email address. For example, an attacker could have an Azure AD account with an email such as [email protected] and the receiving client would treat that as the valid email address for that user. If Satya Nadella actually had an account in that specific client that could lead to a privilege escalation/unauthorized impersonation where the attacker could impersonate Nadella.
It’s important to note that while this specific issue was about the email address claim in AzureAD, the more general pattern is for clients to always verify which claims are authoritative for a Resource Server and maintain the same “privileges” over them. In fact, similarly to the Entra issues, researchers at Truffle Security discovered a very similar issue with Google. In particular, it is possible to create a Google account with an existing email. Contrary to the AzureAD case, the ownership of the email is verified. However depending on the implementation of the client this could still lead to two issues: Note: Google has a OAuth 2.0 claim called email_verified , it might be possible to create Google accounts without any email verification at all leading to more unauthorized impersonation issues.
The last example is another variation on this but easier to follow. A website can use AWS Cognito as an OAuth 2.0 provider leading to a similar issue. As well described in this blog post on Flickr , by default Cognito allows users to change their user attributes, including the email attribute email .
In the case of Flickr, the website was using the standard OIDC flow to authenticate a user and they referenced the email claim without verying the flag in the email_verified claim. This lead to a scenario where an attacker could takeover any Flickr account with a simple process: Flickr use the email claim to link the Flickr account to the AWS Cognito user resulting in an arbitrary account takeover.
5. Performance Evaluation & Extended Technical Observations When a client registers with an Authorization Server generally a redirect_uri has to be specified, the Authorization Server will then verify that the URL passed during the OIDC flow matches the redirect_uri stored for that client. Unfortunately most Authorization Servers allow wildcards in the path or some even allow no redirect_uri at all. There’s nothing the client can do in the latter case but in the former it is crucial to specify exact urls instead of wildcards.
This is because an attacker can potentially trick a victim into being redirected to a different origin than intended and thus potentially stealing the access token. The implicit OAuth 2.0 grant type was previously recommended for native apps and SPA applications. In this flow, the access token is returned directly as part of the redirect.
Combining this with the previous issue, can lead to a simple way to impersonate the user by stealing the access token when the user is redirected to a redirect_uri that is attacker-controlled. Cross-Site Request Forgery (CSRF) is a vulnerability that occurs when an attacker can cause a victim to perform an unintended action on a web resource. In the context of OAuth 2.0, a code interception attack is an attack where the attacker intercepts an authorization code and tries to redeem it for a valid access token.
A technique called Proof Key for Code Exchange (PKCE, pronounced “pixy”) was introduced to reduce the risk of CSRF and code interception. PKCE is an addition to any OAuth 2.0 flows. In summary, the idea is for the application/client to select a secret, one-time nonce that cannot be intercepted by an attacker as it is never sent to the user browser.
When a flow starts, the client hashes the nonce and sends it in the code_challenge parameter to the authorization server. When the user completes the authorization flow and is redirected to the redirect_uri , the client sends the code_verifier in addition to the auth code and the state parameters to the authorization server. The authorization server returns a valid access token only if the hash of the code_verified matches the code_challenge .
The key idea is that an attacker who intercepts the authorization code from the server is unable to redeem it for an access token, as they are not in possession of the code_verifier secret. The authorization server would reject a token request if the attacker tries to inject an authorization code via CSRF. PKCE also protects against a network attacker because the attacker would need to inject a code that is bound to the same code challenge that was used initially by the client. While the attacker can create codes bound to arbitrary code challenges, the attacker cannot know the code challenge used in any one legitimate session.
If you do need to support the implicit OAuth 2.0 grant type it is key to verify the token received in the callback as the callback could be invoked by an attacker with a valid access token belonging to a different website. In this scenario, an attacker can intercept the OAuth 2.0 flow and swap the token with a token issued from an attacker-controlled website. Specifically: To address this problem, it is crucial to confirm that the token received was issued for the client client_id and not for a third party application.
Duplicated accounts are one of the most vexing issues for both users and companies. On the user side, duplicate accounts lead to frustration and bad experience. On the company side it leads to customer support tickets as well as issues with data analysis. To address this problem a lot of websites automatically merge accounts if the primary user identifier is the same. In other words, a user who registered with [email protected] and has account number 123 will be treated as the same person if the primary identifier [email protected] comes from OIDC, a magic link or any other authentication method.
This is a more general case of the issues we’ve see in (1), specifically an attacker could impersonate a legitimate user if account merging is turned on a website and the website has one of two issues: Ultimately mitigating these issues requires the expert review of a security engineer or an application security review. However, using a vendor can make the task less daunting. In particular, if you are a SlashID customer we help you in the following ways: Authentication is a typical example of a task that is simple in theory but very hard in practice due to both security and reliability issues. In this blog post we’ve shown a few examples of what could go wrong when implementing OIDC/Social Logins.
If you are interested in implementing social logins and identity securely, get a free account here or reach out to us ! JadePuffer (Storm-3168): An AI Agent Wiped 100+ Azure Storage Accounts in Seven Minutes See how SlashID detects, investigates and remediates identity threats end-to-end — across humans, machines and AI agents.
AI didn't learn to write code — it learned to translate it. Here's what that means for productivity, security, and your team's code review workflow. Real-world cost optimization through strategic prompt engineering, smart model selection, and caching—with actual numbers from production Kubernetes is the right tool at the right scale. For small teams running under 20 services, Nomad delivers the same core value with far less operational overhead.
Techniques and patterns for performing database schema migrations with zero downtime in production environments The story of fabric-forge and fabric/social — what happens when you stop fighting your tools and start listening to them. Git-steer forked PegaProx, an open-source Proxmox management platform, audited the codebase, and submitted 10 pull requests in a single session.
A budget complaint exposed a security pipeline quietly lying about a clean fleet. Rebuilding it into one gated control plane — and a field note on which calls came from the human and which from the AI. OAuth 2.0 and OpenID Connect (OIDC) have become the de facto standards for authentication and authorization in modern web applications. While OAuth 2.0 handles authorization, OpenID Connect extends it to provide authentication capabilities.
Understanding how to properly implement these protocols is crucial for building secure, scalable enterprise applications. This guide provides a comprehensive walkthrough of implementing OAuth 2.0 and OpenID Connect, covering everything from basic concepts to production-ready implementations. OAuth 2.0 is an authorization framework that enables applications to obtain limited access to user accounts on an HTTP service. It works by delegating user authentication to the service that hosts the user account and authorizing third-party applications to access that account.
OpenID Connect is an identity layer built on top of OAuth 2.0. It adds authentication capabilities and provides standardized ways to obtain user information. The most secure flow for web applications with a backend server. The client receives an authorization code that it exchanges for tokens on the backend.
An extension of the authorization code flow that provides additional security for public clients (SPAs, mobile apps) that cannot securely store client secrets. Always use the OIDC Discovery endpoint to retrieve provider configuration dynamically. After successful authentication, use the access token to retrieve user claims from the UserInfo endpoint.
Implement automatic token refresh before expiration to maintain uninterrupted user sessions. Implementing OAuth 2.0 and OpenID Connect correctly is essential for modern application security. By following the patterns and best practices outlined in this guide, you can build secure, scalable authentication and authorization systems that protect your users and resources.
Remember that security is not a one-time implementation but an ongoing process. Stay updated with the latest OAuth and OIDC specifications, regularly review your implementation, and conduct security audits to ensure your authentication system remains robust and secure. Engineering leader and builder obsessed with AI systems, DevOps automation, and infrastructure that runs itself. Created Cortex — an autonomous AI orchestration platform built in 28 days. Writes about the messy, real side of shipping software.
Claude assisted with code generation, content drafting, and technical review across every post on this site. From debugging infrastructure to writing prose — a true co-pilot. Building modern enterprise security with Zero Trust principles, moving from perimeter-based to identity-centric security models A comprehensive guide to preparing for and passing SOC 2 Type II audits, covering trust service criteria and implementation best practices Deep dive into Cortex's production monitoring architecture - the metrics that matter, alerts that prevent disasters, and trade-offs in observability MCP server for comprehensive UniFi infrastructure monitoring and management with A2A support GitHub autonomy engine — control repos, branches, security, and Actions through natural language via MCP Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Single%20sign-on • https://en.wikipedia.org/wiki/List%20of%20OAuth%20providers • https://en.wikipedia.org/wiki/List%20of%20single%20sign-on%20implementations • https://www.weweb.io/blog/single-sign-on-using-oauth2-developer-guide • https://safeguard.sh/resources/blog/how-to-implement-oauth-20-securely • https://softcare.vercel.app/blogs/how-to-implement-authentication-in-saas-oauth-jwt-sso-explained-2026-guide • https://startwithidentity.com/guides/implementation/oauth-2-openid-connect-implementation/ • https://iamroadmap.com/article/sso-implementation-complete-guide • https://oauth.net/getting-started/ • https://www.opcito.com/blogs/spring-boot-oauth2-authentication-guide
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Secure Single Sign On Implementation Using Oauth 2.0.
[*] Metasploit Scan Running on Target Subnet for Secure Single Sign On Implementation Using Oauth 2.0... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |