Complete Technical Paper Content — Secure Socks5 Proxy Server Implementation In Python
Overview & System Context
Secure Socks5 Proxy Server Implementation In Python: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~5831 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background SOCKS is an Internet protocol that exchanges network packets between a client and server through a proxy server. SOCKS5 optionally provides authentication, so only authorized users may access a server. Practically, a SOCKS server proxies TCP connections to an arbitrary IP address and provides a means for UDP packets to be forwarded. The SOCKS protocol operates between the application layer and the transport layer. A SOCKS server accepts incoming client connection on TCP port 1080.
A circumvention tool, allowing traffic to bypass Internet filtering to access content otherwise blocked, e.g., by governments, workplaces, schools, and country-specific web services. Since SOCKS is very detectable, a common approach is to present a SOCKS interface for more sophisticated protocols: The Tor onion proxy software presents a SOCKS interface to its clients. Providing similar functionality to a virtual private network, allowing connections to be forwarded to a server's "local" network: Some SSH suites, such as OpenSSH, support dynamic port forwarding that allows the user to create a local SOCKS proxy.
This can free the user from the limitations of connecting only to a predefined remote port and server. VER: 8 bits SOCKS version number, 0x04 for this version CMD: 8 bits Command code: 0x01: Establish a TCP/IP stream connection. 0x02: Establish a TCP/IP port binding. DSTPORT: 16 bits Destination port number, in network byte order. DESTIP: 32 bits Destination IPv4 address, in network byte order. ID: variable The User ID string, null-terminated. The server responds with: VN: 8 bits Reply version (a null byte). REP: 8 bits Reply code: 0x5a: Request granted. 0x5b: Request rejected or failed. 0x5c: Request failed because client is not running identd (or not reachable from server). 0x5d: Request failed because client's identd could not confirm the user ID in the request. DSTPORT: 16 bits Destination port number, meaningful if granted in BIND, should otherwise be ignored. DESTIP: 32 bits Destination IPv4 address. Together with DSTPORT the ip:port the client should bind to.
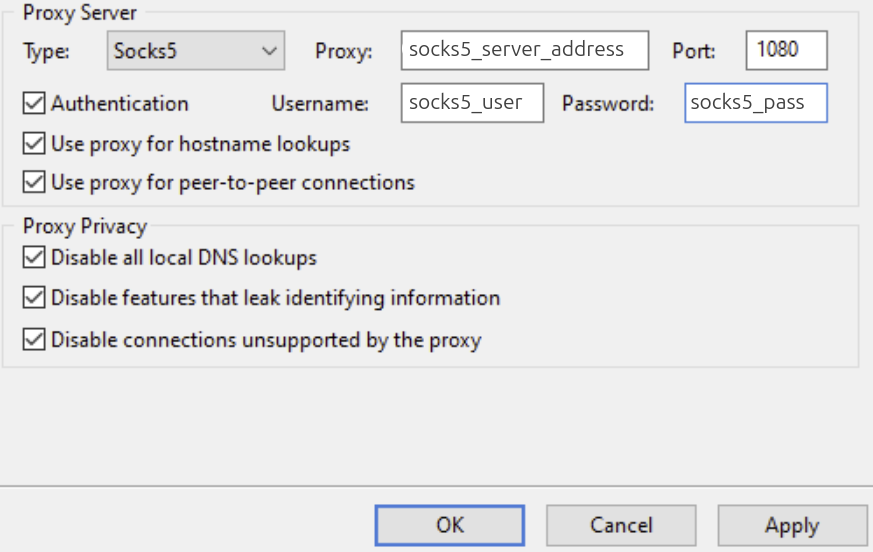
Figure 1: uTorrent SOCKS5 Configuration - Privado For example, this is a SOCKS4 request to connect Fred to 66.102.7.99:80, the server replies with an "OK": Client: 0x04 | 0x01 | 0x00 0x50 | 0x42 0x66 0x07 0x63 | 0x46 0x72 0x65 0x64 0x00 The last field is "Fred" in ASCII, followed by a null byte. Server: 0x00 | 0x5A | 0xXX 0xXX | 0xXX 0xXX 0xXX 0xXX 0xXX can be any byte value. The SOCKS4 protocol specifies that the values of these bytes should be ignored. From this point onwards, any data sent from the SOCKS client to the SOCKS server is relayed to 66.102.7.99, and vice versa. The command field may be 0x01 for "connect" or 0x02 for "bind"; the "bind" command allows incoming connections for protocols such as active FTP.
SOCKS4_C SOCKS4 client handshake packet (above) DOMAIN the domain name of the host to contact, null (0x00) terminated Server to SOCKS client: (Same as SOCKS4) A server using protocol SOCKS4a must check the DSTIP in the request packet. If it represents address 0.0.0.x with nonzero x, the server must read in the domain name that the client sends in the packet. The server should resolve the domain name and make connection to the destination host if it can.
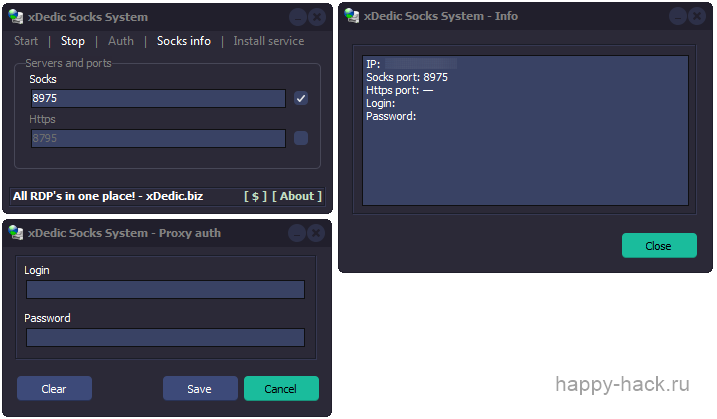
Client connects and sends a greeting, which includes a list of authentication methods supported. Server chooses one of the methods (or sends a failure response if none of them are acceptable). Several messages may now pass between the client and the server, depending on the authentication method chosen. Client sends a connection request similar to SOCKS4. Server responds similar to SOCKS4. The initial greeting from the client is: Figure 2: GitHub - amazond/Socks5-proxy-server: Socks5 proxy server Windows ...
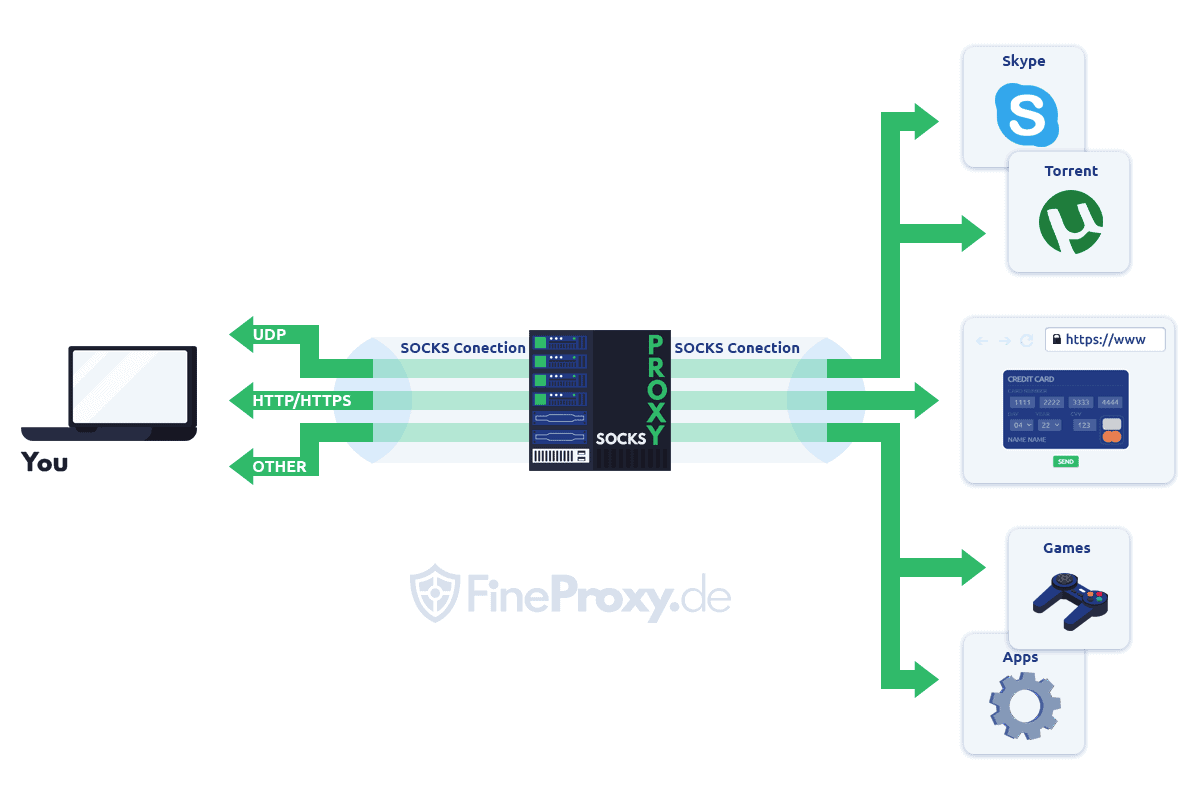
VER SOCKS version (0x05) NAUTH Number of authentication methods supported, uint8 AUTH Authentication methods, 1 byte per method supported The authentication methods supported are numbered as follows: 0x00: No authentication 0x01: GSSAPI (RFC 1961) 0x02: Username/password (RFC 1929) 0x03–0x7F: methods assigned by IANA 0x03: Challenge–Handshake Authentication Protocol 0x04: Unassigned 0x05: Challenge–Response Authentication Method 0x06: Secure Sockets Layer 0x07: NDS Authentication 0x08: Multi-Authentication Framework 0x09: JSON Parameter Block 0x0A–0x7F: Unassigned 0x80–0xFE: methods reserved for private use VER SOCKS version (0x05) CAUTH chosen authentication method, or 0xFF if no acceptable methods were offered The subsequent authentication is method-dependent. Username and password authentication (method 0x02) is described in RFC 1929: VER 0x01 for current version of username/password authentication IDLEN, ID Username length, uint8; username as bytestring PWLEN, PW Password length, uint8; password as bytestring VER 0x01 for current version of username/password authentication STATUS 0x00 success, otherwise failure, connection must be closed After authentication the connection can proceed. We first define an address datatype as: Figure 3: What Is a SOCKS5 Proxy Server, Its Uses, and the Mobile Advantage TYPE type of the address. One of: 0x01: IPv4 address 0x03: Domain name 0x04: IPv6 address ADDR the address data that follows. Depending on type: 4 bytes for IPv4 address 1 byte of name length followed by 1–255 bytes for the domain name 16 bytes for IPv6 address VER SOCKS version (0x05) CMD command code: 0x01: establish a TCP/IP stream connection 0x02: establish a TCP/IP port binding 0x03: associate a UDP port RSV reserved, must be 0x00 DSTADDR destination address, see the address structure above. DSTPORT port number in a network byte order VER SOCKS version (0x05) STATUS status code: 0x00: request granted 0x01: general failure 0x02: connection not allowed by ruleset 0x03: network unreachable 0x04: host unreachable 0x05: connection refused by destination host 0x06: TTL expired 0x07: command not supported / protocol error 0x08: address type not supported RSV reserved, must be 0x00 BNDADDR server bound address in the "SOCKS5 address" format specified above BNDPORT server bound port number in a network byte order Since clients are allowed to use either resolved addresses or domain names, a convention from cURL exists to label the domain name variant of SOCKS5 "socks5h", and the other simply "socks5". A similar convention exists between SOCKS4a and SOCKS4.
Proxifier, a paid proprietary program for Windows and macOS that can force programs to use a SOCKS, HTTPS or HTTP proxy using the Windows Filtering Platform (on Windows) or the Network Extension Framework (on macOS). tun2socks, an open-source tool that creates virtual TCP TUN adapters from a SOCKS proxy, capable of UDP if supported on another end. Works on Linux and Windows, has a macOS port and reimplementation in Golang. Another implementation, written in C with good performance, works on Linux/Android/BSD/macOS and iOS. proxychains, a Unix program that forces TCP traffic through SOCKS or HTTP proxies on (dynamically linked) programs it launches. Works on various Unix-like systems.
Lack of request and packets exchange encryption makes SOCKS practically vulnerable to man-in-the-middle attacks and IP addresses eavesdropping, which in consequence clears a way to censorship by governments. A lightweight, easy-to-deploy SOCKS5 proxy server implementation in Python 3.12 with Docker support. We needed a simple SOCKS5 proxy for our infrastructure, and initially tried to use Dante proxy . However, we discovered that: After seeing countless GitHub issues and Stack Overflow posts about Dante proxy Docker problems, we decided to write our own solution . This Python implementation is: I Simple to deploy - Just docker-compose up I Easy to configure - Environment variables only I Well documented - Clear examples and troubleshooting I Production ready - Proper logging, health checks, and graceful shutdown I No external dependencies - Pure Python implementation TL;DR : You can use this for anything, including commercial projects. Just keep the license notice.
A lightweight, easy-to-deploy SOCKS5 proxy server in Python. Simple alternative to complex Dante proxy configurations. For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation . SOCKS5 proxy implementation in Python using httplib2 provides a secure and efficient way to route network traffic through intermediary servers. This guide explores everything you need to know about httplib2.socks.PROXY_TYPE_SOCKS5 .
SOCKS5 is a secure proxy protocol that enables clients to establish TCP connections through an intermediary server. It supports various authentication methods and provides better security compared to earlier versions. Before implementing SOCKS5, you need to have httplib2 installed. If you haven't installed it yet, check out How to Install and Use httplib2 in Python: A Complete Guide .
Once configured, you can make HTTP requests through the SOCKS5 proxy. Here's how to perform a simple GET request: Implementing proper error handling is crucial when working with SOCKS5 proxies. Here's a more robust implementation: When using SOCKS5 proxy with httplib2, security should be a top priority. You might want to integrate it with secure client authentication. Learn more about this in our guide about Python httplib2.Http.add_certificate: Secure Client Authentication .
2. System Architecture & Core Working Principles httplib2.socks.PROXY_TYPE_SOCKS5 provides a robust solution for implementing SOCKS5 proxy connections in Python. With proper configuration and error handling, it enables secure and reliable proxy communication. Remember to always follow security best practices and properly handle errors when implementing proxy connections in your applications.
A SOCKS Protocol Version 5 proxy server written in Python. Implements RFC 1928 (SOCKS5) and RFC 1929 (username/password authentication). Setting SOCKS5_AUTH_REQUIRED=false explicitly acknowledges the choice: the open-proxy warning banner is replaced by a single INFO line. The default-credentials warning still appears unless you set your own SOCKS5_USERNAME / SOCKS5_PASSWORD . See Security .
If you override the image's command or healthcheck, or parse its logs, read Upgrading from 2.1 . The healthcheck is now python -m simple_socks5.healthcheck , ERROR lines mean a fault in the proxy, and repeated handshake-timeout and failed-login warnings are rate-limited. To keep the 2.1 behaviour, pin jcaponigro20/simple-socks5:2.1.0 . 2.1 changes some defaults: the image logs at info , proxying to loopback and link-local addresses is refused unless SOCKS5_ALLOW_LOOPBACK=true , nothing is written to /app/errors.log unless SOCKS5_LOG_FILE is set, and latest moves only on releases. Each of these has an opt-out. An empty SOCKS5_USERNAME or SOCKS5_PASSWORD can no longer be used to log in, with no opt-out. See Upgrading from 2.0 . To keep the 2.0 behaviour, pin jcaponigro20/simple-socks5:2.0.0 .
python3 app.py runs straight from a clone, but reports its version as 0+unknown until you install the package ( pip install -e . ). To install the simple-socks5 command, which takes the same flags: Timeouts accept any positive number of seconds, such as 2.5 . SOCKS5_MAX_CONNECTIONS must be a positive integer. An invalid value stops the proxy at startup with an error.
Logs go to stderr. Each connection logs one line once it has connected to the destination and one when it closes: up counts bytes from the client to the destination, down the other way. The destination is the hostname the client sent, with the address the proxy connected to, or just the IP the client sent: the proxy never does reverse-DNS lookups. A CONNECT that fails logs only its reply code. A UDP association logs the same two lines: it closes with its TCP control connection, and up and down count the datagram payloads relayed. Individual UDP datagrams are logged at debug .
Colours are used only when stderr is a terminal. Nothing is written to disk unless SOCKS5_LOG_FILE is set. The examples below forward SOCKS5_USERNAME and SOCKS5_PASSWORD from your shell (export them as in Quick Start ). The container always listens on 0.0.0.0 inside Docker; the -p flag decides which host interfaces the port is published on.
Docker's default bridge network has no IPv6. A client that resolves names itself ( curl --socks5 , socks5:// URLs) may send the proxy an IPv6 address, which then fails with reply 0x03 (network unreachable). Let the proxy resolve names instead ( curl --socks5-hostname , socks5h:// , "Proxy DNS when using SOCKS v5" in Firefox), or enable IPv6 on the container's network. The proxy tries a name's addresses in the order the system returns them, usually IPv6 first, and moves on to the next when one fails. It stops after 4 attempts, so a name with 4 or more IPv6 addresses listed before its IPv4 ones still needs IPv6.
The image's HEALTHCHECK runs python -m simple_socks5.healthcheck every 30 seconds. It sends a SOCKS5 greeting to 127.0.0.1 on SOCKS5_HEALTHCHECK_PORT (default 1080 ) and passes on any SOCKS5 reply, so it works with and without authentication, and the proxy logs it at debug only. If you override the command with a different --port , set SOCKS5_HEALTHCHECK_PORT to match. If you bind a specific non-loopback address instead of 0.0.0.0 or :: , the healthcheck can't reach it.
docker stop (SIGTERM) shuts the proxy down gracefully: it stops accepting connections, gives open connections up to 5 seconds to finish, then closes them and exits with code 0. Ctrl-C (SIGINT) does the same. Docker kills the container if it hasn't exited by the stop timeout, so keep that above 5 seconds: Docker Engine's default is 10, but some Docker Desktop versions use less. Run with --stop-timeout 10 or stop with docker stop -t 10 to be sure.
Authentication is optional and off by default. To require it, set credentials and SOCKS5_AUTH_REQUIRED=true : Authentication is optional and off by default. With authentication off and the server listening on a non-loopback address, anyone who can reach the port can relay traffic through the proxy, and that traffic appears to come from your IP address. The Docker image listens on 0.0.0.0 , so a plain docker run -p 1080:1080 jcaponigro20/simple-socks5 on a public host is an open proxy.
The warnings are shown at -L debug , info and warning . They are hidden at error and critical , and nothing is printed at -L disabled or with the :logging-disabled image. Bind or publish the port only where you need it, e.g. -p 127.0.0.1:1080:1080 or a specific LAN address ( -p 192.168.1.10:1080:1080 ). Ports published by Docker bypass host firewalls such as ufw. Never expose the proxy to the internet without authentication.
The check is made on each resolved IP address just before connecting to it, so localhost and names that resolve or rebind to these addresses are refused too. A refused address is skipped and the name's next address is tried. A CONNECT whose addresses are all refused gets reply 0x02 (connection not allowed by ruleset), and a WARNING naming the client, the destination and SOCKS5_ALLOW_LOOPBACK is logged at most every 10 seconds. A refused UDP datagram is dropped and logged at DEBUG; the association stays open. Private ranges ( 10.0.0.0/8 , 172.16.0.0/12 , 192.168.0.0/16 , fc00::/7 ) and public addresses are allowed, so the proxy and other services stay reachable on the host's or container's own non-loopback addresses. A request with an empty domain name gets 0x04 (host unreachable).
With the Docker image on its default bridge network nothing changes for you: the container's loopback is the container itself, and services on the host are reached through a private address such as host.docker.internal . If you run the proxy directly on a host, or with --network host , and proxy to services on localhost , set SOCKS5_ALLOW_LOOPBACK=true . It lifts the whole policy above.
Data is transmitted in cleartext, including authentication credentials. Use additional encryption (e.g., SSH tunnel, VPN) in environments where interception is a risk. A simple SOCKS Protocol Version 5 implementation in Python using only the standard library (no external deps). A secure web proxy server can enhance privacy and security when browsing the internet. In this article, we will learn how to create a Python-based secure web proxy server using the SOCKS5 protocol. SOCKS5 is a versatile and widely-used protocol that supports various applications.
Please note that this is a basic example and may require additional security features for production use. Always follow best practices to ensure a secure environment. Here’s an in-depth guide on best practices for secure coding in Python . A proxy server acts as an intermediary between a client (like a web browser) and the internet. It receives requests from clients and forwards them to the target server. This setup helps hide the client’s identity and location, thus improving privacy.
SOCKS5 is a popular proxy protocol that allows secure and flexible communication between clients and servers. It supports various authentication methods and is widely used in networking applications. Ensure you have Python installed on your system. Additionally, we’ll use the ‘pysocks’ library to handle SOCKS5 connections. Install it via pip: Create proxy_server.py file in your project directory. We’ll be writing all of our code here.
3. Software Implementation, Frameworks & Protocols We need to import the required libraries before diving into the code. We’ll use ‘socket’ for network communication and ‘threading’ for handling multiple client connections. Next, we’ll set up the proxy server with a chosen IP address and port. Replace ‘proxy_ip’ and ‘proxy_port’ with your desired values.
Now, we’ll define a function to handle incoming client connections. This function will read client requests, forward them to the target server, receive the server’s response, and send it back to the client. Now, let’s create the main function to set up the proxy server, listen for incoming connections, and handle them using the previously defined function.
Run the proxy_server.py file to start the proxy server. Once it’s running, you can configure your web browser or other applications to use the proxy server at the specified IP address and port. Congratulations! You’ve successfully built a Python-based secure web proxy server using the SOCKS5 protocol. This proxy server enhances privacy and security while browsing the internet.
A complete developer guide to using SOCKS5 proxies in Python — authenticated and rotating setups with requests and aiohttp, socks5h DNS, and troubleshooting. SOCKS5 is the proxy protocol of choice for developers who need speed, flexibility, and protocol-agnostic routing. Unlike HTTP proxies, SOCKS5 can tunnel any kind of traffic — HTTP, HTTPS, WebSockets, even raw TCP — which makes it a favorite for scraping, automation, and privacy tooling in Python.
Yet SOCKS5 trips up a surprising number of developers. A missing dependency, the wrong URL scheme, or a subtle DNS-leak bug can silently break your setup or expose your real IP. As of 2026 , SOCKS5 remains one of the most-searched proxy topics among Python developers precisely because the details matter. This guide shows you exactly how to use SOCKS5 proxies in Python — from a basic request to authenticated, rotating, and async setups with requests and aiohttp — plus how to avoid DNS leaks and fix the most common errors. Every snippet is copy-paste ready.
SOCKS5 is the fifth version of the SOCKS (Socket Secure) protocol. It operates at a lower level than HTTP proxies, forwarding packets between your client and the destination without inspecting or modifying the application-layer data. That makes it protocol-agnostic : it works for web traffic, email, P2P, gaming, and any TCP or UDP connection. SOCKS5 also adds authentication support and, crucially, the ability to resolve DNS on the proxy side rather than locally.
Combined with the trust of a residential proxy , SOCKS5 gives you a fast, flexible, low-detection tunnel — ideal for Python scraping and automation. Python developers reach for SOCKS5 for three reasons. First, versatility — the same proxy works across libraries and protocols, not just HTTP. Second, performance — because SOCKS5 does not parse application data, it adds minimal overhead. Third, privacy — with remote DNS resolution it prevents the DNS leaks that can expose your real location even when your traffic is proxied.
For scraping and automation specifically, SOCKS5 pairs perfectly with rotating residential pools, letting you spread requests across many exit IPs while keeping a single, consistent client configuration. It is a core building block for any serious web scraping with Python project. You will need Python 3.7+ and a SOCKS5 proxy endpoint (host, port, and optionally a username and password). Most providers give you these in the format host:port:username:password . The standard requests library does not support SOCKS out of the box, so the first step is installing the right extension.
Follow these steps in order — each builds on the last, from a basic request to a production-ready async, rotating setup. Point both the http and https keys at your SOCKS5 endpoint using the socks5:// scheme. Most commercial SOCKS5 proxies require credentials. Embed them directly in the proxy URL. This is the step most developers miss. The plain socks5:// scheme resolves DNS locally, which can leak the hostnames you visit. Use socks5h:// instead to resolve DNS through the proxy.
For multiple requests through the same proxy, a session reuses the underlying connection and is far more efficient. Spreading requests across many exit IPs keeps you from being rate-limited. Pick a random proxy per request. For high-throughput scraping, go async. The aiohttp_socks connector adds SOCKS5 support to aiohttp. That covers the full range — basic, authenticated, leak-proof, pooled, rotating, and async. For more on credentials, see our guide to proxy authentication methods .
Before relying on a SOCKS5 setup in production, confirm it actually changes your exit IP. Compare a direct request against a proxied one — if the IPs match, your proxy is not being used. Run this as a quick health check whenever you add new proxies or debug a setup. For a deeper check of speed and anonymity, our proxy testing guide walks through the full process.
Should you use SOCKS5 or an HTTP proxy? Here is how they compare for Python workloads. SOCKS5 is not limited to requests. Here is how to enable it in the most popular Python HTTP clients. Your code is only as good as the proxies behind it. These three providers offer reliable SOCKS5 endpoints that work seamlessly with the setups above.
IPRoyal offers SOCKS5 support across its ethically sourced residential network, with pay-as-you-go traffic that never expires — ideal for developers who want flexible, affordable SOCKS5 without a big commitment. Coverage spans 195 countries with both HTTP and SOCKS5 protocols. Its simple credential-based authentication drops straight into the Python examples above, making it a great starting point for SOCKS5 scraping and automation projects.
4. Practical Deployment, Analysis & Case Studies PyProxy is a standout for SOCKS5 specifically, selling SOCKS5 by the IP at some of the lowest unit prices on the market and offering a dedicated S5 client popular with automation and multi-accounting users. It is a natural fit for developers who need large volumes of SOCKS5 endpoints.
With city, state, and ASN-level targeting on its residential plans, PyProxy gives Python developers fine-grained control over exit locations at a budget-friendly price. Decodo (formerly Smartproxy) pairs SOCKS5 support with a huge 115M+ residential pool, 99.99% uptime, and a beginner-friendly dashboard. Its high success rates and clean documentation make it easy to get SOCKS5 working in Python quickly.
For developers who want premium reliability without enterprise complexity, Decodo is an excellent SOCKS5 choice. Browse more options in our proxy directory . SOCKS5 is not just a scraping tool. Here are the most common Python workflows that rely on it. The biggest use case. SOCKS5 lets your scraper route requests through residential exit IPs, spreading load across a rotating pool so target sites see ordinary visitors rather than one hammering address. Paired with requests or aiohttp, it keeps success rates high on protected sites while adding minimal latency.
Bots that manage multiple accounts assign each identity a distinct SOCKS5 exit IP so platforms cannot link them by network footprint. A sticky SOCKS5 endpoint per account keeps the IP stable across a session, which is essential for avoiding the bans that come from sharing one address across profiles. Because SOCKS5 with remote DNS hides both your IP and the hostnames you resolve, it is a building block for privacy scripts, research tools, and anything that must not expose the operator's location. The socks5h scheme is what makes this leak-resistant.
Unlike HTTP proxies, SOCKS5 can tunnel any TCP traffic, so Python tools that speak non-HTTP protocols — torrent clients, custom socket apps, database connectors — can all route through the same SOCKS5 endpoint without protocol-specific workarounds. Browser automation frameworks can also route through SOCKS5, with one important caveat: most Chromium-based engines do not support SOCKS5 username and password authentication. For authenticated proxies, use IP whitelisting in your provider dashboard, or run a local proxy bridge that handles the credentials.
Selenium follows the same pattern via a Chrome option: --proxy-server=socks5://proxy.example.com:1080 . Because of the auth limitation, residential providers that support IP whitelisting are the smoothest fit for browser automation. For driving headless browsers at scale, our web scraping with Python guide goes deeper. Most SOCKS5 problems come down to a handful of recurring mistakes. Here is how to diagnose and fix them.
This error means PySocks is not installed. Run pip install requests[socks] pysocks and restart your interpreter. The bracketed extra is required even if you think requests is already installed. If a leak test still shows your real location, you are almost certainly using socks5:// instead of socks5h:// . The h forces DNS resolution through the proxy. Always use socks5h:// for privacy-sensitive work and verify with a proxy speed and anonymity test .
Timeouts usually mean a dead proxy, wrong port, or an overloaded endpoint. Always set an explicit timeout , wrap requests in try/except, and rotate to a fresh proxy on failure rather than retrying the same dead IP repeatedly. This means your credentials are missing or wrong. Double-check the username and password in the proxy URL, ensure special characters are URL-encoded, and confirm your IP is whitelisted if the provider uses IP-based authentication.
If requests are sluggish, reuse a session instead of creating a new connection each time, run requests asynchronously with aiohttp for concurrency, and choose a provider with low latency. For high-volume jobs, see our guide on building a rotating proxy script in Python . Always use socks5h — Resolve DNS through the proxy to prevent leaks unless you have a specific reason not to.
Set timeouts everywhere — Never make a proxied request without an explicit timeout to avoid hanging on dead proxies. Reuse sessions — Pool connections for repeated requests to the same endpoint for better performance. Rotate and retry — Cycle through a pool and fail over to a fresh IP on errors instead of hammering one proxy. Verify your exit IP — Periodically hit an IP-echo endpoint to confirm rotation is working and your real IP is hidden.
SOCKS5 gives Python developers a fast, versatile, protocol-agnostic way to route traffic — but the details make or break it. Install requests[socks] , prefer socks5h:// to avoid DNS leaks, reuse sessions, rotate across a pool, and go async with aiohttp when you need throughput. With those patterns in place, SOCKS5 becomes a reliable foundation for scraping, automation, and privacy tooling. Pair your code with a quality residential SOCKS5 provider and you will have a setup that is both fast and hard to detect. The patterns in this guide scale from a single script to a distributed scraping fleet without changing the fundamentals.
Ready to build? Explore SOCKS5-ready providers in our proxy directory , compare options in our proxy comparison tool , or deepen your toolkit with our best residential proxies for web scraping guide. PySocks is a Python library for proxy support. It allows you to route network traffic through SOCKS or HTTP proxies. This guide will show you how to install and use it.
PySocks simplifies proxy usage in Python. It wraps the SOCKS4, SOCKS5, and HTTP proxy protocols. This makes it easy to integrate proxy support into your applications. You can install PySocks using pip. Run the following command in your terminal or command prompt. If you need help with pip, check our guide on how to install pytz in Python easily for similar steps.
After installation, import the library in your Python script. Use the set_default_proxy function to configure the proxy. 5. Performance Evaluation & Extended Technical Observations This code routes all socket traffic through a SOCKS5 proxy. Replace the IP and port with your proxy details. PySocks supports authentication for proxies. Use the set_default_proxy function with username and password.
This ensures secure proxy connections. For more on secure setups, see our Flask-Login installation guide . You can combine PySocks with the Requests library. First, install Requests if you haven't already. This sends HTTP requests through the proxy. It's useful for web scraping or API calls. Always handle proxy connection errors. Use try-except blocks to manage failures gracefully.
This prevents crashes if the proxy is unreachable. For more on testing, see Pytest-mock installation . PySocks is a powerful tool for proxy support in Python. It works with SOCKS and HTTP proxies. Follow this guide to integrate it into your projects. Remember to handle errors and secure your connections. For more Python guides, explore our other tutorials.
To understand what a proxy does, build one. This page implements an HTTP proxy and a SOCKS5 proxy from scratch in Python with asyncio, so you can see how each byte is parsed, where the security boundaries are, and why real proxy software makes the choices it does. To use a proxy with Pydoll rather than build one, see Proxies ; Pydoll also ships a SOCKS5Forwarder in pydoll.utils , so you don't have to build the authenticated-SOCKS5 case yourself.
These implementations favor clarity over robustness. They lack connection limits, access control, and many error-recovery paths a production proxy needs. Do not expose them to untrusted networks. An HTTP proxy operates in two modes. For plaintext HTTP, it receives the full request (with an absolute-form URL like GET http://example.com/path HTTP/1.1 ), rewrites the request-target to origin-form ( GET /path HTTP/1.1 ), connects to the target server, forwards the request, and pipes the response back. For HTTPS, the client sends a CONNECT host:port request, the proxy opens a TCP connection to the target, responds with 200 Connection Established , and then blindly relays bytes in both directions without inspecting the encrypted content.
The implementation below handles both modes. A few things to note as you read through it. The _pipe_data method calls write_eof() when one side closes, which sends a TCP FIN to the other side. Without this, the tunnel hangs indefinitely because the other read() never returns empty bytes. The HTTP forwarding path uses the same piping approach rather than a single read() call, because HTTP responses can be arbitrarily large and a fixed-size read would silently truncate them. The request-target rewrite preserves query strings, which urlparse().path alone would drop.
A few protocol details worth understanding. HTTP headers are encoded as ISO-8859-1 (Latin-1), not UTF-8. Latin-1 maps every byte value 0-255 to a character, so decode('latin-1') never raises a UnicodeDecodeError , while decode('utf-8') would crash on certain header values. The Proxy-Authorization header uses Base64 encoding, but Base64 is not encryption: the credentials travel in cleartext (or rather, trivially reversible encoding) unless the connection between client and proxy is itself protected by TLS. The hop-by-hop headers ( Connection , Keep-Alive , TE , Trailer , Upgrade , Proxy-Connection ) are meant for the immediate connection between two nodes, not for end-to-end forwarding. RFC 9110 Section 7.6.1 requires proxies to strip them before forwarding.
This implementation does not validate destination addresses. A client could request CONNECT 127.0.0.1:6379 to reach a local Redis instance, or CONNECT 169.254.169.254:80 to access cloud instance metadata (AWS, GCP, Azure). Any proxy exposed to untrusted clients must validate destinations against a deny list of private and link-local ranges ( 127.0.0.0/8 , 10.0.0.0/8 , 172.16.0.0/12 , 192.168.0.0/16 , 169.254.0.0/16 , ::1 , fc00::/7 ).
A SOCKS5 proxy operates at a lower level than HTTP. It uses a binary protocol defined in RFC 1928, consisting of three phases: method negotiation, optional authentication, and the connection request. The proxy does not parse HTTP at all. Once the tunnel is established, it relays raw bytes without understanding what protocol flows through it. The binary nature of SOCKS5 means every read must receive exactly the expected number of bytes. TCP is a stream protocol and does not guarantee that read(4) returns 4 bytes: it may return 1, 2, or 3 bytes depending on network conditions.
The implementation below uses readexactly() from asyncio, which buffers internally until the requested number of bytes arrives or the connection closes (raising IncompleteReadError ). When the address type is 0x03 (domain name), the proxy resolves DNS itself via asyncio.open_connection() . This is the defining privacy property of SOCKS5 proxying: the client sends the domain name rather than resolving it locally, which prevents DNS queries from leaking to the client's local network. This is the same behavior Chrome relies on when configured with --proxy-server=socks5://... , as discussed in SOCKS Proxies .
The _reply method fills BND.ADDR and BND.PORT with the actual local socket address after a successful connection, as RFC 1928 requires. Many SOCKS5 implementations return 0.0.0.0:0 here because most clients ignore these fields for CONNECT commands, but filling them correctly costs nothing and avoids a protocol violation. These implementations omit several things that production proxies handle. Understanding what is missing is as instructive as understanding what is present.
There are no connection limits. asyncio.start_server accepts connections without bound, so a single client opening thousands of connections would exhaust file descriptors. Production proxies use semaphores or connection pools to cap concurrency. There is no destination validation. Both proxies connect to whatever address the client requests, including 127.0.0.1 , 169.254.169.254 (cloud metadata), and internal network ranges. This is a Server-Side Request Forgery (SSRF) vector.
Production proxies maintain deny lists of private and link-local address ranges. There is no traffic logging or metrics. Production proxies track request counts, bytes transferred, error rates, and latency percentiles, typically exporting to Prometheus or similar systems. The HTTP proxy does not add a Via header. RFC 9110 Section 7.6.3 requires intermediaries to append a Via field to forwarded messages. This was omitted for simplicity, but a standards-compliant proxy must include it.
Neither proxy implements graceful shutdown. When the server stops, active tunnels are terminated abruptly rather than being drained. Production proxies track active connections and wait for them to complete (with a deadline) before shutting down. Chaining proxies means routing traffic through multiple proxies in sequence: client to proxy A, proxy A to proxy B, proxy B to the target server. Each proxy in the chain only knows its immediate neighbors, not the full path.
The main use case is distributing trust. If you do not fully trust any single proxy provider, chaining two providers means neither one sees both your real IP and your destination. The tradeoff is latency: each hop adds its own connection setup time and forwarding delay. A single proxy typically adds 50 to 100ms of overhead. Two proxies roughly double that, and three proxies can push total overhead past 300ms.
Beyond two hops, the marginal privacy gain diminishes while latency and failure probability increase. Most practical setups use one or two proxies. Tor uses three relays (guard, middle, exit) because its threat model assumes some relays are compromised, but Tor accepts the latency penalty as an explicit design tradeoff. Chaining a SOCKS5 proxy through another SOCKS5 proxy works by having proxy A treat proxy B as the target. The client connects to proxy A and sends a CONNECT request for proxy B's address. Once that tunnel is established, the client sends a second SOCKS5 handshake through the tunnel, this time requesting the real target. Proxy A sees traffic flowing to proxy B but cannot read it if the inner connection is encrypted.
A lightweight SOCKS5 proxy server in Python, implementing RFC 1928 with support for CONNECT, IPv4/domain addresses, and multi-client threading, plus Duke-network IP allowlisting. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/SOCKS • https://github.com/zfusx/simple-socks5-proxy • https://pypi.org/project/pysocks5server/ • https://pytutorial.com/python-socks5-proxy-implementation-with-httplib2-complete-guide/ • https://github.com/j0shcap/simple-socks5 • https://www.edopedia.com/blog/building-a-python-based-secure-web-proxy-server-with-socks5/ • https://www.proxyhorizon.com/blog/how-to-use-socks5-proxies-in-python • https://pytutorial.com/install-and-use-pysocks-for-proxy-support/ • https://pydoll.tech/docs/deep-dive/network/build-proxy/ • https://github.com/benita1024/SOCKS5-Proxy-Server
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Secure Socks5 Proxy Server Implementation In Python.
[*] Metasploit Scan Running on Target Subnet for Secure Socks5 Proxy Server Implementation In Python... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |