Complete Technical Paper Content — Secure Software Supply Chain Monitoring Tool In Devsecops
Overview & System Context
Secure Software Supply Chain Monitoring Tool In Devsecops: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9503 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background The Microsoft Security Development Lifecycle (SDL) is the approach Microsoft uses to integrate security into DevOps processes (sometimes called a DevSecOps approach). The SDL guidance and documentation can be used to adapt these practices to other organizations.
Software – whether you are developing software code for firmware, AI applications, operating systems, drivers, IoT Devices, mobile device apps, web services, plug-ins or applets, hardware microcode, low-code/no-code apps, or other software formats. Note that most practices in the SDL are applicable to secure computer hardware development as well. Platforms – whether the software is running on a ‘serverless’ platform approach, on an on-premises server, a mobile device, a cloud hosted VM, a user endpoint, as part of a Software as a Service (SaaS) application, a cloud edge device, an IoT device, or anywhere else.
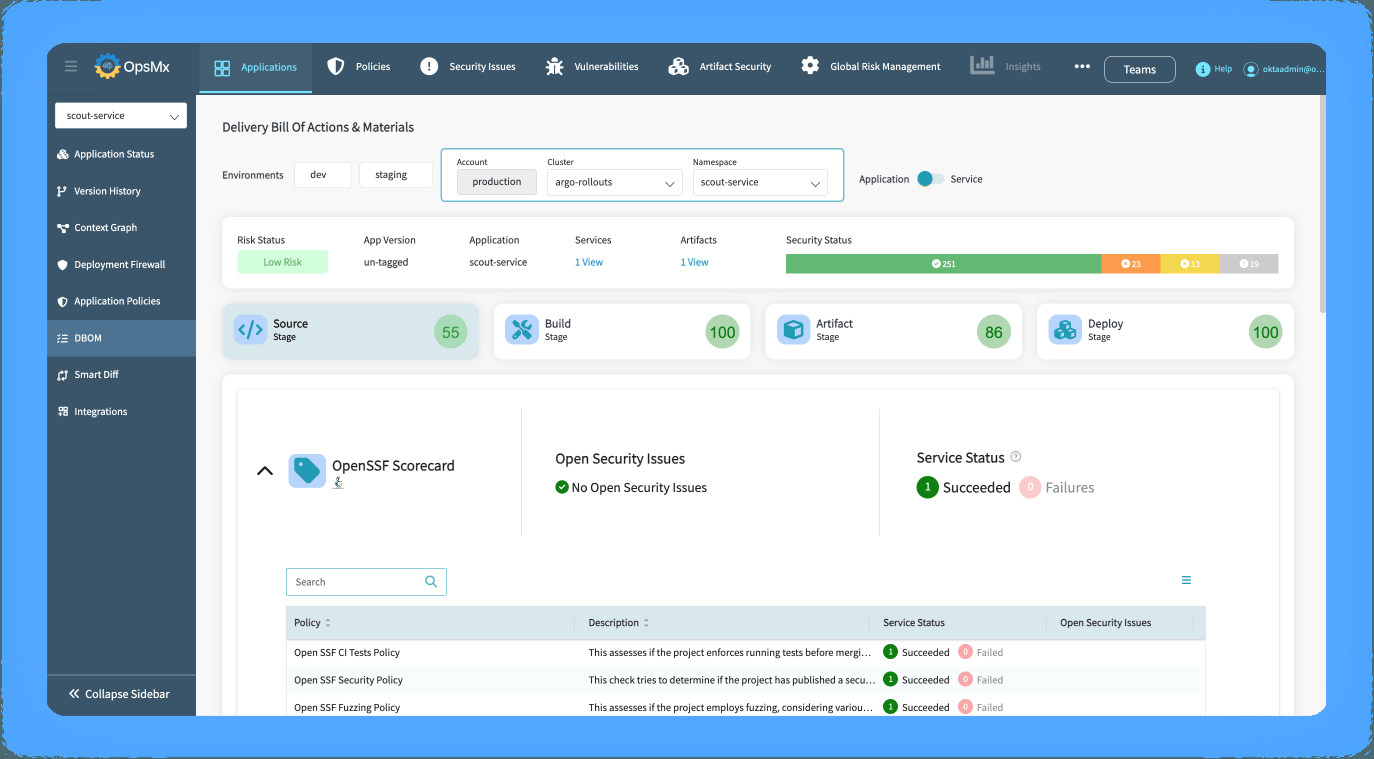
Establish security standards, metrics, and governance Require use of proven security features, languages, and frameworks Perform security design review and threat modeling Define and use cryptography standards Secure the software supply chain Secure the engineering environment Perform security testing Ensure operational platform security Implement security monitoring and response Provide security training In the computer security or Information security fields, there are a number of tracks a professional can take to demonstrate qualifications. Four sources categorizing these, and many other credentials, licenses, and certifications, are: Figure 1: OpsMx DevSecOps for Delivery Module | OpsMx Delivery Flow Schools and universities Vendor-sponsored credentials (e.g. Microsoft, Cisco) Association- and organization-sponsored credentials Governmental (or quasi-governmental) licenses, certifications, and credentials Quality and acceptance vary worldwide for IT security credentials, from well-known and high-quality examples like a master's degree in the field from an accredited school, CISSP, and Microsoft certification, to a controversial list of many dozens of lesser-known credentials and organizations. In addition to certification obtained by taking courses and/or passing exams (and in the case of CISSP and others noted below, demonstrating experience and/or being recommended or given a reference from an existing credential holder), award certificates also are given for winning government, university or industry-sponsored competitions, including team competitions and contests.
Microsoft 1 year *: you have to do a free refresh exam within 180 days before expiration. if not done, the certificate expire otherwise it extends by 1 year. DevSecOps tools are automated applications that embed security testing into the development lifecycle to protect the software supply chain.
DevSecOps tools are applications designed to embed continuous security testing within the development, security, and operations (DevSecOps) lifecycle. These platforms replace manual audits with automated vulnerability scanning and policy checks inside the delivery pipeline. By catching code flaws before deployment, this strategy minimizes corporate risk and lowers remediation costs.
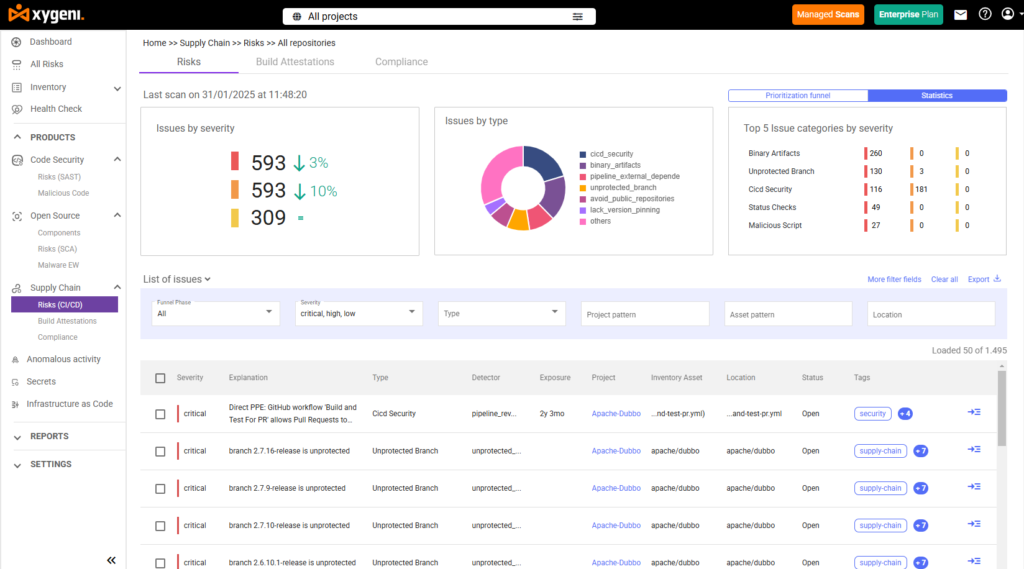
Figure 2: Software Supply Chain Security Automation | Xygeni DevSecOps tools transform security from a final deployment bottleneck into a continuous, automated mechanism embedded directly within the DevOps pipeline. Because DevSecOps has a broader scope than application code alone—encompassing infrastructure security, compliance automation, and operational security practices—these tools must secure multiple layers of the software supply chain.
Within this comprehensive approach, Application Security (AppSec) serves as a key pillar. By extending standard workflows with specialized AppSec capabilities, such as vulnerability scanning, policy enforcement, and artifact integrity checks, DevSecOps tools secure the delivery lifecycle without degrading release velocity. No single tool covers all of DevSecOps. The discipline requires a coordinated ecosystem of capabilities that act proactively on source code, infrastructure configurations, dependencies, and binaries the moment they are created or modified.
Mapping a DevSecOps framework to the Software development lifecycle (SDLC) ensures that AppSec testing and policy enforcement occur contextually as code progresses from the developer’s workstation to the production environment. This lifecycle-aligned strategy relies on distinct categories of tooling tailored for planning, building, testing, deploying, and observing software.
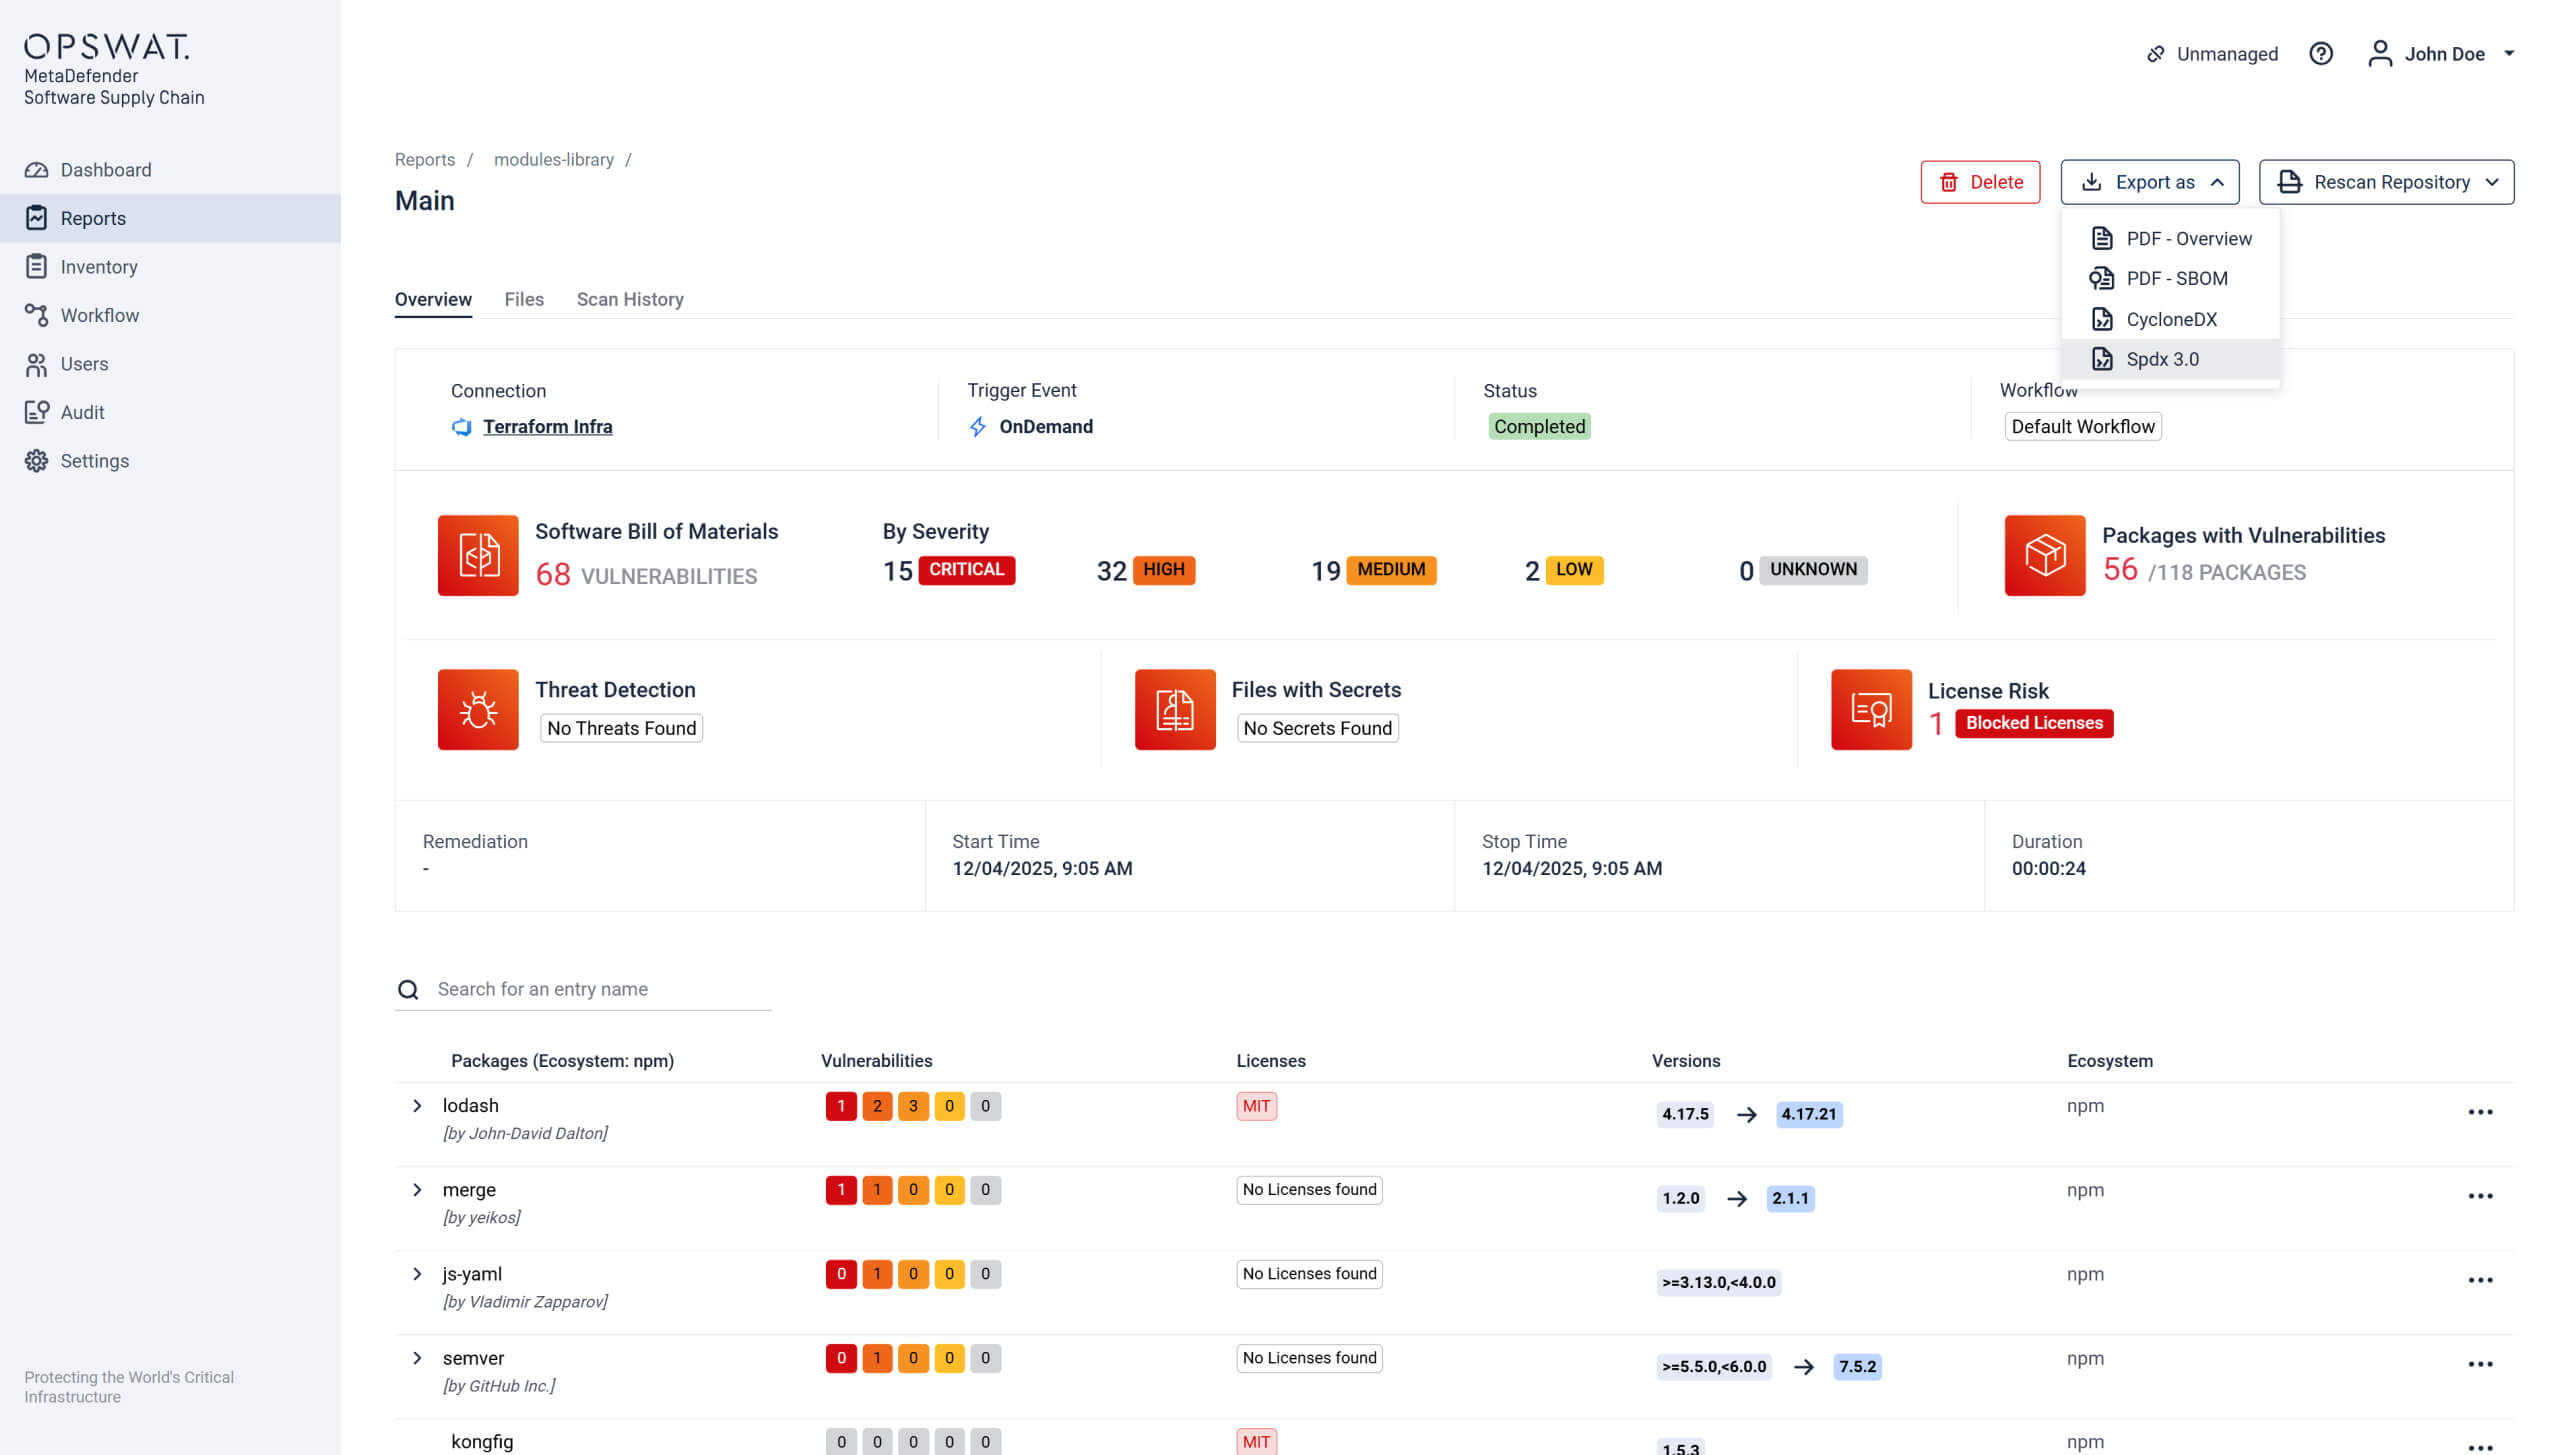
Figure 3: MetaDefender Software Chain™ v3.1.0: IIII IIIIII IIIIIII DevSecOps ... During the initial phases of development, security requirements must be codified alongside functional requirements. As source code is compiled and dependencies are resolved, the toolchain must validate the integrity and safety of all inputs. Testing verifies that compiled applications and their execution environments are resistant to active exploits.
Deployment mechanisms must act as rigid security gates that prevent non-compliant software from reaching production. Post-deployment, continuous monitoring is required to identify zero-day threats and operational anomalies in live environments. A well-architected DevSecOps platform relies on a specific taxonomy of tools, each addressing distinct Application Security vectors.
While active scanning and testing frequently dominate conversations surrounding DevSecOps tools, the artifact repository acts as the fundamental connective tissue of the entire toolchain. If the central store for build outputs is not secure, immutable, and strictly governed, all downstream security controls are inherently compromised. Every tool in the AppSec pipeline interacts directly with artifacts. SCA scanners inspect them, SAST runs against their underlying source, DAST evaluates what they produce, and deployment gates manage their promotion. An ungoverned artifact store undermines every other security control, as mutable tags, unsigned binaries, and uncontrolled access create critical risks that traditional scanners cannot catch. A mature artifact management layer guarantees immutable storage, rigorous access control, cryptographic signing, SBOM attachment, and structured promotion workflows. Advanced supply chain security platforms build upon this foundation to provide continuous scanning, strict license policy enforcement, and malicious package detection across all artifact types.
Selecting the right components for a DevSecOps platform requires evaluating tools against strict technical criteria to ensure true risk reduction rather than superficial compliance. A practical evaluation framework prevents the adoption of siloed tools that generate alert fatigue or create a false sense of security. Because no single tool covers the entirety of AppSec, organizations must architect a coordinated set of capabilities designed to minimize security blind spots and operational overlaps. The objective is a unified DevSecOps framework that provides seamless traceability and automated enforcement from code commit to production deployment.
Start with the artifact layer; a strictly governed binary repository forms the foundation that every other security tool relies upon. Ensure you instrument every phase of the pipeline, as coverage gaps in Plan, Build, Test, Deploy, or Observe create highly exploitable blind spots. Automate enforcement mechanisms wherever possible, because tools that merely alert without blocking create severe alert fatigue without tangibly reducing risk. Finally, build toward full traceability, keeping the end goal focused on a one-click trace from any production issue directly back to the specific commit, dependency, build, and approval that caused it.
DevSecOps tools are not an isolated checklist; they form an interconnected ecosystem that must operate cohesively across the full SDLC to effectively secure modern application delivery. By establishing a governed artifact repository as the foundational layer, organizations close critical supply chain gaps that attackers frequently exploit, maximizing the value of continuous scanning and testing.
Transitioning from fragmented security tools to a unified DevSecOps framework requires robust infrastructure capable of securing every binary, container, and dependency. The JFrog Platform empowers you with end-to-end visibility, security, and control for automating delivery of trusted releases. By providing immutable storage, continuous vulnerability scanning, and automated policy enforcement, JFrog ensures that only thoroughly verified, compliant software reaches your production environments.
A comprehensive open-source curation solution for blocking malicious packages from entering your organization. A module in the JFrog platform ensuring early detection and remediation or potential vulnerabilities at all stages of the SDLC. A unified security solution that protects software artifacts against threats that are not discoverable by siloed security tools. No piece of software is developed in a vacuum; regardless of the technologies used to develop it, software is embedded in a Software Supply Chain (SSC). According to NIST , an entity's SSC can be defined as "a collection of steps that create, transform, and assess the quality and policy conformance of software artifacts". From a developer's perspective, these steps span the entire SDLC and are accomplished using a wide range of components and tools. Common examples (by no means exhaustive) of components that are especially relevant from a developer's perspective include: Each of these components must be secured; a flaw in a single component, such as a vulnerable third-party dependency or misconfigured VCS, can put an entire SSC in jeopardy. Thus, in order to strengthen Software Supply Chain Security (SCSS), developers should possess a general understanding of what the SSC is, common threats against it, and practices and techniques that can be applied to reduce SSC risk.
Given the breadth and complexity of the SSC, it is unsurprising that the threat landscape for SSC is similarly expansive. Threats include dependency confusion , compromise of an upstream providers infrastructure, theft of code signing certificates, and CI/CD system exploits. More broadly, threats may be grouped into four categories based upon what component of the supply chain they seek to compromise ( Google supply-chain threat categories , SLSA 1.0 threats ): The characteristics of threat actors seeking to exploit the SSC are similarly diverse. Although SSC compromise is often associated with highly sophisticated threat actors, such sophistication is not inherently necessary for attacking the SSC, especially if the attack focuses on compromising the SSC of entities with poor security practices. Threat actor motive also varies widely. A SSC exploit can result in loss of confidentiality, integrity, and/or availability of any organization's assets and thus fulfill a wide range of attacker goals such as espionage or financial gain.
Finally, it must be recognized that many SSC threats have the capability to propagate across many entities. This is due to the consumer-supplier relationship that is integral to an SSC. For example, if a large-scale software supplier, whether proprietary or open-source, is compromised, many downstream consuming entities could also be impacted as a result. The 2020 SolarWinds and 2021 Codecov incidents are excellent real-world examples of this.
Mitigating SSC related risk can seem daunting, yet it need not be. Even for sophisticated attacks that may focus on compromising upstream suppliers, individual organization can take reasonable steps to defend its own assets and mitigate risk even if its supplier is compromised. Although some parts of SSCS may remain outside direct control of development teams, those teams must still do their part to improve SSCS in their organization; the guidance below is intended as starting point for developers to do just that.
The practices described below are general techniques that can be used to mitigate risk related to a wide variety of threat types. Compromised accounts, particularly privileged ones, represents a significant threats to SSCs. Account takeover can allow an attacker can perform a variety of malicious acts including injecting code into legitimate dependencies, manipulating CI/CD pipeline execution, and replacing a benign artifact with a malicious one. Strong access control for build, development, version control, and similar environments is thus critical. Best practices include adhering to the basic security principles of least privileges and separation of duties, enforcing MFA, rotating credentials, and ensuring credentials are never stored or transmitted in clear text or committed to source control.
When considering SSCS, the importance of detective controls should not be overlooked; these controls are essential for detecting attacks and enabling prompt respond. In the context of SSCS, logging is critical. All systems involved in the SSC, including VCS, build tools, delivery mechanisms, artifact repositories, and the systems responsible for running applications should be configured to log authentication attempts, configuration changes, and other events that could assist in identifying anomalous behavior or that could prove crucial for incident response efforts. Logs throughout the SSC must be sufficient in both depth and breadth to support detection and response However, logging events is not sufficient. These logs must be monitored, and, if necessary, acted upon. A centralized SIEM, log aggregator, or similar tool is preferred, especially given the complexity of SSCs. Regardless of the technology used, the basic objective remains the same: log data should be actionable.
For complex SSCs, automation of security tasks, such as scanning, monitoring, and testing is critical. Such automation, while not a replacement for manual reviews and other actions performed by skilled professionals, is capable of detecting, and in some cases responding to, vulnerabilities and potential attacks with a scale and consistency that is hard to achieve through manual human intervention. Types of tools that support automation include SAST, DAST, SCA, container image scanners and more. The exact tools most capable of delivering value to an organization will vary significantly based on the characteristics of the organization. However, regardless of the type of tools and vendors used, it is important to acknowledge that these tools themselves must be mainlined, secured, and configured correctly. Failure to do so could actually increase SSC risk for an organization, or at the very least, fail to bring meaningful benefit to the organization. Finally, it must be clearly understood that these tools are but one component of an overall SSCS program; they cannot be considered a comprehensive solution or be relied on to identify all vulnerabilities.
The practices described below can help reduce SSC risk associated with source code and development. Manual code reviews are an important, relatively low cost technique for reducing SSC risk; these reviews can act as both detective controls and deterrents. Reviews should be performed by peers possessing both experience in the technology being used and secure coding processes and should occur before code is merged within a source control systems ( Google source safeguards ). The reviews should look for both unintentional security flaws as well as intentional code that could serve malicious purposes. The results of the review should be documented for later review if needed.
2. System Architecture & Core Working Principles Compromise or abuse of the source control system is consistently recognized as a significant SSC risk ( Google supply-chain threat categories , SLSA 1.0 threats ). The general security best practices of strong access control and logging and monitoring are two methods to help secure VCS. Security features specific to the VCS system, such as protected branches and merge policies in git, should also be leveraged. You can find a wide variety of recommended policies in this documentation . There are tools available to help manage configuration of SCM systems, such as Legitify , an open-source tool by Legit security .
Legitify is designed to detect misconfigurations in GitHub and GitLab and assist with the implementation of best practices. Regardless of any security controls added a VCS, it must be remember that secrets should never be committed to these systems. IDEs, development plugins, and similar tools can help assist the development process. However, like all pieces of software, these components can have vulnerabilities and become an attack vector. Thus, it is important to take steps not only to ensure these tools are used securely, but also to secure the underlying system. The development system should have endpoint security software installed and should have threat assessments performed against it ( ESF developer practices ). Only trusted, well-vetted software should be used in the development process; this includes not only "core" development tools such as IDEs, but also any plugins or extensions. Additionally, these tools should be included as part of an organization's system inventory.
Best practices and techniques related to secure use of dependencies are described below. Before incorporating a third-party service, product, or software component into the SSC, the vendor and specific offering should both be thoroughly assessed for security. This applies to both open-source and proprietary offerings. The form and extent of the analysis will vary substantially in accordance with both the criticality and nature of the component being considered. Component maturity, security history, and the vendor's response to past vulnerabilities are useful information in nearly any case. For larger vendors or service offerings, determining whether or not a solution has been evaluated against third-party assessments and certifications, such as those performed against FedRAMP , CSA , or various ISO standards (ISO/IEC 27001, ISO/IEC 15408, ISO/IEC 27034), can be a useful data point, but must not be relied on exclusively.
Due to its transparent nature, open-source projects offer additional assessment opportunities. Questions to consider include ( OpenSSF component evaluation ): While third-party software dependencies can greatly accelerate the development process, they are also one of the leading risks associated with modern applications. Dependencies must not only be carefully selected before they are incorporated into an application, but also carefully monitored and maintained throughout the SDLC. In order achieve this, having insight into the various dependencies consumed by software is a crucial first step. To facilitate this, SBOMs may be used. Both production and consumption of these SBOMs should be automated, preferably as part of the organization's CI/CD process.
Once the organization has inventoried dependencies, it must also monitor them for known vulnerabilities. This should also be automated as much as possible; tools such as OWASP Dependency Check or retire.js can assist in this process. Additionally, sources such as the NVD , OSVDB , or CISA KEV catalog may also be monitored for known vulnerabilities related to dependencies used in the organization's SSC.
Although using SAST to detect potential security in custom developed code is a widely used security technique, it can also be used on OSS components within the SSC ( ESF developer practices ). As when using SAST on internally developed code, one must recognize that these tools can produce both false positives and false negatives. Thus, SAST results must not be accepted without manual verification and should not be interpreted as providing a comprehensive view of the project's security. However, as long as their limitations are understood, SAST scans can prove useful when analyzing both internally developed or OSS code.
To reduce the likelihood that a compromised or vulnerable version is unwittingly pulled into an application, one should limit the applications dependencies to a specific version that has been previously verified as legitimate and secure. This is commonly accomplished using lockfiles such as the package-lock.json file used by npm. The section below describes techniques that are especially relevant for securing build related threats.
Knowing the components used in the SSC is essential to the security of that SSC. This concept extends to build tools. An inventory of all build tools, including versions and any plugins, should be automatically collected and mainlined, One must also monitor vulnerability databases, vendor security advisories and other sources for any vulnerabilities related to the identified build tools.
Compromised build tools can enable a wide range of exploits and thus represent an appealing target for attackers. As such, all infrastructure and tools used in build process must be hardened to mitigate risk. Techniques for hardening build environments include ( ESF developer practices ): From a the perspective of software consumers, only accepting components which have been digitally signed and validating the signature before utilizing the software is an important task step in ensuring the component is authentic and has not been tampered with. For those performing code signing, it is imperative that the code signing infrastructure is thoroughly hardened.
Failure to do so can result in compromise of the code signing system and lead further exploits, including those targeting consumers of the software. Using a private artifact repository increases the control an organization has over the various artifacts that are used within the SSC. Artifacts should be reviewed before being allowed in the private repository and organizations must ensure that usage of these repositories cannot be bypassed. Although usage of private repositories can introduce extra maintenance or reduce agility, they can also be an important component of SSCS, especially for sensitive or critical applications.
The benefits of VCSs can be realized for items beyond source control; this is especially true for config and scripts related to CI/CD pipelines. Enforcing version control for these files allows one to incorporate reviews, merge rules, and like controls into the config update process. Using VCS also increase visibility, allowing one easy visibility into any changes introduced, whether malicious or benign ( ESF developer practices ).
Having assurance that an SSC component comes from a trusted source and has not been tampered with is a important part of SSCS. Generation and consumption of provenance, defined in SLSA 1.0 as "the verifiable information about software artifacts describing where, when and how something was produced" is an important part of this. The provenance should be generated by the build platform (as opposed to a local development system), be very difficult for attackers to forge, and contain all details necessary to accurately link the result back to the builder ( SLSA 1.0 provenance requirements ). SLSA 1.0 compliant provenance can be generated using builders such as FRSCA or Github Actions and verified using SLSA Verifier Reuse and sharing of build environments may allow attackers to perform cache poising or otherwise more readily inject malicious code. Builds should be performed in isolated, temporary ("ephemeral") environments. This can be achieved using technologies such as VMs or containers for builds and ensuring the environment is immediately destroyed afterward.
Although passing user controllable parameters to a build process can increase flexibility, it also increases risk. If parameters can be modified by users in order to alter how a build is performed, an attacker with sufficient permission will also be able to modify the parameters and potentially compromise the build process ( Google build safeguards ). One should thus make an effort to minimize or eliminate any user controllable build parameters.
The section below outlines a couple of techniques that can be used to protect software during the deployment and runtime phases. Once the build process has finished, one should not simply assume that the final result is secure. Binary composition analysis can help detect exposed secrets, detect unauthorized components or content, and verify integrity ( ESF developer practices ).
This task should be performed by both suppliers and consumers. SSCS does not end with the deployment of the software; the deployed software must be monitored and maintained to reduce risk. New vulnerabilities, whether introduced due to an update or simply newly discovered (or made public), are a continual concern in software systems ( Google supply-chain threat categories ). When performing this monitoring, a wholistic approached must be used; code dependencies, container images, web servers, and operating system components are just a sampling of items that must be consider. To support this monitoring, an accurate and up-to-date inventory of system components is critical. Additionally, insecure configuration changes must be monitored and acted upon.
Sixty-one percent of organizations experienced a software supply chain attack in 2025, according to the Sonatype State of the Software Supply Chain report. Most of those attacks did not exploit zero-days. They walked right through unguarded CI/CD pipelines, untrusted dependencies, and plaintext secrets committed to version control. If your pipeline is just running unit tests and deploying artifacts, you are not running a DevSecOps pipeline. You are running a conveyor belt that ships vulnerabilities faster.
The shift to DevSecOps is not a cultural rebranding exercise. It is an architectural commitment to embedding security controls at every stage of the software development lifecycle, from the first git commit to the final container running in production. Done right, it compresses the time-to-detect and time-to-remediate vulnerabilities from weeks down to minutes. Done wrong, it becomes security theater: a checkmark on a compliance form while actual risk accumulates in your artifact registry.
This guide covers what a production-grade DevSecOps pipeline actually looks like in 2026, including the tools, the gate logic, the SBOM strategy, the secret scanning posture, and the supply chain controls that separate serious engineering teams from everyone else. Think of a DevSecOps pipeline as a series of security gates layered over your existing CI/CD workflow. Each gate has a defined failure condition, a defined severity threshold, and a clearly owned remediation path. The moment a gate becomes optional or routinely bypassed, the pipeline integrity collapses.
A production-grade pipeline in 2026 typically spans these stages: pre-commit hooks, pull request analysis, CI build-time scanning, artifact signing and SBOM generation, staging environment dynamic testing, and post-deployment runtime monitoring. That is not a suggestion. That is the minimum viable security surface for any team handling sensitive data or operating in a regulated environment.
Shift-left security starts before code ever reaches a repository. Pre-commit hooks using tools like the pre-commit framework or Husky enforce baseline checks locally: secret detection, license compliance flags, and basic linting for obvious misconfigurations. The cost of catching a hardcoded AWS access key in a pre-commit hook is essentially zero. The cost of catching it after it has been pushed to a public repository and scraped by a credential harvesting bot is, historically, catastrophic.
IDE plugins from vendors like Snyk, Semgrep, and SonarQube bring SAST feedback directly into the developer editor. This is not just convenience. It closes the feedback loop to the point where secure coding practices become the path of least resistance. Developers are not context-switching to a separate security portal. They are seeing inline warnings as they type. That is the behavioral change that actually moves the needle on security outcomes.
Static Application Security Testing lives in the CI build phase. Your SAST tool analyzes source code or compiled bytecode for vulnerability patterns, including injection flaws, insecure deserialization, improper error handling, and the rest of the OWASP Top 10 and CWE Top 25. The key decision is not which SAST tool to use. It is how you configure your quality gates. A SAST scan that blocks the pipeline on every low-severity finding will be disabled by a frustrated developer within a week.
Gate on Critical and High findings with a CVSS score above 7.0 or an EPSS score above 0.5. Let Medium findings generate tickets and trend reports without blocking merges. Low findings belong in a separate backlog reviewed quarterly. This triage logic is what separates a functional security program from alert fatigue. Semgrep, CodeQL, and Checkmarx dominate the enterprise SAST space in 2026. For teams using SAST capabilities within the Secrails platform , the advantage is tight integration with the rest of the security posture. Findings from static analysis correlate directly with runtime observations and infrastructure misconfigurations, giving you actual exploitability context rather than just raw vulnerability counts.
Dynamic Application Security Testing runs against a live application, typically in a staging environment. DAST tools like OWASP ZAP, Burp Suite Enterprise, and Invicti probe running services for authentication bypasses, injection endpoints, misconfigured CORS policies, and business logic flaws that static analysis fundamentally cannot detect. DAST is also where API security testing becomes critical. REST and GraphQL APIs are the attack surface most teams underinvest in scanning, and they are where attackers are spending their time in 2026.
Full DAST scans can take hours. Running them on every commit is impractical. The pragmatic approach is to run a fast, targeted DAST scan on every PR merge to the main branch, focusing on changed endpoints and taking fifteen to twenty minutes, then run a full deep scan nightly or before every release candidate. This keeps the feedback loop tight without making developers wait half a day for a green light.
Secrets, including API keys, database credentials, OAuth tokens, and private certificates, have no business being in source code, ever. Yet Gitguardian's State of Secrets Sprawl report found over twelve million new secrets exposed in public repositories in a single year. The majority were from developers who simply did not think the repository would ever be public, or who committed a .env file by accident.
Secret scanning must run at three points: pre-commit to stop secrets leaving the workstation, at CI time to catch anything that slipped through, and continuously against your entire repository history because secrets committed years ago and then deleted are still in your git history and still valid. Tools like TruffleHog, Gitleaks, and the Secret Detection capabilities in Secrails handle both real-time and historical scanning with low false-positive rates when properly configured with allowlist patterns.
Secret scanning is one of those controls where the operational overhead of a false positive is far lower than the operational overhead of a missed detection. Tune aggressively toward recall, not precision. You can tolerate a few false alerts. You cannot tolerate a leaked production database credential. The SolarWinds breach taught enterprises that the supply chain is the attack surface. Log4Shell reinforced it. The XZ Utils backdoor in 2024 made it viscerally real for Linux infrastructure teams. In 2026, software supply chain security is not optional for any organization that handles customer data or operates critical infrastructure.
A Software Bill of Materials is the foundation. Your SBOM is a machine-readable inventory of every component in your software artifact, including direct dependencies, transitive dependencies, their versions, their licenses, and their known vulnerabilities. SPDX and CycloneDX are the two dominant formats. CycloneDX has broader tooling support for security use cases. Tools like Syft, Trivy, and cdxgen can generate SBOMs as part of your CI pipeline in under sixty seconds for most projects.
But generating an SBOM is just the beginning. You need to consume it, correlating component versions against the NVD, OSV, and GitHub Advisory Database, mapping CVEs to EPSS scores to prioritize what actually needs patching versus what is theoretical risk, and feeding high-severity findings back into the development workflow with actionable remediation guidance. This is what dependency vulnerability management looks like when done properly.
Pin your dependencies. Not to major versions. To exact commit SHAs or cryptographic hashes. A dependency pinned to ^4.2.0 is a dependency that can be silently upgraded to include a malicious patch between your CI run and your production deployment. Tools like Renovate and Dependabot can automate the process of keeping pinned dependencies current while still going through a review gate.
Provenance verification, which means confirming that an artifact was built from a specific source commit by a specific pipeline, is increasingly mandatory. SLSA, or Supply chain Levels for Software Artifacts, provides the framework. SLSA Level 3 requires that builds run in a hardened ephemeral build environment, that the build process is fully scripted, and that the provenance attestation is signed. For teams operating in regulated environments, SLSA Level 3 is quickly becoming the baseline expectation from enterprise customers and regulators alike.
Your Terraform, Pulumi, Helm charts, and Kubernetes manifests are code. They have the same vulnerability surface as your application code, including misconfigured S3 buckets, overly permissive IAM roles, unencrypted storage volumes, and containers running as root. IaC security scanning must be part of the same pipeline that scans your application code. 3. Software Implementation, Frameworks & Protocols Checkov, KICS, and Terrascan are the three tools most commonly deployed for IaC security scanning. They map findings to CIS Benchmarks, NIST CSF 2.0 controls, and SOC 2 requirements, which means IaC scan results can feed directly into compliance reporting. Policy-as-Code enforcement through Secrails takes this further by letting security teams define custom policies that enforce organizational standards, for example blocking any Terraform plan that provisions a public-facing storage bucket without server-side encryption enabled.
GitOps teams face a specific challenge here. When your infrastructure state is managed through Git, a misconfigured manifest committed to the repository can be reconciled into production automatically. This means IaC security gates on pull requests are not just about catching bugs early. They are literally preventing production incidents before they occur. Container images are layered artifacts with potentially hundreds of OS packages, language runtimes, and application dependencies. A base image pulled from Docker Hub six months ago is likely carrying dozens of CVEs that have been patched in newer versions. Scanning at build time is not sufficient on its own because images in your registry age, and new CVEs are published daily against components that were clean when you last scanned them.
The Container Image Scanning in Secrails addresses both the build-time and registry-continuous scanning problem, with policy gates that can block deployment of images with Critical vulnerabilities above a defined EPSS threshold. Trivy and Grype are solid open-source options for teams building their own pipeline integration. The critical configuration decision is to scan the final production image, not just the base image, and include both OS packages and application dependencies in the scan scope.
Beyond CVE scanning, container security requires checking for hardening baseline violations: images running as root, writable root filesystems, containers with host network access, and missing seccomp profiles. Tools like Dockle and docker scout surface these misconfigurations alongside vulnerability findings so you have a complete picture of image risk before deployment.
GitOps has become the dominant deployment model for Kubernetes-native organizations, and it has introduced a new attack surface that many teams have not fully internalized. Your Git repository is now your infrastructure control plane. Unauthorized write access to the main branch, a compromised CI service account, or a malicious pull request that passes inadequate review can directly modify production infrastructure without anyone touching the cluster directly.
GitOps security requires branch protection rules with required reviewer counts, signed commits enforced via Sigstore or GPG, CI service accounts scoped to minimum necessary permissions, and audit logging on repository access events. CODEOWNERS files ensure that changes to security-critical paths require review from the security team, not just any developer with merge permissions.
For teams running ArgoCD or Flux, securing the GitOps operator itself is equally important. This means strict RBAC policies, network policies restricting its egress, and regular rotation of the credentials it uses to access the cluster and the repository. A compromised GitOps operator with cluster-admin privileges is a complete infrastructure takeover, and it is one of the highest-value targets in a Kubernetes environment.
A DevSecOps pipeline that actually works in production needs a gate matrix: a clear specification of what each gate checks, what severity threshold triggers a pipeline block, and who owns remediation. Without this, security controls become negotiable, and negotiable security controls get negotiated away under release pressure every single time. Here is the gate logic that works at scale. Pre-commit blocks on secrets and credentials. CI SAST blocks on Critical and High findings with EPSS above 0.3. Dependency scanning blocks on Critical CVEs with a known exploit. Container scanning blocks on Critical OS vulnerabilities in the final image. IaC scanning blocks on CIS Benchmark Level 1 failures. SBOM generation runs on every build and is attached to the artifact. DAST runs on every release candidate against the full application surface.
This is not a burden. This is what a mature code security posture looks like operationally. The teams that execute this well share one trait: they have invested in reducing the signal-to-noise ratio of their security tooling. Every finding that gets surfaced is actionable. Every gate that blocks a pipeline has a clear remediation path. Developers trust the security controls because they are calibrated correctly, and that trust is what makes the shift-left model actually work at scale rather than collapsing under developer frustration.
If you are still building out your security posture, the Vulnerability Management solutions at Secrails provide a unified view across pipeline findings, runtime vulnerabilities, and infrastructure misconfigurations, which is exactly the consolidated visibility you need to prioritize remediation efforts effectively. For organizations navigating compliance requirements alongside DevSecOps maturity, the Compliance solutions map pipeline security controls directly to regulatory frameworks like NIS2, SOC 2, and ISO 27001, so your engineering work generates compliance evidence automatically rather than through manual documentation efforts.
Building a hardened DevSecOps pipeline is not a one-sprint project. It is an iterative program of adding gates, tuning thresholds, improving developer experience, and continuously expanding your threat model as your architecture evolves. Start with secrets scanning and SAST. Those two controls alone will eliminate the majority of the most common vulnerability classes. Then layer in dependency scanning, IaC checks, container hardening, and supply chain controls systematically. The pipeline you build today is the foundation of every secure deployment you ship tomorrow.
DevOps integrates development and operations to accelerate software delivery. DevSecOps extends that model by embedding security controls such as SAST, secret scanning, dependency checks, and container hardening directly into the CI/CD pipeline rather than treating security as a post-deployment audit. The practical effect is that security feedback reaches developers in minutes rather than weeks, and vulnerabilities are caught before they ever reach production.
Shift-left security means moving security checks earlier in the development process, into pre-commit hooks, IDE plugins, and CI build stages, instead of running them only before release or after deployment. The principle is simple: the earlier a vulnerability is caught, the cheaper and faster it is to fix. A flaw detected in a code review costs a fraction of what the same flaw costs if discovered during a production incident.
A Software Bill of Materials is a machine-readable inventory of all components in a software artifact, including direct and transitive dependencies, their versions, licenses, and known vulnerabilities. In 2026, SBOM generation is required or strongly recommended by the US Executive Order on Cybersecurity, the EU Cyber Resilience Act, and NIST guidelines for federal software procurement. Beyond compliance, SBOMs are operationally essential for rapid response to events like Log4Shell, where you need to know within hours which applications are affected.
The key is severity triage: gate on Critical and High findings with an EPSS score above 0.3 or a CVSS above 7.0, let Medium findings generate tracked tickets without blocking merges, and handle Low findings in quarterly backlog reviews. Equally important is signal quality. A gate that fires constantly on false positives will be disabled by developers. Tune your allowlists aggressively and measure your false positive rate as a first-class pipeline metric alongside build time.
SLSA, or Supply chain Levels for Software Artifacts, is a security framework developed by Google and adopted by the Open Source Security Foundation that defines four levels of supply chain integrity for software builds. Each level adds requirements around build environment hardening, build process scripting, and provenance attestation signing. SLSA Level 3, which requires ephemeral hardened build environments and signed provenance, is increasingly becoming a baseline expectation from enterprise customers and regulated industry procurement requirements in 2026.
SAST, secret detection, container scanning, and policy-as-code — all integrated in a single platform built for engineering teams that take security seriously. This repository provides a reference DevSecOps architecture and implementation examples intended for laboratories, research teams, and engineering groups building secure software supply chains.
It demonstrates how multiple open-source security tools can be combined to provide continuous security validation, software supply chain visibility, and structured vulnerability management . This layered model provides defense-in-depth across the software development lifecycle . The detailed design and operational documentation for this reference architecture is located in the docs directory.
The detailed design and operational documentation for this reference architecture is located in the docs directory. This demonstrates how security validation can be fully automated inside CI/CD pipelines . These scripts illustrate how CI pipelines export security findings into long-term monitoring systems. Supporting documents describe how organizations can adopt and operate this architecture: Reference implementation of an open-source DevSecOps software supply chain security stack including CI-based scanning, SBOM generation, vulnerability management, and governance documentation.
Security can no longer be a gate at the end of the development cycle. DevSecOps embeds security testing into every stage of your CI/CD pipeline — from code commit to production runtime. This guide walks you through building a pipeline that catches vulnerabilities early without slowing down your team. DevSecOps is the practice of integrating security into every phase of the software development lifecycle (SDLC) rather than treating it as a separate phase. Instead of a security team reviewing code after it is written, DevSecOps automates security checks directly in the CI/CD pipeline — making security a shared responsibility between development, operations, and security teams.
The goal is not to replace security teams, but to give developers fast, actionable feedback about vulnerabilities while the code is still fresh in their minds. A well-designed DevSecOps pipeline catches critical issues before they reach production, reduces remediation costs by 10–100x compared to post-deployment fixes, and maintains development velocity. of breaches involve a human element or misconfiguration that automated scanning would have caught Modern applications depend on hundreds of open-source packages, deploy to multi-cloud infrastructure, and ship multiple times per day. Manual security reviews cannot keep pace. DevSecOps pipelines automate the repetitive scanning work, surface only actionable findings, and enforce security policies as code.
A comprehensive DevSecOps pipeline integrates security at six key stages. Each stage catches a different class of vulnerability, and together they provide defense in depth from code to cloud. Scan for hardcoded secrets, API keys, and credentials before code is committed. Use git pre-commit hooks to prevent secrets from entering version control.
Analyze source code for security vulnerabilities like SQL injection, XSS, and command injection. Runs on every pull request and blocks merges for critical findings. Scan open-source dependencies for known CVEs, license violations, and malicious packages. Generate SBOM for supply chain visibility.
Scan container images for OS and application vulnerabilities. Check Terraform, CloudFormation, and Kubernetes manifests for misconfigurations before deployment. Test the running application for vulnerabilities by sending crafted requests. Catches issues that static analysis misses, like authentication bypass and business logic flaws.
Monitor production workloads for anomalous behavior, privilege escalation, and network anomalies using eBPF. Enforce security policies at the kernel level. Not every scan needs to run at every stage. The key is balancing thoroughness with speed — fast scans on every commit, deeper scans on pull requests, and comprehensive scans before deployment.
Surfacing every low-severity finding on every PR burns developer trust. Start with critical and high severity only. Tune rules over time. 4. Practical Deployment, Analysis & Case Studies A hard gate that fails the build with no remediation guidance frustrates developers. Always provide fix suggestions and documentation links.
Running security scans only before deployment means developers discover issues days after writing the code. Shift scans to the PR stage. Pre-deployment scanning cannot catch zero-day exploits, misuse of stolen credentials, or configuration drift. Runtime monitoring completes the picture.
The difference between a DevSecOps pipeline that sticks and one that gets bypassed is gate design. A gate is a policy decision — under what conditions does the pipeline stop a change? Get it wrong in either direction and you lose: gates that block on every medium-severity finding teach developers to route around security, while purely advisory gates teach them to ignore it. The proven pattern is graduated enforcement.
Gate on findings introduced by the change itself (diff-aware scanning), at critical or high severity, with evidence of exploitability — a reachable code path or a known exploited CVE. Pre-existing backlog issues belong in a tracked remediation queue, not in someone else's pull request. Real deadlines exist. Allow documented, time-boxed exceptions with a required approver and an automatic expiry that reopens the finding. An auditable override is far safer than developers force-merging around a broken check.
Keep gate thresholds in version-controlled policy files (OPA/Rego, or your platform's policy DSL) rather than per-repo CI configuration. Policy changes then go through review like any other code, and every repository inherits updates without pipeline edits. PR-stage checks should complete in under five minutes; anything slower migrates to merge or nightly scans. Diff-aware SAST, cached dependency databases, and parallel scan execution keep the budget honest — a slow gate is a disabled gate within a quarter.
Roll gates out in audit mode first: run the scan, post the results, block nothing. After two to four weeks of tuning false positives, flip criticals to blocking, then highs. This sequencing builds the trust that makes enforcement politically possible. A DevSecOps pipeline scans your software — but the pipeline is itself software, and attackers know it. SolarWinds, Codecov, and the 2025 wave of compromised GitHub Actions all followed the same logic: subvert the build system and you inherit the trust of everything it ships. Frameworks like SLSA (Supply-chain Levels for Software Artifacts) formalize the defenses, and most of them are practical for ordinary teams today.
Treat these as pipeline stages too: SBOM generation and image signing slot naturally into the container build step, and signature verification becomes one more pre-deploy gate. You cannot tune what you do not measure. Raw finding counts are a vanity metric — they reward scanning more, not securing more. The metrics that actually predict risk reduction measure flow: how fast vulnerabilities move from introduction to remediation, and how little the pipeline costs developers along the way.
Days from first detection to verified fix, segmented by severity. Critical findings should trend toward days, not months. This is the single best health indicator for the whole program. Vulnerabilities found in production (by DAST, runtime monitoring, pentests, or bug bounty) that a pipeline stage should have caught earlier. Every escape is a tuning signal for a specific gate.
Median seconds security checks add to a PR build. Track it like a performance SLO — when it creeps past your budget, invest in diff-aware scanning and caching before developers revolt. Percentage of findings triaged as not-an-issue. Above roughly 20%, developers stop reading results. Measure per rule and disable or rewrite the worst offenders.
Percentage of repositories, images, and cloud accounts actually onboarded to each scan type. A pristine pipeline covering 40% of services is a false sense of security. How often exceptions are used and by whom. Rising overrides signal either miscalibrated thresholds or deadline pressure worth surfacing to leadership.
A unified platform makes these metrics cheap to compute because findings from every stage share one data model — TigerGate, for example, reports MTTR and coverage across SAST, SCA, container, cloud, and runtime findings from a single dashboard rather than six exported CSVs. Teams that try to enable all six stages simultaneously across every repository usually stall in tuning purgatory. A phased rollout gets to durable coverage faster: Enable secret scanning everywhere immediately — it has near-zero false positives and the highest payoff per hour invested.
In parallel, run SAST and SCA in report-only mode on your three most critical services to build a finding baseline. Turn on diff-aware SAST and SCA comments on pull requests for the pilot services. Triage the baseline backlog into a tracked queue with owners and SLAs. Tune the noisiest rules before expanding scope. Flip critical-severity findings to blocking on pilot repos, add container and IaC scanning to image builds, and expand PR scanning to the wider repository fleet in report-only mode.
Deploy runtime monitoring agents to one production cluster in audit mode, add DAST against staging on a nightly schedule, and hold a retrospective: review MTTR, false positive rate, and latency budget, then set thresholds for the next quarter's expansion. Both, staged by severity and age. New critical findings introduced by the change should block; new highs should block after a tuning period; everything else should be visible but non-blocking, flowing into a remediation queue with SLAs. Blocking on pre-existing backlog issues in unrelated PRs is the fastest way to lose developer support.
Secret scanning first — it is fast, accurate, and a leaked credential is the most directly exploitable finding class. SCA second, because dependency CVEs are abundant and fixes are usually just version bumps. SAST third, once you have the triage muscle to handle findings that require code changes. Scanners in CI are the mechanism; DevSecOps is the operating model around them: findings routed to owners with SLAs, policy expressed as reviewable code, metrics that track remediation flow, and runtime feedback that tells you which pre-deployment gates are leaking. A scanner without a remediation loop just produces reports.
Yes. Automated stages catch known vulnerability classes at scale, but business logic flaws, authorization design errors, and chained attacks still need human creativity. The pipeline makes pentests more valuable — testers skip the low-hanging fruit and spend their time on what automation cannot find. TigerGate unifies SAST, SCA, container scanning, DAST, cloud security, and eBPF runtime monitoring in a single platform.
One integration, full pipeline coverage. Modern software development is less about writing code from scratch and more about assembling it. Today's applications are complex mosaics of third-party APIs, open-source libraries, and containerized microservices. While this modular approach accelerates delivery, it has also expanded the attack surface, making software supply chain security a critical priority for engineering teams.
Malicious actors have realized that instead of attacking a well-defended enterprise directly, they can compromise a widely used dependency or build tool to infiltrate thousands of downstream targets simultaneously. To combat this, organizations must evolve beyond traditional perimeter defenses and adopt comprehensive DevSecOps best practices . Here is your foundational guide to understanding modern threats and integrating robust security into your development lifecycle.
Supply chain attacks occur when a threat actor infiltrates a software vendor's network and employs malicious code to compromise the software before it reaches the end user. These attacks are particularly insidious because they exploit the implicit trust developers place in their tools and dependencies. Because these threats bypass traditional runtime firewalls, defending against them requires baking security directly into the development and deployment workflows.
DevSecOps is the philosophy of integrating security practices within the DevOps process. When applied to the software supply chain, it ensures that every component, pipeline, and artifact is continuously verified. Your Continuous Integration and Continuous Deployment (CI/CD) pipeline is the engine of your software delivery. If an attacker gains access to your pipeline, they hold the keys to your entire production environment.
A modern DevSecOps pipeline integrates automated security scanning (SAST, SCA, and DAST) at every stage of the release process. You cannot secure what you do not know you are using. Software Composition Analysis (SCA) tools are essential for scanning your codebase to identify all open-source components and cross-referencing them against known vulnerability databases (like the CVE list).
Automate dependency updates and establish policies to block builds that include libraries with critical, unpatched vulnerabilities. Furthermore, consider implementing internal artifact repositories to proxy and cache approved versions of external packages, insulating your team from upstream tampering. A Software Bill of Materials (SBOM) is a comprehensive inventory detailing all the components, libraries, and dependencies that make up a software application.
Generating an SBOM during every build provides immediate visibility into your software's DNA. If a zero-day vulnerability is announced in a popular logging framework, a well-maintained SBOM allows your security team to determine your exposure in seconds rather than days. Make SBOM generation an automated, non-negotiable step in your CI/CD pipeline. How do you guarantee that the container image deployed to production is the exact same one that passed your security tests? 5. Performance Evaluation & Extended Technical Observations Code signing and provenance attestation provide cryptographic proof of an artifact's origin and integrity. Frameworks like SLSA (Supply-chain Levels for Software Artifacts) offer a standardized approach to tracking how software was built, ensuring that artifacts haven't been tampered with between the build and deploy stages.
Securing the software supply chain is not a one-time project; it is an ongoing operational posture. By integrating these DevSecOps best practices into your daily workflows, you shift security to the leftâIIcatching vulnerabilities before they are merged, built, or deployed. As supply chain attacks continue to grow in sophistication, treating your build pipelines and dependencies with the same level of security scrutiny as your production infrastructure is no longer optional. It is the new baseline for modern software engineering.
Automated web application penetration testing platform. Helping teams find and fix security vulnerabilities. Run automated penetration tests across 9 security modules. Find vulnerabilities in your web applications, APIs, and infrastructure âII before attackers do. In modern software engineering, speed is currency, yet the relentless push for velocity has created a massive blind spot as applications are increasingly assembled from thousands of third-party open-source libraries, cloud services, and automated CI/CD tools rather than written from scratch. Because traditional perimeter defenses and manual, end-of-cycle audits are completely ineffective against upstream supply chain attacks and compromised dependencies, organizations are turning to DevSecOps and Software Supply Chain Security to embed automated testing, validation mechanisms, and compliance guardrails directly into every phase of the development lifecycle. Through this comprehensive guide, you will learn how DevOpsSchool and the official resources at DevOpsSchool help engineers master the strategies needed to transform vulnerable delivery pipelines into resilient, secure ecosystems.
Software Supply Chain Security refers to the collective practices, policies, tools, and automated controls used to secure all the components, dependencies, third-party libraries, tools, and infrastructure that go into building, testing, and deploying a software application. Attackers realize that compromising a single widely used open-source library or a popular CI/CD tool yields a massive return on investment. Instead of hacking an enterprise firewall directly, a threat actor can inject malicious code upstream into a dependency, allowing the payload to propagate automatically downstream to thousands of unsuspecting enterprise consumers.
DevOps broke down silos between development and operations to accelerate delivery. DevSecOps takes the next logical step by breaking down the silo between development, operations, and security. DevSecOps and Software Supply Chain Security ensures that security is baked into the development workflow rather than bolted on as an afterthought. Shift-left security means moving security testing and validation as early in the software development lifecycle as possible.
Instead of finding vulnerabilities in production, DevSecOps and Software Supply Chain Security identifies flaws while code is still being written on a developer’s workstation or during early pull request reviews. Manual security reviews cannot keep pace with modern deployment frequencies. DevSecOps and Software Supply Chain Security relies heavily on automation—integrating Static Application Security Testing (SAST), Dynamic Application Security Testing (DAST), Software Composition Analysis (SCA), and secret scanning directly into automated pipelines.
Modern software development relies heavily on external leverage. Over 80% to 90% of a modern application’s codebase consists of open-source libraries and third-party dependencies. While this accelerates time-to-market, it introduces profound operational risks. Developers frequently import third-party packages without verifying their provenance, maintenance status, or security posture.
If an open-source maintainer’s account is compromised, malicious updates can be pushed to public registries. Enterprise software often integrates commercial vendors, APIs, and plugins. A vulnerability in any third-party integration creates an immediate backdoor into the host enterprise system. Governments and regulatory bodies worldwide are tightening compliance mandates. Frameworks now require organizations to maintain strict visibility over their software supply chains, mandate Software Bill of Materials (SBOM), and prove accountability for every component in production.
Integrating DevSecOps and Software Supply Chain Security requires transforming every phase of the traditional SDLC into a secure workflow. Security requirements, threat modeling, and risk assessments are conducted before a single line of code is written. Teams identify potential attack surfaces and define security acceptance criteria.
Developers follow secure coding standards. Integrated development environment (IDE) plugins provide real-time feedback on vulnerabilities, insecure functions, and potential bugs. Peer code reviews are mandatory. Automated linters and SAST tools scan pull requests, blocking code that fails security gates before it merges into the main branch.
Automated testing suites run continuously. SCA checks third-party dependencies, DAST evaluates running application endpoints, and container scanners verify image layers. Artifacts are signed cryptographically. Deployment pipelines enforce strict access controls, ensuring that only verified, immutable packages reach production environments.
Once live, applications and infrastructure are monitored continuously for anomalous behavior, new vulnerability disclosures, and runtime threats. The CI/CD pipeline is the central nervous system of modern software delivery. If an attacker compromises the pipeline, they control the entire software supply chain.
Implement Software Composition Analysis (SCA) tools within your CI/CD pipeline to analyze all direct and transitive dependencies against known vulnerability databases. Establish clear policies for version pinning, automatic dependency updates, and deprecation tracking to prevent drift and unpatched vulnerabilities.
Utilize private artifact proxies and internal registries to cache, vet, and approve external open-source packages before developers import them into projects. A Software Bill of Materials (SBOM) is a formal, structured inventory of software components, libraries, modules, and their hierarchical relationships used to build an application. Think of it as an ingredient list for software.
Containers package applications with their dependencies, but insecure base images and misconfigured clusters introduce severe security risks. Infrastructure defined as code (Terraform, Ansible, CloudFormation) is susceptible to misconfigurations that can expose cloud environments to attackers.
Cloud platforms (AWS, Azure, Google Cloud) form the foundation of modern application delivery. DevSecOps and Software Supply Chain Security extends directly into cloud environments through native security tooling and IAM governance. Automation is the cornerstone of scalable security. DevSecOps and Software Supply Chain Security replaces manual bottlenecks with automated gates.
By embedding these automated checks into the commit and build phases, vulnerabilities are caught and remediated in minutes rather than months. Meeting compliance standards is no longer a periodic paperwork exercise; it requires continuous verification. To understand how DevSecOps and Software Supply Chain Security operates in practice, consider a global financial technology enterprise: Mastering DevSecOps and Software Supply Chain Security opens doors to high-impact, high-demand roles across the global technology sector: To master these technologies and earn industry-recognized credentials, exploring professional certification tracks at DevOpsSchool offers comprehensive guidance tailored for both India and global markets.
As technology evolves, DevSecOps and Software Supply Chain Security is adapting to new paradigms: It is the practice of protecting every component—including code, dependencies, tools, and infrastructure—that goes into building and delivering software against tampering and vulnerabilities. Because modern applications rely heavily on external components, securing the supply chain prevents attackers from injecting malicious code into automated delivery pipelines.
A Software Bill of Materials is a formal inventory detailing all components, libraries, and modules contained within a software application. It integrates automated security testing, validation, and compliance checks into every stage of the development lifecycle, shifting security left.
Open-source libraries may contain undiscovered vulnerabilities or be compromised if maintainer accounts are hijacked by threat actors. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Microsoft%20Security%20Development%20Lifecycle • https://en.wikipedia.org/wiki/List%20of%20computer%20security%20certifications • https://jfrog.com/learn/devsecops/devsecops-tools/ • https://cheatsheetseries.owasp.org/cheatsheets/Software_Supply_Chain_Security_Cheat_Sheet.html • https://secrails.com/blog/devsecops-pipeline-complete-engineering-guide-2026 • https://github.com/softwarewrap/devsecops-supply-chain-security • https://www.tigergate.dev/blog/devsecops-pipeline-guide/ • https://saaspentest.io/blog/securing-software-supply-chain-devsecops-guide.html • https://devsecopsschool.com/blog/integrating-security-into-every-layer-devsecops-and-software-supply-chain-security/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Secure Software Supply Chain Monitoring Tool In Devsecops.
[*] Metasploit Scan Running on Target Subnet for Secure Software Supply Chain Monitoring Tool In Devsecops... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |