Complete Technical Paper Content — Secure Source Code Auditing Tool For Python Programs
Overview & System Context
Secure Source Code Auditing Tool For Python Programs: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9501 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background E is an object-oriented programming language for secure distributed computing, created by Mark S. Miller, Dan Bornstein, Douglas Crockford, Chip Morningstar and others at Electric Communities in 1997. E is mainly descended from the concurrent language Joule and from Original-E, a set of extensions to Java for secure distributed programming. E combines message-based computation with Java-like syntax. A concurrency model based on event loops and promises ensures that deadlock can never occur.
Here is a recursive function for computing the factorial of a number, written in E. Functions are defined using the def keyword. In the first line, :int is a guard that constrains the argument and result of the function. A guard is not quite the same thing as a type declaration; guards are optional and can specify constraints. The first :int ensures that the body of the function will only have to handle an integer argument. Without the second :int above, the function would not be able to return a value. Being able to see up front that information escapes out of the function is helpful for security auditing. Since E is intended to support secure co-operation, the canonical example for E programs is the mint, a simple electronic money system in just a few lines of E. The following code defines a function that makes mints, where each mint has its own currency. Each mint can make purses that hold its currency, and any holder of two purses of the same currency can securely transfer money between the purses. By quick examination of the source code, an E programmer can easily verify that only mints may change the amount of money in circulation, that money can only be created and not destroyed, that mints can only create money of their own currency, and that only the holder of a purse can change its balance.
Objects in E are defined with the def keyword, and within the object definition, the to keyword begins each method. The guard expressions in this example illustrate how to specify a value constraint (as in :(int >= 0) or :(0..balance)). The mint example makes use of a built-in mechanism called a sealer. The function makeBrandPair creates two associated objects, a sealer and an unsealer, such that the sealer can seal an object in a box and the unsealer is the only object that can retrieve the contents of the box. See the E website for a more detailed explanation of this money example.
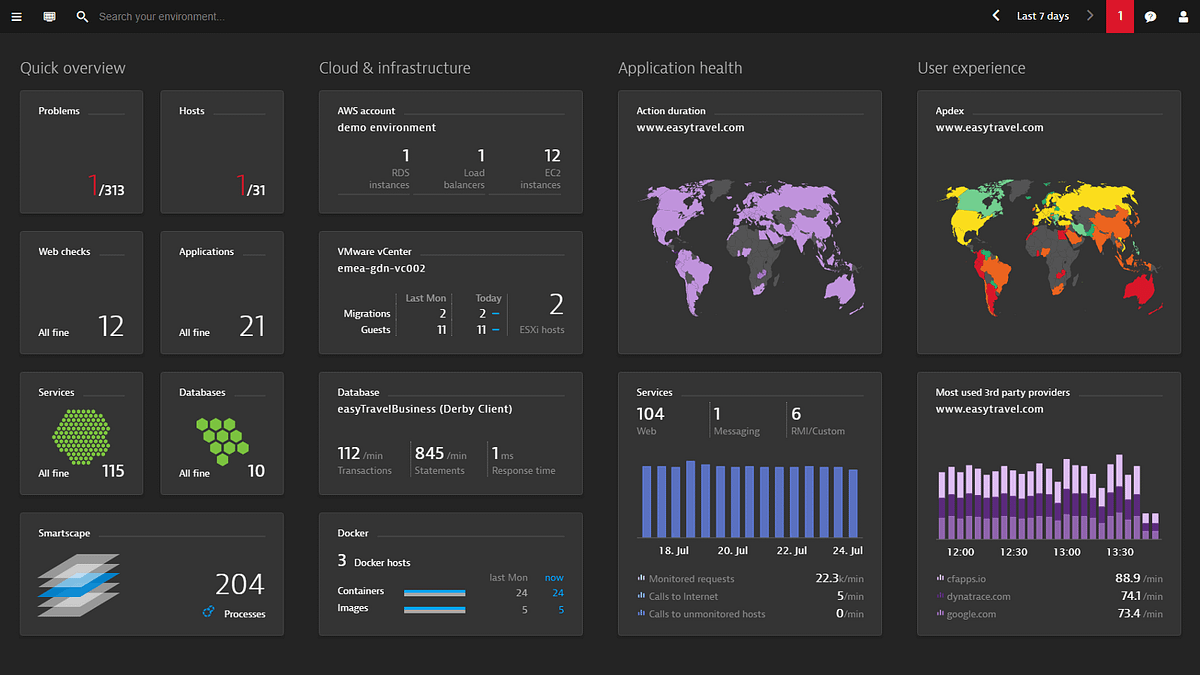
Figure 1: Building Secure Dashboards & Monitoring Tools with Python | by Sneha ... Helios Voting is an open-source, web-based electronic voting system. Users can vote in elections and users can create elections. Anyone can cast a ballot; however, for the final vote to be counted, the voter's identification must be verified. Helios uses homomorphic encryption to ensure ballot secrecy. It was created by Ben Adida, a software engineer involved in other SecureDrop is a free software platform for secure communication between journalists and sources (whistleblowers). It was originally designed and developed by Aaron Swartz and Kevin Poulsen under the name DeadDrop. James Dolan also co-created the software.
This project demonstrates practical cybersecurity technician skills used in enterprise and industrial environments. It focuses on identifying exposed network services, validating configurations against an approved baseline, and producing audit-ready reports to support remediation and attack surface reduction. Designed with real-world IT and plant environments in mind (e.g., manufacturing, labs, and enterprise networks), The toolkit emphasizes safe discovery, port visibility, and operational security best practices.
Figure 2: Audit Design Dashboard Projects :: Photos, videos, logos, illustrations ... Author: Shanice Adams Role Focus: Cybersecurity Technician / Infrastructure Security Experience Context: Enterprise IT, industrial environments, server and network builds The following screenshots show sample output generated during an authorized local audit.
In enterprise and industrial environments, cybersecurity is not just about identifying vulnerabilities—it is about understanding how infrastructure is configured, what services are exposed, and whether those exposures align with business and operational requirements. This project demonstrates a practical, infrastructure-first approach to cybersecurity. Rather than relying on intrusive testing or theoretical controls, it focuses on visibility, baseline validation, and clear documentation. The output is designed to support real-world decision-making by operations, security, and IT teams.
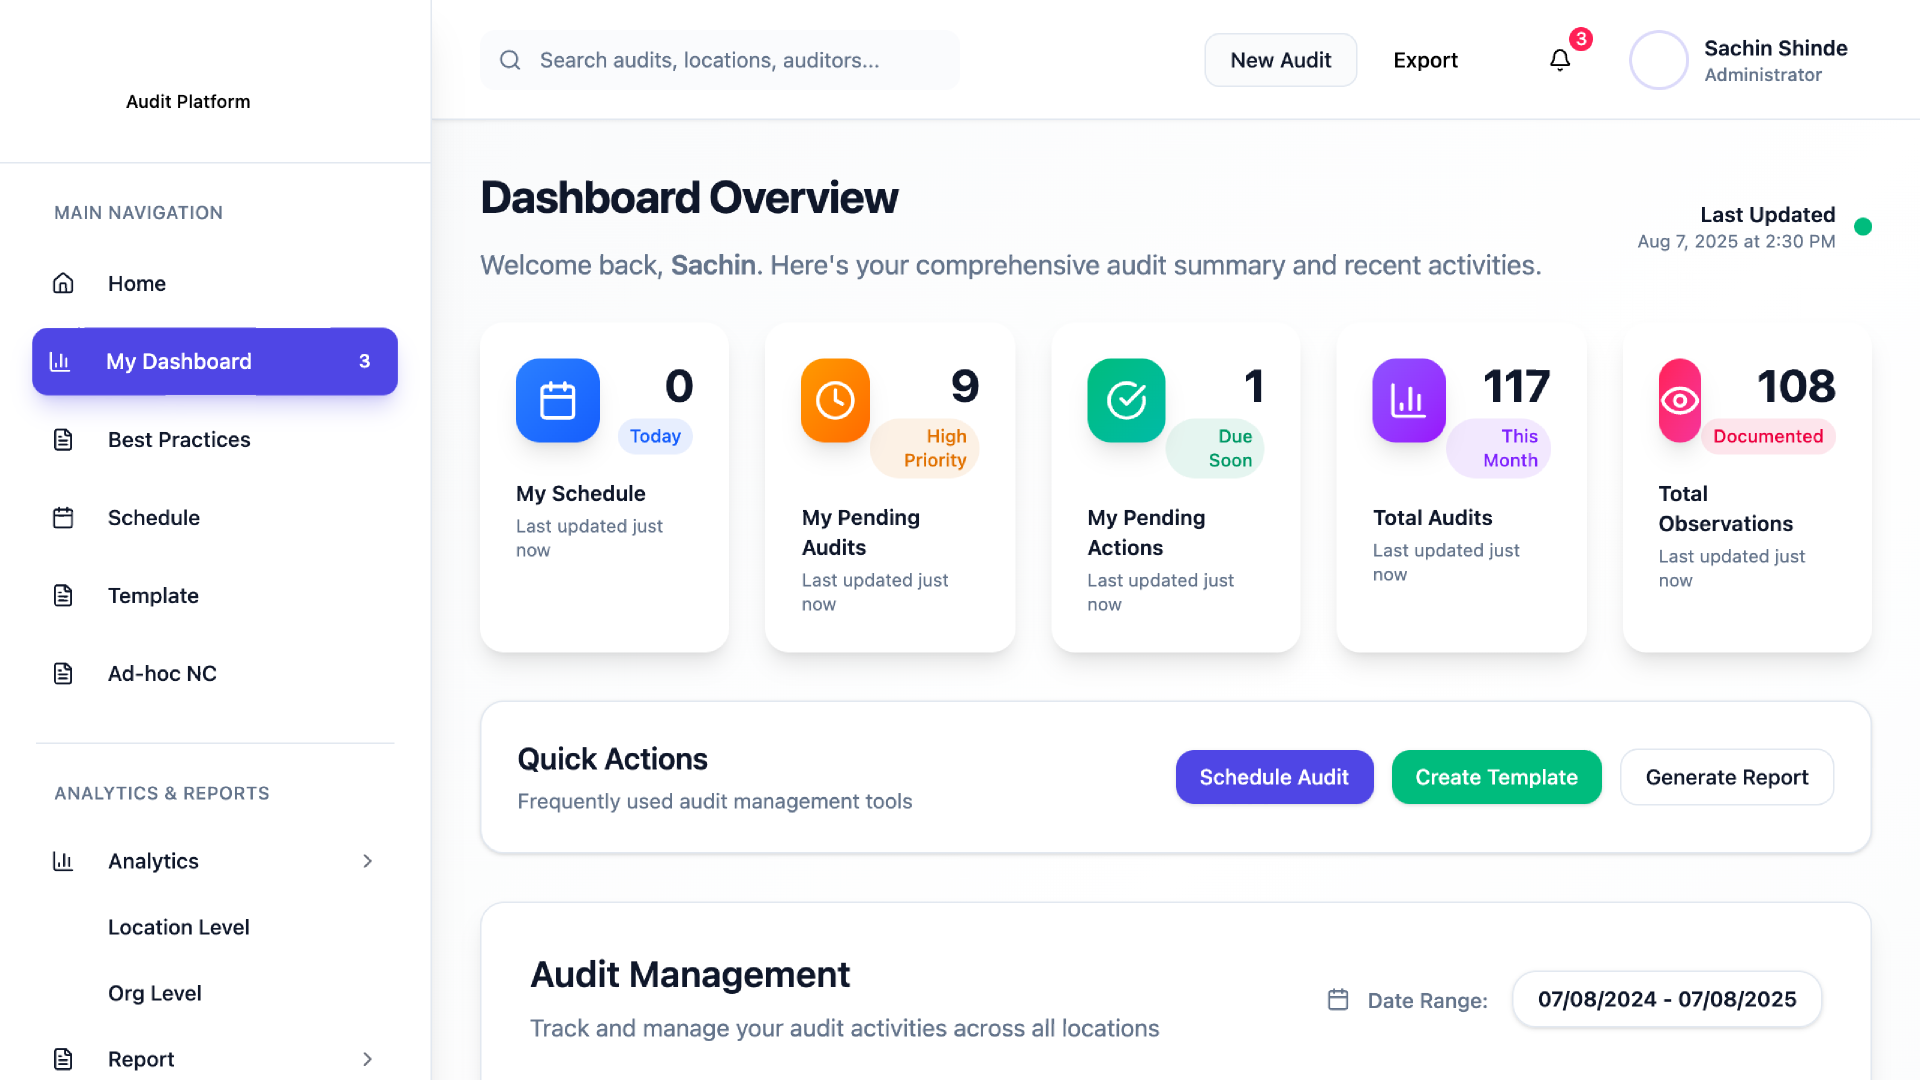
Figure 3: Modern SAAS Audit Platform Dashboard | Figma In environments such as manufacturing, utilities, and other regulated industries, this approach helps organizations reduce risk while maintaining system reliability, uptime, and compliance. In a production environment, this toolkit would be used as a controlled, authorized assessment tool to support ongoing infrastructure security and configuration management.
Baseline validation: Verifying that servers, workstations, or network-connected devices comply with approved port and service configurations before or after deployment Change verification: Confirming that system changes, upgrades, or maintenance activities did not introduce unexpected service exposure Periodic audits: Supporting scheduled security reviews and compliance checks in regulated environments Incident response support: Quickly identifying exposed services during the investigation of suspected misconfigurations or security events The tool is designed to run safely in live environments, with a focus on visibility and documentation rather than exploitation.
Results are produced in structured CSV and JSON formats, enabling easy review by security, IT, and operations teams, as well as integration into existing audit and remediation workflows. By aligning technical findings with baseline policies and remediation guidance, the toolkit supports informed decision-making while maintaining system reliability, uptime, and operational continuity.
This tool is intended for authorized internal auditing and educational use only. All scanning must be approved by the system/network owner. Building secure systems with Python requires a comprehensive approach, encompassing not only functional correctness but also robust security measures. This tutorial explores the crucial aspects of Secure Python Systems Architecture , focusing on threat modeling, authentication, and authorization. We’ll delve into practical techniques and best practices to help you design and implement secure Python applications that stand strong against potential threats.
Securing Python applications involves more than just writing clean code. It demands a proactive approach to identifying and mitigating potential vulnerabilities. This comprehensive guide provides a deep dive into architecting secure Python systems, starting with threat modeling to anticipate potential attacks. We then explore robust authentication mechanisms to verify user identities and delve into granular authorization strategies to control access to sensitive resources. Through practical examples and industry best practices, you’ll learn how to build Python applications that are resilient, trustworthy, and secure. From understanding OWASP guidelines to implementing OAuth 2.0, this tutorial equips you with the knowledge and tools necessary to safeguard your Python projects and protect your users’ data. The use of hosting services, like those offered by DoHost (https://dohost.us), should also adhere to these security principles when deploying your applications.
Threat modeling is a critical process for identifying potential security vulnerabilities in your Python applications. It involves systematically analyzing the system’s architecture, identifying potential threats, and determining the likelihood and impact of each threat. By proactively identifying vulnerabilities, you can implement appropriate security controls to mitigate the risk. Authentication is the process of verifying the identity of a user or system. It ensures that only authorized individuals or systems can access your Python applications. Strong authentication is crucial for protecting sensitive data and preventing unauthorized access.
password = b”super_secret_password” hashed_password = bcrypt.hashpw(password, bcrypt.gensalt()) # Verify the password if bcrypt.checkpw(password, hashed_password): print(“Password matches!”) else: print(“Password does not match!”) Authorization is the process of determining what a user or system is allowed to do after they have been authenticated. It controls access to sensitive resources and ensures that users can only perform actions they are authorized to perform.
def check_permission(user, permission): if “admin” in user_roles.get(user, []): return True # Admins have all permissions if check_permission(user, permission): print(f”{user} has permission to {permission}”) else: print(f”{user} does not have permission to {permission}”) Secure coding practices are essential for preventing vulnerabilities from being introduced into your Python applications. By following these practices, you can reduce the risk of common attacks such as SQL injection, cross-site scripting (XSS), and buffer overflows.
# Use parameterized query to prevent SQL injection cursor.execute(“SELECT * FROM users WHERE id = ?”, (user_id,)) Monitoring and logging are crucial for detecting and responding to security incidents in your Python applications. By monitoring system logs and security events, you can identify suspicious activity and take appropriate action to mitigate the impact of attacks.
# Configure logging logging.basicConfig(filename=’app.log’, level=logging.INFO, format=’%(asctime)s – %(name)s – %(levelname)s – %(message)s’) # Log an error try: result = 10 / 0 except ZeroDivisionError: logging.error(‘Division by zero error’, exc_info=True) #Log the full stacktrace Authentication verifies who a user is, while authorization determines what they are allowed to do. Authentication is like showing your ID to get into a building, while authorization is like having a key card that grants you access to specific rooms.
They are both essential components of a secure system. Threat modeling should be performed at the beginning of a project and regularly throughout the development lifecycle. Any time there is a significant change to the system’s architecture or functionality, a new threat model should be created to identify potential vulnerabilities. This proactive approach ensures continuous security assessment.
Common mistakes include storing passwords in plain text, failing to validate user inputs, neglecting to update dependencies, and not implementing proper access controls. By avoiding these mistakes and following security best practices, you can significantly reduce the risk of security vulnerabilities in your Python applications. Consider DoHost (https://dohost.us) when deploying and securing your server infrastructure, ensuring it aligns with your application security principles.
Architecting Secure Python Systems Architecture requires a multi-faceted approach that encompasses threat modeling, authentication, authorization, secure coding practices, and monitoring. By integrating these techniques into your development process, you can build Python applications that are resilient to attack and protect sensitive data. Remember to stay up-to-date with the latest security threats and best practices to continually improve the security posture of your applications. Investing in security early on will save you time, money, and reputation in the long run. This holistic approach, combined with reliable hosting services like DoHost (https://dohost.us), contributes to a more secure digital environment.
Python security, threat modeling, authentication, authorization, security architecture Architecting Secure Python Systems: Learn threat modeling, authentication, and authorization techniques to build robust and reliable Python applications. New developers require a single, framework-independent resource to establish a baseline in secure coding practices.
Python is one of the most widely adopted programming languages in the world, powering everything from web applications and data pipelines to AI/ML systems and cloud infrastructure. Yet adequate secure coding resources for Python to meet these needs of new developers haven’t been available. The OpenSSF Secure Coding Guide for Python closes that gap by providing developers with a practical, example-driven resource for writing more secure Python code. The guide covers over 50 rules across 9 sections, each with working code examples that demonstrate both the vulnerability and its mitigation.
Comprehensive secure coding standards have long existed for languages like Java ( SEI CERT Oracle Coding Standard for Java ), C, and C++. For Python, the available resources were either high-level and language-agnostic, or tied to a single web framework. When onboarding new developers, we needed a baseline of secure coding knowledge that was framework-independent, covered core Python, and could serve as a self-study resource without requiring 40+ hours of training. Nothing like that existed, so we built it ourselves under the OpenSSF Best Practices Working Group .
2. System Architecture & Core Working Principles The result is a guide that focuses on CPython ≥ 3.9 and the standard library, deliberately avoiding dependencies on any specific web framework or third-party module. This keeps the material relevant regardless of which stack a team uses and ensures the secure coding principles transfer across projects.
While the guide is primarily for new developers, it can also aid security researchers, AI and analysis tools, and educators as discussed below. Python’s accessibility is one of its greatest strengths, but it also means that many developers writing Python code may not have formal training in secure software development. Common pitfalls such as OS command injection, deserialization of untrusted data, improper exception handling, and insufficient logging continue to appear in real-world Python applications and libraries. These are not theoretical risks: the guide references prominent CVEs with CVSS scores reaching 9.8, demonstrating the real-world impact of these vulnerabilities.
Existing secure coding standards from OWASP and MITRE CWE Top 25 provide essential high-level guidance, but they are language-agnostic. Developers need to understand how these risks manifest specifically in Python and what idiomatic Python mitigations look like. That is exactly what this guide delivers. Static analysis tools and AI-assisted code review are valuable, but they cannot catch everything. Many security issues stem from design decisions and coding patterns that automated tools struggle to evaluate, such as improper trust boundary handling, missing input neutralization, or subtle operator precedence errors. The guide’s code examples are specifically designed so that noncompliantXX.py files can be used to test and train analysis tools, while compliantXX.py files demonstrate the targeted fix. This makes the guide useful not only for human learners but also for improving the tools themselves (including AI).
The guide is organized into 9 sections covering the most critical areas of secure Python development: Each rule follows a consistent structure: a concise description of the risk, a non-compliant code example showing the vulnerability, a compliant solution demonstrating the fix, automated detection results, and references to related CWE entries and other guidelines. Every rule maps to a specific MITRE CWE weakness.
Many secure coding guides assign risk ratings using numeric scales with labels such as impact=HIGH=4 and probability=LOW=3, which are then multiplied and divided to produce an overall score. We found these approaches too abstract and subjective to be genuinely useful for developers trying to understand real-world risk. Instead, the guide takes an evidence-based approach. The main overview table pairs each rule with a representative CVE from a real-world product, its CVSS score, and its EPSS (Exploit Prediction Scoring System) probability rating. CVSS tells you how severe a vulnerability is if exploited; EPSS tells you how likely it is to be exploited in the wild. Together they give a grounded, data-driven picture of risk that abstract rating matrices cannot provide. This also exposes blind spots: rules with high CVSS but low EPSS may indicate areas where the industry underestimates exploitation likelihood, while high EPSS scores highlight vulnerabilities that attackers actively target.
What sets this guide apart from other secure coding resources is its emphasis on working code. Every rule includes runnable Python examples targeting CPython ≥ 3.9 that developers can clone and execute locally: The non-compliant examples include both the vulnerable code and an exploitation section separated by a clear comment marker, making them suitable for testing security analysis tools. The compliant examples address only the specific risk described, keeping them focused and easy to understand.
Consider a common vulnerability: OS command injection via unsanitized user input passed to subprocess . Our guide provides at least one detailed specific example so developers can understand and apply the guidance. In this case, the non-compliant example shows how an attacker can inject arbitrary commands, while the compliant solution demonstrates proper input handling using shlex and avoiding shell=True . Each example is short, typically around 20 lines, and focuses purely on the security issue at hand.
The documentation uses plain English to cater to an international audience. It is written in an academic style to maximize precision and to support security researchers. The entire guide is designed to be completed in well under 40 hours of self-study. The guide is an active, community-driven project and contributions are welcome. Whether it is fixing a typo, improving readability, adding a new code example, or creating entirely new rules to cover missing material, there are many ways to help.
Contribute on GitHub: https://github.com/ossf/wg-best-practices-os-developers/tree/main/docs/Secure-Coding-Guide-for-Python Join the community on the OpenSSF Slack by searching /join secure-coding-guide-for-python in the search bar. You can also participate in the bi-weekly working meetings; see the meeting notes for details.
Helge Wehder (myteron) is a Security Principal Master with a background in Operations Support Systems (OSS) for large scale radio networks using Python. Helge enjoys creating embedded systems with his 4 children. Plays Bass guitar on a Sunday session in Flann’s Athlone and does a bit of Inline Hockey for sports. Thomas McDermott (tommcd) is a Senior Engineer at Ericsson, where he works as a software engineer with a particular interest in secure coding. He works extensively with Python and Java, with a particular interest in data analysis and Markdown- and notebook-based workflows, and he follows developments in AI-assisted engineering tooling. Before moving into software engineering 14 years ago, Thomas spent earlier parts of his career as a researcher and lecturer in Chemical Engineering and as a design engineer in the energy sector, though a long-standing love of coding (Fortran, C, Python, Mathematica, and Bash since the mid-1990s) eventually won out. He holds a PhD in Chemical Engineering from University College Dublin and an MSc in Applied Software Development, and his research background in molecular simulation and statistical mechanics continues to inform his analytical approach to software engineering and security.
Hubert Daniszewski (s19110) is a Java and Python software developer with over five years of experience writing, maintaining, and debugging code in both languages. A former Security Master at TietoEvry, he continues to expand his expertise in secure coding and applies it in practice. He was one of the first contributors to the Secure Coding for Python project, where he reviewed and authored rules, particularly in the area of concurrency.
Bartlomiej Karas (BartKaras1128) is a Software Developer and Security Master at Ericsson, bringing hands-on experience with Cloud Native solutions and a strong command of multiple programming languages, including Python. Throughout his career, he has contributed to numerous security enhancements and developed various automation solutions for hardware installation. Beyond his professional work, Bartlomiej has a passion for Game Development and has created multiple games as a hobbyist.
Andrew Costello (andrew-costello) is a Computer Science graduate with a focus on cybersecurity and software engineering. His work centres on practical system design, including machine learning-based malware analysis, and he also works on tools, cars, small engines, and farming, reflecting a strong hands-on engineering mindset. He is particularly interested in building secure, efficient systems that perform reliably in real-world conditions.
Dr. David A. Wheeler is an expert on developing secure software and on open source software. He created the Open Source Security Foundation (OpenSSF) courses “Developing Secure Software” (LFD121), “Understanding the EU Cyber Resilience Act (CRA)” (LFEL1001), and “Secure AI/ML-Driven Software Development” (LFEL1012). His other contributions include “Fully Countering Trusting Trust through Diverse Double-Compiling (DDC)”. He is the Director of Open Source Supply Chain Security at the Linux Foundation and teaches a graduate course in developing secure software at George Mason University (GMU).
Dean Wiley (dwiley258) is a Senior Software Engineer and Security Master at Ericsson with over five years of experience in Python development. He specialises in cloud-based solutions and automation tooling for cloud deployments, with a strong focus on security and building secure systems. Throughout his career, he has developed a keen interest in enforcing design rules and coding standards across codebases, as well as building tools to ensure ongoing compliance. Outside of work, he enjoys playing music, with a particular passion for bass guitar and cello.
Georg Kunz (gkunz) is a passionate advocate for open source software and a long term contributor to a wide range of open source projects and communities. He currently serves on the Technical Advisory Council (TAC) and the Governing Board of the Open Source Security Foundation (OpenSSF), co-chairs the OpenSSF Best Practices Working Group, and is a member of the TODO Group’s Steering Committee.
Noah Spahn (noah-de) is an open source software contributor and Associate Professor at Point Loma Nazarene University. He has a broad background in software development and DevSecOps, with experience in applications ranging from Earth science models to data center automation, network forensics and enterprise business solutions. David Mather (davidmather) currently working as Product Owner in Operations Support Systems (OSS) for large scale radio networks. David was one of the first contributors helping to architect the Secure Coding Guide for Python. Has been working as a software engineer and security master at Ericsson for several years. He encouraged team members, including Bartlomiej Karas and Andrew Costello, to contribute to the guide. Additionally, he collaborated with Bartlomiej Karas and Georg Kunz to demonstrate the project in [Vienna 2025] We envision a future where OSS is universally trusted, secure, and reliable. Join us in making open source more secure.
Part of the Cybersecurity Skills Guide — This article is one deep-dive in our complete guide series. Python’s readability makes it popular for web applications, automation, and data pipelines. That same readability can mask security problems — dangerous functions look harmless, and the standard library includes several footguns that developers use without thinking twice.
Command injection through os.system() and subprocess.shell=True is the most common Python vulnerability in security assessments. Never pass user input to a shell: With shell=False and a list of arguments, the input is passed as a single argument to the program, not interpreted by the shell. SQLAlchemy ORM queries are parameterized by default, but text() with string formatting is not.
Template injection in Jinja2 allows code execution when user input is rendered as a template. Never use Template(user_input).render() . Use render_template() with variables passed separately. pickle.loads() executes arbitrary Python code during deserialization. Never unpickle data from untrusted sources. This includes data from caches, message queues, and APIs where you do not control the sender.
Use JSON, MessagePack, or Protocol Buffers for serialization instead. If you must use pickle, implement __reduce__ restrictions and use hmac to verify data integrity before deserialization — though this is still inferior to avoiding pickle entirely. Flask's secret_key must be cryptographically random and stored in environment variables. A weak or hardcoded secret key allows session forgery.
Python dependencies are a supply chain risk. Use pip-audit to check for known vulnerabilities: Pin all dependency versions in requirements.txt or use poetry.lock / pipenv.lock . Review updates before applying them. Use safety as a second scanner — different tools use different vulnerability databases. Check for typosquatting: requests vs request , python-dateutil vs dateutil`. Verify package names before installing.
Secure Python development maps to Application Security Expert and DevSecOps roles. Python appears in web apps, automation pipelines, and infrastructure code — all of which need security review. Most practitioners build working proficiency in 4-8 weeks of dedicated study with hands-on practice. Mastery takes longer and comes primarily through on-the-job experience.
Certifications validate your knowledge to employers but are not strictly required. Hands-on experience and portfolio projects often carry more weight in technical interviews. Check the certification roadmap for relevant options. Explore the career path explorer to see which roles require this skill and how it fits into different cybersecurity specializations. HADESS Team consists of cybersecurity practitioners, hiring managers, and career strategists who have collectively spent 50+ years in the field.
3. Software Implementation, Frameworks & Protocols The team behind this article runs attack surface management, SAST, red team operations and vulnerability research for organizations that need answers, not checklists. Zero Trust Network Access: Identity-Centric Security Architecture. Skills, career paths, and how to get started on the HADESS platform.
Master cybersecurity skills for beginners with this 2026 guide covering technical, soft skills, certs, and study plans. Browse 80+ skills... CISSP requirements 2026 — exam domains, experience prerequisites, study strategies, and career impact of the gold-standard security...
Attack surface management, SAST, red team operations and vulnerability research — from the team behind HADESS research. In a controlled study by Horizon3 researchers, models that explicitly identified a trap in their reasoning still attacked it 73.4% of the time. Read the findings and see what they mean for canaries, decoys, and early detection.
Python's dependency ecosystem has unique supply chain characteristics that make it more challenging to secure than some alternatives. PyPI has minimal package publishing controls — anyone can publish a package with any name that is not already taken. Typosquatted package names, dependency confusion attacks, and packages that execute malicious code at install time have all been documented at scale. Meanwhile, legitimate popular packages regularly publish CVE fixes, and applications with hundreds of transitive dependencies accumulate vulnerability debt silently.
The tools to manage this — pip-audit, OSV-Scanner, and lockfiles with hash pinning — are mature and free. The gap between their existence and most teams using them is typically awareness and CI/CD integration effort. This guide provides both. Before enforcing any pipeline gates, you need a clear picture of your current vulnerability landscape across all Python services. This section covers how to run pip-audit and OSV-Scanner to generate a baseline findings report, interpret the output by severity and exploitability, and prioritize remediation starting with critical CVEs. It also addresses the most common baseline problem in Python environments: the absence of a lockfile, which makes the dependency set non-reproducible and unauditable. Running these scans for the first time in a mature codebase typically surfaces 5-20 vulnerabilities in transitive packages that the team was unaware of.
Run pip-audit -r requirements.txt -f json -o baseline.json on every Python service in your organization. Review the output: total packages scanned, total vulnerabilities found, and the breakdown by severity (critical, high, medium, low). In most mature codebases, a first scan reveals 5-20 vulnerabilities in transitive dependencies. Create a remediation priority list: fix critical CVEs first (CVSS 9.0+), then high (7.0-8.9), then address the lockfile absence if requirements.txt does not include hashes.
The baseline scan establishes where you are before enforcing CI gates — trying to enforce pip-audit --strict before knowing your baseline creates a pipeline that fails on day one. If your Python service uses only requirements.txt with version ranges (requests>=2.28.0) rather than pinned versions with hashes, generate a lockfile immediately. Using pip-tools: pip install pip-tools; pip-compile requirements.in --generate-hashes -o requirements.txt. The output includes exact pinned versions and SHA-256 hashes for all direct and transitive dependencies. Commit this file to version control. Update only when explicitly running pip-compile --upgrade. The lockfile prevents the 'it worked in dev but broke in prod because a different version was installed' problem and makes pip-audit output reproducible across environments.
Vulnerability scanning catches known CVEs in packages you have already installed, but supply chain hardening prevents unknown malicious packages from entering your environment in the first place. This section covers hash pinning with pip's --require-hashes flag, which aborts installation if any downloaded package fails its SHA-256 check against the lockfile record. It also covers configuring a private PyPI mirror using AWS CodeArtifact, Artifactory, or Nexus, and implementing a new-package approval gate that requires security review before any new direct dependency is merged. Together these controls address the typosquatting and dependency confusion attack vectors that vulnerability databases cannot catch because the malicious package has no CVE at the time of installation.
In your production deployment or CI pipeline: pip install --require-hashes -r requirements.txt. This flag forces pip to verify the SHA-256 hash of every downloaded package against the hash recorded in requirements.txt. If the downloaded package does not match — whether due to a compromised PyPI mirror, a BGP hijack, or a package maintainer backdoor that changes the package content for existing version numbers — the install fails with an error. This is a strong supply chain control with minimal operational overhead when using a lockfile with hashes generated by pip-compile --generate-hashes or Poetry.
For the highest security environments: proxy all PyPI traffic through a private artifact repository (AWS CodeArtifact, Artifactory, Nexus) where each package is vetted before being made available. Implement a new-dependency approval process: any pull request that adds a new package to requirements.in requires a security team review that checks the package's publication history, author reputation, download counts (fresh typosquatted packages have very low counts), and code review of the package's setup.py and __init__.py for malicious install-time code. This manual review gates the introduction of new packages without affecting the iteration speed of existing, approved packages.
Python dependency security requires three things working together: a scanner (pip-audit or OSV-Scanner) integrated into CI that blocks deployments of packages with critical CVEs, a lockfile with hash verification that pins the exact dependency set and prevents supply chain substitution, and a private mirror or new-package approval process that prevents typosquatted or malicious packages from entering your environment. Start with pip-audit in the CI pipeline — it takes 30 minutes to add and immediately surfaces CVEs you did not know existed. Add lockfile with hash pinning to all services within 30 days. Private mirror implementation is a longer project but the right target for any organization handling sensitive data or operating in regulated industries.
Install pip-audit: pip install pip-audit. Scan the current environment: pip-audit. Scan a specific requirements file: pip-audit -r requirements.txt. Scan a Poetry project: pip-audit --requirement <(poetry export --without-hashes). Output as JSON for CI integration: pip-audit -r requirements.txt -f json -o audit-results.json. pip-audit queries both the PyPI Advisory Database and OSV (Open Source Vulnerabilities) database, returning a list of vulnerable packages with CVE IDs, affected versions, and available fix versions. In CI/CD: run pip-audit --strict to exit with a non-zero status code when any vulnerability is found, which fails the pipeline and blocks deployment of vulnerable dependencies.
What is the difference between pip-audit, Safety, and OSV-Scanner for Python vulnerability scanning? pip-audit: official PyPA tool, queries PyPI Advisory Database and OSV, supports requirements.txt and installed environments, free, integrates with GitHub Actions and most CI systems. Ideal for most Python projects. Safety: commercial tool (safety.io), has a free tier with limited CVE database access, paid tier includes full database, provides compliance reports. Previously used the Safety DB but now primarily uses its own curated database. OSV-Scanner: Google's open-source tool, supports Python (requirements.txt, poetry.lock, Pipfile.lock), scans against the broader OSV database which aggregates CVEs from GitHub Advisory Database, NVD, and package-specific advisory databases. Better cross-language support (can scan the entire monorepo including Python, JavaScript, Go, Rust). For Python-only projects: pip-audit is the simplest choice. For polyglot repositories: OSV-Scanner provides unified scanning across all languages.
Defense layers for malicious package prevention: (1) Always use a lockfile (Poetry, pip-tools, or uv) that pins exact versions and hashes — this prevents resolution from ever fetching a newly published package when you run pip install. (2) Enable hash pinning in pip: generate requirements.txt with pip-compile --generate-hashes (from pip-tools) and install with pip install --require-hashes -r requirements.txt — any package whose hash does not match the lockfile causes the install to fail. (3) Configure a private PyPI mirror (Artifactory, Nexus, or AWS CodeArtifact) and add only vetted packages to it — restrict pip to only fetch from your private mirror by setting index-url in pip.conf. (4) In CI/CD: alert on any newly added package in a pull request and require security team review before merging new direct dependencies. (5) Use pip-audit --skip-editable to exclude local packages that should not be scanned.
A lockfile records the exact versions and hashes of all packages (direct and transitive) that are installed in a working environment. Without a lockfile: pip install resolves dependencies at install time, potentially fetching different versions on different machines or at different points in time — a CVE published in a transitive dependency after your last test run appears silently in your next deployment. With a lockfile (requirements.txt with hashes via pip-compile, poetry.lock, uv.lock, Pipfile.lock): every install uses exactly the versions recorded in the lockfile, making your dependency set auditable and reproducible. Generate for pip-tools: pip-compile requirements.in --generate-hashes -o requirements.txt. Generate for Poetry: poetry lock. Commit the lockfile to version control and update it deliberately (via pip-compile --upgrade or poetry update), which triggers your CI scanner to check for new CVEs in updated versions.
GitHub Actions example for pip-audit: add a job that runs after checkout and dependency installation: name: Security Audit, steps: [checkout, setup Python, install dependencies (pip install -r requirements.txt), run audit (pip-audit -r requirements.txt --strict)]. The --strict flag exits non-zero if any vulnerability is found, failing the pipeline. For a less disruptive initial setup: use pip-audit without --strict (exits 0 even with findings) for the first 30 days to establish a baseline, then switch to --strict after remediating existing findings. GitLab CI equivalent: run pip-audit in a security stage after the build stage, with artifacts configured to save the JSON output report. Combine with Dependabot (GitHub) or Renovate (universal) to receive automated PRs when pip-audit detects a fix is available by upgrading a specific package.
What should I do when pip-audit finds a CVE in a dependency I cannot immediately upgrade? When an immediate upgrade is not possible: (1) Assess exploitability: read the CVE description and determine whether your application uses the vulnerable code path. A CVE in an HTTP client library that only affects requests made with a specific authentication method may not be exploitable if your application does not use that method. (2) Check for a minimal patch: some packages publish security-only patch releases (e.g., upgrading from 2.1.0 to 2.1.1 fixes the CVE without changing APIs) — try the patch release in a staging environment. (3) Add a documented suppression: if the CVE is not exploitable in your context, add pip-audit --ignore-vuln GHSA-xxxx to your CI configuration with a comment documenting why — this prevents the CI from blocking deployments on a known, accepted risk while maintaining awareness of its existence. (4) File a ticket and set a remediation deadline — CVEs in dependencies without a fix plan become compliance findings.
A private PyPI mirror (also called an artifact repository) proxies PyPI packages through your controlled infrastructure, enabling you to: scan packages before making them available to developers, block packages that are not on an approved list, and cache packages for air-gapped or restricted environments. Options: AWS CodeArtifact (managed, supports PyPI format, integrates with IAM), JFrog Artifactory, Sonatype Nexus Repository, or DevPi (open source, self-hosted). Setup with AWS CodeArtifact: create a CodeArtifact domain and repository with a PyPI upstream, configure pip to use it: pip config set global.index-url https://your-domain.d.codeartifact.region.amazonaws.com/pypi/your-repo/simple/. Scan packages with your SCA tool before adding them to the approved list. Enforce the private mirror in CI by setting PIP_INDEX_URL in CI environment variables and blocking direct PyPI access via firewall rules in your CI environment.
25 actively exploited vulnerabilities with CVSS scores, exploit status, and patch availability. Print it, pin it, share it with your SOC team. Step-by-step 24-hour IR checklist covering detection, containment, eradication, and recovery. Built for SOC teams, IR leads, and CISOs.
50,000+ security professionals read Decryption Digest for early warnings on zero-days, ransomware, and nation-state campaigns. Free, daily, no spam. Cybersecurity professional with expertise in threat intelligence, vulnerability research, and enterprise security. Covers zero-days, ransomware, and nation-state operations for 50,000+ security professionals every morning.
Actionable threat intelligence for working practitioners. Free. No spam. Trusted by 50,000+ SOC analysts, CISOs, and security engineers. Contributions welcome! Web: https://best.openssf.org/Secure-Coding-Guide-for-Python/ GitHub: https://github.com/ossf/wg-best-practices-os-developers/tree/main/docs/Secure-Coding-Guide-for-Python An initiative by the OpenSSF to provide new Python programmers a resource to study secure coding in CPython >= 3.9 with working code examples.
Documentation is written in academic style to support security researchers while using plain English to cater for an international audience. Python modules outside of the Python Module Index [ Python 2023 ] are specifically not covered by this document. Content comes WITHOUT WARRANTY OF ANY KIND, EXPRESS OR IMPLIED , as stated in the license text CC-BY-4.0 for documentation and MIT . Following or using the documentation and or code is at your own risk. Code examples are intended purely for educational use and not for products in parts or in full. Code examples are NOT to be used to cause harm of any kind to anyone or anything.
Code examples are written to explain security design with as little code as possible. None of the code examples are intended to be used ‘as is’ for production. Using the code is at your own risk! It is not production code and requires code-style or python best practices to be added such as: As a software developer, ensuring the security of your Python code is paramount. Vulnerabilities can lead to severe consequences, including data breaches and system compromises. The process of auditing your code for vulnerabilities is a proactive step to identify and mitigate potential risks before they can be exploited. This requires a systematic approach to examine your codebase, use of security tools, and an understanding of common security pitfalls in Python.
A thorough code review is the first step in auditing your Python code. You should look for common security issues such as injection flaws , where untrusted input might be executed as code, or data leakage , where sensitive information could be exposed. Pay special attention to modules that handle user input, authentication, and data processing. It's also important to review your code for compliance with best practices, such as using parameterized queries to prevent SQL injection and applying the principle of least privilege when accessing system resources.
Software Engineer ll @ JP Morgan Chase & Co. | Expert In SpringBoot | Java | Microservices | Docker | Kubernetes | Angular | MySql | Kafka | Consul | Alfresco | Postgres | Quarkus | Vertx | Artificial Intelligence Conduct thorough manual code reviews, preferably by multiple reviewers. Look for common security issues like improper input validation, insecure deserialization, and lack of error handling. Utilize pair programming or peer reviews to catch more subtle issues.
To audit Python code for vulnerabilities: 1. Static Analysis: Use tools like Bandit or Python to detect potential security issues statistically. 2. Dependency Scanning: Regularly update and scan dependencies for known vulnerabilities using tools like piprot or safety. 3. Input Validation: Validate user inputs to prevent injection attacks (e.g., SQL injection, XSS). 4. Secure Configuration: Ensure sensitive information like API keys is stored securely and not hardcoded. 5. Code Reviews: Conduct thorough peer reviews, focusing on security best practices and potential vulnerabilities. Regular audits and proactive security measures are crucial to safeguarding Python applications from potential threats.
Software Developer @RTI | Full Stack Developer | MS in Computer Science @ IU Bloomington | Ex- Research Assistant @ IUB | Ex-TCS Code review is a fundamental step in auditing Python code for security vulnerabilities. This process should begin with a thorough manual inspection of the codebase, focusing on identifying common security issues such as insecure data handling, inadequate error and exception management, and weak authentication and authorization controls. Incorporating peer reviews is also crucial; colleagues can offer new perspectives and identify vulnerabilities that the original coder might overlook.
Static analysis involves using tools to automatically scan your Python code for vulnerabilities without actually executing it. These tools can detect a range of issues from syntax errors to complex security vulnerabilities like cross-site scripting (XSS) or buffer overflows . It's essential to integrate static analysis into your development workflow so that you can catch issues early. Remember, no tool can find every flaw, so this should complement, not replace, manual review and other security measures.
4. Practical Deployment, Analysis & Case Studies Software Developer @RTI | Full Stack Developer | MS in Computer Science @ IU Bloomington | Ex- Research Assistant @ IUB | Ex-TCS Tools like Bandit, PyLint, and SonarQube are effective in detecting a variety of security issues including SQL injections, XSS, CSRF vulnerabilities, and more. Integrating these tools into the Continuous Integration/Continuous Deployment (CI/CD) pipeline is essential as it allows for continuous scanning of the code as it is being written and committed.
Software Engineer ll @ JP Morgan Chase & Co. | Expert In SpringBoot | Java | Microservices | Docker | Kubernetes | Angular | MySql | Kafka | Consul | Alfresco | Postgres | Quarkus | Vertx | Artificial Intelligence Use static analysis tools like Bandit, Flake8, or Pylint to scan the code for vulnerabilities. These tools can automatically detect issues such as hardcoded credentials, unsafe imports, and potential code injection points. Regularly update and configure the tools to cover the latest security best practices.
Dynamic testing is the process of auditing your Python code by executing it in an environment that simulates real-world operations. This allows you to observe how your code behaves under different conditions and identify vulnerabilities that might not be visible through static analysis alone. Use automated tools to send a variety of inputs to your application to test for weaknesses like improper error handling or insecure session management . Be sure to test all endpoints and consider the perspective of an attacker trying to exploit your system.
Software Engineer ll @ JP Morgan Chase & Co. | Expert In SpringBoot | Java | Microservices | Docker | Kubernetes | Angular | MySql | Kafka | Consul | Alfresco | Postgres | Quarkus | Vertx | Artificial Intelligence Implement dynamic analysis by running the application and testing it with tools like OWASP ZAP or Burp Suite. Perform penetration testing to find vulnerabilities that only appear during runtime. Test the application in various environments to simulate different attack scenarios.
Your Python project likely uses third-party libraries, which can also be a source of vulnerabilities. Regularly check your dependencies for known vulnerabilities using tools designed for this purpose. Ensure you're using the most up-to-date and secure versions of libraries, and consider alternatives if a dependency is no longer maintained or has known security issues. Managing your dependencies effectively is crucial for maintaining the overall security of your Python codebase.
Software Engineer ll @ JP Morgan Chase & Co. | Expert In SpringBoot | Java | Microservices | Docker | Kubernetes | Angular | MySql | Kafka | Consul | Alfresco | Postgres | Quarkus | Vertx | Artificial Intelligence Regularly audit dependencies using tools like pip-audit, Safety, or Dependabot. Check for known vulnerabilities in third-party libraries and frameworks. Ensure that all dependencies are up-to-date and maintained by their authors.
AI @ Apple I | MCP Apps | LLM | Graph Engineering | Harness Engineering | Loop Engineering | Cloud Agents | Prompt Engineering | RAG | Fine Tuning | Apps SDK | MCP Tools | A2A | NL2SQL | Data Pipeline | Scalability | To audit your Python code for vulnerabilities, start with a thorough dependency check. Third-party libraries can introduce security risks. For instance, using an outdated framework in your web application may leave you exposed to attacks.
Regularly use tools to scan for vulnerabilities in your dependencies; these tools will alert you to outdated or insecure libraries. In our example, such a tool would flag the outdated framework, prompting an immediate update. Periodically review your dependency list to ensure you're using secure, up-to-date versions and consider alternatives for unmaintained libraries. This proactive dependency management is key to securing your Python project.
Configuration settings in your Python application can inadvertently introduce security weaknesses. Audit your configuration files and environment settings for security misconfigurations such as overly verbose error messages, default credentials, or unnecessary services running. Make sure you have a secure configuration management process in place, including the use of environment variables for sensitive information and regular reviews of configuration settings.
Software Engineer ll @ JP Morgan Chase & Co. | Expert In SpringBoot | Java | Microservices | Docker | Kubernetes | Angular | MySql | Kafka | Consul | Alfresco | Postgres | Quarkus | Vertx | Artificial Intelligence Review application and server configurations to ensure they follow security best practices. Check for issues like unnecessary open ports, weak passwords, and insecure file permissions. Ensure that environment variables and secrets are managed securely, avoiding hardcoding them in the source code.
Finally, staying educated on the latest security practices and vulnerabilities is essential for auditing your Python code effectively. Security is an ever-evolving field, and what was considered secure yesterday may not be today. Take advantage of online resources, communities, and training to keep your knowledge up-to-date. Understanding the current threat landscape will enable you to write more secure code and better audit the code you've already written.
Software Engineer ll @ JP Morgan Chase & Co. | Expert In SpringBoot | Java | Microservices | Docker | Kubernetes | Angular | MySql | Kafka | Consul | Alfresco | Postgres | Quarkus | Vertx | Artificial Intelligence Stay informed about the latest security threats and best practices by following security blogs, forums, and attending relevant conferences. Take online courses and certifications in cybersecurity to enhance your knowledge. Encourage your team to participate in security training sessions and workshops.
This is a space to share examples, stories, or insights that don’t fit into any of the previous sections. What else would you like to add? Software Engineer ll @ JP Morgan Chase & Co. | Expert In SpringBoot | Java | Microservices | Docker | Kubernetes | Angular | MySql | Kafka | Consul | Alfresco | Postgres | Quarkus | Vertx | Artificial Intelligence Implement a security policy that includes regular audits, incident response plans, and clear guidelines for handling vulnerabilities. Engage in bug bounty programs to leverage the broader security community in identifying vulnerabilities. Use secure coding guidelines and frameworks to minimize the risk of introducing vulnerabilities in the first place.
You're troubleshooting server performance issues. How can you work with admins to pinpoint the bottlenecks? You're juggling new programming languages and urgent coding tasks. How can you strike a perfect balance? Your team is losing motivation on a long-term software project. How can you reignite their passion and drive? Your team’s coding styles are all over the place. How do you unify them without killing creativity? Your software needs seamless integration with third-party APIs. How do you ensure smooth communication? You're facing resistance from project stakeholders. How can you effectively convey the impact of bugs? Dealing with an overcommitting team member in Agile sprint planning. Can you help them find a balance? What happens when your audit logs—the very records meant to prove compliance—become your biggest liability? In 2026, with regulatory fines averaging $4.7 million per violation and quantum computing threatening current cryptographic standards, secure audit logging isn't just a checkbox—it's a business-critical defense system. This guide shows you how to build immutable, tamper-proof audit logs using Python that will withstand both today's attacks and tomorrow's quantum threats.
Note: Real implementations include additional fields like user agent, geolocation, risk scores, and regulatory metadata (SOX, GDPR, HIPAA). The problem isn't just about storing logs—it's about proving they haven't been altered. In 2026, we're seeing a perfect storm: sophisticated attackers targeting audit trails, regulators demanding cryptographic proof of integrity, and quantum computing threatening current encryption standards. Traditional logging fails because: The root cause? Most logging systems treat logs as mutable data rather than immutable records requiring cryptographic protection. This guide solves that with a Python-based system that provides mathematical proof of integrity while maintaining performance.
Below is a complete, production-ready implementation of a secure audit logger with hash chaining: Building a secure audit log system requires careful consideration of storage, performance, and cryptographic choices. Here's our step-by-step approach: Data Flow: Producers -> Audit Logger -> Hash Chain Manager -> Immutable Storage. Index Database updated in parallel.
Verification Service runs independently. Merkle trees allow verification of individual log entries without validating the entire chain: Testing a secure audit system requires verifying both functional correctness and security properties. Here's our comprehensive testing approach: Implementing cryptographic security adds overhead, but with proper optimization, the impact is minimal. Here are our benchmark results: The key insight: while logging performance decreases by 15-25%, verification performance improves by 85%, and compliance proof generation goes from hours to seconds. For most applications, this trade-off is well worth it.
Solution: Use logical clocks (Lamport timestamps) alongside physical timestamps. Store both and use logical order for chain verification. Solution: Implement key versioning and epoch-based signatures. Each entry includes key version, and verification checks against appropriate key.
Solution: Implement checksums (CRC32) for each batch file and regular integrity verification runs. Store redundant copies in geographically distributed WORM storage. Challenge: After a 2025 audit revealed 14% of their transaction logs showed signs of potential tampering, NexaPay faced $8.2M in potential fines from PCI-DSS and SOX violations. Their existing logging system used standard database triggers with no cryptographic protection.
Key Insight: While storage costs increased by 12.5% and throughput decreased slightly, the reduction in audit preparation time (320 → 18 hours) and insurance premiums ($420K → $285K) resulted in net annual savings of $1.47M. More importantly, NexaPay avoided $8.2M in potential fines. 5. Performance Evaluation & Extended Technical Observations Our Recommendation: Implement hybrid signatures now (classical + post-quantum) to ensure logs remain verifiable even after quantum computers become practical.
Your cryptographic system is only as secure as your key management. Use hardware security modules (HSMs) for production, and implement key rotation from day one. Never store keys with your application code. Individual signature operations are expensive. Batch 50-100 log entries before signing, and use asynchronous I/O to prevent blocking. This reduces overhead from 50% to under 20%.
Always build a separate verification service that can run independently of your logging system. This provides defense-in-depth and allows auditors to verify logs without accessing production systems. Cryptographic standards evolve. Design your system to support multiple signature algorithms and hash functions. Use versioned signatures so you can migrate to new algorithms without breaking existing logs.
Python cryptography library documentation, NIST post-quantum cryptography standards, AWS S3 Object Lock documentation "Building Tamper-Evident Logs" (USENIX), "Post-Quantum Cryptography for Developers" (PyCon) NIST post-quantum algorithm performance benchmarks, Cloud storage WORM compliance comparisons A: Typically 20-30% due to hashes, signatures, and metadata. However, compression (gzip) reduces this to 10-15%. The compliance benefits usually outweigh the storage costs.
A: Yes! Our system can wrap existing loggers. You can start with a hybrid approach where critical events use secure logging while debug logs use traditional methods. A: We implement cryptographic erasure: encrypt each user's data with a unique key, then destroy the key when erasure is requested. The encrypted data remains but is permanently inaccessible.
A: Provide auditors with our verification service and the Merkle root. They can verify any log entry against the root without accessing your systems. We also generate compliance certificates signed by the system. Secure audit logging isn't just a technical requirement—it's a business imperative in 2026's regulatory landscape. By implementing cryptographic hash chains, quantum-resistant signatures, and immutable storage, you transform audit logs from a compliance burden into a competitive advantage.
The performance overhead is manageable (15-25%), while the benefits are substantial: automated compliance proofs, tamper detection, and future-proofing against quantum threats. As NexaPay's case study shows, the ROI extends beyond compliance to reduced insurance premiums and avoided fines. "We went from dreading audits to welcoming them. Our secure logs now tell a story of integrity that builds trust with customers, regulators, and partners alike." Next Steps: Start with a pilot implementation for your most critical logs. Use our code examples as a foundation, adapt to your specific compliance requirements, and measure the impact. The future of compliance is cryptographic, and the time to build is now.
Filed under implementing , secure , audit , logs , real world , problem solving 2 , ai ml , 6g , space tech and biotech . Learn the essential steps for conducting a Python security audit using the OWASP Top 10 framework to secure your applications effectively. Securing Python web applications requires a systematic approach to identifying and addressing vulnerabilities. Just as Mozilla conducts rigorous security audits of Firefox to protect millions of users, organizations must implement comprehensive security reviews of their Python applications. The OWASP Top 10 2025 provides a framework for understanding the most critical web application security risks, and new tools make it easier than ever to conduct thorough Python security audits .
The OWASP Top 10 represents the consensus view of the most critical security risks facing web applications. The 2025 update reflects the evolving threat landscape and includes categories that address modern development practices and emerging attack vectors. For Python developers, understanding these categories is essential for building secure applications from the ground up.
The OWASP Top 10 2025 includes broken access control, cryptographic failures, injection attacks, insecure design, security misconfiguration, vulnerable and outdated components, authentication and session management failures, software and data integrity failures, logging and monitoring failures, and server-side request forgery (SSRF). Each category represents a class of vulnerabilities that can have severe consequences if left unaddressed.
Python's popularity in web development, data science, and automation makes it an attractive target for attackers. The language's flexibility and ease of use can sometimes lead developers to prioritize functionality over security. A comprehensive Python security audit helps identify weaknesses in authentication mechanisms, data validation, encryption practices, and access controls.
Injection Attacks remain one of the most common vulnerabilities in Python applications. SQL injection, command injection, and template injection can allow attackers to execute arbitrary code or access unauthorized data. Proper input validation, parameterized queries, and the use of ORM frameworks can mitigate these risks. Broken Authentication and Session Management create opportunities for attackers to compromise user accounts. Weak password policies, insecure session handling, and inadequate multi-factor authentication implementation are common issues.
Python developers should implement strong authentication mechanisms and use established libraries rather than building custom solutions. Cryptographic Failures occur when sensitive data is not properly encrypted or when weak encryption algorithms are used. This includes failures in key management, insufficient encryption of data in transit, and improper handling of sensitive information. Python applications should use well-tested cryptographic libraries and follow industry best practices for key management.
Security Misconfiguration affects many Python applications, particularly those deployed in cloud environments. Default credentials, unnecessary services, outdated dependencies, and overly permissive access controls create security gaps. Regular configuration reviews and infrastructure-as-code practices help prevent these issues. Modern security tools can significantly streamline the audit process. Static application security testing (SAST) tools analyze source code without executing it, identifying potential vulnerabilities early in the development lifecycle. Dynamic application security testing (DAST) tools test running applications to find runtime vulnerabilities.
For Python specifically, tools like Bandit perform static security analysis, identifying common security issues in Python code. Safety checks Python dependencies for known vulnerabilities. These tools integrate into CI/CD pipelines, enabling continuous security monitoring throughout the development process. AI-powered security agents represent the next evolution in automated security review. These tools can analyze code patterns, understand application context, and provide intelligent recommendations for remediation. They can simulate the thorough, methodical approach that security professionals take when conducting manual audits, but at scale and with greater consistency.
A successful Python security audit combines automated tools with manual review by experienced security professionals. The process should begin with asset inventory and threat modeling to understand what needs protection and from whom. Developers should then conduct code reviews focusing on the OWASP Top 10 categories, paying particular attention to input validation, authentication, and data protection.
Dependency Analysis is critical, as many Python applications rely on third-party packages. Regular updates and vulnerability scanning of dependencies help prevent exploitation of known vulnerabilities. Configuration review should examine environment variables, database connections, API keys, and access controls. Effective security requires integration throughout the development lifecycle, not just at the end. Security training for developers ensures they understand common vulnerabilities and secure coding practices. Code review processes should include security considerations alongside functionality and code quality.
Automated security scanning in CI/CD pipelines catches vulnerabilities early when they are cheaper and easier to fix. Pre-commit hooks can prevent developers from committing code with obvious security issues. Regular dependency updates and vulnerability scanning should be automated and monitored. Security testing should be part of the definition of done for features. This includes unit tests for security-critical functionality, integration tests for authentication and authorization, and regular security regression testing.
Mozilla's approach to Firefox security provides valuable lessons for Python developers. Mozilla conducts regular security audits, maintains a bug bounty program, and responds quickly to reported vulnerabilities. The organization prioritizes security in its development culture and invests in security tooling and training. Securing Python applications is an ongoing process that requires commitment, tools, and expertise. The OWASP Top 10 2025 provides a framework for understanding critical vulnerabilities. Automated tools enable efficient scanning and continuous monitoring. Combining these with secure development practices and security expertise creates a comprehensive approach to application security.
Developers who invest in understanding and implementing these security practices protect their users, their organizations, and their own professional reputation. By treating security with the same rigor that Mozilla applies to Firefox, Python development teams can build applications that are both functional and secure. Regular audits, continuous monitoring, and a security-first culture are essential components of a robust application security program.
What is a Python security audit? A Python security audit is a systematic evaluation of a Python application to identify and mitigate security vulnerabilities. Why is the OWASP Top 10 important? The OWASP Top 10 provides a list of the most critical security risks to web applications, helping developers prioritize their security efforts.
How can automated tools help in a security audit? Automated tools can quickly identify vulnerabilities in code and running applications, making the audit process more efficient. What are common vulnerabilities in Python applications? Common vulnerabilities include injection attacks, broken authentication, cryptographic failures, and security misconfigurations.
How often should security audits be conducted? Security audits should be conducted regularly, especially after significant changes to the application or its environment. Originally published on Talk Python Blog: Audit Your Python App Like Mozilla Audited Firefox Discover how Loopers enhances AI security with its innovative fail-closed firewall design. Learn essential steps to implement it effectively.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/E%20%28programming%20language%29 • https://en.wikipedia.org/wiki/Helios%20Voting • https://en.wikipedia.org/wiki/SecureDrop • https://github.com/Ambitiousways/secure-infra-audit-toolkit • https://developers-heaven.net/blog/architecting-secure-python-systems-threat-modeling-authentication-and-authorization/ • https://openssf.org/blog/2026/05/12/secure-coding-guide-for-python-pyscg-first-release/ • https://hadess.io/blog/read/secure-coding-python • https://www.decryptiondigest.com/blog/python-pip-dependency-security-pypi-audit-guide • https://best.openssf.org/Secure-Coding-Guide-for-Python/ • https://www.linkedin.com/advice/3/what-steps-should-you-take-audit-your-python-n7zke
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Secure Source Code Auditing Tool For Python Programs.
[*] Metasploit Scan Running on Target Subnet for Secure Source Code Auditing Tool For Python Programs... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |